


Abstract
A paradigm that combines cloud computing and the Internet of Things (IoT) allows for more impressive services to be provided to users while addressing storage and computational resource issues in the IoT environments. This cloud-based IoT environment has been used in various industries, including public services, for quite some time, and has been researched in academia. However, various security issues can arise during the communication between IoT devices and cloud servers, because communication between devices occurs in open channels. Moreover, issues such as theft of a user’s IoT device or extraction of key parameters from the user’s device in a remote location can arise. Researchers interested in these issues have proposed lightweight mutual authentication key agreement protocols that are safe and suitable for IoT environments. Recently, a lightweight authentication scheme between IoT devices and cloud servers has been presented. However, we found out their scheme had various security vulnerabilities, vulnerable to insider, impersonation, verification table leakage, and privileged insider attacks, and did not provide users with untraceability. To address these flaws, we propose a provably secure lightweight authentication scheme. The proposed scheme uses the user’s biometric information and the cloud server’s secret key to prevent the exposure of key parameters. Additionally, it ensures low computational costs for providing users with real-time and fast services using only exclusive OR operations and hash functions in the IoT environments. To analyze the safety of the proposed scheme, we use informal security analysis, Burrows–Abadi–Needham (BAN) logic and a Real-or-Random (RoR) model. The analysis results confirm that our scheme is secure against insider attacks, impersonation attacks, stolen verifier attacks, and so on; furthermore, it provides additional security elements. Simultaneously, it has been verified to possess enhanced communication costs, and total bit size has been shortened to 3776 bits, which is improved by almost 6% compared to Wu et al.’s scheme. Therefore, we demonstrate that the proposed scheme is suitable for cloud-based IoT environments.
1. Introduction
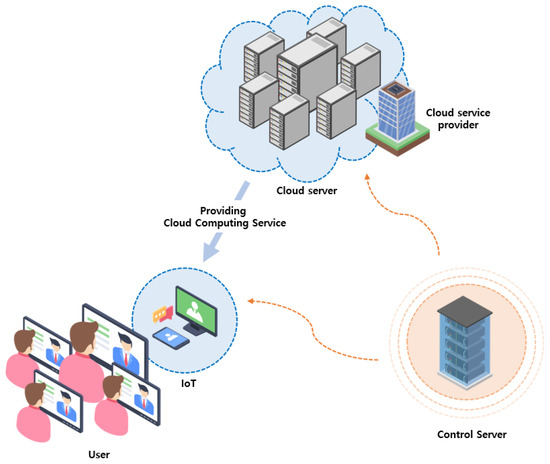
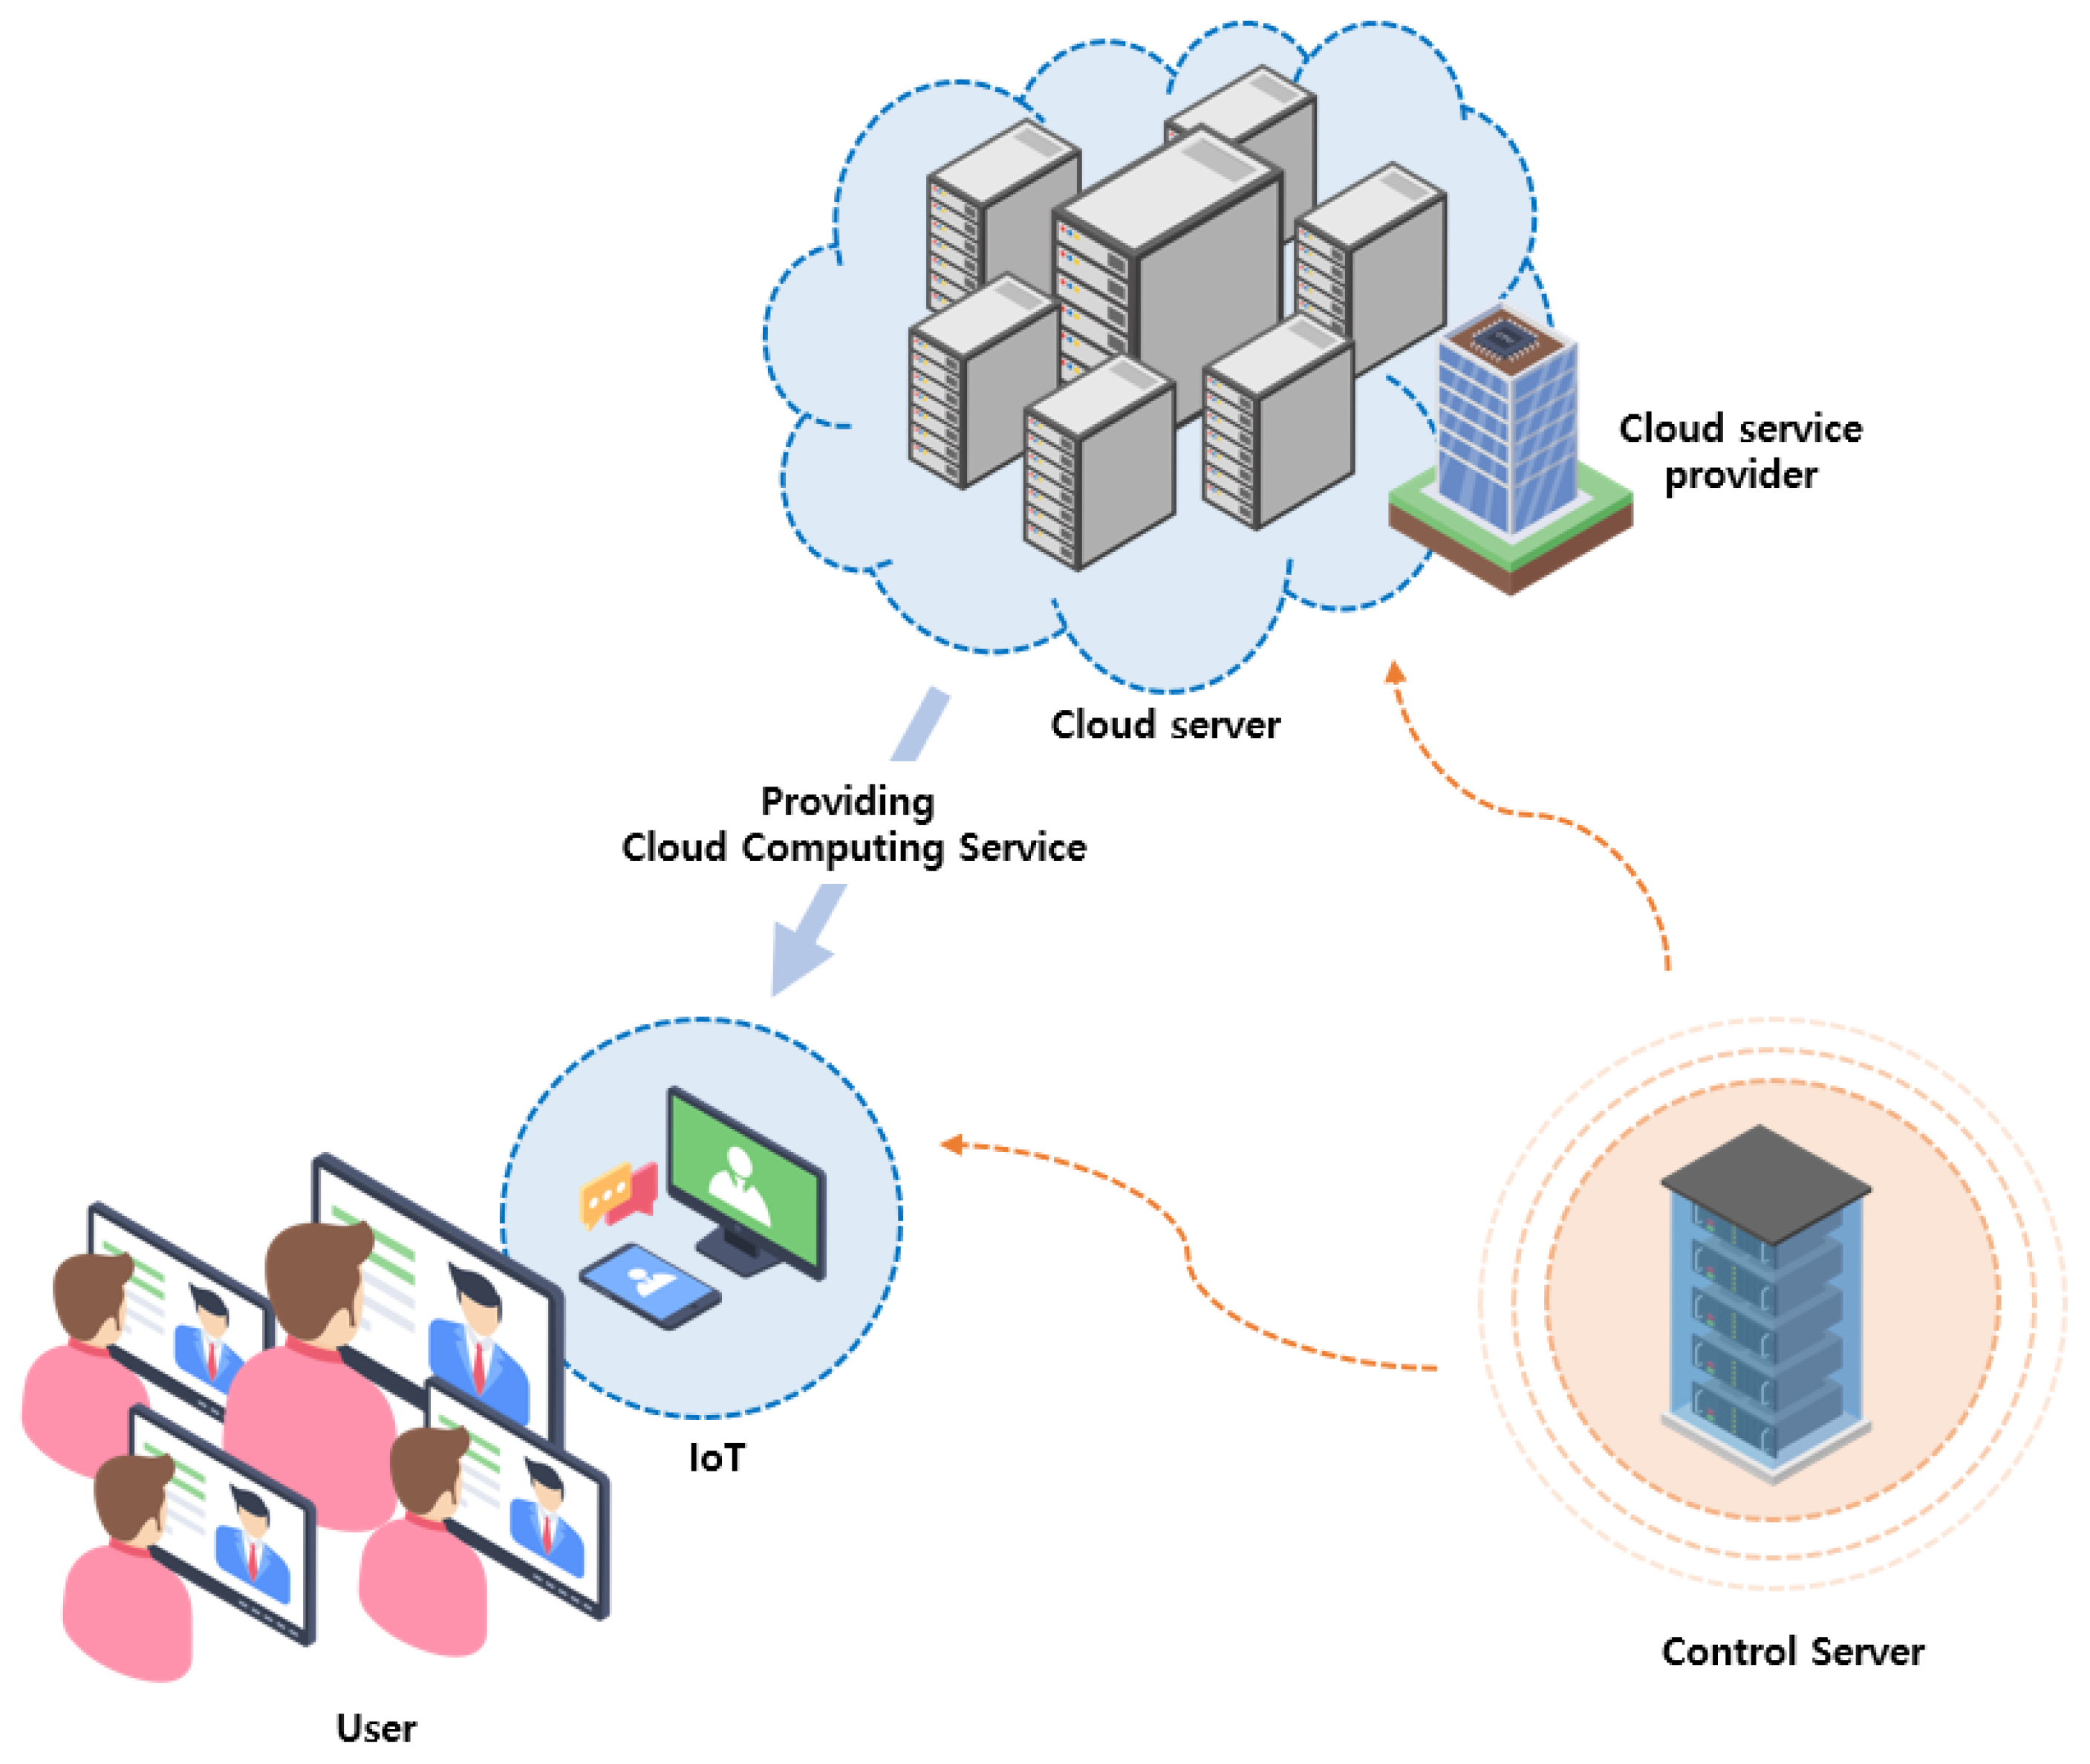
The Internet of Things (IoT) is a network in which Internet-enabled objects interact with each other through the internet [1,2]. IoT objects collect data from their surroundings, provide web services to users, and communicate with each other. Therefore, IoT objects such as smart devices need significant resources to store data collected from sensors and perform real-time computations using limited hardware. Hence, addressing the limitations of storage and computing capacities is crucial for the formation of a network of IoT objects [3,4,5]. However, cloud computing technology refers to the practice of moving computational power and storage space from individual devices to larger shared data centers [6]. Cloud computing allows access to a shared pool of computing resources such as networks, servers, storage, and applications. By using cloud computing, it becomes possible to overcome the limitations inherent in IoT devices [7,8,9,10]. The development and discussion of cloud-based IoT (CloudIoT) have been ongoing since before 2008 and continue to evolve. Figure 1 illustrates the structure of CloudIoT. This structure comprises three entities: user, cloud server, and control server. Users with IoT devices can access the resources provided by the cloud service provider’s server anytime and anywhere through IoT objects. The cloud server collects user’s requests and delivers the right service through IoT. The control server, acting as a trusted entity, generates the necessary parameters for communication between authenticated users and the cloud server through the registration process. Additionally, it monitors the key agreement phase to ensure that users and the cloud server establish the same session key for subsequent communications when needed.
Figure 1.
Cloud-based IoT enviroment.
In 2022, Wu et al. [11] proposed a lightweight authentication protocol for IoT-enabled cloud computing environments. The authors argued that their scheme could resist various attacks, such as man-in-the-middle, insider, DDoS, and masquerade attacks, and provides privacy, traceability, and integrity. However, we identified several vulnerabilities in Wu et al.’s scheme, including susceptibility to insider attacks, verification table attacks, user impersonation, and cloud server impersonation. Furthermore, the scheme lacks user untraceability, allowing an attacker to track the same user across different sessions through message eavesdropping alone. To address these vulnerabilities, we propose a provably secure lightweight mutual authentication and key agreement (MAKA) scheme. In our proposed scheme, we protect crucial parameters stored in the user’s IoT smart card using the user’s biometric information to prevent attacks like user impersonation and offline password-guessing. We also enhanced security by adding a secret key to the cloud server, preventing attackers from exploiting leaked database values. Additionally, we reduced the communication and computation overhead by employing only hash functions and exclusive-OR operations.
1.1. Research Contributions
We review and conduct a security analysis of Wu et al.’s authentication scheme. We demonstrate that Wu et al.’s scheme is vulnerable to insider attacks, verification table leakage attacks privileged insider attacks, user impersonation, and cloud server impersonation. Additionally, we propose an MAKA for cloud-based IoT environments that leverages biometric information. The proposed scheme is tailored to the IoT environments, using only exclusive OR operations and hash functions to align with a lightweight architecture. Additionally, we use a Real-or-Random (RoR) model and Burrow–Abadi–Needham (BAN) logic to demonstrate formally the security and robustness of the proposed. Moreover, we substantiate the security of our scheme against different attacks, including insider attacks, impersonation attacks, reply and man-in-the-middle (MITM) attacks, privileged insider attacks, ephemeral security leakage, stolen verifier attacks, DoS attacks, and session key disclosure attacks. In addition, we confirmed that our scheme can provide user anonymity, user untraceability, perfect forward secrecy, and mutual authentication. Last, we evaluate the security features, communication costs, and computation costs of the proposed scheme with related schemes, including Wu et al.’s.
1.2. Organization
In Section 2, we introduce studies related to cloud-based IoT, IoT, and cloud computing. We present the system model and adversary model used in our proposed scheme in Section 3. Following that, we discuss Wu et al.’s scheme in Section 4. We then delve into the vulnerabilities we identified in Wu et al.’s scheme in Section 5. In Section 6, we introduce our proposed scheme, and in Section 7, we provide security analyses using tools such as BAN logic, and RoR model. Performance analyses, including security features, communication, and computation costs, are presented in Section 8. Finally, in Section 9, we conclude our paper and outline future plans.
2. Related Works
When providing services to users over the internet, application security is crucial in gaining user trust. To access various services, including storage services provided by cloud service providers, the environments should be well prepared to handle various attacks and security threats that may exist. Furthermore, in IoT environments, lightweight protocol computations are essential to provide users with a seamless real-time service anytime, anywhere. In the following sections, we will review the authentication protocols in the existing cloud-based IoT environments.
In 2019, Schouqi et al. [12] introduced an authentication protocol for IoT built on Nikooghadam et al.’s [13] protocol. The protocol of Nikooghadam et al. was developed as a responses to issues with the authentication protocol proposed by Kumari et al. [14]. However, Nikooghadam et al.’s scheme has already been analyzed by researchers in the field, including Limbasiya et al., Chandrakar-Om, and Sharma-Kalra [15,16,17]. These researchers raised concerns about its security, highlighting vulnerabilities to various attacks such as password-guessing, insiders, and modification attacks. They also indicated that the protocol lacked forward secrecy and did not provide session key verification and a biometric update phase. The author of the new scheme reviewed the security issues known in Nikooghadam et al.’s protocol and proposed enhancements based on these findings.
Prosanta and Biplab (Prosanta-Biplab) [18] proposed lightweight two-factor authentication scheme for IoT devices in 2019. They argued that two-factor authentication schemes that use a passwords and smartcards, often vulnerable to physical attacks. To overcome these security issues they suggested physically uncloneable functions(PUF) as an authentication factor for IoT devices. However, in 2020, Siddiqui et al. [19] demonstrated that the scheme is vulnerable to man-in-the-middle, impersonations, session- hijacking and conventional and differential template attacks.
In 2019, Zhou et al. [20] presented a lightweight two-factor authentication scheme for IoT devices available in the cloud environments. In the same year, Rafael et al. [21] indicated that Zhou et al.’s scheme has several security issues. Rafael et al. demonstrated that Zhou et al.’s scheme failed to provide mutual authentication, was unsuccessful in protecting the secret key, and was vulnerable to various attacks, including insider attacks and man-in-the-middle attacks.
In 2020, Alzahrani et al. [22] presented an authentication protocol for IoT environments based on self-certified public keys and elliptic curve cryptography (ECC). Alzahrani conducted research on protocols proposed by Islam-Biswas [23] and Mandal et al. [24], highlighting their failure to ensure user anonymity and vulnerability to impersonation attacks. Therefore, the author developed a protocol that guarantees anonymity among connected devices and addresses security vulnerabilities. However, this scheme does not guarantee security against physical attacks.
Chen et al. [25] proposed a lightweight user authentication and key-agreement scheme for IoT. Chen et al. utilized XOR operations, hash functions, and elliptical multiplication. Lee et al. [26] indicated that Chen et al.’s scheme did not provide a steal-resistant smartcard offline password, offline identity guessing and reply attack. Subsequently, in 2020, Ye et al. [27] proposed an authentication and key agreement scheme for IoT-based cloud computing environments by advancing the protocol developed by He et al. [28]. Ye et al. addressed various security issues in the scheme proposed by He et al, such as failure to resist insider attacks, offline password-guessing, user impersonation, and potential DoS attacks.
Table 1, summarizes cryptographic technologies and limitations of various authentication schemes related to IoT, cloud-based IoT, and cloud computing environments. Related papers propose various protocols to provide users with secure and fast services in the CloudIoT environment. However, there are still vulnerabilities and challenges in fully supporting security features, as some attacks persist. Additionally, methods using symmetric keys like ECC may incur higher computation costs in IoT environments. Therefore, our goal is to design a lightweight protocol tailored for IoT environments using XOR and to achieve higher security in our scheme.
Table 1.
Authentication scheme overview.
3. Preliminaries
3.1. System Model
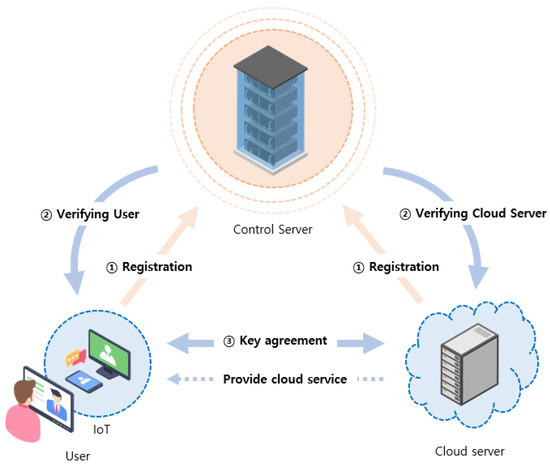
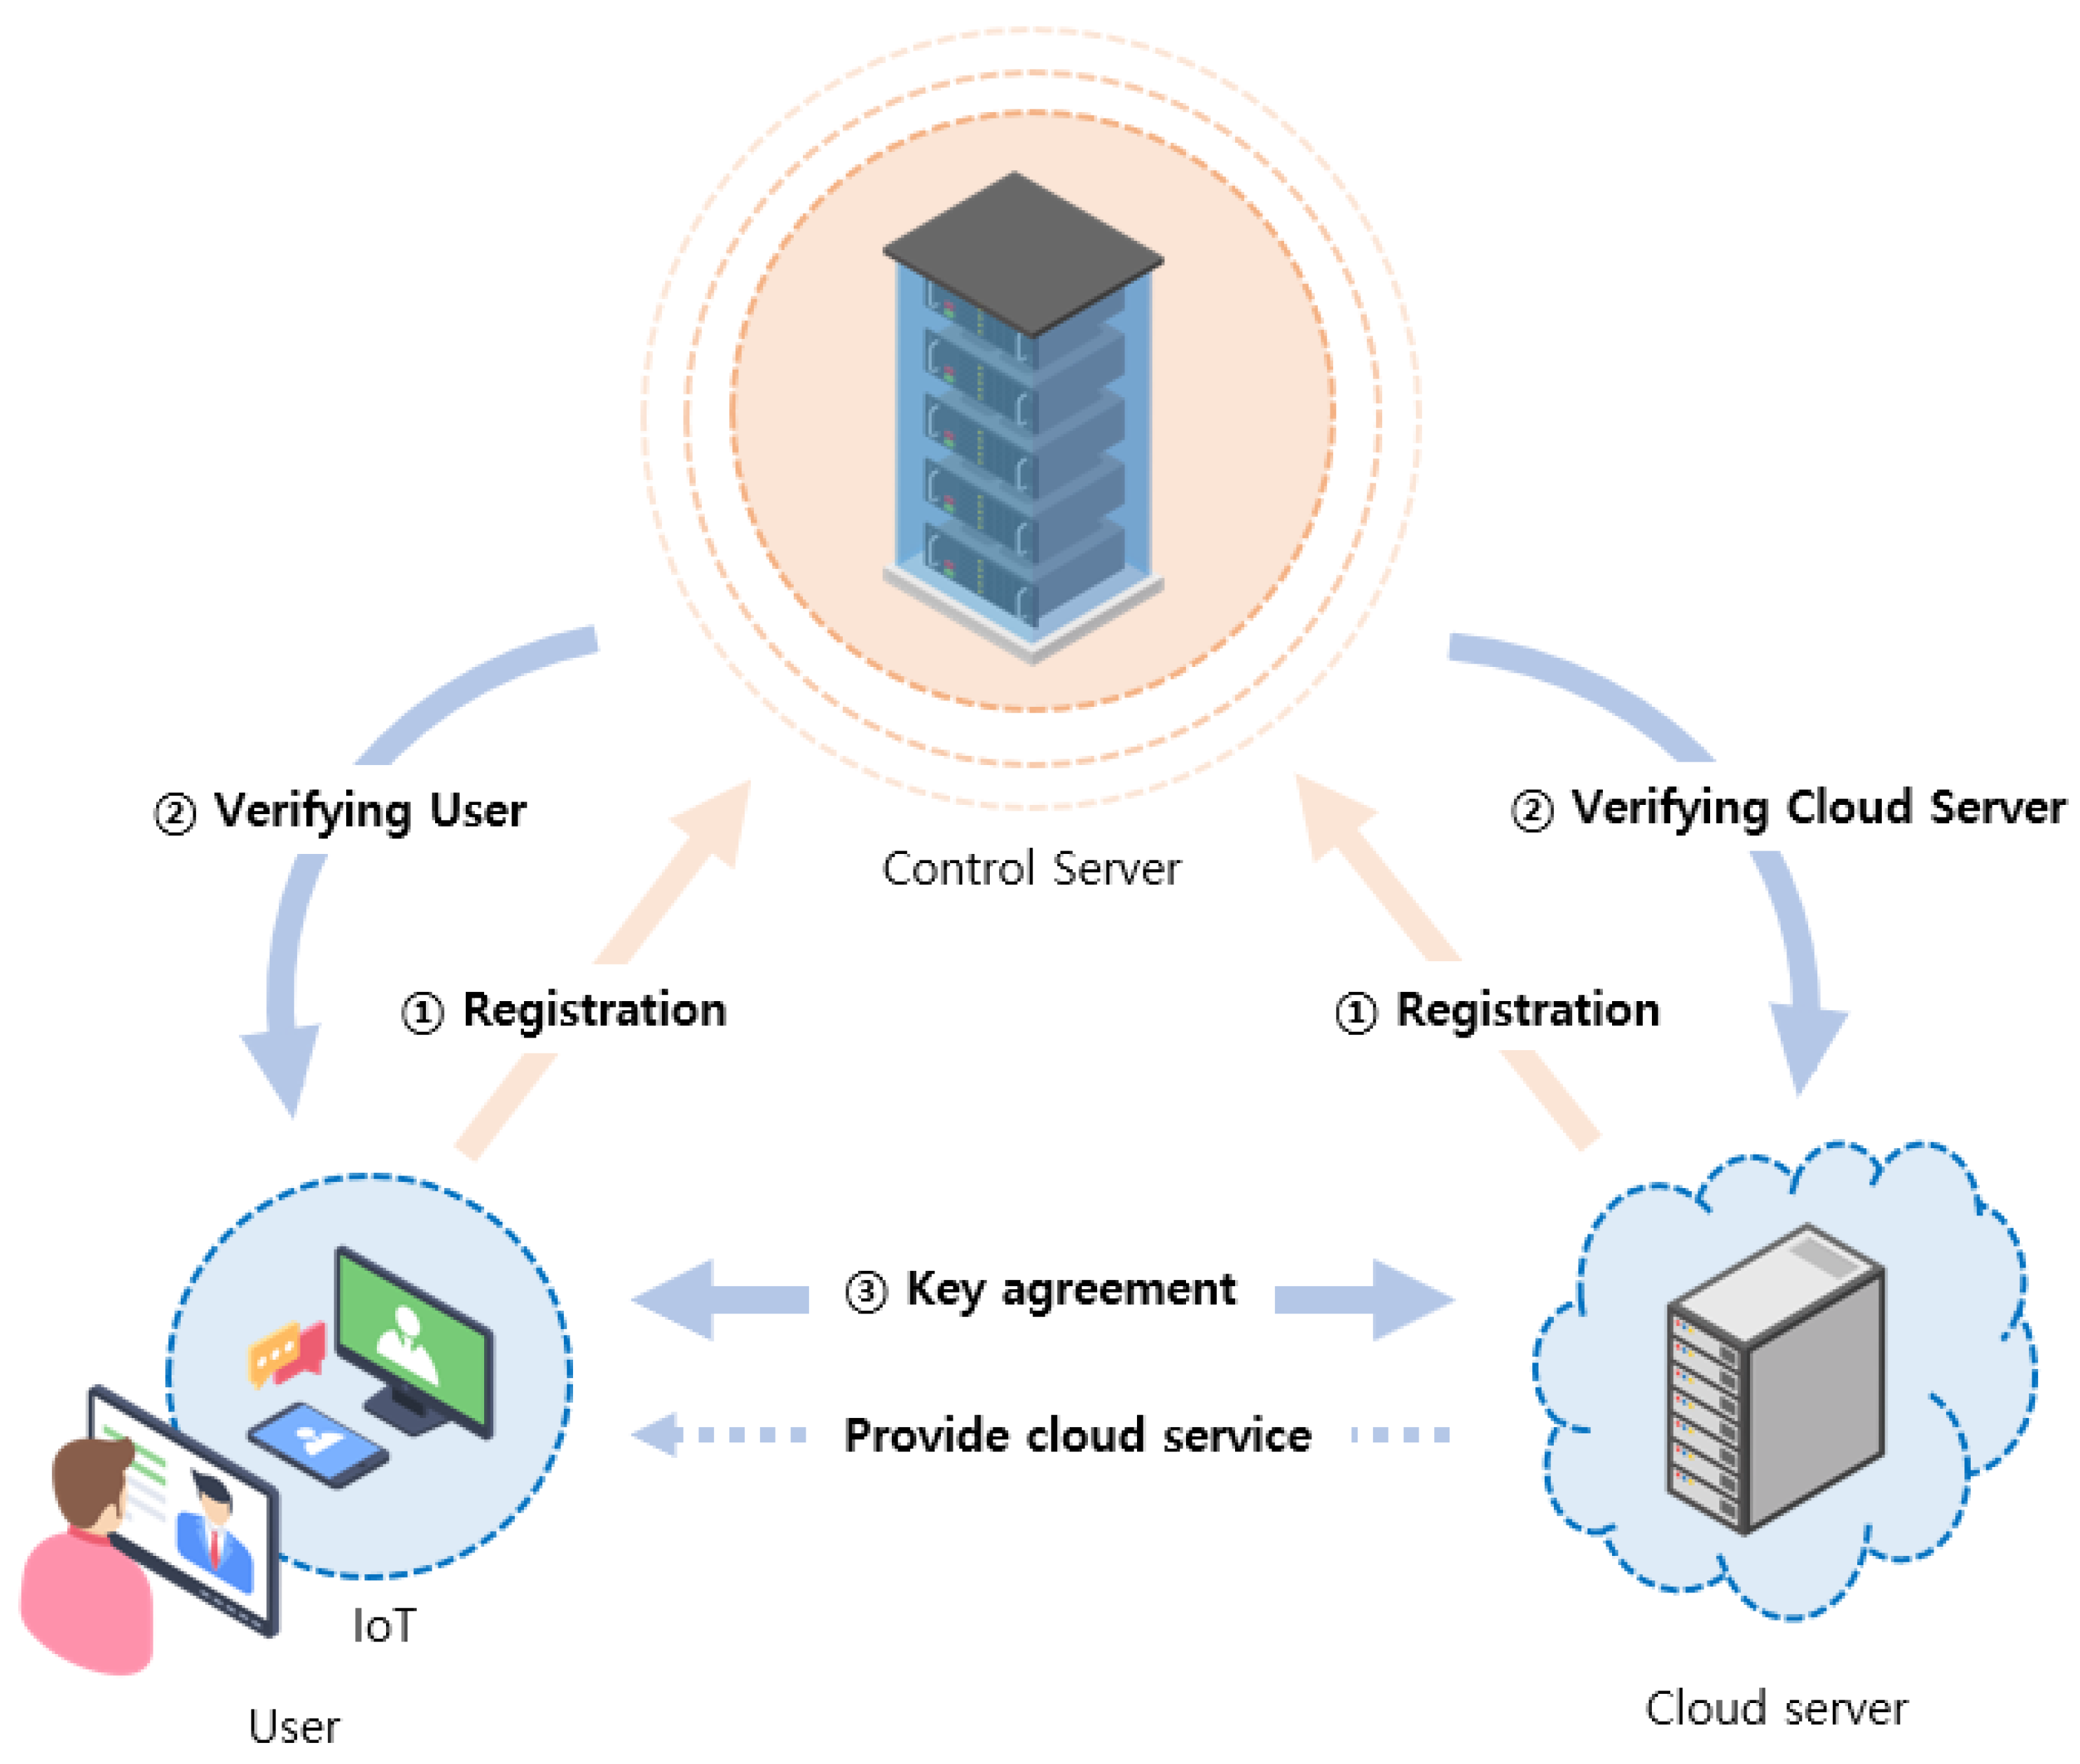
As shown in Figure 2, an IoT-enable cloud computing environment includes three entities: user, cloud server, and control server. Users can also use cloud computing provided by a cloud server, using IoT-enabled devices. Therefore, the user and cloud server should register and authenticate it through the control server. Finally, the user and cloud server share a session key for communication. The details are as follows
Figure 2.
System model.
- User (): User uses IoT devices with cloud services. Communicates with the cloud servers, then the user should register with the control server. The user can use smart cards and biometric technology to store sensitive information or the user’s identity and password. We assumed that the user is an untrusted entity, implying that the user can execute unauthorized or malicious attacks.
- Cloud server (): A cloud server provides cloud services to users using IoT devices. To achieve this, the cloud server should be registered with the control server. As a semi-trusted entity, the cloud server can misbehave; however, it cannot directly collude or participate.
- Control server (): This manages the registration of the user and cloud server, and helps generate the session key for authentication and subsequent communication. As a semi-trusted entity, the control server can misbehave; however, it cannot directly collude or participate.
3.2. Adversary Model
We employ the widely used “Dolev–Yao (DY) model” [32] to define the capabilities of the adversary. The details are as follows:
- Within the DY model, entities in the IoT environments are considered trustworthy, and the communication channel is also considered insecure. Consequently, the adversary can engage in various actions through the insecure channel, including resending, eavesdropping, blocking, and deleting any messages transmitted.
- The adversary can extract sensitive information through power analysis attacks from stolen user smart cards. Additionally, because the control and cloud servers are semi-trusted entities, the adversary can also extract information from their databases.
Furthermore, the “Canetti–Krawczyk (CK) model” [33] assumes that stronger adversaries can also be adapted to our protocol. The adversaries in the CK model can obtain and use ephemeral values or long-term values, and using those, ephemeral leakage attacks can be performed.
4. Revisit of Wu et al.’s Scheme
4.1. Registration Phase
Before generating a session key for communication, the user and cloud server must go through the registration process via a secure channel. The detailed process is as follows.
4.1.1. User Registration Phase
- Step 1:
- The enters , and imprints on the device. Then, calculates , and sends to as a registration request message through a secure channel.
- Step 2:
- checks if ’s identity is new, and generates a random number to calculate , . Then, stores in its database, and stores to smart card . After that, sends to through a secure channel.
- Step 3:
- computes and store in .
4.1.2. Cloud Server Registration Phase
- Step 1:
- selects and random number and sends as a request message to through a secure channel.
- Step 2:
- checks if ’s identity is new, and chooses ’s pseudo identity , computes , then stores in its database. Next, sends to through secure channel.
- Step 3:
- computes , and stores .
4.2. Login and Authentication Phase
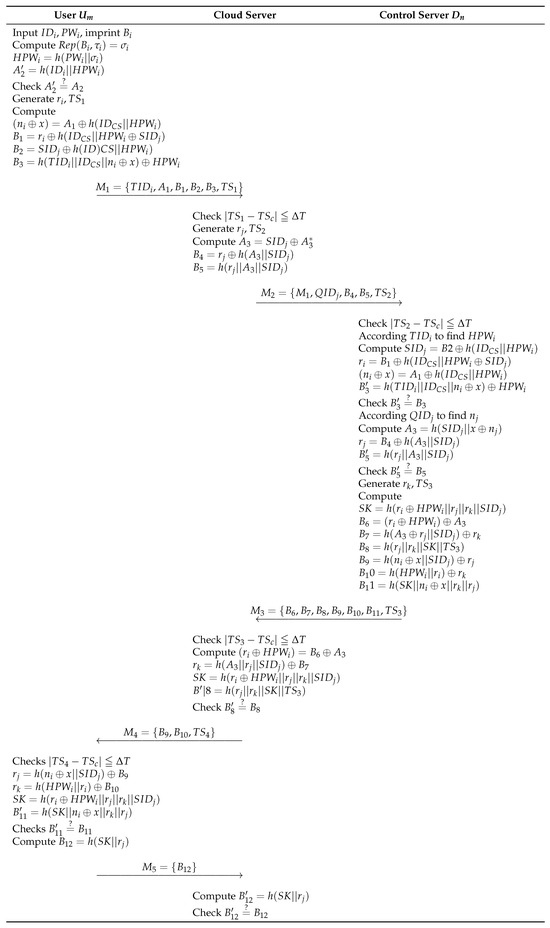
In this phase, the control server first verifies the identities of the user and the cloud server. If both are confirmed, a shared session key for subsequent communication is generated. The detailed process is as follows and illustrated in Figure 3.
Figure 3.
AKA phase of Wu et al.’s scheme.
- Step 1:
- enters , and imprints , and calculates , , . Then, by confirming , can be verified as a legitimate user. If this is valid, selects a random number and timestamp , then calculates , , , and . Finally, generates a message and sends it to via open channel.
- Step 2:
- Upon receiving ’s message, confirms timestamp . If the timestamp is valid, chooses a random value and timestamp . computes , , and . Finally, message is sent through an open channel.
- Step 3:
- After receiving the , confirms timestamp . If the timestamp is successfully verified, uses to find and performs the following computations: , , and . And by checking , the confirms whether is the legitimate user. Next, utilizes the value of to find and then performs the following computations: , , and . After checking is valid, CS then selects , , computes , , , , , , and , . At last, generates message and sends to through an open channel.
- Step 4:
- Upon receiving , checks timestamp . If the timestamp is valid, calculates following computations: , , and , and confirms . If it confirms, generates message to via open channel.
- Step 5:
- verifies timestamp . If the timestamp is valid, calculates , , , and and calculates . If it confirms, computes and generates and sends to .
- Step 6:
- calculates the equation and then checks . If they match, stores for future communication.
5. Cryptanalysis of Wu et al.’s Scheme
Following the description of Section 3, adversary can obtain important values from the user’s smart card by using a power analysis attack. Furthermore, can extract parameters from the cloud server and control server itself, because they are considered semi-trusted. With this information, various security attacks, including insider attack, verification table leakage attack, privileged insider attack, user impersonation, and cloud server impersonation, can be executed by . Details are described below.
5.1. Insider Attack
An adversary A, who has undergone the registration process as a legitimate user, can obtain session keys from another user ’s sessions or impersonate . The detailed process is as follows:
- Step 1:
- After completing the registration process, A obtains of during their AKA process. Subsequently, A calculates of using their own and .
- Step 2:
- In another user ’s session, A obtains message and uses and the previously acquired to deduce .
- Step 3:
- From B of , A calculates user ’s and , and from , A calculates .
- Step 4:
- Using the computed values, A can generate the session key for another user and potentially disclose or exploit it.
Therefore, Wu et al.’s scheme cannot resist insider attacks.
5.2. Verification Table Leakage Attack
If extracts verification table of cloud server, can disclose session key. The following procedures are below:
- Step 1:
- extracts the verification table to take from . And also intercept message transmitted in public channel.
- Step 2:
- calculates , and to extract and .
- Step 3:
- takes message .
- Step 4:
- computes , and . In addition by calculating , A can generate a session key to disclose or exploit it.
Therefore, Wu et al.’s scheme cannot resist verification table leakage attacks.
5.3. Privileged Insider Attack
A privileged insider can take important information like from the registration message and values stored in the user’s smart card such as . Through support from this privileged insider, a malicious can generate a session key through the following:
- Step 1:
- computes , and , ; therefore, can extract parameters , , and .
- Step 2:
- intercepts message .
- Step 3:
- calculates , and . Hence, can compute session key and disclose it.
Thus, Wu et al.’s scheme is insecure against privileged insider attacks.
5.4. Impersonation
When obtains the table information of the control center, can calculate .
- (1)
- User impersonation: If the privileged insider described in Section 5.3 generates random number and time stamp , can forge message . In addition, by to take message from an unsecured public channel, can generate session key and . Thus, can send message impersonates user.
- (2)
- Cloud server impersonation: According to the previous verification table attack in Section 5.2, generates random number and time stamp , and can send . Second, can generate after intercept message . Hence can impersonate cloud server.
Therefore, Wu et al.’s scheme cannot resist user and cloud impersonation attack.
5.5. Lack of Untraceability
If an attacker A continues to eavesdrop on and compares the value of contained in , A can track the user . The reason is that the pseudo identity of , , is a fixed value, and an attacker can easily obtain it through eavesdropping on the message. Indeed, by verifying whether the value of matches the values from previous or subsequent communications, A can detect the user. In conclusion, Wu et al.’s scheme lacks anonymity and untraceability.
5.6. Impossibility of Offline Password Update
In the user registration phase in Wu et al.’s scheme, the value of is created by concatenating the user’s password with their biometric information . Additionally, this is transmitted to the control server and undergoes the operation , and stored in the ’s database as . However, this design leads to a problem where users must communicate with the to update the value stored in the if they wish to change their password, because cannot create the on its own. Consequently, Wu et al.’s scheme does not support offline password updates.
6. Proposed Protocol
6.1. Registration Phase
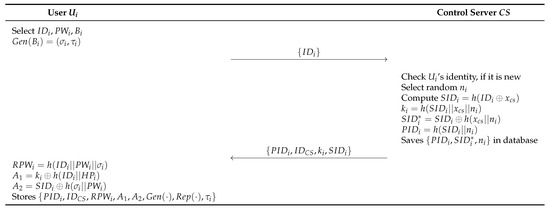
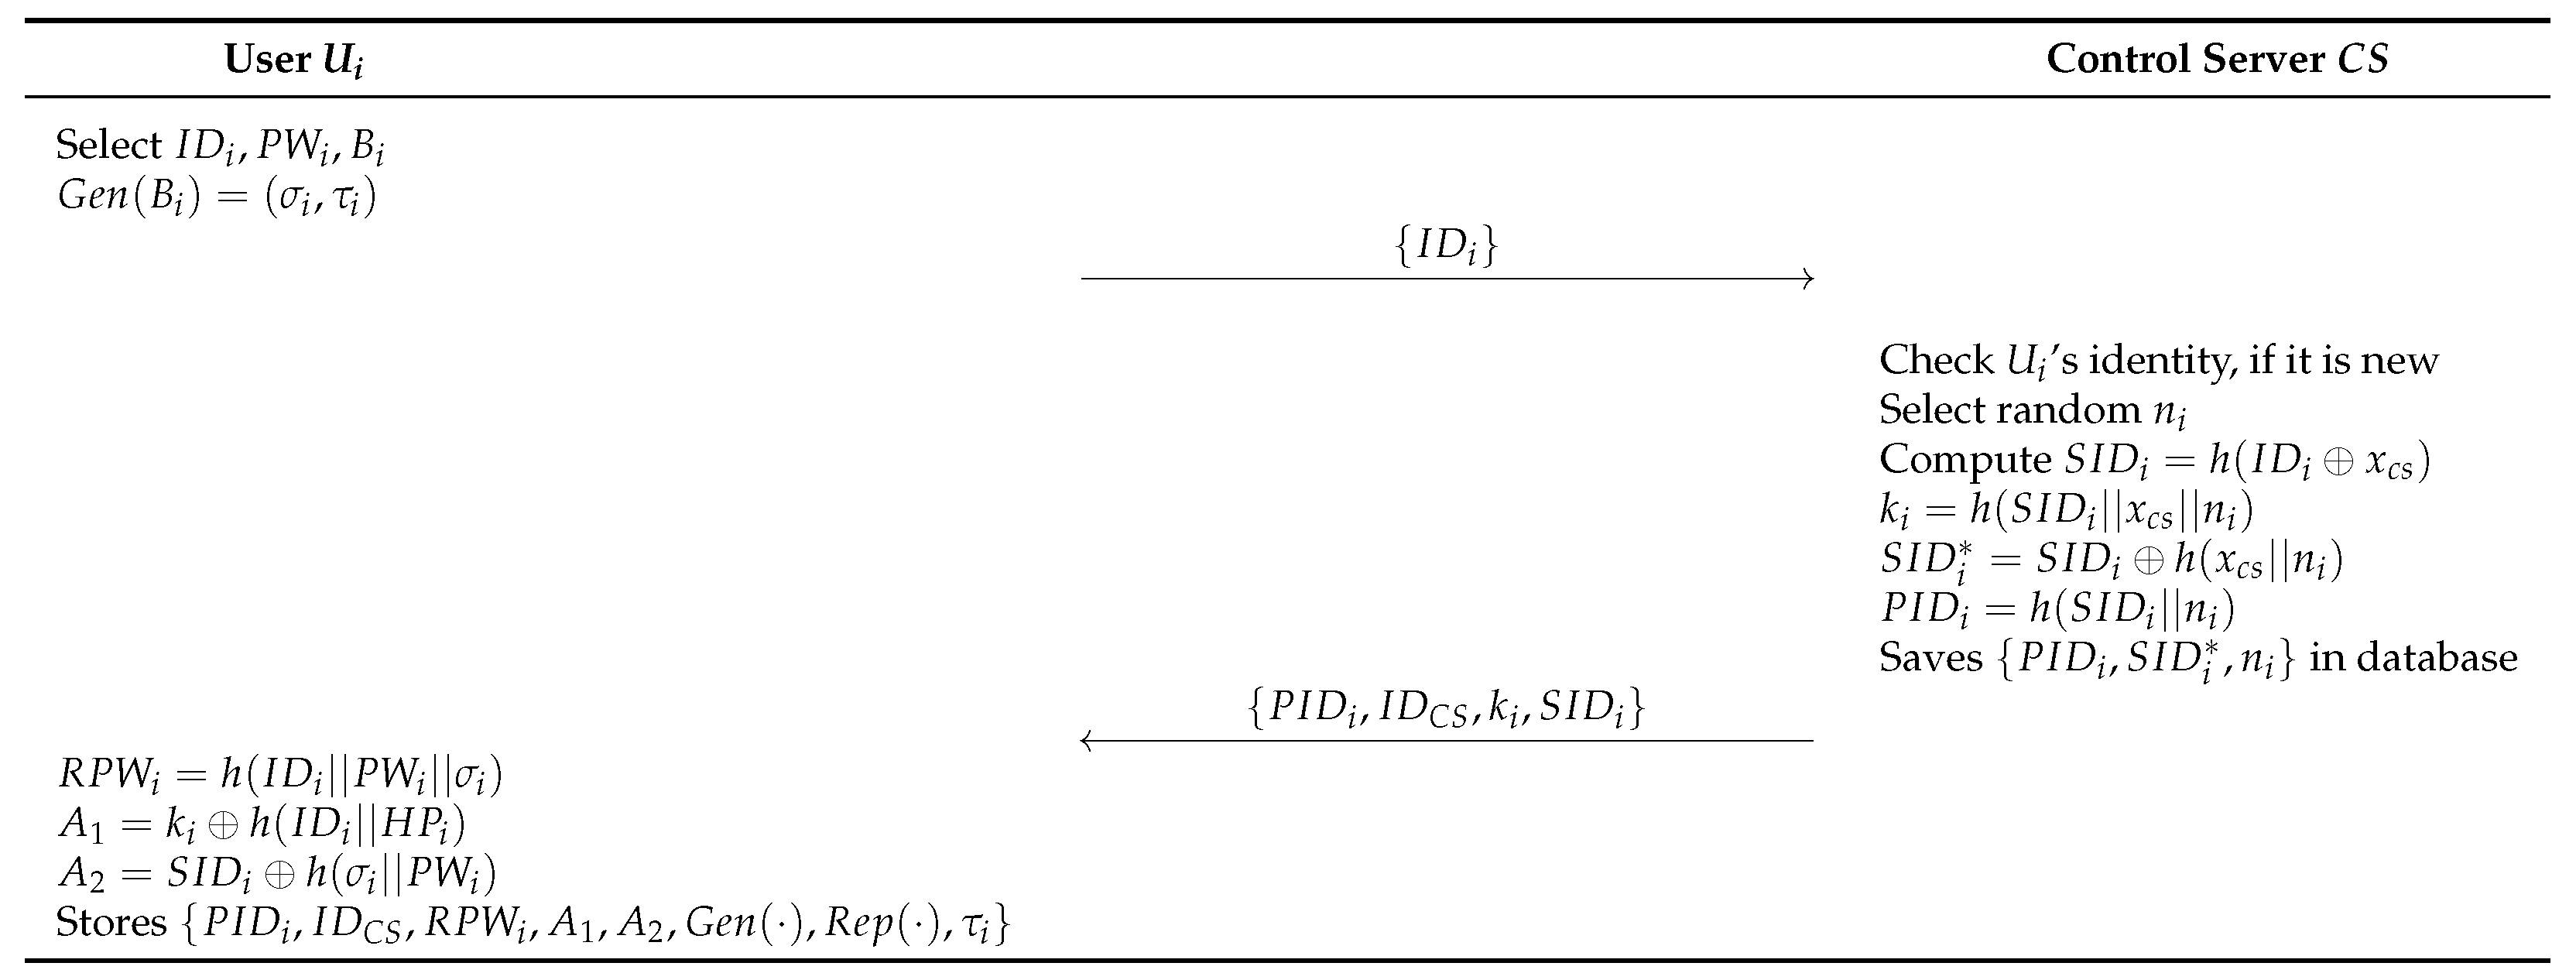
Before generating a session key for communication, the user and the cloud server must go through the registration process with the control server via a secure channel. In this phase, users register the information, such as identity, password, and biometrics, with the control server. The detailed process is as follows and illustrated in Figure 4.
Figure 4.
User registration phase of proposed scheme.
6.1.1. User Registration Phase
- Step 1:
- The enters , and imprints on the device. Then, calculates and sends to as a registration request message through a secure channel.
- Step 2:
- checks if ’s identity is new, and generates a random number to calculate , . and . Then, stores in its database, and sends to through secure channel.
- Step 3:
- computes , , and . Then, store in .
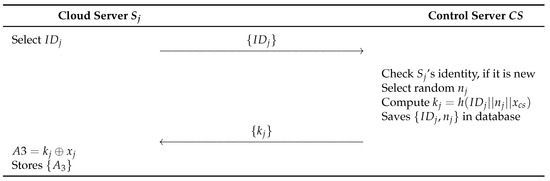
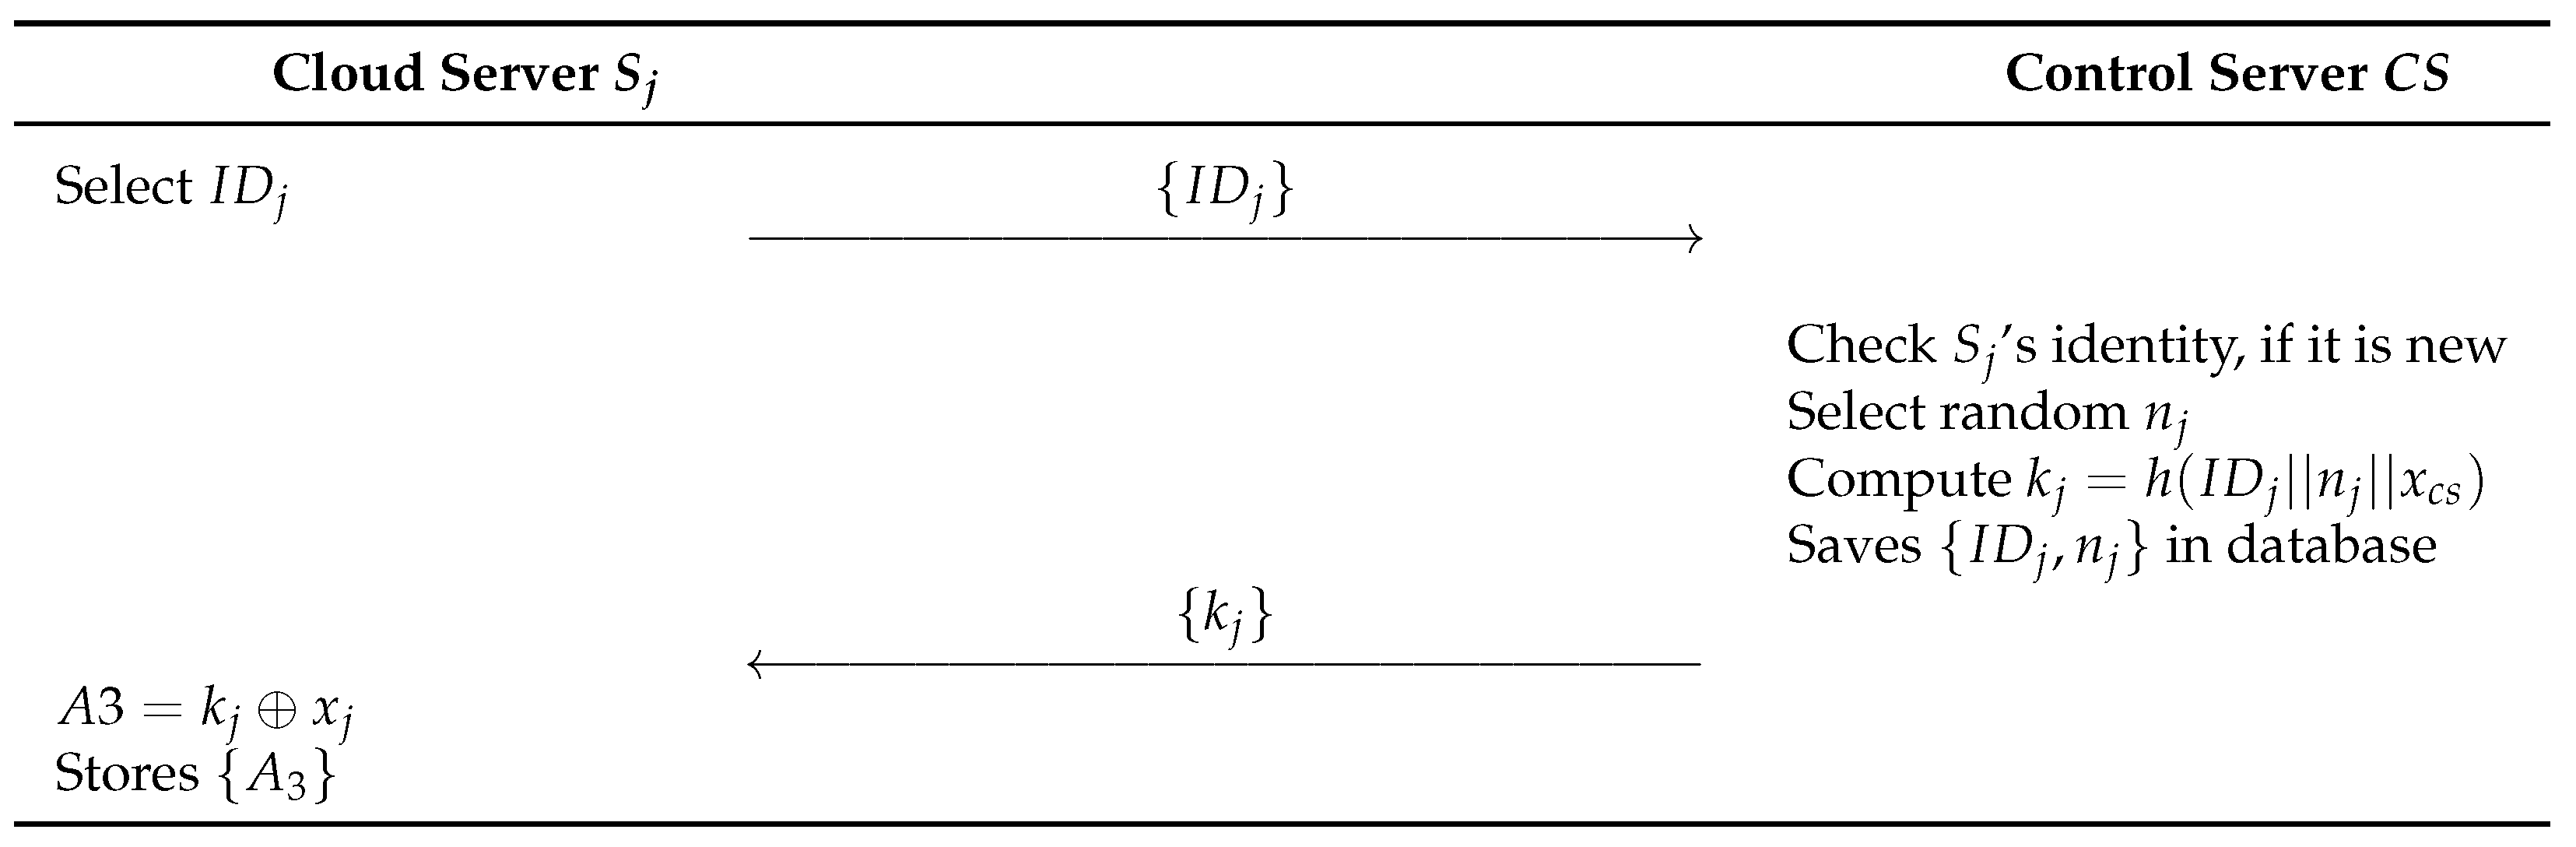
6.1.2. Cloud Server Registration Phase
In this phase, cloud servers register the information with the control server. The detailed process is as follows and illustrated in Figure 5.
Figure 5.
Cloud server registration phase of proposed scheme.
- Step 1:
- selects and sends as a request message to through a secure channel.
- Step 2:
- checks if ’s identity is new, and chooses random number , computes . Then, stores in its database. Next, sends to through secure channel.
- Step 3:
- computes , and stores .
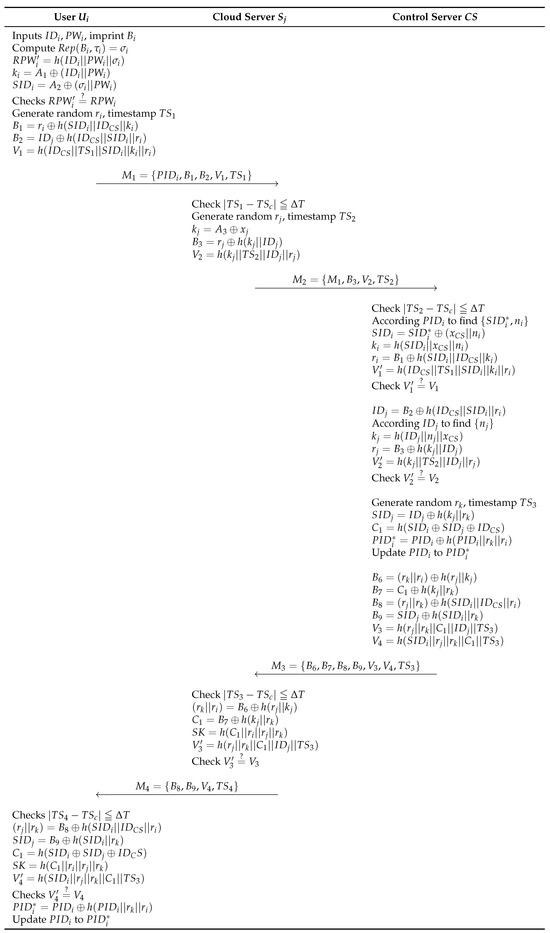
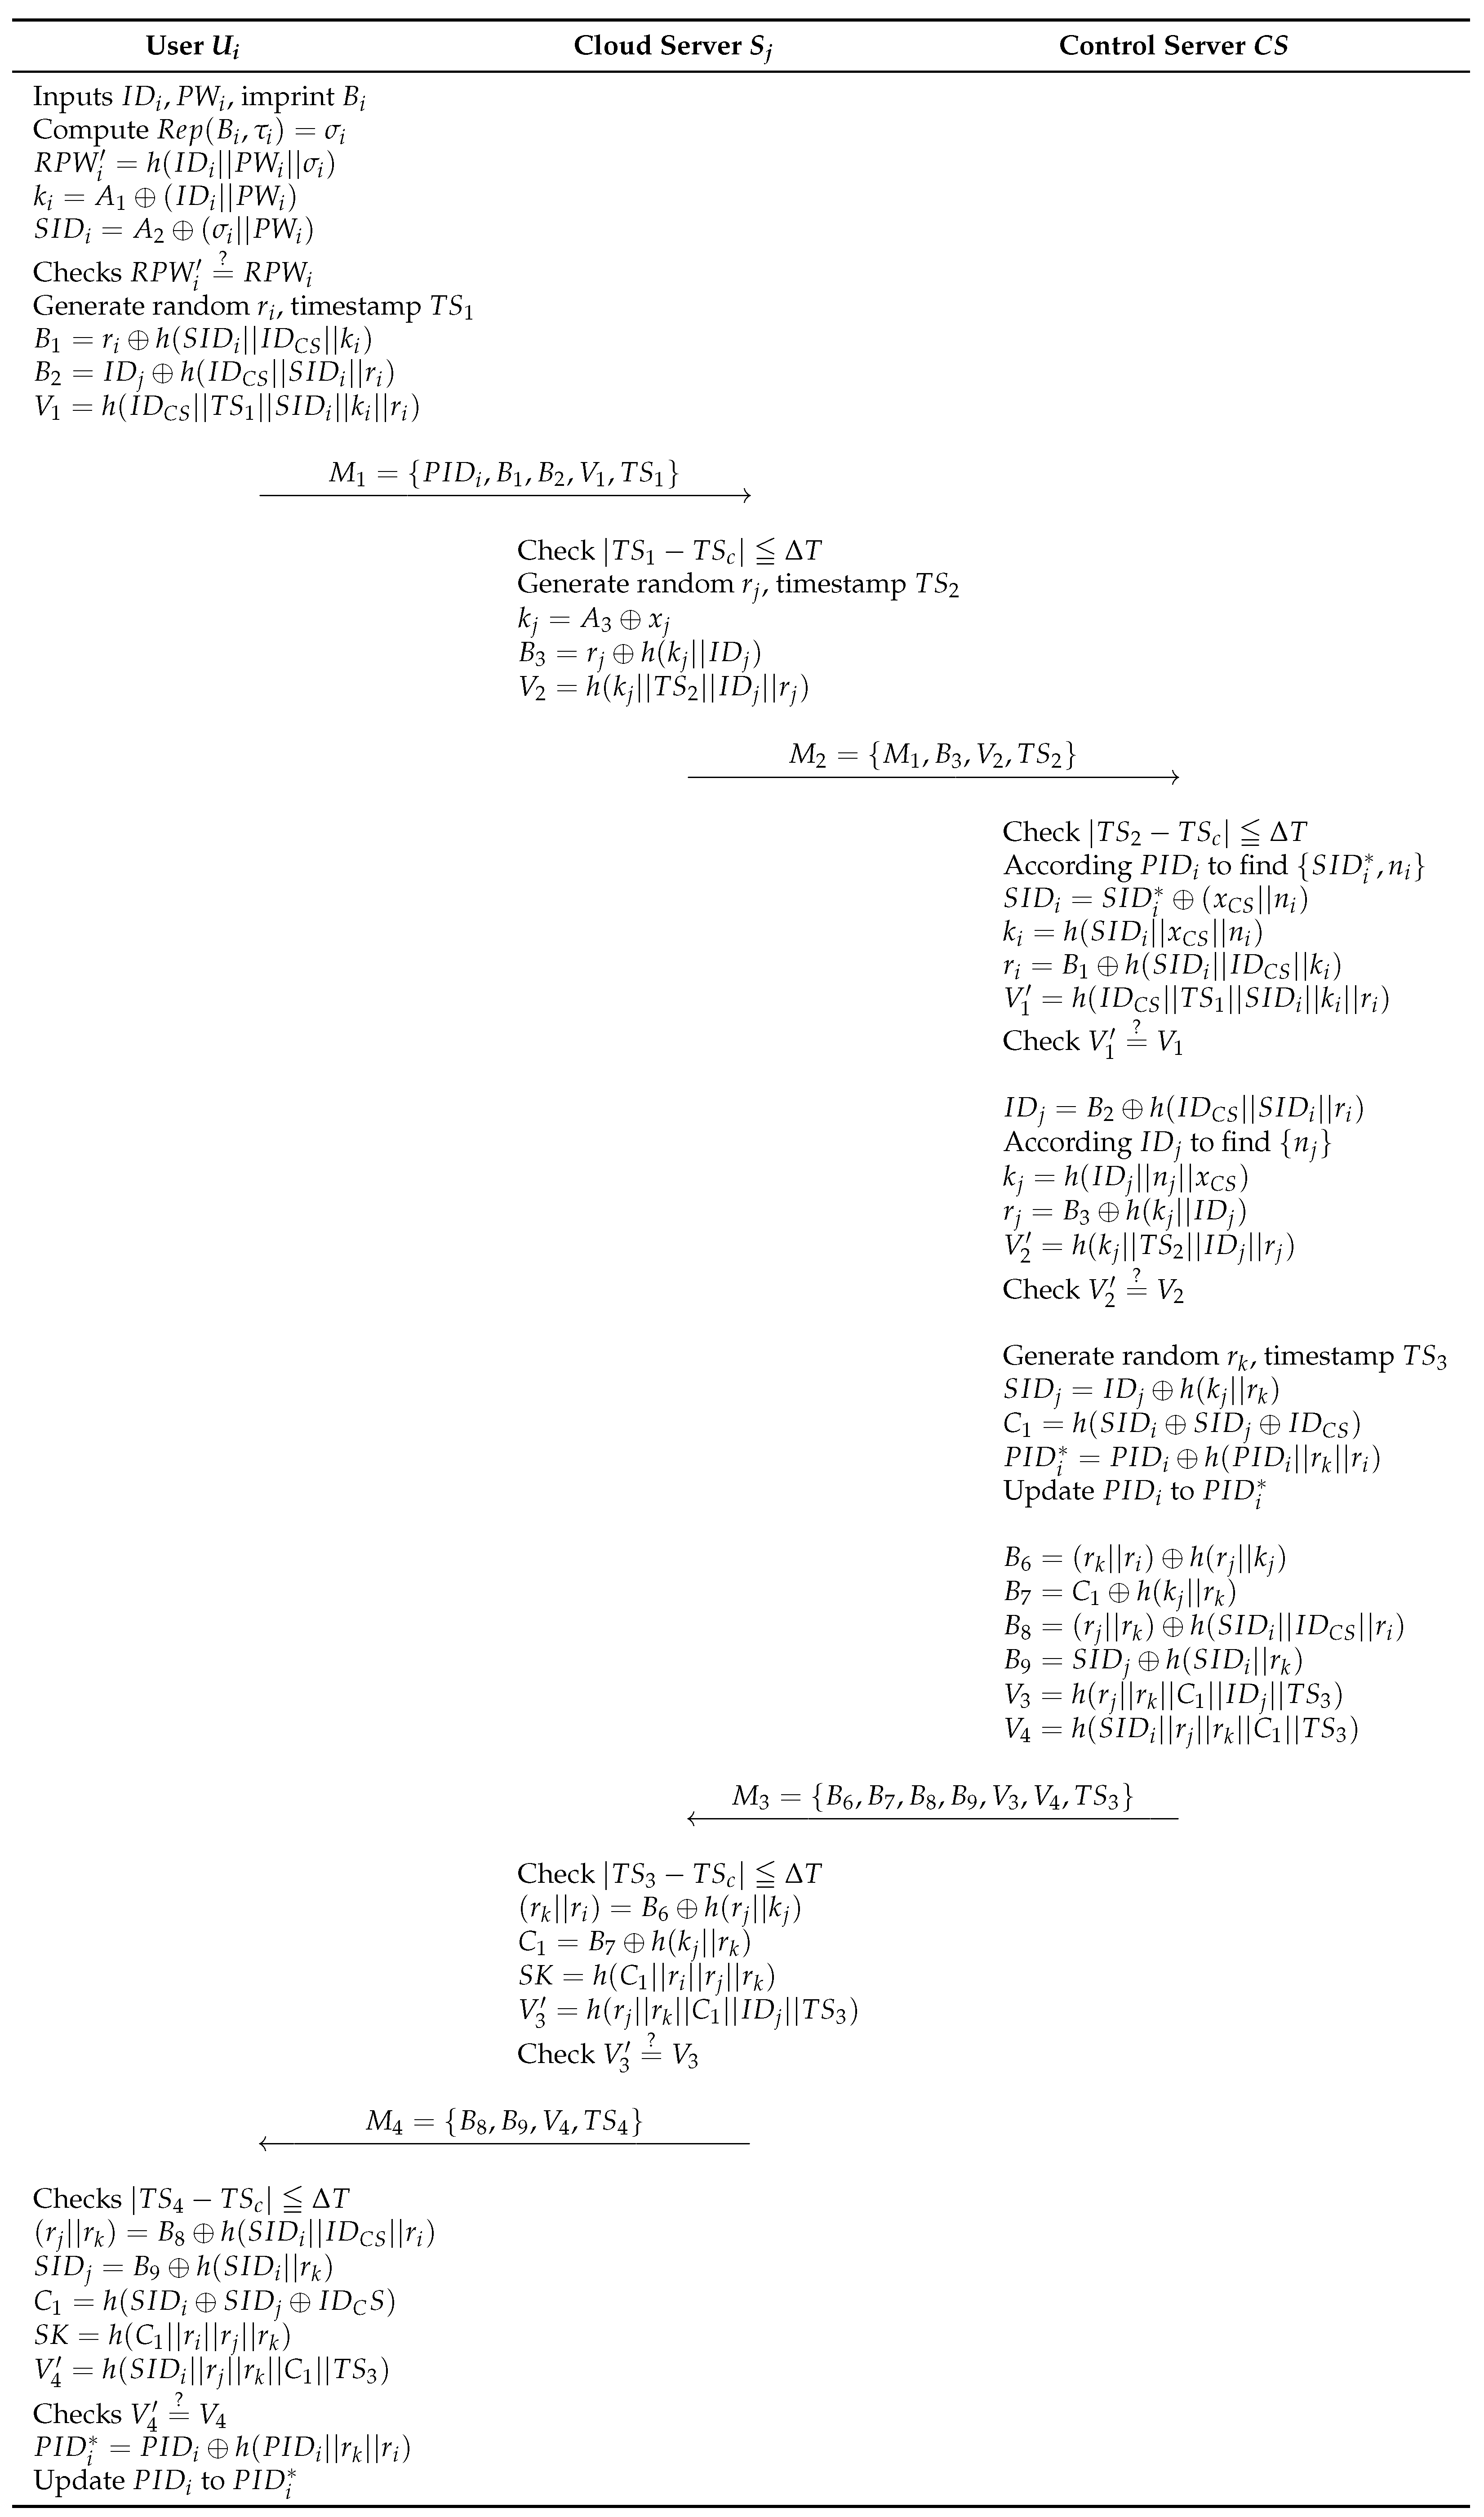
6.2. Login and Authentication Phase
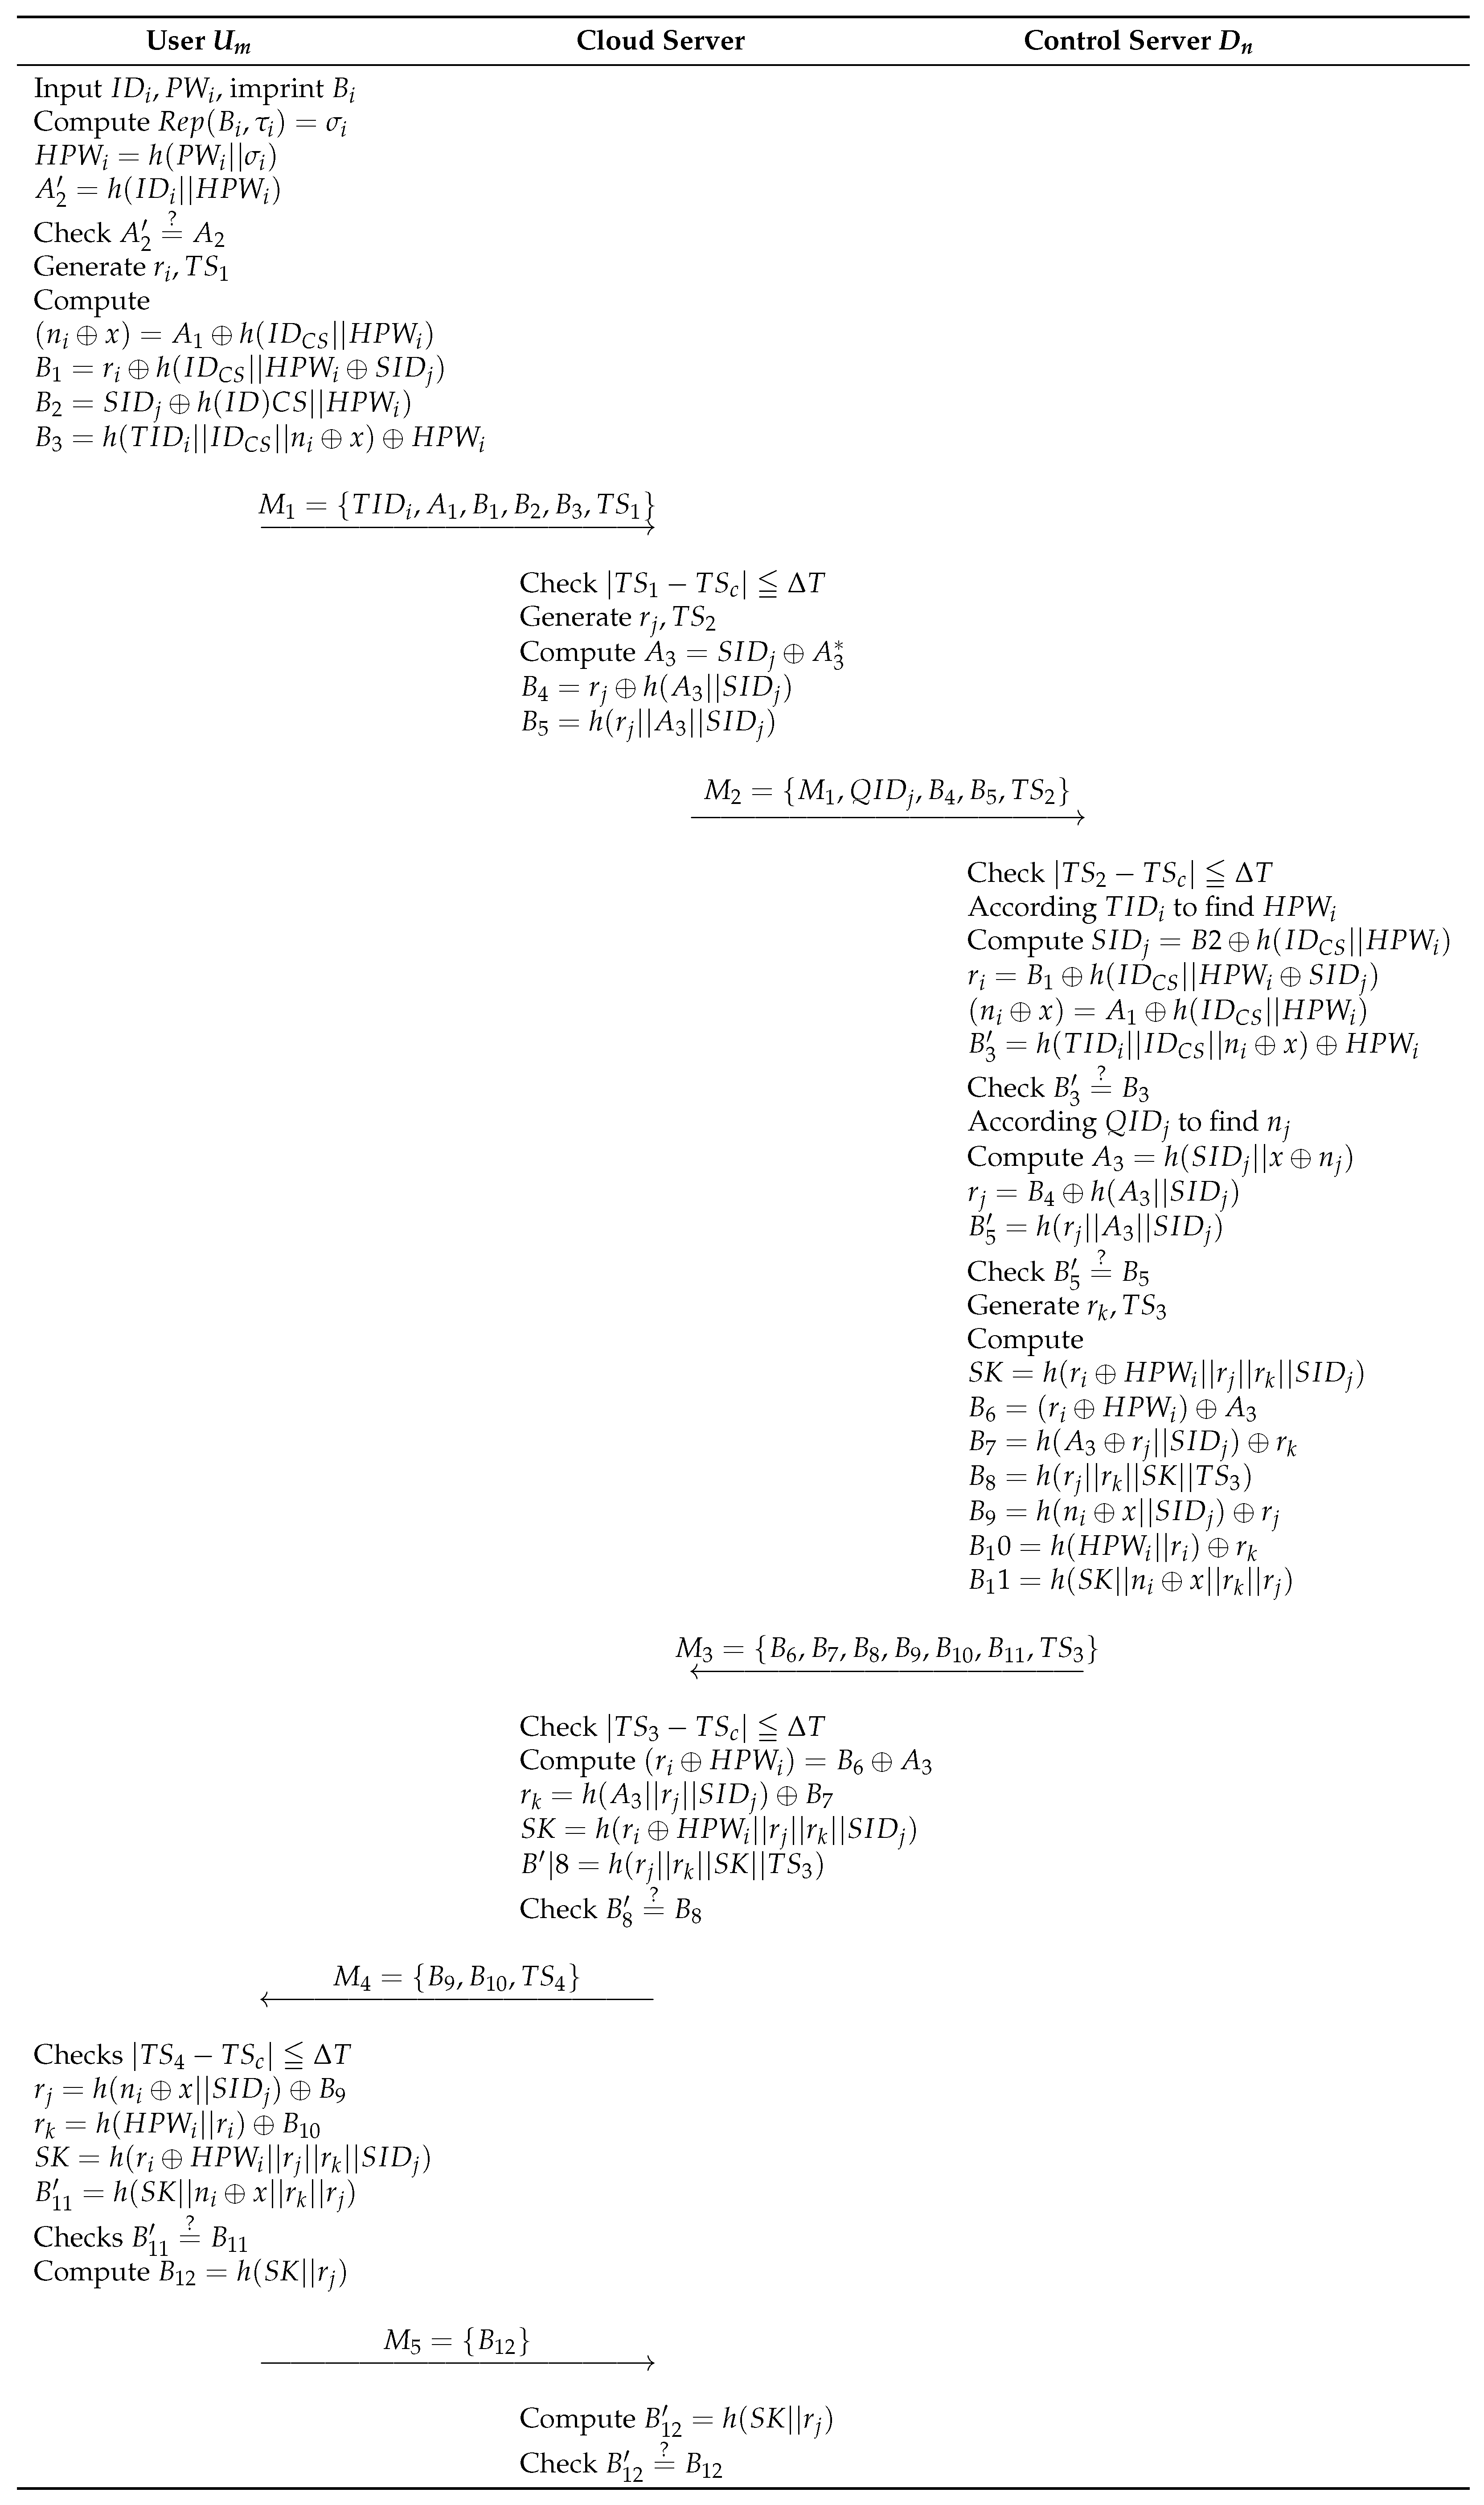
In this phase, the control server first verifies the identities of the user and the cloud server. If both are confirmed, a shared session key for subsequent communication is generated. The detailed process is as follows and illustrated in Figure 6.
Figure 6.
AKA phase of proposed scheme.
- Step 1:
- enters , , imprints , and calculates , , and . Then, by confirming , can be verified as a legitimate user. If this is valid, selects a random number and timestamp then calculates , and . Finally, it generates a message and sends it to via open channel.
- Step 2:
- Upon receiving ’s message, confirms timestamp . If thetimestamp is valid, chooses a random value and timestamp . computes , , and . Finally, message is sent through an open channel.
- Step 3:
- After receiving the , confirms timestamp . If the timestamp is successfully verified, uses to find and performs the following computations: , , and . And by checking , the confirms whether is the legitimate user.
- Step 4:
- Next, calculates and utilizes the value of to find . Then, it performs the following computations: , , and . Subsequently, it checks if is valid.
- Step 5:
- CS then selects , , computes , , . Next, it updates the old to .
- Step 6:
- , , , , and . At last, generates message and sends to through an open channel.
- Step 7:
- Upon receiving , checks timestamp . If the timestamp is valid, calculates following computations: , , , and . Subsequently, it confirms . If it confirms, generates message to via an open channel.
- Step 8:
- verifies timestamp . If the timestamp is valid, calculates , , , , and calculates to check . If it confirms, computes and update old to .
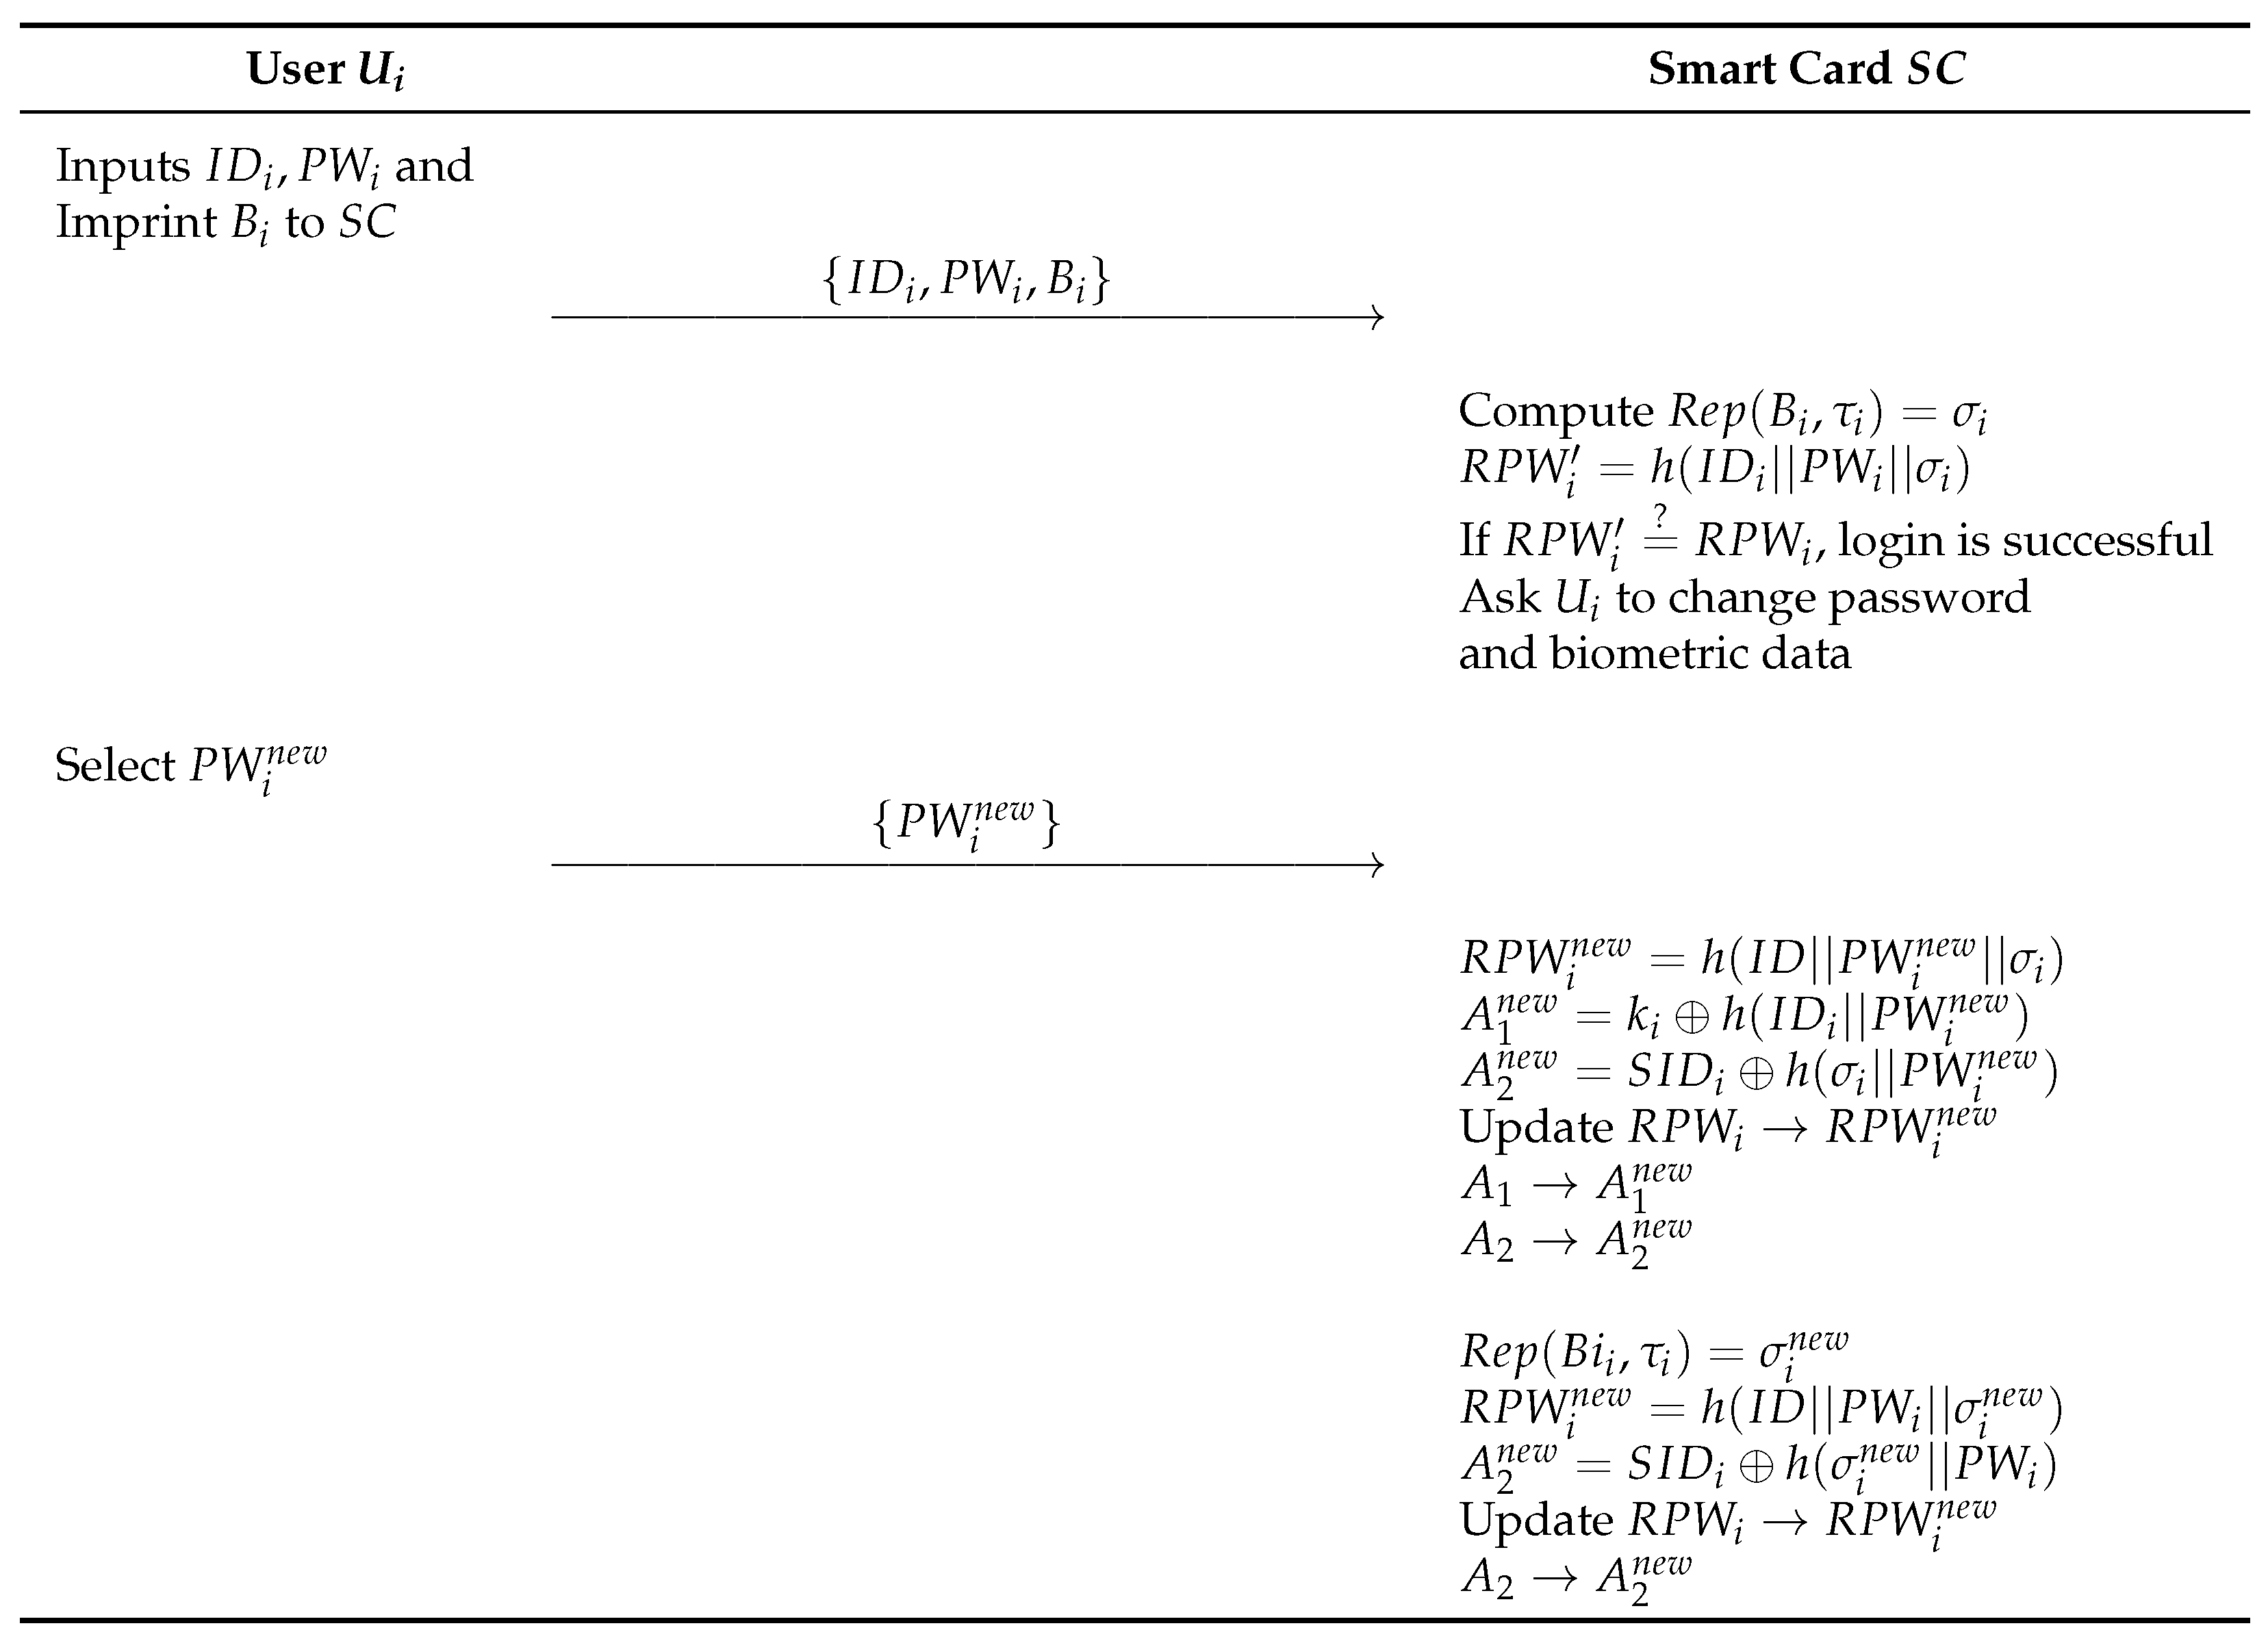
6.3. Offline Password and Biometric Template Update
In this phase, an authenticated user U can locally change their password and biometrics without a connection to CS. U must perform the login process on the IoT device before updating data offline. A logged-in user can update their password or biometric template. The detailed process is as follows and illustrated in Figure 7.
Figure 7.
Offline password and biometric template update of proposed scheme.
- Step 1:
- enters , and imprint on the device. Compute and check for login phase and confirm user.
- Step 2:
- Then, ask to change password and biometric data. select new password , and compute , and . Subsequently, update , , and with new data to change the password.
- Step 3:
- Compute , and . Subsequently, update and with new data to change the biometric template.
7. Security Analysis
7.1. ROR Model
In this section, we conduct an analysis of session key security using the ROR model [34]. To apply the proposed protocol to the ROR model, we first define participants, especially , , and as user, cloud server, and control server, respectively. Note that is an instance for each participant. In ROR model, the adversary can eavesdrop, delete, intercept, and send messages through the public channel. Moreover, the adversary can extract secret parameters from the user . These actions of the adversary can be defined as queries in the ROR model.
- : This query is an eavesdropping attack that the adversary can obtain messages transmitted via a public channel. Thus, this query can be defined as a passive attack.
- : In this query, the adversary extracts secret parameters using the smart device of . Therefore, we can define the query is an active attack.
- : The adversary sends messages to legal participants through open channels. This query is an active attack.
- : In this query, the adversary flips an unbiased coin. When the result of the flipped coin is 0, the session key is not fresh. When the result of the flipped coin is 1, we can demonstrate that the session key is fresh. Otherwise, the result outputs (⊥).
Theorem 1.
We take a definition of , , , and as the possibility of breaking session key, range space of hash function, number of hash functions, and number of send queries, respectively. Moreover, we define that s and C are the Zipf’s parameters [35]. From that, the adversary tries to reveal the session key of the proposed protocol in polynomial time. Following [36,37,38], the ROR model analysis of the proposed protocol is composed of four games (, ) and the winning possibility of the adversary is for each game .
- : In this game, the adversary has no knowledge about the session key. Thus, the adversary picks a random bit B.
- : The adversary conducts query to collect the messages transmitted via public channels. Thus, the adversary obtains , , , and . After that, the adversary flips an unbiased coin to execute the query. However, the adversary has no knowledge of the session key because it is composed of random numbers , and and masked in the hash functions. For these reasons, the adversary can obtain the following:
- : The adversary conducts and queries to reveal session key in this game. However, the session key is composed of fresh random numbers and a cryptographic hash function. Therefore, the adversary cannot make hash collisions to calculate the session key. Applying the birthday paradox [39], we obtain the following:
- : In the last game, the adversary conducts query to obtain the secret parameters . However, the adversary cannot decrypt the secret parameters because these parameters are encrypted using the identity , password , and biometrics . Since simultaneously guessing , , and is a computationally infeasible task, the adversary has no advantage in this game. We obtain the following using Zipf’s law [35].When all the games end, the adversary becomes a random bit B.We obtain the in Equation (10) which is the same as (1). It means that the adversary cannot distinguish random nonce and the session key using various security attacks, such as , , and . Thus, we can prove the session key security of the proposed protocol.
7.2. BAN Logic
We analyze the mutual authentication of the proposed protocol using BAN logic [40]. Following [41,42,43], we define basic notations and descriptions of BAN logic in Table 2.
Table 2.
Basic notations and decriptions.
7.2.1. Rules
In BAN logic, there are five rules, such as “Message meaning rule (MMR)”, “Nonce verification rule (NVR)”, “Jurisdiction rule (JR)”, “Belief rule (BR)”, and “Freshness rule (FR)”.
- 1.
- Message meaning rule (MMR):
- 2.
- Nonce verification rule (NVR):
- 3.
- Jurisdiction rule (JR):
- 4.
- Belief rule (BR):
- 5.
- Freshness rule (FR):
7.2.2. Goals
In our protocol, each participant authenticate the communication partner by establishing session key . Thus, goals of the proposed protocol can be shown as follows:
- Goal 1:
- Goal 2:
- Goal 3:
- Goal 4:
- Goal 5:
- Goal 6:
- Goal 7:
- Goal 8:
7.2.3. Idealized Forms
In the proposed authentication phase, four messages are transmitted via open channels (, , , ). To analyze these messages, we convert them into idealized forms.
7.2.4. Assumptions
In the proposed protocol, participants agree on the freshness of the random number and secret parameters. Therefore, we show the assumptions to analyze the proposed authentication phase.
- :
- :
- :
- :
- :
- :
- :
- :
7.2.5. BAN Logic Proof
- Step 1:
- We obtain using .
- Step 2:
- We use , , and MMR to obtain and from .
- Step 3:
- From and , we use , , and FR to obtain and .
- Step 4:
- From , , and , we use NVR to obtain and .
- Step 5:
- We obtain using .
- Step 6:
- We use and MMR to obtain from .
- Step 7:
- From , we use and FR to obtain .
- Step 8:
- From and , we use NVR to obtain .
- Step 9:
- Using and , and computes the session key .Thus, we obtain the following:
- Step 10:
- Using JR into and , We obtain the following goals:
- Step 11:
- We obtain using .
- Step 12:
- We use and MMR to obtain from .
- Step 13:
- From , we use and FR to obtain .
- Step 14:
- From and , we use NVR to obtain .
- Step 15:
- Using and , and agrees the session key .Thus, we obtain the following:
- Step 16:
- Using JR into and , We obtain the following goals:
7.3. Informal Security Analysis
7.3.1. Insider Attack
Malicious actor A, who has gone through the registration phase as a legitimate user, can attempt an insider attack using the acquired information. However, the attacker is unable to know the random values and . As a result, the attacker cannot calculate , rendering the attack impossible.
7.3.2. Impersonation Attack
- (1)
- User impersonation: Adversary A needs to create a valid message to impersonate the legitimate user . While A might obtain from the user’s device, it is impossible for A to access the necessary and to calculate needed to create the message. Therefore, A cannot generate the message on behalf of the user and transmit it to the cloud server and control server. Thus, the proposed scheme is secure against user impersonation attacks.
- (2)
- Cloud server impersonation: To execute this attack, A needs to send the message to the control server on behalf of the cloud server . Even if A intercepts the transmission of over an open channel, they cannot generate the necessary for the message until they know . Therefore, the proposed scheme is secure against cloud server impersonation attacks.
7.3.3. Reply and MITM Attacks
All users, the cloud server, and the control server attempt to validate the received messages through . Also, the sent messages are masked with different random values for each session, ensuring freshness. Therefore, the proposed scheme is secure against reply attacks and MITM attacks.
7.3.4. Privileged Insider Attack
In this attack scenario, external entity A is considered a privileged insider, implying that A possesses the user’s registration request message and confidential values such as However, without the precise biometric information, ID, or PW values of the user, calculating or is not possible. As a result, the proposed scheme is secure against privileged insider attacks.
7.3.5. Ephemeral Security Leakage Attack
To prevent adversary A from carrying out valid attacks, such as obtaining the session key through this attack scenario, it is essential to ensure that the session key is preserved even if the random values used in the session are exposed. Therefore, assuming A knows the values of , it is postulated here that even with this knowledge, A cannot calculate without knowing . Additionally, valid attacks like impersonating the user or cloud server using random values are not possible. Therefore, the proposed scheme is secure against ESL attacks.
7.3.6. Stolen Verifier Attack
We can assume that a malicious A, upon obtaining from the cloud server’s database, attempts to calculate the session key or impersonate the cloud server. However, without the cloud server’s secret key , A cannot deduce the value of from the stored , nor can A determine the randomly generated values , or . Therefore, A is unable to compute the session key or impersonate the cloud server. Consequently, the proposed scheme is secure against verification table leakage attacks.
7.3.7. DoS Attack
The adversary A may intentionally attempt to send the message repeatedly. However, to generate message , A must go through the login process and pass the verification . However, to create a valid , A cannot have the required . Therefore, A cannot create and repeatedly send the message , making the proposed scheme secure against DoS attacks.
7.3.8. User Anonymity and Untraceability
Due to the use of as a pseudo identity, the user’s identity cannot be deduced by an adversary A. Additionally, the is updated as a new value with random elements for each session, making it impossible for A to compare values between previous and current sessions to compromise the user’s untraceability. Therefore, the proposed scheme provides user anonymity and untraceability.
7.3.9. Session Key Disclosure Attack
To calculate the session key , adversary A needs to have access to the values of , , , , and . However, for A to discover , , they would need access to the secret key and the random values and . Additionally, random values like , , are used temporarily and exist only within a single session. Therefore, the proposed scheme is secure against session key disclosure attacks.
7.3.10. Perfect Forward Secrecy
If the control server’s secret key is compromised, adversary A may attempt to calculate the session key for a previous session. However, since does not contain and the values of are random and cannot be deduced, A cannot perform the calculation. Furthermore, without through , A cannot compute . Therefore, the proposed scheme ensures perfect forward secrecy.
7.3.11. Mutual Authentication
In the login and authentication phases, the messages and included can be used by the control server to verify the legitimacy of the user and the cloud server through the transmitted and . Additionally, messages and allow both the user and the cloud server to validate each other’s identity using and . Due to the unavailability of , values, and random values to adversaries through the open channel, the transparency of authentication is ensured. Therefore, the provided scheme offers mutual authentication.
8. Performance Analysis
8.1. Security Features Comparison
We visually compare the safety elements of the proposed scheme and related schemes [11,21,44,45,46,47,48] and record them in Table 3, which includes various types of safety elements such as “insider attack”, “impersonation attack”, “stolen verification attack”, “ESL attack”, “privileged attack”, “perfect forward secrecy”, “reply attack”, “offline password-guessing attack”, “session key disclosure”, “mutual authentication”, “DoS attack”, “user anonymity”, and “untraceability”. Ultimately, the proposed scheme offers more security features compared to Wu et al.’s scheme, and it exhibits fewer features that are either unidentified or not provided, even when compared to the schemes of other related works.
Table 3.
Security and functionality features(SFF) comparison.
8.2. Communication Costs Comparison
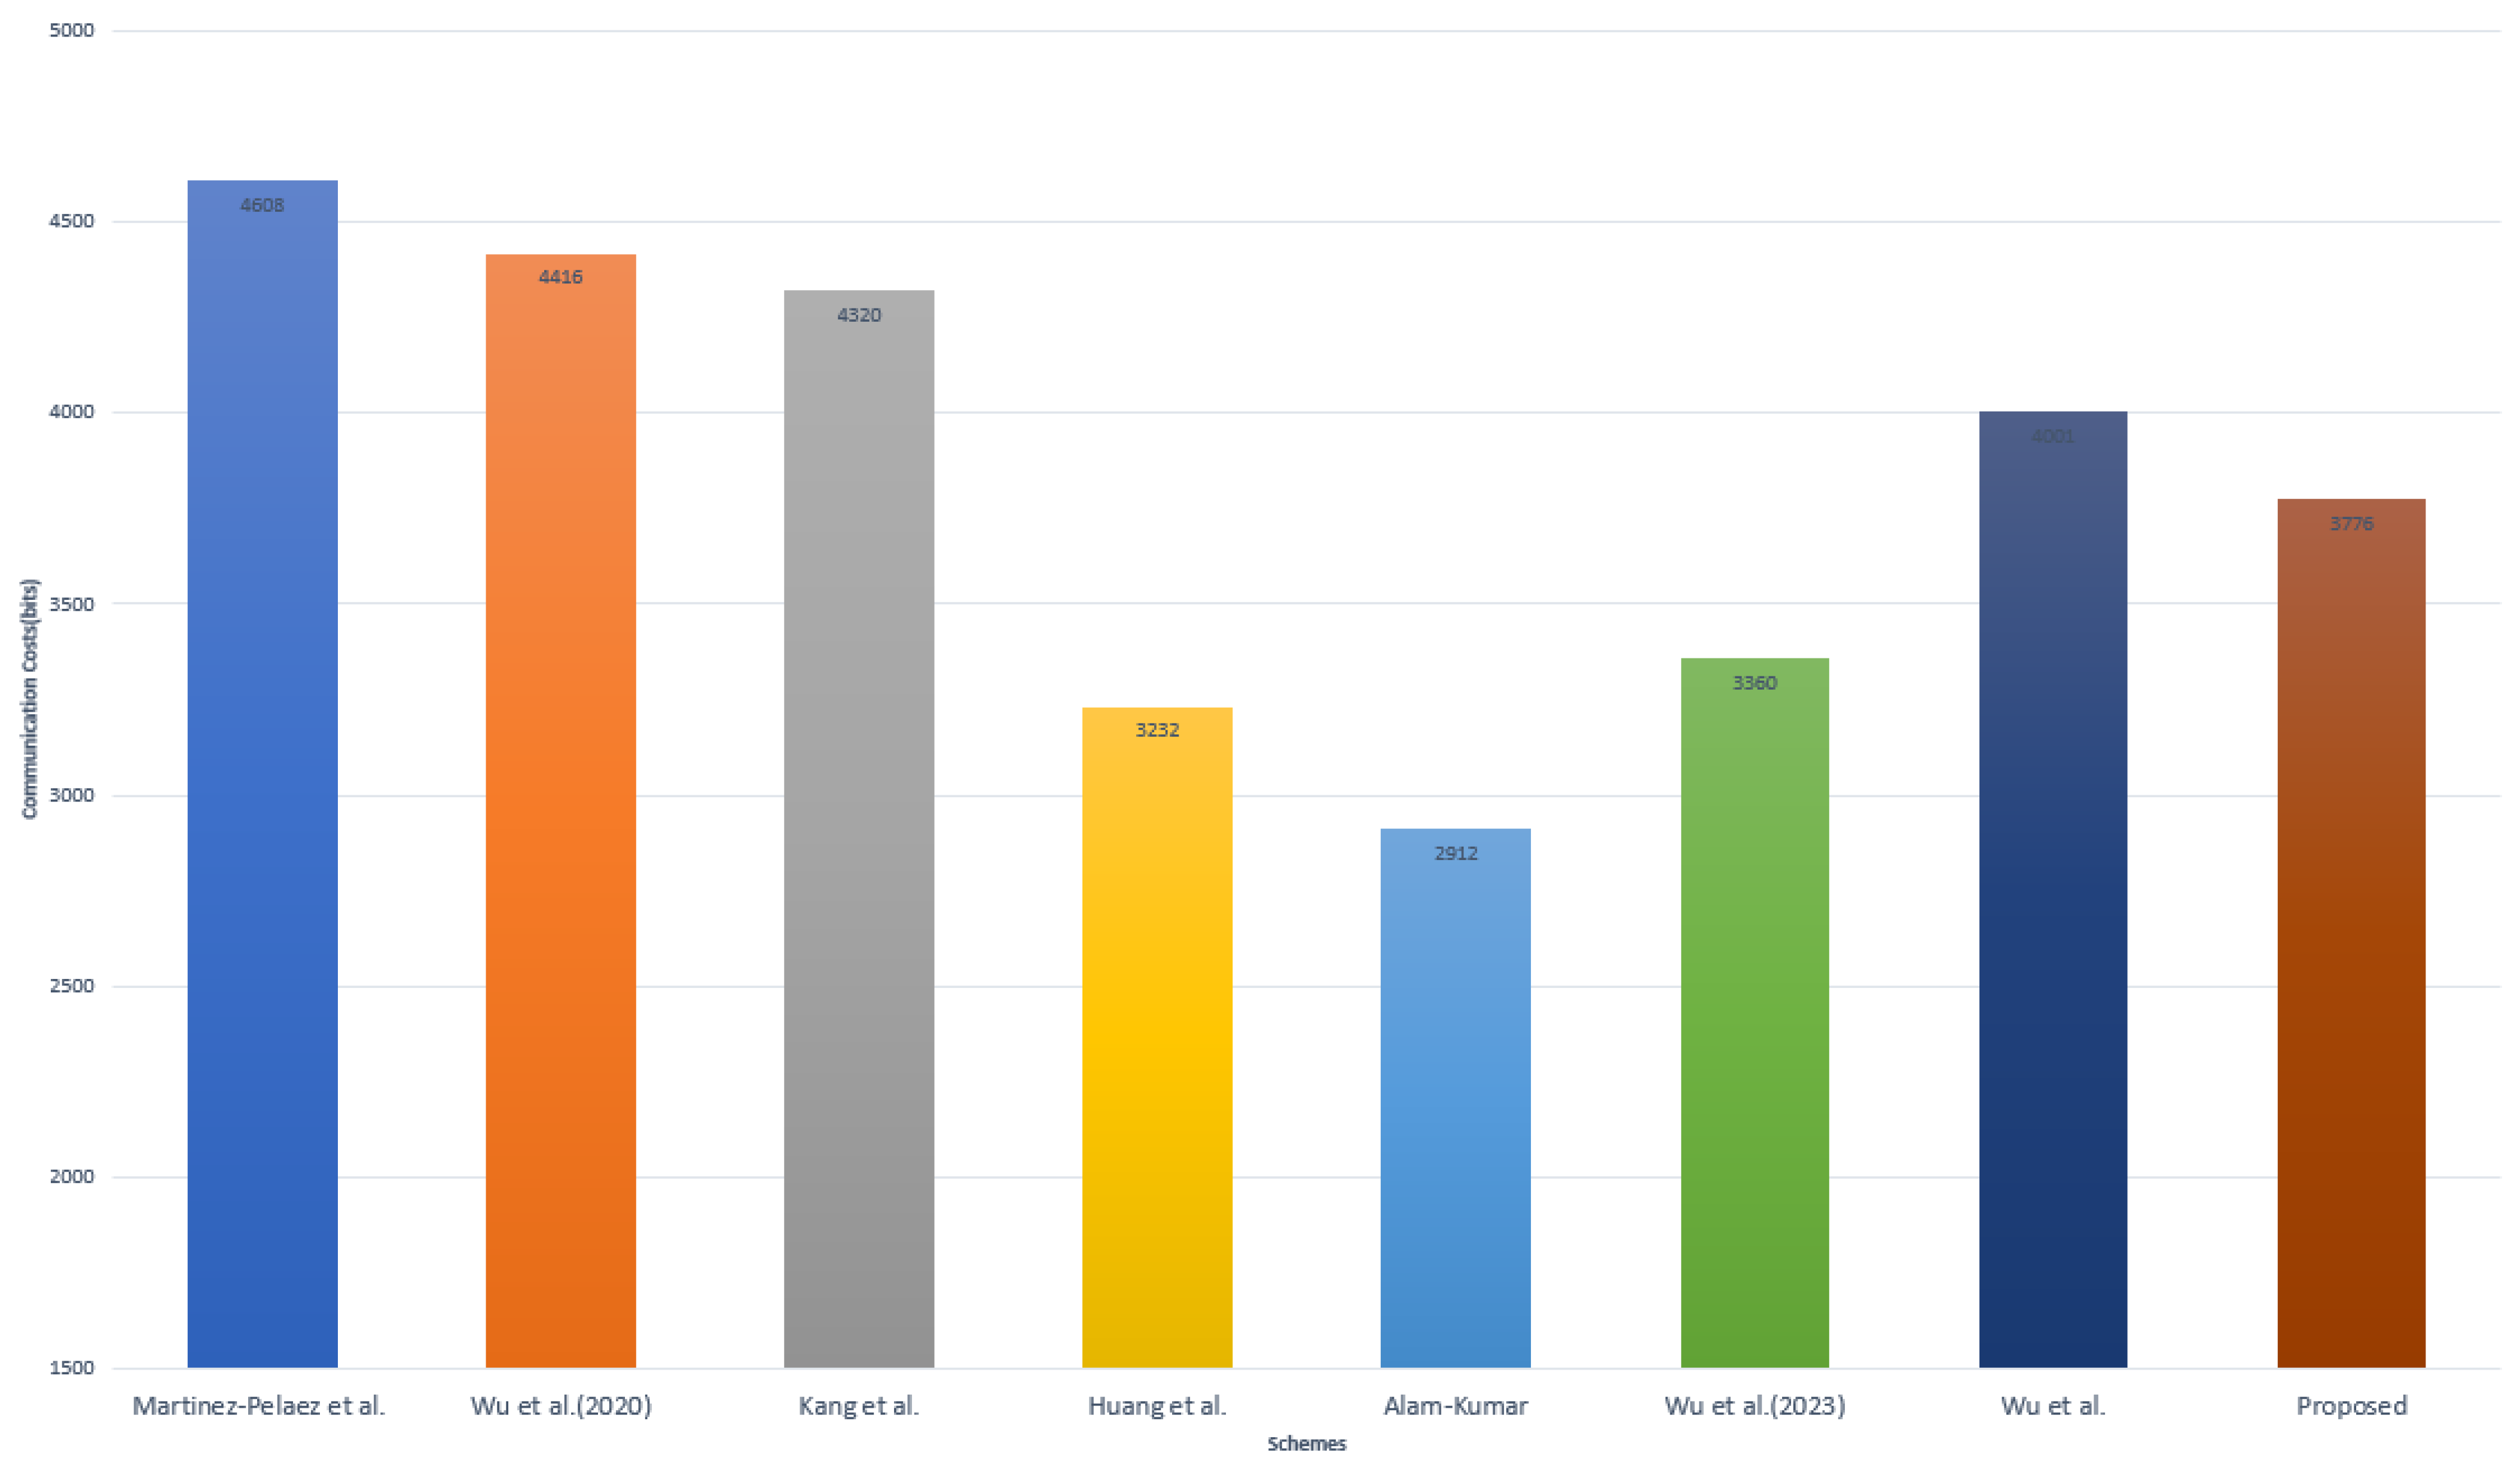
We conducted a comparative analysis of communication costs between the related schemes [11,21,44,45,46,47,48] and the proposed scheme. Based on [11], we assume the bit lengths of hash function, timestamp, string, identity, random number, fuzzy extractor, and encryption operation to be 256, 32, 160, 160, 160, 8, and 256 bits, respectively. Therefore, during the MAKA phase of our proposed scheme, the exchanged message requires (160 + 160 + 160 + 256 + 32 = 768 bits), message requires (768 + 160 + 256 + 32 = 1216 bits), message requires (160 + 160 + 160 + 160 + 256 + 256 + 32 = 1184 bits), and message requires (160 + 160 + 256 + 32 = 608 bits). Table 4 and Figure 8 present a summary of the communication costs for the associated schemes [11,21,44,45,46,47,48] and the proposed scheme.
Table 4.
Comparison analysis of communication costs.
Figure 8.
Communication costs comparison [7,11,17,21,40,41,42,43,44,45,46,47,48].
8.3. Computation Costs Comparison
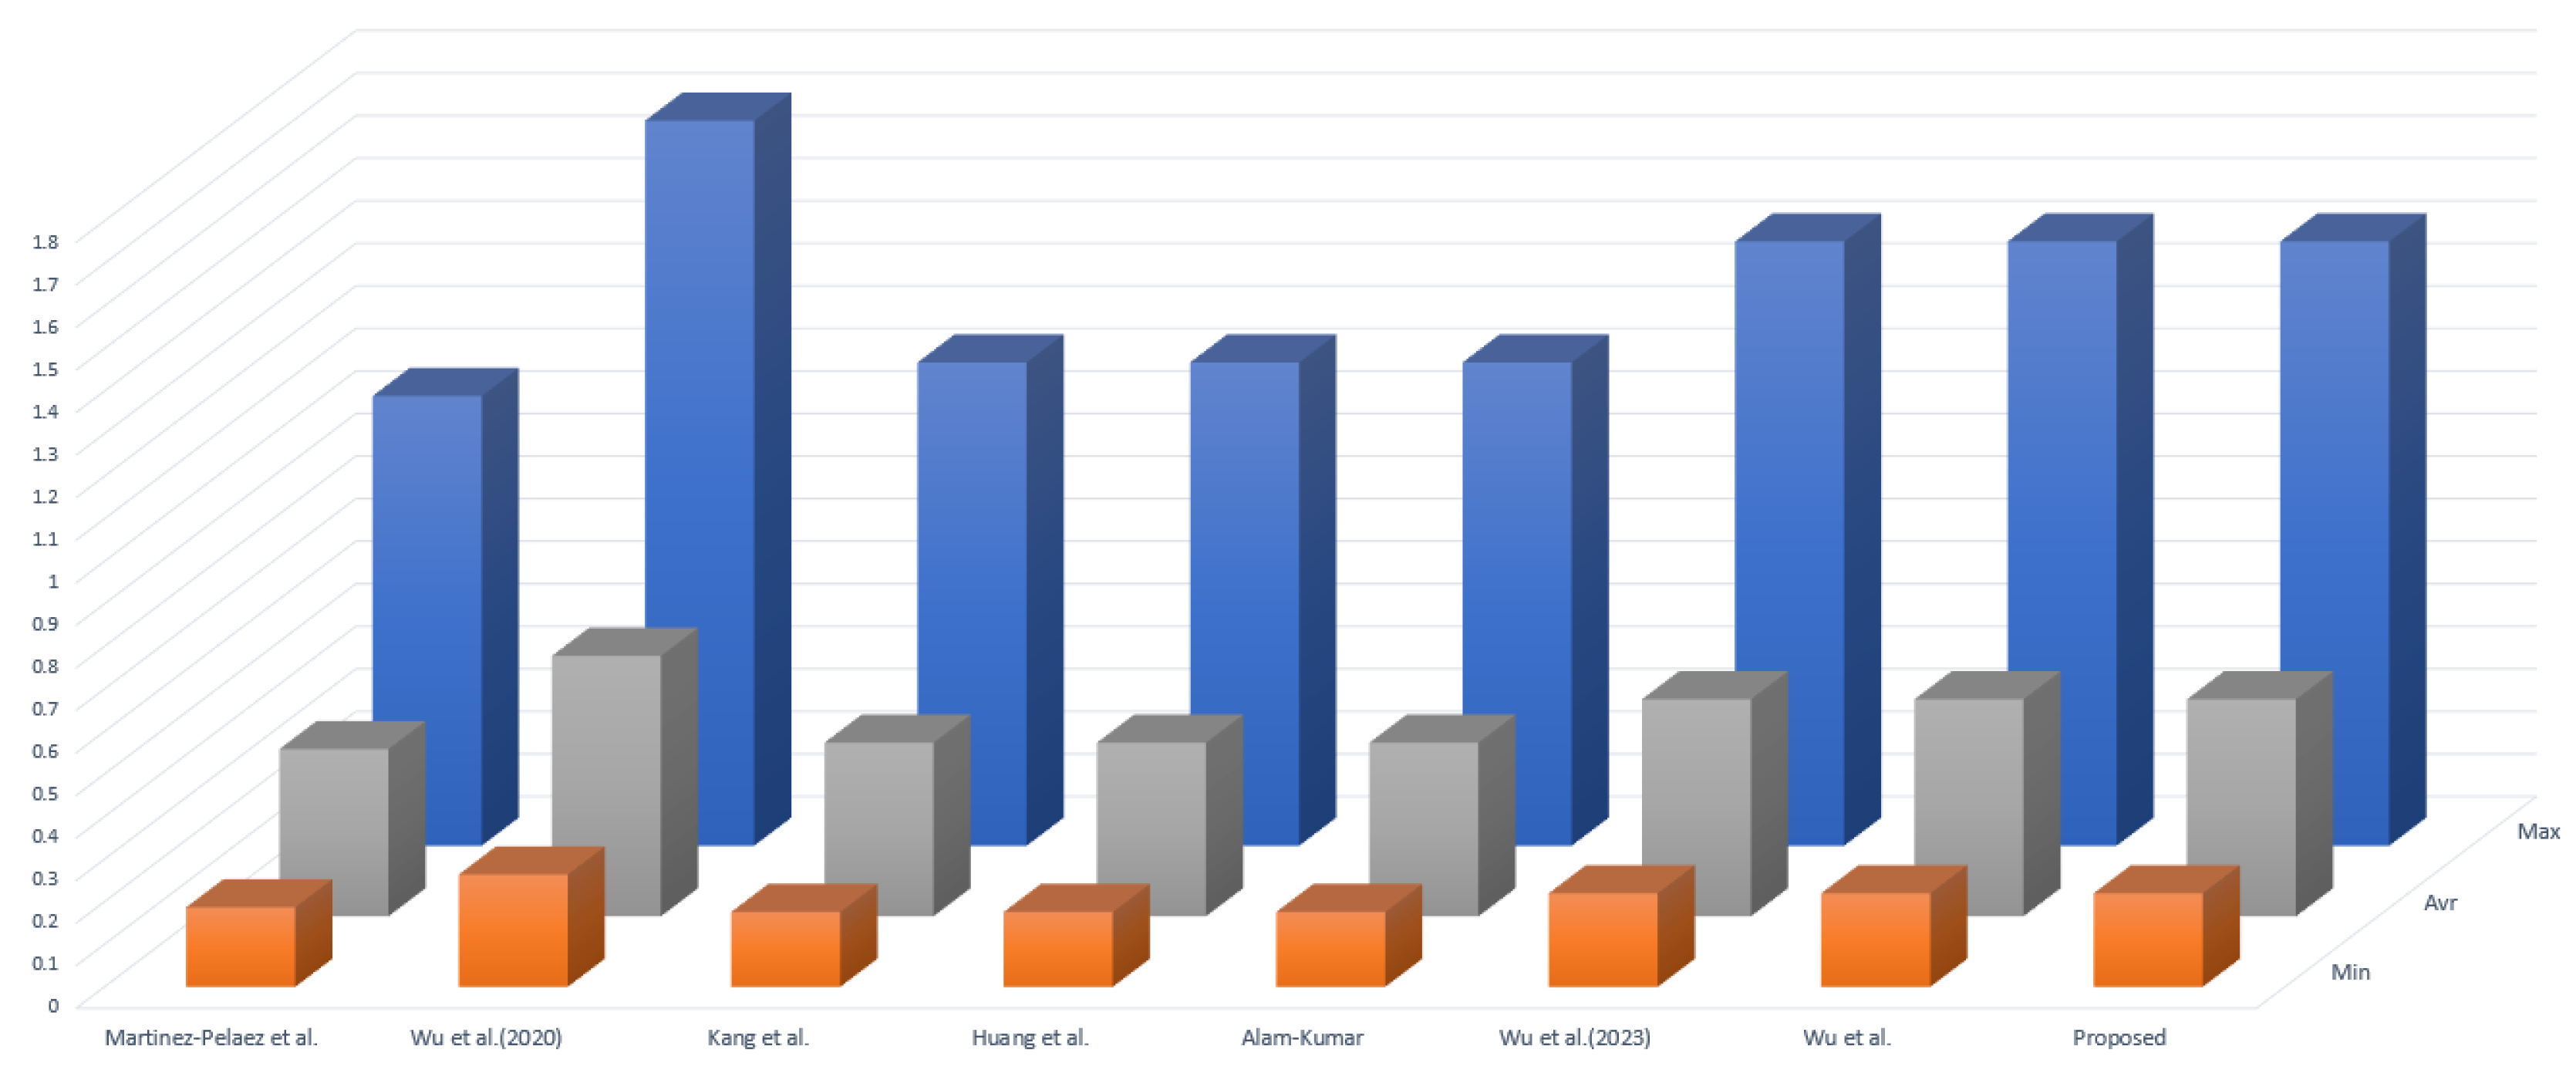
We conducted a comparative analysis of computation costs for the AKA phase of the proposed scheme and related schemes [11,21,44,45,46,47,48]. Based on [49], we designed the environment for computing costs. The experimental environment and the performance of operation costs, including the minimum, maximum, and average values, are summarized in Table 5. We represent hash function as and encryption/decryption operations of AES-256 as . Using these values, we conducted a comparison of computation costs as shown in Table 6 and Figure 9.
Table 5.
Hardware software enviroment and operation costs.
Table 6.
Comparison analysis of user side computation costs.
Figure 9.
Computation costs comparison on user side devices [7,11,17,21,40,41,42,43,44,45,46,47,48].
We can observe that the computational costs for users using the proposed scheme and users using Wu et al.’s scheme are the same. Next, we calculated the computational costs of the cloud server and control server for the proposed scheme and related schemes based on the environments provided in [49] as well. Table 7 represents the calculated computational costs for the proposed scheme and related schemes.
Table 7.
Comparison analysis of cloud server side control server side computation costs.
When comprehensively examining the results of the comparison with related schemes, we can elaborate as follows. Our proposed scheme offers more security elements compared to other schemes and is secure against various attacks such as insider attacks, impersonation attacks, stolen verification attacks, ESL attacks, privileged insider attacks, reply attacks, and offline password-guessing attacks. Simultaneously, it maintains reasonable user-side computation cost and communication cost suitable for the CloudIoT environment. However, it is noteworthy that to provide such robust security, additional computation operations on the server side have been introduced.
9. Conclusions
This study analyzed the key agreement protocol between cloud-enabled IoT devices and cloud servers as proposed by Wu et al. The scheme proposed by Wu et al. was found to be vulnerable to insider, privileged insiders, impersonation, and verification table leakage attacks and lacks user untraceability. In addition, it is inconvenient for users to update their passwords offline. To overcome these vulnerabilities and inconveniences, this study proposed a provably secure lightweight MAKA protocol for the cloud-based IoT environments.
The proposed protocol ensures safety against various attacks by preventing the exposure of critical parameters using user biometric information, and the cloud server’s secret key. Furthermore, user untraceability was ensured by updating the user’s pseudonym in every session and convenience was enhanced by adding an offline user password change and biometric template update phase. The safety of mutual authentication and the resulting session key was verified using the RoR model and BAN logic. Moreover, informal analysis was conducted to verify safety against attacks such as insider attacks, impersonation attacks, privileged attacks, ESL attacks, stolen verifier attacks and DoS attacks, while confirming security features such as user anonymity, untraceability, and perfect forward secrecy. The security features, communication costs, and computation costs of the proposed scheme were compared. This comparison demonstrated that the proposed scheme is rational in terms of communication and computation amounts in the cloud-based IoT environments, while being verified for safety.
In conclusion, the proposed scheme demonstrated robust safety and the ability to provide users with real-time services securely. Future research will focus on integrating the proposed scheme into real-world environments and various industrial settings where cloud-based IoT is applied.
Author Contributions
Conceptualization, S.J. and Y.P.; Methodology, S.J. and Y.P.; Formal analysis, Y.P.; Writing—original draft, S.J.; Writing—review editing, Y.P.; Supervision, Y.P.; Project administration, Y.P. All authors have read and agreed to the published version of the manuscript.
Funding
This research was supported by the Bisa Research Grant of Keimyung University in 2022.
Institutional Review Board Statement
Not applicable.
Informed Consent Statement
Not applicable.
Data Availability Statement
Data are contained within the article.
Conflicts of Interest
The authors declare no conflict of interest.
References
- Gubbi, J.; Buyya, R.; Marusic, S.; Palaniswami, M. Internet of Things (IoT): A vision, architectural elements, and future directions. Future Gener. Comput. Syst. 2013, 29, 1645–1660. [Google Scholar] [CrossRef] [Scilit]
- Zhao, J.C.; Zhang, J.F.; Feng, Y.; Guo, J.X. The study and application of the IOT technology in agriculture. In Proceedings of the 2010 3rd International Conference on Computer Science and Information Technology, Chengdu, China, 9–11 July 2010; IEEE: Piscataway, NJ, USA, 2010; Volume 2, pp. 462–465. [Google Scholar]
- Park, Y.; Park, Y. Three-factor user authentication and key agreement using elliptic curve cryptosystem in wireless sensor networks. Sensors 2016, 16, 2123. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Lee, S.; Kim, S.; Yu, S.; Jho, N.; Park, Y. Provably Secure PUF-Based Lightweight Mutual Authentication Scheme for Wireless Body Area Networks. Electronics 2022, 11, 3868. [Google Scholar] [CrossRef] [Scilit]
- Park, Y.; Ryu, D.; Kwon, D.; Park, Y. Provably secure mutual authentication and key agreement scheme using PUF in internet of drones deployments. Sensors 2023, 23, 2034. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Jadeja, Y.; Modi, K. Cloud computing-concepts, architecture and challenges. In Proceedings of the 2012 International Conference on Computing, Electronics and Electrical Technologies (ICCEET), Nagercoil, India, 21–22 March 2012; IEEE: Piscataway, NJ, USA, 2012; pp. 877–880. [Google Scholar]
- Dinh, T.; Kim, Y.; Lee, H. A location-based interactive model of internet of things and cloud (IoT-Cloud) for mobile cloud computing applications. Sensors 2017, 17, 489. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Babu, S.M.; Lakshmi, A.J.; Rao, B.T. A study on cloud based Internet of Things: CloudIoT. In Proceedings of the 2015 Global Conference on Communication Technologies (GCCT), Thuckalay, India, 23–24 April 2015; IEEE: Piscataway, NJ, USA, 2015; pp. 60–65. [Google Scholar]
- Zargar, S.; Shahidinejad, A.; Ghobaei-Arani, M. A lightweight authentication protocol for IoT-based cloud environment. Int. J. Commun. Syst. 2021, 34, e4849. [Google Scholar] [CrossRef] [Scilit]
- Kim, M.; Yu, S.; Lee, J.; Park, Y.; Park, Y. Design of secure protocol for cloud-assisted electronic health record system using blockchain. Sensors 2020, 20, 2913. [Google Scholar] [CrossRef] [Scilit]
- Wu, T.Y.; Meng, Q.; Kumari, S.; Zhang, P. Rotating behind security: A lightweight authentication protocol based on iot-enabled cloud computing environments. Sensors 2022, 22, 3858. [Google Scholar] [CrossRef] [Scilit]
- Shouqi, C.; Wanrong, L.; Liling, C.; Xin, H.; Zhiyong, J. An improved authentication protocol using smart cards for the Internet of Things. IEEE Access 2019, 7, 157284–157292. [Google Scholar] [CrossRef] [Scilit]
- Nikooghadam, M.; Jahantigh, R.; Arshad, H. A lightweight authentication and key agreement protocol preserving user anonymity. Multimed. Tools Appl. 2017, 76, 13401–13423. [Google Scholar] [CrossRef] [Scilit]
- Kumari, S.; Chaudhry, S.A.; Wu, F.; Li, X.; Farash, M.S.; Khan, M.K. An improved smart card based authentication scheme for session initiation protocol. Peer Netw. Appl. 2017, 10, 92–105. [Google Scholar] [CrossRef] [Scilit]
- Limbasiya, T.; Soni, M.; Mishra, S.K. Advanced formal authentication protocol using smart cards for network applicants. Comput. Electr. Eng. 2018, 66, 50–63. [Google Scholar] [CrossRef] [Scilit]
- Chandrakar, P.; Om, H. An extended ECC-based anonymity-preserving 3-factor remote authentication scheme usable in TMIS. Int. J. Commun. Syst. 2018, 31, e3540. [Google Scholar] [CrossRef] [Scilit]
- Sharma, G.; Kalra, S. A lightweight multi-factor secure smart card based remote user authentication scheme for cloud-IoT applications. J. Inf. Secur. Appl. 2018, 42, 95–106. [Google Scholar] [CrossRef] [Scilit]
- Gope, P.; Sikdar, B. Lightweight and privacy-preserving two-factor authentication scheme for IoT devices. IEEE Internet Things J. 2018, 6, 580–589. [Google Scholar] [CrossRef] [Scilit]
- Siddiqui, Z.; Gao, J.; Khan, M.K. An improved lightweight PUF–PKI digital certificate authentication scheme for the Internet of Things. IEEE Internet Things J. 2022, 9, 19744–19756. [Google Scholar] [CrossRef] [Scilit]
- Zhou, L.; Li, X.; Yeh, K.H.; Su, C.; Chiu, W. Lightweight IoT-based authentication scheme in cloud computing circumstance. Future Gener. Comput. Syst. 2019, 91, 244–251. [Google Scholar] [CrossRef] [Scilit]
- Martínez-Peláez, R.; Toral-Cruz, H.; Parra-Michel, J.R.; García, V.; Mena, L.J.; Félix, V.G.; Ochoa-Brust, A. An enhanced lightweight IoT-based authentication scheme in cloud computing circumstances. Sensors 2019, 19, 2098. [Google Scholar] [CrossRef] [Scilit]
- Alzahrani, B.A.; Chaudhry, S.A.; Barnawi, A.; Al-Barakati, A.; Shon, T. An anonymous device to device authentication protocol using ECC and self certified public keys usable in Internet of Things based autonomous devices. Electronics 2020, 9, 520. [Google Scholar] [CrossRef] [Scilit]
- Islam, S.H.; Biswas, G. Design of two-party authenticated key agreement protocol based on ECC and self-certified public keys. Wirel. Pers. Commun. 2015, 82, 2727–2750. [Google Scholar] [CrossRef] [Scilit]
- Mandal, S.; Mohanty, S.; Majhi, B. Cryptanalysis and enhancement of an anonymous self-certified key exchange protocol. Wirel. Pers. Commun. 2018, 99, 863–891. [Google Scholar] [CrossRef] [Scilit]
- Chen, Y.; López, L.; Martínez, J.F.; Castillejo, P. A lightweight privacy protection user authentication and key agreement scheme tailored for the Internet of Things environment: LightPriAuth. J. Sensors 2018, 2018, 7574238. [Google Scholar] [CrossRef] [Scilit]
- Lee, J.; Yu, S.; Kim, M.; Park, Y.; Das, A.K. On the design of secure and efficient three-factor authentication protocol using honey list for wireless sensor networks. IEEE Access 2020, 8, 107046–107062. [Google Scholar] [CrossRef] [Scilit]
- Yu, Y.; Hu, L.; Chu, J. A secure authentication and key agreement scheme for IoT-based cloud computing environment. Symmetry 2020, 12, 150. [Google Scholar] [CrossRef] [Scilit]
- He, D.; Zeadally, S.; Kumar, N.; Wu, W. Efficient and anonymous mobile user authentication protocol using self-certified public key cryptography for multi-server architectures. IEEE Trans. Inf. Forensics Secur. 2016, 11, 2052–2064. [Google Scholar] [CrossRef] [Scilit]
- Tsai, J.L.; Lo, N.W. A privacy-aware authentication scheme for distributed mobile cloud computing services. IEEE Syst. J. 2015, 9, 805–815. [Google Scholar] [CrossRef] [Scilit]
- Kumari, A.; Kumar, V.; Abbasi, M.Y.; Kumari, S.; Chaudhary, P.; Chen, C.M. Csef: Cloud-based secure and efficient framework for smart medical system using ecc. IEEE Access 2020, 8, 107838–107852. [Google Scholar] [CrossRef] [Scilit]
- Bhuarya, P.; Chandrakar, P.; Ali, R.; Sharaff, A. An enhanced authentication scheme for Internet of Things and cloud based on elliptic curve cryptography. Int. J. Commun. Syst. 2021, 34, e4834. [Google Scholar] [CrossRef] [Scilit]
- Dolev, D.; Yao, A. On the security of public key protocols. IEEE Trans. Inf. Theory 1983, 29, 198–208. [Google Scholar] [CrossRef] [Scilit]
- Canetti, R.; Krawczyk, H. Universally composable notions of key exchange and secure channels. In Proceedings of the Advances in Cryptology—EUROCRYPT 2002: International Conference on the Theory and Applications of Cryptographic Techniques, Amsterdam, The Netherlands, 28 April–2 May 2002; Springer: Berlin/Heidelberg, Germany, 2002; pp. 337–351. [Google Scholar]
- Abdalla, M.; Fouque, P.A.; Pointcheval, D. Password-based authenticated key exchange in the three-party setting. In Proceedings of the Public Key Cryptography-PKC 2005: 8th International Workshop on Theory and Practice in Public Key Cryptography, Les Diablerets, Switzerland, 23–26 January 2005; Springer: Berlin/Heidelberg, Germany, 2005; pp. 65–84. [Google Scholar]
- Wang, D.; Cheng, H.; Wang, P.; Huang, X.; Jian, G. Zipf’s law in passwords. IEEE Trans. Inf. Forensics Secur. 2017, 12, 2776–2791. [Google Scholar] [CrossRef] [Scilit]
- Kwon, D.K.; Yu, S.J.; Lee, J.Y.; Son, S.H.; Park, Y.H. WSN-SLAP: Secure and lightweight mutual authentication protocol for wireless sensor networks. Sensors 2021, 21, 936. [Google Scholar] [CrossRef] [Scilit]
- Yu, S.; Lee, J.; Sutrala, A.K.; Das, A.K.; Park, Y. LAKA-UAV: Lightweight authentication and key agreement scheme for cloud-assisted Unmanned Aerial Vehicle using blockchain in flying ad hoc networks. Comput. Netw. 2023, 224, 109612. [Google Scholar] [CrossRef] [Scilit]
- Kim, M.; Lee, J.; Oh, J.; Kwon, D.; Park, K.; Park, Y.; Park, K.H. A Secure Batch Authentication Scheme for Multiaccess Edge Computing in 5G-Enabled Intelligent Transportation System. IEEE Access 2022, 10, 96224–96238. [Google Scholar] [CrossRef] [Scilit]
- Boyko, V.; MacKenzie, P.; Patel, S. Provably secure password-authenticated key exchange using Diffie-Hellman. In Proceedings of the Advances in Cryptology—EUROCRYPT 2000: International Conference on the Theory and Application of Cryptographic Techniques, Bruges, Belgium, 14–18 May 2000; Proceedings 19. Springer: Berlin/Heidelberg, Germany, 2000; pp. 156–171. [Google Scholar]
- Burrows, M.; Abadi, M.; Needham, R. A logic of authentication. ACM Trans. Comput. Syst. (TOCS) 1990, 8, 18–36. [Google Scholar] [CrossRef] [Scilit]
- Kwon, D.; Son, S.; Park, Y.; Kim, H.; Park, Y.; Lee, S.; Jeon, Y. Design of secure handover authentication scheme for urban air mobility environments. IEEE Access 2022, 10, 42529–42541. [Google Scholar] [CrossRef] [Scilit]
- Son, S.; Kwon, D.; Lee, S.; Jeon, Y.; Das, A.K.; Park, Y. Design of Secure and Lightweight Authentication Scheme for UAV-Enabled Intelligent Transportation Systems using Blockchain and PUF. IEEE Access 2023, 11, 60240–60253. [Google Scholar] [CrossRef] [Scilit]
- Cho, Y.; Oh, J.; Kwon, D.; Son, S.; Yu, S.; Park, Y.; Park, Y. A secure three-factor authentication protocol for e-governance system based on multiserver environments. IEEE Access 2022, 10, 74351–74365. [Google Scholar] [CrossRef] [Scilit]
- Wu, H.L.; Chang, C.C.; Zheng, Y.Z.; Chen, L.S.; Chen, C.C. A secure IoT-based authentication system in cloud computing environment. Sensors 2020, 20, 5604. [Google Scholar] [CrossRef] [Scilit]
- Kang, B.; Han, Y.; Qian, K.; Du, J. Analysis and improvement on an authentication protocol for IoT-enabled devices in distributed cloud computing environment. Math. Probl. Eng. 2020. [Google Scholar] [CrossRef] [Scilit]
- Huang, H.; Lu, S.; Wu, Z.; Wei, Q. An efficient authentication and key agreement protocol for IoT-enabled devices in distributed cloud computing architecture. EURASIP J. Wirel. Commun. Netw. 2021, 2021, 150. [Google Scholar] [CrossRef] [Scilit]
- Alam, I.; Kumar, M. A novel protocol for efficient authentication in cloud-based IoT devices. Multimed. Tools Appl. 2022, 81, 13823–13843. [Google Scholar] [CrossRef] [Scilit]
- Wu, T.Y.; Kong, F.; Meng, Q.; Kumari, S.; Chen, C.M. Rotating behind security: An enhanced authentication protocol for IoT-enabled devices in distributed cloud computing architecture. EURASIP J. Wirel. Commun. Netw. 2023, 2023, 36. [Google Scholar] [CrossRef] [Scilit]
- Park, K.; Park, Y. IAKA-CIOT: An improved authentication and key agreement scheme for cloud enabled internet of things using physical unclonable function. Sensors 2022, 22, 6264. [Google Scholar] [CrossRef] [Scilit] [PubMed]

Disclaimer/Publisher’s Note: The statements, opinions and data contained in all publications are solely those of the individual author(s) and contributor(s) and not of MDPI and/or the editor(s). MDPI and/or the editor(s) disclaim responsibility for any injury to people or property resulting from any ideas, methods, instructions or products referred to in the content. |
© 2023 by the authors. Licensee MDPI, Basel, Switzerland. This article is an open access article distributed under the terms and conditions of the Creative Commons Attribution (CC BY) license (https://creativecommons.org/licenses/by/4.0/).