Journal Description
Network
Network
is an international, peer-reviewed, open access journal on science and technology of networks, published quarterly online by MDPI.
- Open Access— free for readers, with article processing charges (APC) paid by authors or their institutions.
- High Visibility: indexed within ESCI (Web of Science), Scopus, EBSCO, and other databases.
- Journal Rank: JCR - Q2 (Computer Science, Information Systems) / CiteScore - Q1 (Engineering (miscellaneous))
- Rapid Publication: manuscripts are peer-reviewed and a first decision is provided to authors approximately 23.2 days after submission; acceptance to publication is undertaken in 4.8 days (median values for papers published in this journal in the first half of 2026).
- Recognition of Reviewers: Reviewers whose reports are timely and of high quality receive an APC discount voucher for a future publication in an MDPI journal. Become a reviewer.
- Network is a companion journal of Electronics.
- Journal Clusters of Network and Communications Technology: Future Internet, IoT, Telecom, Journal of Sensor and Actuator Networks, Network, Signals.
Impact Factor:
3.7 (2025);
5-Year Impact Factor:
3.1 (2025)
Latest Articles
Agentic AI-Driven SOC-as-a-Service for Optimizing Incident Response in Cloud Environments: A Conceptual Framework
Network 2026, 6(4), 84; https://doi.org/10.3390/network6040084 (registering DOI) - 1 Oct 2026
Abstract
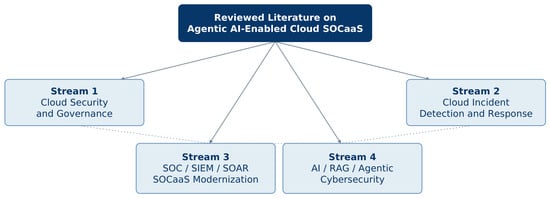
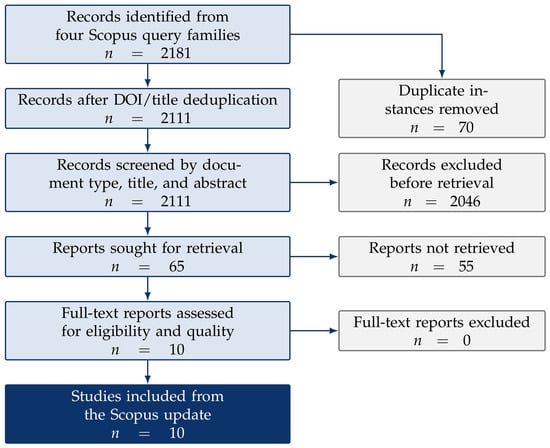
Cloud security operations must process high-volume, rapidly changing telemetry within short response windows while maintaining governance and accountability. However, the literature on cloud defense, SOC modernization, retrieval-augmented generation (RAG), and Agentic AI remains fragmented. This paper combines a legacy corpus of 23 studies
[...] Read more.
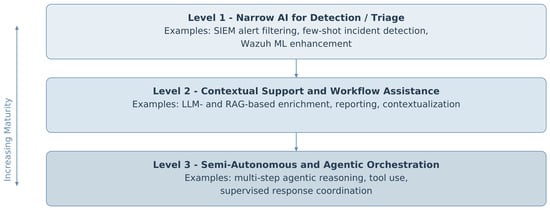
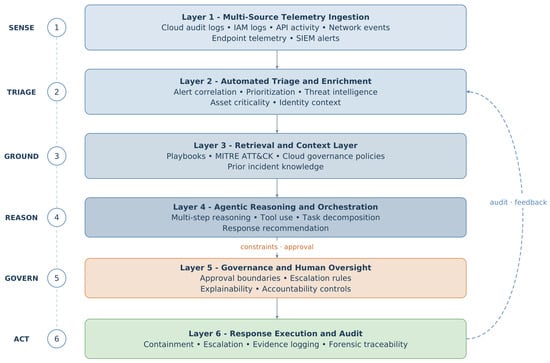
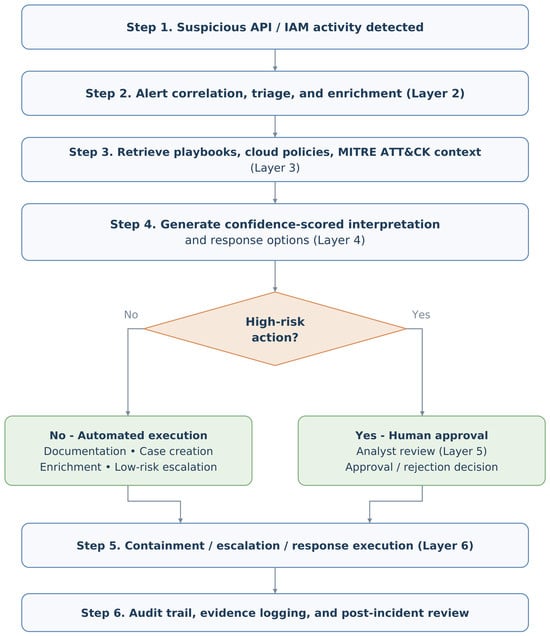
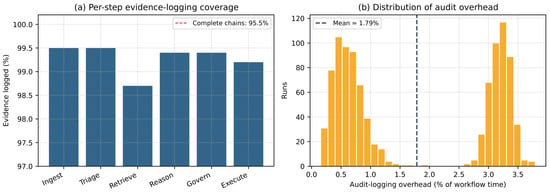
Cloud security operations must process high-volume, rapidly changing telemetry within short response windows while maintaining governance and accountability. However, the literature on cloud defense, SOC modernization, retrieval-augmented generation (RAG), and Agentic AI remains fragmented. This paper combines a legacy corpus of 23 studies with a reproducible Scopus update of 10 quality-appraised studies and proposes a secure Agentic AI-driven SOC-as-a-Service (SOCaaS) framework. The review identifies long-standing problems of alert fatigue, limited operational context, fragmented tooling, and weak validation, together with unresolved concerns regarding trust, explainability, bounded autonomy, forensic preparedness, and prompt injection. The principal technical contribution is a six-layer architecture supported by a cross-cutting security and trust-enforcement plane that separates untrusted telemetry from agent instructions, constrains retrieval and tool use, applies deterministic governance checks, requires human approval for high-impact actions, and enables auditable execution. Four simulation experiments evaluate component-level behavior for automated triage, retrieval grounding, governance-gated orchestration, and audit completeness. Under the stated synthetic assumptions, the governed agentic configuration yields a 6.8-fold reduction in mean response time relative to the modeled manual baseline. These results indicate internal feasibility rather than production efficacy.
Full article
(This article belongs to the Special Issue Advanced 6G Networks for the Internet of Things)
►
Show Figures
Open AccessArticle
Improved Soft Rough Set Covering Model for Wireless Indoor Localization: Modeling and Accuracy Analysis
by
Aya Ayad Hussein, Goh Chin Hock, Sieh Kiong Tiong, Hazem Noori Abdulrazzak and Ahmed Khaleel Hasan
Network 2026, 6(4), 83; https://doi.org/10.3390/network6040083 - 28 Sep 2026
Abstract
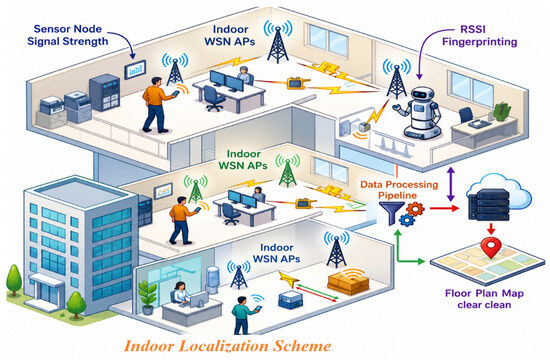
Indoor localization based on Received Signal Strength (RSS) fingerprinting remains a prominent paradigm owing to its economic viability and seamless integration with existing wireless infrastructure. Nevertheless, positioning accuracy is frequently compromised by spatiotemporal environmental dynamics, device heterogeneity, and high-variance noise fluctuations inherent in
[...] Read more.
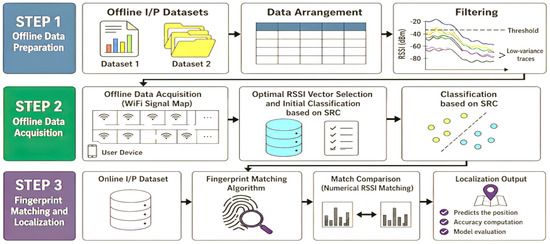
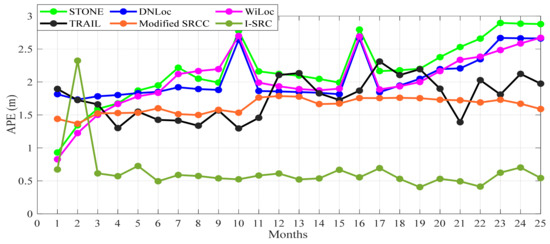
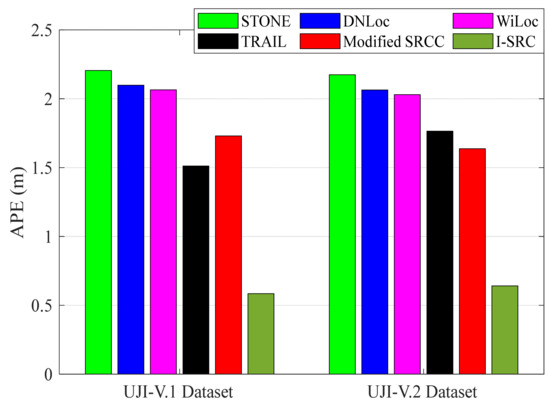
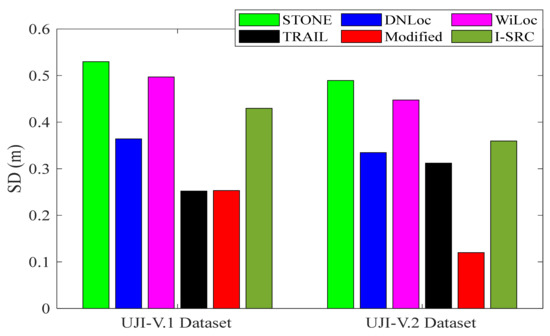
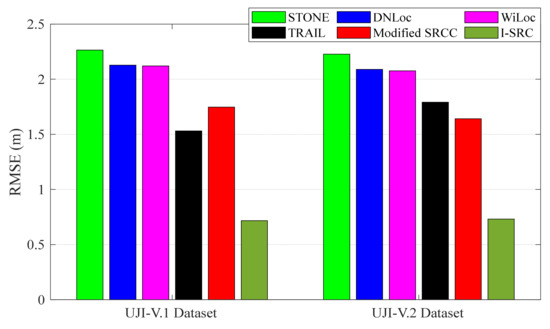
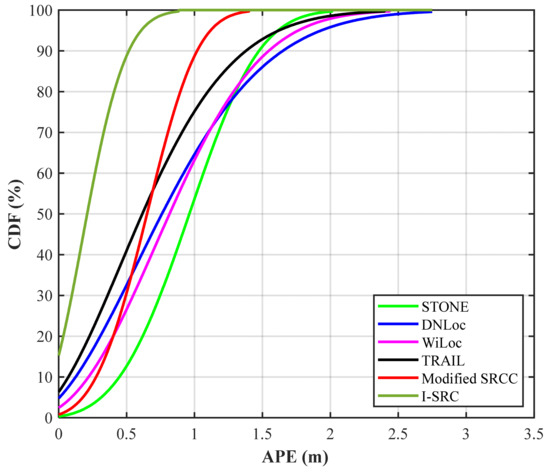
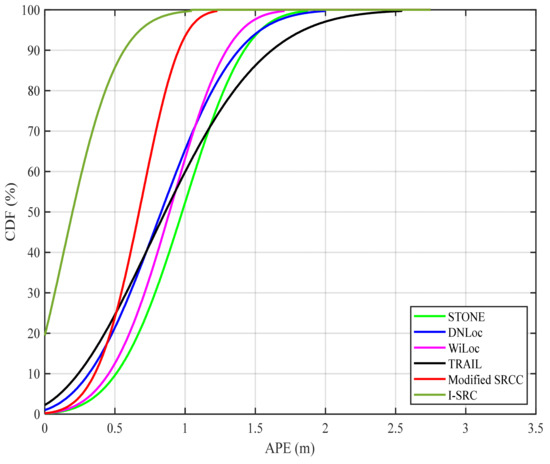
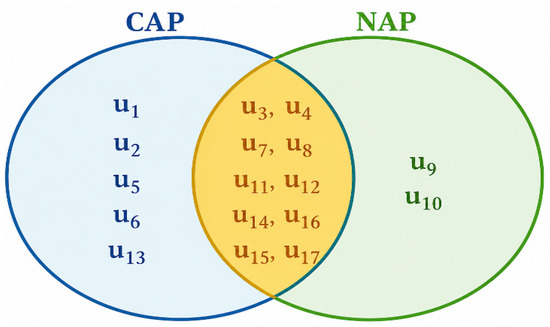
Indoor localization based on Received Signal Strength (RSS) fingerprinting remains a prominent paradigm owing to its economic viability and seamless integration with existing wireless infrastructure. Nevertheless, positioning accuracy is frequently compromised by spatiotemporal environmental dynamics, device heterogeneity, and high-variance noise fluctuations inherent in individual Reference Points (RPs). To overcome these limitations, this paper introduces an Improved Soft Rough set-based Covering (I-SRC) model underpinned by a rigorous three-stage localization architecture. Stage (i): Raw offline RSS measurements undergo advanced filtering and structural optimization to construct a robust, noise-resilient radio map. Stage (ii): A specialized SRC methodology is deployed to classify the training instances, effectively mitigating the high dimensionality of the RSS feature space while preserving critical spatial characteristics. Stage (iii): A high-fidelity online matching algorithm correlates real-time RSS vectors with the established offline database to estimate coordinates. Comprehensive evaluations across multiple benchmark datasets demonstrate that the proposed I-SRC framework achieves a robust classification accuracy of approximately 96.38% and 97.75% on the UJI-V.1 and UJI-V.2 datasets, respectively. Crucially, the model yields outstanding positioning precision, recording low Average Positioning Errors (APE) of 0.58 m and 0.64 m on the respective datasets, thereby significantly outperforming contemporary state-of-the-art fingerprinting baselines. These results confirm that the I-SRC framework offers an efficient, scalable, and highly accurate solution for complex indoor positioning environments.
Full article
(This article belongs to the Special Issue Recent Advances in Wireless Sensor Networks and Mobile Edge Computing)
►▼
Show Figures

Figure 1
Open AccessArticle
ASIF: A Resource-Aware Selective Network Traffic Inspection Framework Integrating Certificate Screening, Targeted Decryption, and Feature Fusion
by
Liangbin Yang, Lulu Liu, Xiaomei Liu, Jing Bai and Lizhen Liu
Network 2026, 6(4), 82; https://doi.org/10.3390/network6040082 - 28 Sep 2026
Abstract
►▼
Show Figures
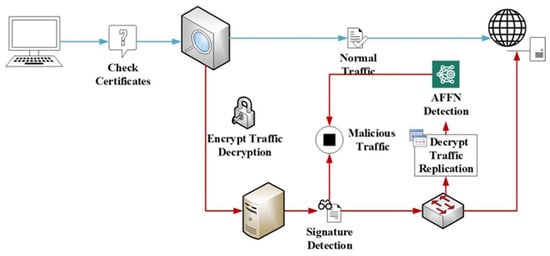
The widespread use of TLS in IoT and networked systems increases inspection cost while restricting direct access to payload content. This paper presents the Adaptive Secure Inspection Framework (ASIF), a resource-aware selective network traffic inspection framework that coordinates certificate-based routing, authorized targeted decryption,
[...] Read more.
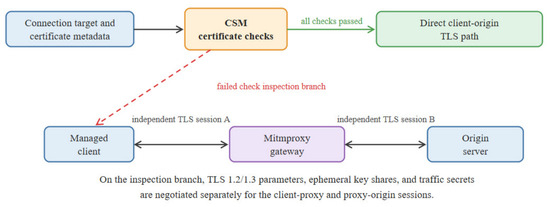
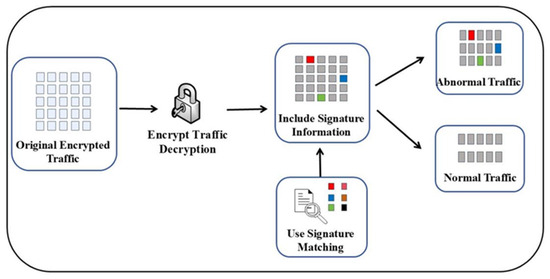
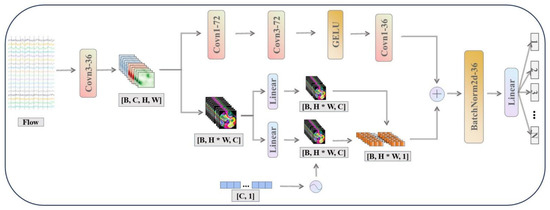
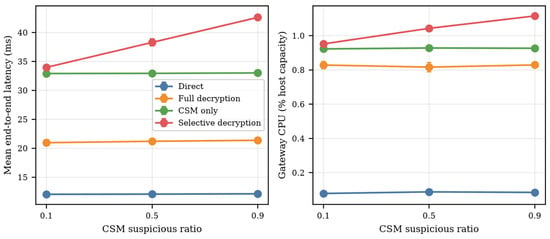
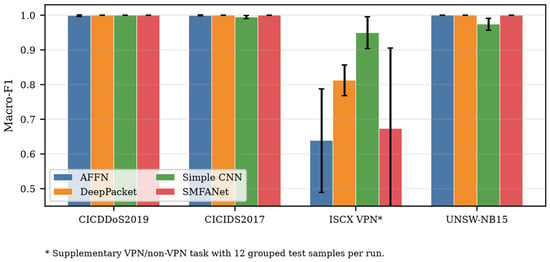
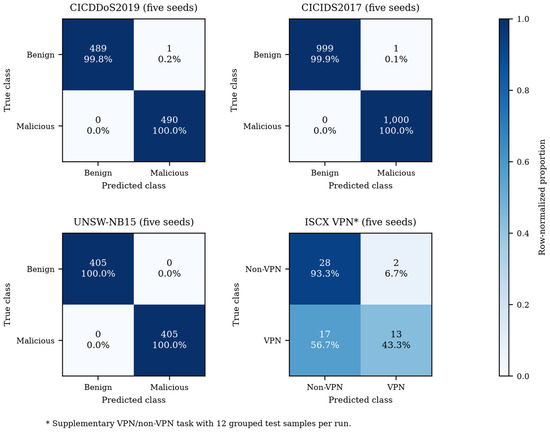
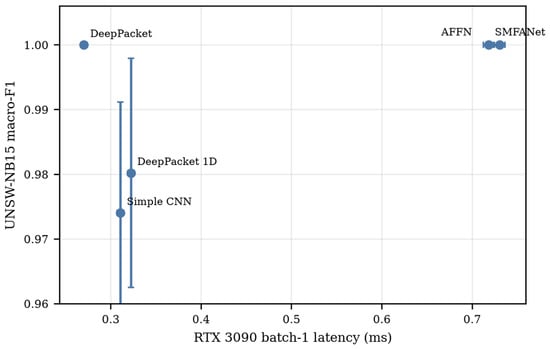
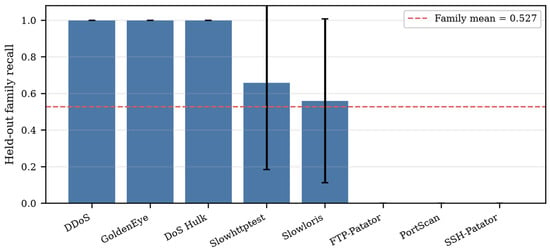
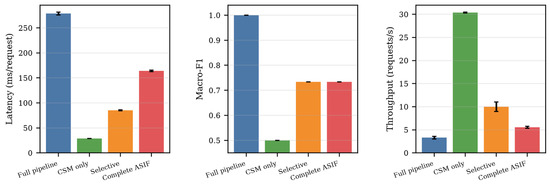
The widespread use of TLS in IoT and networked systems increases inspection cost while restricting direct access to payload content. This paper presents the Adaptive Secure Inspection Framework (ASIF), a resource-aware selective network traffic inspection framework that coordinates certificate-based routing, authorized targeted decryption, known-signature matching, and learned flow classification. ASIF contains three components: (1) a Certificate Screening Module (CSM), which applies configured checks of root trust, chain integrity, and leaf-certificate validity as an early routing signal; (2) a Targeted Decryption and Signature Matching Module (TDSMM), which directs certificate-suspicious traffic to authorized Mitmproxy interception and Snort inspection; and (3) an Attentive Feature Fusion Network (AFFN), which combines global and local representations for network-flow classification. The evaluation covers controlled certificate cases, selective-decryption overhead, known-signature matching, learned classification on three intrusion datasets, a supplementary VPN/non-VPN task, held-out attack families, and the integrated pipeline. The intrusion-dataset labels do not establish that every flow is encrypted. Several models obtain near-ceiling scores under the balanced grouped protocol, while AFFN achieves a macro-F1 of 0.639 ± 0.149 on the supplementary ISCX VPN/non-VPN task and does not outperform all baselines. Across held-out attack families, recall averages 0.527 ± 0.466, indicating strong family dependence. In the controlled end-to-end experiment, complete ASIF decrypts 50% of requests and reduces mean latency from 278.78 to 164.19 ms/request relative to full decryption, while malicious-class recall decreases to 0.500 and macro-F1 to 0.733 because valid-certificate malicious traffic bypasses deeper inspection. These results characterize ASIF as a resource-aware selective inspection strategy with explicit coverage limitations rather than a universal encrypted-malicious-traffic detector.
Full article

Figure 1
Open AccessArticle
SNMP Exposure Within Corporate Networks
by
Pelayo Nuño, David Álvarez, Alicia Flórez, Francisco G. Bulnes and Juan C. Granda
Network 2026, 6(3), 81; https://doi.org/10.3390/network6030081 (registering DOI) - 21 Sep 2026
Abstract
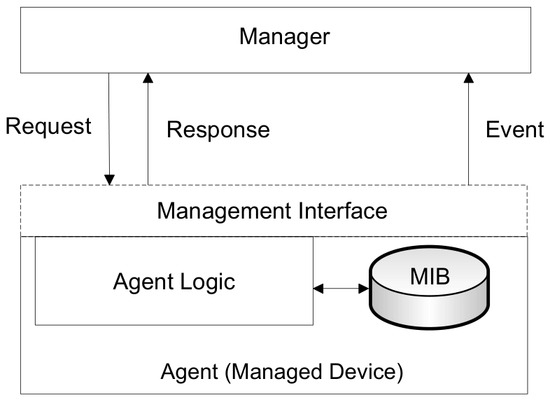
The Simple Network Management Protocol (SNMP) remains the de facto standard for monitoring corporate networks. However, many devices lack support for its latest version, and common administrator misconfigurations expose organizations to severe security risks. This study aims to provide guidance on improving SNMP
[...] Read more.
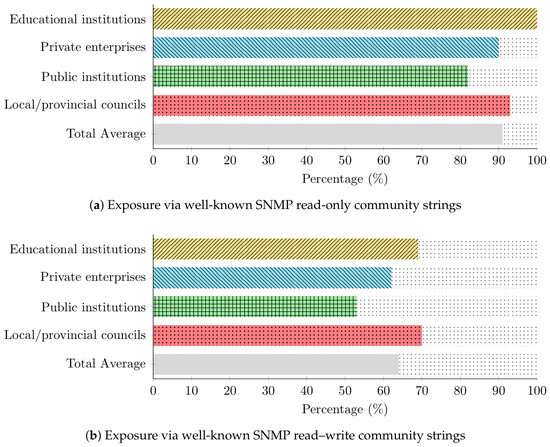
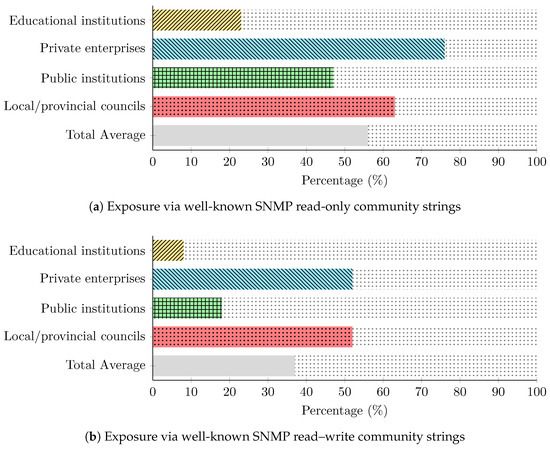
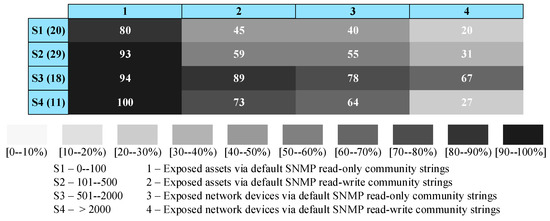
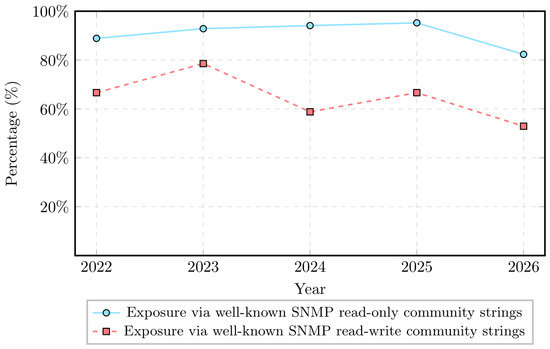
The Simple Network Management Protocol (SNMP) remains the de facto standard for monitoring corporate networks. However, many devices lack support for its latest version, and common administrator misconfigurations expose organizations to severe security risks. This study aims to provide guidance on improving SNMP configuration security by identifying devices exposed through legacy SNMPv1 and SNMPv2c within private corporate networks. A grey-box penetration testing methodology was conducted across 78 public and private organisations in Spain, employing the scanning tools Onesixtyone and Metasploit to identify active devices utilising well-known community strings. The assessment reveals widespread vulnerabilities: more than 90% of the analysed organisations have assets exposed via well-known read-only community strings, and over 60% are vulnerable through well-known read–write community strings, resulting in a total of 2403 and 645 vulnerable devices, respectively. This exposure is highly critical in network hardware, affecting over 50% (read-only) and nearly 40% (read–write) of the organisations. Furthermore, multiple active disclosed vulnerabilities using OpenVAS and prevalent administrative flaws were identified. These findings underscore that basic deployment misconfigurations leave extensive internal assets exposed, highlighting an urgent need for structural remediation and improved administrative training within corporate environments.
Full article
(This article belongs to the Collection Advanced Technologies in Network and Service Management, 2nd Edition)
►▼
Show Figures

Figure 1
Open AccessArticle
Machine-Learned Mismatch and Task Preservation Beliefs in CoSMA DAI for Common Knowledge Aware Semantic Alignment
by
Iacovos Ioannou, Christophoros Christophorou, Marios Raspopoulos and Vasos Vassiliou
Network 2026, 6(3), 80; https://doi.org/10.3390/network6030080 - 17 Sep 2026
Abstract
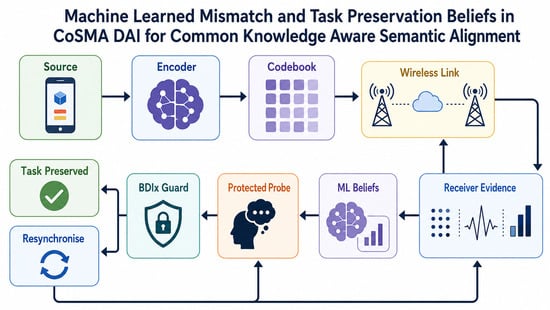
Correct packet delivery does not guarantee correct semantic interpretation when endpoint meanings for the same learned codeword diverge. CoSMA DAI is proposed for mismatch detection, protected confirmation, task preservation and semantic repair. Channel-conditioned global evidence, semantic class local evidence, temporal dynamics, channel context
[...] Read more.
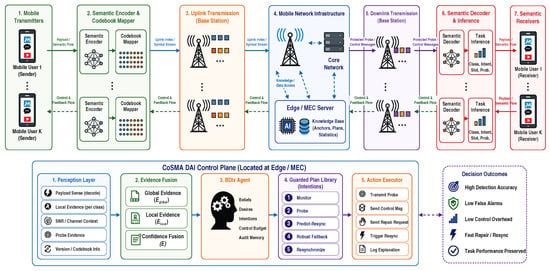
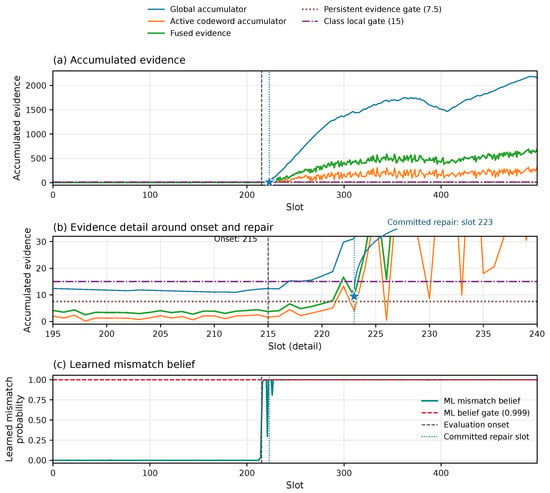
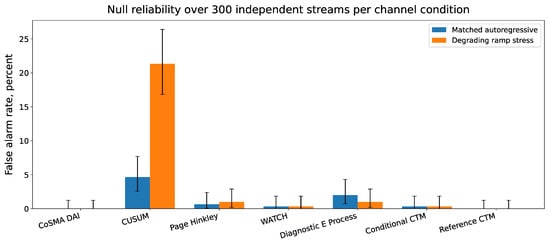
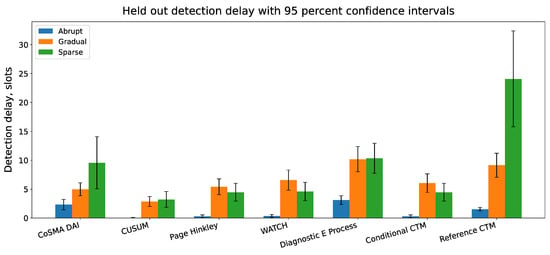
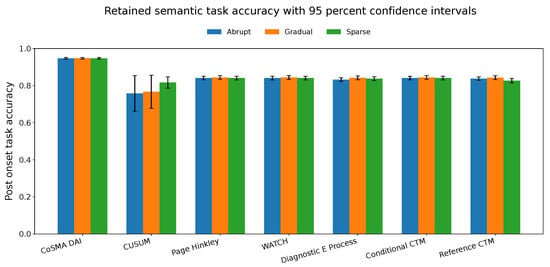
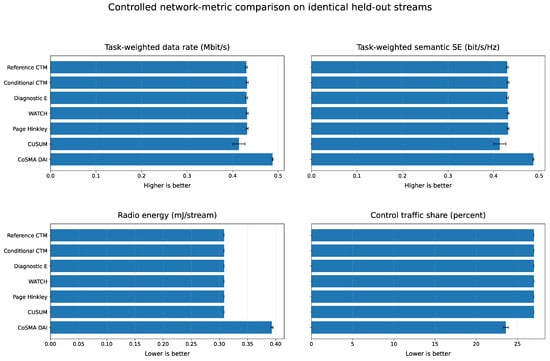
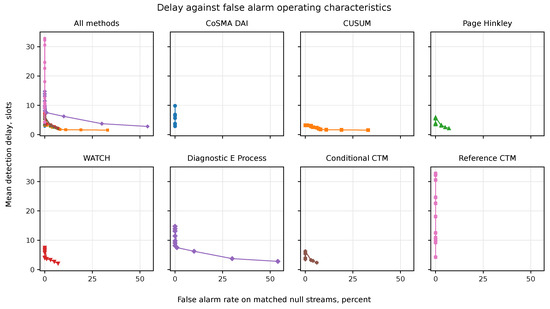
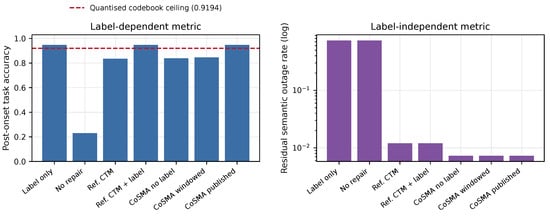
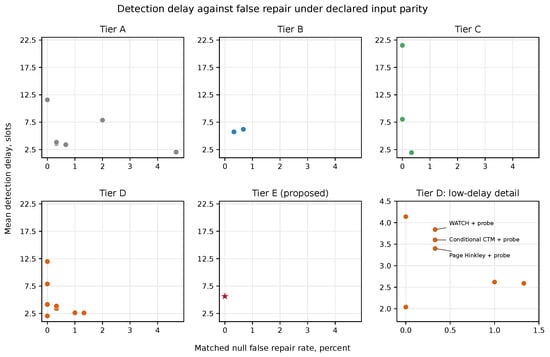
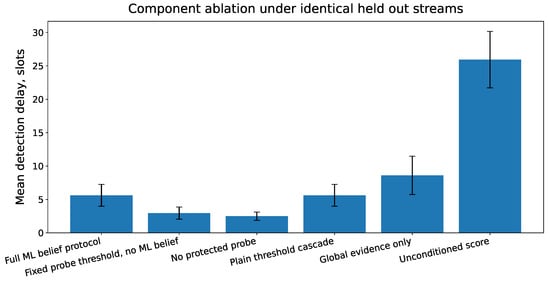
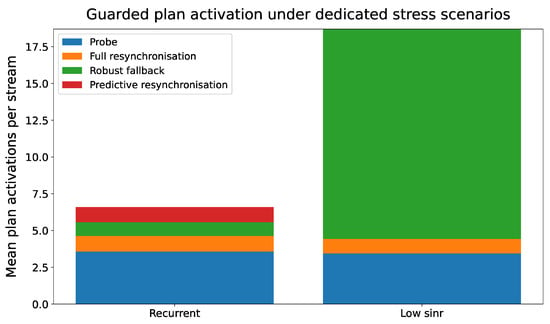
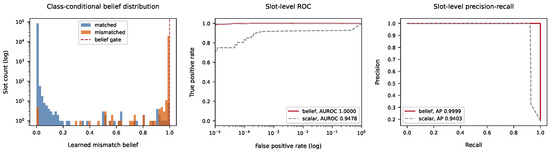
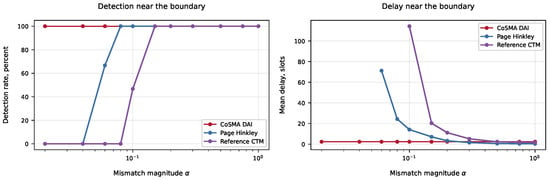
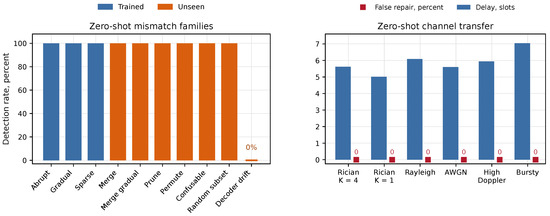
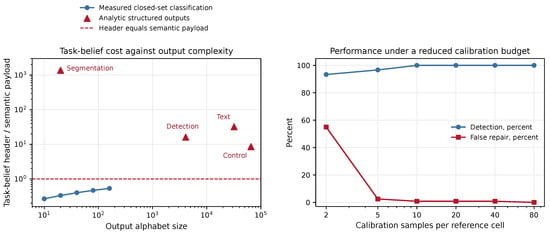
Correct packet delivery does not guarantee correct semantic interpretation when endpoint meanings for the same learned codeword diverge. CoSMA DAI is proposed for mismatch detection, protected confirmation, task preservation and semantic repair. Channel-conditioned global evidence, semantic class local evidence, temporal dynamics, channel context and protected probe evidence are fused by a causal machine-learned mismatch belief. A transmitter-derived task belief preserves the downstream decision while repair is pending and BDIx agents select guarded intentions for probing, fallback and resynchronisation. Evaluation uses 30 held-out drift seeds, 300 matched null streams and 300 degrading channel controls. Six referenced sequential monitors receive the same conditioned payload score. CoSMA DAI obtains 100.00 percent balanced accuracy, precision, recall, F1 score and Matthews correlation coefficient with zero observed matched null false alarms. Its aggregate delay is 5.62 slots, compared with 11.58 slots for the other zero false alarm method. The task-preservation belief maintains 94.73 percent task accuracy through every divergence scenario, above the quantised accuracy ceiling of 0.919 of the semantic path, because it is derived from the unquantised transmitter latent. A task-label-only control confirms that this accuracy is secured by the preservation belief alone, independently of the detector, so task preservation and mismatch detection are decoupled by design and detectors are compared on residual functional semantic outage, outage duration and semantic reconstruction fidelity, which measure the restoration of the semantic representation itself. Without repair, the residual semantic outage is 73.69 percent at 15.97 dB reconstruction fidelity, whereas CoSMA DAI reduces it to 0.73 percent over 6.62 slots at 21.74 dB. Under five declared parity tiers, in which multivariate and supervised baselines receive the identical features, training seeds, protected probe and candidate budget, the protected confirmation stage reduces false repair for every detector to which it is attached. Zero-shot evaluation over 7 unseen mismatch families and 5 unseen link models retains full detection with zero observed false repair in 6 of the 7 families and on every link and identifies receiver-side decoder drift as a condition the present observation model cannot detect. The learned belief is validated at slot level with an area under the receiver operating characteristic curve of 0.99997 and a class overlap of 0.00039, leave-one-mechanism-out and cross-channel retraining are reported, behaviour is characterised down to the practical detection boundary and scaling to 64-dimensional representations with 2048-entry codebooks is demonstrated. The task-belief mechanism is shown to be economical only for small closed-set output spaces and the channel-conditioning tables are shown to reduce to 6 cells without loss. Every comparator is additionally retuned on the same development budget, paired bootstrap intervals and signed-rank tests are reported over the shared streams, auxiliary traffic and radio energy are normalised per correct decision, authentication of the task belief is specified and charged and transfer to MNIST, Fashion-MNIST, CIFAR-10 and CIFAR-100 is demonstrated without retraining, including on a convolutional VQ-VAE representation with a jointly learned 512-entry codebook, where foreground segmentation and localisation are restored to within the quantisation limit while a class decision cannot serve either task. The control traffic share is 23.59 percent, which is 12.62 percent lower than the monitor value. The additional semantic side information increases radio energy to 0.393 mJ per stream and reduces control-adjusted resource efficiency to 6.203 source-equivalent bits per channel use. The results therefore establish reliable detection and semantic repair within the principal comparison, with comparator-specific delay advantages and without claiming task-accuracy, semantic-rate or energy superiority.
Full article
(This article belongs to the Topic Challenges and Future Trends of Wireless Networks)
►▼
Show Figures

Graphical abstract
Open AccessArticle
Benchmarking Frequency Hopping Algorithms for Resilient Wireless Communications Under Multiple Jamming Environments
by
Ivan Laktionov
Network 2026, 6(3), 79; https://doi.org/10.3390/network6030079 - 16 Sep 2026
Abstract
►▼
Show Figures
Frequency-hopping spread spectrum (FHSS) information and communication systems are widely used to enhance the resilience of wireless networks to interference. The effectiveness of traditional algorithms is significantly reduced in the presence of active and intelligent jammers. The aim of this manuscript is to
[...] Read more.
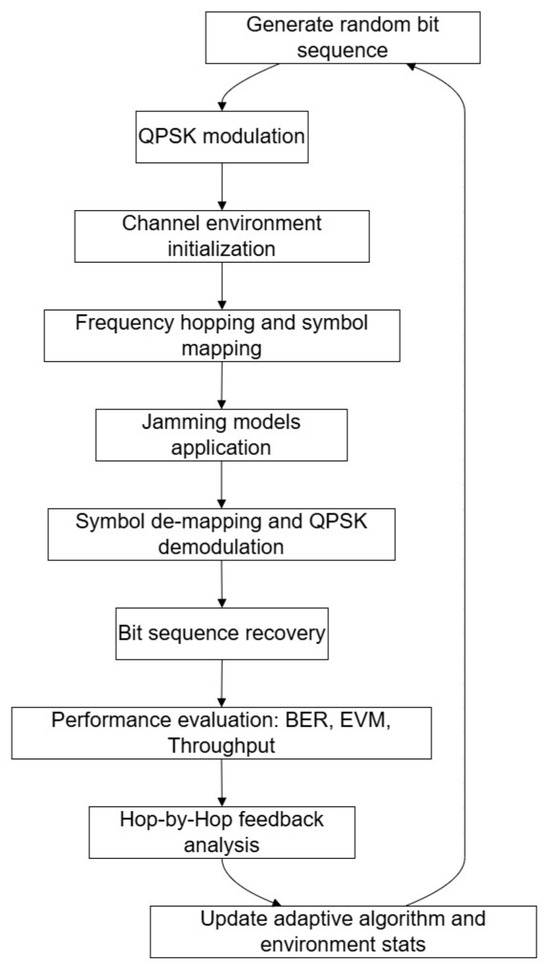
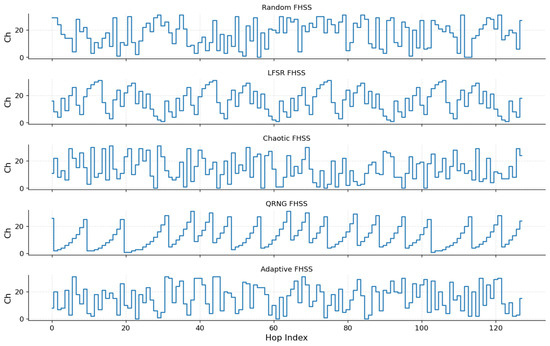
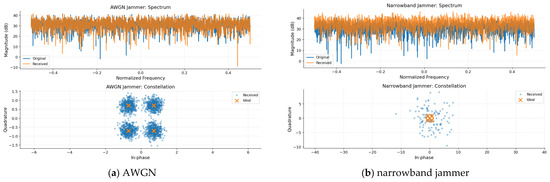
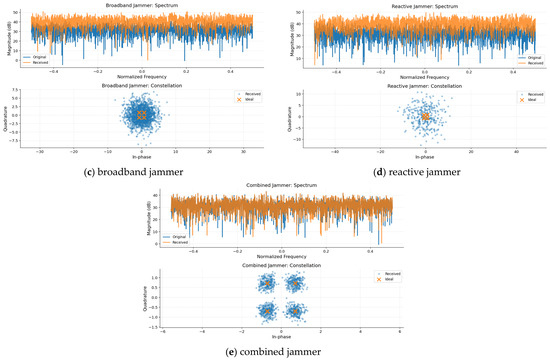
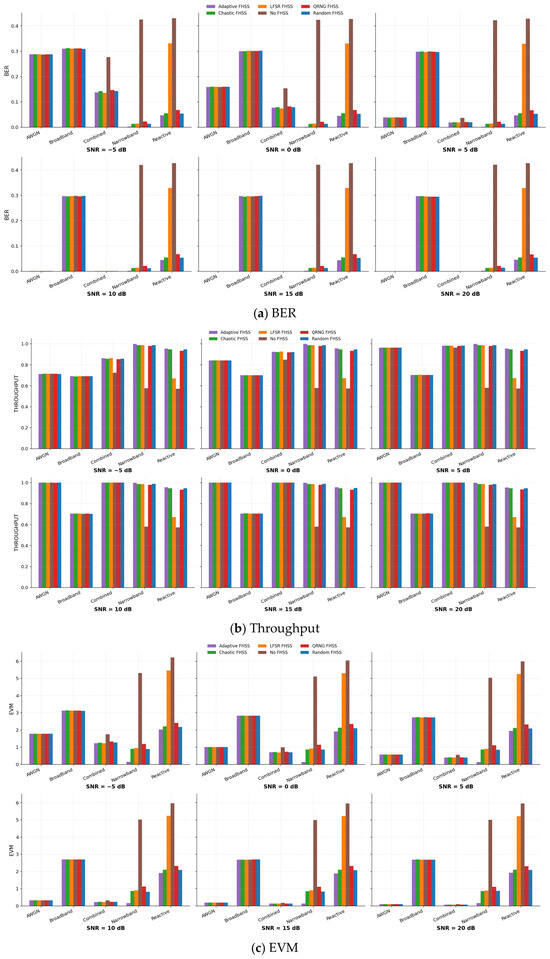
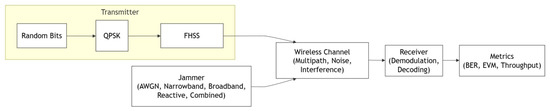
Frequency-hopping spread spectrum (FHSS) information and communication systems are widely used to enhance the resilience of wireless networks to interference. The effectiveness of traditional algorithms is significantly reduced in the presence of active and intelligent jammers. The aim of this manuscript is to develop an adaptive FHSS algorithm based on statistical learning of frequency-channel quality and to analyze its effectiveness compared with existing algorithms. A software simulator has been developed that implements six FHSS algorithms, four intentional jamming models, and one baseline noise condition, and provides statistical evaluation based on sequential packet-level simulation, including bit error rate, error vector magnitude, normalized throughput, computational complexity, and resource assessment. The software-implemented adaptive algorithm delivered the best results among all those studied, achieving the highest overall performance metric. Compared with a system without FHSS, a 64.43% reduction in the bit error rate, 22.80% increase in throughput and 60.71% reduction in the error vector magnitude were achieved. The results obtained confirm the feasibility of using adaptive statistical frequency channel selection to improve the interference resilience of FHSS systems. Promising areas for further research include the modeling of intelligent jammers and the experimental verification of the implemented algorithm on computing platforms with limited resources.
Full article

Figure 1
Open AccessArticle
Measurement-Driven Modeling of End-to-End Latency in an Indoor Private Standalone 5G Network
by
Osman Bodur, Sami Çağlayan, Neslihan Demir, Günther Poszvek and Friedrich Bleicher
Network 2026, 6(3), 78; https://doi.org/10.3390/network6030078 - 15 Sep 2026
Abstract
►▼
Show Figures
This paper presents a measurement-driven study of end-to-end latency in an indoor private standalone 5G network deployed at TU Wien IFT TEC-Lab. The testbed combines pico radio units, edge computing resources, and a local 5G core to form a campus-scale private network architecture
[...] Read more.
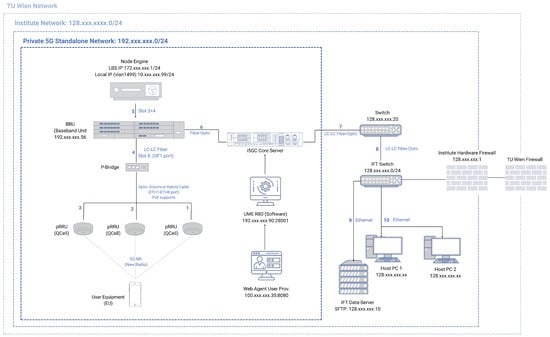
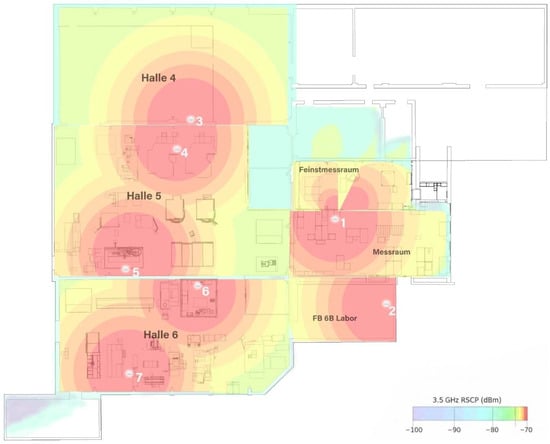
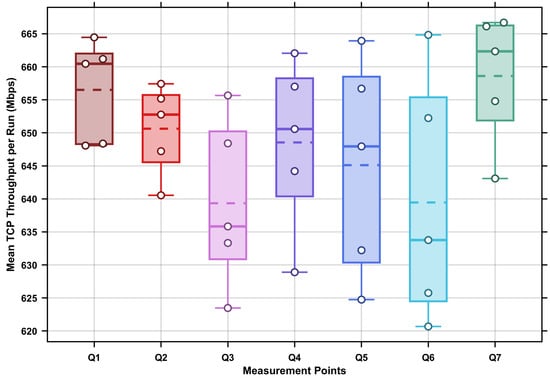
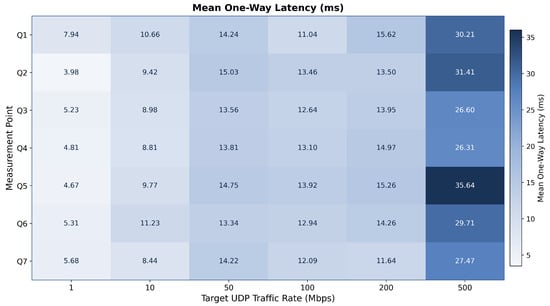
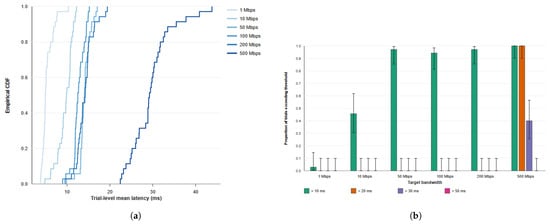
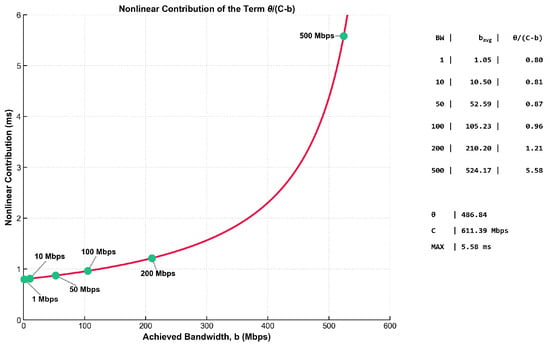
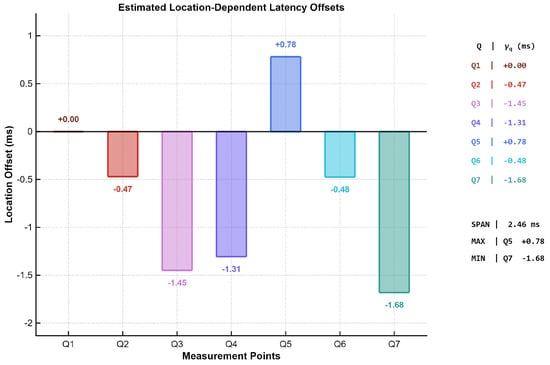
This paper presents a measurement-driven study of end-to-end latency in an indoor private standalone 5G network deployed at TU Wien IFT TEC-Lab. The testbed combines pico radio units, edge computing resources, and a local 5G core to form a campus-scale private network architecture designed for low-latency communication. To characterize network performance, TCP throughput and UDP one-way latency measurements were collected in a single-user, constant-bit-rate downlink setting at seven predefined indoor locations using iPerf-based tests at six traffic levels (1–500 Mbps), with five repetitions per condition. Based on these measurements, a compact parametric model was calibrated for this deployment to describe latency as a function of achieved bandwidth and location-dependent effects. The results show that latency remained low and relatively stable at low and medium traffic levels, generally staying below 20 ms between 1 and 200 Mbps, but increased more strongly as the operating point approached the practical throughput limit of the setup. The fitted model captured the overall latency trend with an in-sample MAE of 2.52 ms, an RMSE of 3.13 ms, and an of 0.842, while retaining comparable predictive performance under a trial-based test split ( ) and leave-one-location-out validation ( ). The compact model also achieved lower out-of-sample errors than the minimal M/M/1-type and polynomial-regression baselines under both validation schemes. Overall, the findings indicate that traffic load was the main driver of latency growth in the studied environment, while spatial effects remained measurable but secondary. The resulting formulation should be understood as an interpretable empirical model of end-to-end latency for one indoor private standalone 5G deployment under single-user, constant-bit-rate downlink conditions, rather than as a general latency model for private 5G networks. Within that scope, the model provides an interpretable description of the measured latency behavior and a basis for preliminary capacity assessment in this deployment. Its applicability to another private 5G network has not been established and would require a new measurement campaign, complete parameter re-estimation, and independent validation.
Full article

Figure 1
Open AccessArticle
Multi-Layer Network Optimization of Data Centers Siting and Capacity Development
by
Amirhosein Gholami, Kshitija Chinchkar and Nasim Nezamoddini
Network 2026, 6(3), 77; https://doi.org/10.3390/network6030077 - 14 Sep 2026
Abstract
►▼
Show Figures
The rapid growth of artificial intelligence applications and digital ecosystems, especially in industry, has highlighted the need for proposing new data centers. Data center siting requires consideration of many different factors including power grid capacity, fiber network resources, and environmental and regional considerations.
[...] Read more.
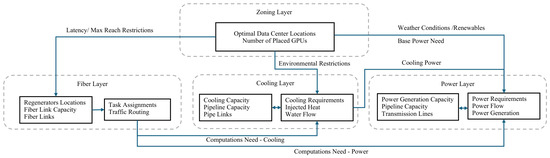
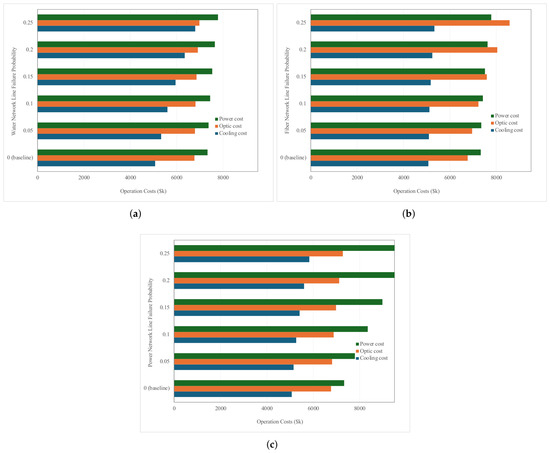
The rapid growth of artificial intelligence applications and digital ecosystems, especially in industry, has highlighted the need for proposing new data centers. Data center siting requires consideration of many different factors including power grid capacity, fiber network resources, and environmental and regional considerations. This research proposes a multi-layer network optimization in which the master plan optimizes data center siting and their capacity decisions while the other lower-level layers analyze the feasibility and optimality of these decisions in terms of grid congestion and transmission network expansion, fiber routing and latency, and cooling resources. The efficiency of the proposed plan and its reliability will be evaluated by simulating different scenarios including unexpected power grid outages because of natural disasters. The results of the model highlight the importance of integrated decision making for siting data centers while considering zoning restrictions and required capacities and operation costs of water, fiber/optic, and power networks.
Full article

Figure 1
Open AccessSystematic Review
Machine Learning Applications for IoT Intrusion Detection: Network Dependencies, Dataset Limitations, and Regulatory Compliance—A Systematic Review
by
Majed Alzahrani, Priyadarsi Nanda, Manoranjan Mohanty and Farag El Zegil
Network 2026, 6(3), 76; https://doi.org/10.3390/network6030076 - 10 Sep 2026
Abstract
Background: Internet of Things (IoT) deployments face complex network dependencies and persistent data limitations that constrain machine learning (ML) intrusion detection systems (IDS). Objective: To synthesise peer-reviewed machine learning IDS research for IoT, focusing on dependency-driven failure propagation and chronic data scarcity, positioned
[...] Read more.
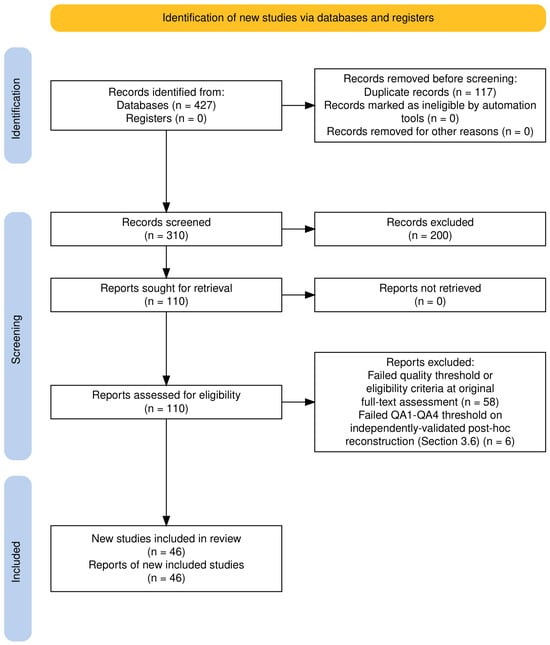
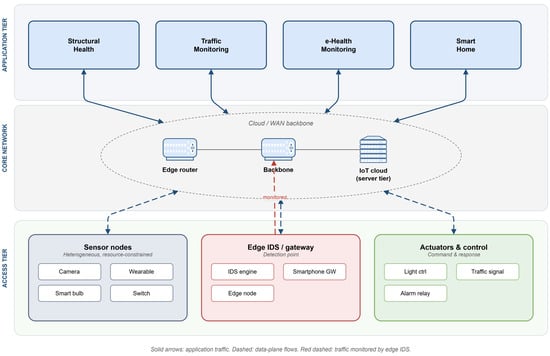
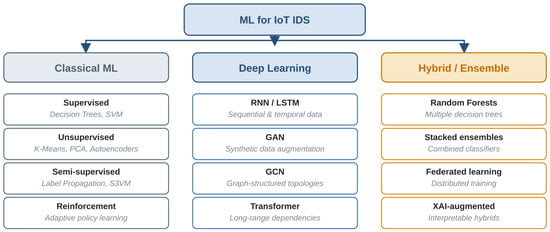
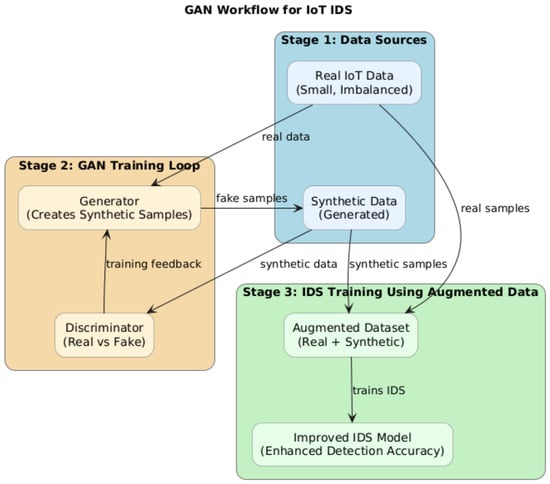
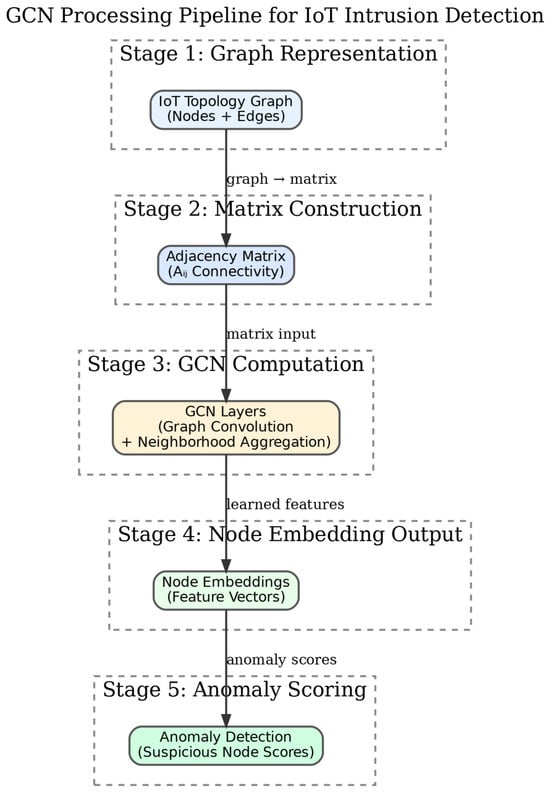
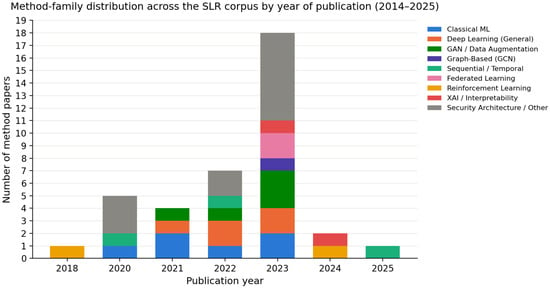
Background: Internet of Things (IoT) deployments face complex network dependencies and persistent data limitations that constrain machine learning (ML) intrusion detection systems (IDS). Objective: To synthesise peer-reviewed machine learning IDS research for IoT, focusing on dependency-driven failure propagation and chronic data scarcity, positioned against 2024–2025 EU regulatory requirements (NIS2, the Cyber Resilience Act). Eligibility criteria: Peer-reviewed empirical studies proposing or evaluating a machine learning or deep learning IoT intrusion detection method published in English from January 2018 (limited pre-2018 exceptions for seminal works). Information sources: IEEE Xplore, SpringerLink, Elsevier ScienceDirect, Scopus, Web of Science, and Google Scholar, searched on 12 February 2025. Risk of bias: Each candidate was scored against four criteria (objectives clarity, methodological soundness, reproducibility, IoT-security relevance); studies scoring at least 3 out of 4 were retained. Screening and scoring were performed by one reviewer, with a second reviewer independently checking 20 percent of records. Synthesis methods: Narrative thematic synthesis; heterogeneous metrics and incompatible datasets across studies precluded quantitative meta-analysis. Included studies: Of 427 records identified, 52 studies initially met inclusion criteria; a post hoc independently validated reconstruction of individual QA1–QA4 scores subsequently found that six did not meet the threshold or topical eligibility criteria, yielding a final 46-study corpus. Main findings: Generative adversarial networks (GANs) dominate dataset augmentation work, graph-based communication analysis addresses dependency modelling, and methods based on transformers or federated learning emerge from 2023 onward. Certainty of evidence: No formal grading (GRADE) applies to this narrative synthesis. Confidence in the corpus composition is high, following independent QA1–QA4 validation, while confidence in the thematic findings is moderate given single-reviewer screening and judgment-based classification. Conclusions: We identify three recurring gaps: real-time detection under resource constraints, dependency-aware detection, and regulatory compliance. Closing these gaps requires detection methods that treat IoT security as a networked and regulated system rather than an isolated device classification problem. Registration: Open Science Framework, 10.17605/OSF.IO/NMAK4 (registered retrospectively). No external funding supported this review.
Full article
(This article belongs to the Special Issue Latest Advancements in Machine Learning Applications for Cybersecurity)
►▼
Show Figures

Figure 1
Open AccessReview
Secure Programming and Secure Design in DevSecOps: A Literature-Based Conceptual Synthesis
by
Faisal A. Al-Qadda, Abdulaziz Y. Alhumaidi and Nazar Abbas Saqib
Network 2026, 6(3), 75; https://doi.org/10.3390/network6030075 - 9 Sep 2026
Abstract
►▼
Show Figures
Secure programming and secure design are often managed as separate activities, leaving a gap between architectural intent and the implementation that reaches production. This paper presents a structured conceptual synthesis of twenty core publications, supplemented by standards and recent work on AI-assisted development.
[...] Read more.
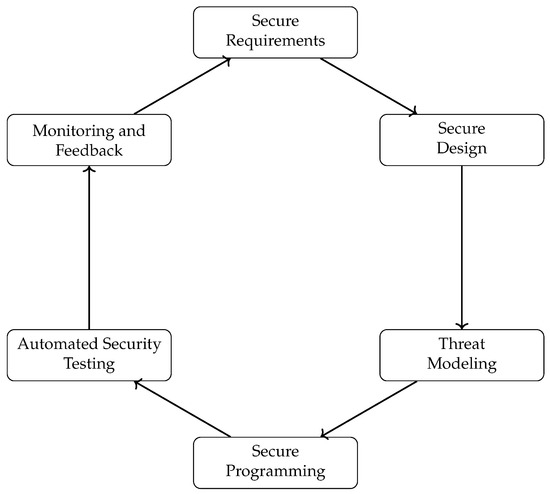
Secure programming and secure design are often managed as separate activities, leaving a gap between architectural intent and the implementation that reaches production. This paper presents a structured conceptual synthesis of twenty core publications, supplemented by standards and recent work on AI-assisted development. It makes three contributions. First, it frames secure programming as the implementation-facing realization of secure design within a closed feedback loop. Second, it uses an explicit 0–5 rubric to produce an illustrative comparison of Waterfall, Iterative, Spiral, and Agile with DevSecOps across six security-integration dimensions. These profiles are structured author judgments, not empirical measurements of security effectiveness. Third, it proposes an operational Secure SDLC–DevSecOps framework that links six stages through named artifacts, accountable roles, traceability rules, release gates, exceptions, and outcome measures. A comparison with NIST SSDF, OWASP SAMM, Microsoft SDL, ISO/IEC 27034, and OWASP implementation guidance shows that the individual practices are established; the framework’s intended contribution is the project-level control loop that connects design decisions to pipeline evidence and production feedback. The illustrative profiles place Spiral and Agile with DevSecOps close together under the baseline weights, while sensitivity scenarios show that their ordering depends on whether design-time risk analysis or delivery-time verification is emphasized. The synthesis therefore supports contextual tailoring rather than a universal ranking.
Full article

Figure 1
Open AccessArticle
Sentinel: Proactive Elastic Controller Scaling with MARL-Guided Load Redistribution for Resilient SD-WANs
by
Abdulrahman M. Abdulghani, Azizol Abdullah, Amir Rizaan Abdul Rahiman, Nor Asilah Wati Abdul Hamid and Bilal Omar Akram
Network 2026, 6(3), 74; https://doi.org/10.3390/network6030074 - 9 Sep 2026
Abstract
Controller placement in software-defined wide area networks (SD-WANs) is commonly optimized assuming continuously available controllers, leaving the control plane vulnerable to overload and abrupt reassignment after controller unavailability. This paper presents Sentinel, an auditable supervisory mechanism that extends GMM-MARL placement into proactive elastic
[...] Read more.
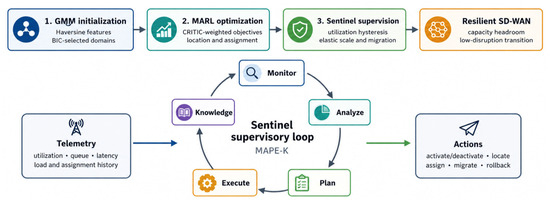
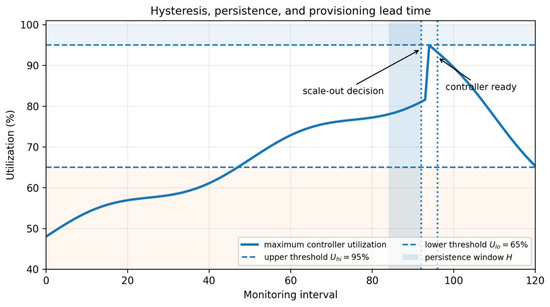
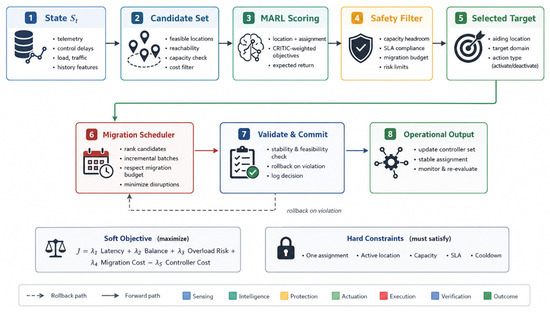
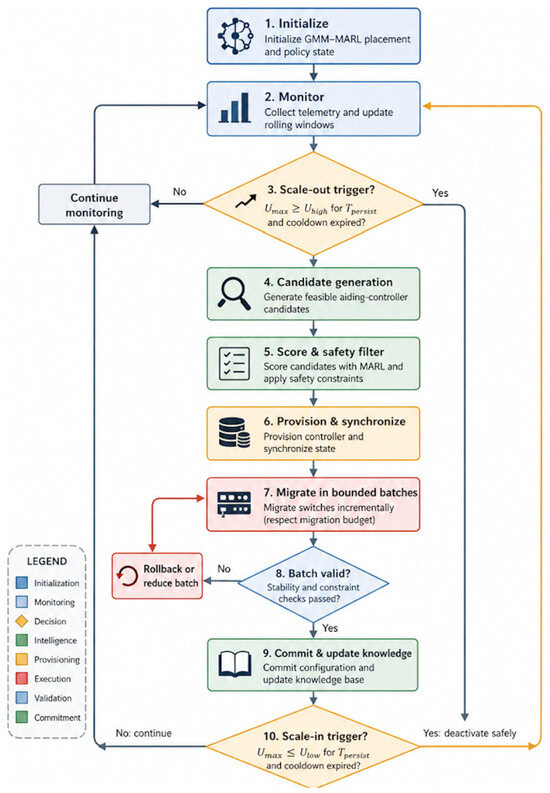
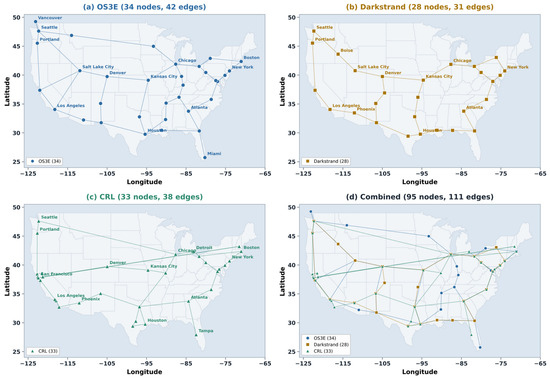
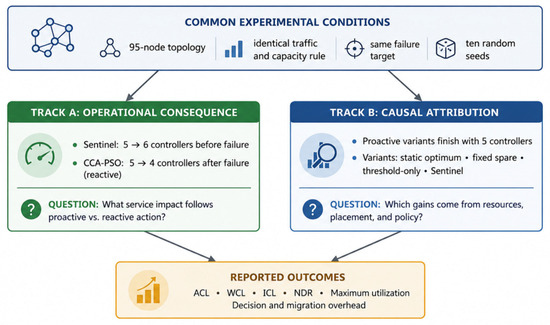
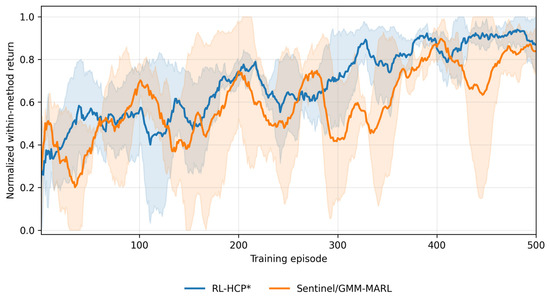
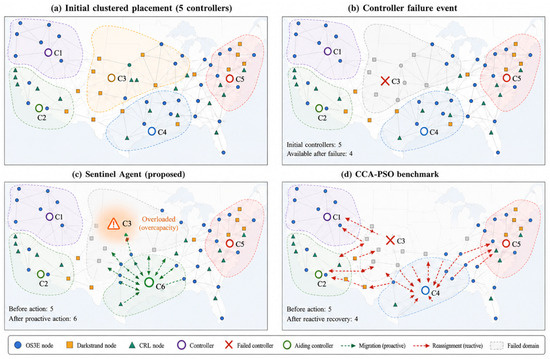
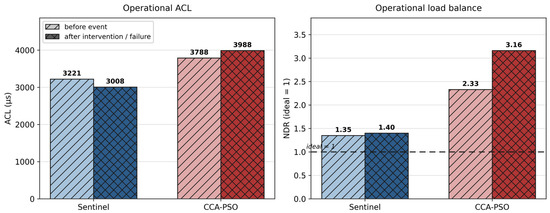
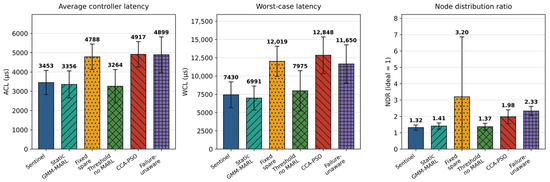
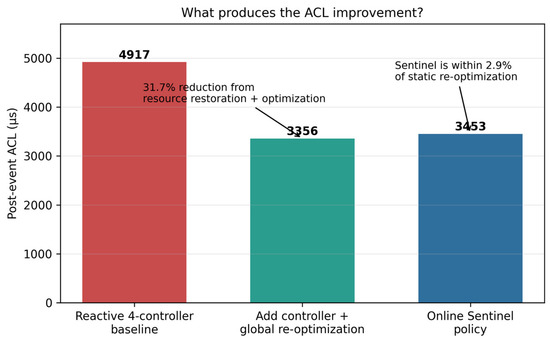
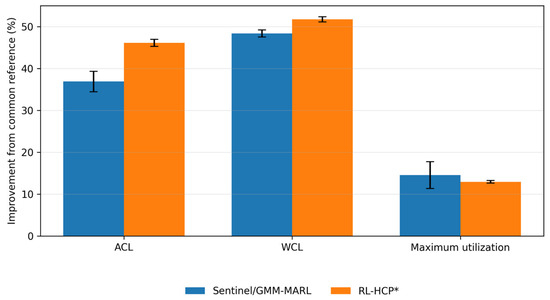
Controller placement in software-defined wide area networks (SD-WANs) is commonly optimized assuming continuously available controllers, leaving the control plane vulnerable to overload and abrupt reassignment after controller unavailability. This paper presents Sentinel, an auditable supervisory mechanism that extends GMM-MARL placement into proactive elastic controller management through utilization monitoring, hysteresis-based scaling, learned aiding-controller placement, and bounded incremental migration. Deterministic supervision decides when scaling is authorized, whereas the learned policy selects placement and assignment subject to capacity and latency constraints. Evaluation uses a 95-node composite topology derived from OS3E, Darkstrand, and CRL. An operational track compares proactive Sentinel scale-out with reactive CCA-PSO, and an equal-resource ablation separates resource restoration from placement quality. Sentinel reduces operational average case latency (ACL) from 3988 to 3008 µs and limits maximum utilization to 87.5%, versus 98.4% under CCA-PSO. Under equal resources, Sentinel achieves 3453 ± 627 µs ACL, within 2.9% of static GMM-MARL re-optimization. An auxiliary matched RL application benchmark on OS3E against a reconstruction (RL-HCP*) shows lower ACL and worst-case latency for RL-HCP*, while Sentinel retains competitive load and coordination behavior. Overall, proactive controller headroom restoration, learned placement, and bounded migration provide resilient control-plane management without disruptive global reassignment.
Full article
(This article belongs to the Collection Advanced Technologies in Network and Service Management, 2nd Edition)
►▼
Show Figures

Figure 1
Open AccessArticle
Hybrid Watermarking and Adaptive Misinformation for Protection Against AI Model Extraction in Edge-Deployed Cyber-Physical Security
by
Fatimah Azzahrah binti Razali, Mohamed Hadi Habaebi and Mohammed Abdullah Salem Al-Hussaini
Network 2026, 6(3), 73; https://doi.org/10.3390/network6030073 - 8 Sep 2026
Abstract
►▼
Show Figures
Artificial intelligence (AI) models are increasingly deployed in edge-deployed cyber-physical security systems for tasks encompassing monitoring, threat classification, and automated decision-making. While these models offer robust performance, their deployment through open or semi-open Machine Learning as a Service (MLaaS) interfaces exposes them to
[...] Read more.
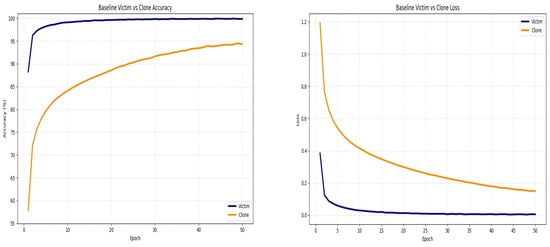
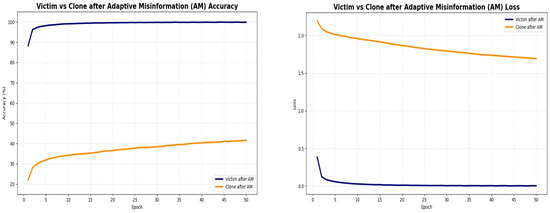
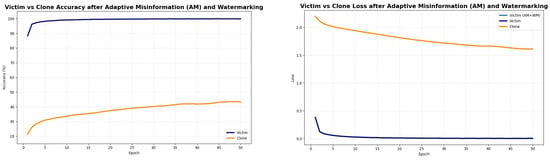
Artificial intelligence (AI) models are increasingly deployed in edge-deployed cyber-physical security systems for tasks encompassing monitoring, threat classification, and automated decision-making. While these models offer robust performance, their deployment through open or semi-open Machine Learning as a Service (MLaaS) interfaces exposes them to severe security threats, prominently model extraction attacks. In such attacks, an adversary systematically queries a target API to replicate the victim model’s behavior. This study proposes a novel hybrid defense framework combining Adaptive Misinformation (AM) and Trigger-Based Watermarking (WM) to protect AI models against black-box extraction. Utilizing a LeNet architecture, the victim model was trained on the MNIST dataset, while a simulated attack utilized 50,000 EMNIST samples to train a clone model. The framework employs Maximum Softmax Probability (MSP) for out-of-distribution (OOD) detection to identify suspicious queries and strategically inject misleading responses, alongside a fine-tuned embedded watermark for ownership verification. Experimental evaluations using 10-fold cross-validation reveal that the baseline extraction attack yielded a clone model accuracy of 96.32%. Upon implementing the AM + WM framework, clone model accuracy degraded significantly to 53.67%, while the victim model maintained an accuracy of 98.97%. Furthermore, the protected model achieved a 100% Trigger Match Rate (TMR), ensuring reliable intellectual property verification. The proposed framework provides a prototype validation for lightweight edge architectures to balance security, model utility, and ownership protection in cyber-physical deployments.
Full article

Figure 1
Open AccessArticle
A Risk-Gated Security Attention Mechanism for Rare-Threat Detection in Industrial IoT Networks
by
Shaimaa Ahmed Elsaid, Ahmed M. Saad and Eslam Mahmoud Fouda
Network 2026, 6(3), 72; https://doi.org/10.3390/network6030072 - 8 Sep 2026
Abstract
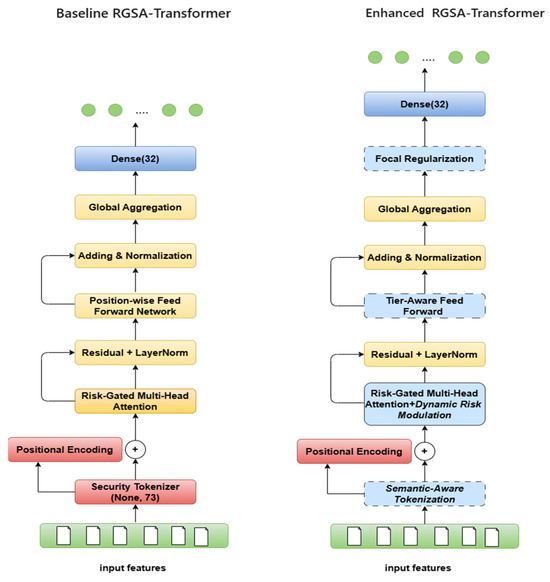
In current state-of-the-art intrusion detection systems (IDSs), models are trained to detect the repetitive behavior of data traffic. This leads to the problem of ignoring rare yet important attacks. To solve the problem stated above, a risk-gated security attention (RGSA) architecture is proposed.
[...] Read more.
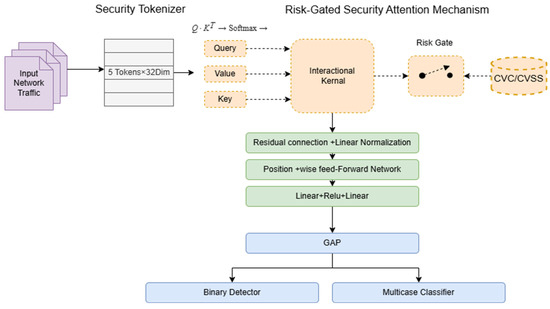
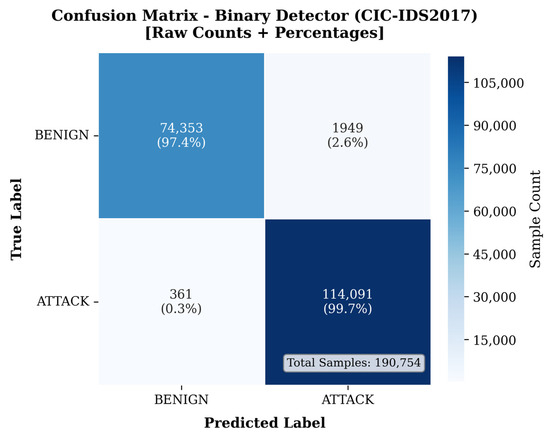
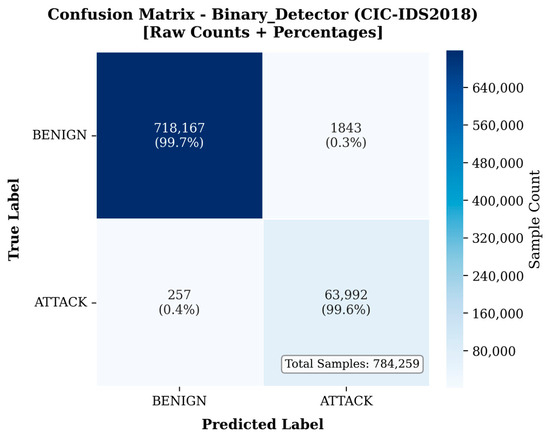
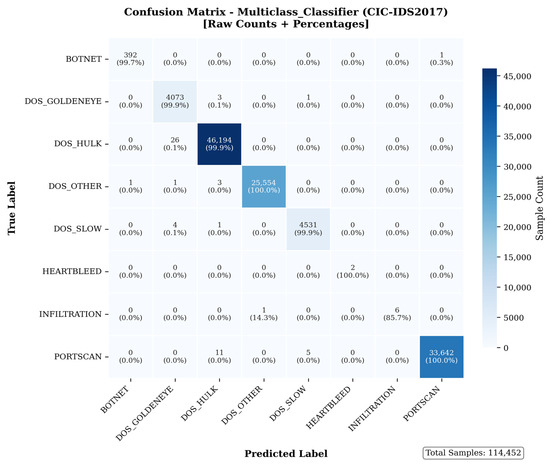
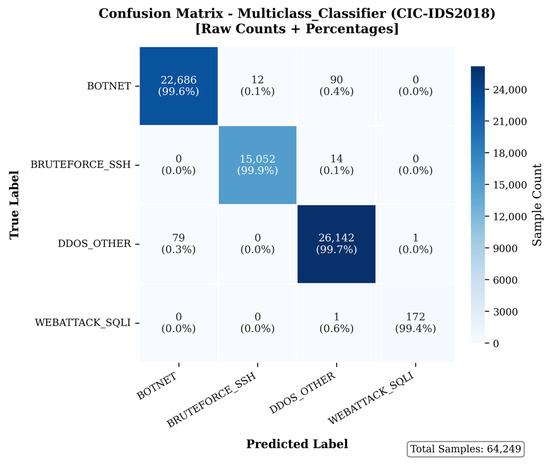
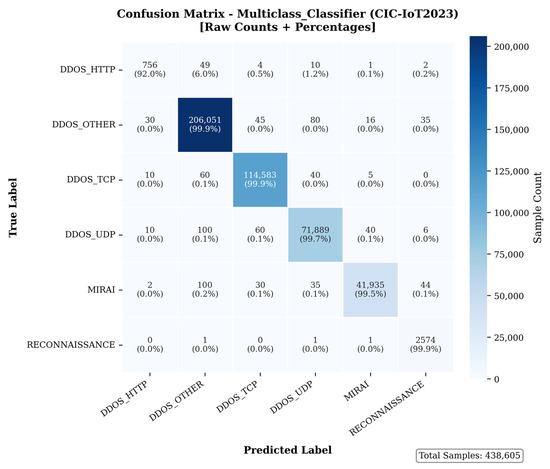
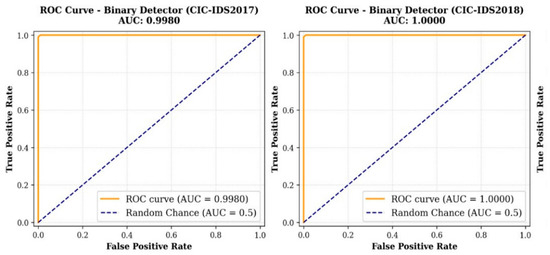
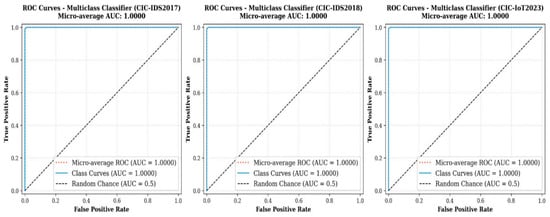
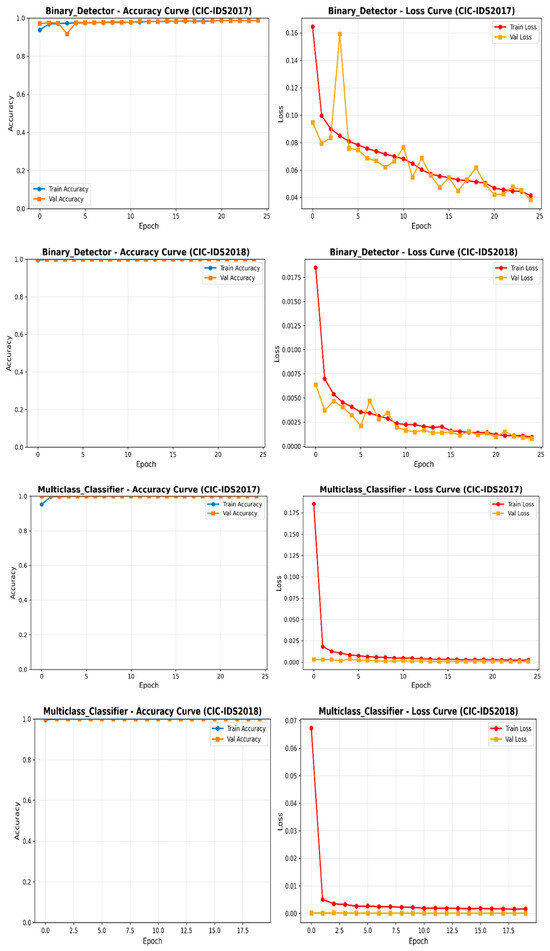
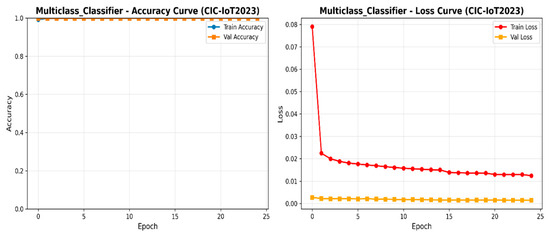
In current state-of-the-art intrusion detection systems (IDSs), models are trained to detect the repetitive behavior of data traffic. This leads to the problem of ignoring rare yet important attacks. To solve the problem stated above, a risk-gated security attention (RGSA) architecture is proposed. The initialization of the risk estimator based on the CVE/CVSS severity score enables the attention network to detect important yet rare patterns. Furthermore, a tier-aware focal loss is proposed to mitigate security threats in the real world without any data augmentation process. Evaluations were conducted on held-out 80/20 test splits of the CIC-IDS2017, CIC-IDS2018, and CIC-IoT2023 datasets. The calibrated binary detection process reached false negative rates (FNRs) of 0.50% and 0.40% on the CIC-IDS2017 and CIC-IDS2018 datasets, respectively, remaining below the 1.0% FNR operational target adopted in this study. For micro-support critical threats, precise discrete analysis had to be applied to maintain statistical validity. Also, weighted F1-scores of at least 99.65% were consistently achieved for all testbeds analyzed. This network contains 284,317 trainable parameters and strictly avoids the creation of any synthetic samples through complete rejection of synthetic oversampling. The findings indicate that adding priors for security tiers to the attention process is favorable for moving towards an impact-based threat management approach.
Full article
(This article belongs to the Special Issue Cybersecurity and Privacy in Internet-of-Things: Advances, Challenges, and Emerging Trends)
►▼
Show Figures

Figure 1
Open AccessArticle
Direct-to-Cell NTN Systems in Terrestrial 5G Bands: Network-Level Sensitivity Analysis and PFD/EPFD Limits for Coexistence
by
Alexander Pastukh, Olga Mironova and Valery Tikhvinskiy
Network 2026, 6(3), 71; https://doi.org/10.3390/network6030071 - 7 Sep 2026
Abstract
Direct-to-cell (D2C) non-terrestrial networks (NTNs) based on 5G technology are emerging as a key complement to terrestrial cellular networks, extending connectivity to underserved and remote areas while enabling integration with existing mobile ecosystems. As these systems begin operating in frequency bands already used
[...] Read more.
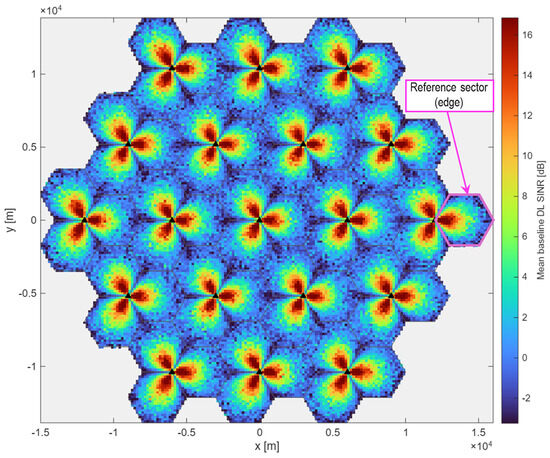
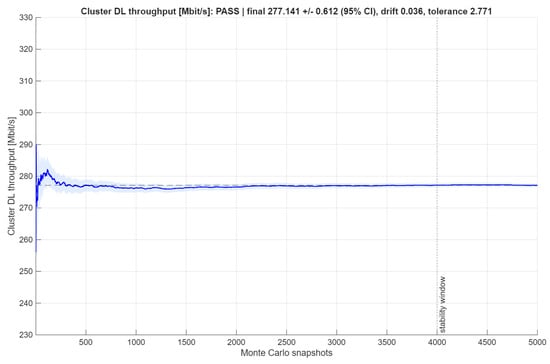
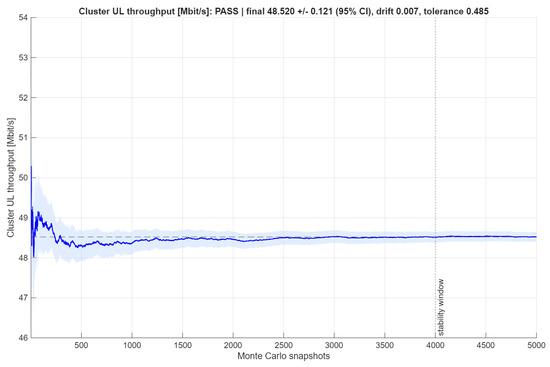
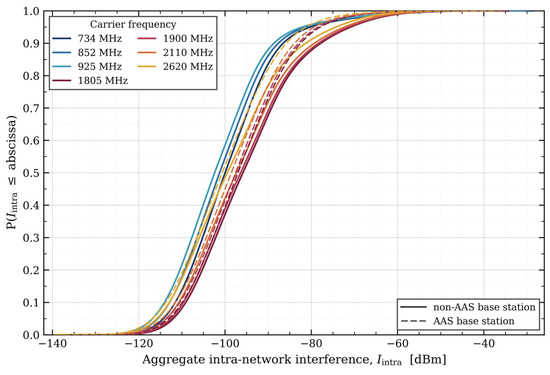
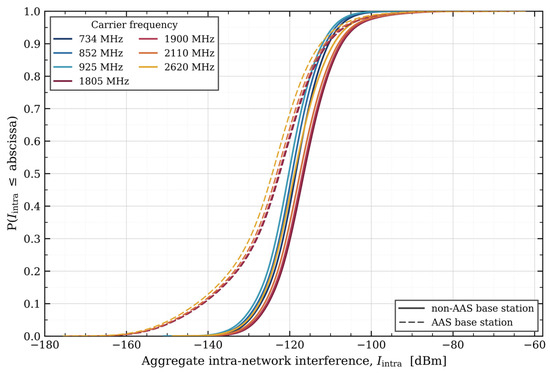
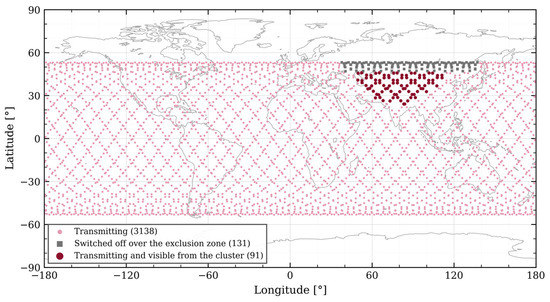
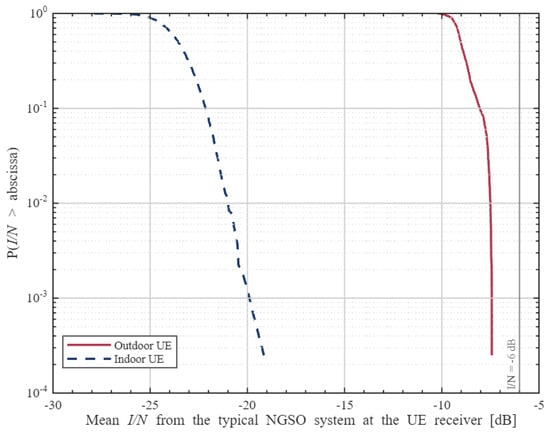
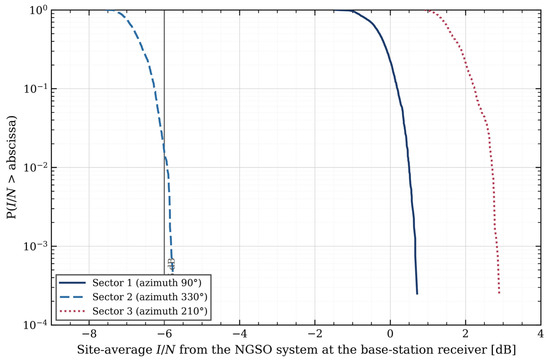
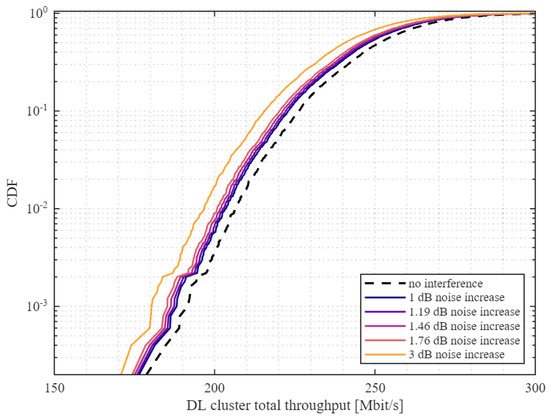
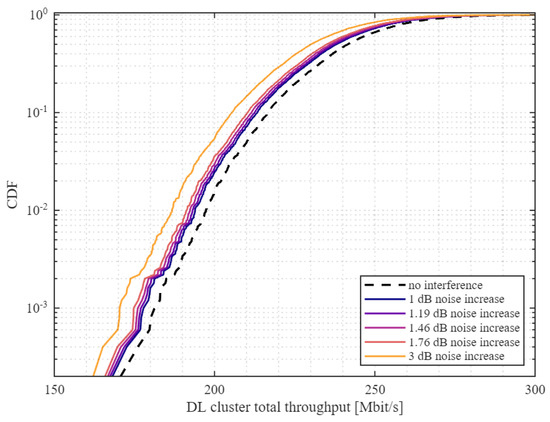
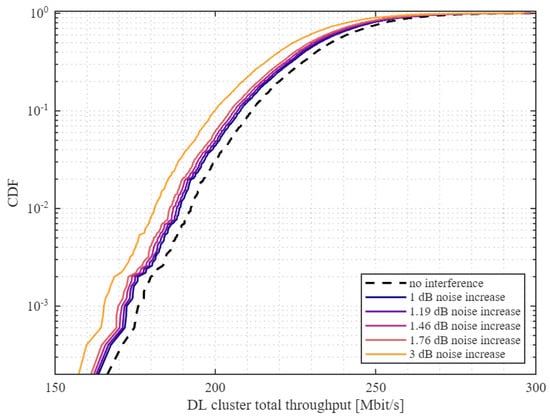
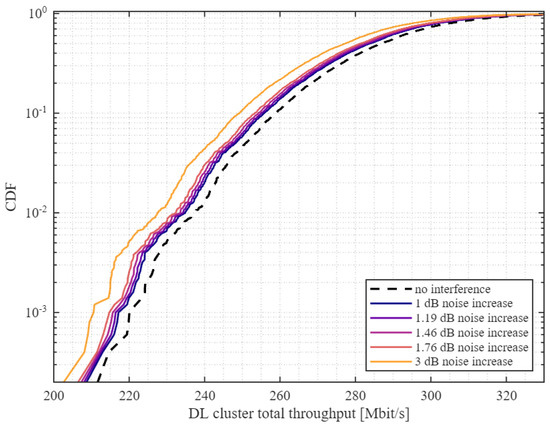
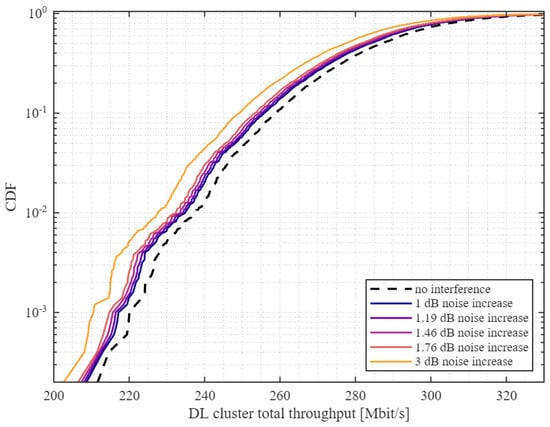
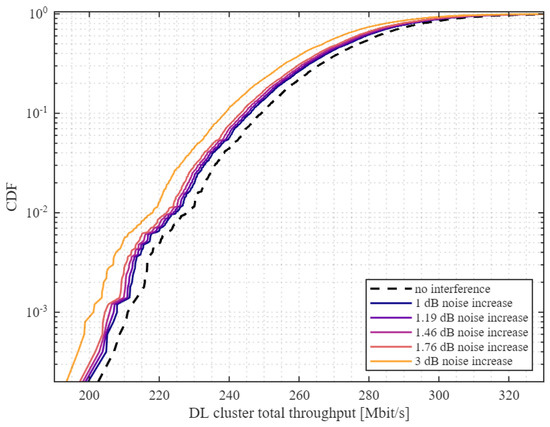
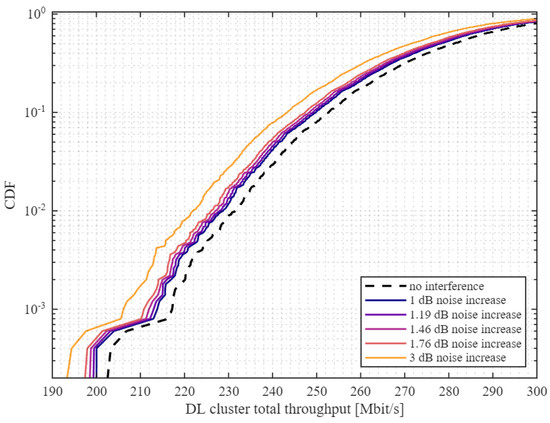
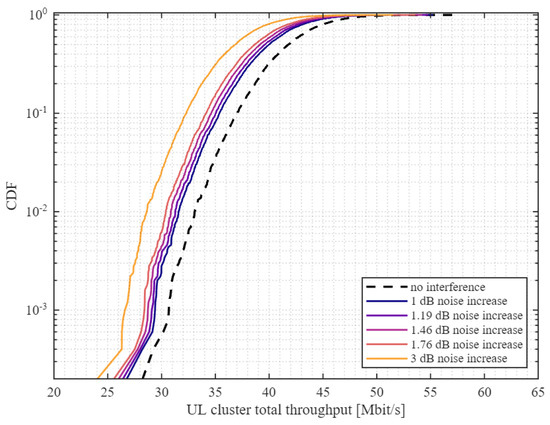
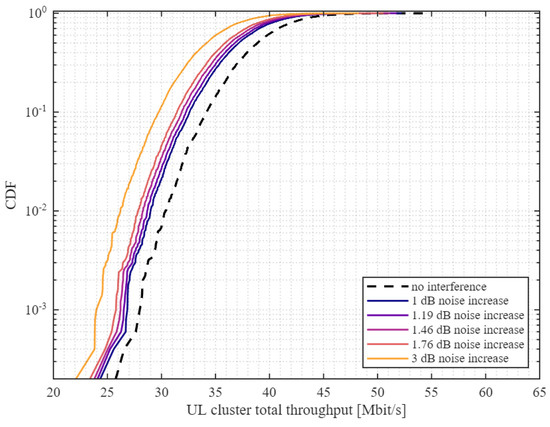
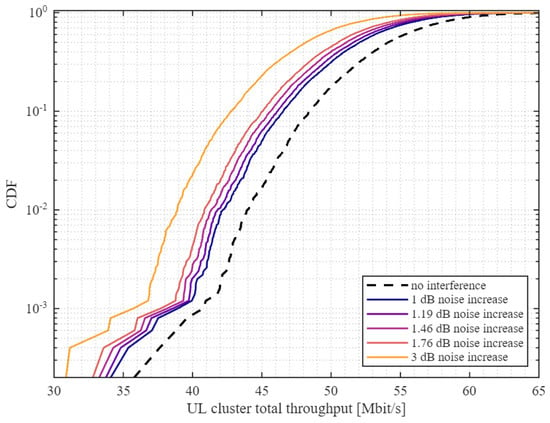
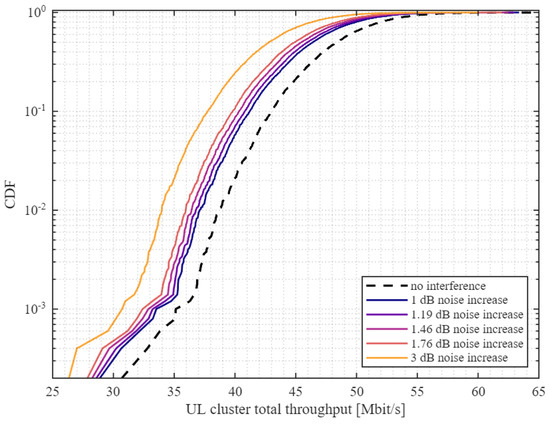
Direct-to-cell (D2C) non-terrestrial networks (NTNs) based on 5G technology are emerging as a key complement to terrestrial cellular networks, extending connectivity to underserved and remote areas while enabling integration with existing mobile ecosystems. As these systems begin operating in frequency bands already used by terrestrial International Mobile Telecommunications (IMT) networks, coexistence becomes critical. This paper presents a victim-centric methodology for evaluating D2C interference into terrestrial 5G networks in the 694/698 MHz-2.7 GHz regulatory study range. Seven downlink carrier cases and four uplink carrier cases between 734 and 2620 MHz are evaluated. For a prescribed external interference-to-noise ratio, the external contribution is referenced to receiver thermal noise, while terrestrial intra-network interference remains part of the baseline and interfered signal-to-interference-plus-noise ratio (SINR). The resulting throughput loss is translated into candidate power-flux-density (PFD) and equivalent-power-flux-density (EPFD) protection levels. A reference non-geostationary-satellite-orbit (NGSO) system is used only to motivate the assumed receiver-exposure fractions; the numerical network results are therefore conditional on those exposure assumptions. The same external interference level produces approximately three times greater network throughput loss at base stations than at user equipment, so direction-specific protection levels are required. For downlink protection, the tested 3 dB noise-rise case gives candidate PFD levels from −109.23 to −98.17 dB(W/(m2·MHz)); for opposite-direction cross-border uplink protection, I/N = −6 dB gives candidate EPFD levels from −138.23 to −130.18 dB(W/(m2·MHz)) for non-AAS base stations. The approximately 11 dB offset for AAS cases results from the maximum-gain normalization used in EPFD and should not be interpreted as evidence of greater satellite exposure. These values are tested candidate levels rather than estimates of an exact 5% crossing point.
Full article
(This article belongs to the Special Issue 5G and Next-Generation Communication Technologies)
►▼
Show Figures

Figure 1
Open AccessSystematic Review
When and How to Use Post-Quantum Cryptography: A Systematic Literature Review
by
Tasneem Annahdi, Albandari Alsumayt and Naya Nagy
Network 2026, 6(3), 70; https://doi.org/10.3390/network6030070 - 31 Aug 2026
Abstract
►▼
Show Figures
Post-quantum cryptography (PQC) is driven by the threat posed by quantum computers, particularly the harvest-now-decrypt-later attack. PQC aims to prepare classical systems and hardware to become resilient against quantum attacks. This research discusses the system vulnerabilities, the need to migrate to PQC, and
[...] Read more.
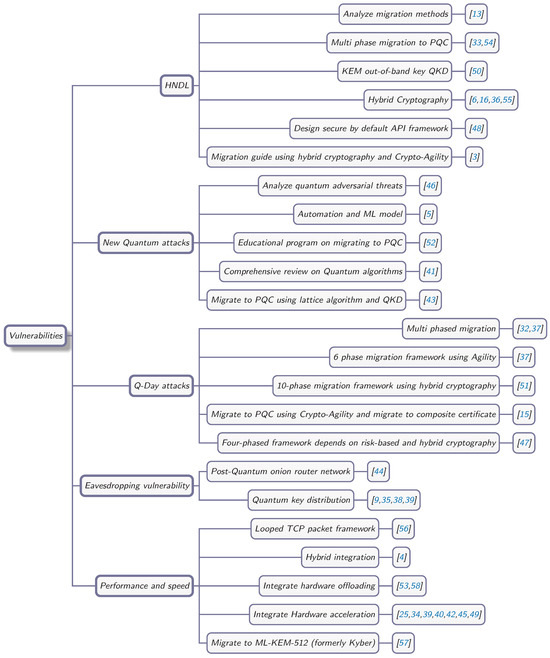
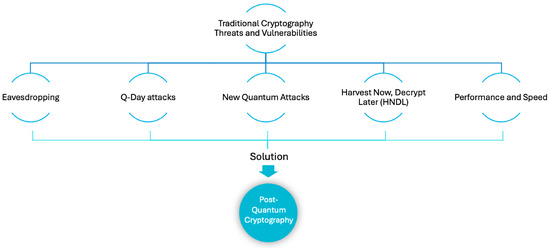
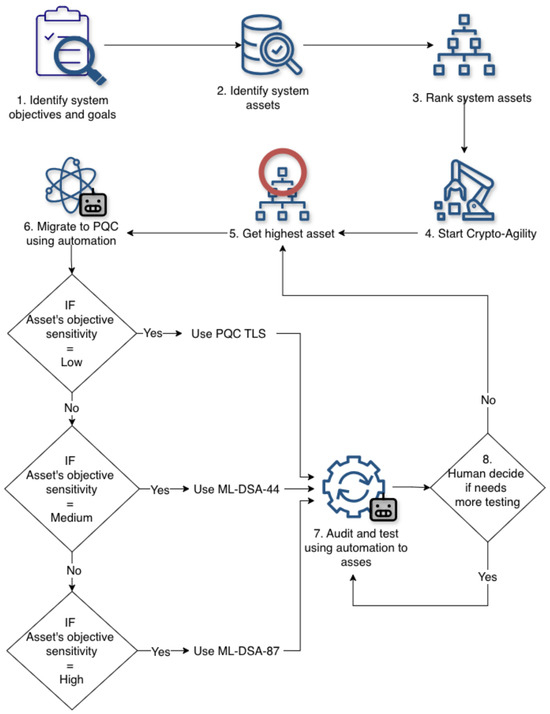
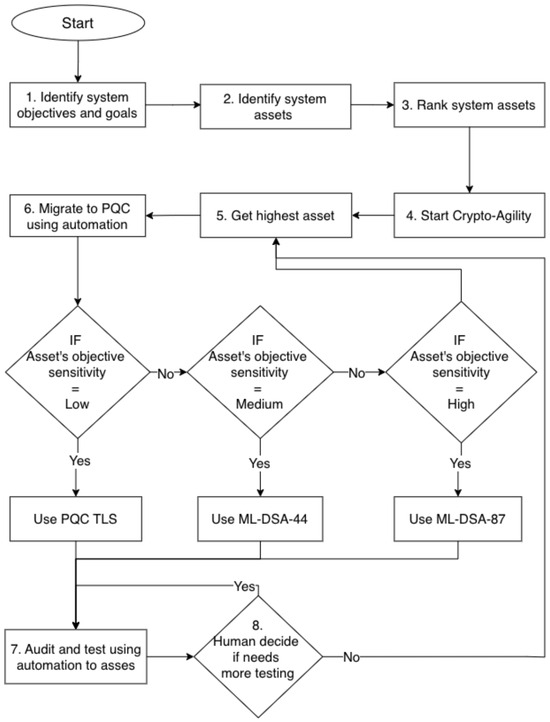
Post-quantum cryptography (PQC) is driven by the threat posed by quantum computers, particularly the harvest-now-decrypt-later attack. PQC aims to prepare classical systems and hardware to become resilient against quantum attacks. This research discusses the system vulnerabilities, the need to migrate to PQC, and how to integrate this migration. PQC has become one of the solutions for addressing today’s vulnerabilities and threats while increasing security. The paper concludes that harvest-now-decrypt-later, Q-Day attacks, and new quantum attacks are today’s most critical threats, which can be addressed by deploying PQC solutions and, thus, increasing security. This research proposes a conceptual multi-phased model framework for the migration. The framework first addresses system objectives, goals and assets, then ranks assets based on the highest sensitivity. Crypto-Agility is achieved via the automation of PQC migration, such as the automation of re-keying endpoints, followed by the automation of auditing and testing of each migration stage. Human judgment is required to review the migration process. Once one asset is successfully transitioned, the framework goes to the next highest asset; otherwise, testing is repeated. This is expected to help systems migrate at the lowest cost and with the fewest consequences. However, the limitation of PQC migration is its high resource cost, time, requirement of human professionals, burden on existing systems, and financial expenses. Lastly, the paper recommends creating an ML model to help rank a system’s data and vulnerabilities. Moreover, the paper recommends conducting experiments to evaluate the effectiveness of the proposed framework. In addition, the paper recommends performing migration in relation to a real-world company.
Full article

Figure 1
Open AccessArticle
Exploiting and Mitigating Staleness in Distributed Edge Offloading via Predictive Load Awareness
by
Sawsan Ali Hamid, Yassine Boujelben and Faouzi Zarai
Network 2026, 6(3), 69; https://doi.org/10.3390/network6030069 - 28 Aug 2026
Abstract
Distributed offloading systems rely on periodic broadcasts to disseminate server state, yet propagation delays inevitably leave agents operating with stale information at decision time. Staleness is typically viewed as a performance limitation that should be minimized. This work revisits this assumption by studying
[...] Read more.
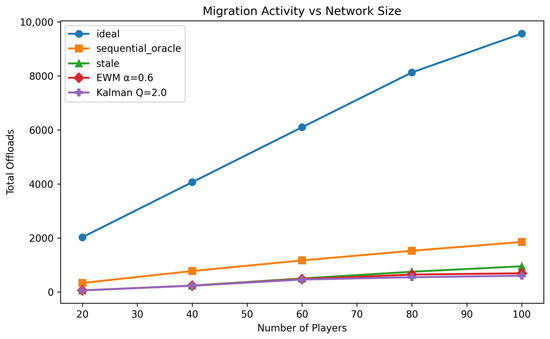
Distributed offloading systems rely on periodic broadcasts to disseminate server state, yet propagation delays inevitably leave agents operating with stale information at decision time. Staleness is typically viewed as a performance limitation that should be minimized. This work revisits this assumption by studying its role in a distributed asynchronous offloading framework that operates under delayed and potentially stale load information. Players make independent server-selection decisions using locally available information and may optionally compensate for staleness through lightweight load-prediction mechanisms. A central finding is that staleness can act as an implicit coordination mechanism. By inducing heterogeneous and desynchronized perceptions of system state, it naturally diversifies agent decisions and mitigates collective migration oscillations that arise under perfect information sharing. These oscillations are shown to significantly delay convergence and can lead to unstable behavior in lightly loaded regimes. In contrast, stale yet diverse views prevent synchronized reactions and promote faster stabilization. The results further show that the value of prediction increases with communication staleness. As broadcast intervals grow and server-state information becomes increasingly outdated, prediction-based approaches substantially reduce performance degradation, improve load-balancing fairness, and lower migration activity relative to stale-information decisions. The numerical results show that increasing the broadcast interval from 0.5 s to 4 s causes a performance deterioration of approximately 95% for stale-information decisions, whereas prediction-based approaches limit this degradation to less than 15% over the same range. These findings suggest that the objective of distributed offloading should not be to eliminate staleness entirely, but rather to combine its stabilizing effects with lightweight predictive mechanisms that mitigate its negative impact on decision quality.
Full article
(This article belongs to the Special Issue Convergence of Edge Computing and Next Generation Networking)
►▼
Show Figures

Figure 1
Open AccessArticle
Green FTTR in Smart Buildings: A Comparative Framework for Energy Efficiency, QoS and QoE Evaluation
by
Jorge Duarte, António Valente, Fernando Santos, Pedro Lopes, Miguel Ângelo Mota, Sérgio Ramos and Sérgio Leitão
Network 2026, 6(3), 68; https://doi.org/10.3390/network6030068 - 25 Aug 2026
Abstract
The growth of cloud services and immersive applications based on extended reality (XR), including Augmented Reality (AR), Virtual Reality (VR), and Mixed Reality (MR), imposes increasingly demanding requirements on access networks. The large-scale integration of IoT devices in smart buildings further increases the
[...] Read more.
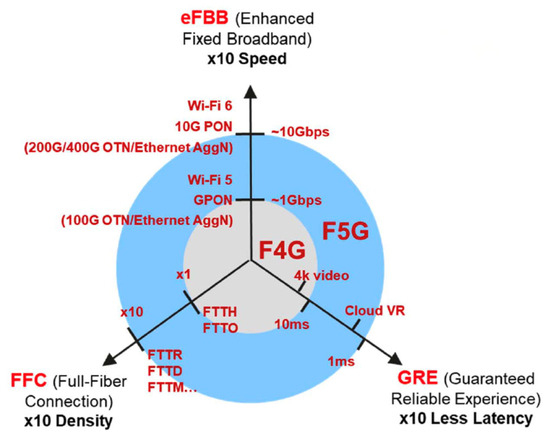
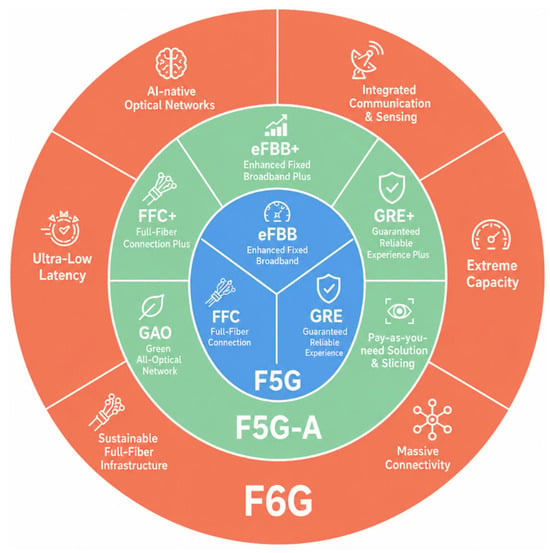
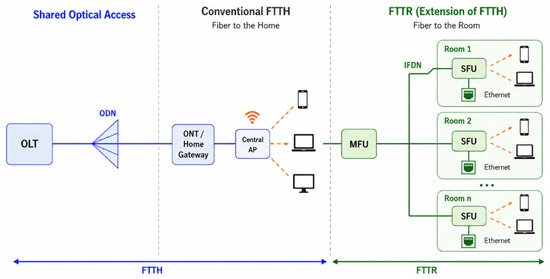
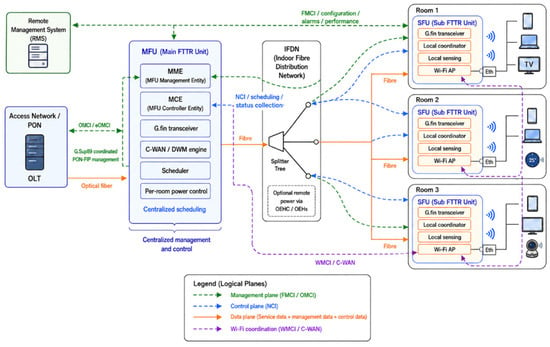
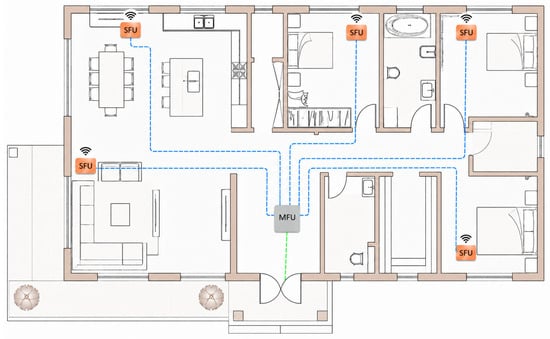
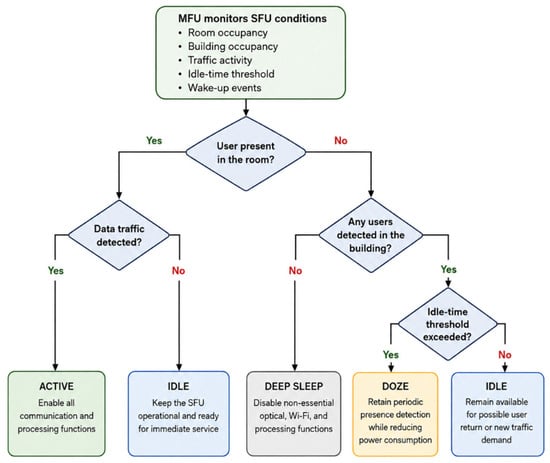
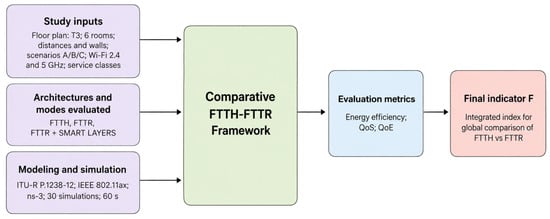
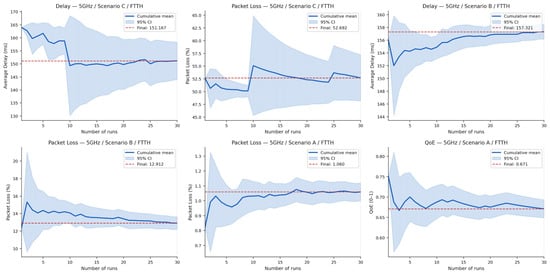
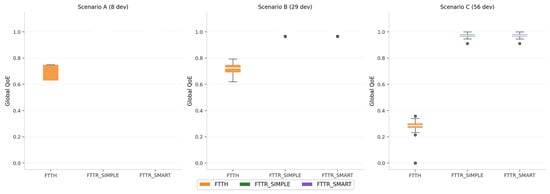
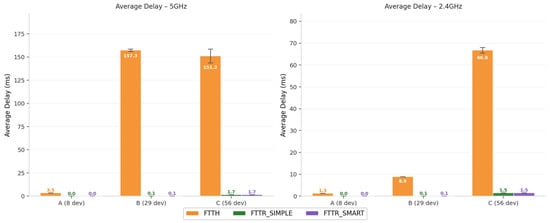
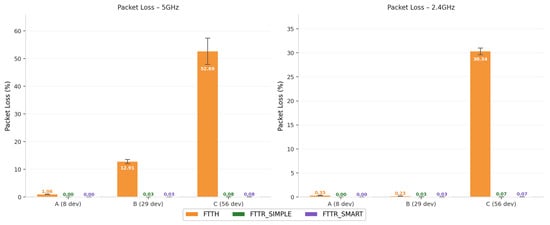
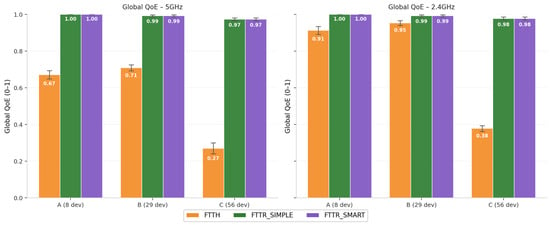
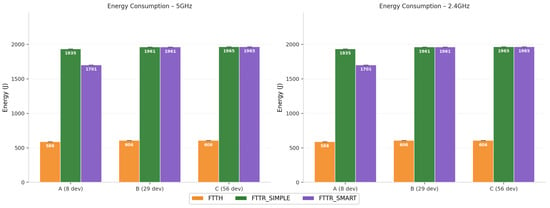
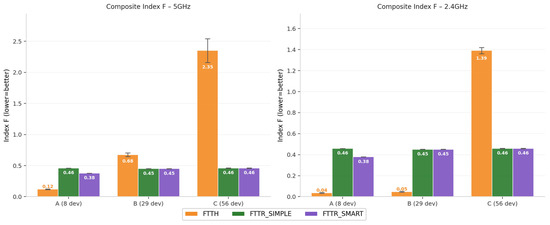
The growth of cloud services and immersive applications based on extended reality (XR), including Augmented Reality (AR), Virtual Reality (VR), and Mixed Reality (MR), imposes increasingly demanding requirements on access networks. The large-scale integration of IoT devices in smart buildings further increases the need for high throughput, low latency and jitter, and reliable connectivity. Traditional Fiber-to-the-Home (FTTH) networks with a single access point (AP) become quite limiting when there are high performance requirements, with many users with indoor mobility and high device density. Fiber-to-the-Room (FTTR) is an extension of FTTH, which brings fiber optics to each room of the house through a Main FTTR Unit (MFU) and several Sub FTTR Units (SFU) along with the APs, with centralized device management. Green FTTR networks are characterized by their energy efficiency through centralized control of signal power and Dynamic Bandwidth Allocation (DBA) management. The fgONT architecture allows for deterministic network slicing, enabling the allocation of specific resources isolated from the rest of the network traffic, allowing for predictable bandwidth and QoS. This work presents a framework that allows for a comparative analysis of FTTR and FTTH networks in different scenarios in order to ensure a compromise between transmission quality, network energy efficiency, and the user’s perceived experience. The results obtained show that, in high device density scenarios, FTTR reduces the average packet loss from 52.69% to less than 0.08%, decreases the average latency from 151 ms to less than 2 ms, and maintains the overall QoE above 0.974, compared to 0.27 in FTTH with a single AP.
Full article
(This article belongs to the Special Issue Advances in Wireless Communications and Networks)
►▼
Show Figures

Figure 1
Open AccessArticle
Interference-Calibrated Algebraically Projected Antenna Selection with Certified Graph Learning for Massive MIMO Under Realistic Multi-Cell Impairments
by
Iacovos Ioannou and Vasos Vassiliou
Network 2026, 6(3), 67; https://doi.org/10.3390/network6030067 - 22 Aug 2026
Abstract
Antenna selection is investigated as a means of reducing radio-frequency (RF) chain power in massive multiple-input multiple-output (MIMO) base stations under realistic channel state information (CSI) impairments. The study is motivated by the mismatch between conventional selection objectives and multi-cell operation with estimation
[...] Read more.
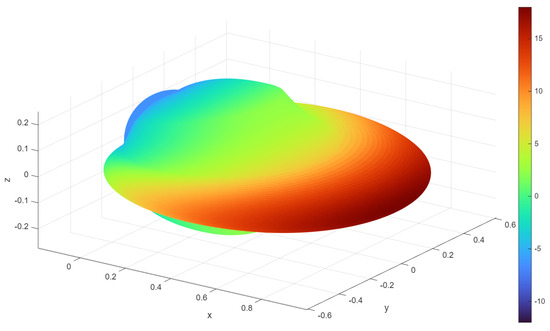
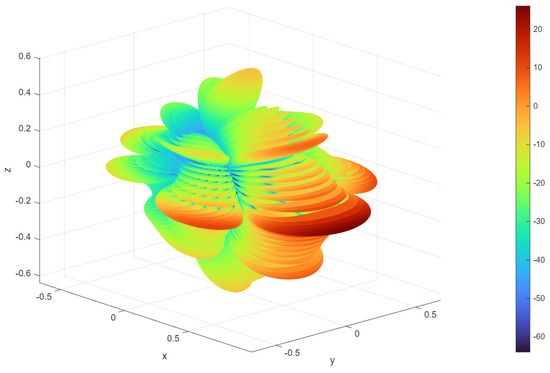
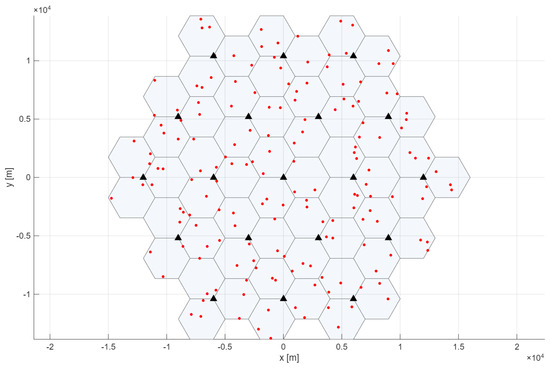
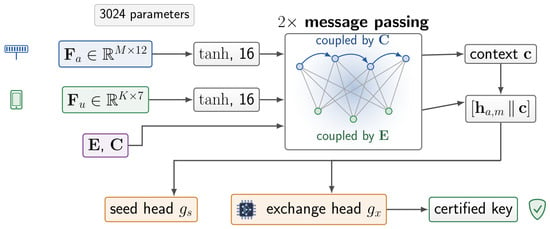
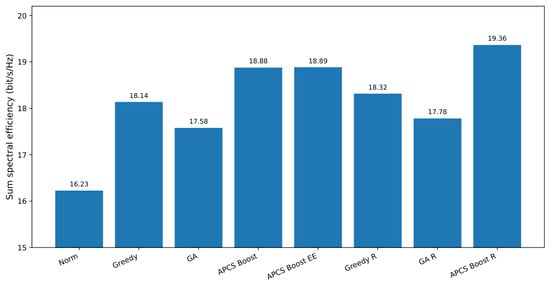
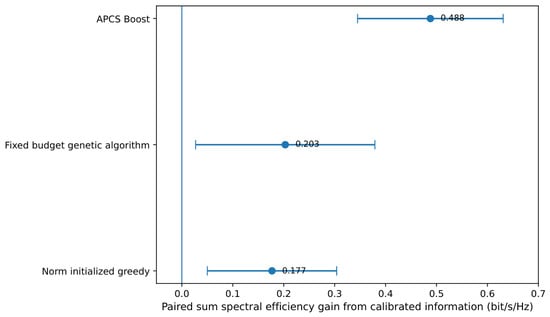
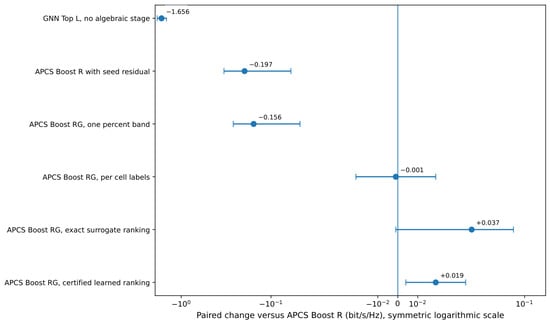
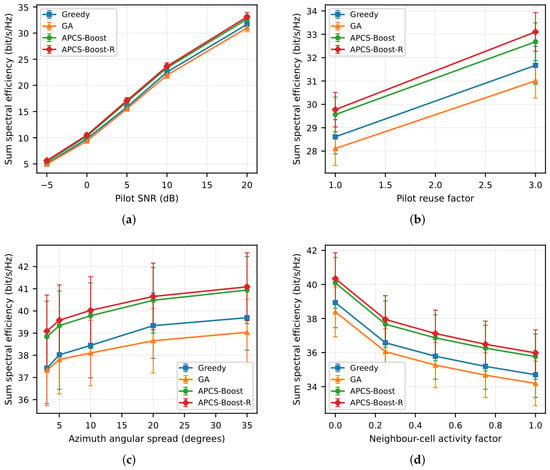
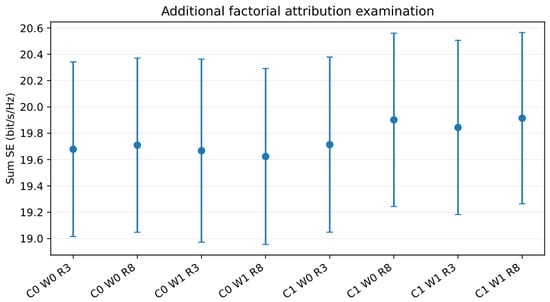
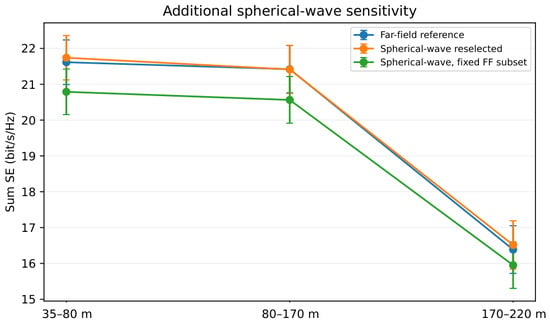
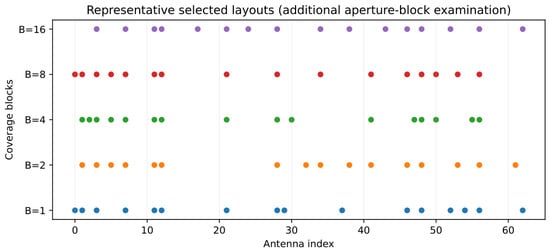
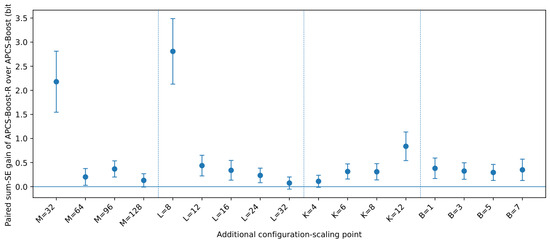
Antenna selection is investigated as a means of reducing radio-frequency (RF) chain power in massive multiple-input multiple-output (MIMO) base stations under realistic channel state information (CSI) impairments. The study is motivated by the mismatch between conventional selection objectives and multi-cell operation with estimation error, pilot contamination, spatial correlation and inter-cell interference. APCS-Boost-R is introduced as the primary contribution. An interference-whitened D-optimal seed is combined with projected rank-one exchanges and a calibrated surrogate that incorporates a user-side interference-plus-noise report and a closed-form estimation-error correction. APCS-Boost-RG is retained as an optional graph neural network (GNN) refinement in which residual exchanges are ranked after the algebraic solution has been formed, while feasibility and non-degradation of the calibrated surrogate are verified deterministically. In a three-cell urban macro configuration derived from Third Generation Partnership Project (3GPP) TR 38.901 with 64 antennas, 16 active RF chains and eight users per cell, APCS-Boost-R achieves 19.364 bit/s/Hz over 200 paired realizations. Improvements of 2.58 percent over APCS-Boost, 6.76 percent over greedy search and 10.16 percent over a genetic algorithm are obtained. APCS-Boost-RG adds 0.019 bit/s/Hz but is treated as an optional refinement because it requires a second-stage neighborhood evaluation and offline model maintenance. In the archived common timing record, APCS-Boost-R requires 20.376 ms per three-cell realization, compared with 12.728 ms for APCS-Boost, 57.775 ms for norm-initialized greedy search and 41.302 ms for the genetic algorithm, while APCS-Boost-RG requires 24.0 ms versus 20.4 ms for APCS-Boost-R in the separate archived learned-stage record. Separate reconstructions on the documented reproducibility host require ms for APCS-Boost-R and ms for a complete APCS-Boost-RG rebuild. Additional paired examinations confirm robustness across stronger search budgets, report imperfections, regularized precoding, coordination, near-field sensitivity, hardware perturbations, and configurations ranging from 32 to 128 antennas and one to seven cells.
Full article
(This article belongs to the Special Issue Advances in Wireless Communications and Networks)
►▼
Show Figures

Graphical abstract
Open AccessReview
Adaptive 360° Video Streaming: Prediction, Tiling, and Transport Trade-Offs
by
Muhammad Farooq, Gioacchino Manfredi, Luca De Cicco and Saverio Mascolo
Network 2026, 6(3), 66; https://doi.org/10.3390/network6030066 - 17 Aug 2026
Abstract
►▼
Show Figures
The growing demand for virtual reality and immersive applications has increased interest in 360° video streaming. When viewing omnidirectional content through a head-mounted display, users observe only a limited portion of the content, i.e., the viewport, at any given time. Consequently, transmitting the
[...] Read more.
The growing demand for virtual reality and immersive applications has increased interest in 360° video streaming. When viewing omnidirectional content through a head-mounted display, users observe only a limited portion of the content, i.e., the viewport, at any given time. Consequently, transmitting the complete panoramic frame at uniformly high quality is bandwidth-inefficient. This review presents a system-level analysis of viewport-adaptive three-degree-of-freedom (3DoF) 360° video streaming, focusing on the coupled roles of viewport prediction, tile-based multi-rate encoding and bitrate allocation, transport mechanisms, and edge-assisted processing. The reviewed literature is examined to identify the design dependencies and trade-offs among these components. Viewport-adaptive approaches seek to reduce the bandwidth allocated to regions outside the instantaneous viewport while preserving the quality of the visible region. The analysis shows that their effectiveness cannot be attributed to prediction accuracy alone: the resulting Quality of Experience (QoE) depends jointly on tile granularity, bitrate allocation, buffer occupancy, transport delay, and whether prioritized tiles arrive before their playback deadlines. Finer tiling can improve spatial selectivity but increases coding, signaling, and request overhead. Moreover, HTTP/2, HTTP/3/QUIC, RTP/RTSP, and WebRTC present different reliability, latency, congestion-control, and scalability trade-offs across buffered video-on-demand, low-latency live streaming, and interactive immersive applications. Based on this synthesis, the review formulates a unified closed-loop cross-layer framework that coordinates prediction, tiling, bitrate allocation, request timing, transport configuration, buffering, and edge processing under bandwidth, latency, and resource constraints.
Full article

Figure 1
Open AccessArticle
Design and Evaluation of PSA-FRR and PSAR-FRR for Fast Reroute in Homogeneous and Hybrid SDN Networks
by
Md Imtiaz Ahmed and Yaser Al Mtawa
Network 2026, 6(3), 65; https://doi.org/10.3390/network6030065 - 10 Aug 2026
Abstract
Fast Reroute (FRR) after link failures is essential for carrier-grade Software-Defined Networking (SDN), yet hybrid deployments remain dominated by slow legacy routing convergence. This paper presents two port-state-driven FRR mechanisms for homogeneous and hybrid SDN networks. First, Port-State-Aware Fast Reroute (PSA-FRR) uses OpenFlow
[...] Read more.
Fast Reroute (FRR) after link failures is essential for carrier-grade Software-Defined Networking (SDN), yet hybrid deployments remain dominated by slow legacy routing convergence. This paper presents two port-state-driven FRR mechanisms for homogeneous and hybrid SDN networks. First, Port-State-Aware Fast Reroute (PSA-FRR) uses OpenFlow port-status events to trigger proactive, rule-based protection in the data plane. Second, Port-State-Aware Neural Fast Reroute (PSAR-FRR) formulates hybrid FRR as a controller-local multi-class classification problem and predicts the backup egress port from a port-centric state representation, enabling microsecond-scale decision latency. We evaluate the methods on the Abilene wide-area network (WAN) topology using Mininet with Open vSwitch (OVS) and a Ryu controller (homogeneous case) and Graphical Network Simulator-3 (GNS3) with Cisco IOS routers (hybrid baseline). In homogeneous SDN emulation, PSA-FRR restores connectivity within 30–100 ms under the evaluated configurations. In the hybrid baseline, conventional routing protocols converge in 13.8–256.1 s (Enhanced Interior Gateway Routing Protocol (EIGRP), Intermediate System to Intermediate System (IS-IS), Open Shortest Path First (OSPF), Border Gateway Protocol (BGP), and Routing Information Protocol (RIP)), confirming that control-plane recovery cannot meet a 50 ms target. Using the collected dataset, PSAR-FRR reduces controller decision time from 6.753 s (PSA-FRR rule evaluation) to 0.214 s (deep neural network (DNN) inference), a 31.5× speedup. These results show that port-state awareness combined with learned, controller-local policies can substantially reduce the decision-to-action latency of FRR, providing a practical path toward low-latency failure recovery in SDN migration scenarios.
Full article
(This article belongs to the Special Issue Recent Advances in Software-Defined Networking (SDN))
►▼
Show Figures

Figure 1
Highly Accessed Articles
Latest Books
E-Mail Alert
News
Topics
Topic in
Applied Sciences, Electronics, IoT, Sensors, Future Internet, JSAN, Telecom, Network
Applications of IoT in Multidisciplinary Areas
Topic Editors: Nurul Sarkar, Ivan CviticDeadline: 31 October 2026
Topic in
Applied Sciences, Future Internet, Information, Algorithms, Computers, Blockchains, Cryptography, Network
Security and Privacy in Distributed and Trustless Systems
Topic Editors: Longxiang Gao, Bruce GuDeadline: 31 March 2027
Topic in
Electronics, Future Internet, Technologies, Telecom, Network, Microwave, Information, Signals
Advanced Propagation Channel Estimation Techniques for Sixth-Generation (6G) Wireless Communications
Topic Editors: Han Wang, Fangqing Wen, Xianpeng WangDeadline: 30 June 2027
Conferences
Special Issues
Special Issue in
Network
AI-Oriented 6G Networks
Guest Editors: Bin Han, Wei JiangDeadline: 31 October 2026
Special Issue in
Network
AI-Based Innovations in 5G Communications and Beyond
Guest Editors: Muddasar Naeem, Antonio CoronatoDeadline: 31 October 2026
Special Issue in
Network
Artificial Intelligence in Effective Intrusion Detection for Clouds
Guest Editor: Stavros ShiaelesDeadline: 30 November 2026
Special Issue in
Network
Advances in AI-Powered Cybersecurity
Guest Editors: Tao Li, Tianchong GaoDeadline: 30 November 2026
Topical Collections
Topical Collection in
Network
Advanced Technologies in Network and Service Management, 2nd Edition
Collection Editors: Hakim Mellah, Filippo Malandra