


Abstract
Post-quantum digital signatures are needed to protect authentication against quantum attacks. Code-based techniques offer a promising foundation for this goal. Linkable ring signatures additionally provide signer anonymity and public linkage, but repeated membership proofs can incur substantial communication costs. We propose a linkable ring signature based on polar codes with reusable anonymous authorization. The scheme supports independently verifiable messages, public linking across rings, and repeated signing. Under the stated primitive assumptions and honest registration, we prove unforgeability, restricted anonymity, linkability, and non-frameability in the classical random oracle model. For parameters selected against a 128-bit classical generic-attack target, the authorization proof is 98.52% shorter than the selected-matrix implementation of the same relation for a 32-member ring, and each cached online packet occupies 807 bytes. Compared with a direct-proof baseline using the same parameters, certificate reuse reduces total communication from the second message onward for all evaluated ring sizes. A prototype executes key generation, authorization, certificate installation, and online signing and verification with actual polar-code keys. For a 1024-member ring, the authorization certificate occupies 189.5 MB. For a single verifier with pre-distributed rings, total communication is lower than that of a reference linkable ring signature scheme for workloads of at least 6561 messages.
Keywords:
post-quantum cryptography; polar codes; linkable ring signatures; anonymous authentication; MPC-in-the-head MSC:
94A60; 94B05; 94B35; 68P25
1. Introduction
Large-scale quantum computers threaten public-key authentication based on factoring and discrete logarithms, motivating the development of post-quantum digital signatures. The standardization of ML-DSA and SLH-DSA provides concrete alternatives [1,2], while NIST’s additional-signature evaluation examines complementary constructions, including code-based and symmetric-primitive-based approaches [3]. Deploying these signatures also requires attention to public-key distribution, signature size, and recurring communication costs [4]. Applications involving anonymous reporting or repeated group authentication additionally require a verifier to authenticate a message without identifying its sender.
Ring signatures address this requirement by allowing a member to sign on behalf of a set of public keys while concealing the signing member [5]. Linkable ring signatures further allow a verifier to recognize signatures associated with the same signer without revealing that signer’s identity [6]. This functionality is useful when anonymous submissions must remain individually verifiable while repeated participation is detectable. Post-quantum constructions include the code-based scheme of Liu and Wang [7] and proof-based approaches. Goel et al. developed MPC-in-the-head set-membership proofs with applications to ring signatures [8]. Xue et al. proposed a framework for linkable ring signatures with post-quantum instantiations and reusable offline signing and verification work [9]. These results provide the context for reducing the recurring cost of anonymous authentication.
Code-based signatures offer several ways to build the underlying authentication primitive. CFS uses a secret Goppa-code decoding structure [10], whereas Wave uses preimage sampling over generalized ternary codes [11]. Wave parameter selection illustrates the trade-off between short signatures and large public keys [12]. Syndrome Decoding in the Head instead proves knowledge of a low-weight solution to a public decoding relation [13]. For ring signatures, the additional cost of hiding the signing key makes both the verification relation and the proof representation important design choices.
Repeated use must also be considered within an explicit anonymity model. Bultel and Olivier-Anclin studied anonymity definitions for linkable ring signatures [14], and Tran et al. introduced threshold-based many-time anonymity with a lattice-based construction in the quantum random oracle model [15]. We consider anonymous authentication with public linkage under honestly registered keys. Messages remain independently verifiable, and signatures from the same registered key remain linkable across different rings and online authorizations.
Polar codes are attractive for this setting because they combine a recursive encoding structure with efficient decoding algorithms [16]. Standard polar encoding and successive-cancellation decoding have complexity for block length N, and list decoding offers further decoding trade-offs [17]. Forghani et al. adapted modified polar codes to digital signatures in PolarSig [18]. We instantiate its modified-polar key family with a longer mother code and successive-cancellation randomized rounding for member authorization and online message signing. Its short basic signature limits recurring message expansion, while its binary parity-check verification relation provides the structure used in our authorization-circuit optimization.
The MPC-in-the-head paradigm supplies a general method for proving the authorization relation without revealing the member [19]. ZKBoo and ZKB++ provide practical Boolean-circuit instantiations [20,21]. Banquet reduces proof costs through specialized AES checks [22], and recent FAEST optimizations combine witness compression with improved VOLE-in-the-head analysis [23]. These approaches motivate adapting the proof representation to the computation being verified. In our binary verification circuit, selecting the public linear-map outputs instead of a hidden matrix reduces the number of nonlinear gates.
Our objective is to reduce communication when members repeatedly authenticate messages over persistent rings. We propose a linkable ring signature based on polar codes with reusable anonymous authorization. A member establishes an authorization before future messages are known. An accepting verifier can then reuse it for subsequent messages while preserving public linkage. The design combines a smaller authorization circuit with short online signatures. Its evaluation accounts for the initial certificate and public-ring distribution, so the reported savings reflect the complete repeated-authentication workload.
The contributions are as follows.
- Polar-code-based construction and security. We design a linkable ring signature based on polar codes with reusable anonymous authorization. Under the stated primitive assumptions and honest registration, we prove unforgeability, restricted anonymity, linkability, and non-frameability in the classical random oracle model. The scheme supports independently verifiable messages and public linking across rings.
- Smaller anonymous-authorization proofs. We specialize standard linearity and one-hot selection to the authorization relation by evaluating public binary linear maps before selecting the hidden member’s output. A hybrid circuit uses syndrome AND gates, where L is the ring size and is the public matrix dimension. For a 32-member ring, the fixed-length FS-ZKB++ proof is 98.52% shorter than the selected-matrix implementation of the same relation.
- Lower communication through authorization reuse. We bind an online signing key and a persistent linking tag to a reusable anonymous certificate, allowing cached online packets of 807 bytes. Relative to a direct-proof baseline with the same parameters, certificate reuse reduces total communication from the second message onward for all four evaluated ring sizes.
2. Preliminaries
2.1. Notation and Primitives
Let denote the security parameter, , and the Hamming weight of a binary vector. Matrix operations are over . The notation denotes an injective, length-delimited encoding, and denotes concatenation.
Polar codes and signatures. Polar codes are binary linear codes obtained through channel polarization. Their recursive structure supports encoding and successive-cancellation decoding in operations for block length N [16]. Successive-cancellation list decoding maintains multiple candidate paths to improve decoding performance [17]. PolarSig adapts modified polar codes to digital signatures [18]. Write for its algorithms. A public key is a binary matrix , and a signature contains an error vector e and a random string a. Verification checks
and , where t is the prescribed weight upper bound. PolarSig’s EUF-CMA theorem is a parameterized reduction under the CSD and MPD hardness assumptions in the classical random oracle model [18] [Theorem 3].
Noninteractive zero-knowledge arguments. For a relation , an argument allows a prover to establish that a public statement has a valid witness without revealing it. Completeness ensures acceptance of valid proofs, adaptive multi-theorem zero knowledge hides the witness, and simulation-sound extractability permits witness extraction from fresh accepting statements even in the presence of simulated proofs [24] [Definitions 4–5]. The extraction setup preserves the simulator’s public-parameter and trapdoor distribution. Such arguments support anonymous membership and credential verification [8,24].
MPC-in-the-head and Fiat–Shamir. MPC-in-the-head constructs zero-knowledge proofs by simulating a multiparty computation and opening selected execution views [19]. ZKBoo and ZKB++ instantiate this approach for Boolean circuits [20,21]. The Fiat–Shamir transformation derives verifier challenges by hashing the public statement and complete first protocol message [25].
Further analyses address strong unforgeability and binding properties of MPC-in-the-head signatures [26], and Fiat–Shamir and commit-and-open protocols in the quantum random oracle model [27,28].
Hash commitments and domain separation. A randomized hash commitment has the form , where is a secret random salt. In the random oracle model, the salt hides the committed value, while collision resistance provides computational binding. Domain separation assigns distinct prefixes to different hash functions so that commitments, identifiers, and protocol challenges use separate hash domains.
2.2. Linkable Ring Signatures
A ring signature authenticates a message under a set of public keys without identifying the signing member [5]. A linkable ring signature additionally provides a public test for whether two valid signatures originate from the same signing key [6]. With common public parameters implicit, its algorithmic interface is
where is a ring containing , and is a ring–message–signature tuple. Verification returns 1 for an accepted signature. Linking returns 1 for linked signatures, 0 for unlinked signatures, and ⊥ if either signature is invalid. The linking scope specifies which pairs of rings or application contexts are eligible for comparison.
Verification correctness. For honestly generated keys, every message m, and every ring R containing ,
The probability is over key generation and signing randomness.
Linking correctness. Let for , with both tuples in the same linking scope. For distinct, honestly generated member keys, valid signatures satisfy
where identify member keys, and is the indicator function.
Anonymity hides the signing member subject to the information disclosed by public linking [14]. Unforgeability prevents unauthorized message signatures. Linkability prevents a signer from evading the linking test. Non-frameability prevents an adversary from producing a fresh signature attributed by linking to an honest member.
3. Proposed Construction
This section specifies the security model, authorization relation, and algorithms of the polar-code-based linkable ring signature.
3.1. Security Model
We consider a managed group with honestly provisioned, immutable registered keys. A ring is a canonical ordered set of distinct registered keys. fixes the parameters and encoding. The certificate cache contains accepted records bound to their ring and parameter identifier. Linking is global per registered key.
Classical probabilistic polynomial-time adversaries access the registration, authorization, signing, and corruption oracles in Appendix A. Let , , and denote corrupted member indices, answered ring-message pairs, and issued authorization tags, respectively.
Unforgeability. A winning forgery is an accepted signature on with and , where denotes its registered member indices.
Anonymity. A uniform bit b selects one of two uncorrupted candidates for the challenge authorization and its messages. The adversary may query further challenge messages and other members, but may neither corrupt nor obtain identity-labeled authorizations or signatures from either candidate before or after the challenge. Its advantage is . Tag and certificate equality remain visible. This model covers managed anonymous reporting in which credentials are provisioned privately and submissions are exposed through pseudonymous tags. An identity-labeled sample from either candidate would identify its persistent tag and all linked submissions.
Linkability. Signatures from the same registered key link. An adversary wins by outputting accepted signatures with more than distinct tags outside .
Non-frameability. Given an uncorrupted target’s tag and signatures, the adversary wins by producing an accepted signature with that tag on a fresh ring-message pair. The target’s long-term and online state remains unexposed.
3.2. Overall Framework
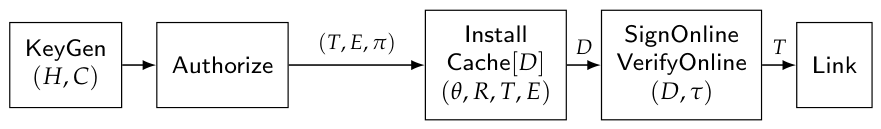
The construction anonymously certifies an online key and reuses its certificate for message authentication (Figure 1). Its interface is
For a standalone signature , installs the certificate in an empty cache and invokes . An installed certificate supports the compact packet . Boolean verification returns v. Linking uses the accepted tag.
Figure 1.
Scheme workflow.
During registration, Algorithm 1 associates a polar-code verification key with a commitment to a linking secret. Algorithm 2 proves that one hidden registered member both possesses this secret and authorizes an independently generated online key. The proof uses the same hidden member index for both checks. This binds the online key to an authorized member while hiding that member’s identity.
Algorithm 3 verifies the authorization and installs its public record. Algorithm 4 uses the authorized polar-code key to sign and verify each message. Its signed encoding includes the certificate identifier and protocol context, preventing a message signature from being transferred to a different authorization. The short polar-code signature is the recurring communication cost, while the membership proof is paid for when the certificate is installed.
The public transcript exposes the ring, messages, online public key, certificate identifier, and linking tag. Equal tags reveal use of the same registered member key. Equal certificate identifiers additionally reveal reuse of an online authorization. The linking tag is derived from the registered member’s secret, independently of the ring and online key. Commitment binding prevents one registered member from obtaining different valid tags, and the joint proof binds every accepted tag to its authorized member. After message verification, Equation (5) compares the tags to implement public linking.
3.3. Authorization Relation
The domain-separated ℓ-bit hashes implement commitments, tags, authorization identifiers, and direct-baseline message digests. Let satisfy the properties in Section 2.1.
Member i registers and keeps , where
Let E be a freshly generated online PolarSig public key. Define
For the statement and witness , the authorization relation is
The same index j selects both the commitment and verification matrix.
3.4. Key Generation and Authorization
Algorithms 1 and 2 generate registered keys and anonymous certificates.
| Algorithm 1 Member key generation |
|
| Algorithm 2 Anonymous authorization |
|
Setup generates and . Authorization precedes application messages.
3.5. Certificate Installation and Online Signing
Algorithm 3 validates and caches certificates. Algorithm 4 authenticates messages under the certified online key.
| Algorithm 3 Certificate installation |
|
| Algorithm 4 Online signing and verification |
|
checks the header, parameter identifier, ring-size bounds, and exact field lengths; canonical distinct registered keys; registered matrix dimensions and full row rank; online-key dimensions; ℓ-bit commitments and tags; and prescribed proof seeds, commitments, views, ternary challenges, and zero padding. Extra bytes are rejected.
3.6. Public Linking
For two ring-message-signature tuples , the linking procedure resolves their certificates and verifies each message:
Equation (2) preserves the tag across rings and online keys.
4. Scheme Analysis
We establish correctness and the four security properties defined in Section 3.1.
4.1. Correctness
Proposition 1.
If the underlying signing algorithms return valid signatures and is complete, the construction is correct and signatures from the same member link.
Proof.
Algorithm 2 satisfies all conditions in Equation (4). Completeness and base-signature correctness give acceptance, while Equation (2) fixes each member’s tag. For U registered members, repeated linking secrets and distinct-input tag-hash collisions each have probability at most . Their union bounds accidental cross-member tag equality by . The construction inherits the base signing failure probability. □
4.2. Unforgeability
Theorem 1.
Assume that the polar-code signature is EUF-CMA secure, satisfies Section 2.1, and is collision resistant. Then, the construction is unforgeable in the classical random oracle model under Section 3.1.
Proof.
Simulate the challenger’s authorization proofs, at cost , and charge collisions to . An unissued payload gives a fresh statement. Apply the extractor to a wrapper returning this authorization alone. Embedding a base-signature challenge key at a uniform registered index requires no member-signing query because authorization proofs are simulated. If the guess matches the extracted index, forges . The winning ring excludes corruption of this member.
For an issued payload, guess its online key among the issued authorizations and answer its signing queries through the base signing oracle. Freshness of makes fresh under that key, yielding the forgery .
Let bound the joint event of a fresh accepting wrapper output and invalid extraction in the simulated experiment. Here, bounds simulated proofs and separates hash domains. Let denote the maximum base-signature EUF-CMA advantage within time T, Q base-hash queries, and signing queries. For at most U members and authorizations,
The two guesses cost factors U and A, respectively, with budgets
include the extractor, wrapper, registration, simulation, and oracle environment over all rewinding executions. The online environment budgets include registration, other key generation, simulation, verification, and state maintenance. Postprocessing covers witness checking and output. Superscript selects base-hash queries, and counts signing queries under the guessed online key. □
4.3. Anonymity
Theorem 2.
Under adaptive zero knowledge of and the domain-separated random-oracle assumptions for and , the construction satisfies the anonymity game of Section 3.1.
Proof.
Simulate all authorization proofs needed by the game. The independent commitment and tag domains hide the candidate-to-tag correspondence until an unexposed linking secret is queried. Replacing the challenge tag by a uniform value and switching candidates preserves the independent online-key and message distributions, including their public equality information. Thus
Let include pre-registration queries. The secret-query event matches any unexposed registered x, or a later registration secret matches an earlier query. An incorrect-salt commitment query counts as an x guess. Conditional on distinct secrets, no public-hash collision, and no earlier hit, each unexposed secret is uniform over at least possibilities. A union bound over registration and query steps yields
For the first term is at most . With distinct inputs in domain , . Query budgets include challenger and verifier evaluations. Proof-programming losses enter . □
4.4. Linkability and Non-Frameability
Theorem 3.
Under the assumptions of Theorem 1, commitment binding and tag collision resistance, the construction satisfies linkability and non-frameability as defined in Section 3.1.
Proof.
The challenger knows each registered opening and canonical tag, including those of subsequently corrupted members. A winning linkability output contains an accepted tag outside both and . A wrapper verifies the outputs and selects the first such authorization. Its statement is fresh because its tag was not issued. Extract once. An uncorrupted extracted member yields the member-level forgery of Theorem 1. A corrupted member has , so its extracted and registered openings collide under . The joint extraction-failure term is . For N outputs, one wrapper run costs . Verification queries enter and all extractor rewinding enters .
For non-frameability, consider a fresh accepted message with the target tag. Outside registered-secret and tag collisions, an issued payload carrying that tag belongs to the target and yields an online forgery. A new payload admits fresh-statement extraction: the target member yields a member-level forgery, while another member yields commitment or tag collision. Repeated registered secrets contribute at most . □
5. Authorization Circuit and Instantiation
This section realizes the authorization relation as a Boolean circuit and instantiates its proof with Fiat–Shamir ZKB++.
5.1. Selecting Public Linear-Map Outputs
Let and encode the hidden index by s witness bits. A binary decoder produces . At each internal node, the two children can be computed as and . Excluding the first split, the decoder requires AND gates. The selected commitment is
Since every is public, Equation (8) is linear in the witness bits. For the syndrome, use
The products are public linear maps and use only XORs. Each of their d output coordinates then requires one AND with . Algorithm 5 evaluates the hidden-member syndrome.
| Algorithm 5 Hidden-member syndrome evaluation |
|
Proposition 2.
Equation (9) computes with AND gates after index decoding, compared with for selecting a secret matrix and multiplying it by e.
Proof.
For , all terms indexed by vanish. Otherwise, only term remains, giving . The stated gate count follows from coordinatewise products of length d. In the selected-matrix baseline, each of the entries multiplies a secret coordinate of e. □
The reduction is strict when . The decoder cost is common to both circuits. Selecting the smaller syndrome circuit gives AND gates, with public XOR work. This specializes standard linearity and one-hot membership selection [8].
5.2. Hash and Weight Constraints
The witness is with length
The circuit outputs commitment, tag, and syndrome residuals, together with the failure bit of the prescribed weight test. Its public target is the all-zero vector of length . Using this vector avoids a final conjunction over all comparison bits.
We select SHAKE256 [29] for the concrete hash interfaces. The commitment and tag inputs occupy 65 and 33 bytes. The authorization message has a four-byte prefix and a 32-byte digest. Its 20-bit random string occupies three bytes with four zero padding bits. The hash returns the first 4179 bits of SHAKE256, requiring four 1088-bit output blocks. Each private-input hash fits one absorption block. The commitment and tag each use one Keccak-f[1600] permutation, and uses four, including the additional squeeze permutations. The six permutations contribute 230,400 AND gates, or 61.22% of the budget. Public authorization hashing and Fiat–Shamir transcript hashing are outside the witness circuit.
For weight evaluation, pad e to bits and use a balanced addition tree. A full-adder carry is
The tree uses AND gates. A constant comparison uses at most additional gates. With , the budget before constant-dependent gate elimination is 16,383 gates.
5.3. Parameters and Proof Encoding
Table 1 specifies the modified-polar instance used for member and online keys. We select it against a 128-bit classical generic-attack target.
Table 1.
Reference parameters.
Finite-length key generation and signing. In , the information set consists of the 1720 smallest estimated Bhattacharyya parameters for BSC(0.24), obtained from 300 Monte Carlo synthetic-channel samples. Starting from the polar transform , key generation uniformly unfreezes 245 other positions and punctures 2048 coordinates, resampling punctures until the generator has rank 1965. For a full-rank parity-check matrix , the public key is , where S is uniform in and P is a uniform coordinate permutation. These are the frozen-set randomization, puncturing, and masking operations of the modified-polar family [18].
Signing first inverts S on the hashed syndrome and forms a systematic preimage under . It randomly fills punctured coordinates and applies successive-cancellation randomized rounding for BSC(0.24) [30]. The original frozen positions remain zero, except that the 245 additionally unfrozen positions receive independent random bits. The punctured quantization error is permuted back to public coordinates. A fresh 20-bit salt and fresh rounding randomness are sampled until its weight is at most 1600.
Concrete generic-attack estimates. An invertible d-column submatrix gives the public forgery trial
Its acceptance probability for a fresh hash input is
The parameters of Table 1 give . General decoding estimates must account for the many solutions: at weight t, their expected number is . Table 2 reports the evaluated classical attacks. The fixed-syndrome values use CryptographicEstimators 2.1.1 with this solution count [31]. The DS-DOOM value uses the authors’ multi-target estimator at targets [32]. The collision-DOOM model [33] is also evaluated with unlimited free targets and zero target-conversion cost. Within its searched auxiliary-length range , summing all weights up to t improves the relevant collision probability by at most a factor 4.42. The table conservatively subtracts 2.15 bits from that model’s 145.20-bit estimate.
Table 2.
Classical generic-attack estimates.
Instantiation assumptions and structural attacks. Theorems 1–3 hold under the CSD and MPD assumptions for the key distribution specified above and the stated proof-system and hash assumptions. Bardet et al. recover permuted polar codes using minimum-weight codewords and recursive code equivalence [34]. Random unfreezing of 245 positions and puncturing of 2048 coordinates of the mother code modify the information set and full-length structure used by that attack [18]. The masks S and P preserve permutation-invariant code properties. The published attack does not directly establish a key-recovery cost for this modified distribution. Structural security remains conditional on its MPD assumption. Table 2 evaluates classical generic attacks. Its 128-bit target is not an established concrete security level against structural or distribution-specific attacks.
FS-ZKB++ instantiation. The public circuit target is . Each repetition uses independent uniform 256-bit seeds. A view commitment binds the seed and canonical view to the parameter identifier, statement, repetition, and party indices. Seed expansion, commitments, and challenges have disjoint domains, separate from . Proof simulation programs only proof-system domains. The Fiat–Shamir hash binds the statement and complete first message, including all output shares and view commitments. Uniform ternary challenges are sampled by rejecting two-bit value 11. The verifier reconstructs the opened views, obtains the unopened output share by XORing the public target with the two opened shares, and checks the recomputed challenge against the encoded vector. This uses ZKB++ output-share compression [21] and the classical-ROM adaptive zero-knowledge and simulation-extraction results of [24] [Lemmas 3–4 and Corollary 1].
For , the knowledge-error term is below when [35]. Seed-and-view commitments give quasi-unique-response error at most [24] [Lemma 4]. The extraction resources are represented separately in Equation (6).
A repetition contains one unopened-view commitment, two opened-view seeds, one AND transcript, and a fixed input-share field. The challenge vector uses two bits per repetition. Unused input-share fields and trailing padding bits are checked zeros. Using the smaller syndrome circuit at each ring size,
Applying the ZKB++ view encoding [21] with byte-aligned, fixed-length fields gives
The four-byte packet header identifies the version, parameter set, ring-size exponent, and record type. Matrices are packed continuously by rows. Equation (13) fixes the proof length.
6. Performance Analysis and Comparison
This section quantifies the communication cost of authorization and online authentication. We compare the optimized circuit with a selected-matrix baseline and derive the savings from certificate reuse. We then evaluate the complete protocol and compare repeated-authentication structures with Liu and Wang [7] and Xue et al. [9], using Xue et al.’s published reference for the numerical communication comparison.
6.1. Circuit Comparison
Table 3 compares Equation (9) with the selected-matrix baseline. Both use the same relation, hashes, repetition count, and proof format. The baseline replaces the syndrome cost by .
Table 3.
Authorization proof sizes.
6.2. Certificate Reuse
Let be the byte lengths of the tag, certificate identifier, and basic signature. A certificate occupies
and an online packet occupies . In the reference instance, these are and 807 bytes. A standalone signature carrying the certificate occupies .
The direct-proof baseline signs each public digest under the hidden member key and proves Equation (4) for that digest. Its circuit and proof length are identical to the authorization circuit. Both schemes share the public ring, and the baseline sends its tag only once. For q messages,
Proposition 3.
Cached authorization reduces total communication relative to the direct-proof baseline exactly when
Proof.
Subtract the second expression in Equation (15) from the first and cancel the common header and tag terms. □
When , the minimum integer satisfying Equation (16) is
It equals two for all four instances in Table 3. For and , the direct-proof and cached constructions require 31,569,734 and 18,995,967 bytes, respectively, a 39.83% reduction. Table 4 includes the initial certificate in the per-message averages.
Table 4.
Certificate and amortized communication (bytes).
For h certificate transmissions, total communication is . Table 5 summarizes the cryptographic operations.
Table 5.
Primitive calls.
6.3. Experimental Evaluation
We evaluate signing performance and complete protocol execution using the parameters in Table 1. The prototype implements polar-code key generation and signing, authorization, certificate installation, and cached online signing and verification.
Experimental setup. The prototype uses Python 3.12.14 and NumPy 2.3.5 on Windows and a C++17 ZKB++ prover and verifier on Ubuntu 26.04 (WSL2), compiled with GCC 15.2.0 (-O2 -std=c++17). Measurements use one worker pinned to logical CPU 0 of an Intel Xeon Gold 5218R at 2.10 GHz. Protocol timings include serialization, process launch, and file I/O.
Test inputs. Eight independently generated, full-rank masked member keys form a canonical ring. One member creates three authorizations, each with an independently generated online key, and signs 32 distinct messages per authorization. Each authorization digest is computed from the actual parameter identifier, ring, tag, and online key as in Equation (3). Installation verifies the proof using only the public statement and stores the resulting online key and tag.
Results. All three authorizations installed successfully, and all 96 online signatures verified and linked to the same member tag. Every proof contained 11,658,856 bytes, matching Equation (13), and every online packet contained 807 bytes. Table 6 reports the measurements. The independent base-signing test produced 140 valid signatures on three masked keys in 187 attempts, averaging 1.34 attempts with a maximum of 4. Additional correctness and tampering checks passed. Peak RSS of the C++ proof processes was 98.81 MiB for proving and 66.94 MiB for verification.
Table 6.
Integrated execution times.
The results demonstrate complete protocol execution and certificate reuse for repeated, publicly linkable message authentication at . For fixed code parameters, proving and proof-verification work scales as , which is linear in L at fixed r. Larger-ring proof sizes and communication costs in Table 3 and Table 4 are derived analytically from the circuit and serialization formulas.
6.4. Published-Scheme Comparison
Liu and Wang [7] bind each Stern-type proof transcript to its message. Xue et al. [9] reuse offline signing and verification work, while each signature retains a message-bound signature of knowledge. Our authorization certificate binds an independent online key before subsequent messages are known. Table 7 summarizes these published formats. Liu and Wang report numerical parameters at 80-bit security, so we use their scheme for this structural comparison.
Table 7.
Repeated-authentication structure.
For the numerical comparison, our instance uses the 128-bit classical generic-attack target and CSD/MPD assumptions of Section 5.3, and Xue et al. use their published 128-bit configuration. For , we use their approximate 29 KiB reference as bytes [9,36]. With the hybrid circuit, Equations (12) and (13) give , a 186,312,125-byte proof, a 189,521,633-byte certificate, and a 189,522,404-byte standalone signature. The public ring occupies
Table 8 gives analytical communication costs with the full initial certificate and matching public-key-list distribution: both lists are available, or each is sent once. All messages reuse one certificate at one recipient. Xue et al.’s reported 32-byte public keys give bytes.
Table 8.
Communication comparison.
Let s count list distributions under the same convention for both schemes, and h count certificate installations. Then
For and , the strict crossover is
With , , and , the thresholds at one recipient are 6561 messages for and 120,324 for . At with each ring distributed once, the calculated communication is 27,327.19 versus 29,696.25 bytes per message, approximately 7.98% lower under this reference workload.
The 3.29 GB public ring and 189.5 MB certificate favor long-lived rings, persistent verifier caches, and many messages per certificate. A candidate workload is periodic pseudonymous monitoring by privately provisioned devices reporting to one persistent collector. At one report per minute under an unchanged certificate, 120,324 messages accumulate in about 84 days. A replacement certificate starts a new amortization period.
6.5. Lifecycle and Deployment Conditions
A certificate binds an exact canonical ring: membership changes require a new authorization, while old certificates refer to the old ring unless that context is rejected. There is no built-in expiration or cryptographic revocation. An authenticated external rejection list may invalidate identifiers or ring versions and remove cache records. Storage eviction requires certificate re-verification before accepting compact packets. Online-key compromise permits further signing under that certificate. Rejection of one identifier applies only to that authorization. Long-term compromise exposes the linking secret and permits future authorizations.
Global tags link a registered key across rings and time. If a side channel identifies one tag, its entire recorded history becomes attributable. Global linking supports cross-context duplicate detection. A scoped extension using would require binding the scope in the statement, identifier, cache, and linking rule. MPC-friendly hashes, preprocessing-based MPC-in-the-head, Banquet, and VOLE-in-the-head provide alternative instantiation directions [22,23,37].
Analytical variants. A systematic key would use bits (1,026,467 bytes), subject to compatible syndrome-basis and trapdoor transformations and security analysis. An opening-only membership relation could omit the member-level PolarSig verification. Under the same layout, its 32-member proof would occupy 3,212,768 bytes. The member-level signature check establishes authorization under a registered verification key in addition to possession of the linking-secret opening.
7. Conclusions
We presented a linkable ring signature based on polar codes with cached anonymous authorization. A certificate binds a hidden member’s authorization signature, a global tag, and an independent online key. Public linear-map evaluation before hidden selection reduces the authorization circuit’s nonlinear cost, while certificate reuse removes the membership proof from subsequent online packets. For parameters selected against a 128-bit classical generic-attack target, the FS-ZKB++ instance provides a 98.52% proof-size reduction against the selected-matrix baseline for a 32-member ring and 807-byte cached online packets. The integrated prototype executes actual key generation, authorization, installation, and online signing and verification. Under the stated primitive assumptions and honest registration, the construction supports repeated anonymous authentication with independently verifiable messages in the classical random oracle model.
Supplementary Materials
The following supporting information can be downloaded at: https://www.mdpi.com/article/10.3390/math14213908/s1, Supplementary File S1: S1_Integrated_Polar_LRS_Prototype.zip. Source code, reproduction instructions, finite-length design parameters, generic-attack calculations, execution environment, raw measurements, and validation records for the complete authorization and online-authentication experiments.
Author Contributions
Conceptualization, Z.L.; methodology, Z.L. and J.L.; formal analysis, J.L.; validation, Q.L.; writing—original draft preparation, Z.L. and J.L.; writing—review and editing, Z.L., J.L. and Q.L. All authors have read and agreed to the published version of the manuscript.
Funding
This research was funded by the National Natural Science Foundation of China (U25A20543).
Data Availability Statement
All analytical expressions and parameters supporting the results are included in the article. The source code, finite-length design, attack-estimation scripts, and raw measurements supporting the integrated experiments are provided in Supplementary File S1.
Acknowledgments
During preparation and revision of this manuscript, the authors used OpenAI Codex (OpenAI; version 26.1007.21434; accessed September–October 2026) to assist with literature searches, checking analytical calculations, prototype implementation and testing, benchmark processing, editing English, and LaTeX. The authors reviewed and revised the assisted content, remain responsible for independently checking the assisted claims, references, calculations, and code, and accept full responsibility for the article.
Conflicts of Interest
The authors declare no conflicts of interest.
Abbreviations
The following abbreviations are used in this manuscript:
| LRS | Linkable ring signature |
| ROM | Random oracle model |
| MPC | Secure multiparty computation |
| FS | Fiat–Shamir |
| ZK | Zero knowledge |
| SC | Successive cancellation |
Appendix A. Security Experiments
Initialize as empty. records identity-labeled authorization recipients. All games use Algorithm A1 and independent classical random oracles. uses a complete certificate or the validated cache.
ANON enforces candidate corruption and identity-labeled authorization/signing restrictions through eligibility and oracle checks before and after the challenge. provides challenge messages. Its advantage is . Other advantages are winning probabilities in Algorithms A2 and A3.
| Algorithm A1 Common stateful game oracles |
|
| Algorithm A2 Unforgeability and linkability experiments |
|
comprises the common and random oracles. Malformed or unregistered inputs are rejected.
| Algorithm A3 Anonymity and non-frameability experiments |
|
References
- FIPS 204; Module-Lattice-Based Digital Signature Standard. National Institute of Standards and Technology: Gaithersburg, MD, USA, 2024. [Google Scholar] [CrossRef] [Scilit]
- FIPS 205; Stateless Hash-Based Digital Signature Standard. National Institute of Standards and Technology: Gaithersburg, MD, USA, 2024. [Google Scholar] [CrossRef] [Scilit]
- Alagic, G.; Bros, M.; Ciadoux, P.; Dang, Q.; Dang, T.H.; Kelsey, J.; Lichtinger, J.; Liu, Y.-K.; Miller, C.; Moody, D.; et al. Status Report on the Second Round of the Additional Digital Signature Schemes for the NIST Post-Quantum Cryptography Standardization Process; NIST IR 8610; National Institute of Standards and Technology: Gaithersburg, MD, USA, 2026. [Google Scholar] [CrossRef] [Scilit]
- Chang, S.-Y.; Khan, Q. Post-Quantum Cryptography in Networking Protocols: Challenges, Solutions, and Future Directions. Cryptography 2026, 10, 12. [Google Scholar] [CrossRef] [Scilit]
- Rivest, R.L.; Shamir, A.; Tauman, Y. How to Leak a Secret. In Advances in Cryptology—ASIACRYPT 2001; LNCS 2248; Springer: Berlin/Heidelberg, Germany, 2001; pp. 552–565. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Liu, J.K.; Wei, V.K.; Wong, D.S. Linkable Spontaneous Anonymous Group Signature for Ad Hoc Groups (Extended Abstract). In Information Security and Privacy—ACISP 2004; LNCS 3108; Springer: Berlin/Heidelberg, Germany, 2004; pp. 325–335. [Google Scholar] [CrossRef] [Scilit]
- Liu, X.; Wang, L.-P. A Postquantum Linkable Ring Signature Scheme from Coding Theory. Secur. Commun. Netw. 2023, 2023, 1794053. [Google Scholar] [CrossRef] [Scilit]
- Goel, A.; Green, M.; Hall-Andersen, M.; Kaptchuk, G. Efficient Set Membership Proofs using MPC-in-the-Head. Proc. Priv. Enhancing Technol. 2022, 2022, 304–324. [Google Scholar] [CrossRef] [Scilit]
- Xue, Y.; Lu, X.; Au, M.H.; Zhang, C. Efficient Linkable Ring Signatures: New Framework and Post-quantum Instantiations. In Computer Security—ESORICS 2024; LNCS 14985; Springer: Cham, Switzerland, 2024; pp. 435–456. [Google Scholar] [CrossRef] [Scilit]
- Courtois, N.; Finiasz, M.; Sendrier, N. How to Achieve a McEliece-Based Digital Signature Scheme. In Advances in Cryptology—ASIACRYPT 2001; LNCS 2248; Springer: Berlin/Heidelberg, Germany, 2001; pp. 157–174. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Debris-Alazard, T.; Sendrier, N.; Tillich, J.-P. Wave: A New Family of Trapdoor One-Way Preimage Sampleable Functions Based on Codes. In Advances in Cryptology—ASIACRYPT 2019; LNCS 11921; Springer: Cham, Switzerland, 2019; pp. 21–51. [Google Scholar] [CrossRef] [Scilit]
- Sendrier, N. Wave Parameter Selection. In Cryptology ePrint Archive; Paper 2023/588; 2023. Available online: https://eprint.iacr.org/2023/588 (accessed on 19 October 2026).
- Feneuil, T.; Joux, A.; Rivain, M. Syndrome Decoding in the Head: Shorter Signatures from Zero-Knowledge Proofs. In Advances in Cryptology—CRYPTO 2022; LNCS 13508; Springer: Cham, Switzerland, 2022; pp. 541–572. [Google Scholar] [CrossRef] [Scilit]
- Bultel, X.; Olivier-Anclin, C. On the Anonymity of Linkable Ring Signatures. In Cryptology and Network Security—CANS 2024; Springer: Singapore, 2024; pp. 212–235. [Google Scholar] [CrossRef] [Scilit]
- Tran, N.; Nguyen, K.; Liu, D.; Pieprzyk, J.; Susilo, W. Many-Time Linkable Ring Signatures. In Provable and Practical Security—ProvSec 2025; LNCS 16172; Springer: Singapore, 2025; pp. 3–22. [Google Scholar] [CrossRef] [Scilit]
- Arikan, E. Channel Polarization: A Method for Constructing Capacity-Achieving Codes for Symmetric Binary-Input Memoryless Channels. IEEE Trans. Inf. Theory 2009, 55, 3051–3073. [Google Scholar] [CrossRef] [Scilit]
- Tal, I.; Vardy, A. List Decoding of Polar Codes. IEEE Trans. Inf. Theory 2015, 61, 2213–2226. [Google Scholar] [CrossRef] [Scilit]
- Forghani, P.; Koochak Shooshtari, M.; Aref, M.R. PolarSig: An Efficient Digital Signature Based on Polar Codes. IET Commun. 2020, 14, 2889–2897. [Google Scholar] [CrossRef] [Scilit]
- Ishai, Y.; Kushilevitz, E.; Ostrovsky, R.; Sahai, A. Zero-Knowledge from Secure Multiparty Computation. In Proceedings of the 39th Annual ACM Symposium on Theory of Computing; ACM: New York, NY, USA, 2007; pp. 21–30. [Google Scholar] [CrossRef] [Scilit]
- Giacomelli, I.; Madsen, J.; Orlandi, C. ZKBoo: Faster Zero-Knowledge for Boolean Circuits. In 25th USENIX Security Symposium; USENIX Association: Berkeley, CA, USA, 2016; pp. 1069–1083. Available online: https://www.usenix.org/conference/usenixsecurity16/technical-sessions/presentation/giacomelli (accessed on 19 October 2026).
- Chase, M.; Derler, D.; Goldfeder, S.; Orlandi, C.; Ramacher, S.; Rechberger, C.; Slamanig, D.; Zaverucha, G. Post-Quantum Zero-Knowledge and Signatures from Symmetric-Key Primitives. In ACM SIGSAC Conference on Computer and Communications Security; ACM: New York, NY, USA, 2017; pp. 1825–1842. [Google Scholar] [CrossRef] [Scilit]
- Baum, C.; Delpech de Saint Guilhem, C.; Kales, D.; Orsini, E.; Scholl, P.; Zaverucha, G. Banquet: Short and Fast Signatures from AES. In Public-Key Cryptography—PKC 2021; LNCS 12710; Springer: Cham, Switzerland, 2021; pp. 266–297. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Baum, C.; Beullens, W.; Braun, L.; Delpech de Saint Guilhem, C.; Klooß, M.; Majenz, C.; Mukherjee, S.; Orsini, E.; Ramacher, S.; Rechberger, C.; et al. Shorter, Tighter, FAESTer: Optimizations and Improved (QROM) Analysis for VOLE-in-the-Head Signatures. In Advances in Cryptology—CRYPTO 2025; LNCS 16005; Springer: Cham, Switzerland, 2025; pp. 124–156. [Google Scholar] [CrossRef] [Scilit]
- Derler, D.; Ramacher, S.; Slamanig, D. Post-Quantum Zero-Knowledge Proofs for Accumulators with Applications to Ring Signatures from Symmetric-Key Primitives. In Post-Quantum Cryptography—PQCrypto 2018; Springer: Cham, Switzerland, 2018; pp. 419–440. [Google Scholar] [CrossRef] [Scilit]
- Fiat, A.; Shamir, A. How to Prove Yourself: Practical Solutions to Identification and Signature Problems. In Advances in Cryptology—CRYPTO ’86; LNCS 263; Springer: Berlin/Heidelberg, Germany, 1987; pp. 186–194. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Kulkarni, M.; Xagawa, K. Strong Existential Unforgeability and BUFF Securities of MPC-in-the-Head Signatures. In Cryptology ePrint Archive, Paper 2024/1069; 2024; revised 2025. Available online: https://eprint.iacr.org/2024/1069 (accessed on 19 October 2026).
- Don, J.; Fehr, S.; Majenz, C.; Schaffner, C. Security of the Fiat-Shamir Transformation in the Quantum Random-Oracle Model. In Advances in Cryptology—CRYPTO 2019; LNCS 11693; Springer: Cham, Switzerland, 2019; pp. 356–383. [Google Scholar] [CrossRef] [Scilit]
- Don, J.; Fehr, S.; Majenz, C.; Schaffner, C. Efficient NIZKs and Signatures from Commit-and-Open Protocols in the QROM. In Advances in Cryptology—CRYPTO 2022; LNCS 13508; Springer: Cham, Switzerland, 2022; pp. 729–757. [Google Scholar] [CrossRef] [Scilit]
- FIPS 202; SHA-3 Standard: Permutation-Based Hash and Extendable-Output Functions. National Institute of Standards and Technology: Gaithersburg, MD, USA, 2015. [Google Scholar] [CrossRef] [Scilit]
- Korada, S.B.; Urbanke, R. Polar Codes are Optimal for Lossy Source Coding. IEEE Trans. Inf. Theory 2010, 56, 1751–1768. [Google Scholar] [CrossRef] [Scilit]
- Crypto-TII. CryptographicEstimators, Version 2.1.1. Available online: https://github.com/Crypto-TII/CryptographicEstimators/releases/tag/v2.1.1 (accessed on 12 October 2026).
- May, A.; Sá Diogo, G. Multi-Instance Security Degradation of Code-Based KEMs. In Cryptology ePrint Archive; Paper 2026/517; 2026. Available online: https://eprint.iacr.org/2026/517. (accessed on 12 October 2026).
- Sendrier, N. Decoding One Out of Many. In Cryptology ePrint Archive; Paper 2011/367; 2011. Available online: https://eprint.iacr.org/2011/367 (accessed on 19 October 2026).
- Bardet, M.; Chaulet, J.; Dragoi, V.; Otmani, A.; Tillich, J.-P. Cryptanalysis of the McEliece Public Key Cryptosystem Based on Polar Codes. In Post-Quantum Cryptography—PQCrypto 2016; LNCS 9606; Springer: Cham, Switzerland, 2016; pp. 118–143. [Google Scholar] [CrossRef] [Scilit]
- Attema, T.; Fehr, S.; Klooß, M.; Resch, N. The Fiat-Shamir Transformation of (Γ1,…,Γμ)-Special-Sound Interactive Proofs. J. Cryptol. 2026, 39, 19. [Google Scholar] [CrossRef] [Scilit]
- Xue, Y. Post-Quantum-Linkable-Ring-Signature: Author Implementation. Proof-Size Reporting in examples/src/main.rs. Available online: https://github.com/yuxi16/Post-Quantum-Linkable-Ring-Signature (accessed on 6 October 2026).
- Katz, J.; Kolesnikov, V.; Wang, X. Improved Non-Interactive Zero Knowledge with Applications to Post-Quantum Signatures. In ACM SIGSAC Conference on Computer and Communications Security; ACM: New York, NY, USA, 2018; pp. 525–537. [Google Scholar] [CrossRef] [Scilit]

Disclaimer/Publisher’s Note: The statements, opinions and data contained in all publications are solely those of the individual author(s) and contributor(s) and not of MDPI and/or the editor(s). MDPI and/or the editor(s) disclaim responsibility for any injury to people or property resulting from any ideas, methods, instructions or products referred to in the content. |
© 2026 by the authors. Licensee MDPI, Basel, Switzerland. This article is an open access article distributed under the terms and conditions of the Creative Commons Attribution (CC BY) license.