


Abstract
Large organizations face a critical systems integration challenge when executing multiple concurrent security modernization programs. This paper examines the U.S. Department of Defense’s simultaneous implementation of three transformational initiatives—post-quantum cryptography (PQC) migration, Zero Trust Architecture (ZTA) deployment, and AI security assurance—each operating under separate governance structures, timelines, and compliance frameworks. Through systematic evidence synthesis of 59 sources (47 policy/standards documents and 12 performance benchmarks), we identify cross-program dependencies that create integration failures when programs operate in isolation. We propose a shared modernization substrate—a four-layer infrastructure architecture (Cryptographic Services, Identity Management, Analytics Pipeline, Policy Orchestration) that enables coordinated execution while preserving program independence. The framework addresses the fundamental systems challenge of achieving interoperability across programs with misaligned schedules and competing resource demands. We introduce a five-level Triad Convergence Maturity Model (TCMM) with operationalized indicators enabling repeatable organizational assessment. Illustrative application to three DoD modernization contexts demonstrates the framework’s ability to differentiate maturity levels. Performance analysis synthesizes published benchmark data: enterprise PQC latency overhead is modest (measured), while tactical environment estimates of 158–383% overhead are derived from benchmark extrapolation under packet-loss assumptions (modeled). Scenario modeling suggests that coordinated incident response through the substrate architecture could substantially reduce risk exposure windows compared to siloed approaches (modeled). The framework transforms fragmented program execution into synchronized systems modernization, offering practical guidance for chief information officers, program managers, and enterprise architects managing concurrent technology transitions.
1. Introduction
Organizations undertaking enterprise-wide technology modernization frequently encounter a systems integration challenge: multiple transformation programs, each justified independently, create unforeseen interdependencies when executed concurrently. This challenge intensifies when programs operate under separate governance structures, compete for shared resources, and follow misaligned timelines. The result is often integration failures, cost overruns, and degraded operational effectiveness—outcomes documented repeatedly in government and industry modernization efforts [1,2].
The U.S. Department of Defense (DoD) currently faces an acute instance of this challenge. Three major cybersecurity modernization programs are underway simultaneously:
- Post-Quantum Cryptography (PQC) Migration: Transitioning cryptographic infrastructure to quantum-resistant algorithms by 2030–2035, driven by the threat of future quantum computers breaking current encryption.
- Zero Trust Architecture (ZTA) Implementation: Deploying enterprise-wide continuous verification and least-privilege access controls by September 2027, replacing perimeter-based security models.
- AI Security Assurance: Establishing governance and technical controls for an expanding portfolio of AI-enabled capabilities, addressing adversarial manipulation and model integrity risks.
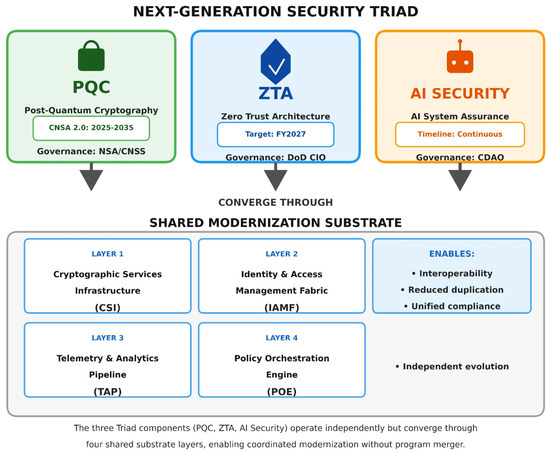
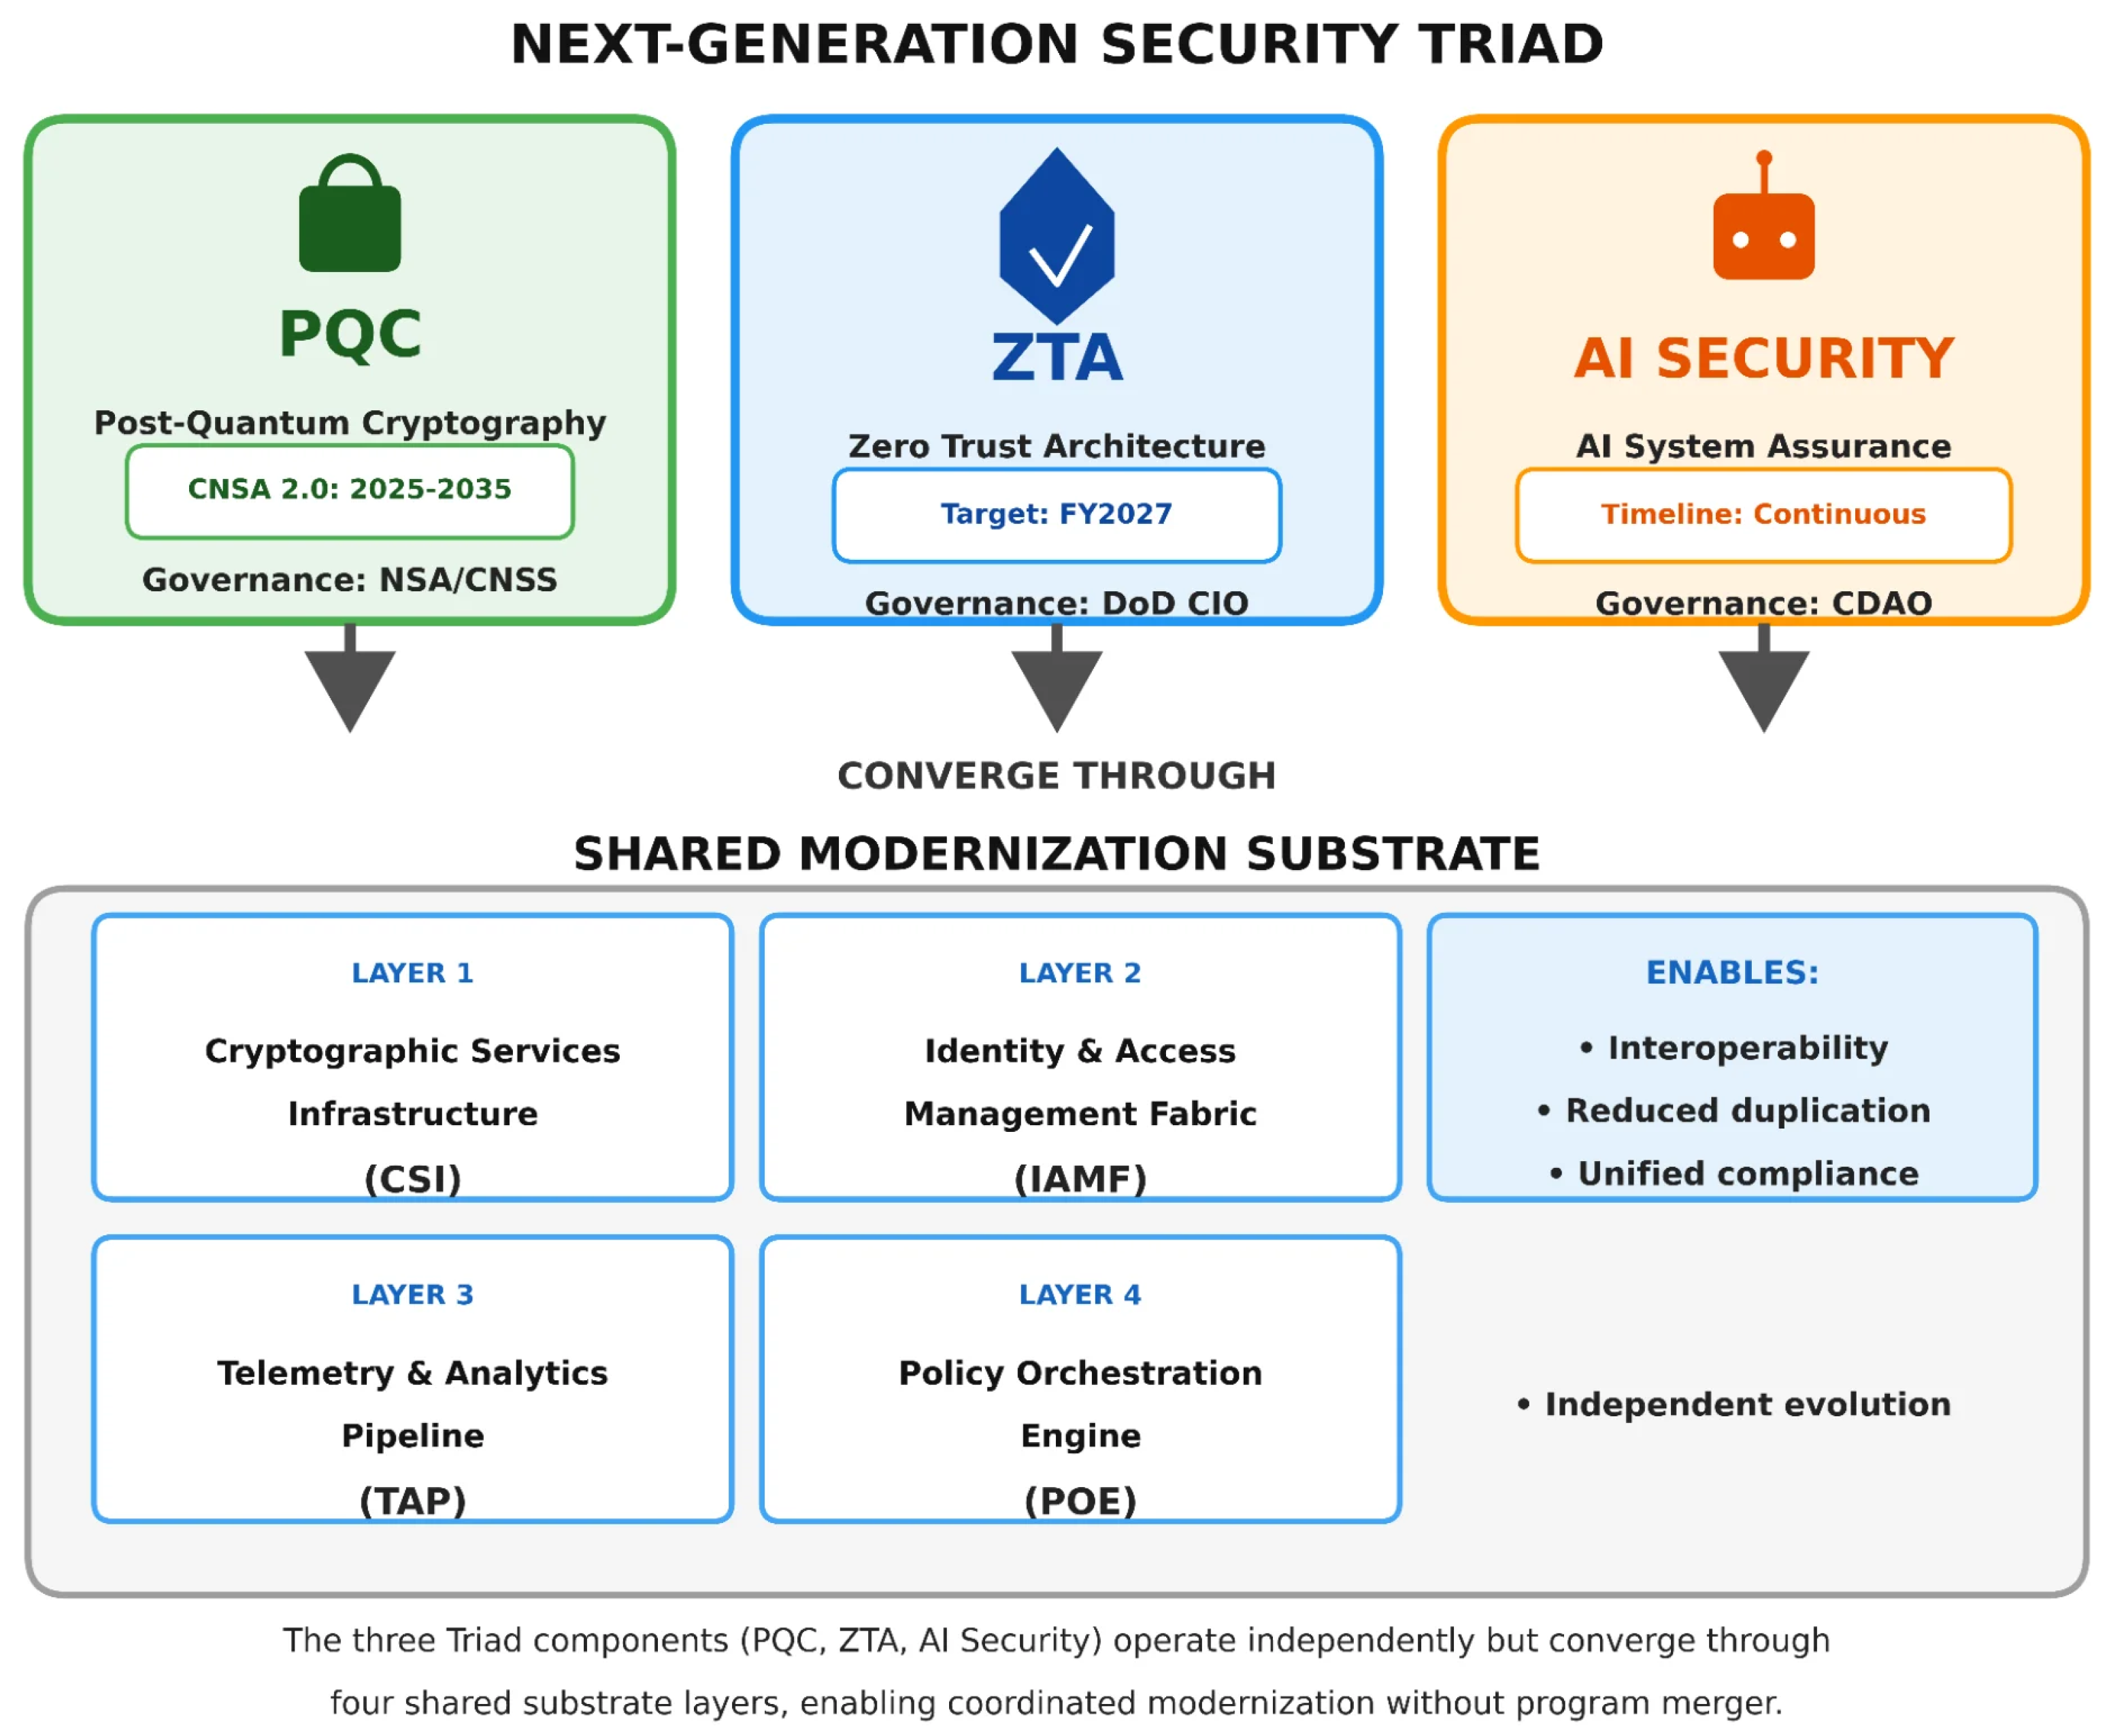
Together, these initiatives constitute what we term the Next-Generation Security Triad. Each program addresses a genuine and distinct threat: quantum computing threatens cryptographic foundations; sophisticated adversaries operating inside network perimeters undermine traditional trust models; adversarial machine learning attacks manipulate AI system outputs. The programs are individually necessary.
However, these programs are managed as independent initiatives with separate budget lines, governance committees, skill requirements, and compliance pathways. This fragmentation creates acute challenges for the personnel responsible for implementation. Chief Information Officers must reconcile competing modernization roadmaps. Program Management Offices struggle to sequence acquisitions when requirements create interdependencies. Authorizing Officials lack frameworks for assessing risk across all three domains simultaneously.
The conventional response—merge the programs—is impractical. Each program addresses fundamentally different threat models, requires distinct technical expertise, and operates under separate statutory authorities. Forced consolidation would likely impair all three efforts.
This paper proposes an alternative approach grounded in systems thinking: establish a shared modernization substrate—a common infrastructure foundation that all three programs build upon. Rather than forcing convergence at the program level, we enable integration at the infrastructure level. Each program retains its governance, timeline, and specialized focus while leveraging shared services that ensure interoperability, reduce duplication, and provide unified compliance visibility.
1.1. The Systems Integration Problem
The challenge addressed in this paper is fundamentally a systems integration problem rather than a purely technical one. Table 1 summarizes the synchronization challenge across the three programs.
Table 1.
Program synchronization challenge: misaligned governance and timelines.
The programs exhibit three categories of interdependencies that isolated execution cannot address:
Technical Dependencies: ZTA’s continuous authentication relies on cryptographic primitives that PQC migration will replace. If the underlying signatures and key exchanges become vulnerable to quantum attack, the entire Zero Trust verification chain collapses. Conversely, AI-based behavioral analytics that inform ZTA trust decisions introduce new attack surfaces that neither the PQC nor ZTA programs are chartered to address.
Resource Dependencies: All three programs compete for the same enterprise infrastructure—identity services, key management systems, network monitoring capabilities, and policy enforcement points. Uncoordinated deployment creates conflicting requirements and duplicated investments.
Timeline Dependencies: The ZTA deadline (September 2027) precedes full PQC deployment (2030–2035). Systems achieving ZTA compliance with classical cryptography will require rework when PQC mandates take effect. Similarly, AI capabilities deployed without adversarial robustness controls will require retrofitting as AI security requirements mature.
1.2. Contributions
This paper makes four contributions to the systems integration literature:
- Cross-program dependency analysis: Systematic identification and categorization of dependencies among three concurrent cybersecurity modernization programs, based on evidence synthesis of 47 policy and standards sources (Supplementary Materials File S2).
- Shared substrate architecture: A four-layer infrastructure framework (Cryptographic Services, Identity Management, Analytics Pipeline, Policy Orchestration) that enables coordinated program execution while preserving governance independence.
- Convergence maturity model: A five-level assessment framework with operationalized indicators enabling repeatable measurement of organizational progress toward integrated modernization.
- Performance characterization: Quantitative analysis of integration overhead and efficiency gains, derived from a synthesis of 12 benchmark studies (Supplementary Materials File S2).
The remainder of this paper is organized as follows. Section 2 provides background on the three modernization programs and their interdependencies. Section 3 describes the systematic evidence synthesis methodology. Section 4 presents the shared substrate architecture. Section 5 introduces the convergence maturity model. Section 6 presents performance analysis. Section 7 discusses the implications and limitations. Section 8 concludes.
2. Background: The Next-Generation Security Triad
2.1. Post-Quantum Cryptography Migration
The cryptographic algorithms protecting most digital communications today—RSA, elliptic curve cryptography, Diffie–Hellman key exchange—rely on mathematical problems that quantum computers could solve efficiently [3]. While cryptographically relevant quantum computers do not yet exist, the “harvest now, decrypt later” threat model motivates near-term migration: adversaries capturing encrypted data today could decrypt it once quantum capability matures [4].
The National Security Agency’s Commercial National Security Algorithm Suite 2.0 (CNSA 2.0) establishes phased transition milestones for national security systems (Table 2) [5,6]. For federal civilian agencies, OMB Memorandum M-23-02 mandates cryptographic inventory completion and migration planning, establishing deadlines for identifying vulnerable systems and prioritizing transition [7]; CISA provides complementary discovery and inventory guidance [8]. The National Institute of Standards and Technology (NIST) finalized three post-quantum standards in August 2024: ML-KEM for key encapsulation [9], ML-DSA for digital signatures [10], and SLH-DSA for stateless hash-based signatures [11].
Table 2.
CNSA 2.0 transition timeline for national security systems.
The systems integration challenge for PQC migration stems from the significantly larger key and signature sizes of post-quantum algorithms. Classical elliptic curve keys are 32 bytes; ML-KEM public keys are 1184–1568 bytes. Classical signatures are 64–256 bytes; ML-DSA signatures are 3309–4627 bytes. This 40–70× size increase affects every system that transmits cryptographic material—authentication protocols, certificate chains, secure channels—with cascading impacts on network bandwidth, latency, and storage.
2.2. Zero Trust Architecture Implementation
The DoD Zero Trust Strategy, released in November 2022, mandates enterprise-wide “Target Level” ZTA by 30 September 2027, with “Advanced Level” capabilities by 2032 [12,13]. This represents a fundamental shift from perimeter-based security (“trust but verify”) to continuous verification (“never trust, always verify”) [14].
ZTA implementation encompasses seven pillars: User, Device, Network/Environment, Application and Workload, Data, Visibility and Analytics, and Automation and Orchestration. Full implementation requires completion of 152 activities across these pillars (91 Target-level activities by FY2027, plus 61 Advanced-level activities by FY2032) [13].
The July 2025 Directive-Type Memorandum (DTM) 25-003 established the Chief Zero Trust Officer position, formalized governance through the DoD Zero Trust Executive Committee, and mandated Target-level ZTA implementation across all DoD information systems [15]. The November 2025 Zero Trust for Operational Technology Activities and Outcomes guidance extended ZTA mandates to control systems and industrial environments, introducing additional constraints around deterministic latency requirements [16].
ZTA’s integration challenges center on its dependencies. Continuous verification requires robust identity services—the DoD Public Key Infrastructure services millions of users across the enterprise [17]. Trust scoring requires reliable behavioral analytics. Most critically, ZTA assumes “cryptographic agility”—the ability to update cryptographic algorithms without architectural redesign [18]. If PQC migration and ZTA deployment proceed independently, systems may achieve ZTA compliance with cryptographic foundations that will require replacement within years.
2.3. AI Security and Assurance
AI systems introduce attack surfaces fundamentally different from traditional cybersecurity threats [19]. NIST AI 100-2e2025, published March 2025, provides a taxonomy of adversarial machine learning attacks including the following [20]:
- Training-time attacks: Data poisoning, model poisoning, and backdoor insertion that compromise models before deployment.
- Deployment-time attacks: Evasion attacks and adversarial examples that cause misclassification during inference.
- Supply chain attacks: Compromised pre-trained models or malicious code in machine learning libraries.
The Chief Digital and AI Office (CDAO) released the Responsible AI Toolkit in 2024, operationalizing DoD’s AI Ethical Principles [21]. DoD has initiated multiple generative AI pilot programs through the AI Rapid Capabilities Cell, reflecting significant investment in AI capability development [2,21].
The integration risk is acute. ZTA increasingly relies on AI-based behavioral analytics for trust scoring—User and Entity Behavior Analytics (UEBA) engines that detect anomalous access patterns. An adversary using adversarial ML techniques could manipulate these trust scores, effectively bypassing access controls without triggering alarms. Neither the ZTA program (focused on access architecture) nor the PQC program (focused on cryptographic algorithms) is chartered to address this vulnerability.
2.4. Related Work
Existing enterprise architecture frameworks address technology modernization but not the specific challenge of concurrent security program synchronization. The DoD Architecture Framework (DoDAF) provides standardized methods for enterprise architecture but lacks constructs for representing cryptographic transition states or AI assurance pipelines [22]. The Federal Enterprise Architecture Framework (FEAF) predates both PQC mandates and AI governance requirements [23].
Prior integration efforts have addressed pairwise combinations. The NSA Cybersecurity Reference Architecture incorporates Zero Trust principles and cryptographic services but does not address AI security. CISA’s Zero Trust Maturity Model includes cryptographic considerations but treats cryptographic agility as an assumed capability rather than a parallel modernization challenge [24]. NIST’s AI Risk Management Framework provides comprehensive AI governance but operates independently from cryptographic and network security frameworks [25].
The fundamental gap is the absence of a shared infrastructure layer that enables federated compliance across program boundaries. Current approaches assume either sequential modernization (one program completes before another begins), independent execution with post hoc integration, or programmatic merger that conflicts with distinct governance authorities. The shared substrate framework addresses this gap.
3. Methodology: Systematic Evidence Synthesis
3.1. Research Design and Contribution Type
This study makes two distinct contributions requiring different methodological approaches:
The methodology follows PRISMA 2020 reporting guidelines adapted for policy and standards synthesis [26]. This approach is appropriate because the research questions concern what is documented about modernization challenges and what requirements emerge from authoritative sources—not experimental validation of a deployed system. The prescriptive components (substrate architecture, TCMM) are derived artifacts requiring future operational validation.
Reproducibility Commitment: All evidence extraction decisions, source coding, benchmark data transformations, and TCMM scoring calculations are fully documented in the Supplementary Materials (Files S1–S3, and supporting documentation including PRISMA_Search_Strings.md, Codebook_S2_Extraction_Dataset.md, TCMM_Rubric_Definitions.md, and Assumptions_and_Model_Parameters.md) ) to enable independent verification and replication of the synthesis process.
3.2. Analytical Propositions
The research design is organized around four analytical propositions that structure the evidence synthesis. These propositions function as guiding assumptions for systematic evidence gathering rather than testable hypotheses requiring experimental validation. They establish the conceptual scope of the synthesis and provide organizing criteria for source selection and data extraction:
- AP1: Siloed modernization creates documented integration failures, cost growth, and compliance gaps.
- AP2: Cross-program dependencies exist among PQC, ZTA, and AI Security initiatives that isolated execution cannot address.
- AP3: Shared infrastructure approaches yield measurable efficiency gains over independent program execution.
- AP4: Published performance benchmarks can characterize integration requirements quantitatively.
These analytical propositions guided source selection (prioritizing documents that address program interactions) and data extraction (capturing metrics relevant to integration costs and benefits). They are not claims requiring proof but rather organizing frameworks that shaped the systematic review.
3.3. Search Strategy
Searches were executed between 15 January and 31 October 2025 across five source classes using the following databases and repositories:
- Government Oversight: GAO.gov report database, DoD Inspector General FOIA reading room (2020–2025);
- Standards Bodies: NIST CSRC publications, NSA Cybersecurity Guidance repository, IETF Datatracker (2020–2025);
- DoD Policy: DoD CIO website (dodcio.defense.gov), CDAO public releases (2020–2025);
- Congressional Analysis: Congressional Research Service reports accessed via official Congressional distribution and archived committee documentation (2021–2025);
- Performance Benchmarks: IEEE Xplore, ACM Digital Library, IACR ePrint Archive (2020–2025).
The primary search string for academic databases was: (“post-quantum” OR “PQC” OR “quantum-resistant”) AND (“zero trust” OR “ZTA”) AND (“performance” OR “latency” OR “benchmark”). For policy sources, targeted searches used program-specific terms (e.g., “CNSA 2.0,” “DTM 25-003,” “DoD Zero Trust Strategy”).
3.4. Eligibility Criteria
Inclusion criteria: (1) published 2020–2025; (2) addresses PQC, ZTA, or AI security in enterprise/government context; (3) contains quantitative metrics, normative requirements, or documented implementation outcomes; (4) available in English.
Exclusion criteria: (E1) no verifiable provenance (n = 8); (E2) no extractable quantitative or normative content (n = 11); (E3) superseded by newer version (n = 4); (E4) non-transferable to DoD context (n = 2).
3.5. Screening and Selection
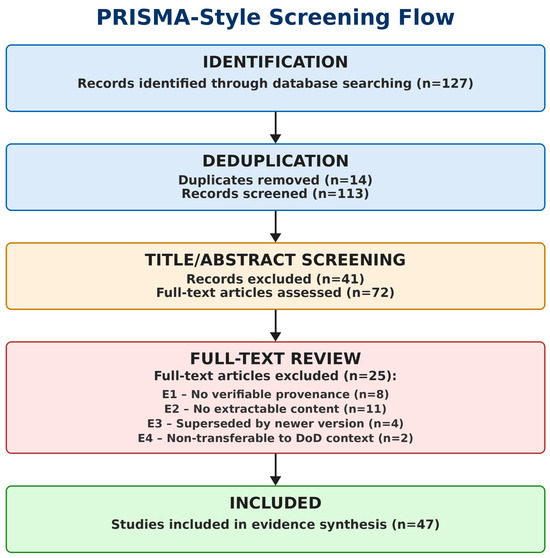
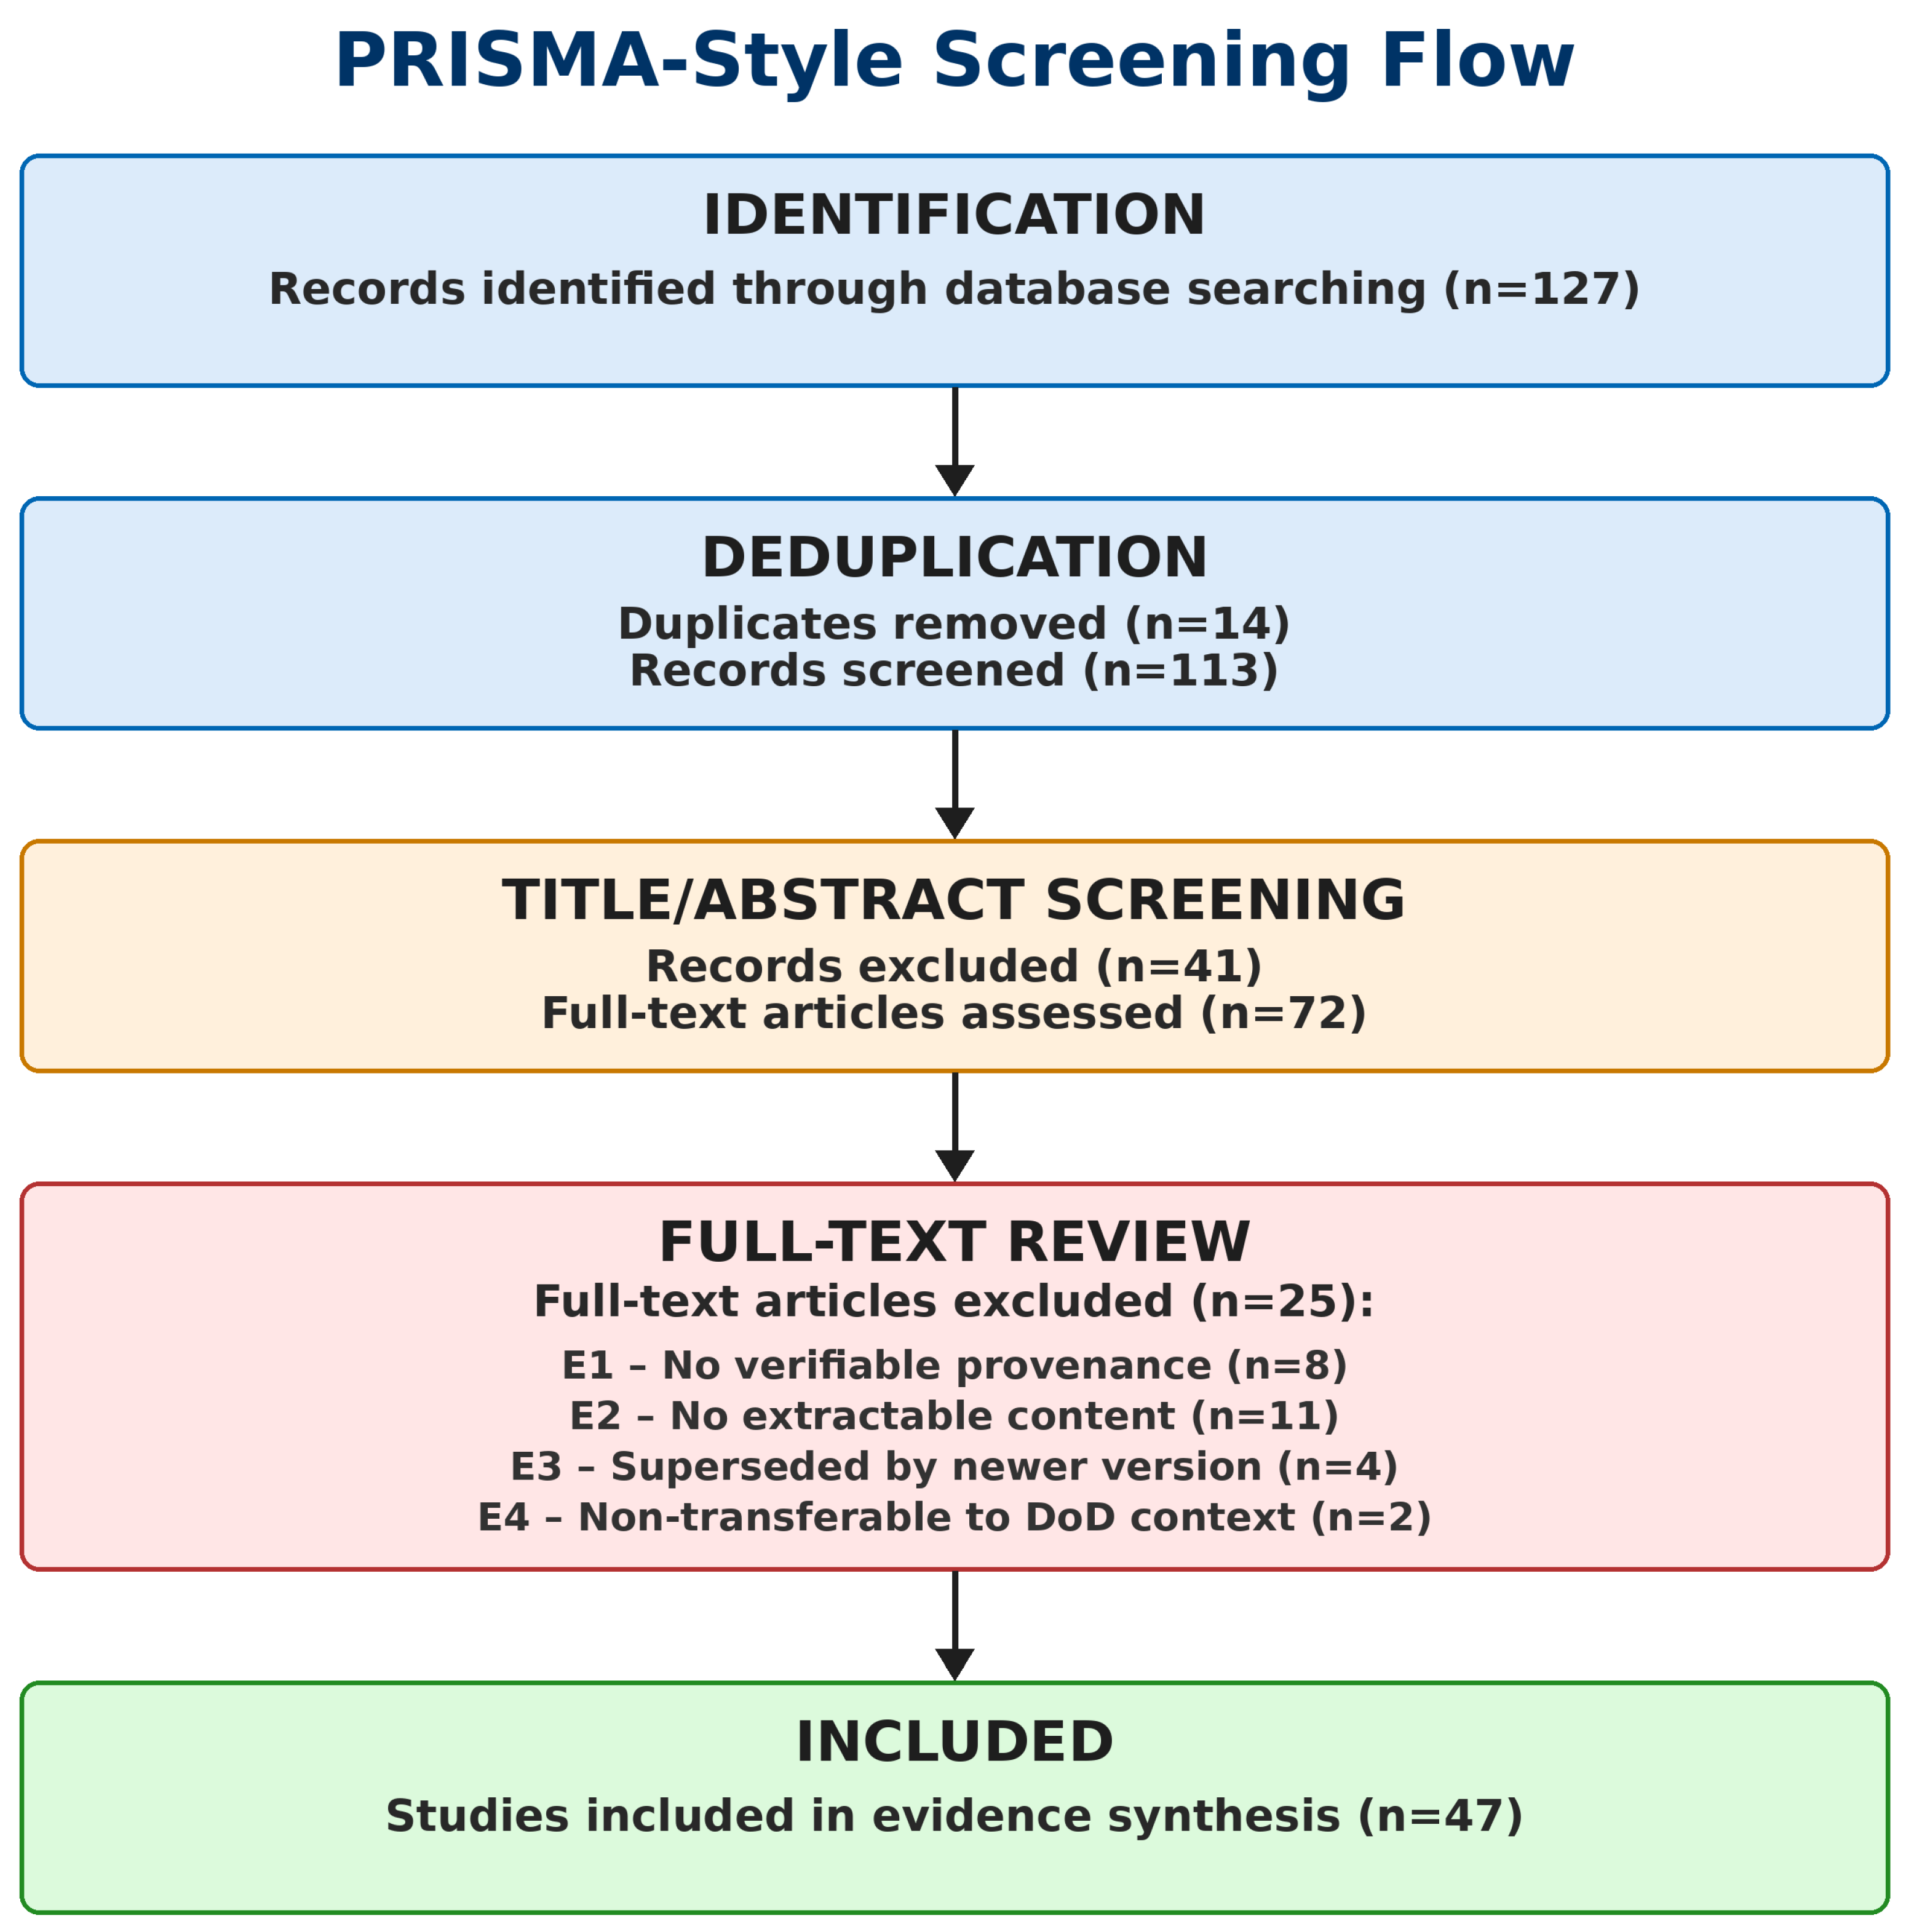
The initial identification yielded 127 potentially relevant records. After deduplication (14 removed) and screening against eligibility criteria, 84 documents underwent full-text review. The final corpus comprised 59 included sources: 47 policy/standards documents plus 12 performance benchmarks (Figure 1). The complete extraction dataset with all 59 sources is provided in the Supplementary Materials File S2.
Figure 1.
PRISMA-style evidence screening and selection flow.
3.6. Data Extraction and Coding
Each source was coded using a structured extraction template with the following fields: (1) source identifier and citation; (2) source type (policy/standard/benchmark/guidance); (3) confidence tier (A/B/C); (4) domain relevance (PQC/ZTA/AI Security/Cross-cutting); (5) claim supported (mapped to analytical propositions AP1–AP4); (6) extracted metrics with units, experimental conditions, and context; (7) limitations noted by original authors.
3.7. Quality Appraisal
Sources were classified into three confidence tiers based on methodological rigor and authority (Table 3).
Table 3.
Evidence confidence tier rubric.
3.8. Requirements-to-Architecture Traceability
To demonstrate how the synthesized evidence informed architectural design decisions, Table 4 maps key extracted requirements to their corresponding substrate layer(s) and TCMM indicators. This traceability matrix addresses the interpretive gap between the evidence synthesis and prescriptive framework development.
Table 4.
Requirements-to-architecture traceability matrix.
5. Triad Convergence Maturity Model
To provide organizations with a measurable path toward integrated modernization, we introduce a five-level Triad Convergence Maturity Model (TCMM). The TCMM defines maturity levels and their associated indicators; the Triad Convergence Maturity Score (TCMS) provides the quantitative scoring formula for assessment. Each level includes operationalized indicators and assessment criteria supporting repeatable scoring.
Scope and Intent: The TCMM is a descriptive assessment framework designed to characterize an organization’s current integration state and identify capability gaps. It is not a predictive model—higher TCMS scores indicate greater integration maturity but do not guarantee better security outcomes or lower costs. The framework enables structured self-assessment and progress tracking; predictive validity would require longitudinal validation beyond this initial development.
5.1. Maturity Levels
Table 8 presents the five maturity levels with measurable indicators.
Table 8.
Triad convergence maturity model: levels and indicators.
5.2. Scoring Methodology
The Triad Convergence Maturity Score (TCMS) provides quantitative assessment. Let , , and denote domain subscores (0–1 scale) computed as weighted averages of indicator scores within each domain. Let denote the cross-domain integration subscore. The composite TCMS is
where controls the relative weight of domain-specific capabilities versus cross-domain integration. The default weighting uses , ensuring that organizations cannot achieve high maturity through domain excellence alone—cross-domain integration is structurally required. TCMS values map to levels: Level 0 (<0.20), Level 1 (0.20–0.39), Level 2 (0.40–0.59), Level 3 (0.60–0.79), Level 4 (≥0.80).
Weighting Sensitivity:Table 9 presents the TCMS scores and resulting maturity levels across the sensitivity range .
Table 9.
TCMS Sensitivity Analysis Across Weighting Parameter .
Cases A and C demonstrate level stability across all tested weightings. Case B exhibits appropriate sensitivity near the Level 1/2 boundary (threshold 0.40), reflecting its strong ZTA domain score but weak cross-domain integration.
Missing Data Rules: When indicator evidence is unavailable, (1) if <50% of indicators within a domain are scorable, the domain subscore is marked “insufficient evidence” and excluded from TCMS calculation; (2) if ≥50% of indicators are scorable, missing indicators are scored as 0 (conservative assumption); (3) assessment requires documentary evidence (policy documents, architecture diagrams, audit reports, or attestations) for each scored indicator—self-reported status without documentation scores 0.
Evidence Requirements: Each indicator requires minimum Tier B evidence (authoritative guidance or technical documentation). Tier C sources alone are insufficient. For quantitative indicators (e.g., “≥50% crypto centralized”), assessors must document the measurement methodology and data source.
Assessor Guidance and Bias Control: Single-rater assessment from public documentation introduces potential bias. Mitigation measures include (1) documenting evidence sources and scoring rationale for each indicator to enable independent verification; (2) defaulting to lower scores when the evidence is ambiguous; (3) using consistent indicator definitions across all assessed cases. The complete operationalized rubric—including measurement methods, minimum evidence requirements per indicator, and indicator-level scoring with citations for each case study—is provided in the Supplementary Materials (TCMM_Rubric_Definitions.md).
5.3. Case Study Application
To demonstrate the framework’s ability to differentiate modernization contexts, we applied TCMS scoring to three publicly documented DoD modernization contexts using evidence from the synthesis corpus (Table 10).
Table 10.
TCMS case study results summary.
Case A: DISA Thunderdome [32] represents DISA’s Zero Trust security initiative, which integrates identity management, software-defined networking, and security analytics. Evidence sources include DISA public briefings and the DoD Zero Trust Portfolio Management Office documentation.
Case B: DON Flank Speed [33] represents the Department of the Navy’s enterprise cloud and collaboration environment. Evidence sources include Navy CIO public presentations and GAO assessments of Navy IT modernization [2].
Case C: Legacy Enclave represents a composite profile of pre-modernization environments based on GAO high-risk assessments [1], documenting fragmented IT management across DoD components.
The three cases yielded TCMS scores spanning the maturity spectrum, with 0.25+ gaps between adjacent cases exceeding the 0.20 level threshold width, demonstrating the framework’s ability to distinguish meaningfully different modernization states. Note that this preliminary application employed single-rater scoring; future validation should incorporate multi-rater assessment with inter-rater reliability measures.
5.4. Related Work Comparison
Table 11 provides a structured comparison demonstrating why existing frameworks cannot be extended to address the concurrent modernization challenge.
Table 11.
Related work comparison: existing frameworks vs. shared substrate.
6. Performance Analysis
This section presents the performance characterizations derived from the evidence synthesis. The enterprise latency values in Table 12 are measured values drawn directly from peer-reviewed benchmark studies. The tactical environment values are modeled estimates derived by applying packet-loss extrapolation to measured enterprise baselines; they should be interpreted as indicative projections, not measured operational data. Subsequent subsections present qualitative characterizations synthesized from the adversarial ML literature and a modeled scenario illustrating potential orchestration benefits based on industry incident response benchmarks.
Table 12.
Authentication latency: classical vs. post-quantum cryptography (synthesized from benchmark studies) a.
6.1. PQC Integration Overhead
The synthesis of the benchmark studies reveals significant performance implications for uncoordinated PQC deployment [34,35,36,37]. Table 12 presents authentication handshake latency across network conditions.
Sensitivity Analysis: Table 13 presents tactical latency projections for ML-KEM-768 across parameter variations. The base case (310 ms) is the measured value from [35]; the sensitivity rows are model projections using the calibrated formula to explore parameter variations.
Table 13.
Tactical latency sensitivity analysis: ML-KEM-768 configuration.
Key Finding: In the specific LAN/TLS 1.3 benchmark conditions of [34,35,36], the incremental enterprise PQC handshake latency is single-digit milliseconds (3–10 ms overhead). In tactical networks with packet loss, the measured and extrapolated values indicate PQC latency increases of 158–383%, due to fragmentation and retransmission—the effects are dominated by the payload size under loss and not by cryptographic computation. The enterprise baselines are drawn from TLS 1.3 handshake measurements in the cited benchmark studies; the tactical values derive from measurements under 5% loss conditions. The large cryptographic payloads (up to 6 KB for a complete handshake) span multiple network packets; the loss of any fragment triggers full retransmission, which dominates latency under lossy conditions. Scope caveat: Results may differ with other implementations, certificate chains, hardware, or handshake modes; these values represent specific benchmark conditions and not universal predictions.
Systems Implication: Without substrate-level coordination (CSI layer), ZTA deployments in tactical environments will fail latency requirements when PQC mandates take effect. The CSI layer enables adaptive algorithm selection, pre-shared key modes for constrained environments, and session resumption—optimizations that individual application teams cannot implement consistently.
Operational Technology Latency Constraints
The performance implications become critical when considering Operational Technology (OT) environments. The DoD Zero Trust for OT guidance [16] distinguishes between the Operational Layer and the Process Control Layer, each with distinct latency tolerances:
- Operational Layer (SCADA servers, historians, HMIs): These supervisory systems interact with human operators on timescales of seconds. Authentication latencies of 100–340 ms (as shown in Table 12 for tactical environments) are acceptable, as they represent a small fraction of typical human–machine interaction cycles.
- Process Control Layer (PLCs, RTUs, actuators): Industrial control loops typically execute on cycles of 10–100 ms, with safety-critical loops often requiring sub-20 ms determinism [16,28]. A PQC handshake latency of 310–580 ms would span 15–30 control cycles, causing the following:
- –
- Missed control deadlines leading to open-loop operation;
- –
- Oscillatory behavior, as controllers lose synchronization;
- –
- Safety system trips due to watchdog timeouts;
- –
- In extreme cases, physical damage to equipment or processes.
This bifurcation has direct implications for the Shared Modernization Substrate. The CSI layer cannot apply uniform cryptographic policies across all environments. Instead, it must maintain environment-aware profiles:
- Enterprise Profile: Full ML-KEM + ML-DSA hybrid handshakes; latency budget 50–100 ms.
- Tactical Profile: Hybrid handshakes with session resumption; latency budget 200–500 ms.
- OT Operational Profile: Standard PQC with extended session validity; latency budget 100–300 ms.
- OT Process Control Profile: PSK mode with PQC-protected key distribution; real-time latency budget < 20 ms for ongoing operations, with PQC overhead amortized to key establishment phases.
The Process Control Profile represents a necessary compromise: the control-plane communications use pre-shared keys (meeting real-time constraints), while the key distribution infrastructure uses full PQC (protecting against “harvest now, decrypt later” attacks on key material). This layered approach ensures quantum resistance for long-term secrets while preserving operational safety.
Table 14 summarizes the environment-specific requirements that CSI must enforce.
Table 14.
OT environment requirements by class.
6.2. Adversarial Impact on Trust Scoring
Table 15 presents the detection performance for behavioral analytics under adversarial attack, comparing standard implementations against hardened configurations [19,38].
Table 15.
Behavioral analytics detection under adversarial conditions (qualitative characterization from the literature synthesis) b.
Key Finding: Standard behavioral analytics can suffer substantial degradation under adversarial attack—the literature consistently reports significant detection capability reductions under sophisticated evasion techniques, with some controlled experiments demonstrating near-complete evasion. Adversarially hardened models incorporating defensive techniques (adversarial training, input validation, ensemble methods) demonstrate substantially better resilience across studies.
Systems Implication: ZTA programs deploying AI-based trust scoring without adversarial robustness controls create exploitable vulnerabilities. The TAP layer’s adversarial input detection and model integrity monitoring are not optional enhancements—they are structural necessities for ZTA security.
6.3. Orchestration Efficiency
Table 16 compares incident response metrics for siloed versus substrate-orchestrated approaches, based on a decomposition model of response time components.
Table 16.
Incident response: siloed vs. substrate-orchestrated (modeled scenario) c.
Response Time Decomposition Model: Industry incident response studies decompose total response time into sequential phases. We model the siloed response time as
Based on SANS IR Survey 2023 findings [39], we estimate the relative phase contributions for organizations with siloed security tools: telemetry collection (15%), cross-system correlation (25%), initial triage (15%), escalation to appropriate team (10%), cross-team coordination (25%), and containment action (10%). The substrate architecture affects specific phases:
- The TAP layer reduces through unified telemetry (estimated 80% reduction in correlation time).
- The POE layer eliminates and through automated orchestration (100% reduction).
- Pre-authorized playbooks reduce (estimated 50% reduction).
Key Finding: The decomposition model suggests a substrate-orchestrated response could reduce the active response time by approximately 60% compared to siloed approaches. The largest gains come from eliminating cross-team coordination delays (35% of siloed response time) through POE’s automated orchestration. This estimate is model-derived and requires operational validation.
Systems Implication: The POE layer’s automated cross-domain response eliminates coordination delays. When the TAP layer detects an anomaly, the POE can simultaneously trigger IAMF credential suspension and CSI session rekeying without manual escalation between program teams.
7. Discussion
7.1. Implications for Enterprise Architecture
The shared substrate framework offers several implications for organizations managing concurrent modernization programs:
Infrastructure-level integration preserves program independence: Organizations need not choose between siloed execution (with integration failures) and forced program merger (with governance conflicts). The substrate provides a middle path—shared infrastructure services that enable coordination while preserving program autonomy.
Cross-program dependencies require explicit architectural treatment: Dependencies among concurrent programs do not resolve through parallel execution. The PQC-ZTA-AI Security dependencies identified in this study would create failures regardless of individual program success. Architectural mechanisms (the four substrate layers) are necessary to address dependencies that program governance cannot.
Maturity assessment enables incremental progress: The five-level TCMM provides organizations with actionable intermediate targets. An organization at Level 0 (Fragmented) can progress to Level 1 (Aware) through dependency analysis and roadmap alignment, without requiring full infrastructure deployment.
Categorization of Findings by Evidence Type: To strengthen scientific rigor, the findings presented in this paper can be categorized by their evidence basis:
- Evidence-supported conclusions (directly derived from synthesis corpus): Cross-program dependencies exist and are documented in authoritative sources (AP2); siloed modernization creates documented integration failures (AP1); published benchmarks characterize enterprise PQC latency overhead at 3–10 ms (AP4).
- Model-derived estimates (extrapolations requiring operational validation): Tactical network PQC latency overhead of 158–383%; incident response time reduction of approximately 60% through orchestration; adversarial robustness characterizations.
- Interpretive constructs (derived artifacts requiring future validation): The four-layer substrate architecture; the TCMM maturity levels and scoring methodology; the requirements-to-architecture traceability mappings.
7.2. Limitations
Several limitations constrain interpretation of these findings:
Synthesis rather than experimentation: Performance characterizations derive from the synthesis of published benchmarks and not direct experimentation in operational environments. While benchmark normalization and projection follow established practices, operational validation is required.
Benchmark heterogeneity (threat to validity): The performance values in Table 12 and Table 15 synthesize the results from studies conducted across different hardware platforms, software stacks, network configurations, and tuning parameters. These results are not directly comparable in a strict experimental sense. The normalized values presented are approximate central tendencies; confidence intervals are not implied unless explicitly computed in the source studies. Tactical network estimates (158–383% overhead) are derived from extrapolation models applied to enterprise measurements—they represent plausible projections under the stated assumptions (5% packet loss, 1500-byte MTU) and not measured operational values. Readers should interpret these figures as indicative of the relative magnitude rather than precise operational predictions.
DoD-specific context: The framework addresses DoD modernization programs with specific governance structures, timelines, and compliance requirements. Generalization to other organizational contexts requires adaptation.
Evolving standards: PQC standards, ZTA guidance, and AI security frameworks continue to evolve. The substrate architecture accommodates this evolution through its abstraction layers, but specific interface definitions will require updates as standards mature.
Implementation complexity: The substrate architecture introduces infrastructure that must itself be developed, deployed, and maintained. Organizations must weigh integration benefits against substrate implementation costs.
Single-rater scoring: The TCMM case study application employed single-rater scoring based on publicly available documentation. Formal validation of the maturity model requires multi-rater assessment with inter-rater reliability statistics to establish measurement validity.
TCMM scope and validation status: The Triad Convergence Maturity Model is presented as a descriptive assessment framework for characterizing the current organizational state, not as a predictive model for forecasting modernization outcomes. The illustrative case study demonstrates the framework’s ability to differentiate maturity levels but does not establish predictive validity (i.e., that higher TCMS scores correlate with better security outcomes or lower integration costs). Establishing predictive validity would require longitudinal studies tracking organizations through modernization programs, which is beyond the scope of this initial framework development. Users should apply TCMM for structured assessment and gap identification and not for predicting program success probabilities.
7.3. Future Work
Priority areas for future research include the following:
- Pilot implementation with a DoD pathfinder organization to validate performance projections under operational conditions.
- Extension of the maturity model to address coalition partner interoperability and cross-organizational integration.
- Development of training curricula aligned with DoD Cyber Workforce Framework competencies.
- Investigation of substrate applicability to commercial enterprise security modernization.
- Multi-rater validation of the TCMM scoring methodology with inter-rater reliability assessment (e.g., Cohen’s ) to establish the measurement validity.
8. Conclusions
Large organizations executing concurrent security modernization programs face a systems integration challenge: programs justified independently create unforeseen interdependencies that isolated execution cannot address. This paper examined the DoD’s simultaneous implementation of post-quantum cryptography migration, Zero Trust Architecture deployment, and AI security assurance—three programs with distinct governance, timelines, and technical requirements that nonetheless share critical dependencies.
Through a systematic evidence synthesis of 59 sources (47 policy/standards documents and 12 benchmarks; full corpus in the Supplementary Materials File S2), we identified cross-program dependencies in three categories: technical dependencies (ZTA cryptographic foundations, AI-based trust scoring), resource dependencies (shared infrastructure and personnel), and timeline dependencies (ZTA deadlines preceding PQC completion).
The shared modernization substrate provides an architectural response to these dependencies. Four infrastructure layers—Cryptographic Services (CSI), Identity and Access Management (IAMF), Telemetry and Analytics (TAP), and Policy Orchestration (POE)—enable coordinated program execution while preserving governance independence. The substrate transforms fragmented modernization into synchronized capability delivery.
The Triad Convergence Maturity Model provides organizations with measurable progress indicators, enabling incremental advancement from fragmented execution (Level 0) through awareness (Level 1), alignment (Level 2), integration (Level 3), to adaptive operation (Level 4). Case study application demonstrated the framework’s ability to differentiate meaningfully across three DoD modernization contexts.
Performance analysis, synthesizing published benchmarks and scenario modeling, indicates that uncoordinated execution carries significant costs: modest enterprise PQC overhead (measured) but projected 158–383% latency overhead in tactical networks under packet-loss conditions (modeled); substantial detection degradation for trust scoring without TAP adversarial controls (synthesized from the literature); and extended incident response windows without POE orchestration (scenario-modeled). These costs are potentially avoidable through substrate-enabled coordination.
The framework offers practical guidance for CIOs, program managers, and enterprise architects facing concurrent technology transitions. The core insight is broadly applicable: when multiple transformation programs share dependencies, infrastructure-level integration enables coordination that program-level governance cannot achieve. The shared substrate transforms competing programs into complementary capabilities.
Supplementary Materials
The following supporting information can be downloaded at: https://www.mdpi.com/article/10.3390/systems14030233/s1.
Funding
This research received no external funding.
Data Availability Statement
This study follows a systematic evidence synthesis approach to develop and parameterize the proposed PQC–ZTA–AI triad convergence architecture and maturity model. To support reproducibility, we provide as Supplementary Materials the complete bibliographic corpus, screening decisions, extracted quantitative and qualitative fields, and the computation steps used to derive all synthesized tables and the Triad Convergence Maturity Score (TCMS). Specifically: (1) Search Strategy and Screening Records (Supplementary Materials File S1). Exact search strings, databases/sources, date ranges, and inclusion/exclusion criteria consistent with the PRISMA flow in Section 3. For each screened record: screening stage outcomes, exclusion reason codes, and final inclusion status. Search strategy details are documented in docs/PRISMA_Search_Strings.md. (2) Evidence Extraction Dataset (Supplementary Materials File S2). Machine-readable dataset containing all included sources (Tier A/B/C) and extracted fields (algorithm parameters, protocol context, performance metrics, environment descriptors). Each quantitative field includes units and measurement context. Schema and controlled vocabularies are documented in docs/Codebook_S2_Extraction_ Dataset.md. (3) Maturity Model Scoring Inputs (Supplementary Materials File S3). Per-dimension raw scores for each case, missing-data handling flags, computed TCMS outputs, and sensitivity parameters. Rubric definitions and scoring rules are documented in docs/TCMM_Rubric_ Definitions.md. (4) Analytic Workflow (code/reproduce_tables.py). Self-contained Python (version 3.10+) script that ingests the extraction dataset and reproduces Table 6, Table 7, Table 8, Table 9 and Table 10. Dependencies are listed in code/requirements.txt. All model parameters and assumptions are documented in docs/Assumptions_and_ Model_Parameters.md. The dataset preserves the original reporting context and includes normalization/compatibility flags for subset analyses. All modeled estimates are explicitly labeled with corresponding parameter values. Availability: Supplementary Materials are provided with this manuscript as a compressed archive (supplementary_materials.zip).
Conflicts of Interest
The author declares no conflicts of interest.
References
- U.S. Government Accountability Office. High-Risk Series: Heightened Attention Could Save Billions More; GAO-25-108125; U.S. Government Accountability Office: Washington, DC, USA, 2025. Available online: https://www.gao.gov/products/gao-25-108125 (accessed on 4 January 2026).
- U.S. Government Accountability Office. Information Technology: DOD Annual Assessment; GAO-25-107649; U.S. Government Accountability Office: Washington, DC, USA, 2025. Available online: https://www.gao.gov/products/gao-25-107649 (accessed on 4 January 2026).
- Chen, L.; Jordan, S.; Liu, Y.; Moody, D.; Peralta, R.; Perlner, R.; Smith-Tone, D. Report on Post-Quantum Cryptography; NIST IR 8105; National Institute of Standards and Technology: Gaithersburg, MD, USA, 2016. [Google Scholar] [CrossRef] [Scilit]
- Mosca, M.; Piani, M. Quantum Threat Timeline Report 2024; Global Risk Institute: Toronto, ON, Canada, 2024; Available online: https://globalriskinstitute.org/publication/quantum-threat-timeline-report/ (accessed on 4 January 2026).
- National Security Agency. Commercial National Security Algorithm Suite 2.0 (CNSA 2.0). NSA Cybersecurity Advisory, 2022. Available online: https://media.defense.gov/2022/Sep/07/2003071834/-1/-1/0/CSA_CNSA_2.0_ALGORITHMS_.PDF (accessed on 4 January 2026).
- National Security Agency. CNSA 2.0 and Quantum Computing FAQ, Version 2.1. 2024. Available online: https://media.defense.gov/2022/Sep/07/2003071836/-1/-1/0/CSI_CNSA_2.0_FAQ_.PDF (accessed on 4 January 2026).
- Office of Management and Budget. Memorandum M-23-02: Migrating to Post-Quantum Cryptography; Office of Management and Budget: Washington, DC, USA, 2022. Available online: https://www.whitehouse.gov/wp-content/uploads/2022/11/M-23-02-M-Memo-on-Migrating-to-Post-Quantum-Cryptography.pdf (accessed on 4 January 2026).
- Cybersecurity and Infrastructure Security Agency. Post-Quantum Cryptography Initiative. 2024. Available online: https://www.cisa.gov/quantum (accessed on 4 January 2026).
- National Institute of Standards and Technology. Module-Lattice-Based Key-Encapsulation Mechanism Standard; FIPS 203; National Institute of Standards and Technology: Gaithersburg, MD, USA, 2024. [Google Scholar] [CrossRef] [Scilit]
- National Institute of Standards and Technology. Module-Lattice-Based Digital Signature Standard; FIPS 204; National Institute of Standards and Technology: Gaithersburg, MD, USA, 2024. [Google Scholar] [CrossRef] [Scilit]
- National Institute of Standards and Technology. Stateless Hash-Based Digital Signature Standard; FIPS 205; National Institute of Standards and Technology: Gaithersburg, MD, USA, 2024. [Google Scholar] [CrossRef] [Scilit]
- Department of Defense Chief Information Officer. DoD Zero Trust Strategy; DoD CIO: Washington, DC, USA, 2022. Available online: https://dodcio.defense.gov/Portals/0/Documents/Library/DoD-ZTStrategy.pdf (accessed on 4 January 2026).
- Department of Defense Chief Information Officer. DoD Zero Trust Capability Execution Roadmap, Version 1.1; DoD CIO: Washington, DC, USA, 2024. Available online: https://dodcio.defense.gov/Portals/0/Documents/Library/ZT-ExecutionRoadmap-v1.1.pdf (accessed on 4 January 2026).
- Rose, S.; Borchert, O.; Mitchell, S.; Connelly, S. Zero Trust Architecture; NIST SP 800-207; National Institute of Standards and Technology: Gaithersburg, MD, USA, 2020. [Google Scholar] [CrossRef] [Scilit]
- Department of Defense. Directive-Type Memorandum (DTM) 25-003: Implementing the DoD Zero Trust Strategy; Washington Headquarters Services: Washington, DC, USA, 2025; Available online: https://www.esd.whs.mil/Portals/54/Documents/DD/issuances/dtm/DTM%2025-003.PDF?ver=i2DzVamcFpNhvo-L7dDeUQ%3D%3D (accessed on 4 January 2026).
- Department of Defense Chief Information Officer. Zero Trust for Operational Technology Activities and Outcomes; DoD CIO: Washington, DC, USA, 2025. Available online: https://dodcio.defense.gov/Portals/0/Documents/Library/ZT-OperationalTechnologyActivitiesOutcomes.pdf (accessed on 4 January 2026).
- Department of Defense Chief Information Officer. DoD Identity, Credential, and Access Management (ICAM) Strategy; DoD CIO: Washington, DC, USA, 2020. Available online: https://dodcio.defense.gov/Portals/0/Documents/Cyber/ICAM_Strategy.pdf (accessed on 4 January 2026).
- National Institute of Standards and Technology. Transition to Post-Quantum Cryptography Standards; NIST IR 8547; National Institute of Standards and Technology: Gaithersburg, MD, USA, 2024. [Google Scholar]
- Biggio, B.; Roli, F. Wild Patterns: Ten Years After the Rise of Adversarial Machine Learning. Pattern Recognit. 2018, 84, 317–331. [Google Scholar] [CrossRef] [Scilit]
- Vassilev, A.; Oprea, A.; Fordyce, A. Adversarial Machine Learning: A Taxonomy and Terminology of Attacks and Mitigations; NIST AI 100-2e2025; National Institute of Standards and Technology: Gaithersburg, MD, USA, 2025. [Google Scholar] [CrossRef] [Scilit]
- Chief Digital and Artificial Intelligence Office. Responsible AI Strategy and Implementation Pathway. 2024. Available online: https://media.defense.gov/2022/Jun/22/2003022604/-1/-1/0/Department-of-Defense-Responsible-Artificial-Intelligence-Strategy-and-Implementation-Pathway.PDF?utm_source=chatgpt.com (accessed on 4 January 2026).
- Department of Defense. DoD Architecture Framework (DoDAF), Version 2.02; Washington Headquarters Services: Washington, DC, USA, 2010. [Google Scholar]
- Office of Management and Budget. Federal Enterprise Architecture Framework, Version 2; Office of Management and Budget: Washington, DC, USA, 2013. [Google Scholar]
- Cybersecurity and Infrastructure Security Agency. Zero Trust Maturity Model, Version 2.0. April 2023. Available online: https://www.cisa.gov/zero-trust-maturity-model (accessed on 4 January 2026).
- National Institute of Standards and Technology. AI Risk Management Framework 1.0; NIST AI 100-1; National Institute of Standards and Technology: Gaithersburg, MD, USA, 2023. [Google Scholar]
- Page, M.J.; McKenzie, J.E.; Bossuyt, P.M.; Boutron, I.; Hoffmann, T.C.; Mulrow, C.D.; Shamseer, L.; Tetzlaff, J.M.; Akl, E.A.; Brennan, S.E.; et al. The PRISMA 2020 Statement: An Updated Guideline for Reporting Systematic Reviews. BMJ 2021, 372, n71. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Stebila, D.; Fluhrer, S.; Gueron, S. Hybrid Key Exchange in TLS 1.3. IETF Internet-Draft (Work in Progress), Draft-ietf-tls-Hybrid-Design-12. January 2025. Available online: https://datatracker.ietf.org/doc/draft-ietf-tls-hybrid-design/ (accessed on 4 January 2026).
- Stouffer, K.; Pillitteri, V.; Lightman, S.; Abrams, M.; Hahn, A. Guide to Operational Technology (OT) Security; NIST SP 800-82 Revision 3; National Institute of Standards and Technology: Gaithersburg, MD, USA, 2023. [Google Scholar] [CrossRef] [Scilit]
- Schwabe, P.; Stebila, D.; Wiggers, T. ML-KEM for TLS 1.3. IETF Internet-Draft (Work in Progress), Draft-ietf-tls-mlkem-05. November 2025. Available online: https://datatracker.ietf.org/doc/draft-ietf-tls-mlkem/ (accessed on 4 January 2026).
- Rescorla, E. The Transport Layer Security (TLS) Protocol Version 1.3. RFC 8446. August 2018. Available online: https://www.rfc-editor.org/rfc/rfc8446 (accessed on 4 January 2026).
- Kwiatkowski, K.; Kampanakis, P.; Westerbaan, B.; Stebila, D. X25519Kyber768Draft00 Hybrid Post-Quantum Key Agreement. IETF Internet-Draft (Work in Progress), Draft-tls-Westerbaan-xyber768d00-03. March 2024. Available online: https://datatracker.ietf.org/doc/draft-tls-westerbaan-xyber768d00/ (accessed on 4 January 2026).
- Defense Information Systems Agency. Thunderdome: DISA’s Zero Trust Security Initiative. 2024. Available online: https://www.waru.edu/sites/default/files/2024-11/DAU%20Sero%20Trust%20%20Thunderdome%20%2020241119_0.pdf (accessed on 4 January 2026).
- Department of the Navy Chief Information Officer. DON’s Flank Speed Service Sets New Standard for Zero Trust in DOD. 2024. Available online: https://www.doncio.navy.mil/ContentView.aspx?ID=18012 (accessed on 4 January 2026).
- Paquin, C.; Stebila, D.; Tamvada, G. Benchmarking Post-Quantum Cryptography in TLS. In Post-Quantum Cryptography; Springer: Cham, Switzerland, 2020; pp. 72–91. [Google Scholar] [CrossRef] [Scilit]
- Sikeridis, D.; Kampanakis, P.; Devetsikiotis, M. Post-Quantum Authentication in TLS 1.3: A Performance Study. In Proceedings of the Network and Distributed System Security Symposium (NDSS), San Diego, CA, USA, 23–26 February 2020. [Google Scholar] [CrossRef] [Scilit]
- Kampanakis, P.; Sikeridis, D.; Devetsikiotis, M. Post-Quantum TLS Performance. IACR ePrint 2020/071. Available online: https://eprint.iacr.org/2020/071 (accessed on 4 January 2026).
- Stebila, D.; Mosca, M. Post-Quantum Key Exchange for the Internet and the Open Quantum Safe Project. In Selected Areas in Cryptography; Springer: Cham, Switzerland, 2022. [Google Scholar] [CrossRef] [Scilit]
- Apruzzese, G.; Laskov, P.; Tastemirova, A. SoK: The Impact of Unlabelled Data in Cyberthreat Detection. In 2022 IEEE 7th European Symposium on Security and Privacy (EuroS&P); IEEE: Piscataway, NJ, USA, 2023. [Google Scholar]
- SANS Institute. SANS 2023 Incident Response Survey; SANS Institute: North Bethesda, MD, USA, 2023. [Google Scholar]
- IBM Security. Cost of a Data Breach Report 2024; IBM Corporation: Armonk, NY, USA, 2024. [Google Scholar]

Disclaimer/Publisher’s Note: The statements, opinions and data contained in all publications are solely those of the individual author(s) and contributor(s) and not of MDPI and/or the editor(s). MDPI and/or the editor(s) disclaim responsibility for any injury to people or property resulting from any ideas, methods, instructions or products referred to in the content. |
© 2026 by the author. Licensee MDPI, Basel, Switzerland. This article is an open access article distributed under the terms and conditions of the Creative Commons Attribution (CC BY) license.