


Abstract
A Security Operation Center (SOC) is a security control center for monitoring, detecting, analyzing, and responding to cybersecurity threats. PT (Perseroan Terbatas) Non-Bank Financial Company (NBFC) has implemented an SOC to secure its information systems, but challenges remain to be solved. These include the absence of impact analysis on financial and regulatory requirements, cost, and effort estimation for recovery; established Key Performance Indicators (KPIs) and Key Risk Indicators (KRIs) for monitoring security controls; and an official program for insider threats. This study evaluates SOC effectiveness at PT NBFC using the ISO 27005:2018 and NIST SP 800-30 frameworks. The research results in a proposed SOC assessment framework, integrating risk assessment, risk treatment, risk acceptance, and monitoring. Additionally, a maturity level assessment was conducted for ISO 27005:2018, NIST SP 800-30, and the proposed framework. The proposed framework achieves good maturity, with two domains meeting the target maturity value and one domain reaching level 4 (Managed and Measurable). By incorporating domains from both ISO 27005:2018 and NIST SP 800-30, the new framework offers a more comprehensive risk management approach, covering strategic, managerial, and technical aspects.
1. Introduction
In the era of increasing digitalization, information security is becoming an increasingly important issue to be tackled, and every company, both large and small, must be able to protect their information systems from external attacks that can have negative impacts in terms of financial losses and reputational damage. Non-bank financial companies are one type that have a high risk of information security threats, considering that they obtain funding from other financial institutions to support economic growth; thus, they must have an effective strategy to protect their assets and infrastructure. According to data from the Indonesian Cyber Security Landscape in 2023 in Figure 1, attacks on organizational information systems amounted to 403,990,813 anomalies, with the highest traffic occurring in August with a total of 78,464,385 anomalies and the lowest occurring in November with a total of 19,296,439 anomalies. Unfortunately, these kinds of activities absolutely have risks and consequences that negatively impact device and network performance, theft of sensitive and secret data, reputation damage, and trust toward the organization [1].
Figure 1.
Traffic anomaly attacks in Indonesia [1].
Furthermore, from Figure 1, it was revealed that the Cyber Contact Center Team at BSSN (Badan Siber dan Sandi Negara) sent around 1762 notifications, and the results of the Classification of Top 5 Incident Indications are presented in detail in Figure 2, namely, Traffic Anomaly with as many as 858, Data Breach with 268, Web Defacement with 172, Sensitive Data Exposure with 113, and Malicious Software with 104 [1].
Figure 2.
Notification Percentages Based on Incident Indication Classification [1].
One solution that is widely used by companies to overcome information security threats to cyberattacks is to build a Security Operation Center (SOC), a typical kind of security control center that focuses on monitoring, detection, analysis, and rapid response to cybersecurity threats. An SOC also aims to protect organizations from any cyberattacks that can harm assets, reputation, and business [2]. Thus, a well-designed SOC can help organizations maintain their security posture, mitigate risks, and respond quickly to security incidents [3]. It is also responsible for cybersecurity incident management, cyberattack detection, continuous and protective security monitoring, log and event management, coordination, and investigation [4]. Thus, having an SOC provides huge benefits for cybersecurity in companies, especially in providing centralized, continuous security monitoring and response [5]. In terms of people, the formation of an SOC can resolve the challenge of the low availability of cybersecurity experts through recruiting, training, and preserving them for better growth so that their skills and experience can match those of the parent company [5]. In terms of process, it also can form an efficient and effective framework, both in terms of manpower and finances [5]. Technologically, it can balance the availability of existing technological infrastructure within a company so that it can be adjusted according to the company’s cybersecurity needs [5]. Although SOCs have become an important part of companies’ information security strategies, there has not been much research evaluating the effectiveness of SOCs in addressing information security threats as there is no unified theoretical model or even agreed metric for whether it correlates with business resilience as a tool of centric evaluation or even improves security outcomes in outcome-centric studies. Previous research on SOCs has been conducted in several countries, but little work has been performed in the Indonesia context, especially in non-bank financial companies. Information technology in Indonesia is undergoing rapid development, so the risk of threats is increasing, and research therefore needs to be conducted to evaluate the effectiveness of SOCs in strategic management in overcoming threats holistically.
The company used as the object of the research is PT NBFC (Non-Bank Financial Company), which functions as an agency whose activities are related to collecting funds from the public by issuing securities then distributing them to finance investment companies that need loans [6]. Interestingly, it has implemented an SOC for its system security but still has problems, namely, not having a process for analyzing the impact on Financial and Regulatory Requirements as well as calculating the costs and efforts required for recovery on detected events/incidents. Unfortunately, there are no Key Performance Indicators (KPIs) or Key Risk Indicators (KRIs) either, which are set by management to monitor the effectiveness of physical access controls and compliance with applicable standards. Also, it does not yet have an official program related to detecting and preventing insider threats within the organization, a watchlist process, or additional monitoring of employees who resign, especially those who have the potential to become insider threats. Essentially, in this case, there is a security and compliance review process carried out on third parties, both onsite and offsite, but there is no full integration between File Integrity Monitoring (FIM) and SIEM (Security Information and Event Management) solutions to detect unauthorized changes to audit logs.
The company currently uses a solution system to analyze the incident trends but does not yet have analytical capabilities to process those incident data as the impact analysis of incident reports does not consider financial and regulatory aspects. It also does not analyze incident data regularly and continually to identify trends, threat patterns, attack types, or key areas that need special consideration and attention. Lastly, in their simple scanning process, there is no Business Continuity Plan (BCP) testing calendar that includes fire, earthquake, and other disaster simulations for each critical process and system listed in the Business Impact Analysis (BIA) linking SOC inputs to processes and outcomes with respect to the contingency plan and dynamic capability of the organization. According to these problems, the real use case of cybersecurity that occurs at PT NBFC can be seen in Figure 3, which explains that the attacks or insecurity in the system occur when users use work email for personal matters, and a breach occurs when they log into a pawnshop account on a device that has no endpoint security and is at risk of malware. Then, the user may open targeted phishing email links, installing apk files, which are not in the Play Store, and as a result their data may be exposed externally on the Deep Web or even the Dark Web. The next problem is that some users indicated that they share passwords with others, do not change their passwords regularly, use them repeatedly on public Wi-Fi, and fail to diversify their passwords, which increases susceptibility of MTM attacks. On certain occasions, some also leave their PCs or laptops unlocked, which may result in the worst-case scenario of illegal access to office and personal data.
Figure 3.
Real cybersecurity use case at PT NBFC.
1.1. Research Gap
Although the increasing role of SOCs in cyber risk management has great significance, the literature on SOC assessment has largely been focused on the implementation of different individual standards or frameworks. Popular standards like ISO/IEC 27005 [7] and NIST SP 800-30 [8] are primarily applied for information security risk management, and there has been very little research published that has combined these two frameworks into a single and coherent process for SOC assessment in detail. Most of the literature works have focused on either risk identification and analysis or control assessment, and there has been little effort to seamlessly tie the result of risk assessment with that of capability or maturity assessment of the SOC. Moreover, there has been little empirical research published related to the role of SOCs in risk management for non-bank financial institutions, especially for developing nations like Indonesia. Most of the studies have been focused on banking institutions or overall information security management systems (ISMSs), and there has been little understanding related to the role of SOCs, how they manage risk, and where they need to improve their processes in specific sectors. In addition, most previous research on SOC-related issues has never integrated risk assessments and maturity evaluations. In current practices, most research on maturity evaluation focuses on the definition of organizational capacity based on maturity models. Less attention has been paid to the study of concrete risk evaluation results based on the predefined ISO/IEC 27005 and NIST SP 800-30 frameworks and even less to the results of such frameworks in the improvement of maturity-related areas in an SOC. Therefore, the current research aims to provide practical applications of the integration of the ISO/IEC 27005 and NIST SP 800-30 frameworks in an operational SOC of a non-bank financial organization in Indonesia, together with the usage of maturity evaluation, focusing on the improvement of SOC-related practices.
1.2. Significance of Study
This research holds importance from both theoretical and practical perspectives as it can contribute positively to the information security and SOC literature by containing an analytical insight with a case study appraisal of an ISO/IEC 27005 and NIST SP 800-30 framework combination. It could be understood in the context that most research conducted on SOC risk management discusses its findings from a conceptual standpoint or in some cases adhering solely to one framework. This research will prove that more than one established framework or combinations thereof can be applied in an organizational SOC context, as such an approach will contain all elements of empirical appraisal. Additionally, it will provide an in-depth study of an underexplored area in social sciences, that of non-bank financial institutions in Indonesia, by providing concrete and empirical evidence on the way SOC risk management can performed in an organizational context that differs from banking institutions. From a practical standpoint, it also provides technical elements of appraisal that will allow information security experts, as well as organizational managers, to focus on more informed methods of risk management. Moreover, within this research, the technical evidence can act as a reference point in that it will contain all elements of the empirical appraisal to prevent misinterpretation and misrepresentation, enabling informed decision making that aligns with best practices and standards.
2. Literature Review
2.1. Integration of Landscape Finance and Non-Finance in Sustainable Landscape Management
In a sustainable management plan, the landscapes of finance and non-finance are the two key fields that achieve economic, ecological, and social balance. The first refers to the use of new financial tools such as green bonds, blended finance, and results-based mechanisms to finance investments that align with sustainable development goals (SDGs) and ecosystem restoration [9,10]. Thus, key barriers to the use of landscape finance are small-scale producers’ limited access to financial products due to unsuitable loan terms, collateral requirements, and transaction costs [11]. Various schemes have been established to overcome these barriers such as payment for ecosystem services (PES) and integrated landscape funds, which have been able to significantly improve climate finance in some regions [10,12]. In addition, the application of FinTech within the economic ecosystem has improved the transparency and efficiency of fund distribution. Interestingly, international trends suggest that climate finance is likely to reach USD 1.46 trillion by 2022, with rapid growth in developed and developing countries altogether, although challenges are still being encountered in international flows of finance, as evidenced in China, where only 2% of finance flows are international [12].
In contrast, the non-finance setting focuses on governance and multi-stakeholder collaboration in landscape management, government, private sector, and society-inclusive governance that takes a focal role in crafting an evident regulatory environment such as the use of blockchain technology for sustainable supply chain management [13]. Digital transformation has also entered the picture by adopting artificial intelligence (AI), big data, and digital payment systems, which accelerate financial inclusion, especially in developing countries with mobile money systems. Further, from a socio-ecological standpoint, the landscape approach balances biodiversity conservation, food security, and human well-being, as documented in case studies within Southeast Asia, where agroforestry integration increased agricultural productivity by 30% [9,10]. The convergence of landscape finance and non-finance is realized by incentive policies consisting of environmental standards, cooperative platforms connecting investors and restoration practitioners, and performance measures that combine economic and ecological criteria. Thus, the existing literature emphasizes the requirement for a system-based approach merging financial tools with technological innovation and participatory governance to achieve an expanded scale of impact.
2.2. Existing Approaches in SOC Assessment
Many studies related to information system security assessment have been conducted previously such as a recent study by Agyepong et al. (2023) [14] that provides valuable insights by introducing the SOC Analyst Assessment Method (SOC-AAM). This research evaluates SOC analysts’ performance in handling cyberattacks through a systematic method by offering structured guidelines for assessing the quality of incident analysis and reports. SOC-AAM was tested in two SOCs and demonstrated its effectiveness, though its applicability to other SOC environments remains a limitation. Further research is needed to adapt the method to different organizational contexts and operational needs. On the other hand, Mughal (2022) [3] provides a different perspective by focusing on building and securing modern SOCs. His study emphasizes an integrated approach combining people, processes, and technology for effective cyber threat detection and response. Key metrics such as incident response time, Mean Time to Detect (MTTD), and Mean Time to Respond (MTTR) are highlighted as essential performance indicators. Therefore, this study lacks specificity regarding industry-specific requirements and emerging cybersecurity technologies, which may impact SOC effectiveness over time. Additional studies have contributed to SOC assessment methodologies and cybersecurity frameworks. Lubis et al. (2020) [15] presented an SOC information system for a car repair company by identifying weaknesses in domain analysis and stressing the importance of long-term structural changes for security integration.
Interestingly, Forsberg & Frantti (2023) [16] proposed a framework to create SOC performance metrics that addresses the gap in customized evaluation methods and improves threat detection capabilities. On the other hand, Kurii & Opirskyy (2022) [17] analyzed NIST SP 800-53 and ISO/IEC 27001, concluding that while both frameworks complement each other, ISO 27001 is preferable for certification, whereas NIST 800-53 strengthens security controls beyond ISO’s scope. Other relevant studies include Azinheira et al. (2023) [18], who assessed cybersecurity in SMEs through a mapping methodology aligned with ISO 27001:2013, and Nugraha & Sembodo (2024) [19], who applied the KAMI (Keamanan Informasi) index to measure ISMS maturity, also proposing a model for Industry 4.0 environments. Furthermore, Taborda et al. (2021) [20] introduced a dynamic cybersecurity model based on ISO 27032:2012 for higher education institutions (IES), while Meher (2021) [21] explored the use of the NIST framework for threat management in recruitment environments. In addition, Saeed et al. (2023) [22] proposed a Cyber Threat Intelligence (CTI) framework featuring a knowledge base, detection model, and visualization dashboard. Meanwhile, Dosari & Fetais (2023) [23] emphasized the need for adaptable IT risk management frameworks for SMEs, and Kamil et al. (2023) [24] investigated ISO/IEC 27001’s legitimacy by highlighting the importance of stakeholder knowledge in its effective implementation. Finally, Kure et al. (2022) [25] developed an integrated cybersecurity risk management (i-CSRM) framework that leverages decision support and machine learning for predicting cybersecurity risks. Overall, while these studies provide a strong foundation for SOC assessment and development, they also pinpoint the need for further refinement in methodology, industry-specific adaptations, and alignment with emerging threats and technologies. In this research, ISO 27005:2018 and NIST SP 800-30 are applied to assess the SOC system at PT NBFC, with the goal of refining existing assessment approaches and providing practical recommendations for improving SOC effectiveness with respect to the non-bank financial sector.
2.3. Frameworks Used
2.3.1. ISO/IEC 27005
ISO/IEC 27005:2018 is a framework that describes risk management methodologies wherein risk management is one of the key concepts specifically for identifying risks (Section 6) and then combines them with the risks potentially faced by organizations. Simply said, this standard consists of 55 pages and can be applied to all types of organizations comprehensively and directly [7]. It is part of the ISO 27000-series family, which includes guidelines for the implementation of an information security management system (ISMS). It is an international standard that provides guidelines for information security risk management to build knowledge concepts, models, and processes to assist implementation by focusing on a risk management approach. The tasks in this case relate to the identification, assessment, and prioritization of risks carried out in the form of an endless iterative process consisting of phases which, if applied correctly, enable improvements in decision making and performance [26]. There are six main steps in ISO/IEC 27005 that must be implemented, namely [27], (1) the process of communicating risk; (2) characteristics of the system or determining the context; (3) the risk assessment process, which consists of two sub-processes: (a) risk analysis and (b) risk evaluation; (4) the risk treatment process; (5) the risk acceptance process; and (6) monitoring risk management and review processes, as can be seen in Figure 4.
Figure 4.
ISO 27005:2018.
2.3.2. NIST CICIF
Moreover, the NIST Critical Infrastructure Cybersecurity Improvement Framework aims to assist critical infrastructure operators in identifying and developing cybersecurity risk guidelines. In short, it is a conceptual framework focusing on structuring and categorizing incident-related information by highlighting the description, consequences, and impacts. It also involves a series of informative cybersecurity assumptions, activities, outcomes, and references presented in several critical infrastructure scenarios [28]. It emphasizes the semantic consistency and comparison of situations during and after incidents take place to support proper governance within the organization. This basic structure consists of four elements: functions, categories, subcategories, and informative references. Functions organize basic cybersecurity activities at the highest level, followed by subdivisions called categories, which are then divided into subcategories that are specific outcomes of the technical and management activities to be implemented [28]. These functions can be seen in Table 1 [21].
Table 1.
NIST functions.
An explanation of each NIST function is as follows:
- Identify: This function develops an organizational understanding for managing security risks. It seeks to cover systems, people, assets, and resources.
- Protect: This role is responsible for developing and implementing the necessary protections to ensure that the service continues to operate. This aims to limit cybersecurity events.
- Detect: This function aims to develop and implement the necessary controls to identify the occurrence of cybersecurity events.
- Respond: This function searches for and implements appropriate activities to perform actions when a cybersecurity incident is detected.
- Recover: This function seeks to carry out activities and maintain a resilience plan to restore services that are out of service due to a cybersecurity incident.
2.3.3. NIST SP 800-30
Primarily, NIST is a standard developed by the National Institute of Standards and Technology, and unlike the previous, NIST SP 800-30 Revision 1 presents a methodology that can be used operationally that has consistent and comprehensive information security for policy making and structured asset models and provides the ability for different risk producers to apply security information, contributing significantly to conducting risk assessments. NIST Special Publication (SP) 800-30r1 provides step-by-step guidance for conducting risk assessments of federal information systems and organizations directly, strengthening the guidance of NIST SP 800-39, which provides guidance for integration by identifying specific risk factors to holistically monitor an ongoing basis so that organizations can determine whether risks have increased to an unacceptable level (exceeding the organization’s risk tolerance) and different actions should be taken. The first emphasizes measurement and analysis, while the latter is related to decision making and accountability within the risk management lifecycle. For instance, SP 800-30 identifies a threat source then assesses its likelihood and impact by producing a risk rating, while SP 800-39 determines the response and allocates proper resources. The stages of activities in conducting risk management using the NIST SP 800-30r1 framework can be seen in Figure 5 [8].
Figure 5.
NIST SP 800-30r1 framework.
2.4. Comparison of SOC Implementations
The deployment of SOC technologies in Indonesia has achieved mixed success in different sectors, in which the examples of successful implementations should include strong management support, seamless integration of SOC with existing systems, and the use of knowledge management accordingly to improve the effectiveness of incident response. In contrast, failures often occurred due to insufficient integration of security into the application development lifecycle and the lack of a user-centric security approach. Table 2 shows the categorization of the successes or failures in relation to SOC implementation in Indonesia based on insights of recent academic work.
Table 2.
Summary of SOC implementations in Indonesia.
There are several critical factors that contribute to the success of an SOC application, including strong executive support to ensure that the SOC solution is effectively integrated with existing security systems. In addition, utilizing a knowledge management system can reduce incident response times and improve workplace efficiency. However, unsuccessful SOC adoption reveals significant drawbacks, and one of the main reasons for failure is the lack of security integration throughout the application development lifecycle, which, in the end, leads to vulnerabilities and compromises the security of users. In addition, the lack of user-centered design of security features leads to poor user experience, which is manifested in applications where users report security issues and access difficulties [33]. Recent research also confirms that successful SOC adoption requires organizational commitment and alignment with operational processes. Adhering to secure design principles in application development and promoting user-centered security measures are important steps to improve the effectiveness of SOCs in general and in Indonesia specifically.
3. Research Methodology
3.1. Research Systematics
The research stages describe the methods used in the research. The research stages that took place in this study can be seen in Figure 6.
Figure 6.
Research stages.
As shown in Figure 6 above, there are several research stages, first related to problem identification, which involves not only listing the symptom but also distinguishing its root causes and defining the gap between the expected and actual condition. Often, non-banking industry identifies problems based on performance and market signals after deviation occurs while banking through risk and compliance perspective before failure occurs. Next, a literature study was conducted, namely, the process of searching for related sources from the internet as references and benchmarks. This was useful for the next phase, related to the analysis of current conditions of the market and relevant organizations from various industries to elucidate the outlook of PT NBFC. Its purpose is not merely descriptive but also diagnostic, with the goal of investigating existing practices. The result is critical for the formation of a new framework by preventing purely normative or speculative models to avoid overgeneralization and conceptual overload. Supposedly, the framework is an enabler that shift complexity into action and clarity, and it is not a constraint that cannot be explained and accidental. Lastly, the conclusions and suggestions, as the logical syntheses of theory and evidence, were derived from alignment between the observed problems and proposed framework elements through the integration of structured consequences data into risk governance process to improve the quality of decision making.
3.2. Case Study Description
This research used a single-case study methodology to investigate the application of an integrated framework of information security risk assessment in a real-world scenario. It was carried out in a non-bank financial company in Indonesia referred to as PT NBFC to avoid revealing any compromises and to preserve its confidentiality. As a non-bank financial institution, it handles a substantial volume of sensitive, confidential, and even secret information as important assets that are essential to its operational continuity. The organization also has an SOC, which oversees and manages security incidents in accordance with information security risk management practices. Unfortunately, it is also attacked by increasing numbers of cyberattacks from various domains, which was a consideration that led to the selection of this company as the research object in this study. Thus, this study specifically examined and analyzed the management of SOC-related risks and associated security practices using an integrated framework of ISO/IEC 27005 and NIST SP 800-30 against the periodical assessment within the organization, particularly within SOC domains such as risk identification, risk analysis, risk evaluation, and their association of risk treatment and security control. The findings are presented in an aggregate and anonymized form to ensure confidentiality while offering insight that may serve as practical reference for others in Indonesia seeking to implement the integrated risk assessment.
3.3. Data Source
This research makes use of varied sources of data to aid in the analysis of the case study and adds validity in the form of data triangulation. The main sources of data in this study pertain to internal organizational data on information security as well as operations of the SOC in PT NBFC. Data sources here relate to information security policies, SOP, risk registers, internal audit reports, as well as data records on the SOC that are relevant in risk identification, risk analysis, as well as the implementation of risk control. This data, apart from being based on documentary evidence, also utilizes expert opinion to aid in the assessment. Input in this regard was gathered from people involved in ISM as well as staff in the SOC of PT NBFC, such as SOC analysts and information security experts. Other sources of data, which were secondary in nature, were also gathered to add depth in the form of varied perspectives related to the relevant literature, as well as relevant and selected international standards, which in this case are ISO/IEC 27005 and NIST SP 800-30 as well as other kinds of guidelines set out by regulatory bodies in the context of Indonesia that might influence the implementation significantly.
The KAMI index was utilized as another complementary method for evaluating the organizational maturity levels in relation to the operations of the SOC. For this research, five domains were included in the evaluation, namely, governance, risk management, information security framework, asset management, and technology, as well as security controls. These domains were evaluated using a questionnaire that was completed by key organizational members directly engaged in the management of SOC processes and information security, namely, the SOC manager, information security officer, and the senior IT security personnel. These organizational members were targeted because of their involvement in security monitoring, response, and management processes within the organization. Evaluation of the score was based on the conventional KAMI index scoring system, whereby the individual scores were weighted at the domain levels; the scores were then aggregated to provide a comprehensive organizational score then validated by a comprehensive review toward organizational documents.
3.4. Documents Used
The documents used in this research directly derive from PT NBFC as a primary source and journals to support the analysis, which is related to the assessment of information security systems presented by using the ontology approach as a formal description of a concept explicitly in an insight from each concept along with its limitations, while the relationship of concepts includes a hierarchy of classes [34].
- Documents from PT NBFC
The documents from PT NBFC consist of the results of the assessment at PT NBFC, SOC Audit Results, NBFC SOC Guidelines, and Technical Studies—Managed Service SOC, and the domain ontology for these documents can be seen in Figure 7.
Figure 7.
PT NBFC document ontology.
- 2.
- Journal Publication Documents from Internet
Journal documents used are related to this research as supporting material for parameter assessment analysis of the SOC information system, the domain ontology of which can be seen in Figure 8.
Figure 8.
Journal document ontology.
3.5. SOC Information System Assessment Parameters
The parameters for conducting security assessments in organizations encompass several key principles that ensure the protection and reliability of information systems [35,36]. One of the fundamental parameters is confidentiality, which ensures that sensitive data is accessible only to authorized individuals, also preventing unauthorized access and data breaches. Furthermore, integrity is another critical factor focusing on maintaining the accuracy, reliability, and consistency of information by protecting it from unauthorized modifications, corruption, or cyber threats such as viruses and hackers. Availability is also essential, ensuring that information systems, websites, or platforms remain accessible to authorized users whenever needed, minimizing downtime and disruptions that could impact organizational operations. In addition to these principles, accountability plays a crucial role in security assessments by ensuring that all actions taken within the system are traceable to responsible individuals, thereby promoting transparency and compliance with security policies. Lastly, authentication strengthens security by verifying the identity of users, ensuring that only legitimate individuals can access protected resources, thereby reducing the risk of unauthorized access and potential cyber threats [37,38]. By applying these parameters, organizations can effectively assess and enhance their security posture, ensuring a robust and resilient cybersecurity framework that safeguards sensitive data and operational integrity [39,40].
4. Result and Discussion
Model development conducted with modern SOCs involves consideration of an organization’s unique cybersecurity risks and requirements, current trends in cybersecurity, and the latest technologies available [3]. Modern SOC models that can be used for development are the Next-Generation Cognitive Computing SOC (NGC2SOC) model, which is an SOC model in a much better position to strengthen cybersecurity strategies. The goal of the NGC2SOC model consists of advanced intelligence-driven tactics to conduct real-time investigations of known and unknown vulnerabilities, direct access, evidence visualization, and additional advanced tools or practices that reduce potential risk to critical assets combined with fully automated cybersecurity problem recovery [36]. In this research, framework evaluation, framework design, and implementation were carried out altogether and accordingly.
4.1. Object of Study
As stated, the object of analysis is the SOC of a non-bank financial company in Indonesia, which deals with security events and incidents as well as the management of responses to these incidents. In this case, the research aims to give a practical basis to the results of risk and maturity analysis. From the results of data analysis conducted, it was found that implementing a modern SOC must involve a holistic approach that considers SOC components consisting of humans, processes, and technology. This will protect the organization from the threat of cyberattacks and can reduce the risk of data breaches that are detrimental to the organization. The results of this study are recommendations for standards/frameworks for SOC information system security assessments at PT NBFC which can be applied to other organizations as well. The proposed standard is the result of an analysis of two frameworks, namely, ISO 27005:2018 and NIST SP 800-30, as the recommendation for conducting SOC guidance assessments. Putra and Soewito (2023) [41] previously conducted risk assessments using ISO/IEC 27005:2018 as a risk management framework and NIST SP 800-30 Rev.1 as risk assessment guidelines. Thus, in this study, SOC effectiveness was reconceptualized and extended through a mediating mechanism by incorporating structured incident consequence information. Essentially, ISO/IEC 27005:2018 supports the general concepts of ISO 27001 and emphasizes the importance of aligning risk management activities with the organization’s overall strategy and objectives [42]. Meanwhile, NIST SP 800-30 has been proven to provide more contributions such as knowledge about information security that is consistent and comprehensive for policy makers, thus supporting decision makers that do not hesitate to take risks because each risk has been well investigated [43]. In addition, this study also applied the KAMI index as a research novelty in evaluating the level of maturity, the level of completeness of the implementation of ISO 27001, and the map of the information system security governance area in an organization. The KAMI index was once used by Sofyan et al. (2024) [44] as well, who successfully employed it in the form of a score for the category of electronic systems used and the results of an evaluation of the level of completeness of implementation based on the ISO 27001 standard. Therefore, through SOC guidance assessment recommendations, which can be seen in Figure 9, the study presents a perimeter of the adaptive ecosystem by reframing security by embedding it from design to deployment.
Figure 9.
Information security 4.0.
4.2. Implementation
At this stage, the steps involved in utilizing SOC guidance assessment recommendations are utilized to ensure a structured and effective approach to system security evaluation. The implementation is formulated as a combination of two widely recognized frameworks: ISO/IEC 27005:2018, which serves as a comprehensive risk management framework, and NIST SP 800-30 Rev. 1, which provides detailed risk assessment guidelines. By integrating these two standards, organizations can successfully conduct risk management processes that align with the industry’s best practices while maintaining a practical and systematic approach to identifying, analyzing, and mitigating security threats. In addition, the ISO/IEC 27005:2018 framework focuses on establishing a structured methodology for managing risks within an organization’s information security system, ensuring that potential threats are assessed and addressed effectively. Meanwhile, NIST SP 800-30 Rev. 1 complements this framework by offering structured guidelines for risk assessment, also enabling organizations to evaluate security vulnerabilities in a methodical manner. This combined approach enhances the effectiveness of risk management efforts, making it easier for organizations to implement security measures that are both comprehensive and practical. By following these guidance recommendations, organizations can improve their SOC operations, ensuring that security risks are proactively managed and mitigated to maintain a resilient cybersecurity posture, thus presenting metrics in terms of cognitive, autonomous, responsive and predictive security.
4.2.1. Cybersecurity
In cybersecurity, maintaining the security of information systems requires the application of fundamental principles that ensure data protection and reliability. One of these principles is confidentiality, which ensures that only authorized individuals have access to sensitive information, preventing unauthorized access and potential data breaches. Meanwhile, integrity is another critical principle focusing on the security and accuracy of data by preventing any unauthorized modifications, corruption, or destruction caused by threats such as viruses or hackers. This ensures that the information remains complete, reliable, and unaltered. Additionally, availability is essential in ensuring that all authorized users within an organization can access the necessary information on designated websites or platforms at any time and from any location. By guaranteeing continuous access, organizations can maintain smooth operations without disruptions caused by cyber threats or system failures. The fulfillment of these principles plays a crucial role in strengthening an organization’s data security, minimizing the risk of cyberattacks, and ensuring the reliability of its information systems. Implementing these security measures not only protects sensitive data but also enhances the overall resilience of the organization’s cybersecurity infrastructure [45,46]. Nonetheless, the organization should move from static compliance to continuous risk intelligence by incorporating real-time risk dashboards and automated audit evidence.
4.2.2. Risk Assessment and Scoring Procedure
At this stage, the KAMI index assessment can be carried out to help determine the condition of information security based on the SNI (Standar Nasional Indonesia) following the ISO/IEC 27001 criteria. In the filling criteria within the list of questions provided in the KAMI index assessment, each answer has a certain value. The assessment also provides methods and formulas for processing obtained data that describe the condition of the company’s information security. The results of the KAMI index assessment are presented in the form of a dashboard that displays the electronic system category score, final evaluation results, the level of completeness of the implementation of the ISO27001 standard according to the electronic system category, and a radar chart that explains the level of information security readiness for each area [47]. After obtaining the analysis results from the KAMI index, context determination is carried out [41]. Then, risk criteria are used to track the level of risk as unacceptable or acceptable, which can include several limits with risk scale targets tailored to the needs of the organization.
This section also describes the methodology that was followed for the risk assessment and scoring process in the case study at PT NBFC, in which the risk assessment was performed by adopting an integrated approach of ISO/IEC 27005 and NIST SP 800-30 to identify, analyze, and evaluate security risks pertaining to SOC activities. The risk assessment process started with the identification of critical information assets linked to SOC operations, followed by the identification of relevant threat scenarios and vulnerabilities affecting such assets. Existing security controls were reviewed to understand the current risk mitigation measures already in place. This led to a set of defined risk scenarios that epitomize the possible security events related to the SOC environment. For each of the identified risk scenarios, the determination of risk levels was performed based on the assessment of likelihood and impact. The likelihood denotes the possibility of a threat exploiting vulnerability, while impact denotes potential consequences on organizational operations, information assets, and security objectives. Both likelihood and impact were assessed based on a five-level ordinal scale, from very low (1) to very high (5), in accordance with commonly adopted practices from ISO/IEC 27005 and NIST SP 800-30. Each scenario’s overall risk was calculated through the combination of scores over likelihood and impact by using the qualitative risk matrix. Consequently, the resulting risk values were categorized into low, medium, and high to support prioritization. The risk categorization was used to determine the proper treatment options for risk, including risk mitigation, risk acceptance, or risk monitoring, in accordance with organizational risk management. The risk scoring has been performed by expert judgment involving personnel in charge of information security and SOC operations. Scoring was carried out through structured review sessions to ensure consistency regarding the interpretation of criteria on likelihood and impact. In case of differences in assessment, discussion was held to obtain a common understanding of the risk level, while the outcome of the risk assessment provided the basis for the following maturity evaluation and analysis. The risk scale based on the NIST SP 800-30 framework can be seen in Table 3.
Table 3.
Risk scale.
In determining the context, the technology alone is insufficient for role-based security training, and gamified phishing simulations and behavior-based metrics become necessity for human-centered cultural transformation in prioritizing data value and ethics. Simply put, security should become a continuous process not a final gate in terms of compliance checks in secure-by-design architecture. Even an internal system must re-authenticate as well as re-authorize in every access request through continuous verification as opposed to one-time login and context-aware access for devices, location, and behavior. In this case, the impact criteria are using the level option, which is based on the level description in NIST SP 800-30 as can be seen in Table 4. The likelihood criteria using the consideration of impacts that allow threats to occur and the possibility of threats arising or occurring can be seen in Table 5.
Table 4.
Impact of system security threats.
Table 5.
Possibility of threats resulting in adverse impact on information systems.
4.2.3. Maturity Assessment Method
Here, the methodology used in assessing the SOC-related processes for maturity at PT NBFC is explained. In general, maturity assessment complements the risk assessment results by providing an additional dimension for evaluating the extent to which the existing practices related to the SOC are established, managed, and continuously improved within the organization. Assessment of maturity was performed according to a structured model that consists of five levels ranging from initial to optimized. With the increase in maturity level, more process definition, implementation, measurement, and continuous improvement are represented. The scope of this evaluation involves SOC-related domains relevant to information security risk management and operational effectiveness. Based on internal organizational documentation review and expert judgment of personnel involved in SOC and information security management, the scores of maturities were derived. Evidence examined included indications for documented procedures, consistency of implementation, monitoring of practices, and the improvement of mechanisms applied. Based on the predefined criteria for each maturity level considered, each domain was assessed, and a maturity level was assigned based on the appropriateness and completeness of meeting that criterion or set of criteria. For comparability, interpretation, and reporting, maturity levels were expressed as percentage values that indicated the degree of attainment of a particular domain. These percentages were utilized to facilitate visualization and comparison across domains rather than as absolute performance indicators. A target maturity level was defined by the organization internally based on its objectives and expectations of risk management, whereas the domains that attain or are near this target were highlighted for further analysis. The maturity assessment outcomes were analyzed jointly with the risk assessment results to determine the strengths, weaknesses, and areas of improvement for the SOC. This combined analysis provided further insight into how exposed risk and process maturity are interacting to influence SOC effectiveness overall.
4.2.4. Risk Assessment
At this stage, an assessment was carried out of the identified risks, and an evaluation was carried out for each risk scenario.
- Risk identification is the process of finding, recognizing, or describing risk attributes as it includes identifying sources, events, and causes of risk in an organization.
- a.
- Asset identification is the process of identifying assets starting with a weighted factor analysis of all ERP assets. Each information asset was scored for each important factor and given weight for each criterion. The weight values were obtained from the risk owner and IT risk officer in the organization. The weighted factor analysis criteria consist of criterion 1 (impact on revenue, 30%), criterion 2 (impact on profitability, 40%), and criterion 3 (impact on public image, 30%). Critical factors were assessed using a score ranging from 0.1 to 1.0, and criteria were given a weight ranging from 1 to 100, each weighted to indicate the importance of the criteria set for the organization. The range of values obtained refers to NIST SP 800-30 revision 1.
- b.
- In threat identification, threat sources are divided into two categories, namely, adversarial and non-adversarial threat sources. Then, identification of all threats that disrupt information security aspects is carried out. The questions used to identify threats are as follows:
- i.
- What threats to assets do you know or suspect?
- ii.
- What threats are the most dangerous to the organization?
- iii.
- What threats would be the most expensive to address if attacked?
- iv.
- What threats would cost the most to prevent?
- c.
- In identification of control, the security controls that the company has implemented to protect the organization’s assets from threats are identified.
- d.
- Vulnerability identification explores the extent to which a company has implemented controls to protect assets from threats. Vulnerabilities that do not have associated threats may not require the implementation of controls, but they need to be identified and monitored. However, ineffective implementation of controls or controls that do not function properly can lead to vulnerabilities.
- Risk analysis is the practice of mapping assets, asset values, threats, security controls, vulnerabilities, and impacts on CIA (confidentiality, integrity, and availability) aspects. In this case, it is intended to obtain impact assessment results and identify potential information security risks. In this study, the calculation of the risk using the formula can be presented as the probability of a successful attack on an organization (frequency of loss = likelihood × probability of attack success) multiplied by the expected loss from a successful attack (magnitude of loss = asset value × probability of loss) plus the uncertainty of estimating all the values mentioned. Loss frequency is a measure of the likelihood of an attack occurring combined with the probability of the attack being successful if it targets an organization. Loss magnitude is a combination of the value of an asset and the probability of its loss due to an attack.
- Risk evaluation in this study aimed to compare the results of the risk analysis with the risk criteria then determine whether the risk rating is acceptable or tolerable. The stages of risk evaluation include the preparation of risk priorities based on the magnitude of the risk, with the following provisions:
- a.
- The highest risk level has the highest priority.
- b.
- If there is more than one risk with the same risk magnitude, then the risk priority is determined based on the order of the impact area from the highest to the lowest according to the amount of loss.
- c.
- If there is still more than one risk that has the same magnitude and area of impact, then the risk priority is determined based on the order of the highest to the lowest risk category according to the frequency of loss.
- d.
- If there is still more than one risk that has the same magnitude, amount of loss, and frequency of loss, then the risk priority is determined based on the assessment of the risk owner.
Risk determination is the initial step before determining risk priorities, while the priority risk matrix is classified based on NIST SP 800-30 revision 1 and is a matrix of relationships between assets and threats.
4.2.5. Risk Treatment and Risk Acceptance Strategy
At this stage, an assessment is carried out of the identified risks, and an evaluation is carried out for each risk scenario.
- Risk Treatment Strategy: Risk handling aims to control the risk that is harmful by developing relevant handling to control the risk causes, measuring the effectiveness of the handling and, if the estimated risk value remains at an intolerable level, prepare alternative handling. According to ISO/IEC 27005:2018, there are four risk handling options, namely, risk modification, risk avoidance, risk sharing, and risk retention. In this study, 142 risks were found with unacceptable decisions for 32 modification risks. The total risk acceptance is 110, consisting of 90 risk retentions, two risk avoidances, and 18 risk sharing incidents. The risk handling scenarios were sorted based on risk priority from the highest to the lowest risk level. The following in Table 6 is an example of risk priority.Table 6. Risk treatment.
- 2.
- A risk acceptance strategy was carried out to explain more clearly some of the security controls that have been selected for risk management. In this study, an information security team was formed to determine the roles and responsibilities of the Person in Charge (PIC) of information security activities in each related division within the organization. In determining information security controls, the PIC is required to be responsible for accepting the risk.
4.2.6. Monitoring
At this stage, monitoring is carried out based on the risk list while documenting and monitoring risks. The process uses a risk list that provides holistic information about risks and allows stakeholders to make decisions related to these risks and their management. In information security 4.0, monitoring is no longer a passive process but it is intelligent, with multi-layer architecture within cycles and should be automated through observability by AI-assisted interpretation or clear expert operational explanation. Of course, the key idea here is that monitoring without response is obsolete, and control deviation instantly influences risk score and triggers mitigation workflow that impacts the risk heatmap. The risk owner or PIC uses the risk list to document and manage risks to the asset organization.
4.2.7. SOC Assessment
At this stage, an SOC assessment of an organization in handling information system security threats is produced. This can minimize the risk of information system security in an organization. The results of the conducted research are expected to provide benefits, while the implications that can be used are as follows:
- They are useful as a reference for the strengths and weaknesses of ISO 27005 and NIST in information system security.
- They can be used as a reference in the SOC information system security assessment for organizations to use the proposed information system security assessment framework to protect organizations from the threat of cyberattacks.
4.3. Evaluation Framework
At this stage, the framework assessment consists of ISO 27005:2018 and NIST SP 800-30, and the proposed framework combines ISO 27005:2018 with NIST SP 800-30 for the assessment of information system security at PT NBFC by calculating the maturity value or level to find out the extent to which the organization has implemented the clauses and annexes in the framework. Essentially, the process does not eliminate humans but augments them to validate high-impact decision. The maturity level measurement instrument used can be seen in Table 7 [48].
Table 7.
Maturity level scale.
To determine the maturity level of the clauses and annexes, use the maturity level Formula (1) [49].
The following are the evaluation results of the ISO 27005:2018 framework, NIST SP 800-30, and the proposed framework:
- ISO 27005:2018 Framework Assessment
In the ISO 27005 framework assessment, the maturity method is carried out based on the domain context establishment, risk analysis/assessment, risk treatment, risk acceptance, risk communication, monitoring, and critical analysis. Furthermore, a spider web graph is created to find out which domain is approaching the maturity target. The desired maturity target for the organization is 80% at category level 4—Managed and Measurable. The spider web graph in ISO 27005:2018 can be seen in Figure 10, from which it can be concluded that only the context establishment has exceeded the target, while the domains that have not reached the maturity target are related to the risk analysis/assessment, risk treatment, risk acceptance, risk communication, monitoring, and critical analysis domains.
Figure 10.
ISO 27005:2018 assessment results.
- 2.
- NIST SP 800-30 Framework Assessment
In the NIST SP 800-30 framework assessment, the capability maturity method is used based on the domain identify, protect, detect, respond, and recovery. Furthermore, a spider web graph is also created to determine which domains are approaching the maturity target. The spider web graph in NIST SP 800-30 can be seen in Figure 11, from which it can be concluded that the detect and respond domains have exceeded the target, while the domains that have not reached the maturity target are the identify, protect, and recover domains.
Figure 11.
NIST SP 800-30 assessment results.
- 3.
- Assessment of the Proposed Framework
In the assessment of the new framework, a combination of the ISO 27005:2018 and NIST SP 800-20 frameworks is carried out using the capability maturity method based on the domain research assessment, risk assessment, risk analysis, risk evaluation, risk treatment, risk acceptance, and monitoring. Furthermore, a spider web graph is created to find out which domains are approaching the maturity target, which is expected by the organization to be 80% at the Managed and Measurable level. The spider web graph in the proposed framework can be seen in Figure 12, from which it can be concluded that the research assessment and risk evaluation domains have exceeded the target, while the domains that have not reached the maturity target are the risk assessment, risk analysis, risk treatment, risk acceptance, and monitoring domains. The risk acceptance domain only reaches level 1 initially, so the organization needs to make improvements in the risk acceptance domain related to the risk approval of information security.
Figure 12.
Assessment of the proposed framework results.
From the description of the framework assessment that has been carried out consisting of the ISO 27005:2018 framework, NIST SP 800-30, and the proposed framework, it was concluded that the proposed framework achieved good maturity because there were two domains that reached the target maturity value and one domain that was at level 4—Managed and Measurable. In addition, the domains used in the new framework include domains from ISO 27005:2018 and NIST SP 800-30 so that organizations can utilize a more comprehensive approach, involving strategic, managerial, and technical aspects of risk management.
5. Strategic Development and Future Research Direction
5.1. Analysis of Network Management Maturity Level
This section analyzes the maturity level of network management at PT NBFC, which is currently undergoing a large-scale digital transformation. This analysis refers to the FCAPS (Fault, Configuration, Accounting, Performance, Security) framework created derived from ISO and ITU-T, which is a common standard in network management [50,51,52]. Thus, the strategy developed should not be a single but rather a multi-layer policy that provides adaptive attributes that align intention with a digital transformation mechanism. Each domain was analyzed based on the main activities associated with the six maturity level parameters, ranging from non-existent (level 0) to optimized (level 5). The analysis was conducted based on two main elements, namely, the Management Domain (FCAPS) in Table 8, Table 9, Table 10, Table 11 and Table 12 and maturity level parameters in Table 13.
Table 8.
Fault management.
Table 9.
Configuration management.
Table 10.
Accounting management.
Table 11.
Performance management.
Table 12.
Security management.
Table 13.
Parameter labels.
Fundamentally, FCAPS is not neglected, but in this case, it was re-engineered into a risk-adaptive management system suitable for various kinds of environment. Sudden service degradation is related to any kind of unusual network behavior, so the system here should auto-isolate nodes and trigger at certain periods for escalation to avoid the worst-case scenario and enable a self-healing workflow with root cause and behavioral analysis. The analysis was performed on the 13 most important activities per FCAPS categories, and the analysis results, as shown in the chart in Figure 13, indicate that fault management has never been one of the top priorities. Most of the activities are on Levels 1–2. Improvement needs to be made in early fault detection, event correlation, and automated recovery of faults.
Figure 13.
Fault management assessment.
The organization should employ policy as code to ensure drift control continuously and secure a default template for an SOC. In the case of a cloud resource and device deviating from the secure baseline, it will autmatically rollback as the configuration governance takes place and compliance log is updated. In Figure 14, PT NBFC is highly mature in this category, primarily due to SD-WAN, SASE, and PASSION system deployment, and most of the activities are at Levels 3–4, i.e., well-organized configuration management.
Figure 14.
Configuration management assessment.
Previously, accounting management utilized billing and usage tracking; therefore, it should employ risk-sensitive accountability through immutable audit logs, data access accounting, identity-based usage tracking, and cost–risk correlation as risk score increases followed by access being throttled. In Figure 15, the integration of SAP and PASSION indicates that there are metering and logging systems in place, while good scores (Levels 2–3) were obtained for some of the strategic activities.
Figure 15.
Accounting management assessment.
Resilience and experience awareness should be the basis for performance management rather than simply throughput metrics, like in certain cases when encryption overhead causes latency and an adaptive policy can be applied without weakening performance by trade-off analysis and SLA monitoring in several scenarios. In Figure 16, the utilization of real-time dashboards, cloud monitoring, and QoS ensure high performance of the network. Work in this space mostly attains levels 3–4.
Figure 16.
Performance management assessment.
Adaptive trust and autonomous defense should be implemented within the organization through security-centric behavior. In Figure 17, security management is the most evolved space at PT NBFC. SASE-based security, active MFA, firewall policies, and ISO 27001 audit provide values at levels 4–5, but anomaly detection and event logging need to be addressed. Overall, the results analysis also indicates that PT NBFC has significant maturity in security, configuration, and performance, while fault and accounting require improvement and advancement, especially systematization of processes and operating documentation to be applied accordingly. Tuning each domain in detail, this company can achieve enterprise-class network management at global levels.
Figure 17.
Security management assessment.
5.2. Future Research and Development Ideas
The results of this study highlight the importance of structured network management maturity assessment, particularly for organizations undergoing digital transformation in critical sectors such as non-bank financial services. While the FCAPS framework and SMART-based evaluation have proven effective in diagnosing operational readiness, they are largely limited to a technical operational scope. SOC management should be integrated and intelligent at the same time to ensure resilience and digital trust for adaptive protection and continuous trust enforcement. In an increasingly interconnected and volatile digital landscape, there is a pressing need to broaden the perspective of network management to encompass strategic alignment, cross-functional integration, and long-term sustainability considerations. To support this evolution, Figure 18 presents a proposed conceptual framework for Future Network Management Dimensions as this model introduces five interconnected domains, namely, Operational, Tactical, Strategic, Cross-Domain, and Sustainability. Each domain reflects a layer of network management complexity, from hands-on infrastructure performance to high-level organizational and environmental alignment. For example, the Operational domain remains focused on core functions such as fault detection, accounting, and configuration, which are essential for baseline performance. Nevertheless, these are augmented in the Tactical domain with components like inventory control, quality assurance, and risk topology, all of which provide actionable insights for mid-level management.
Figure 18.
The five network management domains.
The Strategic domain in Figure 18 introduces governance mechanisms, service-level orchestration, and innovation planning, allowing organizations to align network performance with business objectives and regulatory mandates. This is especially relevant for SOC design, where cybersecurity effectiveness is closely tied to the governance culture and innovation capacity of an organization. On the other hand, the Cross-Domain layer should then address interoperability challenges and the need for ecosystem-wide coordination. With digital infrastructure often spanning cloud platforms, external vendors, and regulatory entities, interoperability becomes a cornerstone of secure and resilient operations. Finally, the inclusion of the Sustainability domain is a novel addition that reflects growing awareness of digital sustainability, green IT, and long-term resilience planning. It encourages future research to consider the carbon footprint of digital infrastructure, lifecycle management of security systems, and sustainable budgeting for cybersecurity investments.
By referencing Figure 18, this framework serves as a foundation for developing next-generation maturity models that go beyond compliance and technical metrics. Instead, it embraces a multidimensional view of network and cybersecurity management as one that is adaptive, proactive, and contextually aware. Future research may focus on validating this framework through empirical studies, developing associated assessment instruments, or mapping it against existing standards like COBIT, TOGAF, or ISO/IEC 27001 family extensions. This expanded framework not only supports more comprehensive SOC maturity assessments but also empowers decision makers to embed network management into broader enterprise strategies. It opens opportunities for innovation in monitoring tools, risk communication protocols, and sustainability-driven SOC architecture. Ultimately, this research seeks to bridge the gap between technical excellence and strategic foresight in network and security operations.
5.3. Research Limitations
There are several limitations associated with the current study, which are important to consider while interpreting the results. First, the current study utilizes the single-case study method applied to a non-bank financial institution. Even though the study benefits from allowing an elaborate analysis of the risk management process related to the SOC at the financial institution, it does not aim to generalize the results to several organizations. Second, the study utilizes the dominant method of risk assessment by using internal organizational records and experts associated with the information technology and SOC operations at the financial institution. Even though the current study employs the technique of triangulation, potential risk associated with a lack of objectivity while estimating the risk scores and maturity could still exist. Third, the current study employed the risk management method using the technique of the cross-sectional survey method applied during a definite period. Thus, the current study did not measure the maturity process developed at the financial institution during the period selected. Future studies could utilize the risk management method during longitudinal observation and could be conducted to benefit the current study through validating the integrated risk management process across several organizations and different sectors. Moreover, the current study could be developed further in different directions such as predictive resilience to improve transparency within the organization in order to benefit the integration of automated risk metrics associated with the current study.
6. Conclusions
The research on the analysis of assessment parameters on the SOC information system in the PT NBFC Case Study was successfully carried out, and the following conclusions were obtained. The evaluation shows that the ISO 27005:2018 and NIST SP 800-30 frameworks each have advantages and disadvantages in assessing information system security within the organization. ISO 27005:2018 focuses more on information security risk management as a whole system, while NIST SP 800-30 provides more detailed guidance on the risk assessment process. The proposed developed framework integrates important parameters from both frameworks with adjustments based on the review results. It uses maturity levels to adjust to the specific needs of PT NBFC, resulting in a context-appropriate evaluation. Meanwhile, the results of the maturity level assessment on ISO 27005:2018 show that only the context establishment has exceeded the target, while the other domain that has not reached the maturity target (80% level 4). On the other hand, in NIST SP 800-30, the detect and respond domains have exceeded the target compared with other domains. Meanwhile, the proposed framework that combines ISO 27005:2018 and NIST SP 800-30 has achieved good maturity and has been successfully implemented because there are two domains that have achieved the target maturity value and one domain that is already at level 4—Managed and Measurable. In addition, the domains used in the new framework include domains from ISO 27005:2018 and NIST SP 800-30 so that organizations can take advantage of a more comprehensive approach, involving strategic, managerial, and technical aspects of risk management. The proposed framework includes several parameters/domains, namely, research assessment, risk assessment, risk treatment, risk acceptance strategy, and monitoring. These parameters are designed to be applicable in various types of organizations by adjusting to the specific needs of each organization. Also, implementation of the proposed framework in the form of SOC assessment guidance involves the development of clear guidance on the assessment process, including practical steps to identify, analyze, and respond to threats. This guidance is designed to be used by SOC teams to improve their ability to assess and manage information security risks, which includes Input, Actions, and Implementation Guidance.
Author Contributions
Conceptualization, M.L., and M.I.L.; methodology, M.L.; software, M.I.L.; validation, R.R.S., and A.R.L.; formal analysis, M.L.; investigation, M.I.L.; resources, M.I.L.; data curation, R.R.S.; writing—original draft preparation, M.I.L.; writing—review and editing, M.L., and A.N.M.; visualization, A.N.M.; supervision, M.L., and R.R.S.; project administration, A.R.L.; funding acquisition, M.I.L. All authors have read and agreed to the published version of the manuscript.
Funding
This research received no external funding.
Data Availability Statement
Data will be made available on request.
Conflicts of Interest
The authors declare that they have no known competing financial interests or personal relationships that could have appeared to influence the work reported in this paper.
Abbreviations
| PT | Perseroan Terbatas (Limited Liability Company) |
| BSSN | Badan Siber dan Sandi Negara (National Cyber and Crypto Agency) |
| OJK | Otoritas Jasa Keuangan (Financial Services Authority) |
| POJK | Peraturan Otoritas Jasa Keuangan (Financial Services Authority Regulation) |
| SEOJK | Surat Edaran OJK (Financial Services Authority Circular Letter) |
| KAMI | Keamanan Informasi (Information Security) |
| SNI | Standar Nasional Indonesia (Indonesian National Standard) |
| CIA | Confidentiality, integrity, and availability |
References
- Badan Keamanan Siber Indonesia. Lanskap Keamanan Siber Indonesia; Badan Keamanan Siber Indonesia: Jakarta, Indonesia, 2023. [Google Scholar]
- Bassey, C.; Chinda, E.T.; Idowu, S. Building a Scalable Security Operations Center: A Focus on Open-Source Tools. J. Eng. Res. Rep. 2024, 26, 196–209. [Google Scholar] [CrossRef] [Scilit]
- Mughal, A.A. Building and Securing the Modern Security Operations Center (SOC). Int. J. Bus. Intell. Big Data Anal. 2022, 5, 1–15. [Google Scholar]
- Onwubiko, C.; Ouazzane, K. Challenges towards Building an Effective Cyber Security Operations Centre. Int. J. Cyber Situational Aware 2022, 4, 2057–2182. [Google Scholar] [CrossRef] [Scilit]
- Falé, P.; Reis, L.; Almeida, R. Cybersecurity—Security Operations Center. In Proceedings of the Recent Advances in Information Technology, Tourism, Economics, Management and Agriculture, Maribor, Slovenia, 27 October 2022; pp. 99–103. [Google Scholar]
- Tinsley, E.; Agapitova, N. Private Sector Solutions to Helping Smallholders Succeed Social Enterprise Business Models in the Agriculture Sector; World Bank: Washington, DC, USA, 2018. [Google Scholar]
- ISO/IEC 27005:2022; Information Security, Cybersecurity and Privacy Protection—Guidance on Managing Information Security Risks. ISO: Geneva, Switzerland, 2022.
- National Institute of Standards and Technology [NIST]. Guide for Conducting Risk Assessments; Special Publication 800-30 Rev. 1; National Institute of Standards and Technology [NIST]: Gaithersburg, MD, USA, 2012. [Google Scholar]
- Louman, B.; Girolami, E.D.; Shames, S.; Primo, L.G.; Gitz, V.; Scherr, S.J.; Meybeck, A.; Brady, M. Access to Landscape Finance for Small-Scale Producers and Local Communities: A Literature Review. Land 2022, 11, 1444. [Google Scholar] [CrossRef] [Scilit]
- Louman, B.; Meybeck, A.; Mulder, G.; Brady, M.; Fremy, L.; Savenije, H.; Gitz, V.; Trines, E. Innovative Finance for Sustainable Landscapes; Center for International Forestry Research (CIFOR): Bogor, Indonesia, 2020. [Google Scholar]
- Mawesti, D.; Aryanto, T.; Yogi, Y.; Louman, B. Finance for Integrated Landscape Management; Tropenbos Indonesia: Bogor, Indonesia, 2021. [Google Scholar]
- Naran, B.; Buchner, B.; Price, M.; Stout, S.; Taylor, M.; Zabeida, D. Global Landscape of Climate Finance 2024. Available online: https://www.climatepolicyinitiative.org/publication/global-landscape-of-climate-finance-2024/ (accessed on 26 February 2025).
- Gulati, A.; Singh, S. The Changing Landscape of Financial Services in the Age of Digitalization: A Bibliometric Analysis. NMIMS Manag. Rev. 2024, 32, 42–57. [Google Scholar] [CrossRef] [Scilit]
- Agyepong, E.; Cherdantseva, Y.; Reinecke, P.; Burnap, P. A Systematic Method for Measuring the Performance of a Cyber Security Operations Centre Analyst. Comput. Secur. 2023, 124, 102959. [Google Scholar] [CrossRef] [Scilit]
- Lubis, M.; Wardana, C.; Widjajarto, A. The Development of Information System Security Operation Centre (SOC): Case Study of Auto Repair Company. In Proceedings of the 2020 6th International Conference on Interactive Digital Media (ICIDM), Bandung, Indonesia, 14–15 December 2020; pp. 1–8. [Google Scholar]
- Forsberg, J.; Frantti, T. Technical Performance Metrics of a Security Operations Center. Comput. Secur. 2023, 135, 103529. [Google Scholar] [CrossRef] [Scilit]
- Kurii, Y.; Opirskyy, I. Analysis and Comparison of the NIST SP 800-53 and ISO/IEC 27001:2013. In Proceedings of the CPITS-2022: Cybersecurity Providing in Information and Telecommunication Systems, Kyiv, Ukraine, 26 October 2022; pp. 21–32. [Google Scholar]
- Azinheira, B.; Antunes, M.; Maximiano, M.; Gomes, R.P. Information Security and Cybersecurity Assessment In SME—An Implementation Methodology. J. Glob. Bus. Technol. 2023, 19, 78. [Google Scholar]
- Nugraha, A.; Sembodo, J.S. Design Of Information Security Management System Based On ISO/IEC 27001: 2013 In The Manufacturing Industry. Innov. J. Soc. Sci. Res. 2024, 4, 6899–6920. [Google Scholar]
- Varona Taborda, M.A. Dynamic Cybersecurity Model Based on ISO Standards for Higher Education Institutions in Colombia. Ing. Solidar. 2021, 17, 1–21. [Google Scholar] [CrossRef] [Scilit]
- Meher, H. Threat Handling Using the NIST Framework in a Recruitment Environment. Master’s Thesis, National College of Ireland, Dublin, Ireland, 2021. [Google Scholar]
- Saeed, S.; Suayyid, S.A.; Al-Ghamdi, M.S.; Al-Muhaisen, H.; Almuhaideb, A.M. A Systematic Literature Review on Cyber Threat Intelligence for Organizational Cybersecurity Resilience. Sensors 2023, 23, 7273. [Google Scholar] [CrossRef] [Scilit]
- AL-Dosari, K.; Fetais, N. Risk-Management Framework and Information-Security Systems for Small and Medium Enterprises (SMEs): A Meta-Analysis Approach. Electronics 2023, 12, 3629. [Google Scholar] [CrossRef] [Scilit]
- Kamil, Y.; Lund, S.; Islam, M.S. Information Security Objectives and the Output Legitimacy of ISO/IEC 27001: Stakeholders’ Perspective on Expectations in Private Organizations in Sweden. Inf. Syst. e-Bus. Manag. 2023, 21, 699–722. [Google Scholar] [CrossRef] [Scilit]
- Kure, H.I.; Islam, S.; Mouratidis, H. An Integrated Cyber Security Risk Management Framework and Risk Predication for the Critical Infrastructure Protection. Neural Comput. Appl. 2022, 34, 15241–15271. [Google Scholar] [CrossRef] [Scilit]
- Hidayatullah, D.E.R.; Kunthi, R.; Harwahyu, R. Design and Analysis of Information Security Risk Management Based on ISO 27005: Case Study on Audit Management System (AMS) XYZ Internal Audit Department. Int. J. Electr. Comput. Biomed. Eng. 2024, 2, 395–413. [Google Scholar] [CrossRef] [Scilit]
- Mahardika, M.S.; Hidayanto, A.N.; Paramartha, P.A.; Ompusunggu, L.D.; Mahdalina, R.; Affan, F. Measurement of Employee Awareness Levels for Information Security at the Center of Analysis and Information Services Judicial Commission Republic of Indonesia. Adv. Sci. Technol. Eng. Syst. J. 2020, 5, 501–509. [Google Scholar] [CrossRef] [Scilit]
- Moreira, F.R.; Da Silva Filho, D.A.; Nze, G.D.A.; de Sousa Junior, R.T.; Nunes, R.R. Evaluating the Performance of NIST’s Framework Cybersecurity Controls Through a Constructivist Multicriteria Methodology. IEEE Access 2021, 9, 129605–129618. [Google Scholar] [CrossRef] [Scilit]
- Husein, Z.Z.; Sirie, M.I. OJK Sets New Cyber Security Best Practices for the Banking Industry. Available online: https://www.ahp.id/ojk-sets-new-cyber-security-best-practices-for-the-banking-industry/ (accessed on 20 February 2025).
- Koty, A.C. Cybersecurity Rules for Financial Institutions in Indonesia. Available online: https://www.aseanbriefing.com/news/new-cybersecurity-rules-for-financial-institutions-in-indonesia/ (accessed on 20 February 2025).
- Rizal, M.; Yani, Y. Cybersecurity Policy and Its Implementation in Indonesia. JAS J. ASEAN Stud. 2016, 4, 61. [Google Scholar] [CrossRef] [Scilit]
- Ali, I. Examining Cyber Security Implementation through TLS/SSL on Academic Institutional Repository in Indonesia. Berk. Ilmu Perpust. Dan Inf. 2021, 17, 238–249. [Google Scholar] [CrossRef] [Scilit]
- Odera, D.; Otieno, M.; Ounza, J.E. Security Risks in the Software Development Lifecycle: A Review. World J. Adv. Eng. Technol. Sci. 2023, 8, 230–253. [Google Scholar] [CrossRef] [Scilit]
- Gomez, L.V.; Miura, J. Ontology Learning of New Concepts Combining Textural Knowledge, Visual Analysis, and User Interaction. IEEE Access 2021, 9, 146023–146037. [Google Scholar] [CrossRef] [Scilit]
- Rosmaini, E.; Kusumasari, T.F.; Lubis, M.; Lubis, A.R. Study to the Current Protection of Personal Data in the Educational Sector in Indonesia. J. Phys. Conf. Ser. 2018, 978, 012037. [Google Scholar] [CrossRef] [Scilit]
- Saraiva, M.; Mateus-Coelho, N. CyberSoc Framework a Systematic Review of the State-of-Art. Procedia Comput. Sci. 2022, 204, 961–972. [Google Scholar] [CrossRef] [Scilit]
- Chamkar, S.A.; Maleh, Y.; Gherabi, N. Security Operations Centers: Use Case Best Practices, Coverage, and Gap Analysis Based on MITRE Adversarial Tactics, Techniques, and Common Knowledge. J. Cybersecur. Priv. 2024, 4, 777–793. [Google Scholar] [CrossRef] [Scilit]
- Chamkar, S.A.; Maleh, Y.; Gherabi, N. The Human Factor Capabilities in Security Operation Center (SOC). Edpacs 2022, 66, 1–14. [Google Scholar] [CrossRef] [Scilit]
- Demertzis, K.; Kikiras, P.; Tziritas, N.; Sanchez, S.L.; Iliadis, L. The Next Generation Cognitive Security Operations Center: Network Flow Forensics Using Cybersecurity Intelligence. Big Data Cogn. Comput. 2018, 2, 35. [Google Scholar] [CrossRef] [Scilit]
- Kokulu, F.B.; Soneji, A.; Bao, T.; Shoshitaishvili, Y.; Zhao, Z.; Doupé, A.; Ahn, G.-J. Matched and Mismatched SOCs. In Proceedings of the 2019 ACM SIGSAC Conference on Computer and Communications Security, London, UK, 11–15 November 2019; ACM: New York, NY, USA, 2019; pp. 1955–1970. [Google Scholar]
- Putra, A.P.; Soewito, B. Integrated Methodology for Information Security Risk Management Using ISO 27005:2018 and NIST SP 800-30 for Insurance Sector. Int. J. Adv. Comput. Sci. Appl. 2023, 14, 625–633. [Google Scholar] [CrossRef] [Scilit]
- Taylor, E. Risk Management in ISO 27001 and ISO 27005; The Knowledge Academy Ltd.: Berkshire, UK, 2025. Available online: https://www.theknowledgeacademy.com/blog/risk-management-in-iso-27001-and-iso-27005/ (accessed on 3 February 2025).
- Diesch, R.; Pfaff, M.; Krcmar, H. A Comprehensive Model of Information Security Factors for Decision-Makers. Comput. Secur. 2020, 92, 101747. [Google Scholar] [CrossRef] [Scilit]
- Sofyan, H.; Kaswidjanti, W.; Ilmiyah, L.S. Information Security Index (ISI) 4.2 for Information Security Evaluation (Case Study: Sleman Regency Communication and Informatics Office). In Proceedings of the 2023 1st International Conference on Advanced Informatics and Intelligent Information Systems (ICAI3S 2023), Yogyakarta, Indonesia, 29–30 November 2023; Atlantis Press: Dordrecht, The Netherlands, 2024; pp. 188–200. [Google Scholar]
- Li, Y.; Liu, Q. A Comprehensive Review Study of Cyber-Attacks and Cyber Security; Emerging Trends and Recent Developments. Energy Rep. 2021, 7, 8176–8186. [Google Scholar] [CrossRef] [Scilit]
- Szczepaniuk, E.K.; Szczepaniuk, H.; Rokicki, T.; Klepacki, B. Information Security Assessment in Public Administration. Comput. Secur. 2020, 90, 101709. [Google Scholar] [CrossRef] [Scilit]
- Jevelin, J.; Faza, A. Evaluation the Information Security Management System: A Path Towards ISO 27001 Certification. J. Inf. Syst. Inform. 2023, 5, 1240–1256. [Google Scholar] [CrossRef] [Scilit]
- Makupi, D.; Masese, N. Determining Information Security Maturity Level of an Organization Based on ISO 27001. Int. J. Comput. Sci. Eng. 2019, 6, 5–11. [Google Scholar] [CrossRef] [Scilit]
- Luthfi, M.I.; Lubis, M.; Saedudin, R.R. Development of Security Operation Center (SOC) Governance Blueprint Based on Consideration of Process Maturity Level Parameters. In Proceedings of the 2023 8th International Conference on Information Technology and Digital Applications (ICITDA), Yogyakarta, Indonesia, 17–18 November 2023; pp. 1–8. [Google Scholar]
- Lubis, F.; Lubis, M. Network Fault Effectiveness and Implementation at Service Industry in Indonesia. J. Phys. Conf. Ser. 2020, 1566, 012080. [Google Scholar] [CrossRef] [Scilit]
- Lubis, M.; Safitra, M.F.; Fakhrurroja, H.; Muslim, A.A. Assessing Network Accounting Management Approaches in the Infrastructure and Information Technology Sector: A Case Study in Indonesia. In Intelligent Sustainable Systems; Nagar, A.K., Jat, D.S., Mishra, D.K., Joshi, A., Eds.; Springer Nature: Singapore, 2024; pp. 273–284. [Google Scholar]
- Putra, S.A.; Lubis, M.; Saedudin, R.R. In Deep Security Management Strategy: Vulnerability Assessment Within Educational Institution. In Proceedings of the 2023 6th International Conference on Electronics, Communications and Control Engineering, Fukuoka, Japan, 24–26 March 2023; ACM: New York, NY, USA, 2023; pp. 118–124. [Google Scholar]
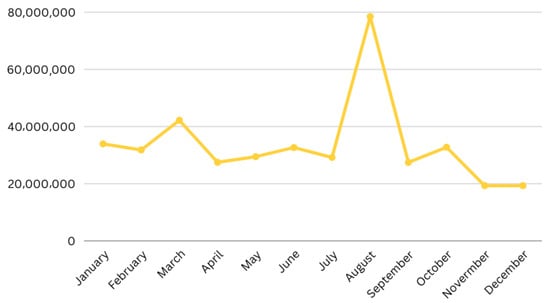
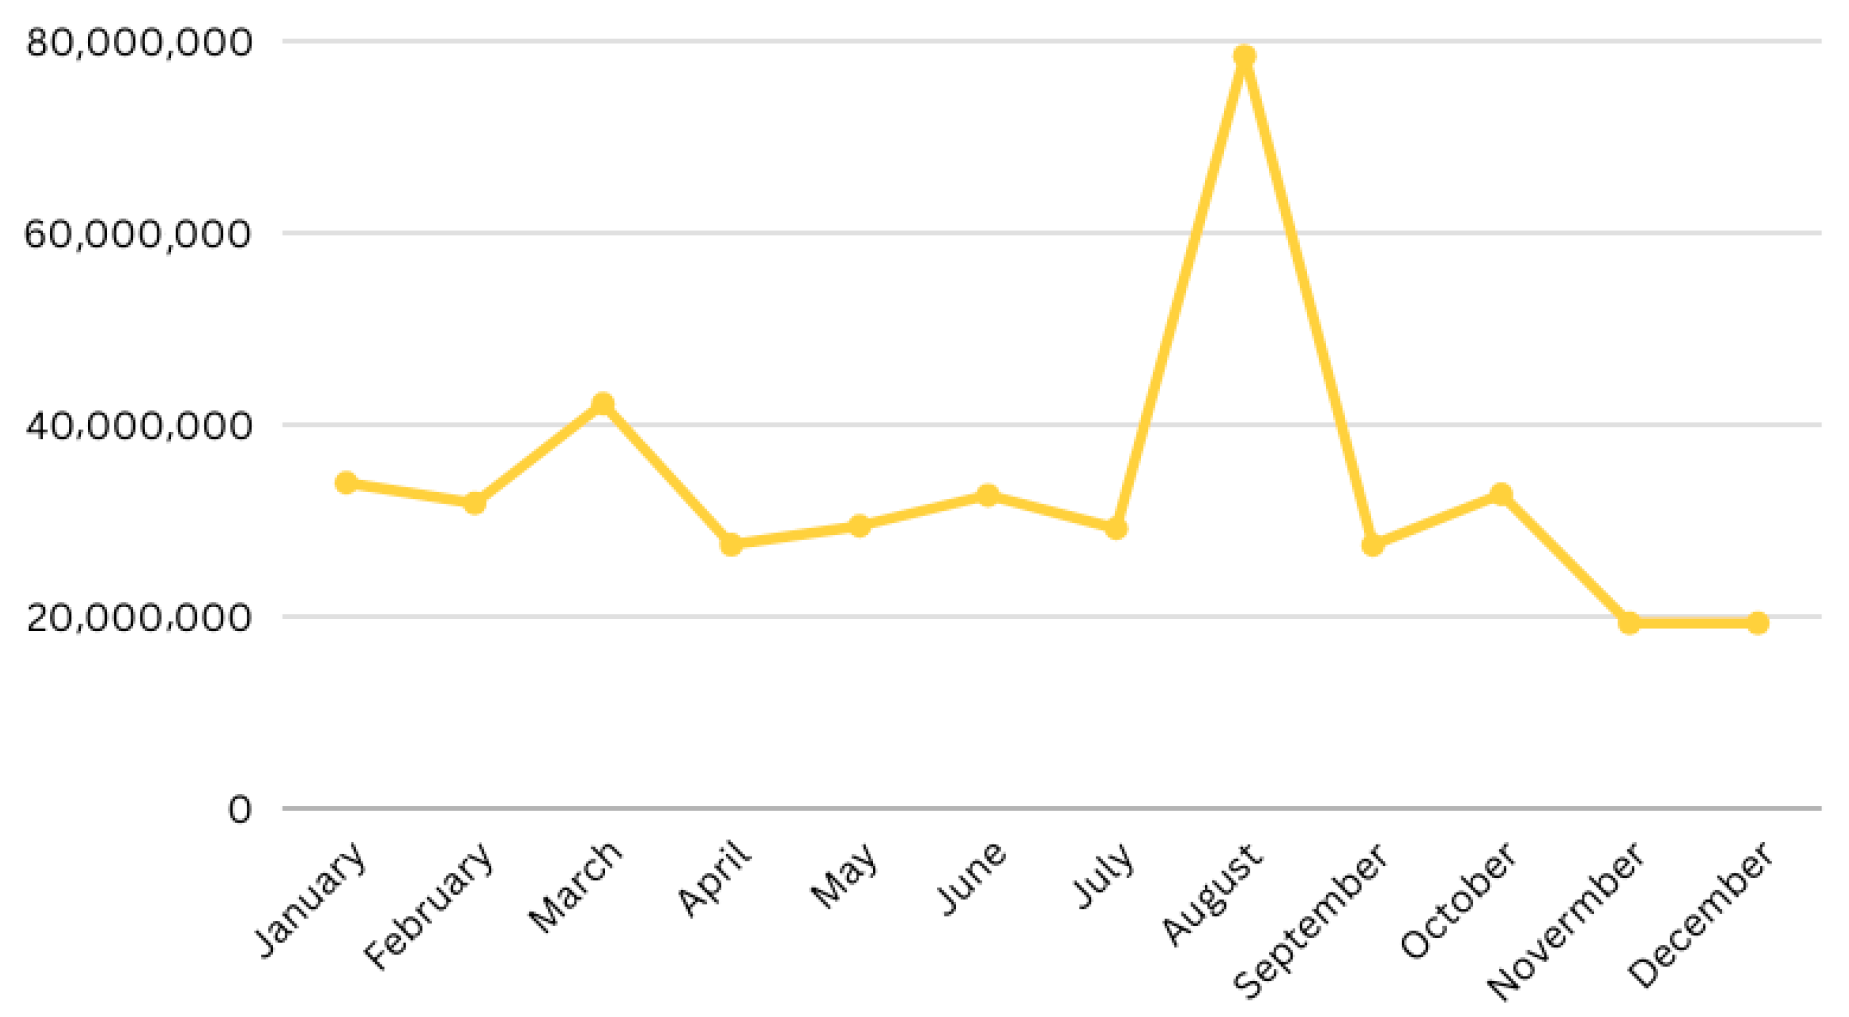
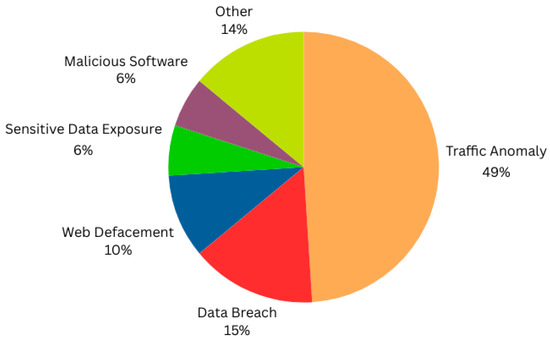
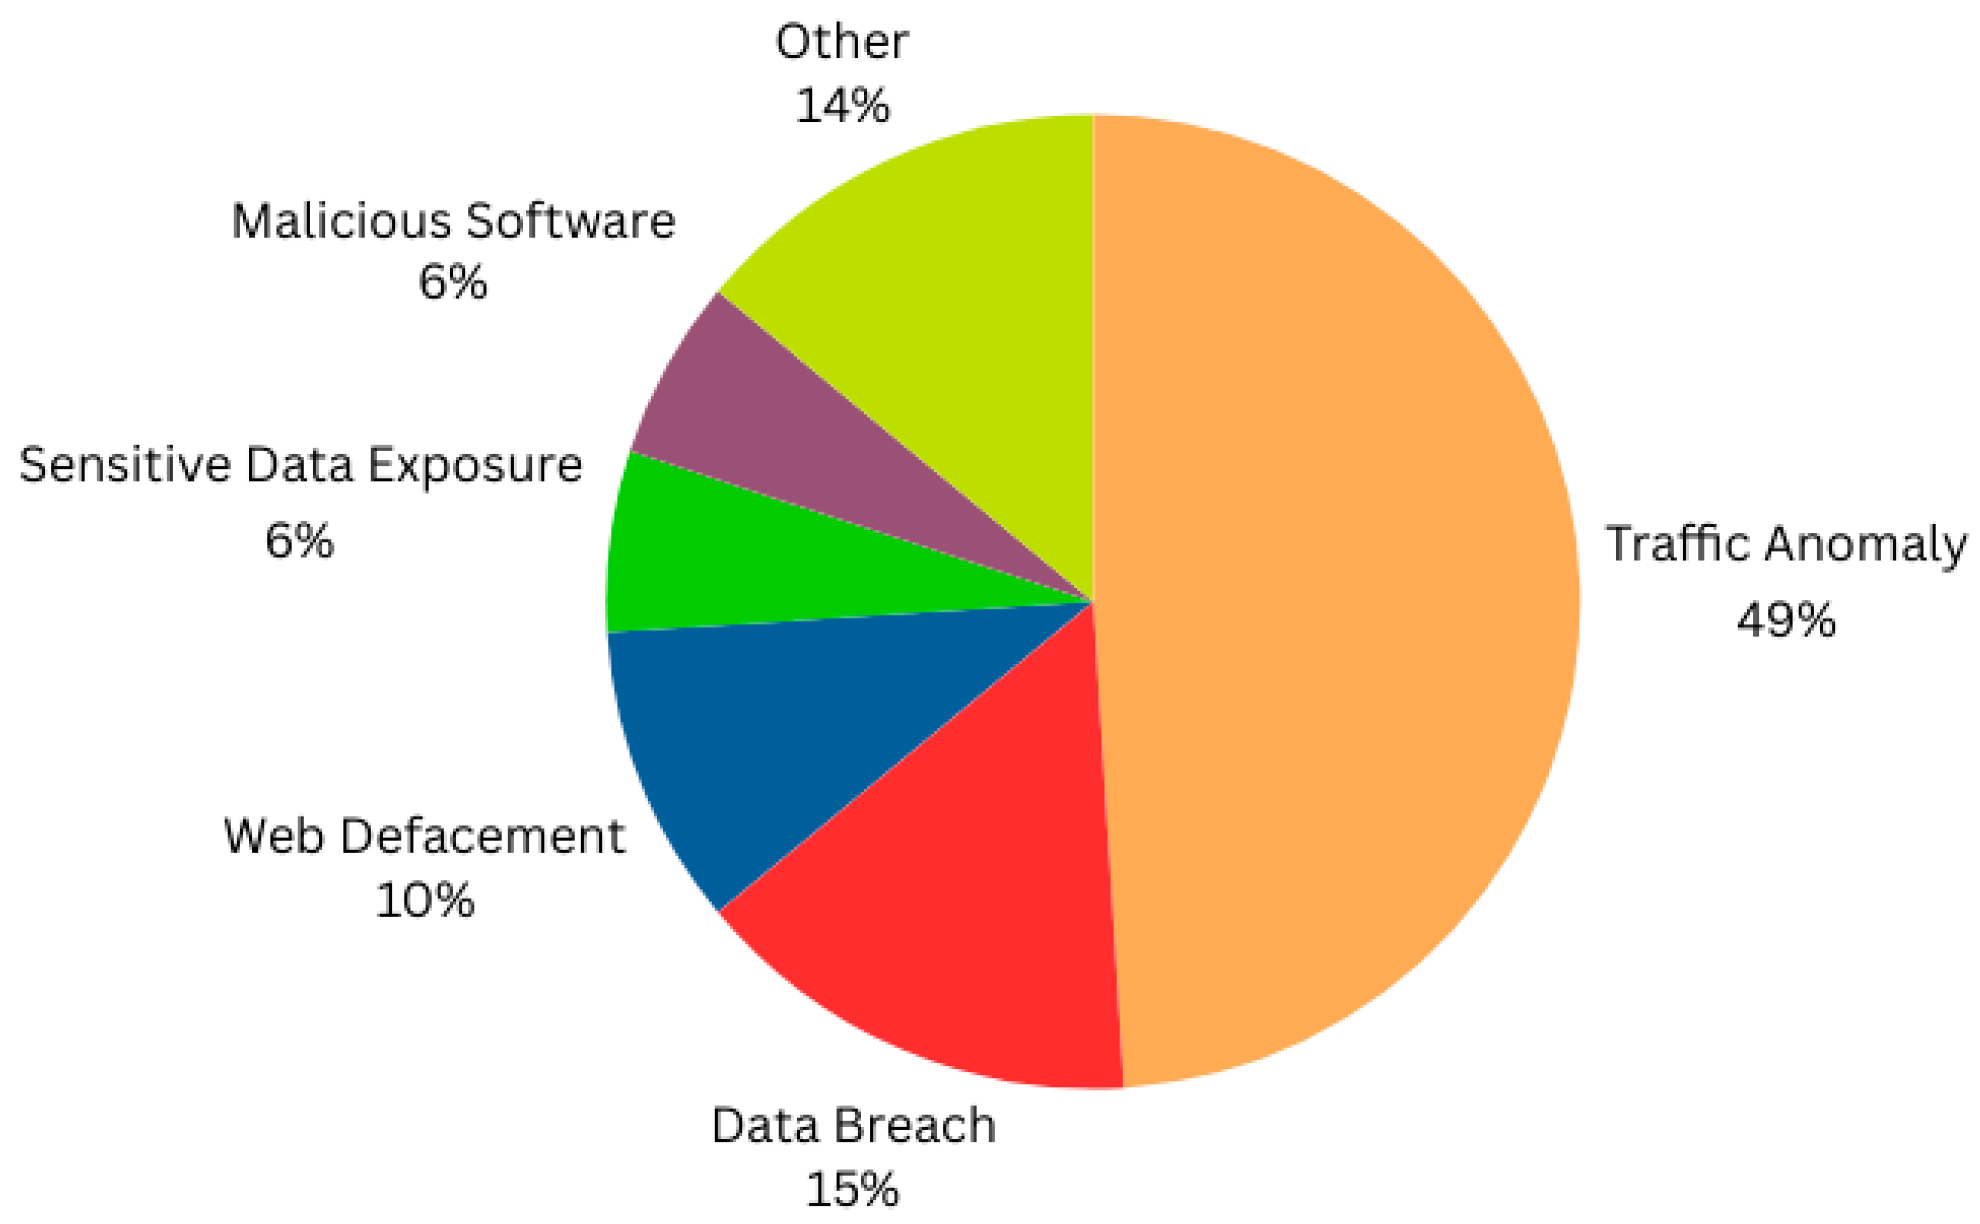
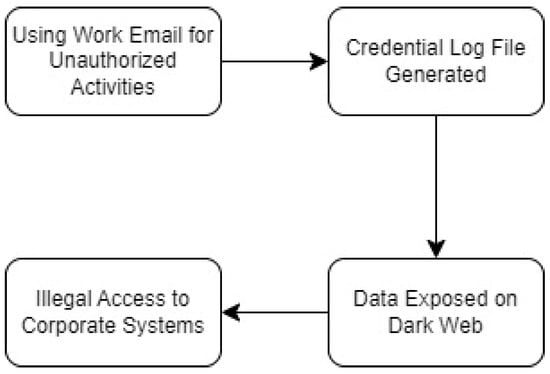
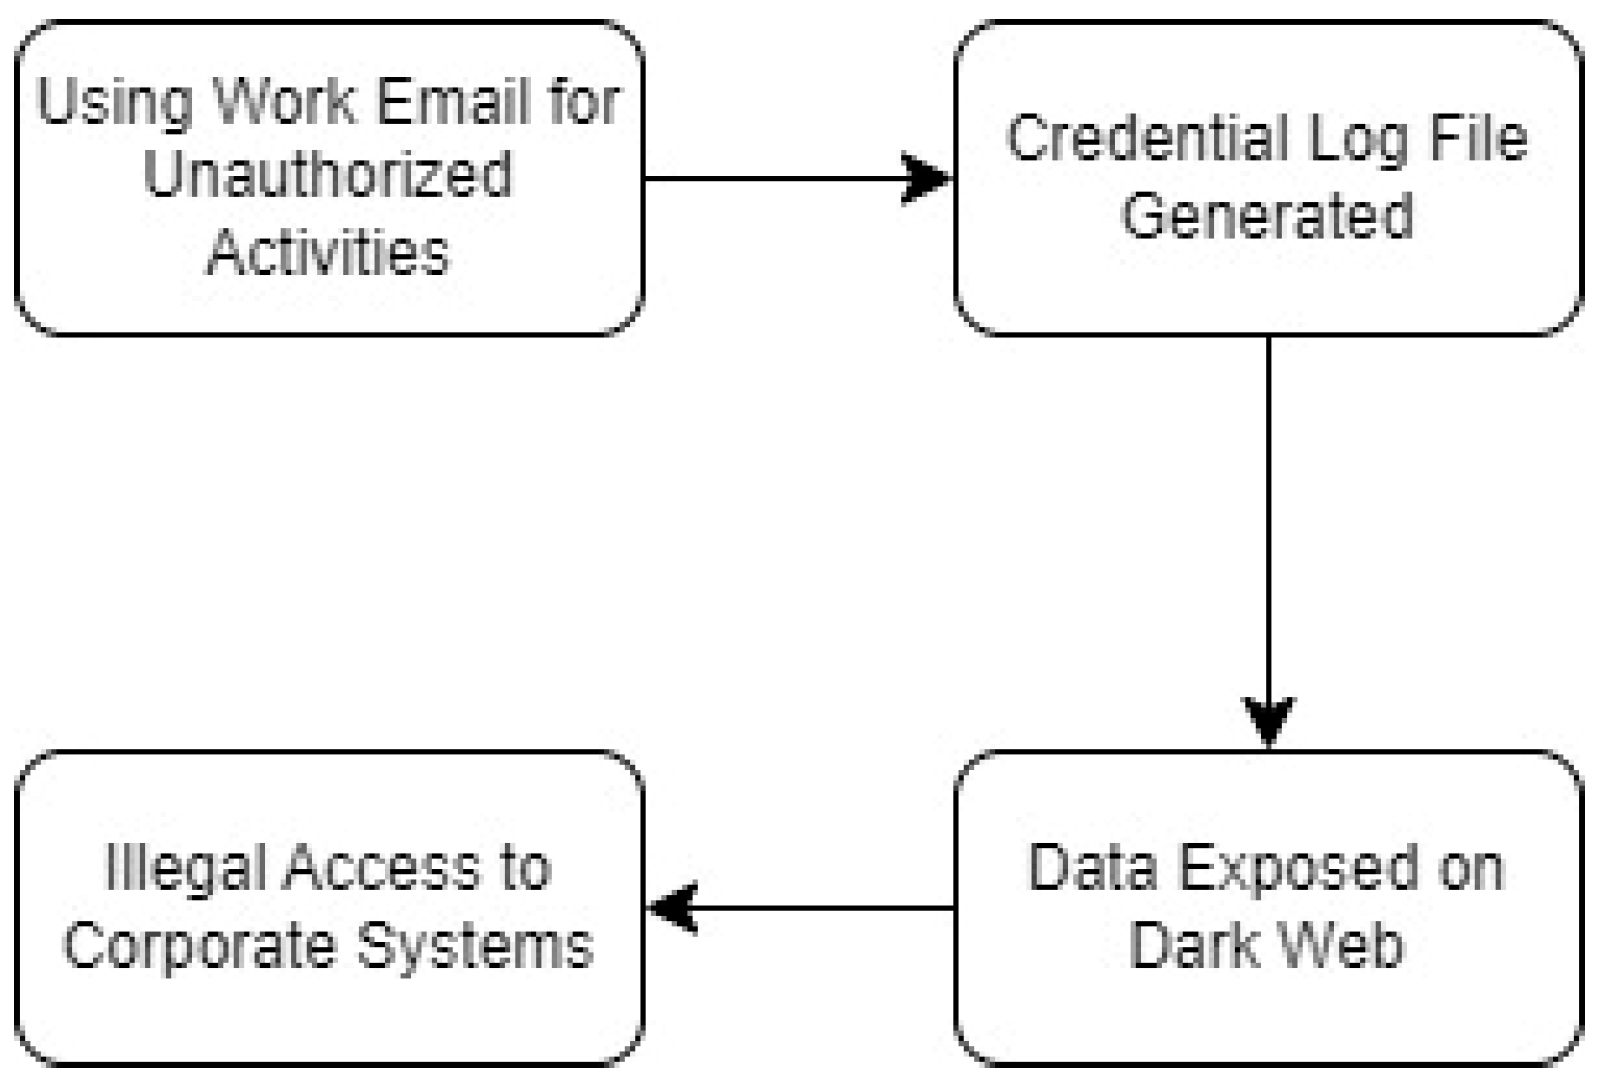
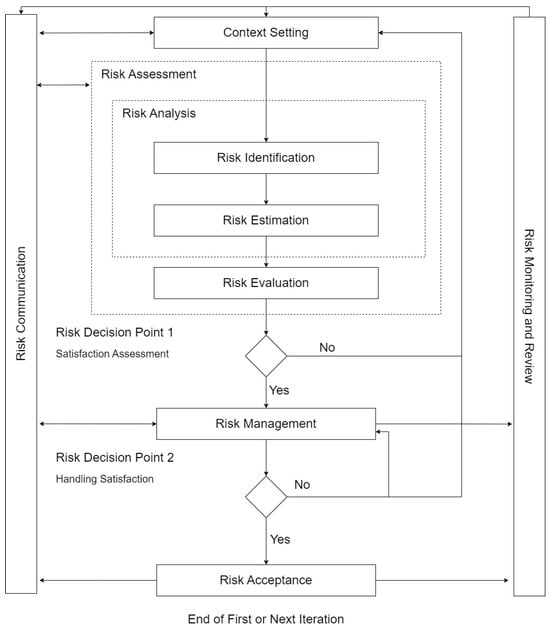
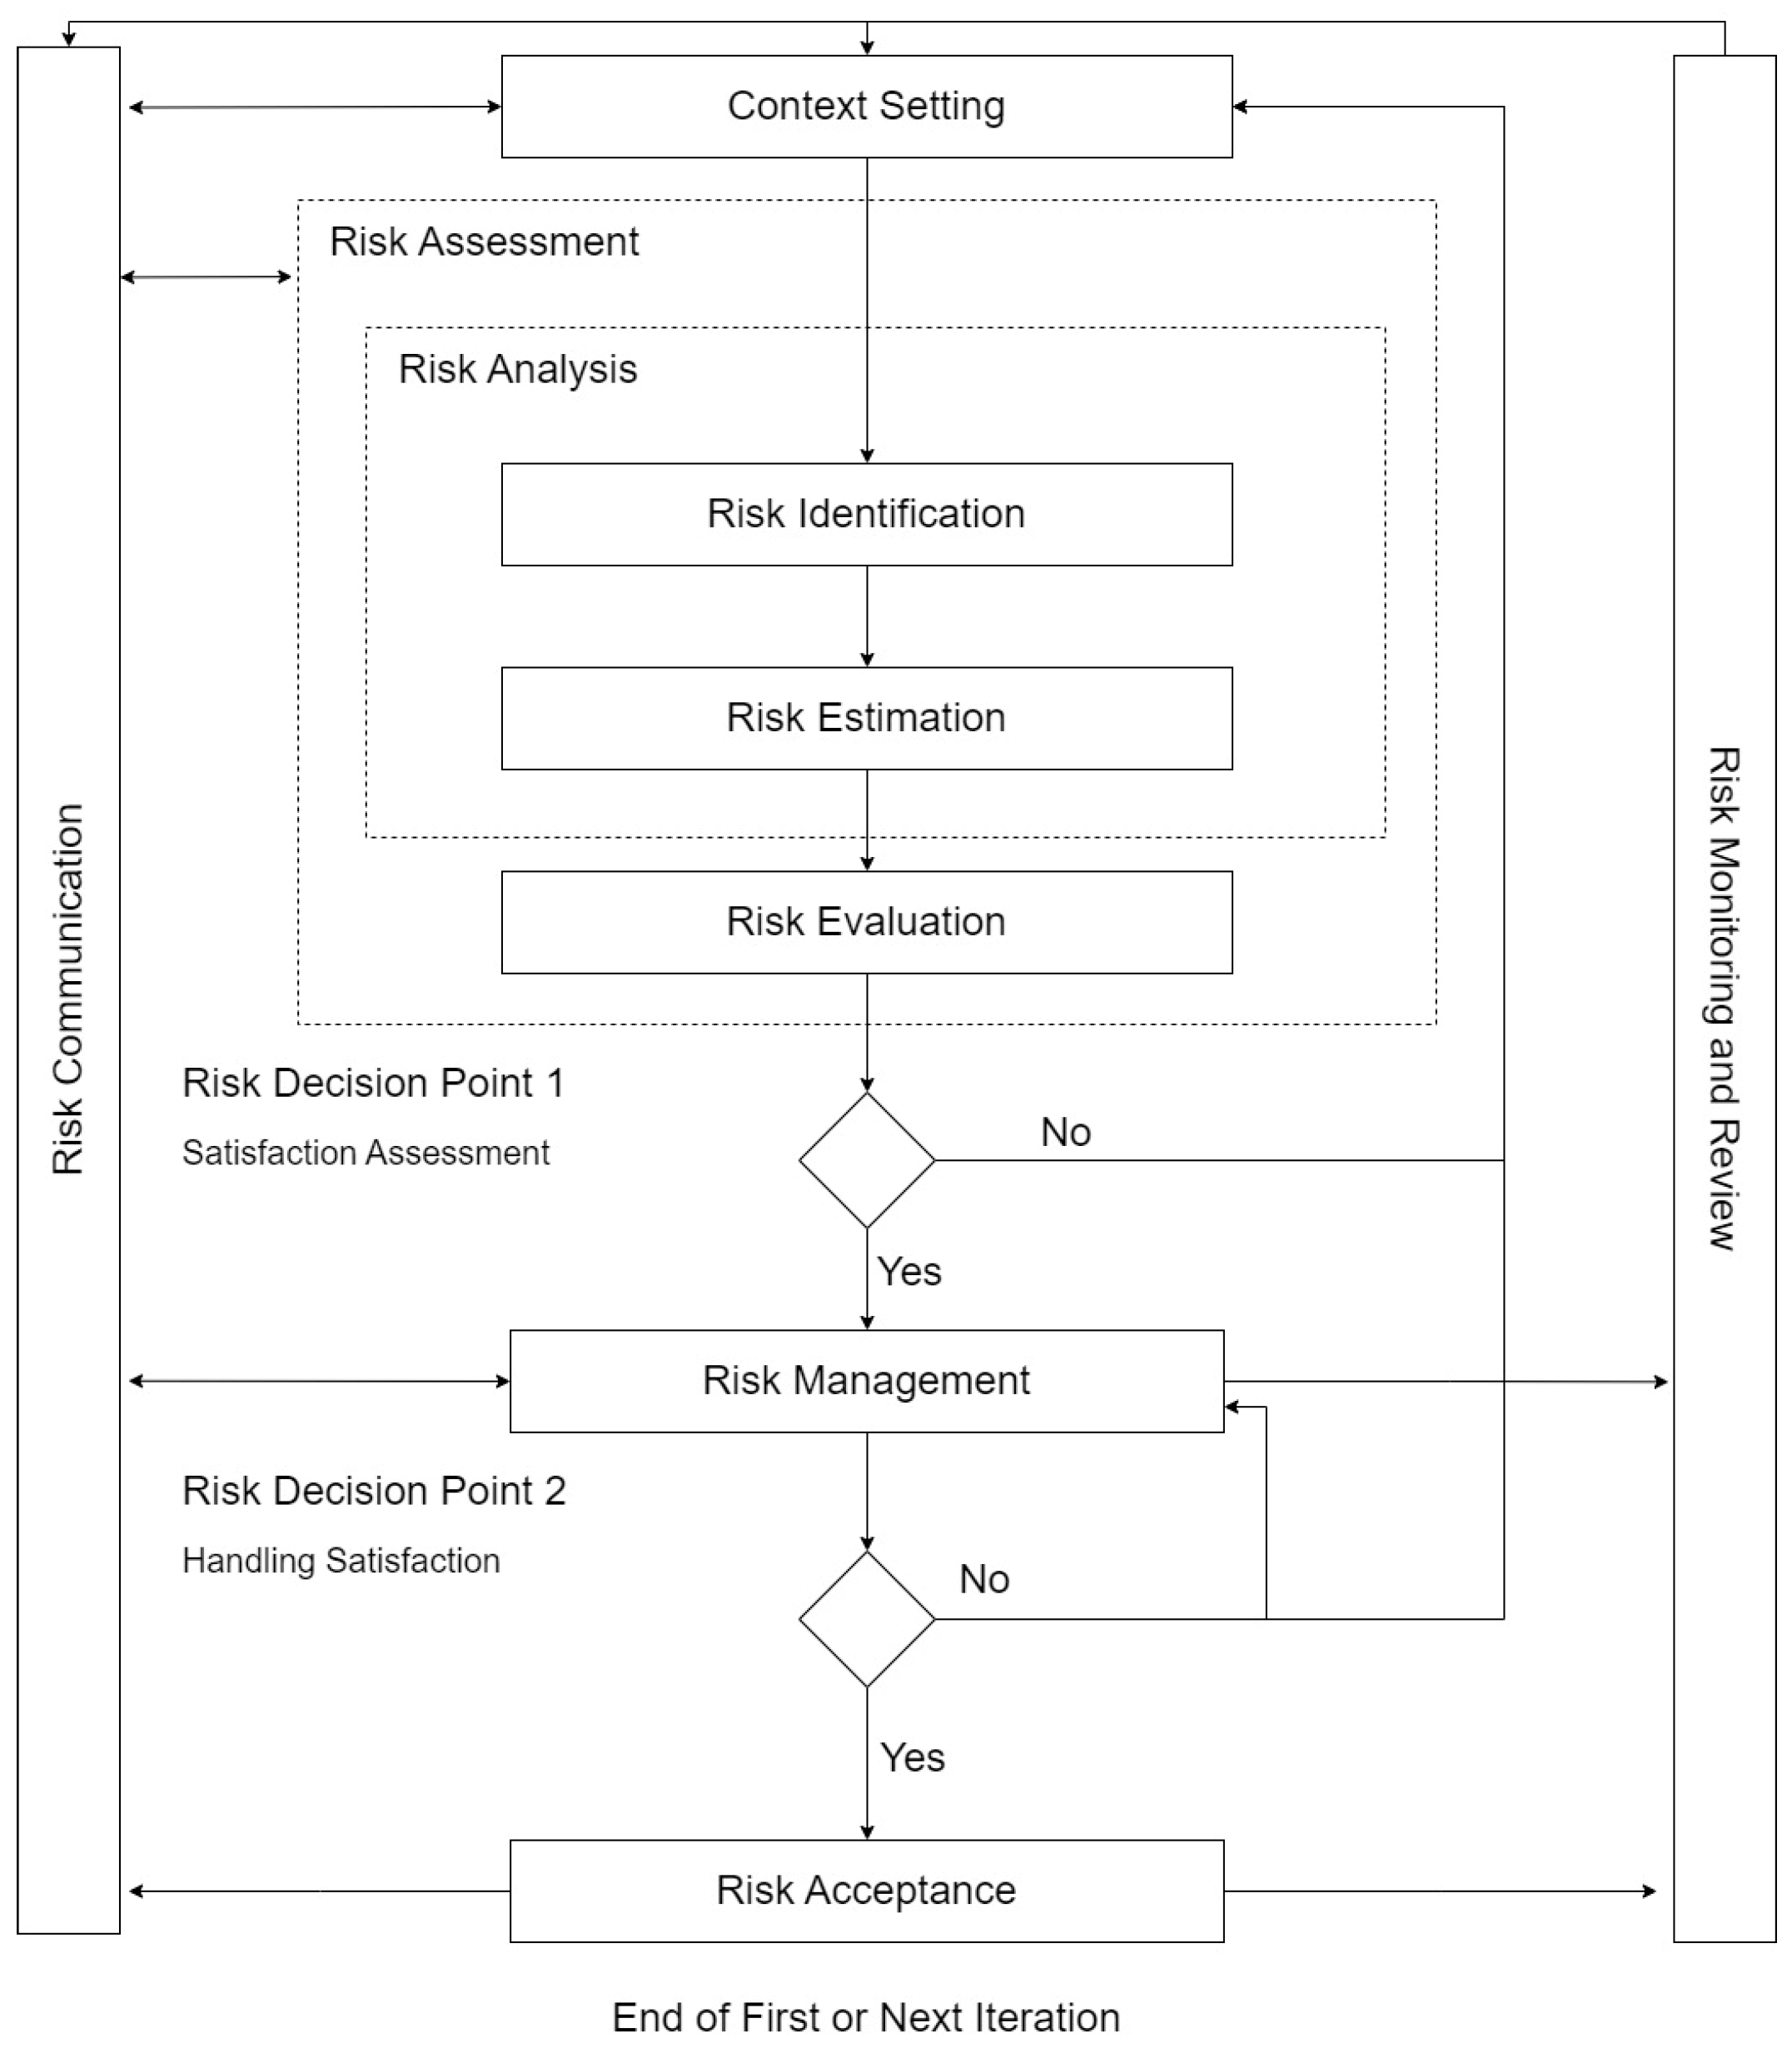
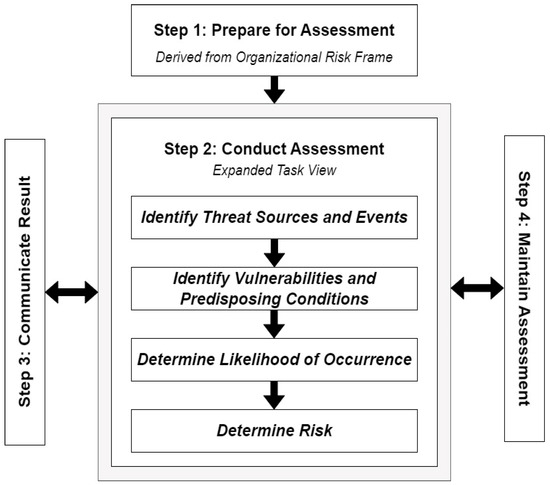
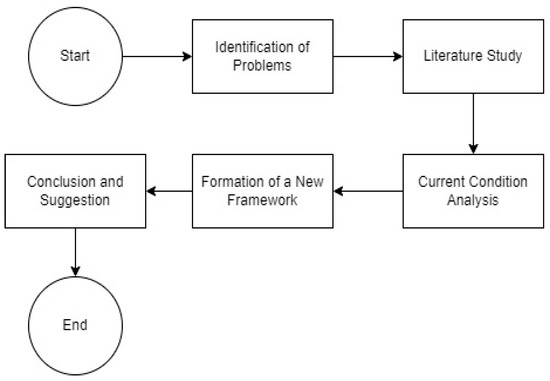
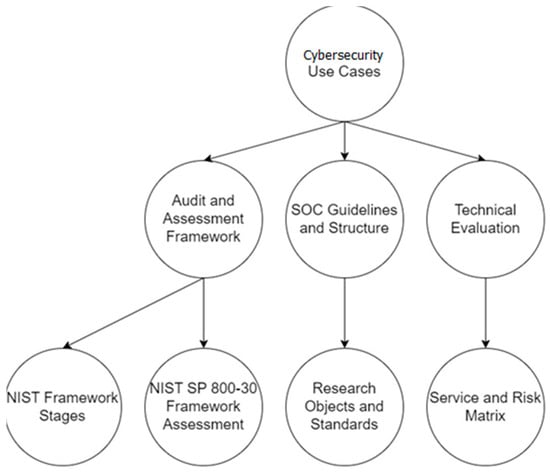
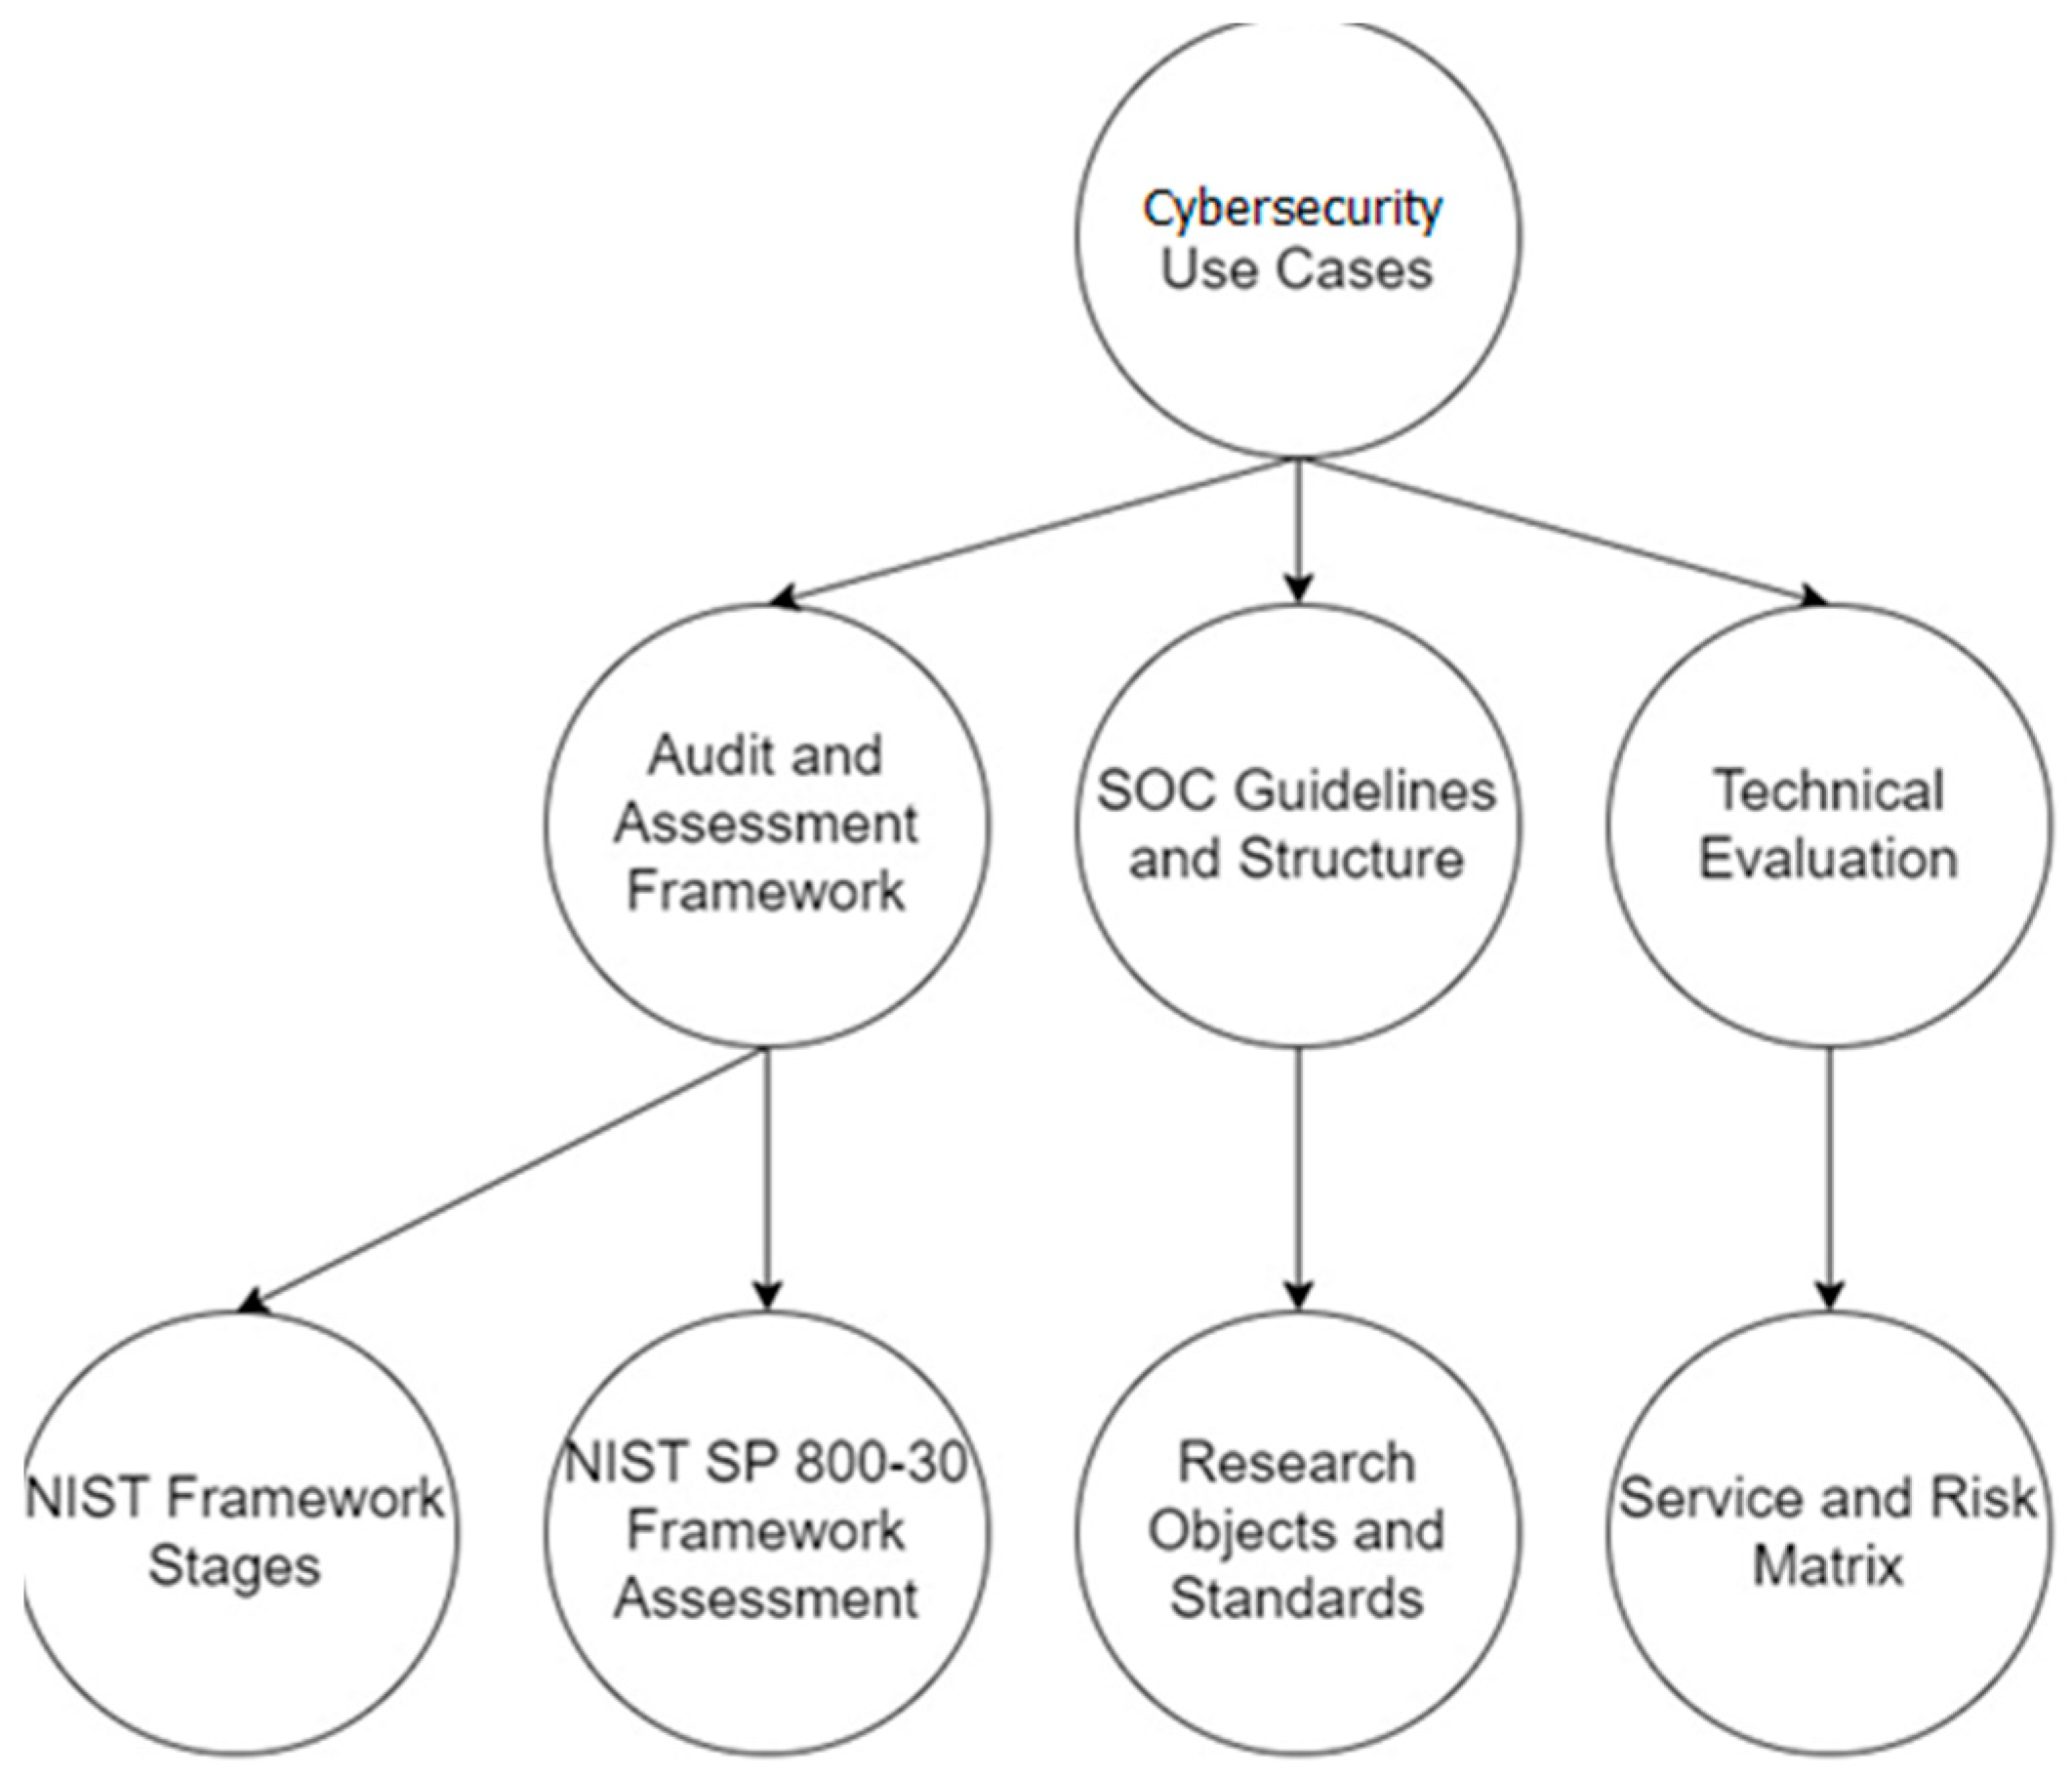
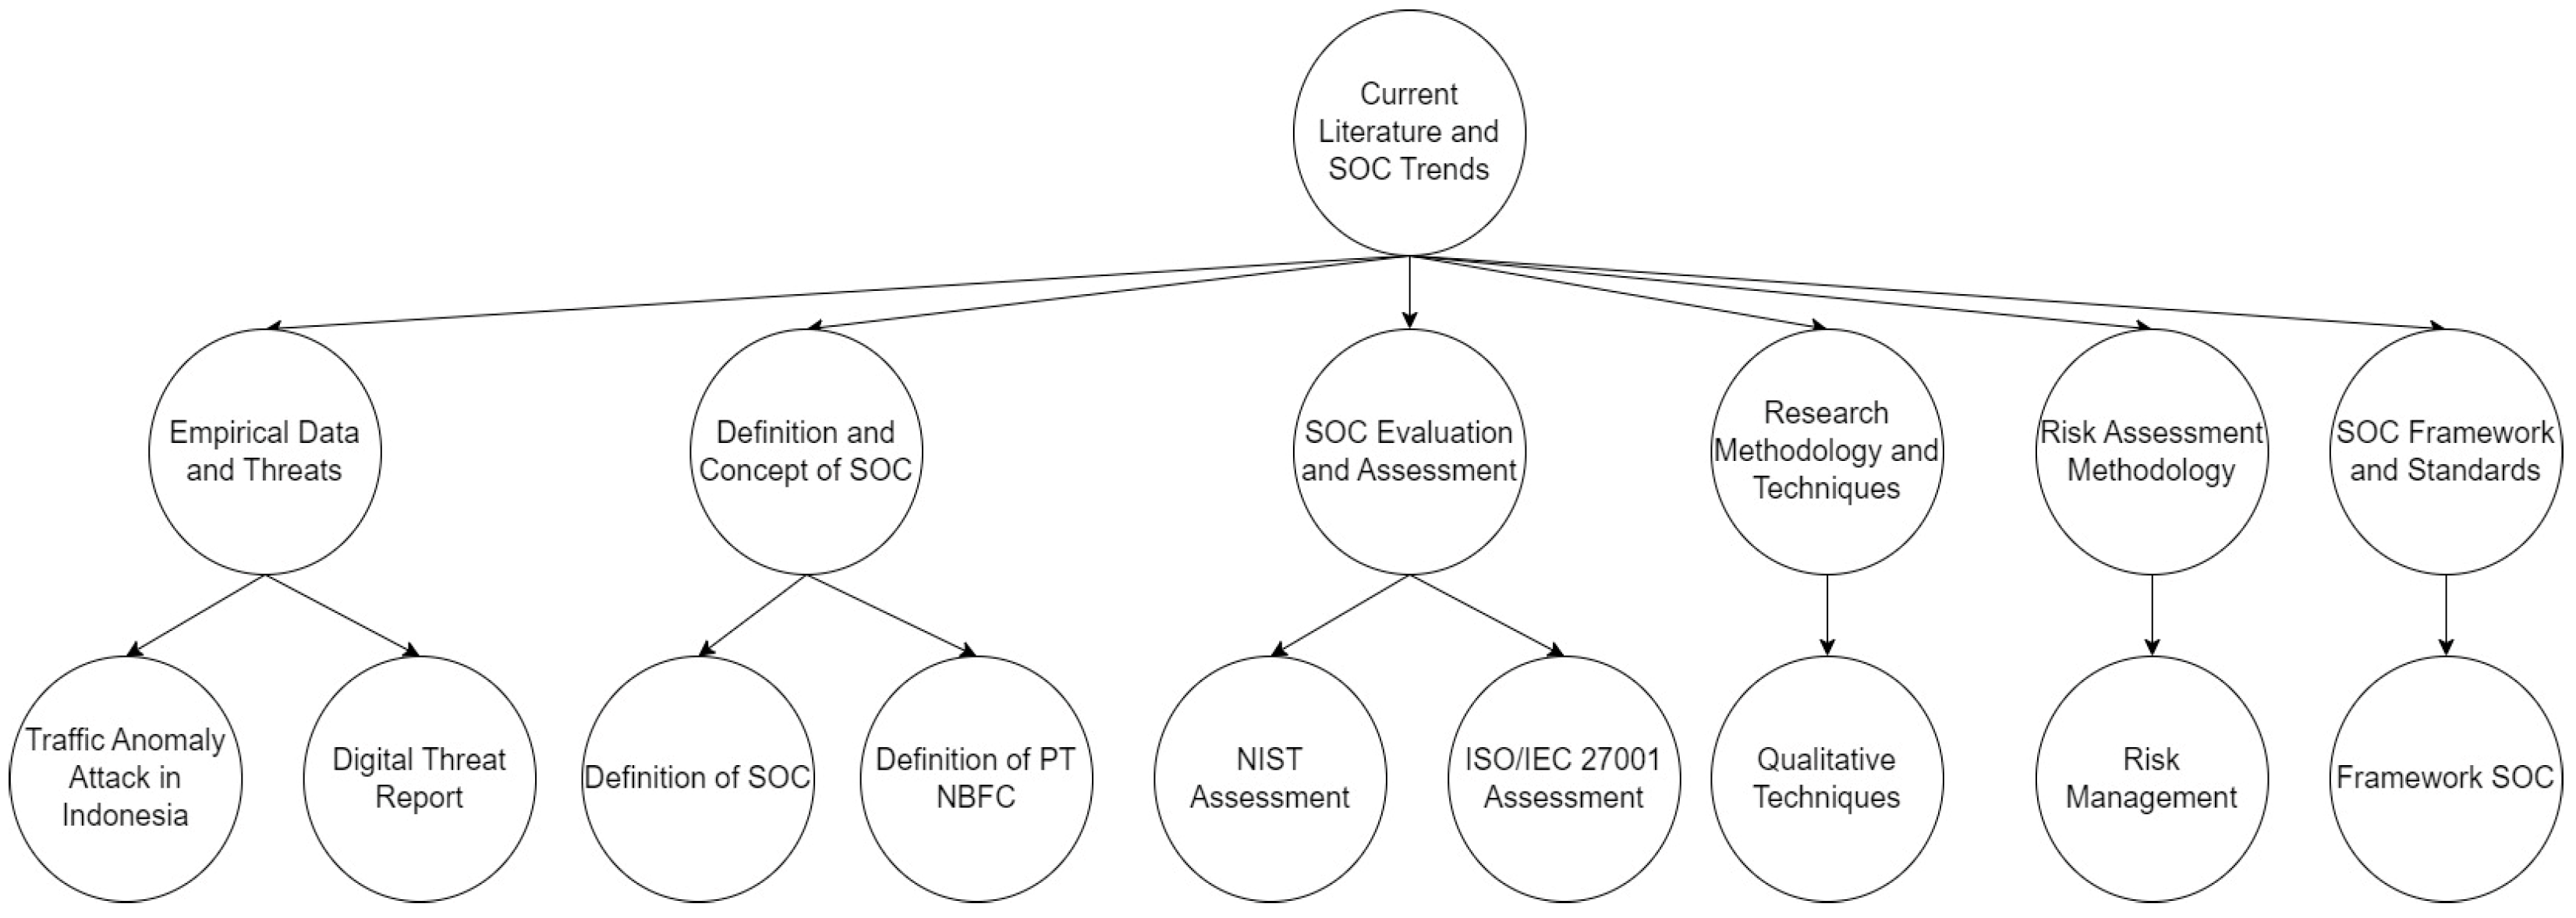
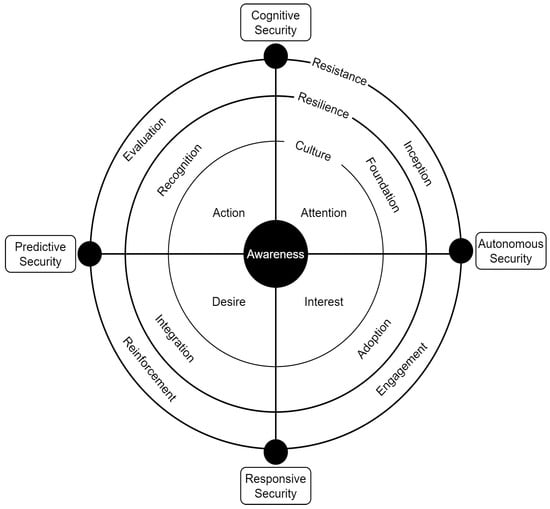
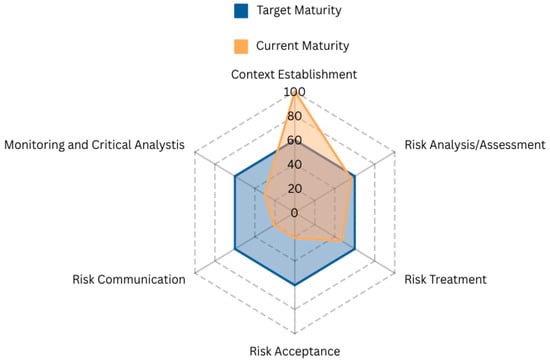
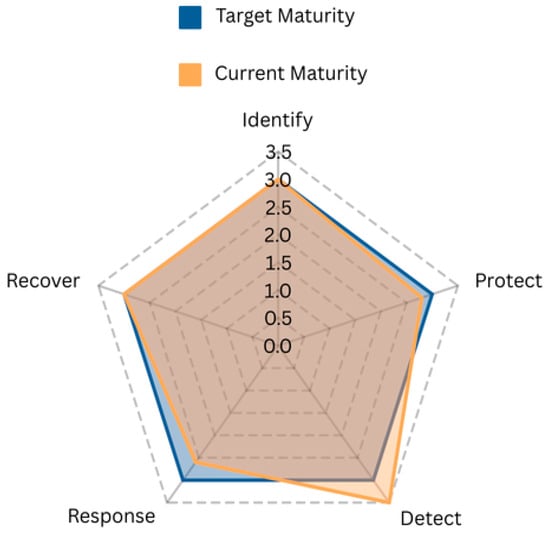
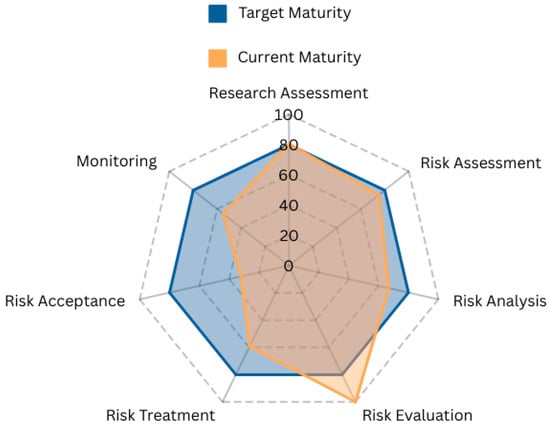
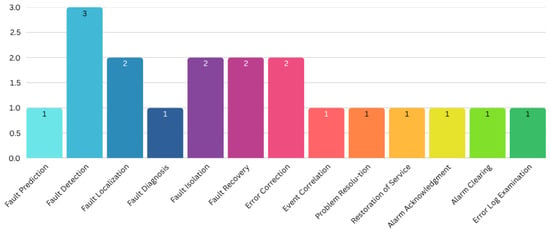
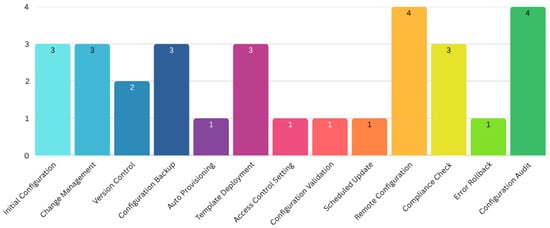
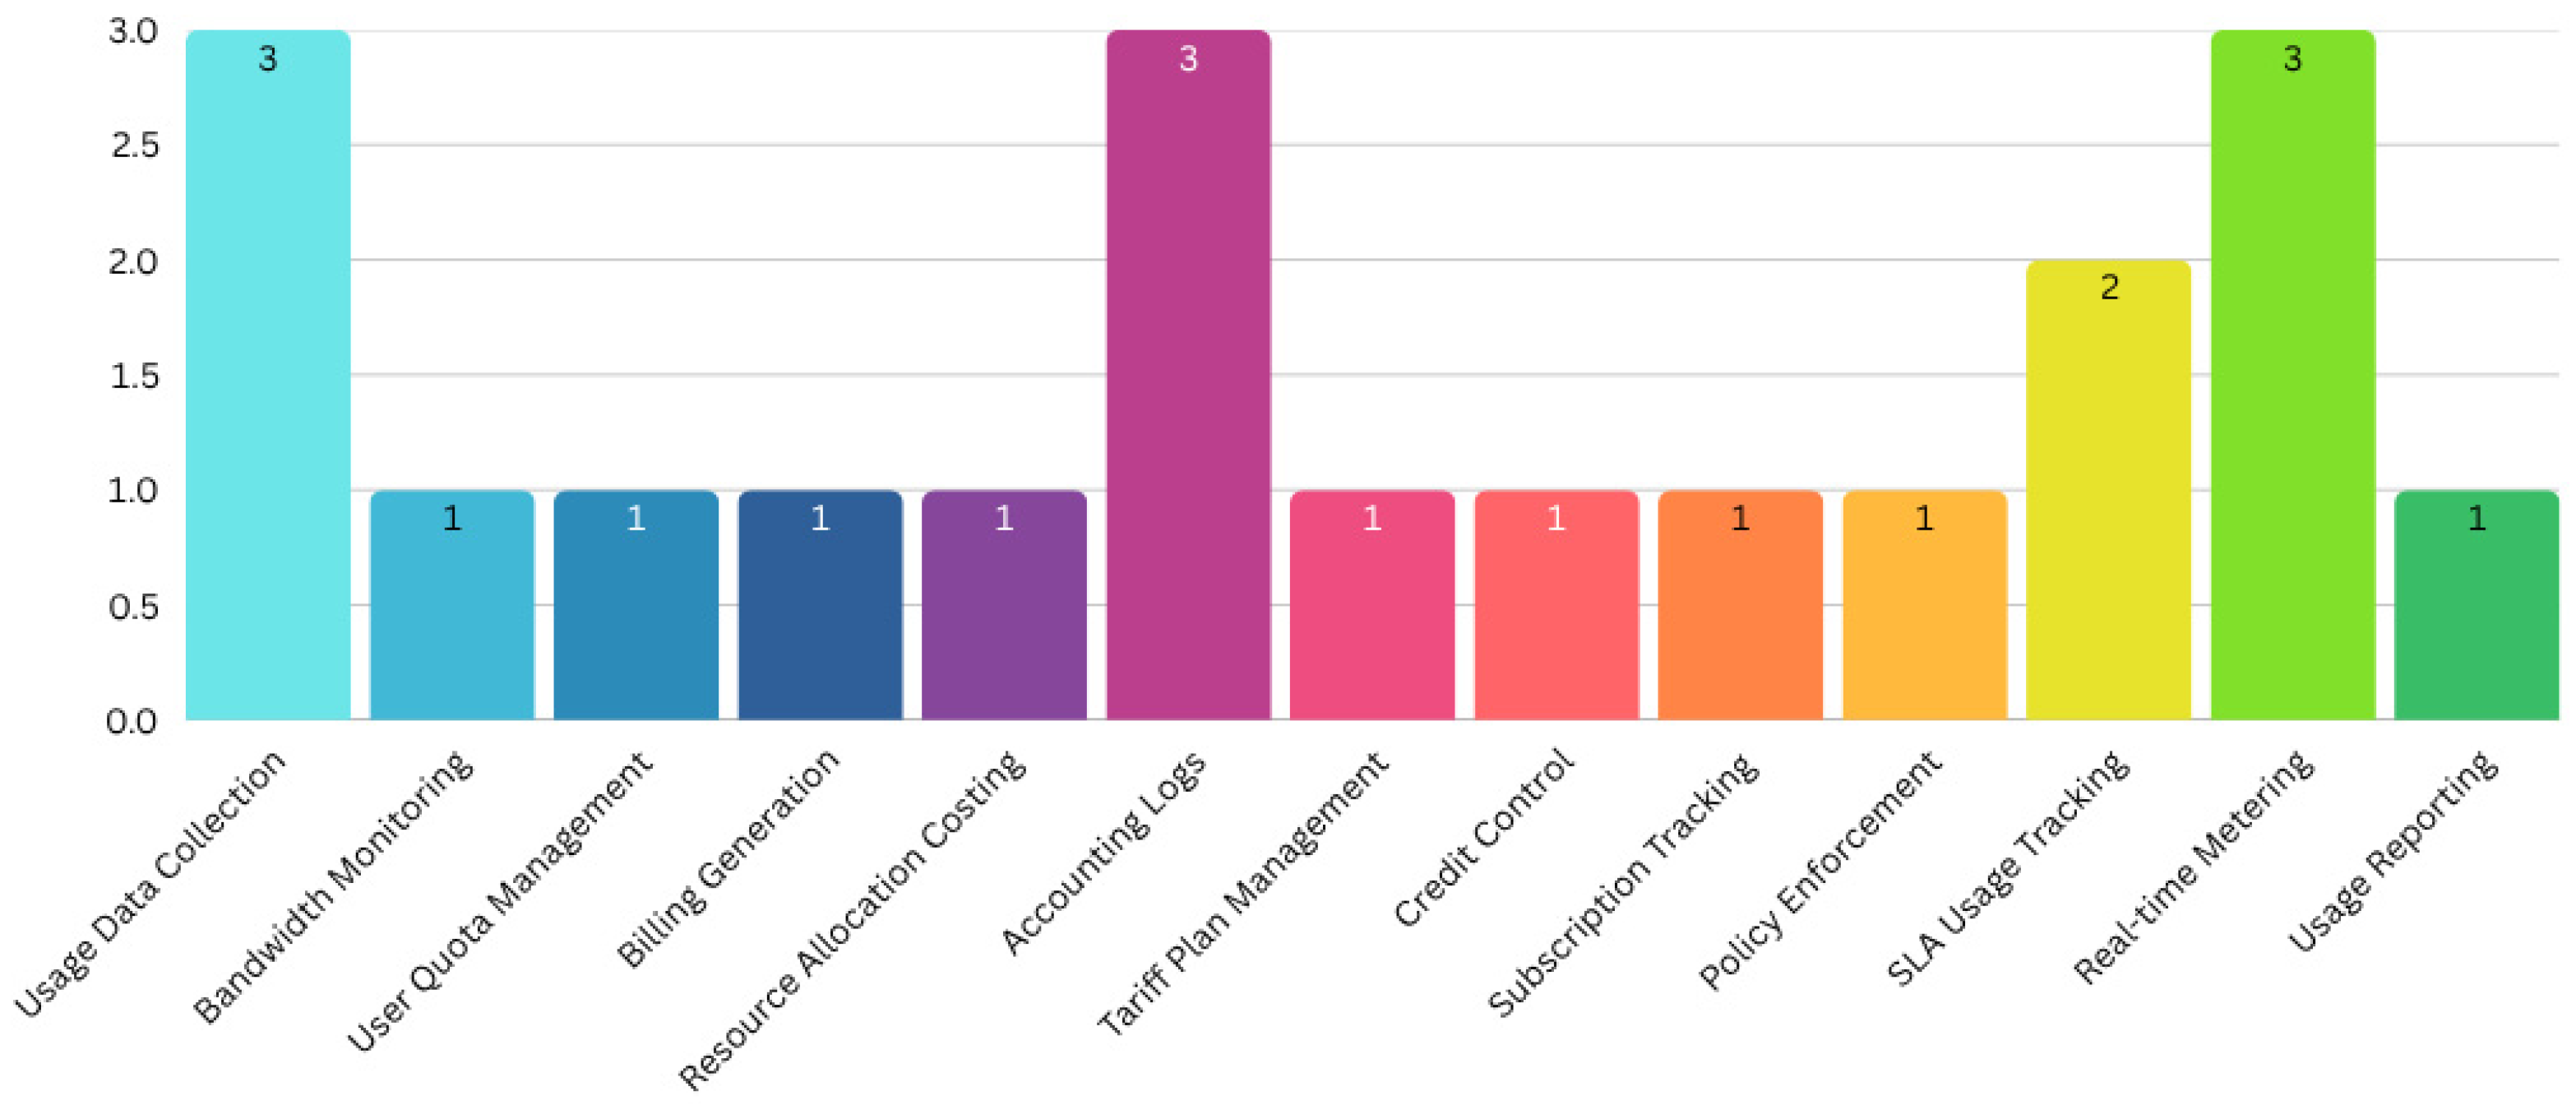
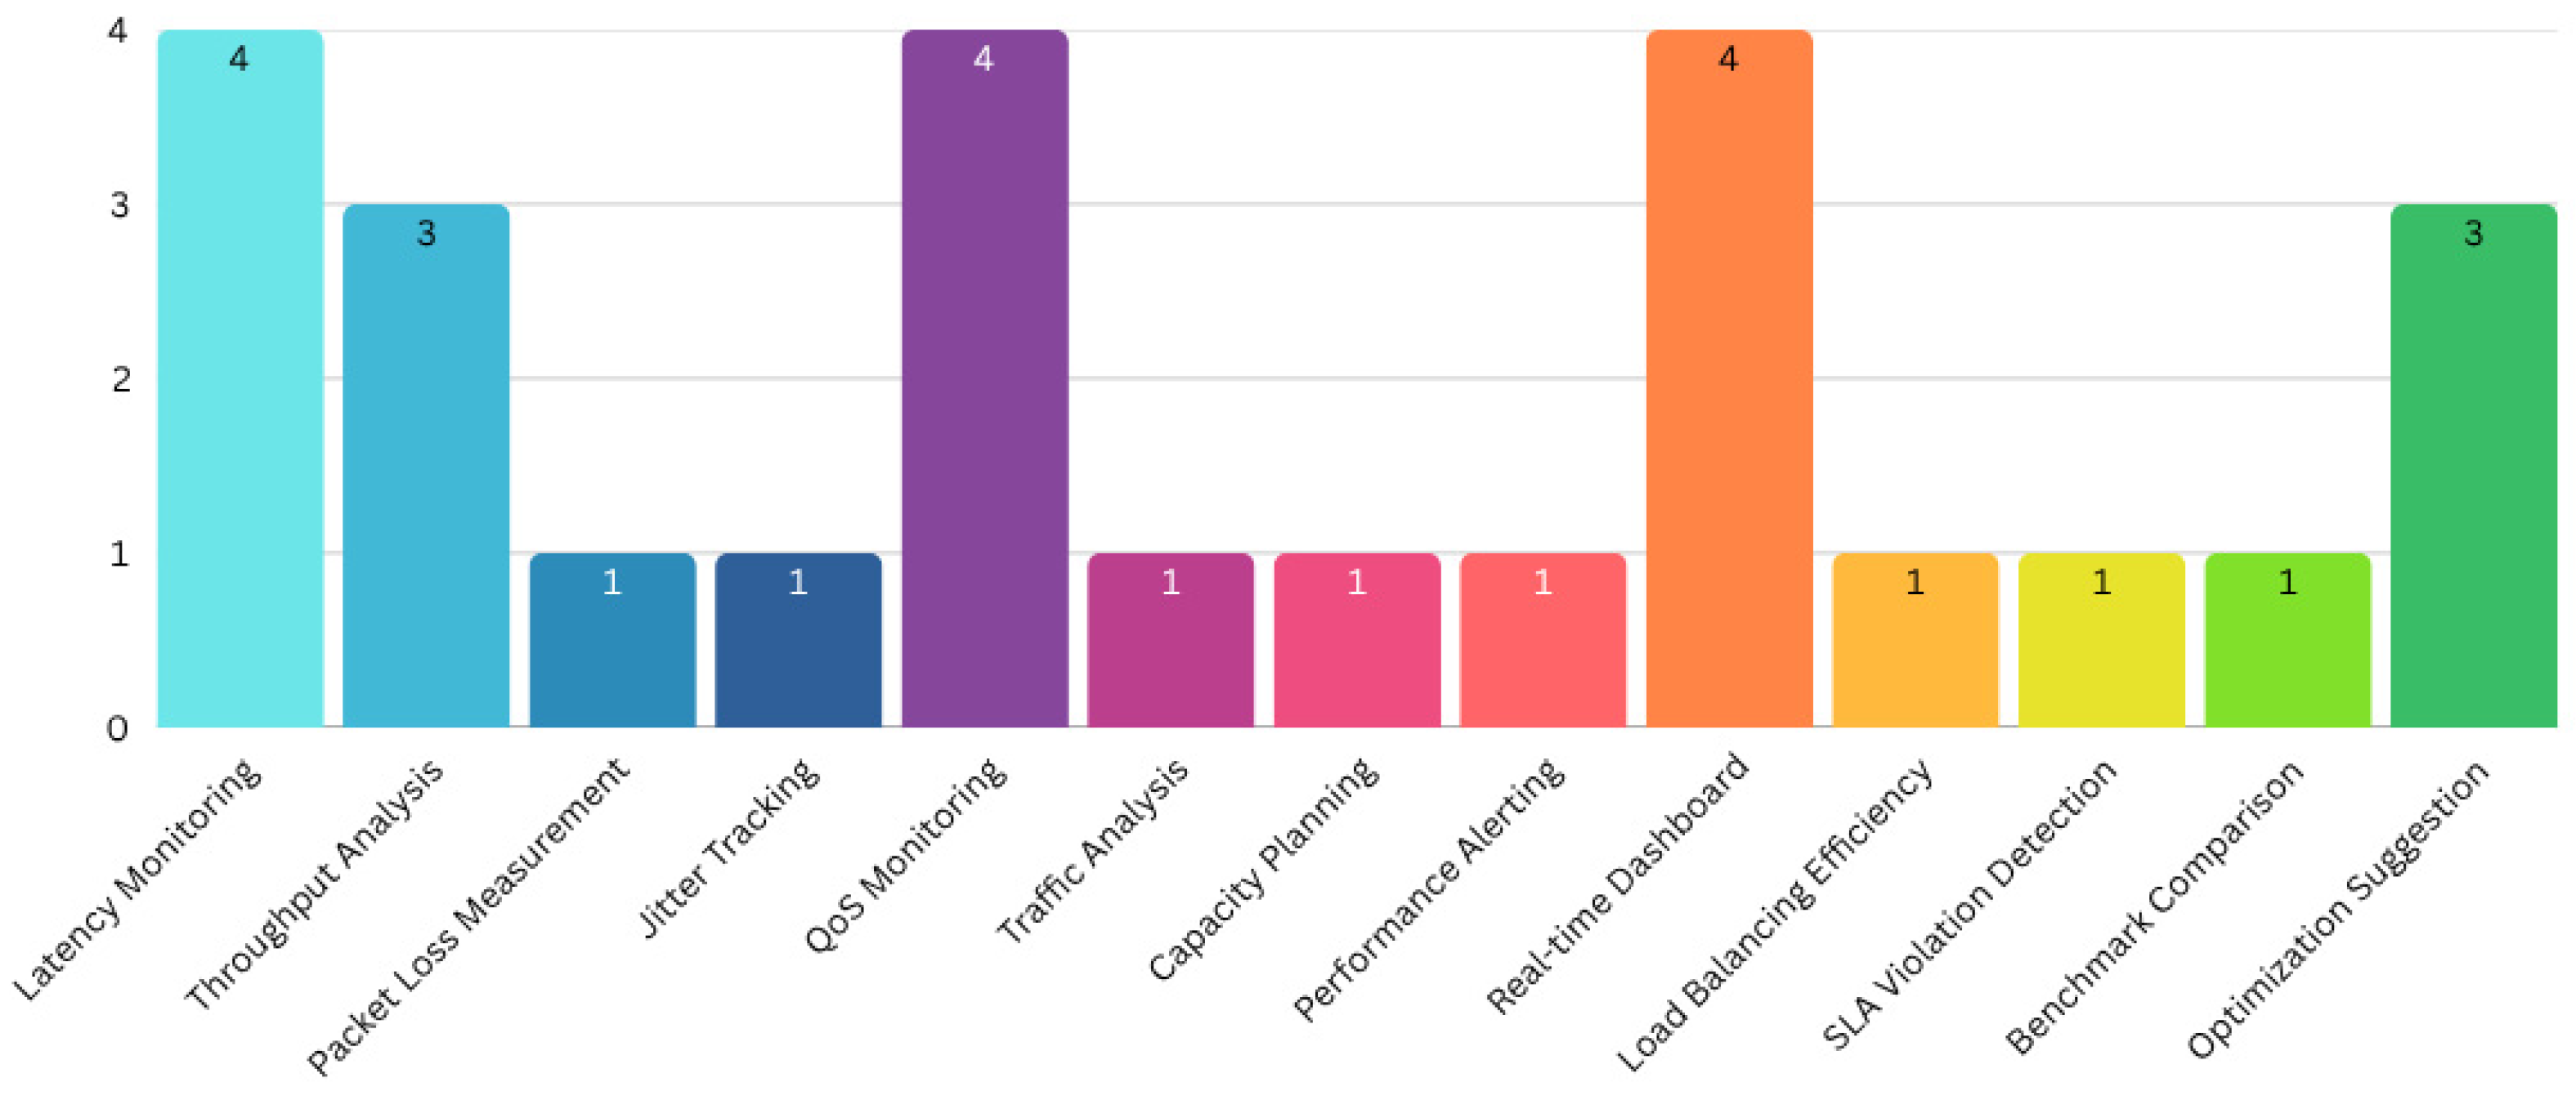
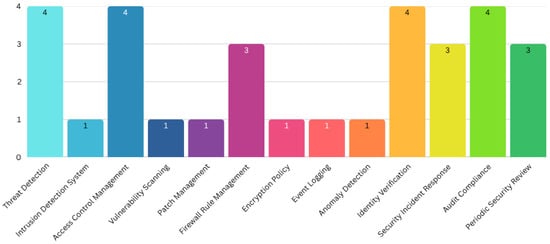
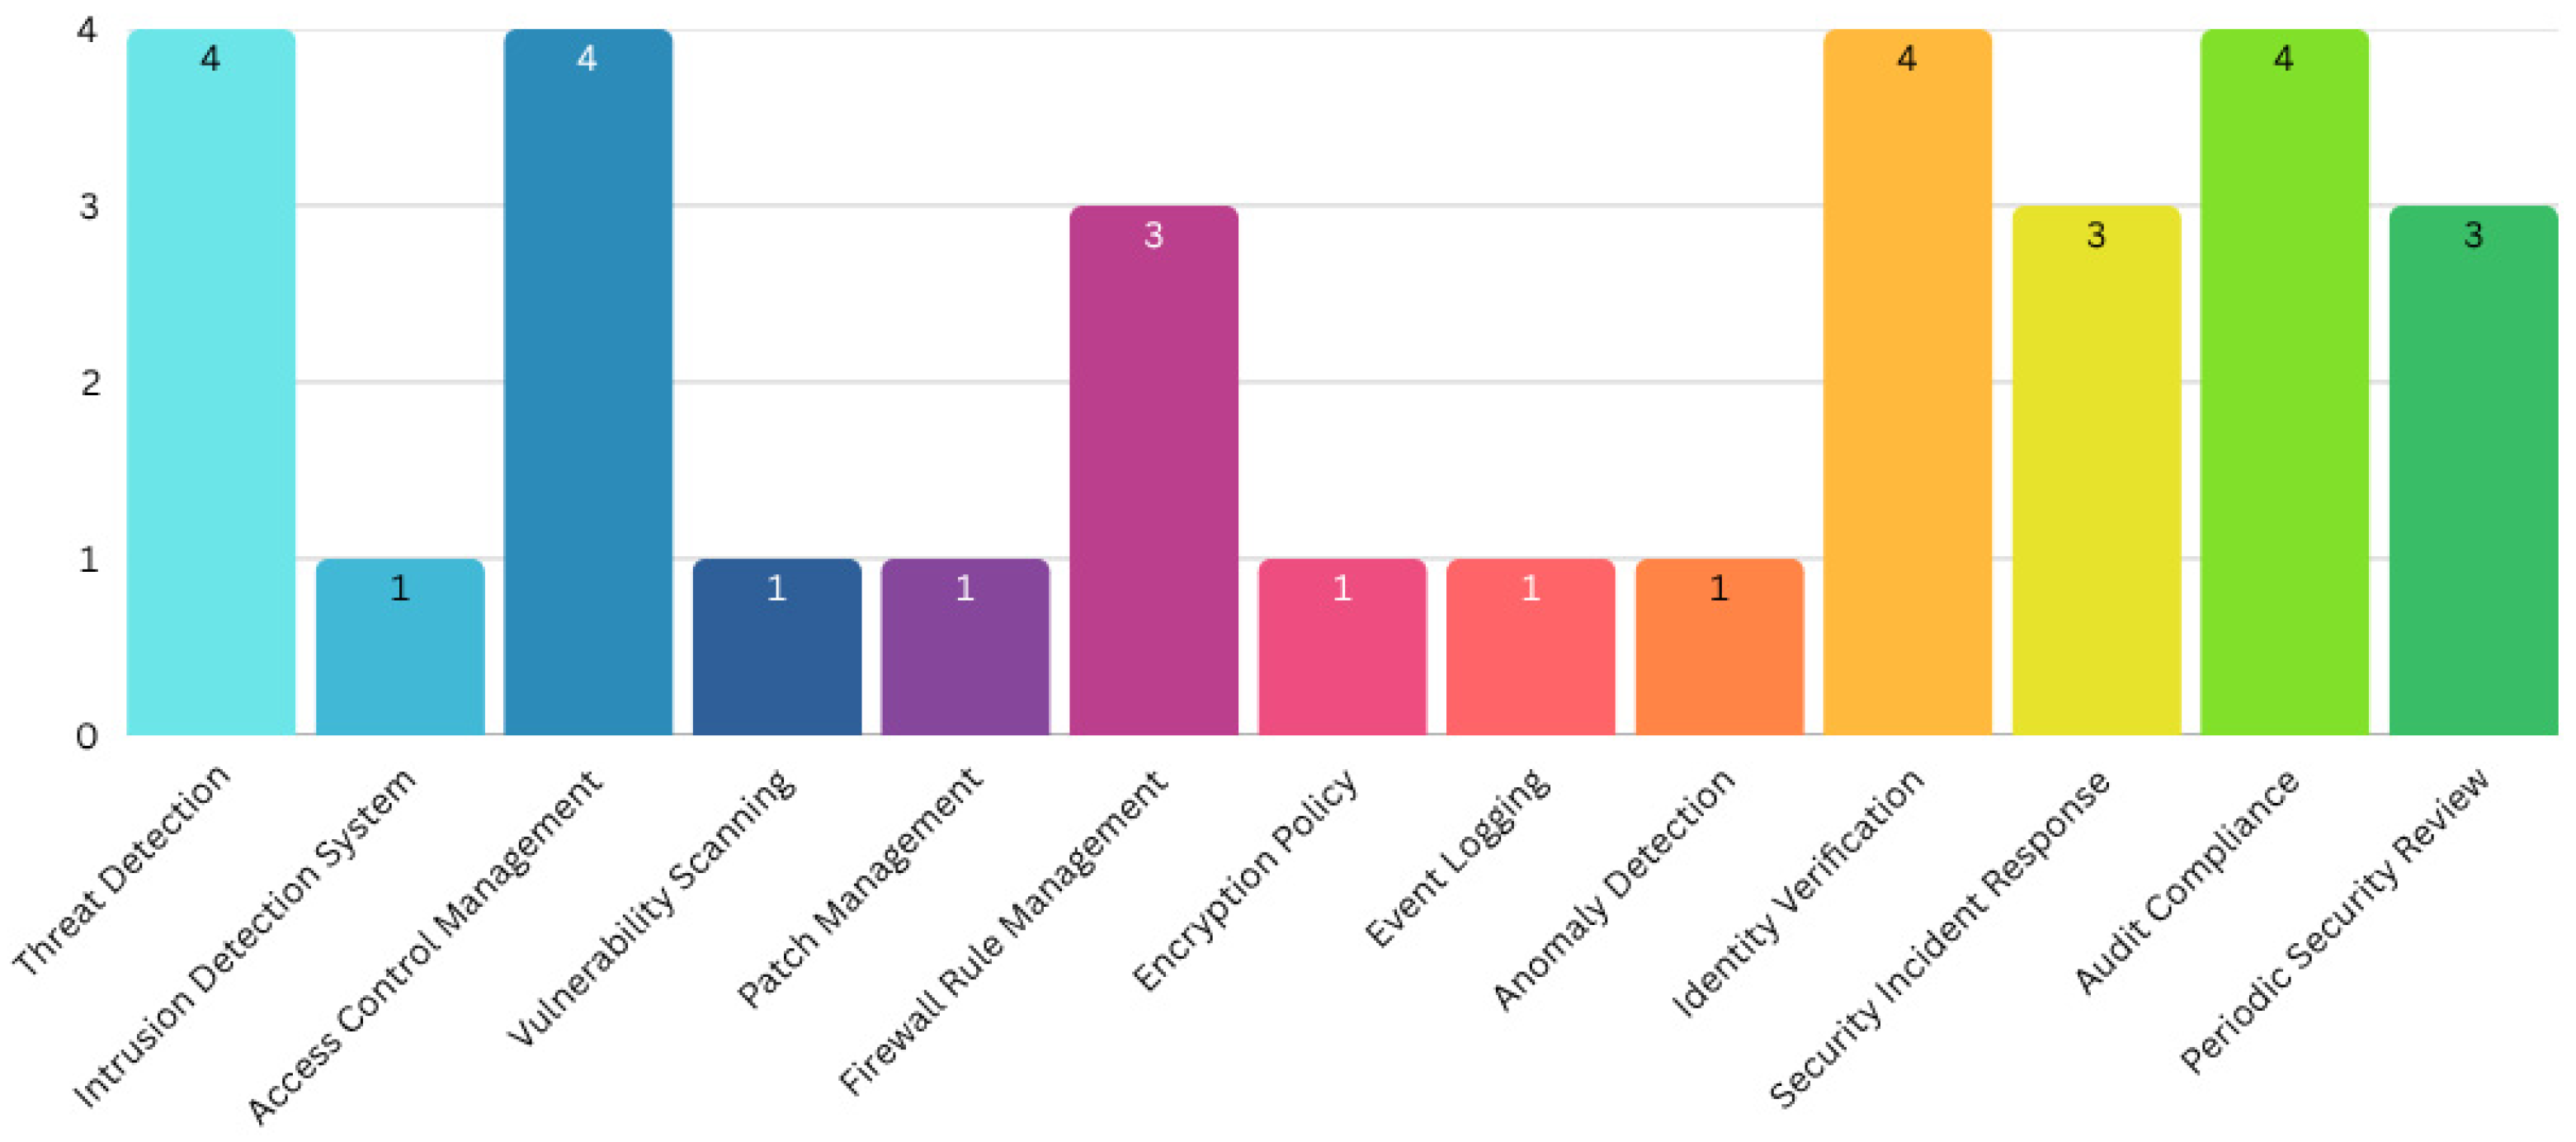
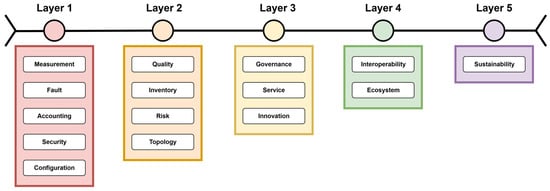
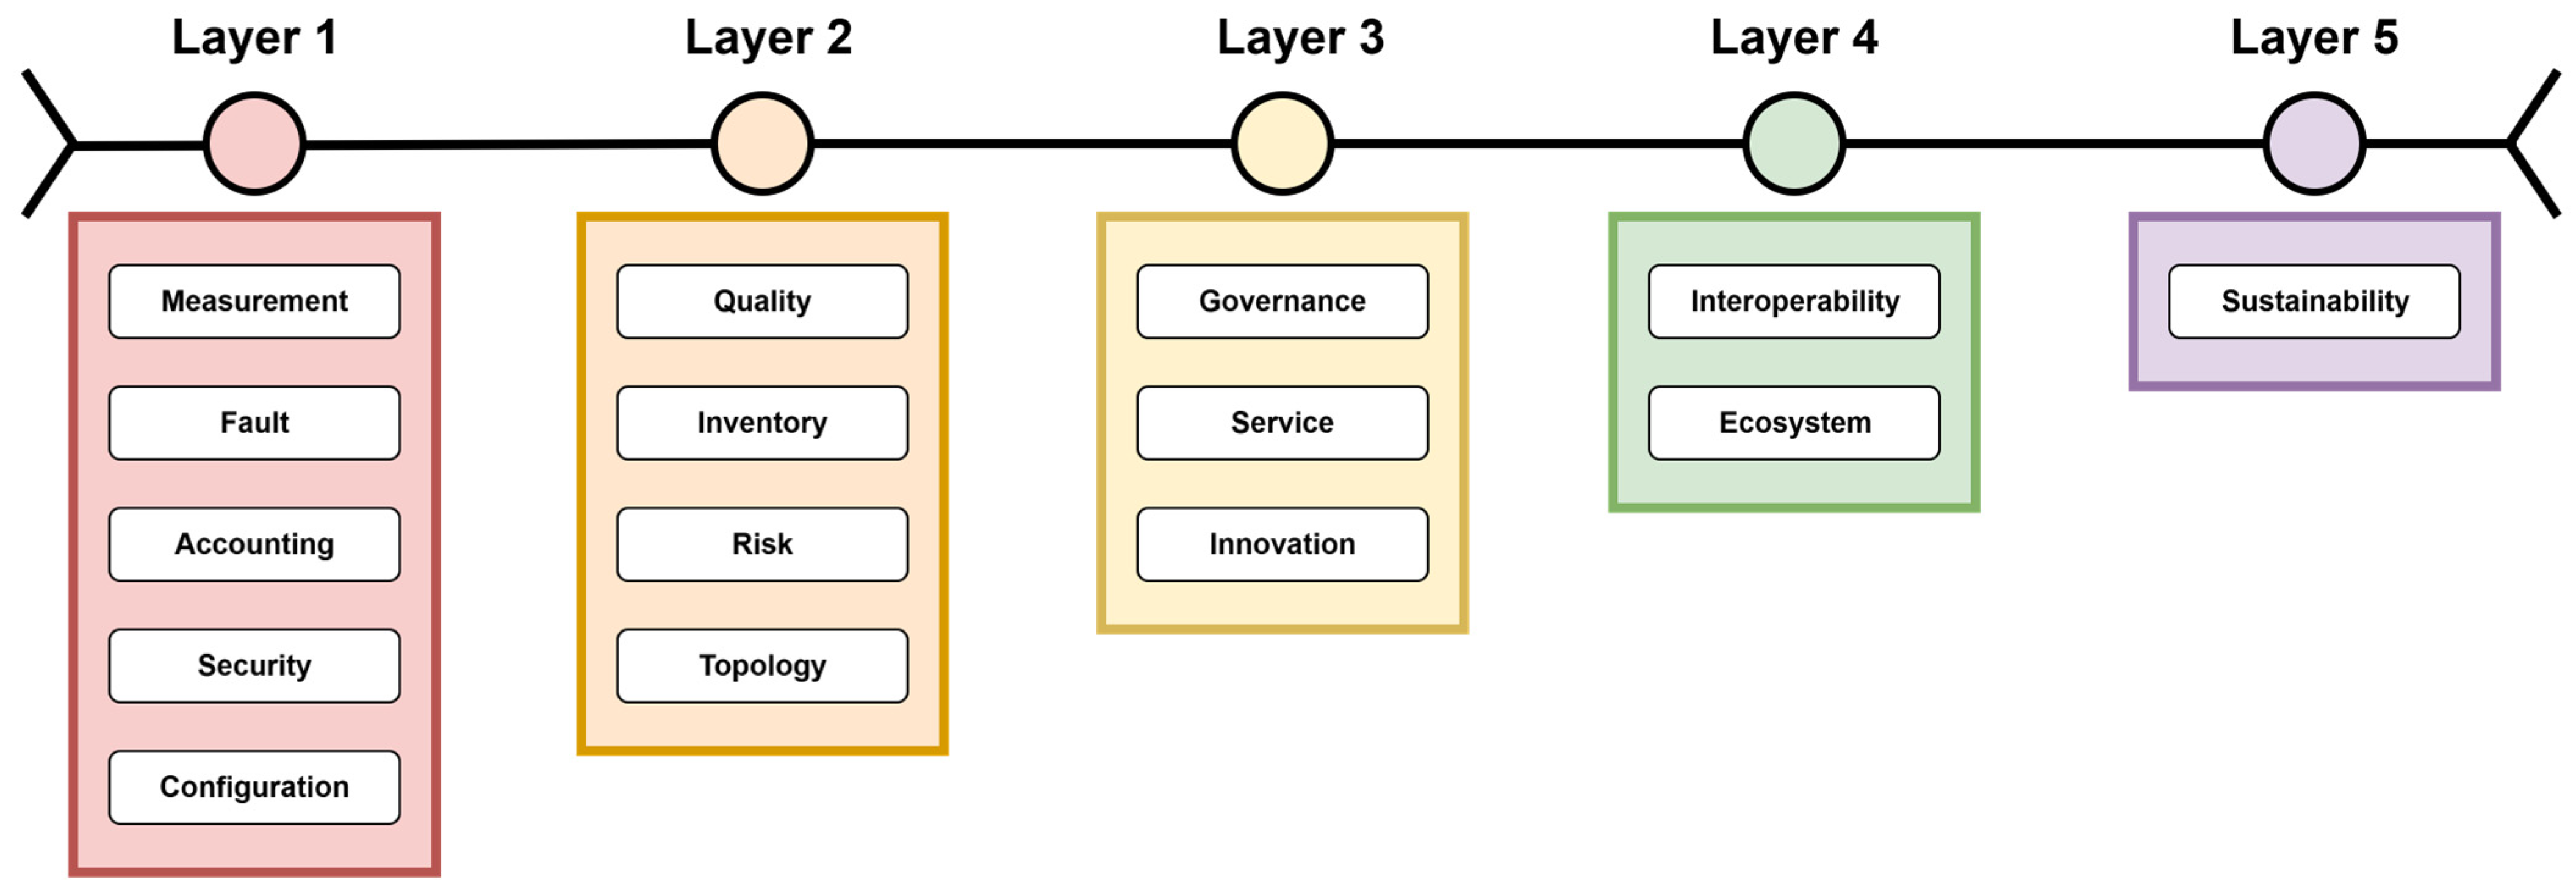

Disclaimer/Publisher’s Note: The statements, opinions and data contained in all publications are solely those of the individual author(s) and contributor(s) and not of MDPI and/or the editor(s). MDPI and/or the editor(s) disclaim responsibility for any injury to people or property resulting from any ideas, methods, instructions or products referred to in the content. |
© 2026 by the authors. Licensee MDPI, Basel, Switzerland. This article is an open access article distributed under the terms and conditions of the Creative Commons Attribution (CC BY) license.