


Abstract
A system is said to be critically observable if the operator can always determine whether the current state belongs to a set of critical states. Due to the communication failures, systems may suffer from intermittent loss of observations, which makes the system not critically observable. In this sense, to characterize critical observability in a quantitative way, this paper extends the notion of critical observability to stochastic discrete event systems modeled as partially observable probabilistic finite automata. Two new notions, called step-based almost critical observability and almost critical observability are proposed, which describe a measure of critical observability for a given system against intermittent loss of observations. We introduce a new language operation to obtain a probabilistic finite automaton describing the behavior of the plant system under intermittent loss of observations. Based on this structure, we also present verification methodologies to check the aforementioned two notions and analyze the complexity. Finally, the results are applied to a raw coal processing system, which shows the effectiveness of the proposed methods.
Keywords:
critical observability; discrete event system; cyber-physical system; stochastic process; Markov chain MSC:
93C65
1. Introduction
In the last decade, numerous reports have addressed state estimation and information security problems in cyber–physical systems (CPSs) under partial observation conditions. Within the realm of discrete event systems (DESs), many studies have concentrated on issues such as opacity verification [1], detectability verification [2,3], attack detection [4,5], predictability [6], and observability [7].
Critical observability [8,9] is a safety property related to state estimation [10,11,12] that concentrates on deciding whether an operator can always identify a given set of critical states in a system through its observation of the system information flow. Several previous works investigated the critical observability of DESs, which are a kind of abstraction of CPSs [13].
By exploiting decentralization and bi-simulation, Pola et al. [14] verify critical observability for networks of finite-state automata. This study proposes a decentralized architecture in which local critical observers perform online detection of critical states, thus significantly reduces the computational effort. Masopust [15] further reveals the computational complexity of verifying critical observability for (networks of) finite-state automata and labeled Petri nets (LPNs). Yan et al. [16] consider the critical observability problem related to a given time step and its inverse problem by using an algebraic model of finite-state automata. Tong and Ma [17] consider communication losses for the problem of k-step and definite critical observability in DESs modeled by finite-state automata. The research in [18,19] extend the formulation of critical observability to timed DESs modeled as max-plus automata and bounded labeled time Petri nets, respectively. Moreover, the research in [20] verifies the critical observability of bounded and live LPNs by using linear integer programming without enumerating the reachability graph. The work of [20] proves a necessary and sufficient condition to check the critical observability when an arbitrary subset of reachable markings describes the critical-state set. Furthermore, the authors extend the results to the case when a critical-state set is modeled by all the reachable markings that satisfy disjunctions of generalized mutual exclusion constraints [21]. The work in [22] also enforces the critical observability of bounded LPNs after verification by using the supervisory control theory [23].
Most approaches to the critical observability of DESs assume that all sensors work properly and all the information recorded by sensors is always transmitted to the operator. However, poor sensor operations or communication malfunctions between the sensors and the operator may lead to event observation losses, which has been considered in diagnosability (codiagnosability) and supervisory control in DESs [24,25,26]. In such a scenario, given a set of predefined critical states, a system under intermittent loss of observations is likely to lose its critical observability to some degree.
In fact, critical observability defined in all the aforementioned works does not take into account the likelihood of violating a critical observability requirement, where only a binary report is outputted: a system is either critically observable or not. However, the binary report cannot provide enough information for the scenarios where different actions of a system have an unequal occurrence likelihood. Thus, the work in [27] formulates the notion of critical observability in a Markov hybrid system called -observability, which characterizes the probability of determining a critical state. Then, it designs an observer to check this property. More precisely, a system is said to be -observable if either we are sure that the system is not in a critical state or the probability of being in a critical state is higher than a given bound . Unlike -observability, we consider other scenarios in which the critical observability with a binary report is not enough for a proper description. In particular, if a non-critically observable system has a small violation probability, it is crucial to consider quantitatively evaluating critical observability via probabilistic models, namely stochastic discrete event systems (SDESs). It is obvious that the work in [27] and our work deal with different kinds of critical observability measures in different kinds of systems. Thus, these two works are incomparable.
This paper makes an investigation analyzing step-based almost critical observability (SA-CO) and almost critical observability (A-CO) of an SDES under intermitting loss of observations modeled by a probabilistic finite automaton (PFA). Compared with a finite-state automaton, a PFA can capture the uncertainty (such as random behaviors) through the state transition probabilities, while the finite-state automaton or the non-probabilistic model cannot. That is to say, a PFA is more powerful to characterize the system accurately than the finite-state automaton. Compared with a hidden Markov model (HMM), the structure of a PFA is relatively simple and the state transitions are directly based on probabilities, while the HMM has a complex structure because it contains hidden states and observed states. Now, the PFA is commonly used in many related problems of state estimation, i.e., diagnosability [28,29], robust and safe fault diagnosis [30,31], prognosability [32], coprognosability [33], detectability [34], and state-based opacity [35,36,37].
The main contributions of this paper are as follows. First, we define the following two notions of critical observability in an SDES under intermittent loss of observations modeled as a PFA, namely SA-CO and A-CO. More precisely, SA-CO requires the a priori cumulated probability of violating critical observability for any sequence with length k and any sequence with infinite length below a given threshold, where k is an arbitrary non-negative integer. A-CO considers the a priori cumulated probability of violating critical observability for any sequence whose prefix does not violate critical observability, and requires such a probability below a given threshold. From the notions of SA-CO and A-CO, the main challenge is to compute the violation language for critical observability under an intermittent loss of observations. Thus, we built a modified system that can capture the behavior of the plant system under an intermittent loss of observations using a PFA. In addition, we propose an algorithm to construct a new finite information structure that can capture the violation language for critical observability of the plant system under the intermittent loss of observations using a PFA and its isomorphic Markov chain. Based on these results, necessary and sufficient conditions are presented to verify SA-CO and A-CO of SDESs under intermittent loss of observations, and the complexity is also given.
Note that the formulations of SA-CO and A-CO are motivated by the formulations of step-based almost current-state opacity and almost current-state opacity in [35], step-based almost initial-state opacity and almost initial-state opacity in [36], and almost k-step opacity and almost infinite-step opacity in [37]. In fact, critical observability is (inversely) related to current state opacity, which aims to protect secret states by ensuring that the current state estimate of a system always includes at least one non-secret state. In contrast, critical observability requires the current state behavior to be identified as critical or non-critical. Thus, SA-CO and A-CO are different with step-based almost current-state opacity and almost current-state opacity in [35]. Moreover, all the above methods in [35,36,37] do not consider communication malfunctions between the plant and the operator. Thus, the methods in [35,36,37] cannot be used to solve the problem raised in this paper, and it is necessary to introduce new methods to verify SA-CO and A-CO in SDESs. To the best of our knowledge, this is the first work to deal with SA-CO and A-CO in SDESs, which may benefit practitioners in the energy and resource industries, where stochastic events are extensively prevalent.
The rest of this paper is organized as follows. Section 2 provides some foundations of a finite-state automaton and a PFA. Section 3 presents how to build a PFA for an SDES that suffers from the intermittent loss of observations. In Section 4, we show the problem formulation of this paper, i.e., SA-CO and A-CO under intermittent loss of observations. Section 5 and Section 6 illustrate the methods to verify SA-CO and A-CO under intermittent loss of observations, respectively. The application of the proposed methods to engineering problems is introduced in Section 7. Finally, Section 8 concludes the paper, and suggests directions for future work.
2. Preliminaries
This section briefly introduces some basic knowledge used throughout the paper, including finite-state automaton (deterministic finite automaton and nondeterministic finite automaton) and probabilistic finite automaton.
2.1. Finite-State Automaton
Let be a set of non-negative integers, E be an alphabet, and be the Kleene-closure [38] of E. A language is defined as a set of strings. We denote the prefix-closure of L by , i.e.,
For a string , we denote by if and denote by if . For any string u, let denote the length of u. For any set A, let denote its cardinality and denote its power set.
A deterministic finite automaton (DFA) is denoted by , where X is the state set, is the deterministic (partial) transition function, and is the initial-state set.
A nondeterministic finite automaton (NFA) is denoted by , where X is the state set, is the nondeterministic transition function, and is the initial-state set. The set of all transitions in G is also denoted by . The active event set at a state is defined as
The function can be extended to the domain by induction as shown in [38]. For the sake of simplicity, let denote . The language generated by G is defined as
The event set E is partitioned into two disjoint sets: , where is the set of observable events and is the set of unobservable events. The natural projection is defined as (i) ; if and otherwise; (iii) . Moreover, the inverse projection is defined as .
Given an NFA G and a set of states , let denote the set of states that are unobservable reached from some state in , i.e., . We use to denote the set of states that are directly reachable upon the occurrence of an observable event , i.e., .
An observer of an NFA G is defined by a DFA , where , and for any , , . Actually, it is necessary to only construct the accessible part of the observer from the set of initial states (the set of states reachable from the set of initial states through some event sequences ).
2.2. Probabilistic Finite Automaton
An SDES is modeled as a PFA [39], where is an NFA, is the transition probability function, and is the initial-state probability distribution vector such that : and :
Particularly, for any , , let denote the probability that event e occurs and the PFA reaches state from state x. If , then state x cannot reach state through event e. We assume that
For any string and state , we denote the occurrence probability of u by , and the probability that u has occurred and the state of the system becomes x by . Then, for any and , we have
A Markov chain is denoted by , where is the transition probability from state x to state for , and is the initial-state probability distribution vector. Let denote the transition probability matrix of M, whose th element is . Given , the current-state probability distribution vector after k steps is defined as . For any PFA , its associated Markov chain or is denoted as , whose transition probability is defined as
3. Modeling the Behavior of PFA Under Intermittent Loss of Observations
This section presents how to build a PFA model that can capture the behavior of an SDES under intermittent loss of observations.
Let be a partition of E, where denotes the set of observable events associated with intermittent loss of observations and denotes the set of observable events that do not suffer from intermittent loss of observations. Moreover, let and .
The dilation function is defined as , where , , if , , if , and where and . The dilation function operation can be extended to languages as follows:
Based on the dilation function D, given an NFA , if it suffers from the intermittent loss of observations, it is defined as , where if and if .
In a PFA, for all , we use to denote the probability that event occurs at state x, leading to state , given that event e occurs at state x, leading to state . In addition, the transition probability dilation function is defined as , where if ; and , if . Then, the PFA characterizing the behavior of that suffers from the intermittent loss of observations is denoted as . Actually, the intermittent loss of observations in this paper can be seen as the transition missing. However, since the PFA has contained all the potential states of the real system, there is no state missing in this paper.
Note that in this paper, the transition probabilities and the event loss probabilities are known and accurate, which is commonly adopted in the literature. Actually, in most of the cases, the number of events that can occur at a given state of a system is fixed, and the probabilities of the occurrence of these events can be usually obtained based on the physical properties of events. In addition, compared with the intermittent loss of observations on sensors, sensor misclassification, false positives/negatives, or correlated sensor failures can generally be seen as faults occurring in the system, which is related to fault diagnosis or prognosis in SDESs.
4. Critical Observability in SDESs Under Intermittent Loss of Observations
This section establishes the formulation of SA-CO and A-CO in SDESs under intermittent loss of observations. To achieve this aim, we first recall the notion of critical observability in DES without considering the probability and the intermittent loss of observations.
Definition 1
([15]). Given an NFA with , a natural projection P, and a set of critical states . The system G is critically observable with respect to and if or for any , where .
In this paper, we assume that . Particularly, if , then G is undoubtedly critically observable. However, for a critically observable NFA G, if it suffers from an intermittent loss of observations, its critical observability may not hold according to Definition 1. In addition, note that a system does not satisfy critical observability even if the probability of a sequence that violates critical observability is very small. In order to quantify critical observability, we introduce the following definition that can characterize the probability of violating critical observability under an intermittent loss of observations.
Definition 2.
Given a PFA , a projection , the probability for all , and a set of critical states , let with be a PFA characterizing the behavior of under an intermittent loss of observations, defined as follows:
Then, PFA is step-based almost critically observable (SA-CO) with respect to , , , and a threshold β if the following two conditions hold:
Note that any sequence w in will violate critical observability, i.e., the operator cannot determine whether the current state of the system is critical or not through the observation . It is obvious that if G satisfies critical observability under an intermittent loss of observations, then also satisfies SA-CO for any under the intermittent loss of observations.
Example 1.
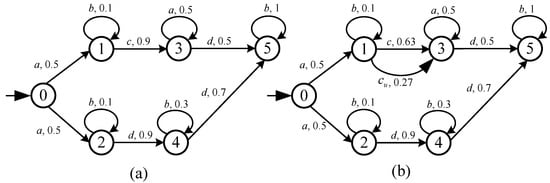
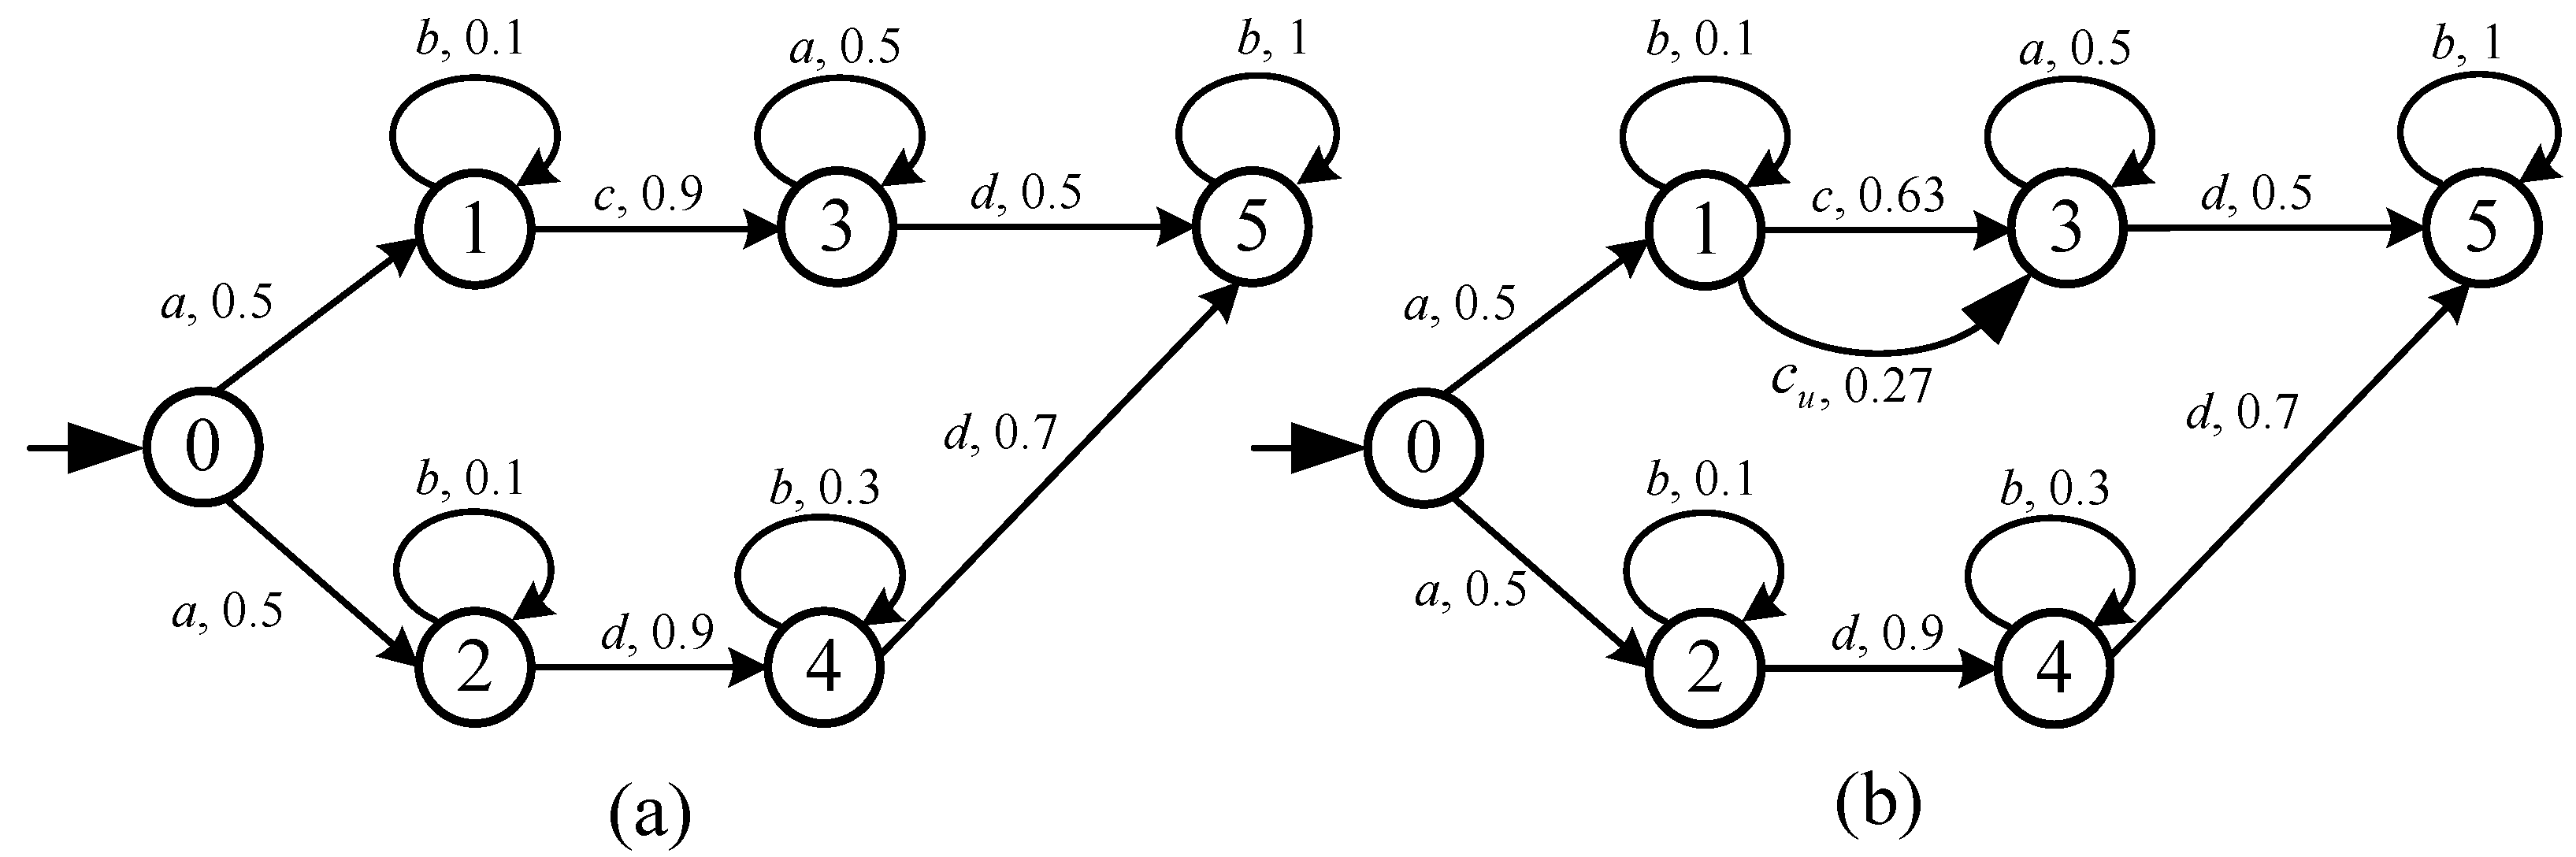
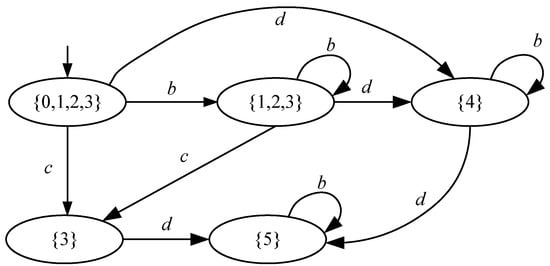
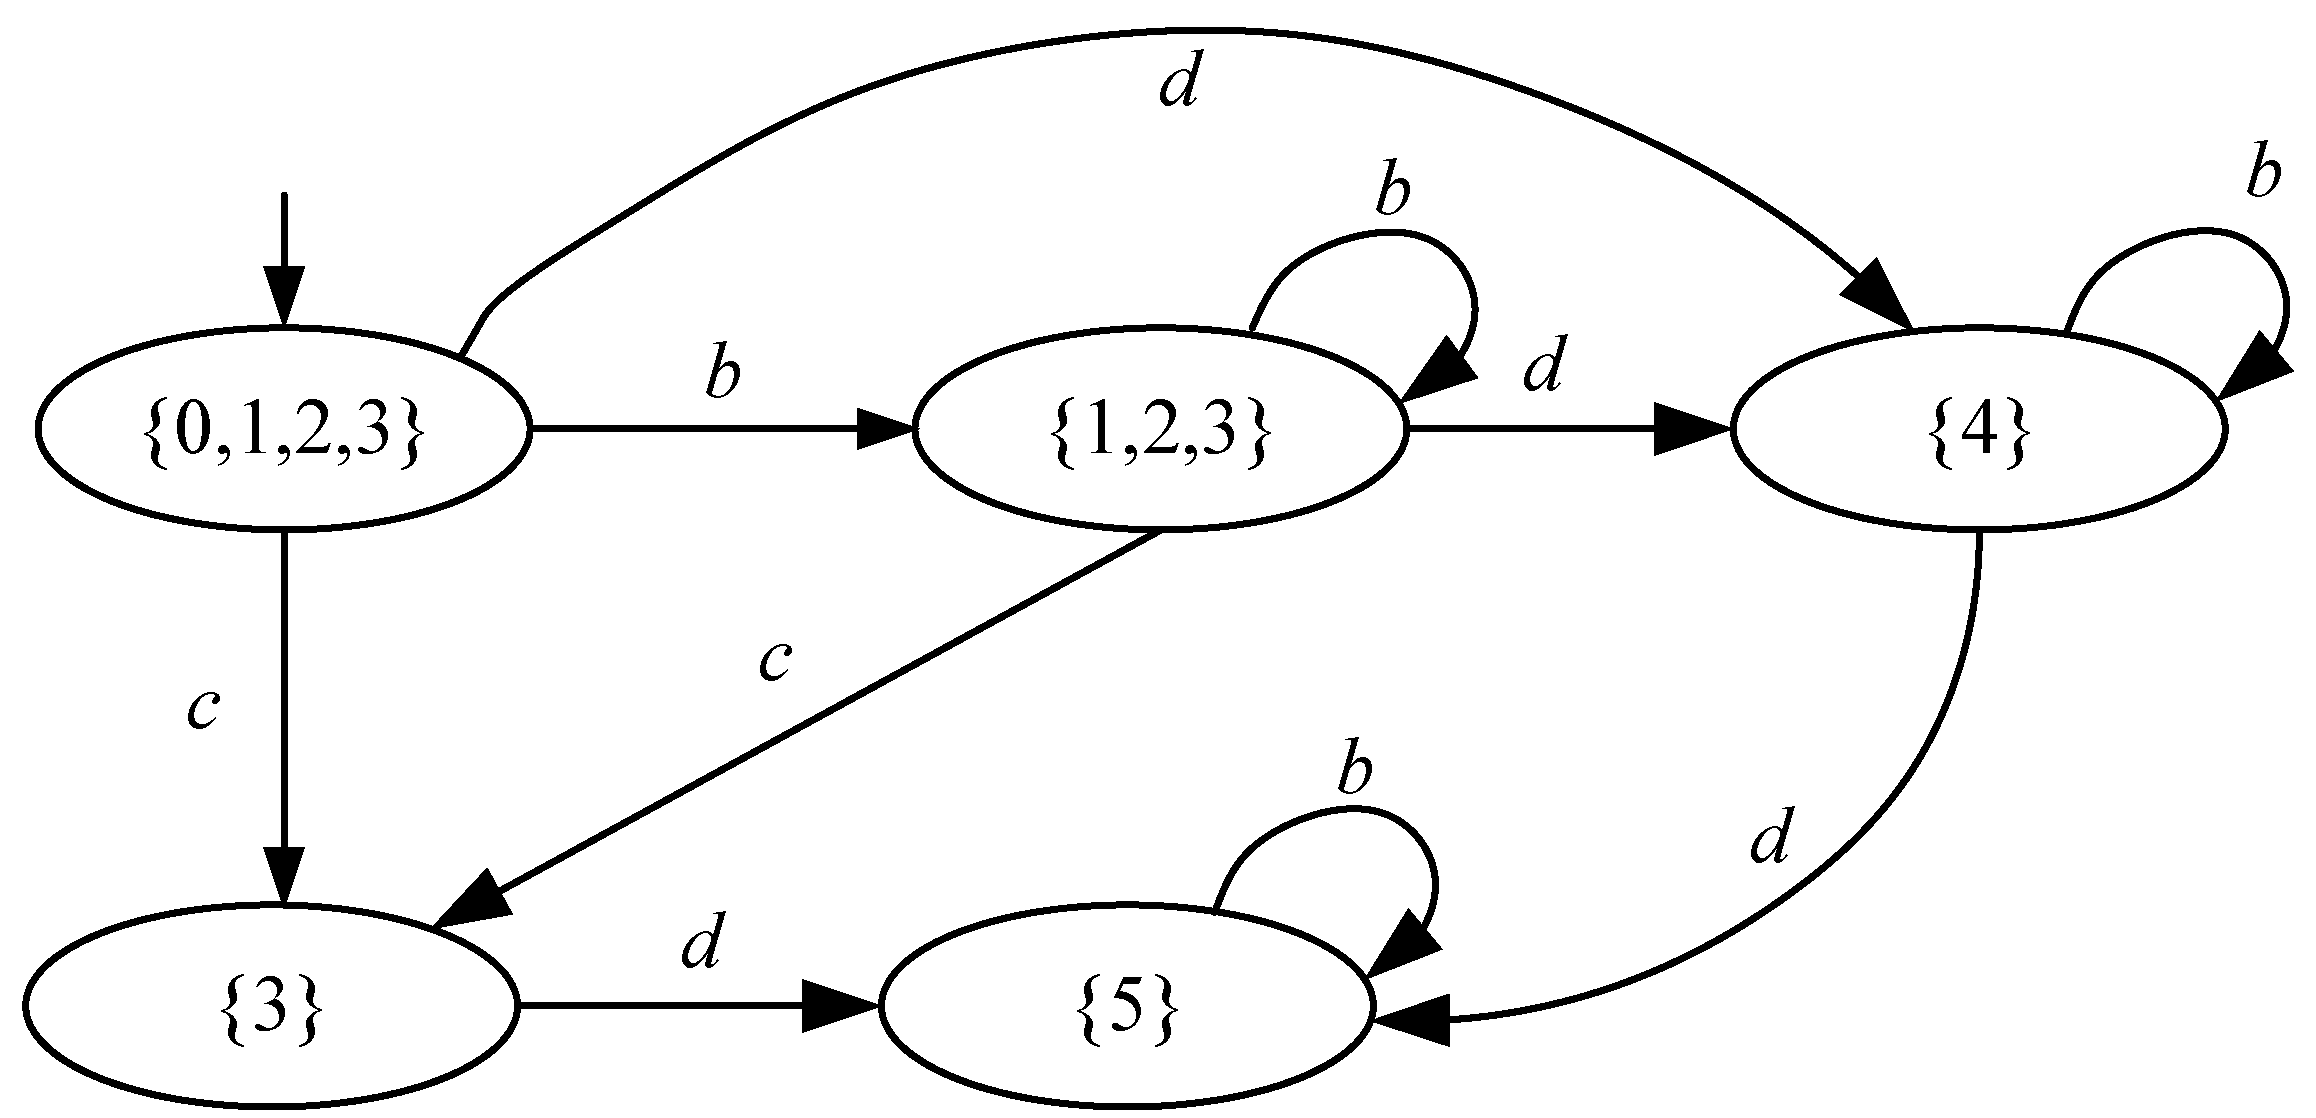
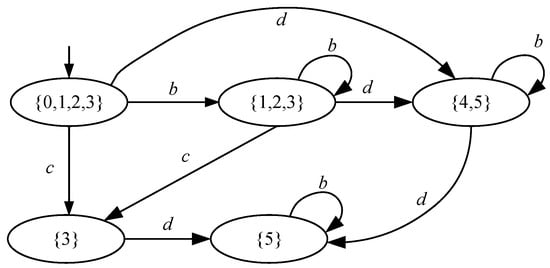
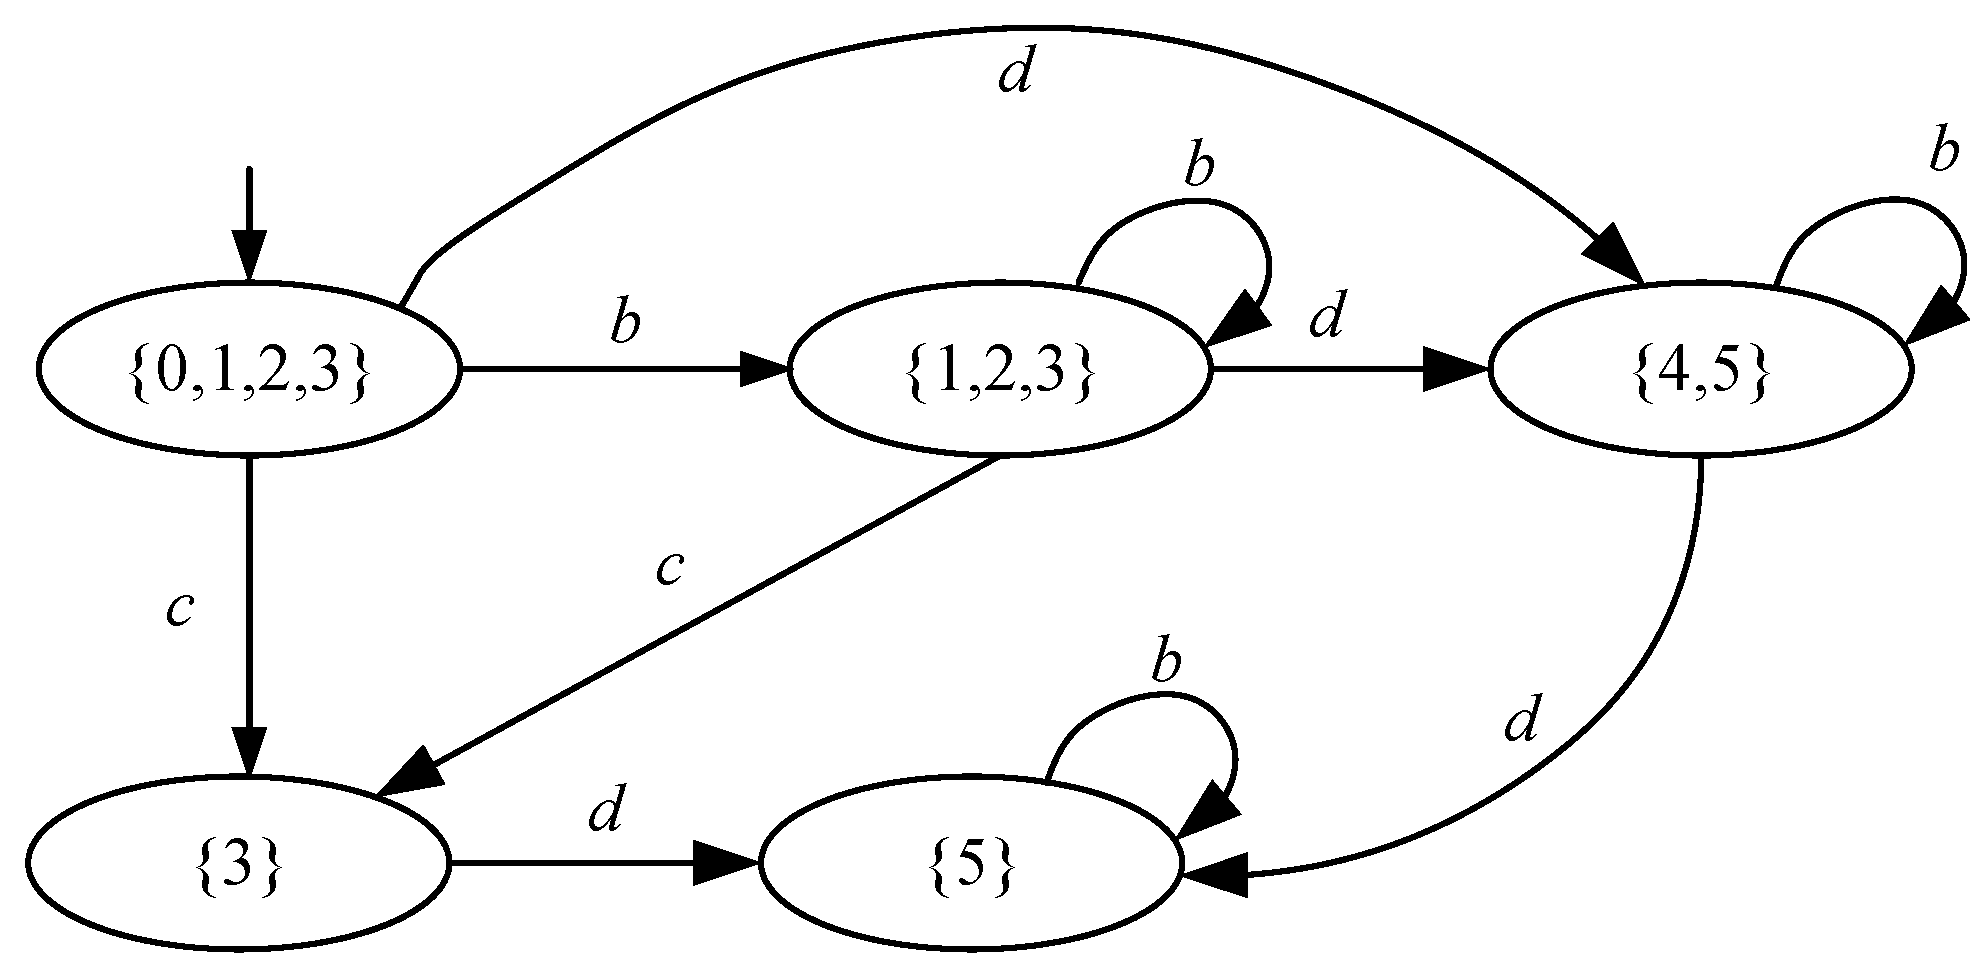
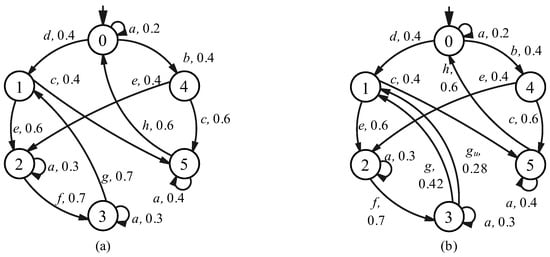
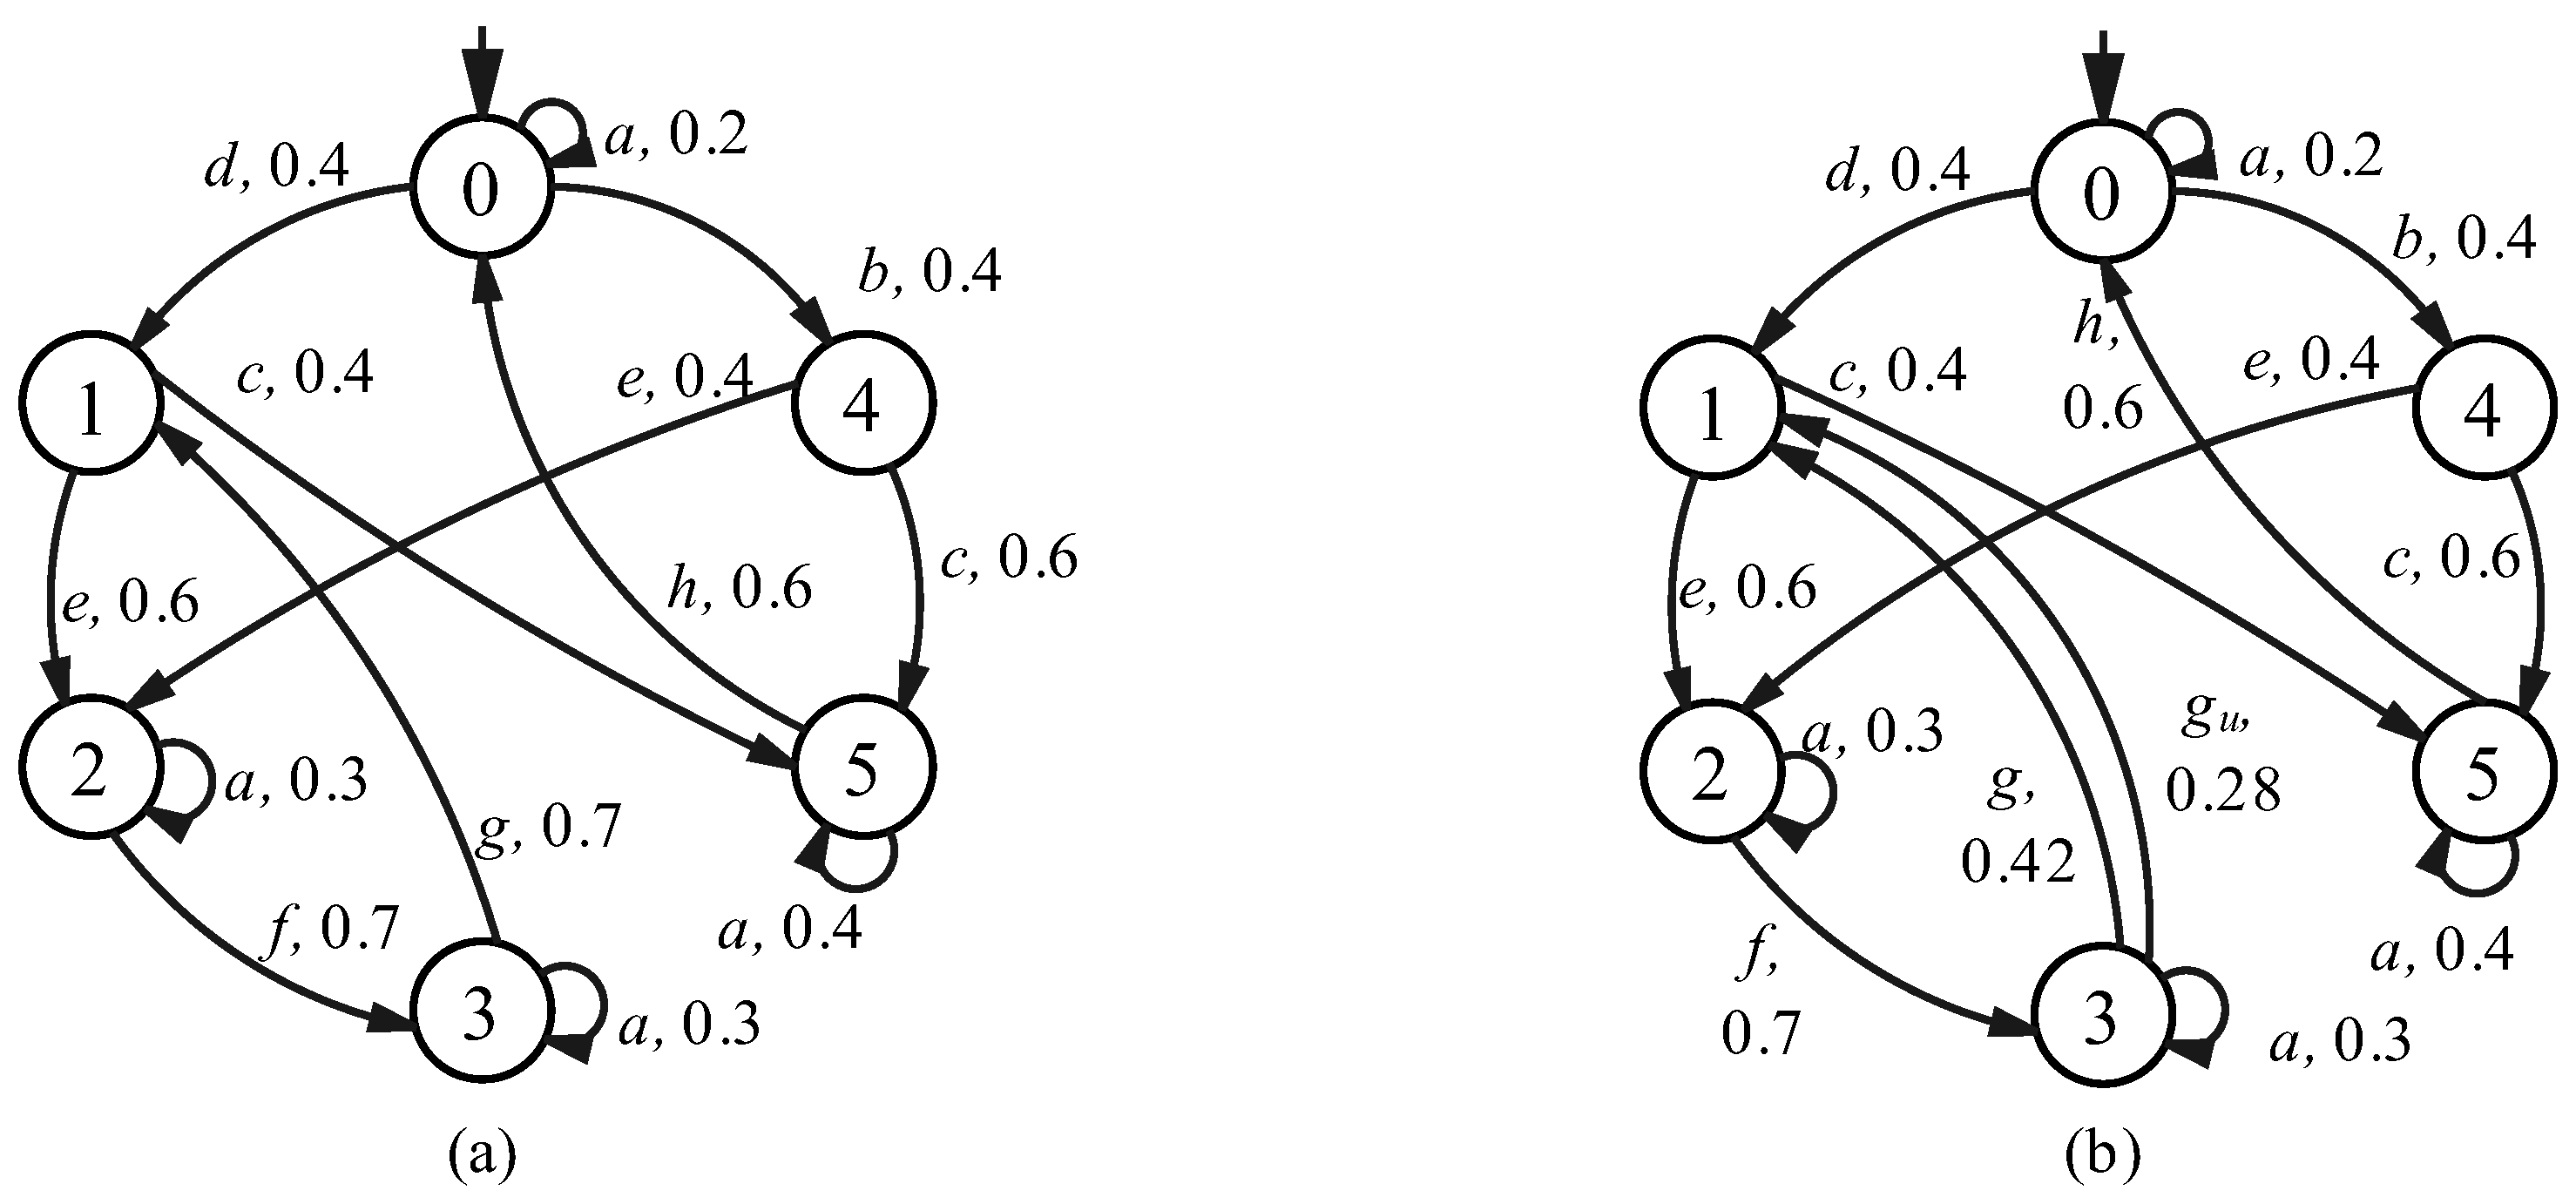
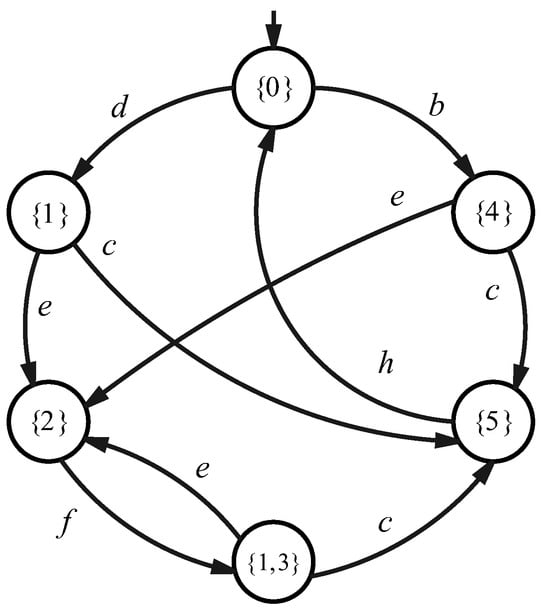
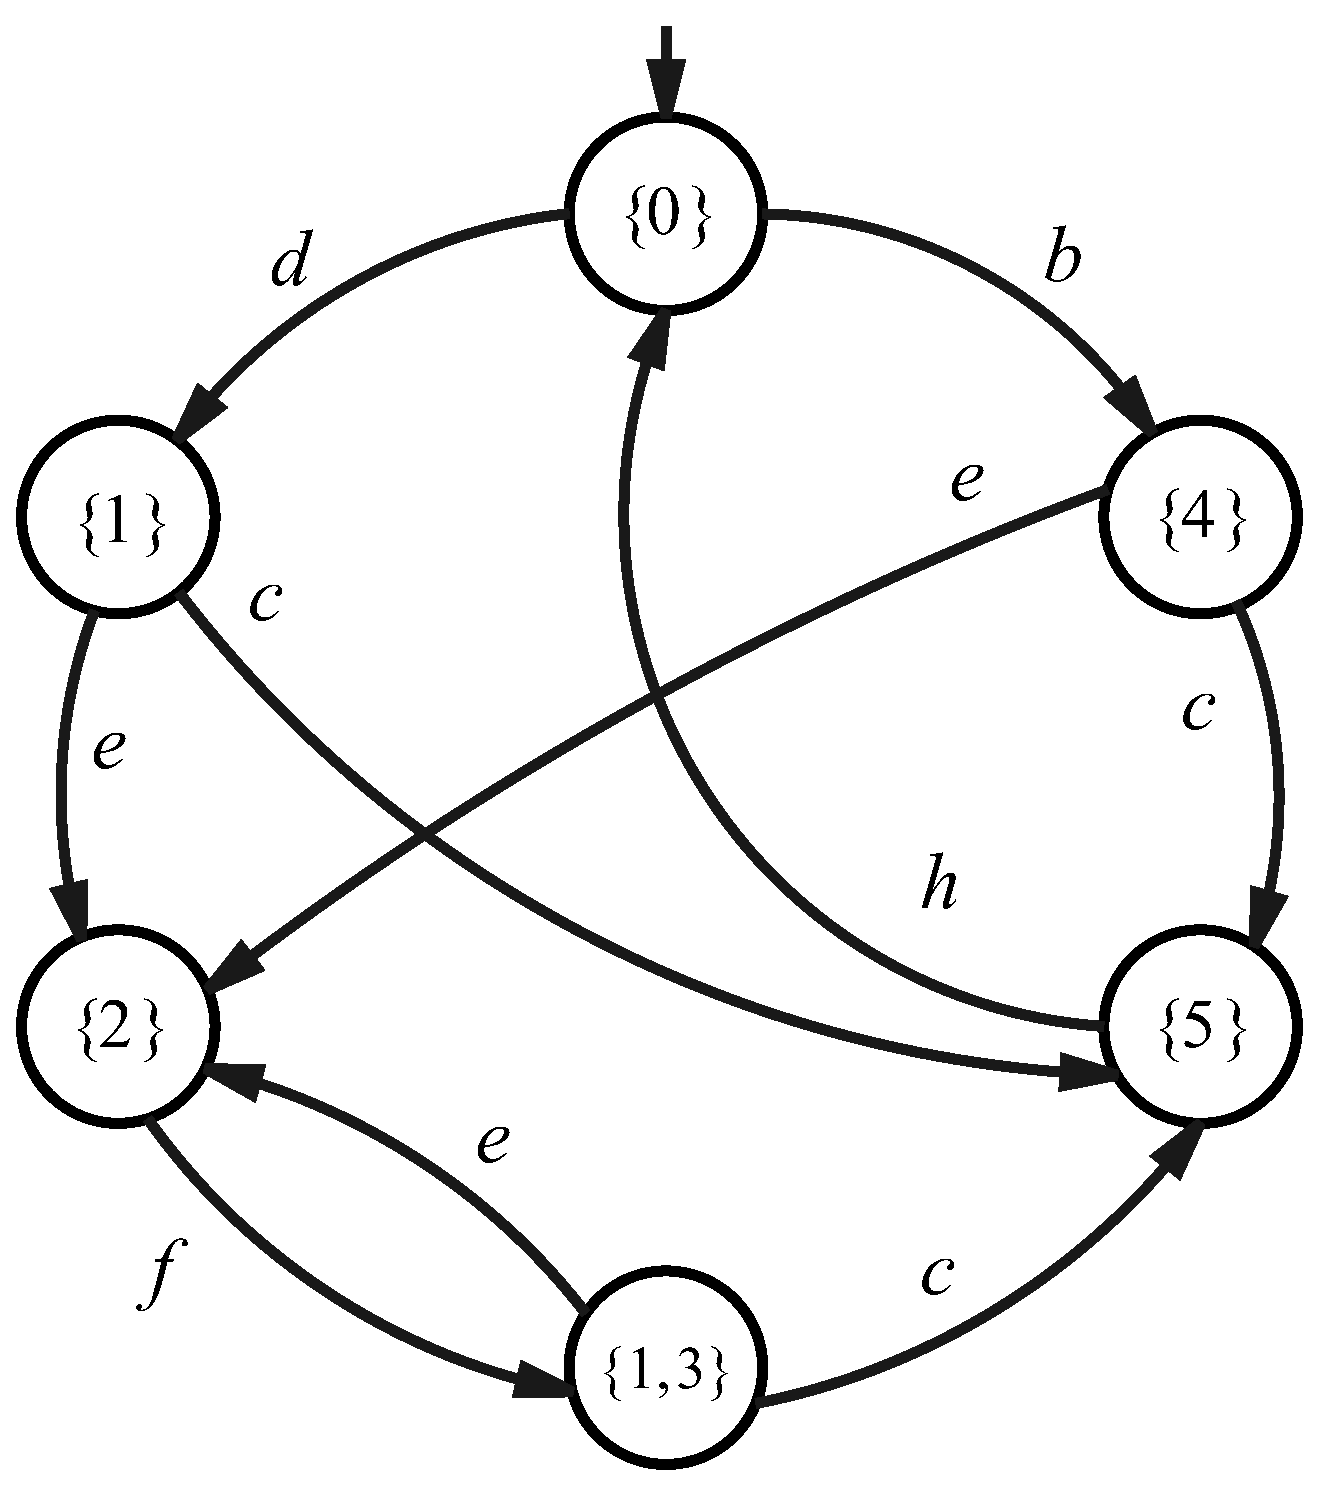
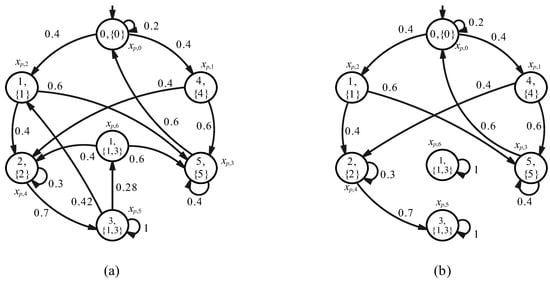
Consider a PFA in Figure 1a with , , , and . First, assume that , the observer of G is shown in Figure 2, and G is critically observable based on Definition 1. Then, let , G become not critically observable, and we have (For brevity, for any , we use instead of to represent the Kleene-closure of . Moreover, for any , we use instead of to represent the concatenation of and ). Let ; then, we have , , and for all transitions in δ except for transition , and we can obtain in Figure 1b. Let us check whether the PFA is SA-CO with respect to , , , and . Since all sequences violating critical observability have lengths greater than or equal to three, we begin with . In particular,
Then, take into account ,
It is obvious that
decreases with k increasing. Thus, the PFA is SA-CO with respect to , , , and a threshold .
Figure 1.
(a) PFA and (b) .
Figure 2.
Observer for the NFA G in Figure 1a.
Definition 3.
Given a PFA , a projection , the probability for all , and a set of critical states , let with be a PFA characterizing the behavior of under the intermittent loss of observations, defined as
Then, PFA is almost critically observable (A-CO) with respect to , , and a threshold β if
Note that if there exist two sequences w and u in with , , and violating critical observability, then we can confirm that the system is not critically observable through the observation , and it is not necessary to consider the rest of the observation, i.e., . Meanwhile, if the two sequences w and u with and violate the critical observability, we only need to consider the probability of the occurrence of w since the sequence w should occur first before the occurrence of u.
Example 2.
Consider a PFA in Figure 1a with , , and . First, assume that , G is critically observable based on Definition 1. Then, let , G becomes not critically observable, and we have and . Let ; then we can obtain in Figure 1b, and the following holds:
Thus, for any , the PFA is A-CO with respect to , , , and a threshold β.
In fact, the threshold in SA-CO and A-CO is usually determined by the safety requirements of the users for the real system. Particularly, for this work, we mainly focus on the verification of SA-CO and A-CO of SDESs under an intermittent loss of observations with respect to the threshold, and the method of threshold acquisition is not the main purpose of this work.
5. Verification of SA-CO Under Intermittent Loss of Observations
In this section, we present a method to verify SA-CO of SDESs under intermittent loss of observations.
To this aim, it is necessary to compute the cumulative probability of violating critical observability for all sequences of length , including an infinite length. The main difficulty to solve this problem is that there are infinite numbers of k, and infinite memory may be needed to calculate the sequences and their probabilities for each k. Thus, in the following, we show how to resolve this issue.
Now, we briefly introduce how Algorithm 1 works, as follows. In particular, Step 1 uses to describe the behavior of suffering from the intermittent loss of observations. Step 2 builds an observer that can capture all the observations that violate critical observability, which transforms all the nondeterminism of transitions in a PFA to deterministic transitions. In order to capture all the event sequences that can generate the observations violating critical observability, Step 3 adds an unobservable self-loop to each state of the observer, and Step 4 uses a product operator applied to a PFA and a DFA derived from Step 3. Finally, Step 5 constructs the Markov chain M associated with the PFA obtained in Step 4, while discarding the labels on the transitions of the PFA.
Definition 4.
Given a PFA , a projection , the probability for all , and a set of critical states , let be a Markov chain defined as in Algorithm 1. A state is said to violate critical observability if . The set of states in M that violate the critical observability is denoted as .
| Algorithm 1 Construction of a Markov chain for verifying SA-CO under intermittent loss of observations |
Input: A PFA with , a set of events suffering from intermittent loss of observations , the probability for all , and a set of critical states Output: The Markov chain M for verifying SA-CO
|
Theorem 1.
Given a PFA , a projection , the probability for all , and a set of critical states , let be a Markov chain constructed in Algorithm 1 with the transition probability matrix , and be the stationary distribution of M. Then, PFA is SA-CO with respect to , , and a threshold β if and only if and for all non-negative integer k:
where , and is a -dimensional binary row vector such that the element whose index in equals to 1 (otherwise, it equals to 0).
Proof.
Given a PFA , a projection , and the probability for all based on the construction of in Algorithm 1, we can characterize the behavior of under the intermittent loss of observations. In addition, by the construction of , we know that the event sequences in PFA violating critical observability are those reaching states in such that .
Note that in Step 5 of Algorithm 1, we do not change the state structure of but only remove its labels. Thus, the language violating critical observability of G under the intermittent loss of observations is captured by the Markov chain M associated with the PFA , i.e., especially the sequences that reach the states in of M.
In Equation (8), represents the current-state probability distribution vector of the Markov chain M after k steps. Based on Definition 4, the cumulative probability of being in any of the state after k steps is . Thus, we have
Note that the results also hold for , which completes the proof. □
Note that for an irreducible and aperiodic Markov chain, its stationary distribution is the unique strictly positive vector that can be computed by solving the equations and
Theorem 1 indicates that a PFA with intermittent loss of observations is SA-CO if and only if Equation (8) holds for all non-negative integers k and an infinite number. In the following, we provide a practical way to verify this condition using finite memory.
Theorem 2.
Given an irreducible and aperiodic Markov chain with the transition probability matrix , assume that and have rational entries and let denote the stationary distribution of M. Let be a row vector of 0’s and 1’s, which is indexed by states in X. Then, for , there exists an integer depending only on , , and β, such that for all , .
Proof.
It follows directly from the proof of Theorem 2 in [35]. □
In Theorem 2, the Markov chain is assumed to be irreducible and aperiodic. Note that this result can be extended to the Markov chain that is irreducible but periodic, which has been proven in the appendix of [35].
Example 3.
Given a PFA under an intermittent loss of observations, assume that an irreducible and aperiodic Markov chain with the transition probability matrix in Theorem 2 are given by , , and
The eigenvalues associated with are , , and . Since all eigenvalues are distinct, it holds that , where
and
In addition, we have
Assume that and , we can verify whether the condition in Theorem 2 holds. First, we compute the stationary distribution of M as such that . Then, the constants , , and in Equation (9) can be computed as , , and , and the constant in Theorem 2 can be obtained using the equation
Due to , we only need to check whether for . In fact, since , , and , we can conclude that the PFA under intermittent loss of observations is SA-CO based on Theorems 1 and 2.
This section concludes by discussing the complexity of the proposed method. To verify SA-CO under an intermittent loss of observations, we use Algorithm 1 to construct the Markov chain M that includes at most states. Then, for finding eigenvalues and computing the state stationary distribution of M, the complexity is . Thus, the total complexity of verifying SA-CO is exponential in the size of the PFA.
6. Verification of A-CO Under Intermittent Loss of Observations
In this section, we show how to formally verify A-CO in SDESs under an intermittent loss of observations. For the sake of solving this problem, we need to make the states of M defined in Definition 4 (the set of critical observability violative states) absorbing. Thus, the probability of violating critical observability is transformed to computing the absorption probability at these absorbing states. The following theorem provides a necessary and sufficient condition to verify A-CO of SDESs under intermittent loss of observations.
Theorem 3.
Given a PFA , a projection , the probability for all , and a set of critical states , let be a Markov chain constructed in Algorithm 1. Build a Markov chain by making states in absorbing. Then, PFA is A-CO with respect to , , , and a threshold β if and only if , where is the absorbing probability at of .
Proof.
For the sake of characterizing the language , it is only necessary to take into account part of the sequences in such that none of their prefixes belong to . That is to say, for any , its continuation in does not belong to . Thus, we make the set of states in the Markov chain M absorbing. By using this procedure, the absorbing probability in the states set equals to the cumulative probability of sequences in . □
In practice, we can compute the absorbing probability in Theorem 3 using a backward recursive technique [40], as follows:
where is the vector of a minimal non-negative solution to Equation (11):
Example 4.
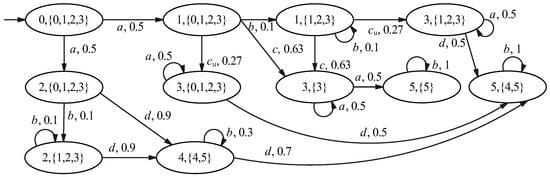
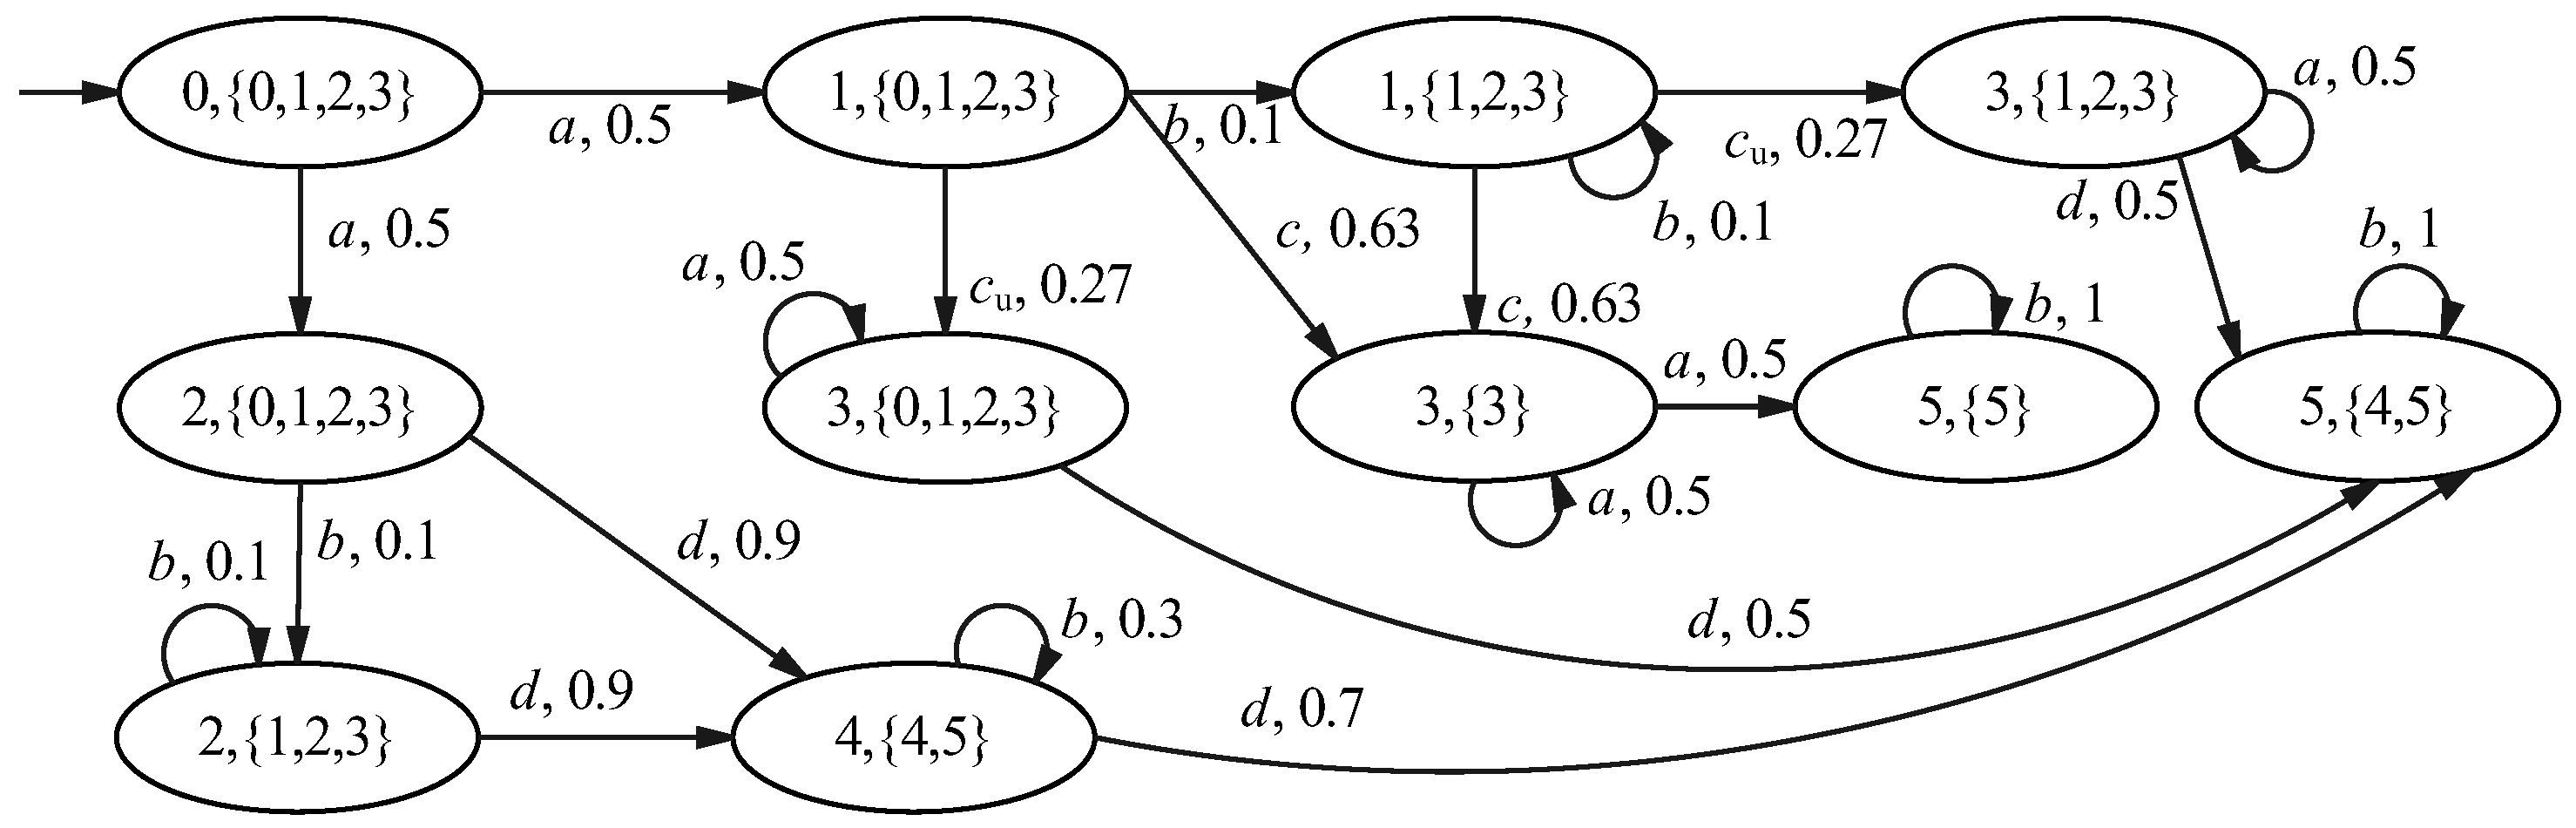
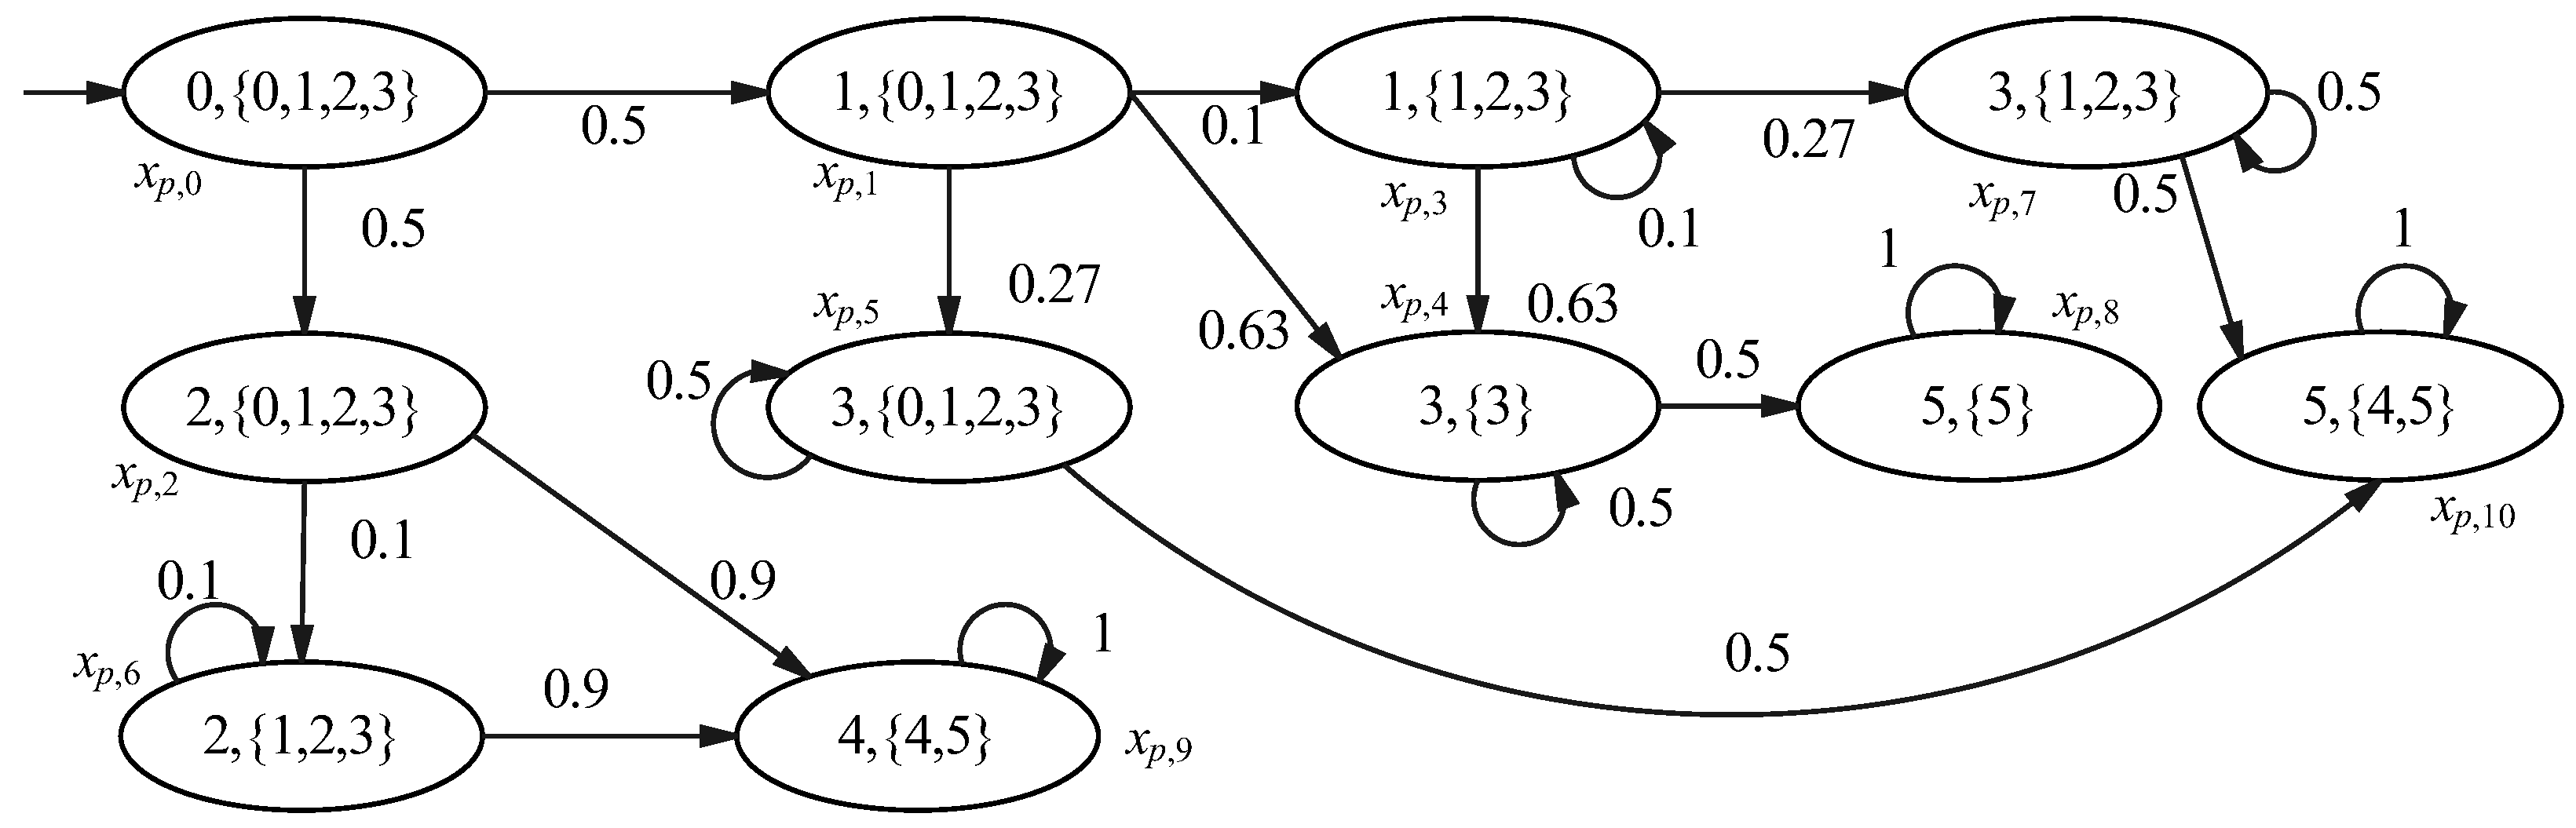
Consider a PFA in Figure 1a with , , , and . We first build the observer of in Figure 3, and the PFA in Figure 4. Then, we construct the Markov chain M associated with the PFA , and transform M to another Markov chain in Figure 5 by changing all the states in to be absorbing. For brevity, we assign labels to to all the states in . Then, we can calculate the absorbing probability in by solving Equation (12) as follows:
Figure 3.
Observer of constructed in Step 2 of Algorithm 1.
Figure 4.
PFA constructed in Step 4 of Algorithm 1.
Figure 5.
Markov chain associated with PFA in Figure 4 by making the states in absorbing.
Since the solution of Equation (12) is not a singleton, we assign the free term and obtain the minimal non-negative solution accordingly. Thus, it holds that
According to Theorem 3, for any , is A-CO with respect to , , and a threshold β, which is consistent with Example 2.
This section concludes by discussing the complexity of the proposed method. To verify A-CO under an intermittent loss of observations, we use Algorithm 1 to construct the Markov chain M that includes at most states. Then, we transform M to another Markov chain by making all the critical observability violative states absorbing, whose complexity is . Finally, for solving Equation (10) of , the complexity is . Thus, the total complexity of verifying A-CO is exponential in the size of the PFA.
Remark 1.
Note that in logic DESs, a modified parallel composition of two copies of NFA G is usually used to check the critical observability of G with polynomial complexity, which can capture all pairs of event sequences having the same observations. However, due to the nondeterminism in the transition function of the corresponding NFA associated with a given PFA, the parallel composition or its modified version cannot maintain the transition probabilities required for computing the probability of event sequences violating critical observability. In particular, as for the SDES modeled as a PFA, when we use the algorithm with polynomial complexity to construct a verifier (or its modified version) for SA-CO or A-CO verification, the sum of probabilities of all defined events at a given state in the verifier may be larger than one. In this sense, the verifier can neither be seen as a PFA nor be transformed to a Markov chain; thus, we cannot use such a structure with polynomial complexity to verify SA-CO and A-CO. Thus, this paper exploits observer-based methods to verify SA-CO and A-CO with exponential complexity.
7. An Industrial Application Example
In this section, the developed results are applied to a raw coal processing system. In the real world, many events are stochastic. Especially in coal mining and processing, spontaneous combustion and fire, raw coal mining quality, and other events are stochastic and difficult to predict. Therefore, the processing flow of coal mines can often be modeled as an SDES. Note that the SDES is still a discrete system but not a continuous system, since the state of the system does not change continuously over time. Based on the theoretical results in this paper, a Matlab tool [41] was developed to verify SA-CO and A-CO of SDESs under intermittent loss of observations. In the following, the experimental results are obtained using this tool.
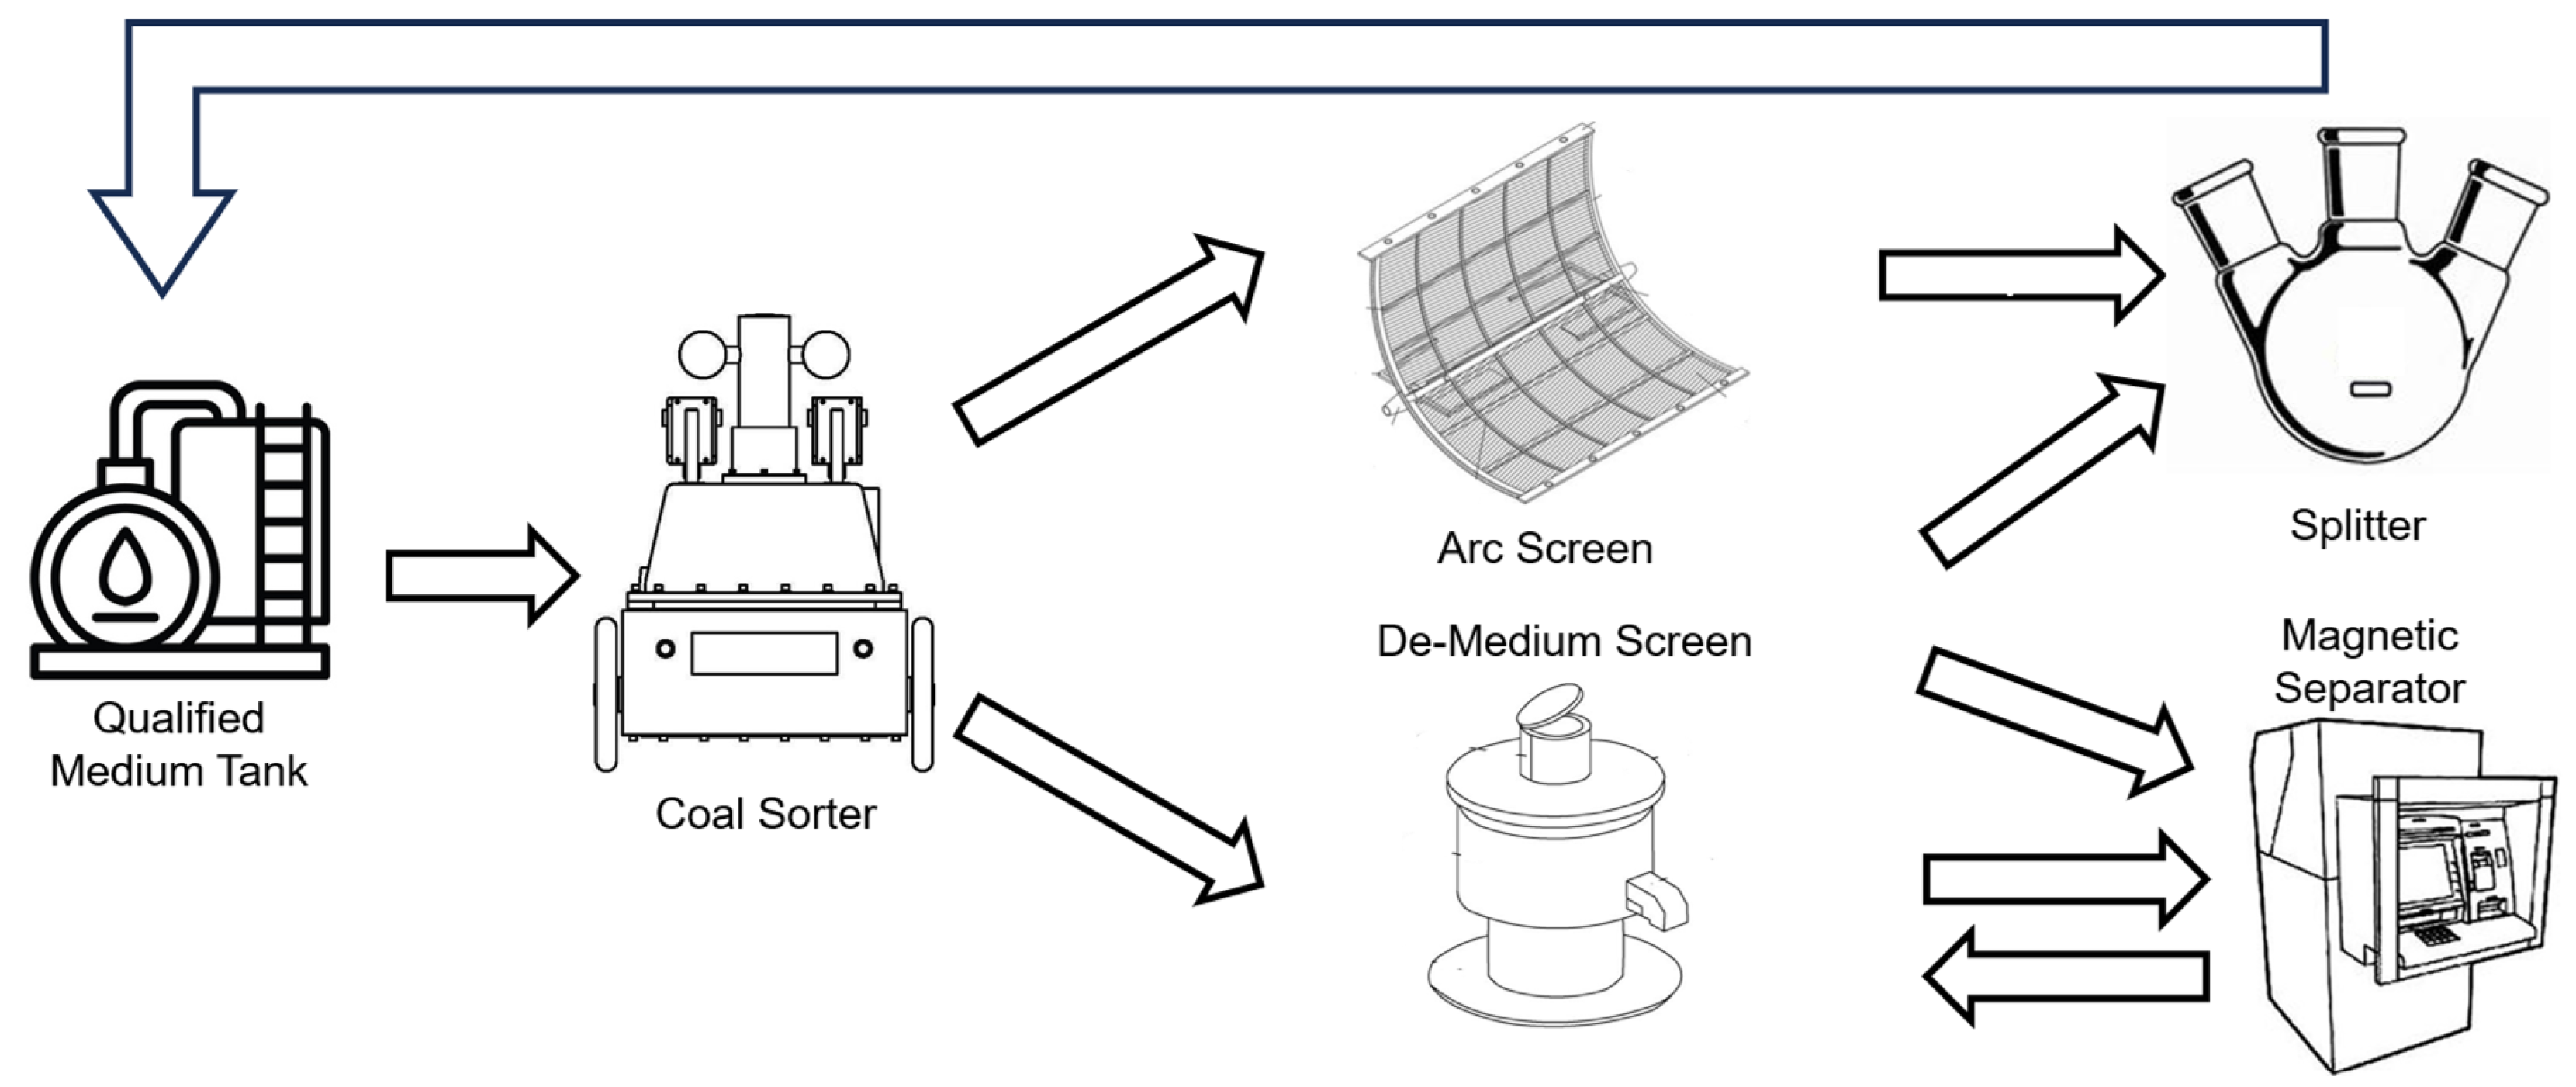
Figure 6 shows a beneficiation plant located in China. This plant uses a dense medium beneficiation system to sort the raw coal. For example, qualified media will be initially stored in a qualified medium tank, waiting for the system to operate. When the system runs, the medium will be transported to the beneficiation system and mixed with raw coal for sorting. After the mixing and sorting process is completed, most of the medium can be directly separated from the coal and returned to the tank through the splitter. A small portion of the medium mixed with coal needs to be repeatedly processed through a De-medium screen and a magnetic separator before returning to the qualified medium tank. In this process, the quality of the medium and whether the medium can directly flow into the splitter are often stochastic.
Figure 6.
A raw coal processing system.
This process is modeled as a PFA shown in Figure 7a, where . Moreover, the meanings of each state and event are listed in Table 1 and Table 2, respectively. In this PFA, the event a represents the waiting process. Thus, the event a is unobservable. Furthermore, we set the critical state to and , which indicates that the medium is processed in the magnetic separator. In a magnetic separator, the medium needs to be separated from various substances such as coal, medium, slurry, etc. This process is important and affects the quality of the medium. Based on the definition of critical observability, the system is critically observable. However, if the event g suffers some faults, i.e., , the event g becomes unobservable, which is modeled as a PFA shown in Figure 7b. Correspondingly, the observer is constructed as Figure 8 and the system becomes not critically observable.
Figure 7.
(a) The raw coal processing system model by PFA and (b) the corresponding .
Table 1.
List of event meanings.
Table 2.
List of state meanings.
Figure 8.
The corresponding observer associated with the NFA in Figure 7b.
Assume that . First, by using Algorithm 1, we can obtain the Markov chain M in Figure 9a and compute its stationary distribution as . Due to , we have and . Then, we can also verify that for all . Based on Theorems 1 and 2, we can conclude that the PFA is SA-CO under the intermittent loss of observations for any .
Figure 9.
(a) Markov chain associated with PFA in Algorithm 1 and (b) Markov chain by making states in absorbing.
To verify A-CO, we modify the Markov chain M in Figure 9a by changing all the states in to be absorbing. Then, we compute the absorbing probability in Theorem 3 by using Equations (10) and (11). For this example, we have . That is to say, the a priori cumulated probability of all the sequences in equals to 1.
Note that we obtain the probabilities of events in a PFA through abstract modeling of the raw coal processing system in this section, which does not rely on real-time data collection and analysis from field operations. In addition, regarding the impact on control decisions or risk mitigation, we plan to integrate our current analytical findings with supervisory control theory to deal with critical observability enforcement.
8. Conclusions
This paper investigates the critical observability in the context of SDESs under intermittent loss of observations. Two new notions, called SA-CO and A-CO, are proposed to quantitatively evaluate the probability that critical observability is violated under the intermittent loss of observations. In particular, we present a new language operation to construct a PFA capturing the behavior of the plant system under the intermittent loss of observations. Then, two effective methods are presented to verify the two properties, respectively, which have the exponential complexity with respect to the number of states of the plant system. Finally, a raw coal processing system is used to demonstrate the feasibility and effectiveness of the practical implications of the proposed methods.
One important future direction for further research is to extend the notion of critical observability to a continuous system (i.e., a continuous time Markov model [12]), and propose the methods to verify this property for such a kind of system by constructing a Markovian observer and analyze the generator matrix of the observer. Then, due to the exponential complexity in this paper, we are also interested in reducing the computational complexity of the proposed methods such that they can be applied to some large complex systems more efficiently.
Author Contributions
Conceptualization, X.C.; methodology, X.C. and H.Z.; software, W.C. and G.Z.; validation, X.C. and H.Z.; formal analysis, X.C. and H.Z.; investigation, X.C. and H.Z.; resources, X.C.; data curation, W.C. and G.Z.; writing—original draft preparation, X.C.; writing—review and editing, X.C. and H.Z.; visualization, W.C. and G.Z.; supervision, Z.Y.; project administration, X.C. and Z.Y.; funding acquisition, X.C. and Z.Y. All authors have read and agreed to the published version of the manuscript.
Funding
This work was supported in part by the Natural Science Foundation of China under Grants 62303375, 62273272, and 61873277, in part by the Natural Science Foundation of Shaanxi Province under Grant 2022JQ-606, in part by the Outstanding Youth Science and Technology Fund of Xi’an University of Science and Technology under Grant 6310224017, and in part by the Youth Innovation Team of Shaanxi Universities under Grant 24JP108.
Data Availability Statement
The data are contained within the article.
Conflicts of Interest
The authors declare no conflicts of interest.
Nomenclature
| A-CO | Almost critical observability |
| DES | Discrete event system |
| PFA | Probabilistic finite automaton |
| SA-CO | Step-based almost critical observability |
| SDES | Stochastic discrete event system |
| Power set of A | |
| D | Dilation function |
| E | Alphabet |
| Kleene-closure of E | |
| Set of observable events | |
| Set of unobservable events | |
| Set of observable events associated with intermittent loss of observations | |
| Set of observable events that do not suffer from intermittent loss of observations | |
| G | Nondeterministic finite automaton |
| PFA | |
| L | Language |
| Prefix-closure of L |
| M | Markov chain |
| Set of non-negative integers | |
| Transition probability matrix | |
| P | Natural projection |
| Inverse projection | |
| p | Transition probability function of a PFA |
| Transition probability function of a Markov chain | |
| Absorbing probability of a state set | |
| Occurrence probability of an event sequence u | |
| Set of states that are unobservable reached from a set of states | |
| X | State set |
| Initial-state set | |
| Set of critical states | |
| Threshold | |
| Nondeterministic transition function | |
| Initial-state probability distribution vector |
References
- Li, X.; Hadjicostis, C.N.; Li, Z. Opacity Enforcement in Discrete Event Systems Using Modification Functions. IEEE Trans. Autom. Sci. Eng. 2025, 22, 3252–3264. [Google Scholar] [CrossRef] [Scilit]
- Lefebvre, D.; Seatzu, C.; Hadjicostis, C.N.; Giua, A. Detectability notions for a class of finite labeled Markovian systems. Nonlinear Anal. Hybrid Syst. 2025, 57, 101586. [Google Scholar] [CrossRef] [Scilit]
- Dong, W.; Zhang, K.; Li, S.; Yin, X. On the verification of detectability for timed discrete event systems. Automatica 2024, 164, 111644. [Google Scholar] [CrossRef] [Scilit]
- Ding, S.; Liu, G.; Yin, L.; Wang, J.; Li, Z. Detection of cyber-attacks in a discrete event system based on deep learning. Mathematics 2024, 12, 2635. [Google Scholar] [CrossRef] [Scilit]
- Labed, A.; Saadaoui, I.; E, H.; El-Meligy, M.A.; Li, Z.; Sharaf, M. Language recovery in discrete-event systems against sensor deception attacks. Mathematics 2023, 11, 2313. [Google Scholar] [CrossRef] [Scilit]
- Cong, X.; Yu, Z.; Fanti, M.P.; Mangini, A.M.; Li, Z. Predictability verification of fault patterns in labeled Petri nets. IEEE Trans. Autom. Control 2025, 70, 1973–1980. [Google Scholar] [CrossRef] [Scilit]
- Ma, Z.; Tong, Y.; Seatzu, C. Verification of pattern–pattern diagnosability in partially observed discrete event systems. IEEE Trans. Autom. Control 2024, 69, 2044–2051. [Google Scholar] [CrossRef] [Scilit]
- De Santis, E.; Di Benedetto, M.; Di Gennaro, S.; D’Innocenzo, A.; Pola, G. Critical observability of a class of hybrid systems and application to air traffic management. In Stochastic Hybrid Systems: Theory and Safety Critical Applications; Springer: Berlin/Heidelberg, Germany, 2006; pp. 141–170. [Google Scholar]
- Zhang, J.; Li, Z. Critical observability enforcement in discrete event systems using differential privacy. Mathematics 2024, 12, 3842. [Google Scholar] [CrossRef] [Scilit]
- Hadjicostis, C.N. Estimation and Inference in Discrete Event Systems; Springer: Berlin/Heidelberg, Germany, 2020. [Google Scholar]
- Zhou, S.; Yu, J.; Yin, L.; Li, Z. Security quantification for discrete event systems based on the worth of states. Mathematics 2023, 11, 3629. [Google Scholar] [CrossRef] [Scilit]
- Lefebvre, D.; Seatzu, C.; Hadjicostis, C.N.; Giua, A. Probabilistic state estimation for labeled continuous time Markov models with applications to attack detection. Discret. Event Dyn. Syst. 2022, 32, 539–544. [Google Scholar] [CrossRef] [Scilit]
- Yu, Z.; Gao, H.; Cong, X.; Wu, N.; Song, H.H. A survey on cyber-physical systems security. IEEE Internet Things J. 2023, 10, 21670–21686. [Google Scholar] [CrossRef] [Scilit]
- Pola, G.; De Santis, E.; Di Benedetto, M.; Pezzuti, D. Design of decentralized critical observers for networks of finite state machines: A formal method approach. Automatica 2017, 86, 174–182. [Google Scholar] [CrossRef] [Scilit]
- Masopust, T. Critical observability for automata and Petri nets. IEEE Trans. Autom. Control 2020, 65, 341–346. [Google Scholar] [CrossRef] [Scilit]
- Yan, Y.; Deng, H.; Chen, Z. A new look at the critical observability of finite state machines from an algebraic viewpoint. Asian J. Control 2022, 24, 3056–3065. [Google Scholar] [CrossRef] [Scilit]
- Tong, Y.; Ma, Z. Verification of k-Step and definite critical observability in discrete-event systems. IEEE Trans. Autom. Control 2023, 68, 4305–4312. [Google Scholar] [CrossRef] [Scilit]
- Lai, A.; Lahaye, S.; Komenda, J. Observer construction for polynomially ambiguous max-plus automata. IEEE Trans. Autom. Control 2021, 67, 1582–1588. [Google Scholar] [CrossRef] [Scilit]
- Cong, X.; Fanti, M.; Mangini, A.; Li, Z. Critical observability of labeled time Petri net systems. IEEE Trans. Autom. Sci. Eng. 2023, 20, 2063–2074. [Google Scholar] [CrossRef] [Scilit]
- Cong, X.; Fanti, M.P.; Mangini, A.M.; Li, Z. Critical observability of discrete-event systems in a Petri net framework. IEEE Trans. Syst. Man Cybern. Syst. 2022, 52, 2789–2799. [Google Scholar] [CrossRef] [Scilit]
- Ma, Z.; Li, Z.; Giua, A. Design of optimal Petri net controllers for disjunctive generalized mutual exclusion constraints. IEEE Trans. Autom. Control 2015, 60, 1774–1785. [Google Scholar] [CrossRef] [Scilit]
- Cong, X.; Fanti, M.; Mangini, A.; Li, Z. Critical observability verification and enforcement of labeled Petri nets by using basis markings. IEEE Trans. Autom. Control 2023, 68, 8158–8164. [Google Scholar] [CrossRef] [Scilit]
- Wonham, W.M.; Cai, K. Supervisory Control of Discrete-Event Systems; Springer: Berlin/Heidelberg, Germany, 2019. [Google Scholar]
- Alves, M.V.; da Cunha, A.E.; Carvalho, L.K.; Moreira, M.V.; Basilio, J.C. Robust supervisory control of discrete event systems against intermittent loss of observations. Int. J. Control 2021, 94, 2008–2020. [Google Scholar] [CrossRef] [Scilit]
- Nunes, C.E.; Moreira, M.V.; Alves, M.V.; Carvalho, L.K.; Basilio, J.C. Codiagnosability of networked discrete event systems subject to communication delays and intermittent loss of observation. Discret. Event Dyn. Syst. 2018, 28, 215–246. [Google Scholar] [CrossRef] [Scilit]
- Carvalho, L.K.; Basilio, J.C.; Moreira, M.V. Robust diagnosis of discrete event systems against intermittent loss of observations. Automatica 2012, 48, 2068–2078. [Google Scholar] [CrossRef] [Scilit]
- Di Benedetto, M.; Di Gennaro, S.; D’Innocenzo, A. Critical observability for a class of stochastic hybrid systems and application to air traffic management. HYBRIDGE D7 2005, 5, 1–22. [Google Scholar]
- Thorsley, D.; Teneketzis, D. Diagnosability of stochastic discrete-event systems. IEEE Trans. Autom. Control 2005, 50, 476–492. [Google Scholar] [CrossRef]
- Chen, J.; Kumar, R. Polynomial test for stochastic diagnosability of discrete-event systems. IEEE Trans. Autom. Sci. Eng. 2013, 10, 969–979. [Google Scholar] [CrossRef] [Scilit]
- Yin, X.; Chen, J.; Li, Z.; Li, S. Robust fault diagnosis of stochastic discrete event systems. IEEE Trans. Autom. Control 2019, 64, 4237–4244. [Google Scholar] [CrossRef] [Scilit]
- He, J.; Wang, D.; Yang, M.; Hu, Y. Asynchronous fault diagnosis of stochastic discrete-event systems in industrial applications. IEEE Sens. J. 2024, 24, 4886–4898. [Google Scholar] [CrossRef] [Scilit]
- Chen, J.; Kumar, R. Stochastic failure prognosis of discrete event systems. IEEE Trans. Autom. Control 2021, 67, 5487–5492. [Google Scholar] [CrossRef] [Scilit]
- Liao, H.; Liu, F.; Zhao, R. Reliable co-prognosability of decentralized stochastic discrete-event systems and a polynomial-time verification. IEEE Trans. Cybern. 2021, 52, 6207–6216. [Google Scholar] [CrossRef] [Scilit]
- Keroglou, C.; Hadjicostis, C.N. Detectability in stochastic discrete event systems. Syst. Control Lett. 2015, 84, 21–26. [Google Scholar] [CrossRef] [Scilit]
- Saboori, A.; Hadjicostis, C.N. Current-state opacity formulations in probabilistic finite automata. IEEE Trans. Autom. Control 2014, 59, 120–133, Erratum in IEEE Trans. Autom. Control 2024, 69, 3480–3481. [Google Scholar] [CrossRef] [Scilit]
- Keroglou, C.; Hadjicostis, C. Initial state opacity in stochastic DES. In Proceedings of the 2013 IEEE 18th Conference on Emerging Technologies & Factory Automation (ETFA), Cagliari, Italy, 10–13 September 2013; pp. 1–8. [Google Scholar]
- Yin, X.; Li, Z.; Wang, W.; Li, S. Infinite-step opacity and K-step opacity of stochastic discrete-event systems. Automatica 2019, 99, 266–274. [Google Scholar] [CrossRef] [Scilit]
- Cassandras, C.G.; Lafortune, S. Introduction to Discrete Event Systems; Springer: Berlin/Heidelberg, Germany, 2021. [Google Scholar]
- Teng, Y.; Li, Z.; Yin, L.; Wu, N. State-based differential privacy verification and enforcement for probabilistic automata. Mathematics 2023, 11, 1853. [Google Scholar] [CrossRef] [Scilit]
- Norris, J.R. Markov Chains; Cambridge University Press: Cambridge, UK, 1998. [Google Scholar]
- Cong, X.; Cui, W.; Zhao, G. Matlab Tool for Verification of Critical Observability in Stochastic Discrete Event Systems Under Intermittent Loss of Observations. Website. Available online: https://github.com/congxuya/Matlab_tool_SA-COA-CO.git (accessed on 16 April 2025).

Disclaimer/Publisher’s Note: The statements, opinions and data contained in all publications are solely those of the individual author(s) and contributor(s) and not of MDPI and/or the editor(s). MDPI and/or the editor(s) disclaim responsibility for any injury to people or property resulting from any ideas, methods, instructions or products referred to in the content. |
© 2025 by the authors. Licensee MDPI, Basel, Switzerland. This article is an open access article distributed under the terms and conditions of the Creative Commons Attribution (CC BY) license (https://creativecommons.org/licenses/by/4.0/).