


Abstract
The Feistel structure represents a fundamental architectural component within the domain of symmetric cryptographic algorithms, with a substantial body of research conducted within the context of classical computing environments. Nevertheless, research into specific symmetric cryptographic algorithms utilizing the Feistel structure is relatively scarce in quantum computing environments. This paper, for the first time, proposes a five-round distinguisher for Camellia under the quantum chosen-ciphertext attack (qCCA) setting, with its effectiveness empirically validated. Additionally, by combining Grover’s algorithm and Simon’s algorithm, we construct a nine-round key-recovery attack model against Camellia. Through an in-depth analysis of Camellia’s key expansion algorithm, we significantly reduce the complexity of the key-recovery attack. The proposed attack achieves a time complexity of 261.5 for recovering the correct key bits and requires 531 quantum bits.
Keywords:
Feistel cipher; quantum chosen-ciphertext attacks; Grover’s algorithm; Simon’s algorithm; Camellia MSC:
94A60; 81P94; 68Q12; 68W40; 68P25
1. Introduction
Quantum computing has the potential to address problems that are intractable for classical computing, particularly in the field of cryptanalysis. For certain complex problems, such as large-scale search or the identification of specific structures, the computational complexity on classical computers often grows exponentially. In contrast, quantum computing leverages quantum superposition and quantum parallelism to significantly improve computational efficiency. For example, Shor’s quantum algorithm [1] can break the classical RSA public-key encryption system in polynomial time, while Grover’s algorithm [2] reduces the time complexity of unstructured database search from the classical to the quantum , posing a direct threat to the key search process of symmetric encryption algorithms. Similarly, Simon’s algorithm [3] can effectively break cryptographic schemes with specific structural properties by identifying the periodicity of certain functions. In addition, recent studies in the field of quantum computing have demonstrated that its applications have expanded to advanced domains such as secure communication and machine learning. For example, Zhou et al. [4] proposed a multi-party semi-quantum private comparison protocol based on d-dimensional GHZ states, which highlights significant advancements in leveraging quantum technology for privacy protection. Similarly, Akrom’s review [5] of quantum support-vector machines underscores the advantages of quantum computing in machine learning. These findings indicate that quantum computing is developing at a rapid pace and has emerged as a powerful tool for the field of cryptography. Thus, employing quantum algorithms to analyze the security of symmetric encryption algorithms is not only a critical approach to evaluating their resistance to quantum attacks but also provides valuable insights into the potential threats quantum computing poses to modern cryptography.
Until 2010, quantum attacks on symmetric ciphers were not considered a significant threat. However, when Kuwakado and others [6] first introduced a polynomial distinguisher for a three-round Feistel cipher under a quantum chosen-plaintext attack (qCPA) setting, this perspective changed. Since then, various quantum attacks on symmetric ciphers have been developed.
Zhandry [7], Kaplan [8], and others have proposed two different models for the quantum cryptanalysis of symmetric ciphers:
Standard Security (Q1 Model): A block cipher is standard secure against quantum adversaries if no efficient quantum algorithm can distinguish the block cipher from pseudorandom permutation (PRP or a PRF) by making only classical queries.
Quantum Security (Q2 Model): A block cipher is deemed quantum secure against quantum adversaries if no efficient quantum algorithm can distinguish the block cipher from PRP (or a PRF) even by making quantum queries.
This paper assumes that the attackers belong to the Q2 model. Recent studies have analyzed the security of symmetric ciphers under this model. In 2012, Kuwakado et al. [9] studied the quantum security of the EM cipher under the Q2 model, utilizing Simon’s algorithm to construct an efficient distinguisher under the qCPA setting, thereby proving that the quantum version of the EM cipher is not secure. Subsequently, in 2015, Dinur et al. [10] combined meet-in-the-middle and partitioning attacks to enhance attacks on Feistel structures of more than four rounds. In 2016, Kaplan [11] utilized Simon’s algorithm to break CBC-MAC, PMAC, and other symmetric cipher systems in polynomial time, demonstrating that Simon’s algorithm could be used for slide attacks, providing exponential acceleration. Leander et al. [12] in 2017 first combined Grover’s algorithm with Simon’s algorithm to construct a quantum attack framework, which was later applied to the analysis of FX structures. Since then, the Grover-meets-Simon algorithm has been extensively utilized by numerous scholars in the quantum analysis of symmetric ciphers. Following Kaplan et al.’s [11] development of quantum slide attacks, Hosoyamada and colleagues [13] in 2019 expanded upon these techniques, introducing a related-key attack on the EM cipher structure and presenting a two-round key-recovery attack on the EM cipher structure.
Dong et al. [14] combined Grover’s algorithm and Simon’s algorithm to introduce a new quantum key-recovery attack on Feistel structures with varying rounds. In 2019, Ito [15] and others proposed a novel distinguisher for Feistel structures under a quantum-chosen ciphertext attack (qCCA) setting. This distinguisher can differentiate, in polynomial time, between four-round Feistel-F and Feistel-KF constructions and six-round Feistel-FK structures from random permutations. Subsequently, quantum key-recovery attacks for r-round Feistel-KF and Feistel-FK structures were performed, achieving key-recovery in and time, respectively. In the same year, Dong et al. [16] conducted a study on quantum distinguisher and key recovery attacks for two generalized Feistel structure (GFS) algorithms. They constructed rounds of quantum distinguisher against d-branch Type-1 GFS and rounds of quantum distinguisher against 2d-branch Type-2 GFS. Using these quantum distinguishers, key-recovery attacks were conducted on the Type-1 and Type-2 GFS ciphers over and rounds, respectively, with time complexities of and .
Ito et al. [17] also designed a polynomial-level quantum distinguisher under the qCPA setting for round configurations of Type-1 GFS, along with a round version under the qCCA setting. Based on these distinguishers, key-recovery attacks were performed on r-round Type-1 GFS ciphers, with complexities of and .
Ni et al. [18] introduce a rounds of quantum distinguisher on Type-1 GFS under the Q2 model and also investigate quantum attacks against the CAST-256 block cipher. In 2020, Cid et al. [19] demonstrated a qCPA on contracting Feistel structures and studied related-key attacks on balanced Feistel structures. That same year, Hodzic et al. [20], based on Simon’s algorithm, developed a construction for seven-round and eight-round quantum distinguishers for generalized Feistel structures under the qCPA setting. In 2021, Li et al. [21] examined the round functions and linear transformation P of Camellia, presenting a five-round quantum distinguisher and, under the qCPA setting, proposed a seven-round Camellia algorithm key-recovery attack with a complexity of .
Cui et al. [22] initially defined weakly periodic functions, thereby extending the application scope of Simon’s algorithm and further constructing several variant Feistel structure distinguishers. They proposed quantum key-recovery attacks for Feistel variants. In 2022, Canale et al. [23] provided an automated periodic function search algorithm under a quantum computing model, implementing key-recovery attacks for the five-round Feistel-FK structure. In 2023, Xu et al. [24], based on the divisibility of branch output functions, proposed quantum attacks on two types of GFS under the qCPA setting. They constructed quantum distinguishers for an 8-round 4F and a 5-round 2F under the Q2 model, conducting 12-round and 7-round quantum key-recovery attacks, respectively. Additionally, they constructed a six-round 2F quantum distinguisher on a weak divisibility basis, performing an eight-round quantum key-recovery attack.
In the same year, Sun et al. [25] studied the security of Type-1 generalized Feistel structures, constructing a quantum distinguisher for a d-branch round Type-1 GFS structure under the qCCA setting. Furthermore, under the qCPA setting for the Type-1 block cipher CAST-256, they introduced a 17-round quantum distinguisher and constructed a quantum key-recovery attack with a complexity of .
The rapid advancement of quantum computing has necessitated the development and evaluation of post-quantum cryptographic (PQC) schemes to ensure secure communication in the quantum era. Recent studies have highlighted both the practical applications and potential vulnerabilities of PQC. For instance, Aslam et al. [26] proposed a quantum-resilient blockchain-enabled secure communication framework for connected autonomous vehicles, demonstrating the applicability of PQC in real-world IoT scenarios. Similarly, Sim et al. [27] investigated the side-channel vulnerabilities of lattice-based cryptographic schemes, particularly CRYSTALS-KYBER, and introduced a chosen-ciphertext clustering attack by leveraging the side-channel leakage of Barrett reduction. Their attack achieved a 100% success rate in recovering secret keys on ARM Cortex-M4 microcontrollers. These findings underscore the dual necessity of ensuring mathematical robustness and addressing side-channel resistance in PQC implementations, especially in resource-constrained environments such as IoT devices.
Based on the findings of prior research, it is apparent that studies conducted under the qCCA model remain inadequate, and numerous aspects remain unexplored. Studies demonstrate that numerous schemes proven secure under qCPA can be compromised by quantum algorithms like Simon’s algorithm in qCCA settings. More significantly, the NIST Post-Quantum Cryptography Standardization Project has adopted the Q2 model (i.e., qCCA security) as a core evaluation criterion. Consequently, analysis under qCCA conditions constitutes an essential benchmark for assessing the quantum security of block cipher algorithms.
The paper presents a five-round distinguisher for Camellia algorithm [28] under the qCCA setting. This is achieved by studying the round function and the characteristics of the key scheduling algorithm. Additionally, a key recovery attack model is proposed, and the complexity of nine rounds of Camellia recovery key under the quantum computing model is analyzed using the distinguisher.
2. Preliminaries
2.1. Notation and Acronyms
The notations used in this paper and their explanations are presented in Table 1.
Table 1.
Notations and Their Definitions.
List of the acronyms and their definitions used in this paper in Table 2.
Table 2.
Acronyms and their definitions.
2.2. Brief Description of Camellia Algorithm
The Camellia algorithm [28], jointly designed by NTT and Mitsubishi Electric in 2000, is known for its high security and efficient performance on both hardware and software platforms. It was selected as a winning algorithm in the European NESSIE project in 2003, recommended in Japan’s CRYPTREC initiative the same year, became an IETF standard in 2004, and adopted as an ISO/IEC standard in 2005.
Camellia is based on a Feistel structure with a block length of 128 bits and supports key lengths of 128, 192, and 256 bits, corresponding to 18, 24, and 32 rounds, respectively.
2.2.1. Camellia Encryption Transformation
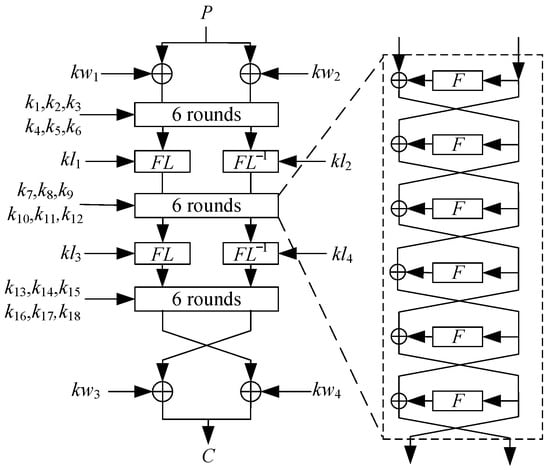
The encryption transformation of Camellia involves differing initial and final whitening keys, with functions inserted every six rounds. For the 128-bit key version, the process consists of three six-round Feistel structures and two rounds of functions. Below, Camellia with a 128-bit key is described in Figure 1.
Figure 1.
Encryption process of Camellia.
The plaintext is 128 bits, the whitening key is 64 bits, and the round key 18) is 64 bits. The key utilized in each function is 32 bits, and the final output ciphertext is 128 bits. The specific encryption process is as follows:
- (1)
- Plaintext WhiteningA 128-bit plaintext M undergoes an XOR operation with the whitening key , resulting in two parts: the left 64 bits and the right 64 bits , such that .
- (2)
- Round IterationFor each round of the Feistel structure, let denote the left output of the i-th round, and denote the right output of the i-th round. For , excluding and , the i-th round transformation is performed as follows:For , the transformation is as follows:
- (3)
- Pre-whitening of ciphertext outputThe final round output is XORed with the whitening keys , producing the whitened ciphertext .The and transformations are defined as follows:
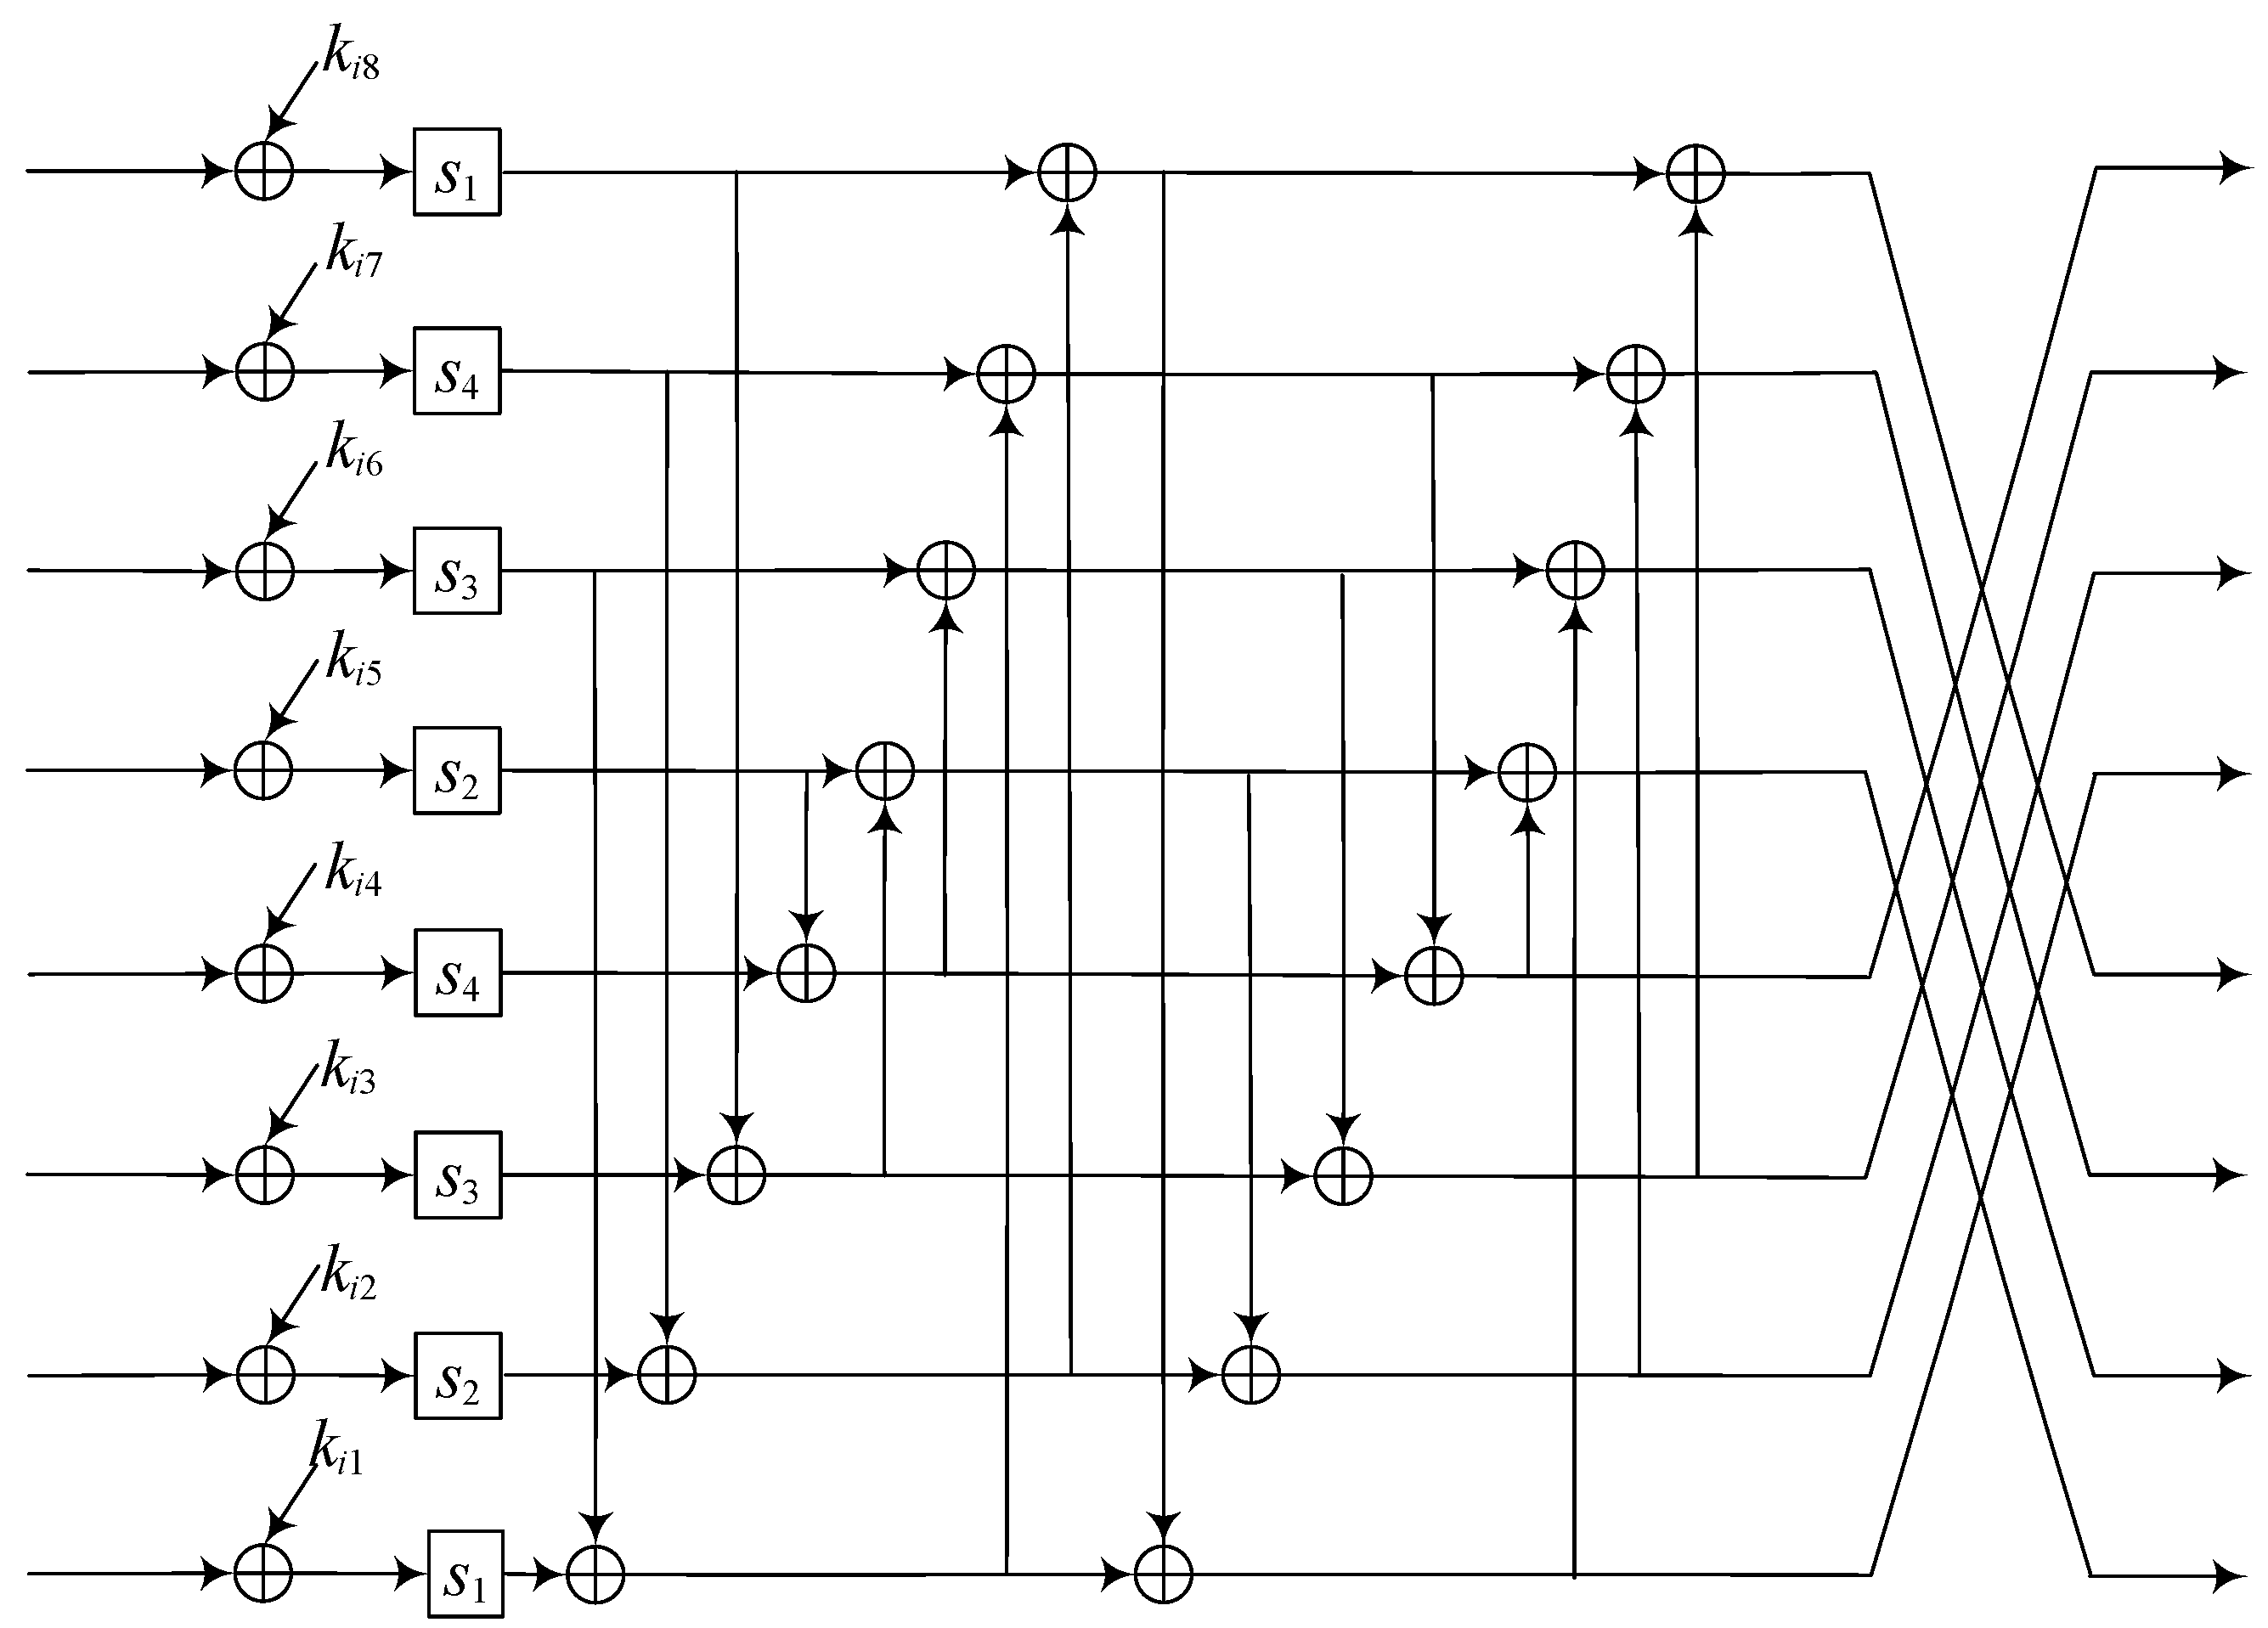
where ∩ represents bitwise logical “AND” operation; ∪ represents bitwise logical “OR” operation. In the Feistel structure, the function F during step (2) utilizes an SP structure design that incorporates round key XOR operations, S-box lookups, and the permutation . The final output of function is formed by the outputs of eight S-boxes after undergoing the permutation , as depicted in Figure 2. The specific steps involved are outlined below:
- (1)
- Round Key XORA 64-bit input is divided into eight bytes. Each byte is then XORed with a corresponding round key byte before proceeding to the next step.
- (2)
- S-Box LookupThe XORed bytes sequentially query eight S-boxes in the order of .
- (3)
- PermutationThe output from the S-boxes undergoes a linear transformation, described as follows.The final output order is . The diffusion layer and its inverse have the following coefficient matrices:
Figure 2.
The round function of Camellia.
2.2.2. Key Expansion Algorithm
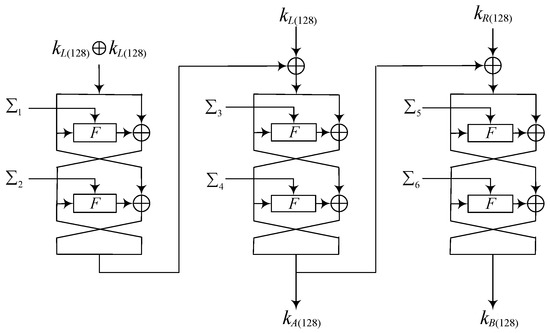
The round keys used in the encryption process are generated from a 256-bit initial key . Initially, is input into the Feistel structure with round constants . After four rounds, 128-bit is generated, and after six rounds, 128-bit is produced. The structure of the algorithm is shown in Figure 3. The six round constants involved in generating and are:
Figure 3.
The key expansion algorithm of Camellia.
In the 128-bit version of the master key, the 256-bit initial key is defined as: . The round keys for each round are derived by shift transformations of the initial key and , as summarized in Table 3.
Table 3.
Wheel keys for each wheel.
2.3. Related Algorithms
In this section, we offer a concise overview of classical quantum algorithms, specifically Simon’s algorithm, Grover’s algorithm, and the Grover-meets-Simon algorithm.
2.3.1. Simon’s Algorithm
Given a Boolean function , which is guaranteed to satisfy , it means the function has a period s and we need to find s. Classically, the optimal time to find period s is . Nevertheless, Simon [3] introduced an algorithm that significantly expedites this process, requiring only queries to determine . This algorithm comprises the following five steps:
- (1)
- Initialize two n-bit quantum registers in state and apply the Hadamard transform to the first register to obtain the corresponding superposition state.
- (2)
- Conduct a quantum query on function f and map it to the current state.
- (3)
- Measure the second register, reducing the first register to the following state:
- (4)
- Apply the Hadamard transform to the first register to obtain
- (5)
- In this superposition state, the amplitudes corresponding to are zero. As a result, for any measurement of y, it is always true that . By iterating this process times, a set of linear equations can be constructed. Solving this system of equations results in determining the value of s.
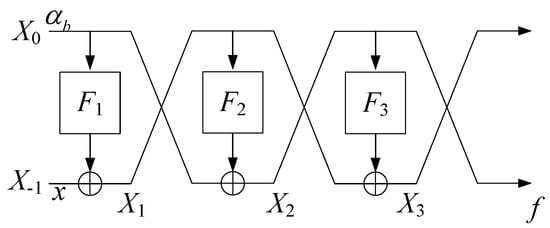
At ISIT2010, Kuwawkado et al. [6] presented a quantum distinguishing attack on a three-round Feistel cipher constructed using Simon’s algorithm. As illustrated in Figure 4, and are arbitrary constants.
Figure 4.
The periodic function of 3-round Feistel structure under qCPA setting.
Let f be a periodic function satisfying . Subsequently, the period can be obtained in polynomial time by employing Simon’s algorithm.
2.3.2. Grover’s Algorithm
When dealing with an unordered set of elements, Grover’s algorithm [2] is employed to pinpoint a unique element that fulfills certain criteria. Specifically, a quantum oracle O is used, which performs the operation , where for all x except within the range , and . The goal is to determine . The most efficient classical algorithm for searching this unordered data has a time complexity of . However, Grover’s algorithm, executed on a quantum computer, dramatically reduces this to merely operations. The algorithm proceeds as follows:
- (1)
- Initialize an n-bit register and apply the Hadamard transform to the first register to achieve the corresponding superposition state, as shown in Equation (12):
- (2)
- Construct a quantum oracle , if x is the correct state, then ; otherwise, .
- (3)
- Define the Grover iteration: , and iterate this operation times:
- (4)
- Return .
2.3.3. Grover-Meets-Simon
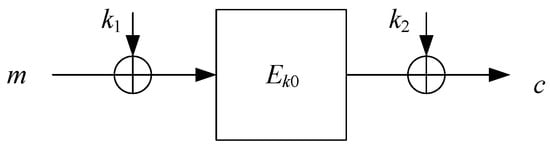
During the 2017 ASIACRYPT conference, Leander et al. [12] presented a quantum key recovery attack approach that integrates Grover’s algorithm with Simon’s algorithm, specifically targeting the FX structure, depicted in Figure 5. The FX structure fulfills the given equation:
Figure 5.
The structure of FX.
Reference [12] constructs the function . When the correct key guess , it holds that . However, for , the function is not periodic. Under the qCPA setting, Reference [10] employs a combination of Simon’s algorithm and Grover’s algorithm to attack the FX structure.
Based on the work of Leander [12], Hosoyamada et al. [29] and Dong et al. [14] added a few rounds behind the three-round Feistel structured distinguisher shown in Figure 4 for recovering the keys of the Feistel encryption algorithm for the r rounds, with a time complexity of .
3. Construction of Periodic Functions
This chapter presents a brief description of the periodic function of four-round Feistel structure proposed by ITO et al. [15]. Additionally, a periodic function for the Camellia algorithm is constructed and verified to be correct.
3.1. The Periodic Function of Four-Round Feistel Structure
At RSA 2019, Ito et al. introduced the design of periodic functions for a four-round Feistel cipher. They developed a quantum distinguisher and presented a key recovery attack against the Feistel structure. We will now describe the method for constructing a periodic function for a four-round Feistel structure, as proposed in Reference [15]. Figure 6 illustrates the structure of the periodic function.
Figure 6.
The periodic function of 4-round Feistel structure.
The four-round Feistel-F encryption structure is denoted as , and its corresponding decryption structure is represented by . The round functions of Feistel-F are signified by Func ( ). The plaintext input to , which outputs the ciphertext . The encryption structure is defined as follows:
The decryption structure is defined as follow:
For the input plaintext , the encryption and decryption structures can be further simplified.The simplified structure is depicted in Figure 7. The function is described as:
Theorem 1.
Define . Then, is a periodic function with a period .
Proof of Theorem 1.
. □
It is straightforward to demonstrate that is a periodic function. The output function can be described as follows:
It can be deduced that is a periodic function with a period of s.
Figure 7.
The equivalent structure of 4-round Feistel structure periodic function.
3.2. Construction of Periodic Functions for Camellia
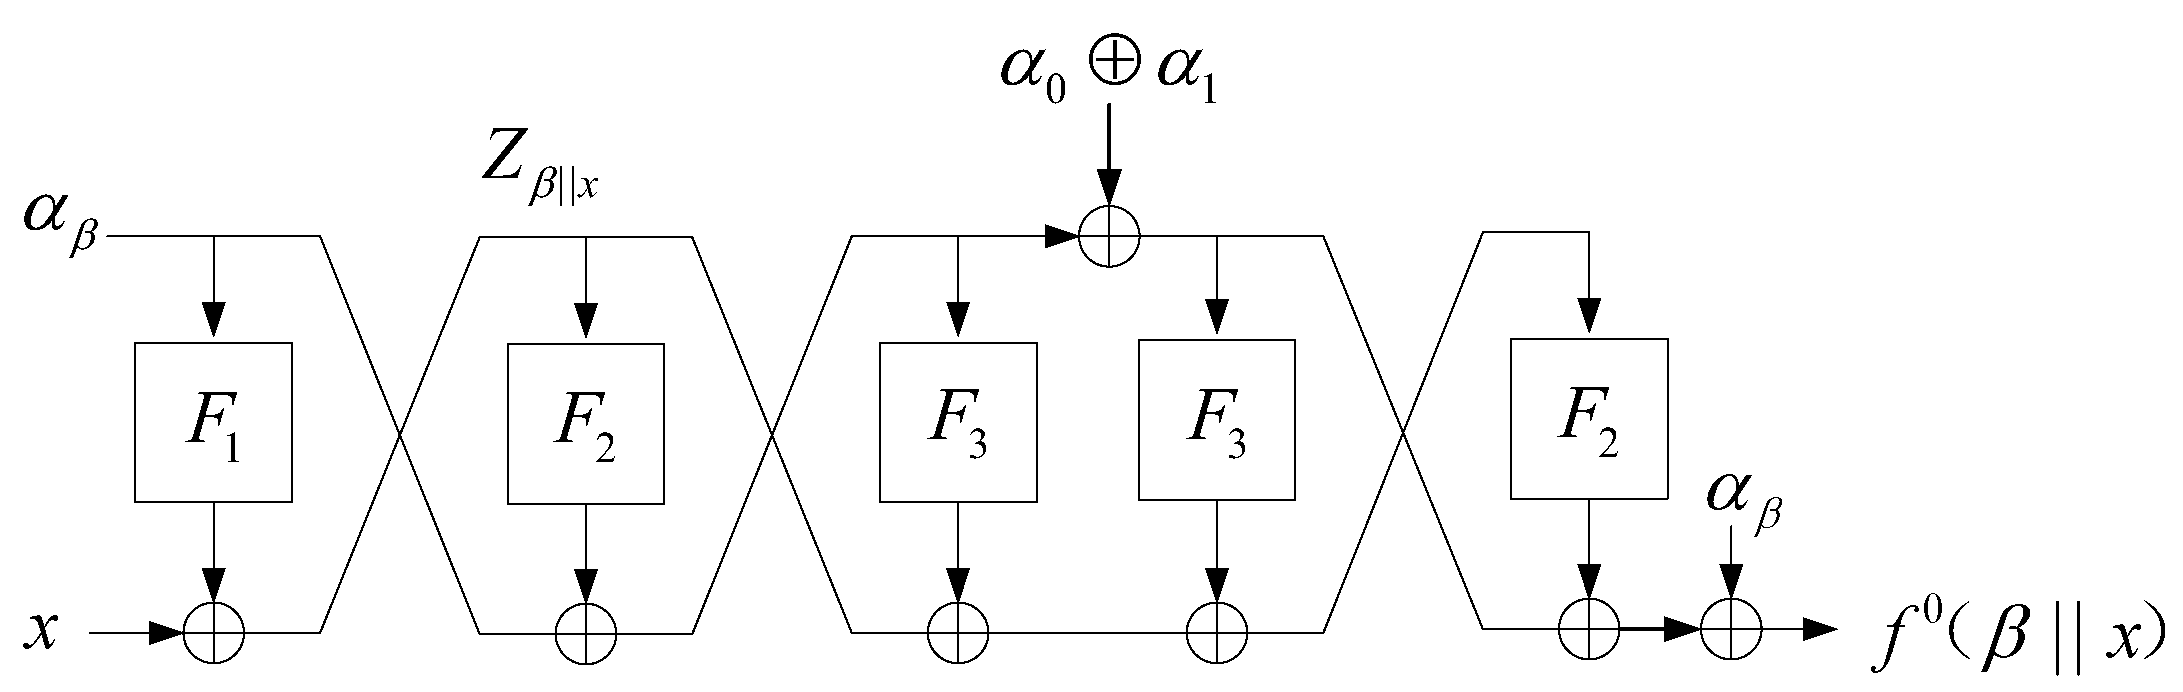
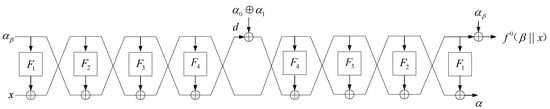
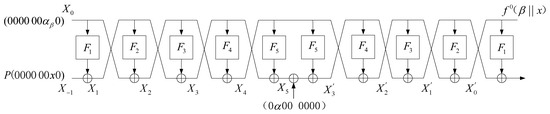
In this section, we aim to construct a periodic function for Camellia, leveraging the periodic function construction methods outlined in the preceding section. To commence, we construct the five-round periodic function structure as illustrated in Figure 8.
Figure 8.
The construction of Camellia’s periodic function.
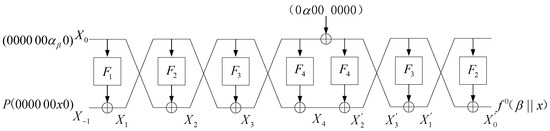
In the illustrated structure, and do not participate in the construction of the periodic function , thus the structure can be further simplified as shown in Figure 9.
Figure 9.
The quivalent structure of Camellia periodic function.
Let the inputs for the two branches be and , where represents a sequence of eight zero bits. The variables and x are both byte variables, both of which are located at the sixth byte. Byte indexing starts at 0 in this article. The input is obtained from ( through a permutation .
After the first round function transformation, we obtain the output as
where is the s transformation of the i-th round function. Given the characteristics of Camellia algorithm’s permutation matrix, we obtain the output as:
Within this structure, each symbol is distinct and consists solely of bytes related to *. The output obtained above continues to participate in the round function operation, and we can obtain the subsequent output as shown in the following equations:
The symbol ? is used to indicate a byte where the periodicity of the function cannot be determined.
Performing the operation on both sides of the above equation, we obtain:
As derived above, the 0 th and first bytes of relate only to the variable *; thus they can be used to construct a periodic function. Define the output byte as the function , i.e., . The theorem states the following:
Theorem 2.
The period of the function is .
Proof of Theorem 2.
When , for . Since the value of relates only to *, it follows that .
When , for . Since the value of relates only to *, it follows that . □
It can be demonstrated that the function exhibits periodicity. In accordance with Theorem 2 of the study [15], a distinguisher against the five-round Camellia can be constructed using the function .
During the research process, we attempted to construct distinguishers with a higher number of rounds. However, distinguishers exceeding five rounds could not be theoretically verified for their correctness. Based on the method proposed in this paper, we consider the five-round distinguisher to be an appropriate choice. On the other hand, the five-round distinguisher offers a balance between complexity and theoretical verifiability, making it the most suitable choice based on the method proposed in this paper. This selection ensures that the distinguisher is both practical to implement and theoretically sound, which is critical for the reliability of our approach.
3.3. Experimental Validation
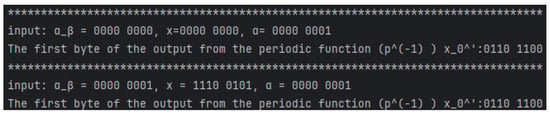
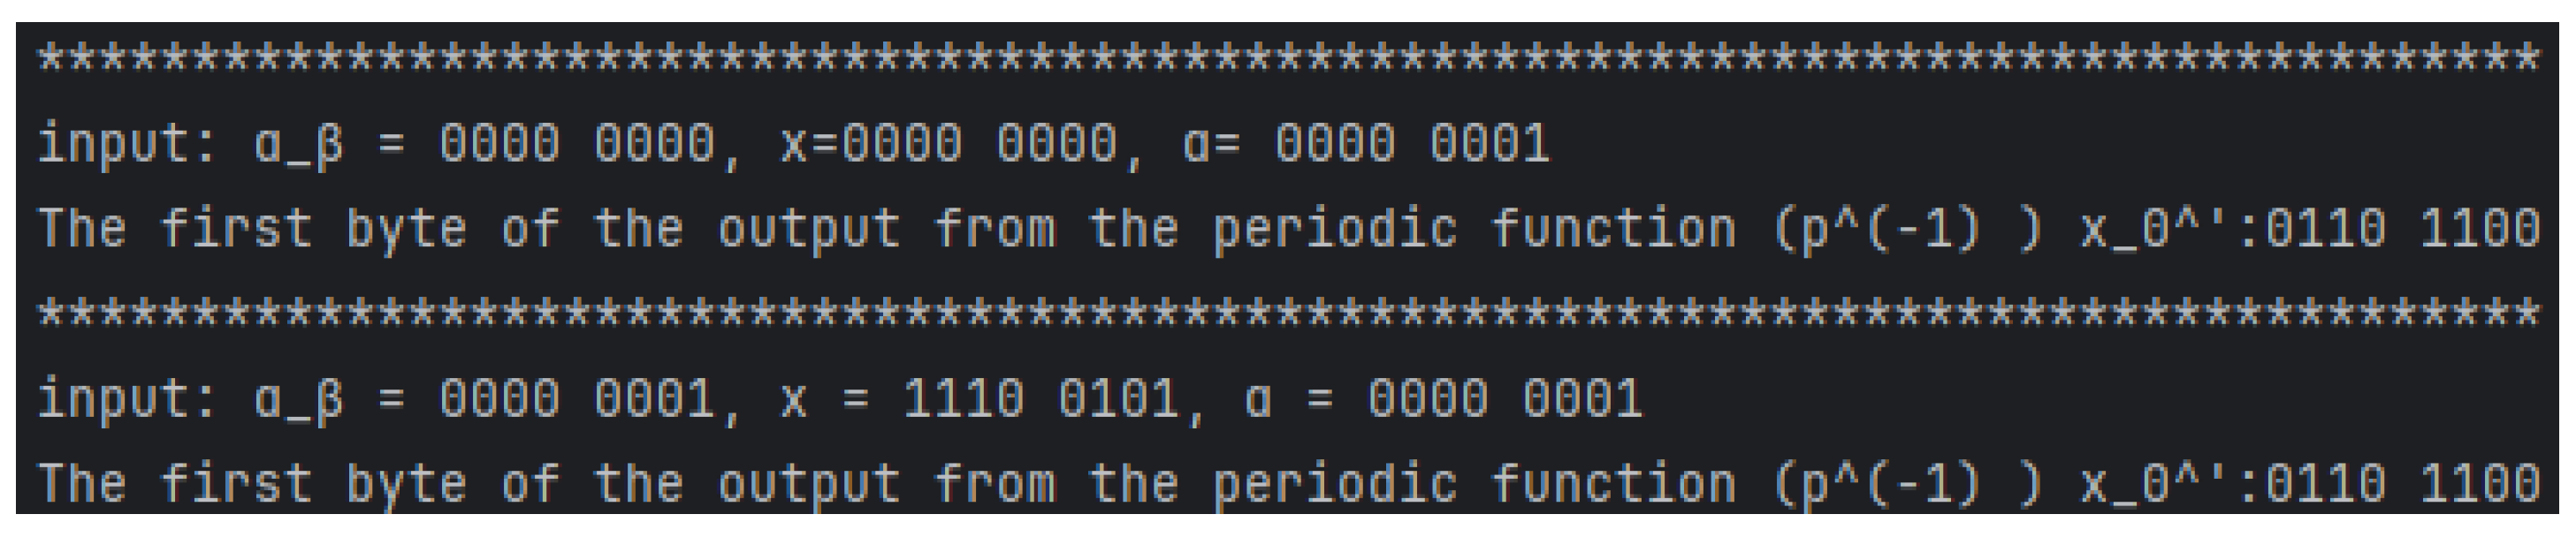
In this subsection, we conducted targeted experiments to validate the correctness of the periodic functions developed in the preceding section. In accordance with the Camellia algorithm criteria outlined in the literature [28], we have constructed the five-round periodic function structure presented in Section 3.2 on the Python 3.7 environment. Our primary aim was to verify the equation . We conducted correctness verification by setting different input parameters. Based on a local computer, we selected sets of distinct parameter data for periodicity testing, all of which confirmed the correctness of the periodic. As illustrated in Figure 10, the periodic function is demonstrated to be correct with a specific set of data.
Figure 10.
Experimental result.
The input plaintext group data are (000000αβ0), P(000000x0), where x = (00000000), α0 = (00000000), and α1 = (00000001). When , for , the plaintext input comprises solely zeros. The output for the first byte, denoted as , is .
For , the plaintext group data is updated to ), and remarkably, the output for the first byte, again denoted as , remains unchanged at .
Given the experimental verification outlined above, Theorem 1 is confirmed to be accurate.
4. The Attack Model for Camellia
This section presents a key-recovery attack model for the Camellia algorithm under the qCCA setting, leveraging the five-round distinguisher proposed in Section 3.2. Here is an outline of our attack methodology:
- Implement a nine-round encryption oracle, denoted as , and decrypt the input of the periodic function over two rounds. The resulting intermediate value after the two rounds and the subkeys for the two rounds as the input to the circuit . Then, the output of undergoes two rounds of decryption and is XORed with a constant.
- Implement a quantum circuit that computes the inverse of . Encrypt the results from the previous step over two rounds, inputting the intermediate value along with subkeys into the circuit . Subsequently, encrypt ’s output over two rounds to acquire the periodic function output .
- Guess the keys for the two rounds preceding and succeeding the quantum circuits and .
- For each key guess, check its correctness with the following procedure.
- (1)
- Apply the five-round distinguisher to and .
- (2)
- If the distinguisher returns “this is a random permutation”, then judge that the guess is wrong. Otherwise, judge that the guess is correct.
Nine-Round Key-Recovery Attack on Camellia
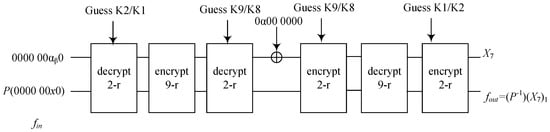
A nine-round key-recovery attack is performed using the established attack model, as shown in Figure 11. The periodic function input is , with the output being . To decrypt through two rounds and retrieve the plaintext, the keys and need to be guessed. Subsequently, the ciphertext is obtained after nine rounds of encryption by the oracle. In addition, the keys to be guessed for the decryption of the ciphertext for two rounds are and . After xOR the obtained intermediate state with the constant , it needs to guess the keys and to encrypt for two rounds to obtain the ciphertext. The plaintext is then obtained by nine rounds of decryption oracle. Finally, the keys and must be guessed in order to encrypt the plaintext for two rounds, thereby obtaining the output .
Figure 11.
The key-recovery attack model of Camellia.
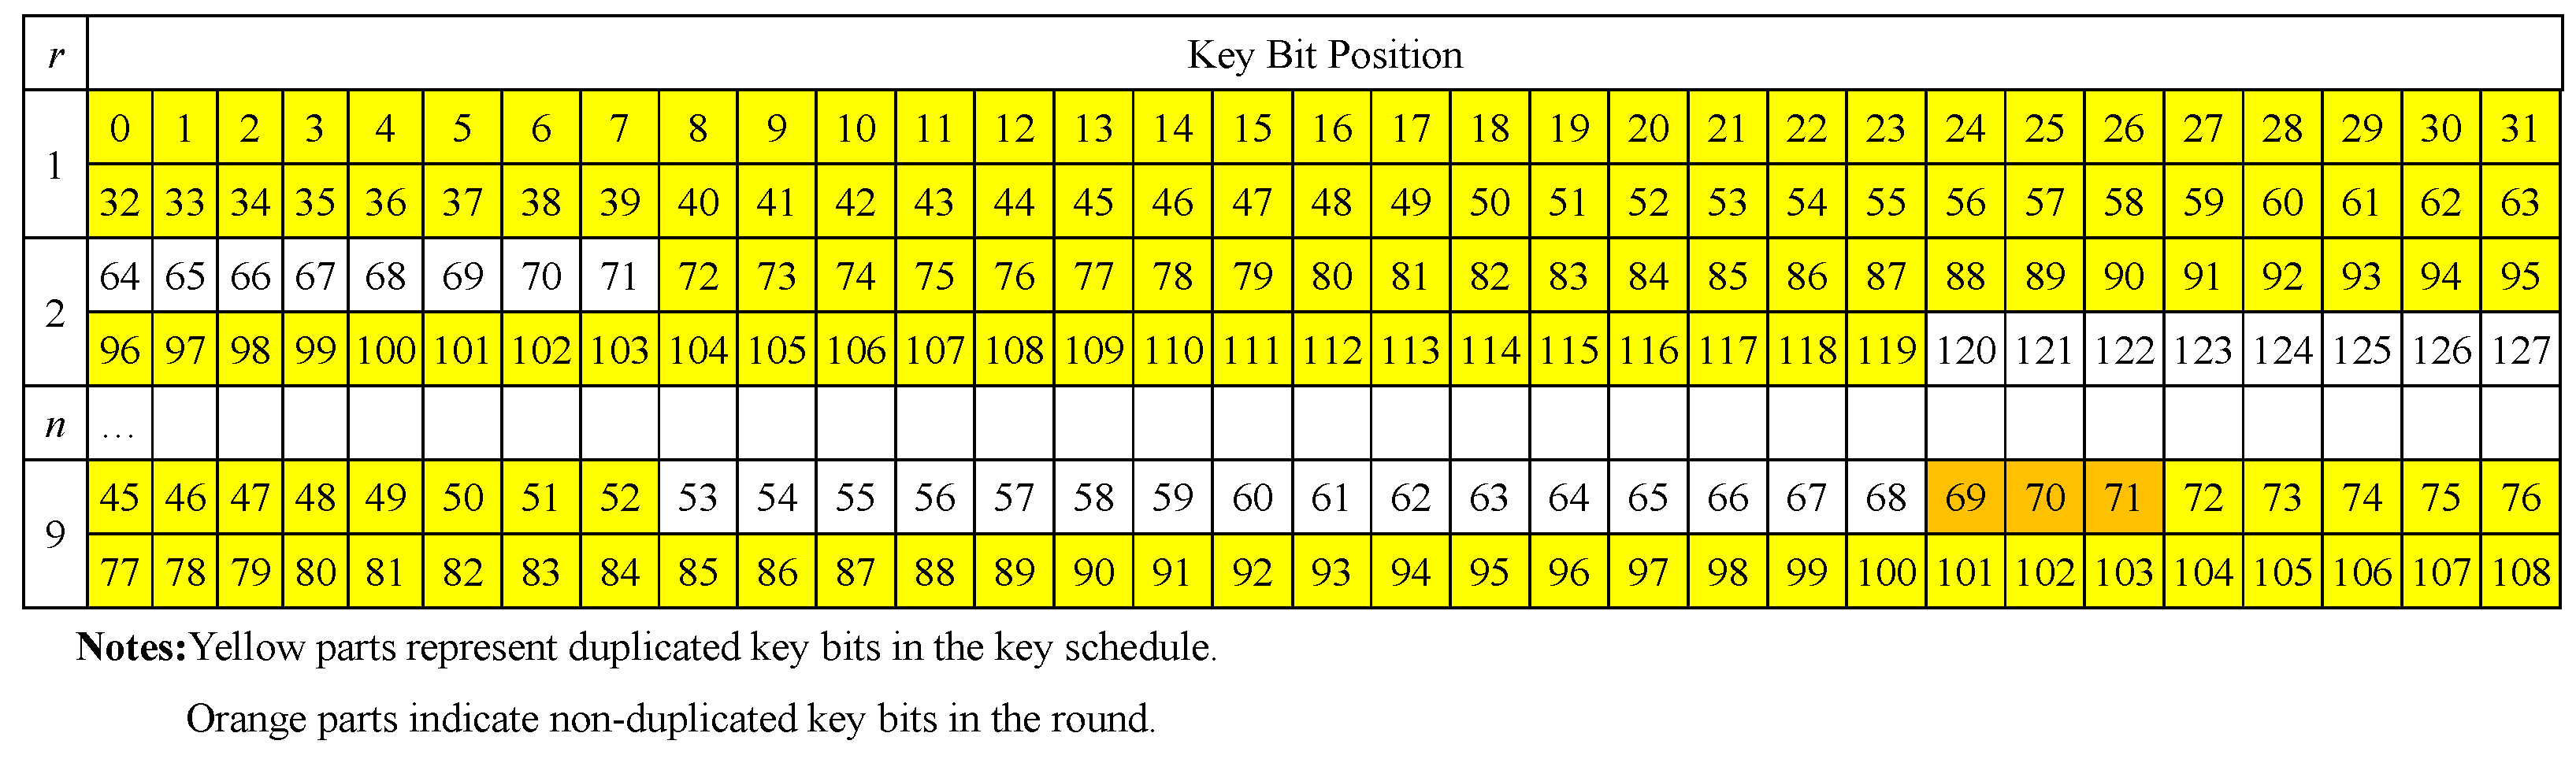
Due to the characteristics of Camellia’s key scheduling, where round keys for F (Round 1), F (Round 2), and F (Round 9) are derived from cyclic shifts of , many key bits are repeated. We guess all key bits for Round 1 and bytes 1–5, 7 for Round 2. Round 9 requires guesses for 0 and 3–7 bytes of the key, with 45 bits being repetitions. As shown in Figure 12, the orange portion of the figure indicates the three-bit non-repeating key positions that must be guessed in Round 9. Thus, the actual key bits to guess are , totaling bits.
Figure 12.
Camellia round key duplicate bits.
Define satisfying , where . If the key guess is correct, the following holds true:
If is a periodic function, then the period of this function can be determined by inputting it into Simon’s algorithm. The guess is correct; otherwise, the guess is incorrect.
As outlined in the literature [12], the formula for the number of quantum bits required for a key recovery attack is as follows:
where sum represents the total number of quantum bits required, the length of the key, the input length of the periodic function, the output length of the periodic function, and the length of the period. For Camellia’s guessed keys , we have that:
The whole attack needs qubits. According to the methods described in References [14,16], the proof is provided as follows: Given an accurate guess of the key:
it holds that:
Let the h be defined as:
where denotes concatenation.
The constructed quantum gate satisfies the following mapping:
By constructing a quantum algorithm A, we achieve a key recovery attack on the Camellia algorithm. The algorithm begins by initializing 531 qubits, all set to the initial state . Among these qubits, the first qubits undergo a Hadamard transform , resulting in the following uniform superposition:
In the proof, represents the full key for the first round, represents , represents , represents , and are auxiliary qubits. The amplitude of this quantum state, which can be ignored, is given by:
Next, the superposition state is processed through the , resulting in the following state:
To extract periodic information, a Hadamard transform is applied again to the register, resulting in the following superposition:
If the guessed key is correct, the period s will be orthogonal to upon measuring . According to Lemma 4 from Reference [12], choosing ensures that the period s can be computed.
The classification of the quantum state is performed using a classifier B, defined as . The classifier operates as follows. First, it checks the dimension of
If , the classifier outputs 0. Otherwise, the unique period s is computed using Lemma 4 from Reference [12]. For any given y, the classifier verifies the equality:
If this equality holds, the classifier outputs 1; otherwise, it outputs 0. The classifier B divides the quantum state into the “good” subspace and the “bad” subspace , such that:
Here, represents the projection onto the “good” subspace, while represents the projection onto the “bad” subspace. The “good” subspace satisfies . Furthermore, the classifier defines a unitary operator , which acts as follows:
Grover’s algorithm is then applied to amplify the probability of the classifier outputting 1. For the initial state , the angle to the “bad” subspace is , where:
Using Grover’s algorithm, the following iterative operator is applied:
The number of iterations required is:
After these iterations, the final state is almost orthogonal to the “bad” subspace, and the probability of measuring a “good” state approaches 1. The entire attack requires 531 qubits, including 123 qubits for storing the key, 9 qubits for the input to the periodic function, 8 qubits for the periodic function’s output, and additional qubits for periodic computation. The time complexity of the attack is:
This approach successfully achieves a key recovery attack on the Camellia algorithm.
The comparison between the work presented in this paper and other methods is shown in Table 4.
Table 4.
Comparison with other attack methods.
5. Conslusions and Future Work
Ref. [15] studied the quantum distinguisher for a four-round Feistel structure under the Q2 model but did not consider the internal structure of the algorithm. The contribution of this paper is the first construction of a quantum key-recovery attack against Camellia under the qCCA model. Specifically, based on the round function and key scheduling features of Camellia, we propose a five-round qCCA distinguisher. Subsequently, leveraging this distinguisher, we present a nine-round quantum key-recovery attack based on the Grover-meets-Simon algorithm, achieving a time complexity of . Compared to previous quantum analyses of Camellia, our attack demonstrates better performance and makes a significant contribution to the study of the quantum security of block cipher algorithms. The ability of symmetric cryptographic algorithms to resist quantum attacks is garnering increasing attention. In addition to conducting quantum security analyses of existing symmetric cryptographic algorithms, researchers are also considering quantum security as a critical criterion in proposing new symmetric cryptographic designs. Future research will focus on constructing quantum distinguishers with an increased number of rounds under quantum computing models. Furthermore, by exploring quantum algorithms, the time complexity of quantum key-recovery attacks may be further reduced. Additionally, the effectiveness of symmetric cryptographic structural schemes against quantum attacks will be further investigated.
Author Contributions
Conceptualization, Y.L.; methodology, Y.L., J.L. and Q.W.; software, D.H.; validation, Y.L. and Q.W.; formal analysis, H.X.; investigation, Y.L. and Q.W.; writing—original draft preparation, Y.L.; writing—review and editing, Y.L. and Q.W.; visualization, Q.W.; supervision, Y.L.; project administration, Y.L.; funding acquisition, Y.L. All authors have read and agreed to the published version of the manuscript.
Funding
This research was funded by the Fund of Yunnan Key Laboratory of Blockchain Application Technology grant No. 202305AG340008, the Beijing Natural Science Foundation grant No. 4234084, and the Key Laboratory of Equipment Data Security and Guarantee Technology, Ministry of Education, under grant No. 2024010102.
Data Availability Statement
The datasets generated during and/or analyzed during the current study are available from the corresponding author on reasonable request.
Conflicts of Interest
Authors Yanjun Li and Jian Liu were employed by the company China Electronics Technology Group Corporation. The remaining authors declare that the research was conducted in the absence of any commercial or financial relationships that could be construed as a potential conflict of interest.
References
- Shor, P.W. Polynomial-time algorithms for prime factorization and discrete logarithms on a quantum computer. SIAM Rev. 1999, 41, 303–332. [Google Scholar] [CrossRef] [Scilit]
- Grover, L.K. A Fast Quantum Mechanical Algorithm for Database Search. In Proceedings of the 28th Annual ACM Symposium on Theory of Computing, Philadelphia, PA, USA, 22–24 May 1996; pp. 212–219. [Google Scholar]
- Simon, D.R. On the power of quantum computation. SIAM J. Comput. 1997, 26, 1474–1483. [Google Scholar] [CrossRef] [Scilit]
- Zhou, N.R.; Chen, Z.-Y.; Liu, Y.-Y.; Gong, L.-H. Multi-party semi-quantum private comparison protocol of size relation with d-level GHZ states. Adv. Quantum Technol. 2024, 2400530. [Google Scholar] [CrossRef] [Scilit]
- Akrom, M. Quantum support vector machine for classification task: A review. J. Multiscale Mater. Inform. 2024, 1, 1–8. [Google Scholar] [CrossRef] [Scilit]
- Kuwakado, H.; Morii, M. Quantum Distinguisher Between the 3-Round Feistel Cipher and the Random Permutation. In Proceedings of the 2010 IEEE International Symposium on Information Theory, Austin, TX, USA, 12–18 June 2010; pp. 2682–2685. [Google Scholar] [CrossRef] [Scilit]
- Zhandry, M. How to Construct Quantum Random Functions. In Proceedings of the 2012 IEEE 53rd Annual Symposium on Foundations of Computer Science, New Brunswick, NJ, USA, 20–23 October 2012; pp. 679–687. [Google Scholar] [CrossRef] [Scilit]
- Kaplan, M.; Leurent, G.; Leverrier, A.; Naya-Plasencia, M. Quantum differential and linear cryptanalysis. arXiv 2015, arXiv:1510.05836. [Google Scholar] [CrossRef] [Scilit]
- Kuwakado, H.; Morii, M. Security on the Quantum-Type Even-Mansour Cipher. In Proceedings of the 2012 International Symposium on Information Theory and Its Applications, Cambridge, MA, USA, 1–6 July 2012; pp. 312–316. [Google Scholar]
- Dinur, I.; Dunkelman, O.; Keller, N.; Shamir, A. New Attacks on Feistel Structures with Improved Memory Complexities. In Proceedings of the Annual Cryptology Conference, Santa Barbara, CA, USA, 16–20 August 2015; Springer: Berlin, Germany, 2015; pp. 433–454. [Google Scholar] [CrossRef] [Scilit]
- Kaplan, M.; Leurent, G.; Leverrier, A.; Naya-Plasencia, M. Breaking symmetric cryptosystems using quantum period finding. In Advances in Cryptology, Proceedings of the 36th Annual International Cryptology Conference (CRYPTO 2016), Santa Barbara, CA, USA, 14–18 August 2016; Proceedings, Part II 36; Springer: Berlin/Heidelberg, Germany, 2016; pp. 207–237. [Google Scholar] [CrossRef] [Scilit]
- Leander, G.; May, A. Grover meets Simon–quantumly attacking the FX-construction. In Advances in Cryptology, Proceedings of the 2017 23rd International Conference on the Theory and Applications of Cryptology and Information Security (ASIACRYPT 2017), Hong Kong, China, 3–7 December 2017; Proceedings, Part II 23; Springer: Berlin, Germany, 2017; pp. 161–178. [Google Scholar] [CrossRef] [Scilit]
- Hosoyamada, A.; Aoki, K. On quantum related-key attacks on iterated Even-Mansour ciphers. IEICE Trans. Fundam. Electron. Commun. Comput. Sci. 2019, 102, 27–34. [Google Scholar] [CrossRef] [Scilit]
- Dong, X.; Wang, X. Quantum key-recovery attack on Feistel structures. Sci. China Inf. Sci. 2018, 61, 102501. [Google Scholar] [CrossRef] [Scilit]
- Ito, G.; Hosoyamada, A.; Matsumoto, R.; Sasaki, Y.; Iwata, T. Quantum chosen-ciphertext attacks against Feistel ciphers. In Topics in Cryptology, Proceedings of the 2019 Cryptographers’ Track at the RSA Conference (CT-RSA 2019), San Francisco, CA, USA, 4–8 March 2019; Springer: Cham, Switzerland, 2019; pp. 391–411. [Google Scholar] [CrossRef] [Scilit]
- Dong, X.; Li, Z.; Wang, X. Quantum cryptanalysis on some generalized Feistel schemes. Sci. China Inf. Sci. 2019, 62, 22501. [Google Scholar] [CrossRef] [Scilit]
- Ito, G.; Iwata, T. Quantum Distinguishing Attacks Against Type-1 Generalized Feistel Ciphers. Cryptology ePrint Archive. 2019. Available online: https://eprint.iacr.org/2019/327 (accessed on 15 April 2025).
- Ni, B.; Dong, X. Improved quantum attack on type-1 generalized Feistel schemes and its application to CAST-256. J. Electron. Inf. Technol. 2020, 42, 295–306. [Google Scholar]
- Cid, C.; Hosoyamada, A.; Liu, Y.; Sim, S.M. Quantum cryptanalysis on contracting Feistel structures and observation on related-key settings. In Progress in Cryptology, Proceedings of the 21st International Conference on Cryptology in India (INDOCRYPT 2020), Bangalore, India, 13–16 December 2020; Proceedings 21; Springer: Cham, Switzerland, 2020; pp. 373–394. [Google Scholar] [CrossRef] [Scilit]
- Hodžić, S.; Knudsen, L.R. A quantum distinguisher for 7/8-round SMS4 block cipher. Quantum Inf. Process. 2020, 19, 411. [Google Scholar] [CrossRef] [Scilit]
- Li, Y.; Lin, H.; Liang, M.; Sun, Y. A new quantum cryptanalysis method on block cipher Camellia. IET Inf. Secur. 2021, 15, 487–495. [Google Scholar] [CrossRef] [Scilit]
- Cui, J.; Guo, J.; Ding, S. Applications of Simon’s algorithm in quantum attacks on Feistel variants. Quantum Inf. Process. 2021, 20, 1–50. [Google Scholar] [CrossRef] [Scilit]
- Canale, F.; Leander, G.; Stennes, L. Simon’s Algorithm and Symmetric Crypto: Generalizations and Automatized Applications. In Proceedings of the Annual International Cryptology Conference, Santa Barbara, CA, USA, 15–18 August 2022; Springer: Cham, Switzerland, 2022; pp. 779–808. [Google Scholar]
- Xu, Y.; Du, X.; Jia, M.; Wang, X.; Zou, J. Quantum attacks on generalized Feistel networks based on the strong–weak separability. Quantum Inf. Process. 2023, 22, 375. [Google Scholar] [CrossRef] [Scilit]
- Sun, H.W.; Cai, B.B.; Qin, S.J.; Wen, Q.Y.; Gao, F. Quantum Attacks on Type-1 Generalized Feistel Schemes. Adv. Quantum Technol. 2023, 6, 2300155. [Google Scholar] [CrossRef] [Scilit]
- Aslam, A.M.; Bhardwaj, A.; Chaudhary, R. Quantum-resilient blockchain-enabled secure communication framework for connected autonomous vehicles using post-quantum cryptography. Veh. Commun. 2025, 52, 100880. [Google Scholar] [CrossRef] [Scilit]
- Sim, B.Y.; Park, A.; Han, D.G. Chosen-ciphertext clustering attack on CRYSTALS-KYBER using the side-channel leakage of Barrett reduction. IEEE Internet Things J. 2022, 9, 21382–21397. [Google Scholar] [CrossRef] [Scilit]
- Aoki, K.; Ichikawa, T.; Kanda, M.; Matsui, M.; Moriai, S.; Nakajima, J.; Tokita, T. Camellia: A 128-bit block cipher suitable for multiple platforms—Design and analysis. In Selected Areas in Cryptography, Proceedings of the 7th Annual International Workshop (SAC 2000), Waterloo, ON, Canada, 14–15 August 2000; Proceedings 7; Springer: Berlin/Heidelberg, Germany, 2001; pp. 39–56. [Google Scholar] [CrossRef] [Scilit]
- Hosoyamada, A.; Sasaki, Y. Quantum Demiric-Selçuk meet-in-the-middle attacks: Applications to 6-round generic Feistel constructions. In Security and Cryptography for Networks, Proceedings of the 11th International Conference (SCN 2018), Amalfi, Italy, 5–7 September 2018; Proceedings 11; Springer: Cham, Switzerland, 2018; pp. 386–403. [Google Scholar] [CrossRef] [Scilit]
- Hosoyamada, A.; Iwata, T. 4-Round Luby-Rackoff Construction is a qPRP. In Proceedings of the International Conference on the Theory and Application of Cryptology and Information Security, Kobe, Japan, 8–12 December 2019; Springer: Cham, Switzerland, 2019; pp. 145–174. [Google Scholar] [CrossRef] [Scilit]
- Qian, X.; You, Q.D.; Zhou, X.; Zhang, Y.; Zhao, X.J. Quantum attack on MARS-like Feistel schemes. J. Cryptologic Res. 2021, 8, 417–431. [Google Scholar] [CrossRef]

Disclaimer/Publisher’s Note: The statements, opinions and data contained in all publications are solely those of the individual author(s) and contributor(s) and not of MDPI and/or the editor(s). MDPI and/or the editor(s) disclaim responsibility for any injury to people or property resulting from any ideas, methods, instructions or products referred to in the content. |
© 2025 by the authors. Licensee MDPI, Basel, Switzerland. This article is an open access article distributed under the terms and conditions of the Creative Commons Attribution (CC BY) license (https://creativecommons.org/licenses/by/4.0/).