


Abstract
This paper proposes a SIM-compatible hardware coordination architecture for secure radio-frequency (RF)-triggered activation in mobile devices. The proposed concept functions as a passive coordination layer rather than as an additional wireless transceiver, enabling controlled interaction between external low-frequency RFID or high-frequency NFC fields and wireless subsystems already available in the host device. The architecture assumes a flexible nano-SIM-compatible form factor integrating passive RF detection structures, a trusted decision component, and a trigger-generation interface aligned with standard SIM/UICC electrical and logical interaction models. Upon detection of an external electromagnetic field, the coordination layer evaluates predefined authorization conditions and produces a controlled trigger event intended to propagate through existing telephony and system-service pathways. In contrast to architectures that embed active wireless transmitters, the proposed approach seeks to minimize hardware redundancy and reduce potential attack surfaces by relying on the host device’s native Bluetooth Low Energy (BLE) capabilities. Rather than directly controlling wireless modules, the interface operates as a hardware-originated coordination mechanism that may support low-power and context-aware activation scenarios in mobile and embedded environments. This paper focuses on the architectural model, system assumptions, security rationale, and implementation constraints of such a SIM-compatible interface. Particular attention is given to integration considerations related to smartphone baseband architectures, operating-system mediation, and secure-element isolation. The presented concept establishes a foundation for future prototype implementation and platform-specific validation of SIM-compatible RF-triggered coordination mechanisms.
1. Introduction
Modern mobile devices increasingly operate as intelligent embedded nodes within heterogeneous Internet of Things (IoT) ecosystems, integrating communication, sensing, secure processing, and low-power management capabilities within compact hardware platforms. The convergence of embedded systems, edge computing, and distributed intelligence has led to the Internet of Intelligent Things (IoIT) paradigm, where mobile terminals function as secure, context-aware interaction hubs in distributed electronic environments [1]. Within this architectural evolution, efficient hardware-originated trigger interfaces capable of initiating coordinated wireless behavior through existing mobile telephony frameworks have become increasingly important.
Traditionally, the Subscriber Identity Module (SIM) has served primarily as a secure authentication component within cellular networks. In mobile payment and authentication infrastructures, the SIM has often been employed as a secure element (SE), providing tamper-resistant storage and cryptographic functionality for NFC-based transactions. However, control over secure element placement has gradually shifted within the mobile ecosystem, with increasing adoption of embedded secure elements, host-based card emulation (HCE), and cloud-based credential management architectures [2]. While this transition improves deployment flexibility, it simultaneously reduces the role of removable SIM components as active hardware interaction interfaces. This evolution motivates renewed investigation into SIM-compatible hardware mechanisms capable of extending functionality beyond authentication toward controlled interaction with device subsystems.
Recent research demonstrates that SIM-based infrastructures can evolve into trusted authentication anchors for advanced application-layer services. Kong et al. [3] introduced a trusted authentication scheme based on a “super SIM card” designed for Industry 4.0 mobile office environments. Their architecture employs the Generic Bootstrapping Architecture (GBA) to establish mutual authentication between terminal devices and network operators, generating secure credentials for higher-layer services while demonstrating resistance to replay and man-in-the-middle attacks.
At the infrastructure level, SIM-centered authentication technologies have also been integrated into enterprise-scale identity management frameworks. Niu et al. [4] proposed a unified 4A (Authentication, Authorization, Accounting, and Audit) identity authentication architecture using SIM-based credentials as a centralized trust anchor within large digital ecosystems. These developments highlight the increasing role of SIM technologies as hardware-rooted trust anchors within distributed digital infrastructures.
Parallel to these developments, the transition from removable SIM cards toward embedded SIM (eSIM) architectures has transformed the telecommunications security landscape. Although modern mobile standards such as UMTS, LTE, and 5G provide stronger cryptographic mechanisms than early GSM systems, new vulnerabilities have emerged through remote provisioning workflows, SIM-swap fraud, and profile hijacking mechanisms. Contemporary analyses indicate that GSMA Remote SIM Provisioning frameworks increase deployment flexibility but also expand socio-technical attack surfaces within mobile identity infrastructures [5].
The rapid expansion of IoT ecosystems has further intensified demand for scalable and quantum-resilient authentication infrastructures. Recent research has proposed post-quantum cryptography (PQC)-enabled eSIM provisioning architectures incorporating NIST-standardized algorithms such as Kyber and Dilithium together with Trusted Execution Environments (TEEs) and distributed validation mechanisms [6]. These developments emphasize the growing importance of hardware-rooted trust anchors within evolving digital ecosystems.
Despite these advancements, most research efforts remain focused on cryptographic strengthening, identity provisioning, and remote management at the protocol or software level. Comparatively little attention has been devoted to hardware-level coordination interfaces capable of generating trusted trigger events within the SIM/UICC domain that may interact with existing telephony frameworks and wireless subsystems.
A research gap therefore exists at the intersection of SIM-based hardware trust anchoring and coordinated wireless subsystem activation within existing mobile system constraints. In particular, there is limited exploration of SIM-compatible mechanisms capable of producing hardware-originated trigger signals derived from passive RF detection while maintaining compatibility with contemporary smartphone integration models.
In this work, we propose a SIM-compatible hardware coordination architecture implemented within a nano-SIM-compatible flexible interface. The proposed concept functions as a coordination layer rather than as an independent wireless communication module. The architecture integrates passive low-frequency RFID (125–134 kHz) and high-frequency NFC (13.56 MHz) field detection structures with a trusted decision component capable of generating controlled trigger events aligned with the UICC electrical interaction model defined in ISO/IEC 7816.
The generated trigger signals are conceptually intended to propagate through existing telephony and system-service pathways within the smartphone architecture. Rather than directly controlling wireless modules, the SIM-compatible interface acts as a hardware-originated coordination mechanism whose signals may be interpreted by the host device’s telephony framework and operating system services. This architectural approach avoids introducing additional active Bluetooth transmitters while preserving compatibility with conventional smartphone integration models.
The main contributions of this work are summarized as follows:
- 1.
- Proposal of a SIM-compatible hardware coordination architecture capable of generating trusted trigger events from passive RF field detection mechanisms;
- 2.
- Design concept of a nano-SIM-compatible flexible interface integrating passive RFID/NFC detection structures with secure decision logic without embedding an active Bluetooth transceiver;
- 3.
- System-level architectural analysis of potential interaction pathways between SIM-originated trigger events and native wireless subsystems within mobile telephony frameworks;
- 4.
- Discussion of integration constraints, security considerations, and architectural limitations associated with SIM-compatible RF-triggered coordination interfaces.
By shifting the architectural focus from embedding additional wireless transceivers toward trusted trigger generation within the UICC domain, the proposed approach explores a coordination-oriented extension of SIM-slot functionality for controlled wireless interaction in modern mobile devices.
The research presented in this paper was conducted within the framework of the national research project BR24993072 (Ministry of Science and Higher Education of the Republic of Kazakhstan), which investigates secure digital infrastructures and intelligent edge-system architectures.
2. Related Work
2.1. Wireless SIM Interfaces and External Reader Architectures
The increasing integration of NFC and short-range wireless interfaces into smartphones has significantly reshaped traditional SIM interaction models. In classical architectures, SIM cards operated strictly within contact-based ISO/IEC 7816-4 [7] electrical interfaces, interacting directly with the mobile baseband processor. However, the emergence of NFC-enabled mobile devices introduced hybrid communication models in which smartphones can operate not only as hosts but also as external readers capable of mediating secure element communication. This transition effectively extends the conventional reader–card paradigm into distributed wireless environments, where authentication and cryptographic services may be facilitated through proximity-based interfaces rather than fixed hardware terminals.
Sportiello [8] demonstrated that NFC-enabled smartphones, when compromised, can function as proxy readers capable of executing relay-based attacks against contactless smart cards. In such architectures, wireless SIM or secure element interaction becomes decoupled from strict physical proximity constraints and may be redirected through malicious intermediate devices. While this paradigm enables flexible service deployment and mobility-centric authentication scenarios, it simultaneously increases the attack surface by introducing reader-side vulnerabilities. These findings underscore the architectural tension between wireless flexibility and proximity-based security assumptions in contactless SIM ecosystems.
Beyond NFC-based reader models, alternative approaches have explored the use of external cryptographic modules to enhance mobile communication security. Boruchinkin et al. proposed a standalone wireless cryptographic communication device that performs encryption and decryption operations within a physically separate hardware unit connected to a smartphone via Bluetooth [9]. By isolating cryptographic processing from the host device, this architecture reduces exposure to malware-based attacks, device substitution, and eavesdropping. However, such external secure modules introduce additional hardware layers, power management requirements, and pairing dependencies. From a systems integration perspective, this increases architectural complexity and reduces transparency compared to tightly integrated SIM-based solutions.
Simultaneously, the evolution of multi-application smart cards and NFC-enabled ecosystems has transformed SIM-based secure elements into dynamic digital wallets capable of interacting with multiple external entities. In these architectures, the SIM operates as a secure execution environment while exchanging credentials with smartphones, NFC readers, and backend provisioning platforms. Akram et al. [10] addressed lifecycle management challenges in such multi-application smart cards by proposing a secure recovery and migration framework aligned with GlobalPlatform consumer-centric models. Their approach enables controlled application restoration in the event of card loss, device upgrade, or service transition. This work highlights the growing dependency of SIM-based infrastructures on remote management, interoperability mechanisms, and coordinated reader–device–cloud architectures.
Collectively, these studies illustrate three major architectural directions in wireless SIM interaction:
- 1.
- Reader-centric architectures, where smartphones act as NFC mediators or proxy readers [8];
- 2.
- Externally isolated cryptographic modules, providing hardware-level security through physical separation [9];
- 3.
- Lifecycle-managed multi-application SIM ecosystems, tightly coupled with remote provisioning infrastructures [10].
While these approaches enhance flexibility, mobility, and service orchestration, they predominantly treat wireless functionality either as an external reader capability or as an isolated cryptographic adjunct. In most cases, additional wireless modules or separate hardware units are introduced, increasing architectural redundancy, energy consumption, and electromagnetic complexity.
Notably, limited attention has been given to SIM-compatible hardware interfaces that coordinate native wireless subsystems of the host device without embedding redundant RF transceivers or requiring external peripherals. This observation motivates a deeper examination of antenna-integrated SIM designs and contactless-enabled SIM architectures, which are discussed in the following subsection.
2.2. Antenna-Integrated and NFC-Enabled SIM Card Designs
A parallel research direction in SIM and secure element evolution focuses on the physical integration of antenna structures and cryptographic modules within highly constrained form factors. Unlike external reader architectures, these approaches aim to embed contactless functionality directly into compact hardware modules, enabling standalone authentication and proximity-based interaction.
Druml et al. [11] introduced a secured miniaturized system-in-package (SiP) contactless authentication device integrating NFC functionality within an embedded wafer-level ball grid array (eWLB) package. Their architecture combines a secure authentication IC, high-frequency (HF) antenna structures, ferrite shielding layers, and discrete impedance matching components within a compact 3 × 3 mm footprint. The study reports improved high-frequency coupling performance compared to conventional coil-on-chip solutions, demonstrating that antenna integration and secure computation can coexist within extremely limited spatial constraints. Although implemented as a dedicated SiP module rather than a SIM-compatible substrate, the work highlights the feasibility of tightly integrated secure contactless systems for authentication and micropayment applications.
Beyond physical miniaturization, optimization of cryptographic operations under constrained power and area conditions has also received significant attention. Druml et al. [12] proposed a lightweight elliptic-curve cryptography (ECC)-based authentication architecture designed for resource-constrained RFID and NFC systems. Their design strategically shifts computationally intensive ECC operations to the authentication terminal while maintaining secure one-way authentication. By incorporating a compact hardware acceleration core within a security controller, the system achieves authentication within 25 ms and backend verification within 66 ms. Although the primary contribution lies in cryptographic efficiency rather than antenna design, this work demonstrates the architectural importance of balancing security strength, latency, and hardware footprint in miniaturized NFC-enabled embedded systems.
Material-level innovations have further expanded possibilities for compact and flexible antenna integration. Asavanarakul et al. [13] proposed a graphene-based RFID tag antenna implemented as a flexible rectangular monopole on a graphene sheet substrate. The antenna exhibited wide bandwidth, stable radiation characteristics, and mechanical bendability suitable for integration into constrained physical environments. While the study targets vehicular border-passing systems rather than SIM-based architectures, it illustrates the broader trend toward flexible, lightweight, and material-optimized RFID antenna structures capable of operating reliably under mechanical deformation.
In contrast to chip-based antenna architectures, Shen et al. [14] reviewed chipless RFID-inspired sensing systems that rely on frequency-domain or time-domain electromagnetic signatures for identification. These passive architectures eliminate integrated circuits entirely, enabling low-cost and maintenance-free sensing. However, chipless RFID systems generally lack secure elements, cryptographic anchoring, and controlled activation mechanisms. As a result, while attractive for sensing and environmental monitoring applications, such architectures are not directly applicable to trusted authentication frameworks or SIM-based secure infrastructures.
Further material advancements were demonstrated by Scidà et al. [15], who fabricated multilayer graphene-based flexible NFC antennas for consumer electronics and smart card applications. Their carbon-based antenna structures maintained stable inductance, resonance frequency, and electrical conductivity under repeated bending cycles while complying with ISO/IEC 15693 communication standards [16]. Performance was shown to be comparable to conventional metallic NFC antennas, validating the viability of graphene-based alternatives in compact contactless systems. The study emphasizes that mechanical stability, conductivity retention, and electromagnetic tuning are critical parameters in integrating antenna structures into flexible smart card-like platforms.
Collectively, these works demonstrate significant progress in antenna miniaturization, flexible material integration, and cryptographic optimization within contactless authentication systems. However, a common architectural characteristic emerges: most antenna-integrated designs embed complete contactless communication subsystems within the hardware module itself. In many cases, active RF circuitry, dedicated transceivers, or standalone authentication controllers are incorporated directly into the device.
While such integration enhances standalone functionality, it may introduce increased electromagnetic complexity, additional power demands, and duplication of wireless subsystems already present in modern smartphones. The challenge therefore lies not merely in embedding antennas or secure elements into constrained form factors, but in determining whether full transceiver integration is necessary when native wireless modules are already available within the host device.
This observation provides a conceptual transition toward examining protocol-level and remote SIM architectures, which are discussed in the following subsection.
2.3. Protocol-Level, Remote and Shared SIM Architectures
A substantial body of research has focused on extending SIM functionality through protocol-level and cryptographic enhancements rather than through modifications of the physical SIM interface. These approaches aim to strengthen authentication, enable secure service portability, and support multi-network interoperability while preserving the existing hardware abstraction of the SIM architecture.
One of the early directions involved integrating Public Key Infrastructure (PKI) capabilities directly within SIM cards. Rongyu et al. proposed the PK-SIM architecture, which embeds PKI-based mechanisms into the SIM to enable secure end-to-end SMS communication [17]. Their framework introduces digital signature support, session key establishment, and asymmetric cryptographic operations while leveraging existing mobile operator infrastructure. This design demonstrates that SIM cards can support advanced cryptographic services beyond subscriber authentication. However, the enhancement remains confined to the logical and cryptographic layers without altering the physical SIM interface or enabling new hardware-level interaction capabilities.
Further research has explored strengthening device-level authentication by binding heterogeneous device identifiers to SIM credentials. Yang et al. proposed enhanced authentication schemes for M2M and LTE-M environments that integrate IMEI–IMSI pairing and hardware fingerprinting techniques such as clock skew analysis into USIM-based authentication processes [18]. By coupling device-specific attributes with SIM credentials, these schemes increase resistance against device impersonation attacks. Nevertheless, they rely on protocol-layer integration and device metadata binding, without extending the SIM interface toward hardware-level control or wireless subsystem coordination.
The transition from removable SIM cards to embedded SIM (eSIM) architectures introduced standardized Remote SIM Provisioning (RSP) mechanisms defined by the GSMA. These frameworks enable secure over-the-air profile download, management, and lifecycle control, particularly in M2M deployments. Ko et al. conducted a formal security and performance analysis of the M2M RSP protocol and identified critical vulnerabilities, including the absence of Perfect Forward Secrecy and performance bottlenecks in cryptographic operations [19]. Their findings illustrate the increasing complexity of SIM-related protocol stacks and the growing reliance on remote provisioning infrastructures. However, RSP mechanisms operate strictly within secure provisioning and credential management domains and do not introduce hardware-level activation or physical-layer interaction capabilities at the SIM interface.
Multi-service smart card architectures have also been investigated to improve portability and reduce user-side complexity. Rossudowski et al. proposed a privacy-aware architecture enabling a single smart card to support multiple applications via dynamic service management and protected messaging schemes [20]. Their protocol integrates mechanisms such as one-time passwords to maintain confidentiality and interoperability across services. While this expands logical functionality and enhances service portability, it does not extend the SIM card’s physical interface or introduce new mechanisms for hardware-level wireless coordination.
The reuse of SIM credentials across heterogeneous wireless environments represents another important research direction. Tsai et al. proposed improved SIM-based authentication protocols enabling seamless roaming between cellular networks and WLAN infrastructures using EAP-AKA-based mechanisms [21]. Similarly, Tsai and Chang demonstrated the feasibility of leveraging GSM/GPRS SIM credentials for WLAN authentication by integrating cellular authentication procedures into WLAN access control systems [22]. These studies confirm the adaptability of SIM-based authentication across heterogeneous network domains. However, they remain confined to credential reuse and protocol refinement, without modifying the physical SIM interface or enabling hardware-triggered wireless module activation.
At a broader protocol level, Extensible Authentication Protocol (EAP) frameworks underpin many SIM-based authentication schemes in wireless networks. Dantu et al. provided a comprehensive analysis of EAP methods used in WLANs and heterogeneous wireless environments, evaluating security strengths and vulnerabilities across multiple deployment scenarios [23]. Their work situates SIM-based EAP mechanisms (e.g., EAP-SIM, EAP-AKA) within the wider context of roaming and fixed-mobile convergence architectures. Yet, these frameworks primarily address authentication flow design rather than hardware-level coordination or activation mechanisms.
Privacy-preserving smart card authentication protocols have also been proposed to mitigate anonymity leakage and password-guessing vulnerabilities. Odelu et al. introduced an elliptic-curve cryptography (ECC)-based client authentication protocol employing smart cards with mutual authentication and key agreement guarantees, formally verified using the AVISPA v1.1 automated security protocol verification tool [24]. While significantly improving protocol-layer security properties, the scheme does not address architectural aspects of SIM-based hardware interaction or wireless subsystem control.
Finally, Davis highlighted critical security pitfalls in contactless smart card deployments, demonstrating that certain access control systems bypass cryptographic authentication entirely and rely solely on card serial number (CSN) reading [25]. Such architectural misconfigurations effectively nullify embedded security guarantees and expose systems to cloning and impersonation attacks. This study underscores that overall system security depends not only on cryptographic protocol strength but also on the hardware interaction model and reader architecture design.
Collectively, these works illustrate a dominant research trajectory centered on cryptographic reinforcement, credential portability, remote provisioning, and multi-network interoperability. SIM-based systems have evolved into powerful trust anchors capable of supporting PKI services, M2M authentication, roaming infrastructures, and privacy-preserving protocols. However, across these studies, the SIM interface itself remains largely static at the physical layer. Enhancements occur at the logical, cryptographic, or provisioning levels rather than through hardware-level extensions enabling controlled activation of native wireless modules or physical-layer interaction mechanisms.
This observation reveals a consistent architectural pattern: while protocol-level sophistication continues to increase, the SIM interface is rarely leveraged as a hardware coordination layer for wireless subsystem control. This gap forms the basis for the design limitations and research challenges discussed in the following subsection.
2.4. Design Limitations and Research Gap
Smart card platforms, including SIM and UICC architectures, operate under stringent hardware and software constraints. Limited non-volatile memory, restricted RAM availability, low-frequency clock domains, and ISO/IEC 7816-based serial communication interfaces define a tightly controlled execution environment [26]. These constraints are intentionally imposed to ensure tamper resistance and predictable behavior. However, they also restrict architectural extensibility when additional functionalities are introduced beyond conventional subscriber authentication. Any attempt to extend SIM capabilities toward hardware-level wireless coordination must therefore carefully balance functional expansion with preservation of security isolation and resource efficiency.
The robustness of smart card platforms has been repeatedly examined in the context of adversarial execution and fault injection attacks. Hamadouche and Lanet demonstrated that malicious Java Card applications can alter their behavior under laser-induced fault injection, potentially bypassing traditional verification mechanisms [27]. These findings highlight that even formally verified smart card applications may exhibit unintended behavior when exposed to physical perturbations. Consequently, extending SIM functionality through complex application-layer logic may inadvertently enlarge the attack surface.
To address computational limitations of individual smart cards, hardware-level scaling approaches have been proposed. Barbosa et al. introduced a Smart Card Cluster (SCC) architecture managed by an FPGA to enable parallelized cryptographic processing across multiple smart cards for IoT security applications [28]. While this approach improves computational throughput and maintains hardware-level protection, it relies on external orchestration hardware and significantly increases system complexity. Rather than extending the SIM interface itself, clustering approaches effectively circumvent intrinsic platform limitations through additional infrastructure.
Software-level vulnerabilities further demonstrate the fragility of extending complex logic within constrained smart card environments. Bouffard and Lanet presented a generic Control Flow Transfer (CFT) attack capable of manipulating the Java Card program counter through type confusion exploits [29]. Their results illustrate how application-layer complexity may introduce new attack vectors within smart card platforms.
System-level integration approaches have also been explored. Catuogno et al. proposed SmartK, a framework embedding smart card functionalities into the Linux kernel to support trusted execution and secure key management [30]. Although such approaches enhance host-level integration, they require deep modifications of the operating system stack and tightly couple smart card services to the host environment. As a result, the SIM interface itself is not repurposed as an independent hardware coordination layer.
Further attempts to expand smart card capabilities toward application environments have revealed additional risks. Kamel and Lanet analyzed Java Card platforms embedding web server functionality and demonstrated susceptibility to traditional web-based attacks such as cross-site scripting (XSS) [31]. These findings suggest that increasing application-layer functionality inside constrained smart card environments may undermine their inherent security advantages.
Hardware-level protection mechanisms have also been investigated to improve resistance against side-channel and fault attacks. Moore et al. developed a balanced self-checking asynchronous logic architecture designed to mitigate differential power analysis and electromagnetic emission attacks [32]. While such techniques significantly enhance internal cryptographic robustness, they primarily address computational security rather than architectural evolution of external interfaces.
Comprehensive surveys of smart card security further highlight the systemic nature of vulnerabilities. Leng [33] reviewed both contact and contactless smart card architectures and discussed common attack vectors including side-channel analysis, fault injection, and logical manipulation. Similarly, Markantonakis et al. [34] emphasized that many vulnerabilities arise not solely from the card itself but from broader system architectures involving readers, wireless interfaces, and distributed infrastructures. These studies demonstrate that secure smart card deployment requires careful consideration of both internal robustness and system-level interaction models.
Beyond the smart card domain, related architectural ideas have been explored in event-triggered control systems and low-power sensing networks. Ji and Zheng [35] investigate distributed mode-dependent event-triggered filtering mechanisms where computation and communication are activated only when predefined event conditions are satisfied. Although developed for robotic control systems, such approaches illustrate a broader architectural principle: passive or condition-based triggers can activate higher-level system processes only when necessary.
A closely related concept appears in ultra-low-power wake-up receiver (WUR) architectures widely used in wireless sensor networks. D’Addato et al. [36] describe a nanowatt clock and data recovery architecture enabling extremely low-power wake-up receivers that continuously monitor incoming signals while the primary communication radio remains inactive. When a valid signal is detected, the wake-up circuit activates the main communication subsystem.
Recent research has extended this concept to cellular Internet of Things networks. Wang et al. [37] present low-power wake-up receiver architectures for resilient cellular IoT deployments, demonstrating how lightweight receivers can monitor RF channels while the primary radio remains in deep sleep.
Similarly, Fromm et al. [38] propose an optimized wake-up receiver using low-frequency pattern matching and passive envelope detection to improve signal sensitivity while maintaining low energy consumption. Maistriaux et al. [39] further explore wake-up architectures for long-range wireless systems using chirp spread spectrum detection mechanisms to increase sensitivity in LPWAN environments.
These studies collectively demonstrate the growing interest in architectures that decouple ultra-low-power signal detection from higher-power communication subsystems. However, these approaches typically assume the presence of dedicated RF detection hardware integrated directly within the wireless node.
In contrast, the possibility of using the SIM/UICC interface itself as a hardware coordination layer capable of triggering wireless subsystem activation within smartphone architectures remains largely unexplored.
Across the reviewed literature, a consistent pattern emerges. Research efforts predominantly address:
- cryptographic strengthening and protocol refinement;
- lifecycle management and remote provisioning;
- fault and side-channel resistance;
- clustering and host-level integration;
- application-layer expansion within Java Card environments.
However, comparatively little attention has been devoted to reinterpreting the SIM slot itself as a hardware coordination interface capable of interacting with native wireless subsystems of the host device. Existing solutions typically (i) extend functionality at the protocol layer, (ii) introduce external hardware modules, (iii) embed complete contactless transceiver subsystems, or (iv) increase application-layer complexity within constrained smart card environments.
What remains largely unexplored is a lightweight, SIM-compatible hardware activation mechanism that:
- 1.
- preserves the nano-SIM (4FF) mechanical and electrical interface;
- 2.
- avoids embedding redundant RF transceivers;
- 3.
- minimizes additional application-layer logic within the SIM execution environment;
- 4.
- enables controlled activation of native wireless modules (e.g., BLE) while supporting passive field detection;
- 5.
- maintains compatibility with existing smartphone architectures without requiring operating system modification.
This research gap motivates the design of a SIM-compatible flexible activation interface that operates not as a standalone communication device but as a hardware-level coordination layer. By shifting the architectural focus from cryptographic expansion or protocol refinement toward controlled physical-layer activation, the proposed approach addresses an underexplored dimension of SIM-based system evolution.
3. System Architecture
The proposed SIM-compatible hardware coordination architecture is conceived as a flexible multilayer electronic interface operating within the nano-SIM (4FF) mechanical form factor. Unlike antenna-integrated SIM modules embedding full contactless communication subsystems, the proposed architecture is not intended to function as an independent wireless transceiver. Instead, it is designed as a hardware-level coordination layer that combines passive RF field detection, trusted decision logic, and controlled trigger generation within a SIM-compatible integration model.
The architecture is assumed to be electrically powered and logically coupled through the standard SIM/UICC interface, thereby preserving compatibility with existing mobile-device integration principles. Rather than directly controlling the host device’s wireless controller, the proposed concept defines a trusted trigger pathway that may interact with native wireless subsystems through existing telephony and system-service mechanisms available on supported platforms.
3.1. Overall System Concept
The proposed SIM-compatible coordination interface is organized around three interacting domains:
- 1.
- The external wireless environment, including low-frequency RFID and high-frequency NFC fields;
- 2.
- The SIM/UICC electrical interface compliant with ISO/IEC 7816;
- 3.
- The native wireless subsystem domain of the host mobile device, represented here by Bluetooth Low Energy (BLE) as a target activation scenario.
Rather than embedding an active RF transmitter or an additional wireless communication module, the architecture performs passive electromagnetic field detection and generates a controlled trigger event intended for delivery through the SIM/UICC interaction chain. This design seeks to avoid duplication of wireless hardware while preserving compatibility with standard mobile system architectures.
As illustrated in Figure 1, the system architecture separates three conceptual layers: the external RF detection stage, the trusted coordination domain, and the host mobile-device domain. Passive LF and HF detection structures feed an RF conditioning and signal-selection stage. The resulting event is then evaluated within a hardware-isolated trusted coordination domain consisting of an activation controller and a secure element responsible for authentication and policy enforcement. Under authorized conditions, the coordination layer produces a controlled trigger event aligned with the standard SIM/UICC interaction model. This event is conceptually intended to be propagated through existing telephony and system-service pathways, enabling context-aware interaction with the native BLE subsystem of the host device without introducing an additional active Bluetooth transmitter.
Figure 1.
Conceptual system architecture of the proposed SIM-compatible hardware coordination interface, illustrating passive dual-band RF detection, secure evaluation within a trusted coordination domain, SIM/UICC-powered operation, and the intended trigger pathway toward native wireless subsystem interaction in the host mobile device.
3.2. Trusted Coordination Domain
At the core of the proposed architecture lies a trusted coordination domain responsible for validating external trigger events and generating controlled interaction signals within the SIM/UICC interface environment. This domain is conceptually isolated from the external RF detection stage and the host mobile-device domain, providing a secure boundary in which policy evaluation and authentication logic can be executed.
The trusted coordination domain consists of two primary functional components: an activation controller and a secure element. The activation controller performs signal validation and coordination logic, while the secure element provides a hardware-rooted trust anchor responsible for authentication and policy enforcement.
The activation controller receives conditioned signals originating from the passive RF detection stage. These signals correspond to detected electromagnetic fields within the low-frequency RFID (125–134 kHz) or high-frequency NFC (13.56 MHz) bands. Rather than directly interpreting the detected signal as a valid activation command, the controller performs preliminary validation procedures, including signal stability verification, threshold evaluation, and temporal filtering. This stage reduces the likelihood of unintended triggers caused by environmental electromagnetic noise or transient interference.
Following preliminary validation, the event may be forwarded to the secure element for policy evaluation. The secure element conceptually acts as a trusted execution environment responsible for enforcing activation policies and managing cryptographic credentials. Such policies may include authentication of external triggers, contextual authorization rules, or cryptographic challenge–response mechanisms with external tags or readers. By delegating authorization decisions to the secure element, the architecture aims to ensure that only trusted external interactions can generate valid trigger events.
If the event satisfies the configured policy constraints, the coordination domain generates a controlled trigger signal aligned with the SIM/UICC interaction model. In this architecture, the trigger is not intended to directly control host-device hardware subsystems. Instead, it represents a structured event originating from the SIM domain that may be propagated through existing telephony frameworks or system services available on supported mobile platforms.
This coordination mechanism enables the SIM-compatible interface to function as a trusted event-generation layer rather than an independent wireless communication device. By separating RF detection, authorization logic, and host-device interaction into distinct architectural domains, the system conceptually reduces the attack surface associated with external RF triggers while preserving compatibility with existing mobile-device integration principles.
From a security perspective, the trusted coordination domain serves as the primary defense layer against unauthorized activation attempts. Because trigger generation is conditioned on policy evaluation within the secure element, the architecture supports flexible authentication models and policy updates without requiring modification of the host device firmware or kernel. This design principle allows the coordination layer to remain modular and adaptable across different device ecosystems.
It should be noted that the trusted coordination domain described here represents a conceptual architectural model intended to illustrate a possible hardware coordination mechanism within the SIM/UICC environment. Specific implementation details, including controller microarchitecture, secure element selection, and cryptographic protocol design, may vary depending on target deployment scenarios and hardware integration constraints.
3.3. Passive RF Detection Layer
The proposed coordination architecture incorporates a passive RF detection layer designed to sense the presence of external electromagnetic fields within two commonly used contactless communication bands. The detection layer operates exclusively in a passive sensing mode and does not include active RF transmission components. Its purpose within the overall architecture is to convert incident electromagnetic energy into electrical signals that can be evaluated by the trusted coordination domain.
To enable dual-band detection capability, the architecture conceptually integrates two antenna subsystems operating in the low-frequency RFID band (125–134 kHz) and the high-frequency NFC band (13.56 MHz). Both subsystems are implemented as planar conductive structures compatible with flexible printed electronics technologies and designed to operate within the mechanical constraints of the nano-SIM (4FF) form factor.
3.3.1. Low-Frequency RFID Detection Structure (125–134 kHz)
The low-frequency detection subsystem is based on a planar multi-turn inductive coil implemented using conductive traces on a flexible substrate. Such structures are commonly used in near-field RFID systems where magnetic coupling between a reader coil and a passive antenna enables field detection.
Within the proposed architecture, the LF coil is intended to operate purely as a magnetic field sensor. When exposed to an external 125–134 kHz RFID field, inductive coupling generates a small induced voltage across the coil terminals. This signal can be routed to an RF conditioning stage where it is filtered and evaluated by the coordination logic. The subsystem does not incorporate modulation circuitry or RF power generation stages, ensuring that the detection layer remains purely passive.
3.3.2. High-Frequency NFC Detection Structure (13.56 MHz)
In addition to the LF coil, the architecture includes a compact loop antenna designed for detection of high-frequency NFC fields around 13.56 MHz. Loop antennas of this type are widely used in contactless communication systems due to their compatibility with near-field magnetic coupling.
Because the available surface area within the nano-SIM footprint is extremely limited, the antenna geometry must be carefully arranged to maintain stable inductive characteristics while preserving mechanical flexibility. The loop antenna serves as a field presence detector rather than a communication transceiver. Incident electromagnetic energy can therefore be converted into a detectable signal without embedding active RF transmitters or standalone NFC controllers within the SIM-compatible interface.
3.3.3. Passive Detection Mode and RF Conditioning
Both detection structures operate in passive mode and are intended solely for sensing the presence of external RF fields. The proposed architecture does not incorporate RF transmitters, active modulation circuitry, or independent wireless communication modules. Instead, the induced signals generated by the LF and HF antennas are routed through an RF conditioning stage responsible for filtering, thresholding, and basic impedance adaptation before entering the trusted coordination domain.
The conditioning stage conceptually serves to stabilize the detected signals and reduce the impact of environmental noise or transient electromagnetic disturbances. In practical mobile-device environments, nearby metallic components, smartphone chassis elements, and coexisting wireless subsystems may influence antenna behavior. Accordingly, relevant design considerations include impedance stabilization and magnetic field confinement techniques that can improve coupling consistency within compact device enclosures.
The dual-band passive detection layer demonstrates how RF field sensing may be integrated within the dimensional constraints of a nano-SIM-compatible interface while avoiding the inclusion of additional active wireless transceivers. The resulting signals provide environmental trigger information that can subsequently be evaluated by the trusted coordination domain described in the following section.
Figure 2 conceptually illustrates the placement of passive RF detection structures within the nano-SIM-compatible footprint.
Figure 2.
Conceptual layout of a flexible nano-SIM-compatible hardware coordination interface illustrating passive LF RFID coil and HF NFC loop antenna placement within the SIM (4FF) form factor constraints.
In realistic smartphone environments, the RF detection layer may be exposed to various electromagnetic sources such as wireless charging systems, NFC payment terminals, or nearby RFID tags. Off-frequency interferers or strong electromagnetic fields could potentially influence antenna coupling characteristics.
To reduce the risk of unintended activations, the architecture relies on threshold-based detection combined with subsequent validation within the trusted coordination domain. Nevertheless, strong electromagnetic interference could theoretically cause denial-of-activation scenarios by masking valid signals. Comprehensive characterization of such interference conditions remains an important topic for future experimental investigation.
3.4. Mechanical Integration Within Nano-SIM (4FF) Constraints
The proposed coordination interface is conceptually designed as a flexible multilayer electronic substrate compatible with the nano-SIM (4FF) mechanical form factor. Flexible polyimide substrates are commonly used in compact electronic assemblies due to their mechanical robustness, electrical insulation properties, and compatibility with printed conductive structures. Such materials provide a suitable platform for integrating passive RF detection structures within the dimensional constraints of the SIM slot.
Within the proposed architecture, the flexible substrate serves as the mechanical carrier for passive antenna structures, signal routing traces, and the trusted coordination circuitry. The design is intended to preserve compatibility with the ISO/IEC 7816 electrical contact layout while remaining mechanically aligned with the nano-SIM footprint used in standard mobile devices. Because the architecture operates within the SIM interface domain, it does not require modifications to the SIM tray, baseband circuitry, or device enclosure.
Figure 3 conceptually illustrates a representative multilayer stack suitable for implementing the proposed interface. The stack includes a protective polymer encapsulation layer, printed conductive antenna traces, a flexible polyimide dielectric substrate hosting coordination circuitry such as a secure element, a ferrite stabilization layer for magnetic field conditioning, and ISO/IEC 7816-compliant contact pads.
Figure 3.
Conceptual cross-sectional layer stack of a nano-SIM compatible coordination interface illustrating the protective encapsulation layer, printed conductive antenna traces, flexible polyimide substrate hosting coordination circuitry, ferrite stabilization layer, and ISO/IEC 7816 contact pads.
The ferrite layer may be positioned beneath the antenna regions in order to improve magnetic field confinement and reduce detuning effects that can arise from nearby metallic structures within smartphone enclosures. Such magnetic conditioning techniques are commonly employed in compact RF designs where antenna proximity to conductive device components can affect coupling efficiency.
From a mechanical perspective, flexible multilayer substrates allow limited bending and deformation without compromising electrical continuity. These characteristics make polyimide-based flexible electronics a suitable candidate technology for integration within confined device environments such as SIM slots, where thin and mechanically compliant structures are required.
The mechanical stack illustrated in Figure 3 therefore represents a conceptual integration model demonstrating how passive RF sensing structures and coordination circuitry may be arranged within nano-SIM dimensional constraints while preserving compatibility with existing mobile-device hardware interfaces.
3.5. SIM/UICC Interface Interaction Model
The proposed coordination architecture is designed to operate within the standard SIM/UICC interaction framework defined by ISO/IEC 7816. In modern mobile devices, the SIM card functions as a secure element connected to the baseband processor through a standardized electrical and protocol interface. This interface enables the SIM to exchange commands, status information, and event notifications with the host system through the telephony stack.
Within the proposed architecture, the coordination interface is conceptually powered through the SIM/UICC electrical contacts and participates in the same communication environment as a conventional SIM card. The interface therefore relies on the existing SIM power supply and communication channels rather than introducing a dedicated power source or independent wireless subsystem.
When an external RF field is detected and validated by the trusted coordination domain, the system generates a structured trigger event within the SIM domain. Rather than directly controlling hardware subsystems of the host device, the trigger is intended to be propagated through standard SIM interaction mechanisms available in mobile platforms. These mechanisms may include SIM Toolkit (STK) / SIM Application Toolkit (SAT) event notifications or other telephony-layer signaling pathways supported by the device operating system.
Through this interaction model, the SIM-compatible coordination interface functions as an event-originating component within the telephony architecture. The host device operating system can then interpret the resulting event through existing system services and determine appropriate actions at the application or system level.
Because the architecture relies on the existing SIM/UICC communication framework, it preserves compatibility with conventional mobile device integration principles. No direct electrical control of host wireless hardware is assumed within the coordination layer. Instead, the architecture defines a trusted event pathway originating from the SIM domain that may interact with higher-level software components of the host device.
This interaction model allows the coordination interface to remain independent from specific mobile operating systems or hardware platforms while still enabling controlled interaction with native device subsystems through standard telephony infrastructure.
In practical smartphone implementations, SIM-generated events are interpreted by the baseband modem and forwarded to higher layers of the telephony framework through standardized SIM Toolkit (STK/SAT) mechanisms. The proposed architecture therefore does not assume direct electrical control of the BLE subsystem. Instead, the trigger event is conceptually interpreted by the telephony stack as a SIM-originated event that may be handled by the operating system or associated services.
Depending on the smartphone platform, such events may be mapped to telephony framework notifications, system interrupts within the modem subsystem, or STK-based signaling mechanisms. The architecture therefore relies on existing SIM communication pathways rather than introducing new hardware signaling channels.
3.6. Host Device Interaction Model
The proposed coordination architecture does not directly control the wireless hardware of the host mobile device. Instead, it defines a conceptual interaction pathway through which trigger events originating in the SIM/UICC domain may be propagated to the host system using existing telephony frameworks.
In modern smartphones, the SIM card communicates with the baseband processor through the ISO/IEC 7816 interface and interacts with higher-level system components through the telephony stack. Within this framework, SIM-originated events can be delivered to the host operating system using mechanisms such as SIM Toolkit (STK) / SIM Application Toolkit (SAT) mechanisms notifications or other platform-specific signaling pathways supported by the device.
In the proposed architecture, when an external RF field is detected and successfully validated within the trusted coordination domain, the system generates a structured event within the SIM interaction layer. This event does not directly activate the Bluetooth hardware. Instead, it serves as a trigger signal that may be interpreted by the host operating system through existing system services.
Depending on the platform implementation, the operating system or associated system applications may respond to such events by initiating actions within native device subsystems, including wireless communication modules such as Bluetooth Low Energy (BLE). The coordination interface therefore acts as an event-originating component within the telephony architecture rather than as a direct hardware controller.
Figure 4 conceptually illustrates the temporal relationship between RF field detection, validation within the trusted coordination domain, generation of a SIM-domain trigger event, and the subsequent response of the host device. Because the interpretation of SIM-originated events is managed by the operating system and telephony framework, the exact timing and behavior of the resulting subsystem activation may vary across mobile platforms.
Figure 4.
Conceptual timing relationship between RF field detection, validation within the trusted coordination domain, generation of a SIM-domain trigger event, and the potential response of the host device wireless subsystem.
Within this model, all BLE communication remains fully managed by the native radio stack and operating system of the smartphone. The SIM-compatible coordination interface does not participate in wireless transmission, device pairing, or data exchange. Its role is limited to providing trusted trigger information derived from external RF field conditions.
By separating RF detection, authorization logic, and host-device response into distinct architectural domains, the proposed system minimizes hardware duplication while preserving compatibility with standard mobile-device integration models.
It should be noted that the exact interpretation of SIM-originated events may vary across smartphone platforms and operating systems. Different modem chipsets and telephony frameworks may implement distinct internal signaling pathways between the SIM interface, baseband processor, and higher-level system services. Consequently, the architecture presented in this work should be interpreted as a coordination concept rather than a device-specific implementation.
In practical deployments, platform-specific adaptations may be required to map SIM-originated events to system-level actions such as BLE subsystem activation or service wake-up. Such integration would typically occur within the telephony framework or trusted system services of the host device.
3.7. Architectural Distinction from Existing Solutions
Several existing approaches address wireless activation or authentication in mobile devices, including antenna-integrated SIM solutions, external Bluetooth Low Energy (BLE) tokens, and operating-system-level activation mechanisms. The proposed coordination architecture differs from these approaches by introducing a SIM-compatible hardware coordination layer that generates trusted trigger events without embedding an independent wireless communication subsystem.
In antenna-integrated SIM designs, passive NFC antennas are typically combined with secure elements to enable contactless payment or authentication services. These systems operate as contactless communication interfaces and require dedicated NFC controllers or reader interactions to exchange data with external devices. In contrast, the architecture proposed in this work does not attempt to implement a full contactless communication stack. Instead, passive RF detection structures are used solely to sense the presence of external electromagnetic fields and provide trigger information to the trusted coordination domain.
Another widely used solution involves external BLE tokens or beacon devices that transmit advertising packets to initiate interactions with smartphones. While such devices can enable proximity-based activation mechanisms, they require active radio transmitters, dedicated batteries, and pairing or discovery procedures within the mobile device. The architecture proposed in this work eliminates the need for additional wireless transmitters by relying on passive RF detection combined with SIM-domain event generation.
Operating-system-level activation mechanisms represent another class of solutions in which mobile applications monitor wireless conditions or sensor inputs to trigger device behavior. These approaches rely entirely on software execution within the host device and may therefore be affected by application permissions, background execution policies, and operating-system restrictions. By contrast, the proposed coordination architecture introduces a hardware-originated event pathway that operates within the telephony interaction framework of the SIM/UICC interface.
From a security perspective, the integration of a secure element within the trusted coordination domain enables policy-based validation of external trigger conditions before any event is propagated to the host device. This approach allows authentication logic and authorization policies to be enforced within a hardware-rooted trust environment rather than solely within application-layer software.
The resulting architecture therefore represents a hybrid design that combines passive RF field sensing, hardware-based policy enforcement, and SIM-domain event generation. By positioning the coordination layer between the external RF environment and the host device telephony interface, the system provides a structured mechanism for generating trusted trigger events without introducing additional wireless communication modules or modifying existing mobile-device firmware.
4. Conceptual Evaluation and Design Considerations
The proposed SIM-compatible coordination architecture is evaluated conceptually with respect to its feasibility within typical mobile-device integration constraints. Rather than presenting a fully optimized hardware implementation, this section discusses key design considerations that influence practical deployment of the architecture in real-world mobile environments.
The evaluation focuses on four principal aspects: RF field detection feasibility within nano-SIM dimensional constraints, interaction with the SIM/UICC interface, mechanical integration within compact device enclosures, and system-level compatibility with existing mobile-device subsystems.
4.1. RF Field Detection Feasibility
Passive detection of external electromagnetic fields within the low-frequency RFID (125–134 kHz) and high-frequency NFC (13.56 MHz) bands is widely used in near-field communication systems. Inductive coupling between a reader coil and a passive loop structure enables detection of incident magnetic fields without requiring active RF transmission.
Within the proposed architecture, passive antenna structures serve only as field presence sensors rather than as communication interfaces. The limited physical footprint of the nano-SIM form factor imposes constraints on achievable inductance and coupling efficiency. However, compact loop and coil geometries can still generate detectable signals under sufficiently strong reader-field conditions typically present in contactless interaction scenarios.
Design considerations therefore include antenna geometry optimization, impedance stabilization, and mitigation of detuning effects caused by nearby metallic components inside the smartphone enclosure. Magnetic field conditioning layers such as ferrite backing may improve field confinement and coupling consistency under such constraints.
4.2. SIM/UICC Power and Interface Constraints
The coordination interface operates within the electrical environment provided by the SIM/UICC interface defined by ISO/IEC 7816. In conventional mobile architectures, the SIM receives power through the VCC line and communicates with the baseband processor via standardized serial communication protocols.
Because the proposed architecture does not incorporate active RF transmitters or independent wireless subsystems, its power requirements are conceptually limited to event detection, coordination logic, and secure policy evaluation. Such operations typically fall within the power envelopes commonly associated with SIM-based secure elements and low-power microcontroller logic.
This design approach allows the coordination layer to rely on the existing SIM power supply rather than requiring an onboard battery or auxiliary energy storage element.
4.3. Mechanical Integration Considerations
Integration within the nano-SIM (4FF) footprint imposes strict dimensional constraints on electronic structures. Flexible printed electronics technologies, particularly polyimide-based substrates with printed conductive traces, provide a feasible approach for embedding passive RF detection structures within thin mechanical assemblies.
Flexible multilayer substrates can accommodate antenna traces, routing conductors, and coordination circuitry while maintaining mechanical compliance required for insertion into standard SIM trays. Encapsulation layers and ferrite stabilization structures may further improve environmental robustness and magnetic coupling stability.
Although precise mechanical characteristics depend on specific fabrication technologies, flexible printed electronic assemblies have been widely demonstrated in compact consumer electronics and wearable devices, indicating their suitability for constrained form-factor integration scenarios.
4.4. System-Level Compatibility
An important architectural objective of the proposed coordination interface is to avoid introducing additional wireless transmitters or modifications to the host device firmware. Instead, the architecture generates structured trigger events within the SIM/UICC interaction domain.
These events may be propagated through existing telephony frameworks and interpreted by system-level software components of the host device. Because the exact behavior of such interactions depends on operating-system policies, telephony stack implementations, and device vendor configurations, the resulting subsystem responses may vary across mobile platforms.
By separating RF detection, policy validation, and host-device response into independent architectural domains, the coordination interface minimizes coupling between external trigger conditions and device hardware subsystems. This separation contributes to improved modularity and reduces the risk of unintended interactions with existing wireless communication components.
4.5. Security and Deployment Considerations
From a security perspective, the trusted coordination domain introduces a hardware-rooted control layer capable of evaluating external trigger conditions before any event is propagated to the host system. Integration of a secure element allows authentication policies, cryptographic verification procedures, and access-control logic to be enforced within a tamper-resistant hardware environment.
This architecture may help mitigate risks associated with unauthorized activation attempts, replay attacks, or spoofed RF signals. At the same time, practical deployment would require careful consideration of provisioning procedures, secure element policy management, and potential platform-specific integration constraints.
Overall, the conceptual evaluation presented in this section indicates that the proposed coordination architecture aligns with typical design principles of compact mobile electronics and SIM-based secure infrastructures. While detailed hardware implementations and performance characterization would depend on specific fabrication technologies and platform integrations, the architecture provides a plausible framework for enabling trusted RF-triggered interaction mechanisms within mobile devices.
5. Security Analysis
5.1. Threat Model
The security analysis considers a proximity-capable adversary operating under realistic mobile-device deployment conditions.
The attacker is assumed to be capable of generating controlled low-frequency (125–134 kHz) or high-frequency (13.56 MHz) electromagnetic fields, attempting replay of previously observed trigger conditions, manipulating external SIM electrical contacts at the ISO/IEC 7816 interface level, injecting electromagnetic interference, or physically accessing the nano-SIM substrate in a non-invasive manner.
The adversary is not assumed to have the capability to compromise internal smartphone hardware, extract cryptographic secrets from the secure element (SE), obtain operating-system-level control of the host device, or perform invasive semiconductor-level attacks on secure hardware components.
Under this model, potential attack objectives include unauthorized trigger generation, replay of previously observed RF conditions, electrical manipulation of the SIM interface, or attempts to exploit weaknesses in the validation logic implemented within the trusted coordination domain.
The trusted coordination domain therefore represents the primary security boundary of the architecture, where RF detection signals are validated before any event is propagated toward the host device interaction layer.
5.2. Passive RF Detection Security Implications
The proposed architecture relies exclusively on passive RF field detection and does not include active wireless transmission capabilities. As a result, the coordination interface does not expose an RF communication endpoint that could be directly interrogated by external devices.
Compared with antenna-integrated SIM designs that incorporate full NFC or wireless transceiver stacks, passive RF detection significantly reduces the complexity of the wireless interface. Because the system does not implement bidirectional RF communication protocols, it avoids many classes of attacks that typically target wireless protocol parsing or session negotiation mechanisms.
However, passive detection systems remain susceptible to intentional RF field generation by nearby devices. Consequently, detection alone cannot be considered a secure activation condition. For this reason, the proposed architecture introduces additional validation stages within the trusted coordination domain before any trigger event is generated.
5.3. Secure Element-Based Policy Enforcement
Within the trusted coordination domain, a secure element provides a hardware-rooted environment for policy evaluation and authentication logic. The secure element can store policy parameters, cryptographic credentials, and validation rules that determine whether a detected RF event should be considered valid.
By placing these decisions inside a tamper-resistant hardware environment, the architecture aims to reduce the risk that external RF stimulation alone can trigger unintended system behavior. Instead, external field detection must be combined with successful policy evaluation before any event is propagated through the SIM/UICC interaction model.
This approach allows activation policies to be defined in a flexible manner while maintaining separation between external RF conditions and host-device subsystem responses.
5.4. Replay and Signal Injection Considerations
Because the system reacts to RF field presence rather than to modulated command sequences, classical replay attacks targeting wireless communication protocols are not directly applicable. Nevertheless, an attacker may attempt to reproduce electromagnetic field conditions that resemble legitimate activation scenarios.
To address this possibility, the architecture introduces validation procedures within the trusted coordination domain. These procedures may include signal stability verification, contextual policy checks, or cryptographic validation performed by the secure element.
While such mechanisms cannot completely eliminate the possibility of malicious RF stimulation, they can significantly increase the difficulty of generating valid trigger conditions without satisfying the required policy constraints.
5.5. SIM Interface Isolation
The architecture interacts with the host mobile device through the standard SIM/UICC communication framework. Rather than directly controlling wireless hardware subsystems, the coordination interface generates structured events within the SIM interaction layer that may be interpreted by the host operating system.
This design preserves separation between the external RF detection domain and host device software components. Because the coordination layer does not require modification of the operating system or direct hardware control of wireless subsystems, it reduces the coupling between the external trigger mechanism and internal device firmware.
5.6. Policy Provisioning and Lifecycle Considerations
Activation policies and credentials stored within the secure element are expected to be provisioned during a trusted initialization phase, such as device enrollment or manufacturing configuration. Policies may include threshold parameters, authorization keys, or contextual activation rules.
In practical deployments, policy updates could be performed through authenticated management channels using secure element update mechanisms or SIM management infrastructure. Revocation or modification of policies may therefore be implemented through cryptographically authenticated update procedures.
A potential attack scenario involves physical replacement of the SIM-compatible activation substrate with a malicious device that always authorizes external RF fields. In realistic deployments, such risks may be mitigated through device-bound credentials, backend authentication mechanisms, or attestation procedures that verify the authenticity of the activation interface before accepting trigger events.
5.7. Example Policy Logic
Activation policies implemented within the secure element may follow simple deterministic rules designed to prevent unauthorized triggering. Examples of such policies may include:
- minimum RF field-strength thresholds to avoid activation by weak or distant sources;
- contextual constraints such as time-of-day or device-state conditions;
- challenge–response authentication sequences with authorized external tags;
- replay-protection mechanisms based on nonce validation or session freshness checks.
Such policy mechanisms allow the trusted coordination domain to evaluate activation conditions before generating a trigger event for the host device.
5.8. Residual Risks and Limitations
Despite the architectural precautions described above, several residual risks remain. As with any passive RF detection system, intentional electromagnetic interference could suppress or disturb detection events. Additionally, physical access to the SIM tray could allow removal or replacement of the interface module.
Furthermore, the ultimate response to a SIM-originated trigger event depends on the host device operating system and telephony stack implementation. Platform-specific behavior may therefore influence how such events are interpreted in practice.
These limitations highlight that the proposed coordination architecture should be viewed as one component within a broader mobile-device security ecosystem rather than as a standalone protection mechanism.
5.9. Side-Channel Considerations
Like any secure element-based architecture, the proposed design may be subject to potential side-channel leakage through power consumption or timing behavior during activation events. Although such attacks typically require specialized laboratory equipment and physical proximity, they represent a relevant research direction for future security evaluation.
The present work focuses on architectural design and coordination mechanisms; detailed side-channel resistance analysis of the secure element and activation controller remains a topic for future experimental study.
6. Comparative Analysis and Discussion
6.1. Architectural Comparison with Existing Approaches
The proposed SIM-compatible coordination interface can be conceptually positioned between three dominant architectural approaches currently used for proximity-triggered wireless activation:
- 1.
- Antenna-integrated SIM architectures embedding contactless RF transceivers;
- 2.
- External wireless modules providing BLE-based activation;
- 3.
- Software-driven activation mechanisms implemented at the operating-system level.
Antenna-integrated SIM solutions typically incorporate active RF front-ends, modulation circuitry, and bidirectional protocol stacks that allow direct wireless communication with external readers. While such architectures enable rich interaction scenarios, they also increase hardware complexity and expand the RF communication surface.
External BLE activation modules represent another common approach. These modules integrate independent wireless transceivers and antennas that communicate with the host device through peripheral interfaces. Although flexible, this strategy duplicates radio hardware already present in modern smartphones and introduces additional power-management requirements.
Software-based activation mechanisms rely entirely on operating-system services, application-layer APIs, or middleware logic to control wireless subsystem behavior. While easy to deploy, such approaches inherently depend on the integrity and availability of the host software environment.
In contrast, the architecture proposed in this work introduces a passive RF detection layer combined with hardware-level validation within a trusted coordination domain. Instead of embedding an additional wireless transceiver, the interface conceptually acts as a trigger-generation layer that interacts with the SIM/UICC framework while leaving all wireless communication tasks to the host device.
Table 1 summarizes the architectural differences between these approaches.
Table 1.
Architectural comparison with representative alternative approaches.
6.2. Power, Integration, and Mechanical Trade-Offs
Architectural simplification has direct implications for energy efficiency and mechanical integration.
Because the proposed interface does not include active RF transmission stages or embedded BLE hardware, the power consumption profile is primarily determined by passive RF detection and validation operations within the trusted coordination domain. Under conceptual operating assumptions, standby current may remain within ultra-low-power regimes, while event-driven activation currents remain within typical nano-SIM power budgets.
From a mechanical perspective, the interface is designed to operate within the dimensional constraints of the nano-SIM (4FF) form factor. Maintaining compatibility with ISO/IEC 7816 contact geometry allows the coordination layer to coexist with a conventional SIM card inside existing SIM trays without modification of smartphone hardware.
In contrast, external BLE modules generally require additional enclosure space, power routing, and peripheral communication channels. Antenna-integrated SIM solutions may also increase structural complexity due to the integration of active transceiver components and RF matching networks.
The principal trade-off of the simplified architecture is the absence of bidirectional RF communication capability. Instead of exchanging structured wireless commands, the interface relies on passive field detection combined with internal validation logic to determine when activation events should be generated.
6.3. Security Surface and Design Trade-Offs
From a system security perspective, architectural simplicity can influence the size and structure of the potential attack surface.
Solutions incorporating active RF transceivers typically introduce wireless protocol stacks that must parse incoming frames, manage communication sessions, and support firmware updates. Each additional communication layer may introduce potential vulnerabilities depending on implementation details.
External BLE modules similarly rely on pairing procedures, wireless session management, and coexistence with other wireless subsystems operating in the same spectrum.
Software-driven activation approaches depend on the integrity of the operating system and application-layer components, which may be affected by privilege escalation vulnerabilities or compromised device firmware.
The architecture proposed in this work conceptually reduces some of these dependencies by avoiding the integration of active wireless transceivers and by limiting internal logic to event validation within the trusted coordination domain. Because wireless communication remains entirely within the host device’s native subsystem, the coordination interface itself does not implement additional RF protocol stacks.
Nevertheless, such simplification introduces functional limitations. In particular, the interface does not support structured RF command exchange or remote firmware updates, and therefore cannot provide the same degree of configurability as more complex wireless modules.
6.4. Broader Architectural Implications
Beyond the specific activation scenario considered in this study, the presented architecture illustrates how SIM/UICC interfaces may potentially be repurposed as hardware coordination layers within mobile-device ecosystems.
By combining passive RF detection, secure element validation, and SIM-level signaling mechanisms, the SIM slot may conceptually act as a bridge between external physical events and internal wireless subsystems. Such coordination mechanisms could support proximity-triggered services, low-energy authentication workflows, or hardware-mediated IoT interactions without introducing additional wireless transmitters.
While further experimental and system-level evaluation would be required for real-world deployment, the proposed design highlights a potential architectural direction in which SIM-based hardware interfaces extend beyond traditional subscriber identity management and participate in broader device-level coordination frameworks.
7. Limitations and Future Work
7.1. Architectural and Operational Constraints
While the proposed SIM-compatible coordination architecture illustrates a potential approach for RF-triggered interaction with mobile devices, several limitations should be acknowledged.
First, the architecture operates exclusively in passive RF detection mode and does not support bidirectional RF communication or structured command exchange. Activation is therefore based on validated field presence rather than protocol-level negotiation. While this simplification reduces architectural complexity, it also limits functional flexibility compared with full transceiver-based solutions.
Second, the coordination interface generates a SIM-domain trigger event but does not directly control BLE stack configuration, pairing policies, or higher-layer application logic. The ultimate response to such trigger events therefore depends on the host device operating system and telephony framework implementation.
Finally, variations in SIM electrical characteristics, telephony stack behavior, and device-specific firmware policies across smartphone platforms may influence how trigger events are interpreted. As a result, system-level behavior may vary between device vendors and operating-system environments.
The limited physical footprint of the nano-SIM (4FF) form factor also imposes constraints on antenna geometry and achievable inductive coupling. The effectiveness of LF and HF detection structures may therefore depend on the specific smartphone enclosure design, SIM tray materials, and proximity of other RF subsystems. Detailed antenna characterization and optimization across diverse device platforms remain topics for future experimental work.
7.2. Environmental and Security Scope Limitations
Passive RF detection performance may be influenced by device-specific electromagnetic environments. Smartphone enclosure materials, internal shielding structures, and the proximity of other RF subsystems may affect antenna coupling characteristics and detection thresholds.
Although design strategies such as ferrite stabilization and impedance conditioning may improve coupling consistency, comprehensive evaluation across diverse commercial smartphone platforms would be required to fully characterize environmental variability.
From a security perspective, the present work focuses primarily on architectural security considerations associated with hardware-isolated trigger validation. Detailed adversarial modeling, side-channel analysis, and fault-injection resilience have not been explored in depth and remain topics for future investigation.
7.3. Future Research Directions
Several research directions may extend the proposed architecture:
- adaptive RF detection threshold calibration for heterogeneous electromagnetic environments;
- advanced secure element policy logic enabling contextual activation decisions;
- integration with emerging eSIM infrastructures and trusted execution environments;
- formal timing and energy modeling of trigger-event propagation;
- large-scale validation across heterogeneous smartphone platforms and industrial deployment scenarios.
Future research will also include experimental validation of the proposed coordination architecture. Prototype-level implementations and controlled laboratory studies will be conducted to evaluate RF detection robustness, trigger propagation latency, and energy characteristics across different smartphone platforms. Such empirical evaluation will complement the present architectural analysis and provide quantitative insight into practical deployment feasibility.
More broadly, the concept of the SIM slot functioning as a hardware coordination interface suggests new possibilities for secure wake-up architectures and proximity-triggered interaction models in mobile and IoT ecosystems.
8. Conclusions
This work presented a SIM-compatible coordination architecture intended to support secure hardware-mediated activation scenarios in mobile devices based on passive RF field detection. In contrast to antenna-integrated SIM solutions embedding active contactless transceivers, the proposed design concept avoids RF transmission stages, redundant BLE hardware, and independent energy sources.
The presented approach reinterprets the SIM slot as a hardware coordination interface rather than a wireless communication endpoint. Passive LF (125–134 kHz) and HF (13.56 MHz) electromagnetic field detection is conceptually combined with a hardware-isolated trusted coordination domain comprising a lightweight control unit and a secure element. Following policy validation within this domain, a SIM-level trigger event may propagate through existing telephony pathways and potentially activate the host device’s native BLE subsystem, which subsequently manages wireless communication through its standard protocol stack.
Architectural analysis suggests that such an approach may enable low-power proximity-triggered activation mechanisms while remaining compatible with nano-SIM (4FF) mechanical and electrical constraints. By avoiding embedded wireless transceivers and minimizing runtime logic within the SIM execution environment, the proposed architecture may reduce additional RF attack surface exposure while maintaining predictable activation behavior within a hardware-isolated coordination domain.
More broadly, the presented concept highlights the potential of SIM-based hardware interfaces to function not only as subscriber identity modules but also as coordination layers connecting external physical events with internal wireless subsystems of mobile devices. Such coordination-oriented architectures may support energy-efficient proximity-triggered services, secure mobile interactions, and embedded IoT activation scenarios.
Future work will focus on prototype implementation and experimental validation of the proposed architecture, including evaluation of RF detection robustness, trigger propagation latency, and system-level energy characteristics across multiple smartphone platforms. These experiments will provide empirical insights into the feasibility and portability of SIM-compatible RF-triggered coordination mechanisms.
This research was conducted within the framework of the national research project BR24993072 (Ministry of Science and Higher Education of the Republic of Kazakhstan), which investigates secure digital infrastructures and intelligent edge-system architectures. The presented coordination architecture contributes to the exploration of trusted mobile interaction mechanisms and hardware-rooted activation models for next-generation embedded and mobile systems.
Author Contributions
Conceptualization, A.K.; methodology, A.K. and Z.M.; software, Z.M.; validation, Z.M. and A.K.; formal analysis, A.K.; investigation, A.K.; resources, A.A.; data curation, Z.M.; writing—original draft preparation, A.K.; writing—review and editing, A.A.; visualization, Z.M.; supervision, A.K.; project administration, A.A.; funding acquisition, A.K. All authors have read and agreed to the published version of the manuscript.
Funding
This research was funded by the Committee of Science of the Ministry of Science and Higher Education of the Republic of Kazakhstan (Grant No. BR24993072).
Institutional Review Board Statement
Not applicable.
Informed Consent Statement
Not applicable.
Data Availability Statement
No new data were created or analyzed in this study. All relevant data supporting the findings are included within the article.
Acknowledgments
During the preparation of this manuscript, the authors used ChatGPT (OpenAI, GPT-5.3; https://chat.openai.com; accessed on 1 March 2026) exclusively for language translation and linguistic refinement. All scientific ideas, methodology, analysis, system design, and conclusions were developed independently by the authors. The authors have carefully reviewed and edited all generated text and take full responsibility for the content of this publication.
Conflicts of Interest
The authors declare no conflicts of interest. The funders had no role in the design of the study; in the collection, analyses, or interpretation of data; in the writing of the manuscript; or in the decision to publish the results.
Abbreviations
The following abbreviations are used in this manuscript:
| SIM | Subscriber Identity Module |
| eSIM | Embedded Subscriber Identity Module |
| NFC | Near Field Communication |
| RFID | Radio Frequency Identification |
| BLE | Bluetooth Low Energy |
| PKI | Public Key Infrastructure |
| ECC | Elliptic Curve Cryptography |
| PQC | Post-Quantum Cryptography |
| RSP | Remote SIM Provisioning |
| TSM | Trusted Service Manager |
| HCE | Host Card Emulation |
| GBA | Generic Bootstrapping Architecture |
| IoT | Internet of Things |
| WSN | Wireless Sensor Network |
| DoS | Denial of Service |
| MITM | Man-in-the-Middle |
| CRFID | Chipless Radio Frequency Identification |
| SAW | Surface Acoustic Wave |
| API | Application Programming Interface |
References
- Oliveira, F.; Costa, D.G.; Assis, F.; Silva, I. Internet of Intelligent Things: A Convergence of Embedded Systems, Edge Computing and Machine Learning. Internet Things 2024, 26, 101153. [Google Scholar] [CrossRef] [Scilit]
- de Reuver, M.; Ondrus, J. When technological superiority is not enough: The struggle to impose the SIM card as the NFC secure element for mobile payment platforms. Telecommun. Policy 2017, 41, 253–262. [Google Scholar] [CrossRef] [Scilit]
- Kong, L.; Qian, Z.; Xu, L.; Yang, J.; Shao, Q. A Trusted Authentication Scheme Based on Super SIM Card for Mobile Office for Industry 4.0. Neural Comput. Appl. 2023, 35, 21525–21533. [Google Scholar] [CrossRef] [Scilit]
- Niu, R.; Jia, Z.; Liu, Y.; Lin, J.; Huang, X.; Sun, M. Enhanced 4A Identity Authentication Center Based on Super SIM Technology. In Smart Computing and Communication; Lecture Notes in Computer Science; Springer: Cham, Switzerland, 2023. [Google Scholar] [CrossRef] [Scilit]
- Dhanesh, A.; K., J.; Jayaraj, M.; Antony, N.J.; George, A.T. Evolution of SIM and eSIM Security: Authentication, Fraud, and Emerging Defenses. Int. J. Sci. Res. Eng. Manag. 2025, 9, 1–9. [Google Scholar] [CrossRef] [Scilit]
- Subramanian, S.N.; Jain, K.; Krishnan, P.; Prabu, P.; Ganeshkumar, P. Embedded SIM (eSIM) Based PQC-Enabled Authentication and Provisioning Techniques for Enhancing Security in Edge-Based IoT Ecosystem. IEEE Trans. Consum. Electron. 2025, 71, 11183–11197. [Google Scholar] [CrossRef] [Scilit]
- ISO/IEC 7816-4; Identification Cards—Integrated Circuit Cards—Part 4: Organization, Security and Commands for Interchange. International Organization for Standardization: Geneva, Switzerland, 2020.
- Sportiello, L. “Internet of Smart Cards”: A Pocket Attacks Scenario. Int. J. Crit. Infrastruct. Prot. 2019, 26, 100302. [Google Scholar] [CrossRef] [Scilit]
- Boruchinkin, A.; Tolstaya, A.; Zhgilev, A. Cryptographic Wireless Communication Device. Procedia Comput. Sci. 2018, 123, 110–115. [Google Scholar] [CrossRef] [Scilit]
- Akram, R.N.; Markantonakis, K.; Sauveron, D. Recovering from a Lost Digital Wallet: A Smart Cards Perspective Extended Abstract. Pervasive Mob. Comput. 2016, 29, 113–129. [Google Scholar] [CrossRef] [Scilit]
- Druml, N.; Schilling, J.; Pachler, W.; Roitner, B.; Ruprechter, T.; Bock, H.; Holweg, G. Secured miniaturized system-in-package contactless and passive authentication devices featuring NFC. Microprocess. Microsyst. 2017, 53, 120–129. [Google Scholar] [CrossRef] [Scilit]
- Druml, N.; Menghin, M.; Kuleta, A.; Steger, C.; Weiss, R.; Bock, H. A Flexible and Lightweight ECC-Based Authentication Solution for Resource Constrained Systems. In Proceedings of the 17th Euromicro Conference on Digital System Design (DSD), Verona, Italy, 27–29 August 2014. [Google Scholar] [CrossRef] [Scilit]
- Asavanarakul, P.; Ruengwaree, A.; Sakulchat, S. Graphene-Based RFID Tag Antenna for Vehicular Smart Border Passings. Comput. Mater. Continua 2022, 71, 4737–4748. [Google Scholar] [CrossRef] [Scilit]
- Shen, X.; Shi, G.; Cheng, L.; Gu, L.; Rao, Y.; He, Y. Chipless RFID-inspired sensing for smart agriculture: A review. Sens. Actuators A Phys. 2023, 363, 114725. [Google Scholar] [CrossRef] [Scilit]
- Scidà, A.; Haque, S.; Treossi, E.; Robinson, A.; Smerzi, S.; Ravesi, S.; Borini, S.; Palermo, V. Application of graphene-based flexible antennas in consumer electronic devices. Mater. Today 2018, 21, 223–230. [Google Scholar] [CrossRef] [Scilit]
- ISO/IEC 15693-3; Cards and Security Devices for Personal Identification—Contactless Vicinity Objects—Part 3: Anticollision and Transmission Protocol. International Organization for Standardization: Geneva, Switzerland, 2019.
- Rongyu, H.; Guolei, Z.; Chaowen, C.; Hui, X.; Xi, Q.; Zheng, Q. A PK-SIM card based end-to-end security framework for SMS. Comput. Stand. Interfaces 2009, 31, 629–641. [Google Scholar] [CrossRef] [Scilit]
- Yang, T.-W.; Ho, Y.-H.; Chou, C.-F. Achieving M2M-device authentication through heterogeneous information bound with USIM card. Future Gener. Comput. Syst. 2020, 110, 629–637. [Google Scholar] [CrossRef] [Scilit]
- Ko, Y.; Lastre, J.K.; Kwon, H.; You, I. Revisiting the M2M remote SIM provisioning protocol: A comprehensive security and performance analysis. Alexandria Eng. J. 2026, 135, 1–19. [Google Scholar] [CrossRef] [Scilit]
- Rossudowski, A.M.; Venter, H.S.; Eloff, J.H.P.; Kourie, D.G. A security privacy aware architecture and protocol for a single smart card used for multiple services. Comput. Secur. 2010, 29, 393–409. [Google Scholar] [CrossRef] [Scilit]
- Tsai, H.-C.; Chang, C.-C.; Chang, K.-J. Roaming across wireless local area networks using SIM-based authentication protocol. Comput. Stand. Interfaces 2009, 31, 381–389. [Google Scholar] [CrossRef] [Scilit]
- Tsai, Y.-R.; Chang, C.-J. SIM-based subscriber authentication mechanism for wireless local area networks. Comput. Commun. 2006, 29, 1744–1753. [Google Scholar] [CrossRef] [Scilit]
- Dantu, R.; Clothier, G.; Atri, A. EAP Methods for Wireless Networks. Comput. Stand. Interfaces 2007, 29, 289–301. [Google Scholar] [CrossRef] [Scilit]
- Odelu, V.; Das, A.K.; Goswami, A. An efficient ECC-based privacy-preserving client authentication protocol with key agreement using smart card. J. Inf. Secur. Appl. 2015, 21, 1–19. [Google Scholar] [CrossRef] [Scilit]
- Davis, M.L. Contactless smart cards: Dumb (and dangerous) ways to use them. Card Technol. Today 2007, 19, 12–14. [Google Scholar] [CrossRef] [Scilit]
- Saritas, H.B.; Kardas, G. A model driven architecture for the development of smart card software. Comput. Lang. Syst. Struct. 2014, 40, 53–72. [Google Scholar] [CrossRef] [Scilit]
- Hamadouche, S.; Lanet, J.-L. Virus in a smart card: Myth or reality? J. Inf. Secur. Appl. 2013, 18, 130–137. [Google Scholar] [CrossRef] [Scilit]
- Barbosa, G.; Endo, P.T.; Sadok, D. An internet of things security system based on grouping of smart cards managed by field programmable gate array. Comput. Electr. Eng. 2019, 74, 331–348. [Google Scholar] [CrossRef] [Scilit]
- Bouffard, G.; Lanet, J.-L. The ultimate control flow transfer in a Java based smart card. Comput. Secur. 2015, 50, 33–46. [Google Scholar] [CrossRef] [Scilit]
- Catuogno, L.; Gassirà, R.; Masullo, M.; Visconti, I. SmartK: Smart cards in operating systems at kernel level. Inf. Secur. Tech. Rep. 2013, 17, 93–104. [Google Scholar] [CrossRef] [Scilit]
- Kamel, N.; Lanet, J.-L. Risks induced by Web applications on smart cards. J. Inf. Secur. Appl. 2013, 18, 148–156. [Google Scholar] [CrossRef] [Scilit]
- Moore, S.; Anderson, R.; Mullins, R.; Taylor, G.; Fournier, J.J.A. Balanced self-checking asynchronous logic for smart card applications. Microprocess. Microsyst. 2003, 27, 421–430. [Google Scholar] [CrossRef] [Scilit]
- Leng, X. Smart card applications and security. Inf. Secur. Technol. Rep. 2009, 14, 36–45. [Google Scholar] [CrossRef] [Scilit]
- Markantonakis, K.; Tunstall, M.; Hancke, G.; Askoxylakis, I.; Mayes, K. Attacking smart card systems: Theory and practice. Inf. Secur. Technol. Rep. 2009, 14, 46–56. [Google Scholar] [CrossRef] [Scilit]
- Ji, Y.; Zheng, S. Distributed Mode-Dependent Event-Triggered Passive Filtering for Flexible Manipulator with Semi-Markov Parameters. Sensors 2021, 21, 2058. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- D’Addato, M.; Antolini, A.; Renzini, F.; Elgani, A.M.; Perilli, L.; Franchi Scarselli, E.; Gnudi, A.; Magno, M.; Canegallo, R. Nanowatt Clock and Data Recovery for Ultra-Low Power Wake-Up Based Receivers. In Proceedings of the 2020 International Conference on Embedded Wireless Systems and Networks (EWSN), Lyon, France, 17–19 February 2020; pp. 224–229. [Google Scholar]
- Wang, S.; Odelberg, T.J.; Crary, P.W.; Obery, M.P.; Wentzloff, D.D. Low-Power Wake-Up Receivers for Resilient Cellular Internet of Things. Information 2025, 16, 43. [Google Scholar] [CrossRef] [Scilit]
- Fromm, R.; Kanoun, O.; Derbel, F. An Improved Wake-Up Receiver Based on the Optimization of Low-Frequency Pattern Matchers. Sensors 2023, 23, 8188. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Maistriaux, P.; Gonzalez, M.; Louveaux, J.; Bol, D. Leveraging a Digital Chirp Spread Spectrum Detector for LPWAN Wake-Up Receivers. In Proceedings of the 2024 14th International Symposium on Communication Systems, Networks and Digital Signal Processing (CSNDSP), Rome, Italy, 17–19 July 2024. [Google Scholar] [CrossRef] [Scilit]
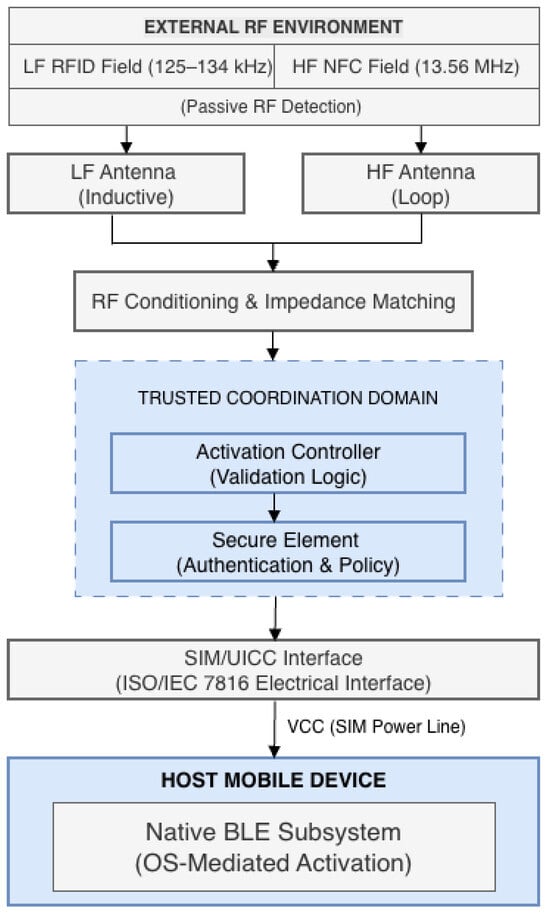
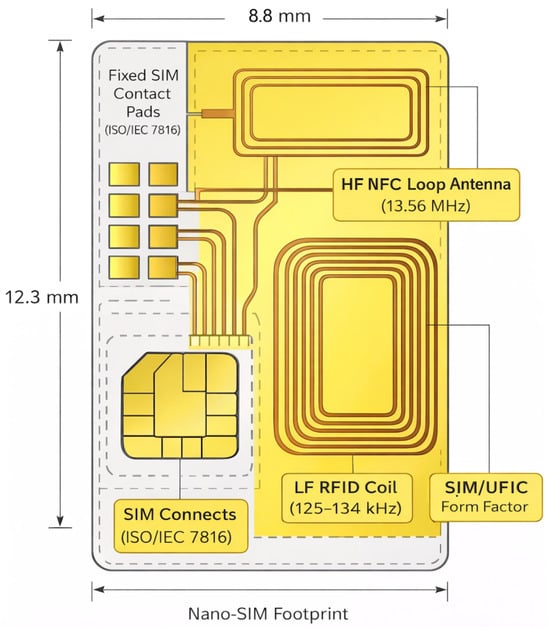
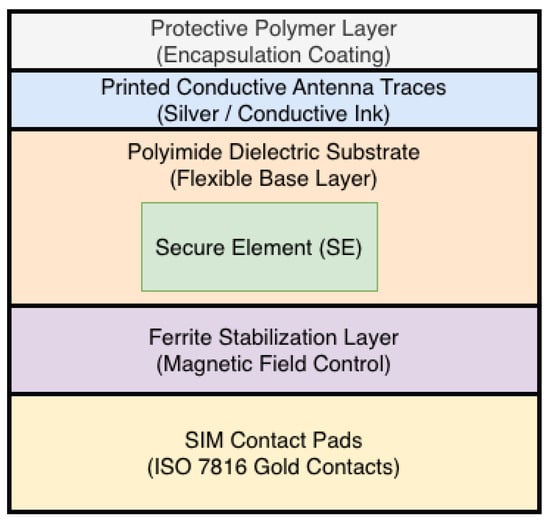
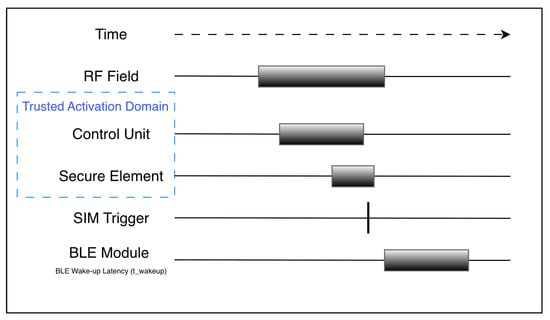
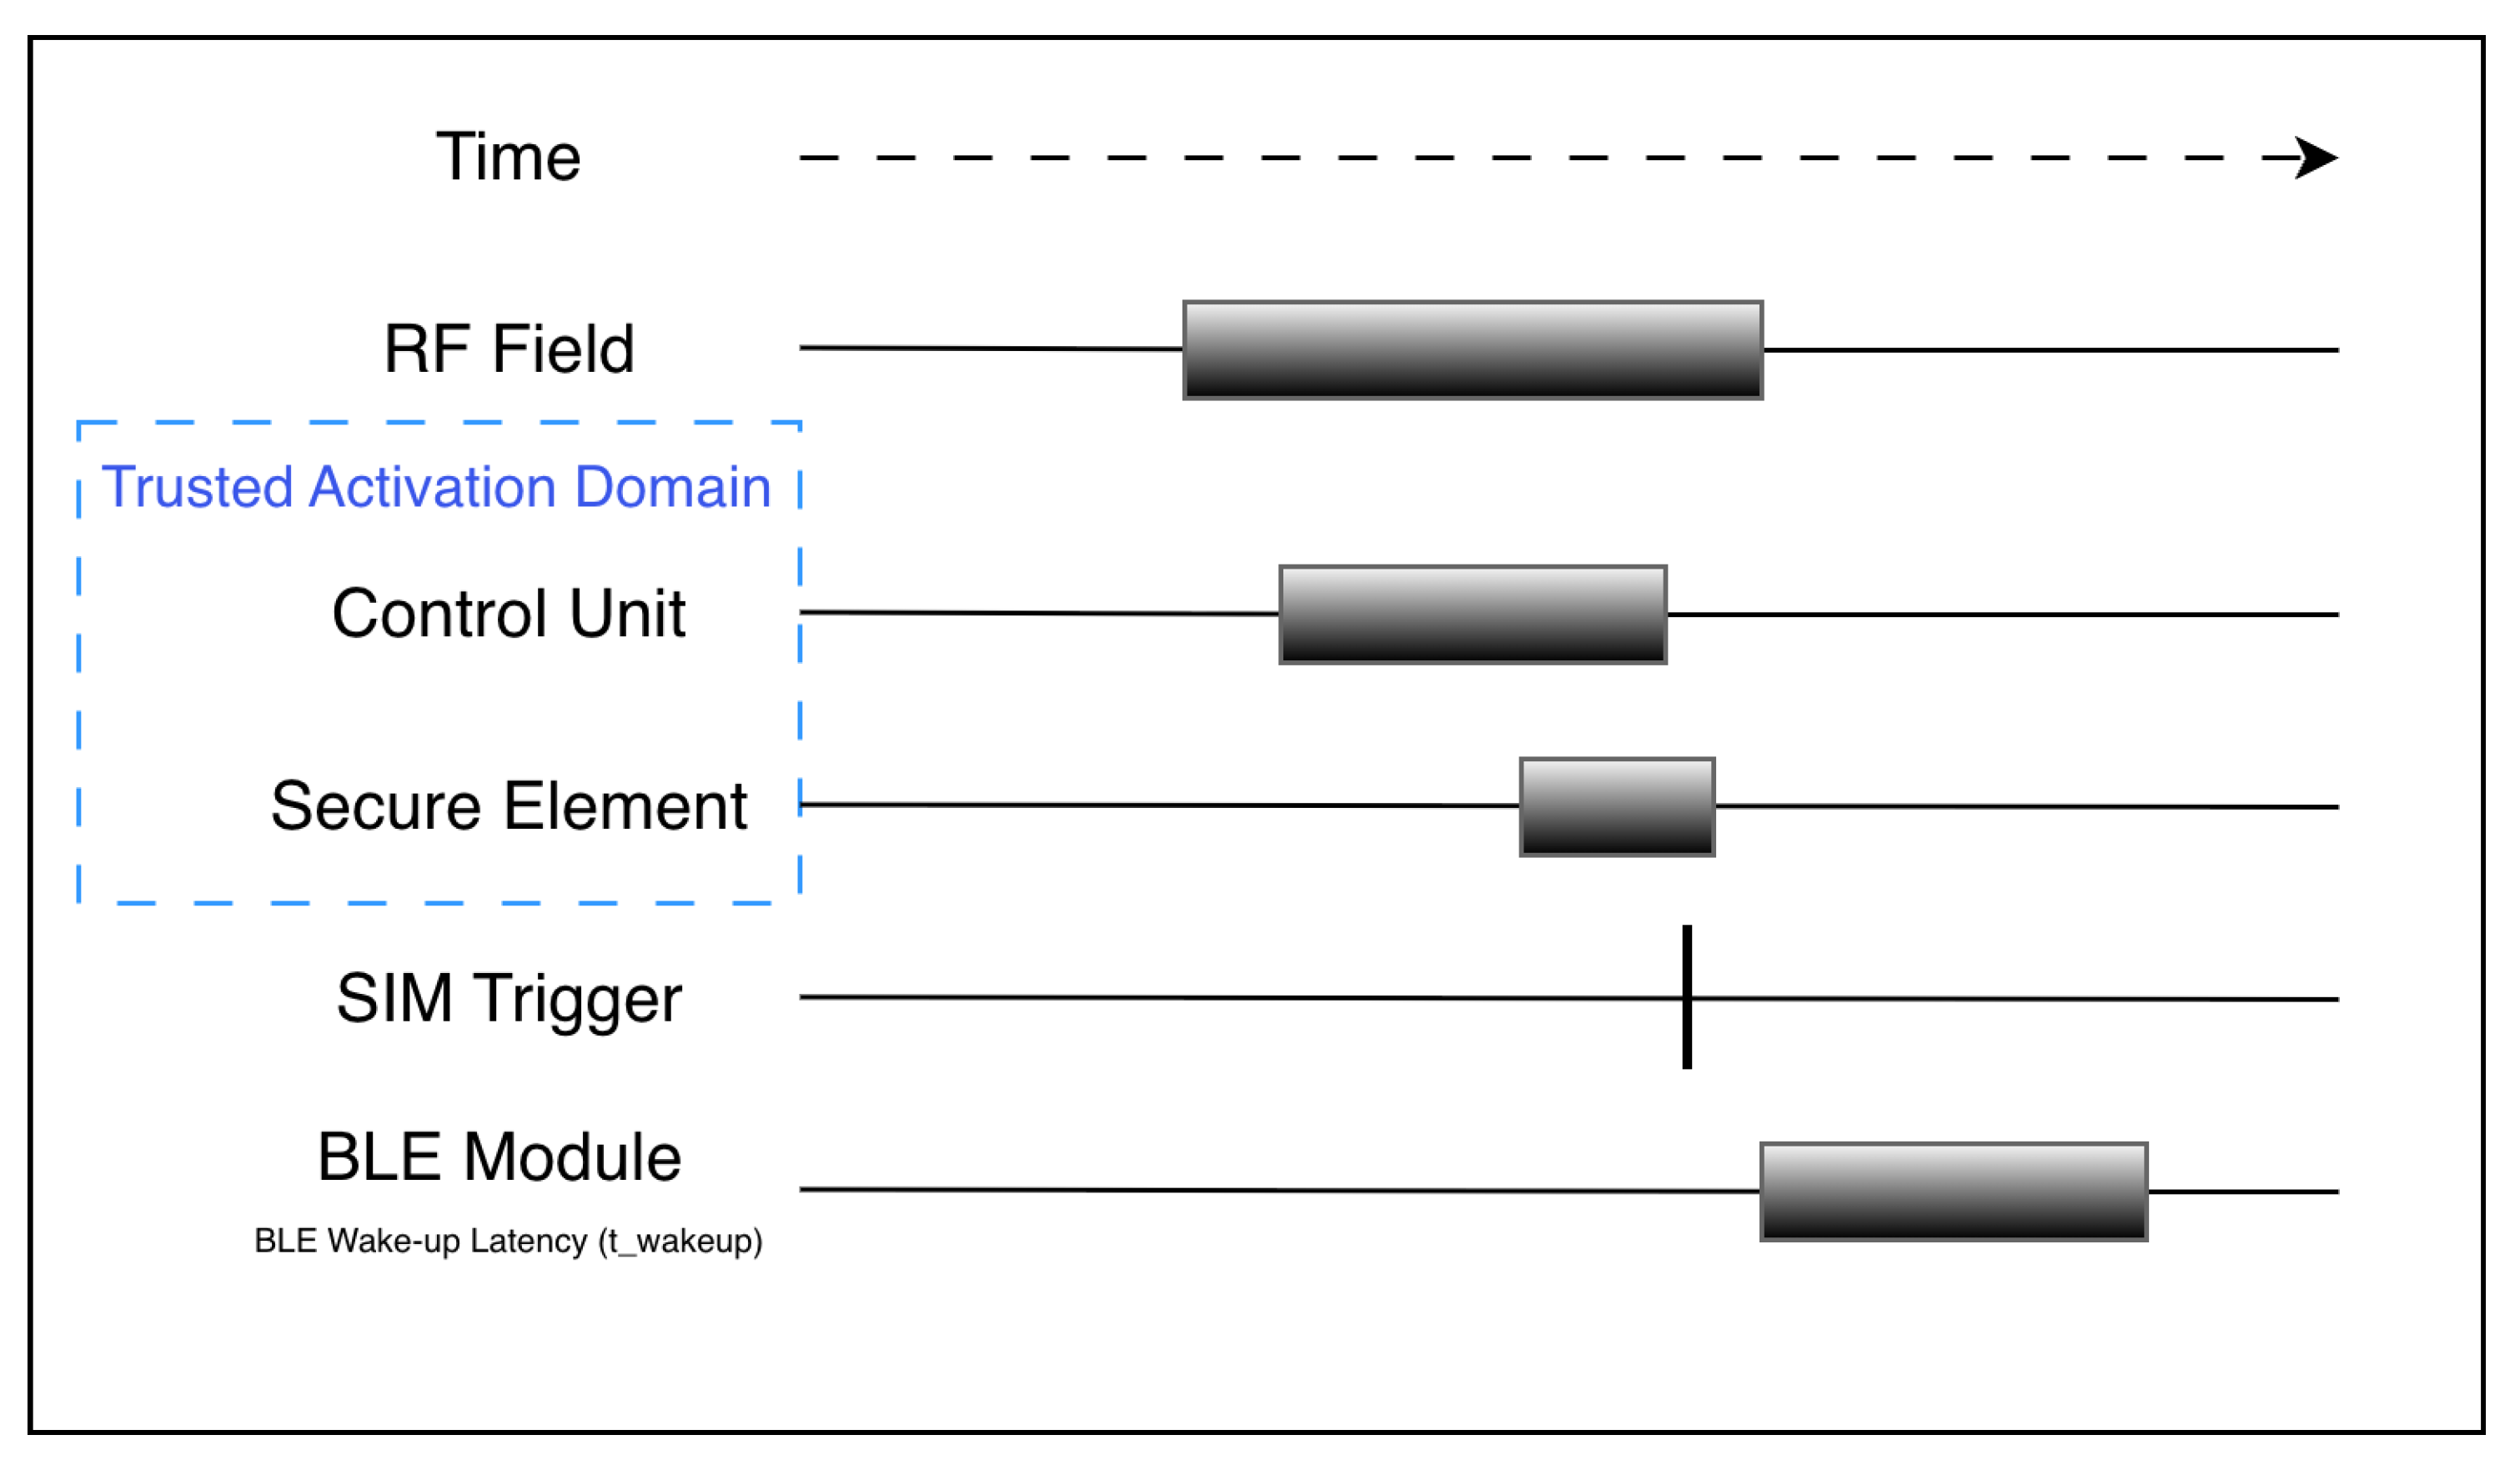

Disclaimer/Publisher’s Note: The statements, opinions and data contained in all publications are solely those of the individual author(s) and contributor(s) and not of MDPI and/or the editor(s). MDPI and/or the editor(s) disclaim responsibility for any injury to people or property resulting from any ideas, methods, instructions or products referred to in the content. |
© 2026 by the authors. Licensee MDPI, Basel, Switzerland. This article is an open access article distributed under the terms and conditions of the Creative Commons Attribution (CC BY) license.