


Abstract
In today’s dynamic business environment, organizations are increasingly investing in strategies to protect themselves against information system violations. While these technologies offer remarkable benefits—boosting efficiency, productivity, and overall performance—they also bring significant risks, particularly regarding information security breaches. This study delves into the critical connections between technostress, techno-strain, and the violation of information security policies. Our research aims to shed light on how technostress, which is commonly experienced by engineers working in technology-intensive environments within the IT sector, drives information security violations. Importantly, we will also explore how techno-strain mediates this relationship. By focusing on engineers who are consistently engaged with advanced technology, we seek to answer essential questions about their experiences. It is worth noting that the requirements for information security technology can widely vary based on factors such as industry type, organizational structure, departmental roles, and cultural norms. Therefore, this study examines how technostress increases the likelihood of information security policy violations and how techno-strain mediates this relationship. Looking ahead, future research should consider both the broader institutional contexts and the individual characteristics that may shape the relationship between information security violations and technostress. Furthermore, understanding the repercussions of information security violations—stemming from technostress—on a company’s financial health is vital for organizations aiming to safeguard their assets and maintain a competitive edge. Emphasizing these insights can lead to more effective strategies for managing both technology and talent in the workplace.
1. Introduction
In today’s highly digitalized organizations, technological capability is no longer a differentiator; it has become a basic requirement. The accelerated proliferation of cloud computing, artificial intelligence (AI), the Internet of Things (IoT), and information and communication technologies (ICT) has changed how organizations create value, make decisions, and operate [1,2,3]. While these innovations offer greater speed and efficiency, they also introduce risks that extend beyond IT departments. Despite massive investments in encryption protocols, firewalls, and threat detection systems, cyberattacks have escalated in both frequency and severity—compromising critical infrastructure, paralyzing operations, and exposing the personal data of millions [4,5].
Contrary to the prevailing notion that these breaches stem primarily from technical malfunctions or malicious external actors, recent studies point to another important source of vulnerability: the human factor. Employees who are cognitively overloaded, emotionally depleted, or lack organizational support may unintentionally engage in behaviors that compromise security, such as clicking phishing links, ignoring updates, or bypassing security procedures [6,7,8]. As such, cybersecurity is increasingly seen not only as a technical issue but also as a behavioral one. Recent studies have begun exploring how organizational stressors, digital fatigue, and emotional strain contribute to employees’ noncompliance with information security policy violations (ISPV) [9,10,11].
An important yet relatively underexplored concept in this context is technostress, referring to technology-related demands such as overload, invasion, and complexity [12,13]. In workplaces saturated with system alerts, task-switching pressures, and rapid technological changes, these stressors trigger techno-strain—the internal psychological response which can make it difficult to maintain consistent security attention [14,15]. While technostress has been extensively linked to burnout, job dissatisfaction, and performance decrements [16,17], its behavioral consequences for cybersecurity compliance—particularly ISPV—remain largely unexamined and theoretically fragmented [18,19,20,21], failing to account for both the psychological mechanisms and direct behavioral triggers like compliance friction.
To address this critical gap, the present study introduces a dual-theoretical framework that integrates the Transactional Model of Stress and Coping (TMS) [22] with the Conservation of Resources (COR) theory [23]. TMS offers a cognitive–relational perspective, which focuses on how individuals evaluate whether a situation can be managed and select coping strategies accordingly, such as problem-focused or emotion-focused responses. COR theory, by contrast, provides a motivational lens—asserting that individuals strive to acquire, retain, and protect valued resources, and that stress arises from resource loss or the threat thereof. When combined, these frameworks offer a holistic explanation: technostress emerges not only from perceived digital demands (TMS) but also from the progressive depletion of cognitive, emotional, and temporal resources (COR), with techno-strain—the internal experience of exhaustion and overwhelm—acting as a critical mediating force between environmental stressors and behavioral outcomes.
This theoretical synthesis enables a novel understanding of why employees under technostress may violate security policies. From a COR standpoint, individuals experiencing chronic resource erosion often resort to psychologically defensive coping behaviors—as a way to manage limited time and cognitive resources. Actions such as bypassing login procedures, disabling notifications, or ignoring security prompts may thus reflect a form of “adaptive deviance” in resource-scarce environments [24]. Accordingly, this study examines whether technostress increases the likelihood of ISPV, and whether techno-strain plays a mediating role in the relationship between technostress and ISPV. Using a scenario-based survey design that simulates realistic security dilemmas, the study develops a psychologically grounded, behaviorally sensitive model of security noncompliance. In this way, it not only deepens our understanding of the stress–security nexus but also contributes to the emerging discourse on human-centered cybersecurity by showing how everyday decisions under pressure can lead to security risks.
Theoretical Background and Hypothesis Development
The widespread integration of information and communication technologies (ICT) into modern workplaces has changed how employees perform their tasks. While these technologies improve operational efficiency, they also introduce cognitive and emotional demands that may exceed individuals’ ability to cope, potentially depleting valuable psychological and cognitive resources over time [25]. In this context, technostress refers to the pressures associated with the use of digital technologies at work [26,27]. Over time, this concept has evolved into a multidimensional construct reflecting the psychological effects of working under continuous technological demands [17,28]. Research has consistently identified five primary stressors associated with technostress: techno-overload (the pressure to work faster or longer because of technology), techno-invasion (the erosion of work–life boundaries), techno-complexity (challenges in understanding and using new technologies), techno-uncertainty (frequent system changes and upgrades), and techno-insecurity (the fear of job loss due to automation or inadequate technological skills) [14,27]. These stressors require sustained cognitive and emotional effort and may gradually deplete internal resources such as attention, mental energy, and emotional resilience. As a result, employees may experience fatigue, frustration, and reduced attentional capacity—often described as techno-strain [29,30]. This process can be explained through the Transactional Model of Stress and Coping (TMS), which suggests that individuals evaluate whether environmental demands can be managed with their available coping resources. When perceived control is high, they are more likely to adopt problem-focused coping strategies; when control is low, they tend to rely on emotion-focused coping [22]. In technology-intensive environments, employees may perceive digital demands and security-related requirements as difficult to manage simultaneously, particularly under time pressure and frequent interruptions [31].
From a Conservation of Resources (COR) perspective, individuals aim to protect and preserve their limited personal resources, such as time, energy, and cognitive capacity, and stress arises when these resources are threatened or depleted [23]. As resource loss accumulates, individuals shift their focus from goal attainment to resource conservation, which may result in withdrawal or reduced engagement with additional demands [25]. In technology-intensive environments, this process helps to explain how sustained exposure to ICT-related demands translates into psychological strain. While TMS explains how such demands are appraised, COR clarifies why continued exposure leads to emotional exhaustion and reduced cognitive capacity. In this sense, techno-strain can be understood as the psychological outcome of ongoing stress appraisal and resource depletion. Empirical studies support this relationship, showing that high levels of technostress are associated with emotional fatigue, reduced attentional control, and burnout [17,32,33]. Rather than being a passive outcome, strain reflects a state in which individuals must actively manage limited cognitive and emotional resources. This perspective provides a basis for understanding how employees adjust their effort, attention, and priorities under conditions of technological pressure. Importantly, TMS suggests that coping responses depend not only on the presence of stressors but on how individuals evaluate their ability to manage these demands. In this sense, security-related requirements may be deprioritized when they are appraised as less controllable or less immediately relevant to task completion. Prior research on information security compliance has frequently relied on Protection Motivation Theory (PMT), which explains compliance behavior in terms of threat appraisal, self-efficacy, and motivational processes [34,35]. While this perspective is useful for understanding intentional compliance decisions, it offers limited insight into how individuals behave under conditions of cognitive overload and resource constraints. In contrast, the present study adopts a stress-based perspective by integrating TMS and Conservation of Resources (COR) theory to explain how technostress leads to resource depletion and cognitive fatigue. This approach provides a complementary explanation, suggesting that noncompliance may emerge not only from motivational deficits but also from the depletion of cognitive and emotional resources.
In contemporary digital workplaces, compliance with information security policies (ISPs) increasingly depends on employees’ discretionary decisions regarding whether to adhere to or bypass prescribed security procedures. Although organizations continue to invest heavily in advanced technological safeguards, the human factor remains a persistent source of vulnerability in protecting sensitive information. Violations of ISPs—such as bypassing secure login protocols, ignoring system updates, or engaging in risky online behaviors—often arise not from malicious intent but from the pressures embedded in digital work environments, including cognitive overload, time pressure, frequent interruptions, and emotional fatigue [18,36]. In such environments, employees are expected not only to perform their core tasks but also to comply with an expanding set of security requirements, many of which are experienced as effortful, disruptive, and misaligned with immediate performance objectives. These conditions are closely associated with technostress, which reflects the strain experienced when individuals struggle to cope with technology-related demands in their work environment [17,27]. A substantial body of research has conceptualized technostress as a multidimensional construct encompassing techno-overload, techno-invasion, techno-complexity, techno-uncertainty, and techno-insecurity [14,27]. As organizations adopt increasingly complex ICT systems, employees are required to manage multiple interfaces, process continuous streams of information, and respond to system-generated prompts under tight deadlines. While these systems are designed to enhance efficiency and resilience, they also introduce competing cognitive demands that may exceed individuals’ processing capacity. Insights from cognitive load theory suggest that when task demands exceed available cognitive resources, performance deteriorates and individuals are more likely to rely on simplified or heuristic responses [37,38]. Consequently, compliance-related tasks—such as managing complex passwords, completing multi-factor authentication, or carefully evaluating security warnings—may be perceived as cognitively demanding, time-consuming, and disruptive to workflow continuity. Under such conditions, employees may reallocate their attention toward primary job tasks while treating security compliance as a secondary priority.
The relationship between technostress and ISPV can be systematically understood within the stressor–strain–outcome (SSO) framework, in which technostress functions as the stressor, techno-strain represents the psychological response, and ISPV constitutes the behavioral outcome [39,40,41]. From the perspective of the Transactional Model of Stress and Coping (TMS), individuals engage in a cognitive appraisal process in which environmental demands are evaluated relative to available coping resources [22]. When technological demands are appraised as manageable, employees are more likely to adopt problem-focused coping strategies, such as complying with security protocols. However, when these demands are perceived as overwhelming or uncontrollable, individuals are more likely to experience psychological strain and rely on disengagement-oriented coping strategies. In digital work environments, where compliance requirements often interrupt task flow and impose additional cognitive effort, such appraisals may lead employees to interpret compliance as a nonessential burden rather than an integral component of their work. Complementing this cognitive perspective, Conservation of Resources (COR) theory explains how psychological strain translates into behavior. According to COR, individuals seek to protect and conserve their limited cognitive, emotional, and temporal resources, particularly under conditions of resource depletion [23]. As technostress accumulates and cognitive capacity becomes constrained, employees shift from performance optimization toward resource preservation. This shift often results in reduced engagement with tasks perceived as secondary or effortful, including compliance with ISPs [25]. In this sense, ISPV can be conceptualized not as deliberate misconduct, but as a resource-conserving coping response that emerges under conditions of cognitive and emotional depletion.
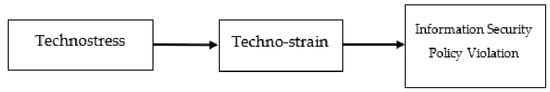
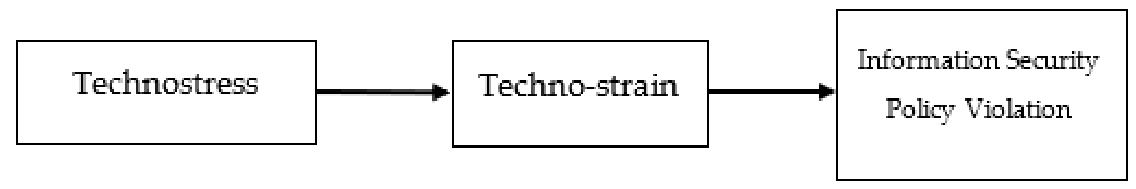
Importantly, this perspective departs from dominant security compliance models, particularly Protection Motivation Theory (PMT), which explains compliance behavior through threat appraisal, response efficacy, and self-efficacy [35,42,43]. While PMT effectively captures whether employees are motivated to comply, it assumes that individuals possess sufficient cognitive capacity to translate intentions into action. This assumption becomes problematic in technology-intensive environments characterized by cognitive overload and resource constraints. In contrast, the present study complements PMT by shifting the focus from motivation to capacity, emphasizing whether employees are cognitively able to comply under conditions of technostress. In this way, it highlights a critical limitation of motivation-based models in explaining behavior under conditions of resource depletion. Empirical evidence supports this integrated perspective. Prior studies demonstrate that employees experiencing techno-overload, time pressure, and cognitive fatigue are significantly more likely to bypass or ignore security procedures perceived as disruptive [44,45,46]. Similarly, psychological strain has been associated with reduced attentional control, impaired vigilance, and increased susceptibility to errors, all of which contribute to a higher likelihood of policy violations [47,48]. These findings suggest that techno-strain functions as a key cognitive–affective mechanism through which technological demands are translated into behavioral risks. Accordingly, techno-strain is expected to mediate the relationship between technostress and ISPV. However, extending prior research, this study further argues that technostress may also exert a direct effect on ISPV. Under conditions of high cognitive load and limited attentional capacity, employees may prioritize task completion over compliance, even in the absence of pronounced psychological strain. In such situations, noncompliance may arise from immediate cognitive constraints rather than deliberate coping processes, reflecting the bounded nature of human information processing in complex environments. Overall, this study reconceptualizes ISPV not merely as a failure of intention or motivation, but as a resource-conserving behavioral response shaped by cognitive constraints. By integrating TMS and COR within the SSO framework, it provides a comprehensive explanation that captures both cognitive appraisal processes and resource-based behavioral adjustments. In this way, the study advances the literature by demonstrating that security noncompliance may emerge not only from motivational deficits but also from the depletion of cognitive and emotional resources that constrain employees’ ability to comply in technology-intensive work environments (see Figure 1).
Figure 1.
Research Model.
H1.
The relationship between technostress and ISPV is mediated by techno-strain.
2. Materials and Methods
2.1. Research Design and Sample
The research model was empirically evaluated using a sample of people working in the field of information technology. The screening method was used to ensure that the participant sample, who intensively used all kinds of technologies such as desktop computers, laptops, tablets or smart devices, fulfilled their job duties. The data of the study was obtained through an online survey platform among the participants in Turkey who were eligible for the study. The total size of the information technology sector in Turkey was 152.7 billion dollars as of 2019, the total number of personnel working in the sector was around 143 thousand, with 77% of the total employment in the sector working in the field of information technologies. The study revealed that 70.8% of the participants were male and 29.4% were female, 94.5% of the participants had a university degree or higher qualification, 72% of them were employed as engineers, 50.5% of the participants had the opportunity to work remotely, and 81.1% of the participants were familiar with their institution’s information security policy. The size of the companies they worked for was also documented: 31.6% had between 1 and 10 employees, 10.3% had between 11 and 50 employees, 12.7% had between 51 and 100 employees, 14.4% had between 101 and 250 employees, and 30.9% had 251 employees or more. The mean age of the participants was 31.54 (SD = 5.97; min. 20; max. 58), and their total experience was 7.52 years (SD = 5.57; min. 1; max. 33). In this context, the present study was conducted with data obtained from 291 information technology employees from the provinces of Istanbul, Ankara, Izmir, Kocaeli, Trabzon and Gumushane in Turkiye.
2.2. Data Collection Tools
The measurement tools employed in this study were translated from English to Turkish and from Turkish to English, following Brislin’s [49] back-translation procedure. This method has been widely utilized in numerous studies in the relevant literature [50]. The study measured technostress, techno-strain, information security violations, and various demographic questions.
Technostress: The measurement of technostress was accomplished through the utilization of a 23-item scale developed by Tarafdar et al. [27]. This scale encompasses five distinct dimensions: Techno-Workload (5 items), Techno-Invasion (4 items), Techno-Complexity (5 items), Techno-Insecurity (5 items), and Techno-Uncertainty (5 items). The scale aligns with extant research in the field, as evidenced by its alignment with studies conducted by Tarafdar, Tu, and Ragu-Nathan [12], Wang, Shu, and Tu [51] and Fuglseth and Sørebø [52]. This conceptualization of techno-strain is also consistent with prior research examining security-related technostress and its organizational consequences [53]. It measures the extent to which employees are exposed to stress due to the technologies they use. Participants rated their agreement on a five-point Likert scale (1 = strongly disagree, 5 = strongly agree). Example items include “I am forced by technology to work much faster” (techno-overload) and “I feel constant pressure due to technology” (techno-overload). In the original study, Cronbach alpha values were 0.89, 0.81, 0.84, 0.84 and 0.82, respectively [27].
Techno-strain: The 4-item techno-strain scale adopted by Shadbad and Biros [2], which is a shortened version of Moore’s [54] 5-item job burnout questionnaire, was utilized. Responses to this questionnaire were evaluated on a 5-point Likert-type scale ranging from 1 (strongly disagree) to 5 (strongly agree). The sample items included the statements “I feel exhausted from my technology-related activities” and “Working with different technologies all day is a burden for me.” The original study reported a Cronbach alpha coefficient of 0.94 [2].
Information Security Policy Violation: The study utilized a “hypothetical scenario approach” to assess the dependent variable, a methodological choice that has been deemed effective [55]. This approach enables the evaluation of a wide range of information security breaches in the real world, as participants are tasked with role-playing these breaches. This technique involves the presentation of written descriptions of realistic situations to participants, who are then requested to provide responses using a series of rating scales that measure the dependent variables of interest [56]. The scenario method offers several advantages in terms of indirectly measuring the user’s intention to engage in unethical behavior to examine undesirable behaviors, providing situational details that influence decisions, and measuring behaviors prospectively with current perceptions [57]. In this regard, Shadbad and Biros [52] utilized six distinct scenarios to assess ISPV, encompassing password sharing, password typing, failure to log out, USB copying, data leakage and link clicking [18,57]. These six scenarios were designed and validated to simulate the cognitive and temporal pressures (e.g., urgency and task-switching) necessary to elicit the ‘adaptive deviance’ predicted by COR theory. Specifically, they induce a resource-constrained trade-off context in which participants are compelled to prioritize primary task performance over secondary security compliance requirements. The scenario descriptions were used to provide contextual grounding for respondents’ evaluations, rather than being operationalized as separate measurement items. Instead, they served as conceptual anchors for assessing overall tendencies toward policy violations.
Demographic Variables: In the research, gender, age, marital status, experience and position were considered as demographic variables.
2.3. Data Analysis
This study investigates the relationships between technostress, techno-strain and information security policy violation. Initially, the study examined the presence of a common method variance error. This was followed by a confirmatory factor analysis (CFA) to evaluate the construct validity. The analysis was conducted in three stages. First, common method bias was assessed using Harman’s single-factor test and variance inflation factor (VIF) values. Second, confirmatory factor analysis (CFA) was conducted to evaluate the measurement model and assess construct validity. During the CFA, four items with factor loadings below the recommended threshold of 0.50 (TW4, TW5, TIS2, and TIS5) were removed to improve construct validity. The remaining items demonstrated satisfactory factor loadings and were retained for all subsequent analyses. Importantly, all latent constructs remained represented in the model after item purification. The results indicate that the seven-factor model exhibited a good fit (χ2 = 508.715; χ2/df = 2.00; CFI = 0.92; TLI = 0.92; SRMR = 0.06; RMSEA = 0.06). Third, the hypotheses were tested using regression-based mediation analysis with the PROCESS macro (Model 4) in SPSS 24, employing bootstrapping procedures with 5000 resamples to estimate direct and indirect effects [58].
The issue of common method variance (CMV) was addressed in two ways. The Harman single factor test and the single factor measurement model were calculated. The Harman single factor test result indicates that, provided that less than 50% of the total variance is explained by a latent construct, the common method variance is within acceptable limits. Principal component analysis was applied to 27 items of the Harman single factor test. The results of the analysis performed without rotation are as follows: the eigenvalues are greater than 1, and collectively they account for 65.99% of the total variance. In addition to Harman’s test, variance inflation factor (VIF) values were examined, and all values were below the recommended threshold, suggesting that common method bias is unlikely to significantly affect the results.
The first factor accounted for 23.85% of the variance, which is below the 50% threshold, indicating that common method variance is not a serious issue in this study. In the second stage, when the data of the single-factor model (χ2: 7306.742; χ2/df: 6.76; p ˂ 0.01; CFI: 0.32; TLI: 0.28; SRMR: 0.12; RMSEA: 0.13) and seven-factor model (χ2: 508.715; χ2/df: 2.00; p ˂ 0.01; CFI: 0.92; TLI: 0.92; SRMR: 0.06; RMSEA: 0.06) were compared, the single-factor model exhibited poor fit whereas the seven-factor model demonstrated acceptable fit indices, indicating that common method variance is unlikely to pose a serious threat to the validity of the results. On the other hand, skewness and kurtosis values were examined to test whether the data set had a normal distribution. Kline [59] states that a data set will have a normal distribution if the skewness value is within ±3 and the kurtosis value is within ±10. In this direction, in our research, the skewness value for Techno-Workload is −0.046 and the kurtosis value is −0.542; for Techno-Invasion, the skewness value is −0.218 and the kurtosis value is −0.644; for Techno-Complexity, the skewness value is 0.513 and the kurtosis value is 0.379; for Techno-Insecurity, the skewness value is 0.810 and the kurtosis value is 0.800; for Techno-Uncertainty, the skewness value is −0.389 and the kurtosis value is −0.176; for Techno-strain, the skewness value was calculated as 0.263 and the kurtosis value as −0.473; and, for information security policy violation, the skewness value was calculated as 0.555 and the kurtosis value as −0.524. Since the skewness and kurtosis values for both scales were within the ranges specified in the literature, it was determined that the data set had a normal distribution.
3. Results
The analysis proceeded in two stages. First, confirmatory factor analysis (CFA) was conducted to validate the measurement model and assess construct validity. The results show that the seven-factor model has a good model fit value (χ2: 508.715; χ2/df: 2.00; p ˂ 0.01; CFI: 0.92; TLI: 0.92; SRMR: 0.06; RMSEA: 0.06) and the seven variables are different from each other. Furthermore, four items with factor loadings below 0.50 (TW4, TW5, TIS2, and TIS5) were excluded to improve construct validity. The remaining items were retained and used in all subsequent analyses. All factor loadings were significant (p < 0.001), indicating that the indicators adequately represent their respective latent constructs. The factor loadings ranged from 0.64 to 0.78 for techno-workload, 0.63 to 0.80 for techno-invasion, 0.54 to 0.77 for techno-complexity, 0.57 to 0.88 for techno-insecurity, 0.62 to 0.84 for techno-uncertainty, 0.62 to 0.84 for techno-strain, and 0.93 to 0.98 for information security policy violation (see Table 1). Each variable’s value for internal consistency was at an appropriate level. Hair et al. [60] stated that composite reliability values greater than 0.7 and AVE values greater than 0.4 are within acceptable limits. The convergent validity of the structure is ensured by the fact that the CR values of the research variables were between 0.76 and 0.96, the AVE values were between 0.43 and 0.91, and CR > AVE. All the composite reliability values were above the recommended values under these conditions (see Table 2). Subsequently, the approach proposed by Fornell and Larcker [61] was employed to assess the discriminant validity.
Table 1.
Results of CFA.
Table 2.
Structure Properties and Correlations.
The results of the study revealed that the square root of the average variance extracted (AVE) of each construct was greater than the correlation between the constructs (see Table 2). The discriminant validity of all variables in the study was observed to be intact. Consequently, the research model demonstrated the presence of appropriate discriminant validity, internal consistency and reliability, and convergent validity. In addition, correlation analysis and hypothesis testing were continued by combining technostress dimensions. As demonstrated in Table 2, technostress exhibited positive correlations with techno-strain (r = 0.61, p < 0.01) and information security policy violation (r = 0.33, p < 0.01). These results are highly consistent and provide a solid foundation for the subsequent testing of our hypothesis. As illustrated in Table 3, the outcomes lend support to the pertinent hypotheses. The fundamental research question underpinning this study was to examine whether techno-strain mediates the relationship between technostress and ISPV. In the initial phase, it was hypothesized that there would be a positive correlation between technostress and information security policy. Regression analysis showed that the relationship between technostress and ISPV was significant (R2 = 0.12, p ˂ 0.001), and the results indicate that elevated levels of technostress (β = 0.31, p ˂ 0.001) are associated with a heightened propensity for ISPV. This finding supports the initial hypothesis that technostress is positively associated with ISPV. In the second stage, it is predicted that technostress will be positively correlated with techno-strain. The regression analysis measuring the relationship between technostress and techno-strain is significant (R2 = 0.37, p ˂ 0.001), and the results indicate that elevated levels of technostress (β = 0.60, p ˂ 0.001) are associated with increased techno-strain. This finding lends further support to the second condition. In the third stage, technostress is predicted to be positively associated with information security policy violation.
Table 3.
Results of Mediation Analysis.
The regression analysis measuring the relationship between techno-strain and information security policy violation is significant (R2 = 0.13, p ˂ 0.001), and the results indicate that elevated levels of techno-strain (β = 0.32, p ˂ 0.001) are associated with an increased propensity for ISPV. Consequently, the third condition is also substantiated.
A summary of the bootstrap analysis results that were utilized for the mediation analysis is provided in Table 3. In the final stage of the research, it was hypothesized that techno-strain mediates the relationship between technostress and ISPV. Should technostress prove to have a significant effect on techno-strain, the hypothesis can be tested for mediation. Additionally, it was observed that technostress exerts a substantial influence on ISPV in the absence of techno-strain. The model demonstrates that techno-strain exerts a substantial influence on ISPV and that, when both technostress and techno-strain are included in the model, the effect of technostress diminishes. Moreover, the analysis was performed using 95% confidence intervals and 5000 bootstraps to calculate the range of indirect effects [62]. Bootstrapping is a robust technique for calculating CIs for indirect effects [63]. The results of the bootstrap test demonstrated that the range of indirect effects of technostress was between 0.06 and 0.34. Given that the bootstrap analysis results did not contain zero, the hypothesis that there is a partial mediator between technostress and information security policy violation was supported. Consequently, the findings of the bootstrap analysis demonstrated statistically significant indirect effects on technostress, thereby validating the primary hypothesis.
4. Discussion
Today, cyber attackers have shifted their focus from targeting systems to directly targeting individuals. Social engineering attacks, often referred to as ‘human hacking,’ highlight that the most vulnerable aspect of information security remains the human factor [63,64].
Considering these threats, employee compliance with Information Security Policies is critical to an organization’s defense [65]. While employees frequently cite time constraints as a reason for non-compliance, the underlying cause often lies in unrecognized psychological motivations [66]. Technostress is not just an individual psychological burden; it also influences employees’ relationships with their organizations and their belief systems about them [67]. Grounded in the Transactional Model of Stress and Coping [22] and the Conservation of Resources theory [23], this study empirically explores the impact of technostress on violations of information security policies. Data analysis revealed that high levels of technostressors significantly increase techno-strain among employees. Furthermore, both TST and TS were found to significantly heighten the tendency to violate ISPs (ISPV). Mediation analysis indicated that the total effect of TST on ISPV was significant, occurring both directly and indirectly through TS. Overall, the findings suggest that exposure to technostressors intensifies techno-strain, thereby increasing the risk of ISP violations, a relationship characterized by partial mediation.
4.1. Theoretical Contribution
This study expands the SSO framework beyond performance- and satisfaction-oriented outcomes to focus on information security behavior. It shifts technostress from a peripheral by-product to a central mechanism influencing tendencies to violate security policies. In this way, the adaptation friction → techno-strain → violation chain becomes theoretically evident, creating a structural connection between the technostress and security behavior literature [55,68,69].
To support this repositioning, we integrate the primary and secondary appraisal processes of the Transactional Model of Stress (TMS) with the “resource loss spiral” and “conservation mode” concepts from the Conservation of Resources (COR) theory. Ancillary security tasks—such as multi-step authentication, complex passwords, and frequent updates—demand cognitive and temporal resources, leading to adaptation frictions. As employees strive to maintain their core functional performance, they may rationally diverge from compliance requirements. These deviations should not only be viewed as stemming from “malicious intent,” but rather as instrumental decisions made to optimize resource allocation [70,71].
In this context, technostress is framed not just as an emotional by-product but as a direct behavioral risk factor. Explanations based on norms—such as deterrence, neutralization, moral disengagement, and moral licensing—are enhanced by the cognitive–emotional exhaustion and resource depletion resulting from techno-strain. This creates a dual-channel explanatory mechanism that combines normative cost–benefit analysis with the resource–rational allocation trade-off [72,73]. The proposed framework also includes governance and cultural aspects. Regulatory regimes not only shape policy content but also set limits on monitoring and surveillance. Embedding security into corporate governance, along with direct oversight at the board level, may foster an environment that weakens the connection between friction and strain within the SSO chain [74,75,76]. Conceptually, we clarify the distinction between technostressors (external demands) and techno-strain (internal psychological costs) to ensure a rigorous delineation within the SSO framework and minimize theoretical overlap. Our results indicate that techno-strain only partially mediates the technostress–ISPV relationship, suggesting that stressors can trigger violations directly even without high strain. We explain this through ‘compliance friction’, operationalized as the ratio of resources required for security tasks to an individual’s available slack. When technological demands are high, employees may make a ‘resource–rational allocation’ decision; they bypass security protocols not out of malice, but as an instrumental choice to optimize limited resources for core functional performance. Thus, technostress acts as a direct behavioral risk factor by reshaping motivational priorities independently of psychological exhaustion. Specifically, we define technostressors as external technological demands—such as overload, invasion, and complexity—while identifying techno-strain as the resulting internal psychological costs, including mental fatigue and emotional exhaustion. Within the Stressor–Strain–Outcome framework, this distinction reflects a processual sequence in which external demands precede and give rise to internal strain responses, thereby ensuring conceptual clarity and minimizing theoretical overlap. “Security fatigue” is defined through the COR lens as a result of cumulative resource depletion, while “compliance friction” is operationalized as the ratio comparing the resources required for secondary security tasks to the individual’s available slack. This refinement decreases overlap between similar constructs, allowing for clearer testing of mediating mechanisms and improving the understanding of how design interventions—such as policy simplification and automation—can be measured [77].
From a process perspective, we introduce a micro-temporal logic which indicates that under clustered daily demands (e.g., patching windows, service interruptions, sprint deadlines), the likelihood of rational deviations increases as resource availability falls below certain thresholds. This logic emphasizes the potential of daily diary methods, behavioral log data, and gamification/feedback interventions to test time-sensitive dynamics [78,79,80].
Contextually, the model sheds light on the resource pressures faced by IT sectors in emerging economies (e.g., Turkiye), characterized by task urgency, compressed release cycles, and stringent security requirements. This environment provides a rich ground for examining moderators such as power distance, collectivism, age or role differences, and task interdependence, thus adding diversity and external validity to a largely Western-centric technostress literature [68,81,82]. Among these contextual factors, cultural dimensions are particularly salient in shaping how individuals respond to technostress. These findings should be interpreted in light of the Turkish cultural context, characterized by relatively high levels of power distance and uncertainty avoidance, which may amplify the technostress–ISPV relationship compared to Western settings. In high power distance environments, top-down security mandates are less likely to be openly questioned, encouraging employees to maintain a compliance-oriented façade while engaging in covert forms of adaptive deviance when resources are depleted. By contrast, in lower power distance contexts, employees may be more inclined to voice concerns or negotiate impractical security requirements, thereby reducing the need for hidden violations. Moreover, high uncertainty avoidance may intensify the strain associated with techno-uncertainty, as frequent technological changes are perceived as greater threats to stability. This heightened sensitivity can increase reliance on resource conservation strategies, such as bypassing security protocols to sustain primary task performance. Conversely, in lower uncertainty avoidance contexts, such changes may be perceived as less disruptive, potentially attenuating both techno-strain and the likelihood of ISPV. Taken together, these cultural contingencies suggest that the behavioral consequences of technostress are not universal but contingent upon the broader institutional and cultural environment.
At the intersection of policy and design, we argue that effective Information Security Policies (ISPs) should not rely solely on deterrence but should incorporate user-centered designs that incentivize secure behavior, integrate effortlessly into workflows, and bolster self-efficacy and social norms. Security education, training, awareness (SETA) programs, simpler rules, and meaningful automation can mitigate compliance friction and, in turn, reduce techno-strain [69,73,83,84]. This framework illustrates that insider risks arise not just from malicious intent, but also from resource pressures and rational deviation behaviors. Regulatory frameworks (e.g., GDPR) should be understood within the context of organizational climate and culture [85,86]. For empirical testing, we propose a model of chained mediation (technostressors → compliance friction → techno-strain → violation intention) and conditional indirect effects (e.g., a strong security climate or ethical leadership weakens the friction–strain relationship).
4.2. Practical Contribution
In corporate information security practices, relying solely on individual awareness to ensure compliance is inadequate for long-term sustainability. Security compliance is not just about awareness; it also depends on the resources available within the organization. Technical controls must align with individuals’ cognitive and emotional capacities to generate lasting effects. Therefore, transforming security behavior at the organizational level requires the design of an integrated intervention framework across four key layers. First, at the system and design level, it is essential to reduce stressors. Importantly, these interventions are not generic but are explicitly aligned with the technostressors identified in this study. Notification hygiene, quiet hours, and structured focus time blocks directly mitigate techno-overload and techno-invasion by reducing interruptions and constant connectivity demands. Micro-learning sessions and secure ‘sandbox’ environments address techno-complexity and techno-uncertainty by enabling gradual, low-risk learning and reducing ambiguity associated with technological change. In contrast, techno-insecurity is best mitigated through interventions that enhance users’ self-efficacy and perceived competence, such as skills-based training and supportive feedback mechanisms, rather than relying solely on punitive controls. Interventions such as maintaining notification hygiene, establishing quiet hours, creating time blocks for focused work, and implementing micro-learning sessions help to preserve employees’ attention, thereby slowing resource depletion [23]. Any technological changes, like software updates and system modifications, should occur at a balanced pace with backward compatibility principles, and be accompanied by “what changed?” summaries to reduce compliance friction. Additionally, embedding learning practices into workflows—such as role-based microlearning, peer coaching, and secure “sandbox” environments—can transform secure behavior into a low-risk, repeatable habit [55,77]. The second layer focuses on structuring technical controls according to secure-by-design principles to minimize the burden on users. Solutions such as passwordless multi-factor authentication (MFA), single sign-on (SSO), and contextual risk-based verification reduce the cognitive load of compliance. Default secure settings, automatic patching systems, and policy-based data loss prevention (DLP) mechanisms should operate in the background. Timely, context-relevant behavioral nudges that provide explanations for “why” decisions need to be made reduce ambiguity and support secure behaviors within the natural workflow [71,83,84]. The third layer emphasizes the importance of human-centered security education and the cultural dimension of the organization. Policy content should address both “how” and “why” security practices are necessary, supported by concrete micro-case studies. This information should be disseminated through role models and peer champions and reinforced with meaningful incentives that promote intrinsic motivation. Cultivating a climate of psychological safety—where error reporting and “near miss” disclosures are encouraged—fosters a learning-oriented security culture instead of one that focuses on punishment [69,76,87]. Finally, at the governance and measurement level, a shared set of indicators formed by integrating HR, IT, and security functions enables a multidimensional evaluation of security practices. Metrics such as alert fatigue, MFA dropout rates, and phishing simulation performance should be monitored alongside human-centered indicators, including retention, well-being, and cognitive load. These indicators allow for a measurable assessment of how streamlining security and user-centric automation impact outcomes, such as increased productivity, reduced incident frequency, and lower intervention costs. Consequently, security investments can be justified not just for compliance, but as part of a tangible “business case” [70,74,75]. Overall, this structure highlights the limitations of punitive, high-friction security strategies and emphasizes that positive reinforcement, embedded behavioral support, and designs aligned with individual resources are essential for sustainable compliance behavior. In hybrid and remote work environments, the importance of complementing technical controls with cultural, leadership, and normative infrastructures becomes even more significant. In conclusion, information security compliance should be viewed not only as a function of individual awareness but also as a result of organizational resource architecture. Aligning technical controls with individuals’ cognitive and emotional capacities is key to transforming secure behaviors into a sustainable norm within the organization [88,89].
4.3. Limitations
The cross-sectional design and reliance on self-reported data limit the ability to directly test causal relationships. This limitation is particularly important given that the proposed relationships involve mediation effects, which ideally require temporal separation to establish causal ordering. This methodological choice should be viewed in light of well-documented issues such as social desirability bias and the intention–behavior gap [35,90]. Critically, responses to hypothetical scenarios may diverge from real-world behavior, particularly under conditions of acute cognitive depletion. While participants may report strong security intentions in controlled survey settings, resource constraints in high-pressure digital environments can impair deliberative processing. Drawing on Conservation of Resources Theory, such depletion shifts individuals toward resource conservation strategies, prioritizing primary task completion over secondary security protocols. As a result, actual security violations may be more likely in practice than suggested by scenario-based self-reports. While scenario-based measures provide standardized and comparable assessment of behavioral tendencies, they may not fully capture actual behaviors. Additionally, since the model is primarily based on IT employees in Turkey, its cultural generalizability requires careful assessment. Accordingly, the findings should be interpreted with caution when generalizing to different institutional and cultural contexts beyond the Turkish IT sector. National cultural dimensions—especially power distance, collectivism, and uncertainty avoidance—can significantly influence perceptions of and compliance with security policies [65,66,90]. Furthermore, the model overlooks several critical factors known to affect information security behavior, such as neutralization strategies, moral licensing, psychological contract breach, organizational justice, and psychological safety [66,73]. Integration with the Job Demands–Resources (JD-R) model has also not been established. These omissions limit the theoretical comprehensiveness of the framework and restrict the ability to fully test potential mediation and moderation mechanisms. Generalizability is further constrained by demographic, structural, and technological factors. Demographic elements like age, tenure, and task criticality can influence resource pressure differently, with individuals in high-responsibility roles facing greater cognitive load. In this regard, the sample composition of the study should be carefully considered. Specifically, with 72% of our participants being engineers and 50.5% working remotely, these factors should be considered as potential moderators in the technostress–ISPV relationship. High-responsibility roles, such as engineering, impose a greater cognitive load and task pressure, which may accelerate the transition into a resource conservation mode. In such a mode, individuals are more likely to prioritize core task completion over secondary security protocols. Furthermore, remote work environments—often characterized by a lack of peer monitoring and direct oversight—may lower the perceived risk of detection, thereby altering the balance between organizational control and the tendency toward adaptive deviance. In hybrid or remote work environments, the absence of formal protective measures such as peer monitoring and direct managerial support can alter the balance between oversight and strain. Moreover, low technological maturity—characterized by outdated infrastructures or overly complex multi-factor authentication—may increase friction and compliance costs. On a cultural level, both power distance and uncertainty avoidance heavily influence how security policies are perceived and adopted [69,91].
4.4. Policy Contribution
The sustainable impact of information security policies depends not only on punitive measures but also on solutions that are aligned with user experience, impose low cognitive load, and are seamlessly integrated into workflows. Therefore, low-friction designs—such as risk-based standards (e.g., passwordless authentication, data minimization principles), context-aware prompts, and automated security protocols—should be prioritized. Training programs should focus not merely on information transfer but on meaning-making, reinforced through micro-scenarios, role models, and peer support. At the organizational level, security compliance should be evaluated not only by the number of violations but also in conjunction with indicators such as productivity, employee well-being, and user satisfaction. To achieve this, it is essential that IT, HR, and security units operate based on shared metrics.
In developing countries, policymakers should prioritize the development of clear, applicable, and sector-specific cybersecurity frameworks at the national level. Particularly in high-risk sectors such as banking, transparent protocols, incentives, and technical tools should be provided. Furthermore, addressing the shortage of qualified personnel should be a strategic priority; scholarship programs, training centers, public–private partnerships, and grants that support local expertise can significantly contribute to this process [89]. In conclusion, effective security policies must go beyond technical accuracy and be grounded in an inclusive architecture that understands, supports, and guides human behavior.
4.5. Future Studies
This study highlights that compliance with information security policies (ISPs) cannot be sufficiently explained by individual awareness or intent alone. Instead, it must be understood through a multi-layered model that integrates organizational, social, technological, and psychological factors [55,69]. Security violations are often not driven by malicious intent, but by cognitive resource depletion, technostress, task pressure, and systemic friction [71,90]. Consequently, theoretical models must incorporate contextual stressors surrounding individual decision-making.
Future research should examine how coercive, monetary, and normative controls interact with personal responsibility [70], and how individual traits—such as decision-making style, security orientation, and psychological ownership—influence threat and coping appraisals [92]. Constructs like social support, collective norms, and group interaction should be modeled with empowerment theory [93].
ISP compliance is shaped not only by intrinsic motivation but also by contextual stressors [68,94]. Technostress, role ambiguity, and workload pressures should be examined alongside reward and penalty systems [66]. Intervention strategies targeting psychological contract breach and enhancing trust should also be explored [95]. Cross-cultural and cross-sectoral comparisons are needed, as cultural dimensions like power distance and uncertainty avoidance significantly shape policy perception [71,82].
Methodologically, longitudinal and field experiments are vital to identify causal mechanisms [88]. This is particularly important given that technostress and resource depletion are dynamic processes that unfold over time, making temporal separation essential for accurately capturing mediation effects and establishing causal ordering. Multi-source data—including system logs, EMA, and managerial evaluations—should supplement self-reports [71]. Scenario-based research should diversify violation types and account for factors like gender bias and scenario realism [95].
Intervention studies must assess SETA content, neutralization-disrupting messages, gamification [78], multichannel communication [76], simplified policies, and leadership framing [88]. Analytical approaches should include multigroup SEM and multilevel modeling to examine heterogeneity by age, gender, or role criticality [91]. ROI-focused structural models should trace the chain from violation to incident to financial impact [90].
Emerging tools such as AI-assisted “compliance co-pilots” must be evaluated for their impact on technostress, compliance friction, and decision quality [73,96]. Design science methods should drive the development of contextual, low-friction security solutions [71], which must be field-tested for behavioral efficacy.
Finally, studies should examine how low-risk violations become normalized and whether organizational responses differ by gender [81]. At the ecosystem level, the impact of GDPR-like regulations on insider threats should be analyzed in tandem with the security climate [86]. In developing countries, national security frameworks must include practical guidance, capacity building, and economic incentives tailored to high-risk sectors like banking [89]. In conclusion, future research on ISP compliance should adopt a theoretically robust, contextually sensitive, and methodologically integrative approach. Compliance must be explored not just through the lens of “what should be done?” but also “why isn’t it done?”, “how can it be enabled?”, and “under which conditions is it sustainable?”—positioning cybersecurity not only as a technical issue but also as a behavioral and organizational design challenge.
Author Contributions
Conceptualization, H.A.; methodology, F.A. and H.İ.K.; software, O.D.; validation, F.A. and H.İ.K.; formal analysis, O.D.; investigation, O.D.; resources, H.A.; data curation, O.D.; writing—original draft preparation, O.D.; writing—review and editing, F.A. and H.İ.K.; visualization, O.D.; supervision, H.A.; project administration, H.A. All authors have read and agreed to the published version of the manuscript.
Funding
This research received no external funding.
Institutional Review Board Statement
This study was approved by the Gümüşhane University Scientific Research and Publication Ethics Board on 23 February 2022 (Decision No: 2022/1, Approval No: E-95674917-108.99-81066).
Informed Consent Statement
Informed consent was obtained from all individuals who voluntarily participated in this study prior to data collection.
Data Availability Statement
The data supporting the findings of this study are available from the corresponding author upon reasonable request.
Acknowledgments
The authors would like to express their sincere gratitude to all IT professionals and engineers who voluntarily participated in this study and contributed their valuable time and insights during the survey process. Their participation made this research possible.
Conflicts of Interest
The authors declare no conflicts of interest.
Abbreviations
The following abbreviations are used in this manuscript:
| ICT | Information and Communication Technologies |
| ISP | Information Security Policy |
| ISPV | Information Security Policy Violation |
| IT | Information Technology |
| TST | Technostress |
| TS | Techno-Strain |
| TW | Techno-Workload |
| TI | Techno-Invasion |
| TC | Techno-Complexity |
| TIS | Techno-Insecurity |
| TUS | Techno-Uncertainty |
| TMS | Transactional Model of Stress and Coping |
| COR | Conservation of Resources Theory |
| SSO | Stressor–Strain–Outcome Framework |
| CFA | Confirmatory Factor Analysis |
| CMV | Common Method Variance |
| CR | Composite Reliability |
| AVE | Average Variance Extracted |
| SE | Standard Error |
| LLCI | Lower Limit Confidence Interval |
| ULCI | Upper Limit Confidence Interval |
| SETA | Security Education, Training and Awareness |
| MFA | Multi-Factor Authentication |
| DLP | Data Loss Prevention |
| SEM | Structural Equation Modeling |
| GDPR | General Data Protection Regulation |
References
- Forman, C.; King, J.L.; Lyytinen, K. Information, technology, and the changing nature of work. Inf. Syst. Res. 2014, 25, 789–795. [Google Scholar] [CrossRef] [Scilit]
- Nasirpouri, F.; Shadbad, F.N.; Biros, D. Technostress and its influence on employee information security policy compliance. Inf. Technol. People, 2020; in press. [CrossRef] [Scilit]
- Vial, G. Understanding digital transformation: A review and a research agenda. J. Strateg. Inf. Syst. 2019, 28, 118–144. [Google Scholar] [CrossRef] [Scilit]
- IBM Security. Cost of a Data Breach Report 2023. Available online: https://www.ibm.com/reports/data-breach (accessed on 12 March 2026).
- European Union Agency for Cybersecurity. ENISA Threat Landscape 2022. Available online: https://www.enisa.europa.eu/publications/enisa-threat-landscape-2022 (accessed on 12 March 2026).
- Chen, X.; Chen, L.; Wu, D. Factors that influence employees’ security policy compliance: An awareness–motivation–capability perspective. J. Comput. Inf. Syst. 2018, 58, 312–324. [Google Scholar] [CrossRef] [Scilit]
- Alhogail, A. Design and validation of information security culture framework. Comput. Secur. 2021, 102, 102151. [Google Scholar] [CrossRef] [Scilit]
- Alshaikh, M. Developing cybersecurity culture to influence employee behavior: A practice perspective. Comput. Secur. 2020, 98, 102003. [Google Scholar] [CrossRef] [Scilit]
- Klahr, R.; Shah, J.N.; Sheriffs, P.; Rossington, T.; Pestell, G. Cyber Security Breaches Survey 2017: Main Report; Department for Digital, Culture, Media & Sport: London, UK, 2017. [Google Scholar]
- Ahmed, M.; Sharif, L.; Kabir, M.; Al-Maimani, M. Human errors in information security. Int. J. Adv. Trends Comput. Sci. Eng. 2012, 1, 82–87. [Google Scholar]
- Deng, L.; Lv, Y.; Liu, Y.; Zhao, Y. Impact of Fintech on Bank Risk-Taking: Evidence from China. Risks 2021, 9, 99. [Google Scholar] [CrossRef] [Scilit]
- Tarafdar, M.; Tu, Q.; Ragu-Nathan, T.S. Impact of technostress on end-user satisfaction and performance. J. Manag. Inf. Syst. 2010, 27, 303–334. [Google Scholar] [CrossRef] [Scilit]
- Kumar, P.S. Technostress: A comprehensive literature review on dimensions, impacts, and management strategies. Comput. Hum. Behav. Rep. 2024, 16, 100475. [Google Scholar] [CrossRef] [Scilit]
- Ragu-Nathan, T.S.; Tarafdar, M.; Ragu-Nathan, B.S.; Tu, Q. The consequences of technostress for end users in organizations: Conceptual development and validation. Inf. Syst. Res. 2008, 19, 417–433. [Google Scholar] [CrossRef] [Scilit]
- Fischer, T.; Reuter, M.; Riedl, R. The digital stressors scale: Development and validation of a new survey instrument to measure digital stress perceptions in the workplace context. Front. Psychol. 2021, 12, 607598. [Google Scholar] [CrossRef] [Scilit]
- Tarafdar, M.; Pullins, E.B.; Ragu-Nathan, T.S. Technostress: Negative effect on performance and possible mitigations. Inf. Syst. J. 2015, 25, 103–132. [Google Scholar] [CrossRef] [Scilit]
- Ayyagari, R.; Grover, V.; Purvis, R. Technostress: Technological antecedents and implications. MIS Q. 2011, 35, 831–858. [Google Scholar] [CrossRef] [Scilit]
- D’Arcy, J.; Herath, T.; Shoss, M.K. Understanding employee responses to stressful information security requirements: A coping perspective. J. Manag. Inf. Syst. 2014, 31, 285–318. [Google Scholar] [CrossRef] [Scilit]
- Posey, C.; Bennett, R.J.; Roberts, T.L. Understanding the mindset of the abusive insider: An examination of insiders’ causal reasoning following ISPV. MIS Q. 2011, 35, 109–126. [Google Scholar]
- Ifinedo, P. Information systems security policy compliance: An empirical study of the effects of socialisation, influence, and cognition. Inf. Manag. 2014, 51, 69–79. [Google Scholar] [CrossRef] [Scilit]
- Tams, S.; Thatcher, J.B.; Grover, V. Concentration, competence, confidence, and capture: An experimental study of age, interruption-based technostress, and task performance. J. Assoc. Inf. Syst. 2018, 19, 857–908. [Google Scholar] [CrossRef] [Scilit]
- Lazarus, R.S.; Folkman, S. Stress, Appraisal, and Coping; Springer: New York, NY, USA, 1984. [Google Scholar]
- Hobfoll, S.E. Conservation of resources: A new attempt at conceptualizing stress. Am. Psychol. 1989, 44, 513–524. [Google Scholar] [CrossRef]
- Hobfoll, S.E. The influence of culture, community, and the nested-self in the stress process: Advancing conservation of resources theory. Appl. Psychol. 2001, 50, 337–421. [Google Scholar] [CrossRef] [Scilit]
- Halbesleben, J.R.B.; Neveu, J.-P.; Paustian-Underdahl, S.C.; Westman, M. Getting to the “COR”: Understanding the role of resources in conservation of resources theory. J. Manag. 2014, 40, 1334–1364. [Google Scholar] [CrossRef] [Scilit]
- Brod, C. Technostress: The Human Cost of the Computer Revolution; Addison-Wesley: Reading, MA, USA, 1984. [Google Scholar]
- Tarafdar, M.; Tu, Q.; Ragu-Nathan, B.S.; Ragu-Nathan, T.S. The impact of technostress on role stress and productivity. J. Manag. Inf. Syst. 2007, 24, 301–328. [Google Scholar] [CrossRef] [Scilit]
- Tarafdar, M.; Cooper, C.L.; Stich, J.F. The technostress trifecta—Techno eustress, techno distress and design: Theoretical directions and an agenda for research. Inf. Syst. J. 2019, 29, 6–42. [Google Scholar] [CrossRef] [Scilit]
- Maier, C.; Laumer, S.; Wirth, J.; Weitzel, T. Technostress and the hierarchical levels of personality: A two-wave study with multiple data samples. Eur. J. Inf. Syst. 2019, 28, 496–522. [Google Scholar] [CrossRef] [Scilit]
- Sarabadani, J.; Carter, M.; Compeau, D. Ten years of research on technostress creators and inhibitors: Synthesis and critique. In Proceedings of the Americas Conference on Information Systems (AMCIS), New Orleans, LA, USA, 16–18 August 2018; pp. 86–95. [Google Scholar]
- Folkman, S. Stress: Appraisal and coping. In Encyclopedia of Behavioral Medicine; Gellman, M.D., Turner, J.R., Eds.; Springer: New York, NY, USA, 2013; pp. 1913–1915. [Google Scholar]
- Gaudioso, F.; Turel, O.; Galimberti, C. The mediating roles of strain facets and coping strategies in translating technostressors into adverse job outcomes. Comput. Hum. Behav. 2017, 69, 189–196. [Google Scholar] [CrossRef] [Scilit]
- Turel, O.; Gaudioso, F. Technostressors, distress and strain: The roles of leadership and competitive climates. Cogn. Technol. Work 2018, 20, 309–324. [Google Scholar] [CrossRef] [Scilit]
- Rogers, R.W. Cognitive and Physiological Processes in Fear Appeals and Attitude Change: A Revised Theory of Protection Motivation; Cacioppo, J.T., Petty, R.E., Eds.; Social Psychophysiology; Guilford Press: New York, NY, USA, 1983; pp. 153–176. [Google Scholar]
- Siponen, M.; Mahmood, M.A.; Pahnila, S. Employees’ adherence to information security policies: An exploratory field study. Inf. Manag. 2014, 51, 217–224. [Google Scholar] [CrossRef] [Scilit]
- Hwang, I.; Cha, O. Examining technostress creators and role stress as potential threats to employees’ information security compliance. Comput. Hum. Behav. 2018, 81, 282–293. [Google Scholar] [CrossRef] [Scilit]
- Sweller, J. Cognitive load during problem solving: Effects on learning. Cogn. Sci. 1988, 12, 257–285. [Google Scholar] [CrossRef]
- Kahneman, D. Attention and Effort; Prentice-Hall: Englewood Cliffs, NJ, USA, 1973. [Google Scholar]
- Choi, S.H.; Kim, Y.H.; Hebisch, M.; Sliwinski, C.; Lee, S.; D’Avanzo, C.; Chen, H.; Hooli, B.; Asselin, C.; Muffat, J.; et al. A three-dimensional human neural cell culture model of Alzheimer’s disease. Nature 2014, 515, 274–278. [Google Scholar] [CrossRef] [Scilit]
- Islam, F.; Wang, J.; Farooq, M.A.; Khan, M.S.S.; Xu, L.; Zhu, J.; Zhao, M.; Muños, S.; Li, Q.X.; Zhou, W. Potential impact of the herbicide 2,4-dichlorophenoxyacetic acid on human and ecosystems. Environ. Int. 2018, 111, 332–351. [Google Scholar] [CrossRef] [Scilit]
- Yu, L.; Shi, C.; Cao, X. Understanding the effect of social media overload on academic performance: A stressor–strain–outcome perspective. In Proceedings of the Hawaii International Conference on System Sciences (HICSS), Maui, HI, USA, 8–11 January 2019. [Google Scholar]
- Herath, T.; Rao, H.R. Protection motivation and deterrence: A framework for security policy compliance in organisations. Eur. J. Inf. Syst. 2009, 18, 106–125. [Google Scholar] [CrossRef] [Scilit]
- Ifinedo, P. Understanding information systems security policy compliance: An integration of the theory of planned behavior and the protection motivation theory. Comput. Secur. 2012, 31, 83–95. [Google Scholar] [CrossRef] [Scilit]
- Fischer, C.; Malycha, C.P.; Schafmann, E. The influence of intrinsic motivation and synergistic extrinsic motivators on creativity and innovation. Front. Psychol. 2019, 10, 137. [Google Scholar] [CrossRef] [Scilit]
- Califf, C.B.; Sarker, S.; Sarker, S. The bright and dark sides of technostress: A mixed-methods study involving healthcare IT. MIS Q. 2020, 44, 809–856. [Google Scholar] [CrossRef] [Scilit]
- Sellberg, C.; Susi, T. Technostress in the office: A distributed cognition perspective on human–technology interaction. Cogn. Technol. Work 2014, 16, 187–201. [Google Scholar] [CrossRef] [Scilit]
- Chen, A.; Karahanna, E. Life interrupted: The effects of technology-mediated work interruptions on work and nonwork outcomes. MIS Q. 2018, 42, 1023–1042. [Google Scholar] [CrossRef] [Scilit]
- Singh, T.; Johnston, A.; Thatcher, J. How much is too much: Employee monitoring, surveillance, and strain. In Proceedings of the International Conference on Information Systems (ICIS), Munich, Germany, 15–18 December 2019. [Google Scholar]
- Brislin, R.W. Cross-Cultural Research Methods. In Environment and Culture; Springer: Boston, MA, USA, 1980; pp. 47–82. [Google Scholar]
- Liu, Y.; Keller, R.T. How psychological safety impacts R&D project teams’ performance. Res.-Technol. Manag. 2021, 64, 39–45. [Google Scholar]
- Wang, K.; Shu, Q.; Tu, Q. Technostress under different organizational environments: An empirical investigation. Comput. Hum. Behav. 2008, 24, 3002–3013. [Google Scholar] [CrossRef] [Scilit]
- Fuglseth, A.M.; Sørebø, Ø. The effects of technostress within the context of employee use of ICT. Comput. Hum. Behav. 2014, 40, 161–170. [Google Scholar] [CrossRef] [Scilit]
- Hwang, I.; Kim, S.; Rebman, C. Impact of regulatory focus on security technostress and organizational outcomes: The moderating effect of security technostress inhibitors. Inf. Technol. People 2022, 35, 2043–2074. [Google Scholar] [CrossRef] [Scilit]
- Moore, J.E. One road to turnover: An examination of work exhaustion in technology professionals. MIS Q. 2000, 24, 141–168. [Google Scholar] [CrossRef] [Scilit]
- Straub, D.W.; Welke, R.J. Coping with systems risk: Security planning models for management decision making. MIS Q. 1998, 22, 441–469. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Trevino, L.K. The social effects of punishment in organizations: A justice perspective. Acad. Manag. Rev. 1992, 17, 647–676. [Google Scholar] [CrossRef] [Scilit]
- Siponen, M.T.; Vance, A. Neutralization: New insights into the problem of employee information systems security policy violations. MIS Q. 2010, 34, 487–502. [Google Scholar] [CrossRef] [Scilit]
- Podsakoff, P.M.; MacKenzie, S.B.; Lee, J.Y.; Podsakoff, N.P. Common method biases in behavioral research: A critical review of the literature and recommended remedies. J. Appl. Psychol. 2003, 88, 879–903. [Google Scholar] [CrossRef] [Scilit]
- Kline, R.B. Principles and Practice of Structural Equation Modeling, 4th ed.; Guilford Press: New York, NY, USA, 2016. [Google Scholar]
- Hair, J.F.; Black, W.C.; Babin, B.J.; Anderson, R.E.; Tatham, R.L. Multivariate Data Analysis, 6th ed.; Pearson Prentice Hall: Upper Saddle River, NJ, USA, 2006. [Google Scholar]
- Fornell, C.; Larcker, D.F. Structural equation models with unobservable variables and measurement error: Algebra and statistics. J. Mark. Res. 1981, 18, 382–388. [Google Scholar] [CrossRef] [Scilit]
- MacKinnon, D.P.; Lockwood, C.M.; Williams, J. Confidence limits for the indirect effect: Distribution of the product and resampling methods. Multivar. Behav. Res. 2004, 39, 99–128. [Google Scholar] [CrossRef] [Scilit]
- Williams, J.; MacKinnon, D.P. Resampling and distribution of the product methods for testing indirect effects in complex models. Struct. Equ. Model. 2008, 15, 23–51. [Google Scholar] [CrossRef] [Scilit]
- Cochran, K.A. Cybersecurity Essentials: Practical Tools for Today’s Digital Defenders; Springer Nature: Cham, Switzerland, 2024. [Google Scholar]
- Ussher-Eke, D. Building a cyber-resilient workforce through HR. World J. Adv. Res. Rev. 2025, 27, 706–716. [Google Scholar] [CrossRef]
- Lee, D.; Lallie, H.S.; Michaelides, N. The impact of an employee’s psychological contract breach on compliance with information security policies: Intrinsic and extrinsic motivation. Cogn. Technol. Work 2023, 25, 273–289. [Google Scholar] [CrossRef] [Scilit]
- Shin, J.W.; Shin, H.C. Effects of technostress on psychological contract violation and organizational change resistance. Behav. Sci. 2024, 14, 768. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Safa, N.S.; von Solms, R.; Furnell, S. Information security policy compliance model in organizations. Comput. Secur. 2016, 56, 70–82. [Google Scholar] [CrossRef] [Scilit]
- McLeod, A.; Dolezel, D. Information Security Policy Non-Compliance: Can Capitulation Theory Explain User Behaviors? Comput. Secur. 2022, 112, 102526. [Google Scholar] [CrossRef] [Scilit]
- Chen, Y.; Ramamurthy, K.; Wen, K.W. Organizations’ information security policy compliance: Stick or carrot approach? J. Manag. Inf. Syst. 2012, 29, 157–188. [Google Scholar] [CrossRef] [Scilit]
- Yazdanmehr, A.; Li, H.; Wang, J. Employee responses to information security related stress: Coping and violation intention. Inf. Syst. J. 2023, 33, 598–639. [Google Scholar] [CrossRef] [Scilit]
- Bulgurcu, B.; Cavusoglu, H.; Benbasat, I. Information security policy compliance: An empirical study of rationality-based beliefs and information security awareness. MIS Q. 2010, 34, 523–548. [Google Scholar] [CrossRef] [Scilit]
- Balagopal, N.; Mathew, S.K. Exploring the factors influencing information security policy compliance and violations: A systematic literature review. Comput. Secur. 2024, 147, 104062. [Google Scholar] [CrossRef] [Scilit]
- von Solms, B.; von Solms, R. The 10 deadly sins of information security management. Comput. Fraud Secur. 2004, 2004, 11–13. [Google Scholar] [CrossRef] [Scilit]
- Damianides, M. Sarbanes–Oxley and IT governance: New guidance on IT control and compliance. Inf. Syst. Manag. 2005, 22, 77–85. [Google Scholar] [CrossRef] [Scilit]
- Hong, Y.; Furnell, S. Motivating information security policy compliance: Insights from perceived organizational formalization. J. Comput. Inf. Syst. 2022, 62, 19–28. [Google Scholar] [CrossRef] [Scilit]
- Backhouse, J.; Hsu, C.W.; Silva, L. Circuits of power in creating de jure standards: Shaping an international information systems security standard. MIS Q. 2006, 30, 413–438. [Google Scholar] [CrossRef] [Scilit]
- Schell, J. The Art of Game Design: A Book of Lenses; CRC Press: Boca Raton, FL, USA, 2008. [Google Scholar]
- Dickson, B.J. The Dictator’s Dilemma: The Chinese Communist Party’s Strategy for Survival; Oxford University Press: Oxford, UK, 2016. [Google Scholar]
- Bakker, A.B.; Bal, P.M. Weekly work engagement and performance: A study among starting teachers. J. Occup. Organ. Psychol. 2010, 83, 189–206. [Google Scholar] [CrossRef] [Scilit]
- Kuo, K.M.; Talley, P.C.; Huang, C.H. A meta-analysis of deterrence theory in security-compliant and security-risk behaviors. Comput. Secur. 2020, 96, 101928. [Google Scholar] [CrossRef] [Scilit]
- Haag, S.; Siegfried, N.; Winkler, N. Informal control responses to ISPV: A factorial survey on insurance employees’ moral licensing of insider threats. Comput. Secur. 2025, 139, 104575. [Google Scholar] [CrossRef] [Scilit]
- Leach, J. Improving user security behaviour. Comput. Secur. 2003, 22, 685–692. [Google Scholar] [CrossRef] [Scilit]
- Wahid, S.D. Cyber Security Behavior in Online Distance Learning: Utilizing National E-Learning Policy. Turk. J. Comput. Math. Educ. 2021, 12, 1719–1728. [Google Scholar]
- Gwebu, K.L.; Wang, J.; Zhu, D.X. Does IT security investment matter? Accounting for the influence of institutional factors in IT security behavior. J. Strateg. Inf. Syst. 2020, 29, 101621. [Google Scholar]
- Lowry, P.B.; Moody, G.D.; Willison, R.; Posey, C. The “Signalgate” Case is Waving a Red Flag to All Organizational and Behavioral Cybersecurity Leaders, Practitioners, and Researchers: Are We Receiving the “Signal” Amidst the Noise? arXiv 2025, arXiv:2509.07053. [Google Scholar]
- Ruighaver, A.B.; Maynard, S.B.; Chang, S. Organisational security culture: Extending the end-user perspective. Comput. Secur. 2007, 26, 56–62. [Google Scholar] [CrossRef] [Scilit]
- Arif, M.; Badila, M.; Warden, J.M.; Ur Rehman, A. Human factors toward compliance with organizational information security policy. Inf. Secur. J. A Glob. Perspect. 2025, 34, 235–250. [Google Scholar] [CrossRef] [Scilit]
- Alrawhani, E.M.; Romli, A.; Al-Sharafi, M.A. Evaluating the role of protection motivation theory in information security policy compliance: Insights from the banking sector using PLS-SEM approach. J. Open Innov. Technol. Mark. Complex. 2025, 11, 100463. [Google Scholar] [CrossRef] [Scilit]
- Kim, B.-J.; Kim, M.-J. The influence of work overload on cybersecurity behavior: A moderated mediation model of psychological contract breach, burnout, and self-efficacy in AI learning such as ChatGPT. Technol. Soc. 2024, 77, 102543. [Google Scholar] [CrossRef] [Scilit]
- Hofstede, G. Culture’s recent consequences: Using dimension scores in theory and research. Int. J. Cross Cult. Manag. 2001, 1, 11–17. [Google Scholar] [CrossRef] [Scilit]
- Donalds, C.; Osei-Bryson, K.M. Cybersecurity compliance behavior: Exploring the influences of individual decision style and other antecedents. Int. J. Inf. Manag. 2020, 51, 102056. [Google Scholar] [CrossRef] [Scilit]
- Gutierrez, L.M. Beyond coping: An empowerment perspective on stressful life events. J. Soc. Soc. Welf. 1994, 21, 201–219. [Google Scholar] [CrossRef] [Scilit]
- Aggarwal, A.; Dhurkari, R.K. Association between stress and information security policy non-compliance behavior: A meta-analysis. Comput. Secur. 2023, 124, 102991. [Google Scholar] [CrossRef] [Scilit]
- van Gilst, E.; Schalk, R.; Kluijtmans, T.; Poell, R. The role of remediation in mitigating the negative consequences of psychological contract breach: A qualitative study in the banking sector. J. Change Manag. 2020, 20, 264–282. [Google Scholar] [CrossRef] [Scilit]
- Hubbard, D.W.; Seiersen, R. How to Measure Anything in Cybersecurity Risk; John Wiley & Sons: Hoboken, NJ, USA, 2023. [Google Scholar]

Disclaimer/Publisher’s Note: The statements, opinions and data contained in all publications are solely those of the individual author(s) and contributor(s) and not of MDPI and/or the editor(s). MDPI and/or the editor(s) disclaim responsibility for any injury to people or property resulting from any ideas, methods, instructions or products referred to in the content. |
© 2026 by the authors. Licensee MDPI, Basel, Switzerland. This article is an open access article distributed under the terms and conditions of the Creative Commons Attribution (CC BY) license.