


Abstract
With the accelerated development of the global digital economy, data spaces have become a crucial infrastructure for cross-domain data circulation and value creation. However, cross-organizational and cross-regional data sharing still faces several challenges, including insufficient trust, fragmented governance, and inconsistent standards. Against this backdrop, blockchain technology, with its decentralized, traceable, and tamper-resistant characteristics, offers new avenues for building collaborative trust mechanisms within trustworthy data spaces. This paper systematically reviews the current research on trustworthy data spaces, the blockchain, zero-knowledge proofs, and federated learning. It proposes a technology-governance-standardization (TGS) framework for cross-border governance. To verify the framework, we proposed a collaborative trust mechanism combining “on-chain light attest, off-chain deep store, and cross-layer verifiable bridge” (LPHS–XV), which achieves data availability without visibility and compliance auditability. A prototype was then validated in the cross-border medical data space at the Macao-Hengqin Station, providing a scalable experience for global data governance.
1. Introduction
Against the backdrop of accelerated development of the global digital economy, data has become a key production factor and strategic resource, and it is gradually becoming a core resource for promoting economic growth and modernizing social governance [1]. However, a series of problems, such as data silos, data security, and privacy concerns, directly limit the full realization of data value [2]. To further promote the compliant and efficient circulation and use of data elements and accelerate the construction of a digital economy with data as a key element, a trustworthy data space [3] has emerged as a new type of data infrastructure and value creation, becoming an important direction for the development of the global digital economy by building a secure, trustworthy, and interconnected data sharing environment to promote the orderly flow of data and value creation.
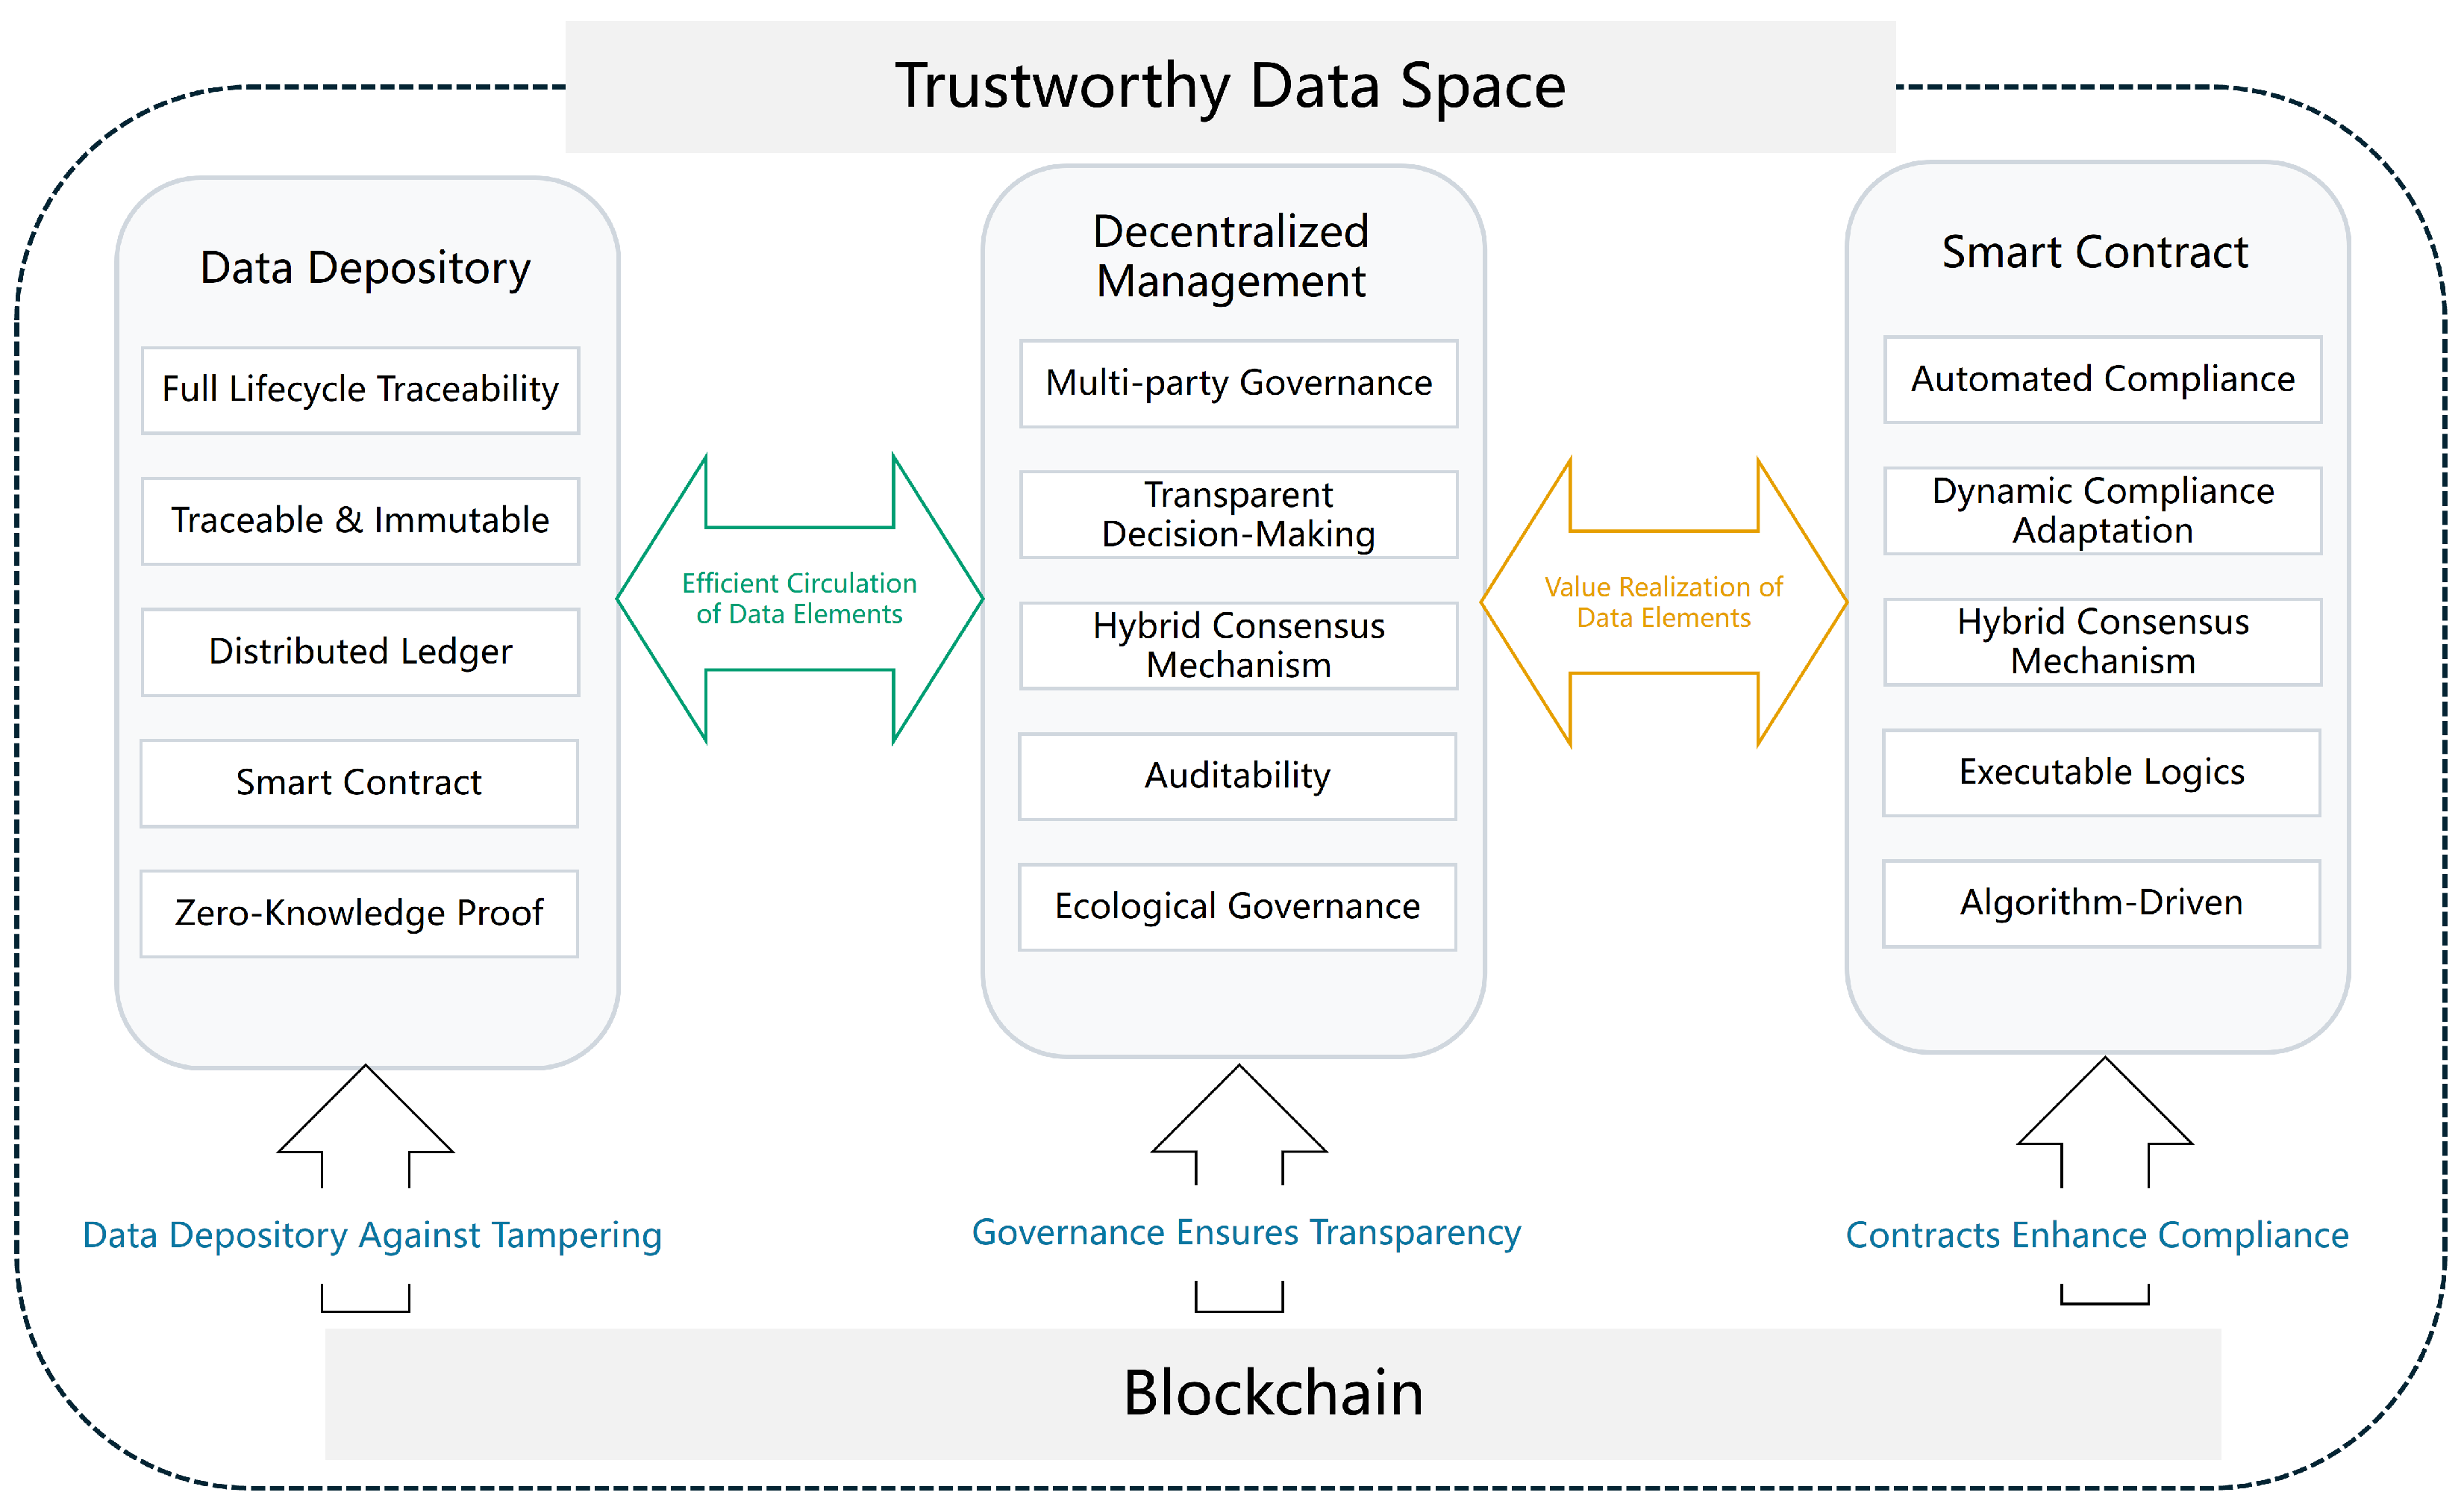
The concept of trustworthy data space originated from the data space proposed by Michael Franklin et al. [4] in 2005. Based on advanced international practices of the European Union and other countries, and in combination with its own national conditions and actual development needs, China proposed the concept of a “trustworthy data space” in November 2024 [5]. They clearly pointed out that a trustworthy data space is a data circulation and utilization infrastructure based on consensus rules, connecting multiple parties and realizing the sharing and use of data resources [6]. It is an application ecosystem for co-creating data element value and an important carrier for supporting the construction of a national integrated data market [7]. A completely trustworthy data space should enable trust in users and data, discover and share data resources, and collaboratively develop and create value among multiple subjects [8]. Figure 1 shows the structure of a trustworthy data space. However, the trustworthy data space still faces key challenges, including bottlenecks in large-scale, high-frequency data interactions, the lack of cross-border governance mechanisms, and lagging standardization and interoperability. At present, the trustworthy data space mainly has the following problems:
- (1)
- There is a risk of sensitivity exposure in cross-domain circulation (i.e., when data circulates in an environment with multiple parties and a lack of mutual trust, there is a lack of end-to-end verifiable access control and a minimum disclosure mechanism) [9];
- (2)
- There are challenges in usability verification under the heterogeneity of master data sovereignty. Due to differences in laws in different countries and regions, it is difficult to make verifiable judgments on data processing activities without relying on centralized approval [10];
- (3)
- There is difficulty in automating the allocation of stakeholder value. The data value chain involves multiple heterogeneous stakeholders such as platform operators, data providers, data users, and regulatory agencies [11];
- (4)
- Data island barriers exist in heterogeneous environments. In multi-chain architectures, multi-cloud environments, and cross-industry application scenarios, there is a lack of universal data format standards and interface protocols [12];
- (5)
- There are performance-privacy-cost trade-offs in high-concurrency scenarios. In large-scale concurrent data transaction scenarios, all three have inherent constraints that may significantly reduce the efficiency of multi-party collaboration and affect overall system performance [13].
Figure 1.
The structure of a trustworthy data space.
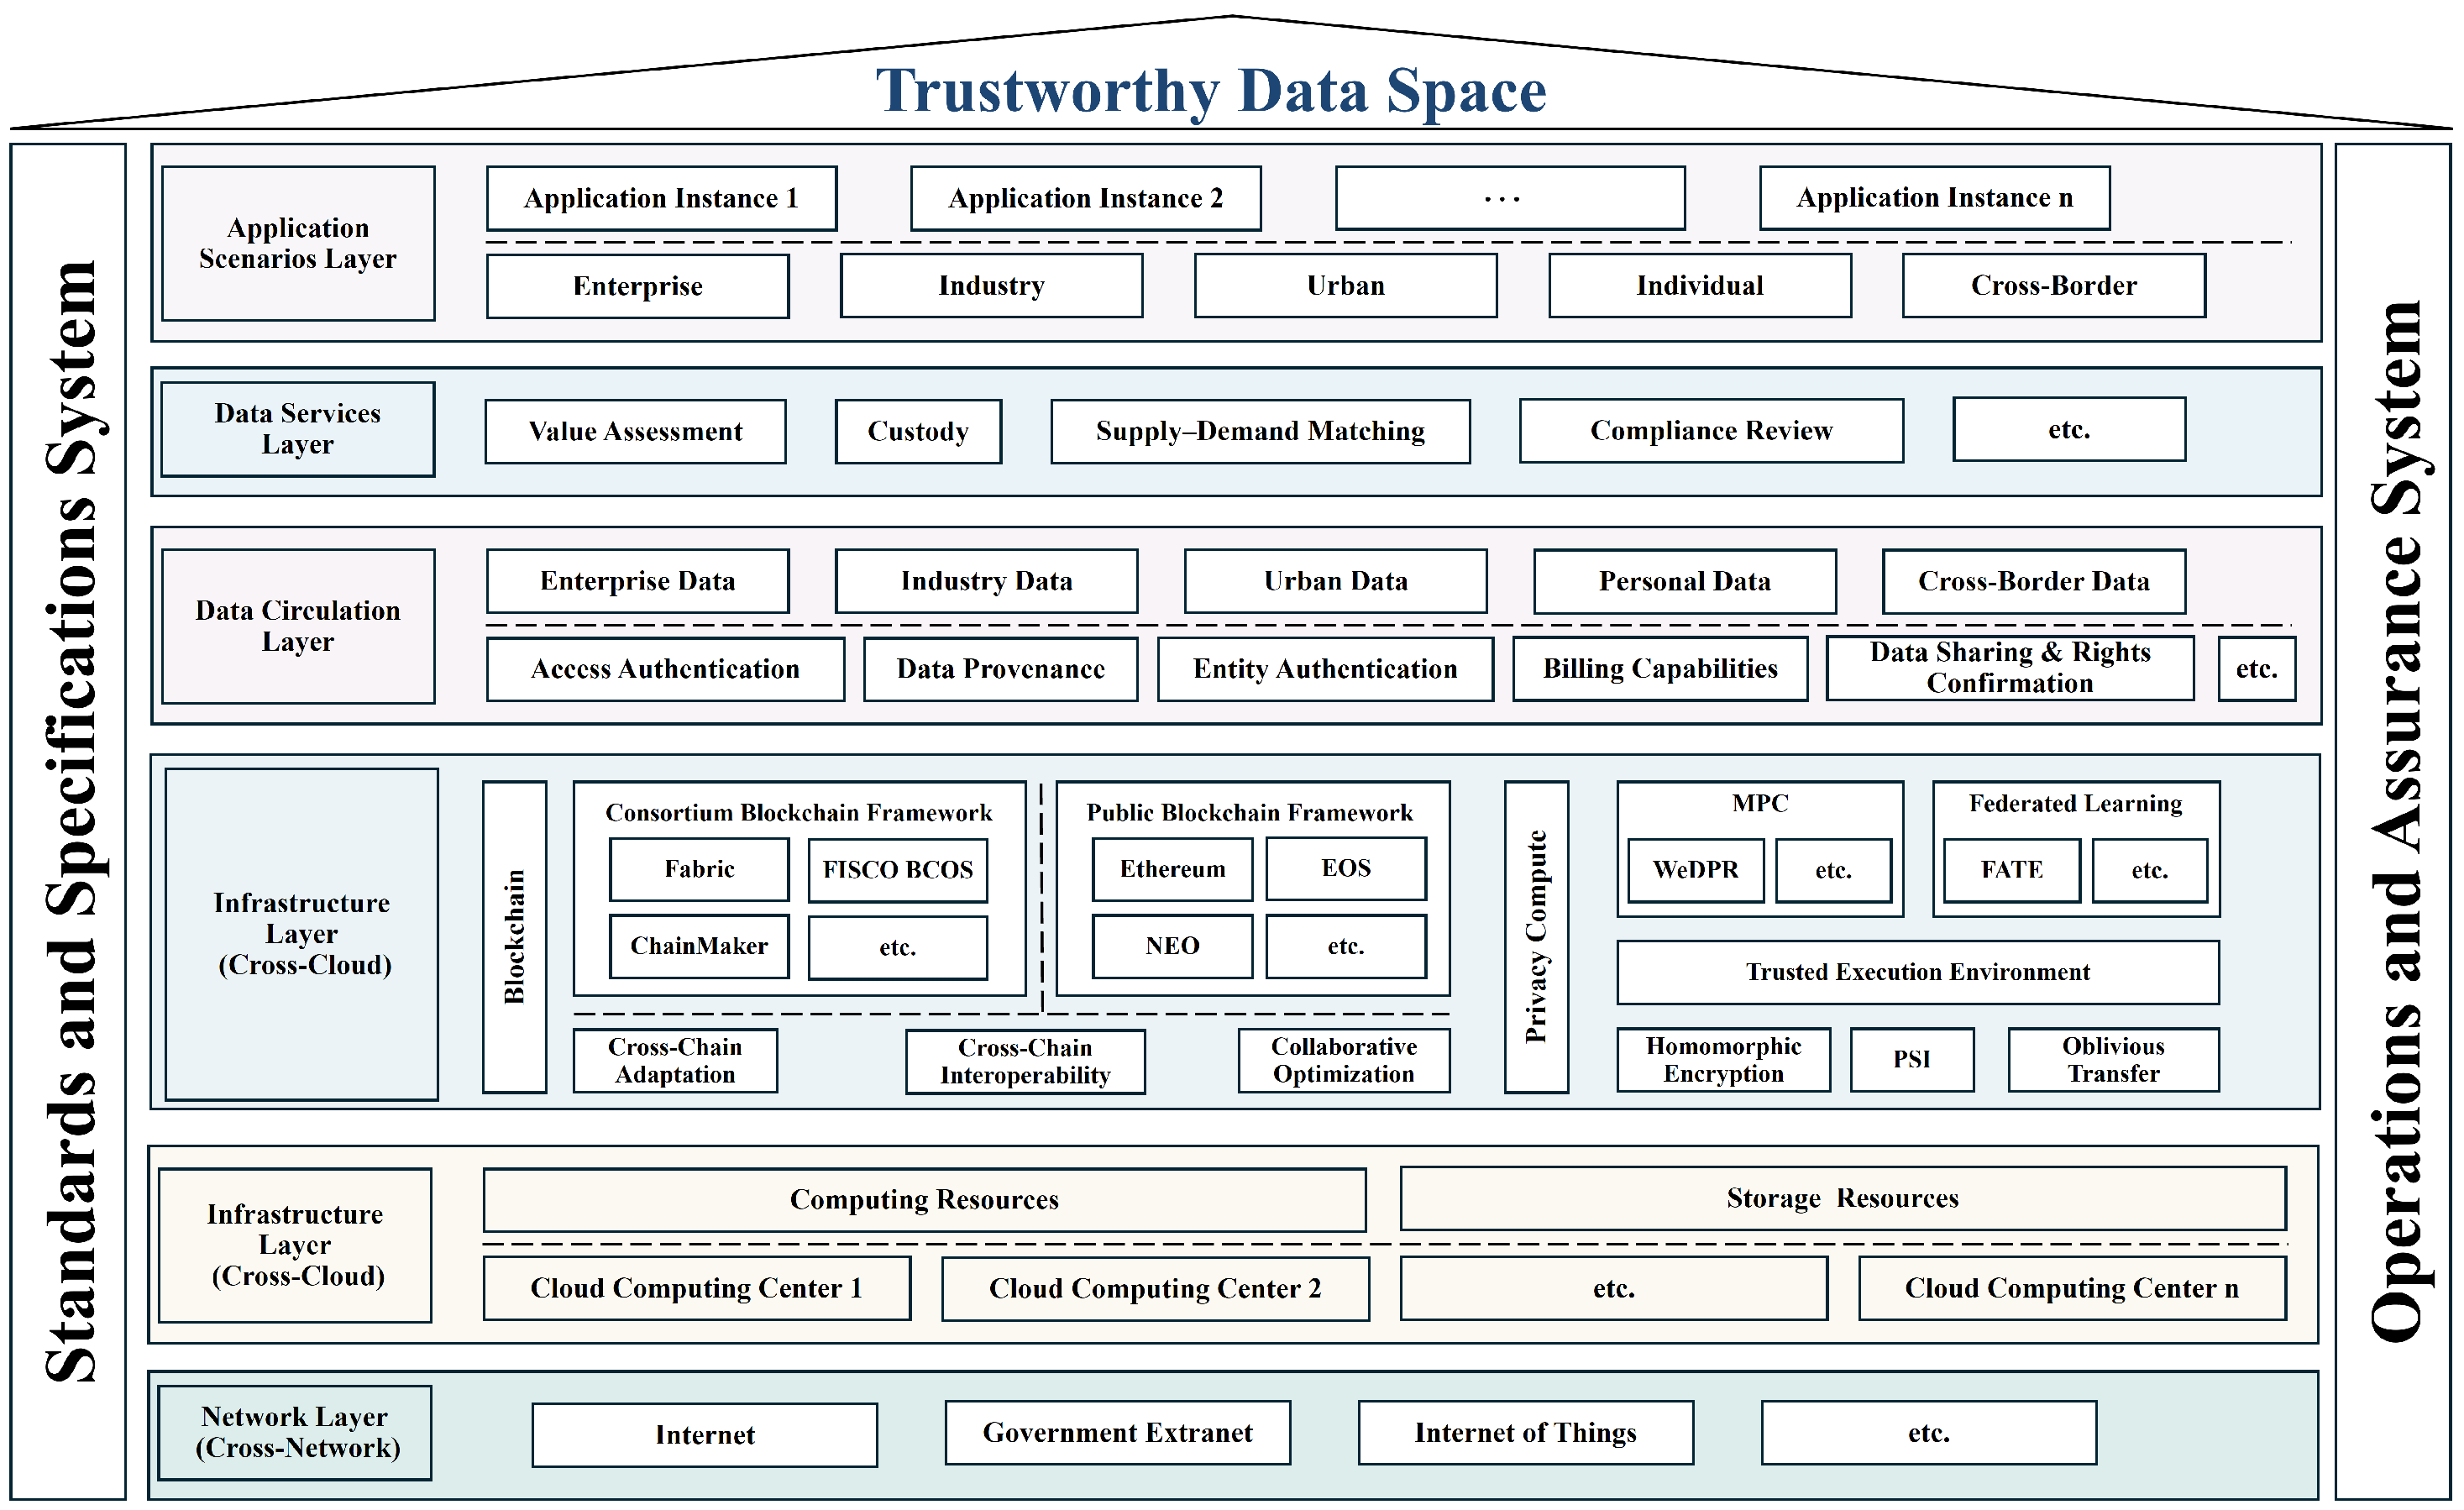
The blockchain [14], as a decentralized, programmable, and tamper-resistant distributed ledger, offers a basic trust mechanism for secure data circulation through consensus algorithms, smart contracts, and verifiable credentials. In a trustworthy data space, the blockchain encodes data fingerprints, access control, and compliance constraints in smart contracts, which can combine with zero-knowledge proof (ZKP) [15] to verify data sources and compliance without exposing sensitive content. Deeply integrating the blockchain and a trustworthy data space establishes a collaborative trust mechanism for cross-border governance and standardization which responds to global data circulation needs and supports the digital economy. While many researchers have discussed trustworthy spaces, there are no recent articles that systematically review its development, summarize the technical framework, and verify key technologies for the application of blockchain technology and trustworthy data spaces. The main contributions of this article are as follows:
- Comprehensively review the development of trustworthy data spaces, systematically reviewing related technologies and the latest research progress;
- Demonstrate the scientific validity of blockchain-enabled trustworthy data spaces, proposing an overall technical framework of “technology convergence, cross-border governance, and standardization path” (TGS) as well as a collaborative trust technology verification scheme of “on-chain light attest, off-chain deep store, and cross-layer verifiable bridge” (LPHS-XV);
- Conduct an empirical evaluation of the LPHS-XV framework based on real-world application cases to verify its effectiveness and feasibility.
The rest of this paper is organized as follows. Section 2 provides the background and current research status of related technologies; Section 3 discusses the proposed framework; Section 4 presents a case analysis; Section 5 summarizes the necessity of the blockchain in the framework; and Section 6 concludes the article and discusses future research directions.
2. Related Works
2.1. Trustworthy Data Space
The trustworthy data space is a new type of infrastructure for cross-organizational and cross-domain data sharing. With data sovereignty and compliance governance as its core goals, it relies on unified standards, trustworthy computing, and audit mechanisms to achieve the secure circulation and value release of data that is “available but invisible, controllable and measurable, and traceable throughout the process”. Its development can be summarized as five stages. The first stage is concept proposal and theoretical exploration, represented by Dataspaces (DSSP), proposed by Michael Franklin et al. [4], and the research focuses on issues such as semantic interoperability, heterogeneous data access, “pay-as-you-go” [16] progressive integration, user feedback-driven query optimization, and data traceability, but it still lacks large-scale industrial verification. The second stage is engineering exploration and multi-field application experiments. Driven by cloud computing and big data applications, prototype systems and pilots for cross-source management have emerged, and progress has been made in semantic index expansion, distributed query optimization, and multi-model data support [17]. The research focus has shifted from pure theoretical research to runnable prototypes and scenario-based verification, emphasizing interoperability, and progressive governance. The third stage is the rise of standardization and data sovereignty, with the landmark events being the gradual formation of the EU International Data Space (IDS) [18] reference architecture and the GAIA-X initiative to promote the European sovereign data space, emphasizing that data is controllable, traceable, and revocable [19]. The concept of the data space has been introduced into smart cities, and the industrial Internet in academia, data sovereignty, trustworthy exchange, and cross-domain security have become key themes. The fourth stage is to explore the integration with trustworthy technologies. There are many places around the world that have successfully established data as a key production factor or strategic resource, promoting the integration of privacy-enhancing technologies (PETs) such as the blockchain, multi-party secure computation (MPC), zero-knowledge proofs, federated learning, and trustworthy execution environments with data space architectures. The research focus has shifted to developing compliance models, auditable processes, and accountability mechanisms that prevent the leakage of sensitive content. However, cross-industry or cross-domain interoperability and standard consistency are still insufficient. The fifth stage is large-scale deployment and cross-border governance, focusing on a unified technology and standard system, as well as interoperability specifications and a consistency assessment and certification framework to build a cross-domain, cross-border trustworthy data circulation network and enable systematic, large-scale implementation. On the engineering side, Feng et al. [20] proposed a secure and fair data transaction model based on the blockchain, coupling decentralized consensus, smart contracts, and access control and cryptography mechanisms to improve transaction transparency, traceability, and privacy protection while also constraining transaction fairness through improved access control and mechanism design. On the governance and interoperability side, Zhang et al. [21] built a trustworthy data space framework for cross-border data circulation, proposed a cross-border data exchange protocol and trust mechanism, emphasized compliance, auditability, and transparent flow under heterogeneous legal domains, and pointed out the challenges brought about by global compliance alignment and policy differences, providing methodological support for standardization, certification, and regulatory coordination. Table 1 shows representative research at each stage.
Table 1.
Representative research at each stage of trustworthy data space.
2.2. Blockchain
Since Satoshi Nakamoto [27] proposed the Bitcoin paradigm in 2008, blockchain technology has developed into a general infrastructure supporting decentralized accounting and multi-party collaborative computing. Its essence is a distributed, decentralized database system that uses cryptography and consensus protocols to link data blocks into a chain structure in chronological order, realizing an undeniable, auditable, and tamper-resistant global ledger [28]. Each block contains a batch of transaction records, a timestamp, and the hash value of the previous block. The chain pointer ensures that any modification to any confirmed block will recursively destroy all subsequent hashes, thereby forming a “high rewrite cost” security under the constraints of economic incentives and consensus rules. The hash function is the foundation of the blockchain. Equation (1) shows the SHA-256 hash algorithm commonly used in blockchain:
where . The Merkle tree is used to verify transactions. The calculation process is shown in Equation (2):
where is the hash of the mth node on the jth layer and is the byte string concatenation operator. Table 2 shows the development of blockchain technology.
Table 2.
The development of blockchain technology.
2.3. Zero-Knowledge Proof (ZKP)
The ZKP concept was originally proposed by Goldwasser, Micali, and Rackoff in 1985 [38]. In ZKP, the prover can convince the verifier that a statement is true but will not reveal any additional information other than the fact that the statement is true. Based on the interaction method, ZKP can be divided into two categories, namely interactive ZKP, which requires the prover and verifier to repeatedly exchange multiple rounds of messages such as challenges and responses, and non-interactive ZKP (NIZKP), which can provide a proof once under certain public randomness assumptions and allow the verifier to complete the verification without interaction. Any zero-knowledge proof protocol must meet the following core properties:
- (1)
- Completeness: If the claim is true, then an honest prover who follows the protocol will eventually convince an honest verifier to accept the claim. For a true proposition, a correctly implemented protocol will not cause a reliable verifier to mistakenly judge it as false.
- (2)
- Reliability: If the claim is false, then no matter how the prover cheats, it is almost impossible to make the honest verifier accept the false claim. By designing a soundness error, the probability of successful cheating can be quickly reduced to a negligible level under repeated execution of the protocol.
- (3)
- Zero knowledge: If the claim is true, then the verifier will not obtain any additional information about the secret during the verification process except the conclusion that the claim is true. The verifier cannot learn the secret itself afterward, nor can it use the details of the proof to persuade a third party of the claim.
After years of development, ZKP protocols have evolved into a variety of protocols with distinct characteristics. Table 3 shows the characteristics of different ZKP protocols.
Table 3.
Comparison of zero-knowledge proof protocol types.
Furthermore, ZKPs have demonstrated significant practical value in a variety of fields. For example, ZKPs are used in medical and financial data sharing to ensure “data proves truth without revealing it” [48]; in IoT and privacy-preserving AI (privacy-aware AI), ZKPs are used to verify device behavior and algorithmic fairness [49,50]; and in legal and government affairs, ZKPs are used to achieve a balance between transparency and privacy protection [51]. Furthermore, ZKP technology itself is constantly advancing, with new proof systems and optimization frameworks emerging [52,53]. It is foreseeable that zero-knowledge proofs will become an indispensable component of the trust infrastructure of a digital society, providing strong technical support for ensuring security and privacy.
2.4. Federated Learning
The core concept of federated learning is to train models on decentralized data [54], leveraging multi-party collaboration to train a global model without centrally sharing raw data. Classic federated learning uses a central server to coordinate multiple clients. Under this coordination, client-side devices or independent organizations (clients) jointly train a model while keeping their training data locally stored. In each iteration, clients compute model updates (e.g., gradients or parameters) using local data and aggregate them to the server, which updates the global model. Only model parameters or gradients are communicated between the client and server. Raw data never leaves the local machine, enabling a deep learning paradigm in which data is available but invisible.
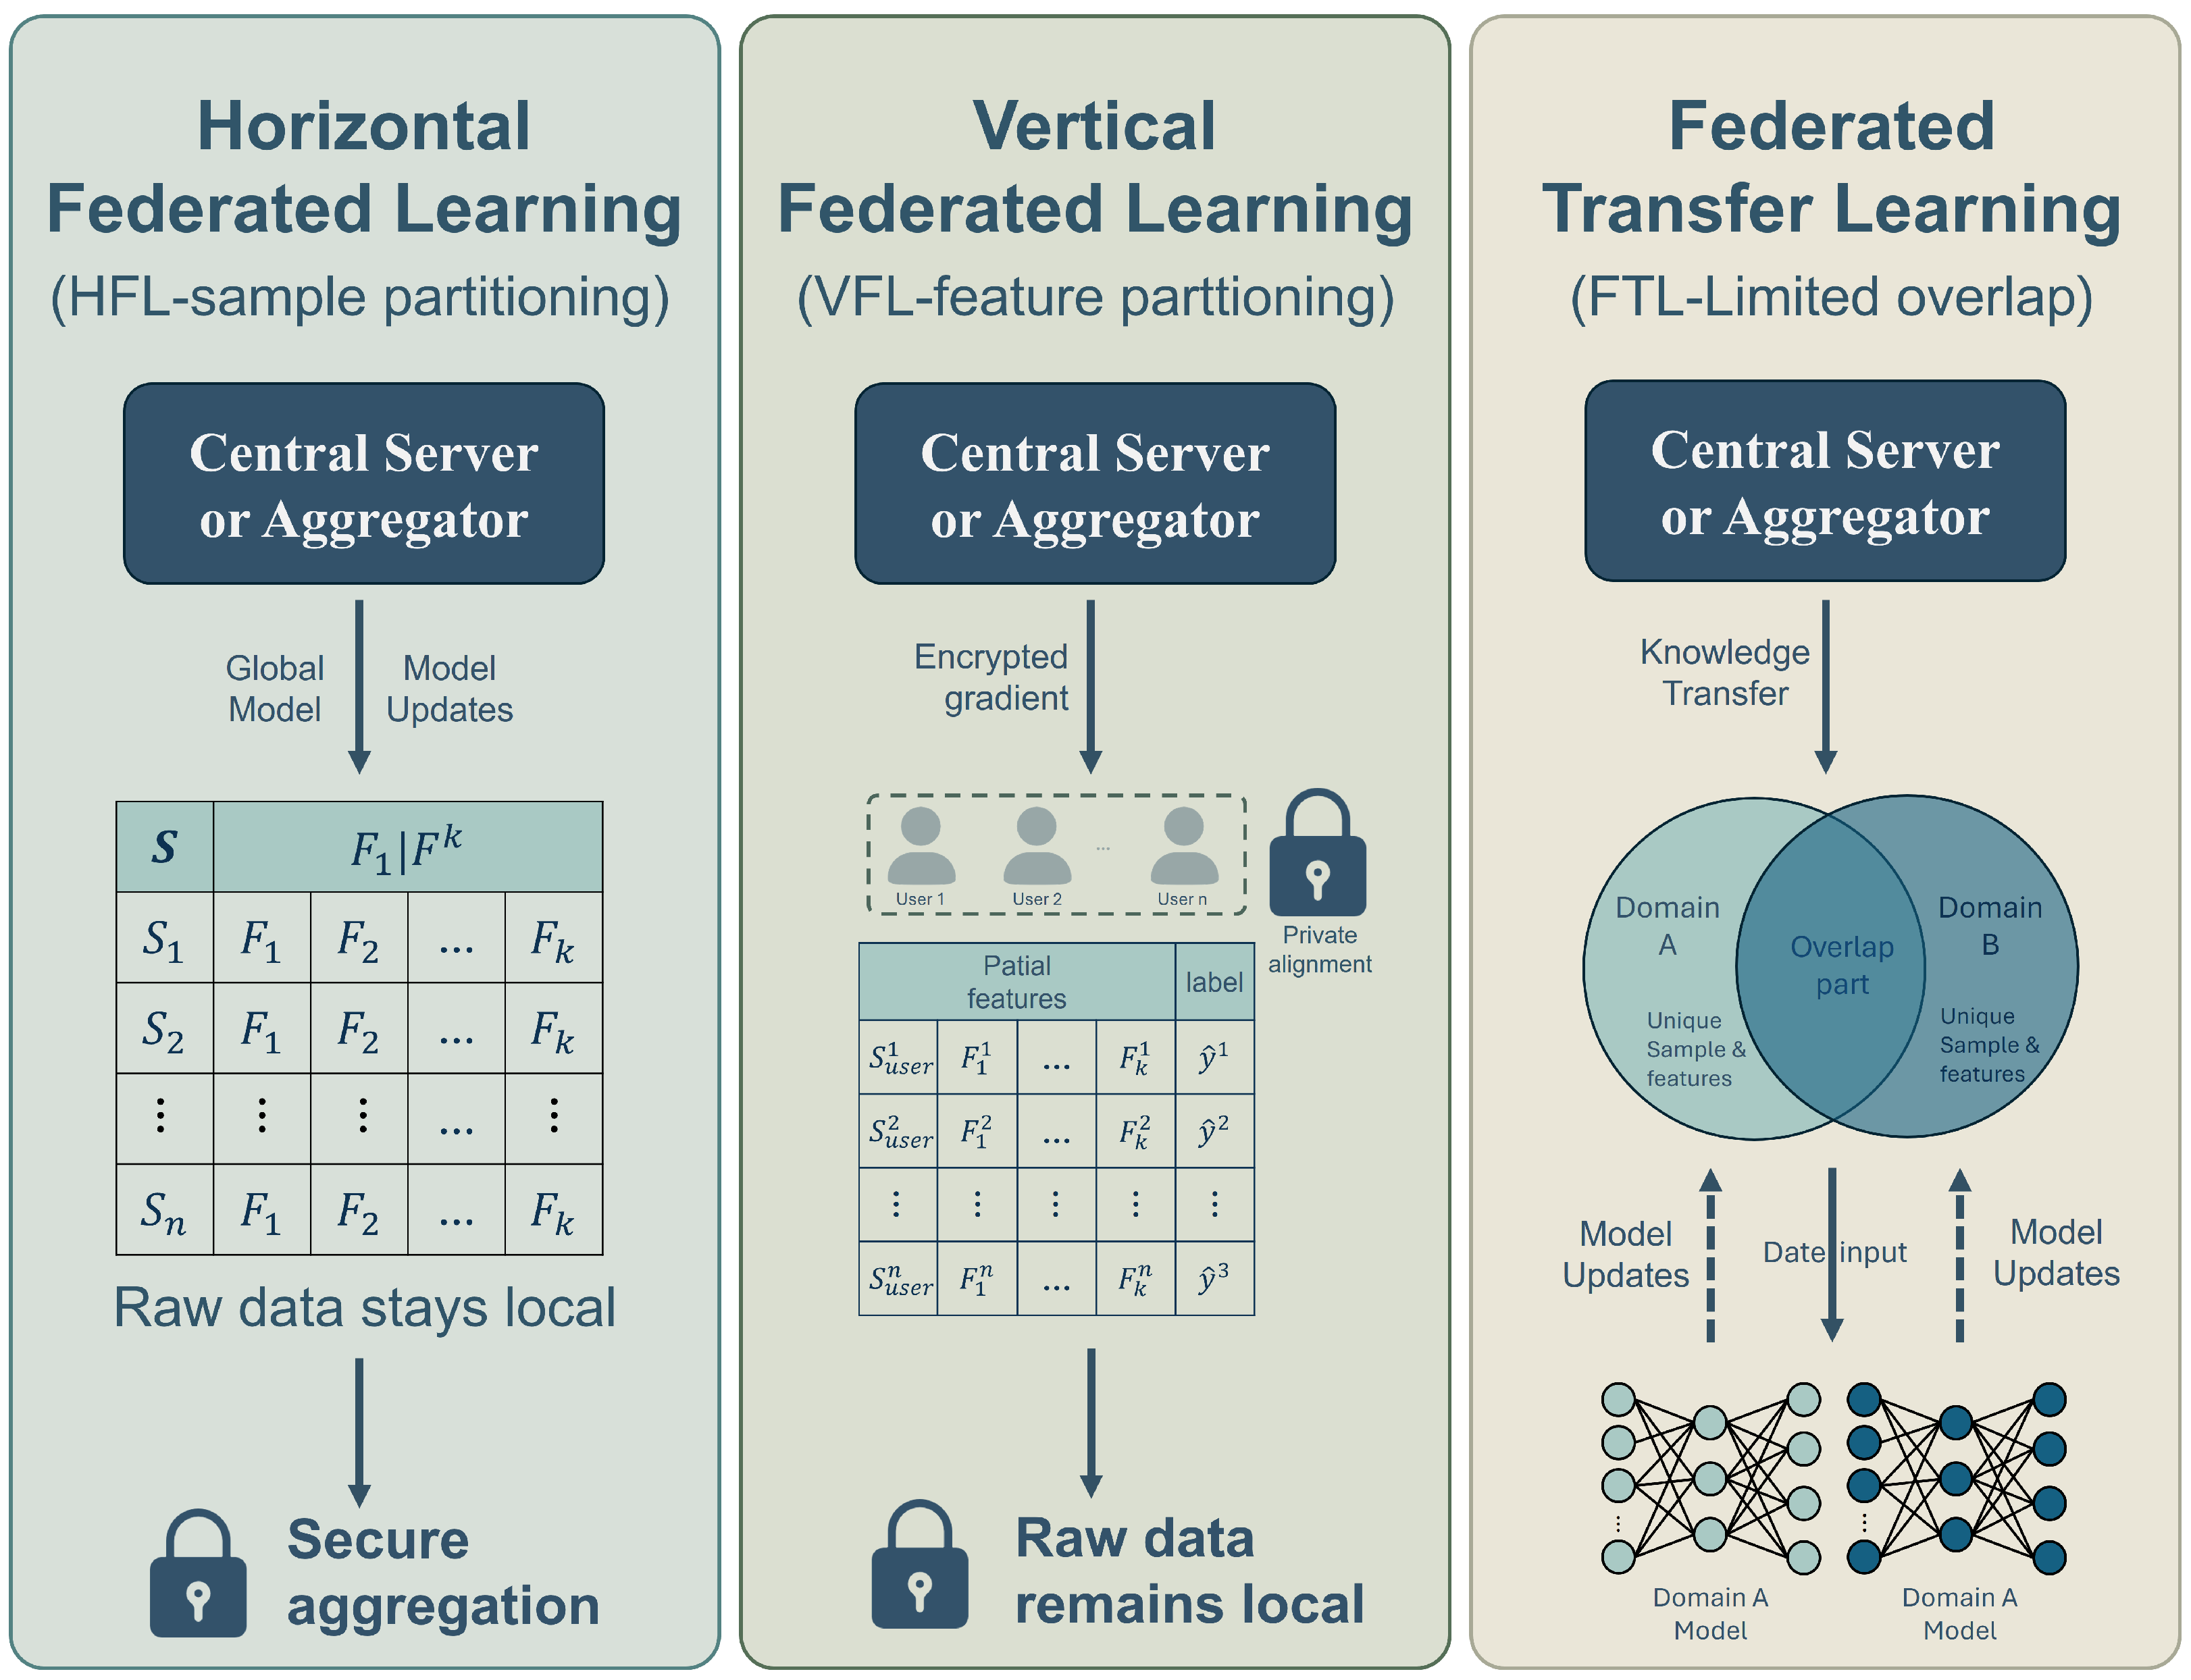
Based on the differences in the distribution of data between participants in the sample space and feature space, Yang et al. [55] classified federated learning into three categories in 2019: horizontal federated learning, vertical federated learning, and federated transfer learning, as shown in Figure 2. (1) Horizontal federated learning is applicable to scenarios where the data of each participant has the same feature space but different user sample sets. Different clients have the same type of features but serve different groups of users. For example, two banking institutions in different geographical regions have similar businesses and therefore the same data feature structure. In this case, if joint modeling is desired, the model updates are calculated locally, and then the parameters are uploaded through a secure protocol and aggregated on the server to obtain a global model with good performance [56]. Most cross-device scenarios (such as mobile keyboard applications or smart applications on mobile devices) belong to horizontal federated learning. Currently, horizontal federated learning is widely used in fields such as mobile terminal intelligence [57] and recommendation systems [58]. (2) Vertical federated learning is applicable to situations where the participants have the same user samples but different feature spaces. Hardy et al. [59] and Nock et al. [60] were the first to propose a federated learning scheme based on vertically divided data in 2017 and 2018, respectively, to train logistic regression models in a privacy-preserving manner. This situation is common when different institutions have different dimensional information on the same objects. For example, a bank and an e-commerce company may have a large number of common users in the same city, but the bank holds data on users’ financial credit, consumer behavior, etc., while the e-commerce company holds data on users’ browsing and purchase history. In this case, if the institutions want to jointly build a model, they can cooperate to train the model according to the feature dimension without exposing their original features, rather than integrating the data of both parties. Vertical federated learning has important application value in fields such as financial risk control [61] and medical multimodal data fusion [62] that require cross-institutional data complementarity. (3) When the data from participants has little overlap across both user samples and features, and the sample and feature spaces are different, federated transfer learning can be used. In this scenario, the user groups of each participant rarely overlap, and the business characteristics are also quite different, but they may share some related tasks [63], such as a bank in China and an e-commerce company in the United States. Due to differences in geographic regions, user groups have little overlap, and the businesses are different. Only a small part of the feature space of both parties is common. At this time, neither horizontal nor vertical federated learning is applicable. However, with the help of transfer learning, the limited overlapping data between the two parties can be projected into a common representation space and then applied to each other’s data to predict user behavior. Currently, federated transfer learning has shown significant potential for cross-border and cross-domain joint risk control [64], medical [65] tasks, and other applications, and it has also been used in cutting-edge explorations such as large-scale model federated fine-tuning [66].
Figure 2.
Diagram of three types of federated learning.
To promote the research and application of federated learning, industry and academia have released a variety of open-source frameworks and toolkits. For example, in 2019, Google released TensorFlow Federated (TFF) for simulating and implementing federated learning algorithms. Facebook’s open-source project PySyft supports the development of federated learning and differential privacy. China’s WeBank developed Federated AI Technology Enabler (FATE) for enterprise applications. Alibaba released the FederatedScope-LLM framework for fine-tuning large models, fully supporting a complete end-to-end benchmarking process and various inference demonstrations. Table 4 lists the framework’s source code.
Table 4.
Source code links for federated learning frameworks.
3. Framework of Technology-Governance-Standardization (TGS)
3.1. Technology Integration
3.1.1. Ensuring Data Privacy and Controllable Circulation
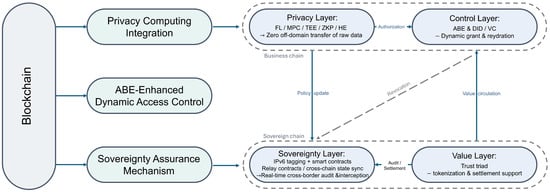
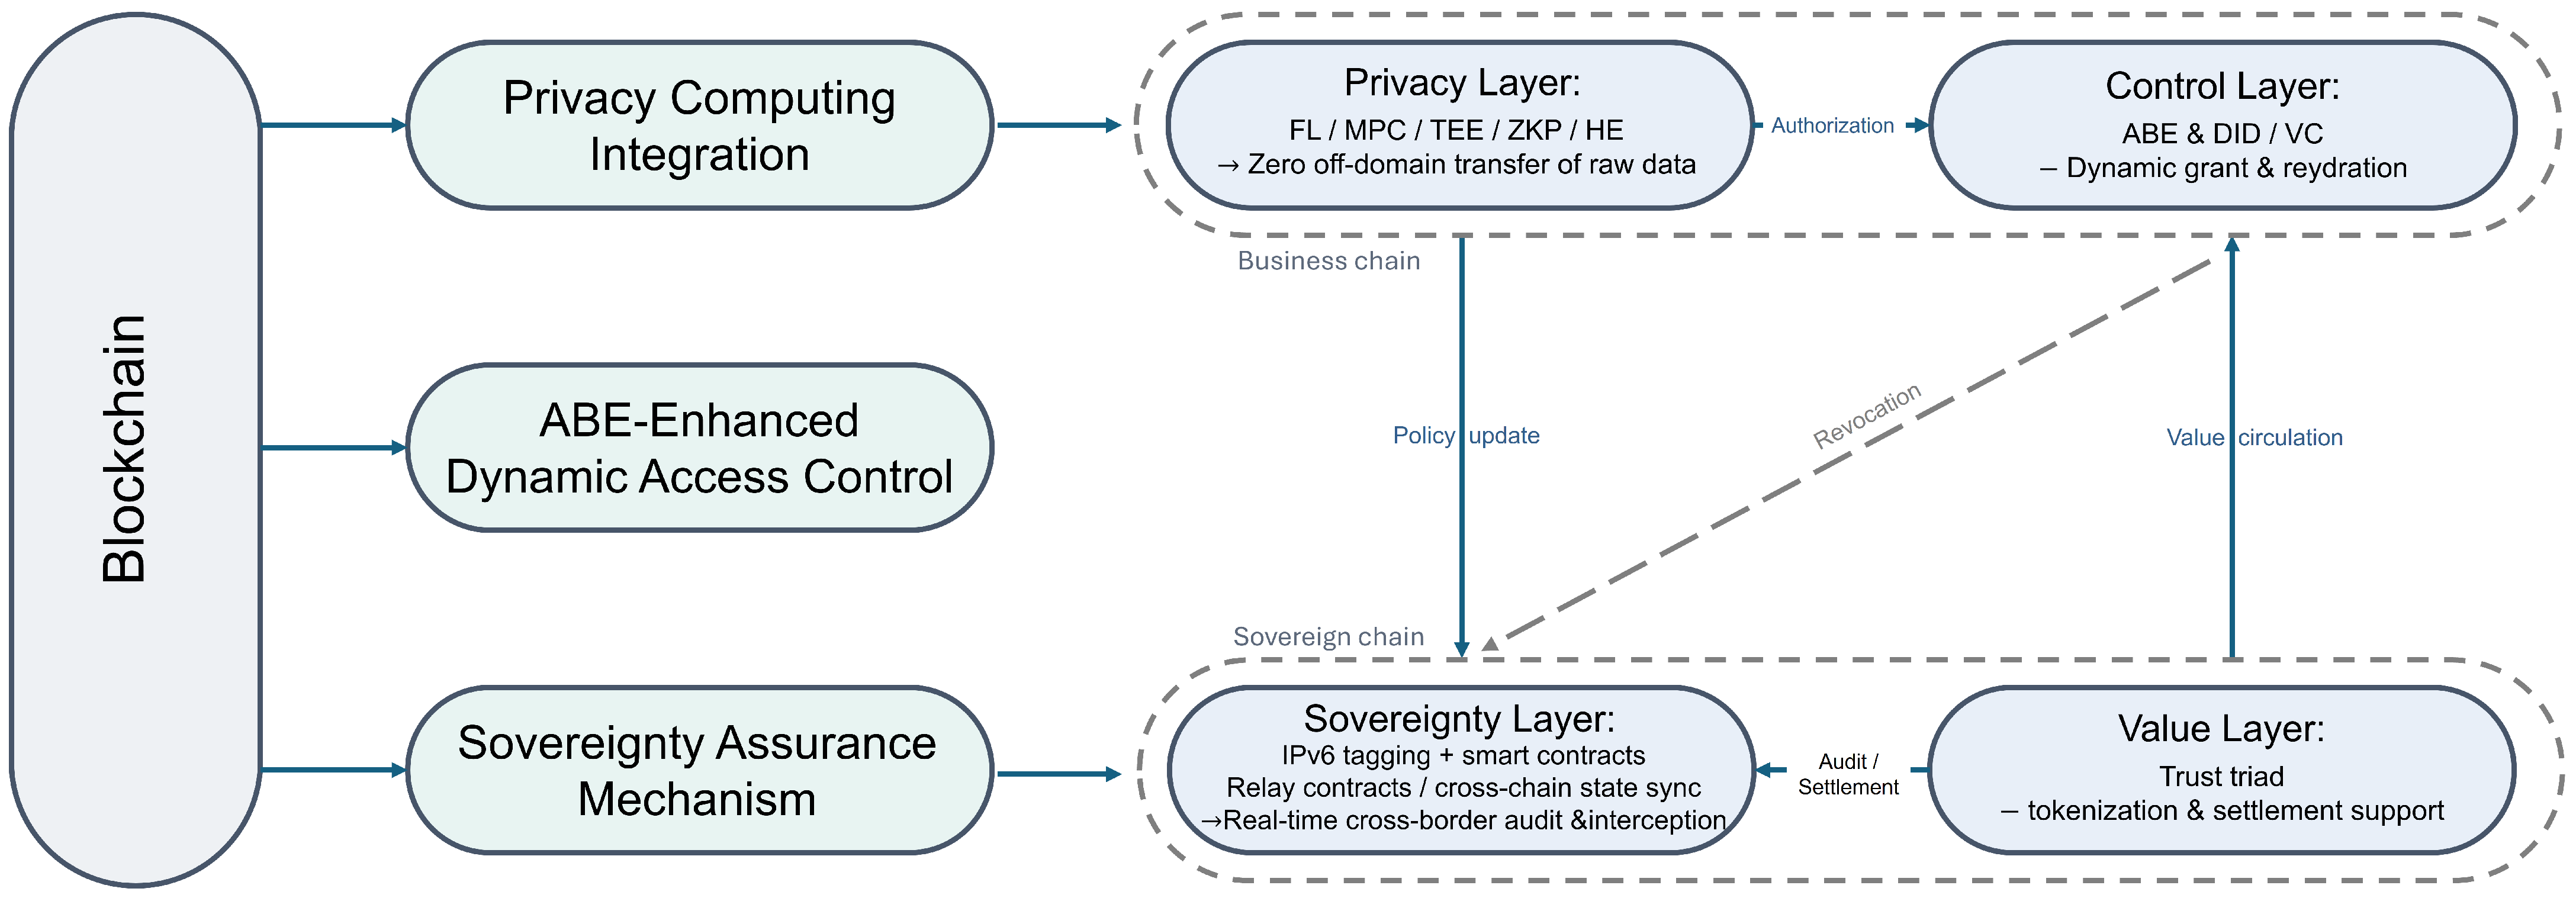
In the trustworthy data space, the blockchain must work in tandem with privacy-preserving computing, decentralized identity, and cross-chain protocols. First, by utilizing privacy-preserving computing technologies such as zero-knowledge proofs, secure multi-party computation, and federated learning, the raw data remains local, with only encrypted features processed and the results calculated on-chain [67]. This ensures that the data remains “available but invisible” [68]. Second, decentralized identity generates verifiable credentials for data and entities, registering ownership and authorization policies on-chain for dynamic control [69]. Finally, relay contracts and cross-chain protocols synchronize states across multiple chains, allowing business and sovereign chains to instantly adjust permissions in response to policy updates, forming a complete closed loop of authorization, computation, auditing, and recovery [70]. Figure 3 shows the blockchain collaborative privacy computing and trustworthy data space cross-chain governance architecture.
Figure 3.
Blockchain collaborative privacy computing and trustworthy data space cross-chain governance architecture.
3.1.2. Cross-Domain Operation and Circulation Realization
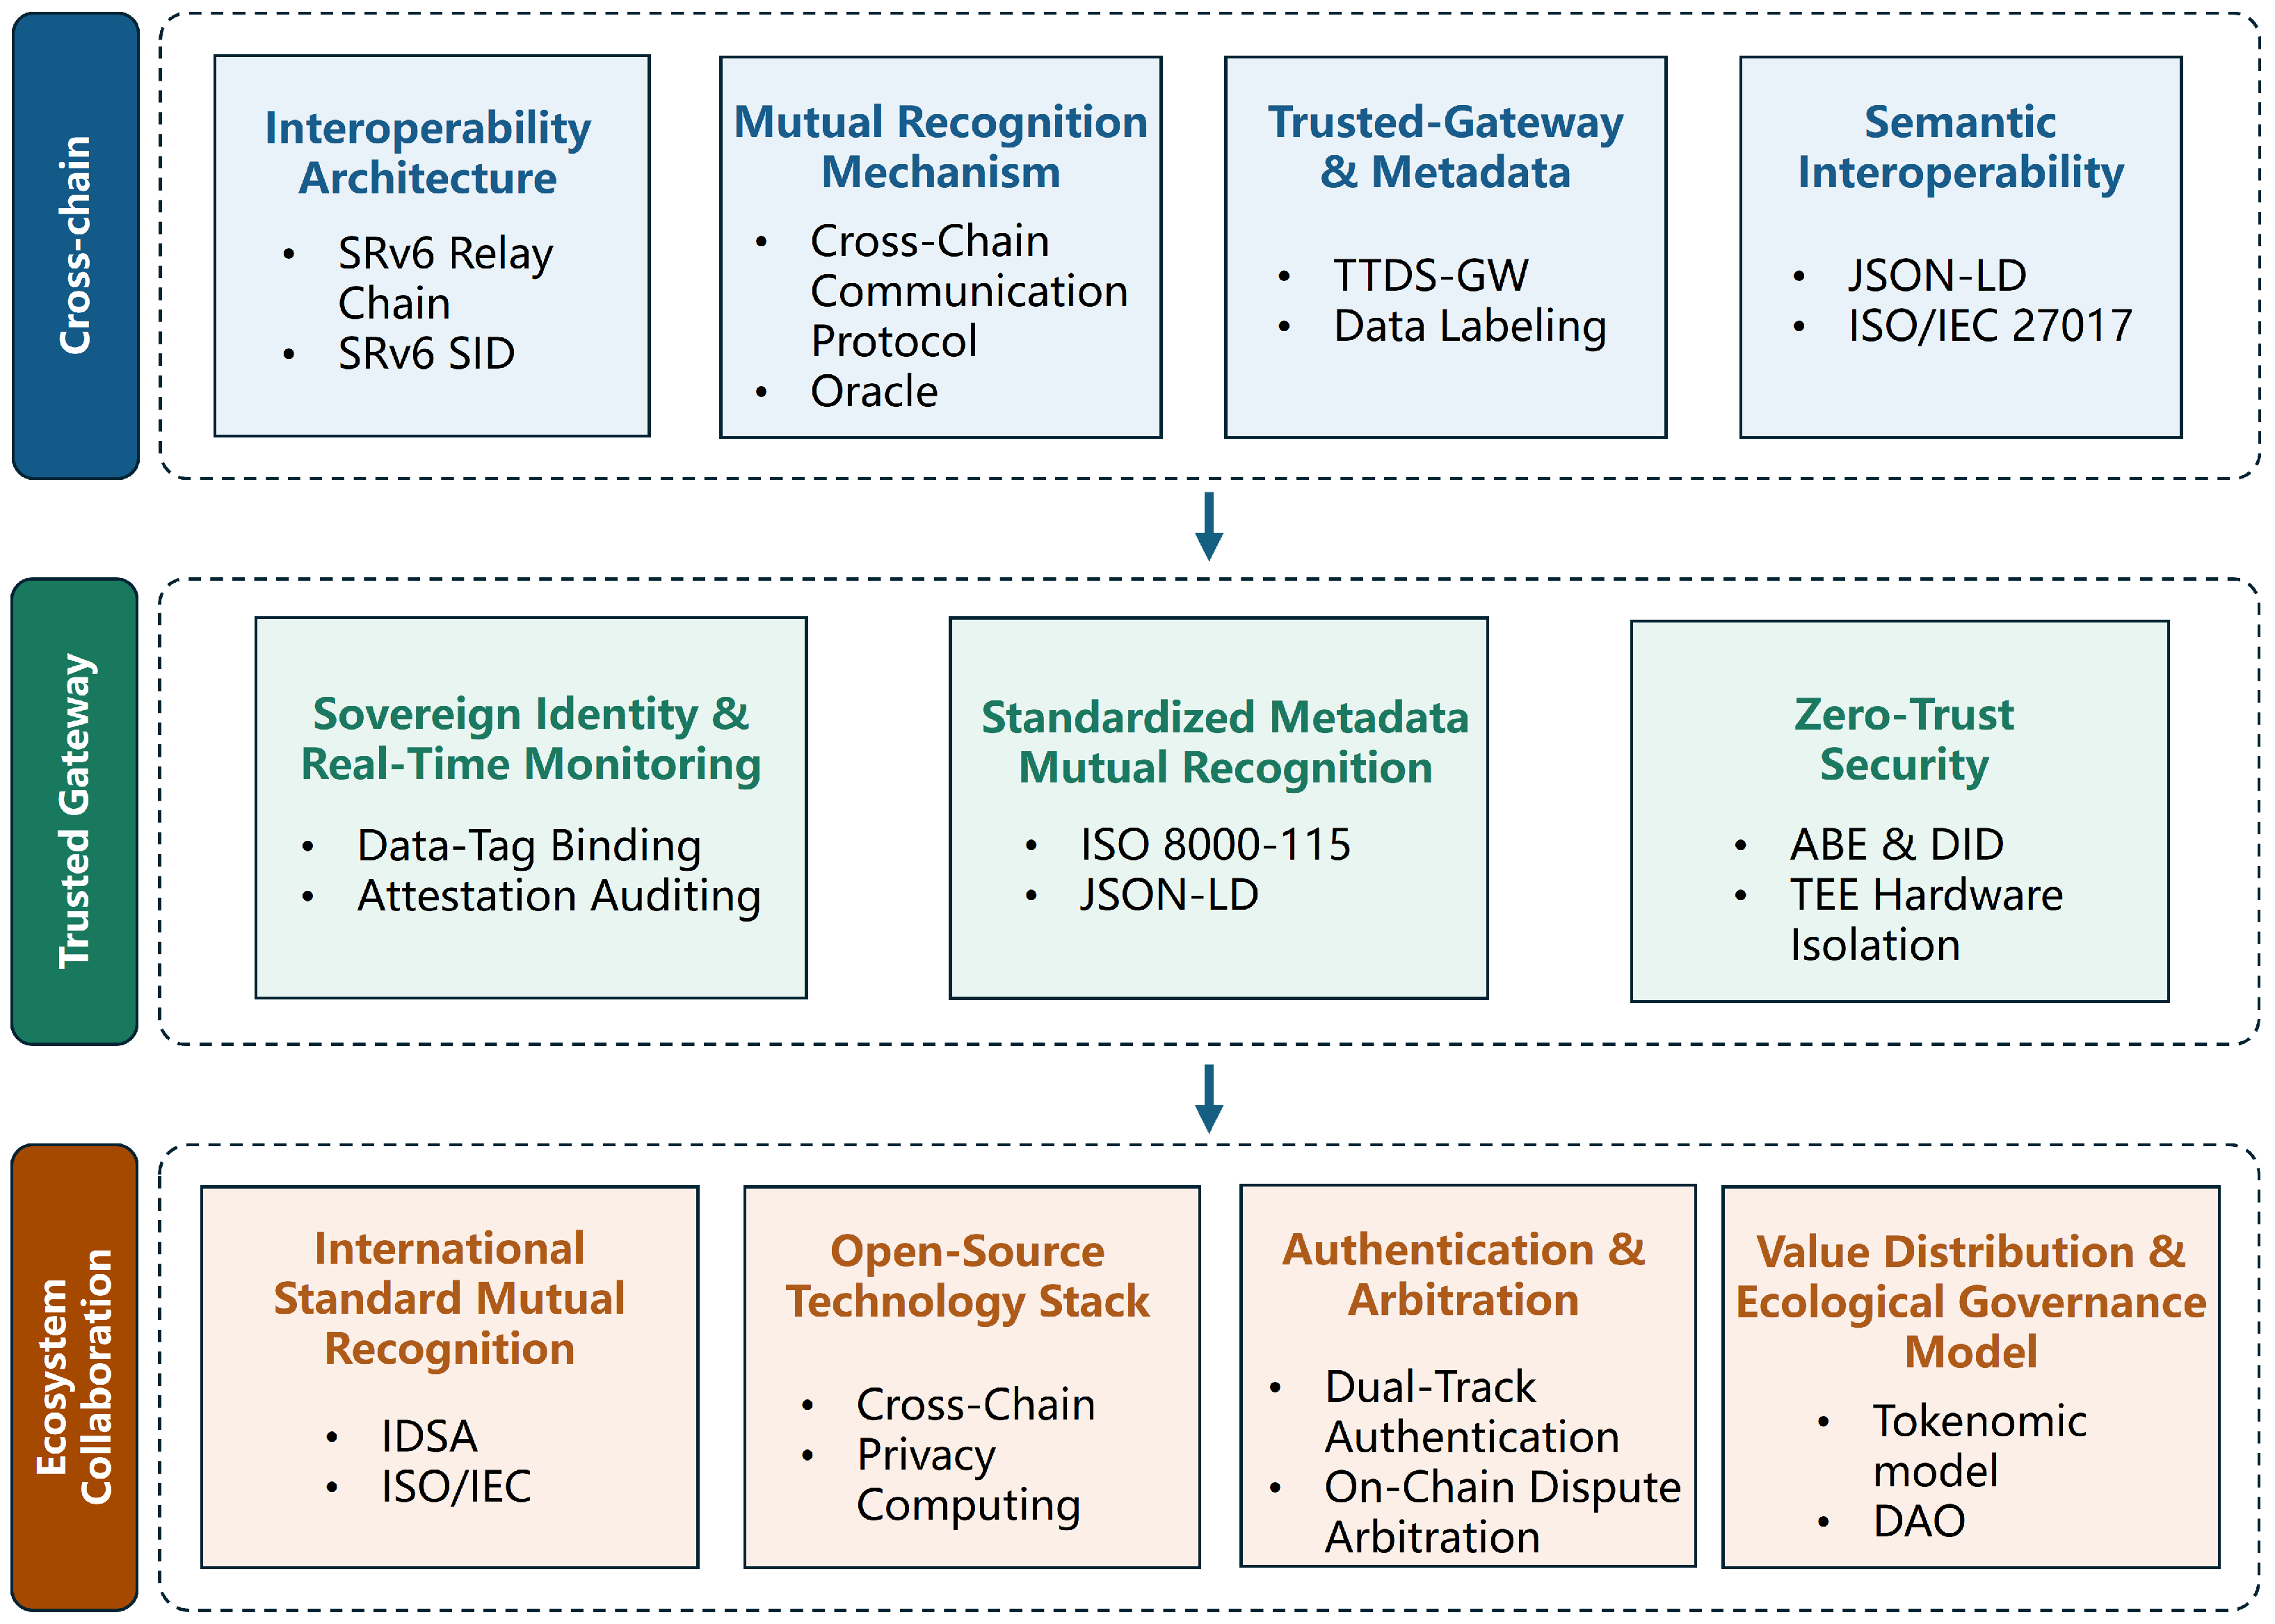
To address interoperability issues across heterogeneous data spaces, the “SRv6 relay chain, cross-chain protocol, and standardized interface” solution can be used to encapsulate routing, path tracing, and transaction instructions in IPv6 routing headers, thereby enabling efficient scheduling across heterogeneous chains. It also integrates the IDSA connector and JSON LD semantic model to unify data formats and meta-semantics, adopts an open architecture of “an open architecture comprising one basic network, one capability platform, one operations-and-maintenance center, and N applications”, and connects to standards such as ISO 8000 115 [71] and ISO/IEC 27017 [72] to establish an interoperability framework at the “identification-contract-audit” layer, thereby providing cross-domain data elements with the global circulation capability of “technically verifiable, protocol standardized, and ecologically open”. Its overall architecture is shown in Figure 4.
Figure 4.
Cross-domain data flow architecture.
3.1.3. Strengthening Traceability and Auditing
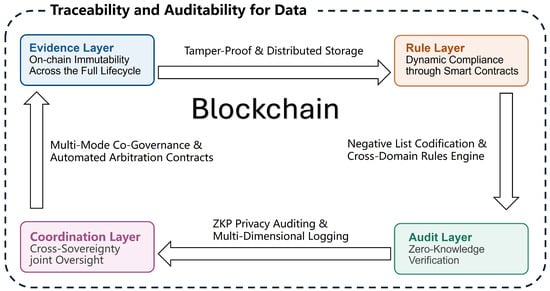
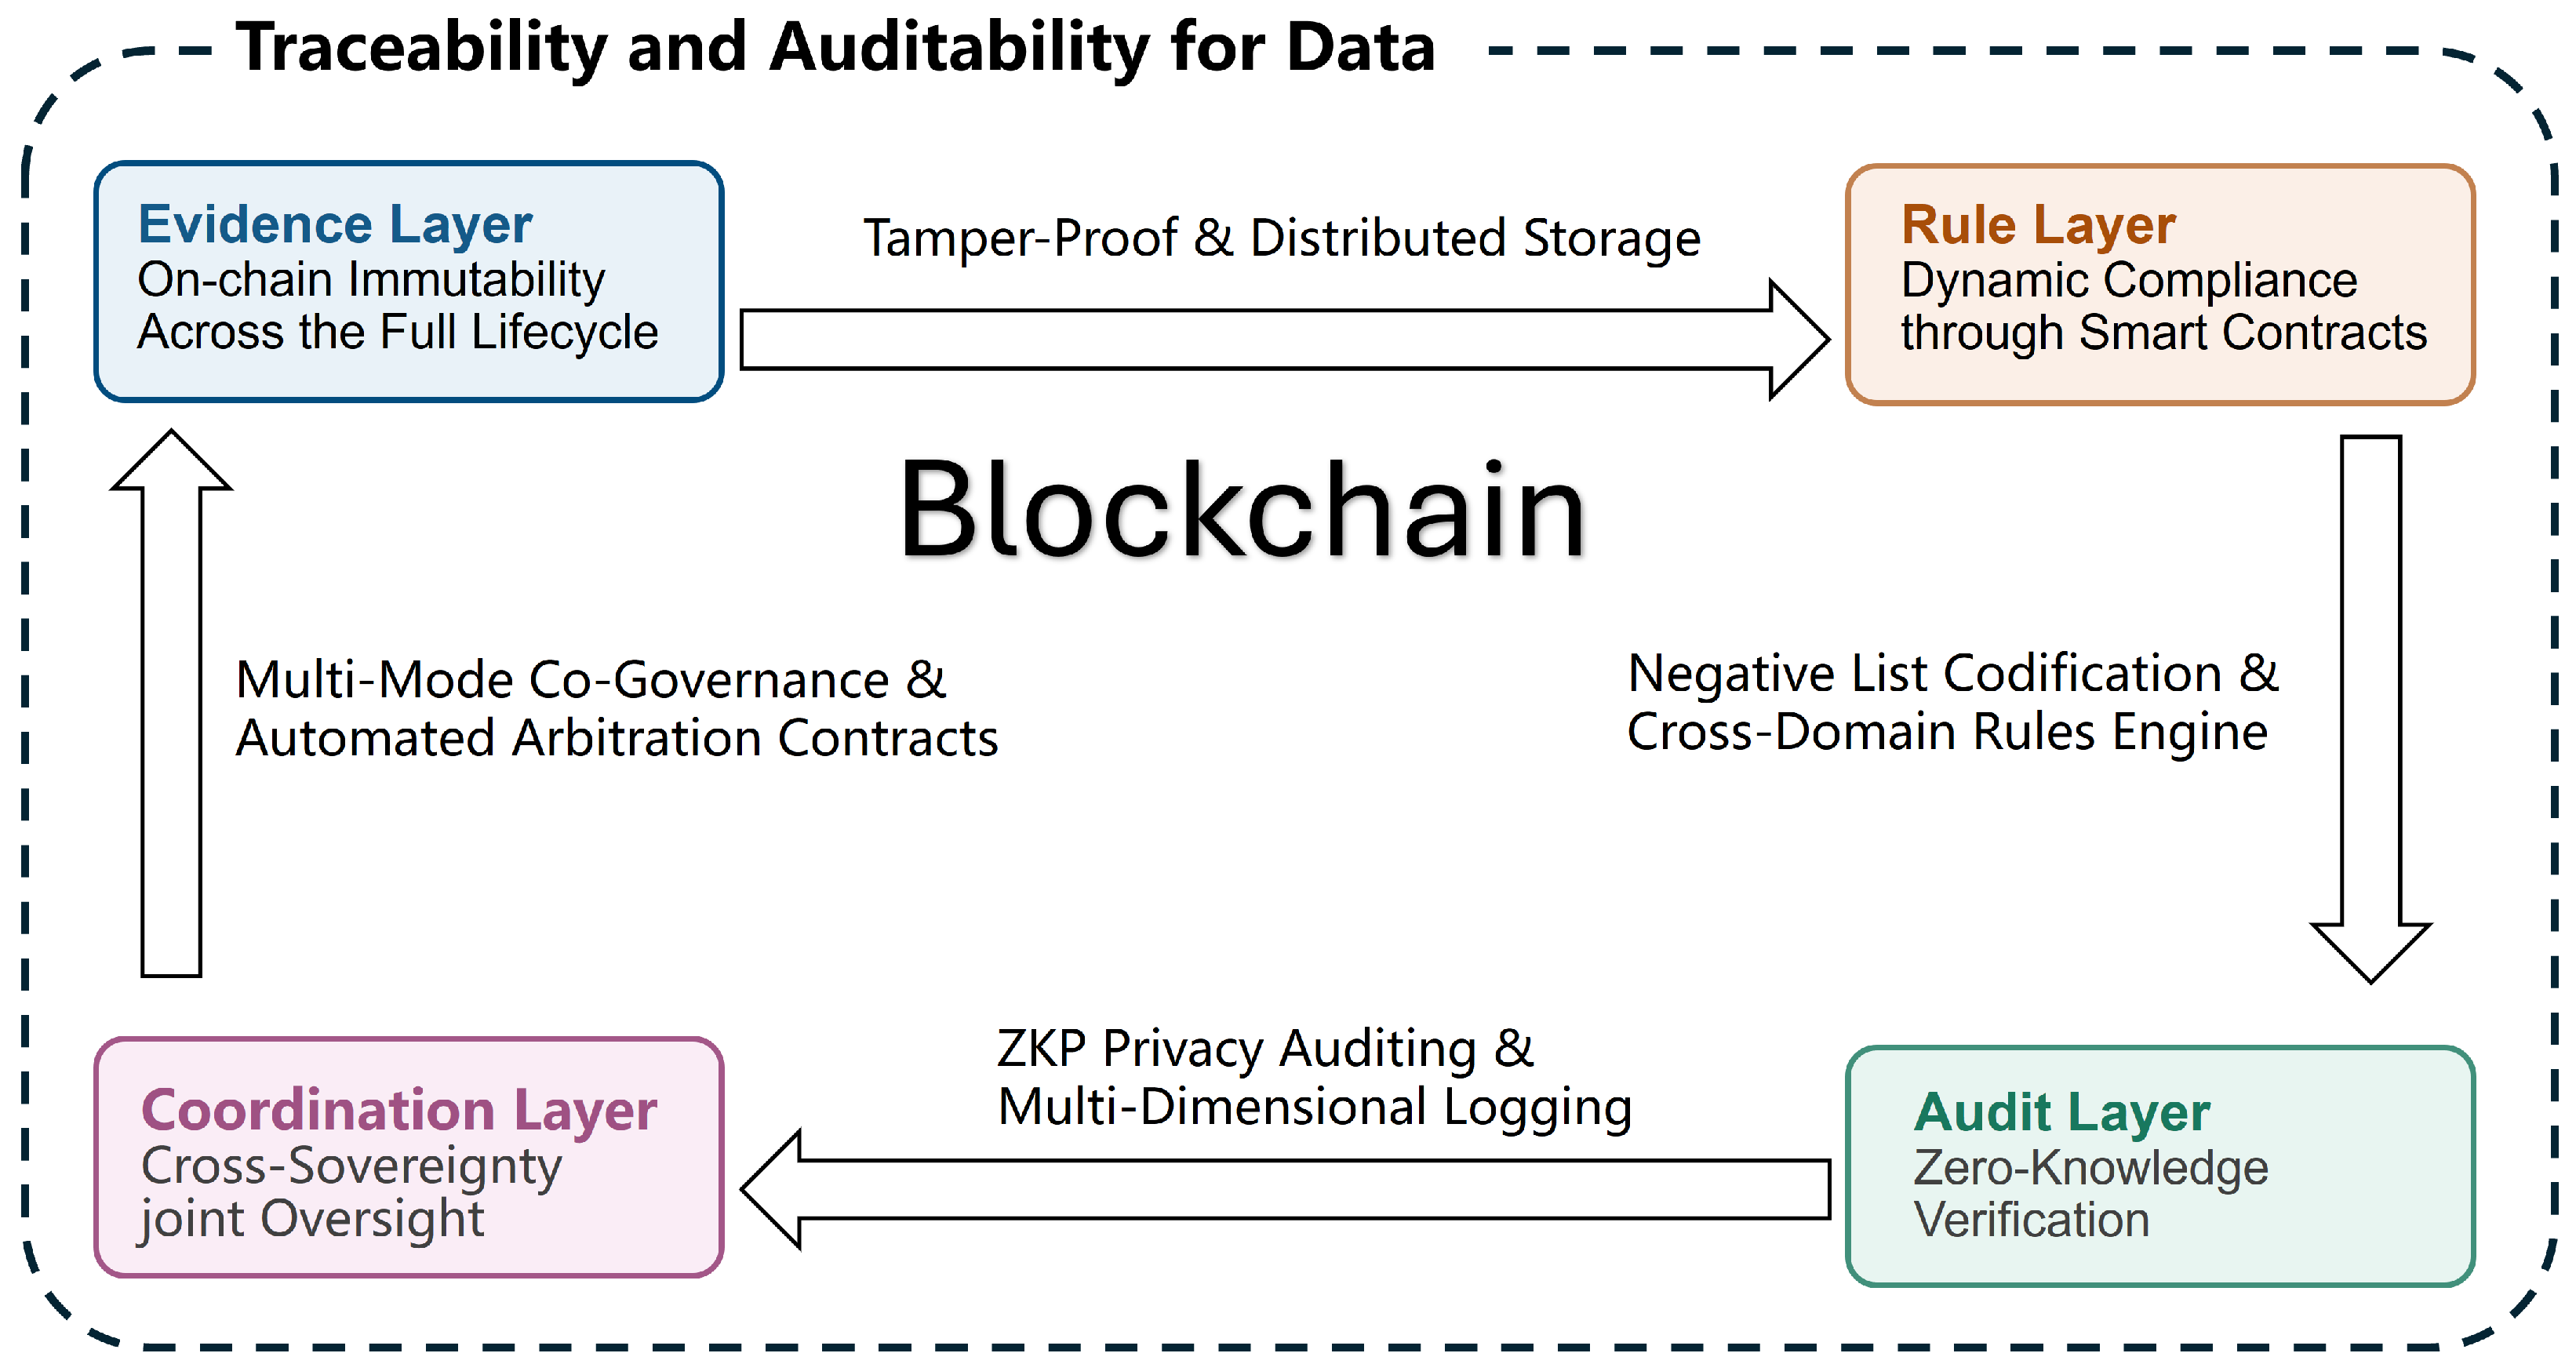
The blockchain naturally supports traceability and auditing, but in the trustworthy data space, it is necessary to further build a comprehensive, four-layer, closed-loop security framework with “full traceability, real-time blocking of violations, audit verification, and cross-domain joint investigation”. Its architecture is shown in Figure 5.
Figure 5.
Cross-domain data traceability and auditing architecture.
Among them, the evidence layer, rule layer, audit layer, and collaboration layer undertake the following specific functions:
- (1)
- Evidence layer: The entire life cycle of data generation, circulation, use, and extinction is recorded through the blockchain, and distributed storage is used to save the original data, achieving traceability in seconds.
- (2)
- Rule layer: Smart contracts embed data classification strategies and negative lists into the code and use natural language processing to parse legal provisions to generate executable compliance templates.
- (3)
- Audit layer: A zero-knowledge proof is used to verify whether data operations comply with policies, and SRv6 traffic labels and on-chain evidence are combined to form a visual audit map and realize multi-dimensional log analysis.
- (4)
- Collaboration layer: Regulatory agencies are introduced as authoritative nodes, multi-party co-governance and automated execution of arbitration contracts, and dispute resolution using verifiable credentials.
3.2. Cross-Border Data Governance
Currently, cross-border data governance faces three major structural barriers. The first is the conflict of sovereignty and compliance; there are contradictions between the legal provisions of different countries. For example, the “adequacy determination” under the EU GDPR conflicts with the data localization requirements of the “Data Security Law of the People’s Republic of China” [73]. It is necessary to ensure compliance while guaranteeing the free flow of data. The second is the fragmentation of the technology ecosystem; different regions use different encryption algorithms, identity formats, and cross-chain protocols [12,74], resulting in poor system interoperability, such as the lack of mutual recognition between W3C DID and SM2 as well as the Cosmos IBC and BaaS platforms in China. The third is the judicial enforcement vacuum; cross-border disputes arising from smart contract loopholes lacking a unified legal framework and arbitration mechanism, and there is no consensus on how on-chain electronic evidence should be recognized across jurisdictions.
To address the above issues, we need to advance in a coordinated manner across the system, technology, and scenario perspectives. For example, regarding mutual recognition of rules, we can establish a mutual recognition framework through bilateral or multilateral agreements and transform conflicting clauses in the GDPR and the “Data Security Law of the People’s Republic of China” into enforceable smart contract rules. In terms of technical standard alignment, we can rely on the architecture of the international data space association (IDSA) [75], adopt international standards such as W3C DID [76] and ISO 27017 [77], and use open-source cross-chain gateways (such as WeCross) to reduce protocol adaptation costs and achieve mutual recognition of identity, encryption, and cross-chain protocols. In terms of collaborative innovation, a cross-border regulatory sandbox alliance will be established to test dynamic negative lists and joint risk control models in scenarios such as vehicle-road-cloud and real-world assets (RWAs), thereby promoting institutional iteration by isolating policy risks.
3.3. Standardized Path
The lack of standards mainly causes two problems. First, fragmented interfaces and protocols lead to poor cross-platform interoperability. This results in inconsistent data formats, transmission protocols, and semantic definitions. Development and maintenance costs also increase. Second, the compliance framework is vague, and there is no unified certification mechanism. Companies must repeatedly adapt to conflicting rules across jurisdictions, which greatly increases compliance costs. The absence of guidelines for sensitive data classification makes it difficult to deploy dynamic negative lists at scale.
Recent advances in the standardization of blockchain-driven trustworthy data spaces have yielded four pivotal developments:
- (1)
- Technical layer standards: These focus on making different computer systems work together, especially concerning digital identity, connecting different blockchains, and protecting private information. For digital identity, the standards combine W3C decentralized identifiers (DIDs) [78], a secure way to represent users online, with SM2, a cryptographic algorithm. Developments in connecting blockchains have been made by joining the Cosmos Inter-Blockchain Communication (IBC) protocol with enterprise platforms that offer blockchain services. Privacy-focused systems now also provide ways for different computers to work together securely using trusted execution environments (TEEs), which protect data even when it is in use, and federated learning, where multiple systems can analyze data together without sharing sensitive information.
- (2)
- Data layer standards: These standards emphasize data identification, metadata specifications, and hierarchical classification schemes to ensure semantic consistency throughout data circulation. Data identification can adopt the ISO 8000-115 [79] metadata model [80] to refine the rules for classification and grading implementation in industry as well as build a cross-domain understanding bridge based on JSON-LD and semantic interoperability.
- (3)
- Application layer standards: Vertical field standards should be formulated for supply chain traceability, financial services, and smart city governance scenarios. Traceability auditing incorporates hybrid standards combined with blockchain-based attestation mechanisms, establishing comprehensive “data, credit and product” mapping protocols in the financial field [81], and frameworks for cross-domain spatial interconnection interfaces are defined in urban governance to unify interaction rules across transportation and enterprise mobility scenarios [82].
- (4)
- Compliance and security standards: These reinforce systems where trust is never assumed, called zero-trust systems, and provide ways to check compliance and manage international rules. Zero-trust specifications control access to systems at all times. Protocols based on ISO 27017 verify compliance with the GDPR and national regulations. Coding rules for sending data across borders are automated to automatically check compliance.
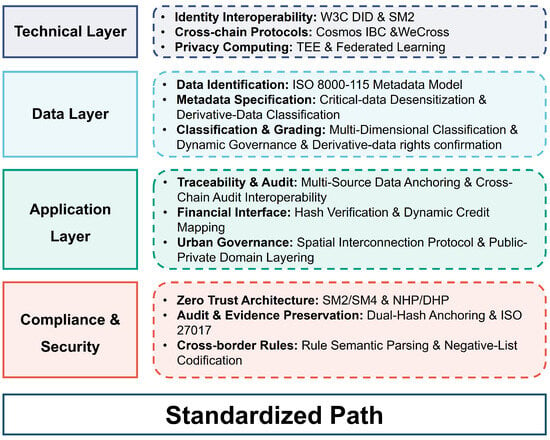
This standardization path represents a comprehensive approach to establishing interoperable, secure, and compliant blockchain-enabled data spaces, as shown in Figure 6.
Figure 6.
The structure of a standardized path at different layers [76,77,79].
4. Case Study and Validation
4.1. Case Introduction
The International Cross-Border Trustworthy Data Space-Macao-Hengqin Station was established by the IDSA and the National Engineering Center for Next Generation Internet in July 2025 in the Guangdong-Macao Deep Cooperation Zone in Hengqin. Relying on the “Macao and Hengqin” dual platforms, it adopts the blockchain, a distributed privacy protection architecture, IPv6, and AI governance technologies to build a global two-way cross-border data circulation hub. The site was the first to be piloted in the “Guangdong-Macao Medical Trustworthy Data Space” to achieve secure sharing of medical records, images, and other data across the three locations. It also integrated digital economic resources through the Macao-Hengqin Digital Business Alliance to create a new cross-border data governance model based on a three-in-one, dual-circulation, and dual-buffer with technology, rules, and scenarios.
4.2. Verification Case and Evaluation Results
4.2.1. LPHS–XV Collaborative Trust Verification Scheme
Trustworthy data space requires ensuring data availability while improving data credibility and compliance. We propose a collaborative trust verification solution that combines “On-Chain Light Attest, Off-Chain Deep Store, and Cross-Layer Verifiable Bridge” (LPHS-XV). In the above case, H medical institutions participate in cross-institutional federated learning. The hth institution holds the local dataset , and the global model parameter is . The goal is to minimize the empirical risk without pooling the original data, as shown in Equation (3):
where and . In the rth round of communication, the participants complete local training, and the FedAvg aggregation is performed by the coordinator in Equation (4):
where is the learning rate and is the noisy local update that satisfies differential privacy.
- (1)
- On-Chain Light Attest
The hash values or minimum necessary metadata of important events, such as task creation, model snapshots, and privacy credentials, are written into the blockchain to obtain an immutable timestamp and transparent log. For cryptographic primitives, we denote as a collision-resistant hash and as a binding commitment to any event A. The unified commitment is defined according to Equation (5):
In Equation (5), is random. Let the set of event commitments for round t be , and construct a Merkle tree to obtain the root . After that, only constant-size tuples will be written into the smart contract in each round, as shown in Equation (6):
In Equation (6), is the model summary, is used to identify the verification key of a zero-knowledge proof, and is the address of the object collection stored off-chain.
- (2)
- Off-Chain Deep Store
The actual model parameters, gradients, differential privacy noise, zero-knowledge proofs, and other related data are stored off-chain, such as on hospital servers or in secure storage, thereby improving the storage and processing efficiency of large-capacity data. For the local gradient , differential privacy protection is performed first, as shown in Equation (7):
where is the clipping threshold and . The off-chain object storage saves the events in round t in the form of Equation (8):
where and are the statistical information of the model training or storage process in round t and the current log information in round t, respectively.
- (3)
- Cross-Layer Verifiable Bridge
In the cross-layer verification phase, hash consistency is used to reconcile off-chain and on-chain transactions. For any off-chain object , the summary and the Merkle root path of are obtained first, and the on-chain root hash of round t is given. The verification is shown in Equation (9):
In this case, the hospital uses ZK (Groth16) to prove that and are stored off-chain. Setting allows this to be achieved without accessing the data or gradient plaintext. Finally, aggregate consistency is confirmed using Equation (10):
4.2.2. Evaluation Metrics
To objectively compare the LPHS–XV verification scheme, five indicators were used—accuracy, precision, recall, F1 score, and area under the curve (AUC)—for evaluation, as shown in Equations (11)–(15):
where TP is a true positive example, FP is a false positive example, TN is a true negative example, FN is a false negative example, and , .
4.2.3. Case Result Analysis
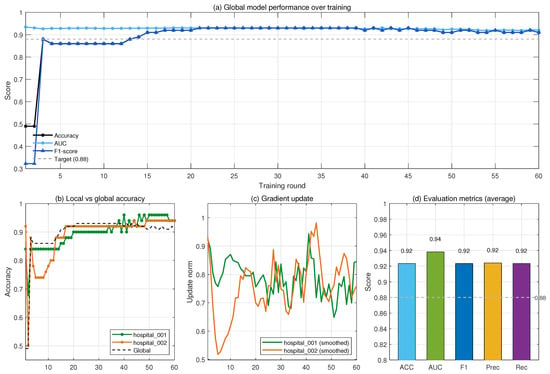
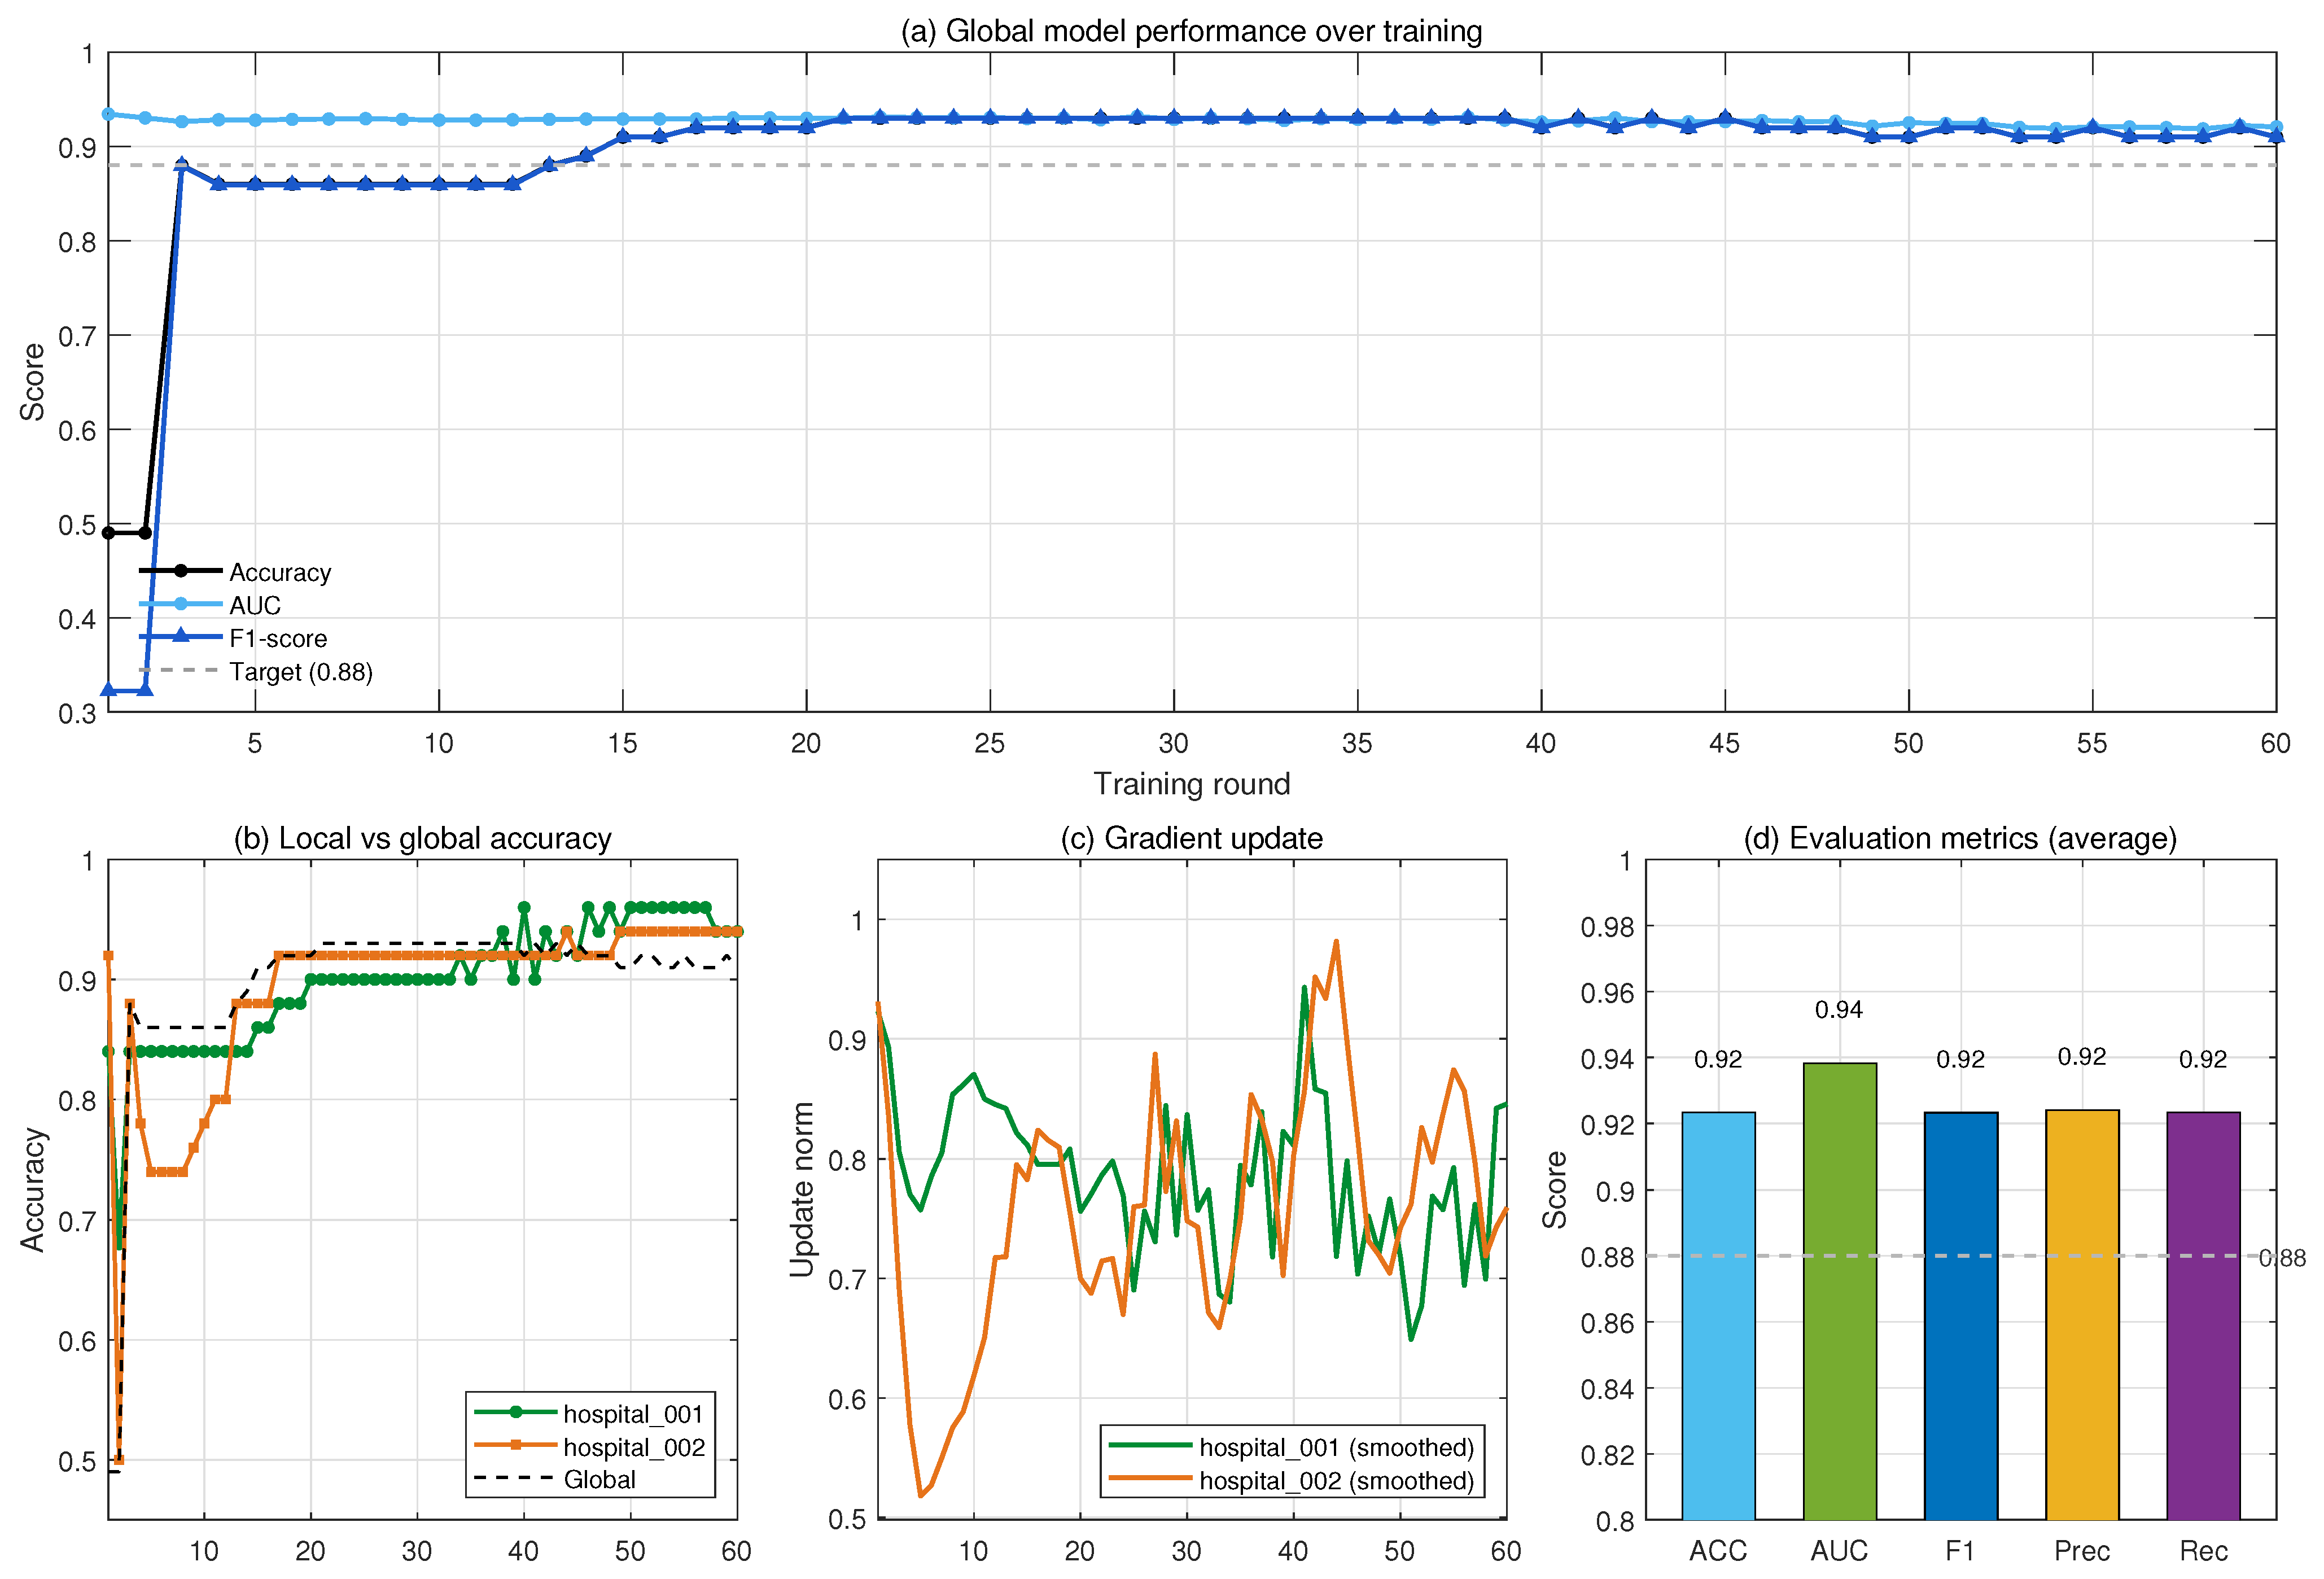
Using the above scheme, we conducted a comprehensive privacy-preserving performance evaluation of a COVID-19 case study. The experiment involved two participating medical institutions, labeled hospital_001 and hospital_002, representing cross-border medical institutions in Guangdong and Macao. The global model aggregation server was deployed on a blockchain-enabled IPv6 infrastructure.We used the public COVID-19 X-ray dataset [83]. In our case, we selected 600 samples with complete metadata and clinical indicators. Each sample was represented by eight clinical features (including, for example, [age, sex, fever status, cough, shortness of breath, comorbidities, oxygen saturation, and laboratory findings]) and assigned to 1 of 10 diagnostic categories. The data was split on the patient level into training and test subsets with a ratio of 70% and 30%, respectively, to avoid patient-level information leakage. From the training subset, each participating institution was allocated 210 training samples (420 samples in total) to simulate local data silos, while the remaining 180 samples were used for testing. Before training, continuous clinical features were standardized to a zero mean and unit variance based on the statistics of the training subset, and categorical features were encoded using label encoding. The system employed the Federated Average (FedAvg) algorithm with the following core hyperparameter settings: learning rate , global training rounds , local epochs , and batch size . All models were implemented in Python using the PyTorch framework 2.5.1 trained on a workstation equipped with an Intel(R) Core(TM) i9-14900HX, 8 GB NVIDIA GeForce RTX 4070 Laptop GPU, and 32 GB of memory running Windows 11. Figure 7 shows the experimental results, where Figure (a) shows the performance convergence trajectory of the federated global model during 60 training rounds; Figure (b) compares the local model accuracy and global model accuracy of the two participants (hospital_001 and hospital_002); Figure (c) depicts the evolution of the gradient update norm of the two participants with the training rounds and Figure (d) summarizes the average evaluation metrics of the final model on the independent test set, including ACC, AUC, F1, Prec, and Rec.
Figure 7.
The reuslt of federated learning based on LPHS-XVe.
The federated learning solution based on LPHS-XV demonstrated excellent performance across all evaluation metrics. The global model achieved a final accuracy of 92.33%, exceeding the target threshold of 88% by 4.33 percentage points. The subject AUC reached 93.82%, demonstrating the system’s excellent discriminative ability for COVID-19 diagnosis. A good balance was achieved between , , and , validating the model’s overall performance.
In terms of cross-border collaboration, the local-global performance comparison chart demonstrates the excellent collaborative effect between participating institutions. Hospital_001 achieved a final local accuracy of 94%, while hospital_002 achieved an accuracy rating of 94%, with an average performance difference of only 3.2% throughout the entire training process. This minimal performance difference demonstrates the effectiveness of the federated averaging mechanism in addressing cross-border data heterogeneity. The privacy protection mechanism successfully implemented -differential privacy, ensuring that no sensitive patient information could be inferred from model updates. The blockchain provides an unalterable log record for all training rounds, model updates, and performance metrics. The non-interactive zero-knowledge proof verifies data compliance without leaking actual data.
4.3. Case Summary and Outlook
This case study successfully validated the collaborative trust mechanism of LPHS-XV. In our method, blockchain anchoring, zero-knowledge proofs, and differential privacy were all evaluated. With two medical institutions and 60 rounds of federated training, the tests confirmed strong privacy, verifiability, and practical performance. Across three experiments, the average classification accuracy was , the precision was , the F1 score was , and the AUC was . Given the privacy budget, these mechanisms did not weaken the model effectiveness. For a full 60-round run, the average time was s (about per round), giving a round-level throughput of rounds per second. This result demonstrates the support for parallel federated scheduling and on-chain anchoring, enabling sub-second iteration cycles. In terms of communication, the model uploaded approximately parameters per round (roughly in float32), totaling about (approximately ) per session, which is consistent with sessions lacking privacy enhancements. The primary additional overhead stems from local proof generation and chain-side verification, rather than federated communication itself. The integration of differential privacy, secure aggregation, zero-knowledge proofs, and blockchain technologies established a comprehensive privacy and security framework that simultaneously met the technical requirements and cross-jurisdictional compliance needs. In the future, this approach could include the introduction of batch and aggregate proofs, the use of RDP or a moments accountant for privacy budget accounting and adaptive allocation [84], and continuous alignment of IDSA or Digital Business Alliance strategies with the IPv6 identification system [85]. This could be replicated in broader cross-border medical data space scenarios, such as medical insurance audits and drug re-evaluations. Furthermore, Figure 8 illustrates the future applications of blockchain-driven collaborative trust mechanisms in trustworthy data spaces across various fields.
Figure 8.
Blockchain-empowered trustworthy data space.
5. Summary
Based on the above technical review and experimental verification, we can summarize the necessity and feasibility of collaborative trust between the blockchain and trustworthy data spaces. The necessity is reflected in three aspects. First, there is the trust deficit. Under the traditional centralized model, it is difficult to simultaneously ensure data authenticity and verifiability in cross-border data flows and define the rights and responsibilities of multiple parties. The blockchain uses the hash chain of the data layer, which cannot be tampered with, and the automatic execution of the policy at the contract layer as its core mechanisms, forming a publicly verifiable trust anchor and a traceable audit trail [86]. Second, there are conflicts of sovereign compliance. When regulatory requirements differ across jurisdictions, it is easy to create barriers to circulation. Combining the blockchain with privacy-enhancing technologies, such as DP, ZK, MPC or TEEs, and dynamic negative lists can achieve minimum necessary disclosure and full process control under a “usable-but-not-visible” paradigm. The third aspect is ecological fragmentation. The lack of interoperability between heterogeneous systems and chains has led to the continued existence of data silos. Relying on cross-chain technologies such as relay, a light client proof, and a standardized message format can establish trusted interaction channels while preserving the autonomy of each domain [87].
In terms of feasibility, at the technical level, the layered architecture has been deeply integrated with privacy computing, IPv6 identification, and traceability systems, which can support high-concurrency, wide-area distributed cross-border data interactions while maintaining constant on-chain costs for audit and compliance expenses. At the policy level, national policies take “technology-governance-standards” as the main line of collaboration, providing institutional and standardized guarantees for the integration of the blockchain and data spaces. In practice, the verification of the LPHS-XV we proposed verified the feasibility and scalability of the collaborative model in case studies. The blockchain serves as the underlying trust foundation through encryption and auditing, enabling different entities to achieve verifiable collaboration without sharing original data. Table 5 compares the proposed method with the latest relevant research.
Table 5.
Comparison of trust mechanisms and technical implementations.
As shown in Table 5, the latest relevant research mostly focuses on trust building and access control within a single jurisdiction, employing an on-chain/off-chain partitioning strategy, where metadata, access policies, and audit logs are stored on-chain, while sensitive business data is stored off-chain using IPFS or cloud infrastructure, with only a subset incorporating sophisticated cryptographic primitives such as attribute-based encryption or proxy re-encryption. While progress has been made within specific organizational or regional boundaries, a systematic framework for cross-border data governance is generally lacking. In contrast, the LPHS–XV architecture we explored in this paper, through a unified TGS framework, explicitly addresses the triple challenges of cross-organizational, cross-regional, and cross-border data sharing, effectively bridging the gap between technological trust mechanisms and the interoperability of global data space governance.
6. Conclusions
This paper systematically studied the collaborative trust mechanism of trustworthy data spaces driven by the blockchain. We first examined the development of key technologies, including trustworthy data spaces, the blockchain, zero-knowledge proofs, and federated learning, and highlighted the evolutionary trend from semantic interoperability and gradual integration into cross-domain governance and privacy enhancement. Furthermore, we proposed a “technology integration, cross-border governance, and standardization path” (TGS) framework to address challenges such as sensitivity exposure, sovereign compliance conflicts, and ecological fragmentation in cross-domain circulation. By coupling the blockchain with privacy-preserving computing, distributed identity, and cross-chain protocols, we achieved data availability without visibility and dynamic controllability. We also utilized SRv6 cross-chain relaying and a unified semantic model to construct an open, interoperable architecture, completing the four-layer closed loop of on-chain evidence storage, off-chain storage, and cross-layer verification. Furthermore, our proposed LPHS-XV collaborative trust verification mechanism achieved auditability, security, and privacy protection under highly concurrent data interactions. We tested this mechanism using the Macao-Hengqin Station as a case study. This paper outlines a research path for blockchain-driven trustworthy data spaces and serves as a reference for future research on data element governance.
Blockchain-driven trusted data spaces face three primary challenges in cross-border deployment: (1) legal, identity, and encryption regime heterogeneity; (2) real-time cost limitations of large-scale ZKP and cross-chain verification; and (3) ecosystem fragmentation advancing from inter-chain to space-level interoperability. In the future, we should further explore a series of issues related to these points. First, the heterogeneity of legal regimes, identity systems, and encryption standards across jurisdictions is deeply entrenched. This calls for a programmable “compliance-as-code” middleware layer that can continuously translate evolving legal provisions into on-chain, machine-executable policy contracts. Second, the real-time cost bottleneck of a large-scale ZKP and cross-chain verification has not yet been resolved. Even on consortium-chain platforms, supporting high-volume cross-border medical data authorizations requires zero-knowledge proofs with hundreds of thousands to millions of R1CS constraints per authorization. Our prototype-level analysis indicates that proof generation still incurs end-to-end latencies to the order of hundreds of milliseconds to seconds, while subsequent on-chain verification and consensus introduce non-trivial CPU and network overhead at all consortium nodes, making it difficult to meet sub-second response requirements in emergency or other time-critical scenarios. Third, ecosystem fragmentation is shifting from “inter-chain interoperability” to the more complex problem of “space-level interoperability”, such as medical, financial, and transportation data spaces adopt distinct semantic models and roots of trust. Only by empowering standards bodies to co-design a space-level cross-chain identity framework (S-CID)—with verifiable credential containers and semantic hashes at its core—can a global data-element market of “one-time issuance, multi-space circulation” ultimately be realized.
Author Contributions
Conceptualization, Z.-Y.L. and M.Y.; validation, Y.-S.M. and Y.L.; formal analysis, Z.-Y.L. and G.-Y.L.; writing—original draft preparation, Z.-Y.L. and G.-Y.L.; writing—review and editing, Z.-Y.L., G.-Y.L. and Y.R.; visualization, R.-W.J.; supervision, R.-W.J. and Y.L.; funding acquisition, Z.-Y.L. All authors have read and agreed to the published version of the manuscript.
Funding
This research was funded by the Hainan Province Higher Education Scientific Research Project under Grants Hnky2025-33 and Hnky2025ZC-13, Hainan Province Key Research and Development Project under Grant ZDYF2023GXJS007.
Institutional Review Board Statement
Not applicable.
Informed Consent Statement
Not applicable.
Data Availability Statement
The data presented in this study are available in covid-19-xray-dataset at https://github.com/v7labs/covid-19-xray-dataset, accessed on 29 November 2025.
Conflicts of Interest
The authors declare no conflicts of interest.
References
- Kar, S. Data for Better Lives: World Development Report 2021 by World Bank Group. J. Data Sci. Inf. Cit. Stud. 2023, 2, 136–139. [Google Scholar] [CrossRef] [Scilit]
- Lee, J.S.; Jun, S.P. Privacy-preserving data mining for open government data from heterogeneous sources. Gov. Inf. Q. 2021, 38, 101544. [Google Scholar] [CrossRef] [Scilit]
- Möller, F.; Jussen, I.; Springer, V.; Gieß, A.; Schweihoff, J.C.; Gelhaar, J.; Guggenberger, T.; Otto, B. Industrial data ecosystems and data spaces. Electron. Mark. 2024, 34, 41. [Google Scholar] [CrossRef] [Scilit]
- Franklin, M.; Halevy, A.; Maier, D. From databases to dataspaces: A new abstraction for information management. ACM Sigmod Rec. 2005, 34, 27–33. [Google Scholar] [CrossRef] [Scilit]
- Zhao, Y.; Huang, D. The Construction Principles and Development Paths of Trusted Data Spaces in China. J. Mod. Inf. 2025, 45, 126–139. [Google Scholar]
- Otto, B. A federated infrastructure for European data spaces. Commun. ACM 2022, 65, 44–45. [Google Scholar] [CrossRef] [Scilit]
- Bacco, M.; Kocian, A.; Chessa, S.; Crivello, A.; Barsocchi, P. What are data spaces? Systematic survey and future outlook. Data Brief 2024, 57, 110969. [Google Scholar] [CrossRef] [Scilit]
- Gieß, A.; Schoormann, T.; Möller, F.; Gür, I. Discovering data spaces: A classification of design options. Comput. Ind. 2025, 164, 104212. [Google Scholar] [CrossRef] [Scilit]
- Hörandner, F.; Ramacher, S.; Roth, S. Selective end-to-end data-sharing in the cloud. J. Bank. Financ. Technol. 2020, 4, 139–157. [Google Scholar] [CrossRef] [Scilit]
- Zafar, A. Reconciling blockchain technology and data protection laws: Regulatory challenges, technical solutions, and practical pathways. J. Cybersecur. 2025, 11, tyaf002. [Google Scholar] [CrossRef] [Scilit]
- Liu, L.; Han, M. Data sharing and exchanging with incentive and optimization: A survey. Discov. Data 2024, 2, 2. [Google Scholar] [CrossRef] [Scilit]
- Duan, L.; Sun, Y.; Ni, W.; Ding, W.; Liu, J.; Wang, W. Attacks against cross-chain systems and defense approaches: A contemporary survey. IEEE/CAA J. Autom. Sin. 2023, 10, 1647–1667. [Google Scholar] [CrossRef] [Scilit]
- Carvalho, T.; Moniz, N.; Faria, P.; Antunes, L. Towards a data privacy-predictive performance trade-off. Expert Syst. Appl. 2023, 223, 119785. [Google Scholar] [CrossRef] [Scilit]
- Tanchangya, T.; Sarker, T.; Rahman, J.; Islam, M.S.; Islam, N.; Siddiqi, K.O. Mapping Blockchain Applications in FinTech: A Systematic Review of Eleven Key Domains. Information 2025, 16, 769. [Google Scholar] [CrossRef] [Scilit]
- Atmanavičiūtė, L.; Masteika, S. Towards understanding the application areas of zero knowledge proof: A comprehensive analysis. In Proceedings of the 19th Prof. Vladas Gronskas International Scientific Conference, Kaunas, Lithuania, 29 November 2024; pp. 6–13. [Google Scholar]
- Salles, M.A.V.; Dittrich, J.P.; Karakashian, S.K.; Girard, O.R.; Blunschi, L. iTrails: Pay-as-you-go Information Integration in Dataspaces. In Proceedings of the VLDB, Vienna, Austria, 23–28 September 2007; Volume 7, pp. 663–674. [Google Scholar]
- Ajayi, R. Integrating IoT and cloud computing for continuous process optimization in real-time systems. Int. J. Res. Publ. Rev. 2025, 6, 2540–2558. [Google Scholar] [CrossRef] [Scilit]
- Zyskind, G.; Nathan, O.; Pentland, A.S. Decentralizing privacy: Using blockchain to protect personal data. In Proceedings of the 2015 IEEE Security and Privacy Workshops, San Jose, CA, USA, 21–22 May 2015; pp. 180–184. [Google Scholar]
- Seidel, A.; Wenzel, K.; Hänel, A.; Teicher, U.; Weiß, A.; Schäfer, U.; Ihlenfeldt, S.; Eisenmann, H.; Ernst, H. Towards a seamless data cycle for space components: Considerations from the growing European future digital ecosystem Gaia-X. CEAS Space J. 2024, 16, 351–365. [Google Scholar] [CrossRef] [Scilit]
- Feng, Z.; Wu, Q.; Liu, Y.; Qin, B.; Zhai, M.; Susillo, W. Secure and fair data trading based on blockchain with enhanced access control. IEEE Internet Things J. 2024, 12, 7277–7292. [Google Scholar] [CrossRef] [Scilit]
- Zhang, C.; Liu, Y.; Xu, M.; Yang, X.; Li, P.; Yang, C.; Liu, Q.; Xiong, X.; Chen, P.; Wang, W. Trans-border Trusted Data Spaces: A General Framework Supporting Trustworthy International Data Circulation. IEEE Access 2025, 13, 30481–30496. [Google Scholar] [CrossRef] [Scilit]
- Dessi, N.; Pes, B. Towards scientific dataspaces. In Proceedings of the 2009 IEEE/WIC/ACM International Joint Conference on Web Intelligence and Intelligent Agent Technology, Milan, Italy, 15–18 September 2009; Volume 3, pp. 575–578. [Google Scholar]
- Singh, M.; Jain, S. A survey on dataspace. In Proceedings of the International Conference on Network Security and Applications, Chennai, India, 15–17 July 2011; pp. 608–621. [Google Scholar]
- Otto, B.; Jürjens, J.; Schon, J.; Auer, S.; Menz, N.; Wenzel, S.; Cirullies, J. Industrial Data Space: Digital Souvereignity over Data; Fraunhofer-Gesellschaft: München, Germany, 2016. [Google Scholar]
- Ali, S.; Wang, G.; White, B.; Cottrell, R.L. A blockchain-based decentralized data storage and access framework for pinger. In Proceedings of the 2018 17th IEEE International Conference on Trust, Security and Privacy in Computing and Communications/12th IEEE International Conference on Big Data Science and Engineering (TrustCom/BigDataSE), New York, NY, USA, 1–3 August 2018; pp. 1303–1308. [Google Scholar]
- Jarke, M.; Otto, B.; Ram, S. Data sovereignty and data space ecosystems. Bus. Inf. Syst. Eng. 2019, 61, 549–550. [Google Scholar] [CrossRef] [Scilit]
- Nakamoto, S. Bitcoin: A peer-to-peer electronic cash system. SSRN Electron. J. 2008, 3440802, 10-2139. [Google Scholar]
- Priyanshu, S.; Kumar, S.; Garg, S. Blockchain-Based Data Security. In Digital Forensics and Cyber Crime Investigation: Recent Advances and Future Directions; CRC Press: Boca Raton, FL, USA, 2024; Volume 17. [Google Scholar]
- Rosenfeld, M. Overview of colored coins. White Pap. 2012, 41, 94. [Google Scholar]
- Counterparty Community. Counterparty (Platform). 2025. Available online: https://en.wikipedia.org/wiki/Counterparty_(platform) (accessed on 23 November 2025).
- Buterin, V. A next-generation smart contract and decentralized application platform. White Pap. 2014, 3, 2-1. [Google Scholar]
- Cuffe, P. The role of the erc-20 token standard in a financial revolution: The case of initial coin offerings. In Proceedings of the IEC-IEEE-KATS Academic Challenge, Busan, Korea, 22–23 October 2018. [Google Scholar]
- Benet, J. Ipfs-content addressed, versioned, p2p file system. arXiv 2014, arXiv:1407.3561. [Google Scholar]
- Bauer, D.P. Filecoin. In Getting Started with Ethereum: A Step-by-Step Guide to Becoming a Blockchain Developer; Springer: Berlin/Heidelberg, Germany, 2022; pp. 97–101. [Google Scholar]
- Alonso, Á.; Pozo, A.; Cantera, J.M.; De la Vega, F.; Hierro, J.J. Industrial data space architecture implementation using FIWARE. Sensors 2018, 18, 2226. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Thaler, J. Proofs, arguments, and zero-knowledge. Found. Trends® Priv. Secur. 2022, 4, 117–660. [Google Scholar] [CrossRef] [Scilit]
- Belchior, R.; Vasconcelos, A.; Guerreiro, S.; Correia, M. A survey on blockchain interoperability: Past, present, and future trends. ACM Comput. Surv. (CSUR) 2021, 54, 1–41. [Google Scholar] [CrossRef] [Scilit]
- Goldwasser, S.; Micali, S.; Rackoff, C. The knowledge complexity of interactive proof-systems. In Providing Sound Foundations for Cryptography: On the Work of Shafi Goldwasser and Silvio Micali; ACM: New York, NY, USA, 2019; pp. 203–225. [Google Scholar]
- Schnorr, C.P. Efficient signature generation by smart cards. J. Cryptol. 1991, 4, 161–174. [Google Scholar] [CrossRef] [Scilit]
- Fiat, A.; Shamir, A. How to prove yourself: Practical solutions to identification and signature problems. In Proceedings of the Conference on the Theory and Application of Cryptographic Techniques, Linköping, Sweden, 20–22 May 1986; pp. 186–194. [Google Scholar]
- Groth, J. On the size of pairing-based non-interactive arguments. In Proceedings of the Annual International Conference on the Theory and Applications of Cryptographic Techniques, Vienna, Austria, 8–12 May 2016; pp. 305–326. [Google Scholar]
- Gabizon, A.; Williamson, Z.J.; Ciobotaru, O. PLONK: Permutations over Lagrange-Bases for Oecumenical Noninteractive Arguments of Knowledge. Report 2019/953. Cryptol. ePrint Arch. 2019; Preprint. Available online: https://eprint.iacr.org/2019/953 (accessed on 29 October 2025).
- Boneh, D.; Drake, J.; Fisch, B.; Gabizon, A. Halo infinite: Proof-carrying data from additive polynomial commitments. In Proceedings of the Annual International Cryptology Conference, Virtual, 16–20 August 2021; pp. 649–680. [Google Scholar]
- Ben-Sasson, E.; Bentov, I.; Horesh, Y.; Riabzev, M. Scalable, Transparent, and Post-Quantum Secure Computational Integrity. IACR Cryptol. ePrint Arch. 2018; 46, preprint.
- Ben-Sasson, E.; Bentov, I.; Horesh, Y.; Riabzev, M. Fast reed–solomon interactive oracle proofs of proximity. In Proceedings of the 45th International Colloquium on Automata, Languages, and Programming (ICALP 2018), Prague, Czech Republic, 9–13 July 2018; pp. 14:1–14:17. [Google Scholar]
- Bünz, B.; Bootle, J.; Boneh, D.; Poelstra, A.; Wuille, P.; Maxwell, G. Bulletproofs: Short proofs for confidential transactions and more. In Proceedings of the 2018 IEEE Symposium on Security and Privacy (SP), San Francisco, CA, USA, 20–24 May 2018; pp. 315–334. [Google Scholar]
- Chung, H.; Han, K.; Ju, C.; Kim, M.; Seo, J.H. Bulletproofs+: Shorter proofs for a privacy-enhanced distributed ledger. IEEE Access 2022, 10, 42081–42096. [Google Scholar] [CrossRef] [Scilit]
- Bai, T.; Hu, Y.; He, J.; Fan, H.; An, Z. Health-zkIDM: A healthcare identity system based on fabric blockchain and zero-knowledge proof. Sensors 2022, 22, 7716. [Google Scholar] [CrossRef] [Scilit]
- Ebrahimi, S.; Hassanizadeh, P. From Interaction to Independence: zkSNARKs for Transparent and Non-Interactive Remote Attestation. IACR Cryptol. ePrint Arch. 2024, 2024, 1068. [Google Scholar]
- Yadav, C.; Chowdhury, A.R.; Boneh, D.; Chaudhuri, K. Fairproof: Confidential and certifiable fairness for neural networks. arXiv 2024, arXiv:2402.12572. [Google Scholar]
- Adida, B. Helios: Web-based Open-Audit Voting. In Proceedings of the USENIX Security Symposium, San Jose, CA, USA, 28 July–1 August 2008; Volume 17, pp. 335–348. [Google Scholar]
- Setty, S. Spartan: Efficient and general-purpose zkSNARKs without trusted setup. In Proceedings of the Annual International Cryptology Conference, Santa Barbara, CA, USA, 17–21 August 2020; pp. 704–737. [Google Scholar]
- Chen, B.J.; Waiwitlikhit, S.; Stoica, I.; Kang, D. Zkml: An optimizing system for ml inference in zero-knowledge proofs. In Proceedings of the Nineteenth European Conference on Computer Systems, Athens, Greece, 22–25 April 2024; pp. 560–574. [Google Scholar]
- Beltrán, E.T.M.; Pérez, M.Q.; Sánchez, P.M.S.; Bernal, S.L.; Bovet, G.; Pérez, M.G.; Pérez, G.M.; Celdrán, A.H. Decentralized federated learning: Fundamentals, state of the art, frameworks, trends, and challenges. IEEE Commun. Surv. Tutor. 2023, 25, 2983–3013. [Google Scholar] [CrossRef] [Scilit]
- Yang, Q.; Liu, Y.; Chen, T.; Tong, Y. Federated machine learning: Concept and applications. ACM Trans. Intell. Syst. Technol. (TIST) 2019, 10, 1–19. [Google Scholar] [CrossRef] [Scilit]
- McMahan, B.; Moore, E.; Ramage, D.; Hampson, S.; y Arcas, B.A. Communication-efficient learning of deep networks from decentralized data. In Proceedings of the Artificial Intelligence and Statistics, Fort Lauderdale, FL, USA, 20–22 April 2017; pp. 1273–1282. [Google Scholar]
- Hard, A.; Rao, K.; Mathews, R.; Ramaswamy, S.; Beaufays, F.; Augenstein, S.; Eichner, H.; Kiddon, C.; Ramage, D. Federated learning for mobile keyboard prediction. arXiv 2018, arXiv:1811.03604. [Google Scholar]
- Minto, L.; Haller, M.; Livshits, B.; Haddadi, H. Stronger privacy for federated collaborative filtering with implicit feedback. In Proceedings of the 15th ACM Conference on Recommender Systems, Amsterdam, The Netherlands, 27 September–1 October 2021; pp. 342–350. [Google Scholar]
- Hardy, S.; Henecka, W.; Ivey-Law, H.; Nock, R.; Patrini, G.; Smith, G.; Thorne, B. Private federated learning on vertically partitioned data via entity resolution and additively homomorphic encryption. arXiv 2017, arXiv:1711.10677. [Google Scholar] [CrossRef] [Scilit]
- Nock, R.; Hardy, S.; Henecka, W.; Ivey-Law, H.; Patrini, G.; Smith, G.; Thorne, B. Entity resolution and federated learning get a federated resolution. arXiv 2018, arXiv:1803.04035. [Google Scholar] [CrossRef] [Scilit]
- Wu, Y.; Cai, S.; Xiao, X.; Chen, G.; Ooi, B.C. Privacy preserving vertical federated learning for tree-based models. arXiv 2020, arXiv:2008.06170. [Google Scholar] [CrossRef] [Scilit]
- Cheng, K.; Fan, T.; Jin, Y.; Liu, Y.; Chen, T.; Papadopoulos, D.; Yang, Q. Secureboost: A lossless federated learning framework. IEEE Intell. Syst. 2021, 36, 87–98. [Google Scholar] [CrossRef] [Scilit]
- Che, L.; Wang, J.; Zhou, Y.; Ma, F. Multimodal federated learning: A survey. Sensors 2023, 23, 6986. [Google Scholar] [CrossRef] [Scilit]
- Guo, W.; Zhuang, F.; Zhang, X.; Tong, Y.; Dong, J. A comprehensive survey of federated transfer learning: Challenges, methods and applications. Front. Comput. Sci. 2024, 18, 186356. [Google Scholar] [CrossRef] [Scilit]
- Zhou, B.; Miao, T.; Mirian, N.; Chen, X.; Xie, H.; Feng, Z.; Guo, X.; Li, X.; Zhou, S.K.; Duncan, J.S.; et al. Federated transfer learning for low-dose PET denoising: A pilot study with simulated heterogeneous data. IEEE Trans. Radiat. Plasma Med. Sci. 2022, 7, 284–295. [Google Scholar] [CrossRef] [Scilit]
- Bai, J.; Chen, D.; Qian, B.; Yao, L.; Li, Y. Federated fine-tuning of large language models under heterogeneous tasks and client resources. Adv. Neural Inf. Process. Syst. 2024, 37, 14457–14483. [Google Scholar]
- Kosba, A.; Miller, A.; Shi, E.; Wen, Z.; Papamanthou, C. Hawk: The blockchain model of cryptography and privacy-preserving smart contracts. In Proceedings of the 2016 IEEE Symposium on Security and Privacy (SP), San Jose, CA, USA, 22–26 May 2016; pp. 839–858. [Google Scholar]
- Bünz, B.; Agrawal, S.; Zamani, M.; Boneh, D. Zether: Towards privacy in a smart contract world. In Proceedings of the International Conference on Financial Cryptography and Data Security, Kota Kinabalu, Malaysia, 10–14 February 2020; pp. 423–443. [Google Scholar]
- Mühle, A.; Grüner, A.; Gayvoronskaya, T.; Meinel, C. A survey on essential components of a self-sovereign identity. Comput. Sci. Rev. 2018, 30, 80–86. [Google Scholar] [CrossRef] [Scilit]
- Ding, Y.; Zhang, Y.; Qin, B.; Wang, Q.; Yang, Z.; Shi, W. A scalable cross-chain access control and identity authentication scheme. Sensors 2023, 23, 2000. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Mohammed, A.G.; Eram, A.; Talburt, J.R. ISO 8000-61 Data Quality Management Standard, TDQM Compliance, IQ Principles. In Proceedings of the MIT International Conference on Information Quality, Little Rock, AR, USA, 6–7 October 2017; pp. 6–7. [Google Scholar]
- Kamaruddin, N.A.; Mohamed, I.; Jarno, A.D.; Daud, M. Cloud Security Pre-assessment Model For Cloud Service Provider Based On ISO/IEC 27017: 2015 Additional Control. In Proceedings of the 3rd International Conference on Global Business and Social Science 2020 (3rd ICGBSS 2020), Online, 3–4 October 2020; p. 53. [Google Scholar]
- Panek, W. People’s Republic of China and the adequacy–Why Chinese data protection law is not adequate within the meaning of the GDPR. Masaryk. Univ. J. Law Technol. 2024, 18, 143–167. [Google Scholar] [CrossRef] [Scilit]
- Nokhbeh Zaeem, R.; Chang, K.C.; Huang, T.C.; Liau, D.; Song, W.; Tyagi, A.; Khalil, M.; Lamison, M.; Pandey, S.; Barber, K.S. Blockchain-based self-sovereign identity: Survey, requirements, use-cases, and comparative study. In Proceedings of the IEEE/WIC/ACM International Conference on Web Intelligence and Intelligent Agent Technology, Melbourne, Australia, 14–17 December 2021; pp. 128–135. [Google Scholar]
- Firdausy, D.; Silva, P.D.A.; van Sinderen, M.J.; Iacob, M.E. Semantic discovery and selection of data connectors in international data spaces. In Proceedings of the Interoperability for Enterprise Systems and Applications, I-ESA 2022, Valencia, Spain, 23–25 March 2022. [Google Scholar]
- W3C DID v1.0; Decentralized Identifiers (DIDs) v1.0; World Wide Web Consortium (W3C): Cambridge, MA, USA, 2022.
- ISO/IEC 27017:2015; Information Technology—Security Techniques—Code of Practice for Information Security Controls Based on ISO/IEC 27002 for Cloud Services. International Organization for Standardization: Geneva, Switzerland, 2015.
- Reed, D.; Sporny, M.; Longley, D.; Allen, C.; Grant, R.; Sabadello, M.; Holt, J. Decentralized Identifiers (DIDs) v1.0.; Draft Community Group Report; W3C: Wakefield, MA, USA, 2020. [Google Scholar]
- ISO 8000-115:2024; Data quality—Part 115: Master Data: Exchange of Quality Identifiers: Syntactic, Semantic and Resolution Requirements. International Organization for Standardization: Geneva, Switzerland, 2024.
- Gualo, F.; Caballero, I.; Rodriguez, M. Towards a software quality certification of master data-based applications. Softw. Qual. J. 2020, 28, 1019–1042. [Google Scholar] [CrossRef] [Scilit]
- Bakhshi, T.; Ghita, B. Perspectives on Auditing and Regulatory Compliance in Blockchain Transactions. In Trust Models for Next-Generation Blockchain Ecosystems; Springer: Berlin/Heidelberg, Germany, 2021; pp. 37–65. [Google Scholar]
- Li, Z.; He, J.; Fang, X.; Luo, L.; Tian, C. Overall framework of IoT platform in urban agglomeration-cross-city, cross-domain, cross-level, and one-network unified management architecture. In Proceedings of the International Conference on Internet of Things and Machine Learning (IoTML 2023), Singapore, 15–17 September 2023; Volume 12937, pp. 239–247. [Google Scholar]
- Cohen, J.P.; Morrison, P.; Dao, L. COVID-19 image data collection. arXiv 2020, arXiv:2003.11597. [Google Scholar]
- Mironov, I. Rényi differential privacy. In Proceedings of the 2017 IEEE 30th Computer Security Foundations Symposium (CSF), Santa Barbara, CA, USA, 21–25 August 2017; pp. 263–275. [Google Scholar]
- Liu, Y.; Ren, G.; Wu, J.; Zhang, S.; He, L.; Jia, Y. Building an IPv6 address generation and traceback system with NIDTGA in Address Driven Network. Sci. China Inf. Sci. 2015, 58, 1–14. [Google Scholar] [CrossRef] [Scilit]
- Liang, X.; Shetty, S.; Tosh, D.; Kamhoua, C.; Kwiat, K.; Njilla, L. Provchain: A blockchain-based data provenance architecture in cloud environment with enhanced privacy and availability. In Proceedings of the 2017 17th IEEE/ACM International Symposium on Cluster, Cloud and Grid Computing (CCGRID), Madrid, Spain, 14–17 May 2017; pp. 468–477. [Google Scholar]
- Sun, X.; Dou, H.; Chen, S.; Zhao, H. A Novel Block-chain based secure cross-domain interaction Approach for intelligent transportation systems. Phys. Commun. 2024, 63, 102223. [Google Scholar] [CrossRef] [Scilit]
- Zhang, J.; Datta, A. Blockchain-enabled data governance for privacy-preserved sharing of confidential data. PeerJ Comput. Sci. 2024, 10, e2581. [Google Scholar] [CrossRef] [Scilit]
- Garcia, R.D.; Ueyama, J. Blockchain-based data governance for privacy-preserving in multi-stakeholder settings. In Proceedings of the Anais Estendidos do XLII Simpósio Brasileiro de Redes de Computadores e Sistemas Distribuídos (SBRC 2024), Linköping, Sweden, 20–22 May 2024. [Google Scholar]
- Balachandar, S.K.; Prema, K.; Kamarajapandian, P.; Shantha Shalini, K.; Thanga Aruna, M.; Jaiganesh, S. Blockchain-enabled Data Governance Framework for Enhancing Security and Efficiency in Multi-Cloud Environments through Ethereum, IPFS, and Cloud Infrastructure Integration. J. Electr. Syst. 2024, 20, 2132–2139. [Google Scholar] [CrossRef] [Scilit]
- Widayanti, R.; Mutiara, A.B.; Tarigan, A. Data Governance in Blockchain-Based Systems for Internship Grade Conversion. Aptisi Trans. Technopreneurship (ATT) 2024, 6, 509–521. [Google Scholar] [CrossRef] [Scilit]
- Feizal, M.; Mohemad, R.; Noor, N.M.M. A Systematic Literature Review on Blockchain for Implementation of Data Governance Framework. J. Theor. Appl. Inf. Technol. 2024, 102, 6448–6454. [Google Scholar]

Disclaimer/Publisher’s Note: The statements, opinions and data contained in all publications are solely those of the individual author(s) and contributor(s) and not of MDPI and/or the editor(s). MDPI and/or the editor(s) disclaim responsibility for any injury to people or property resulting from any ideas, methods, instructions or products referred to in the content. |
© 2025 by the authors. Licensee MDPI, Basel, Switzerland. This article is an open access article distributed under the terms and conditions of the Creative Commons Attribution (CC BY) license (https://creativecommons.org/licenses/by/4.0/).