


Abstract
To address the severe physical wear of actual circuit breakers, limited logic verification under complex operating conditions, and maintenance scheduling conflicts during operational testing in power systems, this paper presents a portable auxiliary verification device for relay protection based on LoRa spread-spectrum technology. The device adopts a distributed modular architecture consisting of a master unit and multiple slave units, with STM32 MCU and LoRa communication serving as the hardware core. Circuit breaker simulator logic circuits are employed to replace the physical operation of actual high-voltage circuit breakers during testing. A dedicated software platform provides system management, real-time online monitoring, and historical data query and export functions. Experimental results indicate that the proposed device can accurately reproduce the state information of multiple circuit breakers, enabling complex logic verification, including automatic bus transfer (ABT) and busbar protection, without de-energizing primary equipment. Consequently, routine substation maintenance efficiency is significantly improved while operational risks are effectively reduced.
1. Introduction
Relay protection testing is an essential part of commissioning, periodic inspection, and maintenance in substations. During the switching test, the operating logic of the protection system is verified by checking the interaction among protection outputs, circuit-breaker control circuits, and breaker position feedback signals. The test serves as an important method to verify the integrity of secondary circuits and the correctness of protection logic, which is important for equipment commissioning and maintenance [1,2,3,4,5,6].
However, conventional field testing relies heavily on the operation of physical circuit breakers. This practice becomes increasingly difficult when protection functions involve multiple breakers and complex logical relationships. For example, automatic bus transfer (ABT) schemes require the protection system to identify the operating states of both the main and standby power supplies. The verification of such functions therefore requires coordinated changes in multiple breaker position signals. In substations undergoing phased construction, technical modification, or periodic maintenance, however, physical breaker operation may be restricted by power supply reliability requirements. As a result, the complete control and feedback loop of the protection system cannot always be verified under actual operating conditions [7,8,9,10,11].
Similar difficulties arise in the testing of protection systems with multiple trip outputs. Busbar protection, transformer protection, and under-frequency or under-voltage load-shedding systems may involve multiple circuit-breaker outputs, interlocking conditions, and sequential operations. Conventional point-by-point verification using test switches or multimeters can confirm individual signals, but it is difficult to reproduce the coordinated state transitions of several circuit breakers within a complete protection logic loop [9,12,13]. Moreover, repeated manual operations at energized protection panels increase the possibility of wiring errors and unintended operations. Repeated mechanical operations of physical circuit breakers during testing may also introduce unnecessary mechanical wear [14].
As summarized in Table 1, conventional operational testing and point-by-point testing with multiple instruments mainly verify individual signals or local functions. When coordinated reproduction of multiple circuit-breaker states is required, extensive temporary wiring and manual switching are typically necessary, making it difficult to efficiently reproduce complex multi-breaker state sequences. Existing integrated testing platforms can provide various analog and digital input/output channels and support the generation of coordinated test sequences [5,6,15]. However, these platforms are typically implemented in benchtop or rack-mounted configurations, which limits their flexibility in configuring distributed breaker-state signals and their portability for on-site applications. Therefore, a portable verification method for on-site applications is required to maintain closed-loop interaction with the relay protection system while enabling flexible reproduction, coordinated control, and centralized monitoring of multiple distributed circuit-breaker states [1,14].
Table 1.
Comparison of existing relay protection verification approaches and the proposed physical breaker state emulation method.
The proposed method replaces the physical switching actions of selected high-voltage circuit breakers with electrically isolated simulated breaker interfaces. Multiple simulated breaker nodes can be distributed according to the physical locations of the tested circuits. Their states are acquired and coordinated through a master–slave communication architecture, while the protection-device outputs and simulated breaker position feedback form a closed verification loop. This approach enables complex multi-breaker protection logic to be reproduced without repeatedly operating the corresponding primary equipment.
LoRa communication is employed as the wireless communication medium because the proposed application requires communication between the master unit and distributed slave nodes in a substation environment. LoRa-based communication has been investigated for sensing and monitoring applications in electrical substations, demonstrating its applicability to distributed electrical equipment monitoring [16,17]. In addition, LoRa has been applied to power-grid data transmission systems, providing a basis for its use in distributed monitoring and communication applications [18]. A polling-based communication mechanism is implemented to collect the states of multiple simulated breaker nodes and to detect communication abnormalities. The collected states are then transferred to a mobile human–machine interface (HMI), allowing the operator to monitor the complete set of simulated breaker states during testing.
Based on this approach, a portable relay protection auxiliary verification device is developed. The device integrates 220 V and 24 VDC simulated circuit-breaker interfaces to accommodate different protection and control circuits. The 220 V interface is intended to reproduce conventional breaker closing and tripping operations, whereas the 24 VDC interfaces are designed for protection logic verification involving multiple low-voltage outputs. The proposed architecture allows several simulated breakers to operate independently while their states are centrally monitored. This configuration is intended to support the verification of ABT, busbar protection, transformer protection, and under-frequency or under-voltage load-shedding logic without requiring repeated operation of physical high-voltage breakers [19].
The remainder of this paper is organized as follows. Section 2 introduces the proposed physical breaker state emulation method, including the overall verification architecture, simulated circuit-breaker state model, communication and synchronization mechanism, and protection logic verification strategy. Section 3 describes the hardware and software implementation of the proposed device, including the simulated breaker interfaces and remote monitoring system. Section 4 presents the experimental and field verification results, including single-breaker, coupled ABT, and multi-output protection tests, followed by a quantitative comparison with conventional testing approaches and a discussion of practical limitations. Finally, Section 5 concludes the study and summarizes the main findings.
2. Methodology and System Design
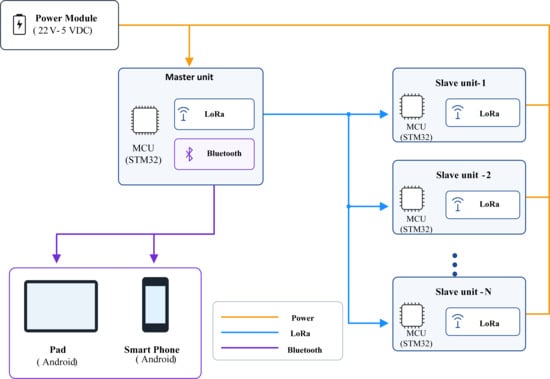
This paper proposes a portable auxiliary verification device for relay protection applied to the on-site periodic inspection of substation relay protection systems. The proposed device integrates multi-channel circuit breaker simulator status display and wireless remote centralized monitoring functions, as shown in Figure 1. A star topology architecture consisting of one master unit and n slave units is adopted in the system. Within the overall architecture, bidirectional data exchange between the master unit and the outdoor distributed sub-units is achieved through a LoRa wireless communication network, thereby realizing remote control of the entire distributed verification system. Additionally, a human–machine interface (HMI) based on mobile terminals is incorporated. Aggregated data are transmitted from the master control unit to Android-based mobile devices via a Bluetooth module. Consequently, test personnel can remotely and intuitively monitor the “Trip” and “Close” positions of all n circuit breaker simulator modules in real time via smartphones, tablets, or remote computer browsers.
Figure 1.
System architecture diagram.
Furthermore, utilizing the microcontroller units, the master and slave devices determine the status of data transmission and reception via broadcast packets. Optocoupler isolation circuits are employed to independently collect and transmit the operational status of each circuit breaker simulator module. When an anomaly occurs (e.g., a sub-unit fails to respond within the designated time window), the microcontroller initiates exception-handling logic and triggers an offline alarm via LED indicators on the device panel.
2.1. Circuit-Breaker State Model
The simulated circuit breaker is modeled according to the operating behavior required for relay protection verification. The model represents not only the breaker position but also the event that causes a state transition and the auxiliary memory required by specific protection logic. This enables the simulated breaker to reproduce the logical behavior of an actual circuit breaker without mechanically operating the primary equipment.
For the -th simulated circuit breaker, the basic position state is defined as:
where OPEN and CLOSED represent the open and closed positions, respectively. These two states describe the physical position that is fed back to the relay protection system.
The operation event is separately defined as:
The TRIP event indicates that the opening operation is initiated by a protection output, and the MANUAL_OPEN event indicates manual opening command, whereas RESET represents a manual operation used to clear the corresponding latched logic when required by the ABT verification process.
For ABT verification, an additional auxiliary memory state is introduced to reproduce the event-dependent behavior of the simulated breaker. It can be represented by:
where indicates that the protection-related post-closing/interlock memory is active. This auxiliary state allows the simulator to distinguish a protection-initiated trip from a manually initiated opening even when both operations result in the same open position.
Therefore, the complete state representation of a simulated circuit breaker can be expressed as:
The state-transition rules used by the simulated circuit-breaker interfaces are summarized in Table 2.
Table 2.
Simulated circuit-breaker state transition rules.
2.2. Communication and Synchronization Mechanism
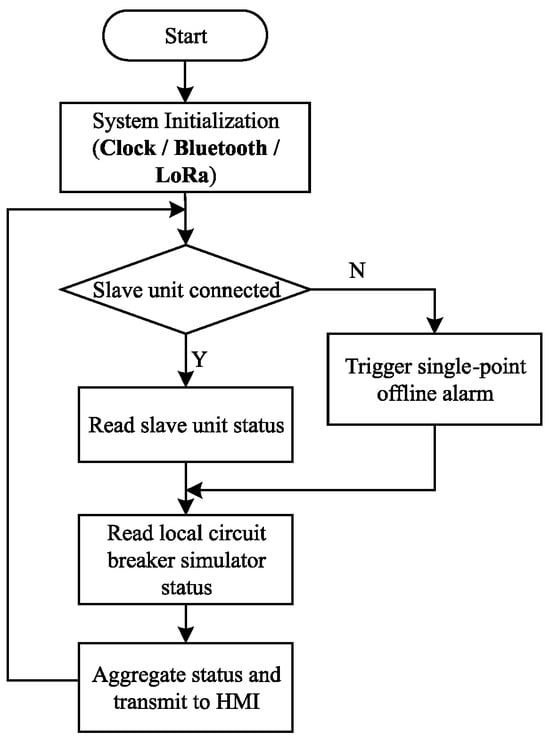
The distributed circuit-breaker state emulation method requires the states of simulated circuit breakers located at different nodes to be acquired and aggregated by the master unit. Therefore, a communication and synchronization mechanism is required to coordinate the distributed slave units and maintain a consistent representation of breaker states at the master side. As shown in Figure 2, a master–slave polling mechanism is adopted. The master unit periodically initiates communication, while each slave unit responds to the broadcast request and reports the local simulated circuit-breaker states.
Figure 2.
Master-unit communication flow.
The communication process consists of four main stages: node availability detection, handshake response, local state acquisition, and state-frame transmission. The communication mechanism is implemented using LoRa wireless communication.
2.2.1. Master-Side Polling Mechanism
After system initialization, the master unit initializes the required communication interfaces and enters the slave-node polling process. For each polling cycle, the master first determines whether the corresponding slave unit is connected. If the node is available, its online status is read and the master proceeds to acquire the state information of the distributed simulated breakers. If no valid response is received within the specified communication period, the corresponding node is identified as offline and a single-point communication fault alarm is triggered.
After the slave-node status has been determined, the master unit reads the state of the locally connected simulated circuit breakers. The states received from the slave units and the local states are then aggregated into a unified state representation and transmitted to the human–machine interface (HMI).
This sequential polling mechanism allows the master unit to obtain the states of multiple distributed nodes within each communication cycle. Compared with independent point-to-point monitoring, the mechanism provides a unified channel for collecting and reconstructing the states of distributed simulated circuit breakers.
2.2.2. Slave-Side Response and Local State Acquisition
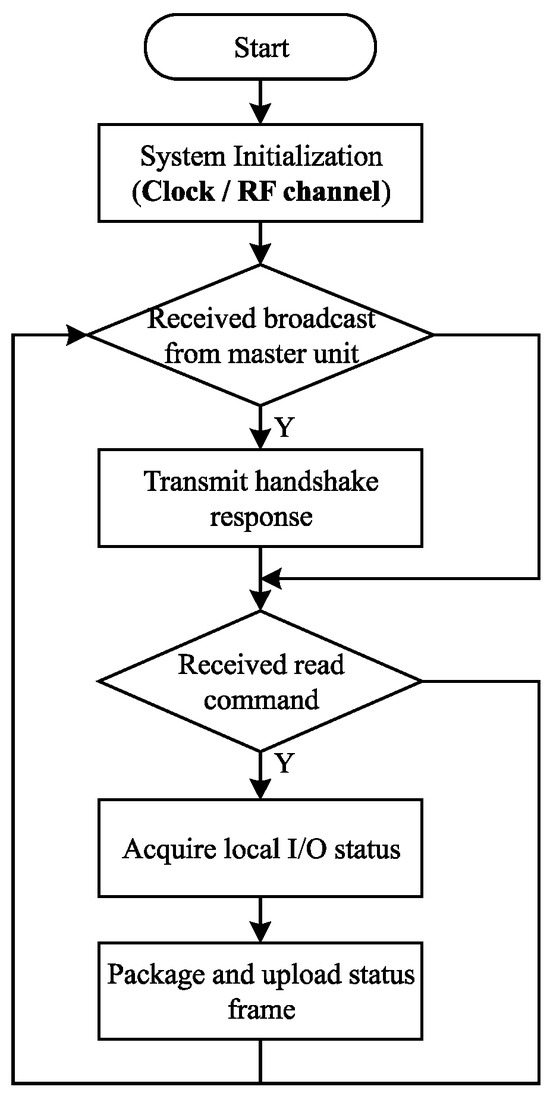
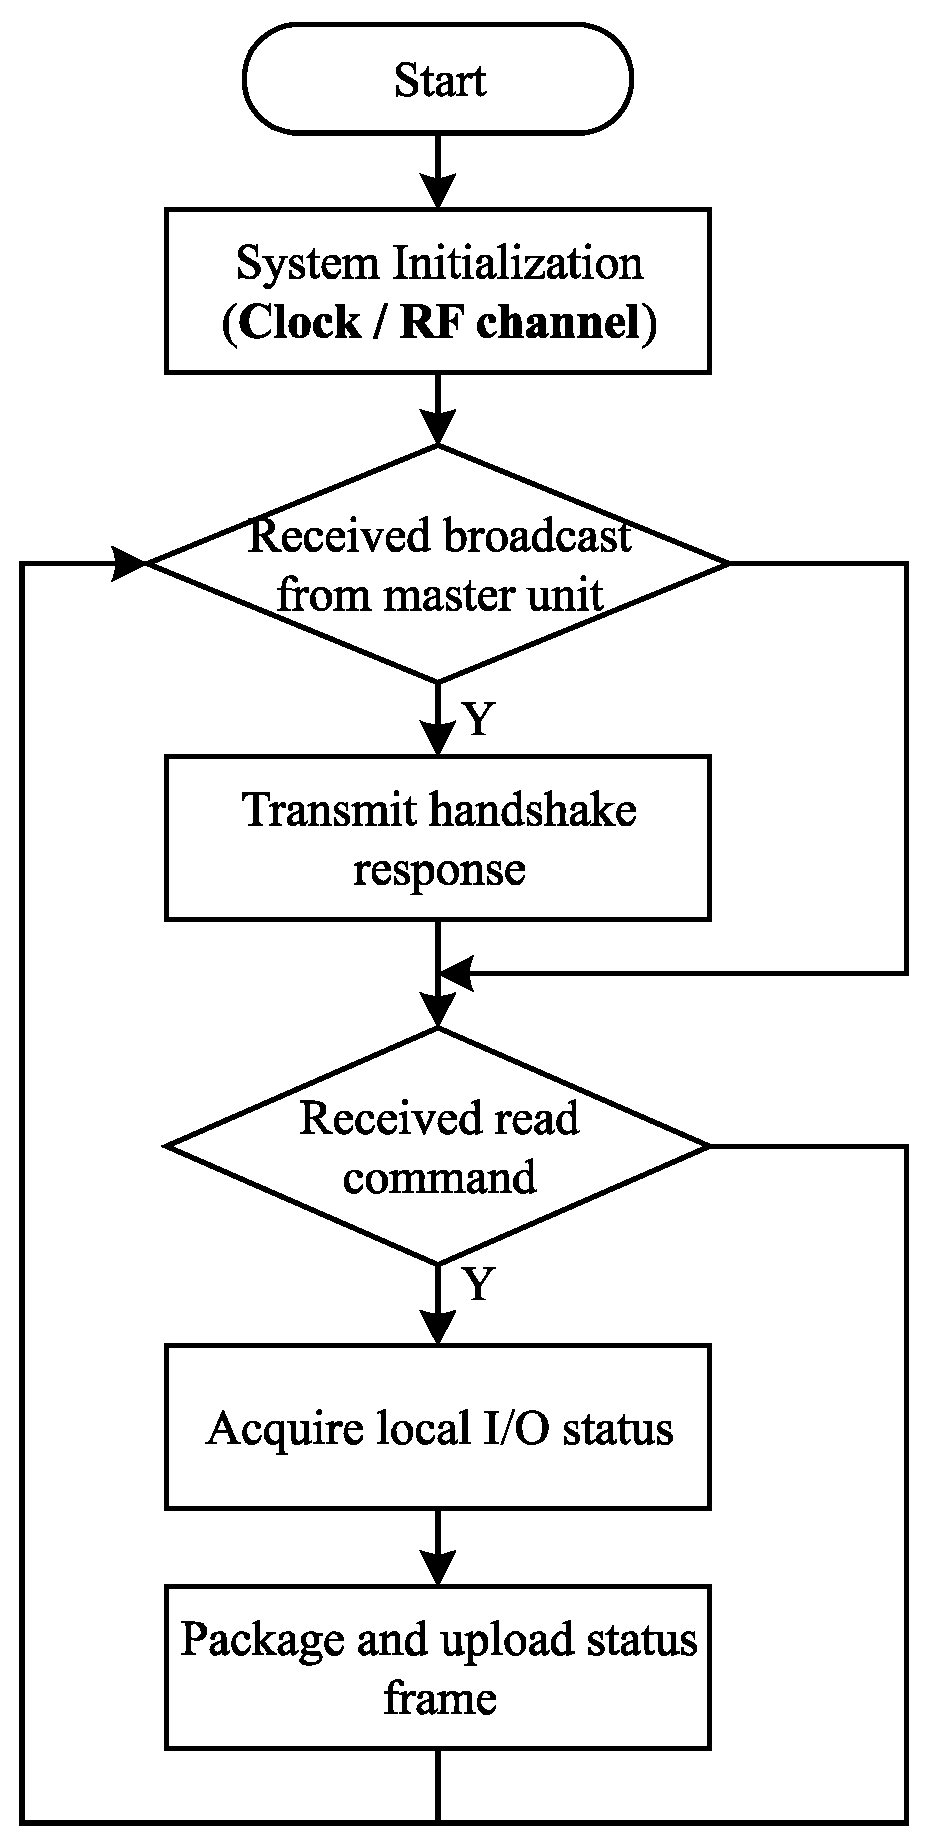
The operating sequence of a slave unit is shown in Figure 3. After initialization, the slave unit remains in the communication waiting state and continuously monitors the wireless channel for a broadcast request from the master unit.
Figure 3.
Slave-unit communication flow.
When a valid broadcast request is received, the slave unit first transmits a handshake response to indicate that the communication link is available. The slave unit then determines whether a state-read command has been received. If the command is valid, the slave controller acquires the local input/output status associated with the simulated circuit-breaker channels.
The acquired states are subsequently organized into a communication frame and transmitted to the master unit. After the transmission is completed, the slave unit returns to the waiting state for the next polling request. The communication frame contains the node-related and breaker-state information required by the master unit for subsequent state aggregation.
The master unit combines the state information obtained from all available slave units with the states of its locally connected simulated circuit breakers. When a valid response is received, the corresponding slave is marked as ONLINE, and its breaker-state information is incorporated into the global state vector. If no valid response is received within the predefined waiting interval, the slave is marked as TIMEOUT. The master unit then generates a single-point offline alarm while continuing the polling process for the remaining nodes.
3. Hardware and Software Implementation
3.1. Hardware System Design
The design of the proposed auxiliary verification device encompasses both hardware and software systems. The hardware system comprises the master and slave units, optocoupler isolation circuits, power supply modules, 220 V conventional switch simulation modules, 24 VDC automatic bus transfer (ABT) logic simulation modules, and 24 VDC low-voltage logic verification circuit breaker simulators. The software system, on the other hand, is specifically developed to meet the requirements of the remote monitoring system. Detailed descriptions of each unit are provided below.
3.1.1. Master Unit Design
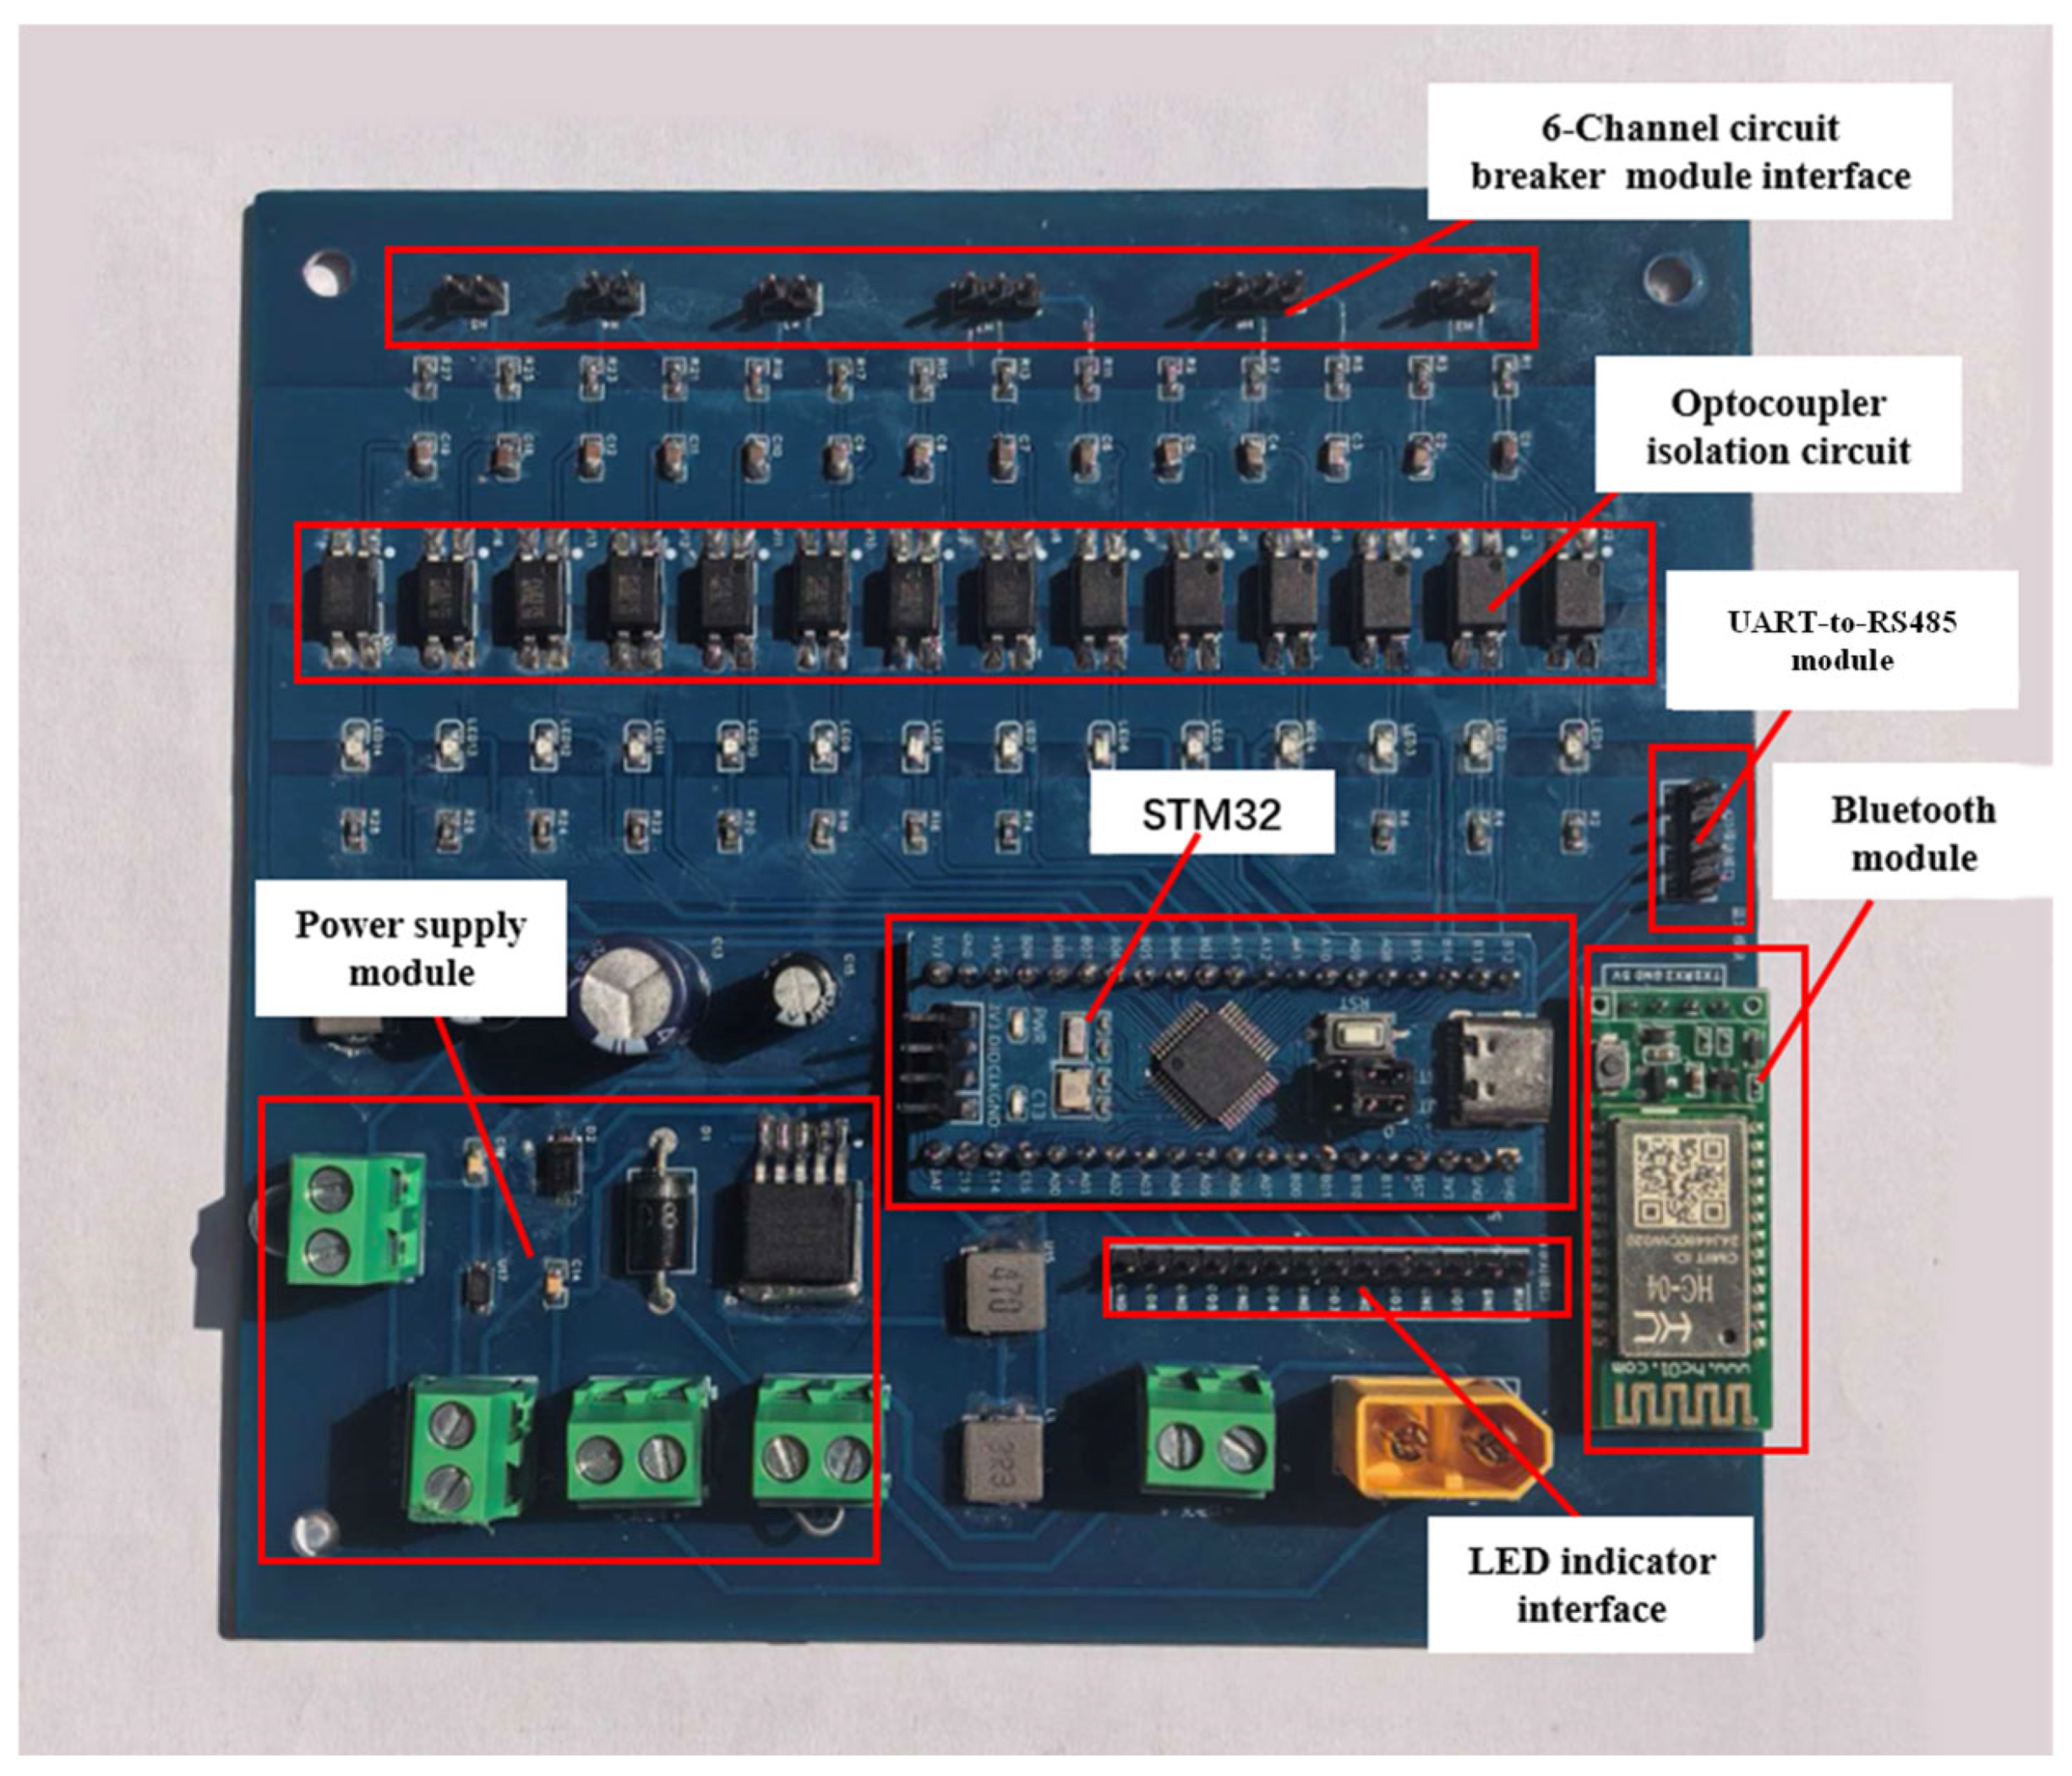
The internal circuitry of the master unit consists of seven functional modules: optocoupler isolation circuit, power supply module, Bluetooth communication module, LoRa wireless communication module, 220 V conventional switch simulation module, 24 VDC automatic bus transfer (ABT) logic simulation module, and a 24 VDC low-voltage logic verification circuit breaker simulator. The system architecture diagram of the master unit is shown in Figure 4, and the circuit board of the master unit is shown in Figure 5.These modules collectively enable real-time monitoring, data acquisition, and wireless communication with the distributed slave units, ensuring coordinated operation and reliable relay protection verification.
Figure 4.
System architecture diagram of the master unit.
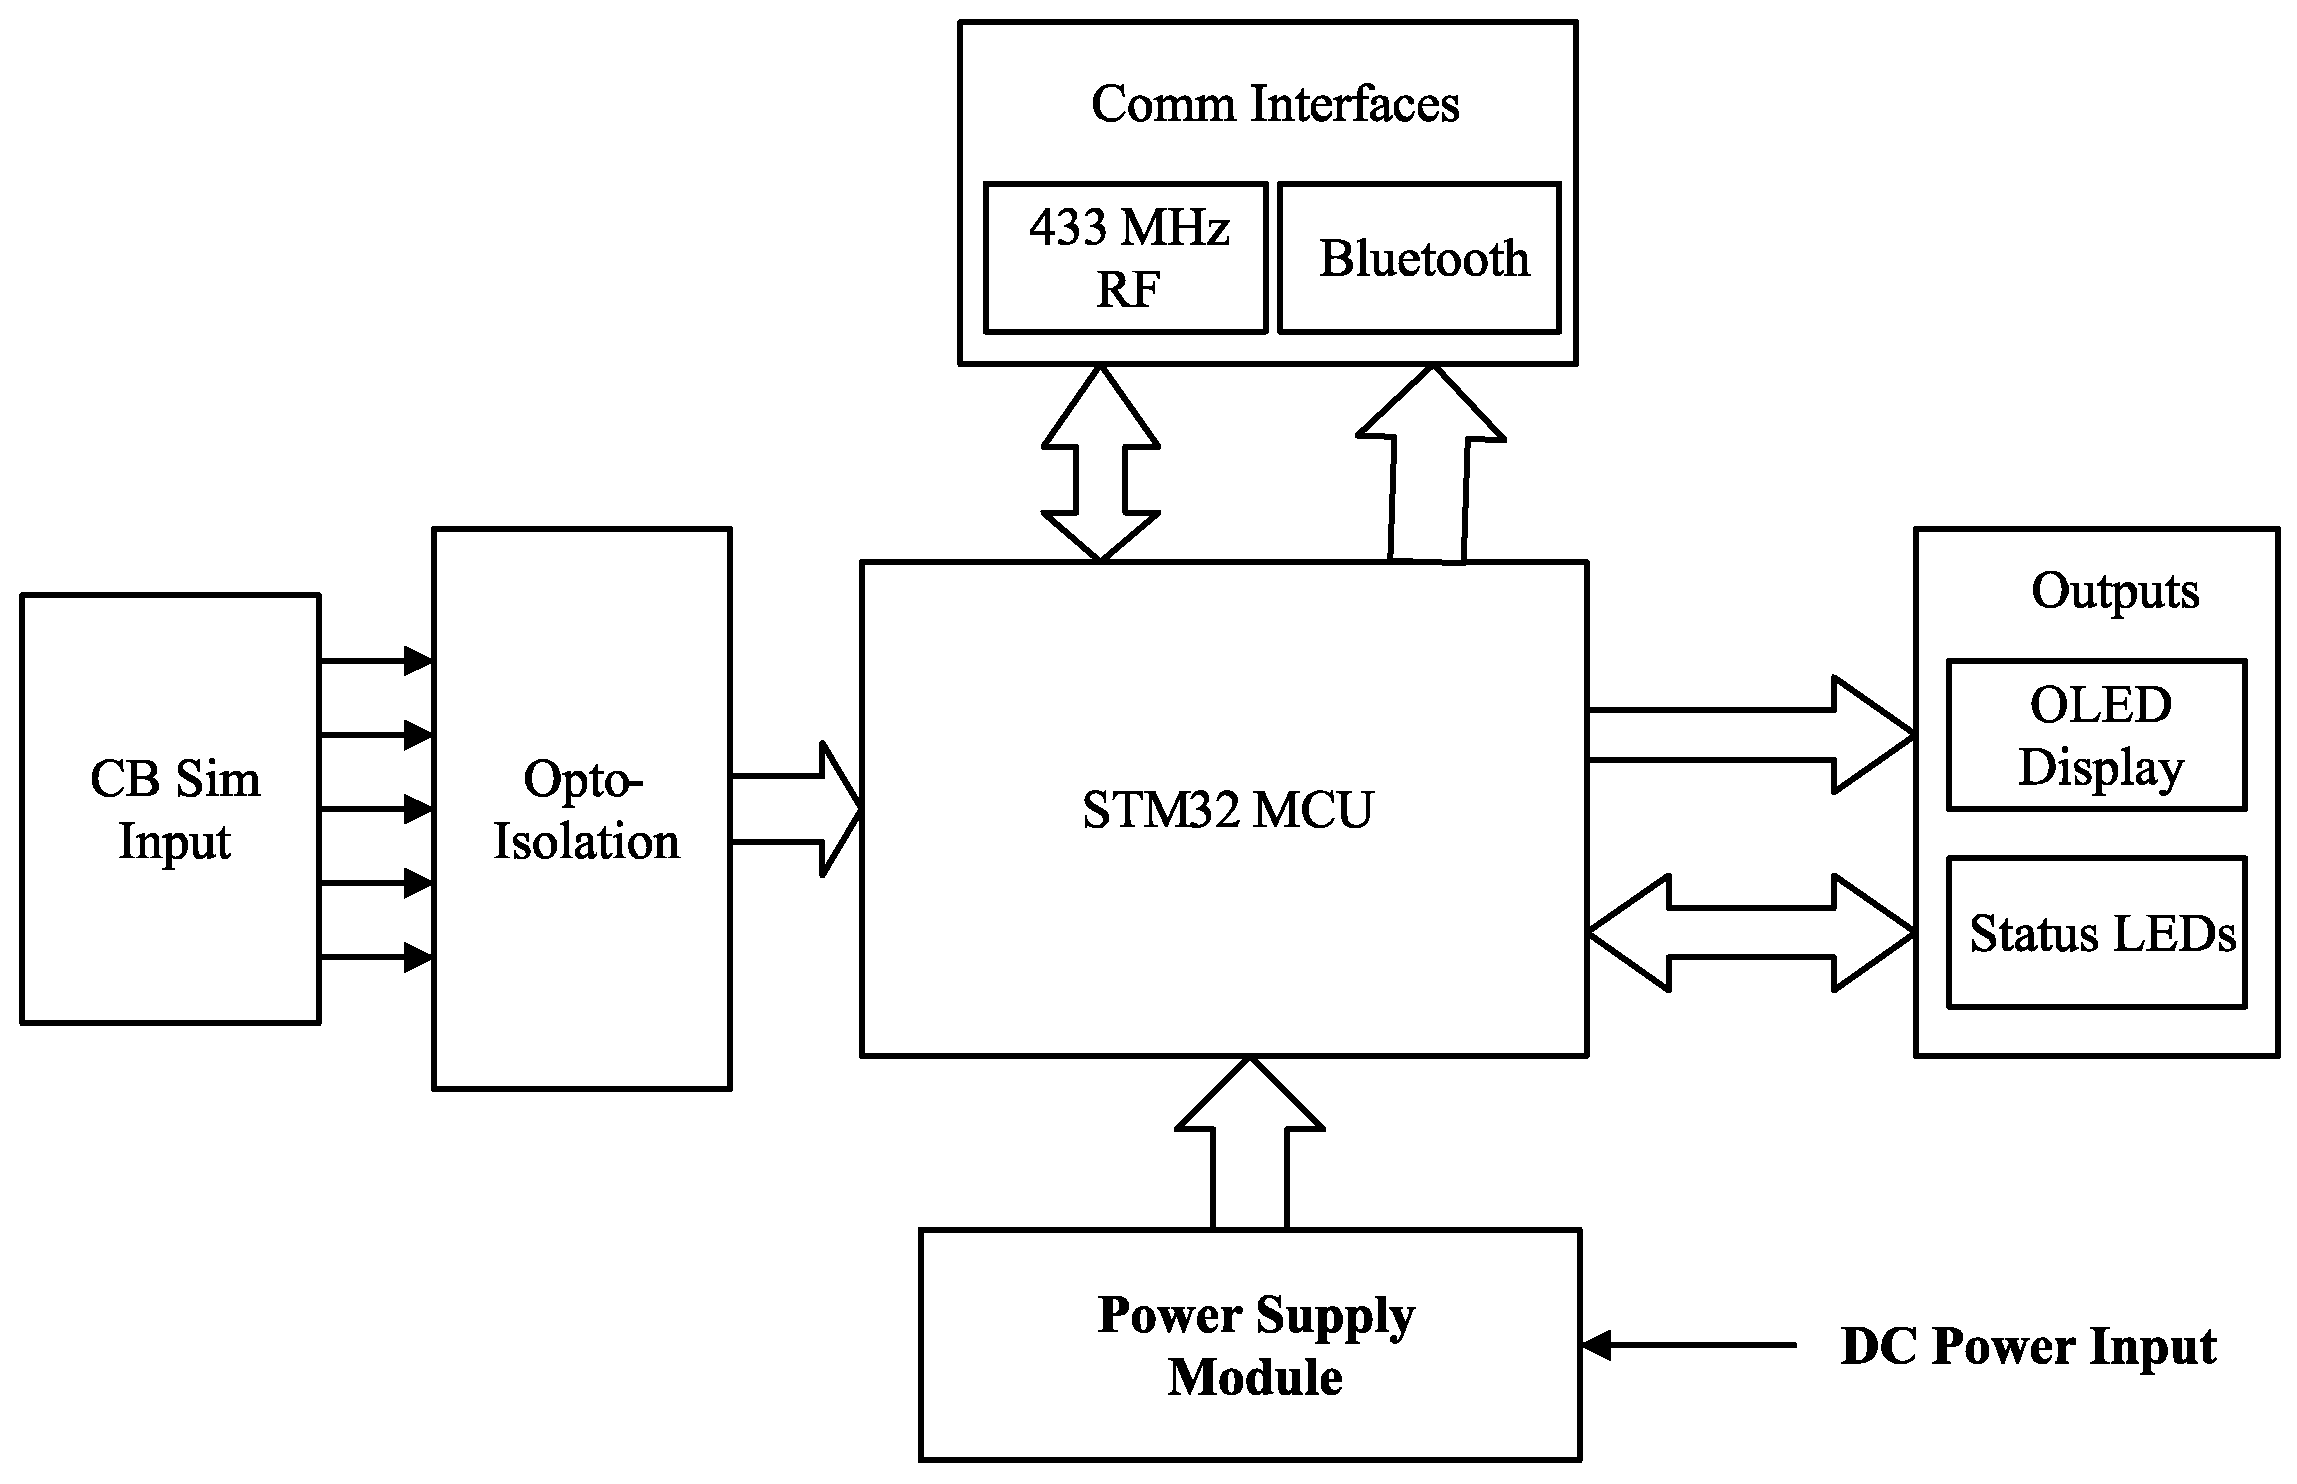
Figure 5.
Circuit board of the master unit.
3.1.2. Slave Unit Design
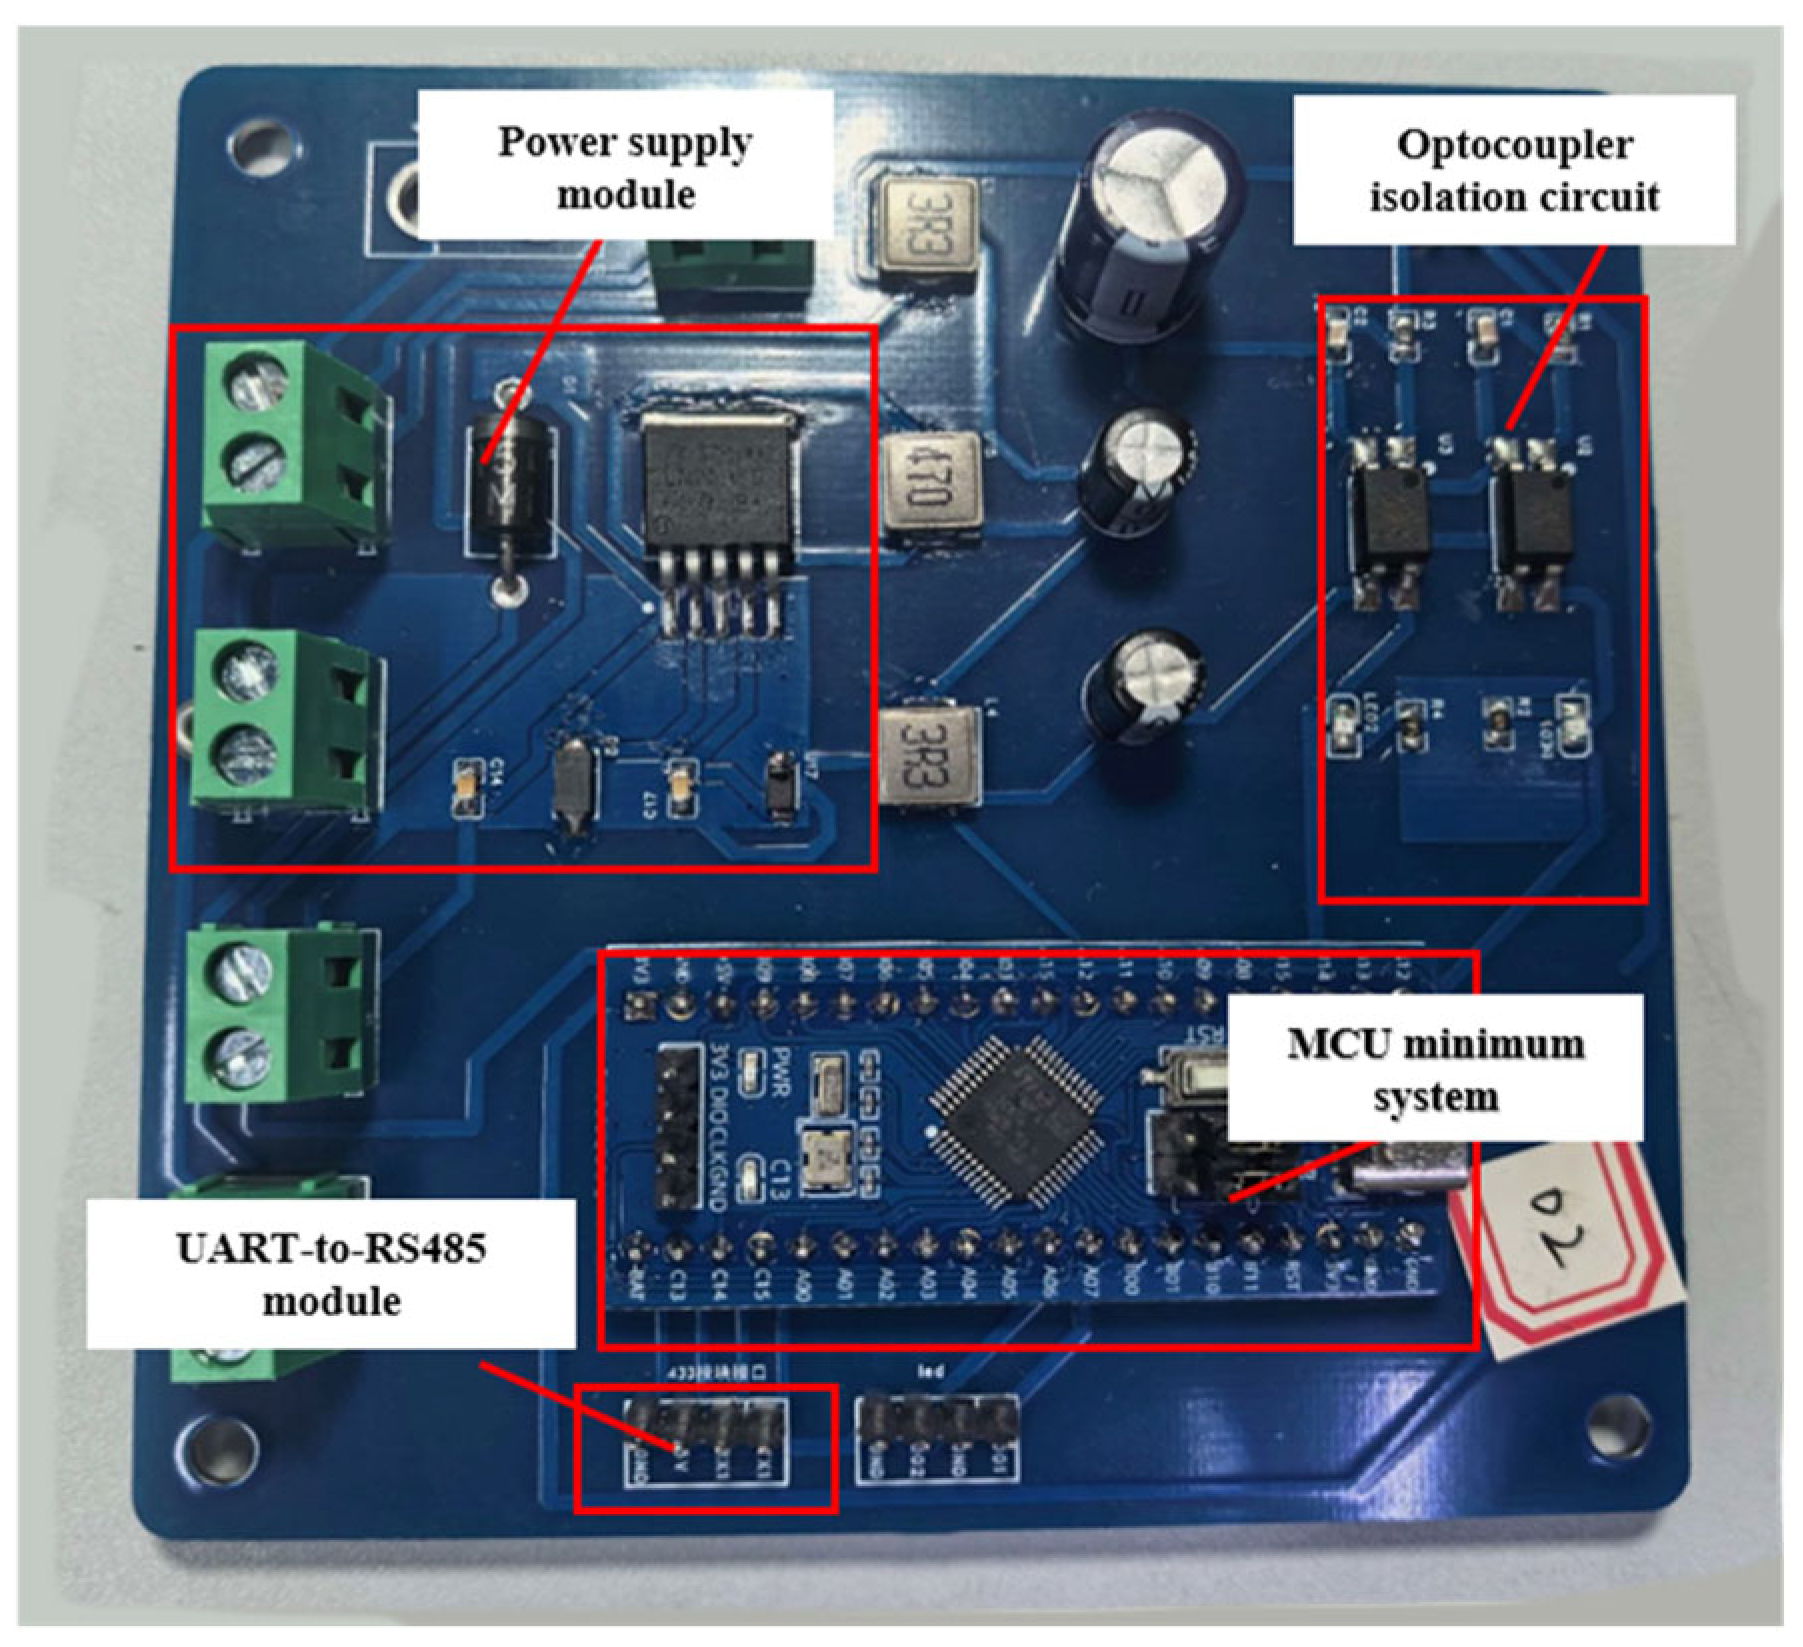
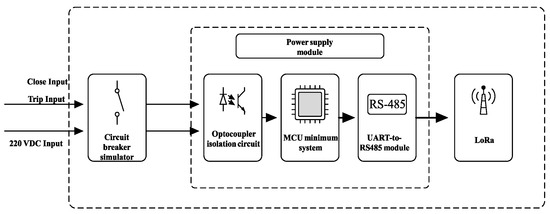
The slave unit functions as the transmitter for the master unit and similarly employs an STM32F103C8T6 microcontroller as its main controller. with the development board manufactured by Yahboom in Shenzhen, China. The system architecture of the slave unit is shown in Figure 6, and the circuit board of the slave unit is shown in Figure 7.
Figure 6.
System architecture diagram of the slave unit.
Through wired connections, this device integrates the wireless distributed 220 V operational actuation module (i.e., the circuit breaker simulator) into the trip and close circuits of an actual high-voltage circuit breaker. It receives the trip and close commands from the relay protection device, simulates the operational behavior of a real circuit breaker, and outputs the corresponding status feedback signals.
The STM32 microcontroller reads the feedback signals from the circuit breaker simulator and transmits the status information to the master unit via the LoRa wireless communication module. This effectively realizes remote monitoring and distributed state acquisition.
Figure 7.
Circuit board of the slave unit.
3.1.3. Signal Isolation and Power Supply Modules
Optocouplers are used to electrically isolate the protection-side signals from the MCU acquisition circuit. A first-order RC low-pass filter with a cutoff frequency of 15.9 Hz is employed at the 24 V signal input to suppress high-frequency interference. The isolated signal is then acquired by the MCU for breaker-state identification.
The master unit is powered by a 22.2 V lithium-ion battery. An LM2596-based buck converter is used to provide the 5 V supply required by the control and communication circuits. TVS protection and LC filtering are incorporated into the power input stage to improve power-interface robustness under field operating conditions. As the converter and protection circuits are conventional implementations, their detailed schematics are omitted for brevity.
3.1.4. Communication Module
The communication module consists of Bluetooth and LoRa wireless communication units. Bluetooth is used for communication between the master unit and the monitoring terminal, while LoRa provides wireless communication between the master unit and distributed sub-units.
An HC-06 Bluetooth module was used for short-range communication between the master unit and the Android-based monitoring terminal. The breaker-state information collected by the master unit is transmitted to the terminal through the Bluetooth serial interface for real-time monitoring.
LoRa is used for wireless communication between the master unit and distributed sub-units. A star network topology is adopted, with the master unit serving as the central node. The master unit periodically polls the sub-units and collects their simulated breaker states.
Considering the communication distance and electromagnetic interference in substations, the LoRa center frequency, bandwidth, and spreading factor were set to 433 MHz, 250 kHz, and SF7, respectively. A CR of 4/6 was used to balance communication reliability and transmission efficiency. These parameters prioritize communication reliability for the low-rate breaker-state data used in the proposed system.
The LoRa communication parameter configuration is shown in Table 3.
Table 3.
LoRa communication parameter configuration.
3.1.5. 220 V Conventional Switch Simulation Module
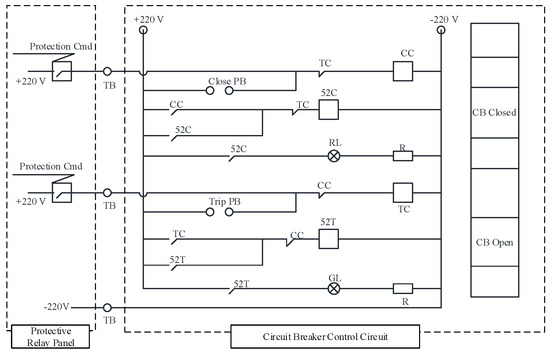
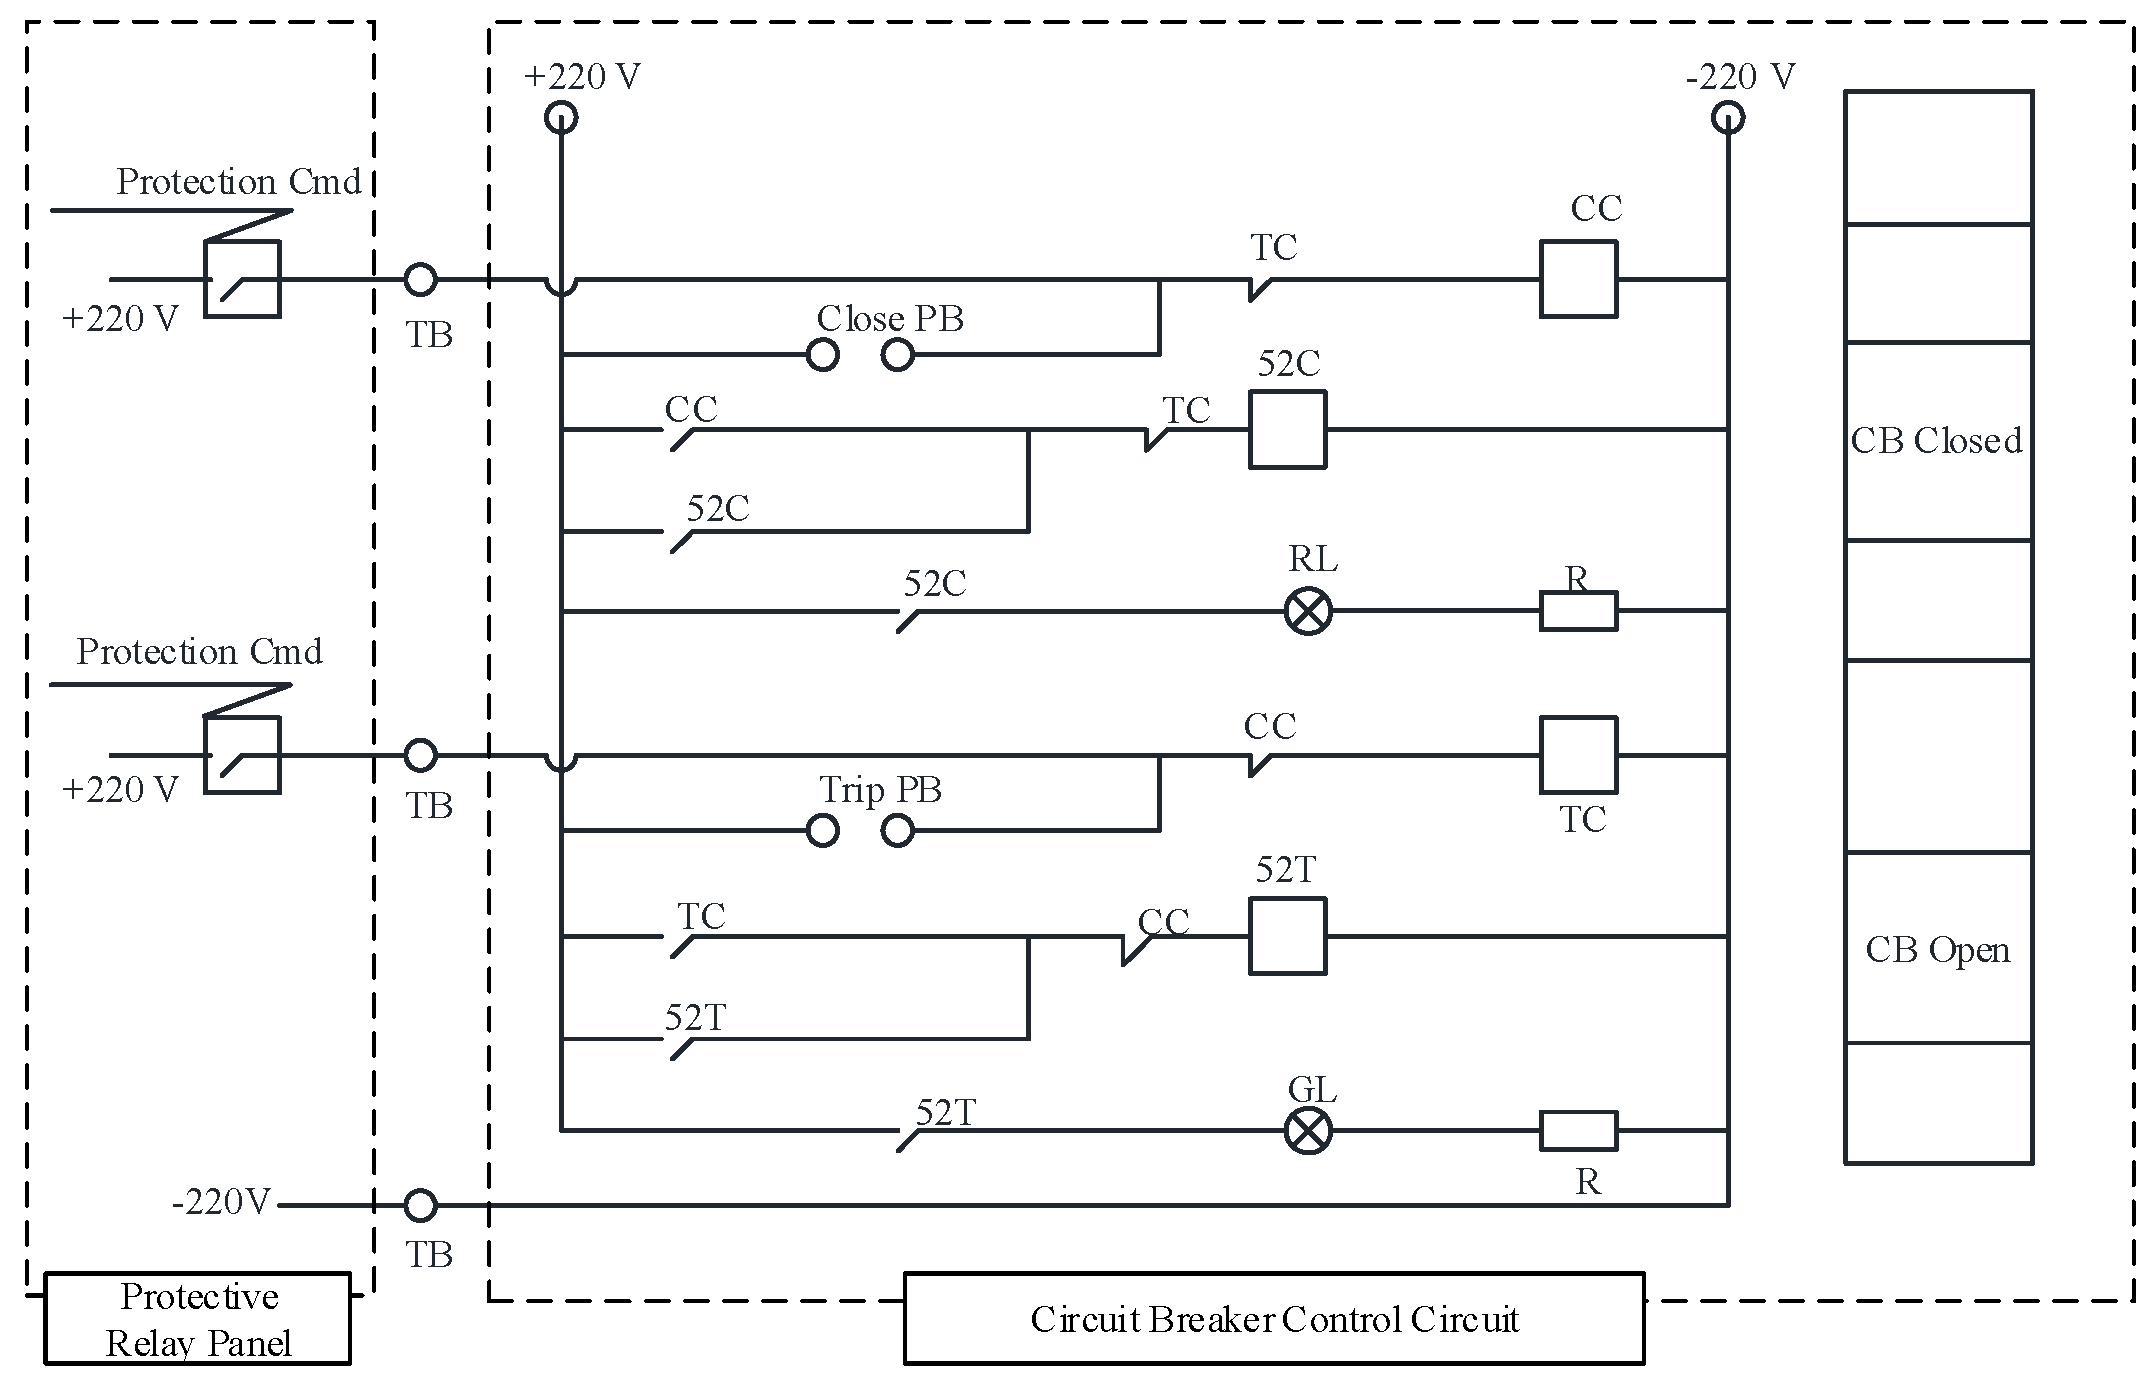
The 220 V conventional switch simulation module is primarily used to simulate the tripping and closing operations of high-voltage circuit breakers in substations. Constructed using 220 V DC relays, the module incorporates closing circuits, tripping circuits, and state-holding logic. This enables functions such as simulating circuit breaker “Close” and “Trip” positions, as well as manual trip/close operations [20].
As shown in Figure 8, the interface receives the closing and tripping commands from the protection device through separate control paths. The corresponding closing and tripping relays actuate the simulated switching circuit, while auxiliary position contacts provide the resulting breaker-state feedback. The control logic prevents contradictory closing and tripping operations and maintains the simulated state after the corresponding operation.
Figure 8.
Schematic diagram of the 220 v conventional switch simulation module.
For a single simulated breaker channel, the operating sequence can be represented as:
The resulting position information is simultaneously returned to the protection device and acquired by the local controller for system-level monitoring. Unlike a direct point-by-point signal check, the simulated breaker maintains the corresponding operating state after the control action. This enables the protection system to continue its logical sequence using the simulated breaker position as feedback.
3.1.6. 24 VDC Automatic Bus Transfer (ABT) Logic Simulation Module
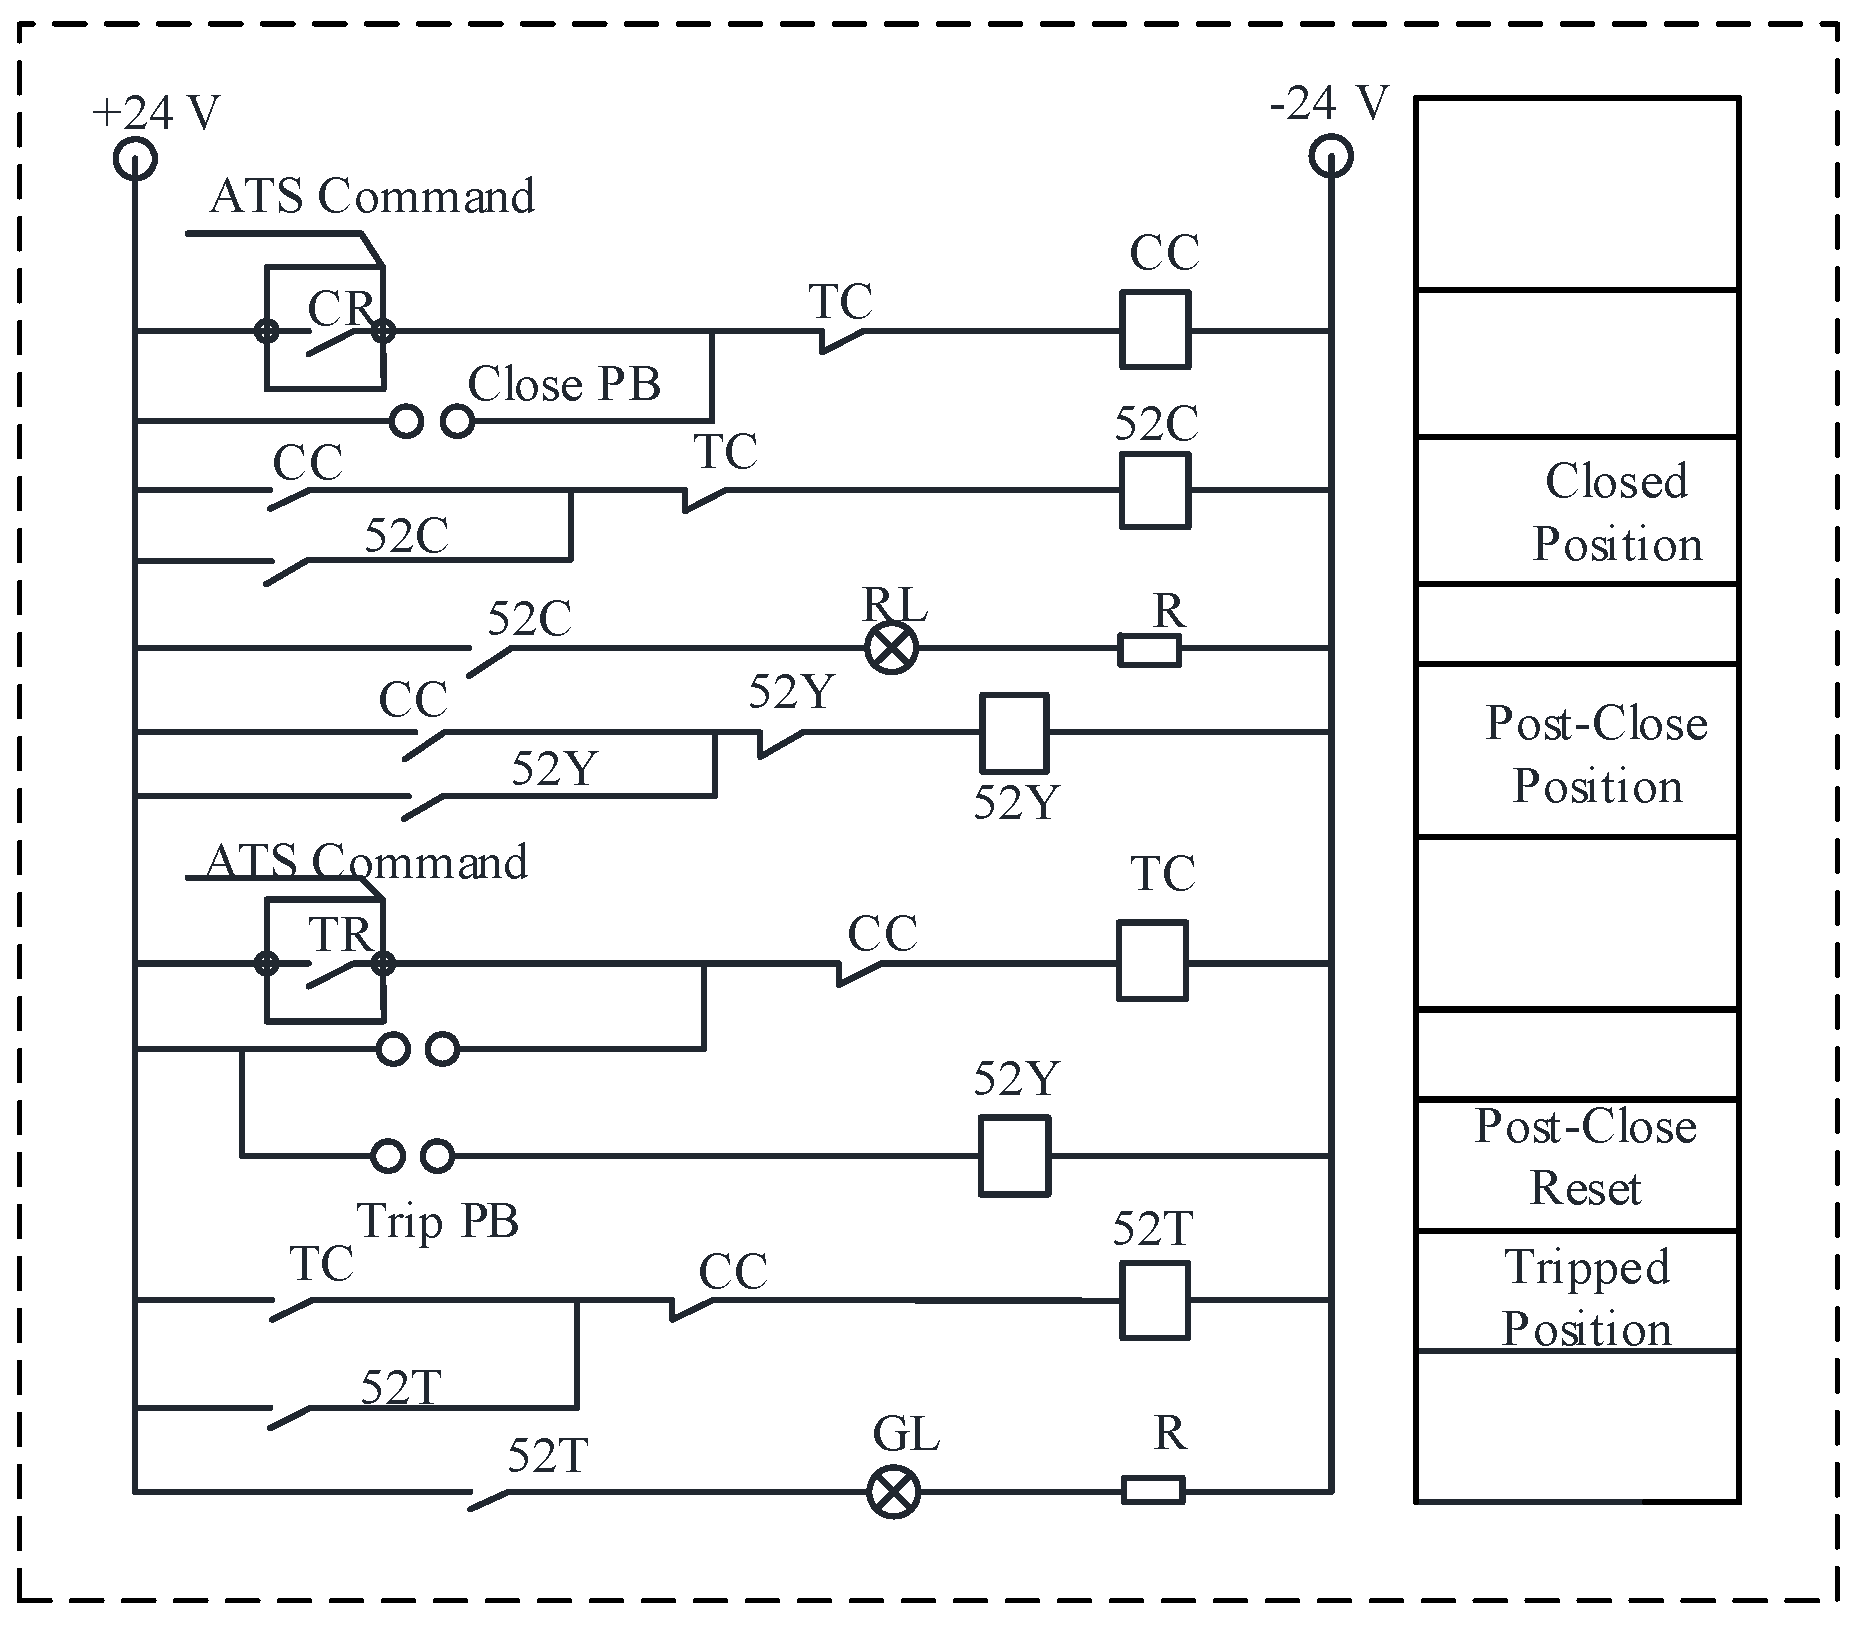
The 24 VDC automatic bus transfer (ABT) logic simulation module is primarily designed for the logic verification of ABT devices. The module employs 24 VDC relays to construct the required logic circuits. Since ABT devices must monitor the status of both the main and standby power supply circuit breakers simultaneously, two independent circuit breaker simulators are incorporated to emulate the operational status and switching sequences of breakers on different power supply sides [19].
Two independent simulated breaker channels are used to represent the main and standby power supply breakers. Their states are evaluated jointly because the subsequent transfer operation depends on the operating condition of both breakers. Under normal conditions, the state vector is represented as:
When an automatic trip command is generated for the main breaker, the simulated state changes accordingly. The transfer process can therefore be represented as:
In addition to the breaker position, the module retains the post-closing interlock memory associated with an automatic transfer operation. After an automatic trip and subsequent standby closing operation, the post-closing state is maintained by the interlock circuit. This state can only be cleared through the specified manual reset operation. The function allows the verification system to distinguish an automatic transfer sequence from a manually configured initial condition. Accordingly, the position sequence in (6) is accompanied by the auxiliary memory state defined in (3), which remains active until the corresponding manual RESET operation is performed.
As shown in Figure 9, the main-breaker and standby-breaker channels are therefore not treated as isolated switching outputs. Instead, their state transitions are considered as a coupled sequence. The module consequently provides a practical means of reproducing the state relationships required for ABT logic verification, including main-breaker tripping, standby-breaker closing, post-closing state retention, and manual reset.
Figure 9.
Schematic Diagram of the 24 VDC ABT Logic Simulation Module.
3.1.7. 24 VDC Low-Voltage Logic Verification Circuit Breaker Simulator
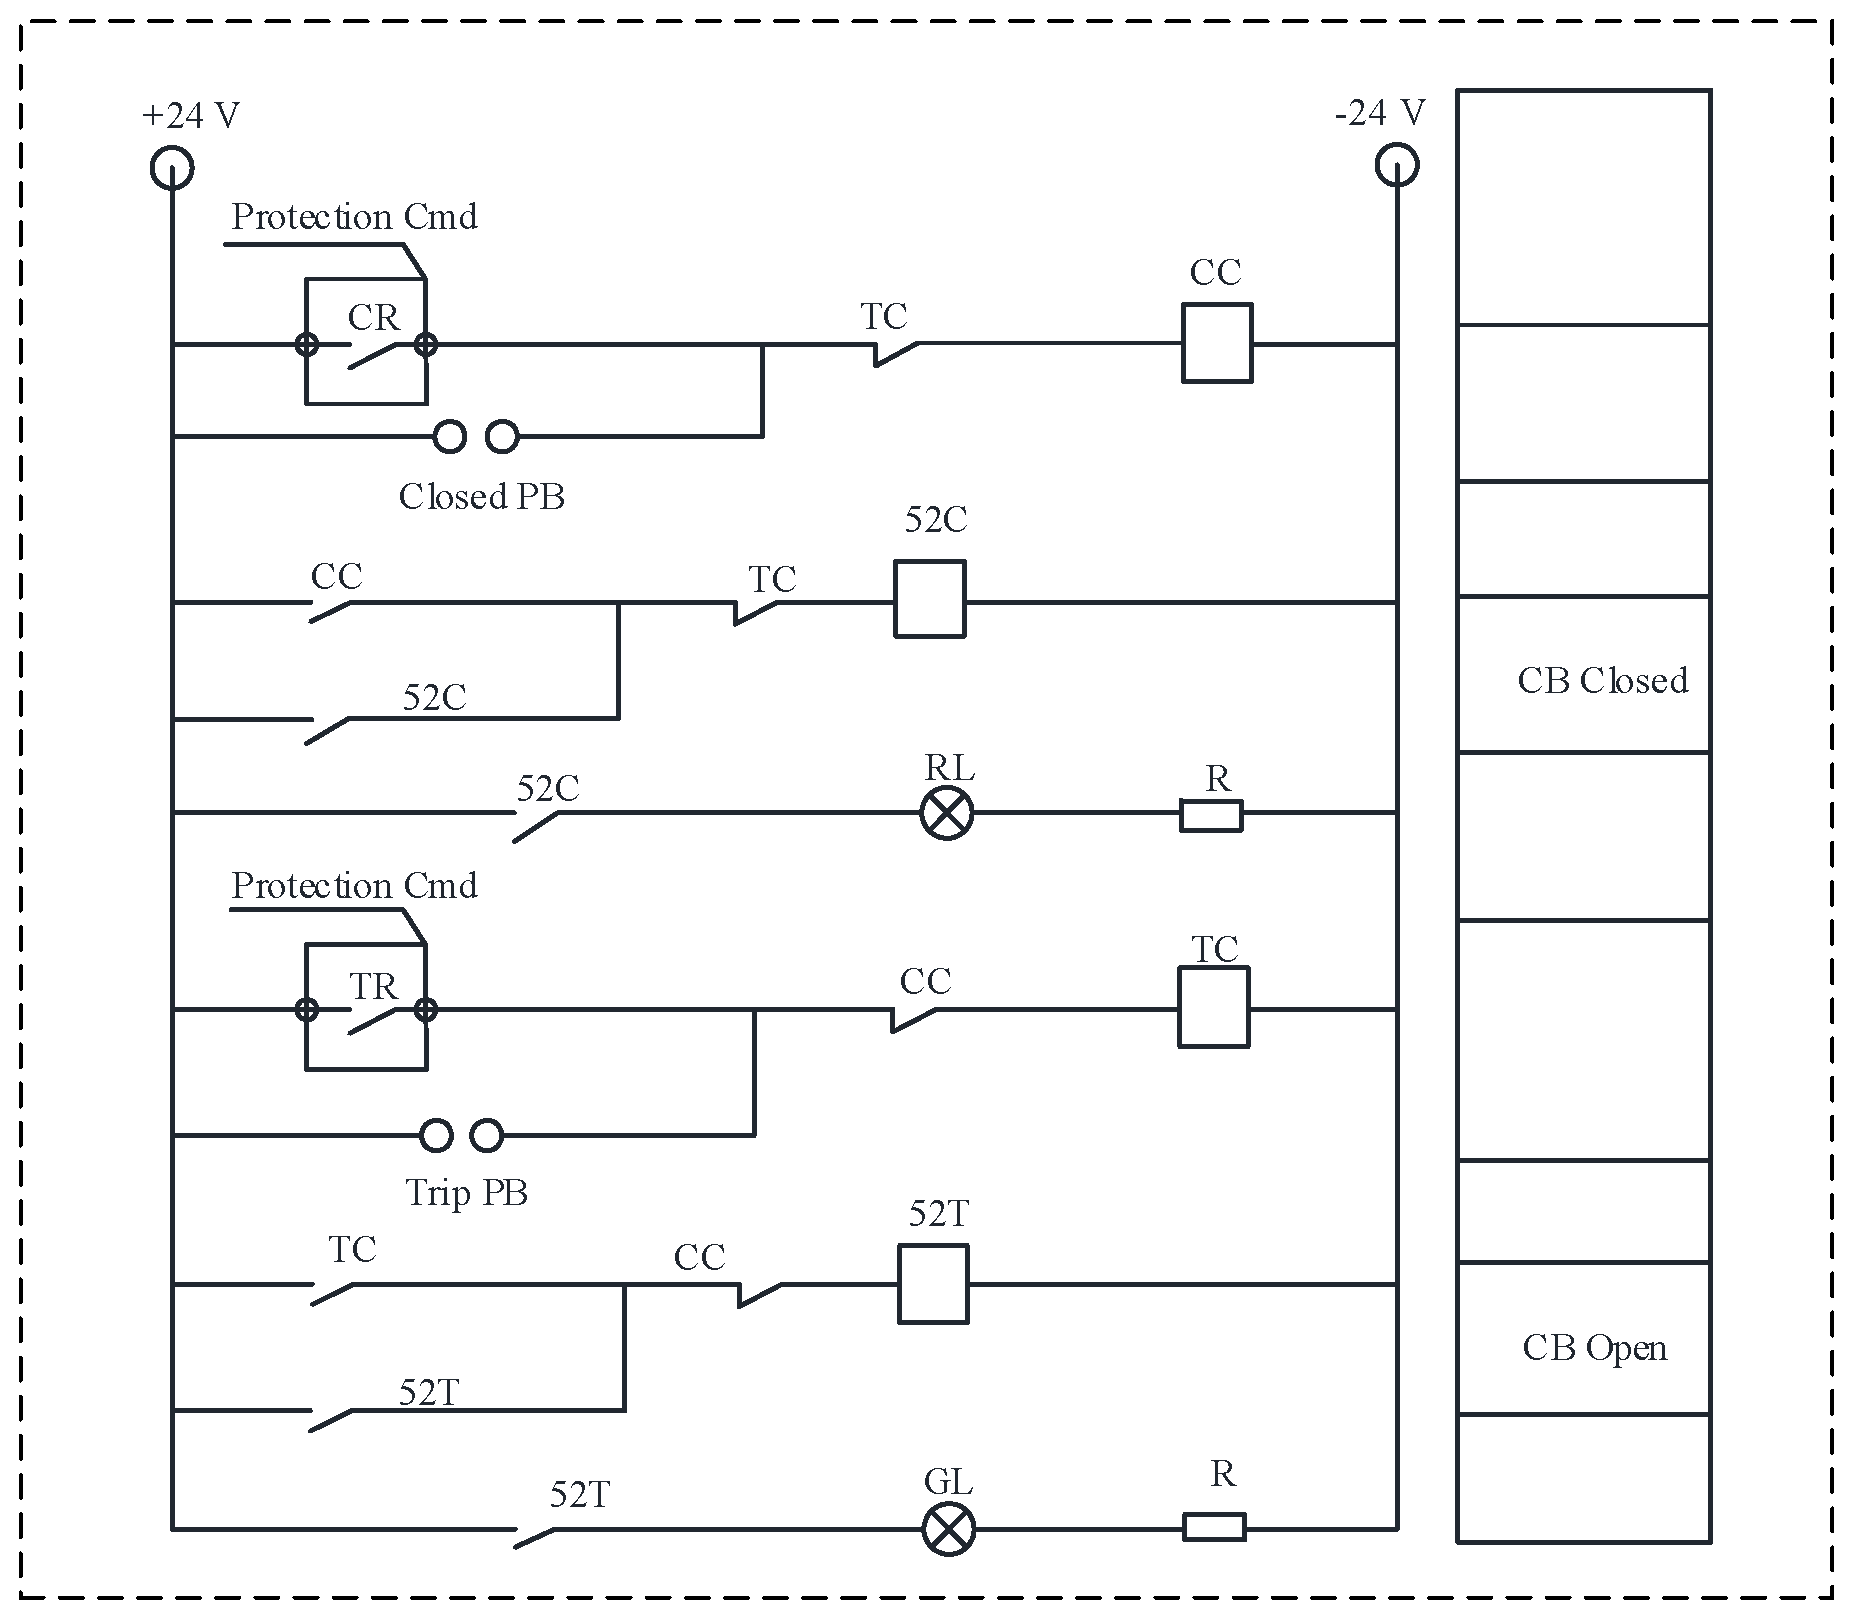
The 24 VDC low-voltage logic verification circuit breaker simulator is designed for the state simulation and verification of low-voltage logic outputs in relay protection devices. The module employs 24 VDC relays to construct the circuit breaker logic circuits.
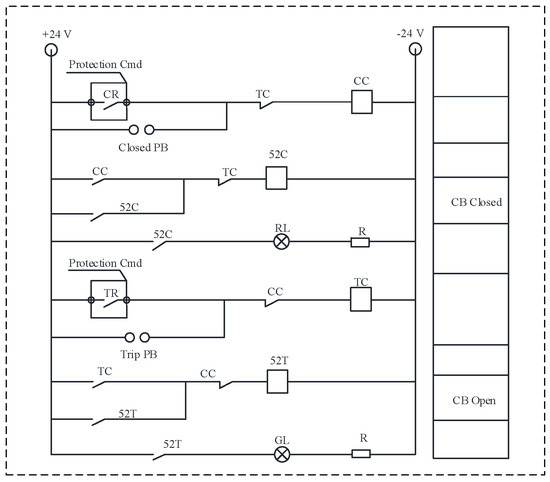
Protection systems such as busbar protection, main transformer protection, and underfrequency or undervoltage load shedding may generate multiple trip outputs during one protection operation. A single simulated breaker channel is therefore insufficient to reproduce the complete output relationship. To address this requirement, multiple independent simulated breaker channels are integrated into the master unit. Each channel is assigned to a corresponding protection output and provides an independent position-feedback signal.
For simulated breaker channels, the overall operating condition can be represented by:
Each channel performs local switching and state holding according to the received protection command. The corresponding auxiliary contacts generate the simulated breaker-position feedback, while the local acquisition circuit records the resulting state. Therefore, multiple protection outputs can be evaluated not only individually but also according to their relative operating sequence and timing relationship.
For example, when several protection outputs are activated within one protection event, the corresponding simulated breaker channels can produce a coordinated state sequence:
where each state vector represents the combined operating condition of all simulated breaker channels at the corresponding time.
This configuration extends the proposed state-emulation method from single-breaker verification to multi-output protection schemes. It enables the verification of simultaneous or sequential breaker-state changes, output timing relationships, and interlocking conditions, thereby allowing the correctness of relay protection logic relationships to be verified without de-energizing the circuit breakers or repeatedly operating the associated high-voltage circuit breakers.
As illustrated in Figure 10, the protection command is applied to the corresponding relay-based channel, and the auxiliary contacts return the simulated breaker position to the protection interface. The contribution of the module therefore lies in the coordinated multi-channel state representation and feedback mechanism rather than in the conventional relay logic used for switching and self-holding.
Figure 10.
Schematic diagram of the 24 VDC low-voltage logic verification circuit breaker simulator.
3.2. Remote Monitoring Communication System Design
During on-site testing, the master unit must operate in coordination with multiple slave units. To enable the effective management and monitoring of the slave units and circuit breaker simulators, the monitoring system features a human–machine interface (HMI) designed to rapidly present the current system status. Through this interface, testing personnel can quickly and intuitively grasp the actual operational conditions of each device. Furthermore, to facilitate on-site procedures, each circuit breaker simulator can be renamed according to specific field conditions, thereby optimizing the testing workflow.
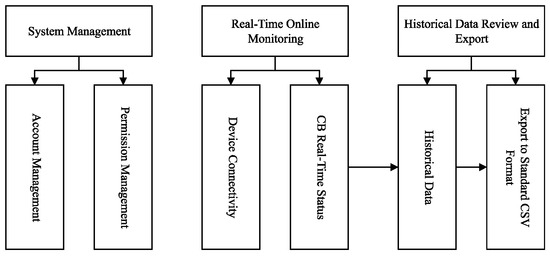
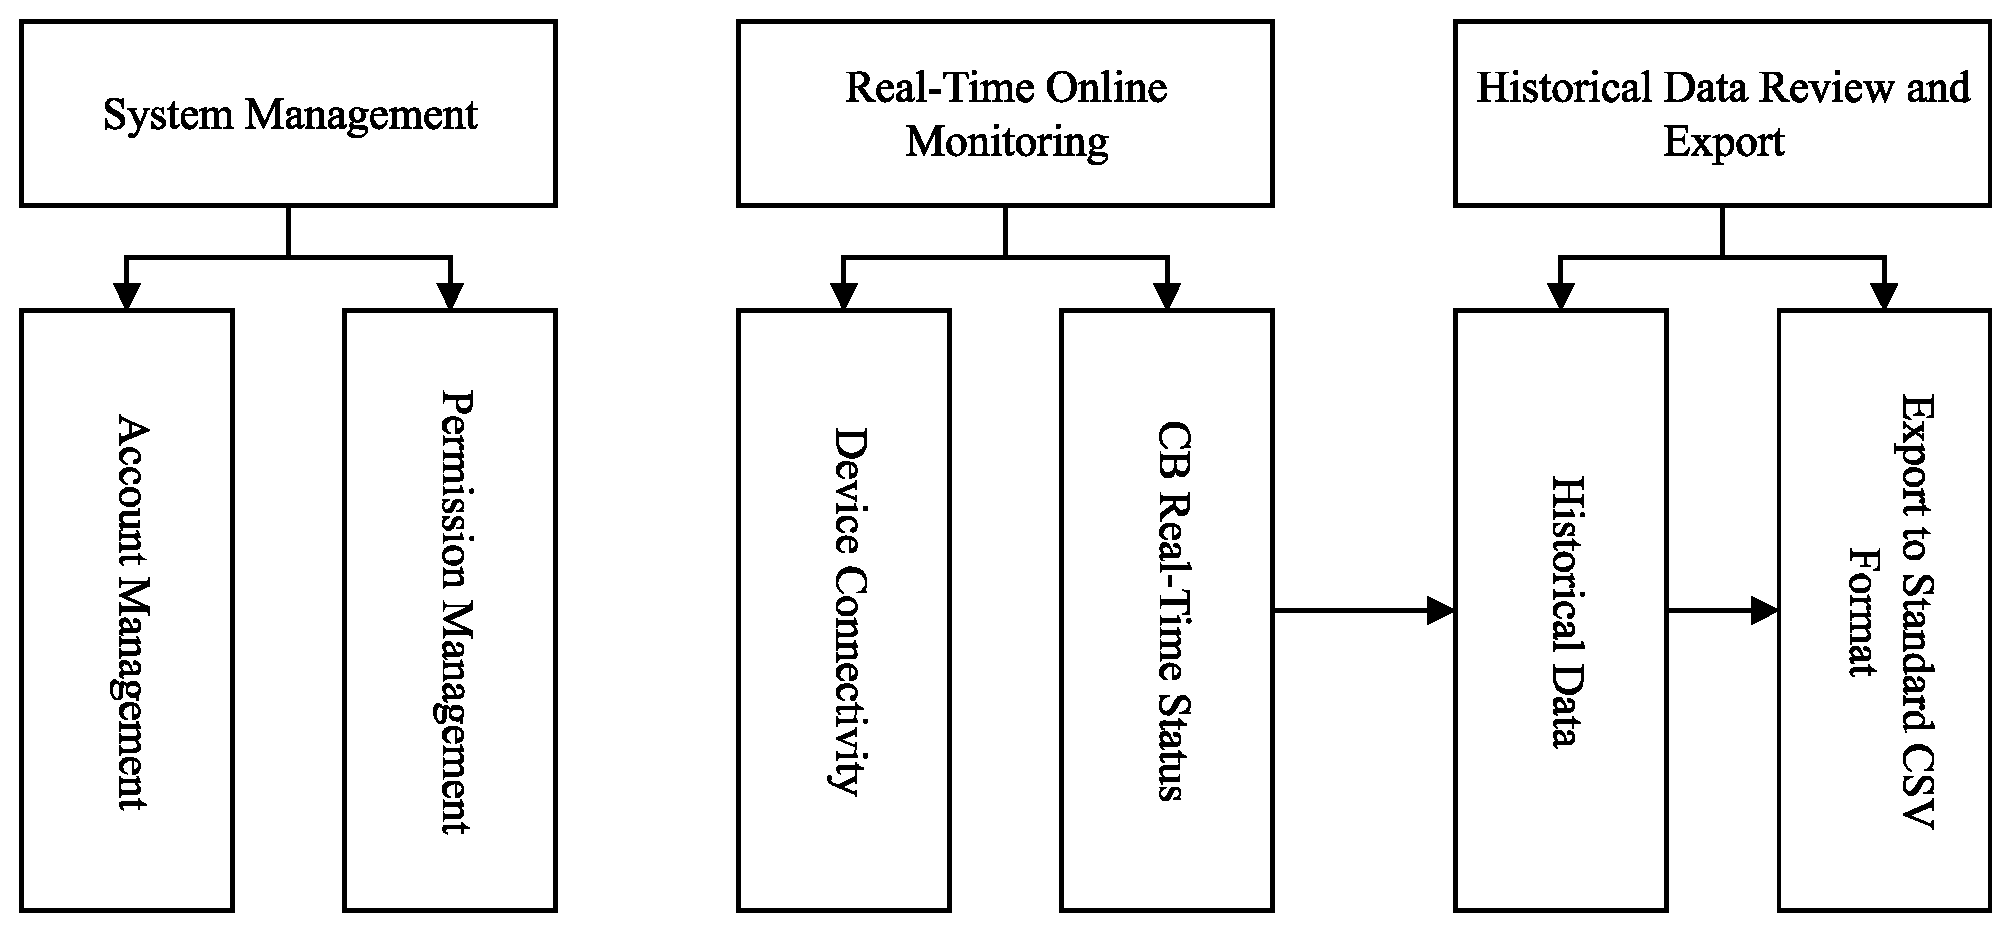
The remote monitoring communication system utilizes LoRa wireless technology to achieve point-to-multipoint long-distance data transmission. As shown in Figure 11, the system functions are divided into three modules: system management, online monitoring, and historical data review and export.
Figure 11.
Architecture of the remote monitoring communication system.
3.2.1. System Management
Throughout system operation and management, a comprehensive user permission management mechanism is implemented to ensure system security, operational stability, and equipment reliability [21]. Users must enter a valid account and password to access the system and perform operations. Based on their respective permission levels, the system grants users access to corresponding functional interfaces and operational authorities.
The highest permission level is assigned to the administrator. Upon logging in, the administrator can centrally manage all system users—including user information maintenance, permission assignment, and functional access control—thereby ensuring standardized and secure system operations.
Personnel responsible for on-site verification are designated as testing personnel. They are authorized to execute operations such as powering equipment on and off, as well as switching device states. When the number of system devices or functional requirements changes, testing personnel can reconfigure system parameters and functional modules according to practical application demands to improve operational efficiency and resource utilization. The standardized execution of these equipment control operations ensures personnel safety and stable system operation throughout the verification process.
3.2.2. Online Monitoring
The online monitoring function provides centralized visualization of the operating states of the simulated circuit breakers. The master unit collects the breaker-position information from the local and distributed slave units and transmits the aggregated data to the HMI.
The HMI displays the real-time position of each simulated circuit breaker, allowing the operator to simultaneously monitor multiple breaker states during the verification process. The breaker names can be configured according to the corresponding protection circuit, which facilitates identification of individual channels during on-site testing.
In addition to breaker positions, the monitoring interface indicates the communication status of the slave units. A communication timeout is identified as an offline condition, allowing abnormal communication states to be detected during verification. The centralized display therefore provides a unified view of distributed breaker states and communication conditions, supporting the observation of coordinated protection operations.
3.2.3. Historical Data Review Function
To achieve the effective management of test data, a historical data storage and query module is developed based on the Android built-in database. In this module, a single whole-group operational test is defined as the basic recording unit. It comprehensively records information during the testing process, including the “Trip” and “Close” state transitions of the circuit breaker simulators and their operational timing sequences, alongside the corresponding test dates and related operating conditions.
Furthermore, the system supports exporting historical data in the universal CSV format, thereby facilitating subsequent data organization, analysis, and long-term archival management. Consequently, the traceability and integrity of the test records are significantly enhanced, providing reliable data support for relay protection verification and maintenance management.
4. Experimental and Field Verification
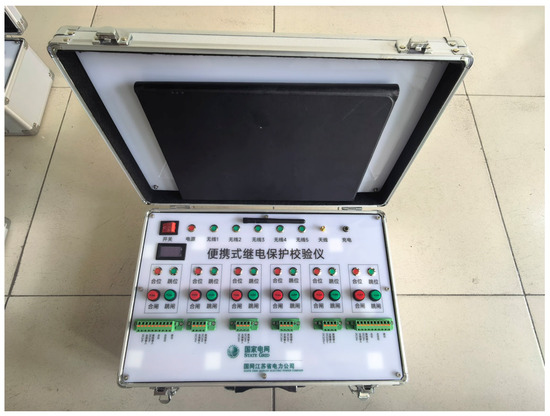
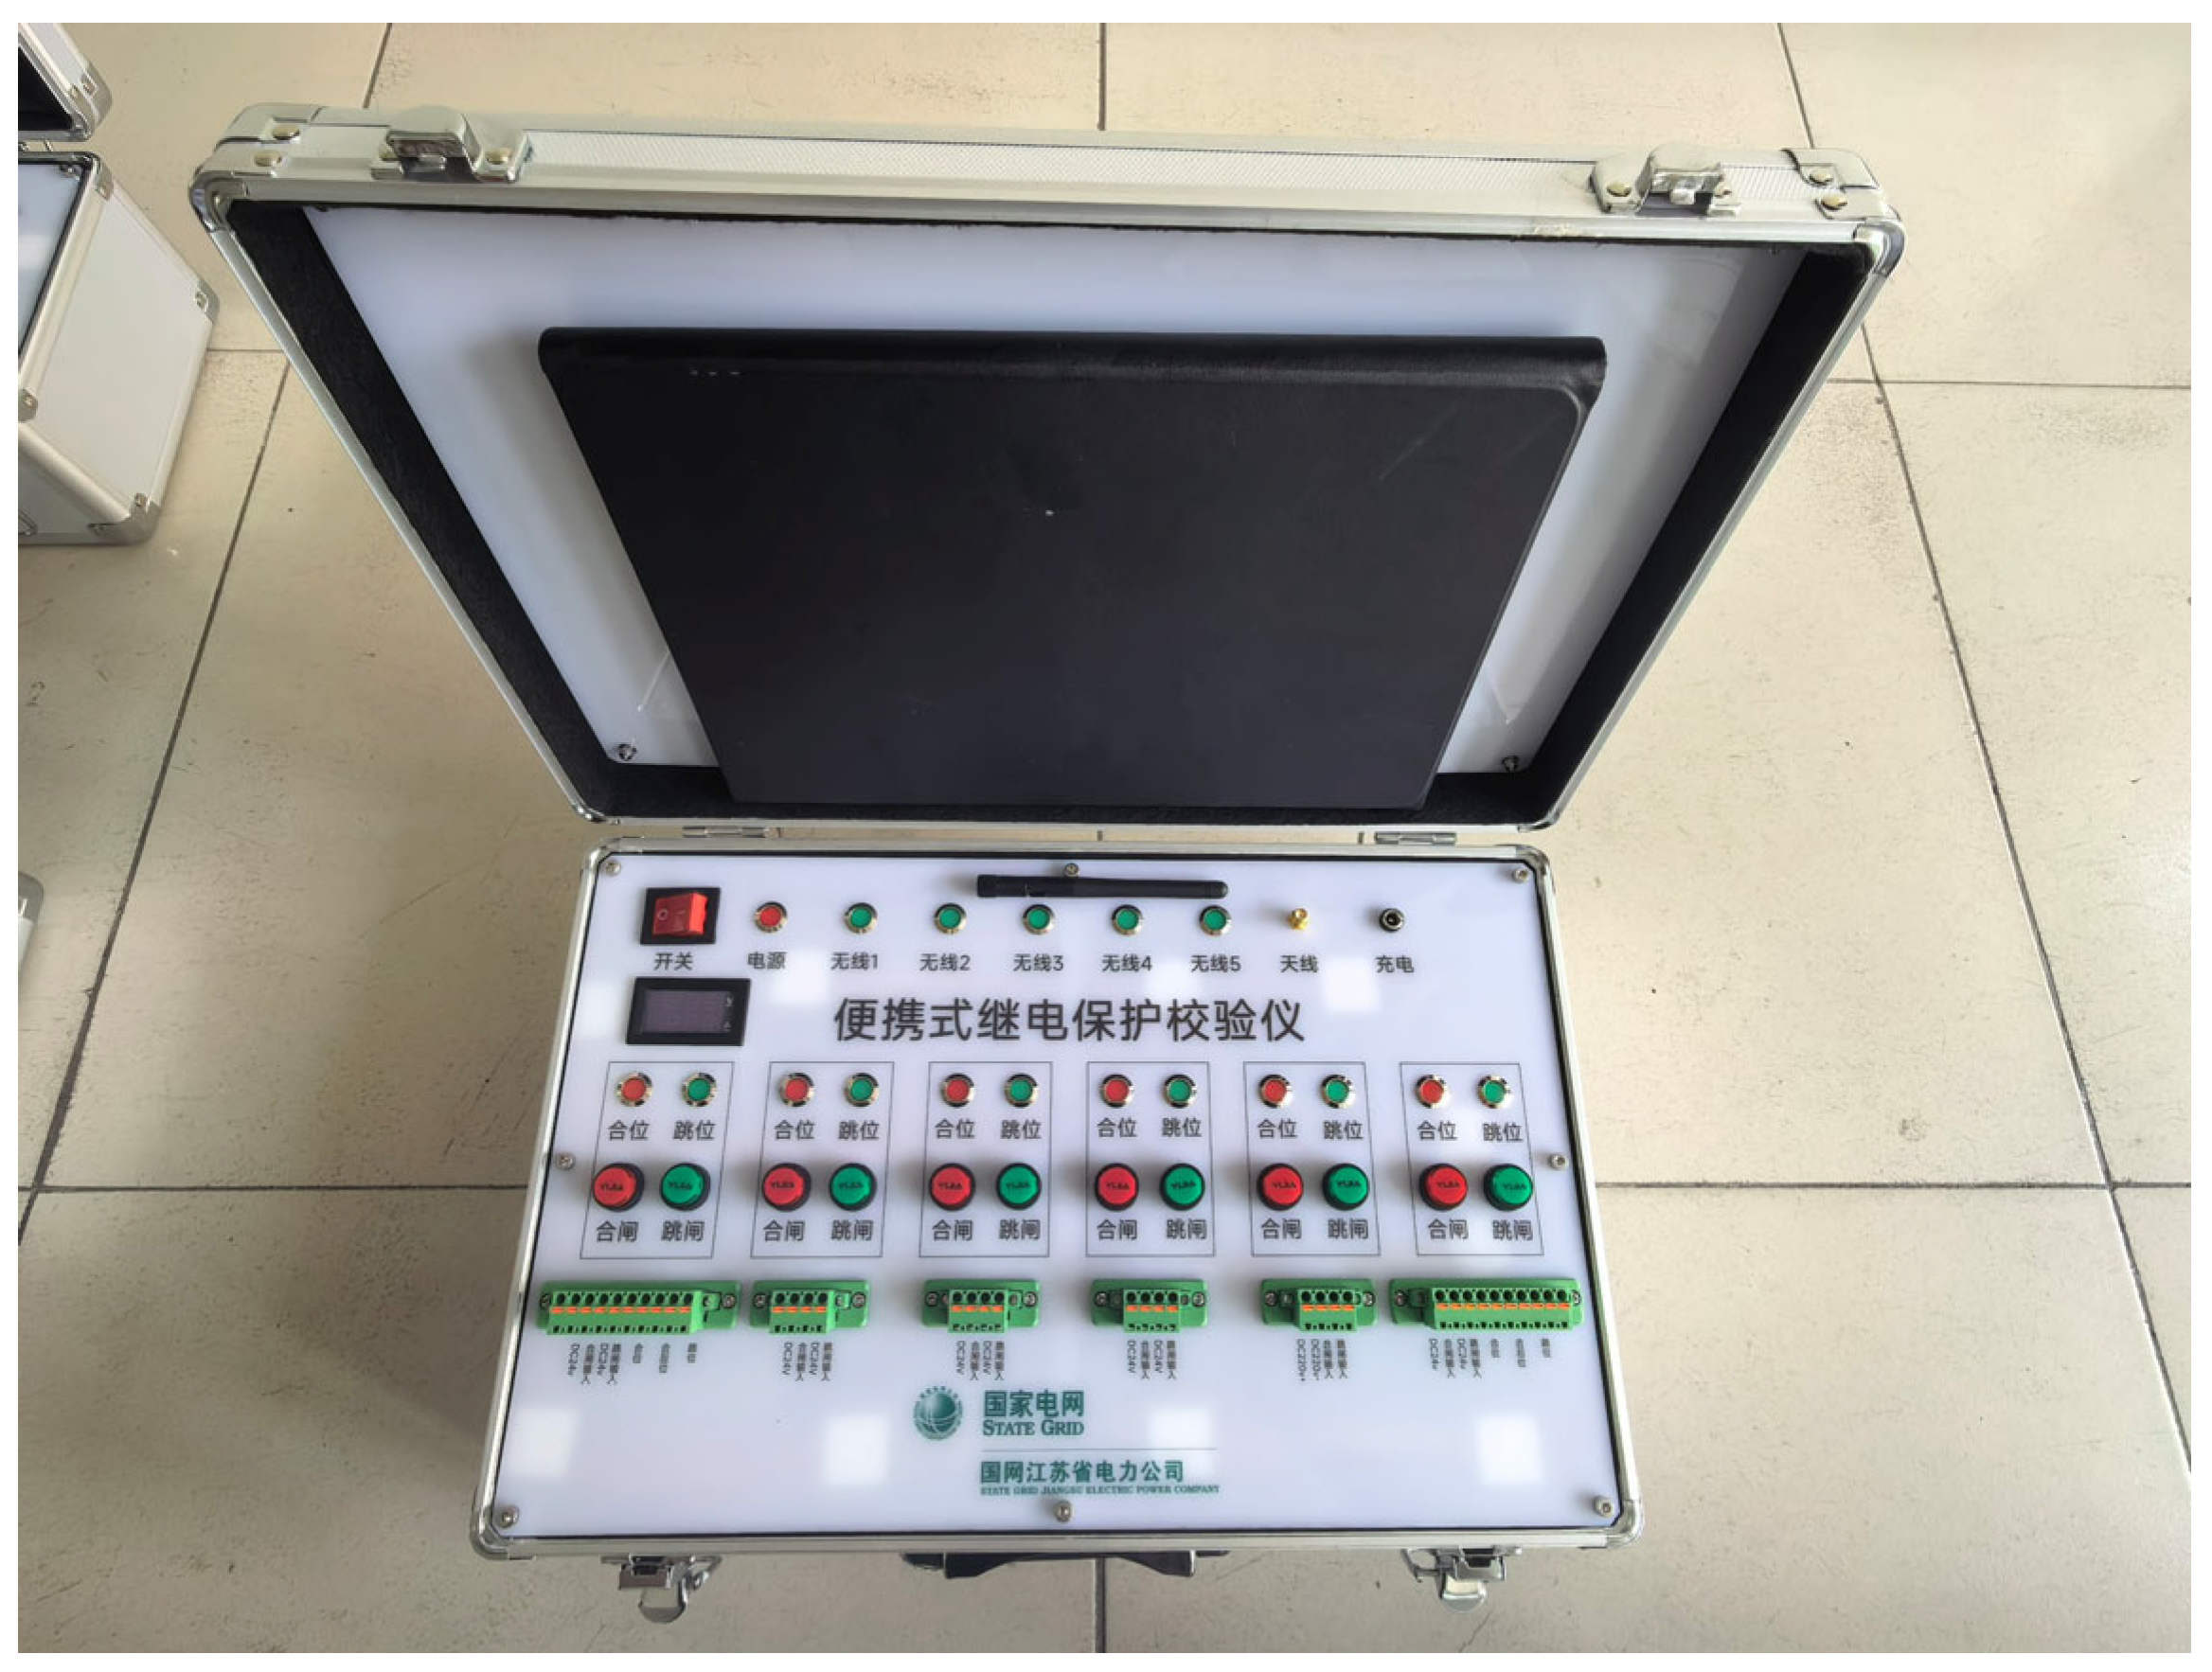
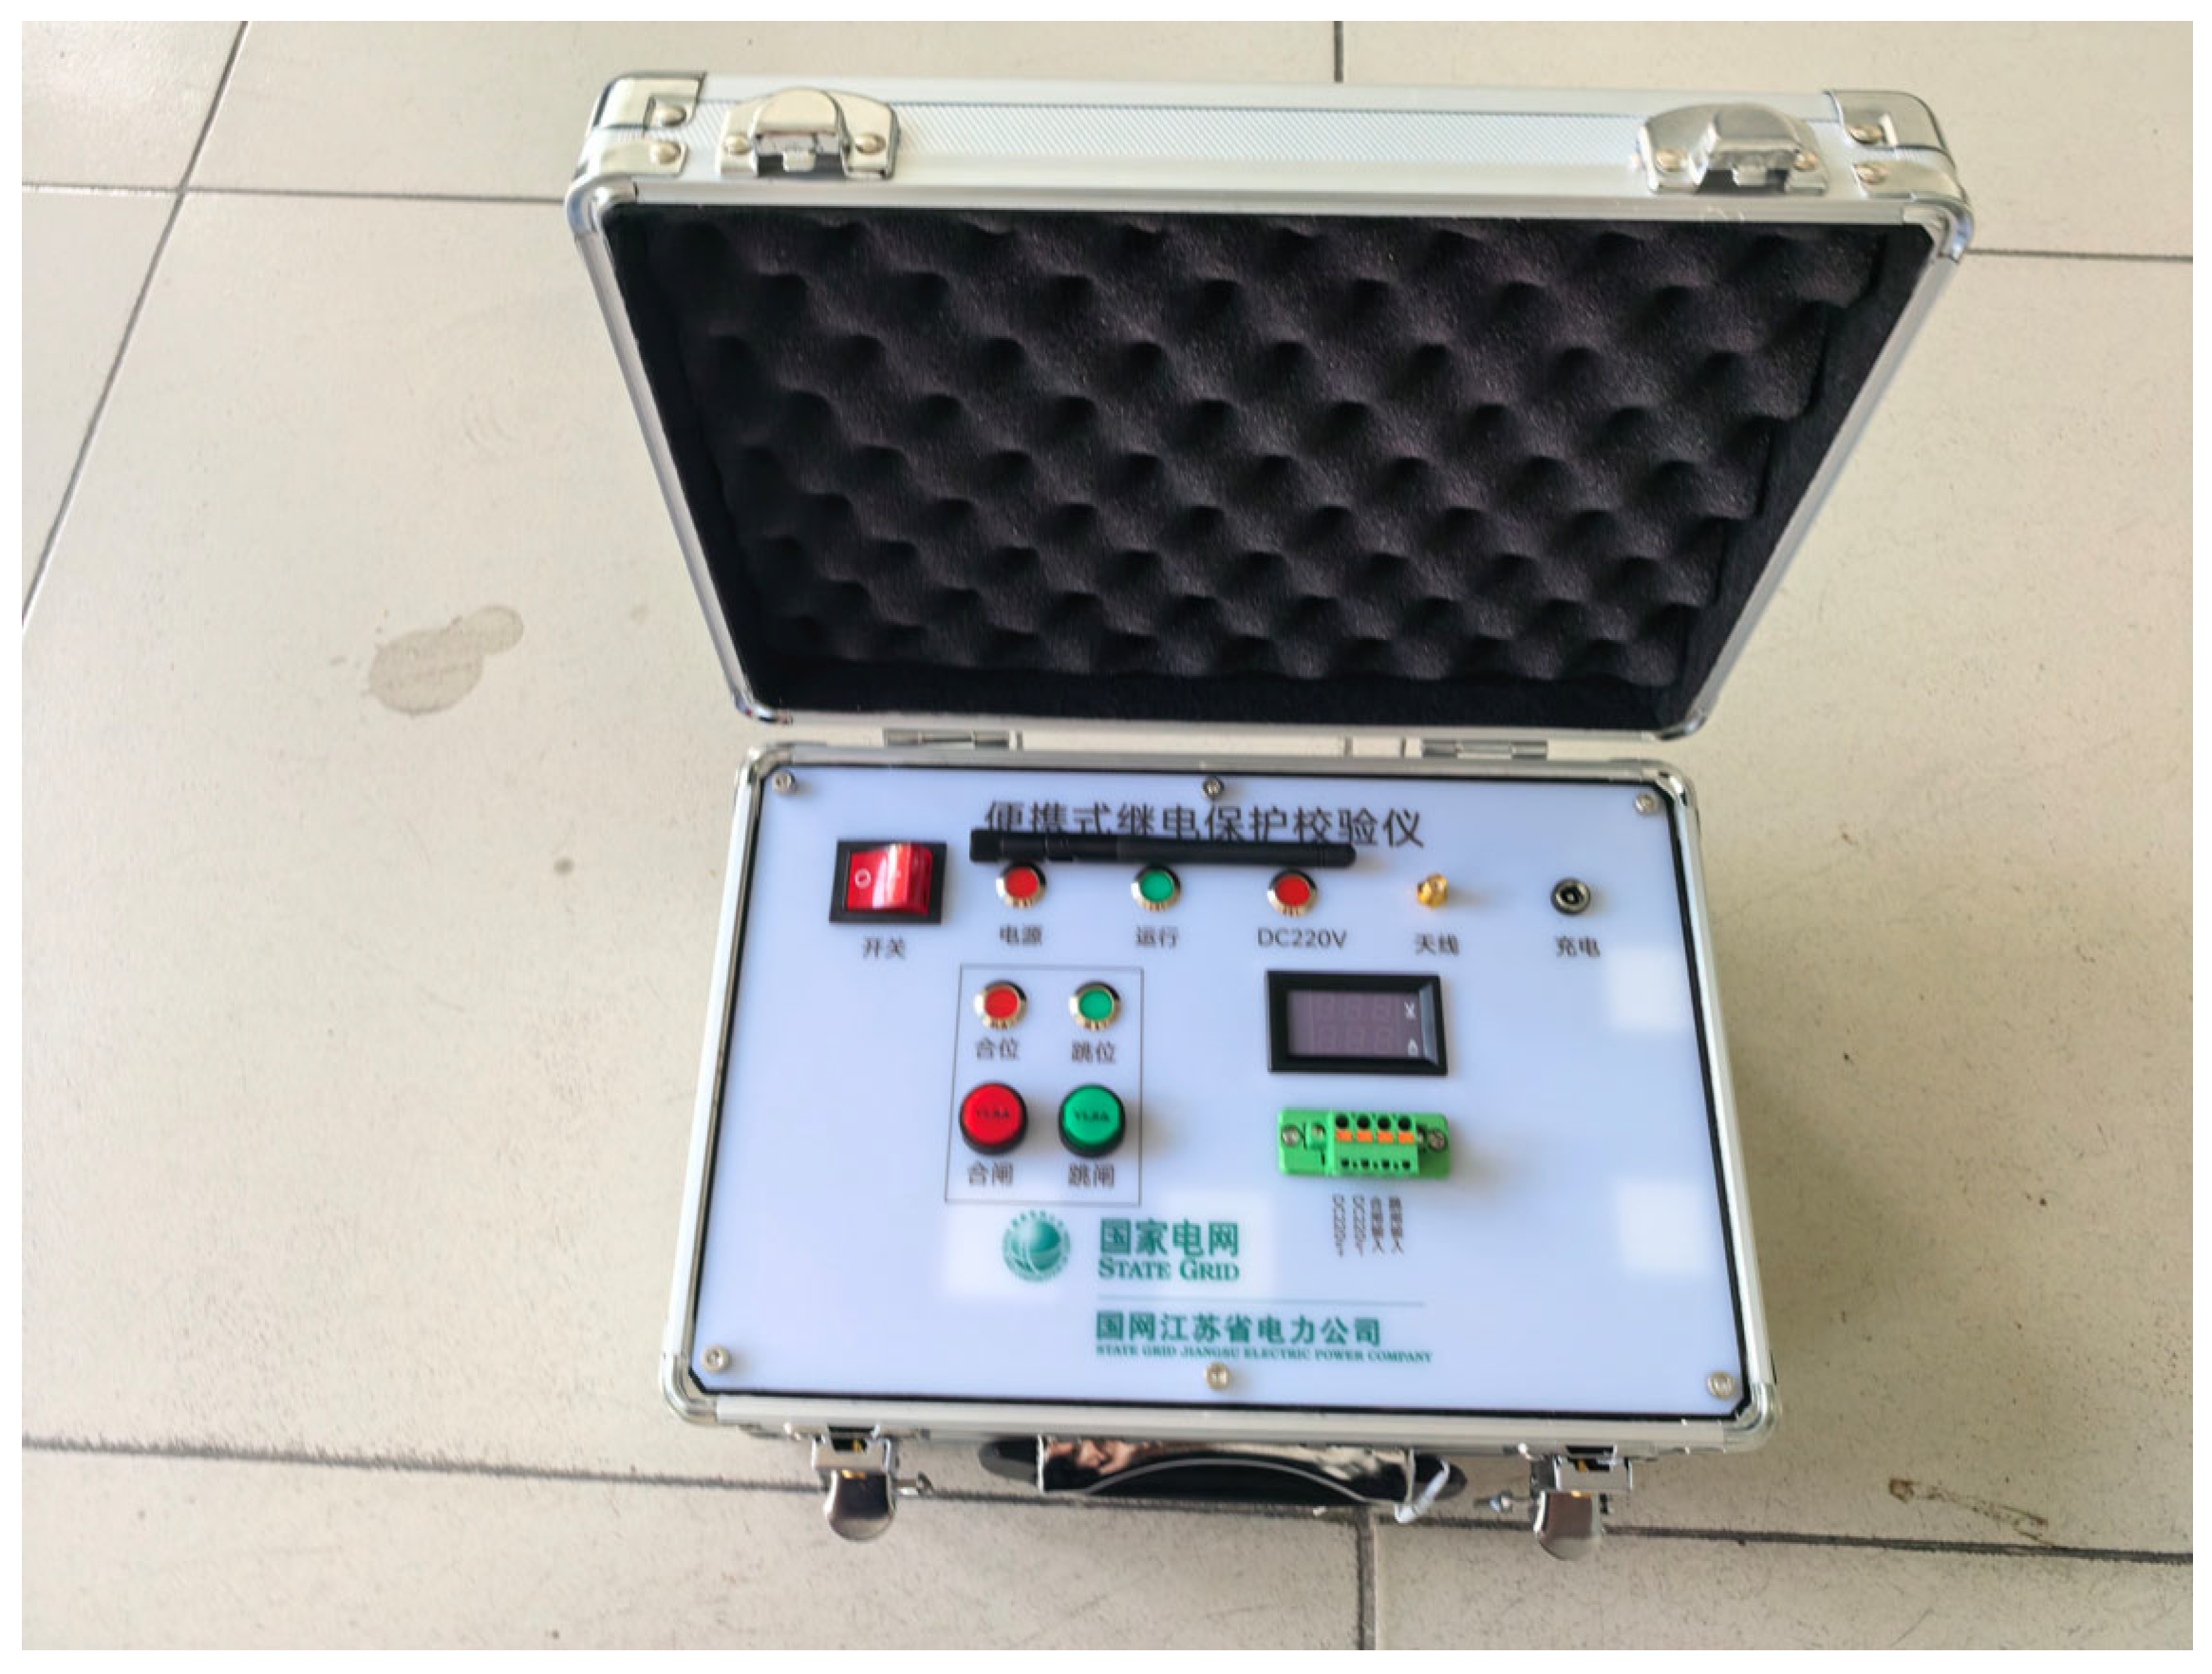
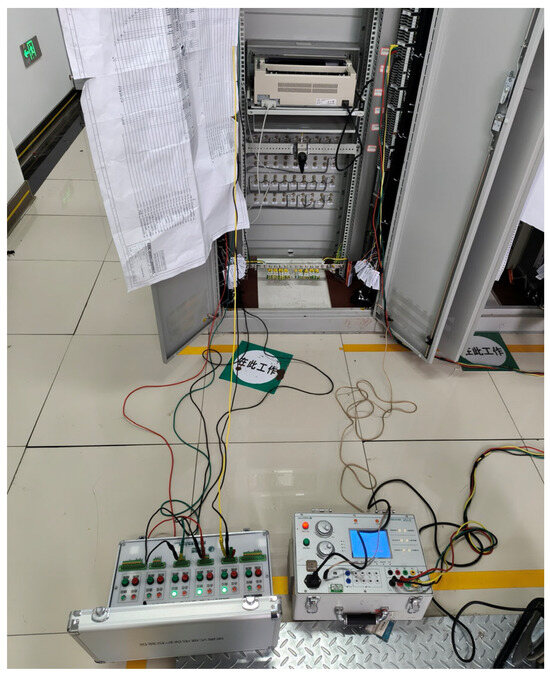
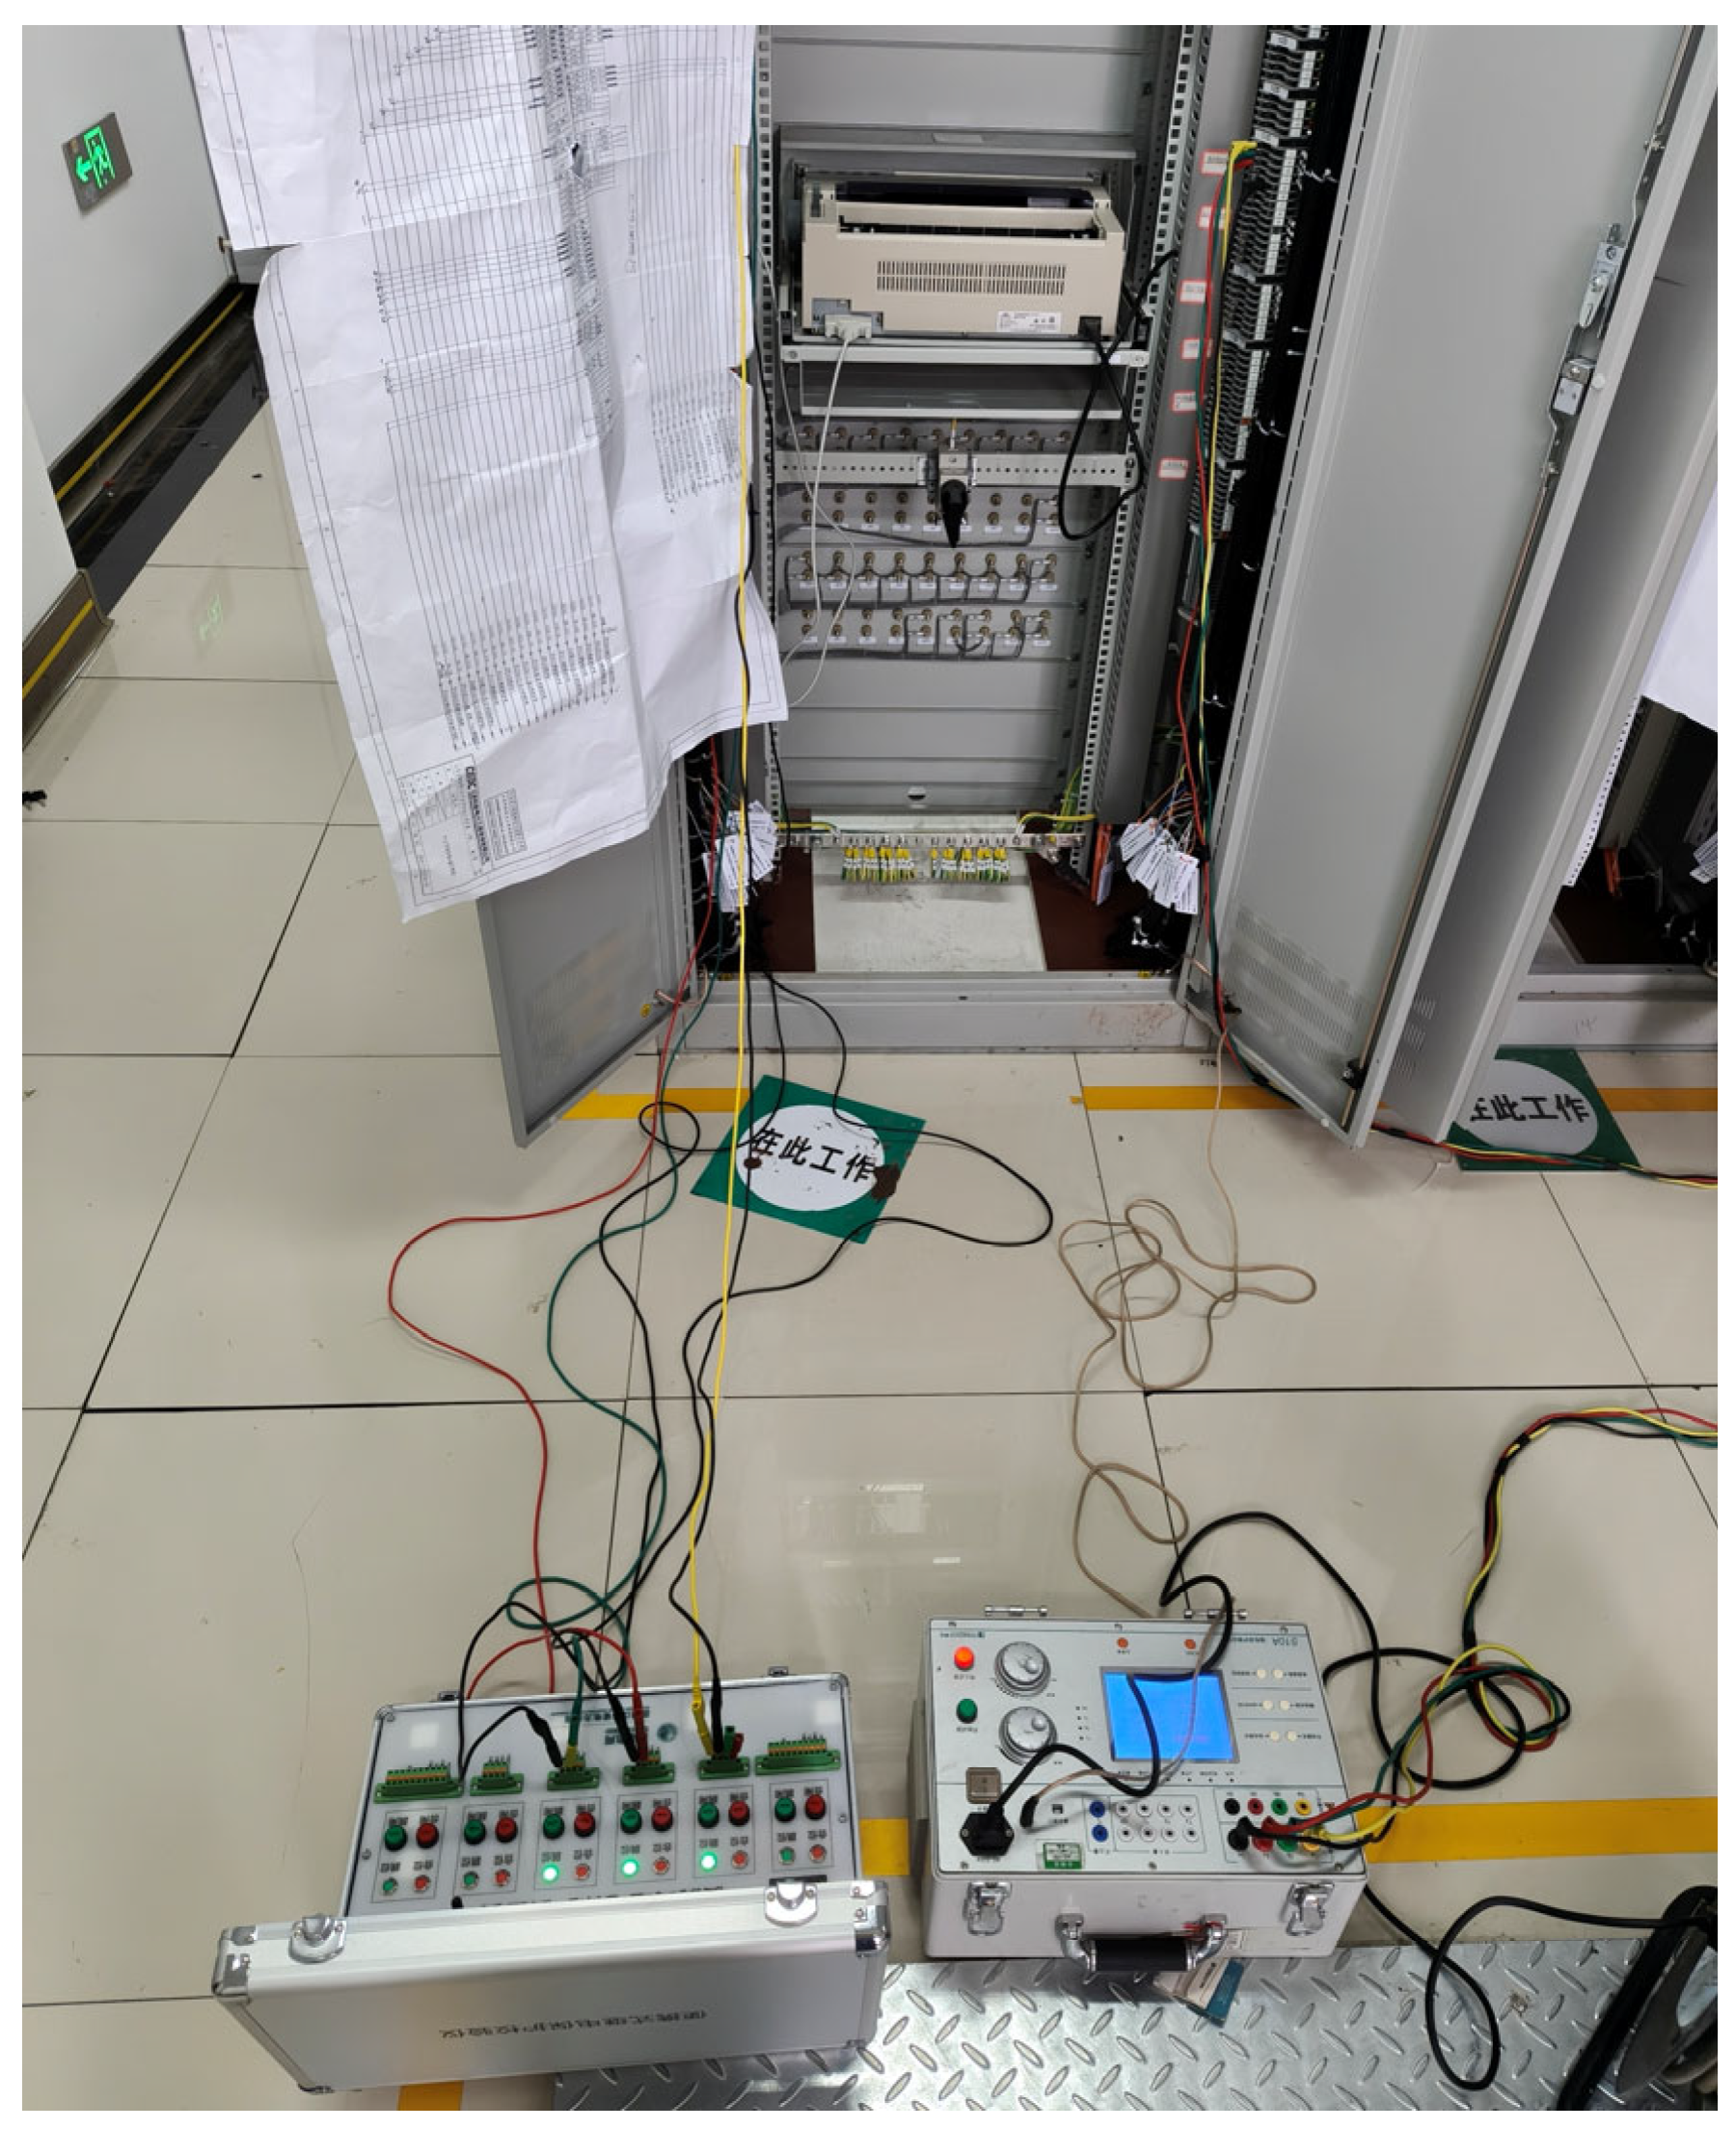
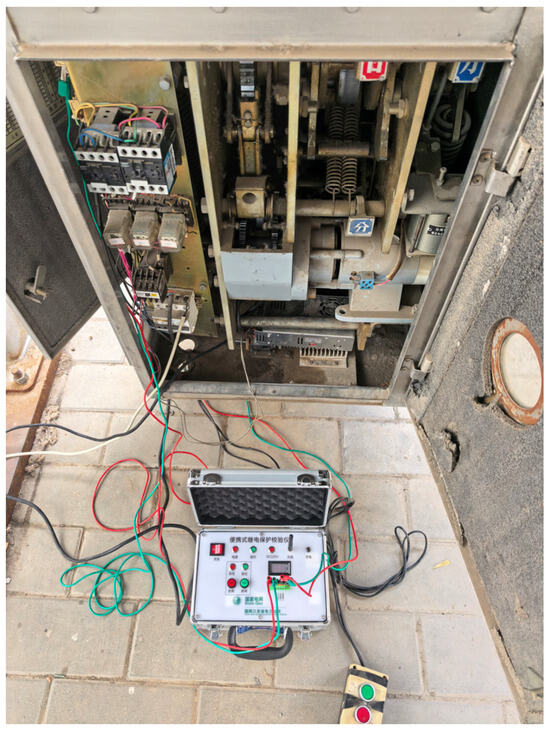
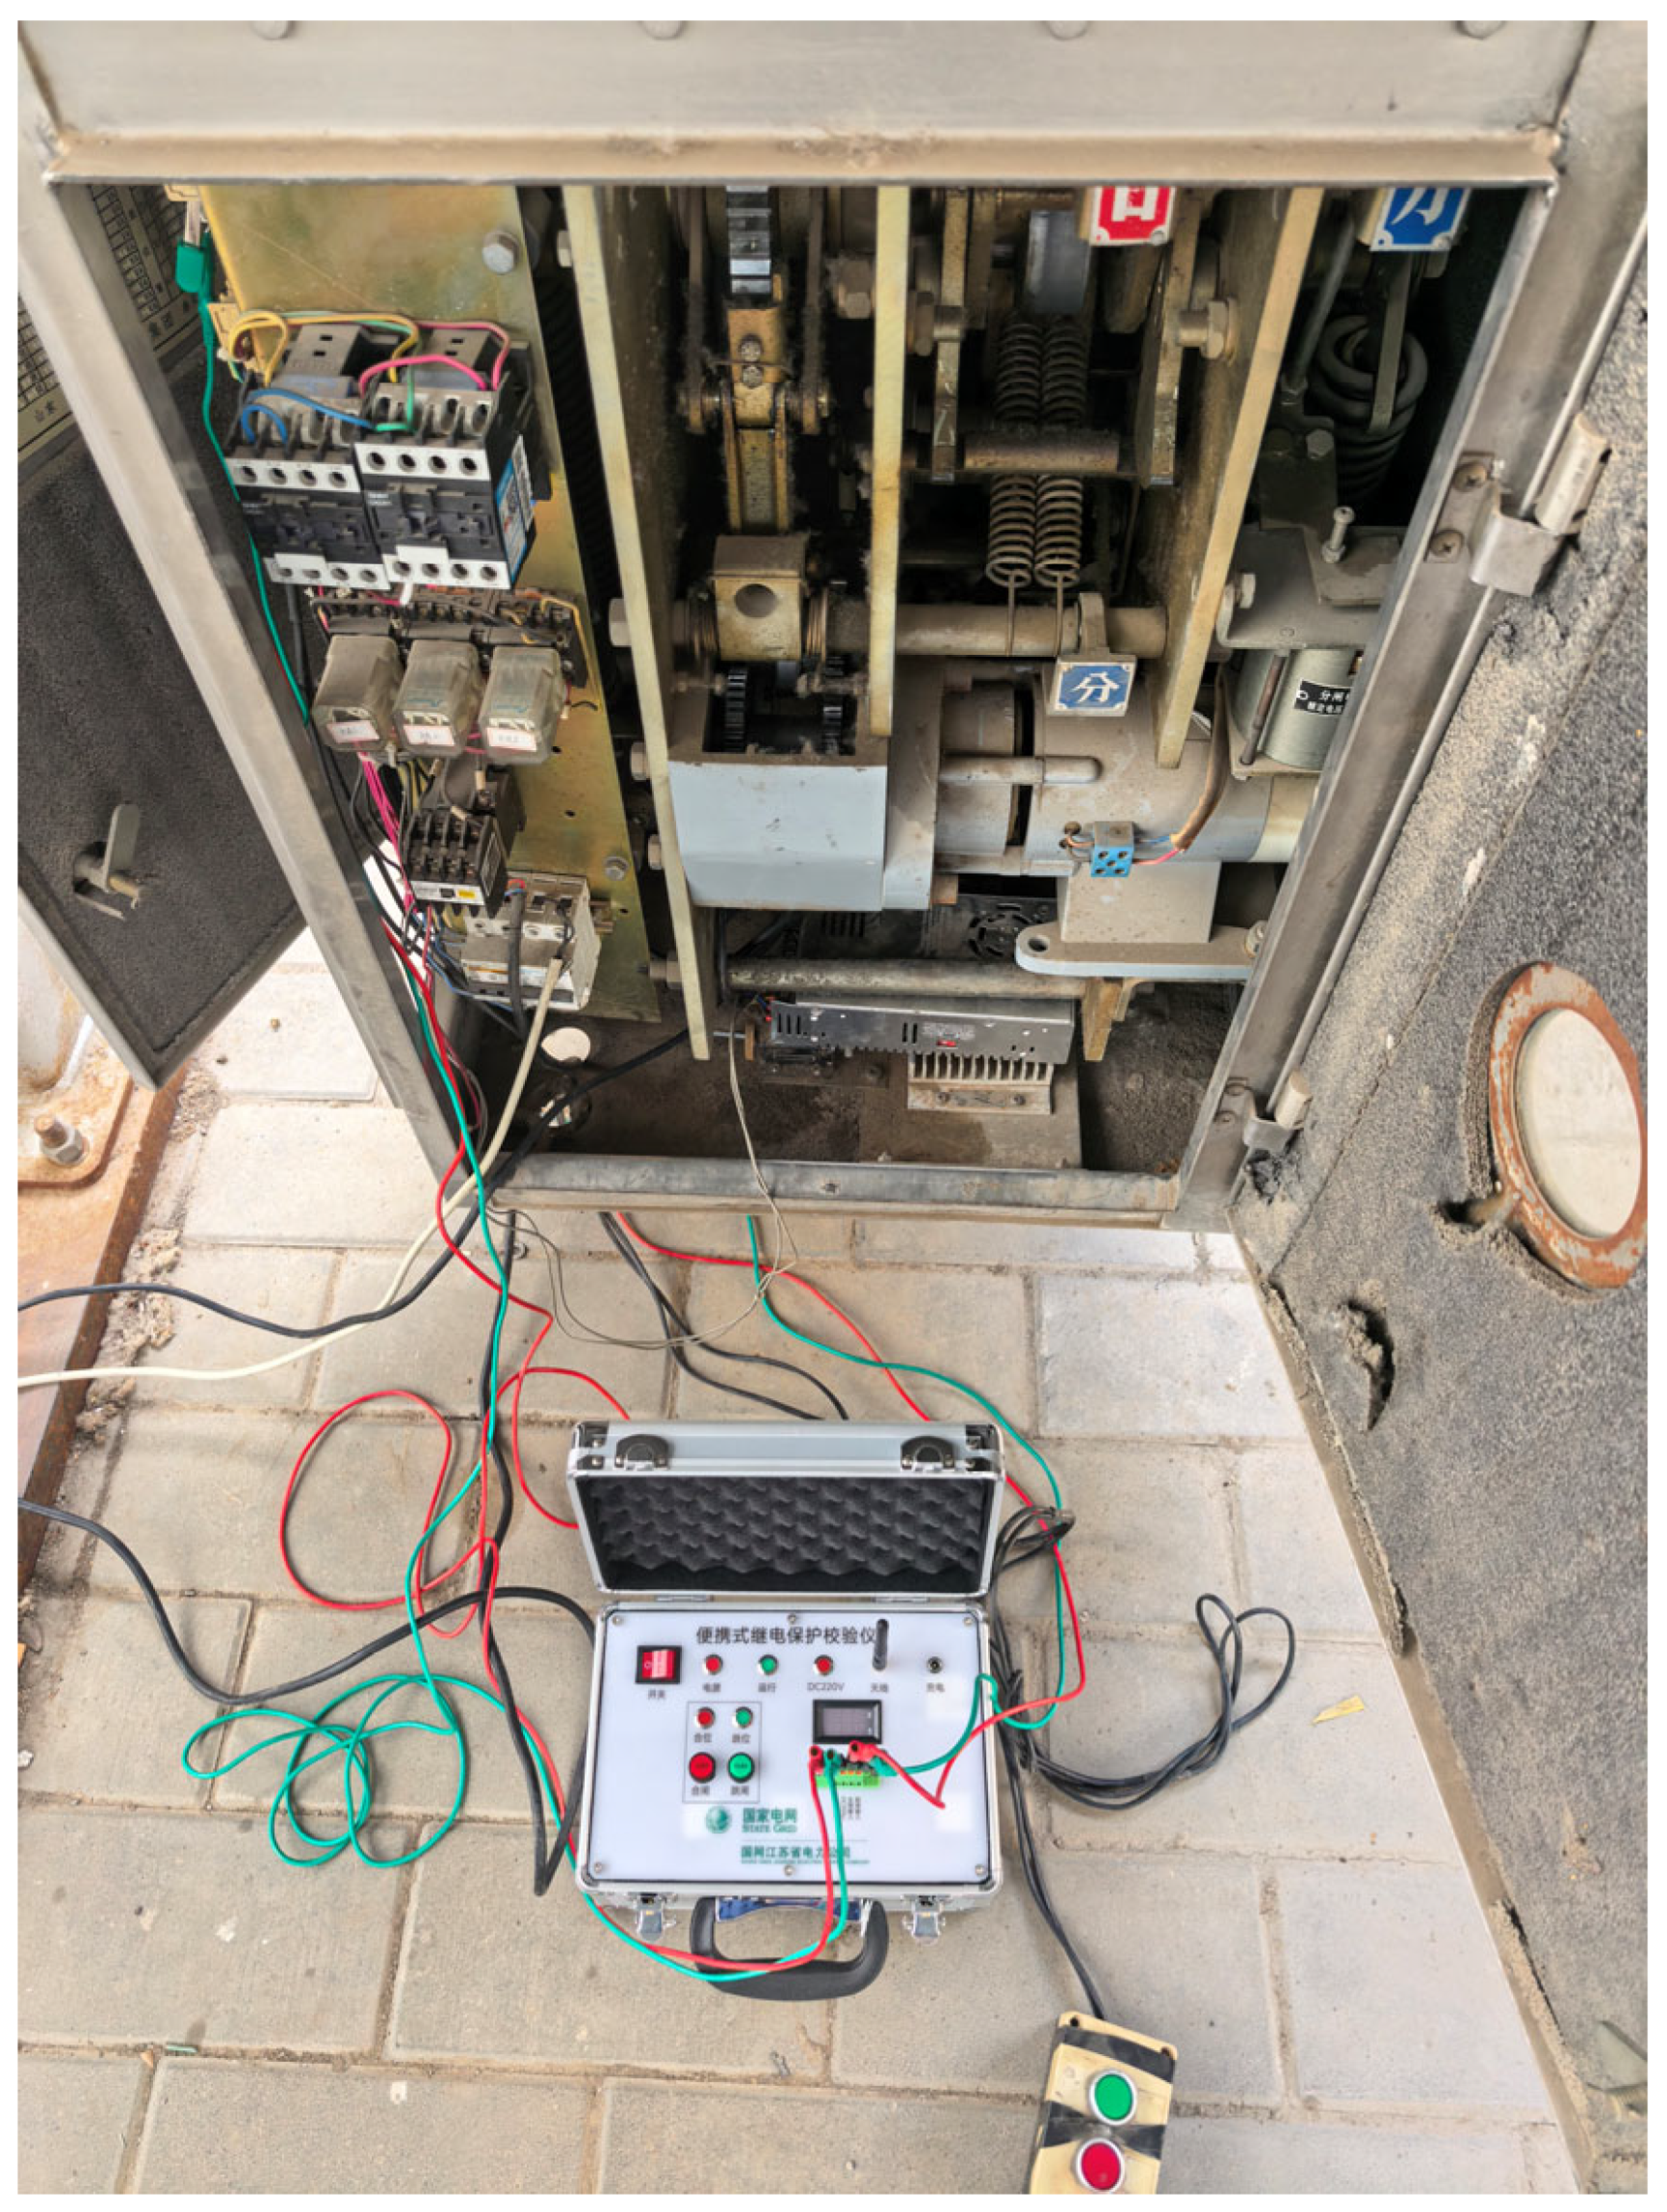
The circuit boards of the master unit and slave unit of the portable auxiliary verification device for relay protection developed and prototyped in this study are shown in Figure 5 and Figure 7, respectively. Figure 12 illustrates the external view of the master unit, while Figure 13 shows the external view of the slave unit. Additionally, Figure 14 and Figure 15 present the experimental configuration in which the master and slave units are connected to a relay protection device for on-site testing.
Figure 12.
External view of the master unit.
Figure 13.
External view of the slave unit.
Figure 14.
Master unit connected in the main control room.
Figure 15.
Slave unit wired in the switchyard.
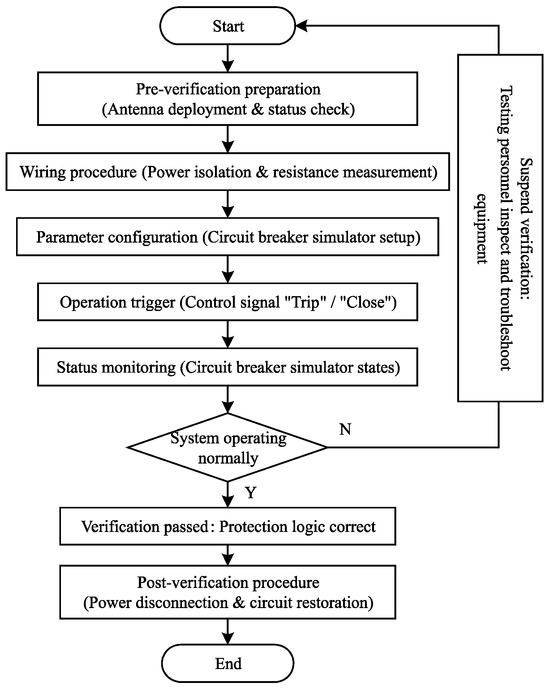
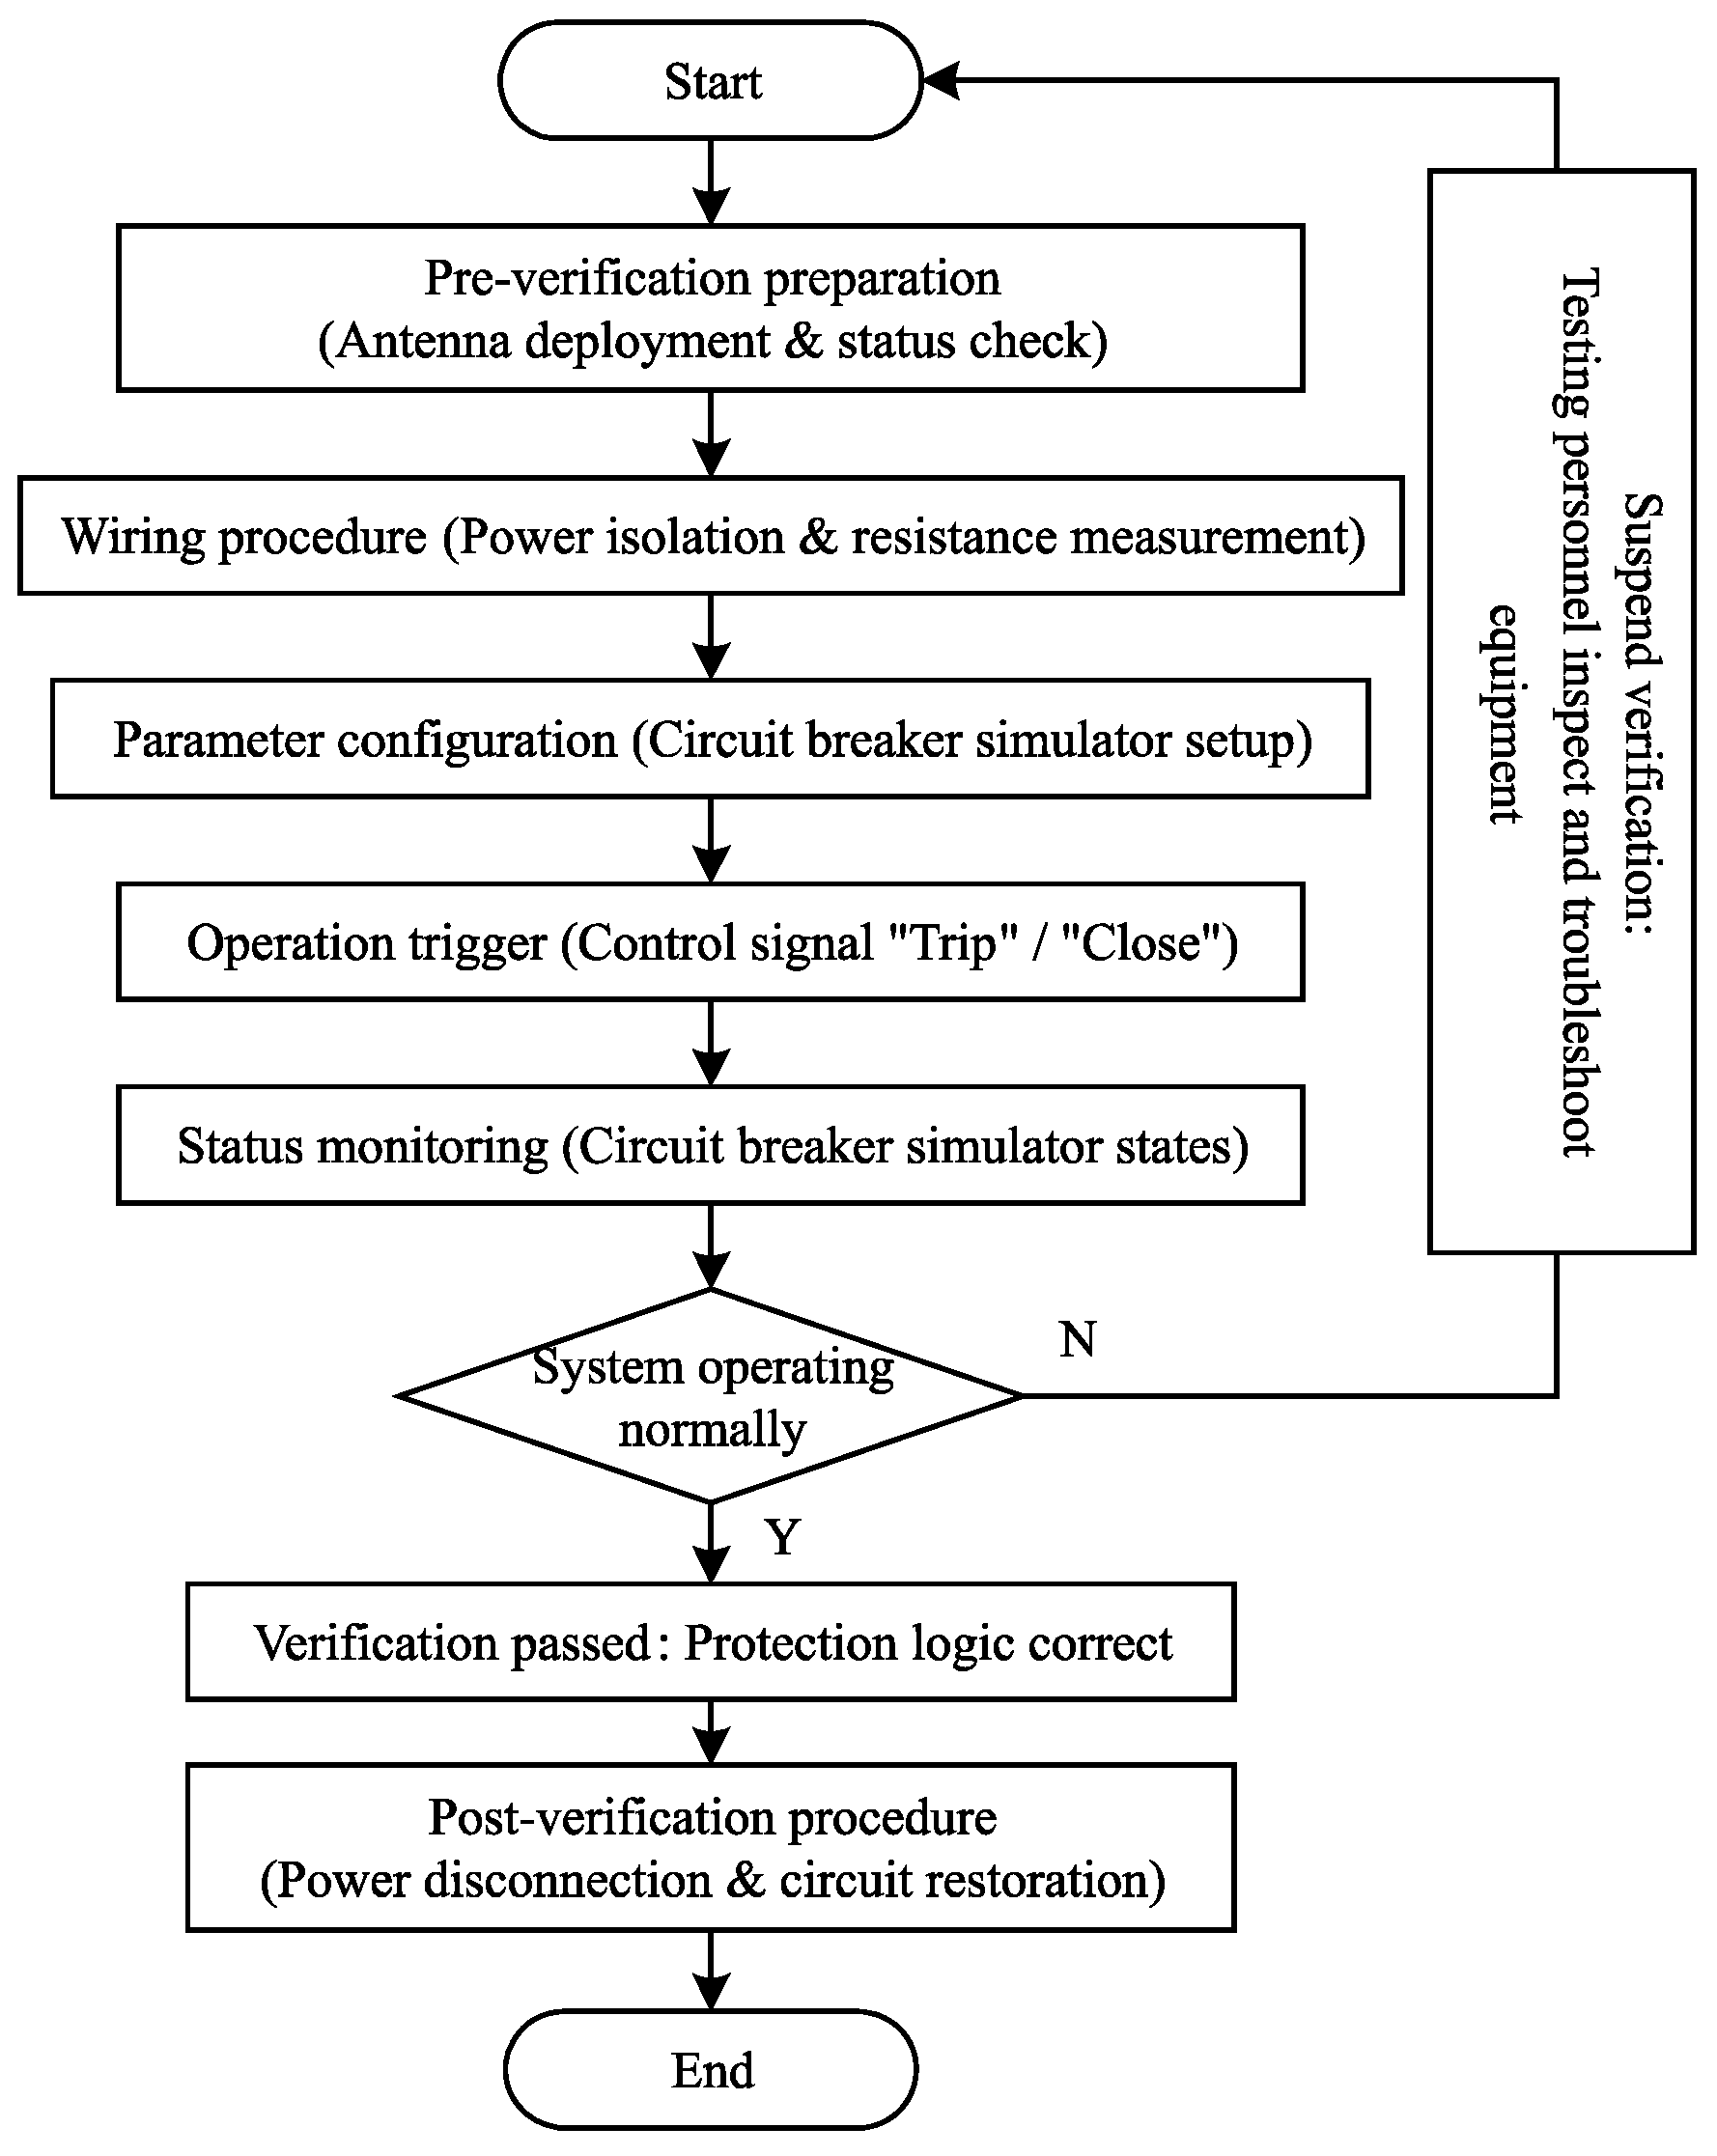
The proposed device was prototyped and tested against the relay protection panels of a 500 kV substation; in the test configuration, the master was placed in the main control room while the slaves were wired at the distributed protection panels and in the switchyard. Each test followed the standardized procedure summarized in Figure 16: after a pre-test inspection of battery voltage and wireless link status, all wiring was performed with the protection outputs de-energized, exposed conductors were insulated and the supply polarity was verified with a multimeter; the simulators were then named in the HMI, driven either manually or by protection outputs, and observed centrally; after the test, power was removed before the wiring was restored against the recorded connection list.
Figure 16.
Operational flowchart of the device verification procedure.
4.1. Single-Breaker State Transition
A single-breaker state-transition test was first conducted to verify the basic state-emulation capability. The protection device generated closing and tripping commands according to the predefined test sequence. The corresponding simulated breaker received these commands and generated the expected position-feedback signals.
The expected and observed state sequences were recorded for each operation. The test focused on the transitions between the open and closed positions and on the consistency of the returned feedback signals.
Among the 12 tested state transitions, 12 transitions were reproduced correctly, resulting in a state sequence matching rate of 100%. The corresponding command-to-state response time ranged from 124 ms to 151 ms, with an average value of 138.2 ms.
4.2. Coupled ABT State Transition
The ABT test was performed to verify the coordinated operation of the main and standby simulated circuit breakers. The test sequence was defined according to the corresponding protection procedure. A trip command was first applied to the main breaker, after which the ABT logic was activated to initiate the standby-breaker operation. The simulated breaker responses were continuously monitored to verify the required operating sequence and logical coordination. The resulting condition was maintained until a manual reset was applied. This test therefore verified both the individual breaker responses and the overall consistency of the coupled operating sequence, including the required state-retention behavior.
For 12 repeated ABT sequences, 12 sequences were reproduced without state-order errors, corresponding to a sequence matching rate of 100%. The maximum measured transition time between two consecutive expected states was 154 ms.
4.3. Multi-Output Protection State Reproduction
The multi-output test was performed to verify the coordinated response of multiple simulated circuit breakers to independent protection outputs. Several breaker channels were connected to the corresponding protection outputs, and predefined simultaneous and sequential operating conditions were applied.
The responses of the simulated breakers were continuously monitored throughout the test to verify the correspondence between the protection outputs and their associated channels. The complete response sequence was evaluated to determine whether multiple outputs could be correctly identified and reproduced without interference between channels. Therefore, the test focused on the consistency of the resulting breaker states, the correctness of channel identification, and the timing relationships among multiple protection outputs.
The multi-output test was performed to verify the coordinated response of three simulated circuit breakers to independent protection outputs. Each simulated breaker underwent 12 state transitions, resulting in 36 transitions in total. All 36 transitions were correctly reproduced, giving a state transition accuracy of 100%. No channel misidentification was observed during the test.
4.4. Quantitative Comparison with Conventional Verification Approaches
To quantitatively evaluate the engineering efficiency of the proposed verification system, a benchmark comparison was conducted for the same six-breaker busbar protection verification task using three testing approaches: conventional physical breaker cycling, conventional point-by-point multimeter testing, and the proposed distributed verification method. The comparison focused on personnel requirements, total test duration, physical breaker operation, distributed state tracking, primary-system outage requirements, and secondary-wiring risks. For all three approaches, the timing interval started when the test preparation began and ended after all six breaker states and associated protection outputs had been verified and recorded. The results are summarized in Table 4.
Table 4.
Quantitative Performance Benchmark Between Proposed Device and Conventional Testing Methodologies.
As shown in Table 3, the proposed distributed verification method required only 38 min to complete the six-breaker verification task, compared with 185 min for conventional physical breaker cycling and 120 min for point-by-point multimeter testing, representing reductions of 79.46% and 68.3%, respectively, relative to the two conventional methods. In addition, the proposed method required no physical switching operations of the primary breakers, while the conventional physical-breaker method involved 12 switching operations for the six-breaker test. The proposed method also provided multi-node state tracking with a maximum measured synchronization delay of 154 ms, which was not available in the conventional point-by-point approach. These results indicate that the proposed method can reduce the time and physical intervention required for multi-breaker verification while providing centralized observation of distributed breaker states.
4.5. Field Application Result Analysis
To further validate its engineering application value, the device was utilized during routine relay protection inspections at a substation, facilitating the on-site verification of typical secondary circuits, including ABT, busbar protection, and main transformer protection systems.
During the testing process, it was entirely unnecessary to physically operate the primary high-voltage circuit breakers. The verification of protection trip outputs and the inspection of logical relationships were accomplished solely utilizing the circuit breaker simulators. Testing personnel could observe the status transitions of each circuit breaker simulator in real time via the mobile terminal, while leveraging the historical data export function to archive comprehensive testing records.
Compared to traditional on-site verification methods, the developed device offers the following advantages:
- It eliminates the mechanical wear caused by the frequent opening and closing of high-voltage circuit breakers.
- It enables the verification of complex protection logic without requiring primary equipment outages.
- Multiple circuit breaker simulators can simultaneously provide status feedback, significantly improving the efficiency of overall scheme tests for complex protection systems.
- Wireless communication substantially reduces the workload associated with long-distance on-site wiring, thereby enhancing both testing safety and operational efficiency.
The comprehensive field application results indicate that the device operates stably, fully satisfies the requirements for the on-site auxiliary verification of relay protection, and possesses significant value for broader engineering implementation.
5. Conclusions
To address the limitations of conventional on-site relay protection verification, this study develops a portable auxiliary verification device based on a distributed circuit-breaker state emulation method. The proposed method uses simulated breaker interfaces to reproduce the required breaker-state transitions and position-feedback signals without repeated operation of primary high-voltage circuit breakers. A master–slave architecture is employed to coordinate distributed breaker states and provide centralized monitoring. The system integrates 220 V and 24 VDC simulated breaker interfaces to support conventional breaker control, automatic bus transfer (ABT), and multi-output protection logic verification.
The results show that the proposed method reduced the total test duration to 38 min, compared with 185 min for conventional physical breaker cycling and 120 min for point-by-point multimeter testing, corresponding to reductions of 79.46% and 68.3%, respectively. The proposed method can complete the verification of relay protection logic without interrupting the power supply of the circuit breaker, while the maximum measured state-update or synchronization latency was 154 ms under the tested conditions. Field verification at a 500 kV substation further demonstrated that the proposed method could reproduce the required breaker-state sequences for ABT, busbar protection, and main-transformer protection without repeated operation of primary high-voltage breakers. The results demonstrate that the proposed distributed state-emulation method can reduce test duration and physical intervention while supporting coordinated verification of multiple breaker states.
Author Contributions
Conceptualization, J.K.; methodology, J.K.; software, Z.Z., K.G. and B.Z.; validation, Z.Z.; formal analysis, W.W.; investigation, J.K., Z.Z., B.Z. and L.W.; resources, B.Z., L.W. and L.D.; data curation, K.G. and W.W.; writing—original draft preparation, D.Y.; writing—review and editing, D.Y.; visualization, K.G.; supervision, L.D.; funding acquisition, L.D. All authors have read and agreed to the published version of the manuscript.
Funding
This research was funded by the Science and Technology Project of State Grid Jiangsu Electric Power Co., Ltd., grant number No. J202502.
Data Availability Statement
The data that support the findings of this study are available from the corresponding author upon reasonable request. Due to the practical constraints associated with the field testing of the proposed device and the involvement of application-specific testing information, the complete dataset is not publicly available. Selected data may be provided upon reasonable request, subject to relevant confidentiality and application requirements.
Conflicts of Interest
Authors Jun Kong, Zhenzhe Zhang, Kaixin Gu, Baitao Zhang, Weiwei Wang, and Luyao Wang were employed by the company State Grid Jiangsu Electric Power Engineering Consulting Co., Ltd. The remaining authors declare that the research was conducted in the absence of any commercial or financial relationships that could be construed as a potential conflict of interest. The authors declare that this study received funding from State Grid Jiangsu Electric Power Co., Ltd. The funder provided project support and practical application requirements for the development of the proposed device. However, the funder had no role in the collection, analysis, or interpretation of the experimental data, manuscript preparation, or the decision to submit the manuscript for publication.
Abbreviations
The following abbreviations are used in this manuscript:
| ABT | Automatic bus transfer |
| CSV | Comma-Separated Values |
| HMI | Human–machine interface |
| LED | Light-emitting diode |
| LC | Inductor–capacitor |
| LoRa | Long Range |
| MCU | Microcontroller unit |
| RC | Resistor–capacitor |
| TVS | Transient Voltage Suppressor |
References
- Gao, L.Y.; Zhao, Y.L.; Liu, X. Analysis of Remote Testing Method for Intelligent Substation Relay Protection Based on Autonomous Controllable Technology. Electron. Technol. 2024, 53, 270–271. (In Chinese) [Google Scholar]
- Han, S.J.; Xu, D.X.; Shi, Y.X.; Han, T.X. Development Direction of Relay Protection Test. Electr. Electr. 2011, 1–4. (In Chinese) [Google Scholar] [CrossRef]
- Huang, R.W. Automatic Control System of Substation Relay Protection Operation Parameters. Electr. Technol. Econ. 2024, 149–151. (In Chinese) [Google Scholar]
- Wei, D.F.; Yue, D.S. On-Site Commissioning of Substation Integrated Automation System. Cent. China Electr. Power 2010, 23, 70–71+74. (In Chinese) [Google Scholar]
- Wang, Y.; Xu, C.; Zhu, J.; Xin, M.; Zhang, L. Research on Automatic Physical Testing Method of Relay Protection Equipment through Data Fusion Technology. J. Phys. Conf. Ser. 2021, 2083, 022019. (In Chinese) [Google Scholar] [CrossRef] [Scilit]
- Xia, Y.; Li, W.; Zhang, X.; Kang, C.; Zhou, H.; Zheng, B. Research on Automatic Test System of On-site Relay Protection Device. In Proceedings of the 2020 2nd International Conference on Smart Power & Internet Energy Systems (SPIES), Bangkok, Thailand, 15–18 September 2020; pp. 59–63. (In Chinese) [Google Scholar] [CrossRef] [Scilit]
- Wang, L. Research on short-circuit fault detection technology of substation relay protection circuit. China’s New Technol. New Prod. 2026, 61–63. (In Chinese) [Google Scholar]
- Yao, H.; Pan, Y.Z. Research on Fault Repair and Improvement Measures of Automatic Relay Protection Device. Mold Manuf. 2023, 23, 283–285. (In Chinese) [Google Scholar]
- Habib, H.F.; Fawzy, N.; Brahma, S. Performance Testing and Assessment of Protection Scheme Using Real-Time Hardware-in-the-Loop and IEC 61850 Standard. IEEE Trans. Ind. Appl. 2021, 57, 4569–4578. [Google Scholar] [CrossRef] [Scilit]
- Habib, H.F.; Patel, T.; Brahma, S. Hardware in the Loop Testing of Main and Backup Protection Scheme for Systems with High Penetration of Inverter-Based Resources. In Proceedings of the 2022 IEEE Industry Applications Society Annual Meeting (IAS), Detroit, MI, USA, 9–14 October 2022; Volume 58, pp. 1–8. [Google Scholar] [CrossRef] [Scilit]
- Penthong, T.; Ginocchi, M.; Ahmadifar, A.; Ponci, F.; Monti, A. IEC 61850-Based Protection Scheme for Multiple Feeder Faults and Hardware-in-the-Loop Platform for Interoperability Testing. IEEE Access 2023, 11, 65181–65196. [Google Scholar] [CrossRef] [Scilit]
- Camarillo-Penaranda, J.R.; Aredes, M.; Ramos, G. Hardware-in-the-Loop Testing of a Distance Protection Relay. IEEE Trans. Ind. Appl. 2021, 57, 2326–2331. [Google Scholar] [CrossRef] [Scilit]
- Yadav, G.; Liao, Y.; Burfield, A.D. Hardware-in-the-Loop Testing for Protective Relays Using Real Time Digital Simulator (RTDS). Energies 2023, 16, 1039. [Google Scholar] [CrossRef] [Scilit]
- Jiang, H.; Mao, X.F. Design of Automatic Testing System for Relay Protection Devices in Intelligent Substation. Electron. Technol. 2023, 52, 278–279. (In Chinese) [Google Scholar]
- Dai, Y.; Li, D.; Chen, Y.; Tang, M. Automatic Relay Protection Calibration Device and System Design for New Intelligent Power Grid. J. Phys. Conf. Ser. 2023, 2560, 012031. (In Chinese) [Google Scholar] [CrossRef] [Scilit]
- Indrawan, A.W.; Lukman, M.P.; Basith, A.M.; Rahman, A.; Sultan, A.R.; Aksan, A.; Thaha, S. LoRa-Based Mesh Network for Distribution Substation Monitoring. In AIP Conference Proceedings; AIP Publishing LLC: Melville, NY, USA, 2024; p. 040021. [Google Scholar] [CrossRef] [Scilit]
- Liccardo, A.; Bonavolonta, F.; Balato, M.; Petrarca, C. LoRa-Based Smart Sensor for PD Detection in Underground Electrical Substations. IEEE Trans. Instrum. Meas. 2022, 71, 1–13. [Google Scholar] [CrossRef] [Scilit]
- Chen, S.; Sun, H.; Wang, Y.; Tang, L.; Song, X.; Hao, F. Design and Research of Power Grid Data Transmission System Based on LoRa Technology. In Proceedings of the 2024 IEEE 3rd International Conference on Electrical Engineering, Big Data and Algorithms (EEBDA), Changchun, China, 27–29 February 2024; pp. 1524–1528. (In Chinese) [Google Scholar] [CrossRef] [Scilit]
- Tang, T.X.; Wang, Y. The Check Method of the Busbar Automatic Transfer Switch in Substation. Electr. Switch 2025, 63, 93–95. (In Chinese) [Google Scholar]
- Filter, R.; Mintz, J.D.; Cherney, D.M. Separable insulated connector loadbreak testing. I. The switching characteristic and its implications. IEEE Trans. Power Deliv. 1992, 7, 554–559. [Google Scholar] [CrossRef] [Scilit]
- Huang, C.-T.; Lien, H.-C.; Lin, C.-P.; Chen, W.-P. Smart Internet of Isolated Capacitor Trip Device for High-voltage Protective Relay of Backup Power. Sens. Mater. 2020, 32, 2781–2799. (In Chinese) [Google Scholar] [CrossRef] [Scilit]

Disclaimer/Publisher’s Note: The statements, opinions and data contained in all publications are solely those of the individual author(s) and contributor(s) and not of MDPI and/or the editor(s). MDPI and/or the editor(s) disclaim responsibility for any injury to people or property resulting from any ideas, methods, instructions or products referred to in the content. |
© 2026 by the authors. Licensee MDPI, Basel, Switzerland. This article is an open access article distributed under the terms and conditions of the Creative Commons Attribution (CC BY) license.