


Abstract
The protection of personal information has become a defining challenge for higher education institutions, particularly in developing contexts where regulatory frameworks are often strong on paper but weak in practice. This study investigates student perceptions of privacy within Zimbabwe’s higher education system, focusing on three constructs: awareness, expectations, and confidence across nine core privacy components derived from international principles (FIPPs, OECD, GDPR) and the Zimbabwe Data Protection Act (ZDPA). Using survey data from 287 students across diverse programmes and modes of study, descriptive and comparative analyses reveal a striking pattern: students demonstrate high awareness and very strong expectations, yet their confidence in institutional compliance remains significantly lower. The largest deficits were found in privacy education, consent, and notice/openness, suggesting that institutions are perceived as technically competent in data handling but weak in transparency, accountability, and student engagement. The research extends privacy perception models by considering the discrepancy between the students’ expectations and the institutional trust. It also encourages universities to go beyond mere compliance by implementing concrete measures such as privacy training, clear consent, and frequent data audits. The findings contribute to global debates on privacy by offering evidence from the Global South, showing that the key challenge is not student ignorance but institutional trustworthiness. Bridging this awareness-confidence gap is essential for building a privacy-conscious academic environment.
1. Introduction
Safeguarding personal data in institutions of higher learning has emerged as a critical concern in the digital age [1]. In developing countries, these concerns are exacerbated by evolving legal frameworks, limited resources, and varying levels of digital literacy, resulting in slow institutional adaptation or lack of enforcement [2]. An example is the Zimbabwe Data Protection Act (ZDPA), which exemplifies recent efforts in Zimbabwe to regulate data practices [3]. Despite these legal efforts, institutions frequently lack context-sensitive tools to monitor and respond to students’ perceptions of privacy. While students tend to be more trusting of institutions than commercial platforms, significant gaps in their understanding of privacy regulations persist, leading to heightened concerns [4,5].
Researchers have investigated several privacy-related issues in higher education, focusing on perceptions among students enrolled in technology-enhanced, hybrid, and online courses [6]; privacy concerns and limited educational awareness regarding LMSs and social media [7]. The studies highlighted privacy compromises, concerns, and comforts. This can be viewed as an opportunity to develop context-specific strategies and ongoing education. Institutions should consider meaningful student engagement when developing policies for implementing privacy and learning analytics [8]. This aligns with [2], who found that technologies alone cannot protect student data privacy and that alternative considerations must be taken into account. Institutions must play an active role in shaping and strengthening students’ perceptions of privacy. Thus, there is a pressing need for greater transparency and targeted educational efforts regarding institutional data collection, usage, and sharing practices [9]. Transparency can help bridge the gap between students’ expectations and the realities of institutional data practices, thereby increasing students’ confidence and enabling informed consent. Inclusion and transparency in this manner will ensure that data are managed within the privacy framework while simultaneously fostering a culture in which students view trust as central to their experience, thereby promoting a safer, privacy-conscious education environment.
From a Zimbabwean perspective, a study by [10], which assessed cybersecurity awareness levels among Zimbabwean university students and staff and proposed a framework for education programs, revealed a lack of knowledge of cybersecurity principles, particularly in data protection, privacy, and risk mitigation. Similarly, ref. [11] established a cybersecurity culture framework for users in Zimbabwe, emphasising the need for a national cybersecurity strategy, privacy awareness, and the inclusion of cybersecurity in the curriculum. This reflects an urgent need for comprehensive awareness and training programs to improve secure and privacy practices among university users. Furthermore, it also emphasises the critical role of information privacy as a foundational element in promoting safe and responsible digital practices. Involving students in the conversation about data privacy will further enhance trust and encourage good practices [12,13].
Despite the introduction of legal instruments such as the ZDPA, institutions in developing countries lack contextually validated tools to assess students’ perceptions of privacy for personal information. This gap is critical given increasing reliance on educational technologies and analytics, which heighten privacy risks and student concerns about data misuse, breaches, and third-party access. Institutions risk policy misalignment, low student trust, and non-compliance with emerging privacy regulations without targeted, context-specific assessment mechanisms [5,14,15,16]. Therefore, this study seeks to develop and validate a diagnostic tool for evaluating student perceptions of personal information privacy, encompassing awareness, expectations, and confidence, within Zimbabwe’s higher education system, with significance for regulatory contexts in developing nations. Thus, the study is guided by the research question: What is the perception of students on privacy, specifically awareness, expectations, and confidence, within Zimbabwe’s higher education system?
2. Conceptual Foundations
Information privacy has evolved from international frameworks designed to regulate the collection, processing, storage, and dissemination of personal data. Central to this evolution within the context of this study are the Fair Information Practice Principles (FIPPs) [17,18], the Organisation for Economic Cooperation and Development (OECD) Guidelines on the Protection of Privacy and Transborder Flows of Personal Data [19], the European Union’s General Data Protection Regulation (GDPR) [18,20], and the Zimbabwe Data Protection Act (ZDPA) [3,21]. Together, these frameworks form the normative foundation for contemporary privacy laws and provide the regulatory context for this study conducted within Zimbabwe’s higher education sector.
Building on these frameworks, this study employs the Information Privacy Perceptions Survey (IPPS), a diagnostic instrument developed to assess students’ perceptions of institutional privacy practices (see Appendix A for the full instrument). At its core, the instrument measures three central dimensions/concepts of privacy perceptions: privacy awareness (what students know), privacy expectations (what they believe should happen), and privacy confidence (the degree of trust they have in the institution’s ability to protect their data), according to [12,22,23]. These dimensions are well recognised in the literature as critical factors shaping how individuals perceive and respond to privacy practices [24,25], but in this study, they are firmly anchored within the socio-legal realities of Zimbabwe’s higher education sector.
To ensure the instrument reflected the letter and spirit of the ZDPA, the three dimensions were mapped to nine privacy components derived directly from the Act’s principles. Each component represents a distinct area of personal data governance: notice/openness, purpose specification, information quality, use limitation, collection limitation, individual participation, privacy education, privacy policy, and consent. Equally, statements were crafted for each component on awareness, expectations, and confidence. This mapping ensured balance, comparability, and depth across all privacy areas. The instrument was developed based on a literature review and an expert panel review, in a prior phase of this study [23]. Below is how each component was operationalised:
- Notice/openness—Derived from FIPPs’ notice principle, OECD’s openness, GDPR’s transparency obligations, and ZDPA’s disclosure requirements [18,19,26,27]. Statements assessed whether students knew about the institution’s obligation to provide clear privacy notices (awareness), whether they expected such notices to be proactively issued (expectations), and whether they trusted that the institution followed through on this obligation (confidence).
- Purpose specification—Anchored in all four regulations/frameworks, ensuring personal data is collected for explicit, legitimate aims [3,18,28,29]. Items explored whether students knew that personal data collection should always be accompanied by a stated purpose (awareness), whether they expected this purpose to be communicated clearly (expectations), and whether they trusted that the stated purposes matched actual data use (confidence).
- Information quality—Embedded across all four regulations/frameworks, emphasising accuracy, relevance, and integrity [29,30]. Statements evaluated knowledge of the institution’s responsibility to maintain accurate, complete, and relevant records (awareness), the belief that institutions should ensure high-quality data management (expectations), and trust in the institution’s commitment to keeping records accurate and secure (confidence).
- Use limitation—From FIPPs and OECD, reinforced by GDPR’s lawful processing and ZDPA’s consent clauses [18,29,31]. Items examined awareness of rules restricting data use to authorised purposes (awareness), the expectation that personal data would never be used beyond agreed limits without consent (expectations), and confidence that the institution adhered to these boundaries (confidence).
- Collection limitation—Present in FIPPs, OECD, GDPR (Article 15), and ZDPA, requiring fair, lawful, and minimal data collection [18,21,28,32]. Statements focused on whether students were aware that data should be collected lawfully, fairly, and only when necessary (awareness), whether they expected limits on collecting sensitive or irrelevant data (expectations), and whether they trusted that such limits were respected (confidence).
- Individual participation—FIPPs and OECD grant rights of access and correction; GDPR expands this to erasure and portability; ZDPA aligns closely [13,18,27,29,33]. Items assessed awareness of students’ rights to access and review their personal data (awareness), the expectation that these rights would be honoured (expectations), and confidence in the institution’s responsiveness to such requests (confidence).
- Privacy education—An extension of OECD’s emphasis on awareness and skills development [29]. It addresses the knowledge gap among Zimbabwean students who often lack awareness of privacy rights [34]. Statements measured knowledge of ongoing privacy education initiatives (awareness), the expectation that the institution would provide regular privacy awareness programmes (expectations), and trust that these initiatives were adequate and consistent (confidence).
- Privacy policy—Though not an explicit FIPPs principle, privacy policies operationalise notice. Both the OECD and the GDPR highlight the need for institutional policies, while the ZDPA encourages transparency mechanisms [35]. Items examined whether students knew a privacy policy existed and understood its purpose (awareness), whether they expected the policy to be clear and accessible (expectations), and whether they believed the policy was actively applied in practice (confidence).
- Consent—While implicit in FIPPs and OECD, GDPR and ZDPA elevate it as a cornerstone, requiring freely given, informed, and revocable consent [3,21,36]. Statements gauged whether students knew they had the right to opt in or out of specific data uses (awareness), whether they expected meaningful consent opportunities (expectations), and whether they trusted the institution to respect their consent decisions (confidence).
Thus, the nine components emerge as harmonised principles bridging global best practices with Zimbabwe’s local context. While FIPPs provide the foundational blueprint, the OECD contextualises these principles for cross-border relevance, the GDPR translates them into legally enforceable rights, and the ZDPA adapts them for national implementation.
3. Relationship to Prior Publications and Study Contribution
This study builds on our previously developed IPPS instrument and its initial validation work. The present manuscript does not introduce a new wave of data collection; rather, it provides a diagnostic application of the IPPS using the same core dataset reported in the doctoral study [13]. Specifically, the study presents a benchmarking profile of privacy principles across nine privacy components and three perception dimensions (awareness, expectations, confidence). It identifies actionable areas of trust deficit where student expectations and awareness substantially exceed confidence in institutional compliance. In doing so, the study translates privacy framework and regulatory principles into practical governance priorities for higher education institutions.
4. Methodology
4.1. Research Design
The research adopted a quantitative, cross-sectional survey design [37] to assess student perceptions. This design enabled comparison of students’ perceptions across a diverse student group without tracking changes over time.
4.2. Sampling and Participants
A non-probability convenience sampling approach was used to recruit participants [38]. The study sampled students from a private university in Zimbabwe, which operates under the Zimbabwe Data Protection Act. Participants comprised undergraduate, postgraduate, and short-course students across different faculties and modes of study. Inclusion criteria required that participants be registered students aged 18 years or older with exposure to institutional data-collection systems such as student registration platforms and learning-management systems. Incomplete questionnaires and responses from non-students were excluded from the analysis.
4.3. Data Collection/Dataset
Data were collected using a dual-channel approach. An electronic version of the questionnaire was distributed via institutional communication platforms, including email lists and learning-management systems. In addition, paper-based questionnaires were administered during selected lectures to ensure participation from students with limited online access. Due to the open nature of distribution across multiple platforms and classes, an exact denominator for the response rate could not be established. Before completing the survey, participants were assured that their responses would be confidential and anonymous and that participation was voluntary, with no consequences for non-participation. The dataset analysed in this paper comprises 287 completed responses. These responses constitute the core dataset used in the original IPPS validation phase. In this manuscript, we conducted a secondary, component-level descriptive analysis to develop a diagnostic privacy profile and actionable gap interpretation (awareness/expectations versus confidence) to inform institutional privacy practice improvement.
4.4. Instrument Development
The survey instrument (the IPPS) was developed by mapping three primary privacy dimensions (awareness, expectations, confidence) to nine components: notice/openness, purpose specification, information quality, use limitation, collection limitation, individual participation, privacy education, privacy policy, and consent. Additionally, six statements were formulated for each component: two for each dimension, resulting in a comprehensive and balanced tool capable of generating elegant insights (Refer to Appendix A for the questionnaire statements). The questionnaire was validated using established statistical criteria [39]. The Kaiser-Meyer-Olkin (KMO) measure of sampling adequacy exceeded the recommended threshold of 0.60, indicating that the data were suitable for factor-based analysis. Bartlett’s Test of Sphericity was statistically significant (p < 0.001), confirming sufficient inter-item correlations. Internal consistency reliability was assessed using Cronbach’s alpha, with coefficients exceeding the acceptable threshold of 0.70 across the privacy dimensions, indicating satisfactory reliability. These results confirm the instrument’s adequacy and internal consistency for the purposes of this study.
4.5. Data Analysis
This paper’s analysis focused on descriptive statistics, including means, standard deviations, and frequency distributions, summarising responses for each item and component. This approach provided a clear overview of where students felt informed and confident and where noteworthy knowledge or trust gaps existed. Participants answered the survey questions using a five-point Likert-type scale (strongly disagree, disagree, neither agree nor disagree, agree, and strongly agree). Data screening was conducted before analysis. Questionnaires with substantial missing data were excluded. The final dataset comprised 287 valid responses and contained minimal missing values; listwise deletion was applied in the descriptive analyses. Component-level scores were calculated by averaging item responses within each privacy component and perception dimension (awareness, expectations, and confidence). All survey items were positively worded; therefore, no reverse coding was required.
4.6. Ethical Considerations
Ethical clearance was obtained from the institution’s research ethics committee (030/KM/2019/CSET_SOC). All participants provided informed consent, and no identifying information was retained in the dataset. Data was securely stored to maintain confidentiality.
5. Results
5.1. Response Rate
The study collected 287 valid responses from a diverse sample of undergraduate, postgraduate, and certificate-level students across multiple learning modes. Given the logistical challenges of administering surveys in developing-country contexts where digital connectivity, institutional access, and survey fatigue often constrain participation, this response rate is both substantial and credible. It reflects strong student engagement and interest in information privacy, signalling its relevance to their academic and personal experiences. The balance in gender representation and the spread across learning modes strengthen the representativeness of the findings. However, most Zimbabwean participants (98.9%) mean that the results are heavily context-specific.
5.2. Demographic Information
The demographic information was analysed based on the age distribution, gender, nationality, mode of learning, year, and programme of study, as summarised in Table 1.
Table 1.
Summary of respondents’ demographic information.
The demographic analysis revealed a diverse student population, primarily aged 1977–1995 (61.7%), with younger (23.3%) and older (14.3%) cohorts contributing intergenerational perspectives on privacy. Gender representation was balanced, with males (48.8%), females (49.8%), and a small “other” group (1.4%), enabling gender-based privacy insights. Most participants were Zimbabwean (98.9%), reflecting the study’s local focus. Learning modes varied, with conventional (49.1%) and parallel (31%) students dominating. Senior undergraduates (60%) and IT-related programmes (57.1%) were prominent, suggesting higher privacy awareness stemming from academic exposure and experience, while postgraduate input added depth to research-related privacy concerns.
5.3. Descriptive Statistics
The survey mapped responses to the nine privacy components: notice/openness, information quality, purpose specification, use limitation, collection limitation, individual participation, privacy policy, privacy education, and consent. The mean values are summarised in Table 2.
Table 2.
Mean values for the 3 privacy concepts across the 9 privacy components.
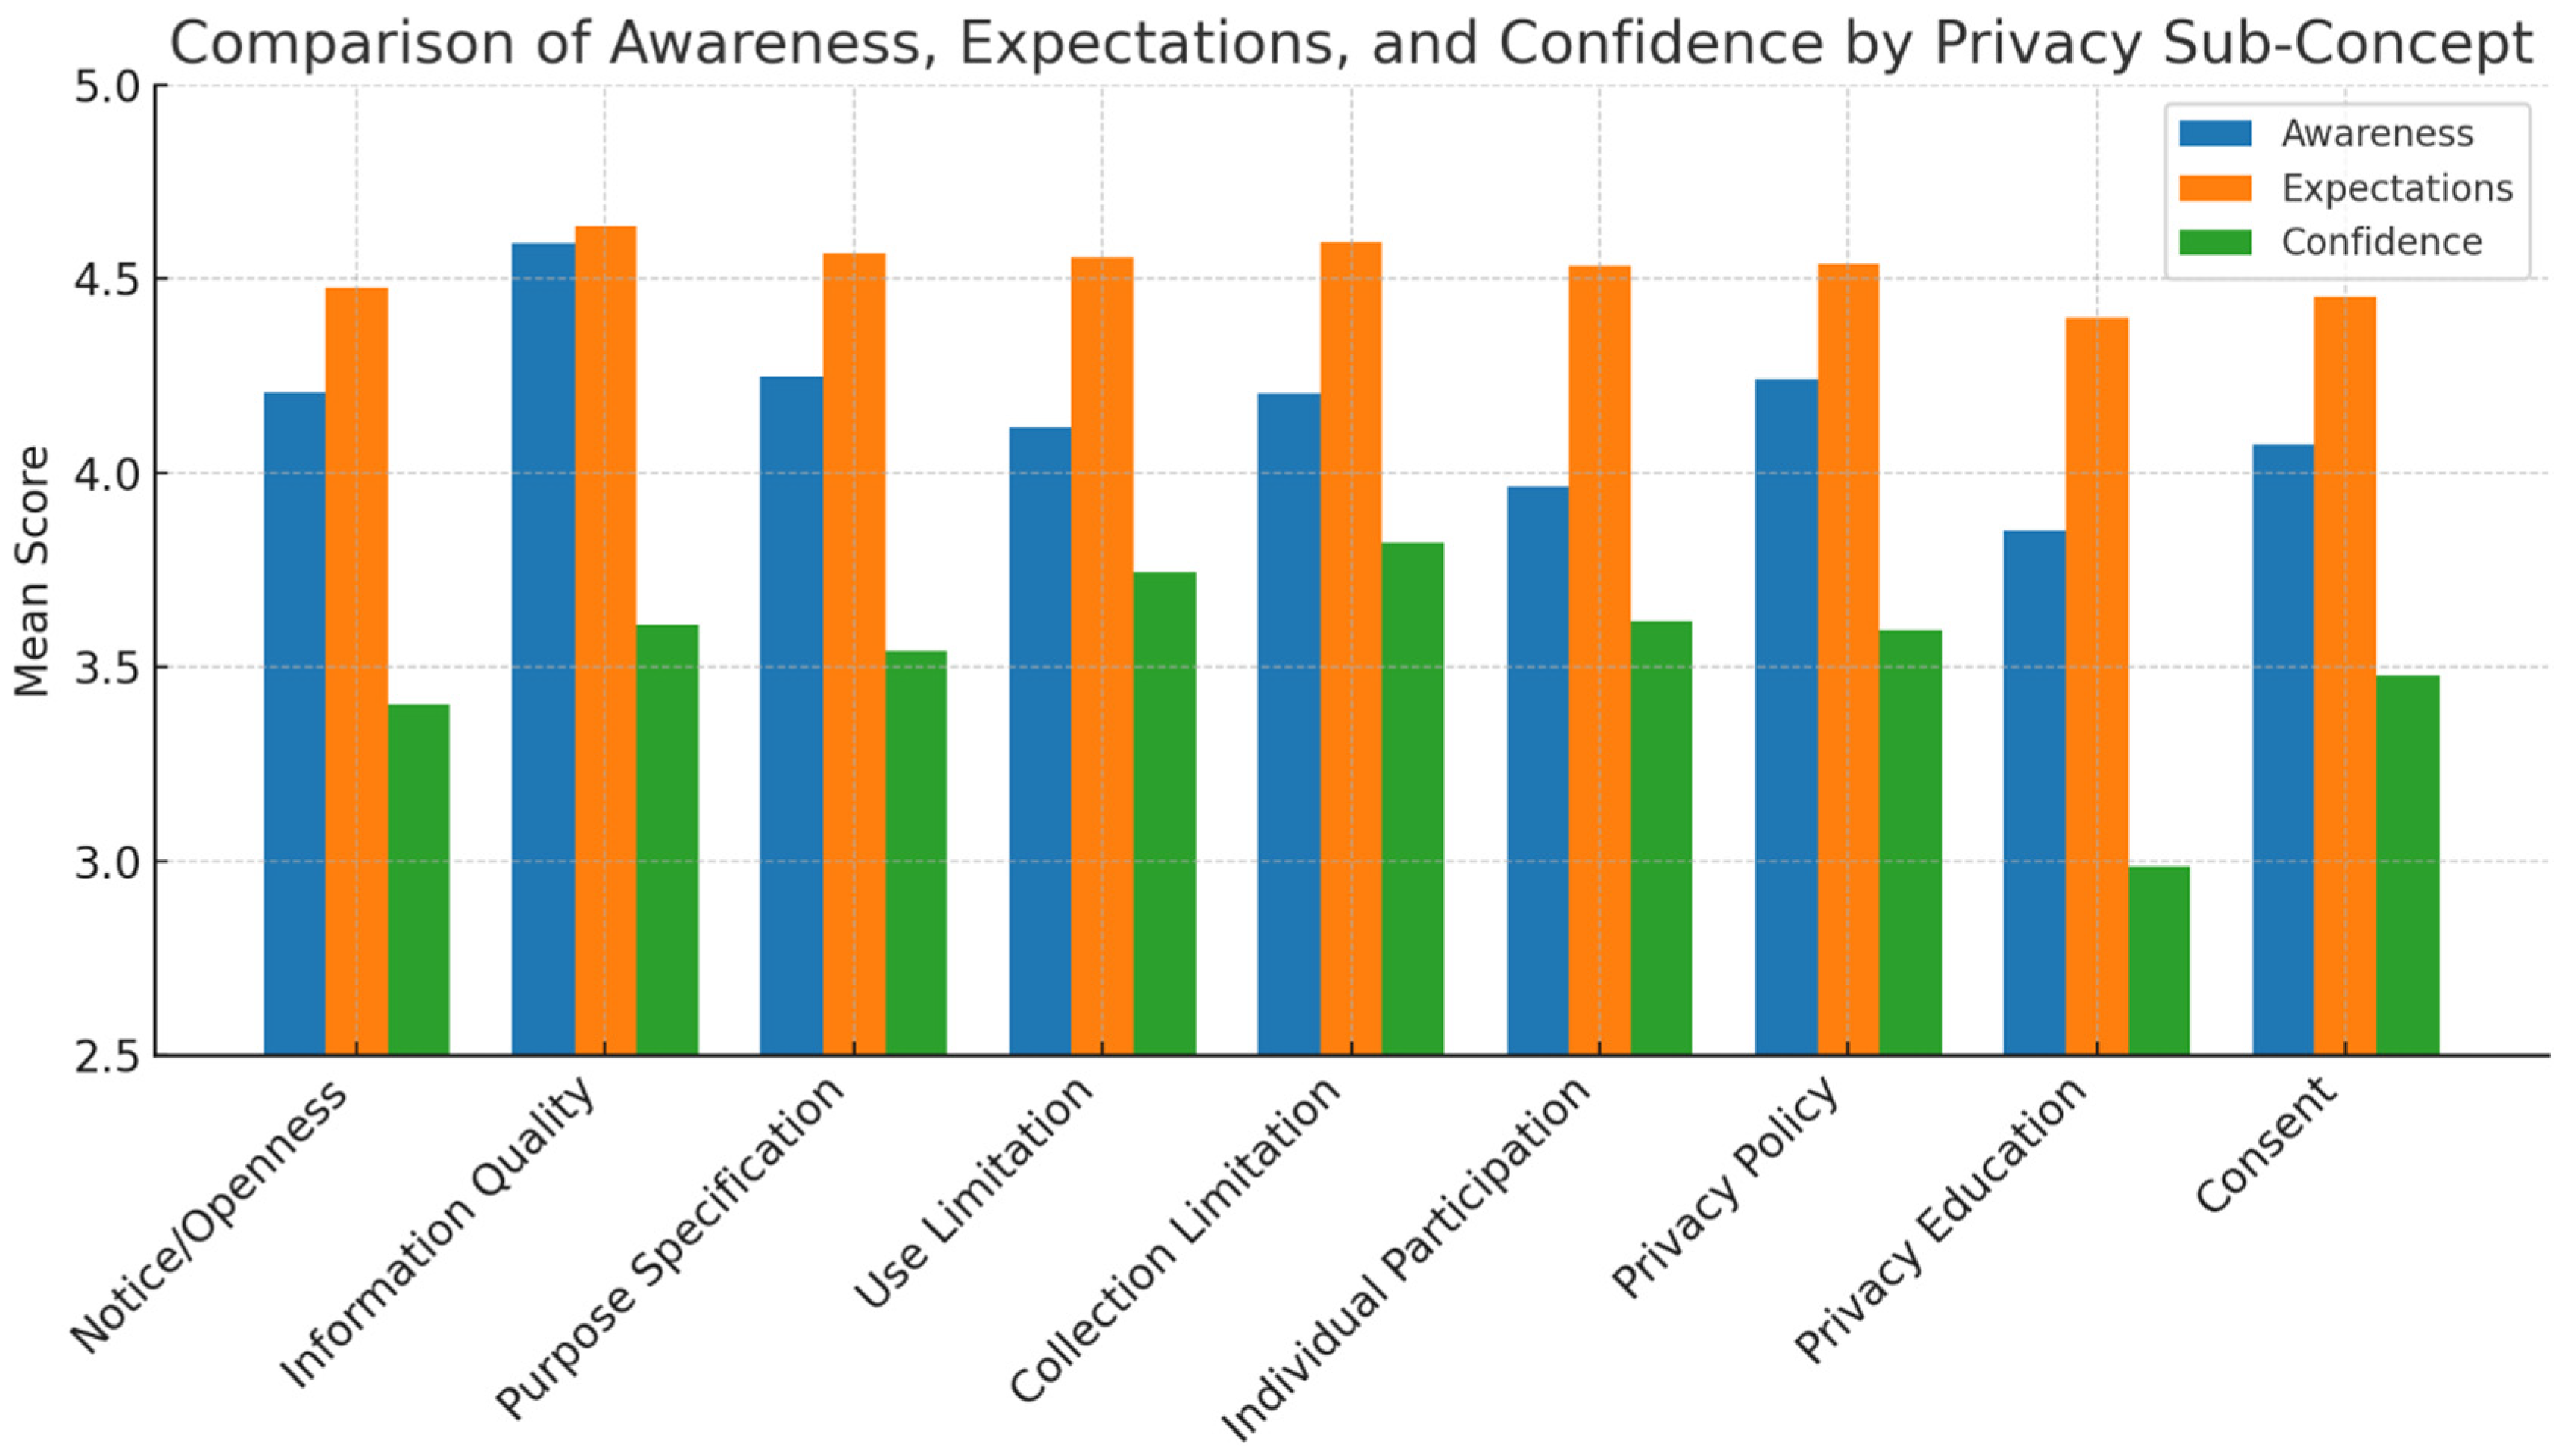
The study applied the interpretation thresholds recommended by [40], where mean scores of 1.00–1.79 reflect strong disagreement, 1.80–2.59 disagreement, 2.60–3.39 neutrality, 3.40–4.19 agreement, and 4.20–5.00 strong agreement. These ranges enabled the study to meaningfully translate numerical values into the intensity of respondents’ perceptions. Across all dimensions, awareness and expectations were high, while confidence consistently lagged, as further depicted in Appendix A. The findings reveal a paradox: students are aware of privacy principles and strongly expect robust measures, yet their confidence in the institutional capacity to implement them remains modest. The mean values for the three privacy concepts across the nine privacy components are also depicted visually in Figure 1.
Figure 1.
Comparison of each privacy component.
The bar graph shows consistently high awareness (≈3.85–4.59) and expectations (≈4.40–4.63) across all nine privacy dimensions, indicating that students clearly understand privacy principles and strongly expect institutions to uphold them. However, confidence levels are noticeably lower (≈2.99–3.82), indicating substantial trust gaps. The lowest scores are in privacy education (2.99), notice/openness (3.40), consent (3.48), and purpose specification (3.54), areas where students doubt institutional compliance despite strong awareness and expectations. In contrast, slightly higher confidence in use limitation (3.74) and collection limitation (3.82) suggests that institutions are viewed as more capable in technical data management than in transparency and engagement. The figure highlights a pronounced awareness-confidence divide: students know and expect more than they believe their institutions deliver, highlighting the urgent need for visible accountability, participatory mechanisms, and strengthened privacy education within Zimbabwe’s higher education landscape.
5.4. Analysis of the Nine Themes Based on Descriptive Statistics
The section below analyses the nine components of this study that were assessed with the IPPS instrument, based on the findings:
- i.
- Notice/openness
Students demonstrated strong awareness and expectations for openness (M = 3.93–4.48; 4.37–4.59), though confidence was much lower (M ≈ 3.36–3.45). This suggests that students know they should be informed about data collection but are sceptical that institutions follow through on this. The policy-practice gap reveals credibility concerns, with transparency often remaining rhetorical rather than actively implemented in institutional systems.
- ii.
- Information quality
Students showed high awareness (M ≈ 4.54–4.65) and high expectations (M ≈ 4.59–4.68), reflecting their understanding of the importance of accuracy in educational records. However, confidence levels (M ≈ 3.54–3.68) reveal doubts about institutional capacity to maintain reliable data. This distrust may stem from prior experiences of errors in academic records or administrative inefficiencies, highlighting operational weaknesses in data stewardship.
- iii.
- Purpose specification
Students have a high awareness (M ≈ 4.19–4.31) and very high expectations (M ≈ 4.54–4.59) of privacy. Yet, confidence remained modest (M ≈ 3.51–3.58). This can be interpreted as students knowing that institutions should specify reasons for data collection and strongly expect this to occur, yet showing lower confidence, reflecting doubt in compliance.
- iv.
- Use limitation
Expectations regarding use limitations were strong (M ≈ 4.50–4.61), with students believing their data should only be disclosed with consent. Equally, students showed high awareness of use limitations (M ≈ 3.93–4.31). However, confidence was lower (M ≈ 3.66–3.82), pointing to doubts about third-party disclosures. This misalignment reflects fear of data misuse, particularly in contexts where enforcement mechanisms are weak, and may reveal apprehension about commercial exploitation or surveillance.
- v.
- Collection limitation
Respondents strongly expected minimisation of data collection (M ≈ 4.49–4.70) and high awareness (M ≈ 4.05–4.36), but confidence was moderate (M ≈ 3.79–3.85). Students are aware of the need for lawful, minimal collection and strongly expect this standard, but confidence is weaker, showing suspicion of over-collection. Their scepticism indicates suspicion that institutions collect unnecessary information, perhaps for administrative convenience.
- vi.
- Individual participation
Awareness and expectations for student participation rights (M ≈ 3.94–4.00; 4.53–4.54) were moderately high and robust, but confidence was lower (M ≈ 3.59–3.65). Students know they should have access to their records and strongly expect institutions to honour this right, yet confidence drops due to doubts about responsiveness.
- vii.
- Privacy policy
Findings showed strong awareness and expectations (M ≈ 4.24–4.54) but weaker confidence (M ≈ 3.59–3.60). Students know policies exist and expect them to be clear, but confidence lags, suggesting policies are symbolic rather than actionable. While policies may be published, students expect these documents to be symbolic rather than functional. Confidence is undermined when policies exist without meaningful enforcement or regular review. Institutions risk reputational harm if policies are perceived as mere compliance exercises, rather than genuine commitments to protecting student data.
- viii.
- Privacy education
Students strongly expected institutional responsibility for privacy education (M ≈ 4.37–4.43), and a moderate awareness (M ≈ 3.84–3.86), yet confidence was very low (M ≈ 2.97–3.00). This component showed the largest gap across all domains. Students want continuous privacy education but have little confidence that it exists. The findings suggest institutions have failed to embed privacy literacy into curricula or training. Students recognise the importance of awareness but perceive a systemic neglect, exposing a critical vulnerability in institutional data governance.
- ix.
- Consent
Respondents demonstrated strong awareness and expectations of consent rights (M ≈ 4.02–4.46), but confidence remained low (M ≈ 3.47–3.48). Students were aware of their right to opt in/out and strongly expected meaningful consent mechanisms, yet confidence was low. This reflects compliance weaknesses under both the GDPR and the ZDPA principles.
6. Discussion
The findings reveal a consistent paradox: students in Zimbabwean higher education institutions are highly aware of privacy rights and strongly expect these to be upheld, yet their confidence in institutional compliance remains low. This pattern points to a credibility gap rather than ignorance. Students clearly understand privacy principles but doubt that institutions practice them meaningfully. Similar patterns have been reported in other developing contexts where policies are sound on paper but weakly enforced in practice [2,3].
The descriptive statistics indicate that awareness and expectations consistently exceeded 4.0 on the five-point Likert scale, while confidence lagged below 3.6 across all components. This demonstrates that students perceive institutions as administratively capable but lack transparency and accountability. Consistent with [41,42], the results suggest that communication alone does not build trust; students need visible, actionable proof of ethical data management. The pronounced deficit in privacy education highlights that institutions are not embedding privacy literacy within their culture. Without such initiatives, awareness remains theoretical and fails to translate into confidence. The low confidence levels for notice and openness echo [43] South African findings, where compliance with consent and disclosure obligations was largely symbolic. Students know they should be informed about how their data is collected and used, yet transparency is often reduced to generic privacy statements. In contrast, GDPR contexts emphasise proactive disclosure and enforcement, which explains higher public confidence [44]. This comparison highlights the urgency for Zimbabwean universities to ensure that privacy notices are not only accessible but also actively explained and enforced.
The component on information quality further exposes institutional weaknesses. Students expect accurate and secure handling of their personal data, but remain doubtful about data integrity, an issue similarly observed by [45,46]. Errors in records and administrative inefficiencies undermine trust, while the absence of independent audits or correction mechanisms reinforces perceptions of negligence. Results from purpose specification, use limitation, and collection limitation reveal that students are uneasy about the breadth of data collected and the opacity surrounding its use. As in Nigeria [47], unclear communication about data purposes undermines institutional credibility. Studies by [48,49] similarly report that students are often unaware of third-party data sharing, heightening concerns of misuse. Ethical data minimisation and clarity of purpose are thus central to restoring trust.
Privacy policy and education emerge as the weakest pillars of confidence. Although students know policies exist, they often view them as symbolic rather than functional, echoing [50]. The lowest privacy education scores confirm a critical gap: institutions have not invested in sustained, meaningful privacy training. As [48] argue, awareness without engagement perpetuates superficial understanding. Integrating privacy education into student orientation, curricula, and research training could transform privacy from compliance rhetoric into shared institutional practice. The consent results illustrate Zimbabwe’s enduring challenge of tokenistic compliance. Students know their opt-in and opt-out rights but doubt their enforcement. This mirrors [43] findings in South Africa, where consent was procedural rather than empowering. By contrast, GDPR enforcement and penalties promote meaningful consent [36]. Without similar accountability structures, Zimbabwe’s legal frameworks risk remaining largely declarative.
Therefore, the issue is not students’ lack of awareness but institutional trustworthiness. The results reveal a culture in which privacy is formalised in policy but absent in practice. Closing the awareness-confidence gap requires universities to demonstrate ethical stewardship through transparency, accountability, and continuous privacy education. Only when institutions move from symbolic compliance to authentic engagement will they cultivate a culture of trust, safeguarding both students’ data and their confidence in the higher education system.
7. Study Implications
7.1. Theoretical Implications
This study deepens privacy theory by empirically validating the tri-construct model: awareness, expectations, and confidence within the context of a developing country’s higher education system. While prior studies have examined these dimensions in isolation, our findings demonstrate that the three are interdependent but unevenly distributed. High awareness and expectations are insufficient without institutional credibility to sustain confidence. This offers a theoretical contribution by framing trust deficit as a distinct construct that mediates between awareness/expectations and actual behaviour. Furthermore, grounding the diagnostic tool in the ZDPA, alongside the FIPPs, the OECD, and the GDPR, strengthens its cross-jurisdictional relevance while still reflecting the socio-legal realities of Zimbabwe.
7.2. Practical Implications
For institutions, the findings signal that policies alone are inadequate if they are not perceived as actionable. Students demand visible, practical interventions: clear privacy notices, transparent consent processes, and accessible mechanisms for record access. The pronounced gap in privacy education underscores the urgent need to integrate privacy literacy into orientation programmes, curricula, and digital literacy initiatives. Practical measures such as dashboards showing how personal data is used, annual privacy audits, and student-centred communication campaigns could build credibility and close the perception-confidence divide.
7.3. Policy Implications
The results highlight the importance of robust enforcement of the ZDPA. While the legal framework is in place, weak institutional compliance risks are eroding trust. As part of a privacy culture, regulators should demand regular compliance reporting, independent audits, and sanctions for non-compliance. Beyond enforcement, policymakers should incentivise institutions to embed privacy education across disciplines and make privacy governance a strategic performance indicator. These measures would align institutional practices with national priorities and international norms.
7.4. Study Limitations
Despite its strengths, the study has limitations. The use of a non-probability sampling approach and the focus on a specific higher-education context have the implication that the findings are diagnostic and context-specific, rather than nationally representative of all Zimbabwean students. Consequently, the study’s contribution lies primarily in its theoretical and methodological insights, particularly in demonstrating how component-level gaps between awareness, expectations, and confidence can be identified using a validated diagnostic instrument, rather than in making population-level inferences. Furthermore, the focus on Zimbabwean institutions limits external validity, as cultural and legal contexts differ across Africa. Finally, the self-reported nature of survey responses introduces potential social desirability and recall biases. In contrast, the cross-sectional design captures perceptions at a single point in time without accounting for how they evolve over time or in response to regulatory shifts.
7.5. Recommendations for Future Studies
Future research should apply probability sampling across diverse faculties and institutions to capture a broader student perspective. Moreover, longitudinal studies would reveal how awareness, expectations, and confidence evolve over time, particularly in response to the introduction of new privacy legislation or digital tools. A mixed-methods approach, combining surveys with interviews or focus groups, would provide richer insights into why gaps persist. Additionally, cross-country comparative studies within the Global South would help determine whether Zimbabwe’s trust deficit is unique or reflects a broader regional challenge. Finally, intervention studies evaluating the impact of privacy education programmes or institutional transparency initiatives could move the field from diagnosis to tested solutions.
8. Conclusions
This study demonstrates that Zimbabwean students are highly aware of privacy rights and strongly expect institutions to uphold them, yet their confidence in institutional practice remains subdued. The most acute deficits lie in privacy education, consent, and transparency, where expectations are unmet by lived experience. Theoretically, this exposes a credibility gap that reframes our understanding of privacy perceptions in higher education. Practically and politically, it challenges institutions and regulators to move beyond symbolic compliance toward demonstrable action. Building student trust will require not only strong legal frameworks but also visible, student-centred practices that embed privacy into the culture of higher education. Only by closing the awareness-confidence gap can institutions in developing contexts align with global best practice while safeguarding the dignity and agency of their learners.
Author Contributions
Conceptualisation, K.M., A.D.V. and N.M.; methodology, K.M., A.D.V. and N.M.; data analysis, K.M., A.D.V. and N.M.; writing, K.M.; review and editing, A.D.V. and N.M. All authors have read and agreed to the published version of the manuscript.
Funding
This research received no external funding.
Institutional Review Board Statement
Ethical clearance was obtained from the institution’s research ethics committee (030/KM/2019/CSET_SOC). All participants provided informed consent, and no identifying information was retained in the dataset. Data was securely stored to maintain confidentiality.
Informed Consent Statement
The study provides each participant with a Participant Information Statement (PIS), clearly outlining the study’s purpose and objectives. Students are informed of their right to opt out at any time should they feel uncomfortable sharing their information, ensuring respect for individual autonomy and voluntary participation.
Data Availability Statement
The original contributions presented in this study are included in the article. Further inquiries can be directed to the corresponding author.
Acknowledgments
The authors used the artificial intelligence tools ChatGPT 5 and Grammarly AI (v1.2.207.1776) for English-language editing. The fluency and spelling of the English manuscript are targeted, and there is no AI-generated content. After the language check using AI tools, the authors rechecked and approved the content and take full responsibility for this publication.
Conflicts of Interest
The authors confirm that there are no potential conflicts of interest related to this publication.
Abbreviations
The following abbreviations are used in this manuscript:
| BTS | Bartlett’s Test of Sphericity |
| FIPPs | Fair Information Practice Principles |
| GDPR | General Data Protection Regulation |
| IPPS | Information Privacy Perceptions Survey |
| KMO | Kaiser-Meyer-Olkin |
| OECD | Organisation for Economic Cooperation and Development |
| ZDPA | Zimbabwe Data Protection Act |
Appendix A
Table A1.
Descriptive statistics for means [13,22].
References
- Angelova, E. Cybersecurity in Higher Education: Challenges and Measures for Information Storage. Bulg. J. Int. Econ. Politics 2024, 4, 110–126. [Google Scholar] [CrossRef] [Scilit]
- Prinsloo, P.; Kaliisa, R. Data privacy on the African continent: Opportunities, challenges and implications for learning analytics. Br. J. Educ. Technol. 2022, 53, 894–913. [Google Scholar] [CrossRef] [Scilit]
- Mutiro, B.; Saki, O. The Cyber and Data Protection Act of Zimbabwe: A critical analysis. Afr. J. Priv. Data Prot. 2024, 1, 50–80. [Google Scholar] [CrossRef] [Scilit]
- Korir, M.; Slade, S.; Holmes, W.; Yingfei, H.; Rienties, B. Investigating the dimensions of students’ privacy concern in the collection, use and sharing of data for learning analytics. Comput. Hum. Behav. Rep. 2023, 9, 100262. [Google Scholar] [CrossRef] [Scilit]
- Sun, J.C. Gaps, guesswork, and ghosts lurking in technology integration: Laws and policies applicable to student privacy. Br. J. Educ. Technol. 2023, 54, 1604–1618. [Google Scholar] [CrossRef] [Scilit]
- Blackmon, S.J.; Major, C.H. Inclusion or infringement? A systematic research review of students’ perspectives on student privacy in technology-enhanced, hybrid, and online courses. Br. J. Educ. Technol. 2023, 54, 1542–1565. [Google Scholar] [CrossRef] [Scilit]
- Yeboah, A.K.; Kim, Y.; Yankson, B.; Aikins, S.; Appiah, Y. Diverse students’ perspectives on privacy and technology integration in higher education. Br. J. Educ. Technol. 2023, 54, 1671–1692. [Google Scholar] [CrossRef] [Scilit]
- Corrin, L. Shifting to digital: A policy perspective on ‘Student perceptions of privacy principles for learning analytics’. Educ. Technol. Res. Dev. 2021, 69, 353–356. [Google Scholar] [CrossRef] [Scilit]
- de Barros, Y.C.; Vilela, J. Data Privacy in Educational Contexts: Analyzing Perceptions, Practices and Challenges in Personal Data Protection. In Proceedings of the 27th International Conference on Enterprise Information Systems (ICEIS 2025), Porto, Portugal, 4–6 April 2025; Volume 2, pp. 978–989. [Google Scholar] [CrossRef] [Scilit]
- Mutunhu, B.; Dube, S.; Ncube, N.; Sibanda, S. Cyber Security Awareness and Education Framework for Zimbabwe Universities: A Case of National University of Science and Technology. In Proceedings of the International Conference on Industrial Engineering and Operations Management, Nsukka, Nigeria, 5–7 April 2022; Available online: https://ieomsociety.org/proceedings/2022nigeria/111.pdf (accessed on 9 September 2025).
- Kabanda, G.; Chingoriwo, T. A Cybersecurity Culture Framework for Grassroots Levels in Zimbabwe. Orient. J. Comput. Sci. Technol. 2021, 14, 17–34. [Google Scholar] [CrossRef] [Scilit]
- Maguraushe, K.; Da Veiga, A.; Martins, N. A conceptual framework for a student personal information privacy culture at universities in Zimbabwe. Kalpa Publ. Comput. 2019, 12, 143–156. [Google Scholar] [CrossRef] [Scilit]
- Maguraushe, K. Development of a Diagnostic Instrument and Privacy Model for Student Personal Information Privacy Perceptions at a Zimbabwean University. Ph.D. Thesis, UNISA, Johannesburg, South Africa, 2021. Available online: https://ir.unisa.ac.za/handle/10500/27557 (accessed on 23 November 2025).
- Mutimukwe, C.; Viberg, O.; Oberg, M.; Pargman, T.C. Students’ privacy concerns in learning analytics: Model development. Br. J. Educ. Technol. 2022, 53, 932–951. [Google Scholar] [CrossRef] [Scilit]
- Velander, J.; Otero, N.; Pargman, T.C.; Milrad, M. “We Know What You Were Doing” Understanding Learners’ Concerns Regarding Learning Analytics and Visualization Practices in Learning Management Systems. In Visualizations and Dashboards for Learning Analytics. Advances in Analytics for Learning and Teaching; Springer: Berlin/Heidelberg, Germany, 2021; pp. 323–347. [Google Scholar] [CrossRef] [Scilit]
- Balash, D.G.; Kim, D.; Shaibekova, D.; Fainchtein, R.A.; Sherr, M.; Aviv, A.J. Examining the Examiners: Students’ Privacy and Security Perceptions of Online Proctoring Services. In Proceedings of the USENIX Security Symposium, Virtual, 12–14 August 2021. [Google Scholar]
- Klemovitch, J.; Sciabbarrasi, L.; Peslak, A. Current privacy policy attitudes and fair information practice principles: A macro and micro analysis. Issues Inf. Syst. 2021, 22, 145–159. [Google Scholar] [CrossRef] [Scilit]
- Stamenkov, G. Genealogy of the fair information practice principles. Int. J. Law Manag. 2023, 65, 242–260. [Google Scholar] [CrossRef] [Scilit]
- Greenleaf, G. It’s Nearly 2020, so What Fate Awaits the 1980 OECD Privacy Guidelines? (A Background Paper for the 2019 OECD Privacy Guidelines Review). Privacy Laws & Business International Report. 2019, Volume 159, pp. 18–21, UNSW Law Research Paper No. 19-42. Available online: https://papers.ssrn.com/sol3/papers.cfm?abstract_id=3405156 (accessed on 23 November 2025).
- Wodi, A. Data Privacy and Security: Fair Information Principles and Data Management Strategies in a Changing World. SSRN Electron. J. 2023, 1–24. [Google Scholar] [CrossRef] [Scilit]
- Saki, O. Data Protection in Zimbabwe with Reference to the Covid-19 Pandemic and International Law. Potchefstroom Electron. Law J. 2024, 27, 1–38. [Google Scholar] [CrossRef] [Scilit]
- Maguraushe, K.; Da Veiga, A.; Martins, N. Validation of an Information Privacy Perception Instrument at a Zimbabwean University. In IFIP Advances in Information and Communication Technology; Clarke, N.L., Furnell, S.S., Eds.; Springer: Berlin/Heidelberg, Germany, 2020; Volume 593, pp. 300–315. [Google Scholar] [CrossRef] [Scilit]
- Maguraushe, K.; da Veiga, A.; Martins, N. A personal information privacy perceptions model for university students. Inf. Secur. J. Glob. Perspect. 2024, 33, 394–424. [Google Scholar] [CrossRef] [Scilit]
- Lee, H.; Kobsa, A. Confident privacy decision-making in IoT environments. ACM Trans. Comput. Hum. Interact. 2019, 27, 1–39. [Google Scholar] [CrossRef] [Scilit]
- Da Veiga, A.; Ophoff, J. Concern for Information Privacy: A Cross-Nation Study of the United Kingdom and South Africa. In IFIP Advances in Information and Communication Technology; Clarke, N.L., Furnell, S.S., Eds.; Springer: Berlin/Heidelberg, Germany, 2020; Volume 593, pp. 16–29. [Google Scholar] [CrossRef] [Scilit]
- Chetty, P. Presentation On Zimbabwe Data Protection Bill. In Harmonization of the ICT Policies in Sub-Saharan Africa. 2013. Available online: https://share.google/AHEcjYzDlp62H3wMk (accessed on 11 September 2025).
- Homeland Security. Privacy Policy Guidance Memorandum; U.S. Department of Homeland Security: Washington, DC, USA, 2008. Available online: https://www.dhs.gov/sites/default/files/publications/privacy_policyguide_2008-02_0.pdf (accessed on 21 September 2025).
- Roos, A. The European Union’s General Data Protection Regulation (GDPR) and its Implications for South African Data Privacy Law: An Evaluation of Selected ‘Content Principles’. Comp. Int. Law J. South. Afr. 2021, 53, 37. [Google Scholar] [CrossRef] [Scilit]
- OECD. The OECD Privacy Guidelines. In The OECD Privacy Framework; OECD: Paris, France, 2013; pp. 1–154. Available online: https://www.itu.int/en/ITU-D/Projects/ITU-EC-ACP/HIPSSA/Documents/In-country%20support%20documents/Zimbabwe_Training%20Data%20Protection_Zimbabwe%20Pria%20Chetty%20July%202013%20Version%201.pdf (accessed on 23 November 2025).
- Teufel, H. The Fair Information Practice Principles: Framework for Privacy Policy at the Department of Homeland Security. 2008. Available online: https://www.dhs.gov/sites/default/files/publications/privacy-policy-guidance-memorandum-2008-01.pdf (accessed on 24 September 2025).
- Gellman, R. Fair Information Practices: A Basic History. SSRN Electron. J. 2017. [Google Scholar] [CrossRef] [Scilit]
- Cavoukian, A. Privacy by Design-The 7 foundational principles-Implementation and mapping of fair information practices. Inf. Priv. Comm. Ont. Can. 2010, 3, 247–251. [Google Scholar] [CrossRef] [Scilit]
- Georgiadou, Y.; de By, R.A.; Kounadi, O. Location Privacy in the Wake of the GDPR. Int. J. Geo-Inf. 2019, 8, 157. [Google Scholar] [CrossRef] [Scilit]
- Isabwe, G.M.N.; Reichert, F. Revisiting students’ privacy in computer-supported learning systems. In Proceedings of the International Conference on Information Society (i-Society), Toronto, ON, Canada, 24–26 June 2013; pp. 256–262. [Google Scholar]
- Chua, H.N.; Herbland, A.; Wong, S.F.; Chang, Y. Compliance to personal data protection principles: A study of how organizations frame privacy policy notices. Telemat. Inform. 2017, 34, 157–170. [Google Scholar] [CrossRef] [Scilit]
- Tikkinen-Piri, C.; Rohunen, A.; Markkula, J. EU General Data Protection Regulation: Changes and implications for personal data collecting companies. Comput. Law Secur. Rev. 2018, 34, 134–153. [Google Scholar] [CrossRef] [Scilit]
- Saunders, M.; Lewis, P.; Thornhill, A. Research Methods for Business Students, 8th ed.; Pearson Education Limited: New York, NY, USA, 2019; Available online: https://www.pearson.com/se/Nordics-Higher-Education/subject-catalogue/business-and-management/Research-methods-for-business-students-8e-saunders.html (accessed on 11 September 2025).
- Creswell, J.W.; Creswell, J.D. Research Design: Qualitative, Quantitative and Mixed Methods Approaches, 5th ed.; SAGE Publications: Thousand Oaks, CA, USA, 2018. [Google Scholar]
- Hair, J.F.; Black, W.C.; Babbin, B.J.; Anderson, R.E. Univariate Data Analysis, 8th ed.; Cengage Learning: London, UK, 2018. [Google Scholar]
- Rahman, F.A.; Ying, W.X.; Chee, T.A.; Xian, V.T.Y.; Kamal, Z.S.B.; Anuar, A.D.B.; Sonjaya, D.; Zamzuri, A.T.B. Dental professionals’ adaptation to COVID-19 transition in Malaysia. Dent. J. 2025, 52, 52–59. [Google Scholar] [CrossRef] [Scilit]
- Taufik, C.I.N.; Juhana, A. The Privacy Paradox of Students’ Personal Data Security in the Digital Age. SATESI J. Sains Teknol. Dan Sist. Inf. 2025, 5, 1–6. [Google Scholar] [CrossRef] [Scilit]
- Sideri, M.; Kitsiou, A.; Tzortzaki, E.; Kalloniatis, C.; Gritzalis, S. Enhancing university students’ privacy literacy through an educational intervention: A Greek case-study. Int. J. Electron. Gov. 2019, 11, 333–360. [Google Scholar] [CrossRef] [Scilit]
- Swartz, P.; Da Veiga, A. PoPI Act-Opt-in and opt-out compliance from a data value chain perspective: A South African insurance industry experiment. In 2016 Information Security for South Africa—Proceedings of the 2016 ISSA Conference, Dallas, TX, USA, 2–3 November 2016; IEEE: New York, NY, USA, 2016; pp. 9–17. [Google Scholar] [CrossRef] [Scilit]
- Li, W.; Xiong, B.; Yang, C. A roadmap to achieving a healthier information ecosystem through GDPR implementation and privacy compliance technologies. J. Assoc. Inf. Sci. Technol. 2024, 75, 1182–1201. [Google Scholar] [CrossRef] [Scilit]
- Nevaranta, M.; Lempinen, K.; Kaila, E. Students’ perceptions about data safety and Ethics in learning analytics. CEUR Workshop Proc. 2020, 2737, 23–37. [Google Scholar]
- West, D.; Luzeckyj, A.; Searle, B.; Toohey, D.; Vanderlelie, J.; Bell, K.R. Perspectives from the stakeholder: Students’ views regarding learning analytics and data collection. Australas. J. Educ. Technol. 2020, 36, 72–88. [Google Scholar] [CrossRef] [Scilit]
- Adelola, T.; Dawson, R.; Batmaz, F. Nigerians’ Perceptions of Personal Data Protection and Privacy. In Proceedings of the Software Quality Management XXIII, Loughborough, UK, 30 March 2015; pp. 113–124. [Google Scholar]
- Jones, K.M.L.; Asher, A.; Goben, A.; Perry, M.R.; Salo, D.; Briney, K.A.; Robertshaw, M.B. “We’re being tracked at all times”: Student perspectives of their privacy in relation to learning analytics in higher education. J. Assoc. Inf. Sci. Technol. 2020, 2019, 1044–1059. [Google Scholar] [CrossRef] [Scilit]
- Jiang, J.A.; Yamamoto, F.R.; Nagy, V.; Zander, M.; Barker, L. Data Privacy in Learning Management Systems: Perceptions of Students, Faculty, and Administrative Staff. In Lecture Notes in Computer Science; Springer: Berlin/Heidelberg, Germany, 2023. [Google Scholar] [CrossRef] [Scilit]
- Pinchevsky, G.M.; Hayes, B.E. College Students Knowledge of Policies, Procedures, and Reporting Options for Sexual Violence: Gaps, Disconnects, and Suggestions for Moving Forward. J. Evid. Based Soc. Work 2022, 19, 608–624. [Google Scholar] [CrossRef] [Scilit]

Disclaimer/Publisher’s Note: The statements, opinions and data contained in all publications are solely those of the individual author(s) and contributor(s) and not of MDPI and/or the editor(s). MDPI and/or the editor(s) disclaim responsibility for any injury to people or property resulting from any ideas, methods, instructions or products referred to in the content. |
© 2026 by the authors. Licensee MDPI, Basel, Switzerland. This article is an open access article distributed under the terms and conditions of the Creative Commons Attribution (CC BY) license.