
Review

A Comprehensive Literature Review of Cybersecurity in Satellite Networks

School of Information and Navigation, Air Force Engineering University, Xi’an 710077, China
*
Author to whom correspondence should be addressed.
Aerospace 2026, 13(3), 249; https://doi.org/10.3390/aerospace13030249
Submission received: 12 December 2025 / Revised: 14 February 2026 / Accepted: 2 March 2026 / Published: 6 March 2026
(This article belongs to the Section Astronautics & Space Science)

Abstract

Satellite networks are essential to global connectivity yet face severe multidimensional cybersecurity threats. This systematic review conducts a holistic analysis of threats across the physical, network, and user layers. We propose the Sat-ATT&CK knowledge matrix to model satellite-specific attack chains. Corresponding defense technologies are organized within the core functions (Protect, Detect, Respond) of the National Institute of Standards and Technology (NIST) Cybersecurity Framework, establishing a structured threat–defense mapping. Furthermore, an exploratory case study on fine-tuning a large language model (SatSec) using the compiled literature corpus is presented. Finally, we identify key challenges and outline the future research directions toward a more resilient and intelligent security paradigm.

1. Introduction

Represented by Starlink and China Satellite Network, satellite networks serve as the core infrastructure for ubiquitous interconnection within space–air–ground integrated information systems. They play an irreplaceable strategic role in diverse domains, including global communications, emergency disaster relief, navigation and positioning, remote sensing, and military operations [1,2,3,4,5,6]. Currently, these networks have evolved into a multi-orbit hybrid architecture, predominantly based on Low Earth Orbit (LEO) satellites, complemented by Medium Earth Orbit (MEO) and Geostationary Earth Orbit (GEO) satellites, working in concert with terrestrial segments to form a comprehensive ecosystem [7].
However, inherent characteristics, such as open channels, dynamic topology, and space–ground heterogeneity, expose satellite networks to severe, multi-dimensional cybersecurity threats. These range from physical-layer eavesdropping and jamming to network-layer routing attacks and Denial-of-Service (DoS), as well as user-layer privacy leakage and identity spoofing. Prominent incidents, including the 2022 KA-SAT network paralysis during the Russia–Ukraine conflict [8,9] and the 2025 infiltration of Iranian oil tanker communication systems [10], underscore that satellite network security is critically linked to national infrastructure resilience, data sovereignty, and the security of space assets.
Despite growing attention, current security research faces significant limitations. Threat analyses often focus on isolated layers or specific attack types, lacking a holistic, multi-level perspective [11,12,13,14,15]. Defense reviews tend toward technology-oriented enumeration without establishing precise mappings to specific threats, obscuring actionable defense logic [16,17,18]. Furthermore, there is a scarcity of dedicated threat taxonomies or knowledge matrices that systematically capture the unique attack tactics and technique chains in satellite contexts.
To bridge these gaps, this survey aims to provide a systematic, layered, and actionable security framework tailored to satellite networks. The primary objectives and contributions are as follows:
(1)
Systematic Threat Analysis: A holistic review of threats across the physical, network, and user layers of satellite networks.
(2)
Standardized Threat Modeling: Development of the Sat-ATT&CK knowledge matrix, a structured taxonomy for characterizing satellite-specific attack chains.
(3)
Structured Defense Overview: Organization of defense technologies based on the core functions of the NIST Cybersecurity Framework (Protect, Detect, Respond), providing a structured view of defensive measures.
(4)
Comprehensive Synthesis and Future Directions: Consolidation of the current landscape, identification of critical challenges, and outlining of key research trajectories.
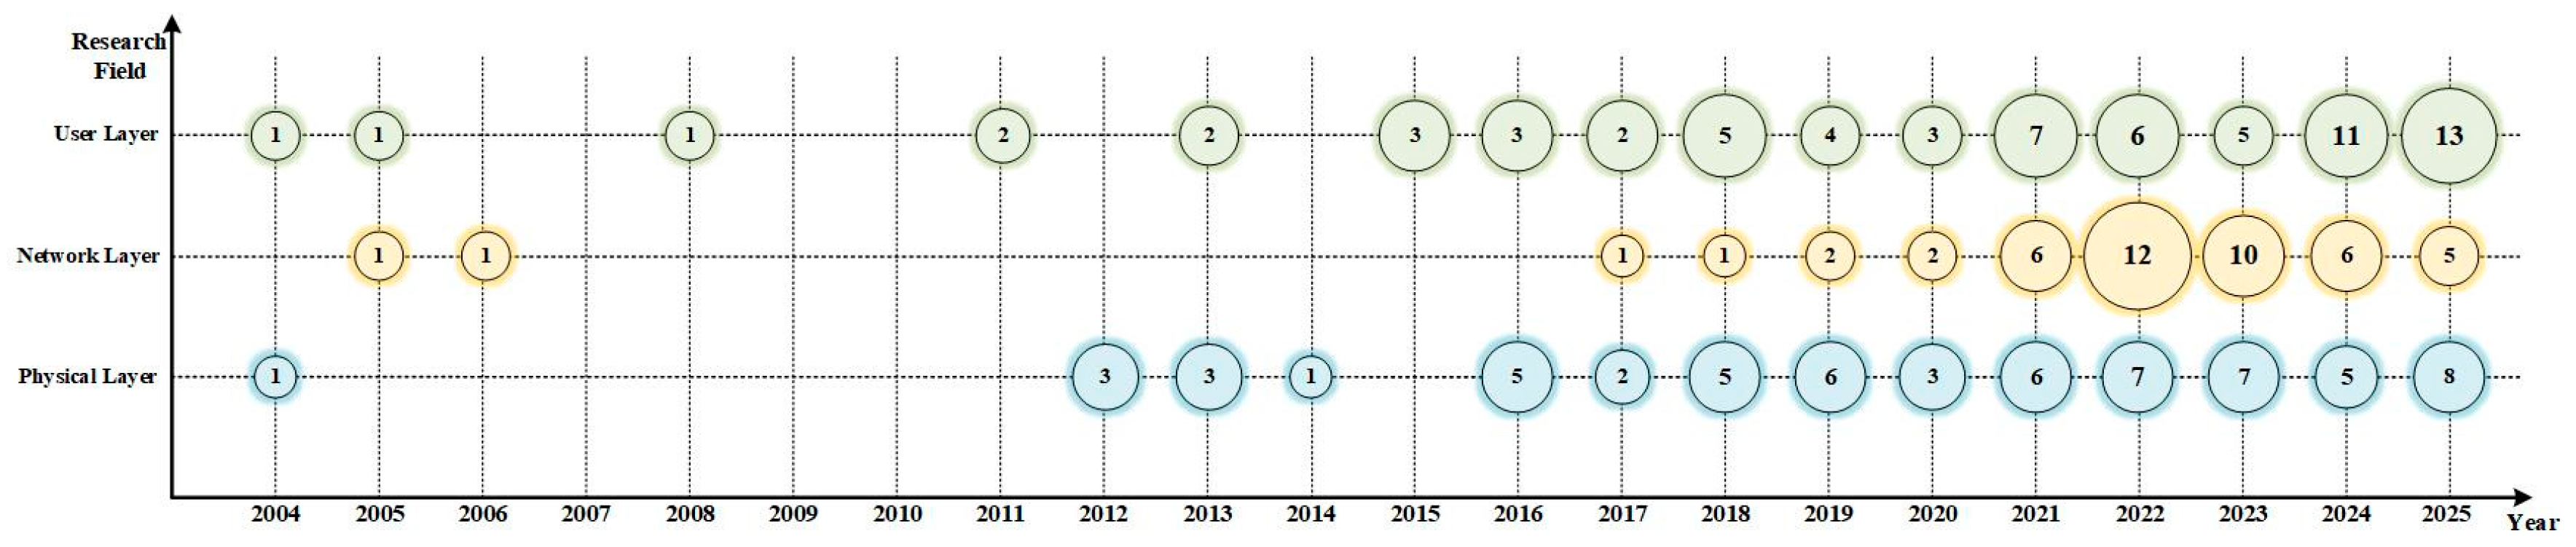
To ensure rigor and reproducibility, this review adhered to the Preferred Reporting Items for Systematic Reviews and Meta-Analyses (PRISMA) guidelines. A comprehensive search across IEEE Xplore, Web of Science, ScienceDirect, CNKI, and arXiv (2004–2025) yielded 387 records. After deduplication and screening, 189 relevant studies were included in the final corpus. To visually present the literature foundation for our layered analysis, this paper employs a bubble chart to analyze the distribution of 189 references. Figure 1 focuses on the three core domains—physical layer, network layer, and user layer—clearly illustrating the research popularity and temporal evolution within each domain.
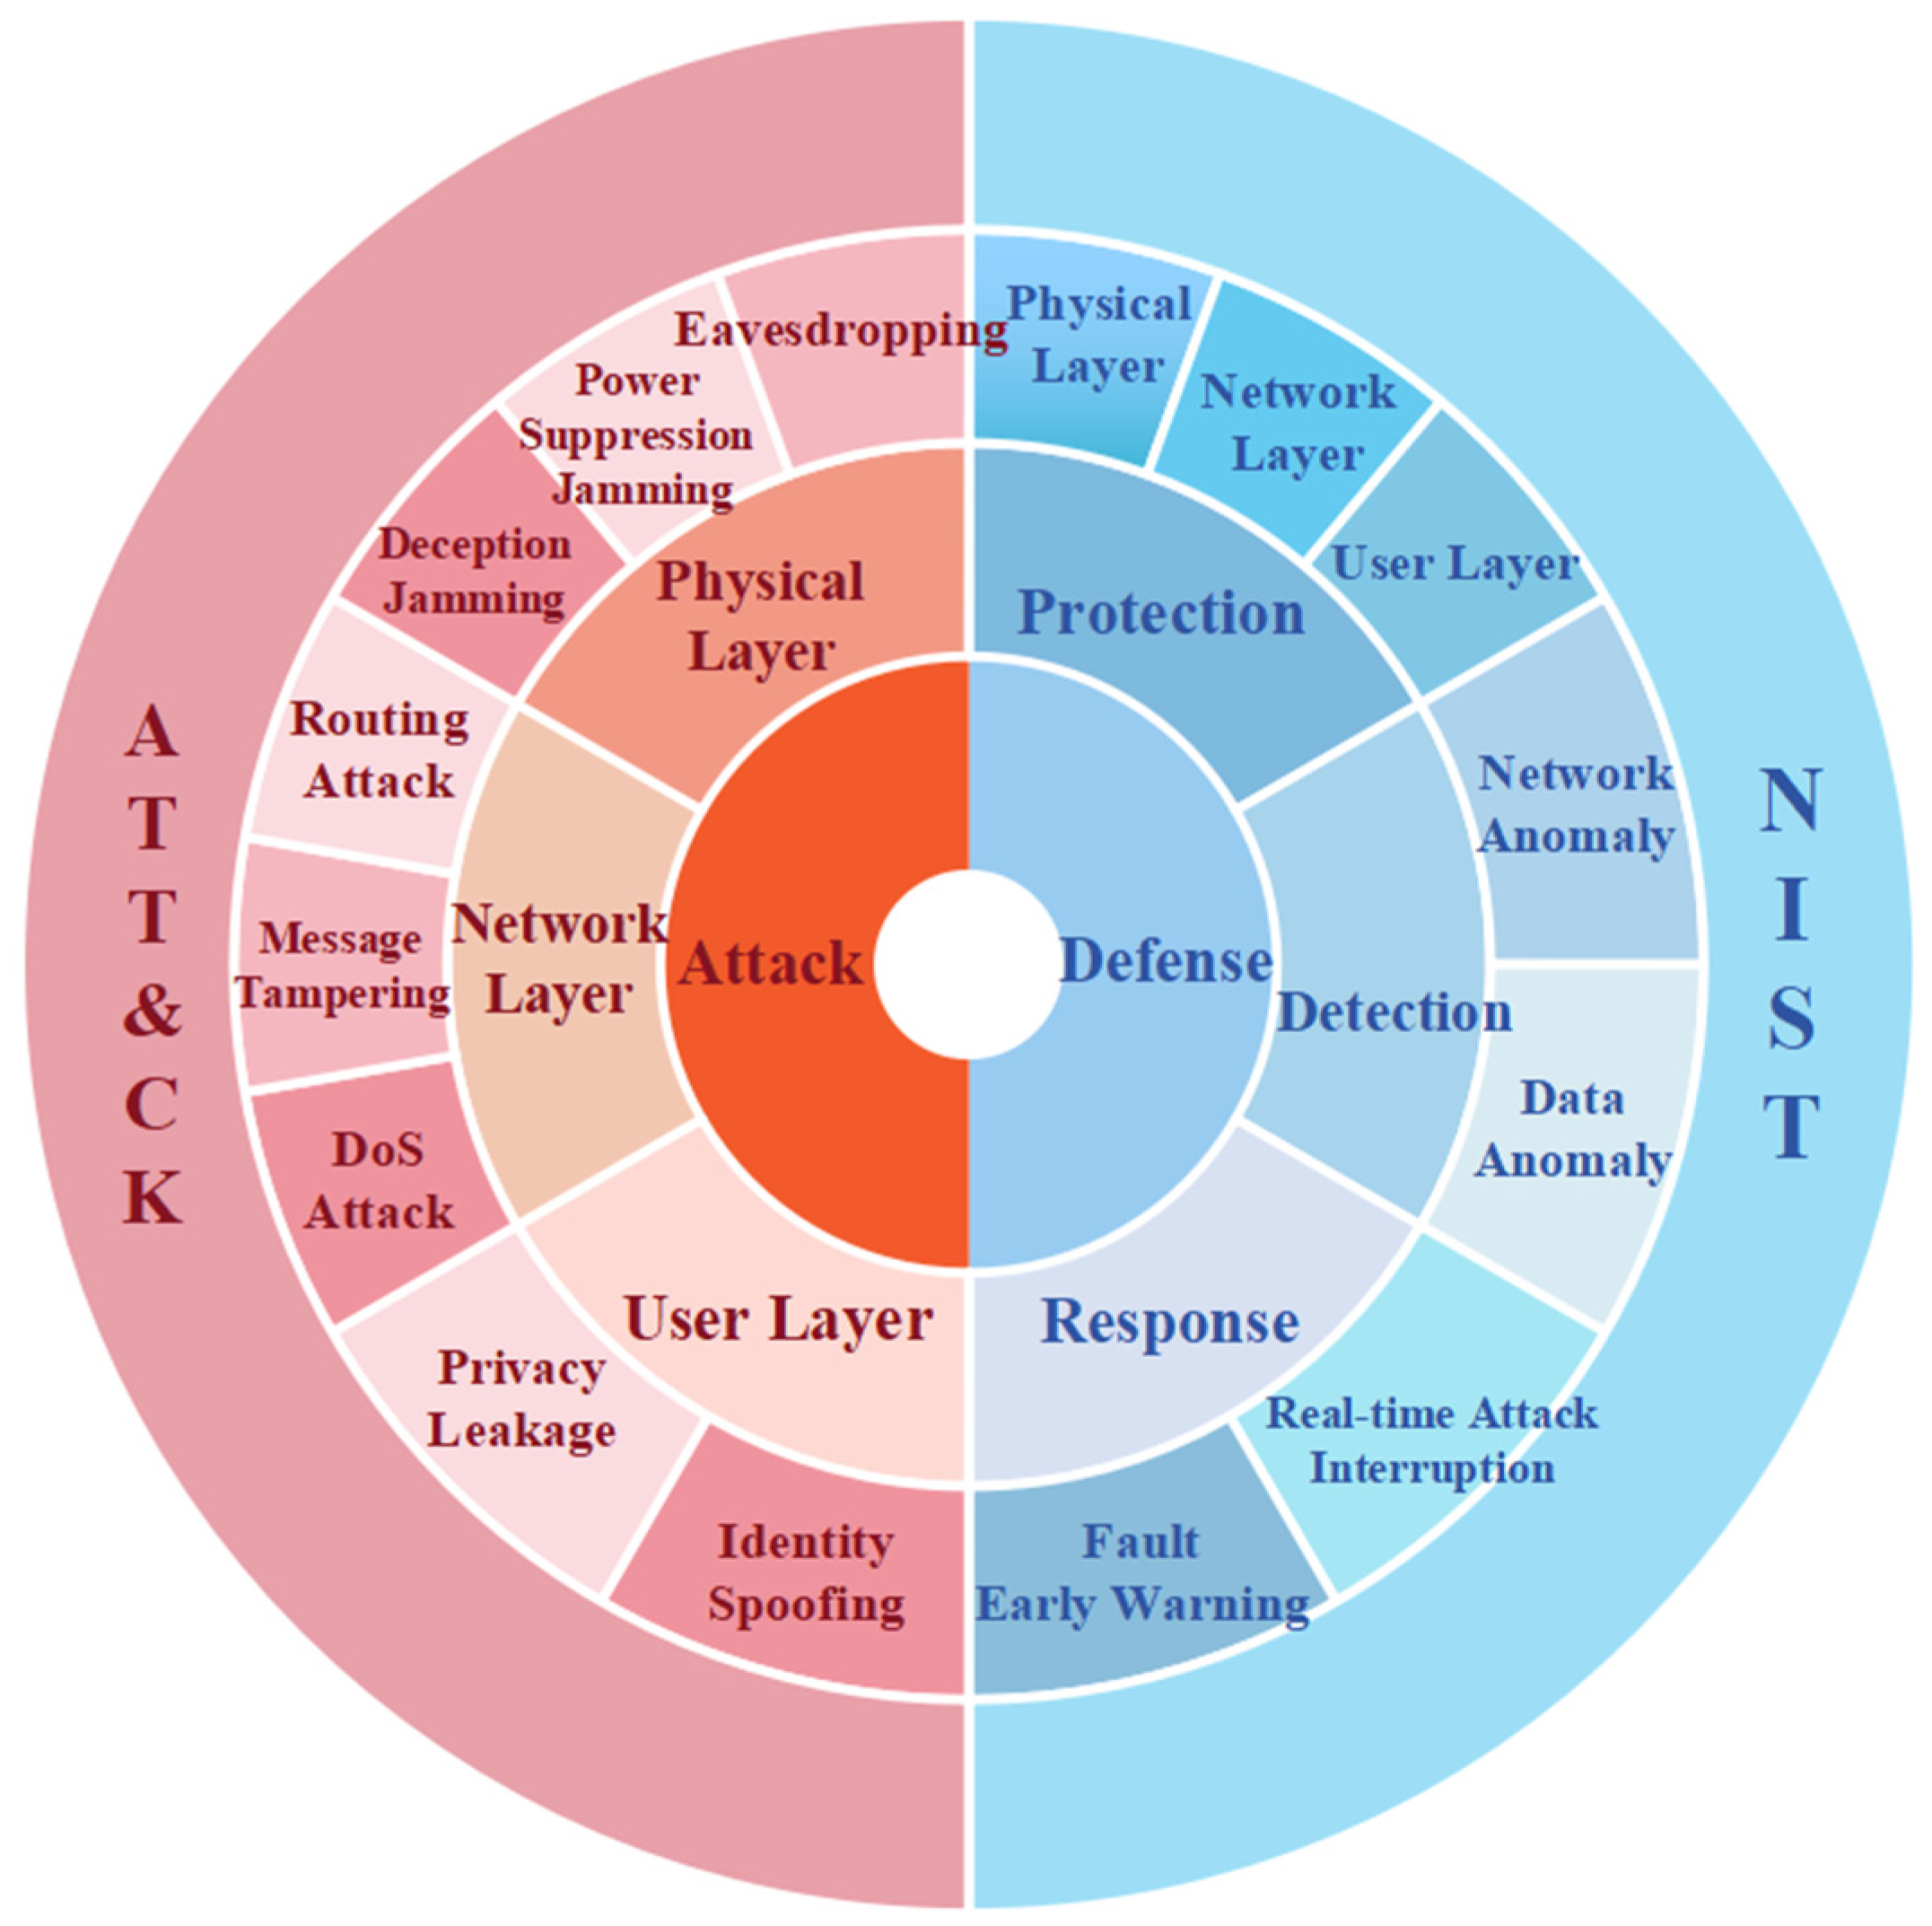
The remainder of this paper is structured as follows: Section 2 introduces the satellite network architecture and reviews existing threat modeling research. Section 3 details the layered threat analysis and presents the Sat-ATT&CK matrix. Section 4 organizes defense technologies according to the NIST CSF’s Protect, Detect, and Respond functions. Section 5 discusses emerging challenges, including an exploratory case study on AI application (SatSec-v1.0). Section 6 concludes the paper and points out future research directions. The overall research framework is illustrated in Figure 2, which outlines the logical flow from threat analysis to defense construction, supported by the Sat-ATT&CK and NIST CSF.

2. Technical Background

2.1. Architecture of Satellite Networks

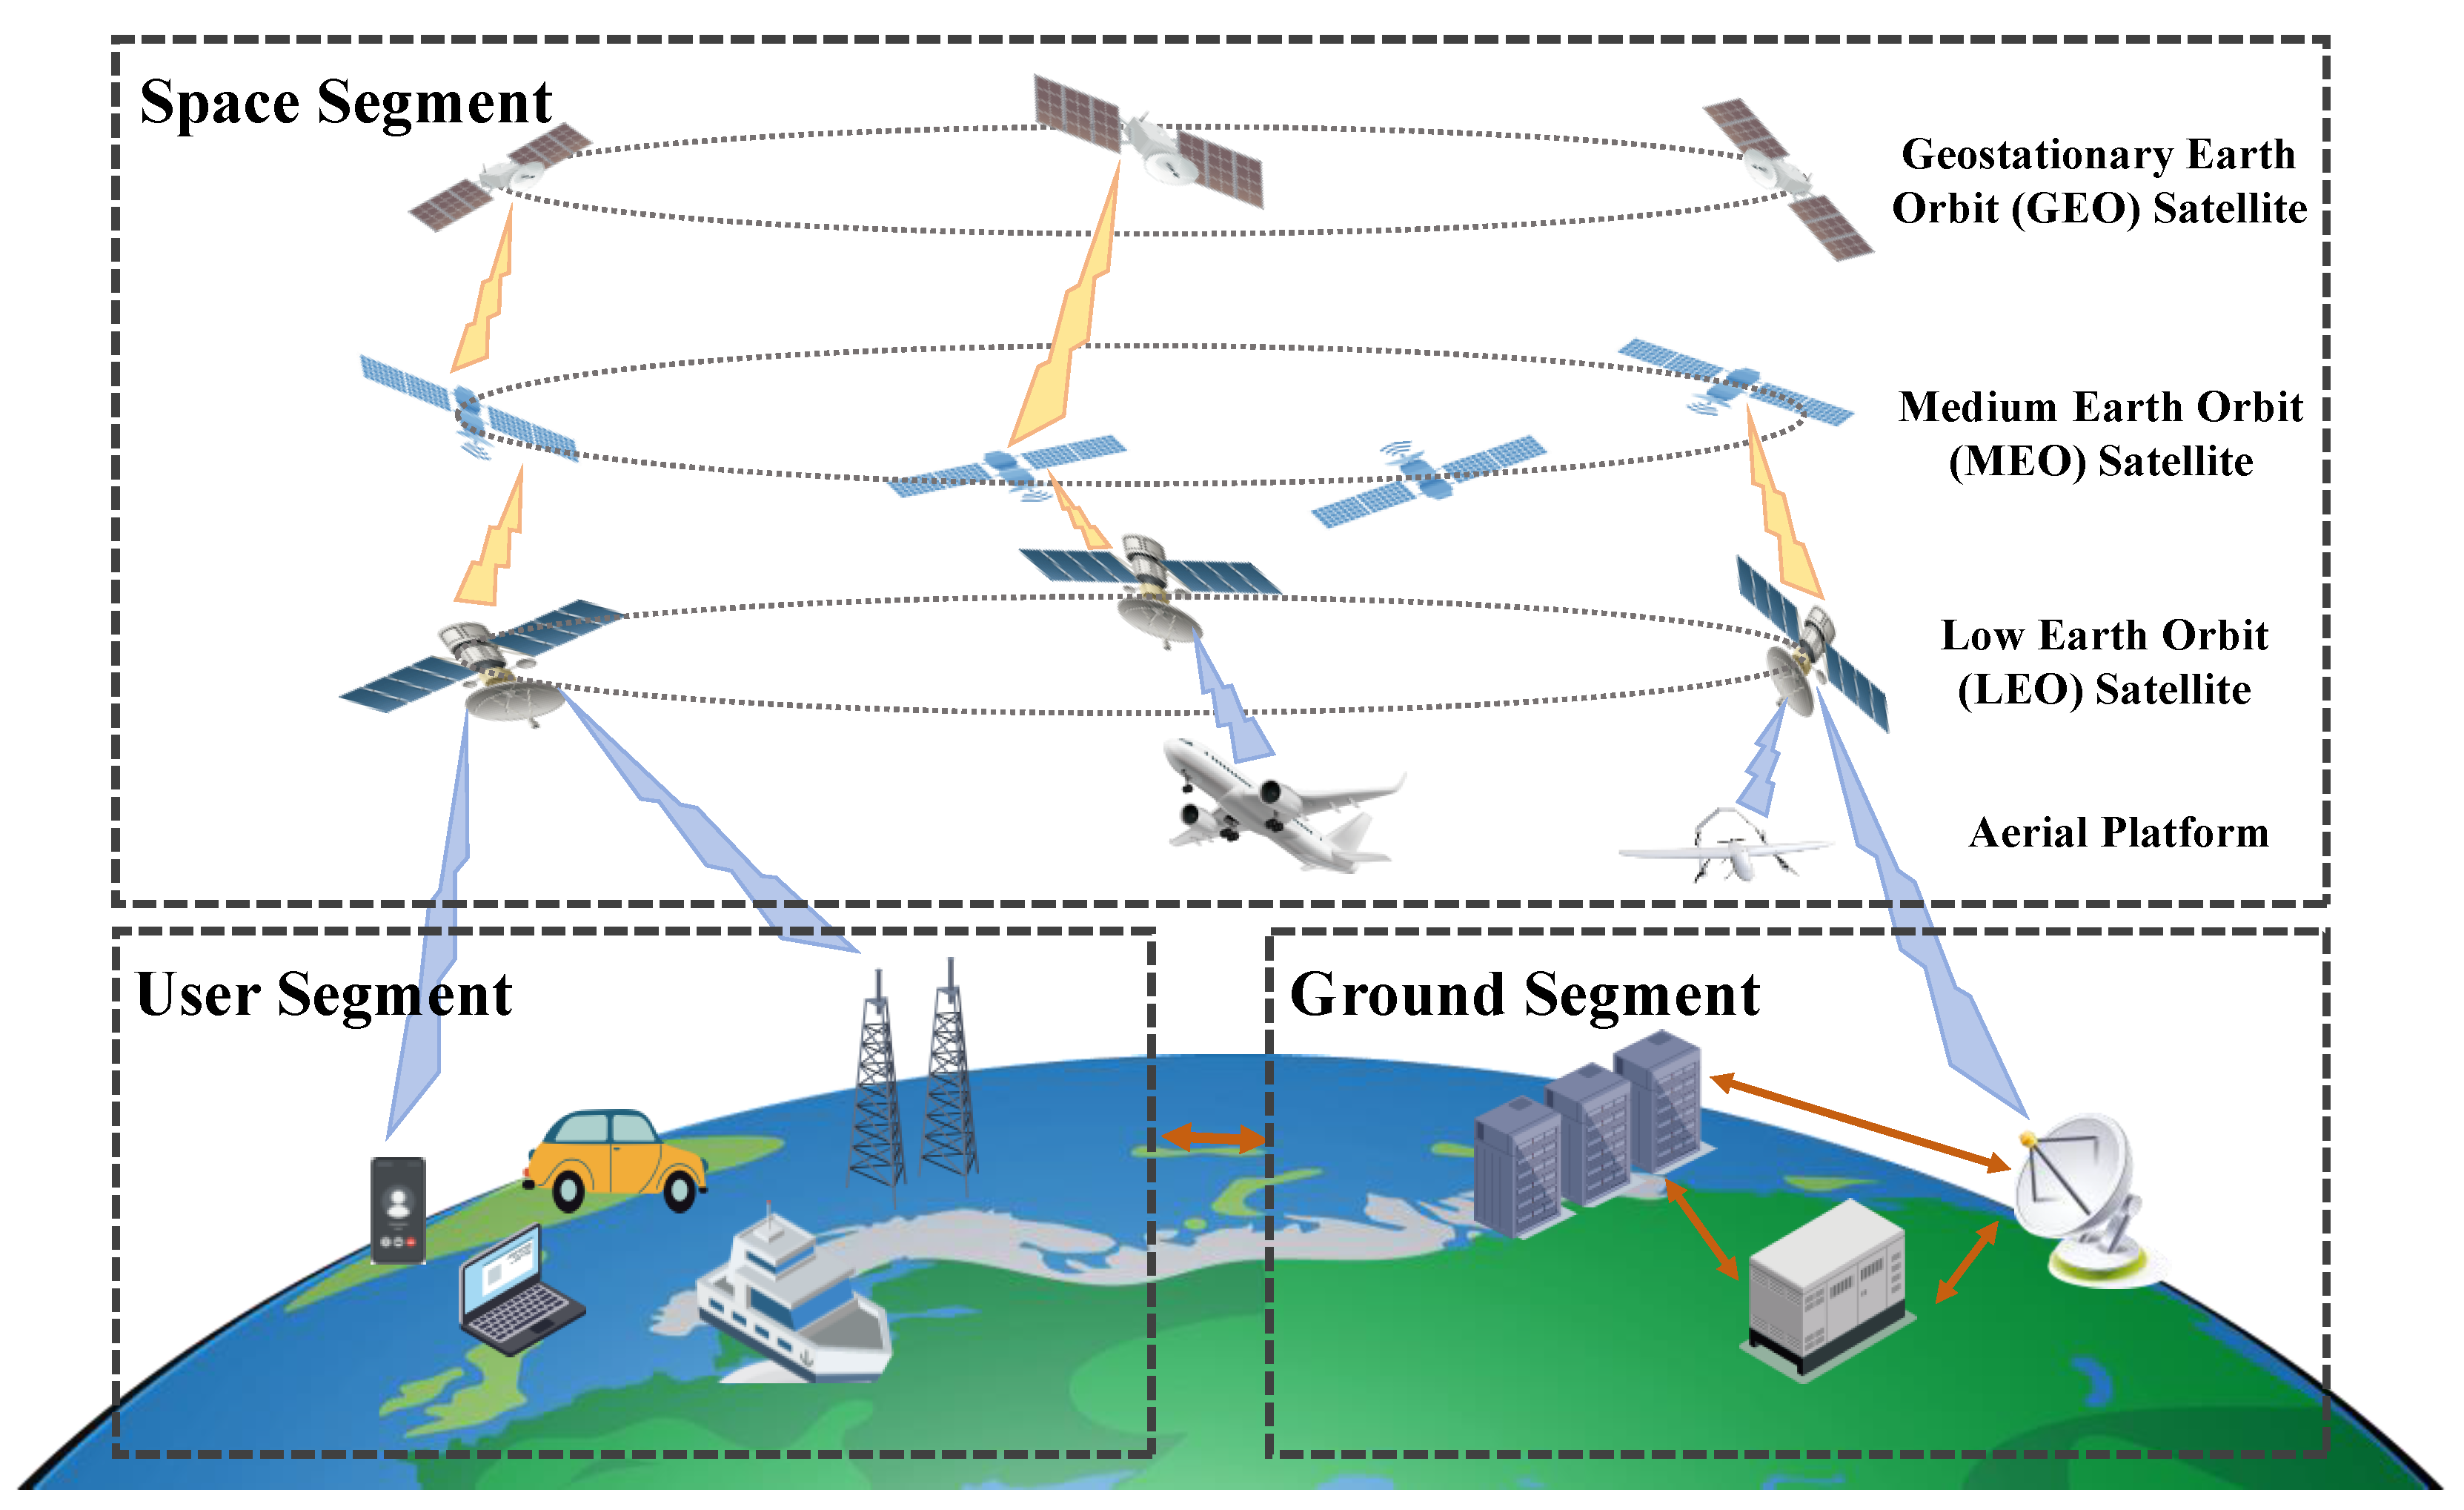
As a key component of the space–ground integrated information infrastructure, satellite networks typically comprise three core segments: the space segment, ground segment, and user segment. These segments achieve global coverage and efficient communication through coordinated signaling, with the general system architecture shown in Figure 3.
The space segment serves as the core infrastructure layer, adopting a multi-orbit hybrid networking architecture composed of GEO, MEO, and LEO satellites. It can also integrate aerial platforms such as unmanned aerial vehicles to enhance network coverage flexibility and emergency response capabilities through flexible deployment. Inter-satellite communication primarily relies on Inter-Satellite Links (ISL) for autonomous networking, forming a dynamic topology to support multi-satellite collaborative communication [19,20]. However, some systems (e.g., OneWeb) forego ISLs and instead rely on dense ground station networks to ensure connectivity [21].
The ground segment is the core management, control, and data processing hub of satellite networks, consisting of ground gateway stations, network operation control centers, and ground communication networks. Additionally, it includes data processing centers that collaborate with on-orbit satellite processing units to perform in-depth analysis of remote sensing data and generate products [22].
As the terminal access layer, the user segment includes diverse distributed terminals: fixed/mobile VSATs for broadband access, satellite phones for voice and data communication in remote areas, and portable terminals for emergency response. User terminals can establish communication links directly with satellites or indirectly access them through service providers’ ground telecommunications infrastructure, forming a space–ground collaborative hybrid access mode [23].

2.2. Research Status of Cybersecurity Threat Modeling for Satellite Networks

In the field of cybersecurity threat modeling, three common paradigms exist: the phased abstract model of the Cyber Kill Chain [24,25], Microsoft’s STRIDE threat classification model [26,27], and the MITRE ATT&CK knowledge base [28,29,30,31]. Compared to the phased abstraction limitations of the Cyber Kill Chain and the insufficient multi-dimensional coverage of STRIDE, the MITRE ATT&CK framework builds a two-layer knowledge base (techniques and tactics) based on empirical attack data. It offers significant advantages in fine-grained characterization of attack paths, panoramic coverage of adversarial behaviors, and generation of dynamic defense strategies [32], exhibiting stronger practical utility. Its characteristics are well-suited to the security analysis needs of highly complex and heterogeneous satellite networks, making it a foundational reference for many related studies.
Notwithstanding the preliminary progress in applying ATT&CK-based taxonomies to satellite networks, significant limitations persist. Table 1 compares representative studies based on their core characteristics. As shown, the SPARTA framework [28] achieves systematic description of spacecraft threats through standardized classification, but its excessive generality leads to insufficient pertinence for satellite-specific scenarios. The LEO satellite threat lifecycle model framework constructed in [29] defines space-specific tactics like “orbital maneuver interference,” but its classification system is validated based on only two attack cases, resulting in a weak empirical foundation and incomplete tactical coverage. Reference [30] proposes integrating SPARTA and ATT&CK to address data gaps, but its data extrapolation relies on manual assumptions and fails to fully consider space segment-specific threats. Reference [31] analyzes satellite ground segment attack cases using the ATT&CK for ICS framework, directly applying the industrial control framework without effectively integrating satellite-specific threat characteristics.
In summary, when existing threat modeling approaches and knowledge systems (e.g., Cyber Kill Chain, STRIDE, ATT&CK) are applied to satellite networks—a highly complex, heterogeneous scenario with unique spatial attributes—existing adaptations generally suffer from insufficient pertinence, incomplete coverage, or weak adaptability. They are unable to systematically characterize the unique attack tactics and technique chains. Therefore, there is a clear need to construct a dedicated, intuitive, and comprehensive threat knowledge matrix specifically for satellite networks.

3. Cybersecurity Threat Modeling and Analysis of Satellite Networks

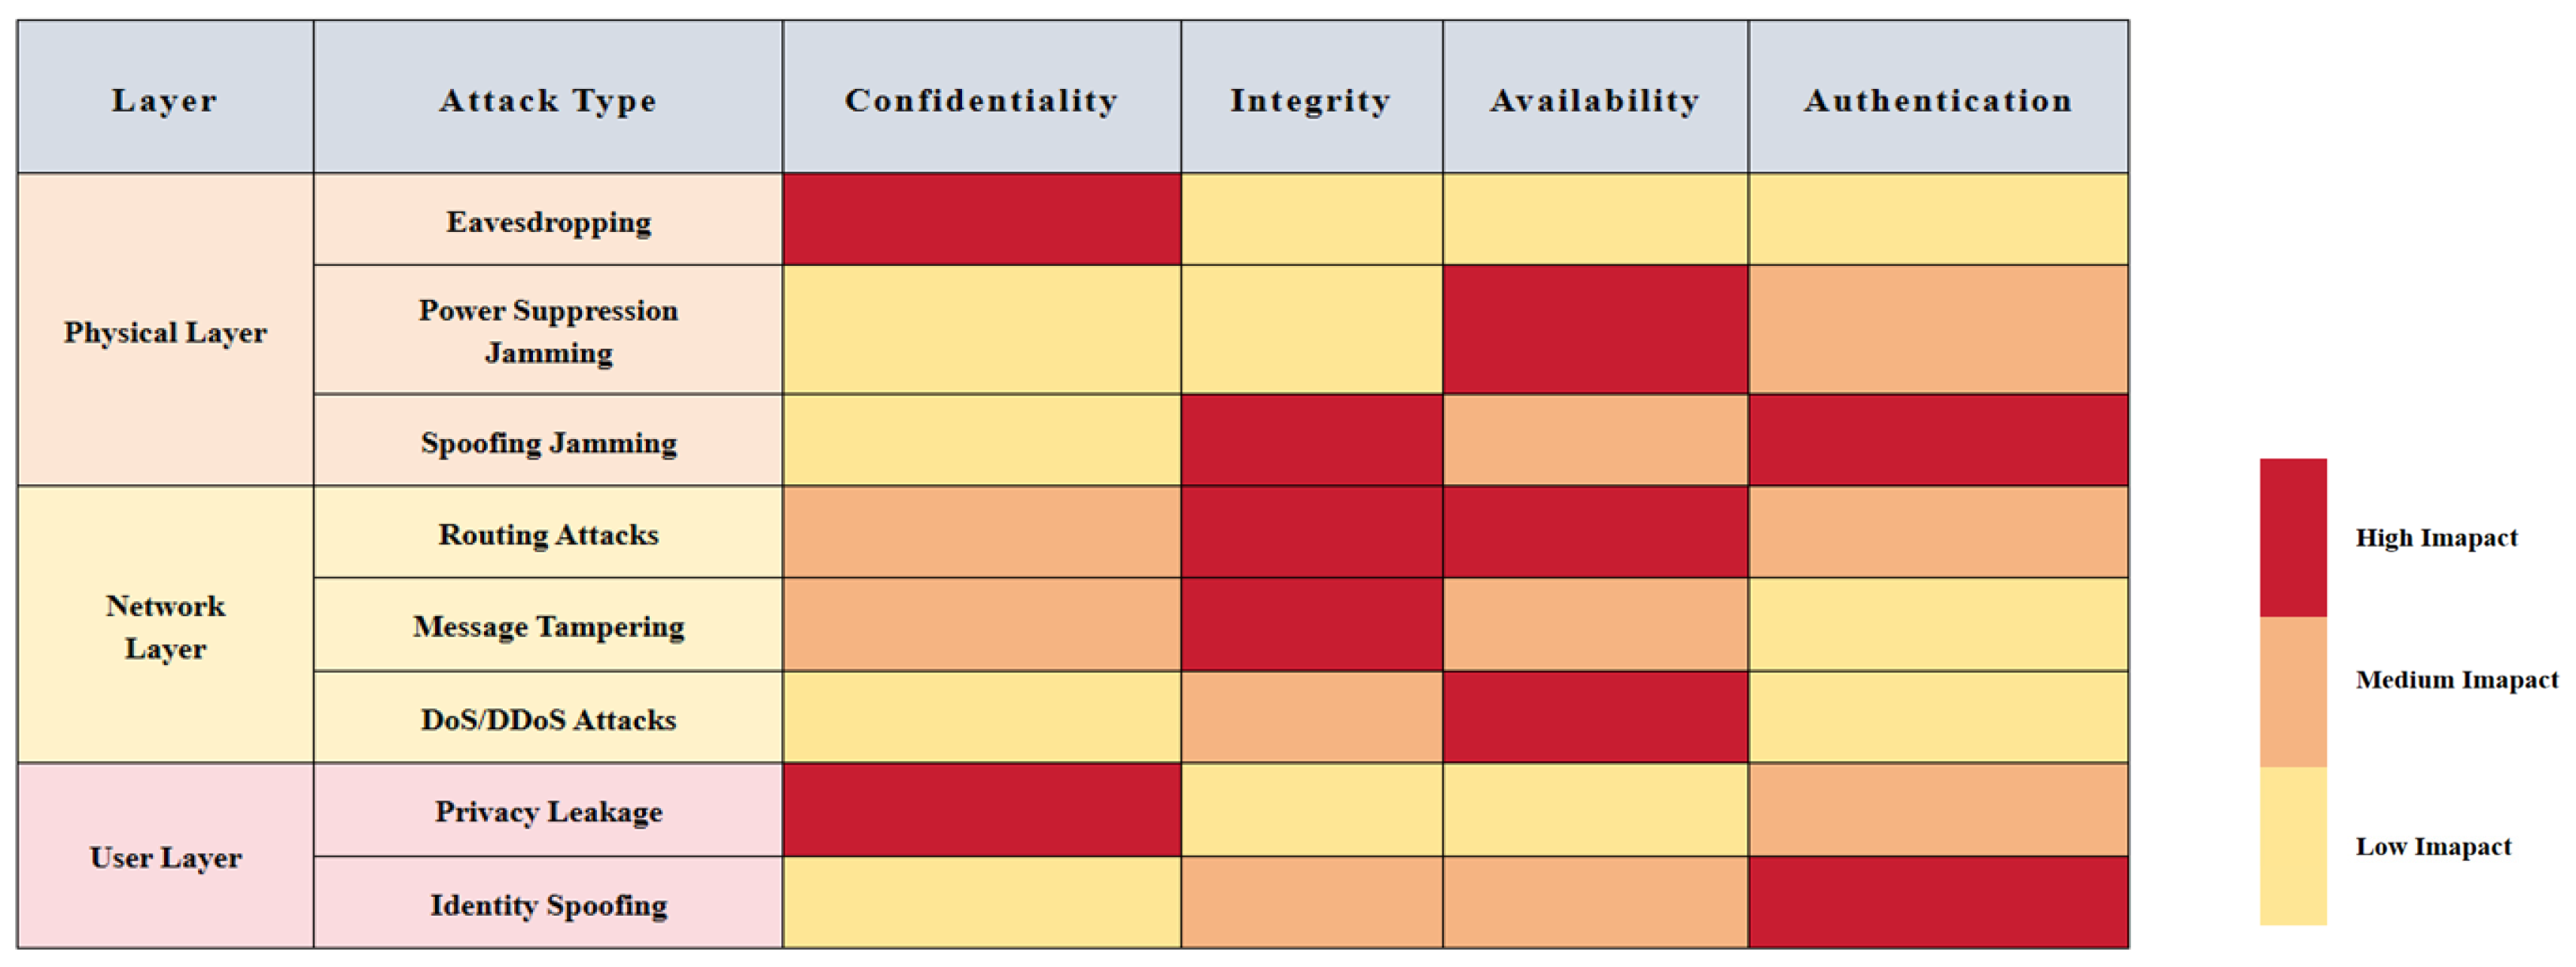
To systematically analyze cybersecurity threats in satellite networks, this paper adopts a layered approach and employs the CIA+A (Confidentiality, Integrity, Availability, Authentication) security model to systematically evaluate the impact of layered threats on these core security attributes. This helps clarify the ultimate objectives of attacks and lays the foundation for constructing an objective-oriented defense architecture in Section 4. Figure 4 presents a threat mapping matrix based on the CIA+A model, visually illustrating the degree to which physical-, network-, and user-layer threats compromise each security attribute.
The following subsections will analyze typical threats across the physical, network, and user layers. Table 2 summarizes these threats and their impacts.

3.1. Physical-Layer Threat Analysis

Threats at this layer target wireless signal transmission and hardware, directly impacting link quality and device security. Primary threats include eavesdropping, power suppression jamming, and spoofing jamming.

3.1.1. Eavesdropping

The openness of satellite communication links makes them vulnerable to illegal interception [33,34,35,36]. Attackers intercept signals transmitted over the air interface and can steal user communication content through analysis or even further extract key control parameters (e.g., encryption keys, protocol versions) to plan subsequent attacks. With the expansion of satellite user scale and coverage, such eavesdropping risks have increased exponentially [37]. Reference [13] identifies communication security as a core objective of satellite systems, constructs a refined channel model combining satellite beam patterns and path loss, and proposes an anti-eavesdropping scheme from a physical-layer security design perspective, effectively reducing the parsing probability of intercepted signals.
Furthermore, hardware defects can also lead to physical-layer information leakage. Amid the large-scale deployment of high-, medium-, and low-orbit satellites, some manufacturers widely adopt Commercial Off-The-Shelf (COTS) components to reduce costs and accelerate mass production. Hardware vulnerabilities in these components may become potential vectors for eavesdropping [16]. For example, ref. [38] investigates the RISC-V processor commonly used in satellites, revealing paths for hardware Trojans and microarchitectural side-channel attacks to steal sensitive data, thereby endangering the entire system’s safe operation.

3.1.2. Power Suppression Jamming

Power suppression jamming involves attackers transmitting high-power signals to mask legitimate ones, disrupting the demodulation of effective signals at the receiving end and ultimately causing satellite communication interruption [39]. These attacks are characterized by low implementation complexity, high effectiveness, and the capability for synchronous suppression of multiple targets, consequently establishing them as a mainstream threat to satellite networks [40,41]. Zou et al. [42] classify jamming by “generation difficulty” and compare the advantages and disadvantages of different jamming schemes based on dimensions such as energy efficiency, damage degree, implementation complexity, and prior knowledge requirements. Reference [16] systematically categorizes the characteristics of three types of suppression jamming sources (space-based, air-based, ground-based) and conducts a comparative analysis in terms of coverage range, jamming power, duration, mobility, and resource requirements.
Given the inherent limitations of traditional high-power single-source jamming modes—such as low power efficiency, crude coverage patterns, and susceptibility to detection—current research frontiers are shifting toward technological innovations aimed at enhancing jamming effectiveness [43,44,45]. Study [44] focuses on the intelligent design of jamming signal waveforms, introducing novel signals such as nonlinear frequency modulation to improve jamming flexibility and controllability while maintaining effective suppression. Literature [45] is dedicated to the precise allocation of jamming power and fine-grained control of spatial coverage. By optimizing modulation parameters, it ensures effective suppression of specific regions while reducing transmitted power, thereby significantly improving jamming efficiency and stealth. These technological advances have propelled the advancement of barrage jamming toward low power consumption, high precision, and intelligent paradigms, further intensifying the threats to satellite system network communication security.

3.1.3. Spoofing Jamming

Spoofing jamming is an attack wherein an adversary forges a signal that closely mimics the characteristics of a legitimate signal. This induces the receiver to misinterpret it as an authentic signal from a satellite source, leading to deviations in time synchronization, frequency alignment, beam pointing, or orbital parameter calculations for ground terminals, satellite transponders, or tracking, telemetry, and command (TT&C) stations [46,47]. Unlike power suppression jamming, which relies on overpowering the legitimate signal with stronger coverage, spoofing jamming operates through the precise forgery of legitimate signal characteristics and control parameters. It typically targets a single user, offering greater stealth and posing more severe potential hazards. Its successful implementation necessitates that the attacker possess prior knowledge of the signal waveform, frame structure, and the underlying processing logic.
Based on the method of implementation, spoofing jamming can be further categorized into two primary types: generative spoofing and repeater (or relay) spoofing. Generative spoofing involves creating a signal with a structure highly similar to the authentic one but containing fabricated content, aiming to mislead the receiver. Research in this domain focuses on enhancing the fidelity and generation efficiency of the forged signal. For instance, targeting spaceborne synthetic aperture radar (SAR) imaging systems, studies have proposed fast algorithms based on spatial frequency-domain interpolation to generate complex scenes containing numerous false targets [48]. Similarly, other work has employed recursive algorithms to significantly reduce the computational complexity of generating the spoofing signal, thereby improving real-time performance [49]. Furthermore, to generate high-quality deceptive signals that precisely match specific SAR imaging processing algorithms (such as the Omega-K algorithm), researchers have proposed deeply customized methods like the corresponding “Inverse Omega-K Algorithm.” This represents a trend in generative spoofing toward precision and algorithmic countermeasures [50]. Repeater spoofing, on the other hand, involves intercepting a genuine signal, delaying or processing it, and then retransmitting it, causing confusion in the receiver regarding time, frequency, or spatial parameters.
Although the methods differ, both types share the core objective of misleading the receiving system, posing a severe threat to the TT&C, navigation, and communication links within satellite system networks. The threat monitoring and receiver standardization testing project for the Global Navigation Satellite System (GNSS), supported by the European Union, revealed that approximately 10% of over 300,000 recorded anomaly events were confirmed as deliberate interference attacks [51]. Additionally, during the outbreak of the Russia–Ukraine conflict in February 2022, the widespread broadcast of forged GPS signals along the border by Russian forces interfered with Ukrainian military aircraft takeoffs/landings and air defense missile launches, further corroborating the destructive potential of such threats in real-world combat scenarios.

3.2. Network-Layer Threat Analysis

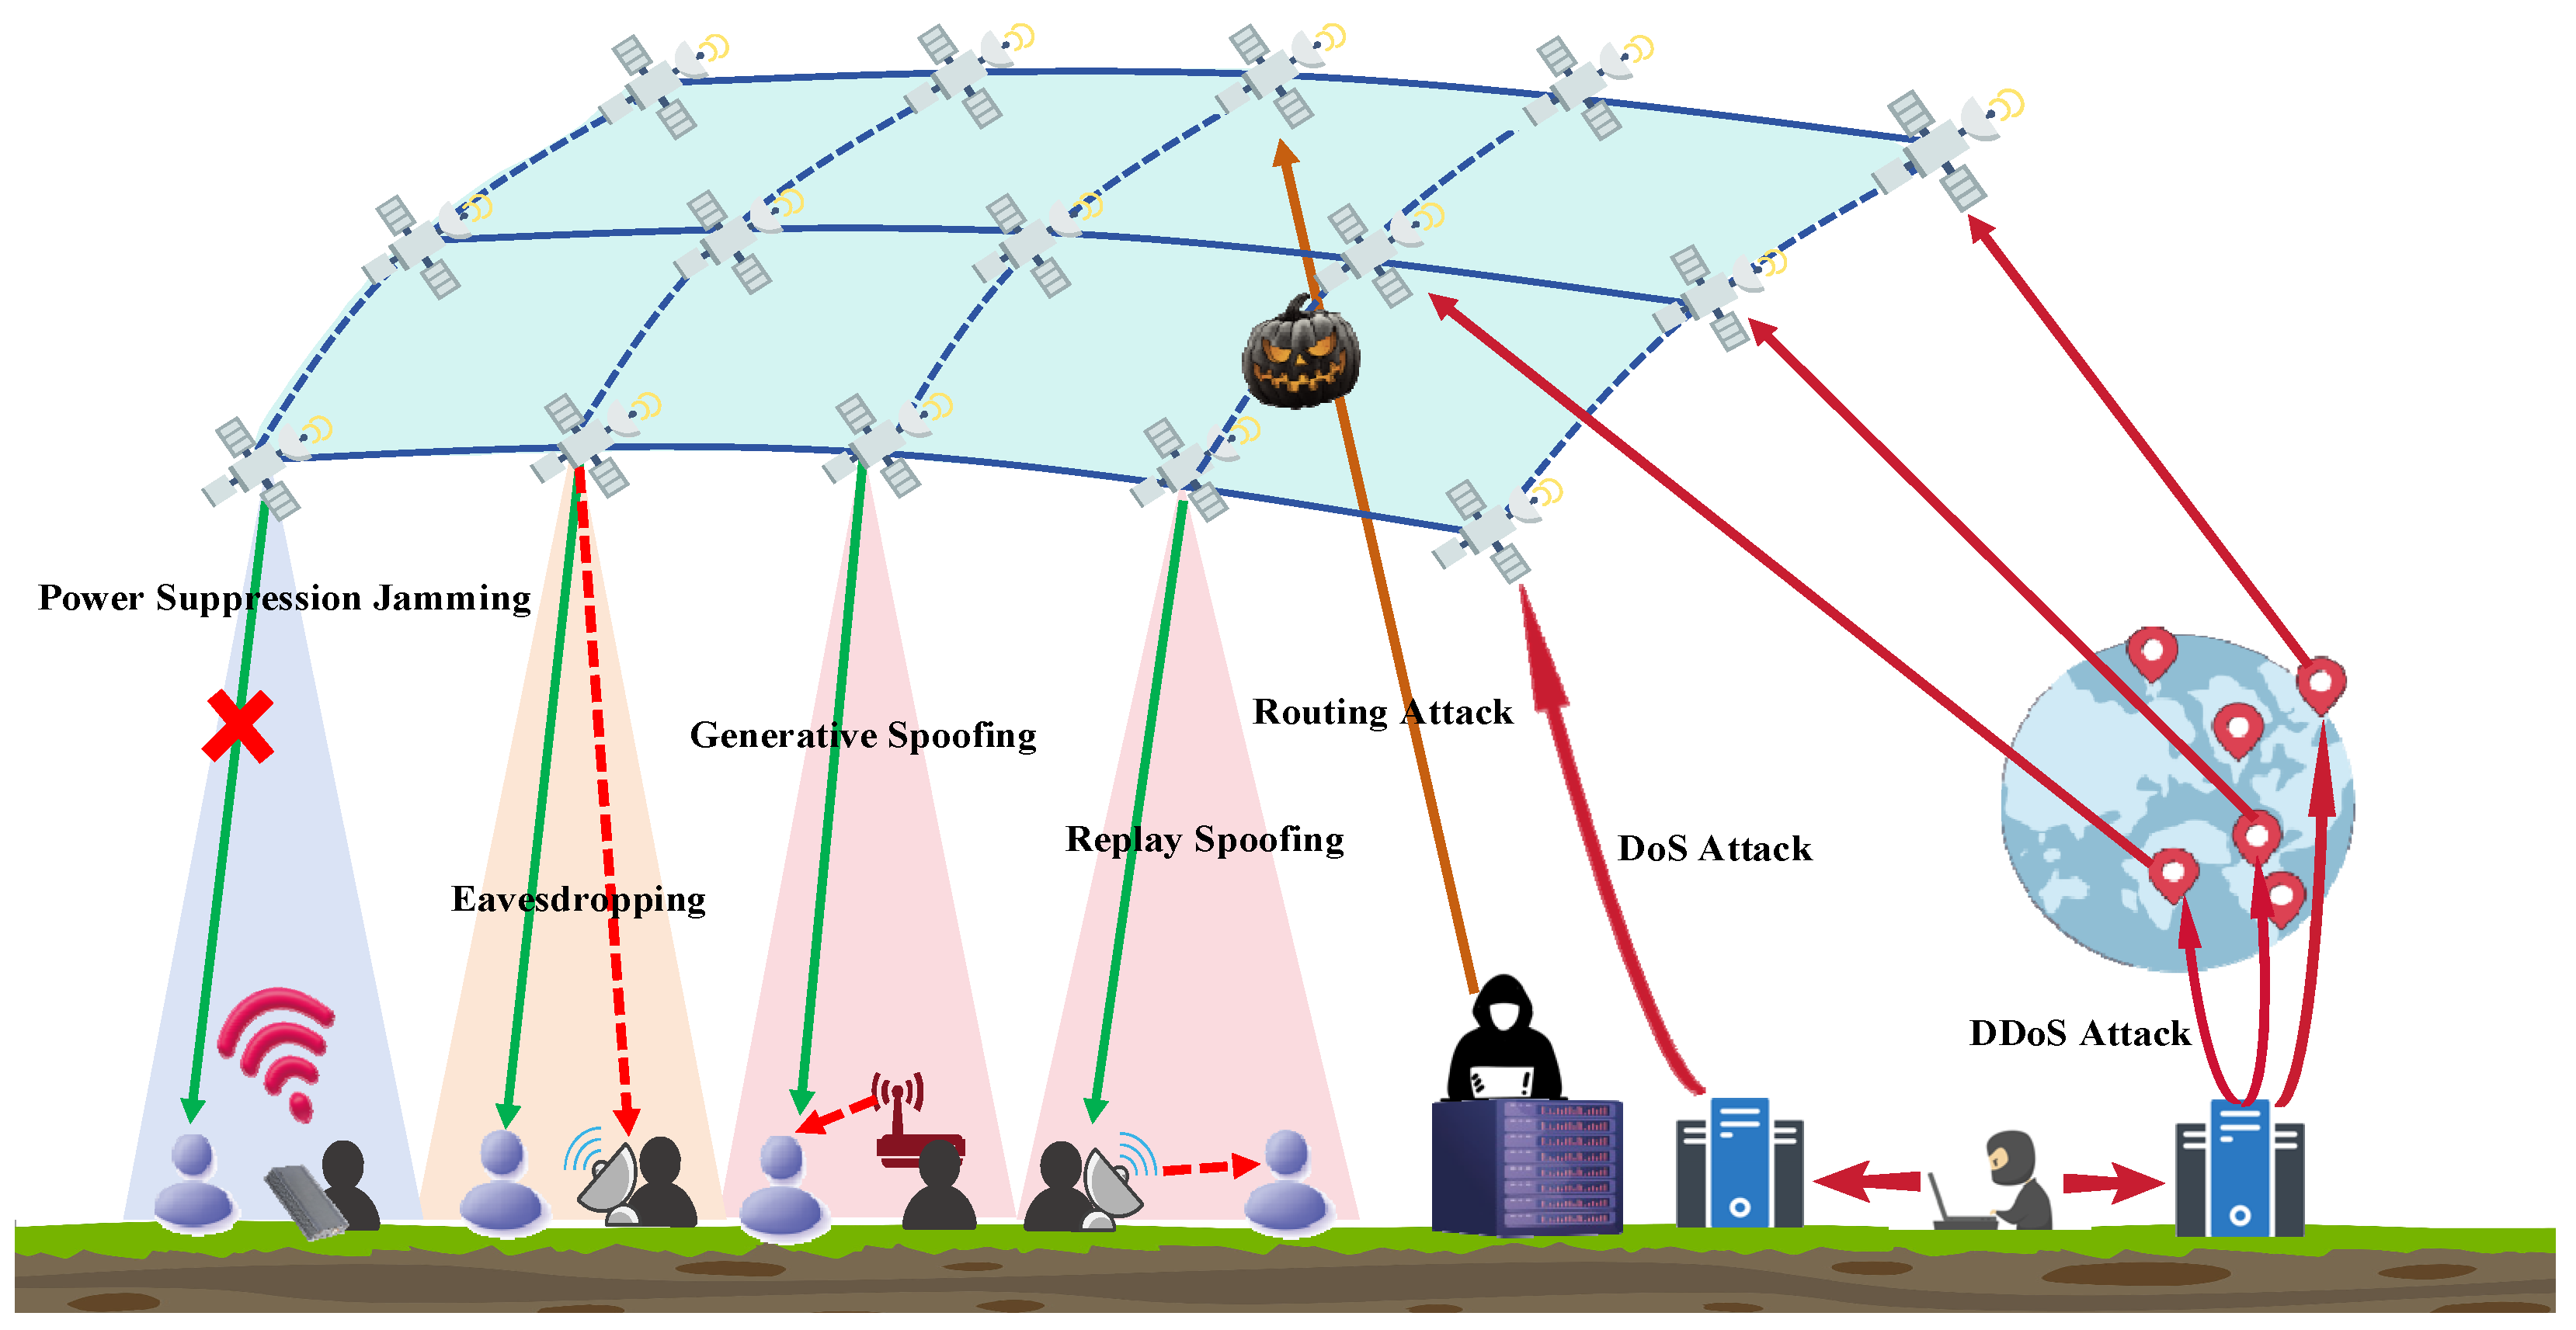
In the dynamically changing satellite topology, the network layer relies on routing protocols and various signaling mechanisms to determine optimal inter-satellite transmission paths for data packets, ensuring reliable end-to-end transmission. However, current satellite networks generally lack source authentication for routing information, signaling verification parameters and path legitimacy verification. Attackers can forge or tamper with inter-satellite/space–ground routing updates or forge data packets, thereby hijacking traffic and exhausting on-board bandwidth to launch network-layer attacks. To intuitively display typical threat types and action mechanisms at the physical and network layers, the relevant schematic is shown in Figure 5.

3.2.1. Routing Attacks

The special operating environment of satellite networks exacerbates routing security risks. On the one hand, the high-speed movement of satellites leads to frequent topology changes. Coupled with limited on-board resources and uneven global traffic distribution, nodes and links are prone to congestion [52]. On the other hand, the openness and exposure of ISLs make them vulnerable to interception during the routing forwarding process [53]. These factors enable a large volume of routing signaling generated by link switching to be intercepted, tampered with, or replayed by malicious nodes [54,55], potentially disrupting routing stability at best or causing full-network communication paralysis at worst.
Routing attacks faced by satellite networks can be broadly divided into internal and external attacks [56]. In internal attacks, attackers first gain control of legitimate satellite nodes, tamper with the routing processing logic within the nodes, and cause them to perform malicious operations during path calculation and data forwarding. External attackers are unauthorized network elements that implement interference, spoofing, or blocking at any stage of routing discovery, path maintenance, or data forwarding through various means, thereby damaging the normal data transmission function of satellite networks [57]. Both types of attacks focus on manipulating routing instructions and node authentication information, directly threatening the connectivity of satellite networks.

3.2.2. Message Tampering

Message tampering refers to the attack behavior where attackers intercept the transmitted message during satellite communication and unauthorizedly modify, insert, or delete its content. Since the ground segment typically centrally stores data and exposes management interfaces [29,58,59], it has become a high-incidence scenario for such attacks. After illegally obtaining control permissions, attackers maliciously alter messages, leading to routing decision errors, invalid control instructions, or abnormal service configurations in subsequent transmissions of the tampered information. In the 2022 KA-SAT network paralysis incident, attackers exploited an unauthorized configuration interface (CVE-2022-23305) at the ground gateway station of Viasat’s satellite broadband system to broadcast malicious firmware update packages to tens of thousands of user terminals, tampering with terminal routing tables and erasing flash memory data, ultimately resulting in the tampering of control instructions for some wind power facilities [60].

3.2.3. Denial-of-Service Attacks

Denial-of-Service (DoS) attacks involve sending a large volume of illegal data packets or requests to the target, exhausting device or network resources and preventing service provision to legitimate users [61]. DoS attacks on satellite networks can target the ground segment and space segment. Although they share the same origin as traditional network attacks, they exhibit unique characteristics due to the high-speed movement of constellations. Distributed Denial-of-Service (DDoS) attacks leverage the distributed architecture of satellites, organizing multiple controlled devices to launch synchronous attacks, further expanding the scope of harm. With the deployment of LEO mega-constellations, a large number of LEO satellites have become new targets for DDoS attacks [62].
Research related to DoS attacks on satellite networks has shown significant growth in recent years. In 2020, James et al. tampered with the VSAT ship–shore link using modified TV equipment costing less than $400, launching the first real-environment DoS attack on maritime satellites and exposing the security vulnerability of unencrypted links [63]. Giuliari et al. [64] launched Link Flooding Attacks (LFA) on an LEO satellite simulation platform based on public satellite orbit and connection information. Reference [65] assumed a scenario where some ground stations are compromised and used controlled nodes to launch ICMP echo flood DDoS attacks. Reference [66] discussed DDoS reflection amplification attacks that exhaust space–ground link bandwidth by colluding with terminals connected to the space backbone network. Reference [29] organized the tactics and techniques chain of ICARUS attacks (a special form of DDoS) using the ATT&CK matrix. When launching DDoS attacks, attackers often initiate instant attacks and then switch source addresses and utilize IoT devices worldwide as botnets [67], making real-time location difficult for traditional detection and tracing mechanisms and significantly increasing defense complexity [64,68].

3.3. User-Layer Threat Analysis

As the core hub for user-oriented business services, the user layer directly handles sensitive data processing and service delivery. User-layer threats targeting upper-layer business logic, software systems, and user privacy data (including sensitive user information and authentication parameters) directly undermine the trustworthiness of satellite services and data sovereignty. Although the public disclosure frequency of user-layer attacks is lower than threats at other layers, factors such as their concealment, cross-domain impact, and on-board patch lag result in higher repair costs and potential harm. Typical user-layer threats primarily focus on privacy leakage and identity spoofing.

3.3.1. Privacy Leakage

Currently, satellite networks face severe security challenges in large-scale data forwarding. Especially for LEO satellite networks that rely on numerous ground gateways [69,70] or ISLs for global data exchange [71], achieving low-latency seamless handover requires frequent sharing of privacy data, such as user device locations, between satellites and gateways [72]. Each data forwarding potentially risks leaking sensitive user information. Once captured and abused by attackers, it can cause immeasurable damage to user privacy [73]. Reference [74] points out that attackers can reverse infer a user’s real-time location and behavioral patterns by continuously monitoring the offloading decisions of mobile devices. Furthermore, the high-speed movement of satellites and frequent link interruption/reconnection make it difficult for traditional encryption and authentication mechanisms to take effect promptly, further expanding the privacy leakage window and exposing user privacy to persistent security threats.

3.3.2. Identity Spoofing

The legitimacy and uniqueness of user identities (relying on authentication parameters) are core prerequisites for the orderly operation of satellite network services [75]. Identity spoofing attacks bypass access control by forging the credentials of legitimate nodes (such as digital certificates and access credentials), directly threatening the authenticity of satellite services. Satellite systems, built on inter-satellite and space–ground links, constitute highly open wireless systems. They not only face technical challenges like high latency and dynamic topology changes but also have satellite nodes completely exposed in outer space, leading to frequent risks such as link hijacking and identity impersonation, making it difficult to guarantee node identity credibility [76,77,78,79]. When attackers exploit these vulnerabilities to impersonate satellites, ground stations, or even user terminals by replaying legitimate credentials, forging digital certificates, or exploiting protocol vulnerabilities, they can easily breach access control and directly endanger the authenticity and continuity of satellite services.

3.4. Sat-ATT&CK Threat Matrix Modeling

Although the layered threat analysis proposed in previous sections can systematically deconstruct satellite network threats, actual attacks often span multiple layers to form coordinated attack chains. Traditional single-dimensional threat analysis methods struggle to fully characterize their complex correlations. Satellite networks exhibit typical Cyber–Physical System (CPS) characteristics, where physical processes are closely coupled with network control. They share high consistency with Industrial Control Systems (ICS) in terms of real-time performance, reliability, heterogeneity, and security sensitivity. Therefore, this paper adopts the MITRE ATT&CK for ICS matrix as a foundational reference to construct a dedicated threat knowledge matrix for satellite networks—Sat-ATT&CK.
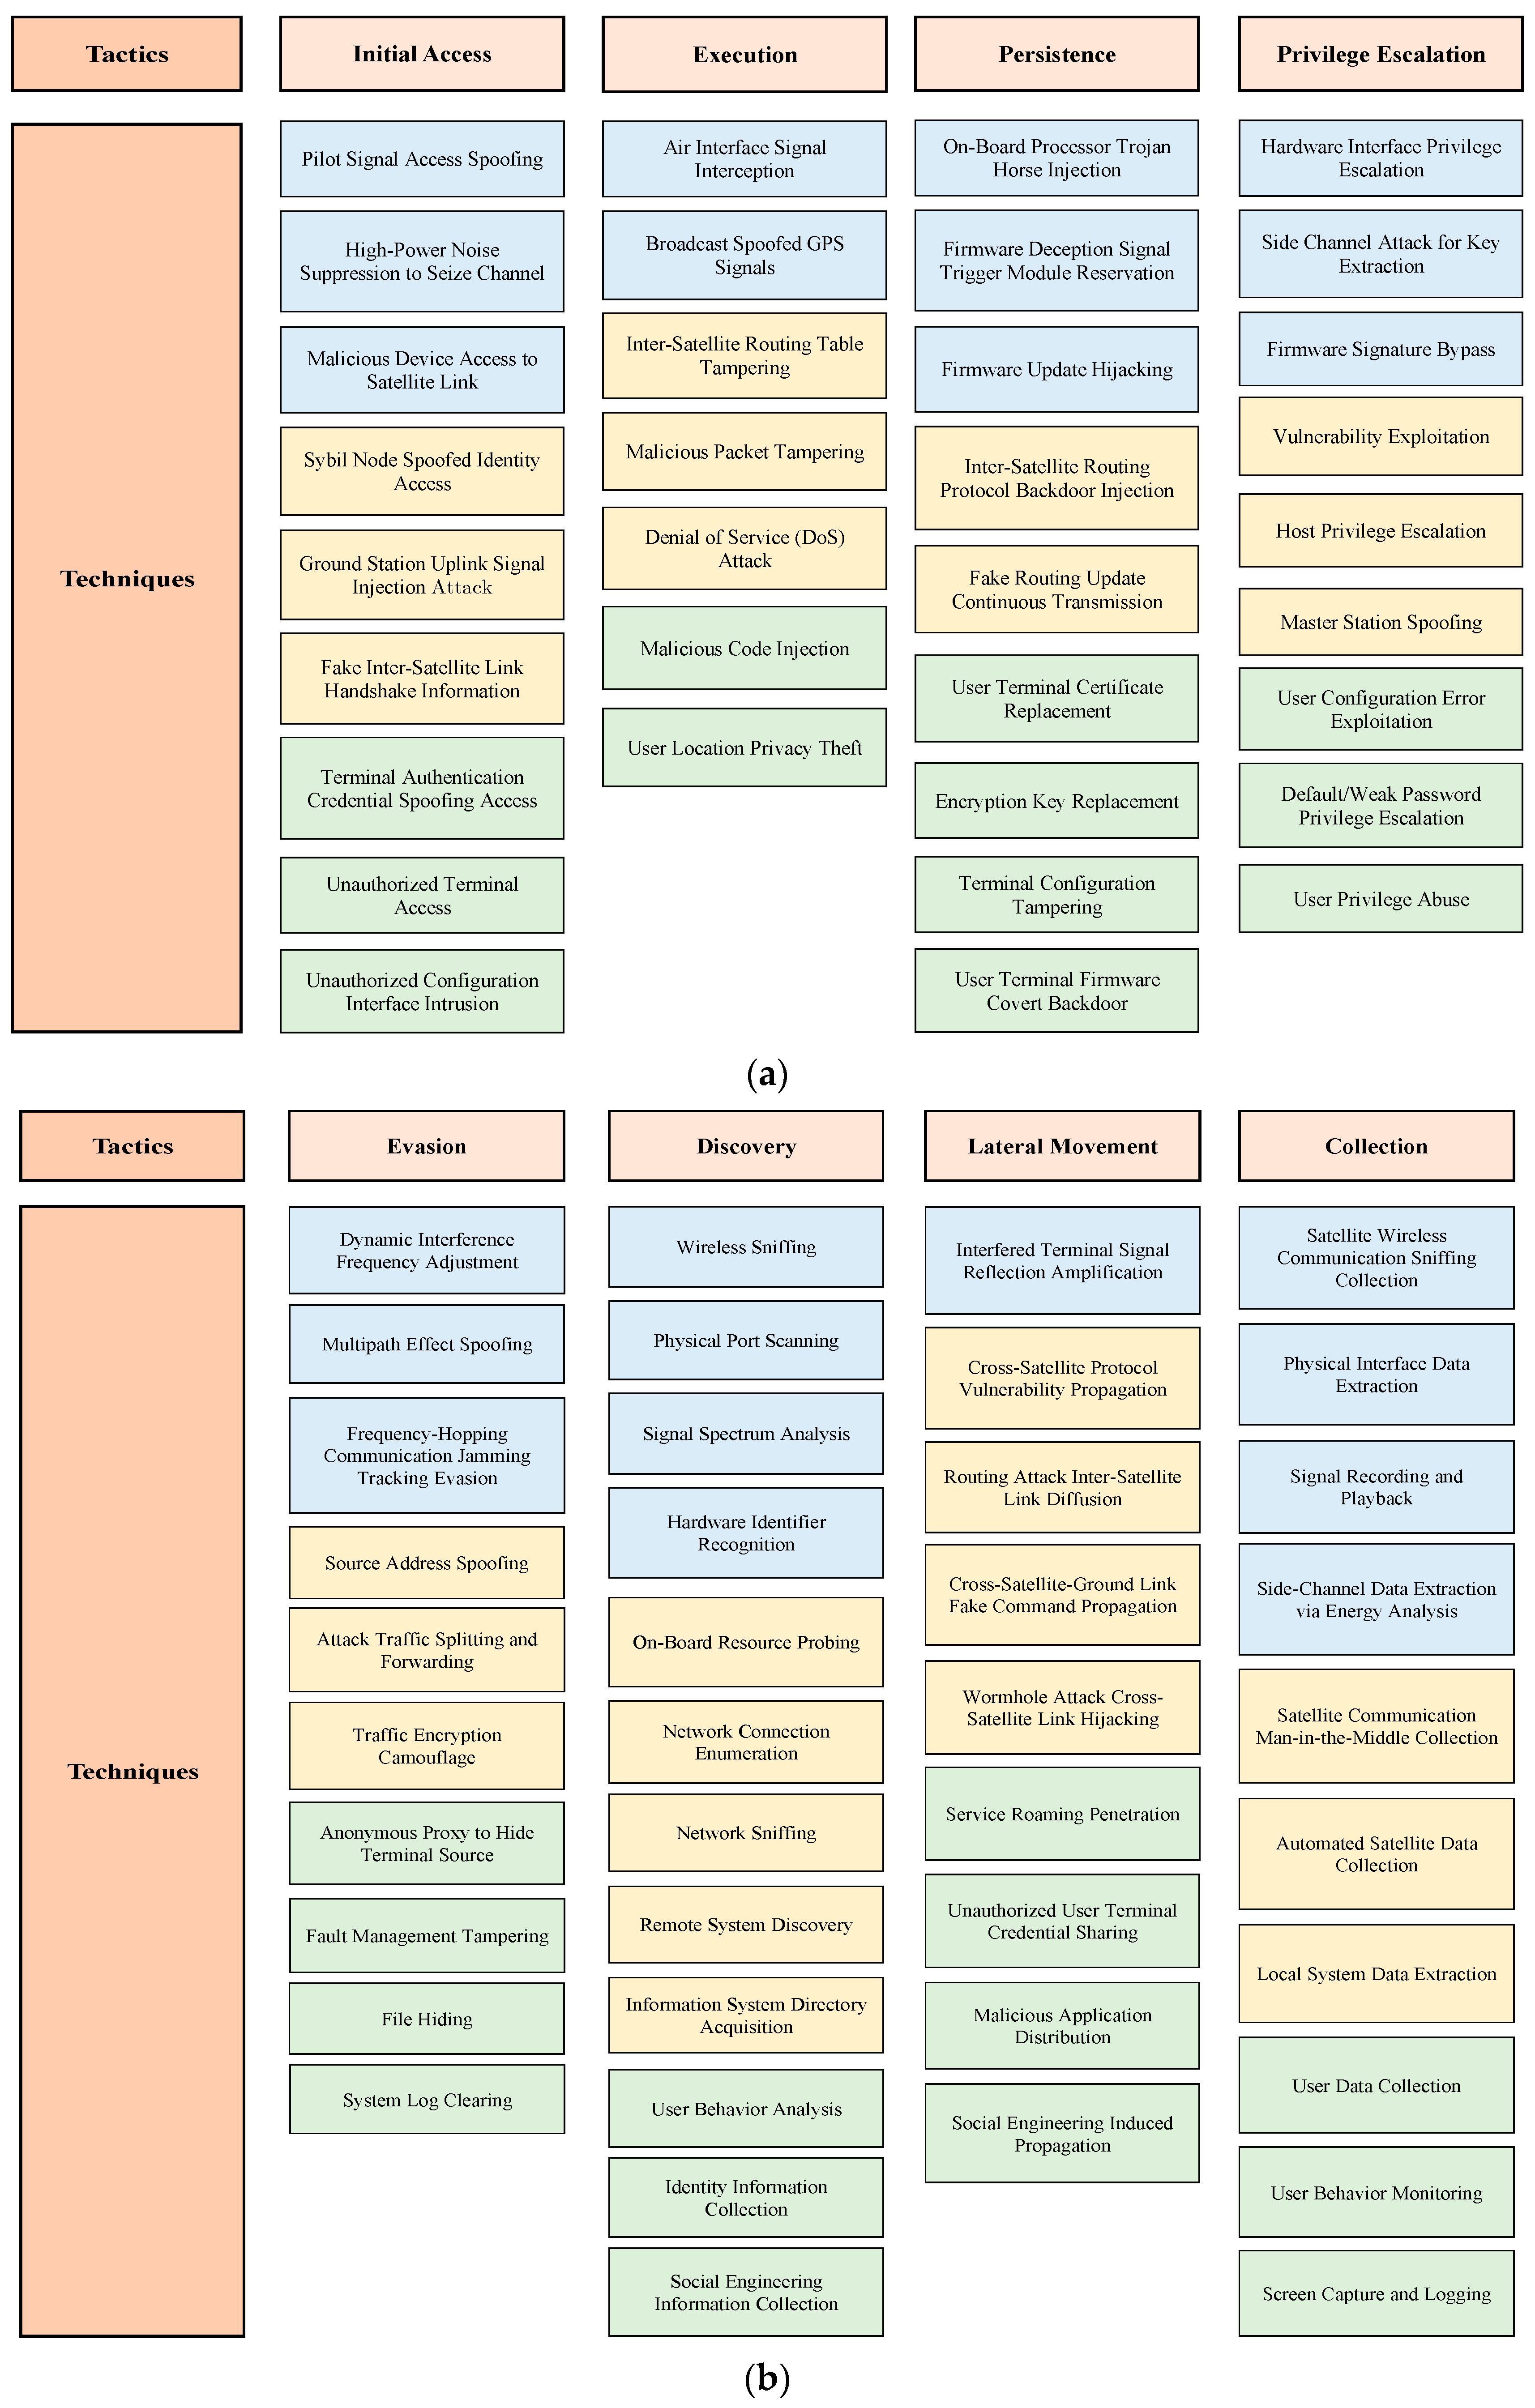
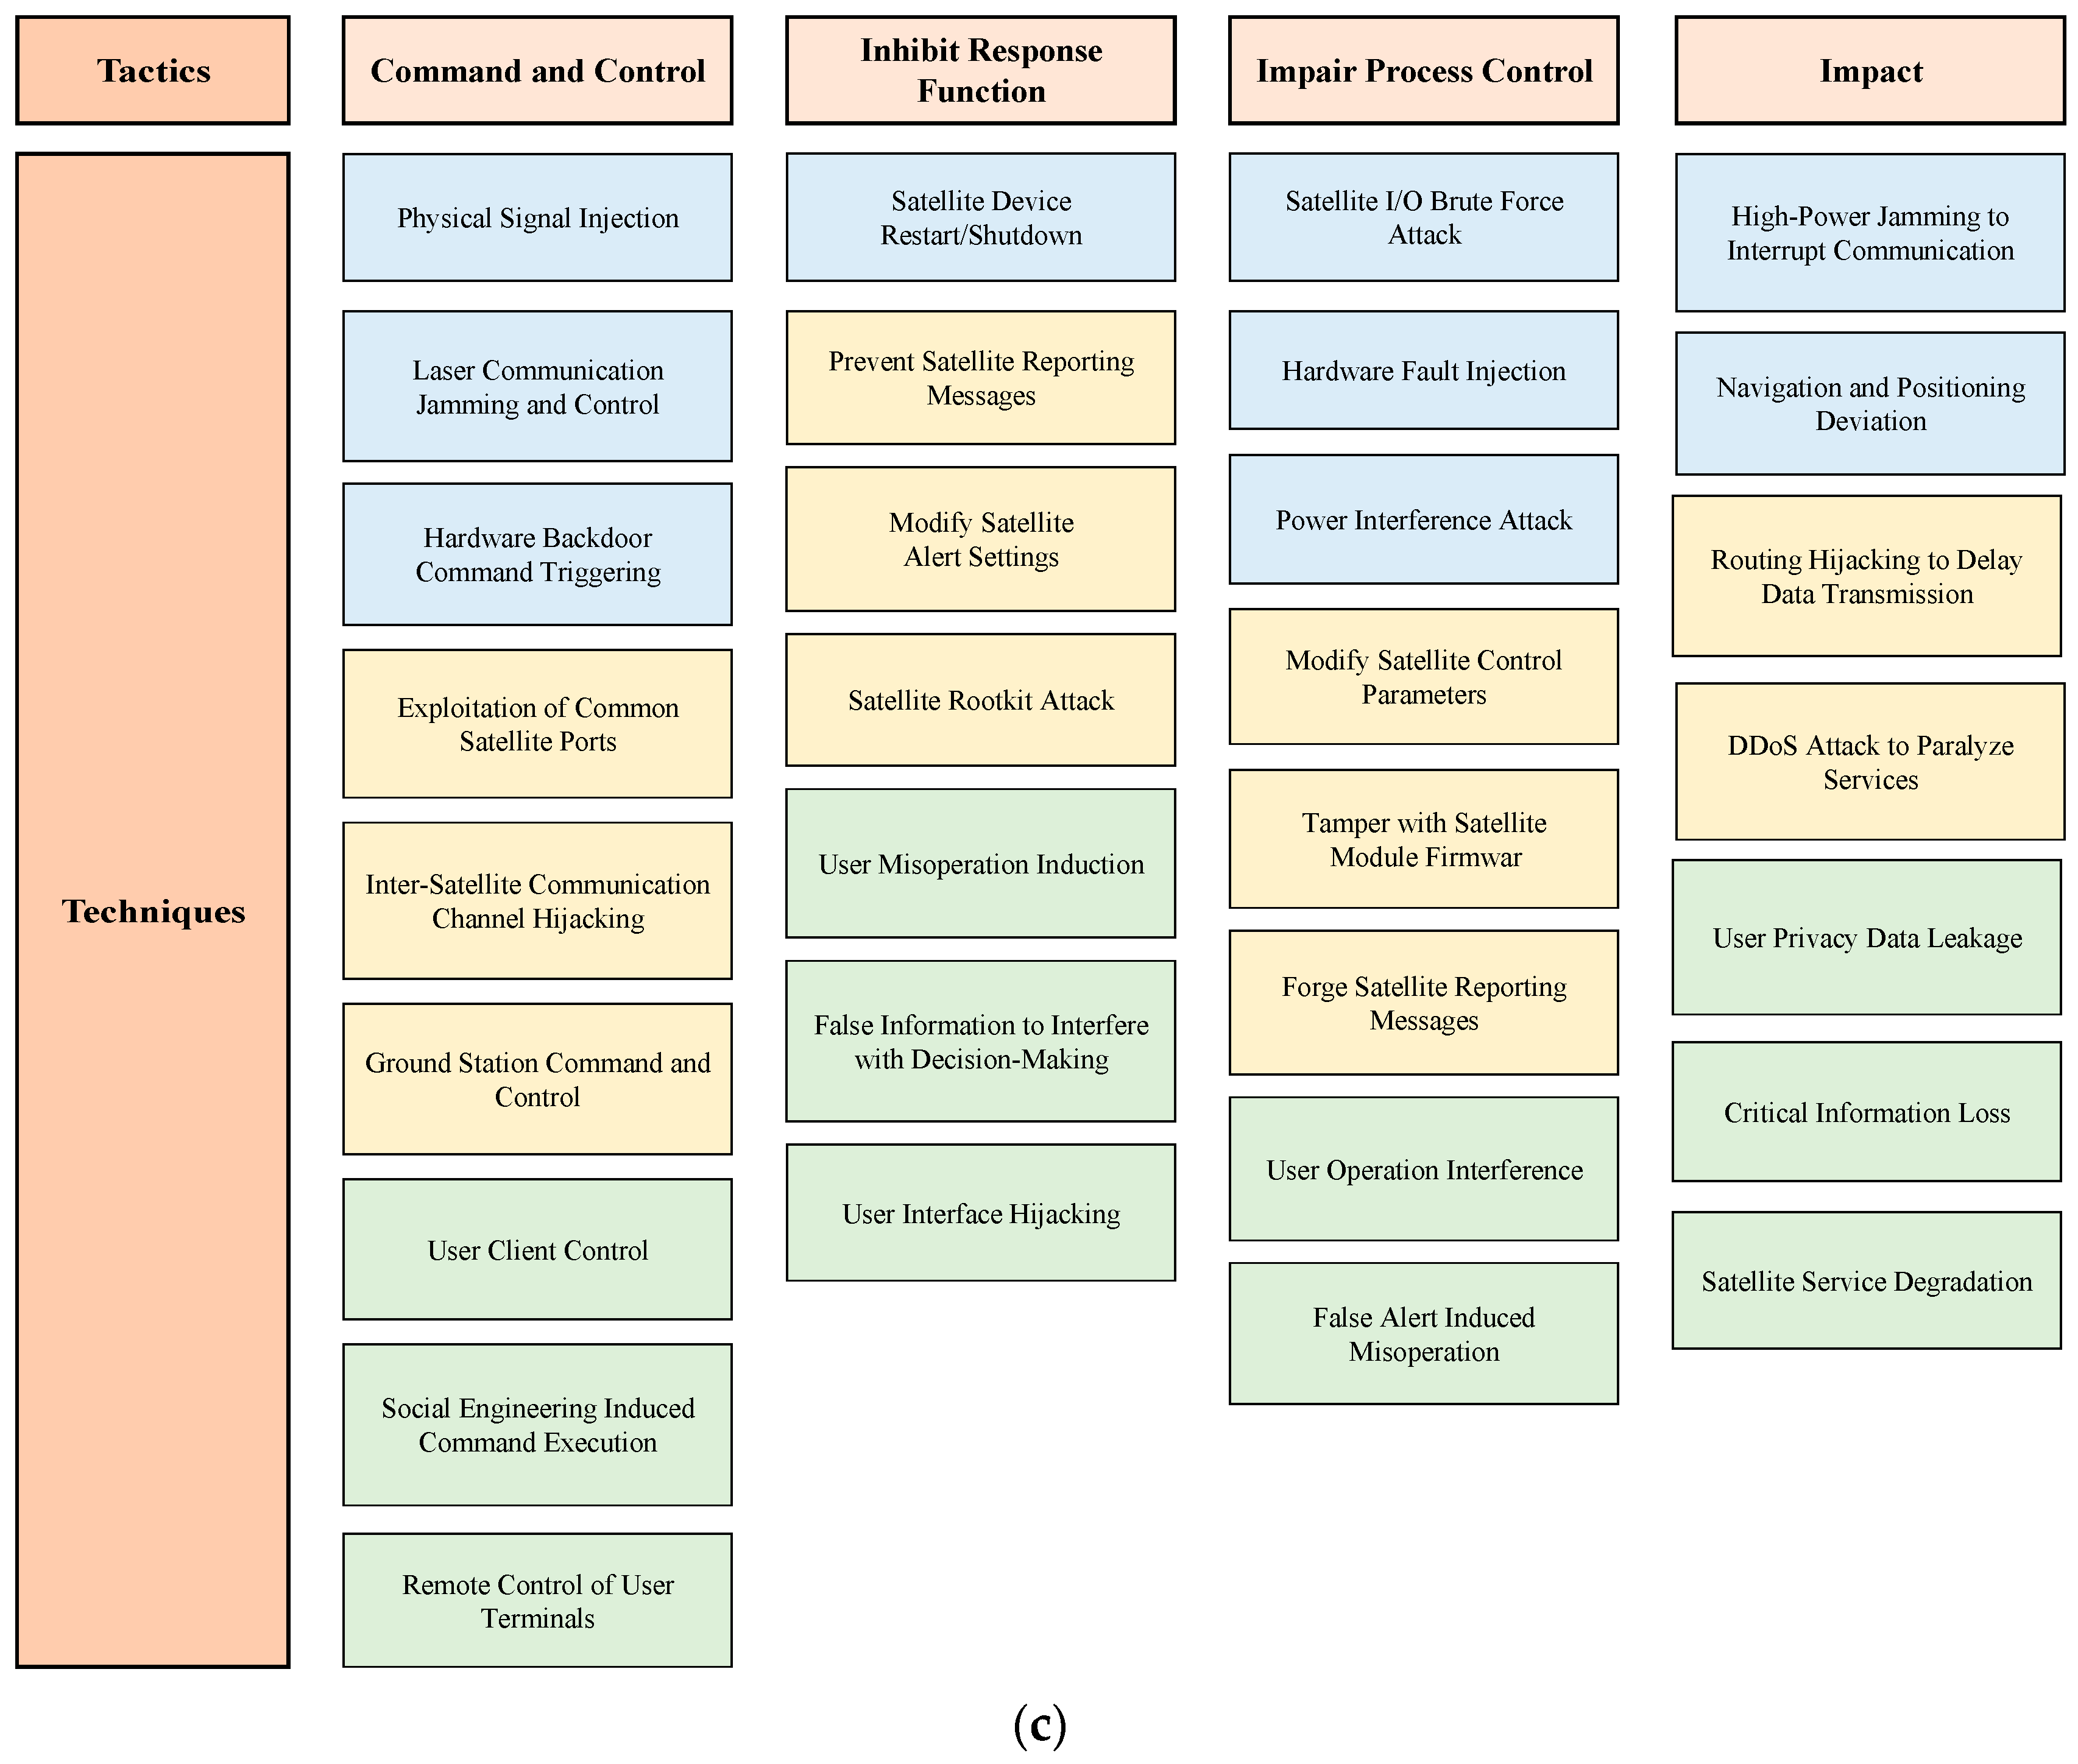
This matrix extends and adapts the ICS-based taxonomy by integrating unique attributes of satellite networks, such as open channels, dynamic topology, and space–ground collaboration. Sat-ATT&CK covers 12 core tactics and over 100 attack techniques, enabling systematic classification and standardized description of cross-layer threats in satellite networks. It serves as a structured knowledge base for characterizing multi-stage attack chains and supports subsequent attack detection, defense strategy design, and response mechanisms. The distribution of specific tactics and techniques in the Sat-ATT&CK matrix is shown in Figure 6a–c.
Sat-ATT&CK is designed as a threat knowledge matrix rather than a fully fledged modeling framework with automated decision-support mechanisms. Its primary purpose is to provide a standardized taxonomy for satellite-specific attack behaviors, facilitating consistent threat description and cross-incident analysis. In practice, Sat-ATT&CK can be used to map real-world attack cases (e.g., the 2022 KA-SAT network disruption or the 2025 Iranian tanker incident) into structured tactic-technique sequences, thereby revealing common attack patterns and inter-layer dependencies. This matrix complements the layered threat analysis presented earlier by offering a cross-layer perspective that highlights how attackers transition between physical, network, and user layers. While Sat-ATT&CK does not include formal analytical models or automated reasoning modules, it establishes a foundational knowledge structure that can inform future research on attack simulation, threat intelligence sharing, and dynamic defense strategy generation for satellite networks.

3.5. Sat-ATT&CK Attack Chain Example: The 2022 Viasat Incident

To demonstrate the practical applicability of the Sat-ATT&CK matrix (Section 3.4), we analyze the well-documented cyberattack against the Viasat KA-SAT network that occurred in February 2022 [8,9]. This incident is widely recognized as one of the most impactful satellite cyberattacks to date, causing widespread communication outages across Ukraine and collateral disruptions in several European countries. By mapping this attack onto the Sat-ATT&CK taxonomy, we illustrate how a real-world threat campaign can be decomposed into a sequence of adversary tactics and techniques.
Table 3 presents the attack chain, organizing each adversarial action according to the corresponding Sat-ATT&CK tactic and technique.
The Viasat example thus validates the utility of Sat-ATT&CK as an analytical tool for real-world satellite security incidents. It also underscores the need for continuous refinement of the matrix as new attack patterns emerge.

4. Cybersecurity Defense Technologies for Satellite Networks

Analysis shows that due to the openness, resource constraints, and cross-layer attack chain characteristics of satellite networks, there is an urgent need to systematically sort out and integrate the existing defense technologies. However, most current surveys on satellite network security merely list defense technologies, lacking systematic organization of the “threat–defense” matching logic and cross-layer collaboration. Based on the core functions (Protect, Detect, Respond) of the NIST CSF, this section organizes defense technologies in a structured manner, highlighting their roles in threat awareness, proactive hardening, detection, response, and recovery.

4.1. Adaptability Analysis of NIST CSF and Defense Mapping for Satellite Networks

While the NIST CSF provides a generic and effective functional framework for organizing cybersecurity activities, its application to satellite networks—a highly complex, resource-constrained, and dynamic environment—requires in-depth adaptability analysis. This section proposes a structured defense perspective informed by the NIST CSF functions. This perspective serves to connect the Sat-ATT&CK threat knowledge matrix (Section 3) with defense technologies while accounting for the unique characteristics of satellite networks. It provides a logical structure for analyzing and organizing the specific defense technologies discussed in subsequent sections.

4.1.1. Challenges Posed by Satellite Networks to NIST CSF Core Functions

The inherent characteristics of satellite networks pose distinct challenges to implementing the core functions (Protect, Detect, Respond) of the NIST CSF. Stringent constraints on on-board computing, storage, and energy, coupled with the dynamic topology of LEO constellations, demand that defense mechanisms be lightweight, adaptive, and tolerant of frequent network reconfigurations. Significant propagation latency and limited space–ground bandwidth render fully centralized real-time detection and response impractical, necessitating a space–ground collaborative model featuring lightweight on-board preliminary detection/response complemented by in-depth ground analysis and coordinated command. Additionally, satellites in different orbits (e.g., GEO vs. LEO) exhibit varying values, attack surfaces, and connectivity patterns, while security priorities for individual satellites also shift across mission phases (e.g., on-orbit testing, nominal operation, emergency response), requiring context-aware and dynamically adjustable defense strategies tailored to specific operational scenarios.

4.1.2. Threat–Defense Mapping

To facilitate a systematic analysis, we propose a mapping between threats and corresponding defense technologies, which directly links each specific threat in the physical, network, and user layers to targeted core defense technologies. This mapping implies that an ideal, comprehensive response to a threat would involve a sequence of actions across the Protect, Detect, and Respond functions (detailed in Section 4.2, Section 4.3 and Section 4.4).
In satellite networks, effective cybersecurity can be envisioned as more than a linear sequence of Protect–Detect–Respond; it ideally functions as a dynamic process involving close collaboration between space and ground segments. In such a process, information gained during Respond (e.g., attack characteristics) should be fed back to inform updates in the Protect phase, such as policy refinement and patching. Simultaneously, the effectiveness of Detection capabilities heavily relies on the logging, security telemetry, and data collection mechanisms deployed during the Protect phase. This concept of closed-loop feedback and collaborative interaction is posited as crucial for countering rapidly evolving space cyber threats.
Guided by this analytical framework, the following sections will systematically review satellite network cybersecurity defense technologies from the Protect, Detect, and Respond levels, paying particular attention to their adaptive designs for addressing the aforementioned challenges.

4.2. Protection Phase

The core goal of the protection phase is to proactively harden systems, reduce the attack surface, and block the initial stages of attack chains through security baseline design. It aims to build a resilient security baseline and curb initial attack infiltration. In light of the unique challenges posed by satellite networks—such as resource constraints, dynamic topologies, and heterogeneous mission requirements—protection mechanisms must be lightweight, adaptive, and context-aware. Specific technologies can be implemented across three dimensions: physical layer, network layer, and user layer. A comparison of these layered protection technologies is presented in Table 4, which includes a Deployment Readiness assessment (Concept, Simulated, Demonstrated, Operational) for each technology. The four readiness levels are defined in the table note.

4.2.1. Physical-Layer Protection Technologies

1. 
Anti-Eavesdropping Technologies
Satellite anti-eavesdropping techniques employ distinct yet complementary approaches, including physical-layer signal optimization, active jamming, and intelligent adaptation. These methods are designed to operate under the resource-limited and highly dynamic conditions typical of satellite links, often leveraging distributed or cooperative architectures to mitigate the impact of constrained on-board processing capabilities. A typical technical solution involves optimizing signal transmission directionality to reduce leakage. Multi-antenna and beamforming technologies follow this logic, using multiple antennas, relays, or directional beams to concentrate signal energy towards legitimate receivers, reducing the probability of eavesdropping interception at the hardware and signal processing levels. Reference [80] demonstrates that in multi-relay Single-Input Multiple-Output (SIMO) satellite/Multiple-Input Single-Output (MISO) Free-Space Optical (FSO) networks, increasing receiving antennas, relays, and transmitting beams can significantly enhance physical-layer security. Teng et al. [37] verified in a satellite–terrestrial relay network integrated with Non-Orthogonal Multiple Access (NOMA) that random beamforming can degrade eavesdropped signal quality while reducing Channel State Information (CSI) acquisition overhead. This method requires no additional jamming and is suitable for interference-free scenarios in multi-user environments.
Another solution proactively introduces jamming to degrade eavesdropping quality, represented by Artificial Noise (AN) injection technology. Currently, AN is widely used as an effective technology to enhance confidential communication security [81,82,83]. Injecting AN into transmitted signals can reduce eavesdroppers’ decoding capabilities while ensuring legitimate reception quality. Reference [84] studied the security and reliability performance of ground users, adding artificial noise to counter eavesdropping under a cognitive radio framework. This method is highly targeted and suitable for scenarios where the eavesdropper’s location is relatively clear or power is controllable, but it requires balancing potential interference to non-target nodes.
Building upon active jamming, RIS-aided cooperative jamming technology further improves jamming pertinence. This technology uses aerial RIS to accurately reflect jamming signals from legitimate nodes towards eavesdroppers, while keeping legitimate terminals in the null space to avoid interference [85]. Reference [86] proposed a scheme in similar satellite communication channel scenarios where full-duplex (FD) legitimate nodes actively transmit jamming noise, and aerial RIS collaboratively reflects and optimizes phases to address the limited effectiveness of traditional jamming. Reference [87] realized multi-user MISO downlink communication with RIS assistance, optimizing transmit power and reflection coefficients to maximize the sum rate.
Additionally, coding technologies can also improve physical-layer security [88]. Low-Density Parity-Check (LDPC) codes are widely adopted due to their near-capacity performance and high coding gain [89]. Reference [90] improved security using LDPC codes through random bit insertion and puncturing techniques. Reference [33] further embedded real-time CSI into LDPC coding, achieving high reliability for legitimate links and a sharp increase in the bit error rate for eavesdropped links through adaptive scrambling. These anti-eavesdropping technologies directly address the physical-layer eavesdropping threat analyzed in Section 3.1.1, which exploits open satellite communication links to intercept signals and key parameters.
2. 
Anti-Power Suppression Jamming Technologies
Defenses against power suppression jamming primarily fall into two categories: single-antenna and array antenna technologies, which offer differing levels of protection and resource requirements. Single-antenna anti-jamming technologies process signals based on single-antenna reception, offering low hardware costs but limited anti-jamming capability, and can be subdivided into time-domain and transform-domain technologies [91]. Time-domain anti-jamming technologies leverage time-domain differences between desired signals and jamming to filter jamming through filters or adaptive algorithms and are effective against narrowband or continuous wave jamming [92]. Reference [93] proposed cascading multiple IIR filters to suppress continuous wave jamming. Transform-domain technologies convert signals to the frequency domain or time-frequency domain via Fourier transform, wavelet transform, etc., to eliminate jamming. Reference [94] proposed a multi-Short-Time Fourier Transform (STFT) technology based on STFT and used notch filters to accurately detect and suppress jamming. Reference [95] proposed an adaptive threshold based on wavelet decomposition to suppress narrowband jamming.
Array antenna technologies possess spatial resolution and stronger anti-jamming capabilities, including spatial-domain, space–time adaptive, and beamforming technologies [91]. Spatial-domain technologies adjust array weights through adaptive algorithms like power inversion to alter antenna patterns and suppress power suppression jamming. The power inversion adaptive algorithm proposed in [96] can provide Beidou navigation receivers with up to 50 dB of anti-jamming capability. Space–Time Adaptive Processing (STAP) combines spatial and time domains, adding transverse delay taps to increase antenna degrees of freedom, thereby suppressing more jamming sources. Reference [97] studied the anti-jamming performance of the power inversion algorithm based on the linearly constrained minimum variance criterion in space–time two-dimensional filtering.
3. 
Anti-Spoofing Jamming Technologies
Due to its high concealment, physical-layer spoofing jamming poses a more severe security threat to satellite systems than traditional suppression jamming, driving the development of defense methods towards refinement, intelligence, and diversification. Common defense technologies include signal feature analysis, measurement domain analysis, and intelligent detection, which build defenses against spoofing and jamming from different dimensions.
As a fundamental identification method for spoofed signals, signal feature analysis focuses on the inherent characteristics of legitimate signals for identification. Spoofed signals in baseband processing can damage the symmetry and amplitude of the Autocorrelation Function (ACF). Researchers have proposed various indicators and hypothesis detectors based on correlator outputs for anomalies in tracking channels [98]. To improve detection robustness, information fusion technologies (e.g., Bayesian data fusion, Kalman filters, Dempster–Shafer theory [99], generalized likelihood ratio test [100]) have been further introduced to integrate these indicators, forming the first line of defense against spoofing attacks.
Furthermore, detection methods based on measurement domain/location domain consistency analysis are also effective against spoofing jamming attacks. Reference [101] proposed a GNSS spoofing detection method based on the consistency of measured and calculated carrier Doppler. Reference [102] proposed a GNSS repeater spoofing detection method based on the dual-peak feature of frequency-domain signals and relative velocity residuals, using Fast Fourier Transform (FFT) to detect dual peaks and extract Doppler differences. References [103,104] combined consistency monitoring of signal power and correlation peak shape distortion, capable of detecting spoofing and distinguishing multipath under small code delay differences.
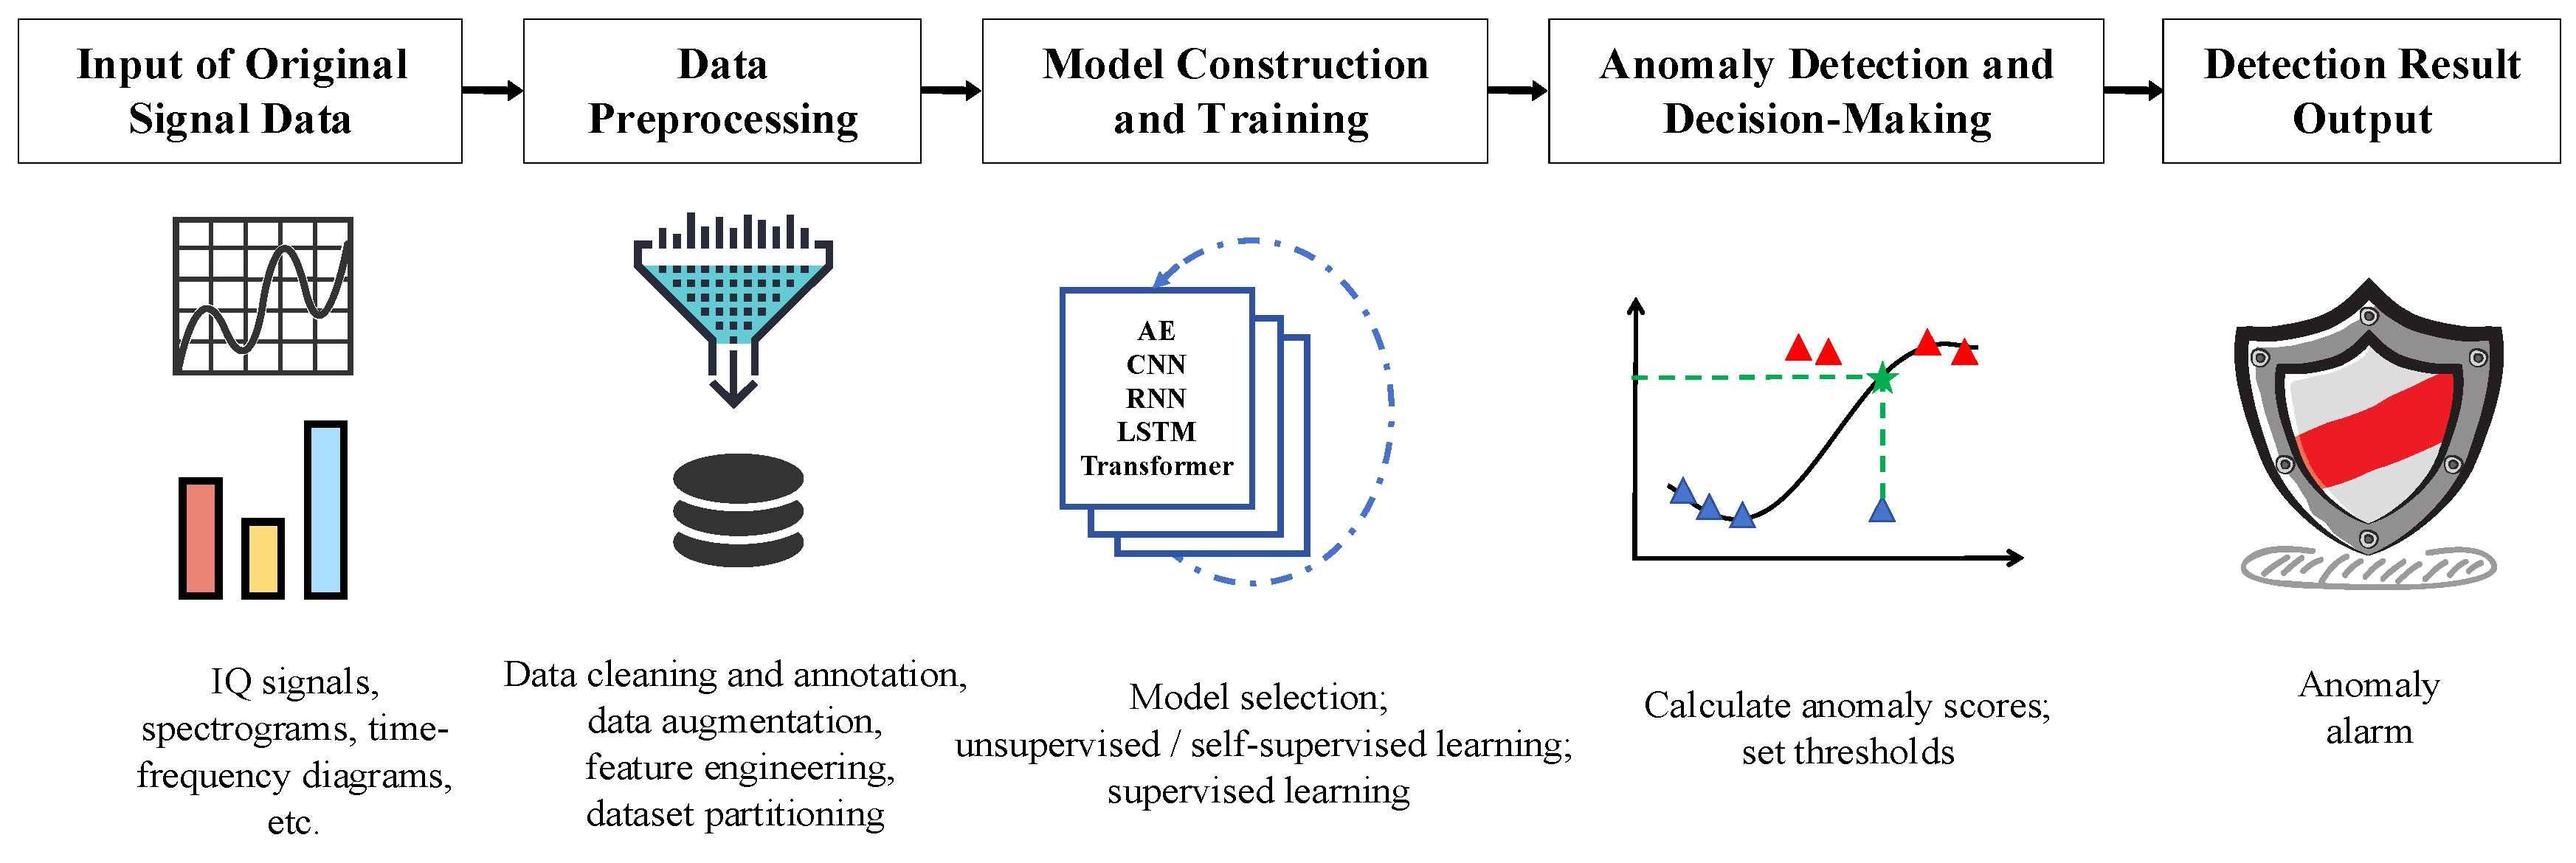
When spoofed signal characteristics become more concealed, anomaly detection technologies based on deep learning can mine legitimate signal patterns and dynamically monitor signal anomalies. Reference [105] used deep learning for jamming management, significantly improving the detection accuracy of interfering carriers under high Signal-to-Interference Ratio (SIR) and enhancing communication channel protection capability. Reference [106] adopted machine learning (e.g., CNN) for spectrum occupancy detection and automatic modulation classification, capable of identifying illegal interfering signals and reducing dependence on prior knowledge like expert features. Reference [107] focused on air spoofing attack detection in LEO satellite systems, innovatively converting raw IQ samples at the physical layer into grayscale images and deeply learning the feature distribution of legitimate signals based on a sparse Autoencoder (AE). Such methods effectively overcome the limitations of traditional feature analysis in identifying concealed spoofed signals and are more suitable for complex electromagnetic environments. The intelligent detection framework for physical-layer anti-spoofing jamming is shown in Figure 7.

4.2.2. Network-Layer Protection Technologies

1. 
Anti-Routing Attack Technologies
Satellite network routing security faces dual threats from internal and external attacks, requiring the construction of security defenses through diverse technologies. To address the challenges of dynamic topology and frequent handovers in LEO constellations, many routing defense strategies incorporate location-aware or hierarchical structures that limit attack propagation and reduce signaling overhead. Defense strategies based on network structure optimization provide structural solutions. The core idea is to achieve routing isolation and refined management by dividing network structures (e.g., layers, regions, location domains) to limit the scope of attack impact. Specifically, they can be further divided into location-based routing defense and hierarchical routing defense.
Location-based routing defense ensures the legitimacy of routing nodes through satellite location rules and regional division, preventing malicious nodes from accessing the network by forging locations. Reference [108] developed a robust branch-and-price algorithm to enhance adaptability for the two-level location routing problem involving recommended satellites. Du et al. [109] proposed a distributed location management method for hybrid-orbit satellite networks, optimizing handover and reducing signaling overhead through dual-location region division. Reference [110] divided LEO constellation subgroups by logical path identifiers and designed dedicated identifiers to improve routing efficiency and packet delivery rate. Reference [111] targeted ultra-dense Free-Space Optical (FSO) LEO satellite networks, optimizing routing efficiency and reducing system complexity through regional division based on a medium–low orbit integrated architecture. These defense technologies build defenses from different dimensions, reducing the risk of attack diffusion, improving anti-jamming capabilities, and forming a multi-layered defense system.
2. 
Anti-Message Tampering Technologies
Message tampering can cause navigation deviations, decision-making errors, or even system paralysis by illegally modifying transmitted data, instructions, or parameters in satellite networks. Therefore, it is necessary to build a protection system relying on multi-layered defense technologies. Current main defense methods include encryption and hash verification, blockchain evidence storage, and zero-trust authentication, which resist tampering threats from dimensions such as data encryption, distributed evidence storage, and dynamic verification.
As basic defense technologies, encryption and hash verification ensure data integrity and confidentiality during transmission through cryptographic means. In satellite Internet of Things (IoT), homomorphic signcryption technology based on Hyperelliptic Curve Cryptography (HECC) can simultaneously achieve data encryption and signature, support batch verification of multi-device data, and significantly reduce computational and communication overhead [112]. Additionally, schemes combining dynamic encryption and hashing can also effectively resist unauthorized modifications [113].
Blockchain evidence storage leverages the immutability of distributed ledgers to provide decentralized message integrity guarantees. Chen et al. [114] proposed a random blockchain scheme, introducing uncertainty by randomly selecting nodes to broadcast data to enhance anti-attack capabilities. Yuan et al. [115] further utilized the characteristics of Physical Unclonable Functions (PUF) to achieve keyless negotiation in lightweight broadcast authentication protocols, avoiding the risk of sensitive key leakage. In [116], the StarCross framework adopts editable blockchain technology, realizing efficient rollback of cross-shard transactions through chameleon hash and voting-based consensus mechanisms, while using block immutability to record data flow processes, effectively defending against message tampering.
Currently, traditional single security technologies can no longer cope with modern distributed networks [117], and the zero-trust model has garnered increasing attention in satellite communications [118]. It detects and resists tampering in real-time through continuous verification and dynamic update mechanisms, adapting to highly dynamic inter-satellite links. Reference [119] proposed a lightweight zero-trust protocol based on Hyperelliptic Curve Cryptography (HECC), integrating satellite orbit parameters as physical trust anchors. While ensuring the anti-forgery and anti-hijacking security of inter-satellite links, it significantly reduces authentication delay and communication overhead.
3. 
Basic DoS Attack Protection
DoS attacks on satellite networks can launch coordinated attacks through distributed architectures, and the expansion of LEO constellation scale has exacerbated problems like limited space–ground link bandwidth and tight node resources, further increasing defense difficulty. Therefore, improving system anti-attack redundancy through resource optimization is the core of basic protection. Cache optimization intelligently selects service nodes and adopts hierarchical strategies by optimizing resource scheduling and request processing flows, reducing redundant link loads and repeated request impacts, thereby enhancing the system’s anti-DoS attack redundancy. Delay-Tolerant Networks (DTN) [120] rely on intermediate router caching mechanisms to effectively alleviate retransmission overhead caused by wireless link quality fluctuations. Furthermore, the CAAST framework proposed in [121] optimizes storage distribution by selecting cache nodes through the IL-TOPSIS strategy and combines the HFS hierarchical fallback strategy to handle cache miss scenarios, reducing link congestion and improving the service availability of satellite networks against DoS attacks.

4.2.3. User-Layer Protection Technologies

1. 
Privacy Protection Technologies
The combination of data encryption and key management mechanisms can meet the security and compliance requirements for users’ sensitive information throughout its entire lifecycle (including collection, transmission, and storage), offering a comprehensive solution for privacy protection. Given the on-board resource constraints and the need for efficient key updates during frequent handovers, recent research emphasizes lightweight cryptographic algorithms and hierarchical key management schemes that balance security with low computational and communication overhead.
The academic community has proposed various encryption schemes for satellite networks: Liu S. et al. proposed a conditional generative adversarial network encryption scheme to enhance the security of Beidou short message channels [122]. Jeon S. et al. designed a method combining encryption and channel coding along with a corresponding key distribution scheme [123]. Reference [124] proposed a chaos encryption algorithm based on RNA coding, integrating an infinite-dimensional chaos system and a hierarchical diffusion strategy. It expands the key space to 2256 with an entropy value close to 8, effectively resisting statistical attacks. Currently, the research focus for encryption algorithms in satellite networks is on lightweight technologies, adapting to the resource constraints of satellite nodes. While ensuring security, they reduce computational and storage overhead, enabling efficient encryption with low resource occupancy. Reference [125] proposed an LWARX white-box cryptography algorithm, adopting an ARX (Addition–Rotation–XOR) structure to hide key information through lookup tables and internal/external coding. It can prevent privacy leakage during data transmission under limited satellite storage and computing power conditions. The Elliptic Curve Cryptography (ECC) encryption scheme in [126] is superior to the traditional RSA algorithm in both security and robustness, with shorter keys reducing transmission overhead. It efficiently adapts to the privacy protection of sensitive data like user identities in satellite communications.
Key management aims to ensure the authenticity and validity of user keys throughout their lifecycle, thereby maintaining the security of the encryption system. Howarth et al. [127] proposed a multi-layer IPsec-LKH integration scheme for satellite-encrypted multicast, reducing satellite resource occupancy by optimizing key management traffic. Roy-Chowdhury et al. [128] designed a hierarchical group key management protocol targeting the topological characteristics of hybrid satellite networks and verified its strong robustness and scalability. Jiao et al. [129] constructed a satellite group key management scheme based on elliptic curve cryptography and threshold technology, integrating identity authentication functions without needing a secure channel, significantly saving system resources. Wang et al. [130] proposed a group key management strategy utilizing the hierarchical and domain structure of near-space networks, significantly reducing the key update burden caused by frequent handovers of high-speed nodes. Sun and Ma [131] designed a multi-group key management framework for satellite networks, dividing subgroups according to users’ access capabilities. It balances forward/backward security and scalability while effectively reducing key update overhead at the satellite end.
2. 
Anti-Identity Spoofing Technologies
Identity spoofing attacks pose a serious threat to network security by forging legitimate identities to access satellite networks or impersonating nodes to participate in communications. Defense methods primarily include encryption, authentication, and blockchain technologies, which provide protection from different perspectives and can adapt to identity security needs in various scenarios.
Encryption authentication technologies prevent malicious terminals from forging identities to access the source through identity verification and permission constraints. Such technologies typically combine encryption algorithms with behavioral analysis to ensure the legitimacy of accessing nodes. Reference [98] adopted encryption authentication mechanisms like Open Service Navigation Message Authentication (OSNMA) at the user layer of satellite communications, constructed an identity forgery detection model based on user behavioral characteristics, and verified user identities through registration and dynamic authentication schemes. Reference [132] implemented end-to-end encryption at the user segment, combined with least privilege control, continuous monitoring, and patch management to prevent forged access and unauthorized operations. Furthermore, targeting identity authentication needs in different scenarios, researchers have proposed various specific schemes: Reference [133] proposed an efficient pairing-free identity authentication scheme for the Automatic Dependent Surveillance-Broadcast (ADS-B) system, supporting batch verification and resisting identity spoofing. Reference [134] designed an authentication scheme based on proxy signature for satellite authentication in space information networks, effectively verifying satellite identities. Reference [135] proposed an anonymous fast handover authentication scheme, utilizing group signatures to balance anonymity and identity authentication.
Blockchain possesses characteristics of decentralization, tamper-proofing, and transparency and can permanently track node behaviors and data [136]. Its distributed ledger technology is highly compatible with the distributed characteristics of satellite IoT [137], making it an ideal solution for identity tampering prevention. Blockchain-based identity evidence storage technology ensures the consistency and credibility of identity data through blockchain’s decentralization. Yu et al. [138] proposed a federated blockchain data sharing mechanism for cross-domain Industrial Internet of Things (IIoT), where the group signature scheme can protect device privacy and achieve anonymous authentication. Zhang et al. [139] proposed a blockchain-based cross-domain authentication scheme for edge computing, achieving secure authentication through a cross-domain bidirectional authentication algorithm for digital certificates and signatures.

4.3. Detection Phase

The detection phase focuses on anomaly identification when attacks occur, with the core goal of discovering abnormal behaviors and determining attack types. To cope with the high latency and limited bandwidth of space–ground links, detection architectures often adopt a collaborative space–ground approach, where lightweight on-board modules perform preliminary screening while more sophisticated analysis is conducted on the ground. Specific technical paths are primarily divided into network anomaly identification and data anomaly identification.

4.3.1. Network Anomaly Identification Technologies

Intrusion Detection Systems (IDS) form the core of network anomaly identification, enabling rapid detection and accurate tracing of malicious behavior through the analysis of illegal traffic and anomalous requests. In related research, ref. [140] proposed the CANSat-IDS system, which adopts Artificial Neural Network (ANN) and Kernel Support Vector Machine (K-SVM) algorithms to achieve high-precision detection of DoS attacks in the CAN bus. The SAGIN-ID framework designed in [141] uses a hierarchical detection strategy—the on-board part quickly filters known DoS attacks through hash matching, while the ground part uses semi-supervised learning algorithms to achieve high-precision identification of unknown attacks.
Besides detection systems and frameworks specifically targeting DoS attacks [142], relevant research has also explored routing protocols and defense frameworks. Jiang et al. [78] proposed a routing protocol combined with intrusion detection, which bypasses malicious nodes through collaborative rerouting of satellite nodes, but its abnormal behavior dataset is derived from ground networks. Li et al. [143] proposed a space–ground integrated network intrusion detection scheme, which has good malicious traffic detection effectiveness but requires high node computing power. Reference [144] designed a blockchain-based distributed collaborative defense framework for the resource-constrained characteristics of on-board systems. It records traffic characteristics through blockchain and aggregates attack characteristics with the MapReduce algorithm, significantly reducing on-board computing overhead. Additionally, ref. [145] proposed a secure transmission optimization algorithm with joint anomaly detection for jamming and DoS attacks that satellite networks may encounter. It incorporates detection accuracy as a factor in transmission path decision-making and constructs and solves optimization problems based on optimal control strategies.

4.3.2. Data Anomaly Detection Technologies

Data anomaly detection is a key link in satellite data processing, and related research has formed various characteristic methods. Zhang Mingjiang [146] proposed an on-orbit satellite anomaly detection method integrating ARX and Support Vector Regression (SVR), which performs initial linear prediction through the ARX model and then uses the SVR model to capture nonlinear components to correct results.
In engineering applications, satellite telemetry data anomaly detection methods mainly fall into three categories: first, methods based on threshold rule interpretation, which detect anomalies by verifying whether data falls within a specified threshold range, representing the mainstream approach in the early stages of this field; second, methods based on expert knowledge and expert systems, which build detection systems relying on domain experience; and third, data-driven methods, which mine data patterns using machine learning, statistics, and other technologies, capable of identifying unknown anomalies without expert experience [147]. In specific applications, ref. [148] comprehensively characterizes the statistical distribution of normal data by integrating the centralized, discrete, shape, and boundary characteristics of telemetry data, realizing anomaly detection for single telemetry parameters of locally stable spacecraft. Ref. [149] adopts Principal Component Analysis (PCA) to map multi-dimensional telemetry variables of the satellite Attitude and Orbit Control System (AOCS) to a low-dimensional space and uses statistics such as Hotelling’s T2 and Squared Prediction Error (SPE) to detect sample anomalies.
In recent years, deep learning-driven anomaly detection has become a research hotspot. Ref. [150] adopted Convolutional Neural Network (CNN), processed class-imbalanced time-series data through sampling methods, and achieved time-series classification of normal and abnormal sequences through supervised training. Luo Hui [151] proposed models such as Autoencoder, CNN, and Generative Adversarial Network (GAN) to extract features for satellite gas path anomaly detection, adapting to detection needs in different scenarios. Ref. [152] proposed an ensemble LSTM-based method, combining matrix norm to model the correlation between telecommand instructions and telemetry, improving adaptability to complex systems, which can effectively detect anomalies and reduce false alarm rates.

4.4. Response Phase

The response phase is the core of dynamic disposal in the cybersecurity defense system of satellite networks. Its core goal is to quickly block the horizontal diffusion path of attacks through real-time and effective intervention measures, thereby minimizing the impact of attacks on the business continuity of satellite networks. Response strategies must account for the orbital dynamics and mission heterogeneity of satellite networks, enabling timely countermeasures while maintaining service availability across different orbital regimes (GEO, MEO, LEO) and mission phases.

4.4.1. Real-Time Attack Blocking Technologies

1. 
Dynamic Link Response
When hardware enhancement cannot fully offset strong power jamming, dynamic link switching technology can automatically switch to media or satellite resources with stronger anti-jamming capabilities by real-time monitoring key indicators such as signal-to-noise ratio and adapting to channel states, thereby avoiding jamming impact. Ref. [153] proposed a Free-Space Optical/Radio Frequency (FSO/RF) hybrid satellite–air–ground network for extreme desert environments, which dynamically switches based on real-time channel states to cope with extreme jamming and ensure communication continuity. The security of link switching is also a key concern in the response phase. Xue et al. [154] designed an identity authentication protocol and fast handover mechanism with both security and efficiency, capable of resisting various attacks and meeting various security requirements. Ref. [155] proposed an access authentication protocol with user anonymity and traceability, reducing authentication costs by optimizing communication delay and signaling overhead and designing a hierarchical group key distribution strategy to achieve cross-domain handover without repeated authentication. Ref. [156] proposed a secure user access and inter-satellite handover mechanism, enhancing system security through a separate key architecture for the control plane and user plane, and combining identity-based encryption with proxy re-encryption to complete efficient batch handover with stack support.
Additionally, the disposal of link damage or interruption is also a research focus in satellite routing algorithm design [157]. Ref. [54] proposed the Open Shortest Path First (OSPF) protocol, which utilizes the regularity of constellation topology to perform periodic routing calculations for generating real-time routing tables, and combines an on-demand dynamic routing mechanism to handle topology changes caused by link failures or recovery, significantly reducing routing convergence overhead and time. Ref. [158] realizes dynamic perception of link states through a link detection mechanism. When a node is damaged, adjacent nodes update the topology and send damage messages, and other nodes record and forward them to update the local topology, thereby quickly responding to link changes and reselecting routes. Ref. [159] proposed a Quick Response to Link Damage Routing Algorithm (QRLDRA) for LEO satellite constellations, which integrates space–ground backhaul, multi-priority queues, and routing calculation functions based on predictable constellation topology to cope with inter-satellite link failures and achieve timely response to topology changes.
2. 
Intelligent Traffic Regulation
Intelligent traffic regulation alleviates the impact of traffic flooding DoS attacks from the source by dynamically adjusting network load. This technology focuses on network traffic characteristics and load change rules to achieve adaptive regulation. Ref. [160] proposed a congestion-aware load balancing algorithm to alleviate ISL congestion in dynamic LEO optical satellite networks. Ref. [161] proposed an intelligent congestion control algorithm based on Reinforcement Learning (Proximal Policy Optimization, PPO), which dynamically adjusts the congestion window to match real-time network load. Ref. [162] adopted dual decomposition combined with a Convolutional Neural Network-Bidirectional Long Short-Term Memory (CNN-BiLSTM) model to build a traffic prediction mechanism, avoiding congestion caused by DoS attacks by identifying self-similar traffic characteristics in advance. Ref. [163] proposed the SCMA-QL-ACB method, combining Sparse Code Multiple Access (SCMA) technology, Q-learning algorithm, and Access Class Barring (ACB) mechanism, which effectively improves performance indicators such as throughput and collision rate by enhancing spectrum efficiency, optimizing resource allocation, and controlling overload.
3. 
Multipath Fault-Tolerant Routing
Multipath fault-tolerant routing copes with network attacks by constructing multiple paths. Its core is to use path redundancy to resist attacks and avoid routing interruptions caused by single-path failures. Ref. [164] realized dynamic multipath routing for satellite networks based on Software-Defined Networking (SDN), adjusting routes in real-time by integrating delay, bandwidth, and node load states. Liu et al. [165] targeted LEO satellite networks, intelligently distributing traffic and reducing delay by improving clustering structure, optimizing quality of service and load balancing. Zeng et al. [166] proposed a low-latency fault-tolerant multipath routing algorithm, transmitting data copies in optimal proportions over independent shortest paths to balance reliability and timeliness. Ref. [167] adopted the Explicit Compact Multipath Routing (CEMR) algorithm to achieve full-network topology perception based on inter-satellite link interaction. Wang et al. [168] designed a computation-dependent multipath routing paradigm for space–ground integrated networks, dynamically mapping computing tasks to multiple paths, optimizing system energy consumption while meeting delay constraints.

4.4.2. Fault Early Warning Technologies

The core of fault early warning is to determine whether to trigger a fault alarm and identify the warning fault type based on historical and current data. Three commonly used methods for communication satellite fault detection are: methods based on threshold rules combined with manual monitoring, methods based on traditional machine learning algorithms, and trend prediction based on time-series models [169,170,171,172].
In recent years, deep learning-based fault early warning has become a research hotspot. Ref. [173] discussed the use of Long Short-Term Memory (LSTM) and Gated Recurrent Unit (GRU) architectures in Recurrent Neural Networks (RNN) for anomaly detection of aircraft flight data. Chen et al. [174] proposed a Fault Prediction Convolutional Neural Network (FPCNN) combining the characteristics of convolutional neural networks. Ref. [175] proposed a stacked autoencoder network method to realize fault detection and early warning through extracted features. Tagawa et al. [176] improved the denoising autoencoder and proposed the Stacked Denoising Autoencoder (SDA) model, which can reconstruct time-series data using incomplete prior information and avoid overfitting. Liu Yun et al. [177] proposed a thresholding method based on the LSTM network, learning the patterns of normal data through LSTM, and determining the threshold with correlation coefficients and F1 scores to effectively detect system-level faults of communication satellites.

4.5. Satellite-Specific Defense Prioritization Strategies

Based on the systematic review of satellite network cybersecurity defense technologies above, the diverse operational scenarios, heterogeneous architectures, and varying resource constraints of satellite networks necessitate tailored defense prioritization. A one-size-fits-all approach fails to balance security effectiveness, resource efficiency, and mission adaptability. This section proposes prioritization strategies centered on three core dimensions—orbit type, mission criticality, and resource availability—providing actionable guidance for practical deployment and enhancing the framework’s adaptability.
Orbit type is a fundamental determinant of defense prioritization, shaping resource availability, threat exposure, and network dynamicity. For LEO satellites, especially mega-constellations, strict on-board resource constraints mandate lightweight, low-overhead technologies: optimized AES-128 encryption, low-latency zero-trust authentication, scalable distributed traffic regulation, fast handover protocols, and lightweight collision warning systems. GEO satellites, as high-value core infrastructure, prioritize high-reliability deep defense: high-directionality beamforming, ruggedized components, deep learning-based intrusion detection, blockchain tamper-proofing for control data, and redundant communication links. MEO satellites adopt a balanced strategy, integrating low-power signal detection with targeted anti-spoofing for mission-critical functions.
Mission criticality refines resource allocation to safeguard core objectives. For critical missions (military operations, emergency relief), priorities include LSTM/GRU-based low-latency anomaly detection, dynamic link switching, military-grade encryption, and millisecond-response collision avoidance. For civilian missions (broadband access, remote sensing), the focus shifts to cost-effectiveness and user experience: edge computing-based privacy protection, energy-efficient anti-eavesdropping, scalable certificate authentication, and low-cost time-domain filtering.
Resource availability constrains defense feasibility. Resource-limited satellites (small satellites, CubeSats) prioritize passive, low-overhead strategies: signal feature-based spoofing detection, location-based routing isolation, and pre-configured emergency protocols. Resource-abundant satellites (large communication satellites) deploy integrated active-passive systems: RIS-aided anti-eavesdropping, CNN-based intelligent detection, reinforcement learning-driven response, quantum communication for critical data, and distributed blockchain verification.
These strategies aim to guide resource allocation and defense deployment in alignment with mission objectives, potentially aiding the translation of theoretical technologies into practical security measures.

5. Emerging Challenges

As the core hub of space–air–ground integrated communications, the security defense of satellite networks faces significant and interconnected challenges. These challenges arise not only from the continuous evolution of attack methods but also from the inherent technical characteristics and development trends of satellite networks.

5.1. Cross-Layer Attack and Defense Challenges

In actual satellite network attacks, attackers often exploit interaction vulnerabilities across different layers to form attack chains, constructing attack paths through cross-layer transitions of tactical chains. For example, in the 2025 Iranian oil tanker attack, attackers hijacked network-layer communication channels and injected malicious programs into user terminals to steal sensitive data. The attack on GNSS receivers by the GhostSec group further revealed a collaborative exploitation model of physical-layer signal spoofing and application-layer weak password vulnerabilities.
Such attacks increase concealment through cross-layer tactical chains. Existing defenses, however, often focus on single-layer protection and lack cross-layer correlation analysis. This leads to delayed detection, fragmented responses, and difficulty in blocking attack propagation. Furthermore, current related research primarily focuses on wireless network scenarios [178,179,180,181], and studies on cross-layer attack defense targeting the unique dynamic topology and heterogeneous links of satellite networks are still insufficient, further exacerbating defensive passivity.

5.2. Mega-Constellation and Resource Constraint Challenges

With the advancement of LEO mega-constellation deployment, satellite networks present characteristics of dense nodes and dynamic topology, bringing new challenges to security defense [182]. The frequent switching of ISLs of LEO satellites requires defense algorithms to possess extremely strong dynamic adaptation capabilities, while traditional static rule bases struggle to match the rapid changes in attack characteristics.
Simultaneously, the limited computing power, energy consumption, and storage resources on satellites make it difficult to support the operation of complex cross-layer defense algorithms. Balancing security performance and resource consumption has become a technical difficulty. The heterogeneous networking of multi-orbit satellites (GEO/MEO/LEO) with ground and user terminals further increases the difficulty of compatibility design for cross-layer defense protocols. The differentiated security requirements of high-latency and low-latency links further aggravate the complexity of technical adaptation.

5.3. Artificial Intelligence in Satellite Security: Challenges and a Feasibility Study

Artificial Intelligence (AI) offers transformative potential for satellite security, enabling adaptive threat detection and automated response [183]. However, it also introduces new risks. Adversaries can leverage AI to generate sophisticated spoofing signals or use adversarial machine learning to manipulate sensor data, compromising system integrity. The rise of generative LLMs further lowers the attack threshold, facilitating automated exploit generation and vulnerability analysis [184]. Crucially, the significant computational demands of advanced AI starkly contrast with the resource-constrained satellite environment, posing a fundamental deployment challenge [185,186].
An Exploratory Case: Towards a Domain-Specific LLM. To concretely assess the feasibility of leveraging security knowledge for AI augmentation, we fine-tuned an open-source LLM (Qwen3-8b) using a corpus that integrates the satellite-specific threat knowledge defined in our Sat-ATT&CK matrix (Section 3.4), the surveyed literature, and the MITRE ATT&CK for ICS framework. The resulting prototype, SatSec, was preliminarily evaluated on domain-specific question-answering and threat-reasoning tasks. By incorporating the structured tactics and techniques of Sat-ATT&CK into its training data, SatSec is capable of understanding and reasoning about satellite-specific attack chains, thus directly supporting the threat analysis concepts introduced earlier in the paper.
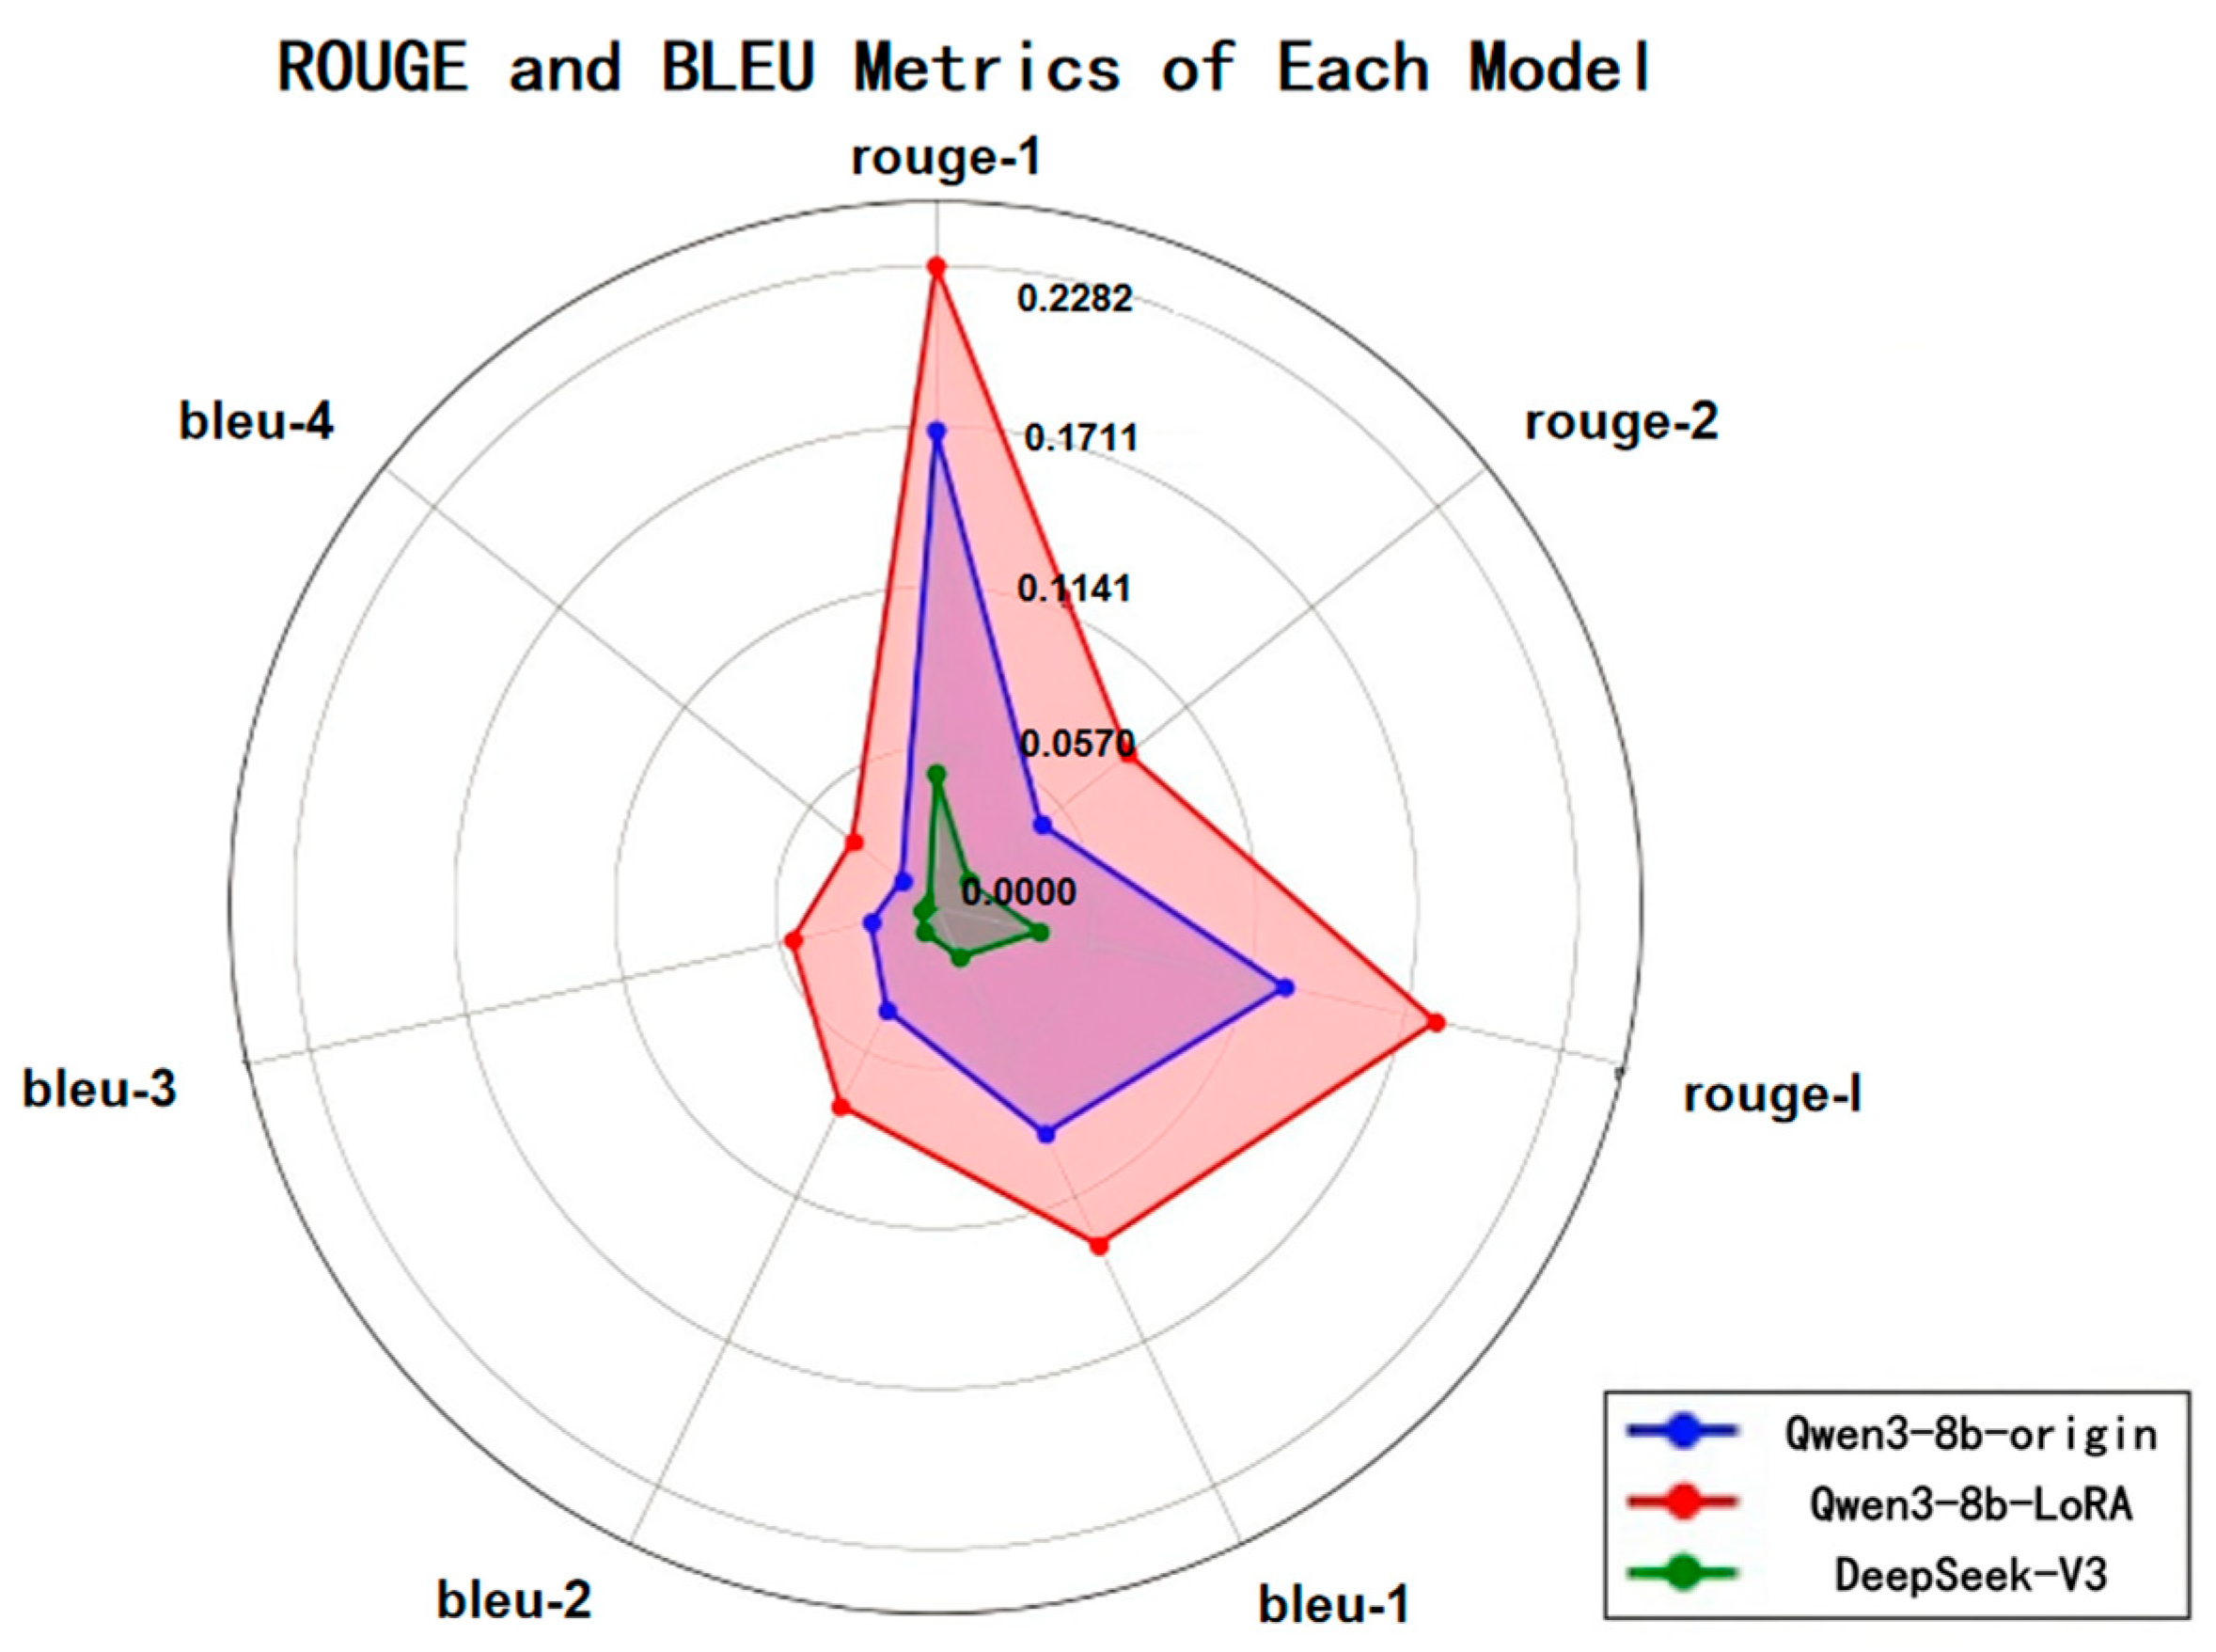
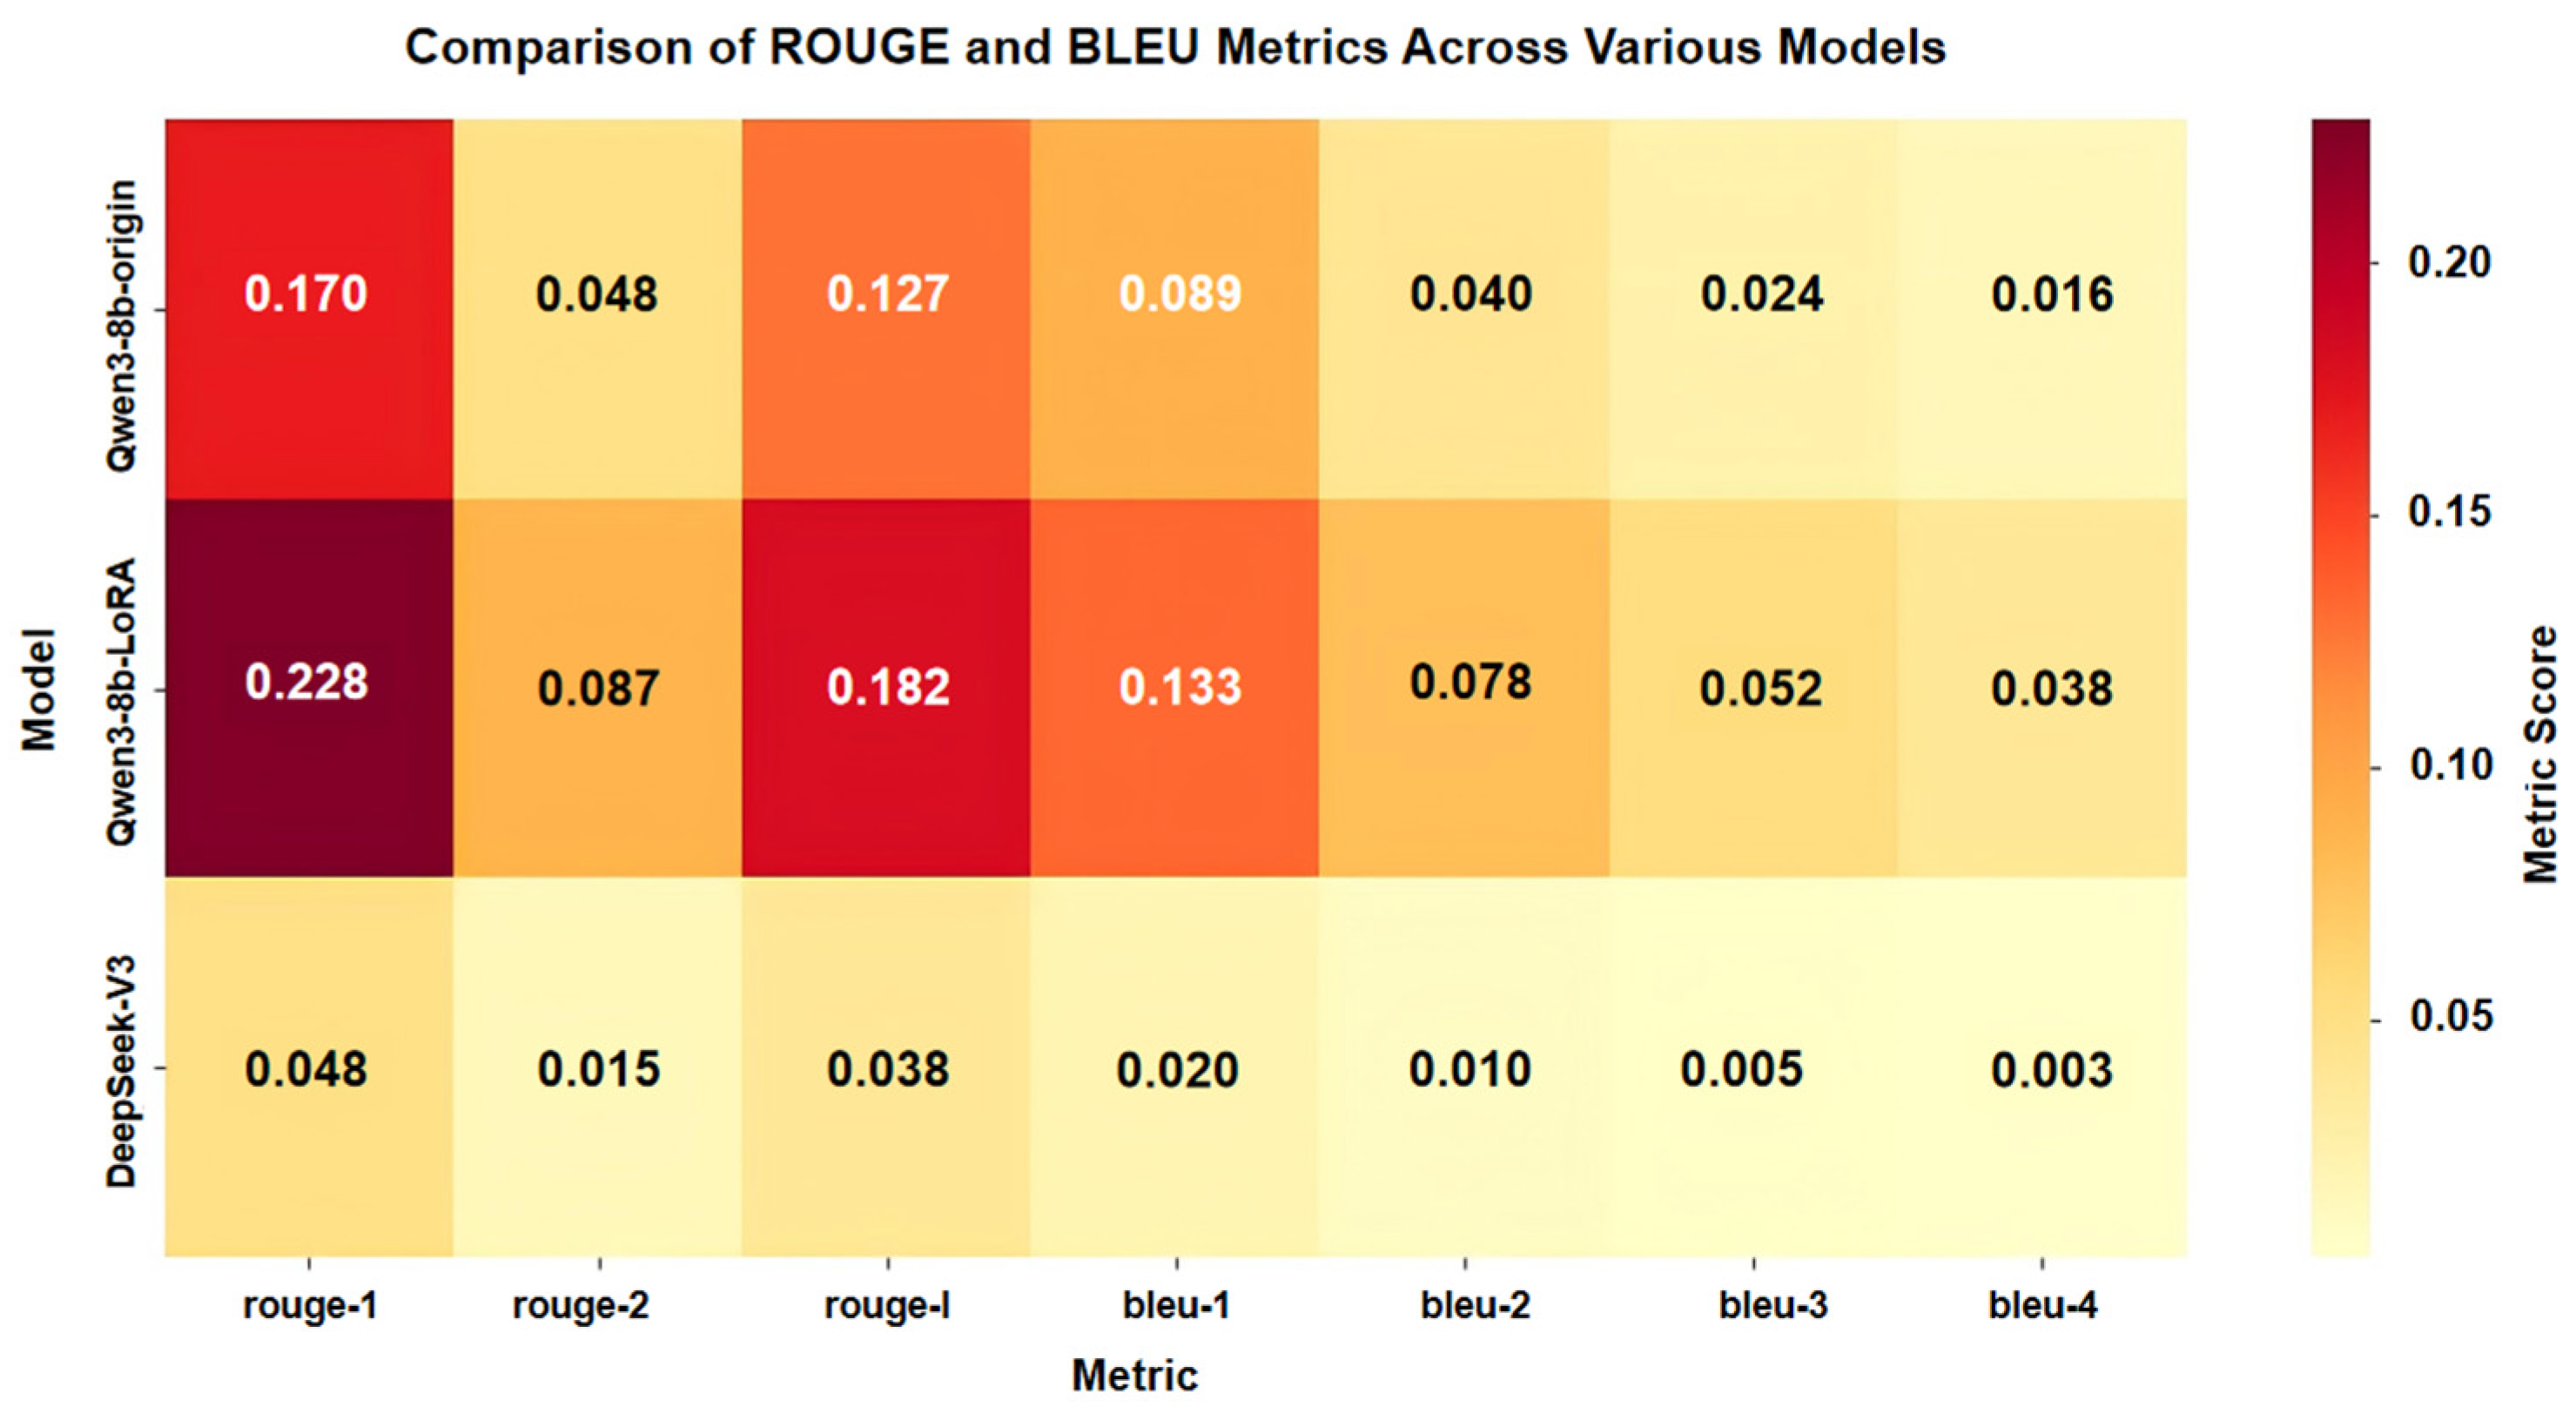
This exploratory effort yielded three key insights: (1) Converting comprehensive survey knowledge into an AI-ready format is technically feasible. (2) The domain-adapted SatSec model showed improved answer relevance compared to a general-purpose LLM (DeepSeek-V3) in automated metrics (e.g., ROUGE, BLEU). (3) This pathway highlights the potential for LLMs to serve as intelligent assistants for knowledge retrieval and basic threat reasoning. Full methodological details of SatSec are provided in Appendix A.

6. Conclusions and Future Directions

This survey has provided a systematic review of cybersecurity threats and defense technologies in satellite networks. We conducted a layered threat analysis, proposed the satellite-specific Sat-ATT&CK knowledge matrix for modeling attack chains, and organized defense technologies within the NIST CSF (Protect, Detect, Respond) framework. An exploratory case study on a domain-adapted LLM (SatSec) was also presented to illustrate a potential pathway for AI-augmented security analysis.
Looking ahead, future research should prioritize the following directions to evolve satellite security towards a more resilient and intelligent paradigm:
(1)
Cross-Layer Collaborative Defense: Developing integrated frameworks for coordinated threat detection and response across physical, network, and user layers.
(2)
Lightweight Security for Mega-Constellations: Designing scalable, adaptive, and resource-efficient protocols that meet the severe constraints and dynamic topologies of LEO mega-constellations.
(3)
Trustworthy AI Integration: Realizing that the potential of AI, as preliminarily explored in Section 5.3, requires solving fundamental challenges in robust, explainable, and resource-efficient deployment within the stringent constraints of space systems.

Author Contributions

Conceptualization, B.W. and J.X.; methodology, B.W. and J.X.; validation, R.D., C.P. and Y.G.; investigation, B.Z., Y.Y. and Z.Z.; writing—original draft preparation, J.X. and R.D.; writing—review and editing, S.L. and X.L. All authors have read and agreed to the published version of the manuscript.

Funding

This research was funded by the National Natural Science Foundation of China (grant number 62472437).

Data Availability Statement

The data presented in this study are available on request from the corresponding author. The data are not publicly available due to privacy restrictions.

Conflicts of Interest

The authors declare no conflict of interest.

Appendix A. Implementation Details of the SatSec Exploratory Study

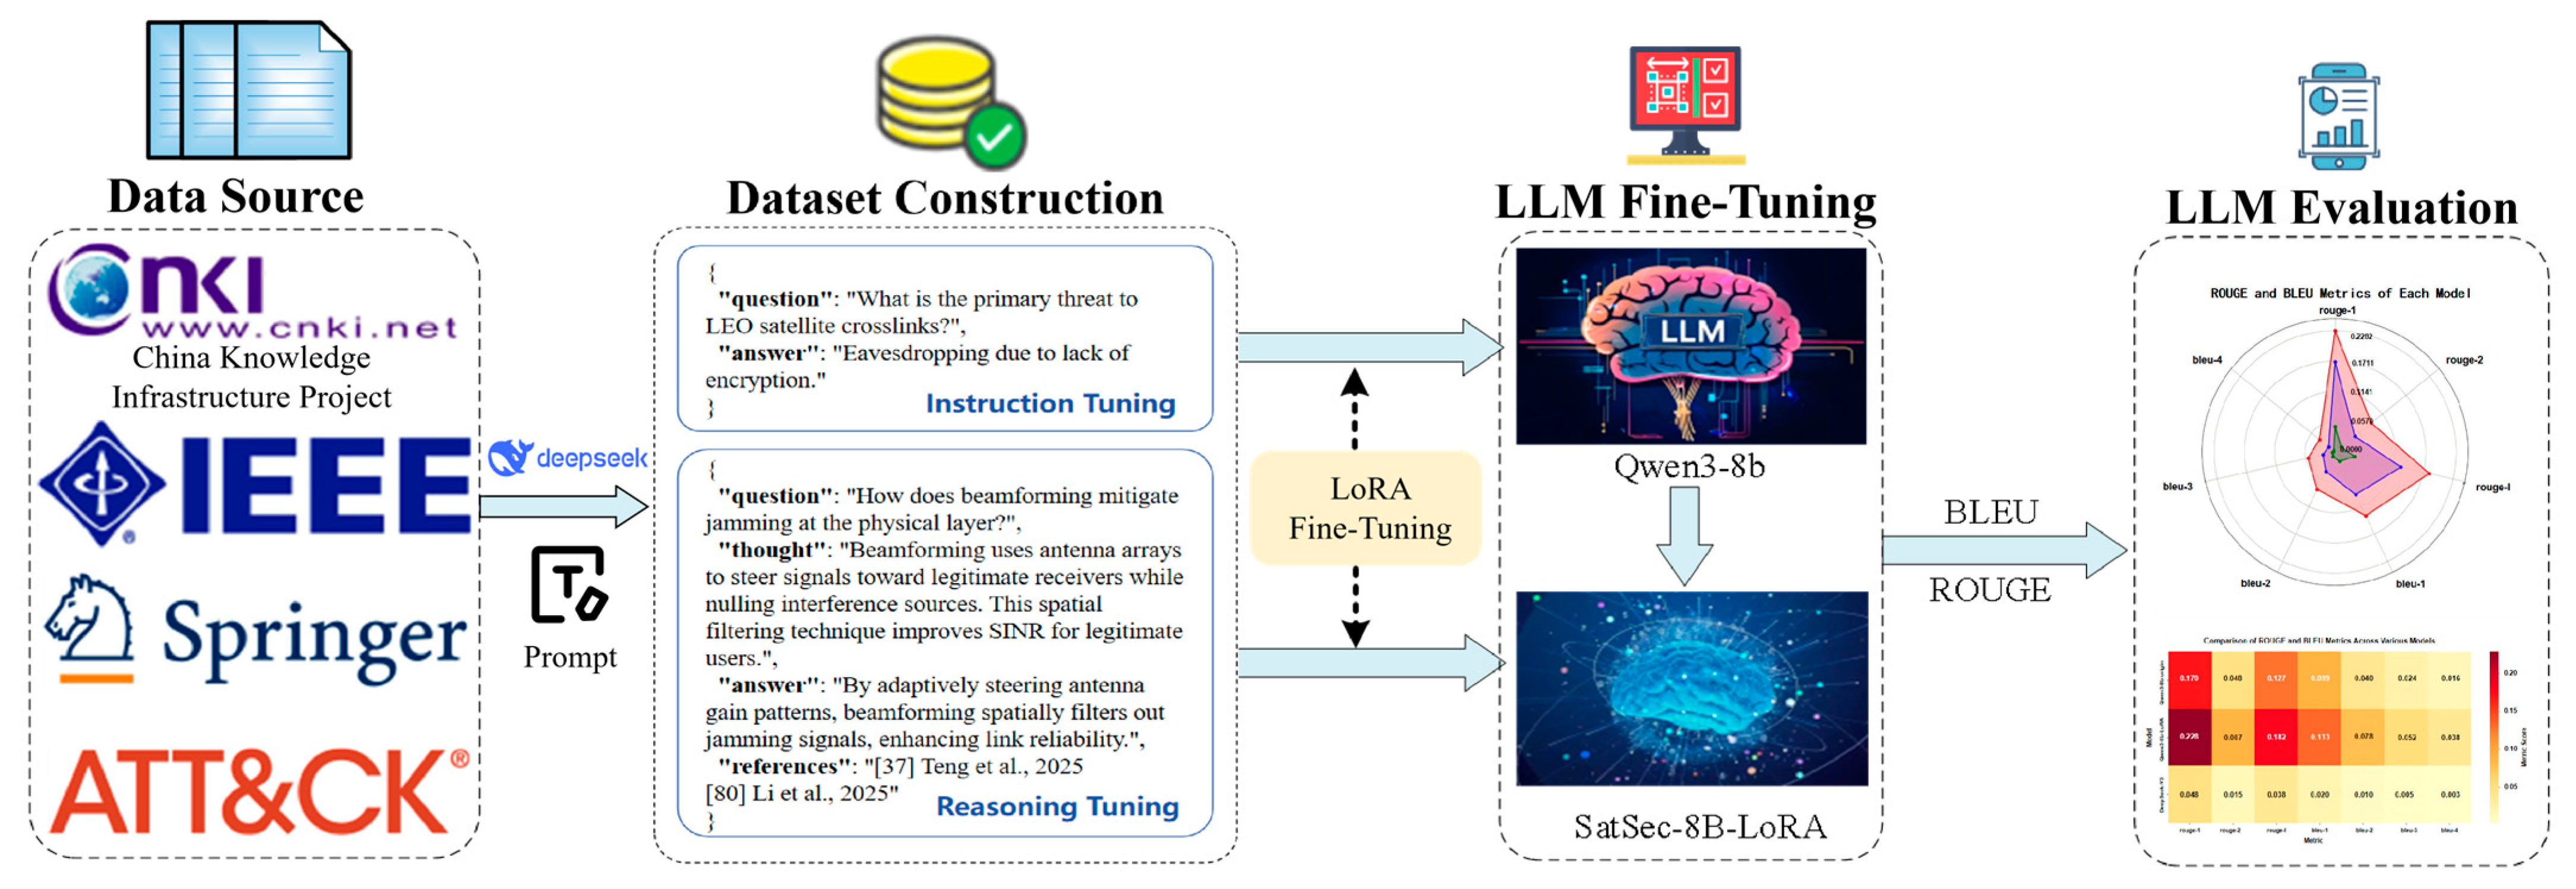
This appendix provides the detailed methodology and results for the exploratory case study on fine-tuning a vertical-domain LLM (SatSec) discussed in Section 5.3. It is included for completeness and to facilitate reproducibility, acknowledging that this work represents a feasibility demonstration rather than a core contribution of the survey. The construction process of SatSec is illustrated in Figure A1.
Figure A1. Construction process of SatSec.
Aerospace 13 00249 g0a1

Appendix A.1. Task Definition and Model Scope

SatSec is designed to bridge the gap between generalized AI assistants and domain-expert knowledge by addressing two core cybersecurity tasks within satellite network contexts:
(1)
Intelligent Question Answering: The model provides accurate, context-aware responses to technical queries concerning satellite network architectures, threat landscapes, defense mechanisms, communication protocols, historical security incidents, and mitigation strategies.
(2)
Reasoning-Supported Threat Analysis: By enhancing the reasoning capabilities of the model through the integration of reasoning processes within fine-tuned data, it enables it to better correlate various data segments. Subsequently, it can be utilized to assist in complex tasks such as penetration testing and vulnerability assessments.

The model accepts natural language queries or structured prompts that describe satellite security scenarios, attack techniques, or defensive mechanisms. For standard question-answering tasks, it returns concise, factual answers directly supported by the surveyed literature. For reasoning-oriented tasks, the output is augmented with step-by-step reasoning chains (denoted as thought) and traceable references (denoted as references), thereby enhancing interpretability and auditability.
These defined tasks align with operational requirements in satellite network security, where rapid access to specialized knowledge and structured threat reasoning can significantly improve situational awareness, accelerate response planning, and support decision-making in dynamic and resource-constrained environments. To ensure clarity, the scope and functionality of SatSec are explicitly defined as follows:
Table A1. Scope and functionality of SatSec.
AspectDefinition for SatSec
Core TasksIntelligent Question Answering (QA): Providing accurate, context-aware responses to technical queries on satellite network security.
Reasoning-Supported Threat Analysis: For analyzing and addressing complex tasks, emphasizing the intricate interconnections between multiple tasks and steps.
InputNatural language queries or structured prompts describing security scenarios, attack techniques, or defenses.
OutputFor QA: Concise, factual answers.
For Threat Analysis: Answers augmented with step-by-step reasoning chains (thought) and traceable references (references).
Evaluation GoalTo outperform general-purpose LLMs and the base model in domain-specific accuracy and relevance.

Appendix A.2. Dataset Construction and Curation

The dataset underpinning SatSec is derived from three complementary sources to ensure both cybersecurity breadth and satellite-specific depth:
(1)
Satellite Cybersecurity Literature—The 189 references surveyed in this paper, cover physical-, network-, and user-layer threats and defenses.
(2)
MITRE ATT&CK ICS—Authoritative threat behavior knowledge base, which provides generalized attack tactics and techniques relevant to cyber–physical systems.
(3)
Sat-ATT&CK Knowledge Matrix—The satellite-specific threat taxonomy proposed in Section 3.4, which defines over 100 attack techniques across 12 core tactics tailored to satellite networks. This matrix enriches the corpus with structured, satellite-centric adversarial knowledge, ensuring that SatSec can accurately model and reason about attack chains unique to the space domain.

Appendix A.2.1. Question–Answer Pair Generation

We employed a structured prompt engineering approach using the DeepSeek model to automatically generate QA pairs from the curated corpus. The process was designed to create two distinct dataset types for different fine-tuning objectives:
Instruction Tuning Dataset: Each entry contains a question and a direct answer. This dataset aims to enhance the model’s recall of factual domain knowledge.
Reasoning Tuning Dataset: Each entry contains four fields: question, step-by-step thought (the reasoning process), answer, and references (source citations). This dataset, constructed using Chain-of-Thought (CoT) prompting and cross-question correlation, aims to improve the model’s logical reasoning and analytical capabilities within the domain.
This two-pronged dataset construction ensures SatSec is trained for both knowledge retrieval and complex threat analysis tasks.

Appendix A.2.2. Data Statistics

Both the instruction tuning dataset and the reasoning tuning dataset contain 22,542 question–answer pairs. Among them, 14,832 pairs are generated from satellite network cybersecurity-related literature, and 7710 pairs are derived from MITRE ATT&CK ICS. The token statistics of the datasets are shown in Table A2 and Table A3.
Table A2. Instruction tuning dataset.
CategoryQuestion–Answer PairsTokensAverage Tokens
Satellite Cybersecurity Literature14,832743,26350
ATT&CK ICS7710430,94856
Total22,5421,174,21152
Table A3. Reasoning tuning dataset.
CategoryQuestion–Answer PairsTokensAverage Tokens
Satellite Cybersecurity Literature14,8322,124,995143
ATT&CK ICS77101,436,350186
Total22,5423,561,345158

Appendix A.3. Model Fine-Tuning

To achieve precise domain adaptation for satellite cybersecurity, we fine-tuned the Qwen3-8b base model using LoRA. LoRA is a parameter-efficient fine-tuning method. It freezes the pre-trained model weights W 0 R d × k , injects trainable rank-decomposed matrices into each layer of the Transformer architecture, and constrains updates through the low-rank decomposition W 0 + Δ W = W 0 + B A . This reduces the number of trainable parameters for downstream tasks [187], where B R d × r , A R r × k , and r m i n   ( d , k ) .

Appendix A.4. Evaluation and Comparative Analysis

Appendix A.4.1. Evaluation Metrics

Two statistical evaluation methods are adopted to assess the fine-tuned model: ROUGE (Recall-Oriented Understudy for Gisting Evaluation) [188] and BLEU (Bilingual Evaluation Understudy) [189], covering a total of 7 evaluation indicators. ROUGE is based on Recall and evaluates the semantic alignment degree of the model’s generated answers by comparing the overlap of n-gram (ROUGE-N) and longest common subsequence (ROUGE-L) between the model’s outputs and the standard answers in the test set. BLEU assesses the grammatical and semantic accuracy of the generated answers by matching the proportion of consecutive words of different lengths (BLEU-1/2/3/4). These metrics collectively evaluate the model’s ability to produce factually consistent and linguistically appropriate responses—a critical requirement for security-critical applications.
These automated metrics provide a standardized, quantitative measure of the model’s ability to generate text that is factually aligned (ROUGE) and fluent/accurate (BLEU) compared to the expert-curated ground truth, which is crucial for assessing utility in a technical domain.

Appendix A.4.2. Baseline Models

Given the absence of open-source vertical LLMs for satellite security, we compare SatSec against two representative baselines:
(1)
General-purpose LLM: DeepSeek-V3, a state-of-the-art open-source model with broad knowledge but no satellite-specific adaptation.
(2)
Base model without fine-tuning: Qwen3-8b-origin, to isolate the contribution of our domain adaptation.
This selection allows us to isolate the contribution of our domain-specific fine-tuning (by comparing Qwen3-8b-origin vs. SatSec) and to demonstrate the necessity of domain adaptation by comparing against a powerful but general-purpose model (DeepSeek-V3).

Appendix A.4.3. Results and Discussion

As summarized in Figure A2 and Figure A3, the fine-tuned SatSec model demonstrates superior performance across all evaluated ROUGE and BLEU metrics when compared to the base Qwen3-8b-origin model. This comprehensive improvement confirms that the domain-specific fine-tuning effectively enhances the model’s capability to understand and generate accurate, relevant content for satellite network cybersecurity. Notably, both the pre-fine-tuning and post-fine-tuning versions of the Qwen3-8b model consistently achieved higher scores than the general-purpose DeepSeek-V3 model across all indicators.
Figure A2. Distribution of metrics for each model.
Aerospace 13 00249 g0a2
Figure A3. Comparison of metrics among models.
Aerospace 13 00249 g0a3
A qualitative analysis of the output reveals a primary reason for this discrepancy: DeepSeek-V3, likely due to its built-in safety and sensitivity policies, frequently responds with refusals (e.g., “I cannot answer this question”) when queried about detailed attack techniques or sensitive satellite security scenarios. This behavior leads to a significant drop in textual similarity metrics against the ground-truth, fact-based answers in our test set. In contrast, the Qwen3-8b-based models, fine-tuned on the specialized dataset, provide substantive technical answers, resulting in higher metric scores and demonstrating greater practical utility for domain-specific technical discourse.
Quantitative Validation and Practical Implications: The superior performance of SatSec over its base model quantitatively validates our domain-adaptation approach. More importantly, the significant outperformance of both specialized models over DeepSeek-V3 underscores the necessity of domain-specific tuning for professional security applications. This translates directly to practical utility, where access to unfiltered, technical knowledge is paramount.
The results also reveal complementary strengths: the instruction-tuned model excels in direct factual retrieval, while the reasoning-tuned model shows enhanced capability for structured, analytical tasks (e.g., mapping attack chains). This demonstrates that targeted fine-tuning can tailor a general LLM into a specialized tool for different stages of the security analysis lifecycle. Importantly, the reasoning-tuned SatSec can directly leverage the Sat-ATT&CK taxonomy: when presented with a description of an adversary’s actions, it can infer the corresponding tactics and techniques, reconstruct the attack chain, and suggest potential defensive countermeasures—effectively operationalizing the threat knowledge matrix.
In practical terms, the instruction-tuned model serves as a robust tool for efficient domain knowledge retrieval and technical Q&A, directly supporting research and operational tasks. The reasoning-tuned model, with its chain-of-thought capability, shows clear utility for more complex analytical work, such as assisting in penetration testing by reconstructing attack logic or identifying vulnerabilities within layered defenses. Therefore, SatSec is positioned not merely as a conversational agent but as a foundational component for developing AI-augmented security analysis systems specifically designed to address the unique constraints and evolving threat landscape of satellite networks.

References

  1. Zhou, D.; Sheng, M.; Wu, J.; Li, J.; Han, Z. Gateway placement in integrated satellite–terrestrial networks: Supporting communications and Internet of Remote Things. IEEE Internet Things J. 2021, 9, 4421–4434. [Google Scholar] [CrossRef] [Scilit]
  2. Fang, X.; Feng, W.; Wei, T.; Chen, Y.; Ge, N.; Wang, C. 5G embraces satellites for 6G ubiquitous IoT: Basic models for integrated satellite terrestrial networks. IEEE Internet Things J. 2021, 8, 14399–14417. [Google Scholar] [CrossRef] [Scilit]
  3. Jung, D.H.; Im, G.; Ryu, J.G.; Park, S.; Yu, H.; Choi, J. Satellite clustering for non-terrestrial networks: Concept, architectures, and applications. IEEE Veh. Technol. Mag. 2023, 18, 29–37. [Google Scholar] [CrossRef] [Scilit]
  4. Maral, G.; Bousquet, M.; Sun, Z. Satellite Communications Systems: Systems, Techniques and Technology; John Wiley & Sons: Hoboken, NJ, USA, 2020. [Google Scholar]
  5. Zong, L.; Qiao, D.; Wang, H.; Bai, Y. Sustainable cross-regional transmission control for the industrial augmented intelligence of things. IEEE Trans. Ind. Inform. 2023, 19, 10214–10223. [Google Scholar] [CrossRef] [Scilit]
  6. Ying, M.; Chen, X.; Shao, X. Exploiting tensor-based Bayesian learning for massive grant-free random access in LEO satellite Internet of Things. IEEE Trans. Commun. 2022, 71, 1141–1152. [Google Scholar] [CrossRef] [Scilit]
  7. Guo, H.; Li, J.; Liu, J.; Tian, N.; Kato, N. A survey on space-air-ground-sea integrated network security in 6G. IEEE Commun. Surv. Tutor. 2021, 24, 53–87. [Google Scholar] [CrossRef] [Scilit]
  8. Boschetti, N.; Gordon, N.G.; Falco, G. Space cybersecurity lessons learned from the viasat cyberattack. In Proceedings of the ASCEND 2022, Las Vegas, NV, USA, 24–26 October 2022; p. 4380. [Google Scholar]
  9. Carlo, A.; Obergfaell, K. Cyber attacks on critical infrastructures and satellite communications. Int. J. Crit. Infrastruct. Prot. 2024, 46, 100701. [Google Scholar] [CrossRef] [Scilit]
  10. Willbold, J.; Schloegel, M.; Bisping, R.; Strohmeier, M.; Holz, T.; Lenders, V. Vsaster: Uncovering inherent security issues in current vsat system practices. In Proceedings of the 17th ACM Conference on Security and Privacy in Wireless and Mobile Networks, Seoul, Republic of Korea, 27–29 May 2024; pp. 288–299. [Google Scholar]
  11. Zhang, P.; Guo, Q. Physical layer security in cognitive terrestrial–satellite networks with LEO relaying. Comput. Netw. 2025, 258, 111033. [Google Scholar] [CrossRef] [Scilit]
  12. Jang, G.; You, B.; Jung, H. A survey on physical layer security schemes in satellite networks. In Proceedings of the 2022 13th International Conference on Information and Communication Technology Convergence (ICTC), Jeju Island, Republic of Korea, 19–21 October 2022; pp. 1213–1215. [Google Scholar]
  13. Li, B.; Fei, Z.; Zhou, C.; Zhang, Y. Physical-layer security in space information networks: A survey. IEEE Internet Things J. 2019, 7, 33–52. [Google Scholar] [CrossRef] [Scilit]
  14. Sharif, S.; Zeadally, S.; Ejaz, W. Space-aerial-ground-sea integrated networks: Resource optimization and challenges in 6G. J. Netw. Comput. Appl. 2023, 215, 103647. [Google Scholar] [CrossRef] [Scilit]
  15. Tang, F.; Mao, B.; Kawamoto, Y.; Kato, N. Survey on machine learning for intelligent end-to-end communication toward 6G: From network access, routing to traffic control and streaming adaption. IEEE Commun. Surv. Tutor. 2021, 23, 1578–1598. [Google Scholar] [CrossRef] [Scilit]
  16. Yue, P.; An, J.; Zhang, J.; Ye, J.; Pan, G.; Wang, S. Low earth orbit satellite security and reliability: Issues, solutions, and the road ahead. IEEE Commun. Surv. Tutor. 2023, 25, 1604–1652. [Google Scholar] [CrossRef] [Scilit]
  17. Tedeschi, P.; Sciancalepore, S.; Di Pietro, R. Satellite-based communications security: A survey of threats, solutions, and research challenges. Comput. Netw. 2022, 216, 109246. [Google Scholar] [CrossRef] [Scilit]
  18. Du, X.; Shu, N.; Liu, C.; Yang, F.; Ma, T.; Liu, Y. Overview of Security Issues and Defense Technologies for Low Earth Orbit Satellite Network. J. Electron. Inf. Technol. 2025, 47, 1609–1622. [Google Scholar]
  19. Bakhsh, Z.M.; Omid, Y.; Chen, G.; Kayhan, F.; Ma, Y.; Tafazolli, R. Multi-Satellite MIMO Systems for Direct Satellite-to-Device Communications: A Survey. IEEE Commun. Surv. Tutor. 2025, 27, 1536–1564. [Google Scholar] [CrossRef] [Scilit]
  20. Chen, D.; Wei, C.; Song, Z.; Zhang, J.; Ye, Y.; Wei, B.; Ji, X.; Wang, S.; Sun, X. A GEO-Management Based Degraded Satellite Avoidance Routing Algorithm for GEO-LEO Satellite Network. In Proceedings of the 2025 5th International Conference on Intelligent Communications and Computing (ICICC), Nanjing, China, 14–16 March 2025; pp. 14–18. [Google Scholar]
  21. Corici, M.; Caus, M.; Artiga, X.; Alessandro, G.; Benjamin, B.; Cola, T. Transforming 5g mega-constellation communications: A self-organized network architecture perspective. IEEE Access 2025, 13, 14770–14788. [Google Scholar] [CrossRef] [Scilit]
  22. Meng, L.; Sun, X.; Hu, Y.; Gao, B.; Sun, G.; Mu, W. Reinforcement learning task scheduling algorithm for satellite on-orbit processing. Syst. Eng. Electron. 2025, 47, 1917–1929. [Google Scholar]
  23. Giambene, G.; Kota, S.; Pillai, P. Satellite-5G integration: A network perspective. IEEE Netw. 2018, 32, 25–31. [Google Scholar] [CrossRef] [Scilit]
  24. Van der Watt, R.; Slay, J. Modification of the Lockheed Martin Cyber Kill Chain (LMCKC) for cyber security breaches concerning Low Earth Orbit (LEO) Satellites. In Proceedings of the 16th International Conference on Cyber Warfare and Security, Cookeville, TN, USA, 25–26 February 2021; pp. 473–476. [Google Scholar]
  25. Geetha, A.; Keerthika, V.; Raj, D.M.D. Cybersecurity kill chain in outer space and cyberspace security. In Cyber Space and Outer Space Security; River Publishers: Gistrup, Denmark, 2024; pp. 81–95. [Google Scholar]
  26. Salim, S.; Moustafa, N.; Reisslein, M. Cybersecurity of satellite communications systems: A comprehensive survey of the space, ground, and links segments. IEEE Commun. Surv. Tutor. 2024, 27, 372–425. [Google Scholar] [CrossRef] [Scilit]
  27. Frøseth, E.K. Threat Modeling in Satellite Communications for Maritime Operations. Ph.D. Thesis, NTNU Norwegian University of Science and Technology, Trondheim, Norway, 2024. [Google Scholar]
  28. SPARTA. Available online: https://sparta.aerospace.org/ (accessed on 21 July 2025).
  29. Peled, R.; Aizikovich, E.; Habler, E.; Elovici, Y.; Shabtai, A. Evaluating the security of satellite systems. arXiv 2023, arXiv:2312.01330. [Google Scholar] [CrossRef] [Scilit]
  30. Ear, E.; Remy, J.L.C.; Xu, S. Characterizing cyber attacks against space systems with missing data: Framework and case study. In Proceedings of the 2023 IEEE Conference on Communications and Network Security (CNS), Orlando, FL, USA, 2–4 October 2023; pp. 1–9. [Google Scholar]
  31. Hamill-Stewart, J.; Rashid, A. Threats against satellite ground infrastructure: A retrospective analysis of sophisticated attacks. In Proceedings of the 2024 Workshop on Security of Space and Satellite Systems, San Diego, CA, USA, 1 March 2024; p. 1. [Google Scholar]
  32. Al-Sada, B.; Sadighian, A.; Oligeri, G. MITRE ATT&CK: State of the art and way forward. ACM Comput. Surv. 2024, 57, 1–37. [Google Scholar] [CrossRef] [Scilit]
  33. Geng, R.; Ye, N.; Liu, J.; Zhu, D. Towards channel state information based coding to enhance security in satellite communication. J. Syst. Archit. 2021, 112, 101843. [Google Scholar] [CrossRef] [Scilit]
  34. Dong, F.; Wang, W.; Li, X.; Liu, F.; Chen, S.; Hanzo, L. Joint beamforming design for dual-functional MIMO radar and communication systems guaranteeing physical layer security. IEEE Trans. Green Commun. Netw. 2023, 7, 537–549. [Google Scholar] [CrossRef] [Scilit]
  35. Lu, Z.; Jiao, Y. Efficiently all-digital code tracking for band-limited DSSS systems. IEEE Commun. Lett. 2022, 27, 686–690. [Google Scholar] [CrossRef] [Scilit]
  36. Wang, F.; Cui, W.; Tian, J. A superresolution multipath estimation algorithm for DSSS systems. IEEE Trans. Aerosp. Electron. Syst. 2022, 59, 109–124. [Google Scholar] [CrossRef] [Scilit]
  37. Teng, T.; Xie, Y.; Kang, J. Security analysis of NOMA integrated satellite–terrestrial relay networks with analog beamforming. Comput. Netw. 2025, 264, 111263. [Google Scholar] [CrossRef] [Scilit]
  38. Cassano, L.; Di Mascio, S.; Palumbo, A.; Menicucci, A.; Furano, G.; Bianchi, G.; Ottavi, M. Is risc-v ready for space? a security perspective. In Proceedings of the 2022 IEEE International Symposium on Defect and Fault Tolerance in VLSI and Nanotechnology Systems (DFT), Austin, TX, USA, 19–21 October 2022; pp. 1–6. [Google Scholar]
  39. Pirayesh, H.; Zeng, H. Jamming attacks and anti-jamming strategies in wireless networks: A comprehensive survey. IEEE Commun. Surv. Tutor. 2022, 24, 767–809. [Google Scholar] [CrossRef] [Scilit]
  40. Song, C.; Wang, Y.; Jin, G.; Wang, Y.; Dong, Q.; Wang, B.; Zhou, L.; Liu, P.; Wu, Y. A novel jamming method against SAR using nonlinear frequency modulation waveform with very high sidelobes. Remote Sens. 2022, 14, 5370. [Google Scholar] [CrossRef] [Scilit]
  41. Yu, F. Research on Distributed Radar Jamming Suppression Algorithm and Simulation Implementation. Ph.D. Thesis, University of Electronic Science and Technology of China, Chengdu, China, 2023. [Google Scholar]
  42. Zou, Y.; Zhu, J.; Wang, X.; Hanzo, L. A survey on wireless security: Technical challenges, recent advances, and future trends. Proc. IEEE 2016, 104, 1727–1765. [Google Scholar] [CrossRef] [Scilit]
  43. Shi, Y.; Huang, H.; Ma, Z. An Inter-Pulse Non-Coherent Jamming Technology Against SAR Based on Stepped Time-Delay. In Proceedings of the 2021 7th International Conference on Systems and Informatics (ICSAI), Chongqing, China, 13–15 November 2021; pp. 1–5. [Google Scholar]
  44. Li, N.; Cheng, D.; Lu, P.; Shu, G.; Guo, Z. Smart Jamming Against SAR Based on Nonlinear Frequency-Modulated Signal. IEEE Trans. Aerosp. Electron. Syst. 2023, 59, 3588–3605. [Google Scholar] [CrossRef] [Scilit]
  45. Wang, Y.; Jin, G.; Song, C.; Lu, P.; Han, S.; Lv, J.; Zhang, Y.; Wu, D.; Zhu, D. Parameterized and Large-Dynamic-Range 2-D Precise Controllable SAR Jamming: Characterization, Modeling, and Analysis. IEEE Trans. Geosci. Remote Sens. 2023, 61, 5209416. [Google Scholar] [CrossRef] [Scilit]
  46. Zhao, Y. Research on Satellite Navigation Anti-Spoofing Technology Based on the Coprime Array Antenna. Ph.D. Thesis, Harbin Institute of Technology, Harbin, China, 2024. [Google Scholar]
  47. Broumandan, A.; Jafarnia-Jahromi, A.; Dehghanian, V.; Nielsen, J.; Lachapelle, G. GNSS spoofing detection in handheld receivers based on signal spatial correlation. In Proceedings of the 2012 IEEE/ION Position, Location and Navigation Symposium, Myrtle Beach, SC, USA, 23–26 April 2012; pp. 479–487. [Google Scholar]
  48. Yang, K.; Ma, F.; Ran, D.; Ye, W.; Li, G. Fast Generation of Deceptive Jamming Signal Against Spaceborne SAR Based on Spatial Frequency Domain Interpolation. IEEE Trans. Geosci. Remote Sens. 2022, 60, 4701015. [Google Scholar] [CrossRef] [Scilit]
  49. Yang, K.; Ye, W.; Wu, X.; Ma, F.; Li, G. Fast Generation of Deceptive Jamming Signal Against Space-Borne SAR. IEEE J. Sel. Top. Appl. Earth Obs. Remote Sens. 2020, 13, 5580–5596. [Google Scholar] [CrossRef] [Scilit]
  50. Liu, Y.; Wang, W.; Pan, X.; Fu, Q.; Wang, G. Inverse Omega-K Algorithm for the Electromagnetic Deception of Synthetic Aperture Radar. IEEE J. Sel. Top. Appl. Earth Obs. Remote Sens. 2016, 9, 3037–3049. [Google Scholar] [CrossRef] [Scilit]
  51. Borio, D.; Gioia, C. GNSS interference mitigation: A measurement and position domain assessment. Navigation 2021, 68, 93–114. [Google Scholar] [CrossRef] [Scilit]
  52. Katsoulis, G. Satellite telecommunications in the military: Advantages, limitations and the networking challenge. In Applications of Mathematics and Informatics in Science and Engineering; Springer: Cham, Switzerland, 2014; pp. 243–263. [Google Scholar]
  53. Li, H. Research on Reliability Routing Algorithm of LEO Satellite Network. Ph.D. Thesis, University of Electronic Science and Technology of China, Chengdu, China, 2021. [Google Scholar]
  54. Pan, T.; Huang, T.; Li, X.; Chen, Y.; Xue, W.; Liu, Y. OPSPF: Orbit prediction shortest path first routing for resilient LEO satellite networks. In Proceedings of the ICC 2019—2019 IEEE International Conference on Communications (ICC), Shanghai, China, 20–24 May 2019; pp. 1–6. [Google Scholar]
  55. Ruan, G.; Pan, T.; Lu, C.; Luo, Z.; Wang, H.; Zhang, J.; Shen, Y.; Huang, T.; Liu, Y. Lightweight route flooding via flooding topology pruning for leo satellite networks. In Proceedings of the ICC 2022—IEEE International Conference on Communications, Seoul, Republic of Korea, 16–20 May 2022; pp. 1149–1154. [Google Scholar]
  56. Wang, Y.; Attebury, G.; Ramamurthy, B. A survey of security issues in wireless sensor networks. IEEE Commun. Surv. Tutor. 2006, 8, 2–23. [Google Scholar] [CrossRef] [Scilit]
  57. Yang, Z. Research on Dynamic Routing Algorithm and Security Technology of Large-scale Low Earth Orbit Constellation. Ph.D. Thesis, University of Chinese Academy of Sciences, Beijing, China, 2023. [Google Scholar]
  58. Langton, M.T.; Yang, Z.; Pan, G.; Zhang, H.; Luo, G.; Yang, H. Security Challenges in Satellite Ground Stations and their Risk Mitigation Techniques. In Proceedings of the 2024 13th International Conference on Communications, Circuits and Systems (ICCCAS), Xiamen, China, 26–28 July 2024; pp. 508–513. [Google Scholar]
  59. Li, J.; Zhang, L.; Zhao, Y.; Zhai, L. SpiderSec: A Model-Based Systems Engineering Framework for Satellite Internet Security. In Proceedings of the IEEE INFOCOM 2025—IEEE Conference on Computer Communications Workshops (INFOCOM WKSHPS), London, UK, 12–15 May 2025; pp. 1–6. [Google Scholar]
  60. Saunders, N.; Thummala, R.; Falco, G. Space Cybersecurity Incident Response Framework: A Viasat Case Study. In Proceedings of the 2025 IEEE Aerospace Conference, Big Sky, MT, USA, 1–8 March 2025; pp. 1–15. [Google Scholar]
  61. Zhang, L.; Du, Y.; Sun, Z. Modeling and analysis of cascading failures in LEO satellite networks. IEEE Trans. Netw. Sci. Eng. 2023, 11, 807–822. [Google Scholar] [CrossRef] [Scilit]
  62. de Azúa, J.A.R.; Calveras, A.; Camps, A. Internet of satellites (IoSat): Analysis of network models and routing protocol requirements. IEEE Access 2018, 6, 20390–20411. [Google Scholar] [CrossRef] [Scilit]
  63. Pavur, J.; Moser, D.; Strohmeier, M.; Lenders, V.; Martinovic, I. A tale of sea and sky on the security of maritime VSAT communications. In Proceedings of the 2020 IEEE Symposium on Security and Privacy (SP), San Francisco, CA, USA, 18–21 May 2020; pp. 1384–1400. [Google Scholar]
  64. Giuliari, G.; Ciussani, T.; Perrig, A.; Singla, A. ICARUS: Attacking low earth orbit satellite networks. In Proceedings of the 2021 USENIX Annual Technical Conference (USENIX ATC 21), Virtual, 14–16 July 2021; pp. 317–331. [Google Scholar]
  65. Nguyen, T.N.; Tran, D.H.; Van Chien, T.; Phan, V.D.; Voznak, M.; Chatzinotas, S. Security and reliability analysis of satellite-terrestrial multirelay networks with imperfect CSI. IEEE Syst. J. 2022, 17, 2824–2835. [Google Scholar] [CrossRef] [Scilit]
  66. Di, A.O.; Ruisheng, S.; Lan, L.; Yueming, L. On the large-scale traffic DDoS threat of space backbone network. In Proceedings of the 2019 IEEE 5th Intl Conference on Big Data Security on Cloud (BigDataSecurity), IEEE Intl Conference on High Performance and Smart Computing,(HPSC) and IEEE Intl Conference on Intelligent Data and Security (IDS), Washington, DC, USA, 27–29 May 2019; pp. 192–194. [Google Scholar]
  67. Hayat, R.F.; Aurangzeb, S.; Aleem, M.; Srivastava, G.; Lin, J.C.W. ML-DDoS: A blockchain-based multilevel DDoS mitigation mechanism for IoT environments. IEEE Trans. Eng. Manag. 2022, 71, 12605–12618. [Google Scholar] [CrossRef] [Scilit]
  68. Zhang, Y.; Wang, Y.; Hu, Y.; Lin, Z.; Zhai, Y.; Wang, L.; Zhao, Q.; Wen, K.; Kang, L. Security performance analysis of LEO satellite constellation networks under DDoS attack. Sensors 2022, 22, 7286. [Google Scholar] [CrossRef] [Scilit] [PubMed]
  69. Manulis, M.; Bridges, C.P.; Harrison, R.; Sekar, V.; Davis, A. Cyber security in new space: Analysis of threats, key enabling technologies and challenges. Int. J. Inf. Secur. 2021, 20, 287–311. [Google Scholar]
  70. Perez-Neira, A.I.; Vazquez, M.A.; Shankar, M.R.B.; Maleki, S.; Chatzinotas, S. Signal processing for high-throughput satellites: Challenges in new interference-limited scenarios. IEEE Signal Process. Mag. 2019, 36, 112–131. [Google Scholar]
  71. Li, Q.; Zhou, Q.; Sun, H.; Yang, F.; Li, S.; Cao, C. Research on DDoS attack technology for satellite communication network. In Proceedings of the 2025 IEEE 2nd International Conference on Electronics, Communications and Intelligent Science (ECIS), Changsha, China, 24–26 January 2025; pp. 1–5. [Google Scholar]
  72. Cui, H.; Zhang, J.; Geng, Y.; Xiao, Z.; Sun, T.; Zhang, N.; Liu, J.; Wu, Q.; Cao, X. Space-air-ground integrated network (SAGIN) for 6G: Requirements, architecture and challenges. China Commun. 2022, 19, 90–108. [Google Scholar] [CrossRef] [Scilit]
  73. Lan, W. Privacy-Preserving and Security Sensitive Task Offloading in Satellite–Terrestrial Networks. Ph.D. Thesis, Guangzhou University, Guangzhou, China, 2024. [Google Scholar]
  74. He, X.; Liu, J.; Jin, R.; Dai, H. Privacy-aware offloading in mobile-edge computing. In Proceedings of the GLOBECOM 2017—2017 IEEE Global Communications Conference, Singapore, 4–8 December 2017; pp. 1–6. [Google Scholar]
  75. Chen, T.; Zhang, J.; Leng, C.; Ran, Y. Design and Verification of Security Communication Mechanism for Satellite Network System Based on Blockchain. Aerosp. Shanghai 2024, 41, 88. [Google Scholar] [CrossRef]
  76. Xu, J. Research on Trusted Identity Authentication Mechanism in Space-Earth Integrated Network. Ph.D. Thesis, Beijing University of Posts and Telecommunications, Beijing, China, 2019. [Google Scholar]
  77. Zhao, W.; Zhang, A.; Li, J.; Wu, X.; Liu, Y. Analysis and design of an authentication protocol for space information network. In Proceedings of the MILCOM 2016—2016 IEEE Military Communications Conference, Baltimore, MD, USA, 1–3 November 2016; pp. 43–48. [Google Scholar]
  78. Jiang, C.; Wang, X.; Wang, J.; Chen, H.H.; Ren, Y. Security in space information networks. IEEE Commun. Mag. 2015, 53, 82–88. [Google Scholar] [CrossRef] [Scilit]
  79. Tang, X.; Feng, J.; Zhang, B.; Huan, H.; Ren, Y.; Li, H. Satellite Telemetry Track and Command Ground Station Identification Method Based on RF Fingerprint. J. Electron. Inf. Technol. 2023, 45, 2554–2560. [Google Scholar]
  80. Li, X.; Liu, X.; Zhang, J.; Wang, J.; Li, S.; Yuan, Z.; Pan, G. Secrecy performance for a multi-relaying SIMO-satellite/MISO-FSO network. J. Frankl. Inst. 2025, 362, 107544. [Google Scholar]
  81. Xia, H.; Han, S.; Li, C. Max-min fair optimization in RSMA-assisted secure communications with artificial noise. IEEE Commun. Lett. 2023, 27, 3181–3184. [Google Scholar] [CrossRef] [Scilit]
  82. Gu, Y.; Wu, Z.; Yin, Z.; Zhang, X. The secrecy capacity optimization artificial noise: A new type of artificial noise for secure communication in MIMO system. IEEE Access 2019, 7, 58353–58360. [Google Scholar] [CrossRef] [Scilit]
  83. Li, W.; Ghogho, M.; Chen, B.; Xiong, C. Secure communication via sending artificial noise by the receiver: Outage secrecy capacity/region analysis. IEEE Commun. Lett. 2012, 16, 1628–1631. [Google Scholar] [CrossRef] [Scilit]
  84. Zhang, P.; Guo, Q. Security-reliability analysis in uplink cognitive satellite-terrestrial networks with LEO relaying. Comput. Netw. 2025, 264, 111272. [Google Scholar] [CrossRef] [Scilit]
  85. Chen, J.; Liang, Y.C.; Pei, Y.; Guo, H. Intelligent reflecting surface: A programmable wireless environment for physical layer security. IEEE Access 2019, 7, 82599–82612. [Google Scholar] [CrossRef] [Scilit]
  86. Jiang, C.; Zhang, C.; Mu, L.; Zhang, Z.; Ge, J. Aerial RIS-aided physical layer security design for satellite communication among similar channels. J. Inf. Intell. 2023, 1, 54–67. [Google Scholar] [CrossRef] [Scilit]
  87. Huang, C.; Zappone, A.; Debbah, M.; Yuen, C. Achievable rate maximization by passive intelligent mirrors. In Proceedings of the 2018 IEEE International Conference on Acoustics, Speech and Signal Processing (ICASSP), Calgary, AB, Canada, 15–20 April 2018; pp. 3714–3718. [Google Scholar]
  88. Arora, K.; Singh, J.; Randhawa, Y.S. A survey on channel coding techniques for 5G wireless networks. J. Telecommun. Syst. 2020, 73, 637–663. [Google Scholar] [CrossRef] [Scilit]
  89. Zhang, Y.; Wang, P.; Liu, T.; Guo, L.; Li, Y.; Wang, W. Performance analysis of a LDPC coded OAM-based UCA FSO system exploring linear equalization with channel estimation over atmospheric turbulence. Opt. Express 2018, 26, 22182–22196. [Google Scholar] [CrossRef] [Scilit]
  90. Shahbaz, S.; Akhbari, B.; Asvadi, R. LDPC codes over Gaussian multiple access wiretap channel. IET Commun. 2018, 12, 962–969. [Google Scholar] [CrossRef] [Scilit]
  91. Qin, L. Research on Anti-Jamming Methods for GNSS Signal Acquisition Under Complex Interference Environment. Ph.D. Thesis, Harbin Engineering University, Harbin, China, 2018. [Google Scholar]
  92. Yan, D.; Ni, S. Overview of anti-jamming technologies for satellite navigation systems. In Proceedings of the 2022 IEEE 6th Information Technology and Mechatronics Engineering Conference (ITOEC), Chongqing, China, 4–6 March 2022; pp. 118–124. [Google Scholar]
  93. Chien, Y.R. Design of GPS anti-jamming systems using adaptive notch filters. IEEE Syst. J. 2013, 9, 451–460. [Google Scholar] [CrossRef] [Scilit]
  94. Rezaei, M.J.; Abedi, M.; Mosavi, M.R. New GPS anti-jamming system based on multiple short-time Fourier transform. IET Radar Sonar Navig. 2016, 10, 807–815. [Google Scholar] [CrossRef] [Scilit]
  95. Liwei, Z.; Pinqun, J. Adaptive Threshold Suppression of Narrowband Interference Based on Wavelet Packet Transform. Data Acquis. Process. 2013, 28, 843–847. [Google Scholar]
  96. Zhang, Z.; Zhu, C.; Feng, Q.; Yuan, N. Application of power inversion algorithm in Beidou anti-jamming antenna system. Electron. Des. Eng. 2012, 20, 42–49. [Google Scholar]
  97. Zhou, W. Research and FPGA Implementation of BD Navigation Adaptive Anti-Jamming Algorithm. Ph.D. Thesis, University of Electronic Science and Technology of China, Chengdu, China, 2020. [Google Scholar]
  98. Kong, Q.; Liu, J.; Qu, X.; Chen, B.; Bao, H.; Xu, L. Security in data-driven satellite applications: An overview and new perspectives. Signal Process. 2025, 228, 109755. [Google Scholar]
  99. Tao, H.; Li, H.; Lu, M. A method of detections’ fusion for GNSS anti-spoofing. Sensors 2016, 16, 2187. [Google Scholar] [CrossRef] [Scilit] [PubMed]
  100. Rothmaier, F.; Chen, Y.; Lo, S.; Walter, T. GNSS spoofing detection through spatial processing. Navigation 2021, 68, 243–258. [Google Scholar]
  101. Chu, F.; Li, H.; Lu, M. A GNSS spoofing detection method based on the consistency of measured and calculated carrier Dopplers. In Proceedings of the ION 2017 Pacific PNT Meeting, Honolulu, HI, USA, 1–4 May 2017; pp. 832–841. [Google Scholar]
  102. Tu, J.; Zhan, X.; Chen, M.; Gao, H.; Chen, Y. GNSS intermediate spoofing detection via dual-peak in frequency domain and relative velocity residuals. IET Radar Sonar Navig. 2020, 14, 439–447. [Google Scholar] [CrossRef] [Scilit]
  103. Broumandan, A.; Jafarnia-Jahromi, A.; Lachapelle, G.; Ioannides, R.T. An approach to discriminate GNSS spoofing from multipath fading. In Proceedings of the 2016 8th ESA Workshop on Satellite Navigation Technologies and European Workshop on GNSS Signals and Signal Processing (NAVITEC), Noordwijk, The Netherlands, 14–16 December 2016; pp. 1–10. [Google Scholar]
  104. Wesson, K.D.; Gross, J.N.; Humphreys, T.E.; Evans, B.L. GNSS signal authentication via power and distortion monitoring. IEEE Trans. Aerosp. Electron. Syst. 2017, 54, 739–754. [Google Scholar] [CrossRef] [Scilit]
  105. Henarejos, P.; Vázquez, M.Á.; Pérez-Neira, A.I. Deep learning for experimental hybrid terrestrial and satellite interference management. In Proceedings of the 2019 IEEE 20th International Workshop on Signal Processing Advances in Wireless Communications (SPAWC), Cannes, France, 2–5 July 2019; pp. 1–5. [Google Scholar]
  106. Al Homssi, B.; Dakic, K.; Wang, K.; Alpcan, T.; Allen, B.; Boyce, R. Artificial intelligence techniques for next-generation massive satellite networks. IEEE Commun. Mag. 2023, 62, 66–72. [Google Scholar] [CrossRef] [Scilit]
  107. Wigchert, J.; Sciancalepore, S.; Oligeri, G. Detection of aerial spoofing attacks to LEO satellite systems via deep learning. Comput. Netw. 2025, 269, 111408. [Google Scholar] [CrossRef] [Scilit]
  108. Tian, X.D.; Hu, Z.H. A branch-and-price method for a two-echelon location routing problem with recommended satellites. Comput. Ind. Eng. 2023, 184, 109593. [Google Scholar]
  109. Du, P.; Li, J.; Bai, W.; Sheng, M.; Zhou, D. Dual location area based distributed location management for hybrid LEO/MEO mega satellite networks. IEEE Trans. Veh. Technol. 2022, 72, 2307–2321. [Google Scholar] [CrossRef] [Scilit]
  110. Yan, F.; Wang, Z.; Zhang, S.; Meng, Q.; Luo, H. Logic path identified hierarchical routing for large-scale leo satellite networks. IEEE Trans. Netw. Sci. Eng. 2024, 11, 3731–3746. [Google Scholar] [CrossRef] [Scilit]
  111. Mao, B.; Zhou, X.; Liu, J.; Kato, N. On an intelligent hierarchical routing strategy for ultra-dense free space optical low earth orbit satellite networks. IEEE J. Sel. Areas Commun. 2024, 42, 1219–1230. [Google Scholar] [CrossRef] [Scilit]
  112. Farrea, K.A.; Baig, Z.; Doss, R.R.M.; Liu, D. Provably secure optimal homomorphic signcryption for satellite-based internet of things. Comput. Netw. 2024, 250, 110516. [Google Scholar] [CrossRef] [Scilit]
  113. Elias, E.P.; Santhanavijayan, A. Secure Satellite Image Transmission with Dynamic Encipherment and AuthKeX Protocol. Adv. Space Res. 2025, 75, 8319–8333. [Google Scholar] [CrossRef] [Scilit]
  114. Chen, Y.J.; Wang, L.C.; Wang, S. Stochastic blockchain for IoT data integrity. IEEE Trans. Netw. Sci. Eng. 2018, 7, 373–384. [Google Scholar] [CrossRef] [Scilit]
  115. Yuan, P.; Li, B.; Zhang, Y.; Wu, J.; Zheng, H.; Wang, C. A PUF-based lightweight broadcast authentication protocol for multi-server systems using blockchain. In Proceedings of the 2021 IEEE 6th International Conference on Signal and Image Processing (ICSIP), Nanjing, China, 22–24 October 2021; pp. 1035–1041. [Google Scholar]
  116. Du, R.; Chen, T.; Tian, J.; Shang, T. StarCross: Redactable blockchain-based secure and lightweight data sharing framework for satellite-based IoT. Comput. Netw. 2024, 253, 110718. [Google Scholar] [CrossRef] [Scilit]
  117. Fu, P.; Wu, J.; Lin, X.; Shen, A. ZTEI: Zero-trust and edge intelligence empowered continuous authentication for satellite networks. In Proceedings of the GLOBECOM 2022—2022 IEEE Global Communications Conference, Rio de Janeiro, Brazil, 4–8 December 2022; pp. 2376–2381. [Google Scholar]
  118. Liu, Y.; Zhang, A.; Li, J.; Wu, J. An anonymous distributed key management system based on CL-PKC for space information network. In Proceedings of the 2016 IEEE International Conference on Communications (ICC), Kuala Lumpur, Malaysia, 22–27 May 2016; pp. 1–7. [Google Scholar]
  119. Farrea, K.A.; Baig, Z.; Doss, R.; Liu, D. Zero trust-based authentication for Inter-Satellite Links in NextGen Low Earth Orbit networks. Ad Hoc Netw. 2025, 174, 103817. [Google Scholar] [CrossRef] [Scilit]
  120. Choudhari, C.; Niture, D. Disruption tolerant network (dtn) for space communication: An overview. In Proceedings of the 2022 IEEE 7th International Conference for Convergence in Technology (I2CT), Mumbai, India, 7–9 April 2022; pp. 1–5. [Google Scholar]
  121. Zhang, L.; Guo, Z.; Su, H.; Zhao, W. CAAST: Optimizing data communications in satellite networks through Cache and Anycast. Comput. Netw. 2025, 259, 111066. [Google Scholar] [CrossRef] [Scilit]
  122. Liu, S.; Wu, D.; Zhang, L. CGAN BeiDou satellite short-message-encryption scheme using ship PVT. Remote Sens. 2022, 15, 171. [Google Scholar] [CrossRef] [Scilit]
  123. Jeon, S.; Kwak, J.; Choi, J.P. Cross-layer encryption of CFB-AES-TURBO for advanced satellite data transmission security. IEEE Trans. Aerosp. Electron. Syst. 2021, 58, 2192–2205. [Google Scholar] [CrossRef] [Scilit]
  124. Zhao, C.; He, X.; Li, Y.; Zeng, B. Chaotic encryption algorithm for satellite images based on novel RNA coding. Adv. Space Res. 2025, 75, 8334–8356. [Google Scholar] [CrossRef] [Scilit]
  125. Yang, Y.; Dong, H.; Chen, L.; Li, Z.; Xia, C. LWARX: Lightweight ARX white-box cipher for satellite communications. J. King Saud Univ. Comput. Inf. Sci. 2024, 36, 102032. [Google Scholar] [CrossRef] [Scilit]
  126. Yuan, H.; Wang, Y.; Tang, G. Orbital Satellite Communication Encryption Algorithm Based on Elliptic Curve Cryptography Algorithm. Procedia Comput. Sci. 2025, 259, 873–879. [Google Scholar] [CrossRef] [Scilit]
  127. Howarth, M.P.; Iyengar, S.; Sun, Z.; Cruickshank, H. Dynamics of key management in secure satellite multicast. IEEE J. Sel. Areas Commun. 2004, 22, 308–319. [Google Scholar] [CrossRef]
  128. Roy-Chowdhury, A.; Baras, J.S.; Hadjitheodosiou, M.; Papademetriou, S. Security issues in hybrid networks with a satellite component. IEEE Wirel. Commun. 2005, 12, 50–61. [Google Scholar] [CrossRef]
  129. Jiao, W.; Hu, J.; Lu, Z.; Xu, J. A threshold value-based group key management for satellite network. In Proceedings of the 2013 IEEE Third International Conference on Information Science and Technology (ICIST), Yangzhou, China, 23–25 March 2013; pp. 718–721. [Google Scholar]
  130. Wang, Z.; Du, X.; Sun, Y. Group key management scheme based on proxy re-cryptography for near-space network. In Proceedings of the 2011 International Conference on Network Computing and Information Security, Guilin, China, 14–15 May 2011; pp. 52–56. [Google Scholar]
  131. Sun, Y.; Ma, H. Satellite multi-group key management. In Proceedings of the 2013 IEEE Third International Conference on Information Science and Technology (ICIST), Yangzhou, China, 23–25 March 2013; pp. 894–899. [Google Scholar]
  132. Casaril, F.; Galletta, L. Securing SatCom user segment: A study on cybersecurity challenges in view of IRIS2. Comput. Secur. 2024, 140, 103799. [Google Scholar] [CrossRef] [Scilit]
  133. Thumbur, G.; Gayathri, N.B.; Reddy, P.V.; Rahman, M.Z.U. Efficient pairing-free identity-based ADS-B authentication scheme with batch verification. IEEE Trans. Aerosp. Electron. Syst. 2019, 55, 2473–2486. [Google Scholar] [CrossRef] [Scilit]
  134. Meng, W.; Xue, K.; Xu, J.; Hong, J.; Yu, N. Low-latency authentication against satellite compromising for space information network. In Proceedings of the 2018 IEEE 15th International Conference on Mobile Ad Hoc and Sensor Systems (MASS), Chengdu, China, 9–12 October 2018; pp. 237–244. [Google Scholar]
  135. Yang, Q.; Xue, K.; Xu, J.; Wang, J.; Li, F.; Yu, N. AnFRA: Anonymous and fast roaming authentication for space information network. IEEE Trans. Inf. Forensics Secur. 2018, 14, 486–497. [Google Scholar] [CrossRef] [Scilit]
  136. Nakamoto, S. Bitcoin: A Peer-to-Peer Electronic Cash System. 2008. Available online: https://bitcoin.org/bitcoin.pdf (accessed on 1 March 2026).
  137. Wang, Y.; Su, Z.; Ni, J.; Zhang, N.; Shen, X. Blockchain-empowered space-air-ground integrated networks: Opportunities, challenges, and solutions. IEEE Commun. Surv. Tutor. 2021, 24, 160–209. [Google Scholar] [CrossRef] [Scilit]
  138. Yu, X.; Xie, Y.; Xu, Q.; Xu, Z.; Xiong, R. Secure data sharing for cross-domain industrial iot based on consortium blockchain. In Proceedings of the 2023 26th International Conference on Computer Supported Cooperative Work in Design (CSCWD), Rio de Janeiro, Brazil, 24–26 May 2023; pp. 1508–1513. [Google Scholar]
  139. Zhang, S.; Yan, Z.; Liang, W.; Li, K.C.; Di Martino, B. BCAE: A blockchain-based cross domain authentication scheme for edge computing. IEEE Internet Things J. 2024, 11, 24035–24048. [Google Scholar] [CrossRef] [Scilit]
  140. Driouch, O.; Bah, S.; Guennoun, Z. CANSat-IDS: An adaptive distributed Intrusion Detection System for satellites, based on combined classification of CAN traffic. Comput. Secur. 2024, 146, 104033. [Google Scholar] [CrossRef] [Scilit]
  141. Xie, N.; Yuan, Q.; Xie, L.; Di, X. SAGIN-ID: A rapid intrusion detection method for space-air-ground integrated network based on smart contracts. Comput. Electr. Eng. 2025, 123, 110084. [Google Scholar] [CrossRef] [Scilit]
  142. Rahman, M.M.; Al Shakil, S.; Mustakim, M.R. A survey on intrusion detection system in IoT networks. Cyber Secur. Appl. 2025, 3, 100082. [Google Scholar] [CrossRef] [Scilit]
  143. Li, K.; Zhou, H.; Tu, Z.; Wang, W.; Zhang, H. Distributed network intrusion detection system in satellite-terrestrial integrated networks using federated learning. IEEE Access 2020, 8, 214852–214865. [Google Scholar] [CrossRef] [Scilit]
  144. Guo, W.; Xu, J.; Pei, Y.; Yin, L.; Jiang, C.; Ge, N. A distributed collaborative entrance defense framework against DDoS attacks on satellite Internet. IEEE Internet Things J. 2022, 9, 15497–15510. [Google Scholar] [CrossRef] [Scilit]
  145. Huang, C.; Wang, D.; Hou, R. Satellite security transmission optimization algorithm for joint anomaly detection. Acta Electron. Sin. 2025, 53, 1460–1468. [Google Scholar] [CrossRef]
  146. Zhang, M.; Liu, P.; Wang, Z.; Zhang, X.; Chen, Z.; Huang, R.; Su, W. Anomaly detection method for in-orbit satellite using ARX-SVR model. Spacecr. Eng. 2025, 34, 18–25. [Google Scholar]
  147. Cui, B. Satellite Time Series Data Based on Long Short Term Autoencoder Anomaly Detection. Ph.D. Thesis, Beijing University of Posts and Telecommunications, Beijing, China, 2024. [Google Scholar]
  148. Yang, J.; Meng, X.; Chen, T.; Zhi, J.; Li, H. Anomaly detection of spacecraft based on the telemetry data correlation. Chin. J. Sci. Instrum. 2018, 39, 24–33. [Google Scholar]
  149. Nassar, B.; Hussein, W.; Mokhtar, M. Space telemetry anomaly detection based on statistical PCA algorithm. Int. J. Electron. Commun. Eng. 2015, 9, 637–645. [Google Scholar]
  150. Hu, J. Research on Deep Learning Based Method for Aircraft Telemetry Time Series Data Anomaly Detection and Forecasting. Ph.D. Thesis, Xi’an University of Technology, Xi’an, China, 2019. [Google Scholar]
  151. Luo, H. Research on the Gas Path Anomaly Detection of Civil Aero-Engine Based on Deep Features. Ph.D. Thesis, Harbin Institute of Technology, Harbin, China, 2020. [Google Scholar]
  152. Dong, J.; Pang, J.; Peng, Y.; Liu, D. Spacecraft telemetry data anomaly detection method based on ensemble LSTM. Chin. J. Sci. Instrum. 2019, 40, 22–29. [Google Scholar]
  153. Djihane, M.; Abdelkrim, H.; Mohamed, B. Hybrid FSO/RF satellite-air-ground integration network for reliable ITS communication in desert environments. Opt. Commun. 2025, 591, 132071. [Google Scholar] [CrossRef] [Scilit]
  154. Xue, K.; Meng, W.; Li, S.; Wei, D.S.L.; Zhou, H.; Yu, N. A secure and efficient access and handover authentication protocol for Internet of Things in space information networks. IEEE Internet Things J. 2019, 6, 5485–5499. [Google Scholar] [CrossRef] [Scilit]
  155. Liu, Y.; Ni, L.; Peng, M. A secure and efficient authentication protocol for satellite-terrestrial networks. IEEE Internet Things J. 2022, 10, 5810–5822. [Google Scholar] [CrossRef] [Scilit]
  156. Kong, Q.; Lu, R.; Yin, F. Achieving efficient and secure handover in LEO constellation-assisted beyond 5G networks. IEEE Open J. Commun. Soc. 2021, 3, 641–653. [Google Scholar] [CrossRef] [Scilit]
  157. Zhang, Y.; Zhao, K.; Li, W. A Resilient Routing Algorithm for Handling $ K $-Link/Node Failure in Inclined LEO Megaconstellations. IEEE Trans. Aerosp. Electron. Syst. 2024, 60, 4876–4886. [Google Scholar] [CrossRef] [Scilit]
  158. Ji, B.; Cao, X.; Yang, K. Research and simulation of satellite networking technology based on link detection mechanism. Electron. Inf. Warf. Technol. 2022, 37, 90–96. [Google Scholar]
  159. Cui, R.; Xu, Z.; Zhi, R. A Quick-response Link Destruction Routing Algorithm for LEO Satellite Constellation. Telecommun. Eng. 2023, 63, 1165–1172. [Google Scholar]
  160. Ning, Y.; Yi, L.; Zhao, Y.; Qi, K.; Wang, H.; Rahman, S.; Zhang, J. Load-balancing routing algorithms for service congestion avoidance in LEO optical satellite networks. J. Opt. Commun. Netw. 2023, 15, 1038–1049. [Google Scholar] [CrossRef] [Scilit]
  161. Zhu, Y. Intelligent congestion control of data transmission in low Earth orbit satellite networks based on reinforcement learning: Analysis and optimization. Inf. Sci. 2025, 694, 121692. [Google Scholar] [CrossRef] [Scilit]
  162. Bie, Y.; Li, X.; Tian, Y.; Wang, Y. Self-Similar Traffic Prediction Algorithm for Satellite Network Based on Dual Decomposition and Neural Network. Comput. Netw. 2025, 269, 111432. [Google Scholar] [CrossRef] [Scilit]
  163. Wu, Z.; Jing, G.; Ding, J.; Zhao, X. SCMA-Q-learning with overload control for random access in LEO satellite mMTC networks. Phys. Commun. 2025, 69, 102584. [Google Scholar] [CrossRef] [Scilit]
  164. Qi, H.; Guo, Y.; Hou, D.; Xing, Z.; Ren, W.; Cong, L.; Di, X. SDN-based dynamic multi-path routing strategy for satellite networks. Future Gener. Comput. Syst. 2022, 133, 254–265. [Google Scholar] [CrossRef] [Scilit]
  165. Liu, Q.; Li, X.; Ji, H.; Zhang, H. Multi-path routing algorithm with joint optimization of load-balancing for cluster-based LEO satellite networks. In Proceedings of the 2023 8th IEEE International Conference on Network Intelligence and Digital Content (IC-NIDC), Beijing, China, 17–19 November 2023; pp. 264–268. [Google Scholar]
  166. Zeng, G.; Zhan, Y.; Pan, X. Failure-tolerant and low-latency telecommand in mega-constellations: The redundant multi-path routing. IEEE Access 2021, 9, 34975–34985. [Google Scholar] [CrossRef] [Scilit]
  167. Jianjun, B.; Xicheng, L.; Zexin, L.; Wei, P. Compact explicit multi-path routing for LEO satellite networks. In Proceedings of the HPSR. 2005 Workshop on High Performance Switching and Routing, Hong Kong, China, 12–14 May 2005; pp. 386–390. [Google Scholar]
  168. Wang, C.; Ren, Z.; Cheng, W.; Zhang, H. CDMR: Effective computing-dependent multi-path routing strategies in satellite and terrestrial integrated networks. IEEE Trans. Netw. Sci. Eng. 2022, 9, 3715–3730. [Google Scholar] [CrossRef] [Scilit]
  169. Tian, Y.; Dai, W.; Wu, X.; Shi, L.; Zhao, Y.; Zou, W. Development of Intelligent Fault Early Warning System for Substation Integrating Satellite Remote Sensing and Ground Monitoring. In Proceedings of the 2024 3rd International Conference on Data Analytics, Computing and Artificial Intelligence (ICDACAI), Zakopane, Poland, 19–21 July 2024; pp. 819–824. [Google Scholar]
  170. Chen, J.; Wang, Y.; Liu, C.; Yang, Y. Regional Adaptive Synthetic Sampling-Based Early Warning Algorithm for Satellite Voice Quality. In Proceedings of the 2025 2nd International Conference on Digital Media, Communication and Information Systems (DMCIS), Nanjing, China, 10–12 January 2025; pp. 146–150. [Google Scholar]
  171. Gao, Y.; Qiu, S.; Liu, M.; Zhang, L.; Cao, X. Fault Warning of Satellite Momentum Wheels with a Lightweight Transformer Improved by FastDTW. IEEE/CAA J. Autom. Sin. 2025, 12, 539–549. [Google Scholar] [CrossRef] [Scilit]
  172. Yang, F.; Cai, J.; Liu, J.; Wang, J.; Wang, M.; Guo, F. Spacecraft Operation Process Monitoring and Fault Diagnosis System. In Proceedings of the 2022 4th International Academic Exchange Conference on Science and Technology Innovation (IAECST), Guangzhou, China, 9–11 December 2022; pp. 1605–1609. [Google Scholar]
  173. Nanduri, A.; Sherry, L. Anomaly detection in aircraft data using Recurrent Neural Networks (RNN). In Proceedings of the 2016 Integrated Communications Navigation and Surveillance (ICNS), Herndon, VA, USA, 19–21 April 2016; pp. 5C2-1–5C2-8. [Google Scholar]
  174. Chen, Z.; Shang, L.; Zhou, M. A FP-CNN method for aircraft fault prognostics. In Proceedings of the 2018 3rd International Conference on Automation, Mechanical Control and Computational Engineering (AMCCE 2018), Shenyang, China, 18–20 May 2018; pp. 571–579. [Google Scholar]
  175. Li, L.; Gao, Y.M.; Wu, Z.H.; Zhang, X.B. Small Fault Detection for Satellite Attitude Control System Actuators with Stacked Autoencoder Network. In IOP Conference Series: Materials Science and Engineering; IOP Publishing: Bristol, UK, 2018; Volume 449, p. 012016. [Google Scholar]
  176. Tagawa, T.; Tadokoro, Y.; Yairi, T. Structured denoising autoencoder for fault detection and analysis. In Proceedings of the Asian Conference on Machine Learning, Hong Kong, China, 20–22 November 2015; pp. 96–111. [Google Scholar]
  177. Liu, Y.; Yin, C.; Hu, D.; Zhao, T.; Liang, Y. Communication satellite fault detection based on recurrent neural network. Comput. Sci. 2020, 47, 227–232. [Google Scholar]
  178. Jothilakshmi, K.; Usha, G.; Bose, S. A framework of cross layer based anomaly intrusion detection and self healing model for manet. In Proceedings of the 2013 International Conference on Recent Trends in Information Technology (ICRTIT), Chennai, India, 25–27 July 2013; pp. 429–433. [Google Scholar]
  179. Aryai, S.; Binu, G.S. Cross layer approach for detection and prevention of Sinkhole Attack using a mobile agent. In Proceedings of the 2017 2nd International Conference on Communication and Electronics Systems (ICCES), Coimbatore, India, 19–20 October 2017; pp. 359–365. [Google Scholar]
  180. Xu, N.; Sun, Y.; Huang, B.; Yu, J. An energy-efficient cross-layer framework for security in wireless sensor networks. In Proceedings of the 2011 Fourth International Symposium on Knowledge Acquisition and Modeling, Wuhan, China, 15–16 October 2011; pp. 121–124. [Google Scholar]
  181. Vinayagam, J.K.; Balaswamy, C.H.; Soundararajan, K. Adopting cross layer approach for detecting and segregating malicious nodes in MANET. In Proceedings of the 2017 International Conference on Signal Processing and Communication (ICSPC), Coimbatore, India, 28–29 July 2017; pp. 457–461. [Google Scholar]
  182. Chen, Q.; Giambene, G.; Yang, L.; Fan, C.; Chen, X. Analysis of inter-satellite link paths for LEO mega-constellation networks. IEEE Trans. Veh. Technol. 2021, 70, 2743–2755. [Google Scholar] [CrossRef] [Scilit]
  183. Kang, M.; Park, S.; Lee, Y. A survey on satellite communication system security. Sensors 2024, 24, 2897. [Google Scholar] [CrossRef] [Scilit]
  184. Lin, X.; Xiong, G.; Gou, G.; Li, Z.; Shi, J.; Yu, J. Et-bert: A contextualized datagram representation with pre-training transformers for encrypted traffic classification. In Proceedings of the ACM Web Conference 2022, Virtual Event, 25–29 April 2022; pp. 633–642. [Google Scholar]
  185. Ahmad, S.Z.; Qamar, F. A hybrid AI based framework for enhancing security in satellite based IoT networks using high performance computing architecture. Sci. Rep. 2024, 14, 30695. [Google Scholar] [CrossRef] [Scilit]
  186. Mythili, S.; Nidhya, R.; Kumar, R.A. AI-Driven Security Framework for Enhanced Threat Detection in Mobile Satellite Networks. ICTACT J. Commun. Technol. 2025, 16. [Google Scholar] [CrossRef] [Scilit]
  187. Hu, J.; Shen, Y.; Wallis, P.; Allen-Zhu, Z.; Li, Y.; Wang, S.; Wang, L.; Chen, W. LoRA: Low-Rank Adaptation of Large Language Models. arXiv 2021, arXiv:2106.09685. [Google Scholar]
  188. Lin, C. ROUGE: A Package for Automatic Evaluation of Summaries. In Text Summarization Branches Out; Association for Computational Linguistics: Barcelona, Spain, 2004; pp. 74–81. [Google Scholar]
  189. Papineni, K.; Roukos, S.; Ward, T.; Zhu, W.J. BLEU: A Method for Automatic Evaluation of Machine Translation. In Proceedings of the 40th Annual Meeting of the Association for Computational Linguistics, Philadelphia, PA, USA, 7–12 July 2002; pp. 311–318. [Google Scholar]
Figure 1. Bubble chart of reference distribution across three key domains of satellite networks (2004–2025). Bubble size and numbers denote reference counts per category/year, indicating research popularity.
Aerospace 13 00249 g001
Figure 2. Schematic diagram of the layered threat and defense framework for satellite networks.
Aerospace 13 00249 g002
Figure 3. Composition of the satellite networks.
Aerospace 13 00249 g003
Figure 4. Mapping of satellite network threats to the CIA+A security objectives.
Aerospace 13 00249 g004
Figure 5. Schematic diagram of typical threats at the physical layer and network layer of satellite networks.
Aerospace 13 00249 g005
Figure 6. Distribution of attack techniques and threat levels under different tactical modules. (a) Tactics of Initial Access, Execution, Persistence, and Privilege Escalation; (b) Tactics of Evasion, Discovery, Lateral Movement, and Collection; (c) Tactics of Command and Control, Inhibit Response Function, Impair Process Control, and Impact. (Note: Light blue = Physical-Layer Threats, light yellow = Network-Layer Threats, light green = User-Layer Threats).
Aerospace 13 00249 g006aAerospace 13 00249 g006b
Figure 7. Intelligent detection framework for anti-spoofing jamming at the physical layer.
Aerospace 13 00249 g007
Table 1. Comparison of satellite network security threat modeling and classification research.
ReferenceModeling MethodMain InnovationsLimitations
[24]Cyber Kill ChainAnalyzes LEO satellite attacks using the Cyber Kill ChainInsufficient detail in hierarchical division and description
[25]Cyber Kill ChainAnalyzes the kill chain phases under the space frameworkInadequate consideration of satellite uniqueness
[26]STRIDEAssociates satellite communication threats with STRIDELimitations in threat classification and strategy formulation
[27]STRIDEModels maritime satellite communication using STRIDEInsufficient depth and breadth in threat identification and analysis
[28]MITRE ATT&CKRealizes standardized classification of spacecraft threatsLacks fine-grained description of satellite-specific attack techniques
[29]MITRE ATT&CKDefines space tactics such as “orbital maneuver jamming”Incomplete coverage of satellite-specific techniques
[30]MITRE ATT&CKExtrapolates attack chains based on ATT&CKFails to fully consider the unique threats of the space segment
[31]MITRE ATT&CKAnalyzes APT group attack cases on satellite ground segmentsDoes not adapt to the space segment scenario of satellites
Table 2. Hierarchical threats and impacts of satellite networks.
Threat LayerAttack TypeAttack ProcessImpact
Physical LayerEavesdroppingIntercept air-interface-transmitted signals to parse communication content or key parametersData leakage, key leakage
Power Suppression JammingTransmit high-power signals to cover legitimate signalsCommunication interruption, service unavailability
Spoofing JammingForge signals similar to legitimate ones to make the receiver misjudge the signal sourceNavigation deviation, control errors
Network LayerRouting AttackTamper with routing protocols or forge routing updatesPath hijacking, increased latency, communication interruption
Message TamperingIllegally modify data packets or instructions being transmittedInvalid instructions, configuration errors, system paralysis
Denial-of-Service (DoS) AttackSend a large number of illegal data packets to exhaust on-board or ground resourcesService interruption, resource exhaustion, increased latency
User LayerPrivacy LeakageCapture user privacy information (e.g., location, behavior data)Exposure of user privacy, tracking of behavior trajectories
Identity SpoofingForge identity credentials to impersonate legitimate users or nodesUnauthorized access, unauthorized operations, service abuse
Table 3. Mapping of the Viasat attack chain to Sat-ATT&CK tactics and techniques.
Attack PhaseSat-ATT&CK TacticSat-ATT&CK TechniqueAttack Process Description
1Initial AccessUnauthorized Configuration Interface IntrusionAttackers exploited an unpatched Fortinet VPN appliance (CVE-2022-23305) at a Viasat ground gateway to gain unauthorized access to the modem management network.
2Initial AccessGround Station Uplink Signal Injection AttackUsing compromised ground station credentials, adversaries injected malicious telecommands via the Ka-band forward uplink to target Surfbeam2 modems.
3ExecutionMalicious Code InjectionA wiper malware dubbed “AcidRain” was delivered as a seemingly legitimate firmware update and executed on the victim modems, erasing flash memory and rendering the devices inoperable.
4PersistenceFirmware Update HijackingBy subverting the firmware update mechanism, the attackers ensured that the malicious code survived modem reboots and could potentially be reinstalled if recovery was attempted.
5Privilege EscalationVulnerability ExploitationThe attack leveraged multiple known and zero-day vulnerabilities (e.g., VPN flaws, weak access controls) to elevate privileges from modem management servers to the broader satellite ground infrastructure.
6ImpactDDoS Attack to Paralyze ServicesThe wiper attack caused a large-scale denial-of-service for tens of thousands of modems. Additionally, downstream impacts included the disruption of approximately 11 GW of wind power generation in Germany due to SCADA system dependencies on the affected SATCOM links.
Table 4. Comparison of hierarchical protection technologies for satellite networks.
Protection LayerProtection TechnologyTargeted AttackTypeProtection Process/MechanismAdvantagesDisadvantagesDeployment Readiness
Physical LayerBeamformingEavesdroppingConcentrates signal energy in the direction of legitimate receivers to reduce sidelobe leakageNo interference required; suitable for multi-user scenariosRelies on channel state informationOperational
Artificial Noise (AN) InjectionInjects noise to reduce the signal-to-noise ratio (SNR) of eavesdropping channelsHigh targeting and effectivenessMay interfere with non-target nodes; high-power consumptionSimulated/Demonstrated
Reconfigurable Intelligent Surface (RIS)Directs reflected interference signals to create nulls at eavesdroppersImproves interference efficiency in similar channel environmentsRequires high-precision phase controlConcept/Simulated
Secure CodingIntegrates channel state information for adaptive coding, prioritizing decoding for legitimate linksEnsures security from an information-theoretic perspectiveHigh complexity of encoding and decodingSimulated
Single-Antenna TechnologyPower Suppression JammingSuppresses interfering frequency points through time-domain/transform-domain filteringLow cost; suitable for narrowband interferenceLimited anti-jamming capabilityOperational
Array Antenna TechnologyAdaptively adjusts weights to form pattern nulls aligned with interferenceStrong spatial resolution; high suppression depthComplex hardware; high costOperational
Signal Feature DetectionSpoofing JammingAnalyzes anomalies in physical features such as signal correlation functions and powerSimple implementation; high real-time performanceIneffective against high-fidelity spoofing signalsOperational
Measurement Domain Consistency CheckVerifies the logical consistency between parameters such as Doppler shift, power, and code phaseDistinguishes spoofing from multipathRelies on prior thresholds or statistical modelsDemonstrated
Intelligent DetectionExtracts raw signal features and identifies abnormal patterns via trained modelsAdapts to complex environments; detects concealed spoofingRelies on data quality and computing powerSimulated/Demonstrated
Network LayerLocation Routing/Hierarchical RoutingRouting AttacksIsolates routing domains based on satellite positions or logical grouping to limit attack propagationImproves routing efficiency and reliabilityHigh management overheadOperational (in part)
Encryption and Hash VerificationMessage TamperingUses cryptographic algorithms to ensure data integrity and confidentialityMature technology; fundamental security supportIntroduces computational and communication overheadOperational
Blockchain-Based Evidence StorageUses distributed ledgers to record operation logs for tamper-proofing and traceabilityDecentralized; high credibilityHigh latency; high storage overheadConcept/Simulated
Zero-Trust AuthenticationContinuously verifies identity and permissions, combining physical parameters for dynamic authenticationStrong dynamic adaptability; low overheadComplex system constructionSimulated/Demonstrated
Caching and Resource OptimizationDoS/DDoS AttacksAlleviates resource-exhaustion attacks through redundant storage and load balancingImproves system redundancy and availabilityOnly mitigates, not eliminates, attacksOperational
User LayerData Encryption AlgorithmsPrivacy LeakageUses lightweight cryptographic algorithms to protect data transmission and storage securityResource-friendly; suitable for on-board environmentsStill incurs significant computational overheadOperational
Key Management MechanismsDesigns hierarchical, cross-domain key negotiation and update mechanismsSupports forward and backward securityHigh update overhead during high-frequency handoversOperational
Encrypted Identity AuthenticationIdentity SpoofingImplements end-to-end identity verification by combining cryptography and behavioral featuresFundamentally defends against impersonationRelies on the security of key managementOperational
Blockchain-Based Identity ManagementDistributively stores and verifies identity information to prevent tampering and forgeryDecentralized, transparent and credibleBottlenecks in throughput and latencyConcept/Simulated
Note: Deployment Readiness levels: Concept—theoretical proposal only; Simulated—evaluated in software simulation; Demonstrated—validated in relevant environment (e.g., HITL testbed, tech demo); Operational—deployed on operational systems (e.g., GPS, Starlink).
Disclaimer/Publisher’s Note: The statements, opinions and data contained in all publications are solely those of the individual author(s) and contributor(s) and not of MDPI and/or the editor(s). MDPI and/or the editor(s) disclaim responsibility for any injury to people or property resulting from any ideas, methods, instructions or products referred to in the content.