Review

Security Challenges in Open Banking: A Systematic Review and Conceptualisation of a Tri-Dimensional Security Framework


NOVA Information Management School (NOVA IMS), Universidade Nova de Lisboa, 1070-312 Lisbon, Portugal
*
Author to whom correspondence should be addressed.
FinTech 2026, 5(2), 38; https://doi.org/10.3390/fintech5020038
Submission received: 6 February 2026 / Revised: 12 March 2026 / Accepted: 10 April 2026 / Published: 2 May 2026
(This article belongs to the Special Issue Fintech Innovations: Transforming the Financial Landscape)

Abstract

Background: Open banking (OB) is rapidly transforming financial ecosystems by enabling controlled data sharing among multiple actors through application programming interfaces (APIs). While this transformation promises innovation and competition, it also introduces complex security challenges that extend beyond purely technical considerations. Despite growing attention in academic and professional domains, existing reviews provide limited integration of security concerns with global adoption patterns and cross regional variation. Methods: This systematic review analyses empirical and conceptual research on security in OB published between 1999 and 2025, capturing early digital banking studies that later informed the development of OB. The literature is structured into three distinct phases: foundational digital banking developments, regulatory formalisation of OB frameworks, and post-implementation expansion of OB ecosystems. A comprehensive search was conducted across major academic databases and scholarly portals, complemented by relevant regulatory and policy sources. Following duplicate removal, title and abstract screening, full-text eligibility assessment, and methodological quality appraisal, 117 studies were retained for qualitative synthesis. Results: The findings reveal recurring security challenges arising from the interaction between technological infrastructures, regulatory frameworks, and user behaviour within OB ecosystems. Technical safeguards such as APIs, strong customer authentication, and encryption are necessary but insufficient when they are misaligned with regulatory implementation and user behaviour. Behavioural factors, including trust, consent understanding, and security-related decision making, play a central role in shaping ecosystem resilience. Based on this synthesis, the study develops a tri-dimensional security framework integrating technological, regulatory, and behavioural dimensions. The bibliometric analysis of 117 studies reveals that technological security dominates the literature (58%), followed by regulatory governance (44%) and behavioural dimensions (42%). However, only 17.9% of studies integrate all three dimensions simultaneously. APIs and authentication mechanisms represent the most frequent technological terms, while PSD2 and GDPR dominate regulatory discourse. Trust and decision-making are the most recurrent behavioural constructs. The relatively low proportion of fully integrated studies confirms a structural fragmentation within OB security research, thereby empirically justifying the proposed tri-dimensional framework. Chronologically, early studies (1999–2015) predominantly focused on technical security mechanisms and regulatory compliance, whereas more recent research (2020–2025) increasingly highlights the interplay between regulatory frameworks and user behaviour, suggesting a shift towards a more holistic understanding of security within OB adoption. Conclusions: This systematic review concludes that integrating technological, regulatory, and behavioural perspectives advances a more comprehensive understanding of security in OB ecosystems. The proposed tri-dimensional security framework provides a structured foundation for future research and supports policy-relevant and practice-oriented security design.
JEL Classification:
G21; G28; O33; D91; K24; L86

1. Introduction

Open banking (OB) has emerged as a transformative development in the financial services sector, redefining how financial data are accessed, exchanged, and leveraged by market participants. By relying on standardised application programming interfaces (APIs), OB technology enables authorised third-party providers (TPPs) to connect with consumer account data under controlled conditions [1,2]. This model brings innovation, enhanced customer experience, and intensified competition, while promoting transparency and interoperability across financial systems. As a result, OB has accelerated the shift towards a more data-intensive and inclusive financial ecosystem, but the growing interconnection among financial actors introduces heightened concerns related to security and privacy [3,4,5]. The circulation of sensitive financial information across multiple entities significantly expands the potential attack surface, increasing exposure to threats such as fraud, phishing, and identity-related abuses. These risks directly challenge trust, which remains a foundational element of digital financial services.
Although the OB ecosystem has attracted substantial attention from both academic researchers and industry practitioners, existing studies often examine security-related issues in isolation. Prior research tends to focus separately on technical safeguards, regulatory and governance arrangements, or user behaviour factors, with limited integration across these perspectives [6,7]. This fragmented approach limits the understanding of how security emerges within OB systems, where technological infrastructure, institutional frameworks, and human behaviour interact continuously [8]. There remains a lack of comprehensive reviews that explain how these dimensions jointly shape security effectiveness, adoption outcomes, and the development of security-oriented financial technologies within OB environments.
The objective of this systematic review is to synthesise existing empirical research on security in OB by examining how technological mechanisms, regulatory frameworks, and behavioural factors jointly shape security outcomes across different regional contexts. A further objective is to develop an integrated tri-dimensional security framework that captures the interdependencies among these dimensions and informs future research and policy design.
This study addresses this limitation by providing a systematic synthesis of empirical research published between 1999, when OB concepts first appeared in academic discourse, and 2025, a period reflecting its wider global diffusion. By covering this extended timeframe, the review captures both the conceptual foundations and the evolving practical implementation of OB across regions. Particular attention is given to the interplay between security-focused technological solutions, regulatory and policy frameworks, and behavioural dynamics that shape the resilience of financial ecosystems. In this respect, the review highlights the importance of user intentions and perceptions in shaping secure digital practices [9,10], while also considering how cultural and regional conditions affect cognitive patterns and security-related behaviour.
The study develops a tri-dimensional security framework that conceptualises technological mechanisms, regulatory structures, and human behaviour as interdependent components of OB security [11]. By explicitly incorporating behavioural dynamics alongside technical and institutional considerations, the framework reflects the practical realities of security management and user decision-making in OB adoption across different regional contexts [12]. This integrative perspective offers a more context-sensitive and human-centred foundation for designing and governing effective security solutions within OB ecosystems.
The review reveals recurring patterns as well as persistent gaps within the existing literature, demonstrating how security challenges and responses vary across technological, regulatory, and behavioural domains. The paper proposes directions for future research and provides implications aimed at supporting informed decision making by scholars, industry practitioners, and policymakers engaged in OB initiatives.
The remainder of the paper is structured as follows. Section 2 introduces the conceptual foundations of OB and the theoretical perspectives that underpin the review. Section 3 describes the methodology employed for data selection, screening, and analysis. Section 4 synthesises prior empirical research, including studies on APIs, FinTech, SecTech, RegTech, and market dynamics. Section 5 presents the empirical results, including the development of the tri-dimensional security perspective, supported by a keyword co-occurrence visualisation that demonstrates how the three dimensions emerge from the bibliometric analysis. Finally, Section 6 discusses the comparative findings, outlines the limitations of existing studies, identifies opportunities for future research, and concludes the paper.

2. Open Banking Concept

OB represents a significant financial technology development that alters competitive dynamics within the banking sector by enabling controlled data sharing between incumbent institutions and new market entrants. By allowing customers to authorise third-party providers to access account information or initiate transactions on their behalf, OB challenges the traditional dominance of banks over financial data while expanding opportunities for innovation and service diversification [13,14]. This model relies on customer consent as a central governance mechanism and positions data portability as a driver of competition and consumer empowerment.
At the technological level, OB is operationalised through APIs that function as secure channels for data exchange between financial institutions and authorised TPPs. These interfaces support interoperability and enable the development of new financial products and services across institutional boundaries [15,16]. Existing OB research spans regulatory design, adoption dynamics, business models, and technological architecture; this review focuses specifically on security challenges arising from increased interconnectivity and data sharing.

2.1. APIs and Their Role in Open Banking

APIs constitute the foundational technological infrastructure of OB. They provide standardised mechanisms through which financial institutions and authorised TPPs exchange data in a controlled and auditable manner. Regulatory authorities play a central role in defining OB standards, ensuring that APIs operate consistently across jurisdictions while meeting baseline requirements for security, interoperability, and reliability [17,18]. Through these interfaces, customers are able to grant informed and granular consent, allowing external applications to connect with their bank accounts for specific purposes.
API-enabled services support a wide range of use cases, including expenditure analysis, product recommendations, and the aggregation of financial information from multiple accounts into unified platforms. This represents a marked departure from traditional banking models, in which customer data are typically confined within institutional silos and accessed primarily through proprietary channels [19,20,21]. OB, by contrast, redistributes control over financial data, enabling customers to selectively share information with trusted third parties under predefined conditions.
Prior to the widespread adoption of API-based access mechanisms, TPPs frequently relied on screen scraping techniques to obtain account information. This practice required customers to disclose their login credentials, creating vulnerabilities related to credential compromise, limited transparency, and weak control over data usage [1,15,22]. The transition towards API-based architectures reflects an effort to address these shortcomings by introducing stronger security guarantees and more precise access control. Within this framework, API flows coordinate interactions among ecosystem participants by standardising processes such as user authentication, consent management, and authorisation [23,24]. These mechanisms ensure that access to sensitive financial data and payment functionalities is restricted to verified entities operating within defined regulatory boundaries.
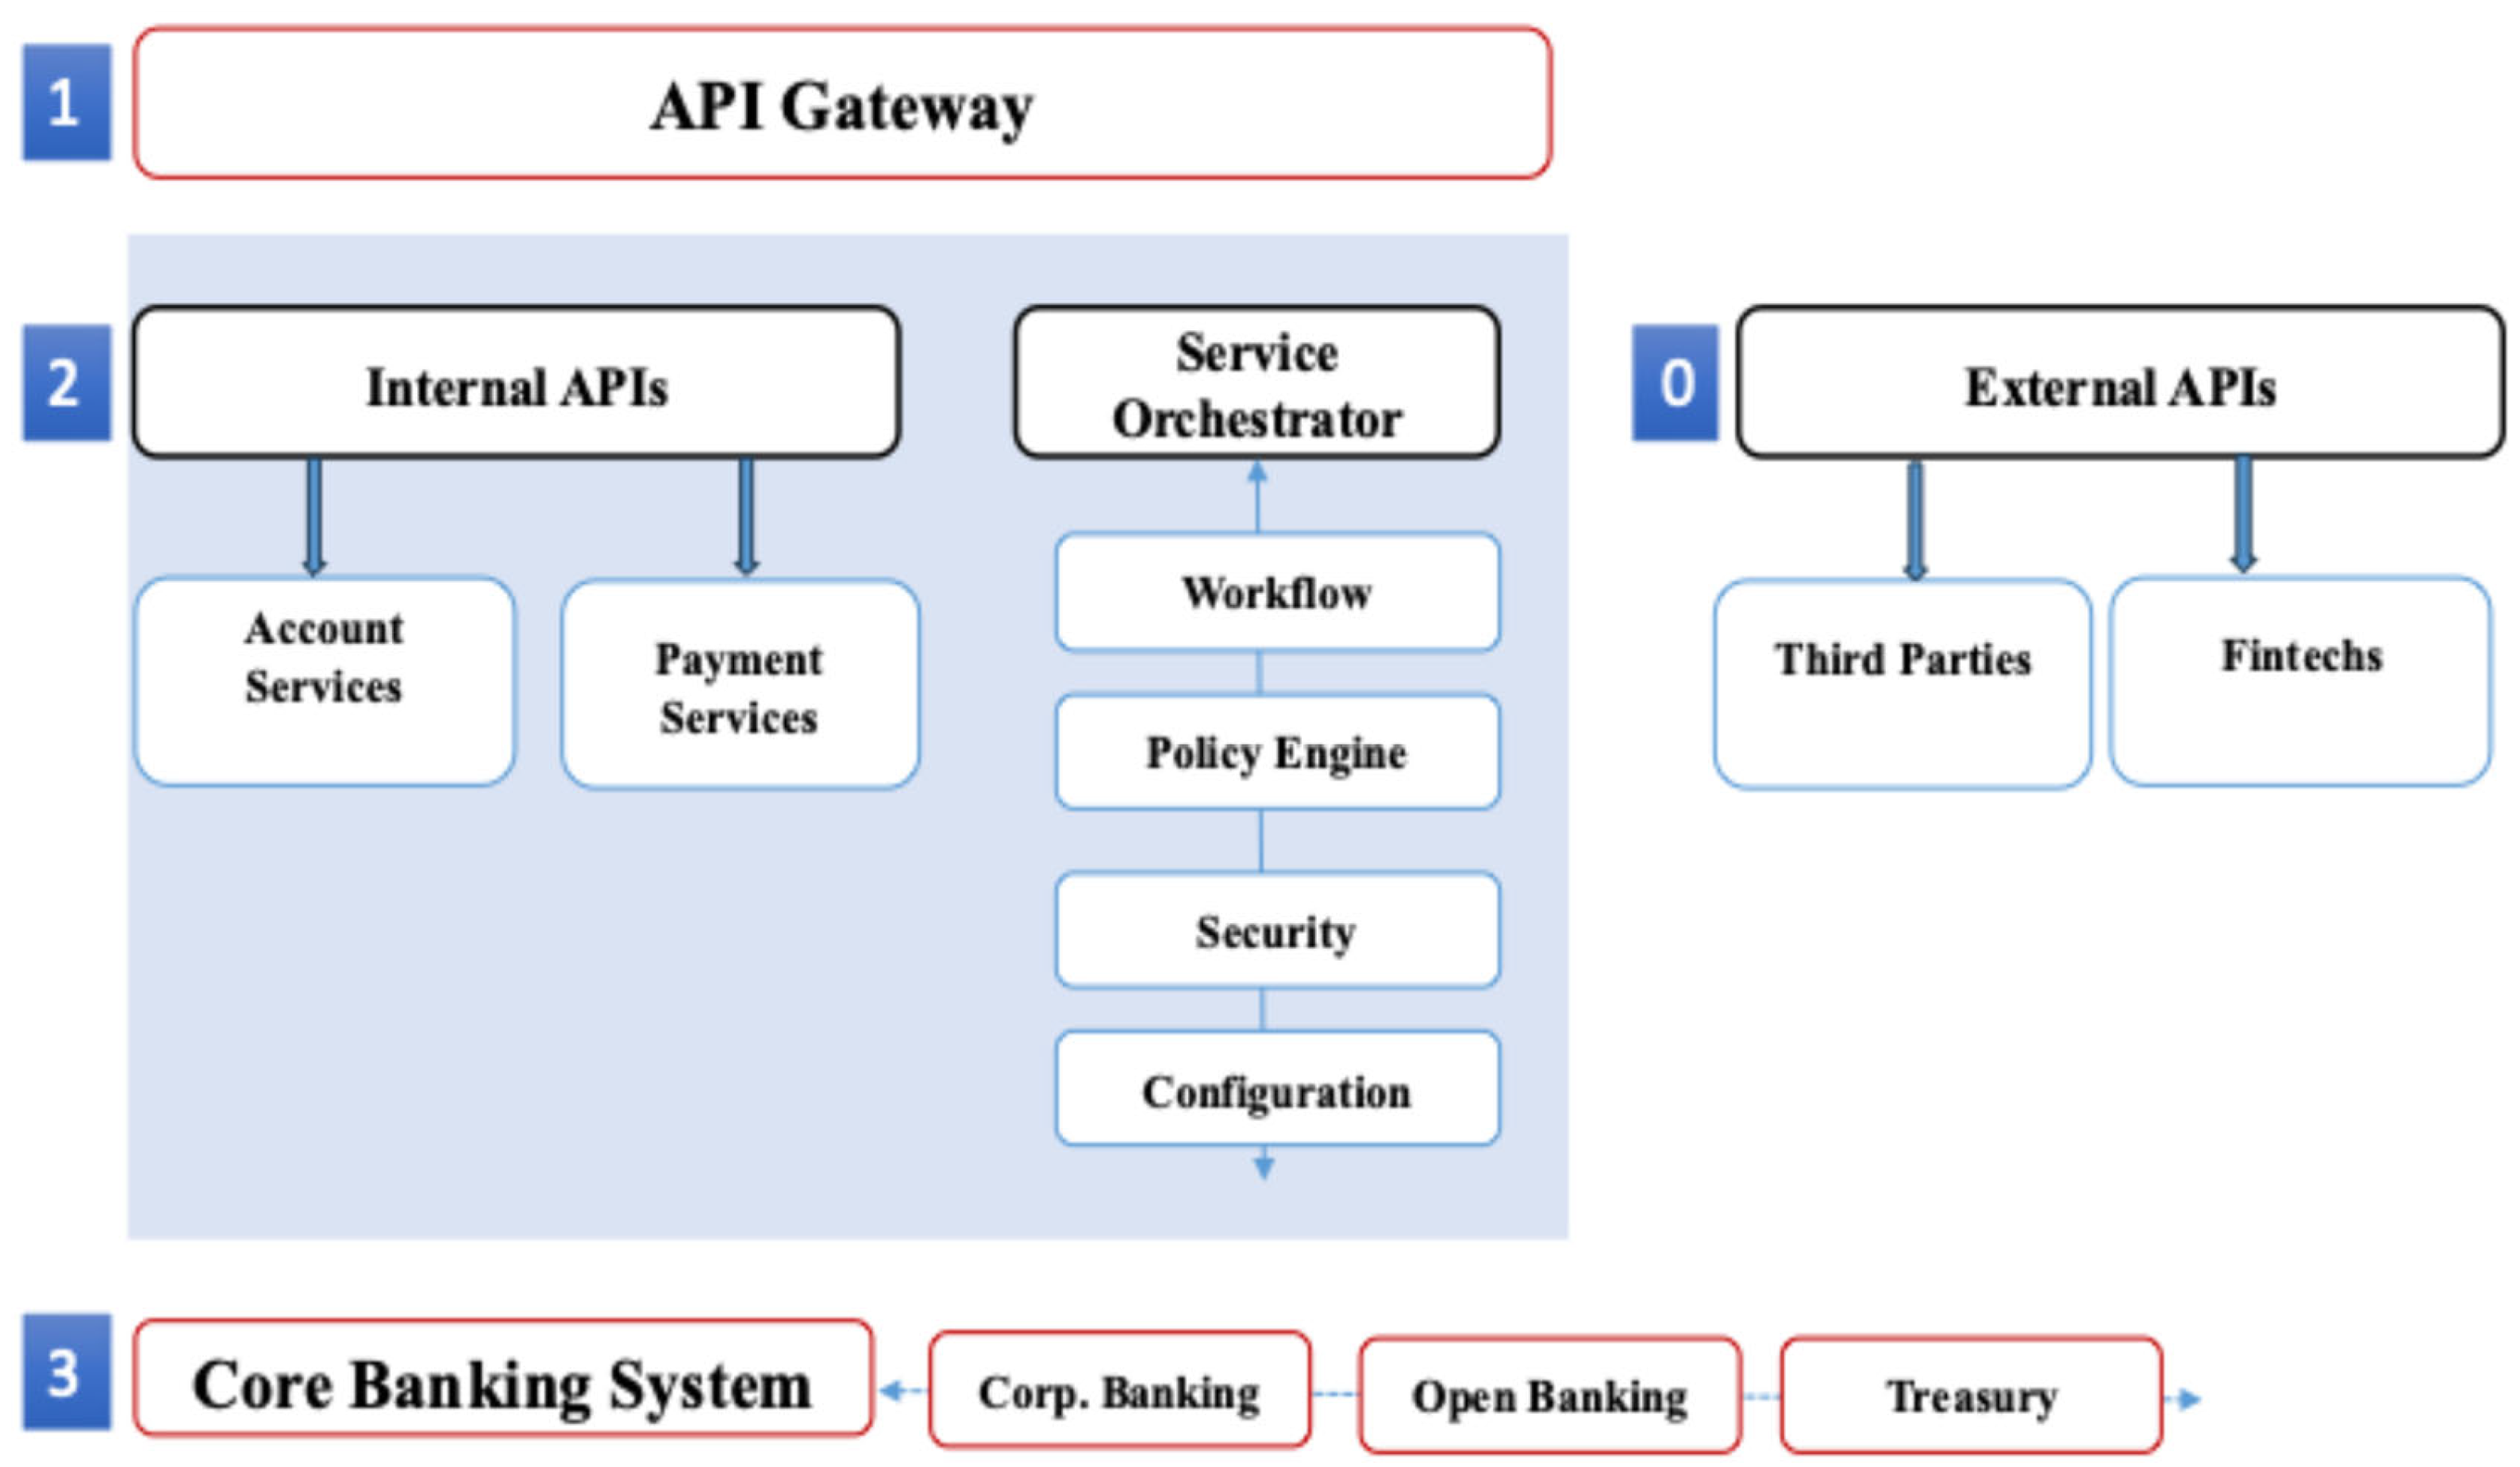
In addition to facilitating secure data exchange, APIs support encryption, standardised communication protocols, and monitoring capabilities that enhance auditability and accountability [21,25,26]. Logging, real-time supervision, and fraud detection mechanisms embedded within API infrastructures contribute to the operational resilience of OB systems and strengthen compliance with regulatory expectations. Collectively, these features play a central role in mitigating malicious activity while reinforcing trust among users, providers, and supervisory authorities, as shown in Figure 1.
External APIs serve as interfaces between financial institutions and TPPs, including FinTech firms, payment service providers, and other regulated entities. Their primary function is to enable secure and standardised access to customer data and financial services, thereby supporting the development of applications such as budgeting tools, comparison services, and payment initiation solutions [27,28]. In the European context, external APIs are closely linked to regulatory mandates introduced under the revised Payment Services Directive (PSD2), which requires banks to facilitate access to account information and payment initiation services for authorised providers [29,30]. From a conceptual standpoint, these interfaces extend the operational boundaries of banks, encouraging a shift from vertically integrated architectures towards ecosystem-based models in which collaboration with external actors complements competitive strategies [29,31,32].
Internal APIs, by contrast, operate within financial institutions and enable communication between front end applications, middleware layers, and core banking systems. These interfaces provide structured access to functionalities such as balance enquiries, transaction histories, and payment processing, supporting efficient integration across internal systems [33,34]. By decoupling user-facing platforms from legacy infrastructure, internal APIs facilitate faster development cycles and greater organisational agility in delivering digital banking services, including mobile and online channels [35,36]. Conceptually, internal APIs reflect the modularisation of banking information systems, allowing services to be recombined and reused while preserving the core banking system as the authoritative source of financial data and transactional integrity.
Figure 1. Open banking API architecture framework, adapted from [37].
Fintech 05 00038 g001
The core banking system (CBS) constitutes the technological backbone of financial institutions, supporting a wide range of critical functions such as deposit management, lending activities, payments, treasury operations, corporate services, and OB-related modules. It enables real-time transaction processing across branches and digital channels, including account administration, deposits and withdrawals, and credit operations [38,39]. Acting as the central repository for financial records, customer accounts, balances, and contractual information, the core banking system integrates with multiple specialised applications to support broader organisational processes.
Despite its central role, the inherent complexity, legacy dependencies, and performance sensitivity of core banking systems make direct external exposure neither practical nor secure [40,41]. Instead, these systems operate as the authoritative source of financial data, while intermediary layers abstract their functionality. APIs and service orchestration components mediate access to core banking capabilities, transforming internal processes into secure, standardised, and consumption-ready services for internal applications and authorised stakeholders.
Within this architecture, the API gateway serves as the principal control point for all API-based interactions. It routes incoming requests to appropriate backend services while enforcing security policies related to authentication and authorisation [37,42]. In addition to access control, the gateway supports operational oversight through traffic management, rate limiting, and performance monitoring. By functioning as the institution’s digital entry point, the API gateway reconciles the need for openness and scalability with consistent governance and control across customer-facing applications, FinTech partners, and internal development teams [1,43,44].

2.2. Open Banking Core Security

Security within OB ecosystems is underpinned by a set of interrelated principles designed to protect sensitive financial data and preserve transaction integrity across multiple participating entities. Rather than relying solely on technical safeguards, OB security encompasses strategic, technological, and regulatory measures that support consumer protection, system reliability, and institutional trust [18,45]. This integrated approach reflects the distributed nature of OB, where responsibility for security is shared across banks, TPPs, and regulatory authorities.
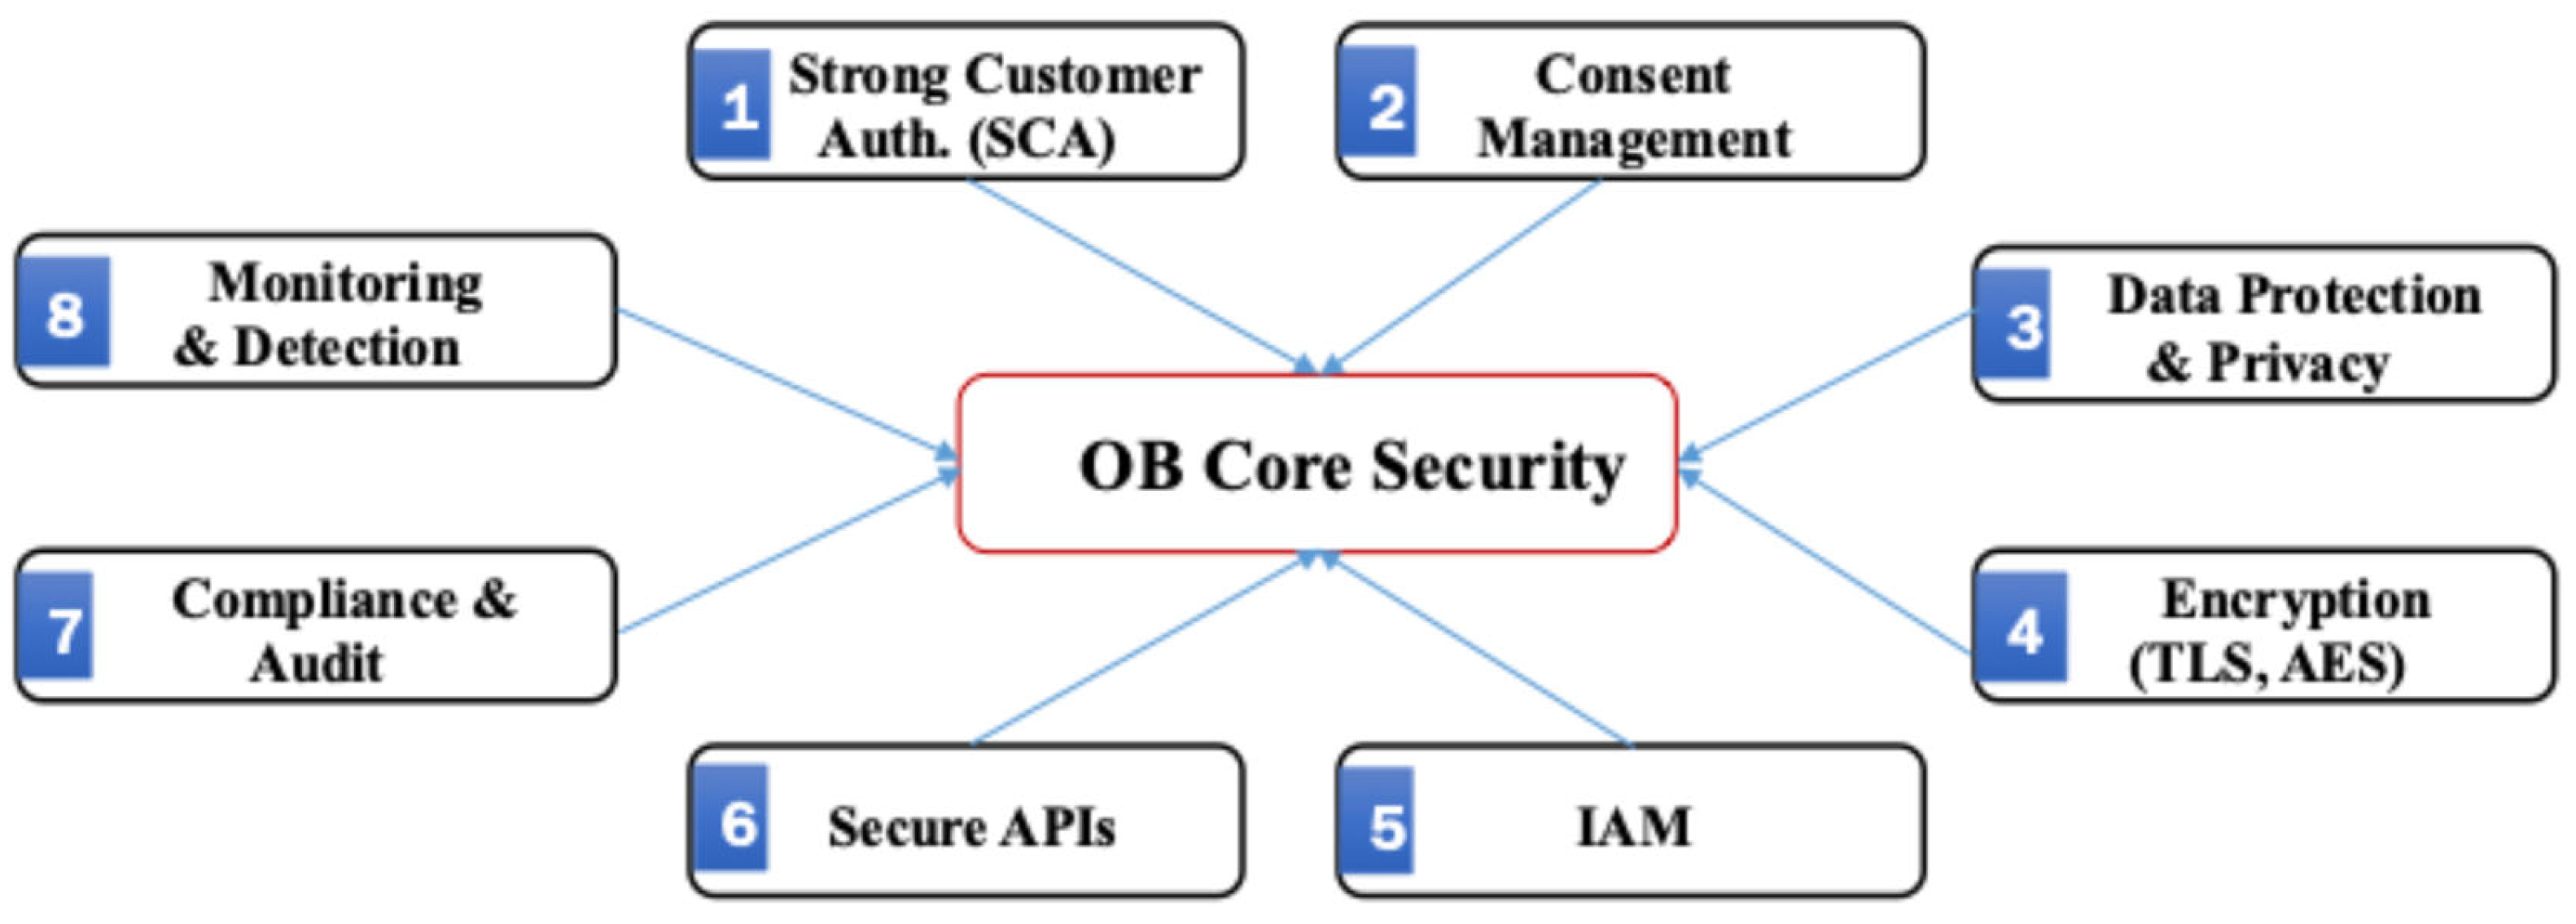
Key elements of this security architecture include the protection of APIs, the deployment of robust identity and access management (IAM) mechanisms, and the implementation of transparent and revocable consent processes. These components ensure that access to financial data and payment functionalities is limited to authenticated and authorised actors operating within clearly defined permissions [46,47]. The secure management of cross-border data flows introduces further requirements related to data localisation, regulatory alignment, and supervisory oversight. When effectively combined, these measures establish a resilient security foundation that enables innovation while maintaining compliance and safeguarding consumer interests, as presented in Figure 2.
Strong customer authentication (SCA) constitutes a central control mechanism within OB security architectures. Its primary function is to establish reliable user identity verification by requiring a combination of at least two independent factors drawn from knowledge, possession, or inherence categories [48,49]. By increasing the assurance level of authentication processes, strong customer authentication reduces the likelihood of unauthorised access to accounts and payment functionalities. Within OB environments, SCA plays a critical role in safeguarding interactions across multiple service providers and distributed access points. Consent management (CM) is closely intertwined with strong customer authentication, as it governs the conditions under which authenticated users authorise data sharing and transaction initiation. Effective consent management ensures that permissions are explicit, informed, and revocable, thereby preserving user agency over financial data and services [49,50]. From a security perspective, consent mechanisms must be transparent in scope, time-bound, auditable, and straightforward to withdraw, particularly in ecosystems where data flows extend across institutional and national boundaries.
Data protection and privacy controls further reinforce system security by limiting exposure and misuse of sensitive information [51,52]. Encryption techniques applied during both data transmission and storage protect confidentiality and integrity, while complementary approaches such as anonymisation or pseudonymisation reduce the risk of re-identification when data are processed or shared for secondary purposes [45,53]. These practices must be aligned with applicable regulatory frameworks, including the General Data Protection Regulation, which establishes requirements for lawful processing, data minimisation, and user rights.
At the operational level, OB security relies on the coordinated use of APIs and IAM mechanisms to ensure that only regulated and verified participants can interact with protected resources [54,55]. Widely adopted industry standards, such as OAuth 2.0 and OpenID Connect, enable delegated and scope-limited access without requiring the disclosure of user credentials, thereby reducing attack surfaces associated with credential reuse and compromise [56,57]. Regulatory oversight reinforces these technical controls by mandating the registration and certification of TPPs, validating credentials, and requiring comprehensive audit trails covering API interactions, consent events, and transaction records.
Despite these layered controls, APIs remain a prominent source of security risk within OB ecosystems. Configuration weaknesses, inadequate monitoring, or inconsistent enforcement of access policies can give rise to vulnerabilities such as broken object-level authorisation, excessive data exposure, token leakage, and session hijacking [58,59]. Maintaining consistent, time-limited, and auditable consent across multiple providers and regulatory jurisdictions continues to pose practical challenges [60,61,62]. Effective OB security depends on a layered and integrated approach that combines technical safeguards, regulatory obligations, and user rights to enhance resilience, trust, and compliance across the financial sector.

2.3. Geographic Adoption and Regulatory Frameworks

OB adoption and regulation exhibit substantial geographical variation, reflecting differences in legal traditions, institutional capacity, and policy priorities [12]. In the European Union and the United Kingdom, OB is governed by comprehensive regulatory regimes combining data protection under the GDPR with secure access mandates through the revised PSD2. These frameworks emphasise consumer consent, data protection, and competition, positioning OB as both a market-enabling and consumer-protecting mechanism [50,63]. High regulatory maturity in these regions supports standardisation, supervisory oversight, and relatively rapid adoption of both technological and behavioural safeguards.
Outside Europe, regulatory approaches are heterogeneous and adapted to local economic and institutional contexts. Australia’s Consumer Data Right [64], represents a consumer-centric model that grants individuals explicit control over how their data are accessed and shared, thereby prioritising transparency and accountability. In Canada, regulatory initiatives remain under development and seek to balance innovation objectives with privacy protections, although current proposals are generally less prescriptive than their European counterparts. Across several African jurisdictions, including Angola and Kenya [65,66], regulatory frameworks are emerging gradually and reflect domestic legal structures, market readiness, and broader financial development strategies.
A number of countries have also introduced national data protection and OB-related regulations that operate alongside or independently of European-style regimes. Brazil enforces OB through the General Data Protection Law, while the United Arab Emirates applies a dedicated data protection framework that governs the processing and sharing of personal financial information [67,68,69]. In India, OB initiatives are overseen by the Reserve Bank of India, which plays a central role in supervising data-sharing arrangements and ensuring systemic stability [70]. Despite jurisdictional differences, these regulatory frameworks consistently require explicit customer consent as a precondition for data sharing and transaction initiation, underscoring consent as a universal governance principle in OB [12,71]. In most cases, central banks or financial supervisory authorities are responsible for enforcement and alignment with national legislation.
Table 1 presents descriptive statistics on OB regulatory policies across all 193 countries. Each column shows how many countries satisfy the respective criteria. The table is adapted from [12].
At the global level, innovation and competition emerge as dominant regulatory drivers, confirming the primacy of the regulatory dimension in shaping OB diffusion [72,73]. However, the uneven distribution of competitive pressure indicates that regulatory intent alone does not guarantee comparable technological or behavioural outcomes [74,75]. This divergence illustrates a core premise of the tri-dimensional framework: regulation establishes formal structures, but its effectiveness depends on technological infrastructure and user trust.
Regional patterns further highlight the interdependence of the three dimensions. Europe and Central Asia prioritise competition and innovation, exhibiting higher levels of technological integration that reflect alignment between regulatory mandates and deployment [71]. In contrast, Africa and the Middle East display lower levels of mandatory data sharing and reciprocal access, suggesting that limited institutional capacity and weaker behavioural trust constrain both regulatory enforcement and technological uptake [19,76]. Latin America and the Caribbean emphasise financial inclusion, while North America and Southeast Asia focus on integrated data and payment models, illustrating how regional priorities reshape the balance between technological functionality and behavioural objectives.
While innovation is a near-universal motivation for OB adoption, competitive pressure varies sharply across regions, remaining comparatively weak in Africa and the Middle East [77,78]. Latin America and the Caribbean prioritise financial inclusion, whereas this objective is less prominent in Europe and Central Asia. Technological implementation also diverges significantly: Southeast Asia and the Pacific display high levels of integrated data and payment functionality, while North America remains comparatively fragmented despite advanced financial infrastructures.
Table 2 provides descriptive statistics on open banking regulatory policies across all 193 countries. Each column reports the percentage of countries listed in Table 1 that satisfy the respective criteria. The table is adapted from [12].
The statistics provide empirical support for the tri-dimensional framework by revealing how regulatory design, technological implementation, and behavioural conditions co-evolve across regions. Rather than presenting regulatory adoption as uniform, the data demonstrate systematic variation in how policy objectives translate into technological capabilities and behavioural readiness across 193 countries.
Crucially, policy complexity does not correspond directly to adoption effectiveness. Although approximately 80 countries report full OB regulation implementation, advanced features such as reciprocal data access and integrated payment systems remain unevenly deployed [79,80]. This misalignment indicates that regulatory compliance does not automatically translate into technological maturity or behavioural acceptance, reinforcing the analytical necessity of treating these dimensions as distinct but interdependent.
The findings also highlight security implications. Regions with weaker supervisory capacity show lower implementation of mandatory data sharing and technical standards, increasing exposure to operational and cyber risks where behavioural trust is fragile [81]. Misalignment between regulatory requirements and technological infrastructure amplifies vulnerability, particularly in contexts with limited stakeholder coordination.
Stakeholder engagement among regulators, financial institutions, and industry consortia emerges as a critical mediating factor linking the three dimensions [82]. OB adoption evolves not only through formal regulation but also through organisational strategies and user behaviour, demonstrating that security outcomes are socially and institutionally embedded rather than purely technical.
Taken together, the evidence in Table 1 and Table 2 provides quantitative grounding for the tri-dimensional framework [12,83]. Effective and secure OB ecosystems do not result from regulation alone but from the coordinated interaction of regulatory policies, technological capabilities, and behavioural trust mechanisms. These findings underscore that context-sensitive, behaviourally informed regulatory design is essential for achieving secure, resilient, and inclusive OB systems.

3. Methodology

This study adopts a systematic literature review (SLR) approach to examine how behavioural factors intersect with technological and regulatory dimensions in shaping security within open banking (OB) environments.
Although OB formally emerged following regulatory initiatives such as the Revised Payment Services Directive (PSD2), the review begins in 1999 to capture the technological and digital banking foundations that later enabled OB ecosystems [84,85]. The timeframe is structured into three analytical phases to ensure conceptual clarity and chronological coherence:
  • Pre-regulatory foundation phase (1999–2014): Research on online banking security, API development, digital trust, and early FinTech integration.
  • Regulatory emergence phase (2015–2018): Formalisation of OB frameworks and introduction of mandatory data sharing under regulatory supervision.
  • Post-implementation expansion phase (2019–2025): Ecosystem consolidation, third-party provider integration, platform governance challenges, and advanced security concerns.
This chronological structuring enables a historically grounded and analytically differentiated examination of the literature, preventing the conflation of pre-OB digital banking research with post-regulatory OB scholarship.
The review adopts a behavioural-first perspective, positioning user intentions, trust formation, cognitive effort, and security-related practices as central mechanisms. These factors influence financial ecosystem resilience. This approach facilitates a systematic assessment of how misalignments between human behaviour, security technologies, and governance structures generate persistent vulnerabilities and regulatory tensions within OB systems. Of the 117 studies retained for qualitative synthesis, 68% were published after 2015, reflecting a marked acceleration of scholarly attention following regulatory formalisation and market implementation of OB frameworks.

3.1. Inclusion and Exclusion Criteria

The initial search process yielded 733 records comprising scientific articles, empirical studies, and scholarly handbooks. Duplicate entries were identified and removed using reference management software. The remaining records were then subjected to a two-stage screening process. First, titles and abstracts were independently reviewed to eliminate clearly irrelevant studies. Second, full-text screening was conducted using predefined inclusion and exclusion criteria. Each study was qualitatively assessed for methodological clarity, relevance, and robustness, using a structured checklist adapted from established SLR protocols. Exclusion criteria were applied if the studies did not address OB or related topics, lacked empirical or theoretical contributions, had insufficient methodological reporting, used data outside the inclusion window, or were duplicate or earlier versions of the same work. Following this screening and quality appraisal process, 117 studies satisfied all criteria and were retained for the final synthesis, as shown in Table 3.

3.2. Data Sources and Search Strategies

The search strategy was developed in accordance with PRISMA 2020 guidelines. Searches were conducted in Scopus, Web of Science, IEEE Xplore, and Google Scholar, with the complete search strings and database-specific filters.
The review draws on a comprehensive search of established academic databases and scholarly portals, including ScienceDirect, Web of Science, Scopus, Taylor & Francis, SAGE Journals, IEEE Xplore, Emerald Insight, SpringerLink, PubMed, and Google Scholar. The strategy combined keywords and controlled descriptors related to open banking and behavioural security, covering themes such as APIs, data protection and privacy, financial regulation, cybersecurity, behavioural aspects of computing, RegTech, FinTech, SecTech, compliance mechanisms, data governance, financial inclusion, banking innovation, digital transformation, and consumer protection.
The search focused on peer-reviewed journal articles and academic books published in leading outlets that explicitly address security challenges within OB contexts. All sources were searched and reviewed up to December 2025.

3.3. Regulatory Policy Sources

To complement the academic literature, regulatory and policy materials were systematically examined using targeted searches of authoritative institutional sources. At the supranational level, official documentation was consulted through the EU law portal, alongside guidance and regulatory instruments issued by the European Banking Authority [86], the UK Financial Conduct Authority [87], and the Data Protection Board [88]. These sources provided insight into the governance and compliance requirements shaping OB security across European jurisdictions.
In addition, national and regional regulatory frameworks were reviewed to capture cross-market variation in OB implementation and oversight. These included materials published by the National Bank of Angola [65], the Central Bank of Kenya [89], the Central Bank of Nigeria [90,91], and the Reserve Bank of India [70]. The regulatory analysis was further extended to data protection regimes beyond Europe, drawing on legislative sources such as the Brazilian data protection law [67] and the United Arab Emirates data protection law [68]. These policy sources supported a comparative assessment of how regulatory approaches influence security practices and expectations within OB ecosystems.

3.4. Data Collection Process

Data from the 117 included studies were extracted independently by two reviewers using a predesigned Excel extraction form. Extracted information included study characteristics, methodological design, security outcomes, regulatory context, and behavioural variables. Discrepancies between reviewers were resolved through discussion and consensus. When information was unclear or missing, study authors were contacted via email to verify or clarify data. Automation tools were only used for deduplication and reference management.
Primary outcomes included:
  • Technical security measures (APIs, encryption, authentication protocols)
  • Regulatory compliance indicators (PSD2, GDPR, regional guidelines)
  • Behavioural outcomes (trust, security decision-making, adoption behaviour)
All results compatible with these outcomes were extracted, including qualitative descriptions, quantitative measures, and reported trends.

3.5. Data Synthesis

Study eligibility: The 117 retained studies were categorised according to the tri-dimensional security framework—technological, regulatory, and behavioural. Inclusion in each category required evidence of outcomes related to security mechanisms, regulatory compliance, or user behaviour within OB ecosystems.
Data preparation: Extracted data were standardised to ensure consistency across categories. Behavioural constructs, regulatory measures, and technical descriptors were harmonised, with terminology aligned across regions. Missing or ambiguous data were flagged for clarification or addressed using conservative assumptions when verification was not possible.
Tabulation and visualisation: Data were systematically tabulated by tri-dimensional category, study type, country or region, and publication year. Visual representations of the tri-dimensional framework, recurring security challenges, and interdependencies were generated to facilitate cross-study comparison and interpretation.
Synthesis approach: A narrative synthesis integrated findings across heterogeneous study designs and outcomes. This approach identified recurring security challenges, emerging trends, and interactions among the three security dimensions. Emphasis was placed on how misalignments between dimensions create persistent vulnerabilities and influence user adoption.
Heterogeneity exploration: Variation across geographic regions, regulatory regimes, technological maturity, and study designs was examined. Comparative tables highlighted differences in security practices, regulatory enforcement, and user behavioural patterns, revealing context-specific dependencies in OB implementation.
Sensitivity analyses: Each study was assessed for methodological clarity, appropriateness of design, transparency of data reporting, and relevance to OB security. Studies with insufficient methodological detail or unclear results were noted as lower robustness and interpreted cautiously in the synthesis. All assessments were conducted by the author, with verification through cross-checking and discussion when uncertainties arose.
Reporting bias assessment: To mitigate reporting bias, multiple academic databases, reference lists, and grey literature sources were searched. Limitations due to missing or unpublished studies were explicitly acknowledged.
Certainty assessment: Overall evidence certainty was assessed narratively using a modified GRADE approach suited for qualitative synthesis. Confidence was judged based on methodological quality, consistency, and transparency of reporting across studies.

4. Empirical Literature of the OB Framework

This section synthesises the empirical scholarship on OB across the three security dimensions. It examines how OB has been operationalised in practice, evaluates the scope and methodological robustness of existing research, and identifies conceptual and empirical gaps that motivate the development of the present study.
The review is structured around three interrelated strands. Section 4.1 analyses studies focusing on API architectures and FinTech technologies, as shown in Table 4, highlighting advances in security protocols, interoperability, and digital infrastructure. Section 4.2 examines regulatory and market-oriented research, as presented in Table 5, assessing how data-access frameworks and governance models reshape competition and industry structure. Section 4.3 integrates these strands through the proposed tri-dimensional analytical framework, placing particular emphasis on behavioural evidence and its implications for adoption, trust formation, and security outcomes, as revealed in Table 6.

4.1. Studies on API and FinTech Technologies

A substantial stream of research examines the technological foundations of OB, particularly the role of APIs in enabling secure data sharing and interoperability between financial institutions and third-party providers. Although APIs were not originally designed for highly regulated financial environments, advances in authentication protocols, encryption mechanisms, and standardised interfaces have facilitated their effective integration into OB ecosystems. Empirical studies in this domain primarily focus on security robustness, architectural design, and user adoption dynamics.
Ref. [27] provides a formal security analysis of the Financial Grade API based on OpenID Connect, demonstrating how strengthened authentication and authorisation mechanisms mitigate vulnerabilities inherent in traditional API implementations. Complementing this technical perspective, Ref. [92] investigate determinants of users’ continuance intention to use mobile banking applications, emphasising the importance of perceived system quality, reliability and virtual service design in sustaining long-term engagement. These findings indicate that technical security alone is insufficient and must be complemented by a positive user experience to support sustained adoption.
Table 4. Overview of OB API and FinTech technology studies.
Author(s)Title/JournalKey DomainResearch Contributions
[27]An extensive formal security analysis of the openid financial-grade API./IEEE symposium on security and privacySecurity and API protocolsPerforms formal security analysis of fAPI, identifies vulnerabilities in authentication flows, and proposes strengthened security mechanisms for open banking APIs.
[18]Security analysis of the open banking account and transaction API protocol./Cyber security and applicationsSecurity and API standardsAnalyzes transaction and account API protocols; identifies potential security threats and recommends technical improvements for secure data sharing.
[93]Open banking: emergent roles, risks & opportunities./Ecis 2018 proceedingsEcosystem and strategic implicationsExplores emergent roles in open banking ecosystem; discusses risks (data privacy, security) and opportunities (innovation, competition) for banks and FinTechs.
[94]Predicting the intention to use the investment aggregate functionality in the context of open banking using ann./Procedia computer scienceConsumer behaviour and technologyUses artificial neural networks to predict consumer intention to adopt investment aggregation features; highlights factors driving adoption in open banking apps.
[34]The open banking era: an optimal model for the emergency fund./Expert systems with applicationsFinancial modelling/open banking applicationsProposes an optimization model for emergency fund management in the open banking era; demonstrates how open banking APIs can improve fund allocation and household financial resilience.
[38]FinTech./Business & information systems engineeringFinTech and open banking foundationsProvides one of the earliest comprehensive analyses of FinTech, highlighting the foundations and evolution of digital finance, including the emergence of open banking ecosystems.
[41]Blockchain-based identity management and access control framework for open banking ecosystem./Future generation computer systemsSecurity and identity managementProposes a blockchain-enabled framework for identity management and access control in open banking ecosystems; enhances privacy, authentication, and security.
Early conceptual contributions by Ref. [38] provide a foundational understanding of FinTech evolution, tracing the development of digital finance and the emergence of OB ecosystems. Subsequent empirical research has examined how FinTech innovations reshape banking processes and customer interactions. Ref. [95], for example, analyse customers’ psychological intentions to recommend mobile payment technologies within social networks, illustrating how social influence and user engagement accelerate FinTech diffusion and contribute to the expansion of OB ecosystems.
More recent contributions adopt a security engineering perspective. Ref. [18] conduct formal analyses of core account and transaction API protocols, identifying residual vulnerabilities and proposing targeted technical improvements. Their work highlights the transformation of APIs from generic data exchange tools into specialised financial infrastructures aligned with standards such as OAuth 2.0 and Financial Grade API.
The studies summarised in Table 4 demonstrate that research on the technological dimension of OB has evolved from exploratory and conceptual discussions towards rigorous security validation and integrated behavioural analysis.

4.2. Studies on Regulatory Policy and Market Analysis

Empirical research consistently demonstrates that regulatory frameworks and data access standards play a central role in shaping market behaviour, competitive dynamics, and innovation within OB ecosystems. Rather than functioning solely as compliance instruments, OB regulations actively restructure financial markets by redefining data ownership, access rights, and the relationships between incumbent banks and FinTech firms.
Large-scale cross-country evidence provided by Ref. [12] shows that customer data access regulations significantly increase FinTech market entry, intensify competition, and expand consumer choice across 168 countries. However, the magnitude of these effects varies across regions, reflecting differences in institutional capacity, legal maturity, and financial market development. These findings suggest that the economic impact of OB depends not only on the existence of regulation but also on its enforcement quality and alignment with local market conditions.
At a more granular level, Ref. [96] analyse the United Kingdom’s OB regime and demonstrate how regulatory standardisation reshapes industry architecture. Mandated technical and governance standards facilitate collaboration between banks and FinTech firms while simultaneously altering competitive boundaries and increasing coordination complexity. Regulation therefore performs a dual function: enabling innovation while generating structural adjustment costs.
Comparative regulatory scholarship further highlights the diversity of OB models. Ref. [97] identify multiple regulatory rationales and implementation approaches, including mandatory, voluntary, and hybrid models, each associated with distinct policy trade-offs. In related work, Ref. [98] draws lessons from the European Union’s experience for the United States, emphasising both the benefits of regulatory-driven data sharing and the institutional challenges posed by fragmented supervisory structures and differing legal traditions.
Table 5. Overview of OB regulatory policy and market studies.
Author(s)Title/JournalKey DomainResearch Contributions
[12]Customer data access and FinTech entry: early evidence from open banking./Journal of financial economicsRegulation and market entryProvides global evidence from 168 countries on how customer data access regulations affect FinTech entry; shows that open banking policies significantly increase competition, promote innovation, and support consumer choice, but with regional variations.
[97]The many shades of open banking: a comparative analysis of rationales and models./Internet policy reviewComparative regulation and modelsCompares open banking rationales across countries; identifies different implementation models (mandatory, voluntary, hybrid) and their policy implications.
[19]Open banking: credit market competition when borrowers own the data./Journal of financial economicsMarket competition and data ownershipInvestigates the impact of customer data ownership on credit markets; finds that open banking enhances competition and credit allocation efficiency.
[96]Regulatory standards and consequences for industry architecture: the case of UK open banking./Research policyRegulation and industry structureAnalyses how UK open banking standards reshape banking industry architecture; shows implications for bank–FinTech collaboration and market dynamics.
[99]Open banking: a bibliometric analysis-driven definition./Plos oneLiterature mapping and conceptualisationProvides a bibliometric analysis of open banking literature; proposes a structured definition and identifies emerging research trends and gaps.
[98]Open banking goes to Washington: lessons from the EU on regulatory-driven data sharing regimes./Computer law & security reviewRegulation and comparative policyExplores lessons from EU open banking regulation for US policy; highlights regulatory-driven data sharing benefits and challenges in cross-jurisdiction adoption.
[100]The impact of open banking on traditional lending in the BRICS./Finance research lettersOpen banking and credit marketsAnalyses how open banking influences lending in BRICS economies; finds that data sharing enhances credit availability and reduces information asymmetry for borrowers.
[84]What drives deregulation? economics and politics of the relaxation of bank branching restrictions./Quarterly journal of economicsPolitical economy of financial regulationUses hazard models to analyse state-level bank deregulation in the USA; finds that private interest group dynamics (large vs. small banks, competing industries) explain deregulation timing better than public interest or political-institutional models.
A growing body of literature further examines OB’s implications for credit markets Ref. [34], show that granting borrowers ownership and control over financial data enhances lender competition, reduces information asymmetry, and improves credit allocation efficiency. Similar results are reported by Ref. [19], in BRICS economies, where OB frameworks increase credit availability, particularly for underserved borrowers. Beyond immediate market outcomes, several studies situate OB regulation within broader institutional and political economy perspectives. Ref. [84] demonstrate that regulatory change in financial markets is often driven by private interest group dynamics rather than purely public interest considerations. These insights remain relevant for contemporary OB reforms, where incumbent institutions, FinTech entrants, and regulators frequently operate under competing incentives.
Meta-level analyses contribute to conceptual consolidation in this rapidly evolving domain. Ref. [99] use bibliometric methods to map OB research, identifying dominant themes and persistent gaps. Complementing this perspective, Ref. [101] analyse the intersection of data protection, regulatory technology, and digital identity, highlighting how user awareness and expectations mediate the effectiveness of regulatory frameworks.

4.3. A Tri-Dimensional Framework for Open Banking

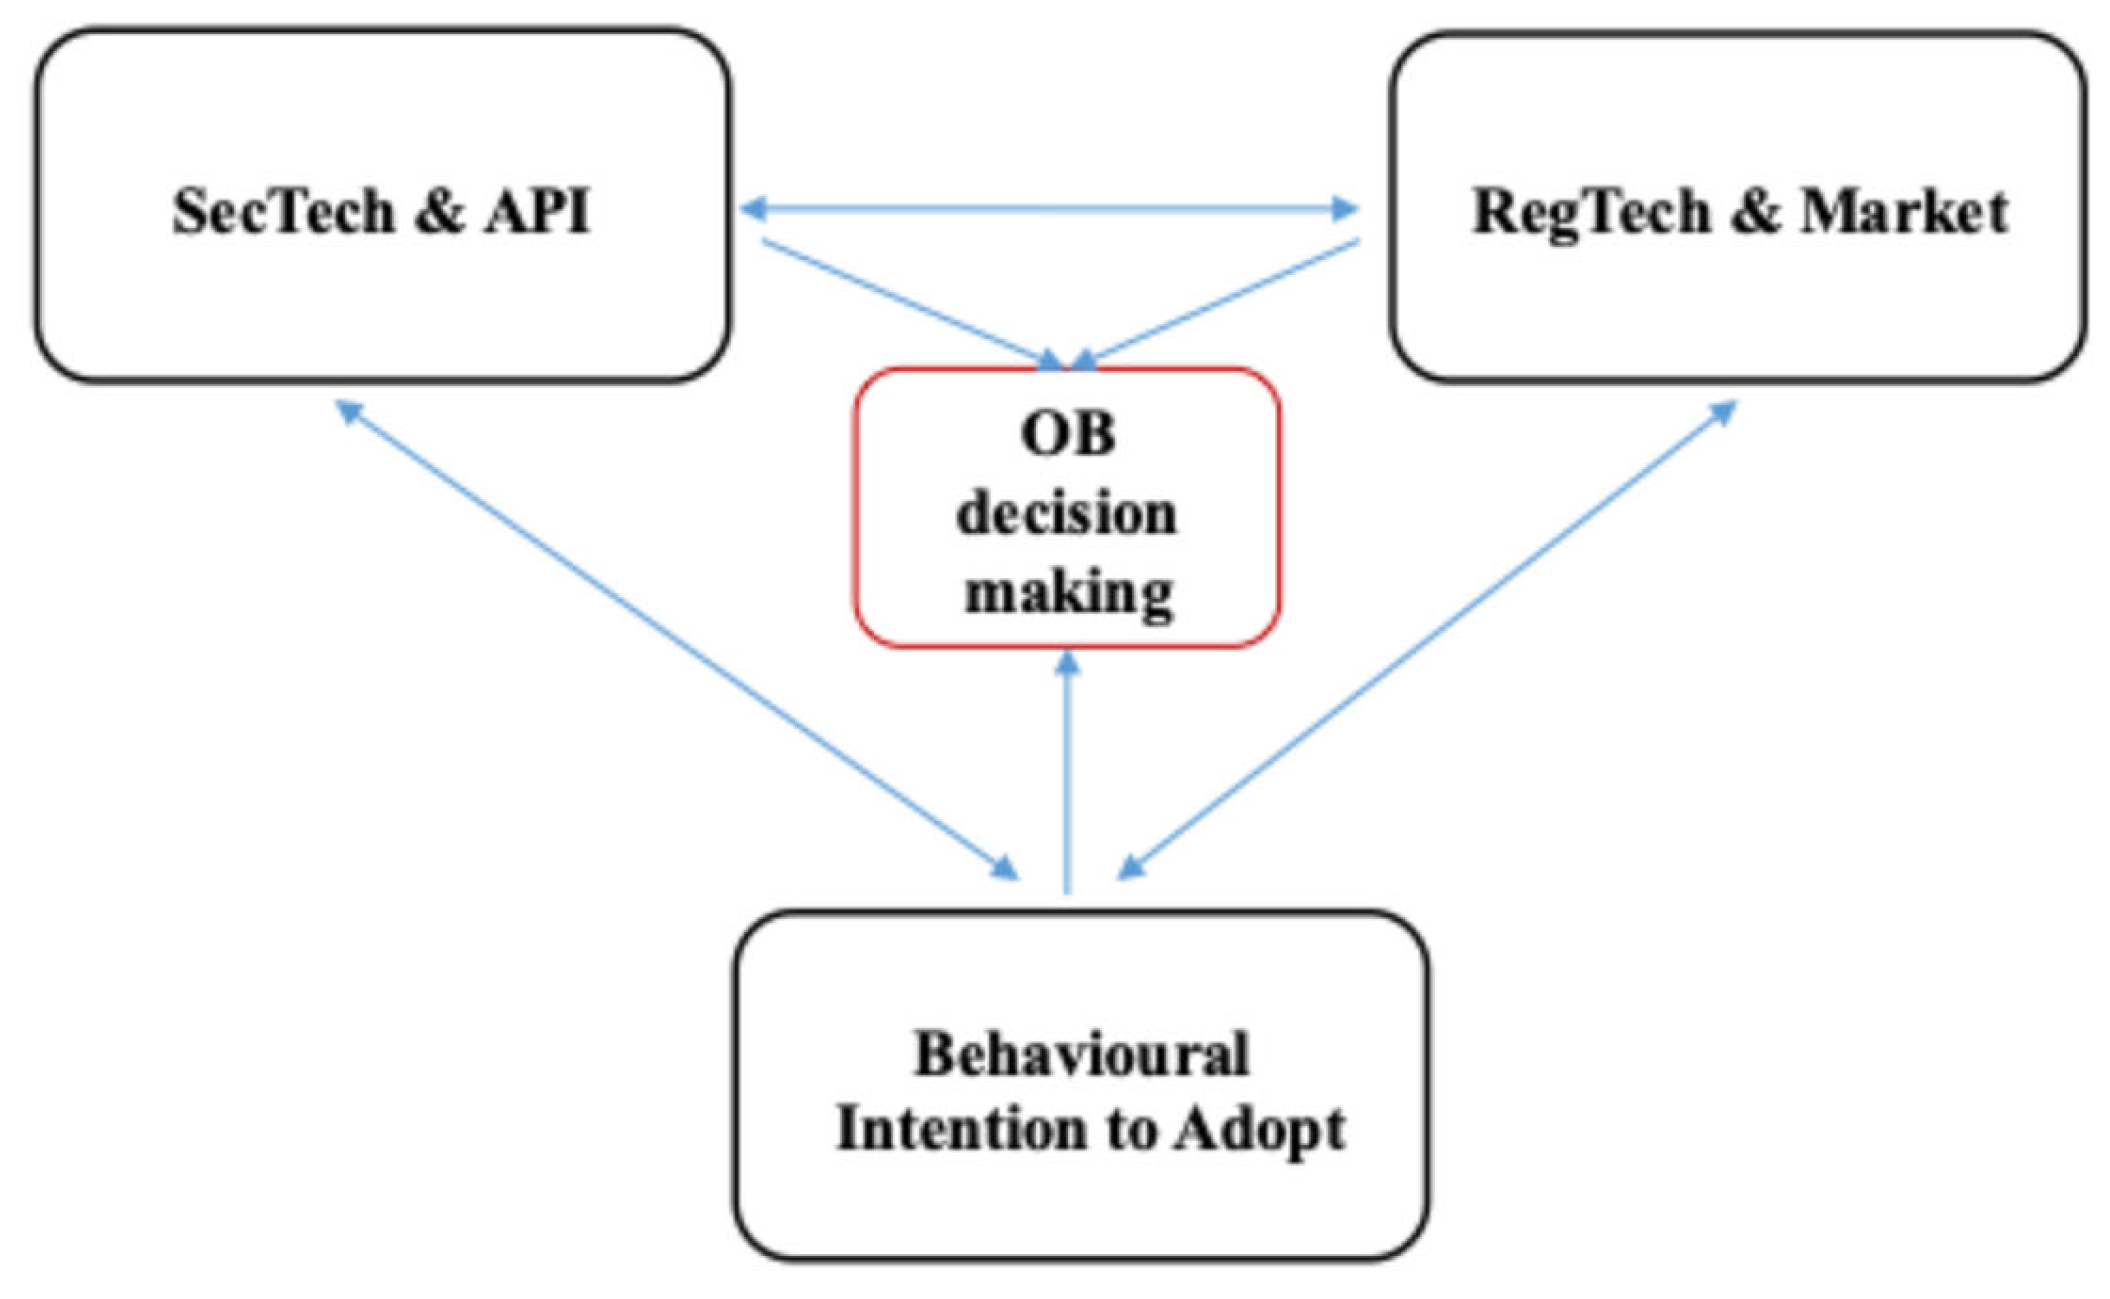
This study proposes a tri-dimensional analytical framework for OB that positions behavioural cognition as a third and equally essential pillar alongside technological and regulatory dimensions, as shown in Figure 3. This ecosystem-based perspective recognises that SecTech, RegTech, and behavioural science applied to digital finance are interdependent and mutually reinforcing.
Technological and regulatory dimensions are extensively represented in the literature, empirical research explicitly examining behavioural aspects of OB security remains comparatively limited. This reflects the relative novelty of research addressing user trust, decision making, and security behaviour in OB environments [92]. To address this imbalance, the framework integrates existing empirical findings with conceptual insights to provide a holistic and human-centred perspective on OB security.
Existing studies identify recurring behavioural mechanisms influencing adoption and compliance. Trust, perceived benefits, and institutional guarantees shape users’ willingness to engage with OB platforms [93,102]. Cognitive effort and usability constraints influence security behaviour, as overly complex controls may lead to non-compliance or circumvention behaviour [103]. Organisational strategies that align policy communication and technical safeguards with user expectations can mitigate behavioural vulnerabilities [94,104]. By integrating these mechanisms, the framework moves beyond a purely technical or regulatory lens and incorporates behavioural drivers that directly influence security outcomes.
Users are not passive recipients of security controls. Their perceptions, decisions, and actions actively shape system effectiveness, compliance levels, and adoption trajectories [105,106]. Incorporating behavioural insights therefore strengthens analytical precision by recognising that security outcomes emerge from the interaction between technological safeguards, regulatory mandates, and human cognition.
The tri-dimensional framework highlights several key interdependencies:
  • Behavioural dynamics → adoption outcomes → technological control deployment.
  • Regulatory policies → platform design constraints → user trust and compliance behaviour.
  • Misalignment between behavioural expectations and SecTech/RegTech → increased security vulnerabilities.
These interactions demonstrate that the framework is not merely descriptive but analytical, revealing how behavioural mechanisms influence the design, adoption, and resilience of OB systems.
The evidence indicates that understanding OB adoption and security requires explicit consideration of behavioural factors. Users’ trust, perceptions of benefit, usability experiences, and institutional context shape their engagement with technological infrastructures and regulatory frameworks in dynamic and mutually reinforcing ways [107,108]. By positioning behavioural cognition as a central element, the framework guides the development of OB ecosystems that are intuitive, resilient, and aligned with real-world usage patterns.
Incorporating behavioural insights into technological and regulatory architectures enables more accurate anticipation of user actions and associated security risks [24,109]. It reduces human error through user-centred design, strengthens trust through transparency and perceived control, and supports adoption by aligning security mechanisms with users’ cognitive capacities and expectations. The tri-dimensional perspective therefore advances a human-centred security paradigm in which protection, usability, and trust are treated as interdependent objectives rather than competing priorities [110,111]. This approach enables adaptive, ethically aligned, and resilient security architectures capable of supporting the long-term evolution of digital finance and OB ecosystems.
Recent literature increasingly supports the centrality of behavioural factors in OB adoption. Ref. [85] demonstrate that consumers’ willingness to share financial data depends more strongly on institutional trust than on technical knowledge, while identifying generational and educational differences in adoption patterns. Ref. [112] shows that trust and satisfaction function as behavioural mediators, positioning user experience as a primary catalyst for technology acceptance in OB environments. Similarly, Ref. [113] develop a trust-based model of OB adoption and provide empirical evidence that perceptions of security, reliability, and value significantly shape behavioural intention under uncertainty.
These findings reinforce the behavioural dimension of the proposed framework, indicating that technological capability and regulatory safeguards must be complemented by trust formation and positive user experience to achieve sustained adoption.
Table 6. Overview of OB behavioural studies.
Author(s)Title/JournalKey DomainResearch Contributions
[85]Characterising online gamblers exceeding financial risk thresholds in the UK: A retrospective analysis using open banking data/Public HealthConsumer behaviour, and financial vulnerabilityProvides survey evidence that consumers’ willingness to share financial data depends more on trust in institutions than on technical knowledge; identifies generational and education differences in adoption.
[75]Data Trusts as a Service: Providing a platform for multi-party data sharing./International Journal of Information Management Data InsightsTrust, privacy, and data governance in multi-party data sharingProvides survey evidence that consumers’ willingness to share financial data depends more on trust in institutions than on technical knowledge; identifies generational and education differences in adoption.
[112]M-banking adoption from the developing countries perspective: A mediated model/Digital BusinessConsumer behaviourExamines how usability perceptions rather than security drive mobile banking adoption in developing markets. By positioning trust and satisfaction as behavioural mediators, it demonstrates that user experience is the primary catalyst for technology acceptance.
[95]Mobile payment: Understanding the determinants of customer adoption/Computers in Human BehaviorBehavioural adoption and trustFinds that mobile payment adoption and recommendation behaviour depend on compatibility, perceived security, innovativeness, and social influence.
[113]Towards an understanding of consumers’ FinTech adoption: the case of open banking./International journal of bank marketingConsumer adoption and trustExamines factors influencing consumer adoption of open banking apps; highlights the role of trust, perceived benefits, and institutional guarantees.
[83]The construction of self-sovereign identity: Extending the interpretive flexibility of technology./Government Information QuarterlyTrust, digital identity, and socio-technical interpretationDemonstrates that stakeholder perceptions and institutional context influence how self-sovereign identity technologies are understood, governed, and implemented.
Empirical research consistently demonstrates that user behaviour plays a central role in OB adoption and security outcomes. Ref. [87] show that even among digitally literate users, adoption of mobile and OB services is driven primarily by perceived usability and service experience, while privacy concerns and institutional trust exert stronger influence on behavioural intentions than technical capability alone. Ref. [83] further demonstrate that stakeholder perceptions and institutional context shape the interpretation and implementation of self-sovereign identity technologies, illustrating that behavioural responses are embedded within broader socio-technical and regulatory environments.
Trust emerges as a particularly influential determinant of sustained engagement. Ref. [98] find that continued use of online banking depends less on initial adoption drivers and more on trust, satisfaction, and perceived value, confirming that long-term engagement is grounded in behavioural outcomes rather than technical availability. Ref. [75] similarly show that trust and privacy concerns govern participation in multi-party data sharing platforms, reinforcing the primacy of institutional confidence over technical safeguards alone.
User experience influences security-related behaviour. Refs. [92,93] demonstrate that behavioural preparedness enhances resilience to misinformation, showing that psychological factors shape trust judgments and decision making under uncertainty. Ref. [95] confirms that mobile payment adoption depends not only on perceived security but also on compatibility, innovativeness, and social influence, illustrating the interaction between technical, social, and behavioural determinants.
For example, in PSD2-compliant systems, user reluctance to share data with third-party providers is mitigated when platforms provide transparent consent mechanisms and visible trust signals [50]. This illustrates how behavioural factors directly shape both adoption and security outcomes within regulated technological environments.
The evidence demonstrates that OB security cannot be adequately understood through technological or regulatory analysis alone. Users’ trust, perceptions of benefit, usability experiences, and institutional context directly shape system effectiveness and resilience. Recognising this, the proposed tri-dimensional framework integrates technical mechanisms, regulatory structures, and behavioural dynamics into a unified analytical model. By incorporating behavioural cognition alongside technological and policy dimensions, the framework reflects real-world security practices and adoption challenges across diverse regulatory and cultural contexts [114,115].
This integrated perspective provides a realistic and user-focused foundation for analysing OB security and supports the design of resilient, trusted, and inclusive digital financial ecosystems.

5. Results

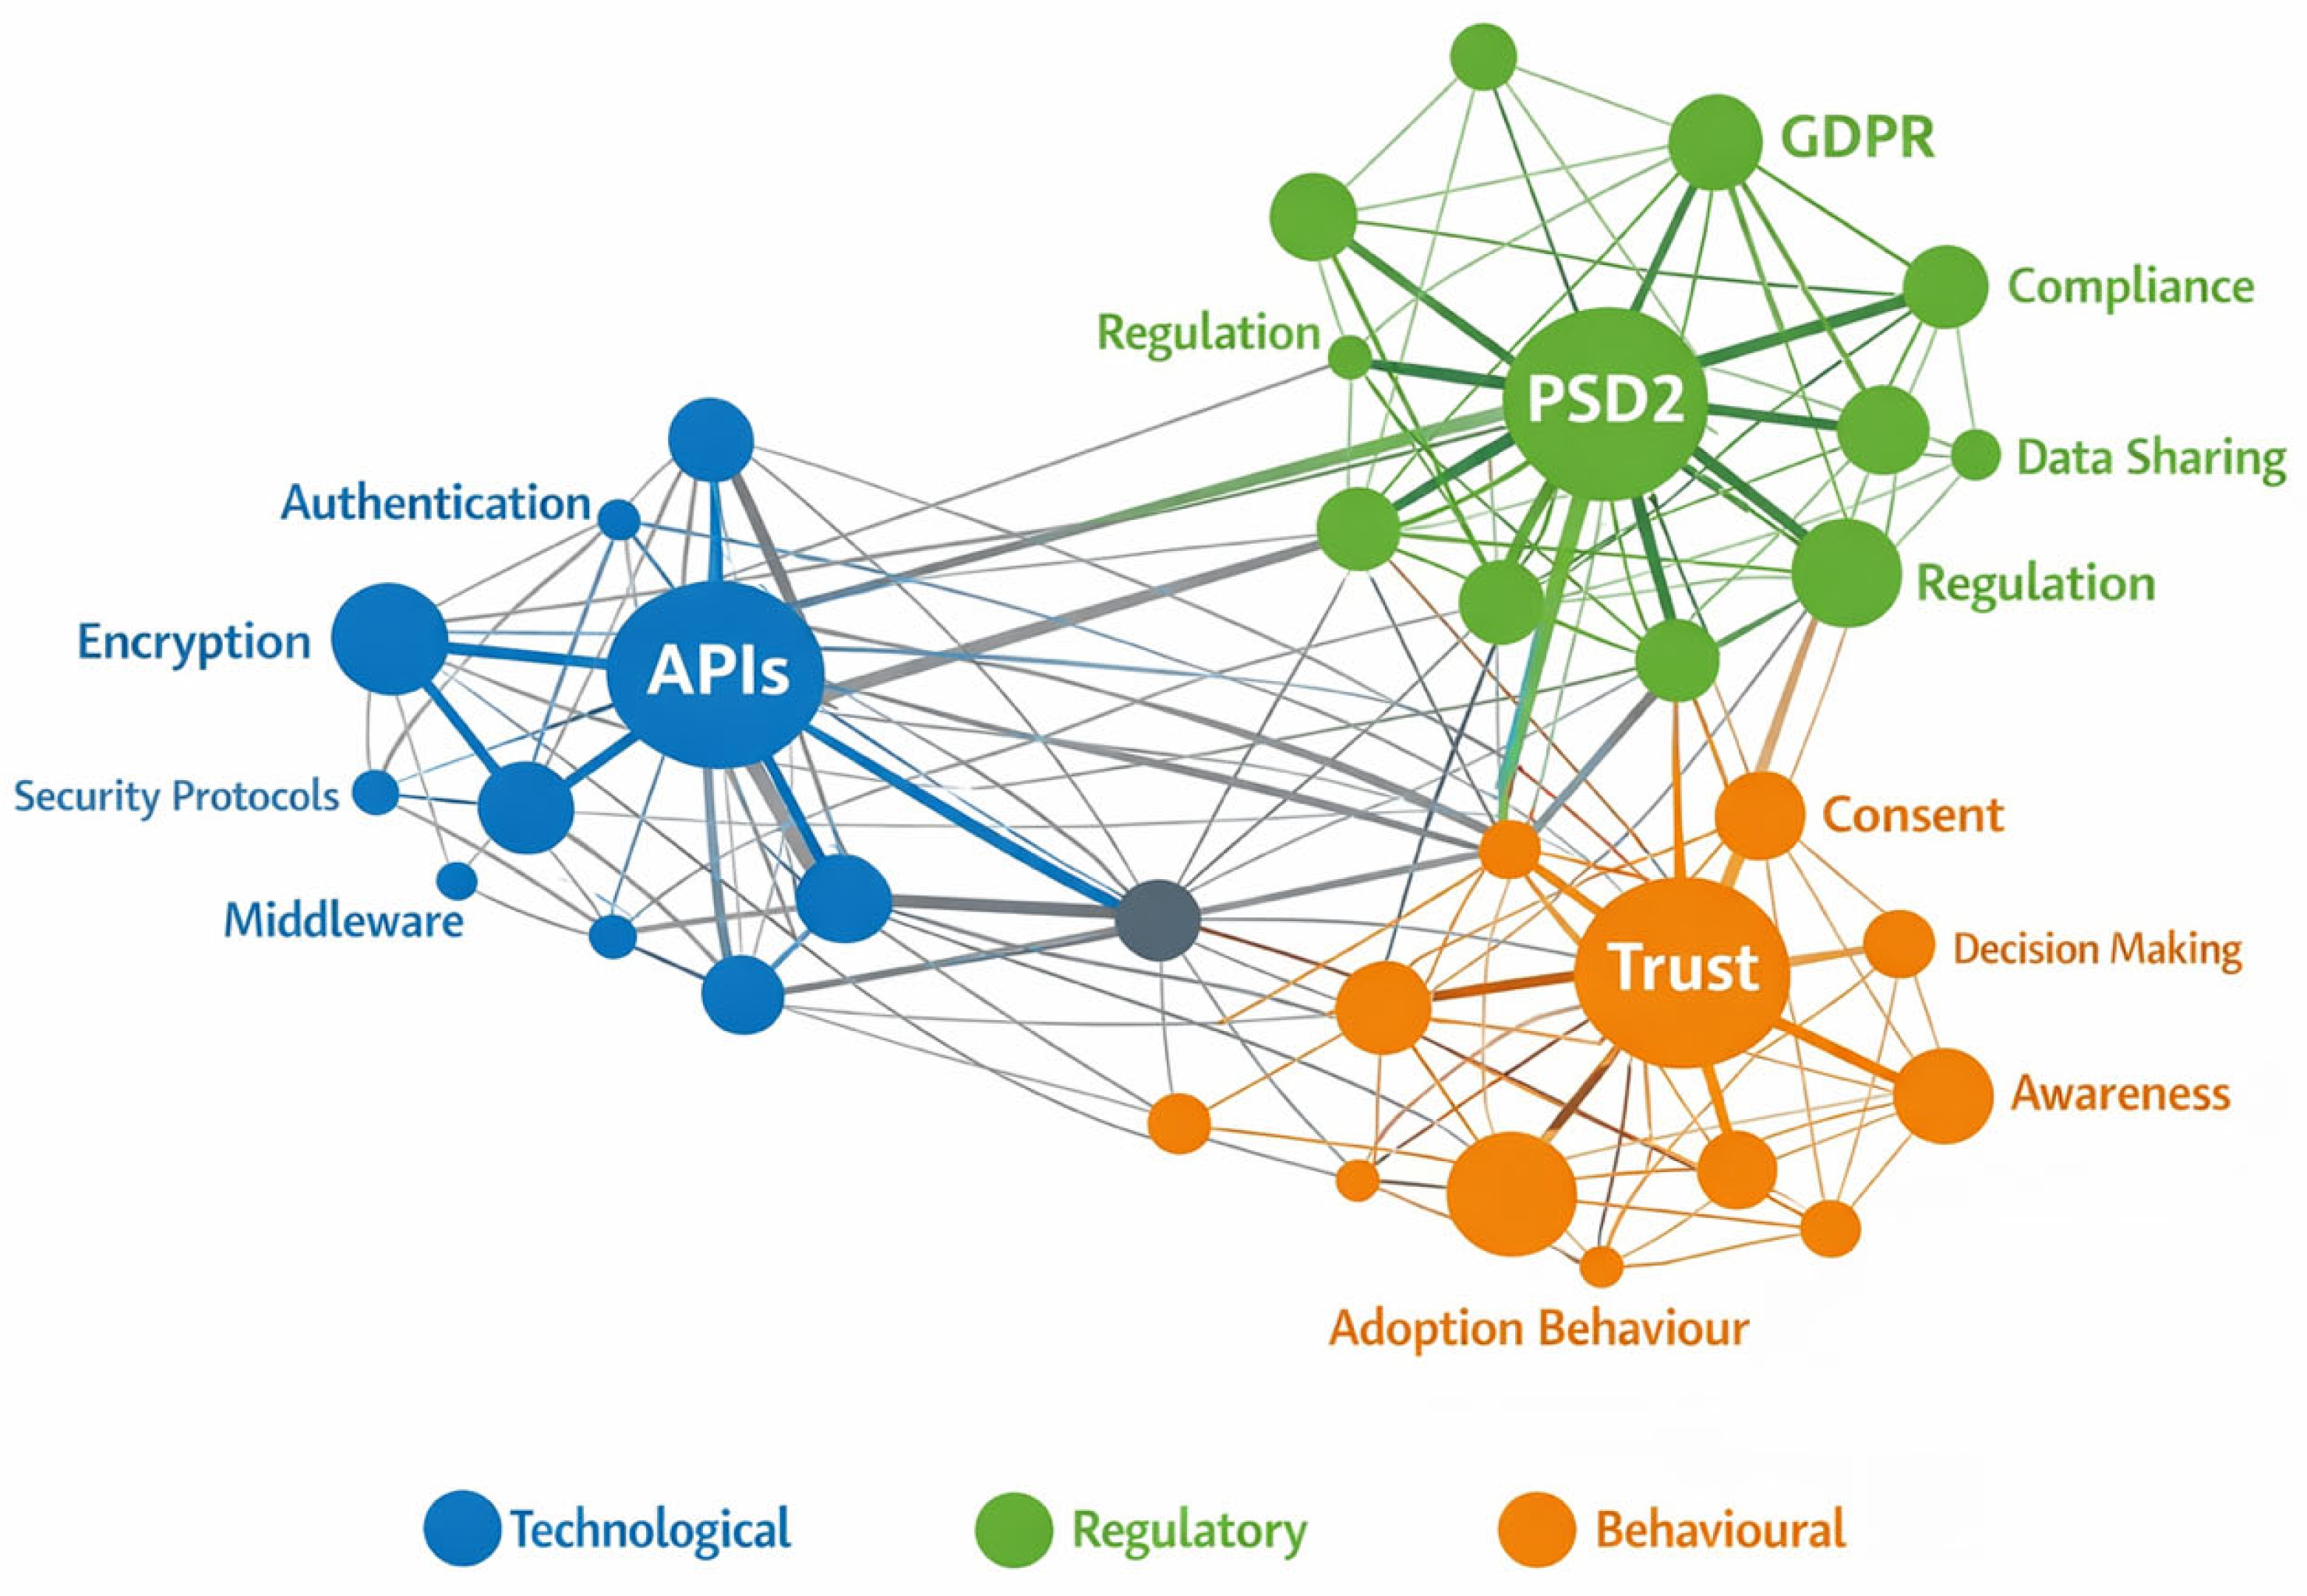
To empirically substantiate the proposed tri-dimensional security framework, a structured bibliometric keyword analysis was conducted on the final dataset of 117 studies included in the systematic literature review. Titles, abstracts, and author keywords were examined and coded using a pre-defined dictionary of technological terms such as APIs, authentication, and encryption; regulatory terms such as PSD2, GDPR, and compliance; and behavioural concepts such as trust, consent, and decision making. Each study could be assigned to more than one category, allowing the identification of cluster overlap and multidimensional integration.
Keyword frequency and co-occurrence patterns were calculated to assess the prominence and interconnections of these dimensions across the literature, as illustrated in Figure 4.
The analysis indicates that technological, regulatory, and behavioural concepts form distinct yet interconnected clusters. Their prominence and overlap suggest that OB security research converges around these three domains. This quantitative mapping provides empirical grounding for the proposed tri-dimensional framework and strengthens the link between literature synthesis and conceptual development. The findings indicate that OB security emerges not solely from technical mechanisms but from the interaction between infrastructure, regulation, and human behaviour, as shown in Table 7.
Technological Security Cluster: To examine the technological dimension of OB security, the full corpus of 117 studies was systematically screened using predefined keywords, including APIs, authentication, encryption, cybersecurity, blockchain, data sharing, protocol, identity management, fraud detection, and access control.
Sixty-eight studies (58.1%) explicitly focused on technological security aspects. Across the full corpus (N = 117): APIs or API-driven architectures appeared in 34 studies (29.0%). Authentication or strong customer authentication featured in 27 studies (23.1%). Encryption or cryptographic mechanisms were discussed in 19 studies (16.2%). Cybersecurity, cyber risk, or fraud detection appeared in 41 studies (35.0%).
The density and centrality of these terms in the co-occurrence network indicate that technological security constitutes the dominant cluster in the literature. This suggests that OB security research remains largely infrastructure-centric. However, most studies prioritise technical control mechanisms, with comparatively limited integration of socio-technical or user-centred considerations.
Regulatory Governance Cluster: The regulatory dimension was identified using keywords such as PSD2, GDPR, compliance, regulation, directive, supervisory authority, policy framework, data protection law, and RegTech.
Fifty-two studies (44.4%) explicitly addressed regulatory governance issues. Within the full corpus: PSD2 was referenced in 21 studies (17.9%). GDPR appeared in 18 studies (15.4%). Compliance frameworks were discussed in 29 studies (24.8%). Broader regulatory governance or RegTech appeared in 33 studies (28.2%).
In the keyword co-occurrence visualisation, these terms form a distinct yet highly connected cluster, frequently bridging technological and behavioural nodes. Regulatory discourse therefore represents a significant, though secondary, pillar of OB security research. The concentration around PSD2 and GDPR reveals a strong European regulatory orientation, suggesting geographic clustering and regulatory diffusion effects within the literature.
Behavioural and Trust Cluster: The behavioural dimension was identified using keywords such as trust, consent, decision making, user adoption, behavioural intention, compliance behaviour, risk perception, and privacy concern.
Forty-nine studies (41.9%) explicitly addressed behavioural factors. Across the full corpus: Trust appeared in 36 studies (30.8%). Consent or privacy understanding featured in 22 studies (18.8%). Decision making or adoption intention was discussed in 31 studies (26.5%). Security behaviour or compliance behaviour appeared in 19 studies (16.2%).
The co-occurrence network positions this cluster around trust and adoption constructs, with observable links to both regulatory compliance and technological safeguards. However, behavioural research within the literature remains predominantly focused on adoption dynamics, with comparatively limited attention to security-specific user practices. This imbalance suggests that, despite its relevance, the behavioural dimension remains underdeveloped relative to infrastructure-oriented research.
Beyond co-occurrence patterns, the reviewed studies provide evidence that behavioural factors emerge through concrete interactions with technological and regulatory structures. For example, studies examining regulatory compliance requirements show that the introduction of strong customer authentication mechanisms, mandated by regulatory frameworks, led to the deployment of multi-factor authentication systems. While these technological implementations enhance security robustness, they also introduce additional steps and complexity into the user experience, which are associated with reduced user adoption and lower perceived usability.
Similarly, other studies indicate that limitations in technological design, particularly in user interface transparency and data-sharing visibility, constrain users’ ability to fully understand consent mechanisms required by regulation. This misalignment increases privacy concerns and weakens trust, influencing behavioural intentions to adopt or continue using OB services.
These findings demonstrate that behavioural outcomes such as trust, adoption, and compliance are not independent variables but are shaped by the interaction between regulatory expectations and technological implementation. The behavioural dimension operates both as a response to and as a mediator of alignment across the three dimensions.
The overlap analysis shows that only 21 studies (17.9%) simultaneously integrate technological, regulatory, and behavioural dimensions. While partial overlaps such as Technology–Regulation (32.5%) and Technology–Behaviour (24.8%) are relatively common, fully integrated approaches remain limited, as shown in Table A1.
This distribution reflects more than variation in research focus. It reveals a structural fragmentation within the literature, where open banking security is predominantly examined through isolated or partially connected perspectives. As a result, the majority of existing studies are not positioned to capture the dynamic interactions through which security risks, adoption barriers, and trust formation emerge in practice.
The absence of tri-dimensional integration in over 80% of the reviewed studies indicates that current approaches are insufficient to explain how regulatory requirements shape technological implementation and how these influence user behaviour. This limitation creates a clear analytical gap in understanding systemic security outcomes.
The proposed tri-dimensional framework directly addresses this gap by providing a unified structure that captures the interdependencies between technological, regulatory, and behavioural dimensions. The framework is not merely an organisational tool, but a necessary analytical model for overcoming the fragmentation identified in the literature.

6. Discussion

6.1. Comparative Implications

The reviewed empirical literature reveals a clear distinction between studies focusing on the technological and security foundations of OB and those examining regulatory, policy, and market dimensions [18,84]. However, the limited integration of these perspectives results in an incomplete understanding of OB security. Incorporating behavioural considerations as a third analytical dimension enables a more comprehensive interpretation of how technological controls, regulatory objectives, and user security behaviour interact to shape effective security practices [116]. This integrated perspective clarifies the dynamics underpinning organisational security decisions, regulatory enforcement, and market responses.
A systematic comparison indicates that technological and regulatory research streams are largely complementary but rarely interconnected. Technological studies provide insights into the secure operational implementation of OB, particularly regarding APIs, authentication, and data protection mechanisms. Regulatory and market analyses, in contrast, examine institutional drivers of adoption, policy rationales, and broader economic implications [13,117]. When considered independently, these streams fail to explain how regulatory intent influences technical design choices or how technological constraints shape regulatory effectiveness.
This limitation becomes particularly evident when examining how misalignments across the three dimensions generate adoption barriers in practice. Evidence from the reviewed literature suggests that regulatory requirements often prioritise formal security compliance, while technological implementations translate these requirements into user-facing mechanisms that introduce additional complexity into the interaction process. Although such measures enhance technical robustness, they frequently reduce usability, thereby discouraging continued engagement and weakening behavioural responses such as trust and adoption, as presented in Table A2.
A similar dynamic can be observed in the context of data-sharing and consent. Regulatory frameworks emphasise informed and transparent user consent, yet technological interfaces do not always effectively communicate these processes in a clear and accessible manner. As a result, users may experience uncertainty and a perceived lack of control, which undermines trust and negatively influences adoption decisions.
These patterns indicate that adoption barriers do not arise from any single dimension in isolation, but from the misalignment between regulatory expectations, technological execution, and user cognitive and behavioural responses. Even well-designed regulatory and technical mechanisms may fail to achieve their intended outcomes when they are not aligned with user behaviour and perception.
This reinforces the need for integrative approaches that explicitly link technological innovation, regulatory objectives, and behavioural realities. Aligning security implementation practices with policy goals and user behaviour is essential for achieving regulatory compliance, trust, and sustained adoption [118]. While existing scholarship has advanced understanding of OB architecture, governance models, and market dynamics, further research is required to connect regulatory ambition, technological execution, and user security behaviour within a unified analytical structure. Such integration is crucial for translating policy frameworks into effective real-world security outcomes.

6.2. Limitations and Future Research

Although research on OB has grown substantially, most studies remain confined to specific disciplinary perspectives. Technological research primarily concentrates on APIs, authentication protocols, and security mechanisms, whereas policy-oriented studies focus on regulatory frameworks, data sharing mandates, and market competition [1,21]. This disciplinary siloing constrains the operationalisation of the tri-dimensional framework, as the interactions between the three security dimensions remain only partially explored. Insights into how user-centred security practices coevolve with regulatory and technical interventions remain indicative rather than empirically validated.
Geographically, the literature is heavily concentrated in advanced economies with mature digital infrastructures, particularly the United Kingdom, the European Union, and Australia. Developing regions in Africa, Latin America, and parts of Asia remain underrepresented. This geographic imbalance limits the generalisability of the framework, as adoption patterns, regulatory enforcement, and trust dynamics may differ substantially across institutional contexts. It also restricts understanding of how OB may support financial inclusion and secure adoption in emerging markets, which may require distinct regulatory and technological strategies.
Methodological limitations are evident. Many studies rely on cross-sectional surveys, secondary datasets, or single-country case studies, restricting causal inference and longitudinal analysis. The temporal evolution of trust, user behaviour, and regulatory effectiveness remains insufficiently understood, limiting the predictive robustness of the proposed framework. Comparative and multi-level research designs linking micro-level behavioural patterns with macro-level regulatory and technological outcomes remain scarce. This gap is particularly significant for the behavioural dimension, which is central to adoption, trust formation, and systemic resilience within OB ecosystems.
Language limitations must be acknowledged. The review included only articles published in English and Portuguese, which may have excluded relevant studies in other languages and thereby reduced the comprehensiveness of the synthesis.
Future research should adopt interdisciplinary approaches integrating regulatory analysis, technological design, and behavioural science. Combining cross-regional datasets on regulatory indicators, technological maturity, and user security behaviour would enable empirical testing of the interactions proposed in the tri-dimensional framework. Longitudinal and comparative studies are needed to assess how trust, security behaviour, and regulatory effectiveness evolve across institutional contexts and over time. Strengthening empirical attention to user security behaviour is essential to ensure that OB systems are not only technically and regulatorily robust but also aligned with human behaviour, thereby promoting secure, confident, and sustainable engagement.

7. Conclusions

This study provides a comprehensive review of the literature on security challenges in OB, synthesising research addressing technological and security foundations with studies examining regulatory, policy, and market dimensions [119]. The review identifies a critical gap in existing scholarship, namely the insufficient integration of behavioural factors, and responds by operationalising a tri-dimensional OB security framework.
The findings demonstrate that technological research predominantly emphasises data protection, authentication mechanisms, and secure API design, whereas regulatory and market-oriented studies focus on governance structures, data ownership, and the promotion of competition and innovation. Considered independently, these perspectives provide only a partial account of OB security. Behavioural factors are equally decisive, as user perceptions, trust formation, and security practices directly shape adoption, compliance, and ecosystem resilience.
By integrating these three security dimensions, this study advances a holistic conceptualisation of OB security. The proposed tri-dimensional framework facilitates alignment between technical standards, regulatory coordination, market readiness, and user security behaviour. Achieving a secure, trusted, and sustainable OB ecosystem therefore requires coordinated attention to technological infrastructure, regulatory governance, and human security practices. This integrative contribution offers actionable guidance for researchers, practitioners, and policymakers seeking to design resilient and user-centred OB systems.

Author Contributions

Conceptualization, C.W.; methodology, C.W.; formal analysis, C.W.; investigation, C.W.; data curation, C.W.; writing—original draft preparation, C.W.; writing—review and editing, C.W.; visualization, C.W.; supervision, C.W. and C.T.; validation, C.W. and C.T. All authors have read and agreed to the published version of the manuscript.

Funding

This research was funded by NOVA Information Management School (NOVA IMS), NOVA University Lisbon.

Data Availability Statement

The data supporting the findings of this study are derived from publicly accessible sources. The dataset was compiled from major academic databases, including Scopus, Web of Science, IEEE Xplore, and Google Scholar, in accordance with the search strategy described in the methodology and aligned with PRISMA 2020 guidelines. Extracted data are available from the corresponding author upon reasonable request.

Acknowledgments

Not applicable.

Conflicts of Interest

The authors declare no conflicts of interest.

Appendix A

Table A1. Table of co-occurrence frequency.
DimensionKeywordStudies (N)Percent of Studies
TechnologyAuthentication2723.1%
TechnologyEncryption1916.2%
TechnologySecurity Protocols4135.0%
TechnologyMiddleware54.27%
TechnologyAPIs3429.0%
RegulationPSD22117.9%
RegulationGDPR1815.4%
RegulationCompliance2924.8%
RegulationData Sharing75.98%
RegulationRegulation3328.2%
BehaviouralTrust3630.8%
BehaviouralConsent2218.8%
BehaviouralDecision Making3126.5%
BehaviouralAwareness65.13%
BehaviouralAdoption Behaviour1916.2%
Table A2. Table of co-occurrence binary exchange.
Study TypeTechnologyRegulationBehavioural
Study ID123
APIs110
Authentication101
Encryption110
Security Protocols111
Middleware101
PSD2111
GDPR011
Compliance110
Data Sharing110
Regulation110
Trust111
Consent110
Decision Making101
Awareness011
Adoption Behaviour001

References

  1. Banerjee, P. System Integration, From Middleware to APIs. Int. J. Comput. Trends Technol. 2024, 72, 37–45. [Google Scholar] [CrossRef] [Scilit]
  2. Omarini, A.E. Banks and Fintechs: How to Develop a Digital Open Banking Approach for the Bank’s Future. Int. Bus. Res. 2018, 11, 23. [Google Scholar] [CrossRef] [Scilit]
  3. Braithwaite, J. Authorized Push Payment’ Bank Fraud: What Does an Effective Regulatory Response Look Like? J. Financ. Regul. 2024, 10, 174–193. [Google Scholar] [CrossRef] [Scilit]
  4. Ngan, J. “The View from below”: Resistance and Change in Authorised Push Payment Fraud. J. Econ. Criminol. 2025, 9, 100166. [Google Scholar] [CrossRef] [Scilit]
  5. Laplante, P.; Kshetri, N. Open Banking: Definition and Description. Computer 2021, 54, 122–128. [Google Scholar] [CrossRef] [Scilit]
  6. Casaló, L.V.; Flavián, C.; Guinalíu, M. The Role of Security, Privacy, Usability and Reputation in the Development of Online Banking. Online Inf. Rev. 2007, 31, 583–603. [Google Scholar] [CrossRef] [Scilit]
  7. Ege Oruç, Ö.; Tatar, Ç. An Investigation of Factors That Affect Internet Banking Usage Based on Structural Equation Modeling. Comput. Human Behav. 2017, 66, 232–235. [Google Scholar] [CrossRef] [Scilit]
  8. Wang, S.; Asif, M.; Shahzad, M.F.; Ashfaq, M. Data Privacy and Cybersecurity Challenges in the Digital Transformation of the Banking Sector. Comput. Secur. 2024, 147, 104051. [Google Scholar] [CrossRef] [Scilit]
  9. Podsakoff, P.; MacKenzie, S.; Lee, J.-Y.; Podsakoff, N. Common Method Biases in Behavioral Research: A Critical Review of the Literature and Recommended Remedies. J. Appl. Psychol. 2003, 88, 879–903. [Google Scholar] [CrossRef] [Scilit]
  10. Hyon, R.; Kleinbaum, A.M.; Parkinson, C. Social Network Proximity Predicts Similar Trajectories of Psychological States: Evidence from Multi-Voxel Spatiotemporal Dynamics. Neuroimage 2020, 216, 116492. [Google Scholar] [CrossRef] [Scilit]
  11. Polasik, M.; Butor-Keler, A.; Widawski, P.; Keler, G. Evaluating the Regulatory Approach to Open Banking in Europe: An Empirical Study. Financ. Law Rev. 2024, 34, 59–90. [Google Scholar] [CrossRef] [Scilit]
  12. Babina, T.; Bahaj, S.; Buchak, G.; De Marco, F.; Foulis, A.; Gornall, W.; Mazzola, F.; Yu, T. Customer Data Access and Fintech Entry: Early Evidence from Open Banking. J. Financ. Econ. 2025, 169, 103950. [Google Scholar] [CrossRef] [Scilit]
  13. Jafri, J.A.; Mohd Amin, S.I.; Abdul Rahman, A.; Mohd Nor, S. A Systematic Literature Review of the Role of Trust and Security on Fintech Adoption in Banking. Heliyon 2024, 10, e22980. [Google Scholar] [CrossRef] [Scilit] [PubMed]
  14. Arner, D.W.; Barberis, J.; Buckley, R.P.; Arner, D.; Barberis, J. FinTech, RegTech, and the Reconceptualization of Financial Regulation. Northwestern J. Int. Law Bus. 2017, 37, 371. [Google Scholar]
  15. Frei, C. Open Banking: Opportunities and Risks. SSRN Electron. J. 2023, 4316760. Available online: https://papers.ssrn.com/sol3/papers.cfm?abstract_id=4316760 (accessed on 2 December 2025). [CrossRef] [Scilit]
  16. Tariq, M.; Maryam, S.Z.; Shaheen, W.A. Cognitive Factors and Actual Usage of Fintech Innovation: Exploring the UTAUT Framework for Digital Banking. Heliyon 2024, 10, e35582. [Google Scholar] [CrossRef] [Scilit]
  17. Nikkhah, H.R.; Grover, V.; Sabherwal, R. Post Hoc Security and Privacy Concerns in Mobile Apps: The Moderating Roles of Mobile Apps’ Features and Providers. Inf. Comput. Secur. 2024, 32, 1–37. [Google Scholar] [CrossRef] [Scilit]
  18. Modesti, P.; Freitas, L.; Shotomiwa, Q.; Almehrej, A. Security Analysis of the Open Banking Account and Transaction API Protocol. Cyber Secur. Appl. 2025, 3, 100097. [Google Scholar] [CrossRef] [Scilit]
  19. He, Z.; Huang, J.; Zhou, J. Open Banking: Credit Market Competition When Borrowers Own the Data. J. Financ. Econ. 2023, 147, 449–474. [Google Scholar] [CrossRef] [Scilit]
  20. Chiew, K.L.; Yong, K.S.C.; Tan, C.L. A Survey of Phishing Attacks: Their Types, Vectors and Technical Approaches. Expert Syst. Appl. 2018, 106, 1–20. [Google Scholar] [CrossRef] [Scilit]
  21. Torshin, I. Open Banking and API-Driven Financial Innovation: Opportunities and Risks. 2025. Available online: https://www.researchgate.net/publication/390486463_Open_Banking_and_API-Driven_Financial_Innovation_Opportunities_and_Risks (accessed on 4 November 2025).
  22. Polo, A.; Taburet, A.; Vo, Q.-A. Screening Using a Menu of Contracts: A Structural Model for Lending Markets. J. Financ. Econ. 2025. Available online: https://www.bankofengland.co.uk/-/media/boe/files/working-paper/2024/screening-using-a-menu-of-contracts-a-structural-model-of-lending-markets.pdf (accessed on 2 December 2025).
  23. Ramdani, B.; Rothwell, B.; Boukrami, E. Open Banking: The Emergence of New Digital Business Models. Int. J. Innov. Technol. Manag. 2020, 17, 2050033. [Google Scholar] [CrossRef] [Scilit]
  24. Waliullah, M.; George, M.Z.H.; Hasan, M.T.; Alam, M.K.; Munira, M.S.K.; Siddiqui, N.A. Assessing the Influence of Cybersecurity Threats and Risks on the Adoption and Growth of Digital Banking: A Systematic Literature Review. Am. J. Adv. Technol. Eng. Solut. 2025, 1, 226–257. [Google Scholar] [CrossRef] [Scilit]
  25. Tam, C.; de Matos Conceição, C.; Oliveira, T. What Influences Employees to Follow Security Policies? Saf. Sci. 2022, 147, 105595. [Google Scholar] [CrossRef] [Scilit]
  26. Beautement, A.; Sasse, A.; Wonham, M. The Compliance Budget: Managing Security Behaviour in Organisations. J. ACM 2008. [Google Scholar] [CrossRef] [Scilit]
  27. Fett, D.; Hosseyni, P.; Kuesters, R. An Extensive Formal Security Analysis of the OpenID Financial-Grade API. arXiv 2019, arXiv:1901.11520. [Google Scholar] [CrossRef] [Scilit]
  28. Hanif, Y.; Lallie, H.S. Security Factors on the Intention to Use Mobile Banking Applications in the UK Older Generation (55+). A Mixed-Method Study Using Modified UTAUT and MTAM—With Perceived Cyber Security, Risk, and Trust. Technol. Soc. 2021, 67, 101693. [Google Scholar] [CrossRef] [Scilit]
  29. European Commission. Directive 2007/64/EC of the European Parliament and of the Council of 13 November 2007 on Payment Services in the Internal Market Amending Directives 97/7/EC, 2002/65/EC, 2005/60/EC and 2006/48/EC and Repealing Directive 97/5/EC (Text with EEA Relevance); European Commission 2007. Available online: https://eur-lex.europa.eu/eli/dir/2007/64/oj/eng (accessed on 14 May 2025).
  30. European Union. Directive (EU) 2015/ of the European Parliament and of the Council of 25 November 2015 on Payment Services in the Internal Market, Amending Directives 2002/65/EC, 2009/110/EC and 2013/36/EU and Regulation (EU) No 1093/2010, and Repealing Directive 2007/64/EC. Off. J. Eur. Union 2015, L337, 35–127. [Google Scholar]
  31. Gimigliano, G.; Beroš, M.B. The Payments Services Directive II; Edward Elgar Publishing Ltd.: Cheltenham, UK, 2021. [Google Scholar]
  32. Adiningtyas, H.; Auliani, A.S. Sentiment Analysis for Mobile Banking Service Quality Measurement. Procedia Comput. Sci. 2024, 234, 40–50. Available online: https://www.sciencedirect.com/science/article/pii/S1877050924003363 (accessed on 14 May 2025). [CrossRef] [Scilit]
  33. Merhi, M.; Hone, K.; Tarhini, A. A Cross-Cultural Study of the Intention to Use Mobile Banking between Lebanese and British Consumers: Extending UTAUT2 with Security, Privacy and Trust. Technol. Soc. 2019, 59, 101151. Available online: https://www.sciencedirect.com/science/article/pii/S0160791X19300132 (accessed on 14 May 2025). [CrossRef] [Scilit]
  34. Liu, J.; Huang, S.; Fu, Q.; Luo, Y.; Qin, S.; Cao, Y.; Zhai, J.; Yang, S. The Open Banking Era: An Optimal Model for the Emergency Fund. Expert Syst. Appl. 2024, 244, 122915. [Google Scholar] [CrossRef] [Scilit]
  35. Tam, C.; Oliveira, T. Does Culture Influence M-Banking Use and Individual Performance? Inf. Manag. 2019, 56, 356–363. [Google Scholar] [CrossRef] [Scilit]
  36. Gill, S.S.; Tuli, S.; Xu, M.; Singh, I.; Singh, K.V.; Lindsay, D.; Tuli, S.; Smirnova, D.; Singh, M.; Jain, U.; et al. Transformative Effects of IoT, Blockchain and Artificial Intelligence on Cloud Computing: Evolution, Vision, Trends and Open Challenges. Internet Things 2019, 8, 100118. [Google Scholar] [CrossRef] [Scilit]
  37. AWS. Financial Services Industry Lens—AWS Well-Architected Framework. 2024. Available online: https://docs.aws.amazon.com/wellarchitected/latest/financial-services-industry-lens/financial-services-industry-lens.html (accessed on 20 December 2025).
  38. Puschmann, T. Fintech. Bus. Inf. Syst. Eng. 2017, 59, 69–76. [Google Scholar] [CrossRef] [Scilit]
  39. Cardoso, S.; Martinez, L.F. Online Payments Strategy: How Third-Party Internet Seals of Approval and Payment Provider Reputation Influence the Millennials’ Online Transactions. Electron. Commer. Res. 2019, 19, 189–209. [Google Scholar] [CrossRef] [Scilit]
  40. Niranjan, S.K.; Raja, J.; Rajini, A.R. Internet of Things (IoT). In Proceedings of the 4th International Conference on Innovative Computing and Communication (ICICC 2021) SSRN, 23 April 2021; Available online: https://ssrn.com/abstract=3832727 (accessed on 20 December 2025).
  41. Liao, C.H.; Guan, X.Q.; Cheng, J.H.; Yuan, S.M. Blockchain-Based Identity Management and Access Control Framework for Open Banking Ecosystem. Future Gener. Comput. Syst. 2022, 135, 450–466. [Google Scholar] [CrossRef] [Scilit]
  42. Takieddine, S.; Sun, J. Internet Banking Diffusion: A Country-Level Analysis. Electron. Commer. Res. Appl. 2015, 14, 361–371. [Google Scholar] [CrossRef] [Scilit]
  43. Sahoo, B.; Pathak, A.; Deco, G.; Banerjee, A.; Roy, D. Lifespan Associated Global Patterns of Coherent Neural Communication. Neuroimage 2020, 216, 116824. [Google Scholar] [CrossRef] [Scilit]
  44. Ling, G.M.; Fern, Y.S.; Boon, L.K.; Huat, T.S. Understanding Customer Satisfaction of Internet Banking: A Case Study in Malacca. Procedia Econ. Financ. 2016, 37, 80–85. [Google Scholar] [CrossRef] [Scilit]
  45. Andrade, R.O.; Yoo, S.G. Cognitive Security: A Comprehensive Study of Cognitive Science in Cybersecurity. J. Inf. Secur. Appl. 2019, 48, 102352. [Google Scholar] [CrossRef] [Scilit]
  46. The World Bank. World Bank Fast Payments Toolkit Case Study: United Kingdom. 2021. Available online: https://fastpayments.worldbank.org/sites/default/files/2021-09/World_Bank_FPS_UK_FPS_Case_Study.pdf (accessed on 13 November 2025).
  47. Greene, C.; Rysman, M.; Schuh, S.; Shy, O. Costs and Benefits of Building Faster Payment Systems: The U.K. Experience and Implications for the United States; Federal Reserve Bank of Boston: Boston, MA, USA, 2014; p. 47. [Google Scholar]
  48. Aboobucker, I.; Bao, Y. What Obstruct Customer Acceptance of Internet Banking? Security and Privacy, Risk, Trust and Website Usability and the Role of Moderators. J. High Technol. Manag. Res. 2018, 29, 109–123. [Google Scholar] [CrossRef] [Scilit]
  49. Desiraju, K.; Mishra, A.N.; Sengupta, P. Customer Perceptions on Open Banking Apps: Insights Using Structural Topic Modeling. J. Retail. Consum. Serv. 2024, 81, 104029. [Google Scholar] [CrossRef] [Scilit]
  50. Gounari, M.; Stergiopoulos, G.; Pipyros, K.; Gritzalis, D. Harmonizing Open Banking in the European Union: An Analysis of PSD2 Compliance and Interrelation with Cybersecurity Frameworks and Standards. Int. Cybersecur. Law Rev. 2024, 5, 79–120. [Google Scholar] [CrossRef] [Scilit]
  51. European Union. Legislative Acts Regulations. Regulation (EU) 2016/679 Of the European Parliament and of The Council of 27 April 2016 on the Protection of Natural Persons with Regard to the Processing of Personal Data and on the Free Movement of Such Data, and Repealing Directive 95/46/EC (General Data Protection Regulation) (Text with EEA Relevance). Off. J. Eur. Union 2016, L679, 1–88. [Google Scholar]
  52. ENISA. Data Protection, 2024. European Union Agency for Cybersecurity. Available online: https://www.enisa.europa.eu/about-enisa/data-protection/data-protection (accessed on 9 October 2025).
  53. Moody, G.D.; Siponen, M. Using the Theory of Interpersonal Behavior to Explain Non-Work-Related Personal Use of the Internet at Work. Inf. Manag. 2013, 50, 322–335. [Google Scholar] [CrossRef] [Scilit]
  54. Hanafizadeh, P.; Keating, B.W.; Khedmatgozar, H.R. A Systematic Review of Internet Banking Adoption. Telemat. Inform. 2014, 31, 492–510. [Google Scholar] [CrossRef] [Scilit]
  55. Vanini, P.; Rossi, S.; Zvizdic, E.; Domenig, T. Online Payment Fraud: From Anomaly Detection to Risk Management. Financ. Innov. 2023, 9, 66. [Google Scholar] [CrossRef] [Scilit]
  56. Souza, C.; Redmiles, D. On The Roles of APIs in the Coordination of Collaborative Software Development. Comput. Support. Coop. Work. 2009, 18, 445–475. [Google Scholar] [CrossRef] [Scilit]
  57. Li, J.; Chen, C.; Rahimi Azghadi, M.; Ghodosi, H.; Pan, L.; Zhang, J. Security and Privacy Problems in Voice Assistant Applications: A Survey. Comput. Secur. 2023, 134, 103448. [Google Scholar] [CrossRef] [Scilit]
  58. Hilal, W.; Gadsden, S.A.; Yawney, J. Financial Fraud: A Review of Anomaly Detection Techniques and Recent Advances. Expert Syst. Appl. 2022, 193, 116429. [Google Scholar] [CrossRef] [Scilit]
  59. Amin, H. Internet Banking Adoption Among Young Intellectuals. J. Internet Bank. Commer. 2007, 12. Available online: https://www.icommercecentral.com/open-access/internet-banking-adoption-among-young-intellectuals.php?aid=38527 (accessed on 26 July 2025).
  60. Martins, C.; Oliveira, T.; Popovič, A. Understanding the Internet Banking Adoption: A Unified Theory of Acceptance and Use of Technology and Perceived Risk Application. Int. J. Inf. Manag. 2014, 34, 1–13. [Google Scholar] [CrossRef] [Scilit]
  61. Yang, Z.; Wu, J.; Xu, L.; Deng, Z.; Tang, Y.; Gao, J.; Hu, Y.; Zhang, Y.; Qin, S.; Li, C.; et al. Individualized Psychiatric Imaging Based on Inter-Subject Neural Synchronization in Movie Watching. Neuroimage 2020, 216, 116227. [Google Scholar] [CrossRef] [Scilit] [PubMed]
  62. Xu, Z.; Wang, Q.; Wang, Z.; Liu, D.; Wen, S.; Hanson, R. PPM: A Provenance-Provided Data Sharing Model for Open Banking via Blockchain. In Proceedings of the ACM International Conference Proceeding Series; Association for Computing Machinery: New York, NY, USA, 4 February 2020. [Google Scholar]
  63. Netherlands PwC. PSD2 in Europe: The Start to a New Future of Banking? 2025. Available online: https://www.pwc.nl/en/industries/banking/finance-and-regulatory-reporting/psd2-in-europe.html (accessed on 27 December 2025).
  64. ACCC. Targeting Scams: Report of the National Anti-Scam Centre on Scams Data and Activity 2024. Available online: https://www.accc.gov.au/about-us/publications/serial-publications/targeting-scams-reports-on-scams-activity/targeting-scams-report-of-the-national-anti-scam-centre-on-scams-data-and-activity-2024 (accessed on 10 December 2025).
  65. The National Bank of Angola (BNA). Angola’s Payment System Law. 2020. Available online: https://www.bna.ao/#/pt/legislacao-e-normas/legislacao-financeira/lei-sistema-pagamentos/detalhe/72 (accessed on 20 October 2025).
  66. Njoroge, P. The Central Bank of Kenya Act. 2022. Available online: https://new.kenyalaw.org/akn/ke/act/1966/15/eng@2025-11-04 (accessed on 16 December 2025).
  67. GOV.BR. Brazilian Data Protection Law LGPD. 2018. Available online: https://www.gov.br/anpd/pt-br/centrais-de-conteudo/outros-documentos-e-publicacoes-institucionais/lgpd-en-lei-no-13-709-capa.pdf (accessed on 19 May 2025).
  68. GOV.AE. Federal Decree-Law No. (33) of 2021. 2021. Available online: https://uaelegislation.gov.ae/en/legislations/1541/download (accessed on 22 October 2025).
  69. Serrado, J.; Pereira, R.F.; Mira da Silva, M.; Scalabrin Bianchi, I. Information Security Frameworks for Assisting GDPR Compliance in Banking Industry. Digit. Policy Regul. Gov. 2020, 22, 227–244. [Google Scholar] [CrossRef] [Scilit]
  70. BIS.org. Rethinking Regulations in an Interconnected Financial System. 2025. Available online: https://www.bis.org/review/r250901e.pdf (accessed on 15 September 2025).
  71. Babina, T.; Howell, S.T. Entrepreneurial Spillovers from Corporate R&D. J. Labor Econ. 2024, 42, 469–509. [Google Scholar] [CrossRef] [Scilit]
  72. Hair, J.F., Jr.; Hult, T.M.; Ringle, C.M.; Sarstedt, M.; Danks, N.P.; Ray, S. Classroom Companion. In Business Partial Least Squares Structural Equation Modeling (PLS-SEM) Using R AAWorkbook; Springer: Cham, Switzerland, 2021. [Google Scholar]
  73. Anderson, R.E.; Hair, J.F.; Black, W.C.; Babin, B.J. Multivariate Data Analysis; Cengage Learning EMEA: Andover, UK, 2010. [Google Scholar]
  74. Chen, P.H.A.; Jolly, E.; Cheong, J.H.; Chang, L.J. Intersubject Representational Similarity Analysis Reveals Individual Variations in Affective Experience When Watching Erotic Movies. Neuroimage 2020, 216, 116851. [Google Scholar] [CrossRef] [Scilit]
  75. Lomotey, R.K.; Kumi, S.; Deters, R. Data Trusts as a Service: Providing a Platform for Multi-party Data Sharing. Int. J. Inf. Manag. Data Insights 2022, 2, 100075. [Google Scholar] [CrossRef] [Scilit]
  76. Simchon, A.; Zipori, T.; Teitelbaum, L.; Lewandowsky, S.; van der Linden, S. A Signal Detection Theory Meta-Analysis of Psychological Inoculation Against Misinformation. Curr. Opin. Psychol. 2026, 67, 102194. Available online: https://www.sciencedirect.com/science/article/pii/S2352250X25002076?via%3Dihub (accessed on 15 September 2025). [CrossRef] [Scilit]
  77. Tan, M.; Teo, T. Factors Influencing the Adoption of Internet Banking. J. Assoc. Inf. Syst. 2000, 1, 1–44. [Google Scholar] [CrossRef] [Scilit]
  78. Iman, N.; Nugroho, S.S.; Junarsin, E.; Pelawi, R.Y. Is Technology Truly Improving the Customer Experience? Analysing the Intention to Use Open Banking in Indonesia. Int. J. Bank Mark. 2023, 41, 1521–1549. [Google Scholar] [CrossRef] [Scilit]
  79. Scheepers, R.; Mathiassen, L.; Ahmad, A.; Bosua, R.; Baskerville, R. Managing Intellectual Property Leakage in the Digital Era: An Integrated Process Model. Int. J. Inf. Manag. 2026, 87, 103021. [Google Scholar] [CrossRef] [Scilit]
  80. Hair, J.F.; Hult, G.T.M.; Ringle, C.M.; Sarstedt, M. A Primer on Partial Least Squares Structural Equation Modeling (PLS-SEM); Sage Publishing: Thousand Oaks, CA, USA, 2017; ISBN 9781483377445. [Google Scholar]
  81. Akyildirim, E.; Corbet, S.; Mukherjee, A.; Ryan, M. Global Perspectives on Open Banking: Regulatory Impacts and Market Response. J. Int. Financ. Mark. Inst. Money 2025, 101, 102159. [Google Scholar] [CrossRef] [Scilit]
  82. Zhang, W.; Bi, C.; Yang, F.; Wang, D. Mitigating Moral Hazard in Financial Leasing: The Role of Open Banking. Expert Syst. Appl. 2025, 294, 128831. [Google Scholar] [CrossRef] [Scilit]
  83. Weigl, L.; Barbereau, T.; Fridgen, G. The Construction of Self-Sovereign Identity: Extending the Interpretive Flexibility of Technology towards Institutions. Gov. Inf. Q. 2023, 40, 101873. [Google Scholar] [CrossRef] [Scilit]
  84. Kroszner, R.S.; Strahan, P.E. What Drives Deregulation? Economics and Politics of the Relaxation of Bank Branching Restrictions. Q. J. Econ. 1999, 114, 1437–1467. Available online: https://academic.oup.com/qje/article-abstract/114/4/1437/1934050?redirectedFrom=fulltext (accessed on 15 September 2025). [CrossRef] [Scilit]
  85. Ghaharian, K.; Azizsoltani, M.; Cohen, C.; Puranik, P.; Chagas, B. Characterising Online Gamblers Exceeding Financial Risk Thresholds in the UK: A Retrospective Analysis Using Open Banking Data. Public Health 2026, 251, 106080. [Google Scholar] [CrossRef] [Scilit] [PubMed]
  86. EBA. European Banking Authority, Report 2011. Available online: https://www.eba.europa.eu/sites/default/files/documents/10180/601534/9d498bb4-b875-4b25-b8f0-91ac3173b222/EBA2012_online_final2.pdf (accessed on 14 June 2025).
  87. Financial Conduct Authority (FCA). The Future of Open Banking and the Joint Regulatory Oversight Committee. 2024. Available online: https://www.fca.org.uk/firms/future-open-banking-joint-regulatory-oversight-committee (accessed on 7 November 2025).
  88. Financial Conduct Authority (FCA). Open Banking and Open Finance in the UK; 6 October 2025. Available online: https://www.fca.org.uk/publication/research-notes/open-banking-open-finance-uk.pdf (accessed on 7 November 2025).
  89. The Central Bank of Kenya (CBK). Banking Sector Innovation Survey 2024. 2024. Available online: https://www.centralbank.go.ke/uploads/banking_sector_reports/1736029340_Banking%20Sector%20Innovation%20Survey%202024.pdf (accessed on 17 November 2025).
  90. The Central Bank of Nigeria (CBN). Operational Guidelines for Open Banking in Nigeria. 2023. Available online: https://nairametrics.com/wp-content/uploads/2023/03/Operational-Guidelines-for-Open-Banking-in-Nigeria.pdf (accessed on 2 November 2025).
  91. The Central Bank of Nigeria (CBN). Payments System Supervision. 2021. Available online: https://www.cbn.gov.ng/PaymentsSystem/ (accessed on 13 November 2025).
  92. Tam, C.; Santos, D.; Oliveira, T. Exploring the Influential Factors of Continuance Intention to Use Mobile Apps: Extending the Expectation Confirmation Model. Inf. Syst. Front. 2020, 22, 243–257. [Google Scholar] [CrossRef] [Scilit]
  93. Pinochet, L.H.C.; Bastos, D.C.M.; Pardim, V.I.; Sun, V.; dos Santos, M. Predicting the Intention to Use the Investment Aggregate Functionality in the Context of Open Banking Using the Artificial Neural Network Approach. Procedia Comput. Sci. 2023, 221, 733–740. [Google Scholar] [CrossRef] [Scilit]
  94. Gozman, D.; Hedman, J.; Sylvest, K. Open Banking: Emergent Roles, Risks & Opportunities. In Proceedings of the 26th European Conference on Information Systems (ECIS2018), Portsmouth, UK, 23–28 June 2018; Available online: https://research-api.cbs.dk/ws/portalfiles/portal/58899604/Gozman_Hedman_Sylvest.pdf (accessed on 3 November 2025).
  95. Oliveira, T.; Thomas, M.; Baptista, G.; Campos, F. Mobile Payment: Understanding the Determinants of Customer Adoption and Intention to Recommend the Technology. Comput. Human Behav. 2016, 61, 404–414. [Google Scholar] [CrossRef] [Scilit]
  96. Dinçkol, D.; Ozcan, P.; Zachariadis, M. Regulatory Standards and Consequences for Industry Architecture: The Case of UK Open Banking. Res. Policy 2023, 52, 104760. [Google Scholar] [CrossRef] [Scilit]
  97. Colangelo, G.; Khandelwal, P. The Many Shades of Open Banking: A Comparative Analysis of Rationales and Models. Internet Policy Rev. 2025, 14, 1821. [Google Scholar] [CrossRef] [Scilit]
  98. Colangelo, G. Open Banking Goes to Washington: Lessons from the EU on Regulatory-Driven Data Sharing Regimes. Comput. Law Secur. Rev. 2024, 54, 106018. [Google Scholar] [CrossRef] [Scilit]
  99. de Araluze, G.K.B.; Cassinello Plaza, N. Open Banking: A Bibliometric Analysis-Driven Definition. PLoS ONE 2022, 17, e0275496. [Google Scholar] [CrossRef] [Scilit]
  100. Fang, J.; Zhu, J. The Impact of Open Banking on Traditional Lending in the BRICS. Financ. Res. Lett. 2023, 58, 104300. [Google Scholar] [CrossRef] [Scilit]
  101. Alhelaly, Y.; Dhillon, G.; Oliveira, T. When Expectation Fails and Motivation Prevails: The Mediating Role of Awareness in Bridging the Expectancy-Capability Gap in Mobile Identity Protection. Comput. Secur. 2023, 134, 103470. [Google Scholar] [CrossRef] [Scilit]
  102. Soyupak, O.; Ipek, H. Exploring User Experience and Usability of Mobile and Open Banking for Digital Natives in Turkiye. Qual. Res. Financ. Mark. 2025, 18, 357–378. [Google Scholar] [CrossRef] [Scilit]
  103. Pee, L.G.; Woon, I.M.Y.; Kankanhalli, A. Explaining Non-Work-Related Computing in the Workplace: A Comparison of Alternative Models. Inf. Manag. 2008, 45, 120–130. [Google Scholar] [CrossRef] [Scilit]
  104. Farzin, M.; Sadeghi, M.; Yahyayi Kharkeshi, F.; Ruholahpur, H.; Fattahi, M. Extending UTAUT2 in M-Banking Adoption and Actual Use Behavior: Does WOM Communication Matter? Asian J. Econ. Bank. 2021, 5, 136–157. [Google Scholar] [CrossRef] [Scilit]
  105. Ng, B.Y.; Kankanhalli, A.; Xu, Y. (Calvin) Studying Users’ Computer Security Behavior: A Health Belief Perspective. Decis. Support Syst. 2009, 46, 815–825. [Google Scholar] [CrossRef] [Scilit]
  106. Du Plessis, L.; Jordaan, Y.; van der Westhuizen, L.M. Consumer Spending Self-Control, Financial Well-Being and Life Satisfaction: The Moderating Effect of Relative Deprivation from Consumers Holding Debt. Int. J. Bank Mark. 2025, 43, 1779–1803. [Google Scholar] [CrossRef] [Scilit]
  107. van Esterik-Plasmeijer, P.W.J.; van Raaij, W.F. Banking System Trust, Bank Trust, and Bank Loyalty. Int. J. Bank Mark. 2017, 35, 97–111. [Google Scholar] [CrossRef] [Scilit]
  108. Besley, J.C.; Benitez Gonzalez, A.; Tiffany, L.A. Differentiating Behavioral Trust and Trustworthiness Beliefs to Improve Science Communication Practice and Research. Curr. Opin. Psychol. 2026, 67, 102192. [Google Scholar] [CrossRef] [Scilit]
  109. Ikhsan, R.B.; Fernando, Y.; Prabowo, H.; Yuniarty; Gui, A.; Kuncoro, E.A. An Empirical Study on the Use of Artificial Intelligence in the Banking Sector of Indonesia by Extending the TAM Model and the Moderating Effect of Perceived Trust. Digit. Bus. 2025, 5, 100103. [Google Scholar] [CrossRef] [Scilit]
  110. Han, J.; Kim, H. Do Employees in a “Good” Company Comply Better with Information Security Policy? A Corporate Social Responsibility Perspective. Inf. Technol. People 2018, 32, 858–875. [Google Scholar] [CrossRef] [Scilit]
  111. Kitkowska, A.; Shulman, Y.; Martucci, L.A.; Wästlund, E. Designing for Privacy: Exploring the Influence of Affect and Individual Characteristics on Users’ Interactions with Privacy Policies. Comput. Secur. 2023, 134, 103468. [Google Scholar] [CrossRef] [Scilit]
  112. Abdennebi, H. Ben M-Banking Adoption from the Developing Countries Perspective: A Mediated Model. Digit. Bus. 2023, 3, 100065. [Google Scholar] [CrossRef] [Scilit]
  113. Chan, R.; Troshani, I.; Rao Hill, S.; Hoffmann, A. Towards an Understanding of Consumers’ FinTech Adoption: The Case of Open Banking. Int. J. Bank Mark. 2022, 40, 886–917. [Google Scholar] [CrossRef] [Scilit]
  114. Alsharida, R.A.; Al-rimy, B.A.S.; Al-Emran, M.; Zainal, A. A Systematic Review of Multi Perspectives on Human Cybersecurity Behavior. Technol. Soc. 2023, 73, 102258. [Google Scholar] [CrossRef] [Scilit]
  115. Ye, J.; Bai, X.; Li, F.; Browning, M.H.E.M.; Eisenman, T.; Yin, J.; Xu, L. What Really Helps Recovery from Stress: The Leafiness or Representational Style of Trees in a Virtual Nature? J. Environ. Psychol. 2026, 109, 102869. [Google Scholar] [CrossRef] [Scilit]
  116. Buckley, G.; Caulfield, T.; Becker, I. How Might the GDPR Evolve? A Question of Politics, Pace and Punishment. Comput. Law Secur. Rev. 2024, 54, 106033. [Google Scholar] [CrossRef] [Scilit]
  117. Casolaro, A.M.B.; Rauber, G.N.; de Lima, U.S.M. Open Banking: A Systematic Literature Review. J. Bank. Regul. 2024, 26, 340–355. [Google Scholar] [CrossRef] [Scilit]
  118. Esmaeilzadeh, P. The Effect of the Privacy Policy of Health Information Exchange (HIE) on Patients’ Information Disclosure Intention. Comput. Secur. 2020, 95, 101819. [Google Scholar] [CrossRef] [Scilit]
  119. Blihar, D.; Delgado, E.; Buryak, M.; Gonzalez, M.; Waechter, R. A Systematic Review of the Neuroanatomy of Dissociative Identity Disorder. Eur. J. Trauma Dissoc. 2020, 4, 100148. [Google Scholar] [CrossRef] [Scilit]
Figure 2. OB Core Security, adapted from [37].
Fintech 05 00038 g002
Figure 3. Technological, regulatory, and behavioural integration framework.
Fintech 05 00038 g003
Figure 4. Tri-dimensional security framework.
Fintech 05 00038 g004
Table 1. Summary statistics of regulatory policies across all 193 countries.
VariableWorldwideAfrica & Middle EastEurope & Central AsiaLA & the CaribbeanNorth AmericaSouth-East Asia & Pacific
Number of Countries193655025350
Regulatory Initiatives168655025325
Promoting competition659393113
Fostering innovation659393113
Financial inclusion6610393113
Under discussion8016408214
Partial implementation8016408214
Fully implemented8016408214
Mandatory data sharing576372111
Reciprocal data access566362111
Regulatory tech standards628392112
Extended scope565363111
Data access only586382111
Payment function586382111
Integrated data & payments586382111
Table 2. Summary statistics of regulatory policies (%), all 193 countries.
VariableWorldwideAfrica & Middle EastEurope & Central AsiaLA & the CaribbeanNorth AmericaSouth-East Asia & Pacific
Number of Countries193655025350
Regulatory Initiatives48%25%80%32%67%56%
Promoting competition82%67%87%100%0%77%
Fostering innovation97%100%97%100%100%92%
Financial inclusion29%40%10%100%100%54%
Under discussion38%75%12%75%100%36%
Partial implementation18%6%12%25%0%43%
Fully implemented44%13%75%0%0%21%
Mandatory data sharing88%67%97%100%100%64%
Reciprocal data access18%33%0%100%100%45%
Regulatory tech standards39%63%15%100%100%83%
Extended scope34%80%3%100%100%91%
Data access only5%0%0%50%100%9%
Payment function0%0%0%0%0%0%
Integrated data & payments95%100%100%50%0%91%
Table 3. Overview of inclusion and exclusion criteria.
Inclusion CriteriaExclusion Criteria
The study should address open banking, security behaviour, regulatory policies, compliance, financial regulation, cybersecurity, FinTech, RegTech or SecTech.
It should include a theoretical research model.
Articles should be written in a language in which the reviewers are proficient (English, Portuguese, Spanish and Polish).
Studies that did not address open banking, security behaviour, regulatory policies, compliance, financial regulation, cybersecurity, FinTech, RegTech, or SecTech were excluded.
Editorials, posters, presentations, position papers.
Articles written in languages beyond the reviewers’ proficiency were also excluded.
Studies without full-text availability were excluded.
Table 7. Overview of the Cluster Distribution of the 117 Reviewed Studies.
Cluster OverlapNumber of StudiesPercentage
Technology + Regulation3832.5%
Technology + Behaviour2924.8%
Regulation + Behaviour2723.1%
All Three Dimensions2117.9%
Disclaimer/Publisher’s Note: The statements, opinions and data contained in all publications are solely those of the individual author(s) and contributor(s) and not of MDPI and/or the editor(s). MDPI and/or the editor(s) disclaim responsibility for any injury to people or property resulting from any ideas, methods, instructions or products referred to in the content.