


Abstract
Recently, the spectacular innovations in the fields of wireless body area networks (WBAN) and the Internet of Things (IoT) have made e-Care services rise as a promising application domain, which significantly advances the quality of the medical system, however, due to the openness of the wireless environment and privacy of people’s physiological data, WBAN and IoT are prone to various cyber-attacks. There is a significant need for an efficient and highly secured cryptographic scheme that can meet the requirements of resource-constrained devices. Therefore, in this paper, we propose a certificate-based signcryption (CB-SN) scheme for the IoT-enabled WBAN. The proposed scheme is based on the concept of hyper-elliptic curve cryptography (HECC) that offers the same level of security as the elliptic curve and bilinear pairing with lower-key size. The formal security verification using the Automated Validation of the Internet Security Protocols and Applications (AVISPA) tool along with informal security analysis demonstrate that the proposed scheme is not just reducing the complexity of resource-constrained IoT devices, but proves to be secure against several well-known cryptographic attacks. Moreover, performance comparison with relevant existing schemes authenticates that the proposed scheme is far more secure and energy efficient.
1. Introduction
In the current era, the Internet of things (IoT) is one of the most debatable topics among the research community of information technology. The IoT includes all those devices, which have the capacity of computing, communication, and connection with the Internet [1]. The IoT has so many applications in our daily lives, i.e., it is used in smart cities, smart homes, and e-health, etc. [2]. By providing faster access to the treatment of patients, the wireless body area networks (WBAN) integrate with the Internet of things (IoT) and play an important role in the patient health care system, because this ecosystem, enables all the users and devices to access the patient’s psychological data from anywhere and anytime in the world by utilizing the Internet [3]. However, due to the open nature of the Internet, authenticity and data security are the two major concerns in the IoT based WBAN [4].
The authenticity of IoT is ensured through digital signature [5], and data security is met by using the encryption method [6], although the IoT has a resource hungry nature and cannot afford these two different algorithms separately, i.e., signature and then encryption at the same time. In 1997, Zheng was the pioneer to merge these two processes in one algorithm, called signcryption [7]. This scheme is based on the concept of old public key cryptography (PKC), which is suffering from certificate overheads, renewing, and revocation problems [8]. Shamir was the first to propose an alternate concept of PKC, called identity-based cryptography (IBC) [9]. This technique removed the limitations of PKC and used the identity in place of a certificate. Later, in 2002, Malone-Lee [10], for the first time merged the concept of IBC with the signcryption technique, namely, identity-based signcryption (IBS). The IBS includes three entities, for example, a sender (signcrypter), a receiver (unsigncrypter), and the private key generation center (PKGC), respectively. In this setup, the users (signcrypter and unsigncrypter) generate their identities and after that, send it to the PKGC. Then, the PKGC produces and delivers the private keys for all the participating users, by using the secured networks. Unfortunately, IBS suffers from the key escrow issue (KEI), because the private key is generated by the PKGC and one can easily use this key for forging the digital signature and decrypting the ciphertext [11].
To eliminate the above problem in IBS, in 2008, Barbosa and Farshim [12], put forward the concept of a certificateless signcryption (CL-SC) scheme. The CL-SC mechanism almost works the same as IBS, but the main difference is that the private key is generated by the users themselves. The central authority known as a key generation center (KGC) only provides the partial private key to the users by using an open link. Although it removes the issue of key escrow in IBS and certificate management in PKC-based signcryption, it still suffers from the needs of the partial private key distribution problem [13]. Another strategy, named heterogeneous signcryption was proposed by Sun [14]. This strategy contains two sub-methods, the first one works under the condition in which the sender belongs to the conventional PKC and the receiver belongs to the IBC, while in the second one, a sender uses the concept of IBC and receiver based on the PKC. Since, these two types (PKC and IBC) of the public key are suffering from some crucial problem, i.e., certificate overheads, renewing, certificate revocation, and KEI, respectively, these types of problems are not suitable for the IoT environment. To cater to this particular issue, heterogeneous signcryption was coined by Li et al. [14], in which the signcryption part belongs to the certificateless cryptosystem (CLC) and the unsigncryption side is based on the functionality of PKC, however, the scheme is affected by the secrete key distributions and certificate management issues. To remove the certificate management at the receiver side, Omala et al. [15], contributed a new heterogeneous signcryption scheme, in which the signcryption part belongs to the CLC and the unsigncryption part works under the notion of IBC. This method is also affected by the key escrow and the secret key distribution problem. A new type of cryptosystem was introduced by Gentry in 2003 [16], namely, certificate-based cryptography (CBC), in which one can use the functionality of old PKC in a better manner. The CBC enables each participant in the network to generate his public and private keys and give their public key to the certifier’s authority (CsA). Later, by using the concept of IBC encryption, based on the participants’ public key which serves its identity, CsA generates a certificate for each participant while using an open link. Noteably, this certificate acts as a partial private key and also uses a decryption key on the receiver side [17]. In 2008, Li et al. [18], provided a new scheme, which is used to merge the concept of CBC with signcryption, called certificate-based signcryption. In 2019, Braeken proposed pairing free certificate-based signcryption schemes using ECQV implicit certificates [19]. However, the proposed approach is based on a hyper-elliptic curve, i.e., it suffers from high computational cost. Moreover, the proposed scheme is not validated through any formal security tool.
Cagalaban and Kim [20], proposed an effective signcryption scheme for access control in the WBAN under the functionalities of IBC, which is suffering from KEI. Similarly, Hu et al. [21], proposed an access control for WBAN using the idea of fuzzy attribute-based signcryption, however, the proposed scheme suffered from high computational cost. In 2016, Li and Hong [22], proposed a signcryption scheme for access control in WBAN while utilizing both CLC and bilinear pairing (BP). In 2018, Li et al. [23], presented a CL-SC approach for an efficient access control in WBAN. These approaches [22,23], faced the issues of secrete key exchange and extra energy consumption. In the same year, Omala et al. [15], by using signcryption, designed an access control scheme for WBAN, where they used CLC in the signcryption part and IBC in the unsigncryption part. Recently, in May 2019, Gao et al. [24], developed a CL-SC with an elliptic curve for secure and efficient access control in WBAN. Nevertheless, these two schemes [15,24] are commonly affected by the secret key distribution problems, more energy utilization, and extra bandwidth consumption.
1.1. Authors’ Motivations and Contributions
The authors, motivated by the aforementioned limitations regarding signcryption-based access control in WBAN, propose a new scheme, called an energy efficient and formally secured certificate-based signcryption (CB-SN), which does not suffer from the problems such as secret key distribution problems, more energy utilization, and extra bandwidth consumption. Some of the salient features signifying contributions of our research work, in this paper, are as follows:
- We first provide the basic syntax for certificate based signcryption and then construct the scheme practically for WBAN with IoT;
- The proposed scheme is shown to be resistant against various attacks through informal security analysis concerning integrity, confidentiality, replay, unforgeability, and forward secrecy, respectively;
- We also generate the high level protocol specification language (HLPSL) code for our scheme in AVISPA Tool for the formal security checking, and the simulation results authenticates that the proposed scheme is SAFE, according to the checking structure of two well-known checker models, i.e., on-the-fly model checker (OFMC) and constraint logic-based attack searcher (ATSE);
- We perform the computational cost and communication overhead comparison analysis with the relevant existing schemes, which demonstrates the presented scheme, in addition, is far more efficient.
1.2. Structure of The Paper
The remainder of the paper is organized as follows: Section 2 gives the basic knowledge of preliminaries, Section 3 presents proposed architecture, Section 4 contains the construction of the proposed scheme, Section 5 presents the informal security analysis, Section 6 give the proposed scheme implementation detail in WBAN, Section 7 delivers implementation of the proposed scheme in AVISPA, and includes the discussion about performance with relevant existing schemes, and, finally, Section 8 culminates conclusions of the entire work.
2. Preliminaries
2.1. Hyper-Elliptic Curve
This section briefly discusses the basic mathematics of a hyper-elliptic curve (hε𝒸). Suppose ℑ𝑡 is a predetermined set and presume 𝜕 is the genus of hε𝒸 having order as 𝜕 ⪰ 2. Let (𝓋), f(𝓋)𝜖ℑ𝑡[𝓋], and deg (𝒽(𝓋)) ⪯ 𝜕; and f(𝓋) is a monic polynomial having deg (f(𝓋)) = 2𝜕 + 1 [25]. Therefore, hε𝒸 of genus 𝜕 ⪰ 2 over ℑ𝑡 is the set of points (𝓋,) ℑ𝑡 * ℑ𝑡 as shown in the Equation (1).
hε𝒸: 𝓌2 + (𝓋) 𝓌 = f(𝓋)
Note, hε𝒸 points are different from elliptic curve [26]. It forms the divisors which are the formal sum of finite integers like 𝒹 = ∑𝑥i𝑧i, where 𝑥i𝜖 ℑ𝑡 and 𝑧i𝜖 hε𝒸. Furthermore, it forms a Jacobian group hε𝒸 (ℑ𝑡) having the following order:
(√𝑡 − 1)2𝜕 ⪯ hε𝒸 (ℑ𝑡) ⪯ (√𝑡 + 1)2𝜕
2.2. Hyper-Elliptic Curve Discrete Logarithm Problem
Assume 𝒹 is the divisor which ispublicly available in the network and is the randomly picked private number from ℑ𝑡. Recovering from 𝒹1 = 𝒹, is said to be [27].
2.3. Automated Validation Tool for Security Validation and Application (AVISPA)
Currently, AVISPA is the utmost valuable tool among researchers of information security, in which they check the authenticity of their newly designed cryptographic protocol security properties. For the overall structure of AVISPA, it can be a better choice to see the article [24], in which it includes the most expensive formal language called high level protocol specification language (HLPSL), a compilation translator called HLPSL2IF, an intermediate format (IF), and the four backends models for checking the security properties, i.e., on-the-fly model checker (O-f-M-C), constraint logic-based attack searcher (CL-ATSe), SAT-based model checker (Sat-M-C), and tree automata based on automatic approximations for the analysis of security protocols (TA-4 SP), respectively. If the cryptographic user famines to trial their approach security, then he/she first compose the HLPSL code for their approach in SPAN, which is the graphical user interface (GUI) for AVISPA, furthermore, the HLPSL2IF is responsible for compiling this code into IF, and IF handover the code to the four model checkers, for example, (O-f-M-C), (CL-ATSe), (SAT-M-C), and (TA-4 SP) for the checking of man-in-the-middle attack and replay attack. Therefore, if these two attacks are possible in their respective protocol then these model checkers give UNSAFE simulation results and if it is not possible then it shows the SAFE results.
2.4. Syntax of Certificate-based Signcryption (CB-SN)
The proposed CB-SN scheme is the improved version of the Braeken et al. [17] scheme, and includes five algorithms such as, setup, public variable generation (PVG), certificate generation (CG), actors key generation (AKG), signcryption generation (SG), and unsigncryptions (US), respectively. We explain the syntax of CB-SN in the following steps:
- Setup: Certifier’s authority (CsA) recognizes a security parameter 𝜇 as input data and runs the setup algorithm to make essential parameters set {hε𝒸, δ, ℑ𝑡, 𝒹, hε𝒸, 𝛵, 1, 2, 3} and a master secret key Y and public key T = 𝛶.𝒹, respectively. The essential parameters set is directly accessible on a network, anyway Y is kept by the CsA secret.
- Public variable generation (PVG): Each actor with identity IDA, runs the PVG algorithm to produce his public variable PVA by taking input, an essential parameter set {hε𝒸, δ, ℑ𝑡, 𝒹, hε𝒸, 𝛵, 1, 2, 3}. Then, the actor having identity IDA, has sent the pair (PVA, IDA) to CsA via an insecure link.
- Certificate generation (CG): By taking input (PVA, IDA), the essential parameter set {hε𝒸, δ, ℑ𝑡, 𝒹, hε𝒸, 𝛵, 1, 2, 3} and Y, CsA run the CG algorithm to produce a certificate CertA for each actor with identity IDA and hand over a certificate with auxiliary variable (𝑒𝓇𝑡A, 𝒶𝓊𝓍A) to the actors via unsecured link.
- Actor’s key generation (AKG): Inputting the pair of an auxiliary variable (CertA, auxA), an essential parameter set {hε𝒸, δ, ℑ𝑡, 𝒹, hε𝒸, 𝛵, 1, 2, 3} and the identity IDA of each actor, the participated actor’s with identity IDA produces his private and public keys (AA, QA).
- Signcryption generation (SG): The SG algorithm is executed by the sender actor to produce signcryption text 𝜓 = {C,A,S}, of a message, m, and delivers 𝜓 to the receiver through an unsecured network. It takes as input the certificate of the sender and receiver (Certs, Certu), the identity of a sender and receivers (IDs, IDu), private and public key of the sender (As, Qs), a message (m), an essential parameter set {hε𝒸, δ, ℑ𝑡, 𝒹, hε𝒸, 𝛵, 1, 2, 3}, and public key of receiver Qu.
- Unsigncryptions (US): The US algorithm is executed by the receiver actor to verify and decrypts the received signcryption text 𝜓 = {C,A,S}. It takes as input the certificate of the sender Certs, the identity of a sender and receivers (IDs, IDu), private and public key of the receiver (Au,Qu), a signcryption text 𝜓 = {C,A,S}, and essential parameter set.
3. Proposed Architecture
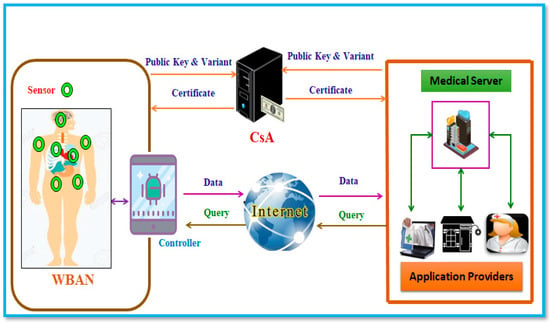
Figure 1 indicates the overall working of a newly designed model of this paper, which includes three main actors, i.e., a certifiers authority (CsA), application providers (APs) and WBAN of a patient’s body, respectively. Hence, in this model, it is the responsibility of CsA to create a certificate for APs and WBAN by using its own secret key and obtained identity with a public variable from actors (APs and WBAN). The APs are responsible for monitoring patient conditions and any time get access to the health related information HRI, by computing certificate-based signcryption of an access request query. The WBAN contains sensor nodes, which are already planted in the body of the patient and at least contain one controller, which receives PHRI. Upon the request from the access control query from APs, the controller checks the authorization of an actor and if the actor is legitimate, then, it sends the data regarding the query request, otherwise it rejects the query demand.
Figure 1.
Proposed architecture.
Safe node and health node are the two wearable sensor nodes on each subject for environmental monitoring and for physiological parameters’ measurements, respectively, in the proposed system. Furthermore, safe node is equipped with four environmental sensors to monitor the ambient temperature, relative humidity, CO2, and ultraviolet (UV) sensor. The health node is comprised of a Bluetooth 5 (802.15.1) module that is used to enable WBAN communication, a photoplethysmogram (PPG) sensor for heart rate monitoring, and a body temperature sensor. Bluetooth 5 (802.15.1) is considered the most favored option for wearable sensor nodes because of its low cost and low power consumption [28], however, to address the short communication range issue of Bluetooth 5 for medical records to a longer distance, a smart android-based mobile device, named “controller”, is used inside the WBAN’s communication range. At the end of this section, in Table 1, we provide an explanation about the symbols used in algorithm.
Table 1.
Notations used in proposed algorithm.
4. Constructions of CB-SN
The proposed scheme is an extension of the scheme presented by Braeken et al. [17], and the working steps of the newly designed CB-SN scheme are as follows:
- Setup: The CsA produce an essential parameter set {hε𝒸, δ, ℑ𝑡, 𝒹, hε𝒸, 𝛵, 1, 2, 3} and after that the CsA select a master secret key Y{1,2, …, t − 1} and calculate the master public key T = Y.d, respectively. The essential parameters set is directly accessible on a network and the master secret key Y is kept by the CsA secret.
- PVG: Given an essential parameter set {hε𝒸, δ, ℑ𝑡, 𝒹, hε𝒸, 𝛵, 1, 2, 3}, each actor with identity IDA, choose a random number 𝜔A and computes his public variable A = 𝜔A.𝒹. Then the actor with identity IDA delivers (PVA, IDA) to the CsA by using the open channel.
- CG: Given an essential parameter set {hε𝒸, δ, ℑ𝑡, 𝒹, hε𝒸, 𝛵, 1, 2, 3}, public variable and identity of each actor (PVA, IDA) and master secret key Y, CsA select a random number 𝜒A𝜖 {1, 2…., 𝑡 − 1} and calculate 𝜑A = 𝜒A.𝒹. After that, CsA computes the certificate CertA = 𝜑A + PVA and auxiliary variable auxA = 1 (CertA, IDA). 𝜒A + 𝛶, then, hands over a certificate CertA with auxiliary variable (CertA, auxA) to the actors via insecure link.
- AKG: Given the tuple (CertA, auxA), identity IDA of each actor, and essential parameter set {hε𝒸, δ, ℑ𝑡, 𝒹, hε𝒸, 𝛵, 1, 2, 3}, each actor makes their private key AA = H1 (CertA, IDA). wA + auxA make their public key as QA = AA. d.
- SG: Given an essential parameter set {hε𝒸, δ, ℑ𝑡, 𝒹, hε𝒸, 𝛵, 1, 2, 3}, the sender and receiver’s certificates (Certs, Certu), the identity of the sender and the receiver (IDs, IDu), the private and public key of the sender (As, Qs), a massage (m), and public key of receiver Qu. Then the sender produces a signcryption tuple 𝜓 = {C, A} by utilizing the following steps:
- The sender first computes the public key of receiver Qu ≟ H2 (Certu, IDu). Certu + T;
- Next, choose a random number 𝛺𝜖 {1, 2, …, t − 1} and compute 𝛽 = 𝛺 . 𝒹;
- Select a fresh nonce N;
- Compute the session key = 𝛺 . u and produced the cipher text = ℇ (𝓂‖ N);
- Compute the hash value 𝛬 = 2(𝓂‖ N) and signature = 𝛺 - 𝛬 , As;
- Then, hand over 𝜓 = {, 𝛬, } to the receiver using insecure channel.
- US: Given the sender’s certificate Certs, identity of a sender and receivers (IDs, IDu), private and public key of the receiver (Au,Qu), a signcryption text 𝜓 = {C, A, S}, essential parameter set {hε𝒸, δ, ℑ𝑡, 𝒹, hε𝒸, 𝛵, 1, 2, 3}, and public key of sender Qs. The receiver performs the following steps to verify and decrypts the received signcryption text 𝜓= {C. A, S}.
- The receiver first computes the public key of sender Qs ≟ H2 (Certs, IDs). Certs + 𝛵;
- Compute 𝛽 = S . d + 𝛬 . Qs;
- Recover the secret key SK = Au . 𝛽 and produced the plaintext (m‖ N) = D (C);
- Compute the hash value 𝛬/ = H2(m‖ N);
- Accept the signcryption text 𝜓 = {,𝛬,} if 𝛬/ = H2(m‖ N) ≟ 𝛬 = H2(m‖ N).
4.1. Correctness
The sender can compute the public key of receiver from the following computations:
- u ≟ 2 (𝑒𝓇𝑡u, IDu). 𝑒𝓇𝑡u + 𝛵
- = 2 (𝑒𝓇𝑡u, IDu) . (𝜑u+ u ) + 𝛶, where 𝑒𝓇𝑡u= 𝜑u+ u and 𝛵 = 𝛶.𝒹
- = 2 (𝑒𝓇𝑡u, IDu) . (𝜑u+ 𝜔u.𝒹) + 𝛶. 𝒹, where u = 𝜔u.𝒹
- = 2 (𝑒𝓇𝑡u, IDu) . (𝜒u.𝒹 + 𝜔u.𝒹) + 𝛶. 𝒹, where 𝜑u= u.𝒹
- = 𝜒u .𝒹. 2 (𝑒𝓇𝑡u, IDu) + 𝜔u.𝒹. 2 (𝑒𝓇𝑡u, IDu) + 𝛶.𝒹
- = (𝜒u . 2 (𝑒𝓇𝑡u, IDu)+ 𝜔u. 2 (𝑒𝓇𝑡u, IDu)+ 𝛶). 𝒹
- = (𝒶𝓊𝓍u + 𝜔u. 2 (𝑒𝓇𝑡u, IDu)), where 𝒶𝓊𝓍u = 1 (𝑒𝓇𝑡u, IDu) . 𝜒u + 𝛶
- = 𝒜u, where 𝒜u = 1 (𝑒𝓇𝑡u, IDu).𝜔u + 𝒶𝓊𝓍u
- = 𝒜u .𝒹 = u , while it same process at the receiver side for making the public key of the sender, by using the following computations.
- s ≟ 2 (𝑒𝓇𝑡s, IDs) . 𝑒𝓇𝑡s + 𝛵
- = 2 (𝑒𝓇𝑡s, IDs) . (𝜑s + s ) + 𝛶. 𝒹, where 𝑒𝓇𝑡s = 𝜑s + s and 𝛵 = 𝛶.𝒹
- = 2 (𝑒𝓇𝑡s, IDs) . (𝜑s + 𝜔s . 𝒹) + 𝛶, where s = 𝜔s . 𝒹
- = 2 (𝑒𝓇𝑡s, IDs) . (𝜒s . 𝒹 + 𝜔s.𝒹) + 𝛶. 𝒹, where 𝜑s = 𝜒s . 𝒹
- = 𝜒s . 𝒹 . 2 (𝑒𝓇𝑡s, IDs) + 𝜔s . 𝒹 . 2 (𝑒𝓇𝑡s, IDs) + 𝛶. 𝒹
- = (𝜒s . 2 (𝑒𝓇𝑡s, IDs) + 𝜔s . 2 (𝑒𝓇𝑡s, IDs) + 𝛶) . 𝒹
- = (𝒶𝓊𝓍s + 𝜔s . 2 (𝑒𝓇𝑡s, IDs)) . 𝒹 where 𝒶𝓊𝓍s = 1 (𝑒𝓇𝑡s, IDs) . 𝜒s + 𝛶
- = 𝒜s . 𝒹, where 𝒜s = 1 (𝑒𝓇𝑡s, IDs) . 𝜔s + 𝒶𝓊𝓍s
- = 𝒜s . 𝒹 = s
- And the receiver also recovers the secret key by using the following steps:
- = 𝒜u . 𝛽
- = 𝒜u . (.𝒹 + 𝛬 . s), where 𝛽 = . 𝒹 + 𝛬 . s
- = 𝒜u . ( . 𝒹 + 𝛬 . 𝒜s . 𝒹), where s = 𝒜s . 𝒹
- = 𝒜u . (𝛺 – 𝛬 . 𝒜s . 𝒹 + 𝛬 . s . 𝒹)), where = 𝛺 – 𝛬 . 𝒜s
- = 𝒜u . 𝒹 (𝛺 – 𝛬 . 𝒜s + 𝛬 . 𝒜s) = 𝒜u . 𝒹= u . (𝛺) = , where 𝒜u . 𝒹 = u
5. Informal Security Analysis
The proposed CB-SN scheme ensures the following informal security requirements.
5.1. Confidentiality
Confidentiality means that the contents of a plain text (m) should hide from intruders and the intruders cannot get any meaning from the signcrypted text without knowing the shared secret key. In the proposed CB-SN scheme, if the intruders desire to scramble the contents of a plain text from a signcryption text 𝜓 = {C,A, S}, then it is mandatory for them to reveal the shared secret key SK by computing Equation (2). To compute this equation, it is important for the intruders to extract 𝛺 from Equation (3), which is hard for them because this leads to computing . Thus, our CB-SN scheme ensures cipher text confidentiality.
= 𝛺 . u
𝛽 = 𝛺 . 𝒹
5.2. Integrity
Integrity means that the contents of a plain text (m) can only be modified by the intended participant or user. In our CB-SN scheme, the sender computes a hash value of a message (m) like 𝛬 = H2(m‖ N) and delivers the value 𝛬 with a cipher text to the receiver. Therefore, if an event occurred, i.e., an intruder tries to modify in cipher text C like C*, then, the intruder must modify m into m* and 𝛬 = H2(m‖ N) into 𝛬* = H2(m‖ N)*, which is infeasible because of the collision resistance property of a hash function.
5.3. Unforgeability
Without the private key of a sender, the illegal user cannot produce the original signature which is called unforgeability. In our proposed CB-SN scheme, the sender computes a digital signature, i.e., = 𝛺 − 𝛬 . 𝒜s. This includes the sender private number 𝛺 and private key 𝒜s, which is only known to the sender. If the intruder tries to create the same signature, he cannot do it, because discovering two unknown variables from the same equation is infeasible. Therefore, our CB-SN scheme meets the unforgeability security service.
5.4. Public Verifiability
Public verifaibility is the property of signcryption , in which the third party removes the clash among the sender and receiver, which is already causing. In our case, the sender computes the digital signature for a plain text by using his private key and it is common practice in asymmetric cryptosystem that the public key of a user is related to his private key. Therefore, for eliminating a conflict, the third party/judge can use either u ≟ 2 (𝑒𝓇𝑡u, IDu) . 𝑒𝓇𝑡u + 𝛵 or u ≟ 2 (𝑒𝓇𝑡u, IDu) . 𝑒𝓇𝑡u + 𝛵, in which the equality of the previous two equations is available in the Section 4.1 of this paper.
5.5. Forward Secrecy
When the private key of a legitimate sender is compromised by an intruder, then, the existing communicated messages that is still safe is called forward secrecy. In our case, the sender encrypts the message (𝓂) like C = ℇ (𝓂‖N), by utilizing the secret shared key SK. If the intruder compromised the private key of the sender, furthermore, he needs the secret shared SK from Equation (2), for the decryption of cipher text. Hence, computing the secret key SK from Equation (2) is infeasible for the intruder, which is already discussed in the confidentiality section.
5.6. Anti-Replay Attack
When an intruder has captured the already communicated signcrypted text and continuously transmits this text to the receiver it is called a replay attack. Therefore, the replay attack is not possible in our case, because the sender sends a fresh nonce (N) in the encrypted text (C), and furthermore, the encryption process (C = ℇ (𝓂‖N)) is processed through a shared secret key SK, in which the nonce (N) and secret key SK are renewed for every session of communication. Therefore, the anti-replay attack is provided in this paper.
6. CB-SN Access Control for WBAN
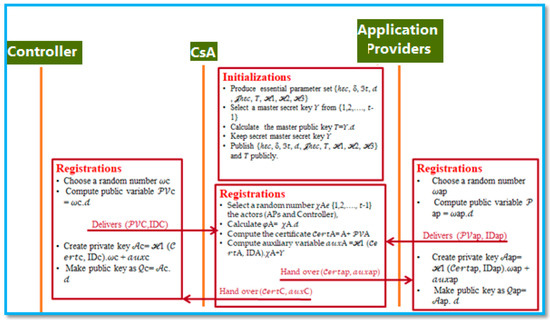
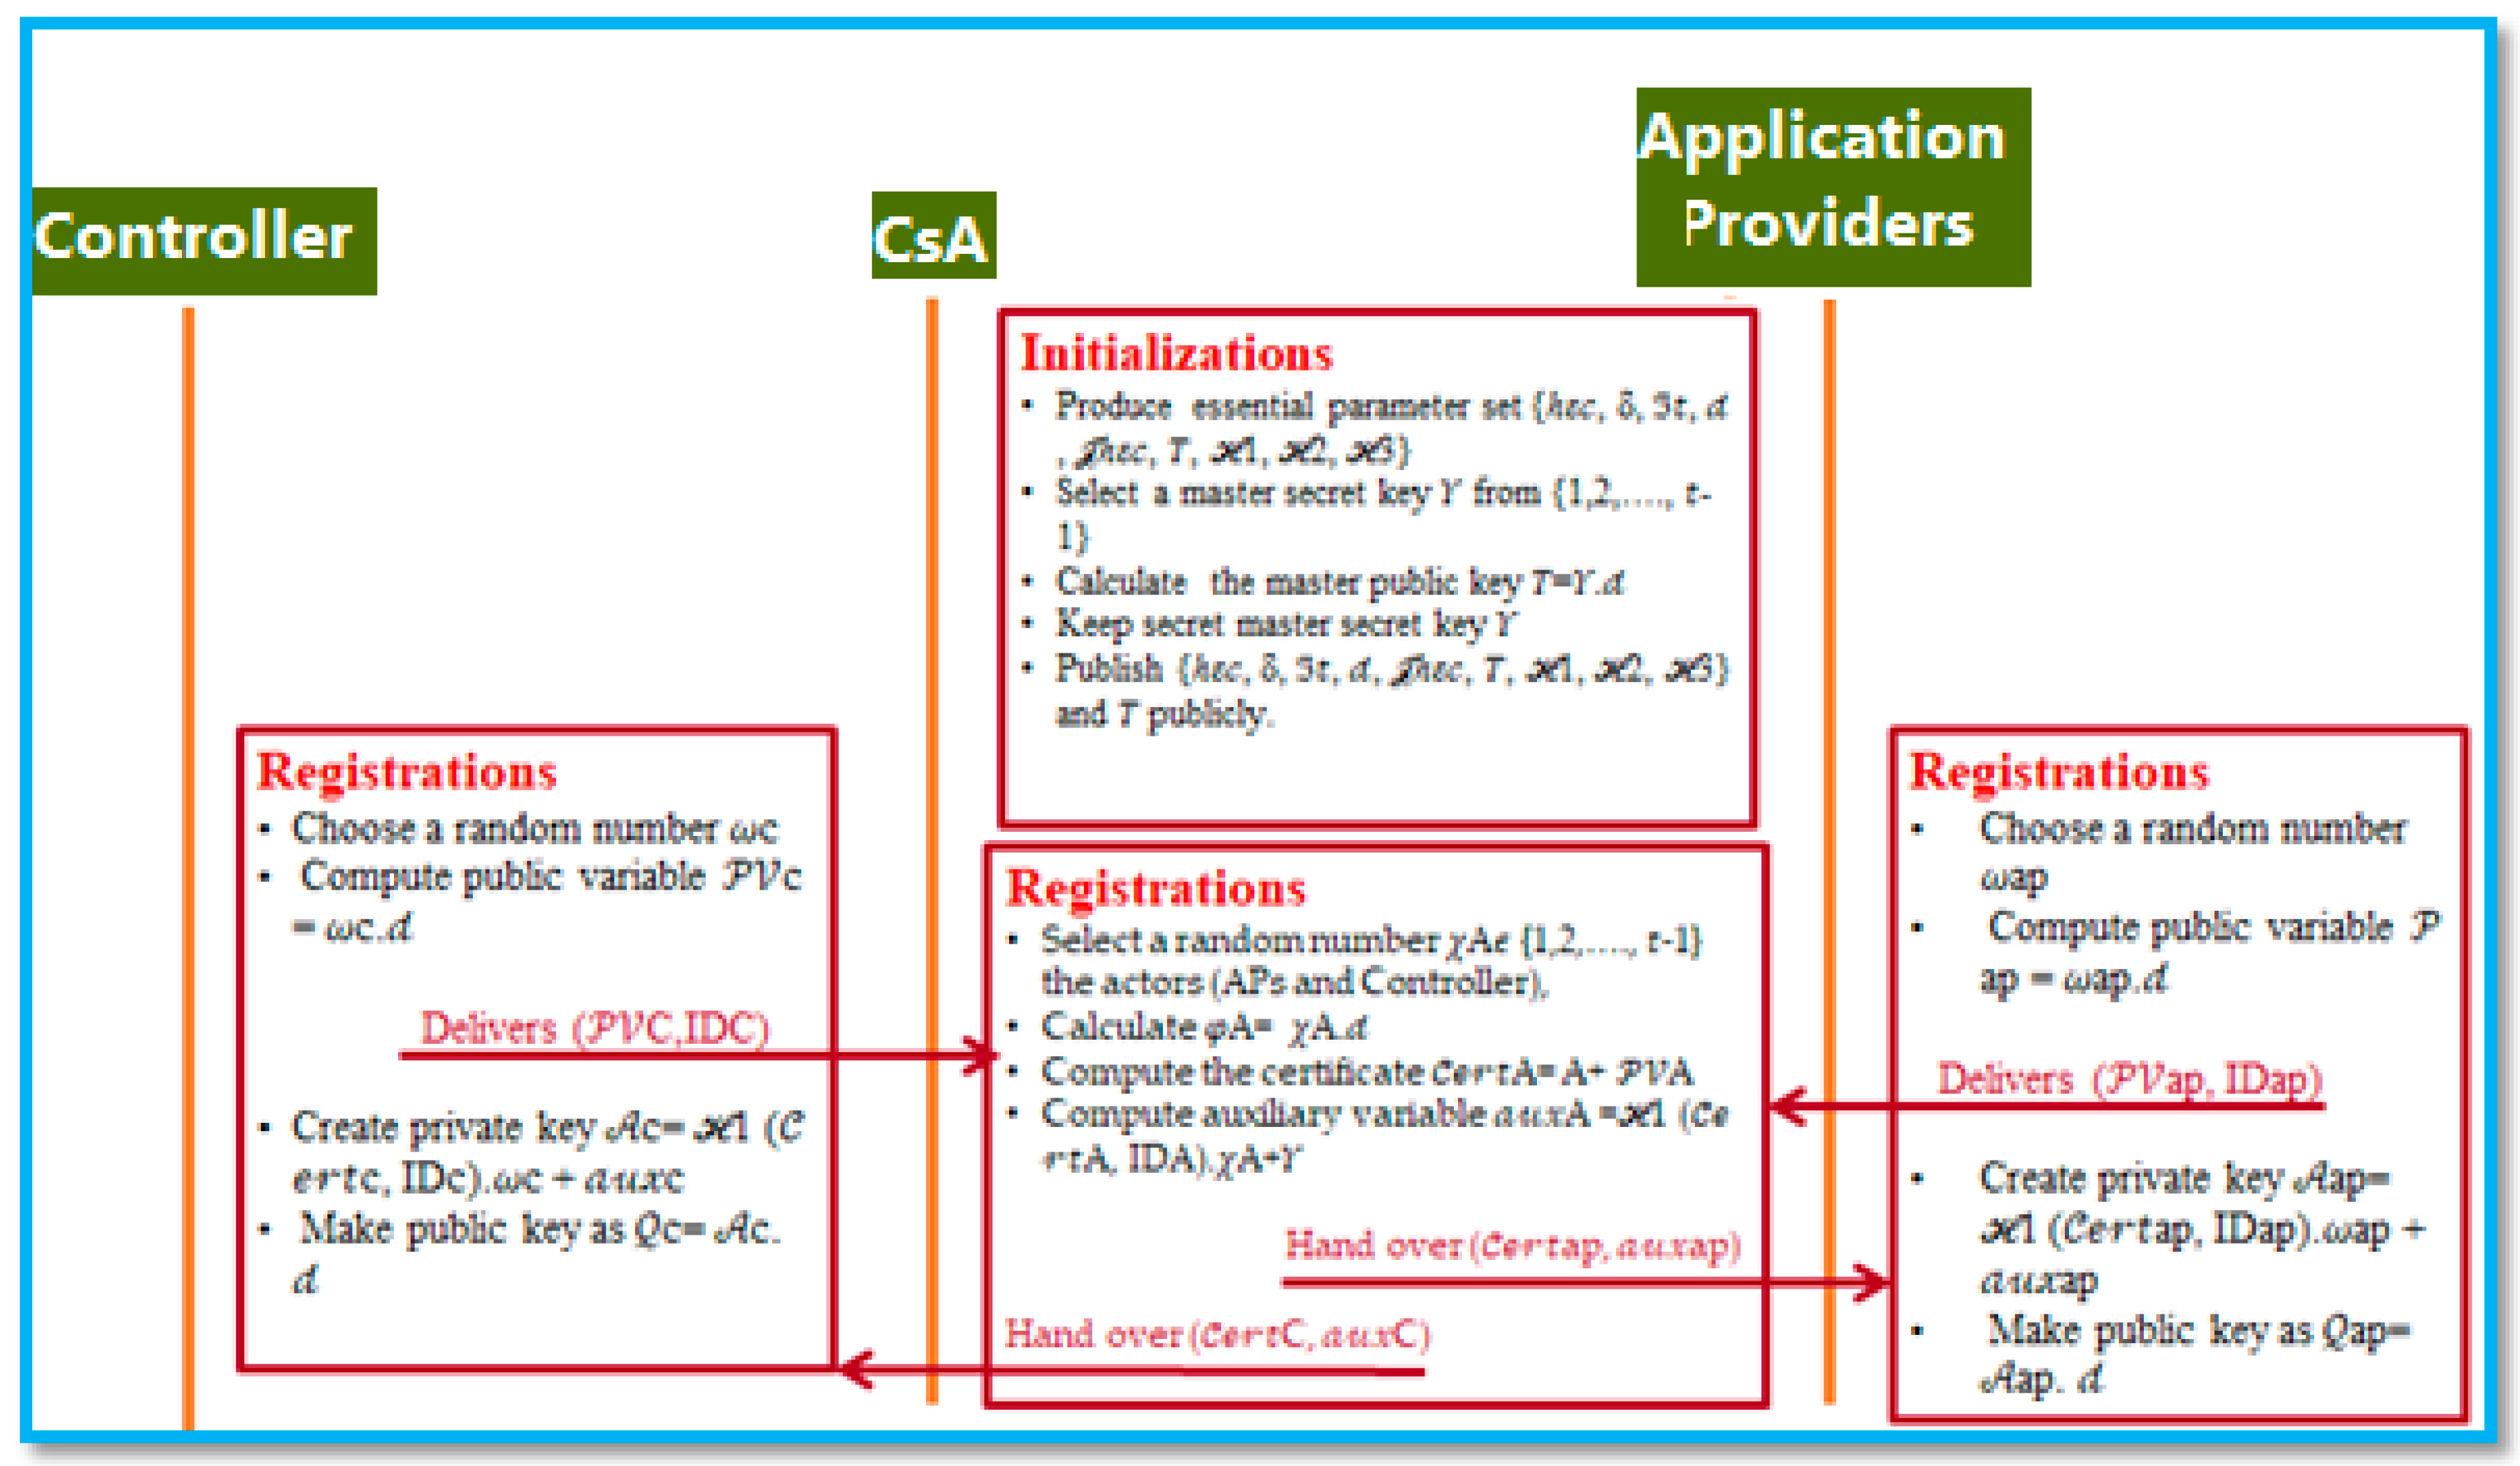
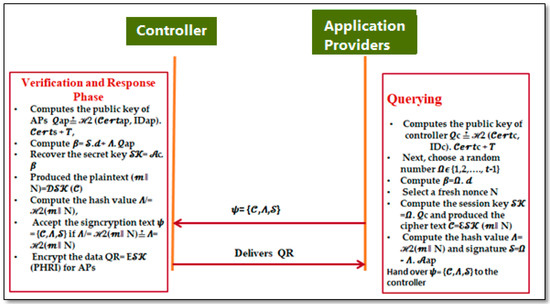
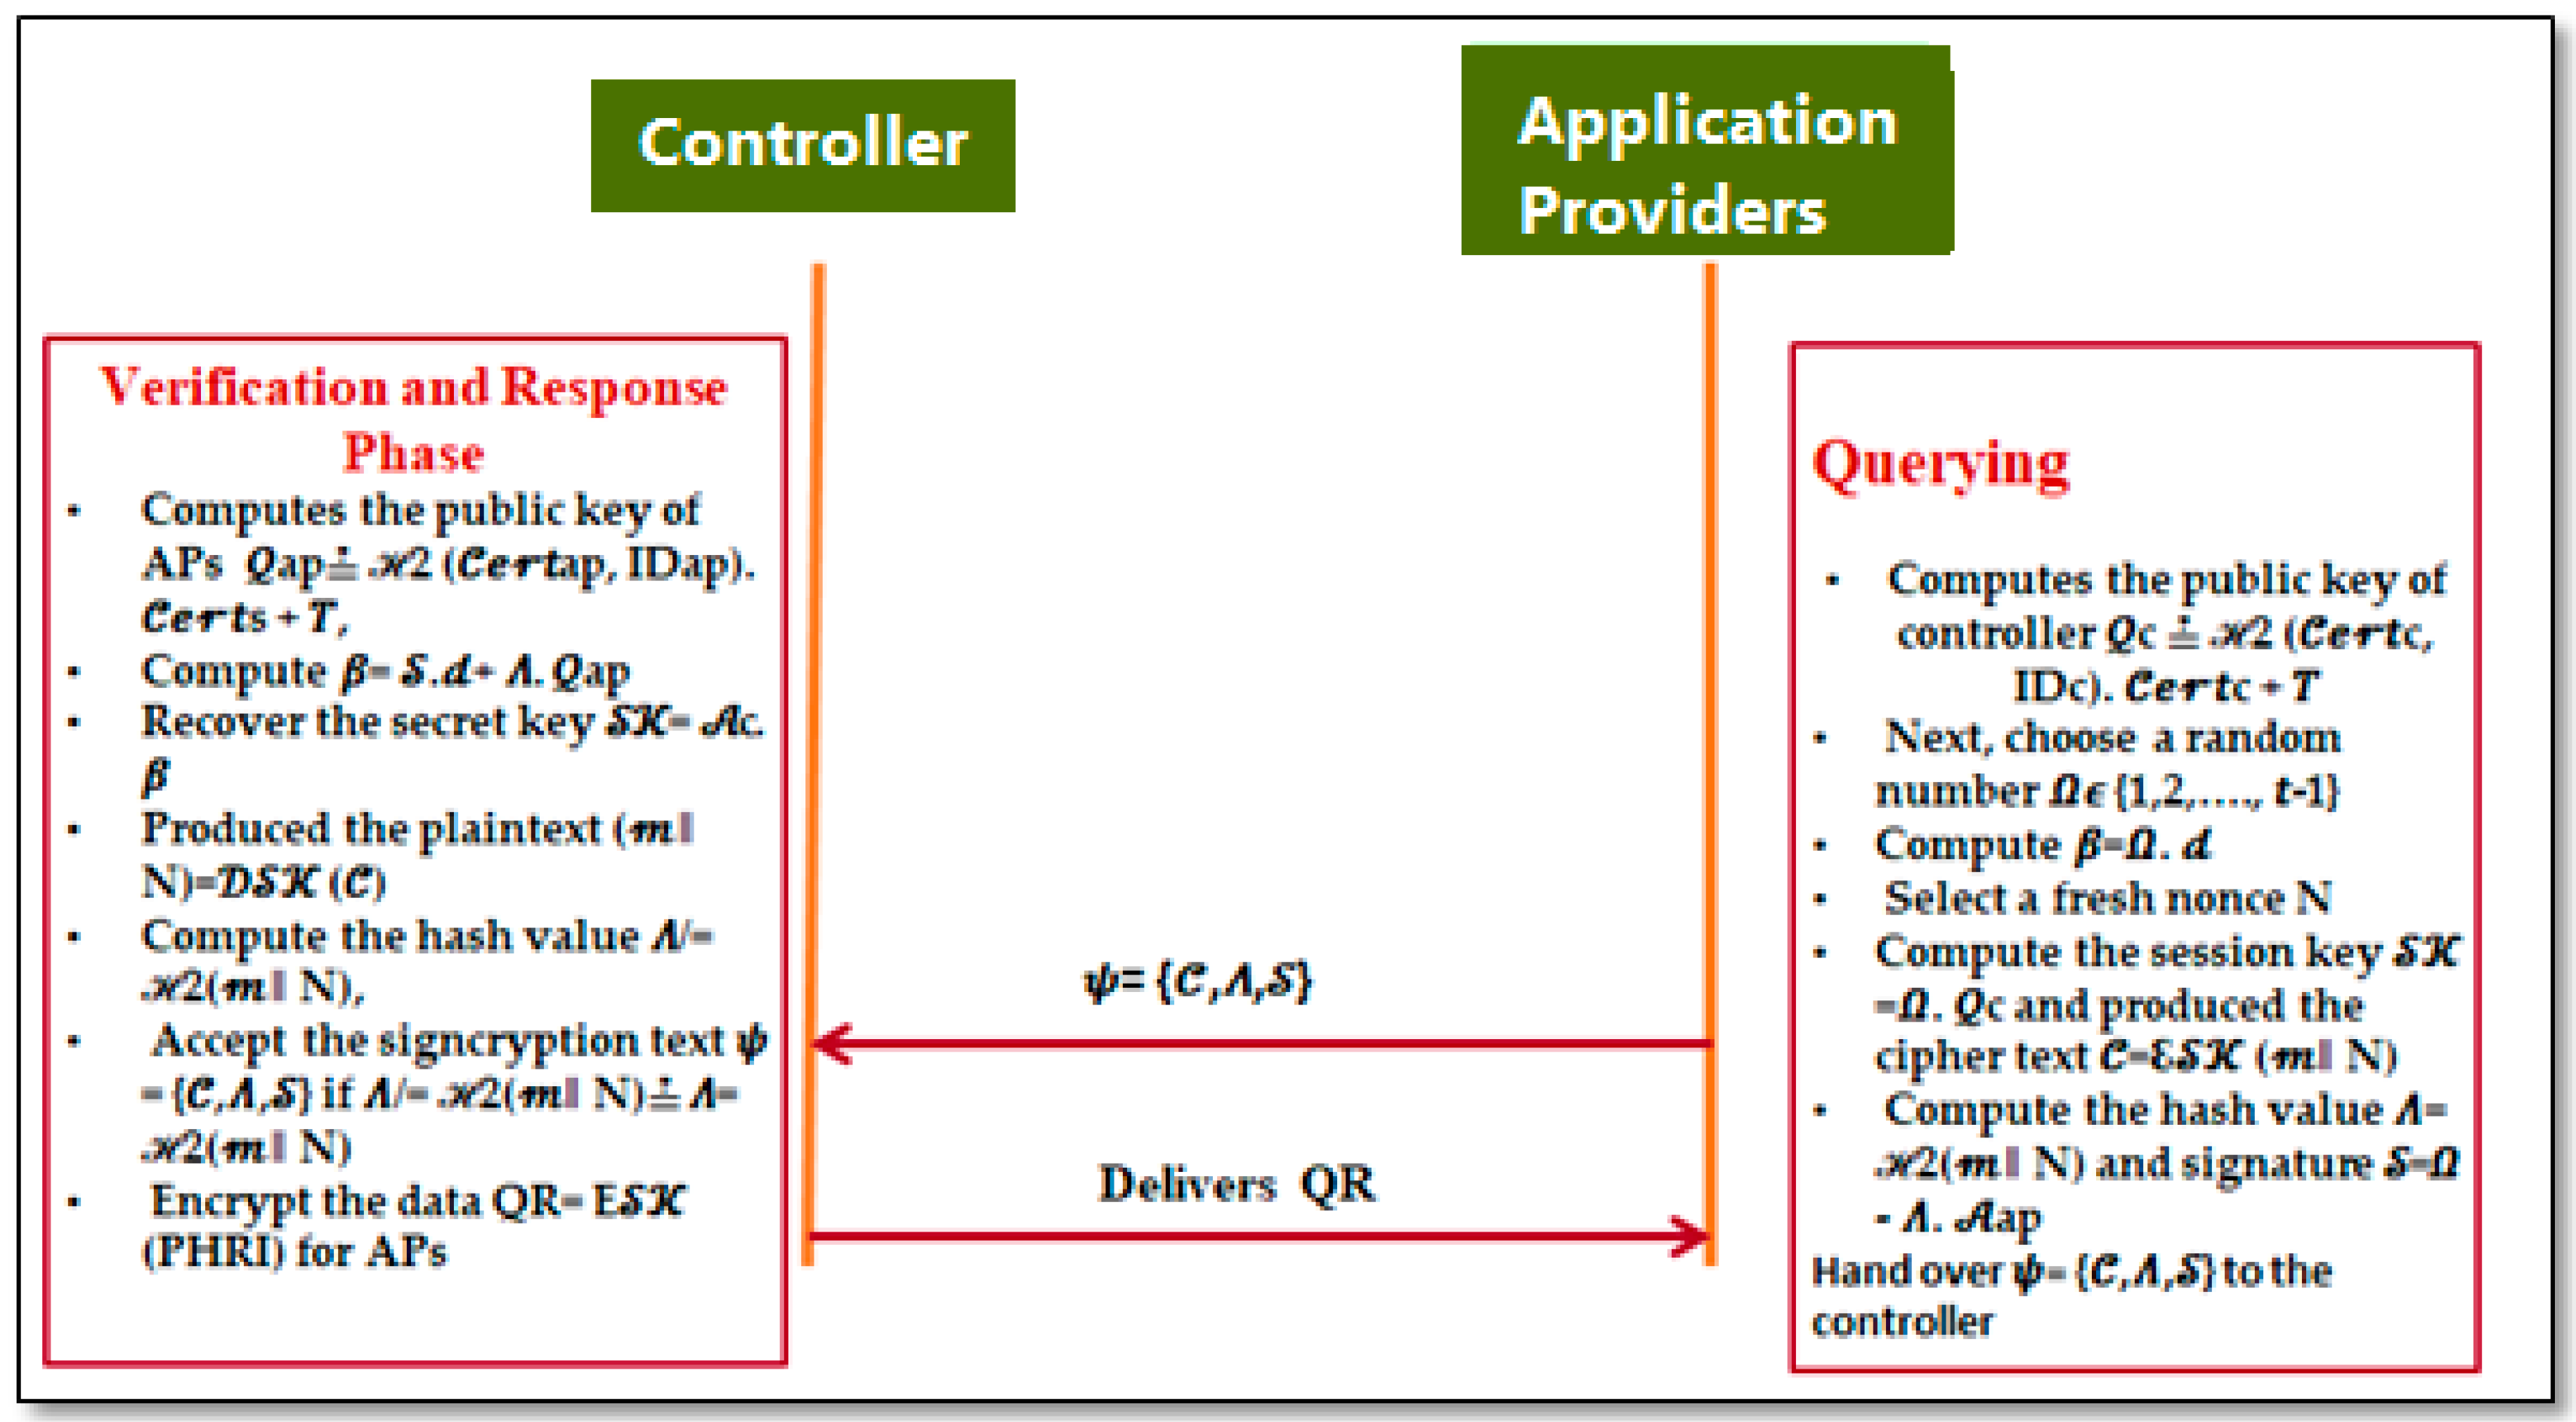
Figure 2 and Figure 3 illustrate the overall process of implementation, which contains the following four steps:
Figure 2.
Initialization and registration phase of certificate-based signcryption (CB-SN) access control for wireless body area networks (WBAN).
Figure 3.
Querying and response phase of CB-SN access control for WBAN.
6.1. Initialization
The CsA calls the setup process where CAs produce an essential parameter set {hε𝒸, δ, ℑ𝑡, 𝒹, hε𝒸, 𝛵, 1, 2, 3} and after that select a master secret key 𝛶 from {1,2, …, 𝑡 − 1} and calculate the master public key 𝛵 = 𝛶 . 𝒹, respectively. The essential parameters set is directly accessible on a network and the master secret key Y is kept by the CsA secret.
6.2. Registration
In addition, each actor (APs and controller) with identity IDA, chooses a random number 𝜔A and computes their public variable A = 𝜔A.𝒹. Then, the actor (APs and controller) with identity IDA delivers (PVA, IDA) to the CsA by using open channel. Furthermore, the CsA selects a random number 𝜒A𝜖 {1,2, …, 𝑡 − 1}, calculates 𝜑A = 𝜒A . 𝒹, computes the certificate CertA = 𝜑A+ PVA, computes auxiliary variable 𝒶𝓊𝓍A = 1 (𝑒𝓇𝑡A, IDA) . 𝜒A + 𝛶 and, then, hand over a certificate CertA with auxiliary variable (CertA, auxA) to the actors (APs and controller) via insecure link. Moreover, each actor (APs and controller) creates his private key AA = H1 (CertA, IDA) . wA + auxA and make his public key as QA = AA . d.
6.3. Querying Phase
The APs call the SG algorithm, that is, the APs compute the public key of controller Qc ≟ H2 (Certc, IDc) . Certc + T. Next, they choose a random number 𝛺𝜖 {1, 2, …, 𝑡 − 1} and compute 𝛽 = 𝛺 . 𝒹, select a fresh nonce N, compute the session key SK = 𝛺 . Qc and produced the cipher text C = ℇ (𝓂 ‖ N), compute the hash value 𝛬 = H2(𝓂 ‖ N) and signature = 𝛺 – 𝛬 . Aap, then, hand over 𝜓 = {C,S} to the controller using insecure channel.
6.4. Verification and Response
For this purpose, the controller first calls a US algorithm, that is, the controller, first, computes the public key of APs ap ≟ 2 (𝑒𝓇𝑡ap, IDap) . 𝑒𝓇𝑡s + 𝛵, computes 𝛽 = . 𝒹 + 𝛬 . ap, recovers the secret key = 𝒜c . 𝛽 and produces the plaintext (𝓂 ‖ N) = (), computes the hash value 𝛬/ = 2(𝓂 ‖ N), accepts the signcryption text 𝜓 = {,𝛬,}, if 𝛬/ = 2(𝓂‖ N) ≟ 𝛬 = 2(𝓂 ‖ N) and encrypts the data QR = E (PHRI) for Aps, and delivers it using the open networks.
7. Performance
We choose three main parameters that are security services, energy (computational cost), and bandwidth (communication cost), in the proposed CB-SN access control scheme and existing ones, i.e., Li et al. [22], Omala et al. [15], Gao et al. [24], Braeken et al. [17], Braeken et al. [19] Schemes 1, 2, and 3, for measuring the performance. Appendix A shows the mplementations of CB-SN Access Control Scheme in AVISPA.
7.1. Security Performance
The security performance of a designed and existing access control scheme as shown in Table 2, in which we pick the security services and verification tool, i.e., confidentiality, unforgeability, authentication, integrity, anti-replay attack, forward secrecy, public verifiability, random oracle model, and formal verification through AVISPA, respectively. The symbols CFY, UFY, ATN, ITY, ARA, FSY, PVY, ROM, FVTA, √, and ⨵ indicate confidentiality, unforgeability, authentication, integrity, anti-replay attack, forward secrecy, public verifiability, random oracle model, formal verification through AVISPA, satisfying the service, and does not satisfy, respectively. Therefore, it is clearly shown that, our proposed CB-SN meet all the claimed security services and the schemes, i.e., Li et al. [22], Omala et al. [15], Gao et al. [24], Braeken et al. [17], Braeken et al. [19] Schemes 1, 2, and 3 do not meet the services such as FSY and PVY, as well as FVTA or some other verification tool.
Table 2.
Comparison with respect to security properties.
7.2. Computational Cost
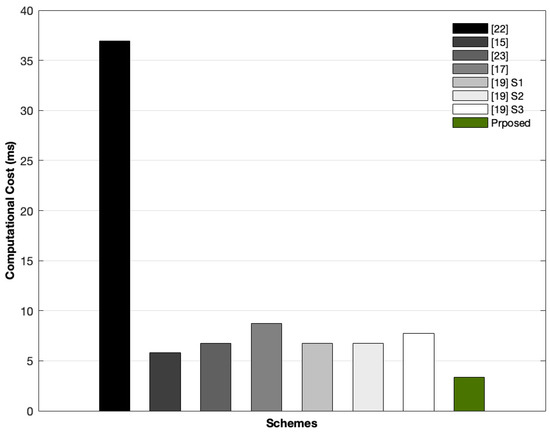
The comparison among the proposed CB-SN access control scheme and existing ones, i.e., Li et al. [22], Omala et al. [15], Gao et al. [24], Braeken et al. [17], Braeken et al. [19] Schemes 1, 2, and 3, on the basis of major operations is provided in this section. Normally, the computational cost includes an expensive mathematical operation, for example, bilinear pairing (𝒷𝓅), modular exponential (𝓂𝓍𝓅), elliptic curve scalar multiplication (𝑒𝓈𝓂), and hyper-elliptic curve divisor scalar multiplication (𝒽𝓈𝓂), while designing a cryptographic algorithm. Next, in Table 3, we provide a required major operation of the proposed CB-SN access control scheme and existing ones, i.e., Li et al. [22], Omala et al. [15], Gao et al. [24], Braeken et al. [17], Braeken et al. [19] Schemes 1, 2, and 3. The calculated values of Table 3, regarding 𝒷𝓅, 𝓂𝓍𝓅, and 𝑒𝓈𝓂 are based on [27], and 𝓈𝓂 is based on the assumption of [29]. Therefore, according to [29], the single 𝒷𝓅 required 14.90 ms, single 𝓂𝓍𝓅 consumes 1.25 ms, and single 𝑒𝓈𝓂 needs 0.97 ms, while the assumption of [29], about single 𝒽𝓈𝓂 is that, it required 0.48 ms. The experiment was performed by using the hardware resources, i.e., Intel Core i74510UCPU, 8 GB RAM, and 2.0GHz processor and software resources such as C++ with Multi-precision Integer and Rational Arithmetic C Library (MIRACL) and window 7. By using the data of Table 3, our scheme reduced the computational cost on the basis of ms from Li et al. [22] is (2𝒷𝓅 + 6𝑒𝓈𝓂 + 2𝓂𝓍𝓅) - (7𝒽𝓈𝓂)/ (2𝒷𝓅 + 6𝑒𝓈𝓂 + 2𝓂𝓍𝓅) = 36.94 – 3.36/36.94*100 = 90.90%, Omala et al. [15] is (6𝑒𝓈𝓂) - (7 𝒽𝓈𝓂)/(6 𝑒𝓈𝓂) = 5.82 – 3.36/5.82*100 = 42.26%, Gao et al. [23] is (7𝑒𝓈𝓂) - (7𝒽𝓈𝓂)/(7𝑒𝓈𝓂) = 6.77 – 3.36/6.77*100 = 50.36%, Braeken et al. [17] is (9𝑒𝓈𝓂) - (7𝒽𝓈𝓂)/(9𝑒𝓈𝓂) = 8.73 – 3.36/8.73*100 = 61.51%, Braeken et al. [19] scheme 1(S1) is (7𝑒𝓈𝓂) - (7𝒽𝓈𝓂)/(7𝑒𝓈𝓂) = 6.77 – 3.36/6.77*100 = 50.36%, Braeken et al. [19] scheme 2(S2) is (7𝑒𝓈𝓂) - (7𝒽𝓈𝓂)/(7𝑒𝓈𝓂) = 6.77 – 3.36/6.77*100 =50.36%, Braeken et al. [19] scheme 3(S3) is (8𝑒𝓈𝓂) - (7𝒽𝓈𝓂)/(8𝑒𝓈𝓂) = 7.76 – 3.36/7.76*100 = 56.70%, respectively. Moreover, in Table 4, we deliver the computational cost on the basis of milliseconds (ms) among the proposed CB-SN access control and those of Li et al. [23], Omala et al. [15], and Gao et al. [24]. Furthermore, in Figure 4, the clear computational cost reduction is shown.
Table 3.
Comparison with respect to major operations.
Table 4.
Computational cost comparison in milliseconds.
Figure 4.
Total computational cost reduction.
7.3. Communication Cost
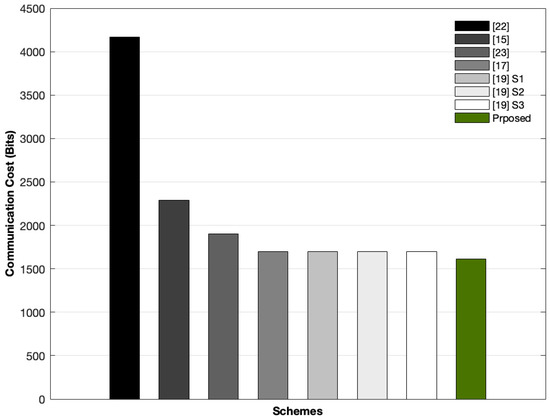
We compare our newly proposed CB-SN access control scheme with the existing related access control schemes, i.e., Li et al. [22], Omala et al. [15], Gao et al. [24], Braeken et al. [17], Braeken et al. [19] Schemes 1, 2, and 3 on the basis of communication cost. Usually, the communication cost of the signcryption schemes is calculated by using the cipher text and the extra parameters such as signature, hash value, and identity, etc., during the communication process. For the comparison, we suppose that, |𝔖1| = |𝔖| = |𝔖2| = 1024 bits, |𝒵𝓆| = 160 bits, |𝒵n| = 80 bits, and |H| = 512 bits, |𝓂| = 1024 bits, and |ID| = 80 bits. According to our suppositions, the communication cost for Li et al. [22] is 3|𝔖1| + |ID| + |𝓂|, for Omala et al. [15] is |𝔖1| + |ID| + |𝓂| + |𝒵𝓆|, for Gao et al. [2] is |ID| + |𝓂| + 5|𝒵𝓆|, for Braeken et al. [17] |ID| + |𝓂| + 5|𝒵𝓆|, for Braeken et al. [19] Scheme 1 is |ID| + |𝓂| + 5|𝒵𝓆|, for Braeken et al. [19] Scheme 2 is |ID| + |𝓂| + 5|𝒵𝓆|, Braeken et al. [19] Scheme 3 is |ID| + |𝓂|+5|𝒵𝓆|, and for our designed CB-SN access control scheme is |𝒵n| + |H| + |𝓂|, respectively.
- The reduction in communication cost of the proposed CB-SN access control scheme from Li et al. [22] is (3|𝔖1| + |ID| + |𝓂|) (|𝒵n| + |H| + |𝓂|)/(3|𝔖1| + |ID| + |𝓂|) = (4176 −1616)/(4176)*100 = 61.30%,
- The reduction in communication cost of our designed CB-SN access control scheme from Omala et al. [15] is (|𝔖1| + |ID| + |𝓂| + |𝒵𝓆|)(|𝒵n| + |H|+|𝓂|)/(|𝔖1|+ |ID| + |𝓂| + |𝒵𝓆|) = (2288 − 1616)/(2288)*100 = 29.37%.
- The reduction in communication cost of of the proposed CB-SN access control scheme from Gao et al. [23] is (|ID| + |𝓂| + 5|𝒵𝓆|) − (|𝒵n| + |H| + |𝓂|)/(|ID| + |𝓂| + 5|𝒵𝓆|) = (1904 − 1616)/(1904)*100 = 15.12%.
- The reduction in communication cost of the proposed CB-SN access control scheme from Braeken et al. [17] and Braeken et al. [19] Scheme 1, 2, and 3 is (|𝓂| +|H| + |𝒵𝓆|) − (|𝒵n| + |H| + |𝓂|)/|𝓂| + 2|𝒵𝓆|) = (1696 − 1616)/(1696)*100 = 4.71%.
Comparative analysis of communication cost of the proposed CB-SN scheme with relevant existing schemes are provided in Figure 5, which shows a clear savings of communication cost.
Figure 5.
Total communication cost.
8. Conclusions
Connected health brings together multidisciplinary technologies, such as the Internet of things (IoT) and wireless body area networks (WBAN), to provide preventive or proactive healthcare services by connecting devices and persons to build up the modern healthcare system. However, due to the openness of the wireless environment, the privacy of people’s physiological data, and resource-constrained nature of IoT devices, especially in terms of energy supply, often body sensors are vulnerable to different kinds of known and unknown cryptographic attacks. To tackle these issues, a comprehensive review of the existing certificate-based signcryption schemes was carried out in the literature. We found that these schemes are based on hard problems, i.e., elliptic curve and bilinear pairing, suffering from high computational cost and communication overhead. Therefore, to solve this problem, a new design scheme, called certificate-based signcryption access control scheme, is introduced, because the new scheme involves a hyper-elliptic curve, which offers the same level of security as the elliptic curve and bilinear pairing with lower key size. Furthermore, in the proposed scheme addresses and resolves intelligently the issues of increased computational cost and undesired communication overhead.
Author Contributions
Conceptualization, I.U and A.A.; Methodology and Implementation, I.U, A.A and M.A.K.; Simulation, I.U, A.A, and M.A.K.; Validation, I.U, A.A, H.K and M.A.K.; Data Curation, A.A, and H.K.; Writing-Original Draft Preparation, A.A, N.U.A and I.U.; Writing-Review & Editing, A. A and M.A.K.; Supervision, N.U.A.
Funding
This research received no external funding.
Conflicts of Interest
The authors declare no conflict of interest.
Appendix A. Implementations of CB-SN Access Control Scheme in AVISPA
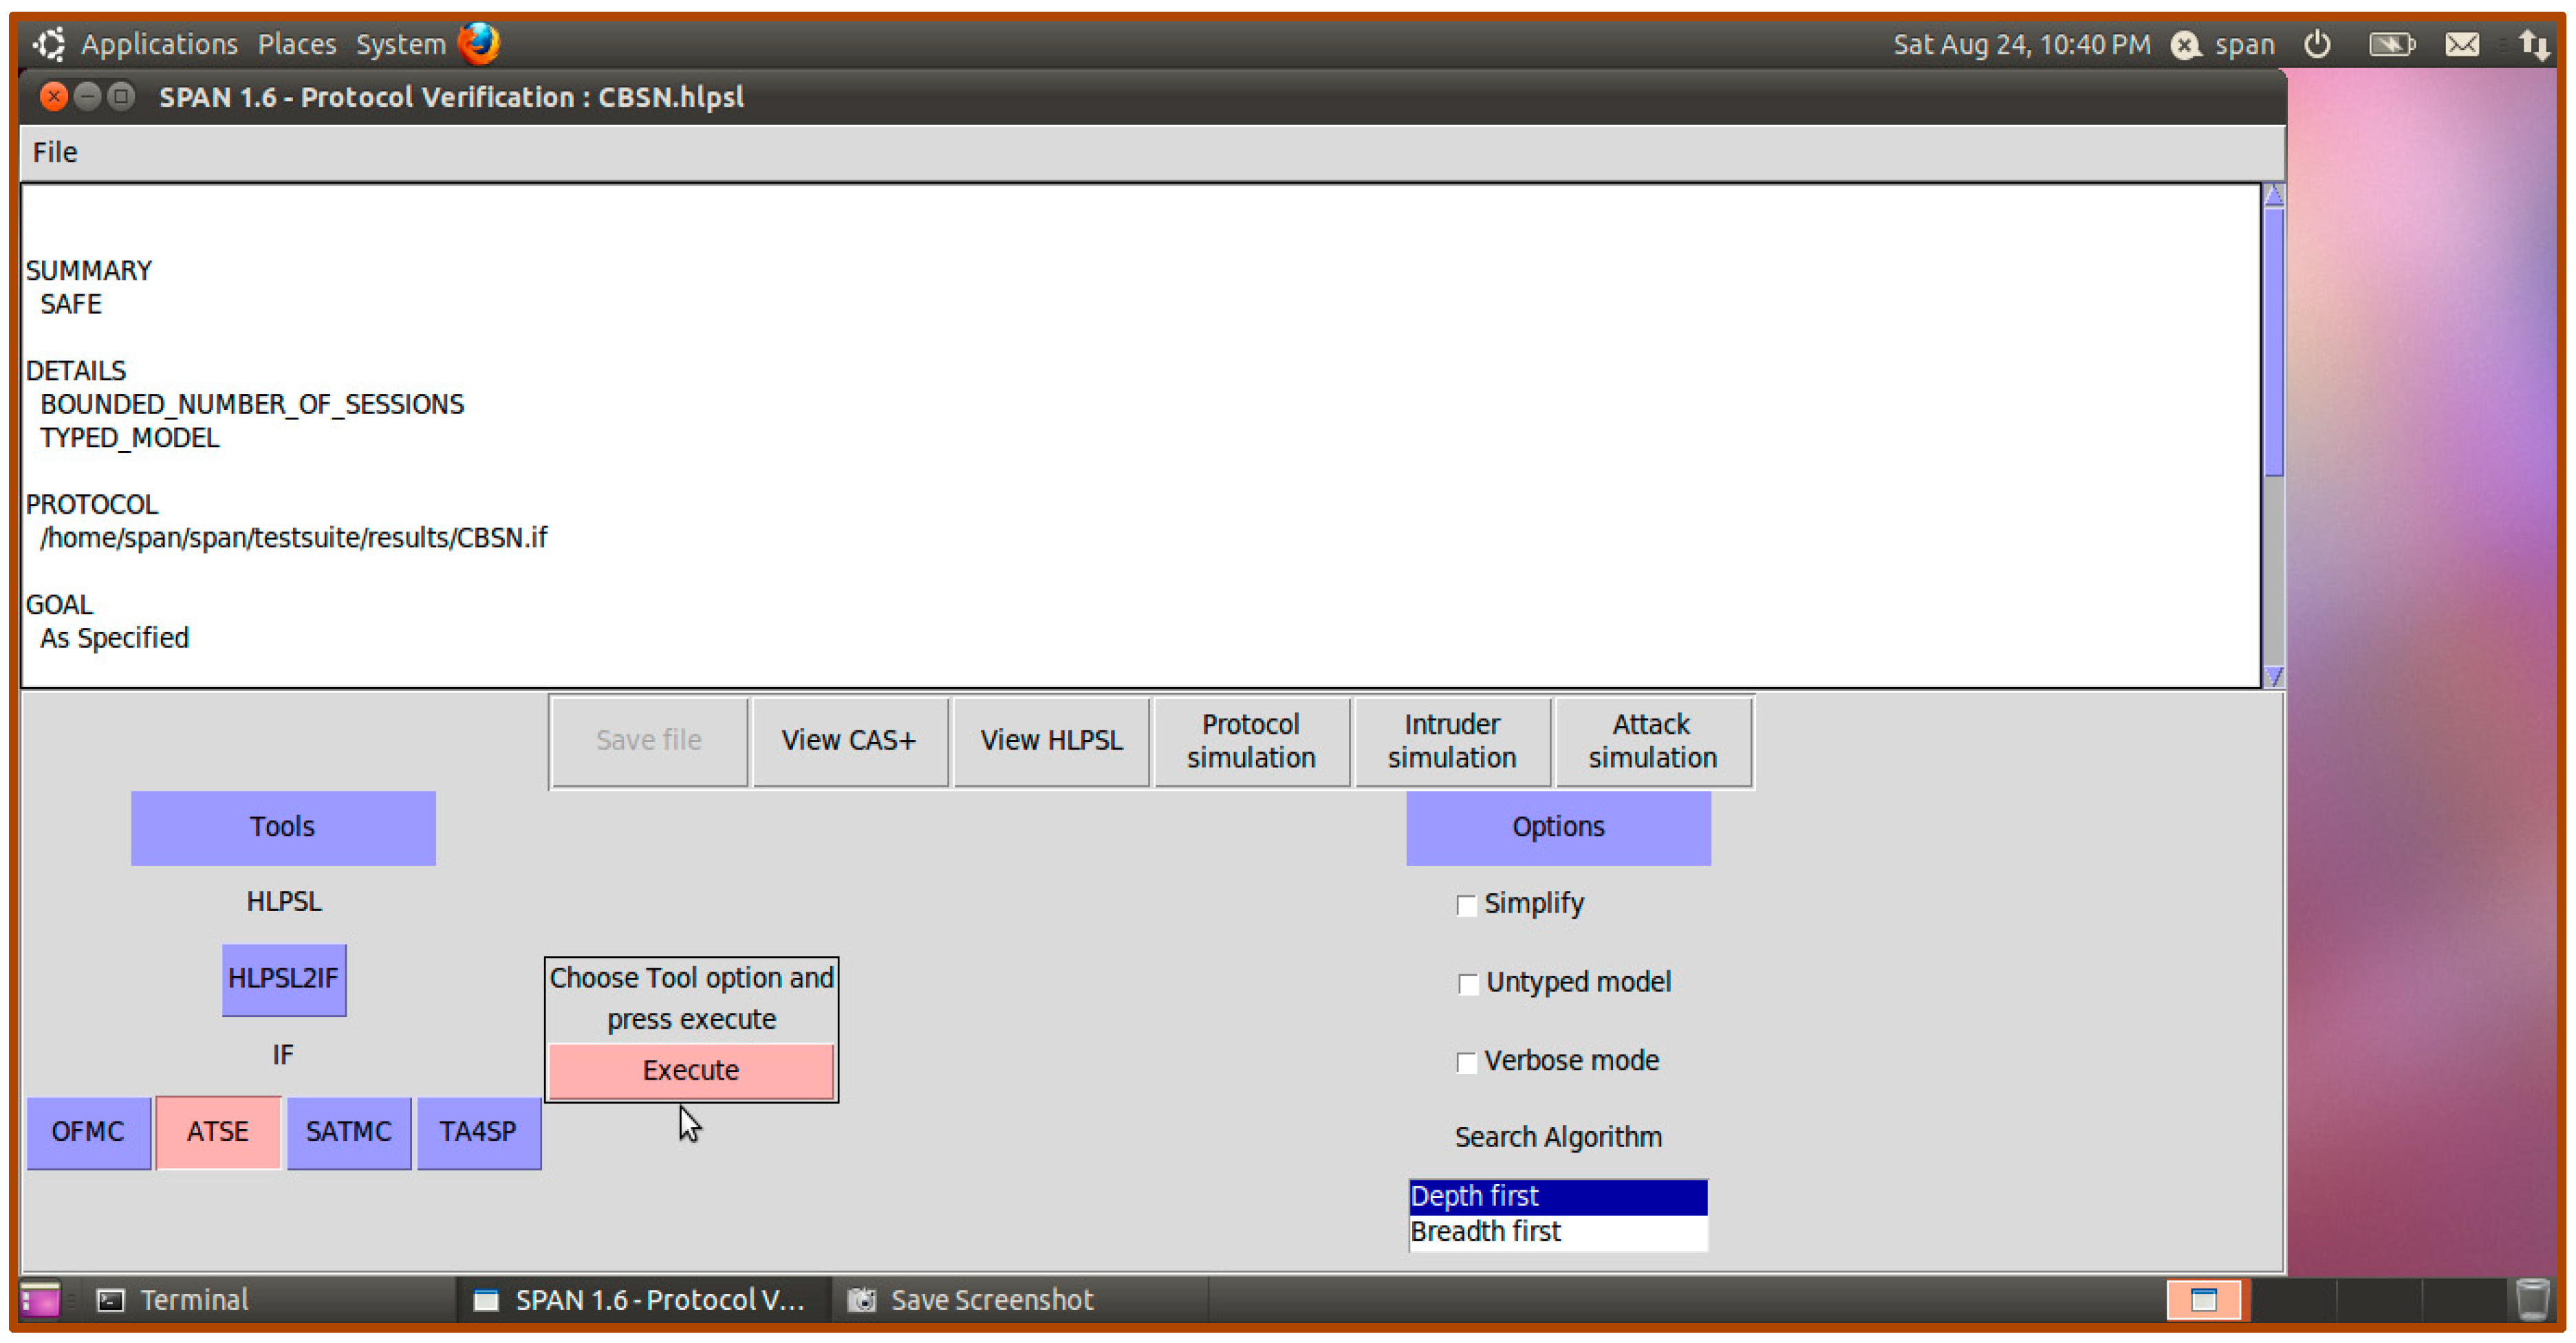
In this subphase, we implement our proposed CB-SN access control for WBAN in AVISPA tool. For this experiment, we used hardware resources, for example, Haier Win8.1 PC, Intel (R) Core (TM) i3-4010U CPU @ 1.70 GHz, supporting 64-bit operating system, and x64-based processor. In addition, the software resources such as Oracle VM virtual Box (version: 5.2.0.118431) and SPAN (version: SPAN-Ubuntu-10.10-light_1). Our implementation contains four roles that are APs which are provided in Algorithm A1, a controller which is shown in Algorithm A2, and environment and session roles which are provided in Algorithm A3, respectively. Here, we provide clarification of some symbols, which are used in HLPSL language in these four roles, as well as in the CB-SN access control for WBAN. We use the arrow sign ⇿ to represent the similarity, whereas the symbol that occurs before this sign represents HLPSL, after using for the algorithm. Therefore, Qap ⇿ ap, Qc ⇿ c, N ⇿ N, Omega ⇿ 𝛺, A ⇿ 𝛬, {E(M')}_Sk' ⇿ = ℇ(𝓂 ‖ N), Sk' ⇿ , M' ⇿ 𝓂, {Minuss(Omega'.A')}_inv(Qap) ⇿ = 𝛺 – 𝛬 . 𝒜ap, and inv (Qap) ⇿ 𝒜ap, respectively. Therefore, we test (1000 times), and our scheme gives SAFE results under the on-the-fly model checker (O-f-M-C) and constraint logic-based attack searcher (CL-ATSe), which are provided in Figure A1 and Figure A2.
| Algorithm A1 High level protocol specification language (HLPSL) code for application providers (Aps) role |
| role role_Aps(Aps:agent,Controller:agent,Qap:public_key,Qc:public_key,SND,RCV:channel(dy)) played_by Aps def = local State:nat, N:text, Minuss:hash_func, Omega:text, A:text, M:text, E:hash_func, Sk:symmetric_key init State := 0 transition 1. State=0 /\ RCV(start) =|> State':=1 /\ SND(Aps.Controller) 2. State=1 /\ RCV(Controller.{N'}_Qc) =|> State':=2 /\ A':=new() /\ Omega':=new() /\ Sk':=new() /\ M':=new() /\ secret(M',sec_2,{Aps}) /\ witness(Aps,Controller,auth_1,M') /\ SND(Aps.{E(M')}_Sk'.{Minuss(Omega'.A')}_inv(Qap)) end role role role_Aps(Aps:agent,Controller:agent,Qap:public_key,Qc:public_key,SND,RCV:channel(dy)) played_by Aps def = local State:nat, N:text, Minuss:hash_func, Omega:text, A:text, M:text, E: hash_func, Sk:symmetric_key init State:= 0 transition 1. State = 0 /\ RCV(start) =|> State':=1 /\ SND(Aps.Controller) 2. State = 1 /\ RCV(Controller.{N'}_Qc) =|> State':=2 /\ A':=new() /\ Omega':=new() /\ Sk':=new() /\ M':=new() /\ secret(M',sec_2,{Aps}) /\ witness(Aps,Controller,auth_1,M') /\ SND(Aps.{E(M')}_Sk'.{Minuss(Omega'.A')}_inv(Qap)) end role |
| Algorithm A2 HLPSL code for controller role. |
| role role_Controller(Aps:agent,Controller:agent,Qap:public_key,Qc:public_key,SND,RCV:channel(dy)) played_by Controller def = local State: nat, N:text, Minuss:hash_func, Omega:text, A:text, M:text, E: hash_func, Sk:symmetric_key init State := 0 transition 1. State=0 /\ RCV(Aps.Controller) =|> State':=1 /\ N':=new() /\ SND(Controller.{N'}_Qc) 6. State=1 /\ RCV(Aps.{E(M')}_Sk'.{Minuss(Omega'.A')}_inv(Qap)) =|> State':=2 /\ request(Controller,Aps,auth_1,M') /\ secret(M',sec_2,{Aps}) end role |
| Algorithm A3 HLPSL code for session and environmental role. |
| role session1 (Aps:agent,Controller:agent, Qap:public_key, Qc:public_key) def = local SND2,RCV2,SND1,RCV1:channel(dy) composition role_Controller(Aps,Controller,Qap,Qc,SND2,RCV2)/\ role_Aps(Aps,Controller,Qap,Qc,SND1,RCV1) end role role session2(Aps:agent,Controller:agent,Qap:public_key,Qc:public_key) def = local SND1,RCV1:channel(dy) composition role_Aps(Aps,Controller,Qap,Qc,SND1,RCV1) end role role environment() def = const hash_0:hash_func,qap:public_key,alice:agent,bob:agent, qc:public_key,const_1:agent,const_2:public_key, const_3:public_key,auth_1:protocol_id,sec_2:protocol_id intruder_knowledge = {alice,bob} composition session2(i,const_1,const_2,const_3) /\ session1(alice,bob,qap,qc) end role goal authentication_on auth_1 secrecy_of sec_2 end goal environment () |
Figure A1.
Simulation result of OFMC.
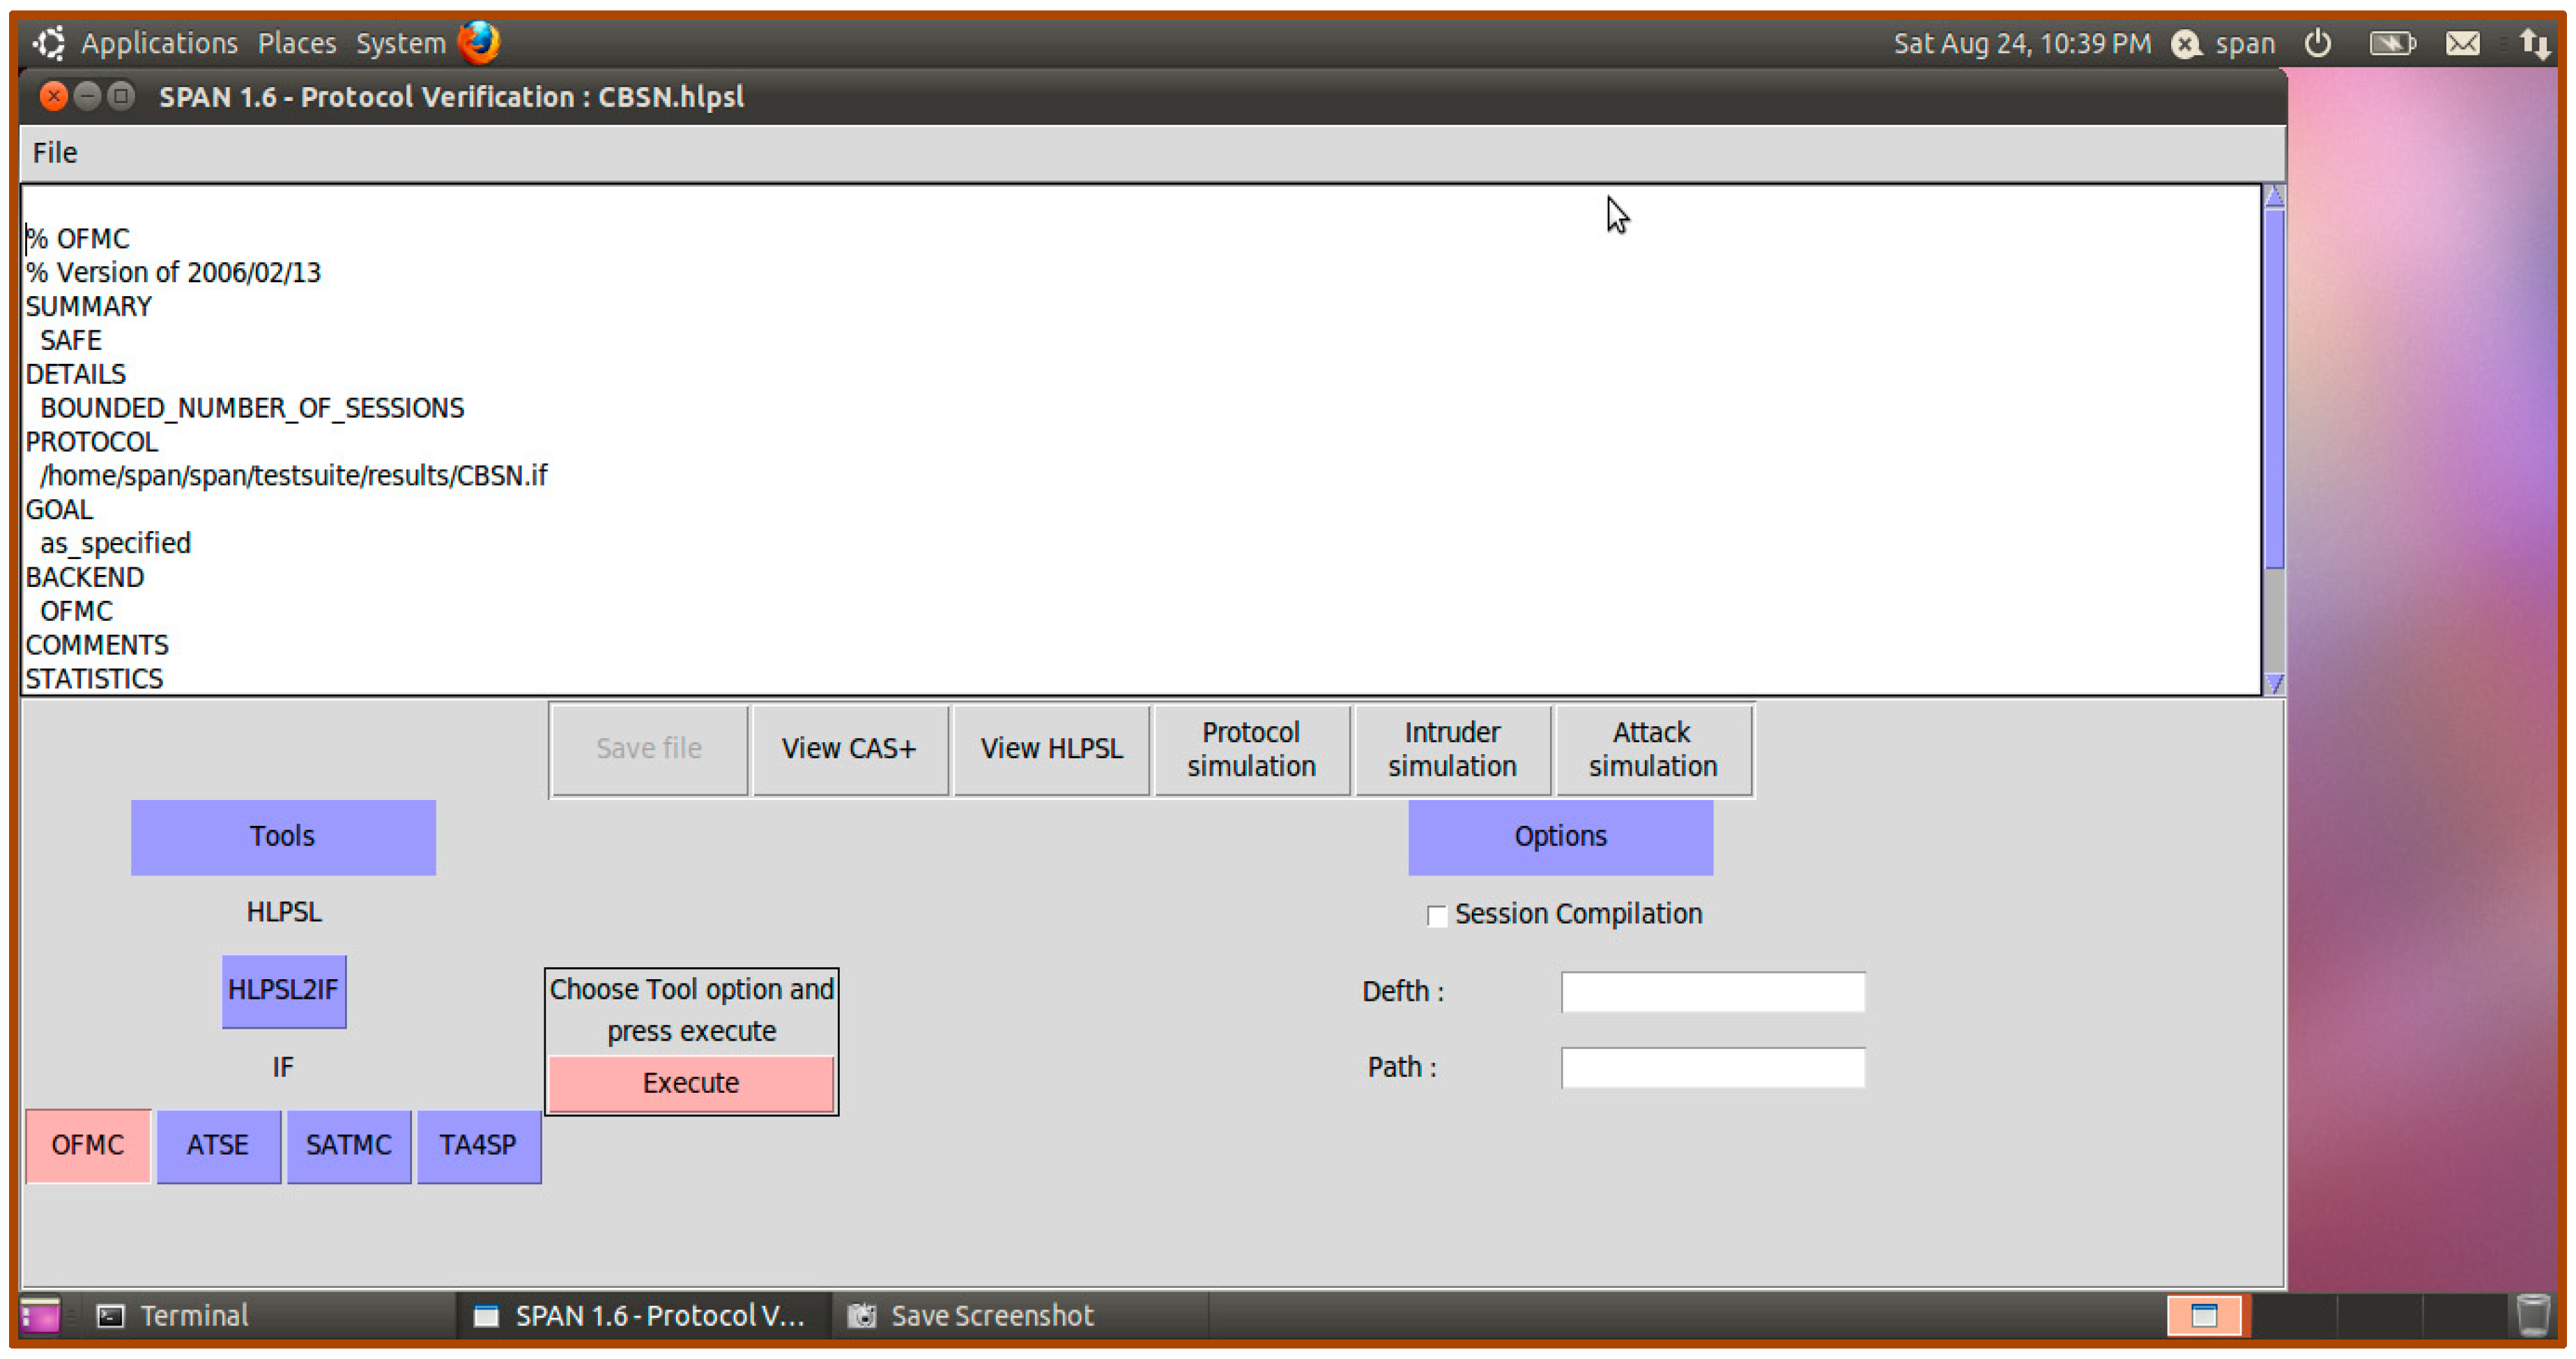
Figure A2.
Simulation result of ATSE.
References
- Alkhayyat, A.; Thabit, A.A.; Al-Mayali, F.A.; Abbasi, Q.H. WBSN in IoT Health-Based Application: Toward Delay and Energy Consumption Minimization. J. Sens. 2019, 2019, 2508452. [Google Scholar] [CrossRef] [Scilit]
- El-hajj, M.; Fadlallah, A.; Chamoun, M.; Serhrouchni, A. A Survey of the Internet of Things (IoT) Authentication Schemes. Sensors 2019, 19, 1141. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Chaudhary, S.; Singh, A.; Kakali, C. Wireless Body Sensor Network (WBSN) Security and Privacy Issues: A Survey. Int. J. Comp. Int. IoT 2019, 2, 515–521. [Google Scholar]
- Zhou, C. An improved lightweight certificateless generalized signcryption scheme for mobile-health system. Int. J. Dist. Sen. Netw. 2019. [Google Scholar] [CrossRef] [Scilit]
- Kumar, M.; Verma, H.K.; Sikka, G. A secure lightweight signature-based authentication for Cloud-IoT crowdsensing environments. Trans. Emerg. Telecommun. Technol. 2018. [Google Scholar] [CrossRef] [Scilit]
- Rajesh, S.; Paul, V.; Menon, V.G.; Khosravi, M.R. A Secure and Efficient Lightweight Symmetric Encryption Scheme for Transfer of Text Files between Embedded IoT Devices. Symmetry 2019, 11, 293. [Google Scholar] [CrossRef] [Scilit]
- Zheng, Y. Digital signcryption or how to achieve cost (signature & encryption) cost (signature)+ cost (encryption). In Advances in Cryptology, CRYPTO’97; Springer: Cham, Switzerland, 1997; pp. 165–179. [Google Scholar]
- Waheed, A.; Iqbal, J.; Din, N.; Islam, S.U.; Umar, A.I.; Amin, N.U. Improved Cryptanalysis of Provable Certificateless Generalized Signcryption. Int. J. Adv. Comput. Sci. Appl. 2019, 10. [Google Scholar] [CrossRef] [Scilit]
- Shamir, A. Identity-based cryptosystems and signature schemes. In Workshop on the Theory and Application of Cryptographic Techniques; Springer: Berlin, Germany, 1985; pp. 47–53. [Google Scholar]
- Malone-Lee, J. Identity Based Signcryption. Cryptology ePrint Archive; Report 2002/098. 2002. Available online: http://eprint.iacr.org/2002/098 (accessed on 30 July 2019).
- Luo, W.; Ma, W. Secure and Efficient Data Sharing Scheme Based on Certificateless Hybrid Signcryption for Cloud Storage. Electronics 2019, 8, 590. [Google Scholar] [CrossRef] [Scilit]
- Barbosa, M.; Farshim, P. Certificateless signcryption. In Proceedings of the ACM Symposium on Information, Computer and Communications Security, Tokyo, Japan, 18–20 March 2008; pp. 369–372. [Google Scholar]
- Lu, Y.; Li, J. Provably Secure Certificate Based Signcryption Scheme without Pairings. KSII Trans. Internet Inf. Syst. 2014, 8, 2554–2571. [Google Scholar]
- Li, F.; Han, Y.; Jin, C. Practical signcryption for secure communication of wireless sensor networks. Wirel. Pers. Commun. 2016, 89, 1391–1412. [Google Scholar] [CrossRef] [Scilit]
- Omala, A.A.; Mbandu, A.S.; Mutiria, K.D.; Jin, C.; Li, F. Provably Secure Heterogeneous Access Control Scheme for Wireless body area networks. JMS 2018, 42, 108. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Gentry, C. Certificate-Based Encryption and the Certificate Revocation Problem. In Proceedings of the International Conference on Theory Application of Cryptographic Techniques, Warsaw, Poland, 4–8 May 2003; pp. 272–293. [Google Scholar]
- Braeken, A.; Shabisha, P.; Touhafi, A.; Steenhaut, K. Pairing free and implicit certificate based signcryption scheme with proxy re-encryption for secure cloud data storage. In Proceedings of the 2017 3rd International Conference of Cloud Computing Technologies and Applications, Rabat, Morocco, 24–26 Octcber 2017. [Google Scholar]
- Le, M.-H.; Hwang, S.O. Certificate-Based Signcryption Scheme without Pairing: Directly Verifying Signcrypted Messages Using a Public Key. ETRI J. 2016, 38, 724–734. [Google Scholar] [CrossRef] [Scilit]
- Braeken, A. Pairing Free Certificate Based Signcryption Schemes Using ECQV Implicit Certificates. KSII Trans. Internet Inf. Syst. 2019, 13, 1546–1565. [Google Scholar]
- Cagalaban, G.; Kim, S. Towards a secure patient information access control in ubiquitous healthcare systems using identity-based signcryption. In Proceedings of the 13th International Conference on Advanced Communication Technology (ICACT), Seoul, Korea, 13–16 February 2011; pp. 863–867. [Google Scholar]
- Hu, C.; Zhang, N.; Li, H.; Cheng, X.; Liao, X. Body area network security: A fuzzy attribute-based signcryption scheme. IEEE J. Sel. Areas Commun. 2013, 31, 37–46. [Google Scholar] [CrossRef] [Scilit]
- Li, F.; Hong, J. Efficient Certificateless Access Control for Wireless body area networkss. IEEE Sens. J. 2016, 16, 5389–5396. [Google Scholar] [CrossRef] [Scilit]
- Li, F.; Han, Y.; Jin, C. Cost-effective and anonymous access control for wireless body area networkss. IEEE Syst. J. 2018, 12, 747–758. [Google Scholar] [CrossRef]
- Gao, G.M.; Peng, X.G.; Jin, L.Z. Efficient Access Control Scheme with Certificateless Signcryption for Wireless body area networkss. Int. J. Netw. Secur. 2019, 21, 428–437. [Google Scholar]
- Ullah, I.; Amin, N.U.; Naeem, M.; Khattak, S.J.; Ali, H. A Novel Provable Secured Signcryption Scheme PSSS: A Hyper-Elliptic Curve-Based Approach. Mathematics 2019, 7, 686. [Google Scholar] [CrossRef] [Scilit]
- Ullah, S.; Li, X.-Y.; Zhang, L.A. Review of Signcryption Schemes Based on Hyper Elliptic Curve. In Proceedings of the 3rd International Conference on Big Data Computing and Communications (BIGCOM), Chengdu, China, 10–11 August 2017. [Google Scholar]
- Ullah, I.; Haqb, U.I.; Amin, N.U.; Umar, I.A.; Khattak, H. Proxy Signcrypion Scheme Based on Hyper Elliptic Curves. IJC 2016, 20, 157–166. [Google Scholar]
- Khan, M.A.; Qureshi, I.M.; Khanzada, F. A Hybrid Communication Scheme for Efficient and Low-Cost Deployment of Future Flying Ad-Hoc Network (FANET). Drones 2019, 3, 16. [Google Scholar] [CrossRef] [Scilit]
- Rahman, A.U.; Ullah, I.; Naeem, M.; Anwar, R.; Amin, N.U.; Khattak, H.; Ullah, S. A Lightweight Multi-Message and Multi-Receiver Heterogeneous Hybrid Signcryption Scheme based on Hyper Elliptic Curve. Int. J. Adv. Comput. Sci. Appl. (IJACSA) 2018, 9, 160–167. [Google Scholar] [CrossRef] [Scilit]

© 2019 by the authors. Licensee MDPI, Basel, Switzerland. This article is an open access article distributed under the terms and conditions of the Creative Commons Attribution (CC BY) license (http://creativecommons.org/licenses/by/4.0/).