Article

WinAPIReplay: Safely Re-Executing Win32 and NT-Native Malware API-Call Logs to Measure Behavioral Reproducibility and Generate Labeled Endpoint Telemetry

1
Faculty of Informatics/Cyber Informatics Research Institute, Kindai University, Higashiosaka-shi 577-8502, Japan
2
Graduate School of Engineering, Kobe University, Kobe-shi 657-8501, Japan
3
Faculty of Science and Engineering, Saga University, Saga-shi 840-8502, Japan
*
Author to whom correspondence should be addressed.
Information 2026, 17(9), 905; https://doi.org/10.3390/info17090905
Submission received: 14 August 2026 / Revised: 12 September 2026 / Accepted: 14 September 2026 / Published: 16 September 2026
(This article belongs to the Special Issue Information Security, Data Preservation and Digital Forensics)

Abstract

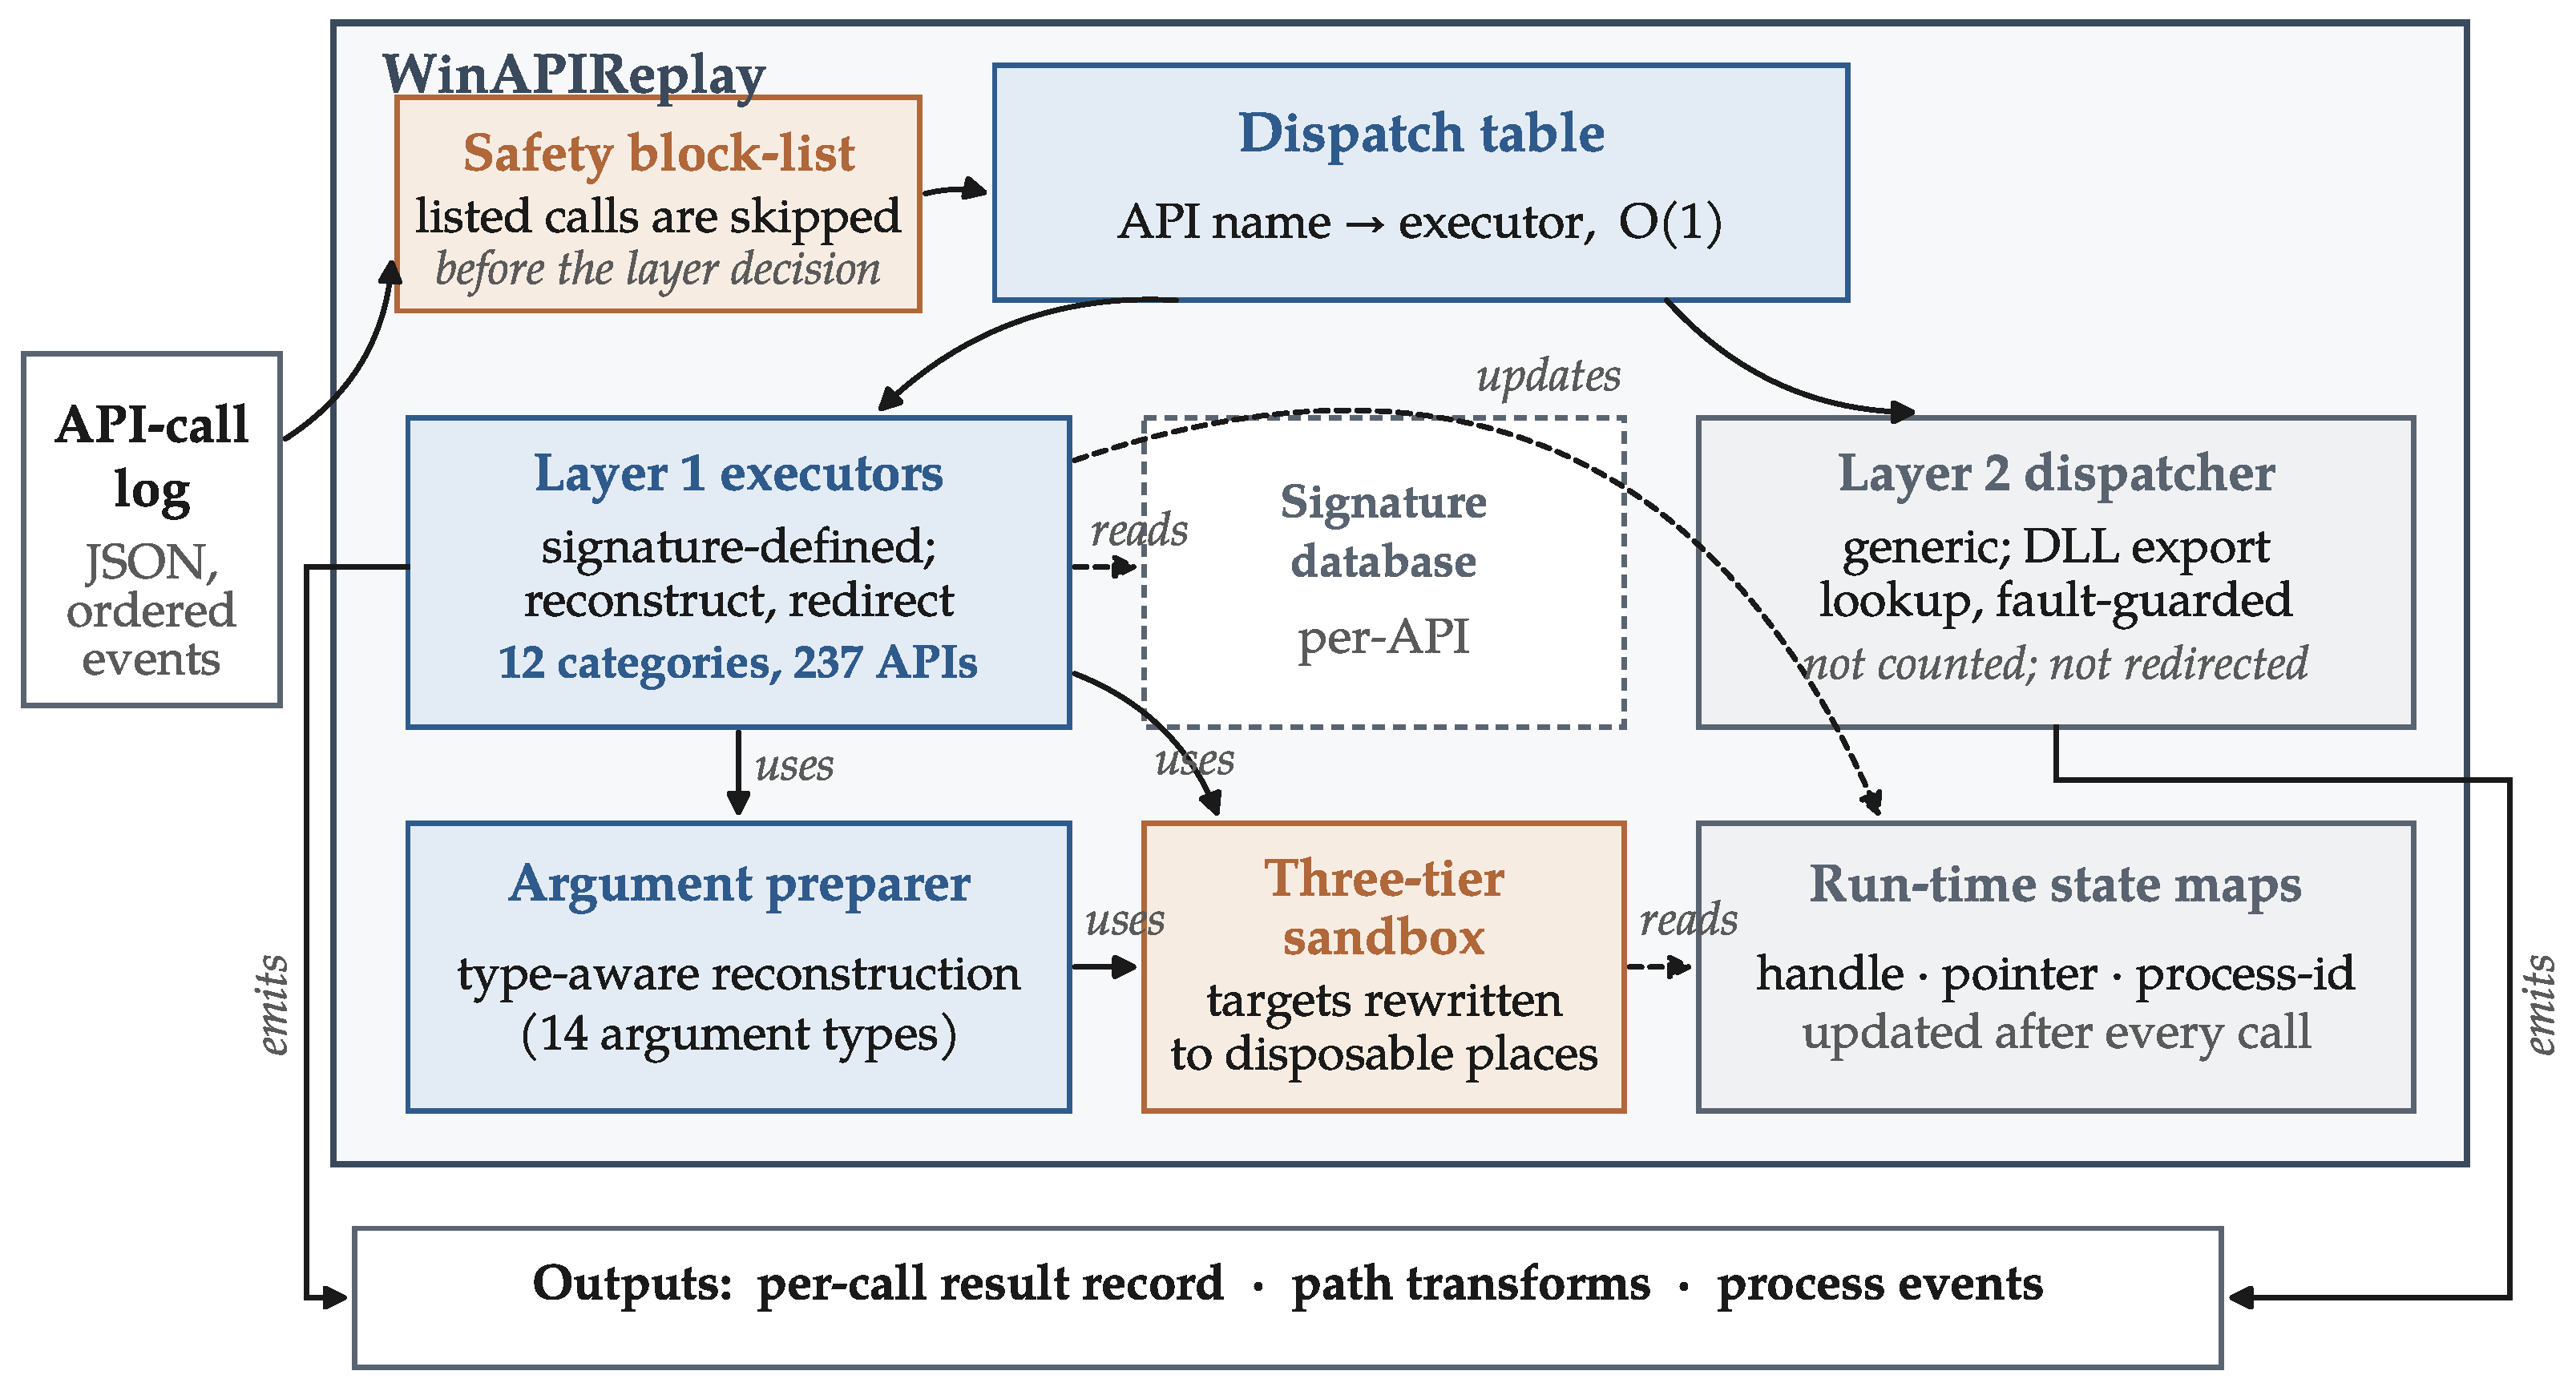
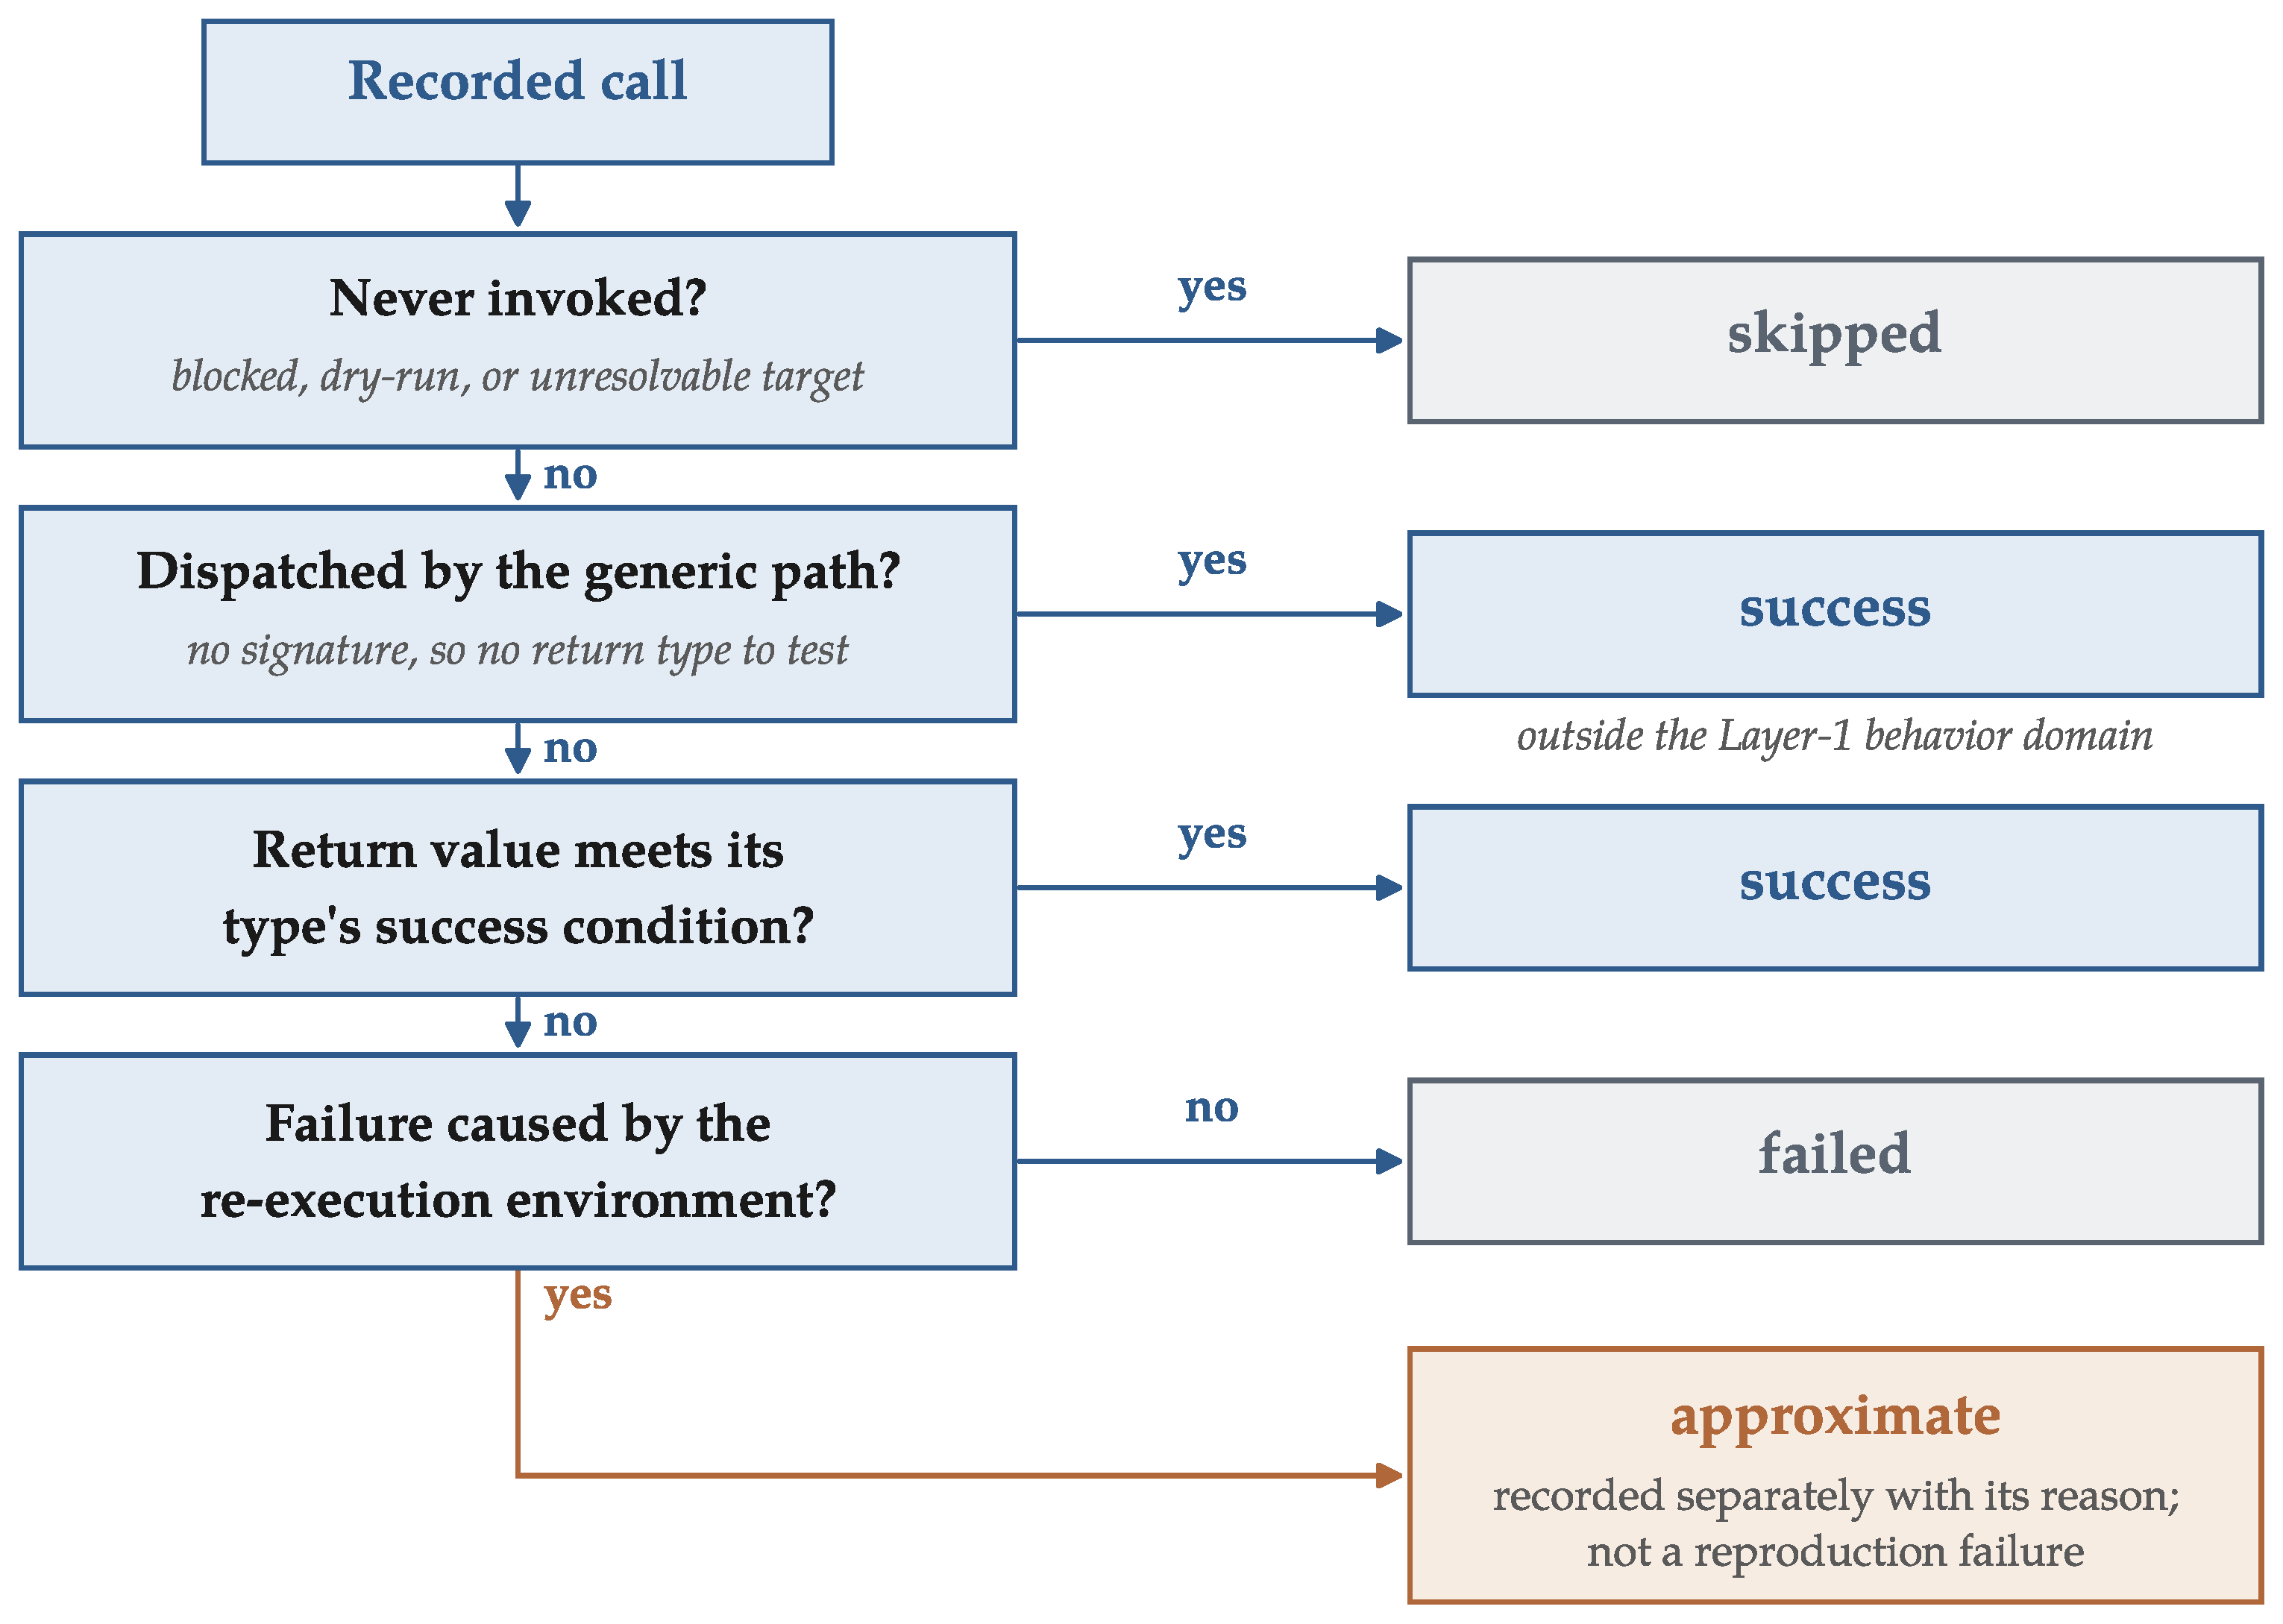
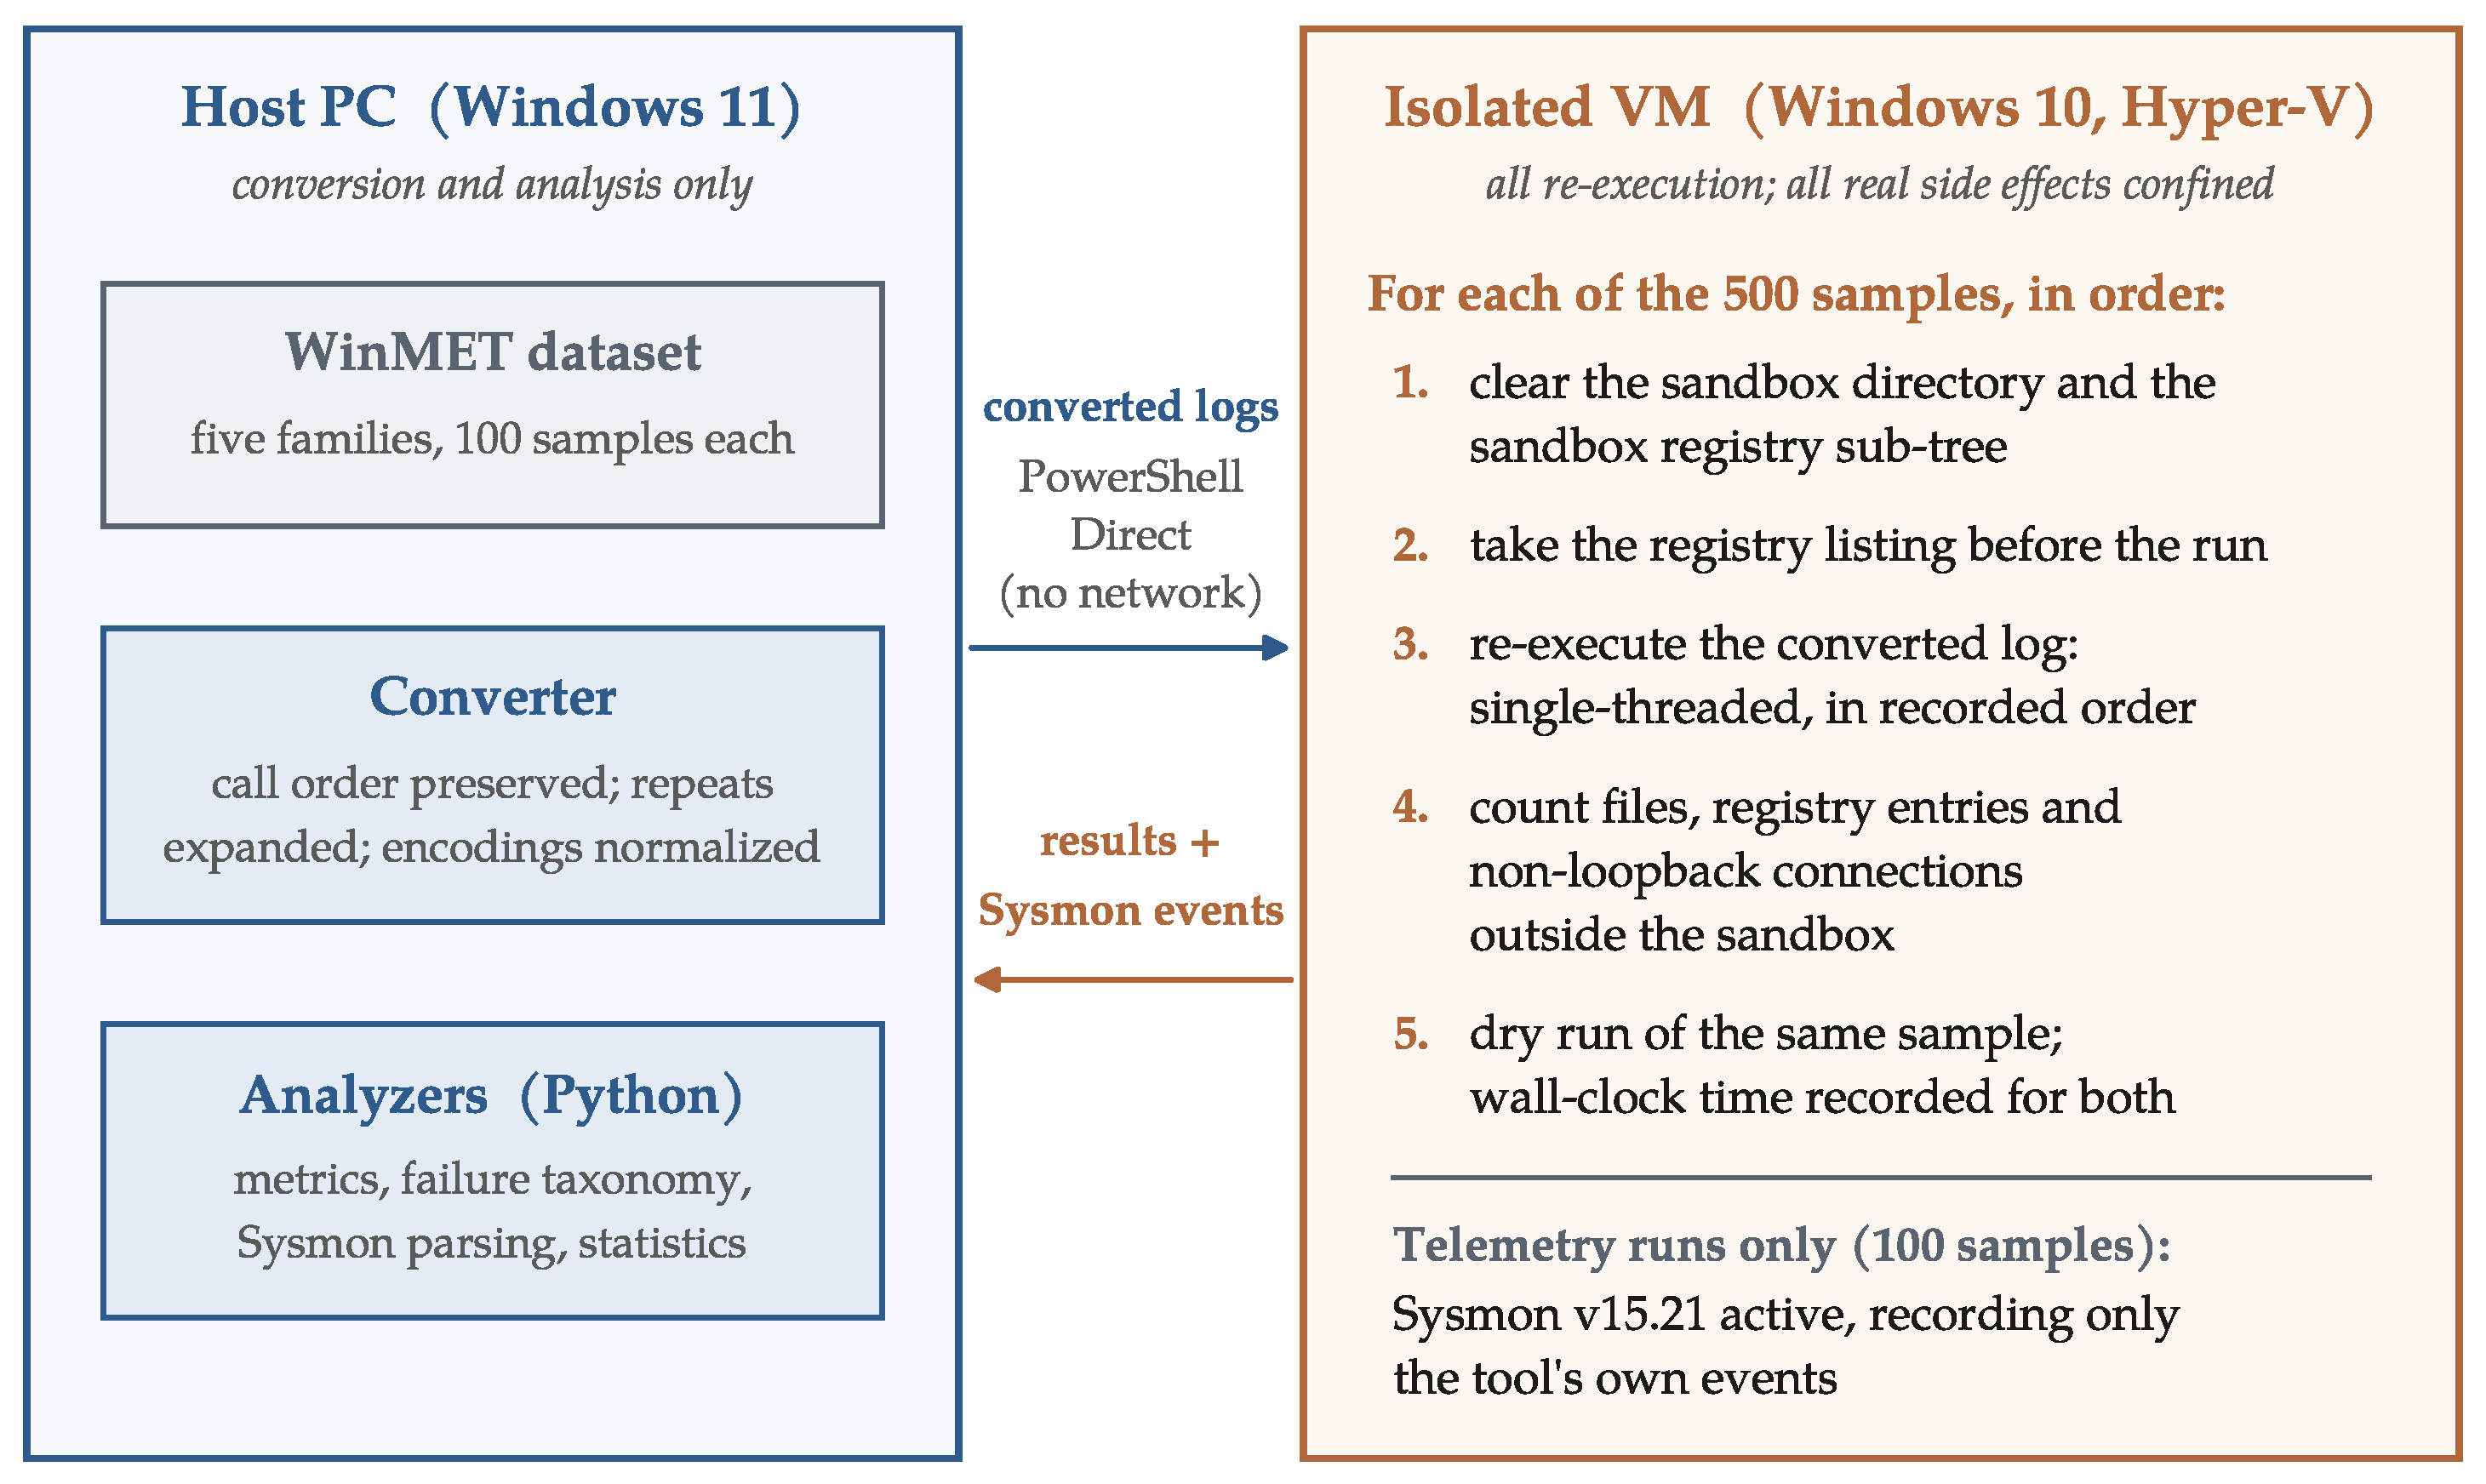
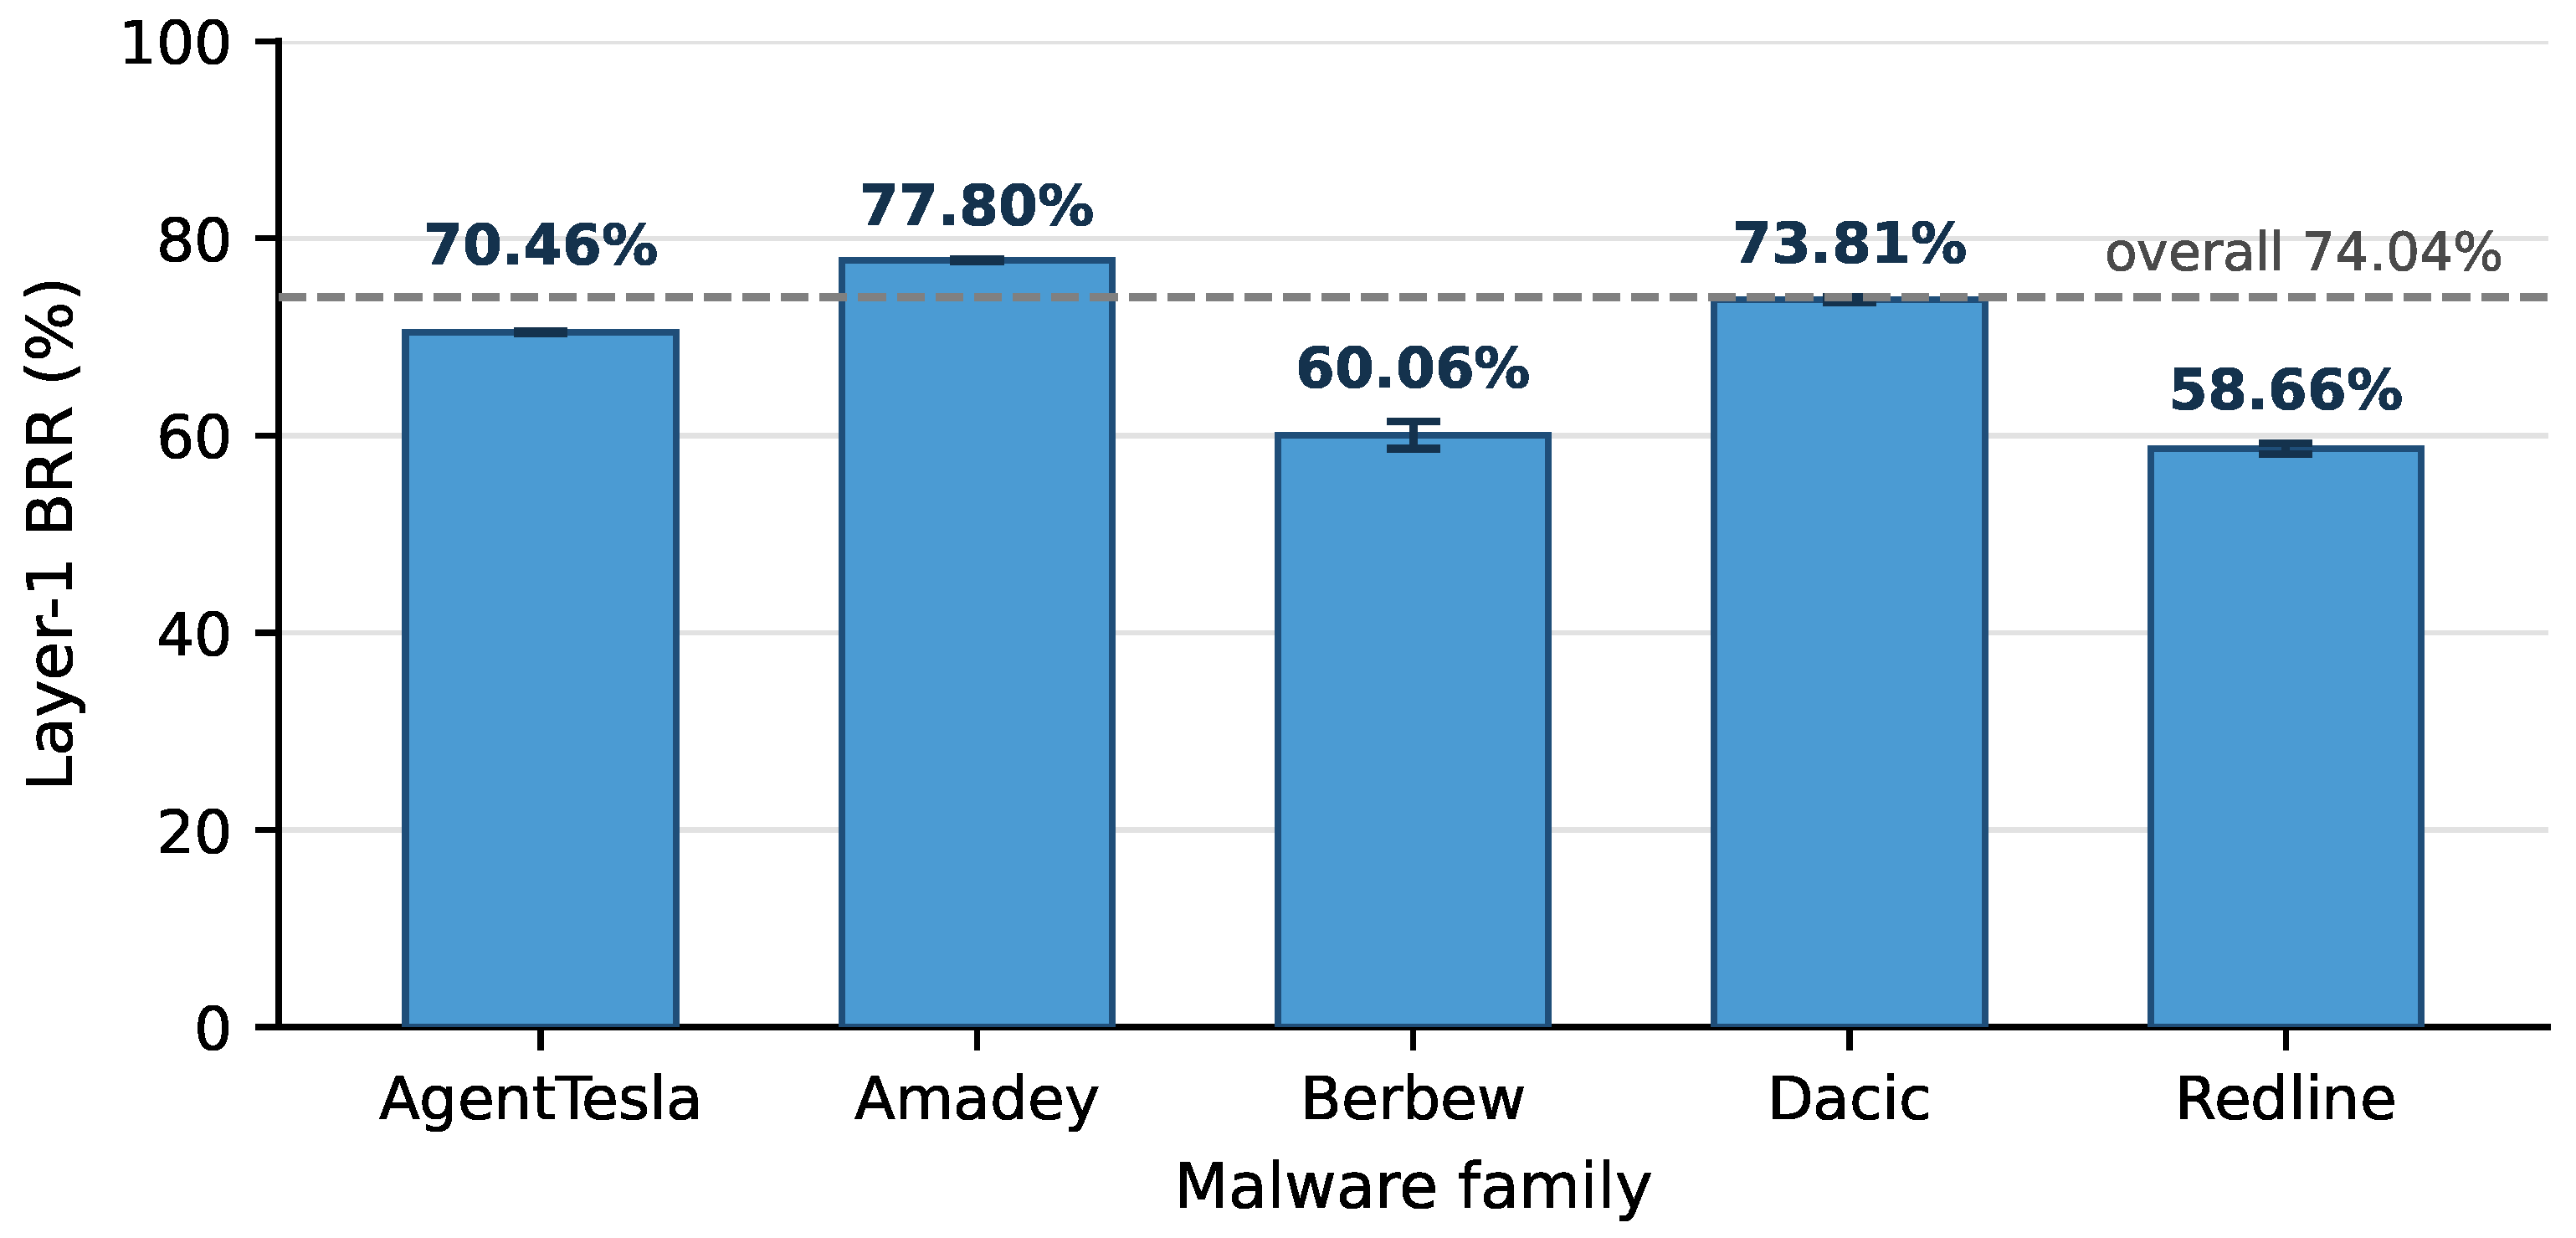
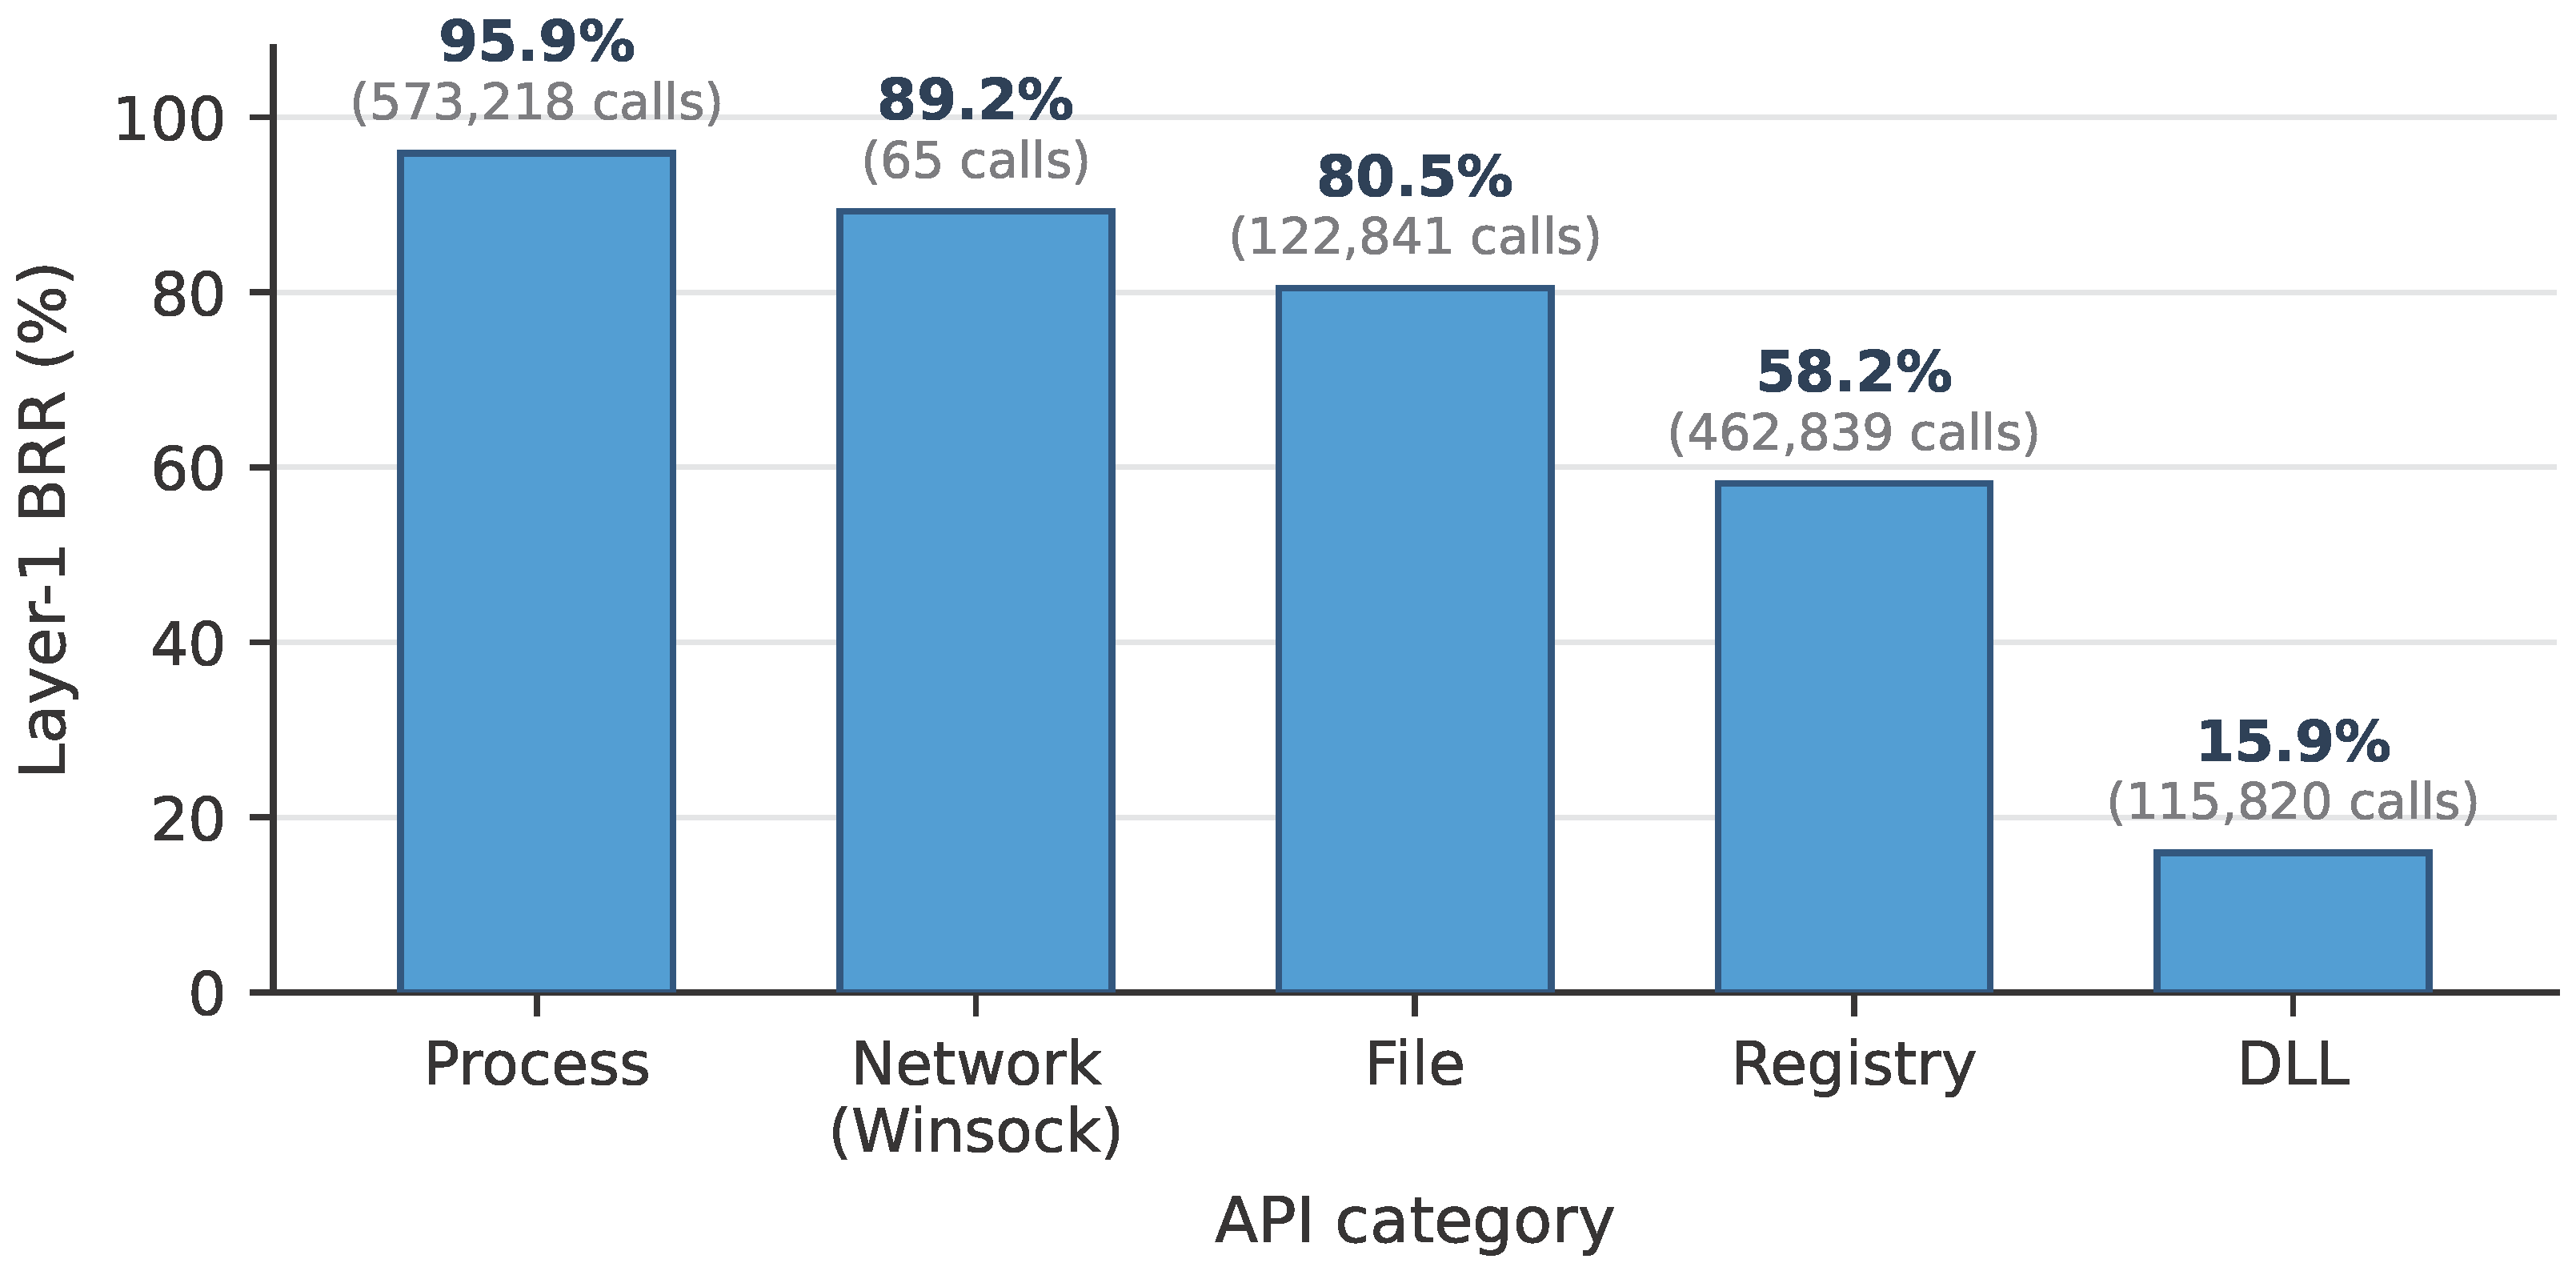
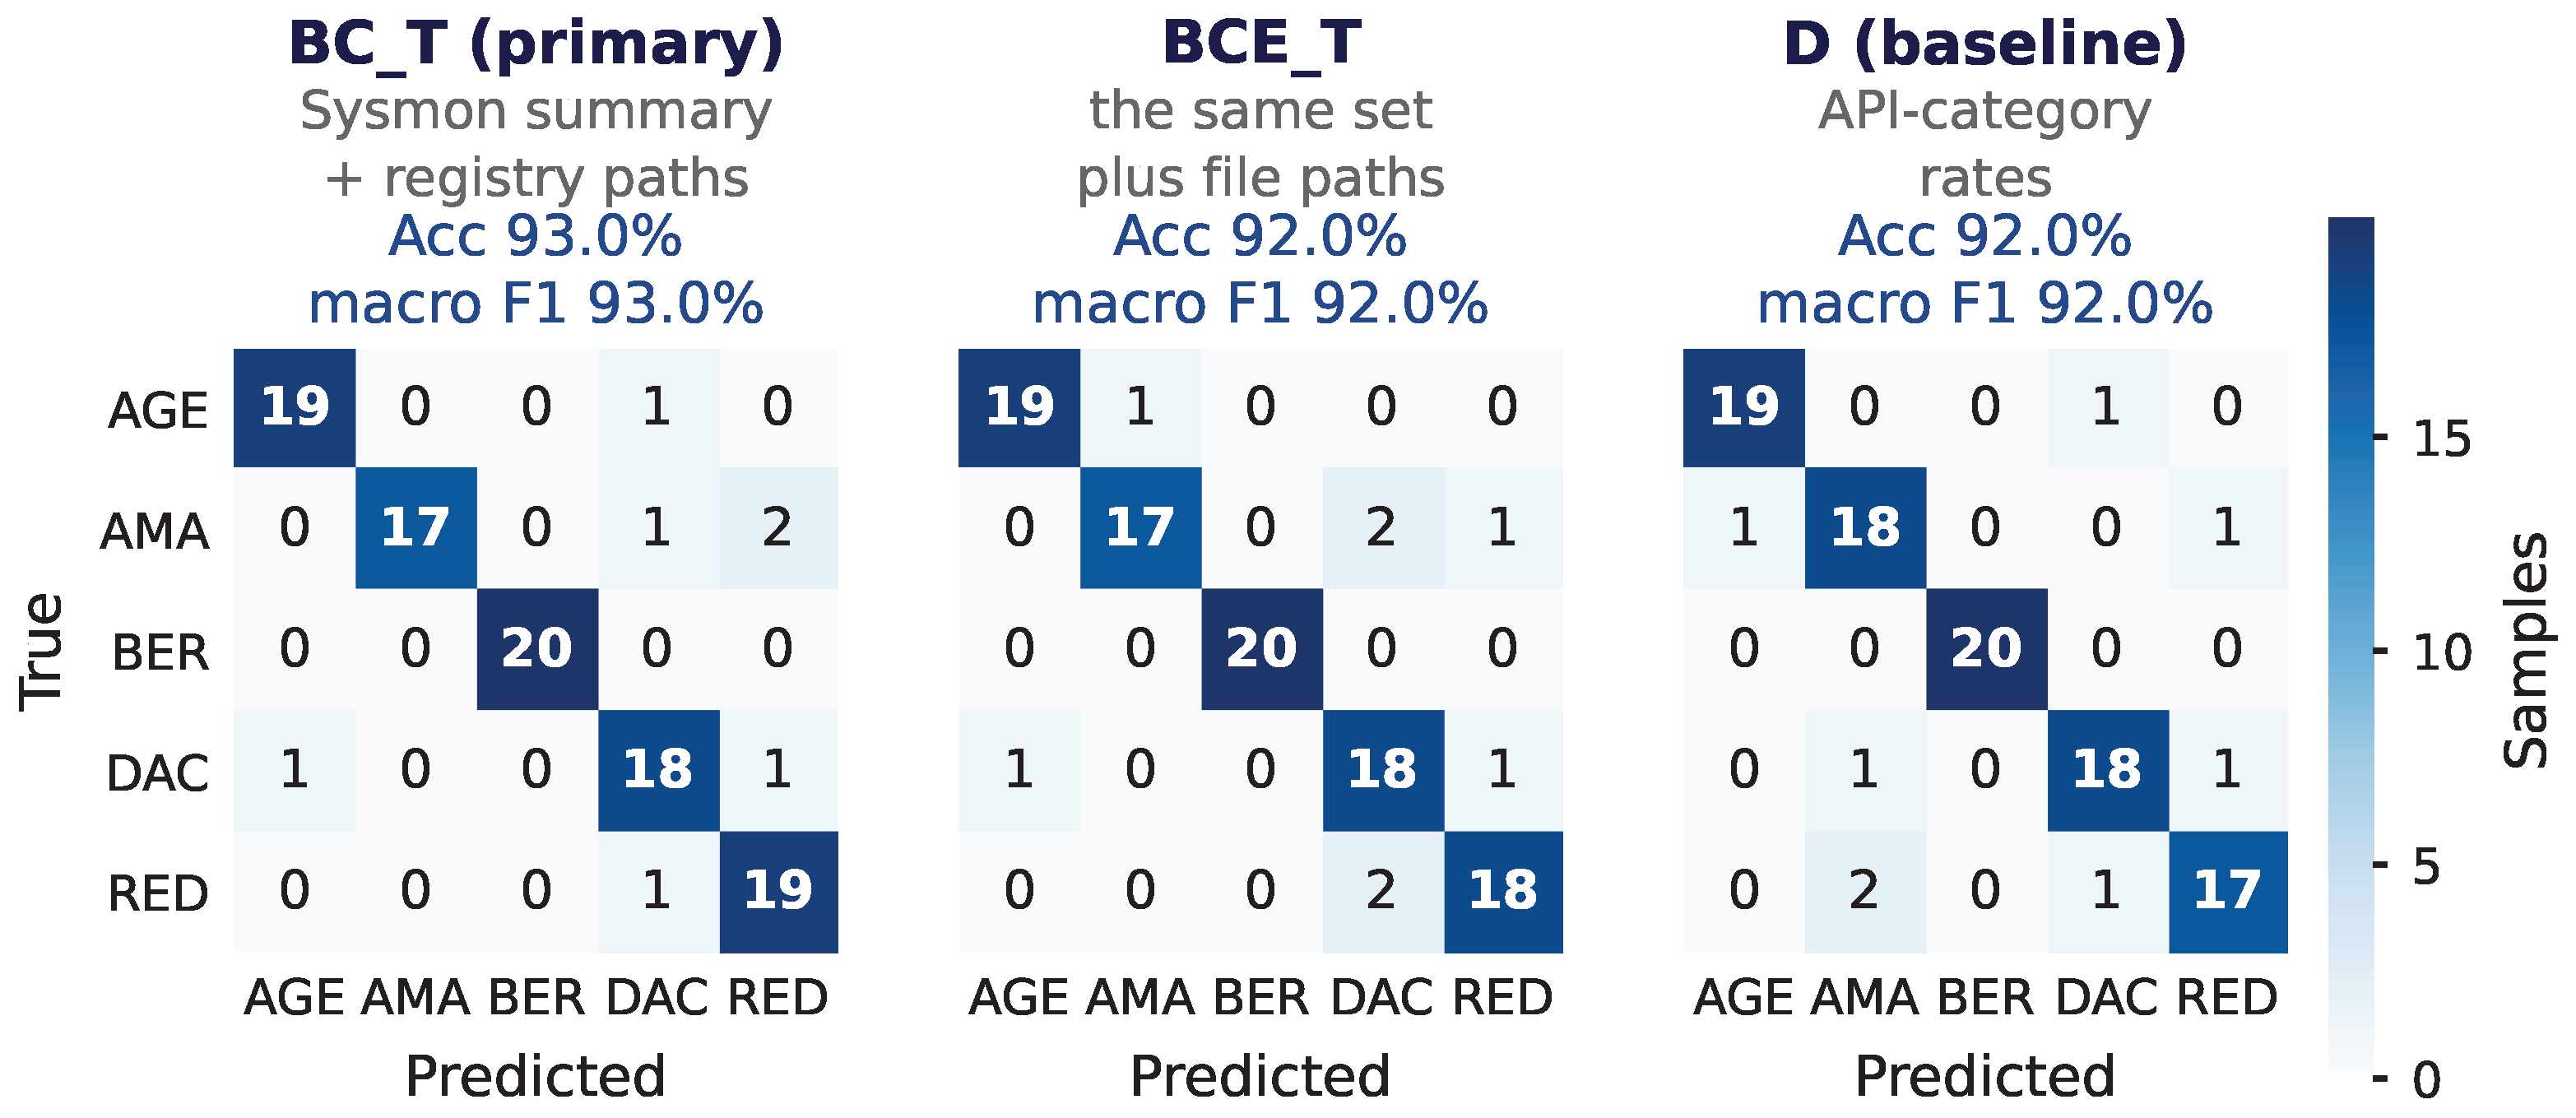
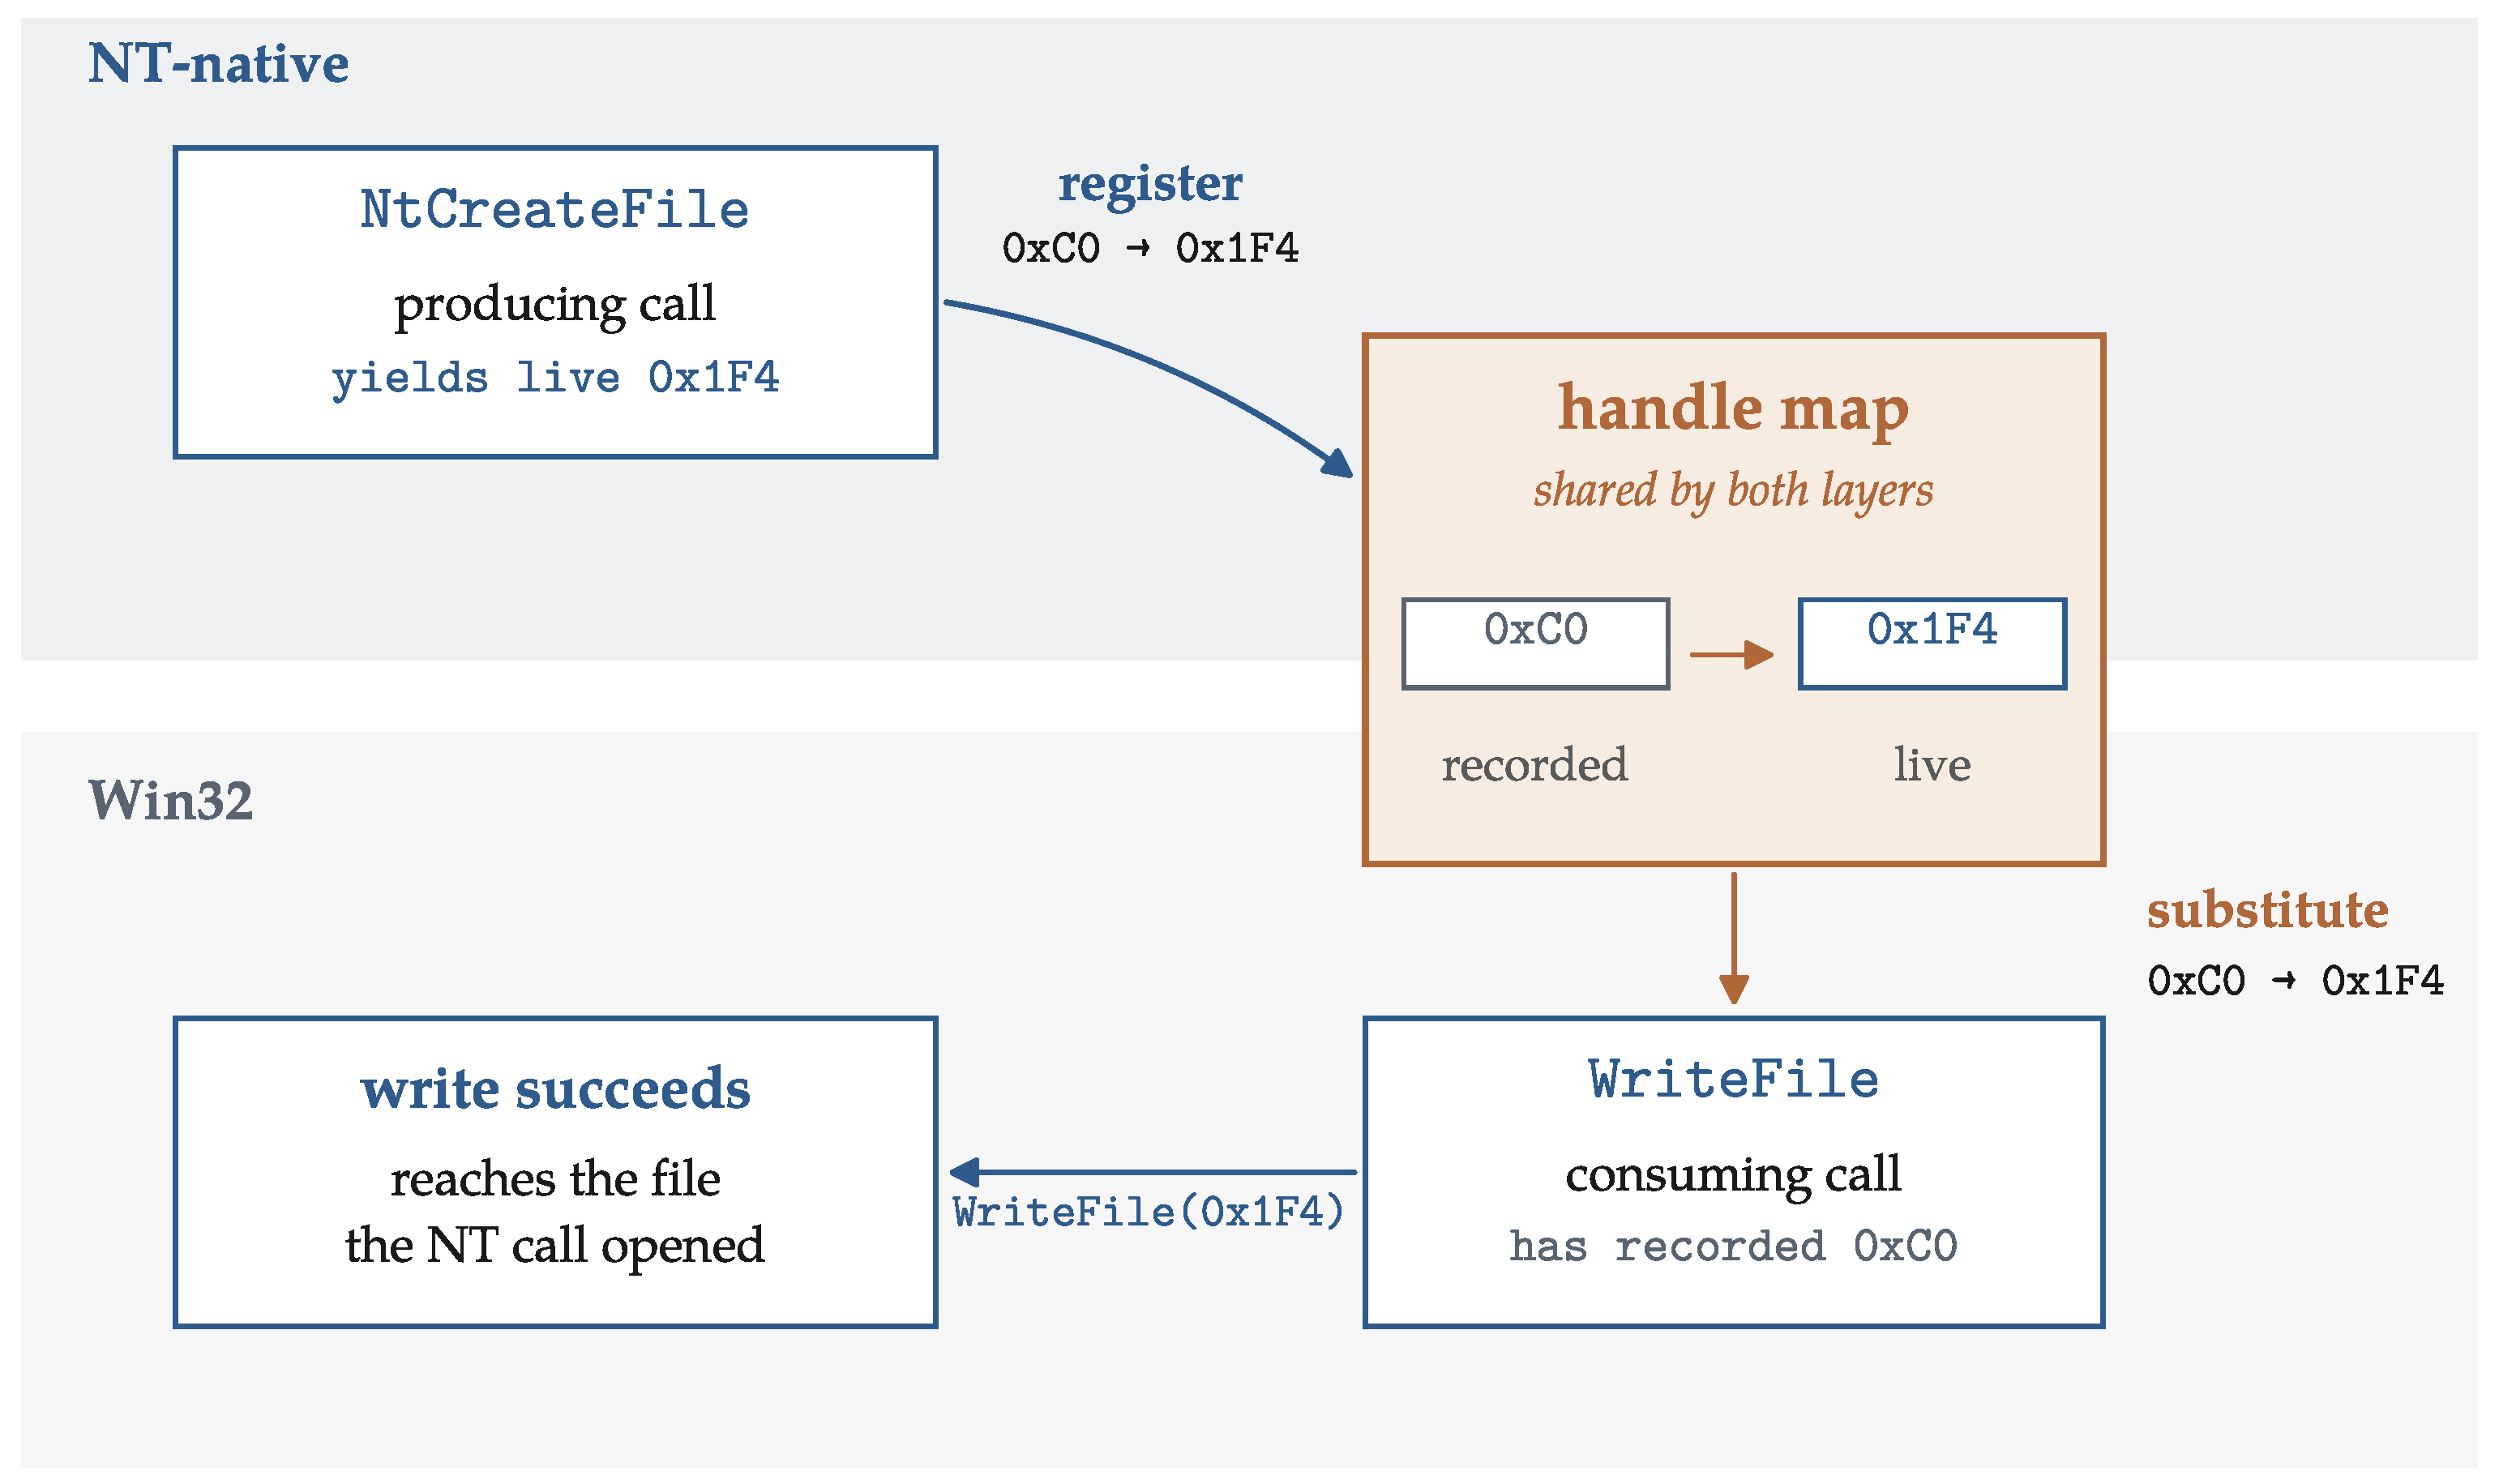
Behavioral malware analysis relies on dynamic-analysis logs—sequences of Windows API calls recorded by sandboxes such as CAPEv2—assumed to represent the malware’s effects faithfully. To the best of our knowledge, this assumption has never been tested by re-executing the recorded calls. We propose WinAPIReplay, which re-executes each recorded Win32 and NT-native call as a real operating-system call, without the malware binary, using a unified handle map for cross-layer handle chains and a three-tier sandbox confining every side effect to disposable places. Across 500 WinMET samples from five families, 74.04% of modeled Layer-1 behavior-domain calls are reproduced (95% bootstrap CI [71.02, 76.75]); the Layer-1 domain covers 57.98% of all recorded calls, and a conservative rate excluding substituted calls is 71.15%. An ablation attributes this causally to the per-category executors—handle-validity falls from 94.9% to 10.2% without them—and no side effect escapes the sandbox on the channels the tool models and monitors. A four-way taxonomy assigns most of the residual to intrinsic, environment-dependent behavior; re-execution is near-deterministic (98.90% stable). Under Sysmon, it safely generates family-labeled file/registry telemetry for the reproduced subset (46,150 events) from static logs alone—while its result record recovers the malware’s process arguments and network destinations—and a classifier over it reaches 92.0% leave-one-out accuracy on 100 samples, statistically indistinguishable from an API-category baseline. WinAPIReplay thus provides, to the best of our knowledge, the first quantitative measurement of dynamic-log reproducibility within a demonstrated safety envelope, and a safe route to labeled, environment-consistent endpoint telemetry.
Keywords: dynamic malware analysis; API-call log re-execution; behavioral reproducibility; NT-native and Win32 API; side-effect containment; Sysmon telemetry generation; malware family classification; WinMET dataset dynamic malware analysis; API-call log re-execution; behavioral reproducibility; NT-native and Win32 API; side-effect containment; Sysmon telemetry generation; malware family classification; WinMET dataset