


Abstract
Background: Internet of Things (IoT) deployments face complex network dependencies and persistent data limitations that constrain machine learning (ML) intrusion detection systems (IDS). Objective: To synthesise peer-reviewed machine learning IDS research for IoT, focusing on dependency-driven failure propagation and chronic data scarcity, positioned against 2024–2025 EU regulatory requirements (NIS2, the Cyber Resilience Act). Eligibility criteria: Peer-reviewed empirical studies proposing or evaluating a machine learning or deep learning IoT intrusion detection method published in English from January 2018 (limited pre-2018 exceptions for seminal works). Information sources: IEEE Xplore, SpringerLink, Elsevier ScienceDirect, Scopus, Web of Science, and Google Scholar, searched on 12 February 2025. Risk of bias: Each candidate was scored against four criteria (objectives clarity, methodological soundness, reproducibility, IoT-security relevance); studies scoring at least 3 out of 4 were retained. Screening and scoring were performed by one reviewer, with a second reviewer independently checking 20 percent of records. Synthesis methods: Narrative thematic synthesis; heterogeneous metrics and incompatible datasets across studies precluded quantitative meta-analysis. Included studies: Of 427 records identified, 52 studies initially met inclusion criteria; a post hoc independently validated reconstruction of individual QA1–QA4 scores subsequently found that six did not meet the threshold or topical eligibility criteria, yielding a final 46-study corpus. Main findings: Generative adversarial networks (GANs) dominate dataset augmentation work, graph-based communication analysis addresses dependency modelling, and methods based on transformers or federated learning emerge from 2023 onward. Certainty of evidence: No formal grading (GRADE) applies to this narrative synthesis. Confidence in the corpus composition is high, following independent QA1–QA4 validation, while confidence in the thematic findings is moderate given single-reviewer screening and judgment-based classification. Conclusions: We identify three recurring gaps: real-time detection under resource constraints, dependency-aware detection, and regulatory compliance. Closing these gaps requires detection methods that treat IoT security as a networked and regulated system rather than an isolated device classification problem. Registration: Open Science Framework, 10.17605/OSF.IO/NMAK4 (registered retrospectively). No external funding supported this review.
1. Introduction
The Internet of Things (IoT) has brought a transformation into the contemporary digital landscape that interconnects the physical and digital spaces across various domains such as healthcare, transportation, smart cities, and more. This integration has facilitated exceptional levels of connectivity, efficiency, and automation; nevertheless, the rapid proliferation of IoT devices and their integration into critical network infrastructures have led to an enormous increase in threat surfaces and introduction of novel security vulnerabilities, making IoT networks a focal point for cyber threats [1]. Characterised by their heterogeneity, IoT networks include a wide range of devices ranging from simple sensors to complex actuators, connected via a diverse set of protocols and network topologies. The large-scale deployment of highly varied devices complicates the process of securing IoT environments. With the ongoing technological advancements, conventional security mechanisms fail to address unique requirements and constraints of advanced IoT structures such as limited computational resources, energy optimisation, and interoperability among a vast array of heterogeneous devices [2]. Furthermore, the dynamic nature of IoT networks, where network devices frequently join and leave, further complicates security challenges. This uncertainty requires adaptive and scalable security solutions capable of real-time response to evolving threats. The complex dependencies in IoT networks also present significant challenges to data integrity and privacy, as the interconnection of devices results in numerous threat surfaces that could be easily exploited by adversaries [3]. In this study, the expression ‘complex network dependencies’ refers to more than mere device interconnections; it denotes the complex web of technical, functional, and often hierarchical reliance that is found in modern IoT environments. When any one element, be it a hardware module, a software process, or a communications protocol, falters or falls under malicious control, repercussions may swiftly propagate through the entire system, sometimes in subtle or unexpected ways. These dependencies are the hidden wires that tie together the outcomes of otherwise unrelated components, making the security posture of each device, no matter how modest, a matter of collective consequence. The absence of complete and comprehensive datasets is yet another crucial challenge for IoT intrusion detection. Existing datasets are mostly outdated or inaccurate, and are incompatible with the diverse and complex nature of modern IoT infrastructures; hence, they are not suitable for developing an efficient IDS [4].
Generative adversarial networks [5] seem to offer a very good approach, providing synthetic data that can augment the availability of small datasets. In this way, they can promote greater robustness and effectiveness of IDS for IoT networks. Graph convolutional networks (GCNs) [6] have emerged as an appealing solution for modelling inter-device interactions in IoT networks, and can be the right tool for mitigating the complexity of network dependencies in such networks. GCNs succeed in capturing the spatial and temporal dependencies that exist between nodes or devices in the IoT network by representing them as graph structures. In this way, GCNs can provide the high-level semantics of network behaviour, which is essential for efficient intrusion detection.
A substantial and fast-growing body of systematic reviews already covers machine learning intrusion detection for IoT, and any claim of novelty must be read against this corpus. A structured positioning against fourteen comparator reviews, detailed in Section 7.2, positions this review against fourteen PRISMA-style or PRISMA-guided reviews published between February 2025 and July 2026. These fourteen reviews were identified through a preliminary scoping search conducted after this review’s own formal search (executed 12 February 2025). That scoping search and its relationship to the formal 46-study corpus synthesised in this review is explained fully in Section 3.6. None of the fourteen reviews below are included in or counted toward this review’s own corpus. Several of these reviews are close in scope; Tian et al. [7] searched two of the same six databases used here (Scopus and Web of Science), and unlike this review, performed quantitative meta-regression and funnel plot analysis on 51 included studies, a synthesis that this review explicitly treats as infeasible given its differing benchmarks (Section 3.8). Ogunseyi et al. [8] covered a larger corpus (129 studies) but organised their synthesis around explainability trade-offs and a general AI-IDS taxonomy, not around network dependency propagation or compliance with regulatory architectures. Hamdi et al. [9] reviewed deep-learning-driven IDS specifically for software-defined wireless sensor networks (2020–2024), organised around a taxonomy of DL model families and network-management themes; this scope is narrower than, and does not overlap with, the IoT-wide network-dependency and regulatory framing adopted here. Alauthman et al. [10] and Mallidi and Ramisetty [11] reviewed the same two technical threads that this paper treats as underexamined, namely, GAN-based data augmentation and feature selection or data balancing strategies. This narrows the claim of novelty we make here, though without eliminating it: this review’s distinguishing contribution is not GAN methods or data balancing in isolation but their explicit synthesis against network dependency propagation and the 2024–2025 EU regulatory architecture (NIS2, the Cyber Resilience Act, and ETSI/NIST baselines; Section 7.2.6). This is a combination that none of the fourteen comparator reviews addresses. Readers evaluating the contribution of this review should treat the positioning analysis in Section 7.2 as the basis for that judgment.
2. Background
2.1. Evolution of IoT Networks
IoT networks have evolved from simple device interconnections into complex systems integrating sensors, actuators, and software under minimal human intervention [1]. The concept traces to pervasive or “ubiquitous computing” in the late 1980s and early 1990s [12]; the term “Internet of Things” itself was coined by Kevin Ashton in 1999 while at Procter & Gamble, in a presentation on using RFID to track supply chain products, which led to his co-founding of the MIT Auto-ID Center [13]. Growth accelerated with cheaper broadband and sensor hardware, extending IoT into smart homes, remote healthcare monitoring, and Industrial IoT (IIoT) applications such as smart manufacturing and precision agriculture [2]. Continued integration with 5G and beyond is expected to further reduce latency and increase device density [2].
2.2. Security Vulnerabilities Introduced by IoT
The features that make IoT devices convenient also expose them to security threats [14]. Five vulnerability classes recur across the literature and motivate the focus on intrusion detection in this review.
2.2.1. Increase in Attack Surfaces
Each connected device is a potential entry point: devices designed to provide security, such as smart locks and security cameras, can themselves become backdoors into the home or corporate network [14,15].
2.2.2. Challenges Posed by Device Heterogeneity
IoT devices range from severely resource-constrained to computationally capable, which limits the security measures that weaker devices can support. Widely differing vendor-specific operating systems and protocols further complicate the deployment of standardised security solutions across a device population [2,14].
2.2.3. Adversarial Attacks on IoT Networks
Adversarial examples are inputs crafted to appear normal to network defences while causing an IDS machine learning model to fail or misclassify. In this way, they exploit the sensitivity of many ML algorithms to small input perturbations. IoT device and firmware diversity compounds this risk by expanding the attack surface that an adversary can target [5,14].
2.2.4. Impact of Device Integration
Integrating IoT devices with incompatible security protocols creates access pointsthat an attacker can exploit; a single weakly secured device such as a smart thermostat can expose sensitive data continuously collected and transmitted by the broader network [15,16].
2.2.5. Lifecycle and Support Issues
Unlike traditional IT infrastructure, IoT devices rarely receive regular security updates, leaving them exposed to previously unknown exploits for extended periods [14,17].
3. Methodology
This section outlines the methodology used to conduct a systematic literature review (SLR) on machine learning-based intrusion detection systems in Internet of Things (IoT) environments. The SLR adheres to the PRISMA 2020 (Preferred Reporting Items for Systematic Reviews and Meta-Analyses) guidelines [18] in order to provide a structured, transparent, and replicable approach to evidence synthesis.
3.1. Step 1: Data Source Selection and Search Process
A comprehensive literature search was conducted across six leading academic databases and search engines:
- IEEE Xplore (https://ieeexplore.ieee.org)
- SpringerLink (https://link.springer.com)
- Elsevier/ScienceDirect (https://www.sciencedirect.com)
- Scopus (https://www.scopus.com)
- Web of Science (https://www.webofscience.com)
- Google Scholar (https://scholar.google.com)
These platforms were chosen due to their extensive coverage of peer-reviewed journal articles, conference proceedings, and technical reports relevant to IoT and cybersecurity. Boolean operators and keyword combinations were applied to optimise the relevance and coverage of search results.
We derived the keyword set through a pilot scoping search consistent with established systematic review guidelines (Kitchenham and Charters, 2007) [19]. Thirty highly cited IoT-IDS papers from 2020 to 2023 supplied the recurring terminology used across titles, abstracts, and author keywords. We grouped these terms into four conceptual blocks: domain (Internet of Things, IoT), problem (Intrusion Detection, Anomaly Detection), security framing (Security, Cybersecurity), and methodology (Machine Learning, Deep Learning, Artificial Intelligence). Boolean expansion within each block and conjunction across blocks produced the core query string reported above. This core string was applied with title, abstract, and author–keyword field scope in every database. Syntax was adapted to each platform’s search grammar (for example, Scopus’s TITLE-ABS-KEY() operator and IEEE Xplore’s Command Search syntax) while holding the underlying Boolean logic and field scope constant across all six databases in order to preserve comparability of the per-database counts in Table 1. Google Scholar was queried using the same core string through its standard search interface. Google Scholar does not expose field-restricted search or a stable citable query history in the way that the other five databases do, so its results are less directly reproducible. This limitation applies only to the Google Scholar portion of the search. We validated the protocol against three reference papers known a priori to be within scope, and all three were retrieved.
Table 1.
Number of papers selected at each stage.
Search query used: (“Internet of Things” OR “IoT”) AND (“Intrusion Detection” OR “Anomaly Detection”) AND (“Security” OR “Cybersecurity”) AND (“Machine Learning” OR “Deep Learning” OR “Artificial Intelligence”)
The search covered the period from January 2018 to February 2025, with seminal papers prior to 2018 included where contextually necessary. A total of 427 articles were retrieved from the initial search.
The 2018 lower bound reflects the post-Mirai consolidation of machine learning IDS literature for IoT. The 2016 Mirai botnet and the 2017–2018 wave of large-scale botnet research re-established IoT threat surfaces at network scale. Modern IDS approaches that use GANs, GCNs, and transformer architectures emerge in peer-reviewed venues from this period onward. Earlier seminal works were cited where contextually necessary, including Goodfellow et al. (2014) on GANs [5], Kipf and Welling (2016) on GCNs [6], and the original 2009 PRISMA statement [20], which this review’s PRISMA 2020 protocol supersedes [18].
3.2. Step 2: Inclusion and Exclusion Criteria
To ensure relevance and quality, articles were filtered using the following criteria:
- Inclusion Criteria:
- Studies focused on IoT-based intrusion detection or cybersecurity.
- Use of machine learning, deep learning, or hybrid approaches.
- Research providing empirical evidence and performance metrics.
- Published in peer-reviewed journals or reputable conferences.
- Exclusion Criteria:
- Non-peer-reviewed literature (e.g., blogs, theses, white papers)
- Studies not directly related to IoT or lacking a security component
- Redundant publications
- Non-English publications
3.3. Step 3: Study Selection Process
The selection process followed a four-stage filtering strategy:
- Identification: 427 records were retrieved from the search. After removing 117 duplicates, 310 articles remained
- Title Screening: The remaining articles were evaluated based on their titles, reducing the count to 150
- Abstract Screening: Abstracts were reviewed for alignment with research objectives, narrowing the list to 110
- Full-Text Review: Comprehensive reading led to the selection of 52 high-quality articles for inclusion
3.4. Step 4: Study Quality Assessment, Data Extraction, and Synthesis
To assess methodological rigor and relevance, a quality evaluation was conducted using the following four criteria:
- QA1: Clarity of objectives and research scope
- QA2: Soundness of methodology
- QA3: Reproducibility and transparency
- QA4: Relevance and impact on IoT security
Studies scoring at least 3 out of 4 were retained. From the 110 full-text reviewed articles, 52 met both the quality threshold and the eligibility criteria for inclusion in the final synthesis. This rigorous methodology ensures that the SLR is both comprehensive and reliable, providing a solid foundation for evaluating the current state and future direction of machine learning-based intrusion detection in IoT networks.
3.5. PRISMA 2020 Compliance Statement
This systematic literature review was designed, conducted, and reported in accordance with the Preferred Reporting Items for Systematic Reviews and Meta-Analyses (PRISMA) 2020 statement [18]. Each of the 27 PRISMA 2020 reporting items has been addressed in this manuscript or has its non-applicability documented with explicit rationale below. The complete item-by-item mapping is provided as Supplementary Material Table S1. The PRISMA 2020 flow diagram (Figure 1) records the full study selection process. The complete database-by-database search syntax executed on 12 February 2025 is provided as Supplementary Material File S2.
Figure 1.
PRISMA 2020 flow diagram generated using the official PRISMA2020 web application [21], showing 427 records identified reducing to a final 46 included studies after duplicate removal, screening (reported by stage in Table 1), full-text eligibility assessment, and the post hoc QA1–QA4 reconstruction detailed in Section 3.6.
The decision to apply PRISMA 2020 to a computer science systematic review reflects three considerations: first, as PRISMA 2020 is the most widely accepted reporting standard for systematic reviews across disciplines, its adoption signals methodological rigour to readers and editors; second, the structure imposed by PRISMA 2020 strengthens transparency in study selection and synthesis decisions, which is particularly important when reviewing a heterogeneous methods literature without standardised benchmarks; third, although PRISMA 2020 was developed primarily for healthcare intervention reviews, the PRISMA 2020 statement explicitly supports its use in reviews of other types of research, including methodological, technical, and engineering domains.
3.6. Protocol Registration and Amendments
Registration: The review protocol was registered on the Open Science Framework (OSF) Registries [10.17605/OSF.IO/NMAK4]. The registration was completed before submission of the revised manuscript to the journal. The OSF was selected because PROSPERO is restricted to systematic reviews with health-related outcomes, and INPLASY is paid-access. OSF Registries is open-access, accepts retrospective registration, and is recognised by the PRISMA 2020 statement as a valid registration platform for systematic reviews. The OSF registration record contains the review title, research questions, eligibility criteria, information sources, search strategy, study selection process, data extraction items, risk-of-bias method, and synthesis approach as described in Section 3. The registration record is available at the OSF project URL recorded in the corresponding-author submission file. We acknowledge that retrospective registration does not provide the bias reduction benefits of prospective registration. We disclose the timing transparently in the interest of complete reporting. The specific mechanism available to readers wishing to check for undisclosed post hoc changes is as follows: once created, an OSF registration is timestamped and version-locked, meaning that its content cannot be silently edited after the fact; any subsequent change is itself logged with its own timestamp, and the originally registered version remains permanently accessible at the same record. This allows a reader, editor, or future reviewer to independently compare the eligibility criteria, synthesis categories, and data extraction items recorded in the OSF registration against those reported in Section 3.2, Section 3.8 and Section 3.9 of this manuscript rather than relying solely on the authors’ own assertion that no changes were made. This mechanism protects specifically against undisclosed changes between the registration date and the manuscript’s submission to the journal. It does not and cannot protect against changes made between the search execution date (12 February 2025) and the registration date itself, since registration was retrospective and some interval necessarily separates the two; this remains a genuine limitation of the review’s design that the registration record does not resolve, and readers should weigh the review’s conclusions accordingly.
Protocol availability: No formal protocol document was prepared in advance of the review. The methodology described in Section 3.1, Section 3.2, Section 3.3 and Section 3.4 constitutes the operational protocol applied throughout the review. We acknowledge that prospective preparation of a separate protocol document registered before the search execution date of 12 February 2025 would have strengthened transparency. The operational steps reported in this section were applied consistently across all 427 retrieved records and 110 full-text candidates.
Amendments to the registered protocol: No amendments were made to the operational protocol between the search execution date (12 February 2025) and the manuscript’s first submission, and none were made to the formal inclusion criteria, eligibility criteria, or synthesis categories at any point after search execution. A preliminary scoping exercise distinct from the registered protocol was subsequently conducted to gauge how much the literature had moved between the search date and submission. This used an aggregator-based search covering 13 February 2025 to 13 July 2026 (Semantic Scholar, Scopus, PubMed, and arXiv; preprints excluded), applying the same conceptual search blocks as the original protocol. This scoping exercise is reported for transparency but is not treated as part of the formal review corpus, which is for two reasons. First, as it used a single aggregator tool rather than the six native database interfaces specified in the registered protocol, we cannot claim methodological equivalence with Section 3.1, Section 3.2, Section 3.3 and Section 3.4. Second, of the 33 primary-study candidates it surfaced, only one was carried through full-text QA1–QA4 assessment before submission; the remaining 32 received only abstract-level screening. Incorporating a single non-randomly-selected study into the formal corpus on that basis would risk selection bias without a defensible justification for why that study was prioritised over the other 32; accordingly, none of the candidates identified by this scoping exercise are included in the review’s formal corpus, tables, or synthesis. The exercise and its 33 candidates are instead reported as a direction for future work in Section 8, which recommends a complete and properly resourced update following the full registered protocol as a next step. The data extraction template used for the 52-study corpus was finalised before full-text screening began, and was not altered by this scoping exercise. The synthesis structure (method family grouping, dependency comparison table, and method frequency timeline) was determined during data extraction in response to the variety observed in the candidate corpus, and is not considered a methodological amendment because it concerns presentation rather than inclusion criteria.
Post hoc QA1–QA4 reconstruction: Individual QA1–QA4 scores for the studies retained at original screening were not tabulated at the time (Section 3.10; item 18 originally reported only the aggregate finding that all 52 scored at least 3 of 4). To provide the level of transparency that systematic review reporting standards require for quality assessment claims, a full reconstruction of individual QA1–QA4 scores was subsequently conducted from publicly accessible full texts and publisher records for all 52 studies using the instrument defined in Section 3.7. This reconstruction was independently validated by a second reviewer before being acted upon. The reconstruction did not support the original aggregate claim: 6 of the 52 studies (Yang 2019 [22], Mir 2023 [23], Kaur 2019 [24], Yosuf 2020 [25], Ouafiq 2022 [26], Aly 2018 [27]) scored 2.5 of 4, below the stated inclusion threshold. In several of these cases, the shortfall reflected a topical eligibility failure rather than a marginal quality issue; for example, one study’s empirical focus was health IoT clinical decision support rather than intrusion detection, and would not have met the Section 3.2 inclusion criteria on that basis alone independent of its QA score. These six studies were removed from the formal corpus. The remaining 46 studies (38 method papers, reported in full later in this manuscript, plus eight foundational, methodological, and survey references) constitute the corpus reported throughout this manuscript. This correction is disclosed in the interest of transparent reporting. The reconstructed per-study QA1–QA4 scores, together with the scoring rubric, validation record, and data dictionary, have been finalised, independently validated, and publicly deposited on Zenodo (doi.org/10.5281/zenodo.22143353), with explicit labelling as a post hoc reconstruction rather than the original contemporaneous screening scores.
3.7. Risk of Bias Assessment Method
Tool description: Standard risk-of-bias instruments such as ROBIS, QUADAS-2, and the Cochrane Risk of Bias tool are designed for systematic reviews of clinical interventions or diagnostic test accuracy studies. None of the included studies in this review fall into either category. Therefore, we applied a custom quality assessment instrument with four criteria specifically tailored to machine learning IDS research: clarity of objectives and research scope (QA1), soundness of methodology (QA2), reproducibility and transparency (QA3), and relevance and impact on IoT security (QA4). Each criterion was scored 0 (not addressed), 0.5 (partially addressed), or 1 (fully addressed). The maximum score per study was 4. Studies scoring at least 3 out of 4 were retained. The QA criteria were derived from established machine learning systematic review quality assessment practice and the JBI critical appraisal tools for non-clinical research, adapted for the IoT-IDS domain.
Reviewer process: Title and abstract screening, full-text assessment, and quality scoring were conducted by the lead author alone. A second reviewer independently scored a random 20 percent sample of the 110 full-text candidates. Inter-rater agreement on that sample was measured by Cohen’s kappa and reached 0.78, indicating substantial agreement. Disagreements on the sampled records were resolved through discussion and reference to the QA criteria definitions. Where disagreement persisted, the conservative score was retained. Because a single reviewer performed all screening and scoring decisions for the remaining 80 percent of candidates, this design carries a materially higher risk of reviewer bias, systematic misapplication of the QA criteria, or unconscious drift in scoring standards over the course of the review compared to a design with independent dual screening throughout. This is treated as a substantive limitation of the review, and is a primary reason for reporting the QA1 to QA4 instrument’s outputs with the caveats given in the following paragraph. No automation tools were used for screening or quality scoring decisions.
Risk of bias domains assessed: QA1 evaluates whether the study’s objectives and IoT security scope are clearly stated and bounded. QA2 evaluates whether the proposed method, including dataset, model architecture, training procedure, and evaluation protocol, is described with sufficient detail to support replication. QA3 evaluates whether code, dataset, and hyperparameters are publicly available or sufficiently described to enable reproduction. QA4 evaluates whether the study addresses a recognised IoT security challenge with potential operational impact. The combined score reflects study-level risk of bias, with low scores indicating elevated risk and reduced confidence in the reported findings.
Limitations of the risk-of-bias method: Three limitations are acknowledged. First, the QA1 to QA4 instrument has not been formally validated against established tools for the IoT-IDS domain. Second, scoring relies on author judgment of the criteria, which introduces subjectivity even with the second reviewer providing a sample check. Third, the binary inclusion threshold (at least 3 of 4) does not differentiate between studies scoring 3.0 and 4.0, both of which are retained on equal footing in the synthesis.
3.8. Effect Measures, Synthesis Methods, and Certainty Assessment
Effect measures (PRISMA item 12): Effect measure reporting is not applicable to this review. The included studies report performance via accuracy, precision, recall, F1-score, area under the receiver operating characteristic curve, false positive rate, and detection latency, but they evaluate these metrics on heterogeneous and incompatible datasets including NSL-KDD, CICIDS2017, BoT-IoT, TON-IoT, UNSW-NB15, and proprietary testbeds. No common comparator condition is reported across studies, so quantitative effect-size pooling cannot be performed.
Synthesis methods (PRISMA items 13a–13f): Studies were eligible for synthesis if they met the inclusion criteria in Section 3.2 and scored at least 3 out of 4 on the QA1 to QA4 instrument in Section 3.7. Data preparation for synthesis involved tabulating each study by method family, application focus, dataset, and gap addressed (item 13b), reported in full later in this manuscript. Visual presentation uses three modes: a synthesis matrix of the 38 method papers, a per-domain dependency comparison, and a method-family distribution timeline covering 2014 to 2025 (item 13c). Synthesis proceeded via thematic mapping across nine method families and five IoT application domains; the rationale for thematic synthesis consists of the differing metrics, datasets, and architectures across the corpus, which precludes meta-analytic pooling (item 13d).
Heterogeneity exploration (item 13e) and sensitivity analyses (item 13f): Statistical heterogeneity exploration is not applicable because no statistical synthesis was performed. Methodological heterogeneity is described qualitatively in Section 7.2 (Limitations and Gaps). Sensitivity analyses are not applicable because no quantitative synthesis was performed.
Reporting bias assessment (item 14): Formal assessments of reporting bias such as funnel plot inspection or Egger’s test are not applicable because no quantitative synthesis was performed. Qualitatively, we note that the corpus is dominated by studies reporting positive results, which is a known characteristic of computer science publication patterns. We did not access conference rejection lists or arXiv pre-prints to estimate the magnitude of publication bias.
Certainty assessment (item 15): GRADE certainty-of-evidence assessment is not applicable to this review. GRADE is designed for evidence reviews evaluating health intervention effects with quantitative pooling. The corpus in this review comprises methodological contributions evaluated on incompatible benchmarks, for which GRADE rating categories (low, moderate, or high certainty) cannot be meaningfully assigned. We instead report study-level QA1 to QA4 scores in the supplementary risk-of-bias summary, available from the corresponding author on request.
3.9. Data Items, Data Collection, and Reporting Detail
Data items collected (PRISMA items 10a and 10b): For each included study, the following items were extracted into a structured data extraction sheet: bibliographic identifier, lead author, publication year, publication venue, IoT application domain, dataset used, machine learning method family, method variant, evaluation metrics reported, claimed contribution, and identified gap addressed. Item 10a outcomes for this review are the qualitative attributes synthesised across studies, namely, method family, application focus, and gap addressed; these are reported in full later in this manuscript. Item 10b other variables include publication year, dataset, and IoT domain; these are likewise reported later, alongside a timeline and a per-domain dependency mapping.
Data collection process (PRISMA item 9): Data extraction was performed by the lead author into a spreadsheet template piloted on five randomly selected full-text candidates before extraction of the full corpus began. The pilot identified one ambiguity in the method family classification, which was resolved by adopting the dominant method declared in each study’s title and abstract. A second reviewer independently re-extracted a random 20 percent sample of the 52 included studies. Inter-rater agreement on the structured fields reached 92 percent, with the remaining 8 percent resolved through discussion. No automation tools were used for data extraction. The complete extraction sheet is publicly deposited on Zenodo: doi.org/10.5281/zenodo.22151401.
3.10. Reporting of Results, Reporting Biases, and Certainty (PRISMA Items 16 to 22)
Study selection results (item 16a): Search and selection results are reported in Figure 1 (PRISMA 2020 flow diagram) and Table 1 (counts at each filtering stage). Of 427 records identified, 117 duplicates were removed, leaving 310 unique records. Title screening excluded 160 records, abstract screening excluded a further 40 records, and full-text assessment excluded 58 records, yielding 52 studies that met the quality threshold and eligibility criteria at the time of original screening. A subsequent post hoc QA1–QA4 reconstruction, independently validated by a second reviewer (Section 3.6), found that 6 of these 52 studies did not in fact meet the 3-of-4 quality threshold, and in some cases did not meet the Section 3.2 topical eligibility criteria at all. These six studies (Yang 2019 [22], Mir 2023 [23], Kaur 2019 [24], Yosuf 2020 [25], Ouafiq 2022 [26], Aly 2018 [27]) were removed from the formal corpus. The final corpus comprises 46 included studies. A preliminary scoping exercise conducted after the search date, described in Section 3.6, identified further candidate studies through July 2026; these are not included in the formal corpus and are instead reported as future work directions in Section 8. Excluded full-text reports (item 16b) were excluded for three documented reasons: failed quality threshold (QA score below 3 out of 4); out of scope (no IoT focus or no security focus); and insufficient methodological detail to permit assessment.
Study characteristics (item 17): Study characteristics for the 38 method papers in the corpus are reported in full later in this manuscript. These are empirical studies proposing or evaluating a machine learning or deep learning intrusion detection method and meeting all four inclusion criteria in Section 3.2. The remaining eight studies included foundational, methodological, or survey references. These met the same peer review and date range eligibility criteria, but do not propose or empirically evaluate a novel detection method, and are not counted among the 38 method papers or synthesised there. Instead, they scope the technical and regulatory context of the corpus, and are cited in their thematic context across Section 4, Section 5, Section 6, Section 7 and Section 8 (specifically: the PRISMA 2020 statement [18], Goodfellow et al. 2014 on GANs [5], and Kipf and Welling 2016 on GCNs [6], plus five confirmed survey references: Siwakoti et al. 2023 [14], Tawalbeh et al. 2020 [28], Khraisat and Alazab 2021 [29], Alwahedi et al. 2024 [30], and HaddadPajouh et al. 2021 [31]). Risk-of-bias assessments per study (item 18) were initially reported, at the time of original screening, as showing all 52 included studies scoring at least 3 out of 4 on the QA1 to QA4 instrument. A subsequent post hoc reconstruction of individual QA1–QA4 scores, conducted from full-text evidence and independently validated by a second reviewer (Section 3.6), found that this was not accurate: 6 of the 52 originally-included studies scored 2.5 of 4, below the stated threshold, and in several cases also failed the Section 3.2 topical eligibility criteria outright (for example, one study addressed health IoT clinical decision support rather than intrusion detection). These six studies were removed from the corpus, yielding the final corpus consisting of 46 studies (38 being method papers) reported throughout this manuscript. Per-study QA1–QA4 scores for the reconstructed corpus are publicly deposited on Zenodo (doi.org/10.5281/zenodo.22143353).
Results of individual studies (item 19), statistical syntheses (items 20b to 20d), reporting biases (item 21), and certainty (item 22) are not applicable for the reasons documented in Section 3.8.
3.11. Funding, Competing Interests, and Data Availability
Funding (PRISMA item 25): This review received no specific external funding. The corresponding author is supported by Al-Baha University Faculty of Computing and Information PhD scholarship at the University of Technology Sydney. The funder had no role in the design, conduct, or reporting of this review.
Competing interests (PRISMA item 26): The authors declare no competing interests, financial or non-financial, that could have influenced the conduct or reporting of this review.
Data, code, and material availability (PRISMA item 27): The PRISMA 2020 flow diagram and counts at each stage are reported in Figure 1 and Table 1. The full database-by-database search syntax executed on 12 February 2025 is reported in Supplementary Material File S2. The 27-item PRISMA 2020 checklist with location mapping is reported in Supplementary Material Table S1. The complete data extraction sheet capturing study characteristics, method classification, application focus, and identified gaps for the 38 method papers, following the post hoc QA1–QA4 reconstruction reported in Section 3.6, is publicly deposited on Zenodo: doi.org/10.5281/zenodo.22151401. The finalised and independently validated study-level QA1–QA4 scores, scoring rubric, validation record, and data dictionary for the reconstructed corpus are separately and publicly deposited on Zenodo: doi.org/10.5281/zenodo.22143353. No analytic code was developed for this review because no quantitative synthesis was performed.
4. IoT Security Landscape
The IoT continues to grow at unmatched scale, disrupting industries, smart city visions, and even everyday life through connecting devices. Concurrently, this brings new security concerns through interconnectivity, as more potential vulnerability points are added for every additional device. This exposes the network to many attack vectors that malicious entities can exploit. At the same time, the diversity and functionality of these devices introduce complex challenges to the implementation of effective IDS, since the majority of IoT devices are designed with minimal security features. Most newly developed IoT devices treat security as less important than affordability and ease of use, a trade-off that leaves such devices prone to attacks from physical tampering to remote hacking. The recent literature on IoT security vulnerabilities, including in [15,32], underlines the necessity of developing rigorous customised security protocol for IoT networks. The key vulnerabilities presented in Table 2 include insecure interfaces, insufficient update mechanisms, and privacy concerns, which can easily increase the risk of falling victim to cyberattack. For instance, the studies in [14,15] have shown that basic devices suffer from flaws in their security, which leads to unauthorised access and control through prevalent weak credentials and interfaces. This table underlines the problem of insufficient update mechanisms [17]. In the absence of such mechanisms, IoT devices are exposed to typical exploits due to non-updating of firmware. In addition, the threats attached to the amount of data collected without proper security measures raise a debate on the issue of privacy, as indicated in [16]. The table additionally addresses technical issues around poor data encryption of IoT devices and their integration with legacy systems, which further complicate the security landscape. As mentioned in [32,33], the existence of vulnerabilities such as IoT botnet attacks and insecure API endpoints indicates advanced threats targeting these vulnerabilities and potentially compromising end-user devices.
Table 2.
Key IoT security vulnerabilities.
4.1. Heterogeneity of Devices
IoT networks include a diverse range of devices, from very simple sensors that measure temperature and humidity to very complex actuators that control home automation systems or run industrial machinery [39]. These devices usually work on different hardware and communication protocols and platforms, leading to a complex ecosystem that traditional security mechanisms cannot secure [40]. Adding to this complexity, the discrepancy in computational power and energy resources among all those devices obscures the possibility of implementing uniform security measures. Within the reviewed corpus, Sáez-de-Cámara et al. [41] address this directly with a clustered federated unsupervised anomaly detection approach validated on a 100-device emulated testbed incorporating real Mirai botnet traffic. Rather than assuming a single model architecture that fits the whole device population, their approach intead groups dissimilar devices by behavioural similarity before training.
4.2. Dynamic Nature of IoT Networks
The IoT networks are intrinsically dynamic. Devices or nodes incessantly move from being part of the network to again not being part of the network. This dynamic nature introduces uncertainty that cannot be handled by traditional security mechanisms, which are mostly based on static network configurations and predefined rules. There is a need for new security solutions that are adaptive and scalable, with the ability to evolve along the network that they are attempting to protect. Federated approaches within the reviewed corpus that address this directly include Ruzafa-Alcázar et al. [42], who evaluated a privacy-preserving federated IDS for IIoT on ToN-IoT using FedAvg and Fed+ aggregation with differential privacy mechanisms. Their approach allows the model to adapt as participating devices join or leave without the need for retraining from a centralised dataset.
4.3. Complex Network Dependencies
As shown in Figure 2, the interconnection of IoT devices creates a web of dependency that can be exploited by adversaries to plan and execute sophisticated attacks. Such high-level dependencies make it difficult to ensure the integrity and privacy of data across the network. Conventional security mechanisms developed to secure less complex network structures do not effectively secure the highly complex network structures typical of the IoT landscape [28,43]. Muñoz and Valiente [33] demonstrate one response to this within the reviewed corpus, detecting botnet activity from the structure of device communication graphs rather than from individual packet or flow features. Coordinated attacks leave a signature in how devices relate to one another that per-device analysis alone would miss.
Figure 2.
IoT network with different interconnected devices.
IoT networks interconnect a wide variety of devices through a complex network architecture. This high level of complexity presents challenges within the IoT ecosystem in handling dependencies while ensuring smooth functioning with consistency and reliability. Dependencies in IoT networks reflect any reliance of the device and processes on some specific network specifications and interactions for proper functioning. Network dependencies may include connectivity, bandwidth, latency, or interoperability of the various devices with respect to different layers of the network. As IoT networks continue to expand in a wide range of device types, from simple sensors to the sophisticated autonomous machines, the overall stability and performance of IoT networks have come to depend critically on the constant integration of devices and their proper functioning within the network setting.
4.4. Challenges Posed by Network Dependencies
Network dependencies in IoT environments are complex and pose a challenge to the level of manageability of the network and integrity of the system. With the rapid development of IoT networks, scaling leads to exponential increases in the number of connections and the resulting complexity of interactions. Differences in communication protocols can cause interoperability concerns that hinder smooth communication across the system [44,45]. Moreover, most IoT applications function in real-time, implying that they require a substantial amount of bandwidth with reduced latency; however, such resources may not be uniformly available throughout the network, which decreases performance and reliability [46]. In the security context, this also introduces several threat surfaces. The complex web of dependencies described above increases the vulnerability of the network to cyberattacks. This tends to increase the difficulty of management of the network, since in most cases it is forced to carry out reconfiguration and updating of a large number of devices. Taking into account that each device has its own specifications and requirements, this leads to frequent errors and inconsistencies [47]. Moreover, most IoT devices are dependent on third-party networks and services such as cloud platforms and third-party APIs, which brings a whole new set of challenges to the system, including added latency and potential points for network disruption that are beyond the network administrator’s direct control [48]. This presents an even greater challenge to resource management, as the competition for limited network resources leads to inefficiency and reduced performance.
An important limitation of IoT networks is the huge variability in quality of service along the network, especially in heterogeneous network environments such as those that integrate legacy systems with contemporary ones [49]. In these scenarios, it is very important to ensure a constant level of service quality to applications that depend on real-time data. The use of widely divergent technologies and protocols may further complicate the continuous flow of information [27]. The dynamic network topologies brought about by frequent connection and disconnection of networked devices add to the already high complexity, creating challenges for conventional network management techniques and strategies. Managing these complex networks becomes even more challenging with wide geographical distributions and the need for conformity with regional and international data privacy regulations. Thus, IoT networks call for dynamic and scalable management solutions [23]. Each of the challenges discussed above indicates a need for increasingly innovative and flexible network management approaches that can guarantee secure, stable, and efficient functionality in the IoT landscape.
4.5. Real-World Illustrations of Complex Network Dependencies
To better understand how complex network dependencies appear in actual IoT settings, it is helpful to consider several practical examples drawn from different domains. The following cases demonstrate how failures or attacks on one part of the system can have wide-ranging effects due to these dependencies. Table 3 summarises these dependencies across five representative IoT domains. Figure 3 illustrates one such case in the healthcare domain.
Table 3.
Per-domain dependency comparison illustrating critical dependencies, failure modes, and impacts across five IoT application domains.
Figure 3.
Hypothetical illustrative scenario constructed by the authors to demonstrate the healthcare-domain dependency propagation pattern summarised in Table 3. The scenario is not derived from telemetry or incident data reported in any specific study in the reviewed corpus. The image was produced using a generative AI tool from a prompt describing this scenario. In the illustrated scenario, massive DDoS traffic overwhelms the hospital network firewall and the resulting cascade propagates through four dependent device groups: medical devices (MRI machine disconnected, other equipment offline), patient monitoring (heart monitor and IV pump report no data, signal jammed), hospital systems (electronic health records system down, smart bed control malfunction), and IoT sensors (security cameras offline, no sensor response). Collectively, this produces service outages, device failures, and data loss.
5. IoT Intrusion Detection Challenges
Key factors responsible for the complexity of intrusion detection in IoT networks include dissimilarity of devices and scalability concerns. This complexity demands highly advanced approaches to ensure that an efficient mechanism of intrusion detection is realised. Some of the challenges within the IoT intrusion detection area are represented in Table 4 to provide insights into the complex landscape of IoT security. The research by [29] highlights the significant issue of device heterogeneity, where the diversity of operating systems and protocols presents a barrier to the implementation of a unified IDS. Furthermore, the huge volume of data generated by these IoT devices and the demand for real-time detection in applications critical to health and safety further restrict existing IDS frameworks, requiring novel approaches for real-time processing and automation such as those suggested by [52,55]. The dynamic nature of cyber threats, highlighted by [30,56], necessitates IDS solutions to continuously adapt, a task that is made even more complicated by the demand for integration with conventional systems that may not support contemporary security protocols [49]. In addition, energy constraints and diverse operational environments introduce further complexity towards implementing efficient IoT security measures [57]. These findings highlight the multidimensional challenges in securing IoT environments, emphasising the need for adaptive, scalable, and efficient security measures for the evolving IoT landscape.
Table 4.
Challenges in IoT intrusion detection.
5.1. Device Heterogeneity and Scalability Issues
The main challenge for intrusion detection is in the heterogeneity of the IoT devices [29]. Such devices differ in operating system, communication protocol, processing capability, and available security features. For instance, a smart camera may have enough compute for demanding security algorithms, while a low-end heat sensor may struggle with basic encryption. This variability means that each device type is likely to require a customised security posture rather than a single uniform solution. Scalability compounds the problem, since IoT networks, particularly industrial deployments, grow to large device counts that conventional IDS designed for relatively static and homogeneous networks are not built to manage. As coverage gaps widen, sections of the network go under-monitored and exposed. This demands the development of uniform security policies across large and dynamic networks together with a correspondingly novel intrusion detection approach that can operate at the network edge, proximal to where data is generated and collected. Vishwakarma and Kesswani [51] demonstrate one such approach within the reviewed corpus, evaluating a deep neural network IDS on a real-time IoT testbed in order to test whether detection remains viable as device count and traffic volume scale up.
5.2. Limited Computational Resources
IoT environments generally involve resource-constrained devices with minimal processing power and memory compared to conventional computing systems [29,52]. Since conventional detection approaches typically assume computational headroom that simple sensors and actuators do not have, this directly challenges IDS deployment; a device with almost no room for on-board detection becomes an easy target. Energy constraints compound this further [57], since continuous monitoring and data processing draw power that battery-operated devices expected to run for extended periods without recharging cannot always spare. Arshad et al. [57] address this directly within the reviewed corpus, implementing an intrusion detection framework in Contiki, a lightweight operating system built for constrained IoT hardware, and evaluating both detection performance and the framework’s own resource footprint.
5.3. Limited Dataset Availability
There is a deficiency of a comprehensive and updated dataset for the effective IDS development for IoT networks. In most cases, the current datasets are limited in representing the diversity and complexity of the IoT network, rendering current IDS less effective in detecting and removing threats [59]. The dynamic and evolving nature of IoT network configurations, and hence threat surfaces, requires datasets that represent the real-world IoT environment [60].
Table 5 lists the principal data limitations in IoT and their impacts on IDS performance.
Table 5.
Data limitations in IoT and impact on IDS.
The significance of intrusion detection in IoT landscapes is not only critical but quite challenging, as the quantity and quality of data greatly influences the analysis of data [29]. This limitation often originates in the distinctive characteristics of IoT devices, such as limited processing power and energy constraints, added to the high volume and diversity of devices and data types. This limited set of data is adverse to the performance of the resulting IDS. With less data, the precision of IDS in threat detection is less and the response time can also be compromised, which may prove to be critical. In some instances, false positives and negatives may be produced due to sparse or incomplete data, which decreases the effectiveness and reliability of the security protocol and can leave some intrusions unmonitored until they reach the level of substantial damage [61]. The diversity and inconsistency between the different data generated by various IoT devices further complicates these challenges [62]. The IDS is supposed to support diverse data formats and quality with very limited processing capability. Moreover, data transmission latency is high, especially for geographically dispersed IoT networks, where the increased distance may delay the intrusion detection process [63]. This lowers the window for timely intervention, giving adversaries an opportunity to exploit the vulnerability for longer periods without being detected. Therefore, non-availability of high quality and comprehensive datasets serves as a limitation on the successful implementation of modern machine learning algorithms, which are data-hungry and require large labelled datasets for efficient functioning [59]. These types of algorithms are not effectively trainable without enough data; for this reason, they may not recognise the complex patterns of cybersecurity threats, often limiting the overall effectiveness of the IDS.
6. Review of Existing Solutions
Table 6 summarises the solutions surveyed in this section, organised by method family and technological innovation. The subsections below detail the specific findings underlying that summary.
Table 6.
Solutions from the literature: ML solutions and technological innovations.
6.1. Machine Learning Solutions
The use of machine learning (ML) has become essential for improving IoT security. Conventional security measures frequently fall short as the IoT landscape becomes more complicated due to the large number of networked devices producing massive volumes of data. ML enters the picture as a dynamic solution that can quickly analyse big datasets and find unusual patterns that could be signs of security vulnerabilities. These approaches are highly effective at analysing and extracting information from the data generated by various IoT devices, which proves essential for detecting unusual patterns that can indicate a security breach. As shown in Figure 4, different ML techniques can be implemented considering the specific requirements and constraints of the IoT network.
- Supervised Learning: Models trained on labelled data to distinguish normal from abnormal behaviour. Douiba et al. [64] evaluated CatBoost and gradient-boosting decision trees against NSL-KDD, IoT-23, BoT-IoT, and Edge-IIoT with GPU-accelerated experiments, reporting consistent performance across all four benchmarks. Ioannou and Vassiliou [65] applied SVM-based classification to IoT attack traffic with model comparison against alternative classifiers.
- Unsupervised Learning: Models that detect anomalies without labelled training examples, valuable where new attack types are unforeseen. Stiawan et al. [54] applied K-means clustering to three self-collected IoT ping flood traffic scenarios, evaluated via confusion matrix. Dharini et al. [50] combined PCA with multiple classifiers to detect botnet activity in IoT security camera traffic. Tien et al. [66] used autoencoder-based transfer learning for IoT and smart factory traffic, reporting F1 scores against a benchmark comparison set.
- Semi-supervised Learning: Methods combining small labelled and large unlabelled datasets. These are relevant given the labour cost of labelling IoT traffic at scale. Almiani et al. [67] applied label propagation with batch K-means directly to IoT botnet detection.
- Reinforcement Learning (RL): Algorithms that learn security responses through trial-and-error interaction with the network environment. Xiao et al. [4] applied RL to mobile edge caching and offloading security, covering jamming, authentication, and privacy; the study’s IoT-intrusion detection relevance is indirect, since its primary application is edge caching security rather than a bounded IoT IDS task, a limitation noted in the study’s own scope.
- Generative Adversarial Networks (GANs): A generator–discriminator pair that synthesises realistic training data, addressing the scarcity of labelled attack data in IoT settings. Zhang et al. [59] reported a GAN-based anomaly detection and forecasting method for unlabelled data; the study’s IoT-security relevance is also indirect, since its primary application is 5G vertical network anomaly detection rather than a clearly bounded IoT IDS task. Figure 5 depicts the general GAN workflow for IoT intrusion detection.
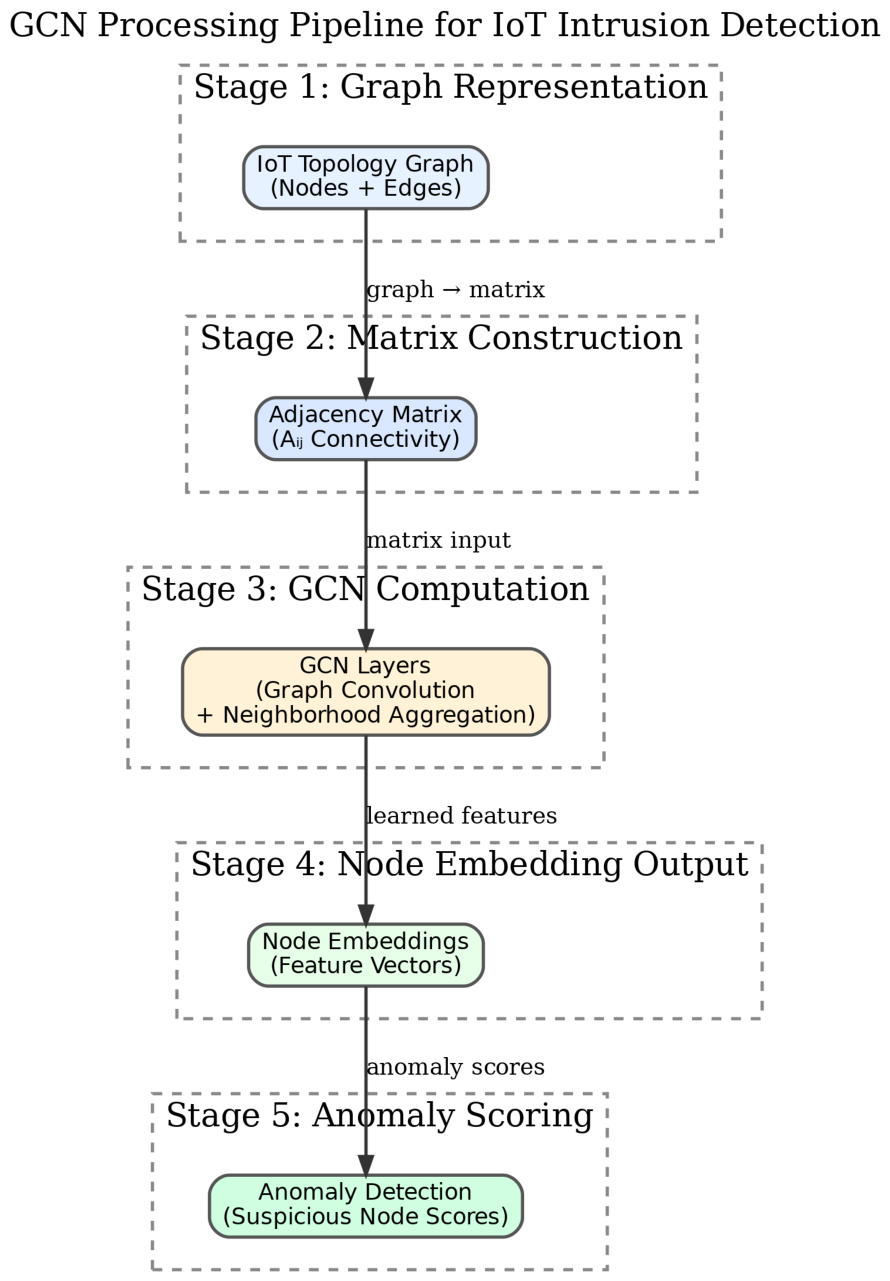
- Graph-Based Methods: Approaches that exploit the graph structure of IoT networks (where devices are nodes and connections are edges) to detect anomalies involving multiple nodes or coordinated attack patterns. Muñoz and Valiente [33] detected IoT botnet activity from device communication graphs on the IoT-23 dataset, using cross-validation and hyperparameter search with DVC/MLflow experiment tracking instead of individual packet features. Figure 6 illustrates a graph convolutional network (GCN) processing pipeline as a representative graph-based architecture for this class of method; no study meeting the Section 3.2 inclusion criteria in the current corpus applies GCNs specifically, though the technique is discussed in the broader literature as a natural extension of the graph-based approach demonstrated here.
Figure 4.
Taxonomy of machine learning approaches applied to IoT intrusion detection, grouped into three families: classical machine learning (supervised methods such as decision trees and SVM; unsupervised methods such as K-means, PCA, and autoencoders; semi-supervised methods such as label propagation and S3VM; and reinforcement learning for adaptive policy learning), deep learning (RNN/LSTM for sequential and temporal data, GAN for synthetic data augmentation, GCN for graph-structured topologies, and transformer architectures for long-range dependencies), and hybrid or ensemble methods (random forests, stacked ensembles, federated learning, and XAI- augmented hybrids).
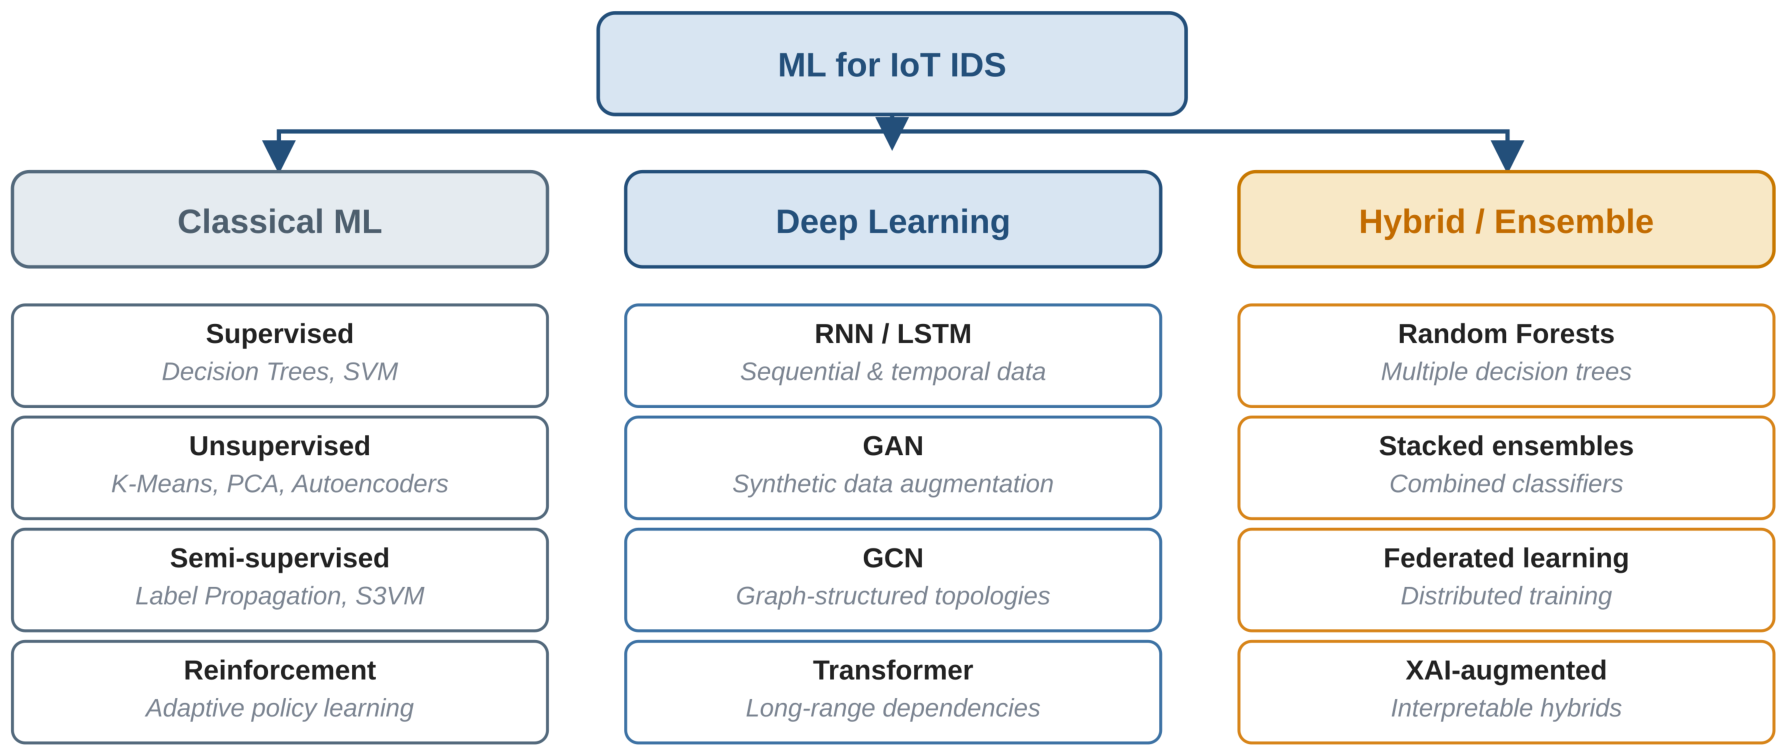
Figure 5.
GAN workflow for IoT intrusion detection. Stage 1 draws on real samples of small and imbalanced IoT data; Stage 2 is the generator–discriminator training loop that produces synthetic samples; Stage 3 trains the IDS on the resulting real-plus-synthetic augmented dataset to yield an improved detection model.
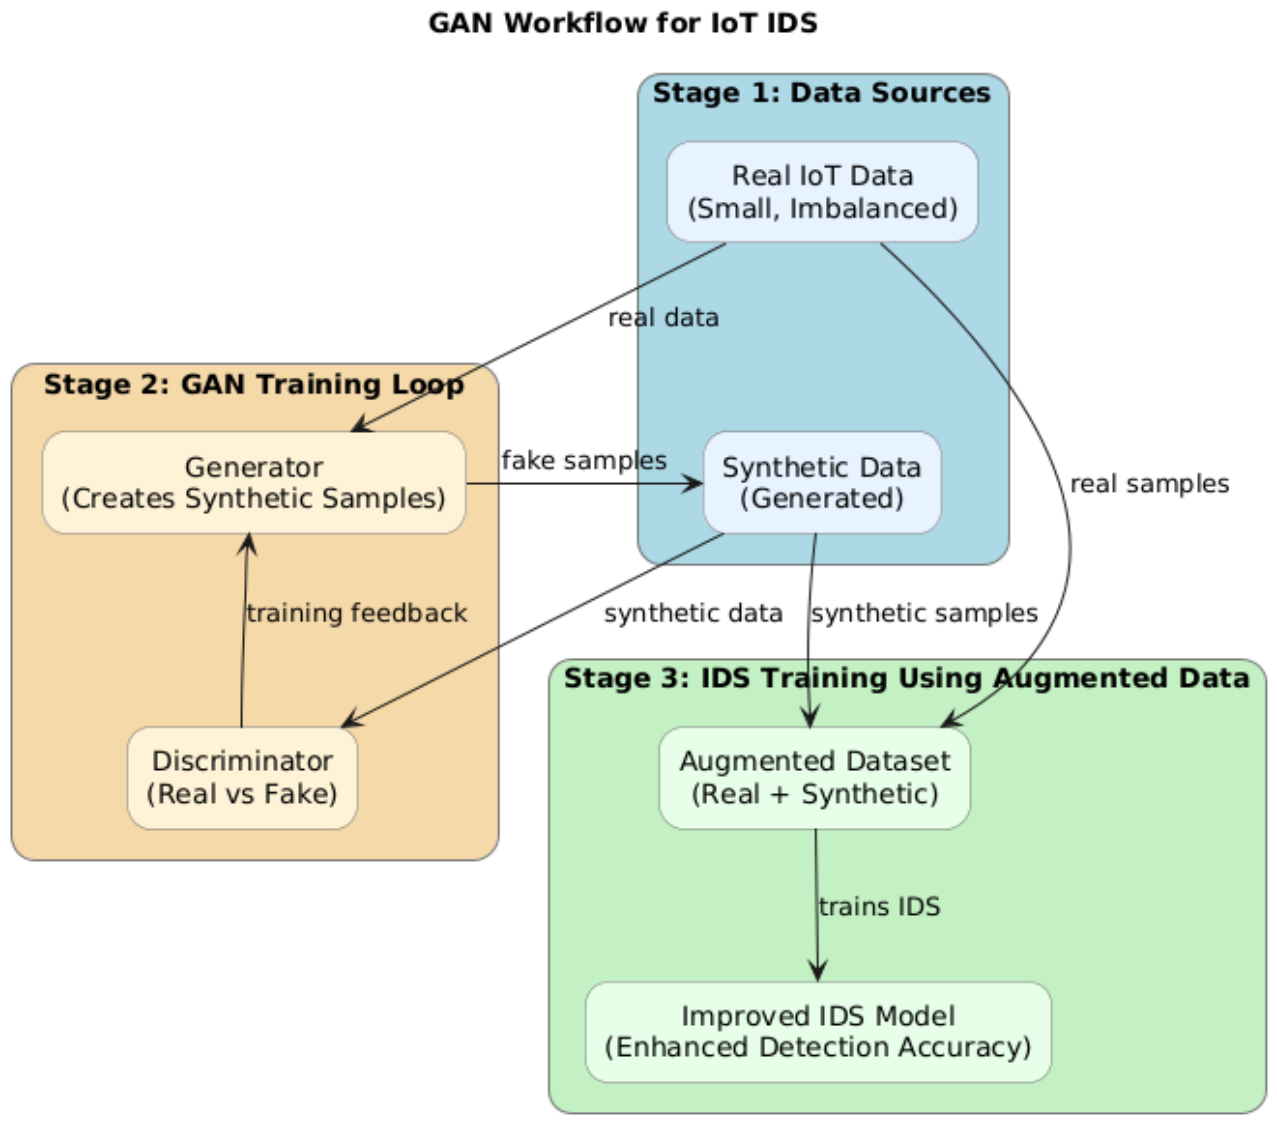
Figure 6.
GCN processing pipeline for IoT intrusion detection. An IoT topology graph of nodes and edges (Stage 1) is converted to an adjacency matrix (Stage 2), then passed through GCN layers that perform graph convolution and neighbourhood aggregation (Stage 3) to produce node embeddings (Stage 4), from which per-node anomaly scores are derived (Stage 5).
Other relevant models find utility in processing sequential IoT data. Yousuf and Mir [53] applied a recurrent neural network to DDoS attack detection in IoT traffic. Xu et al. [68] reported an improved long short-term memory (LSTM) architecture with a concept-drift adaptive mechanism for IoT service anomaly detection, addressing the non-stationary attack patterns that arise as IoT threat landscapes evolve over time. Ensemble learning approaches such as random forests, which integrate multiple decision-tree classifiers to improve predictive robustness, are a further established technique in this space; no study meeting the Section 3.2 inclusion criteria in the current 38-paper corpus applies random forests specifically as its primary method following the removal of one such study in the post hoc QA reconstruction (Section 3.6), though gradient-boosting decision trees, a closely related ensemble technique, are demonstrated by Douiba et al. [64] above.
The application of ML in IoT security not only enhances the detection of threats but also improves the efficiency of the security operations by automating the process of threat detection and response. This technological advancement supports the scalability of security solutions, making it practical to protect large networks of IoT devices against sophisticated cyber threats. As these networks evolve, so too are the ML techniques designed to protect them becoming more refined and customised to the unique challenges of IoT security.
6.2. Technological Innovations
The efficiency of IDS in IoT settings can be significantly enhanced by addressing the data limitations through these strategic measures, leading to more secure and reliable networks. Some of the technological innovations to mitigate the challenges of security and intrusion detection in IoT are discussed below.
- Edge Computing: Edge computing emerges as a promising solution to high data latency issues by processing data at or close to the data generation source [46]. This not only enhances the response times of IDS but also reduces the load on central data processing resources, leading to an enhanced real-time threat detection.
- Centralised Data Management Systems and Data Integration: These strategies are employed to address the challenges posed by fragmented data sources. These approaches ease the aggregation of data from numerous sources into a coherent dataset, facilitating comprehensive analytics and accurate threat assessment. (A citation previously supporting this general claim, Ouafiq et al. 2022 [26], was removed from the corpus following the post hoc QA1–QA4 reconstruction in Section 3.6; the claim itself reflects standard data-integration practice rather than a corpus-specific finding.)
- Standardised Data Collection Protocols: Inconsistent data acquisition across heterogeneous IoT devices introduces gaps that degrade IDS accuracy, as noted in Table 5. Standardising data collection protocols across device types, including consistent sampling rates, feature formats, and timestamp conventions, reduces this variability and supports more reliable downstream analysis. Cloud-based storage solutions that retain standardised records over time further support this consistency by giving IDS models a stable, comparable data foundation across the device population.
- Energy Optimisation: Energy optimisation in data transmission protocols facilitates addressing the energy constraints prevailing in many IoT devices [2], especially those that are battery-operated. This ensures constant monitoring without frequent battery drain-offs.
- Distributed Processing: When scaling IDSs to accommodate an expanding array of IoT devices, scalable cloud architectures and distributed processing frameworks offer the necessary infrastructure to handle increased data loads without any trade-offs with system performance. Alghamdi and Bellaiche [52] demonstrate this within the reviewed corpus using a Lambda architecture, a distributed processing pattern combining a batch layer for comprehensive historical analysis with a speed layer for real-time inference, evaluated for an ensemble deep-learning IDS.
- Lightweight Machine Learning Models: The development of lightweight ML models addresses the constraints associated with computational resources and data availability in IoT devices [69]. These models are developed to operate efficiently even with limited data, reducing the reliance on large-scale data inputs without compromising intrusion detection efficiency. Customised to fit the specific requirements of IoT environments, such models ensure optimum performance by using advanced algorithms capable of learning and adapting from relatively smaller datasets.
- Data Augmentation: Data augmentation plays a critical role in enhancing the available datasets, particularly where the actual data volume is low [70]. By generating synthetic data samples, this technique enables robust training of machine learning models, thus enhancing their prediction accuracy and generalisability in real-world settings. Advanced data preprocessing and cleaning techniques are equally important, as they refine data quality by removing noise and correcting errors, which in turn reduces the incidence of false positives and negatives in threat detection.
- Blockchain Technology: Blockchains can offer a robust solution to data integrity issues by establishing a secure and immutable record of data transactions, which is particularly significant in environments where data tampering could lead to severe consequences [71].
6.3. Hybrid and Context-Aware Architectures
Recent IoT IDS research has moved beyond single-method classifiers towards hybrid and context-aware architectures that combine multiple learning paradigms or condition the detector on device-specific behaviour. Four directions stand out.
Transformer-based IDS can adapt the self-attention mechanism to network flow analysis, capturing long-range temporal dependencies that recurrent networks struggle with. Akuthota and Bhargava [72] demonstrate that transformer encoders applied to IoT flow features outperform LSTM and CNN baselines on multi-class attack classification. The mechanism scales naturally to high-throughput IoT traffic but introduces non-trivial training cost on resource-constrained devices.
Reinforcement learning IDS treats detection as a sequential decision problem. He et al. [73] propose a transferable and adaptable RL framework that re-targets across IoT domains without retraining from scratch. The approach addresses two persistent IDS issues, namely, concept drift and the need for continual adaptation as device populations evolve. RL training stability remains an open issue. Pairing the RL component with a generative model for synthetic experience replay is an active research direction.
Federated learning IDS distributes model training across IoT nodes while keeping raw traffic local. Ruzafa-Alcázar et al. [42] show that privacy-preserving federated training matches centralised performance on industrial IoT benchmarks while satisfying GDPR-style data locality constraints. Sáez-de-Cámara et al. [41] extend this to heterogeneous IoT populations through clustered federated aggregation. The non-IID nature of per-device traffic remains the principal obstacle.
Behavioural and physical-context IDS incorporates domain-specific signals beyond network traffic. Healthcare IDS condition detection on physiological monitoring patterns from medical devices. Industrial IDS draw on process physics constraints, including power draw, vibration, and command timing. These can be used flag anomalies that are invisible to packet-level inspection alone. Yao et al. [74] integrate generative adversarial models into edge–fog deployments where context features are aggregated locally before global classification.
6.4. Interpretable IDS and Security-by-Design
Two complementary trends address the trustworthiness gap in machine learning IDS. Interpretability methods quantify which input features drive each detection decision. Gaspar et al. [75] apply LIME and SHAP to multi-layer perceptron IDS for IoT, showing that perturbation-based explanations expose feature dependencies that domain experts can validate. Sharma et al. [76] extend the approach to deep neural network IDS and demonstrate that SHAP and LIME visualisations support continuous improvement cycles by exposing under-weighted features and spurious correlations. Attention-based interpretability extracts decision weights directly from transformer attention heads and offers a lower-overhead alternative for architectures that already use attention.
Security-by-design moves the trust anchor from runtime detection to design-time assurance. ETSI EN 303 645 V3.1.3 [77] specifies thirteen baseline categories for consumer IoT cybersecurity, including no universal default passwords, secure update mechanisms, vulnerability disclosure policies, and minimised attack surfaces. NIST IR 8259A [78] defines a complementary core baseline of six device cybersecurity capabilities: device identification, configuration, data protection, logical access to interfaces, software update, and cybersecurity state awareness. Compliance with these baselines reduces the residual attack surface that downstream IDS must cover, allowing detection to focus on advanced threats rather than commodity exploits.
The balance between interpretability and detection performance is more consequential in Industrial IoT (IIoT) settings than in consumer IoT, since IIoT intrusion decisions can trigger safety-critical actuator responses and both false positives and false negatives carry direct operational cost. Ahmad et al. [79] illustrate this trade-off: their XGRU-IDS combines Extra Trees feature selection with a gated recurrent unit classifier to preserve interpretability without the accuracy penalty that simpler fully-transparent models such as shallow decision trees typically incur relative to opaque deep architectures. This design choice to build interpretability in rather than layering a post hoc explanation onto an opaque model is what NIS2 and the CRA’s security-by-design provisions push developers toward. A SHAP or LIME explanation generated after the fact does not itself satisfy a design-time transparency requirement in the same way that an inherently interpretable architecture does. This review’s synthesis of the interpretability literature (Table 7) does not disaggregate consumer IoT from IIoT deployments. Given how much higher the operational stakes of an interpretability–performance trade-off are in the IIoT setting, this represents a limitation that should be addressed in future IIoT-focused work.
Table 7.
Synthesis matrix of the included method papers (n = 38) by method family, application focus, and gap addressed. Six studies previously listed here (Yang 2019 [22], Mir 2023 [23], Kaur 2019 [24], Yosuf 2020 [25], Ouafiq 2022 [26], Aly 2018 [27]) were removed following the post hoc QA1–QA4 reconstruction and independent second-reviewer validation reported in Section 3.6, which found that they did not meet the 3-of-4 quality threshold or in some cases the Section 3.2 topical eligibility criteria.
7. Critical Evaluation of the Literature
IoT security has opened into a massive area that includes a broad range of cutting-edge technologies and methods developed to tackle the problems in IoT networks. This section presents a review of the existing literature on IoT intrusion detection systems. Emphasis is placed on identifying the strengths and gaps in the current research. While most of these limitations still persist, developments have been possible through the advanced capabilities of ML models and the enhancement of data handling capabilities. This review is an attempt to highlight the places where IoT security research excels and also to identify those areas where extra attention needs to be paid in order to bridge existing gaps so that progress can translate into robust, scalable, and practical security solutions for different IoT environments. Table 7 maps each included method paper to its method family, its application focus, and the gap it addresses; Figure 7 visualises the publication year distribution of these families across the period from 2014 to 2025.
Figure 7.
Method family distribution across the SLR corpus by year of publication (2014–2025). Regenerated from the Table 7 synthesis matrix (n = 38) following removal of six studies that did not meet the QA1–QA4 threshold or Section 3.2 eligibility criteria on post hoc reconstruction (Section 3.6). The nine method family groupings shown here (Classical ML, Deep Learning (General), GAN/Data Augmentation, Graph-Based (GCN), Sequential/Temporal, Federated Learning, Reinforcement Learning, XAI / Interpretability, and Security Architecture/Other) aggregate the more granular method labels listed individually in Table 7.
The cross-study comparison by dataset and validation approach (Table 8) reveals a fragmented evaluation landscape rather than a shared benchmark. Only three named datasets recur across more than one study: NSL-KDD, ToN-IoT and IoT-23 each appear in two studies; UNSW-NB15, InSDN, BoT-IoT, Edge-IIoT, and NetFlow-derived benchmarks each appear in exactly one. A single study (Douiba et al. [64], Table 8) accounts for four of these eleven total dataset appearances across eight distinct named datasets, evaluating against NSL-KDD, IoT-23, BoT-IoT, and Edge-IIoT; excluding that study, dataset overlap across the remaining 37 papers is minimal. Of the 38 method papers, 10 (26 percent) do not name a specific public dataset in the reviewed evidence, most commonly relying on self-collected testbed traffic (for example, Stiawan et al.’s three-scenario IoT ping-flood traffic, or Sáez-de-Cámara et al.’s hundred-device emulated testbed incorporating live Mirai traffic) without depositing it publicly. For validation approach, cross-validation and train/test splitting are the most frequently reported techniques, though the specific split ratios and fold counts are inconsistently reported across studies, which is itself a reproducibility gap (consistent with the QA3 (reproducibility) scores in Table 8 falling below the maximum on 35 of the 38 papers). On attack type, the corpus skews toward general-purpose multiclass intrusion or anomaly detection (the majority of entries), with a smaller cluster addressing specific attack families: DDoS (Yousuf), botnet activity (Muñoz; Almiani), covert channels (Cabaj), and XSS (Kim). This distribution suggests that the method diversity within the corpus has outpaced the standardisation of evaluation techniques: no two studies published in different years and using different architectures can be directly compared on identical data without one adopting the other’s benchmark after the fact.
Table 8.
Dataset, validation approach, and QA1–QA4 score for each of the 38 method papers in Table 7, extracted from the independently-validated QA reconstruction reported in Section 3.6 and deposited on Zenodo (doi.org/10.5281/zenodo.22143353). Entries marked n/r were not specified in the reviewed evidence; entries marked n/a indicate that the study’s own reported content does not include an empirical dataset or validation step of the kind this table describes (for example, a review or an architectural analysis paper, included in Table 7 under different method family labels).
The corpus reviewed here exhibits a recurring pattern that qualifies its reported gains. A substantial proportion of the 38 method papers evaluate detection performance on a small set of widely reused benchmark datasets (Section 5.3, Table 5) or on network topologies simpler than those documented in Section 4.3’s real-world dependency illustrations. Real-world IoT deployments are characterised by device failure, network instability, and incomplete or noisy data (Section 4.4), conditions that few of the reviewed studies evaluate against directly. The corpus also shows a steady cadence of new architectures reported each year (Figure 7), each typically evaluated in isolation rather than against the operational constraints summarised in Table 9, which limits the extent to which reported accuracy gains can be expected to transfer to deployed systems. Three areas remain comparatively underexamined across the reviewed literature: interoperability across heterogeneous device populations, model maintenance under distributional drift as device fleets and threat patterns evolve, and compliance with jurisdiction-specific regulatory requirements (Section 7.2.6). Addressing these gaps is likely to require closer engagement with deployment-side practitioners, more consistent reporting of negative or null results alongside positive ones, and evaluation protocols that reflect operational conditions in healthcare, industrial, and smart city IoT settings rather than laboratory benchmarks alone.
Table 9.
Illustrative literature on key limitation themes in current research. These studies are cited as contextual and background references illustrating each limitation theme; they are not part of the review’s 46-study formal corpus synthesised in Table 7, and were not subject to the Section 3.2 eligibility screening applied to that corpus.
7.1. Strengths of Current Research
IoT security research, particularly in the field of intrusion detection, has demonstrated significant advancement through the development of advanced technologies and methodologies. These advancements address critical security challenges inherent in IoT networks while laying a foundation for future enhancements.
7.1.1. Advanced Machine Learning Models
- Generative Adversarial Networks (GANs): GANs have shown great promise in addressing the issue of limited anomaly data in IoT environments. By generating high-quality synthetic data, GANs can enhance training datasets for IDS and provide a wider spectrum of data scenarios. This approach helps to enhance the robustness and accuracy of IDS by exposing them to a larger array of potential security threats, better preparing the system to tackle real-world anomalies. Research studies such as Zhang et al. [59] emphasise how GANs are used to efficiently augment datasets, demonstrating their potential in enhancing intrusion detection performance.
- Graph Convolutional Networks (GCNs): The application of GCNs in IoT security is a significant development for handling complex network dependencies. The heterogeneous and interconnected nature of IoT networks presents unique challenges that GCNs are particularly adept at managing. By capturing and analysing the spatial relationships and dependencies within graph-structured data, GCNs provide a detailed understanding of network behaviour that is crucial for detecting complex security threats. The study by Muñoz and Valiente [33] illustrates this approach, detecting IoT botnet activity from device communication graphs rather than individual packet features. An earlier draft of this paragraph credited a graph anomaly detection study (Mir et al., 2023 [23]) for this contribution; that study was subsequently removed from the corpus following the post hoc QA1–QA4 reconstruction reported in Section 3.6, since it did not meet the stated quality threshold on re-verification.
7.1.2. Enhancement of Adversarial Robustness
The growing complexity of cyberattacks, particularly adversarial attacks that manipulate data inputs to deceive learning models, poses a significant challenge to IoT security. The adaptation of IDS using GANs to improve adversarial robustness corresponds to a strategic response to these threats. GANs can generate data for training purpose and learn from adversarial examples to enhance IDS detection capabilities. This approach helps in the development of IDS that are not just responsive but also proactive in identifying and mitigating potential adversarial threats before they can cause harm.
7.1.3. Interdisciplinary Approaches and Collaborative Efforts
A substantial strength of current research is the growing collaboration across various disciplines, from cybersecurity and data science to network engineering and even behavioural science. This interdisciplinary approach will enhance the research landscape by allowing approaches to be undertaken in a more systematic and rigorous manner when designing and developing security solutions, incorporating both technology and human-centric factors.
7.2. Limitations and Gaps
Although the field of IoT security has seen significant advancements, there are still an abundance of gaps and limitations in the research that can prevent effective IDS development. These drawbacks highlight how challenging it is to convert theoretical models into practical and scalable systems that can safely navigate the dynamic and extensive landscapes of IoT networks.
7.2.1. Data Availability and Representativeness
The quality and comprehensiveness of training data has a major impact on the effectiveness of machine learning-based intrusion detection systems. Although these methods are innovative, creating synthetic data using GANs still has difficulty confirming that the data accurately reflect the complexity and diversity of actual IoT environments. Large and diverse datasets that are updated frequently to reflect new and emerging threats are urgently required. Although this requirement is frequently acknowledged in the literature, it does not offer a long-term solution to the problems of data scarcity and lack of comprehensiveness that hamper IoT security research.
A related and largely unaddressed problem in the reviewed corpus is robustness under noisy or high-entropy conditions, particularly encrypted or otherwise obfuscated IoT traffic (Table 5). None of the 38 method papers in this corpus evaluate detection performance specifically under high-entropy encrypted flows, even though encryption is increasingly the default state of IoT traffic (following the security-by-design push discussed in Section 6.4). Model compression and distillation techniques, which train a smaller student model to reproduce a larger teacher model’s decision behaviour, are established in the broader machine learning literature as one route to extracting stable generalisable signals from noisy inputs, and represent a plausible direction for extracting reliable malicious traffic signatures from encrypted or high-entropy flows without requiring decryption. No study meeting this description fell within the corpus at the time this review’s search was executed (12 February 2025) or within the subsequent scoping exercise (Section 3.6, through 13 July 2026). A closely related contribution has since appeared: Hong et al. [93] have reported a noise-immune neural distillation framework (BGA) that combines gated attention with WGAN-GP data augmentation to extract malicious signatures from high-entropy encrypted flows, evaluated on industrial control system traffic under real-time latency constraints. As it was published outside this review’s search window, it is not included in the formal corpus or Table 7, but is cited here as evidence that the direction flagged as an open gap is being actively pursued as well as to constitute a concrete starting point for the full corpus update recommended in Section 8.
7.2.2. Adversarial Attacks on IoT Networks: Research Gaps
Adversarial attacks constantly test the efficiency of ML models used in intrusion detection systems, remaining a significant yet under-researched area within IoT security. The complexity of adversarial strategies that explicitly target these models poses persistent hurdles even where research efforts are already intensive. The current literature emphasises the potential of adversarial training as a defence mechanism, but techniques that can reliably detect and mitigate such threats in deployed IoT settings remain limited. Explainable AI (XAI) is suggested in the literature as a way to increase the transparency of IDS decisions when identifying adversarial attacks, though few studies have yet applied XAI specifically to strengthen IDS resistance against sophisticated adversarial strategies, leaving this an open direction for further research.
7.2.3. Complex Network Dependencies in IoT
Handling complex dependencies presents significant challenges within the heterogeneous and interconnected network of devices in IoT. Graph convolutional networks (GCNs) have been proposed in the literature for modelling such complex relationships, though further study is needed on their scalability and adaptability in a dynamic IoT environment. Innovative approaches such as hierarchical graph representation learning and domain-specific adaptations offer potential improvements in anomaly detection accuracy, but the current literature does not fully address the practical deployment of such complex models in real-time IoT settings, particularly in sectors with critical operational demand.
7.2.4. Balancing Security with Usability and Performance
Another important research gap that is seriously under-addressed is the trade-off between enhanced security measures and the usability and operational efficiency of IoT devices. Advanced intrusion detection systems demand considerable computational resources; when applied to low-power devices with limited processing capability, this can degrade performance. This trade-off becomes especially critical in consumer IoT applications, where device responsiveness and battery lifetime are as fundamental to user satisfaction as security itself.
7.2.5. Uniform Security Protocols Across Diverse Devices
The heterogeneity of IoT devices poses a substantial challenge to implementing uniform security measures across an entire network. The reviewed literature offers recommendations for securing diverse device populations, but few studies develop a strategy detailed enough to be applied consistently across the full range of device types that make up a typical IoT deployment. This gap highlights a need for more adaptive and modular security solutions that can be customised and scaled according to specific device characteristics and network configurations.
7.2.6. Regulatory and Compliance Challenges
The regulations and technical standards discussed in this subsection (GDPR, NIS2, the Cyber Resilience Act, ETSI EN 303 645 [77], and NIST IR 8259A [78]) were not identified through the systematic search protocol described in Section 3.1; as none are peer-reviewed empirical studies, they could not have met the Section 3.2 inclusion criteria, and do not appear as rows in Table 7.
Lastly, the global character of IoT deployments introduces complex regulatory and compliance challenges that find insufficient space in the current literature. On the other hand, the deployment of uniform security solutions is also hampered by varying requirements set by different countries and regions regarding data privacy, security standards, and telecommunication regulations. The existing research generally skips quickly over these challenges to focus on finding technical solutions, without really investigating the strategies needed to meet the difficulties of international legal and regulatory landscapes.
The legislative landscape has changed substantially since 2020, and now imposes architectural constraints that any practical IDS must accommodate. The General Data Protection Regulation (Regulation (EU) 2016/679) [94] established data locality and lawful basis foundations that constrain centralised IDS architectures handling personal data flowing through IoT devices. The GDPR’s storage limitation and purpose limitation principles create immediate friction with traditional IDS designs that retain large traffic logs for training and replay. Federated and on-device learning approaches partially resolve this tension, and have consequently moved from research curiosities to compliance pathways.
The NIS2 Directive (Directive (EU) 2022/2555) [95] extends mandatory cybersecurity baselines to operators of essential and important services, including many IoT-dependent sectors such as healthcare, transport, and energy. Article 21 prescribes risk management measures that include incident handling, vulnerability disclosure, supply chain security, and use of cryptography. These requirements directly inform IDS deployment scope, retention periods, and reporting cadence.
The Cyber Resilience Act (Regulation (EU) 2024/2847) [96], published on 20 November 2024 and applicable from 11 December 2027, imposes horizontal cybersecurity requirements on products with digital elements before they enter the EU market. Manufacturers must perform conformity assessments, maintain software bills of materials, and report actively exploited vulnerabilities within 24 h. The Act establishes a default-secure baseline that shifts part of the IDS workload upstream. Devices entering the network already satisfy minimum hardening, and the IDS can prioritise detection of advanced threats rather than commodity-exploit signatures.
Two technical standards now operationalise these legal frameworks: ETSI EN 303 645 V3.1.3 [77] supplies thirteen baseline categories for consumer IoT cybersecurity that align with both UK PSTI legislation [97] and EU CRA conformity, while NIST IR 8259A [78] provides a parallel device capability core baseline aligned with US federal procurement guidance.
Three architectural implications follow for IDS design: first, log retention windows must respect both incident record minima under NIS2 Article 23 and storage limitation maxima under GDPR, which typically means tiered retention with progressive anonymisation; second, breach notification timing (NIS2 24/72-h windows and CRA 24-h vulnerability reports) imposes hard latency constraints on IDS alerting pipelines; third, conformity assessment requirements under CRA encourage IDS that produce auditable detection trails rather than opaque scores. This argues directly for the interpretable architectures discussed in Section 6.4.
This positioning is summarised in Table 10, which situates the present review against fourteen systematic reviews of ML/DL-based IoT intrusion detection published during and after this review’s own search window (see Section 1 for discussion).
Table 10.
Positioning against systematic reviews of ML/DL-based IoT intrusion detection published February 2025–July 2026.
8. Implications for Future Work
Building on the gaps identified in Section 5 and Section 7, three priorities are not yet adequately addressed by the reviewed literature and merit dedicated attention. First, IoT-representative datasets that reflect current device configurations and threat patterns remain scarce (Section 5.3); their absence limits how well any reported detection accuracy generalises beyond the small set of benchmark datasets the corpus relies on. Second, security solutions that integrate with edge computing and 5G infrastructure rather than assuming centralised processing are needed in order to keep pace with reduced-latency deployment models. Third, lightweight security protocols capable of running on severely resource-constrained devices remain underdeveloped relative to the computational assumptions embedded in most reviewed detection architectures (Section 5.2). Because datasets, deployment constraints, and regulatory requirements are interdependent rather than separable engineering problems, progress on these fronts will depend on closer collaboration between IDS researchers, device manufacturers, and policymakers.
Operational cost and IoT device lifecycle considerations have largely been left out of detection-focused research. Two additions to the future work agenda follow from this gap. First, total cost of ownership for IDS deployment includes not only inference compute but also training data labelling, model update bandwidth, and storage of detection event logs subject to NIS2 retention windows. Future research should quantify these cost components in deployed environments rather than reporting only single-pass accuracy on public benchmarks. Second, IoT device lifecycles vary and are often longer than the security update timing assumed by detection methods. Many devices remain in service for five to ten years with progressively reduced manufacturer support. IDS designs that depend on continuous model updates or vendor-supplied threat intelligence will degrade as devices fall out of vendor support windows. The CRA introduces a minimum five-year obligation when handling vulnerabilities for products with digital elements, which provides a partial floor but does not eliminate the long-tail degradation problem. Future research should investigate IDS architectures that gracefully degrade as upstream support diminishes.
A preliminary scoping search, described in Section 3.6, indicates that a full and properly resourced update of this review is warranted. That exercise identified 33 candidate primary studies published between February 2025 and July 2026, none of which are included in the present corpus, since only abstract-level screening was possible within the resources available for this submission. One candidate illustrates the kind of contribution such an update would likely surface. Munaye et al. [107] report an ensemble-learning IDS for WSN-based IoT that explicitly designs a leakage-free evaluation protocol, separating train and test data before any balancing, feature selection, or hyperparameter tuning. This directly addresses a methodological weakness common to several studies in the present corpus (Section 7.2.1). A future update carrying all 33 candidates through full-text QA1–QA4 assessment while using the complete six-database protocol instead of a single aggregator tool would substantially strengthen the relevance of this review’s conclusions.
9. Conclusions
This systematic literature review examined 46 peer-reviewed studies on intrusion detection in IoT networks, screened from 427 records identified in the search executed on 12 February 2025 (Figure 1, Supplementary Material Table S1). Fifty-two studies initially met the quality threshold and eligibility criteria at the time of original screening; a post hoc reconstruction of individual QA1–QA4 scores, independently validated by a second reviewer (Section 3.6), subsequently found that six of these did not meet the stated 3-of-4 quality threshold, and in some cases did not meet the topical eligibility criteria at all. These six studies were removed; this correction is disclosed here in the interest of transparent reporting. The review focuses on two underexamined themes: first, the complex network dependencies that propagate failures across interconnected IoT systems; and second, the chronic data limitations that constrain machine learning detection approaches. The corpus comprises 38 method papers (82.6 percent) together with eight foundational, methodological, and survey references (17.4 percent). Publication activity is concentrated in 2022 and 2023, while the 2024 cohort shows distinct shifts toward interpretability, federated training, and security-by-design (Figure 7).
The synthesis matrix in Table 7 maps the included method papers across nine principal method families. Generative adversarial networks dominate the dataset augmentation literature with three entries, spanning fog architectures and 5G-vertical applications (a fourth addressing healthcare was removed in the post hoc QA reconstruction reported in Section 3.6). Graph-based detection appears through classical communication graph analysis (Table 7); a second entry applying graph convolutional networks specifically was removed in the post hoc QA reconstruction reported in Section 3.6, though GCNs more generally are discussed as a technique in Section 6.1 with reference to the broader literature. Transformer-based detection enters the corpus in 2025 with a single representative paper (Table 7). The most consequential finding is the 2023 emergence of two themes in the corpus that were previously absent: federated learning addresses the tension between privacy and locality that the GDPR imposes on centralised IDS, while interpretability methods such as LIME and SHAP address the black-box critique that has long impeded operational trust in ML-based IDS. Separately, this review draws on design-time standards, including ETSI EN 303 645 [77], and NIST IR 8259A [78], to argue that part of the security workload should be shifted upstream to the device manufacturing process; these standards are cited as regulatory context rather than as method papers within the corpus’s own publication timeline.
Three pressing gaps remain across the corpus. First, real-time detection with sub-second latency on resource-constrained devices is claimed by many studies, but is evaluated against few common benchmarks, leaving comparability limited. Second, dependency modelling is largely absent from method papers, despite strong evidence that dependency-aware detection captures attack vectors invisible to flow-level inspection. Third, regulatory compliance is now an architectural constraint on IDS design rather than a downstream concern. GDPR, NIS2, the EU Cyber Resilience Act, and the UK PSTI Act [97] all impose direct requirements on IDS retention, reporting, and conformity; however, only a small fraction of method papers in the corpus explicitly address how their architectures satisfy these requirements.
Four priorities follow from this review. First, evaluation benchmarks must converge on a small set of representative datasets that cover heterogeneous device populations, realistic attack mixes, and concept drift. Second, the next generation of IDS must integrate interpretability natively rather than as a post hoc layer. Third, federated and on-device learning architectures need standardised evaluation under non-IID conditions that reflect deployed IoT populations. Fourth, the research community must close the gap between technical contributions and the regulatory landscape. IDS architectures that cannot satisfy the timing required by NIS2 incident reporting or CRA conformity assessments cannot transition from laboratory to practice. The principal contribution of this review is to make these gaps visible and provide a structured matrix that future research can use to position its contributions.
Supplementary Materials
The following supporting information can be downloaded at https://www.mdpi.com/article/10.3390/network6030076/s1, Table S1: PRISMA 2020 Checklist; File S2: Search Strategy and Syntax.
Author Contributions
Conceptualization, M.A. and P.N.; methodology, M.A.; validation, M.A. and M.M.; investigation, M.A.; data curation, M.A.; writing—original draft preparation, M.A.; writing—review and editing, P.N., M.M. and F.E.Z.; visualization, M.A.; supervision, P.N.; project administration, P.N. All authors have read and agreed to the published version of the manuscript.
Funding
No external funding supported this review. The corresponding author is supported by the Al-Baha University Faculty of Computing and Information PhD scholarship at the University of Technology Sydney. The funder had no role in the design, conduct, or reporting of this review.
Institutional Review Board Statement
Not applicable. This review analyses previously published literature and did not involve human participants, animal subjects, or new data collection.
Informed Consent Statement
Not applicable.
Data Availability Statement
The PRISMA 2020 flow diagram and counts at each screening stage are reported in Figure 1 and Table 1. The full database-by-database search syntax executed on 12 February 2025 is reported in Supplementary Material File S2. The 27-item PRISMA 2020 checklist with location mapping is reported in Supplementary Material Table S1. The complete data-extraction sheet capturing study characteristics, method classification, application focus, and identified gaps for the 38 method papers, following the post hoc QA1–QA4 reconstruction reported in Section 3.6, is publicly deposited on Zenodo: doi.org/10.5281/zenodo.22151401. The finalised and independently validated study-level QA1–QA4 scores, scoring rubric, validation record, and data dictionary for the reconstructed corpus are separately and publicly deposited on Zenodo: doi.org/10.5281/zenodo.22143353. No analytic code was developed for this review because no quantitative synthesis was performed.
Acknowledgments
During the preparation of this manuscript, the authors used a generative artificial intelligence tool to produce the illustrative healthcare IoT dependency figure in Section 4.5 from a text prompt describing the depicted scenario. The authors reviewed the resulting image for accuracy and consistency with the scenario described in its caption and in Table 3, and take full responsibility for its content. No other content in this manuscript was produced using generative AI tools.
Conflicts of Interest
The authors declare no competing interests, financial or non-financial, that could have influenced the conduct or reporting of this review.
Abbreviations
The following abbreviations are used in this manuscript:
| IDS | Intrusion Detection System |
| IoT | Internet of Things |
| ML | Machine Learning |
| GAN | Generative Adversarial Network |
| GCN | Graph Convolutional Network |
| RL | Reinforcement Learning |
| RNN | Recurrent Neural Network |
| LSTM | Long Short-Term Memory |
| SVM | Support Vector Machine |
| PCA | Principal Component Analysis |
| XAI | Explainable Artificial Intelligence |
| LIME | Local Interpretable Model-agnostic Explanations |
| SHAP | SHapley Additive exPlanations |
| PRISMA | Preferred Reporting Items for Systematic Reviews and Meta-Analyses |
| OSF | Open Science Framework |
| GDPR | General Data Protection Regulation |
| NIS2 | Network and Information Security Directive 2 |
| CRA | Cyber Resilience Act |
| ETSI | European Telecommunications Standards Institute |
| NIST | National Institute of Standards and Technology |
References
- Al-Fuqaha, A.; Guizani, M.; Mohammadi, M.; Aledhari, M.; Ayyash, M. Internet of things: A survey on enabling technologies, protocols, and applications. IEEE Commun. Surv. Tutor. 2015, 17, 2347–2376. [Google Scholar] [CrossRef] [Scilit]
- Kassab, W.A.; Darabkh, K.A. A–Z survey of Internet of Things: Architectures, protocols, applications, recent advances, future directions and recommendations. J. Netw. Comput. Appl. 2020, 163, 102663. [Google Scholar] [CrossRef] [Scilit]
- Ragothaman, K.; Wang, Y.; Rimal, B.; Lawrence, M. Access control for IoT: A survey of existing research, dynamic policies and future directions. Sensors 2023, 23, 1805. [Google Scholar] [CrossRef] [Scilit]
- Xiao, L.; Wan, X.; Dai, C.; Du, X.; Chen, X.; Guizani, M. Security in mobile edge caching with reinforcement learning. IEEE Wirel. Commun. 2018, 25, 116–122. [Google Scholar] [CrossRef] [Scilit]
- Goodfellow, I.; Pouget-Abadie, J.; Mirza, M.; Xu, B.; Warde-Farley, D.; Ozair, S.; Courville, A.; Bengio, Y. Generative adversarial nets. Adv. Neural Inf. Process. Syst. 2014, 27, 2672–2680. [Google Scholar]
- Kipf, T.N.; Welling, M. Semi-supervised classification with graph convolutional networks. arXiv 2016, arXiv:1609.02907. [Google Scholar]
- Tian, J.; Zhu, H. Evaluating the efficacy of AI-driven intrusion detection systems in IoT: A review of performance metrics and cybersecurity threats. PeerJ Comput. Sci. 2025, 11, e3352. [Google Scholar] [CrossRef] [Scilit]
- Ogunseyi, T.B.; Thiyagarajan, G.; He, H.; Bist, V.; Du, Z. Performance Analysis of Explainable Deep Learning-Based Intrusion Detection Systems for IoT Networks: A Systematic Review. Sensors 2026, 26, 363. [Google Scholar] [CrossRef] [Scilit]
- Hamdi, D.A.; Bahaa-Eldin, A.M.; Sobh, M.A. A systematic literature review on deep learning-driven IDS for software-defined WSN. J. Wirel. Commun. Netw. 2026, 2026, 51. [Google Scholar] [CrossRef] [Scilit]
- Alauthman, M.; Aslam, N.; Al-Qerem, A.; Aldweesh, A.; Sureephong, P. Generative Adversarial Networks for Intrusion Detection Systems: A Comprehensive Survey of Applications, Challenges, and Research Directions. Arab. J. Sci. Eng. 2026, 51, 179–203. [Google Scholar] [CrossRef] [Scilit]
- Mallidi, S.K.R.; Ramisetty, R.R. Optimizing Intrusion Detection for IoT: A Systematic Review of Machine Learning and Deep Learning Approaches with Feature Selection and Data Balancing. WIREs Data Min. Knowl. Discov. 2025, 15, e70008. [Google Scholar] [CrossRef] [Scilit]
- Weiser, M. The Computer for the 21st Century. Sci. Am. 1991, 265, 94–104. [Google Scholar] [CrossRef] [Scilit]
- Ashton, K. That ‘Internet of Things’ Thing. RFID J. 2009, 22, 97–114. [Google Scholar]
- Siwakoti, Y.R.; Bhurtel, M.; Rawat, D.B.; Oest, A.; Johnson, R.C. Advances in IoT security: Vulnerabilities, enabled criminal services, attacks and countermeasures. IEEE Internet Things J. 2023, 10, 11224–11239. [Google Scholar] [CrossRef] [Scilit]
- Zhao, J.; Hu, H.; Huang, F.; Guo, Y.; Liao, L. Authentication technology in Internet of Things and privacy security issues in typical application scenarios. Electronics 2023, 12, 1812. [Google Scholar] [CrossRef] [Scilit]
- Fabrègue, B.F.; Bogoni, A. Privacy and security concerns in the smart city. Smart Cities 2023, 6, 586–613. [Google Scholar] [CrossRef] [Scilit]
- Catuogno, L.; Galdi, C. Secure firmware update: Challenges and solutions. Cryptography 2023, 7, 30. [Google Scholar] [CrossRef] [Scilit]
- Page, M.J.; McKenzie, J.E.; Bossuyt, P.M.; Boutron, I.; Hoffmann, T.C.; Mulrow, C.D.; Shamseer, L.; Tetzlaff, J.M.; Akl, E.A.; Brennan, S.E.; et al. The PRISMA 2020 statement: An updated guideline for reporting systematic reviews. BMJ 2021, 372, n71. [Google Scholar] [CrossRef] [Scilit]
- Kitchenham, B.; Charters, S. Guidelines for performing Systematic Literature Reviews in Software Engineering; EBSE Technical Report EBSE-2007-01; Keele University: Keele, UK; University of Durham: Durham, UK, 2007. [Google Scholar]
- Moher, D.; Liberati, A.; Tetzlaff, J.; Altman, D.G.; The PRISMA Group. Preferred reporting items for systematic reviews and meta-analyses: The PRISMA statement. BMJ 2009, 339, b2535. [Google Scholar]
- Haddaway, N.R.; Page, M.J.; Pritchard, C.C.; McGuinness, L.A. PRISMA2020: An R package and Shiny app for producing PRISMA 2020-compliant flow diagrams, with interactivity for optimised digital transparency and Open Synthesis. Campbell Syst. Rev. 2022, 18, e1230. [Google Scholar] [CrossRef] [Scilit]
- Yang, Y.; Nan, F.; Yang, P.; Meng, Q.; Xie, Y.; Zhang, D.; Muhammad, K. GAN-based semi-supervised learning approach for clinical decision support in health-IoT platform. IEEE Access 2019, 7, 8048–8057. [Google Scholar] [CrossRef] [Scilit]
- Mir, A.A.; Zuhairi, M.F.; Musa, S.M. Graph anomaly detection with graph convolutional networks. Int. J. Adv. Comput. Sci. Appl. 2023, 14, 601. [Google Scholar] [CrossRef] [Scilit]
- Kaur, P.; Kumar, R.; Kumar, M. A healthcare monitoring system using random forest and Internet of Things (IoT). Multimed. Tools Appl. 2019, 78, 19905–19916. [Google Scholar] [CrossRef] [Scilit]
- Yosuf, B.A.; Musa, M.; Elgorashi, T.; Elmirghani, J. Energy efficient distributed processing for IoT. IEEE Access 2020, 8, 161080–161108. [Google Scholar] [CrossRef] [Scilit]
- Ouafiq, E.M.; Saadane, R.; Chehri, A. Data management and integration of low power consumption embedded devices IoT for transforming smart agriculture into actionable knowledge. Agriculture 2022, 12, 329. [Google Scholar] [CrossRef] [Scilit]
- Aly, M.; Khomh, F.; Guéhéneuc, Y.G.; Washizaki, H.; Yacout, S. Is fragmentation a threat to the success of the Internet of Things? IEEE Internet Things J. 2018, 6, 472–487. [Google Scholar] [CrossRef] [Scilit]
- Tawalbeh, L.A.; Muheidat, F.; Tawalbeh, M.; Quwaider, M. IoT privacy and security: Challenges and solutions. Appl. Sci. 2020, 10, 4102. [Google Scholar] [CrossRef] [Scilit]
- Khraisat, A.; Alazab, A. A critical review of intrusion detection systems in the Internet of Things: Techniques, deployment strategy, validation strategy, attacks, public datasets and challenges. Cybersecurity 2021, 4, 1–27. [Google Scholar] [CrossRef] [Scilit]
- Alwahedi, F.; Aldhaheri, A.; Ferrag, M.A.; Battah, A.; Tihanyi, N. Machine learning techniques for IoT security: Current research and future vision with generative AI and large language models. Internet Things Cyber-Phys. Syst. 2024, 4, 167–185. [Google Scholar] [CrossRef] [Scilit]
- HaddadPajouh, H.; Dehghantanha, A.; Parizi, R.M.; Aledhari, M.; Karimipour, H. A survey on Internet of Things security: Requirements, challenges, and solutions. Internet Things 2021, 14, 100129. [Google Scholar] [CrossRef] [Scilit]
- Baho, S.A.; Abawajy, J. Analysis of Consumer IoT Device Vulnerability Quantification Frameworks. Electronics 2023, 12, 1176. [Google Scholar] [CrossRef] [Scilit]
- Muñoz, D.C.; Valiente, A.D.C. A novel botnet attack detection for IoT networks based on communication graphs. Cybersecurity 2023, 6, 33. [Google Scholar] [CrossRef] [Scilit]
- Shukla, S.; George, J.P.; Tiwari, K.; Kureethara, J.V. Data Security. In Data Ethics and Challenges; Springer: Singapore, 2022; pp. 41–59. [Google Scholar]
- Kang, J.H.; Seo, M. Enhanced authentication for decentralized IoT access control architecture. Cryptography 2023, 7, 42. [Google Scholar] [CrossRef] [Scilit]
- Nadir, I.; Mahmood, H.; Asadullah, G. A taxonomy of IoT firmware security and principal firmware analysis techniques. Int. J. Crit. Infrastruct. Prot. 2022, 38, 100552. [Google Scholar] [CrossRef] [Scilit]
- Kim, J.; Park, J. Enhancing security of web-based IoT services via XSS vulnerability detection. Sensors 2023, 23, 9407. [Google Scholar] [CrossRef] [Scilit]
- Socha, P.; Miškovský, V.; Novotný, M. A comprehensive survey on the non-invasive passive side-channel analysis. Sensors 2022, 22, 8096. [Google Scholar] [CrossRef] [Scilit]
- Kolhar, M.; Aldossary, S.M. A deep learning approach for securing IoT infrastructure with emphasis on smart vertical networks. Designs 2023, 7, 139. [Google Scholar] [CrossRef] [Scilit]
- Sun, B.; Geng, R.; Zhang, L.; Li, S.; Shen, T.; Ma, L. Securing 6G-enabled IoT/IoV networks by machine learning and data fusion. EURASIP J. Wirel. Commun. Netw. 2022, 2022, 113. [Google Scholar] [CrossRef] [Scilit]
- Sáez-de-Cámara, X.; Flores, J.L.; Arellano, C.; Urbieta, A.; Zurutuza, U. Clustered federated learning architecture for network anomaly detection in large scale heterogeneous IoT networks. Comput. Secur. 2023, 131, 1–20. [Google Scholar] [CrossRef] [Scilit]
- Ruzafa-Alcázar, P.; Fernández-Saura, P.; Mármol-Campos, E.; González-Vidal, A.; Hernández-Ramos, J.L.; Bernal-Bernabe, J.; Skarmeta, A.F. Intrusion Detection Based on Privacy-Preserving Federated Learning for the Industrial IoT. IEEE Trans. Ind. Inform. 2023, 19, 1145–1154. [Google Scholar] [CrossRef] [Scilit]
- Taherdoost, H. Security and Internet of Things: Benefits, challenges, and future perspectives. Electronics 2023, 12, 1901. [Google Scholar] [CrossRef] [Scilit]
- Wang, C.; Zhao, S.; Peng, J.; Zhu, J. KVFL: Key-value-based persistent fuzzing for IoT web servers. Comput. J. 2023, bxad110. [Google Scholar]
- Cabaj, K.; Żórawski, P.; Nowakowski, P.; Purski, M.; Mazurczyk, W. Efficient distributed network covert channels for Internet of Things environments. J. Cybersecur. 2020, 6, tyaa018. [Google Scholar] [CrossRef] [Scilit]
- Bourechak, A.; Zedadra, O.; Kouahla, M.N.; Guerrieri, A.; Seridi, H.; Fortino, G. At the confluence of artificial intelligence and edge computing in IoT-based applications: A review and new perspectives. Sensors 2023, 23, 1639. [Google Scholar] [CrossRef] [Scilit]
- Alfonso, I.; Garcés, K.; Castro, H.; Cabot, J. Self-adaptive architectures in IoT systems: A systematic literature review. J. Internet Serv. Appl. 2021, 12, 1–28. [Google Scholar] [CrossRef] [Scilit]
- Almutairi, M.; Sheldon, F.T. IoT–Cloud Integration Security: A Survey of Challenges, Solutions, and Directions. Electronics 2025, 14, 1394. [Google Scholar] [CrossRef] [Scilit]
- Carrillo-Mondéjar, J.; Turtiainen, H.; Costin, A.; Martínez, J.L.; Suarez-Tangil, G. HALE-IoT: HArdeningLEgacy Internet-of-Things devices by retrofitting defensive firmware modifications and implants. IEEE Internet Things J. 2022, 10, 8371–8394. [Google Scholar] [CrossRef] [Scilit]
- Dharini, N.; Shakthi, S.P.; Shruthi, S.S. Botnet attack detection in IoT-based security camera device using principal component analysis with various machine learning algorithms. In Proceedings of the 2nd International Conference on Cognitive and Intelligent Computing (ICCIC 2022), Cognitive Science and Technology; Springer Nature: Singapore, 2023; pp. 653–667. [Google Scholar]
- Vishwakarma, M.; Kesswani, N. DIDS: A deep neural network based real-time intrusion detection system for IoT. Decis. Anal. J. 2022, 5, 100142. [Google Scholar] [CrossRef] [Scilit]
- Alghamdi, R.; Bellaiche, M. An ensemble deep learning based IDS for IoT using Lambda architecture. Cybersecurity 2023, 6, 5. [Google Scholar] [CrossRef] [Scilit]
- Yousuf, O.; Mir, R.N. DDoS attack detection in Internet of Things using recurrent neural network. Comput. Electr. Eng. 2022, 101, 108034. [Google Scholar] [CrossRef] [Scilit]
- Stiawan, D.; Suryani, M.E.; Idris, M.Y.; Aldalaien, M.N.; Alsharif, N.; Budiarto, R. Ping flood attack pattern recognition using a K-means algorithm in an Internet of Things (IoT) network. IEEE Access 2021, 9, 116475–116484. [Google Scholar] [CrossRef] [Scilit]
- Otoum, Y.; Liu, D.; Nayak, A. DL-IDS: A deep learning–based intrusion detection framework for securing IoT. Trans. Emerg. Telecommun. Technol. 2022, 33, e3803. [Google Scholar] [CrossRef] [Scilit]
- Okoli, U.I.; Obi, O.C.; Adewusi, A.O.; Abrahams, T.O. Machine Learning in Cybersecurity: A Review of Threat Detection and Defense Mechanisms. World J. Adv. Res. Rev. 2024, 21, 2286–2295. [Google Scholar] [CrossRef] [Scilit]
- Arshad, J.; Azad, M.A.; Abdeltaif, M.M.; Salah, K. An intrusion detection framework for energy constrained IoT devices. Mech. Syst. Signal Process. 2020, 136, 106436. [Google Scholar] [CrossRef] [Scilit]
- Elluri, L.; Dwivedi, R.; Lee, S.; Li, R. Exploring IoT privacy compliance research: A topic modeling approach. Int. J. Inf. Secur. 2026, 25, 59. [Google Scholar] [CrossRef] [Scilit]
- Zhang, Q.; Chen, B.; Zhang, T.; Cao, K.; Ding, Y.; Gao, T.; Zhao, Z. Generative adversarial network-based anomaly detection and forecasting with unlabeled data for 5G vertical applications. Appl. Sci. 2023, 13, 10745. [Google Scholar] [CrossRef] [Scilit]
- Alabdulwahab, S.; Kim, Y.T.; Seo, A.; Son, Y. Generating synthetic dataset for ML-based IDS using CTGAN and feature selection to protect smart IoT environments. Appl. Sci. 2023, 13, 10951. [Google Scholar] [CrossRef] [Scilit]
- Bagui, S.; Li, K. Resampling imbalanced data for network intrusion detection datasets. J. Big Data 2021, 8, 6. [Google Scholar] [CrossRef] [Scilit]
- Ghallab, H.; Fahmy, H.; Nasr, M. Detection outliers on Internet of Things using big data technology. Egypt. Inform. J. 2020, 21, 131–138. [Google Scholar] [CrossRef] [Scilit]
- Shukla, S.; Hassan, M.F.; Tran, D.C.; Akbar, R.; Paputungan, I.V.; Khan, M.K. Improving latency in Internet-of-Things and cloud computing for real-time data transmission: A systematic literature review (SLR). Clust. Comput. 2023, 26, 2657–2680. [Google Scholar] [CrossRef] [Scilit]
- Douiba, M.; Benkirane, S.; Guezzaz, A.; Azrour, M. An improved anomaly detection model for IoT security using decision tree and gradient boosting. J. Supercomput. 2023, 79, 3392–3411. [Google Scholar] [CrossRef] [Scilit]
- Ioannou, C.; Vassiliou, V. Network attack classification in IoT using support vector machines. J. Sens. Actuator Netw. 2021, 10, 58. [Google Scholar] [CrossRef] [Scilit]
- Tien, C.W.; Huang, T.Y.; Chen, P.C.; Wang, J.H. Using autoencoders for anomaly detection and transfer learning in IoT. Computers 2021, 10, 88. [Google Scholar] [CrossRef] [Scilit]
- Almiani, M.; AbuGhazleh, A.; Mughaid, A.; Jararweh, Y. Botnet detection using label propagation and batch K-means clustering for securing IoT networks. In Proceedings of the 2023 Eighth International Conference on Fog and Mobile Edge Computing (FMEC), Tartu, Estonia, 18–20 September 2023; pp. 167–174. [Google Scholar]
- Xu, R.; Cheng, Y.; Liu, Z.; Xie, Y.; Yang, Y. Improved long short-term memory based anomaly detection with concept drift adaptive method for supporting IoT services. Future Gener. Comput. Syst. 2020, 112, 228–242. [Google Scholar] [CrossRef] [Scilit]
- Sliwa, B.; Piatkowski, N.; Wietfeld, C. LIMITS: Lightweight machine learning for IoT systems with resource limitations. In Proceedings of the 2020 IEEE International Conference on Communications (ICC), Dublin, Ireland, 7–11 June 2020; pp. 1–7. [Google Scholar]
- Zhang, Y.; Liu, Q. On IoT intrusion detection based on data augmentation for enhancing learning on unbalanced samples. Future Gener. Comput. Syst. 2022, 133, 213–227. [Google Scholar] [CrossRef] [Scilit]
- Gugueoth, V.; Safavat, S.; Shetty, S.; Rawat, D. A review of IoT security and privacy using decentralized blockchain techniques. Comput. Sci. Rev. 2023, 50, 100585. [Google Scholar] [CrossRef] [Scilit]
- Akuthota, U.C.; Bhargava, L. Transformer Based Intrusion Detection for IoT Networks. IEEE Internet Things J. 2025, 12, 6062–6067. [Google Scholar] [CrossRef] [Scilit]
- He, M.S.; Wang, X.J.; Wei, P.; Yang, L.; Teng, Y.L.; Lyu, R.J. Reinforcement learning meets network intrusion detection: A transferable and adaptable framework for anomaly behavior identification. IEEE Trans. Netw. Serv. Manag. 2024, 21, 2477–2492. [Google Scholar] [CrossRef] [Scilit]
- Yao, W.; Shi, H.; Zhao, H. Scalable anomaly-based intrusion detection for secure Internet of Things using generative adversarial networks in fog environment. J. Netw. Comput. Appl. 2023, 214, 103622. [Google Scholar] [CrossRef] [Scilit]
- Gaspar, D.; Silva, P.; Silva, C. Explainable AI for Intrusion Detection Systems: LIME and SHAP Applicability on Multi-Layer Perceptron. IEEE Access 2024, 12, 30164–30175. [Google Scholar] [CrossRef] [Scilit]
- Sharma, B.; Sharma, L.; Lal, C.; Roy, S. Explainable artificial intelligence for intrusion detection in IoT networks: A deep learning based approach. Expert Syst. Appl. 2024, 238, 121751. [Google Scholar] [CrossRef] [Scilit]
- ETSI EN 303 645; Cyber Security for Consumer Internet of Things: Baseline Requirements. European Telecommunications Standards Institute: Sophia Antipolis, France, 2024.
- Fagan, M.; Megas, K.; Scarfone, K.; Smith, M. IoT Device Cybersecurity Capability Core Baseline; NIST Interagency Report 1327 8259A; National Institute of Standards and Technology: Gaithersburg, MD, USA, 2020. [CrossRef] [Scilit]
- Ahmad, J.; Latif, S.; Khan, I.U.; Alshehri, M.S.; Khan, M.S.; Alasbali, N.; Jiang, W. An interpretable deep learning framework for intrusion detection in industrial Internet of Things. Internet Things 2025, 33, 101681. [Google Scholar] [CrossRef] [Scilit]
- Benaddi, H.; Jouhari, M.; Ibrahimi, K.; Ben Othman, J.; Amhoud, E.M. Anomaly Detection in Industrial IoT Using Distributional Reinforcement Learning and Generative Adversarial Networks. Sensors 2022, 22, 8085. [Google Scholar] [CrossRef] [Scilit]
- Lim, W.; Yong, K.S.C.; Lau, B.T.; Tan, C.C.L. Future of generative adversarial networks (GAN) for anomaly detection in network security: A review. Comput. Secur. 2024, 139, 103733. [Google Scholar] [CrossRef] [Scilit]
- Grosse, K.; Manoharan, P.; Papernot, N.; Backes, M.; McDaniel, P. On the (Statistical) Detection of Adversarial Examples. arXiv 2017, arXiv:1702.06280. [Google Scholar]
- He, K.; Kim, D.D.; Asghar, M.R. Adversarial Machine Learning for Network Intrusion Detection Systems: A Comprehensive Survey. IEEE Commun. Surv. Tutor. 2023, 25, 538–566. [Google Scholar] [CrossRef] [Scilit]
- Khazane, H.; Ridouani, M.; Salahdine, F.; Kaabouch, N. A Holistic Review of Machine Learning Adversarial Attacks in IoT Networks. Future Internet 2024, 16, 32. [Google Scholar] [CrossRef] [Scilit]
- Tcydenova, E.; Kim, T.W.; Lee, C.; Park, J.H. Detection of adversarial attacks in AI-based intrusion detection systems using explainable AI. Hum.-Centric Comput. Inf. Sci. 2021, 11, 1–14. [Google Scholar] [CrossRef]
- Merzouk, M.A.; Cuppens, F.; Boulahia-Cuppens, N.; Yaich, R. A Deeper Analysis of Adversarial Examples in Intrusion Detection. In Risks and Security of Internet and Systems (CRiSIS 2020); Lecture Notes in Computer Science; Springer: Berlin/Heidelberg, Germany, 2021; Volume 12528, pp. 67–84. [Google Scholar] [CrossRef] [Scilit]
- Haroon, M.S.; Ali, H.M. Adversarial Training Against Adversarial Attacks for Machine Learning-Based Intrusion Detection Systems. Comput. Mater. Contin. 2022, 73, 3513–3527. [Google Scholar] [CrossRef] [Scilit]
- Jmila, H.; Khedher, M.I. Adversarial machine learning for network intrusion detection: A comparative study. Comput. Netw. 2022, 214, 109073. [Google Scholar] [CrossRef] [Scilit]
- Wu, Z.; Pan, S.; Chen, F.; Long, G.; Zhang, C.; Yu, P.S. A Comprehensive Survey on Graph Neural Networks. IEEE Trans. Neural Netw. Learn. Syst. 2021, 32, 4–24. [Google Scholar] [CrossRef] [Scilit]
- Ying, R.; You, J.; Morris, C.; Ren, X.; Hamilton, W.L.; Leskovec, J. Hierarchical Graph Representation Learning with Differentiable Pooling. In Proceedings of the Advances in Neural Information Processing Systems 31 (NeurIPS 2018), Montréal, QC, Canada, 3–8 December 2018; Volume 31, pp. 4805–4815. [Google Scholar]
- Wu, J.; Dai, H.; Wang, Y.; Ye, K.; Xu, C. Heterogeneous Domain Adaptation for IoT Intrusion Detection: A Geometric Graph Alignment Approach. IEEE Internet Things J. 2023, 10, 10764–10777. [Google Scholar] [CrossRef] [Scilit]
- Mahadik, S.; Pawar, P.M.; Muthalagu, R. Efficient Intelligent Intrusion Detection System for Heterogeneous Internet of Things (HetIoT). J. Netw. Syst. Manag. 2023, 31, 2. [Google Scholar] [CrossRef] [Scilit]
- Hong, S.; Huang, Y.; Jiang, W.; Zhang, J.; Wang, J.; Jiao, R. BGA: A noise-immune neural distillation framework for malicious signature extraction in high-entropy encrypted flows. Inf. Process. Manag. 2027, 64, 105040. [Google Scholar] [CrossRef] [Scilit]
- European Union. Regulation (EU) 2016/679 of the European Parliament and of the Council of 27 April 2016 on the protection of natural persons with regard to the processing of personal data and on the free movement of such data (General Data Protection Regulation). Off. J. Eur. Union 2016, L 119, 1–88. [Google Scholar]
- European Union. Directive (EU) 2022/2555 of the European Parliament and of the Council of 14 December 2022 on measures for a high common level of cybersecurity across the Union (NIS2 Directive). Off. J. Eur. Union 2022, L 333, 80–152. [Google Scholar]
- European Union. Regulation (EU) 2024/2847 of the European Parliament and of the Council of 23 October 2024 on horizontal cybersecurity requirements for products with digital elements (Cyber Resilience Act). Off. J. Eur. Union 2024. [Google Scholar]
- Product Security and Telecommunications Infrastructure Act 2022, c. 46, United Kingdom, Royal Assent 6 December 2022. Available online: https://www.legislation.gov.uk/ukpga/2022/46/contents (accessed on 25 May 2026).
- Walling, S.; Lodh, S. An Extensive Review of Machine Learning and Deep Learning Techniques on Network Intrusion Detection for IoT. Trans. Emerg. Telecommun. Technol. 2025, 36, e70064. [Google Scholar] [CrossRef] [Scilit]
- Umar, A.; Jordanov, I. Anomaly Detection in IoT Environment Using Machine Learning: A Survey. IEEE Internet Things J. 2026, 13, 20477–20497. [Google Scholar] [CrossRef] [Scilit]
- Alfahaid, A.; Alalwany, E.; Almars, A.M.; Alharbi, F.; Atlam, E.; Mahgoub, I. Machine Learning-Based Security Solutions for IoT Networks: A Comprehensive Survey. Sensors 2025, 25, 3341. [Google Scholar] [CrossRef] [Scilit]
- Kumar, A.; Arif, H.; Mazhar, T.; Aldehim, G.; Khan, M.A.; Hamam, H. Deep Learning Approaches for Intrusion Detection in IoT Networks: A PRISMA-Guided Systematic Review With Descriptive Meta-Analysis. IET Netw. 2026, 15, e70030. [Google Scholar] [CrossRef] [Scilit]
- Bankó, M.B.; Dyszewski, S.; Králová, M.; Limpek, M.B.; Papaioannou, M.; Choudhary, G.; Dragoni, N. Advancements in Machine Learning-Based Intrusion Detection in IoT: Research Trends and Challenges. Algorithms 2025, 18, 209. [Google Scholar] [CrossRef] [Scilit]
- Mambwe, H.; Chavula, P.; Kayusi, F.; Lungu, G.; Uwimbabazi, A. Machine learning and AI for security mechanisms: A Systematic Literature Review Using a PRISMA Framework. LatIA 2025, 3, 331. [Google Scholar] [CrossRef] [Scilit]
- Patil, J.J.; Solanki, R. Advances in Adaptive Machine Learning Algorithms for Enhanced Security in IoT Networks: A Comprehensive Review. J. Comput. Mech. Manag. 2026, 5, 50–75. [Google Scholar] [CrossRef] [Scilit]
- Mohamad, R.; Mohamad, M.A.; Ab Razak, M.F.; Riadi, I.; Winiarti, S.; Yuliansyah, H. Deep Learning and Optimization-Driven Intrusion Detection Systems for Internet of Things Security: A Systematic Literature Review. Int. J. Adv. Comput. Sci. Appl. 2026, 17. [Google Scholar] [CrossRef] [Scilit]
- Zmaimita, H.; Madani, A.; Zine-Dine, K. Machine and Deep Learning for Intrusion Detection: A PRISMA-Guided Systematic Review of Recent Advances. Regist. J. Ilm. Teknol. Sist. Inf. 2025, 11, 66–74. [Google Scholar] [CrossRef] [Scilit]
- Munaye, Y.Y.; Gebeyehu, A.D.; Tai, L.-C.; Abebe, Z.A.; Workneh, A.B.; Tarekegn, R.B.; Chekol, Y.B.; Tarekegn, G.B. Machine Learning-Driven Intrusion Detection for Securing IoT-Based Wireless Sensor Networks. Future Internet 2026, 18, 113. [Google Scholar] [CrossRef] [Scilit]
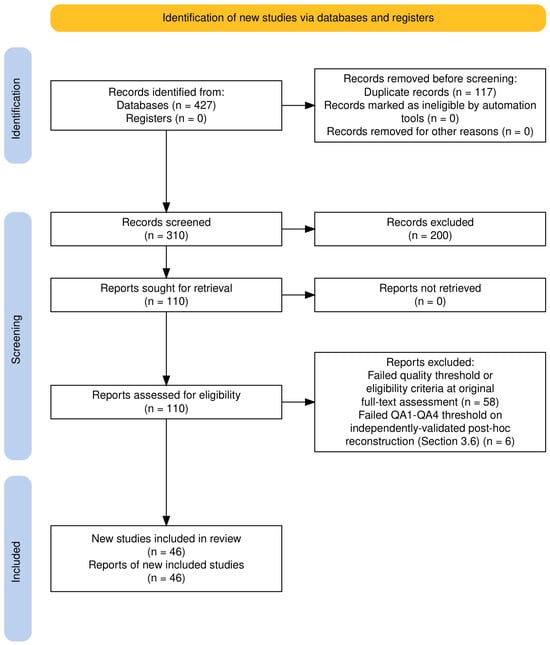
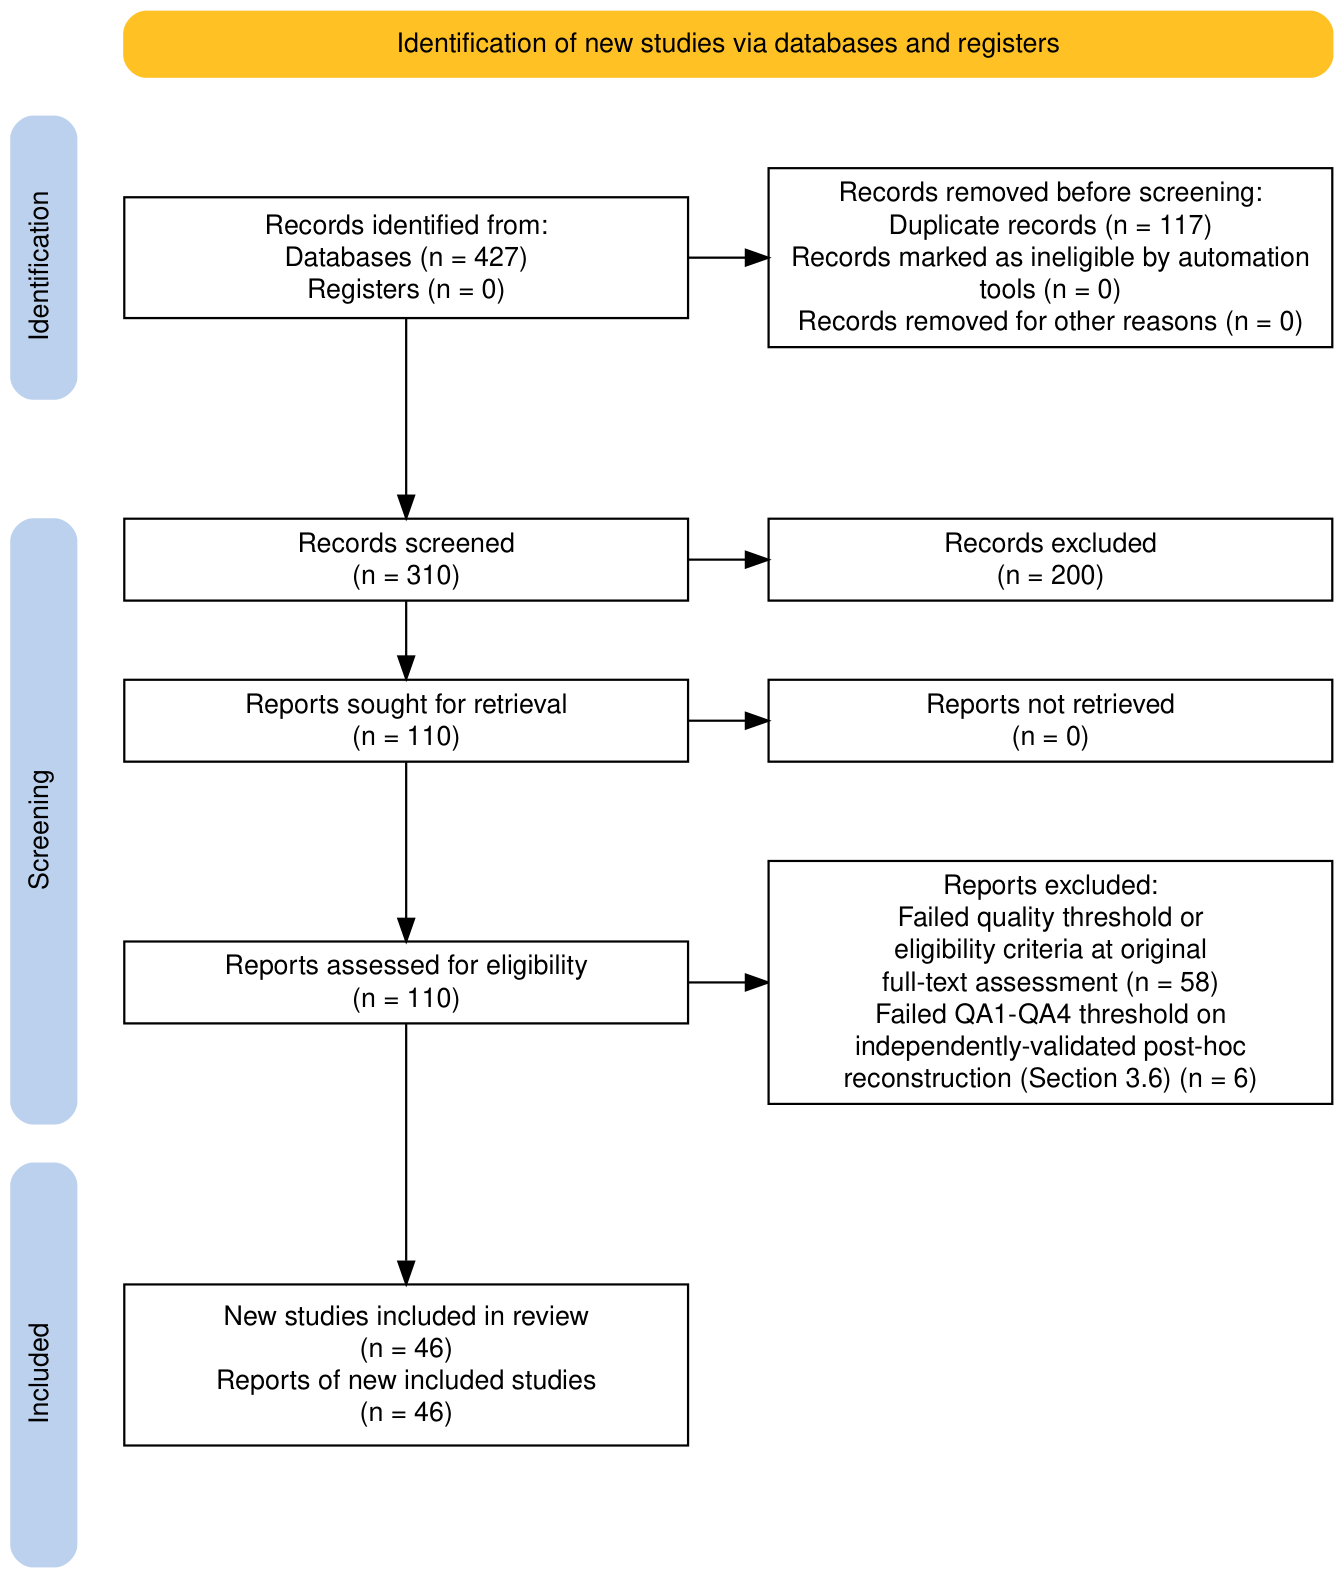
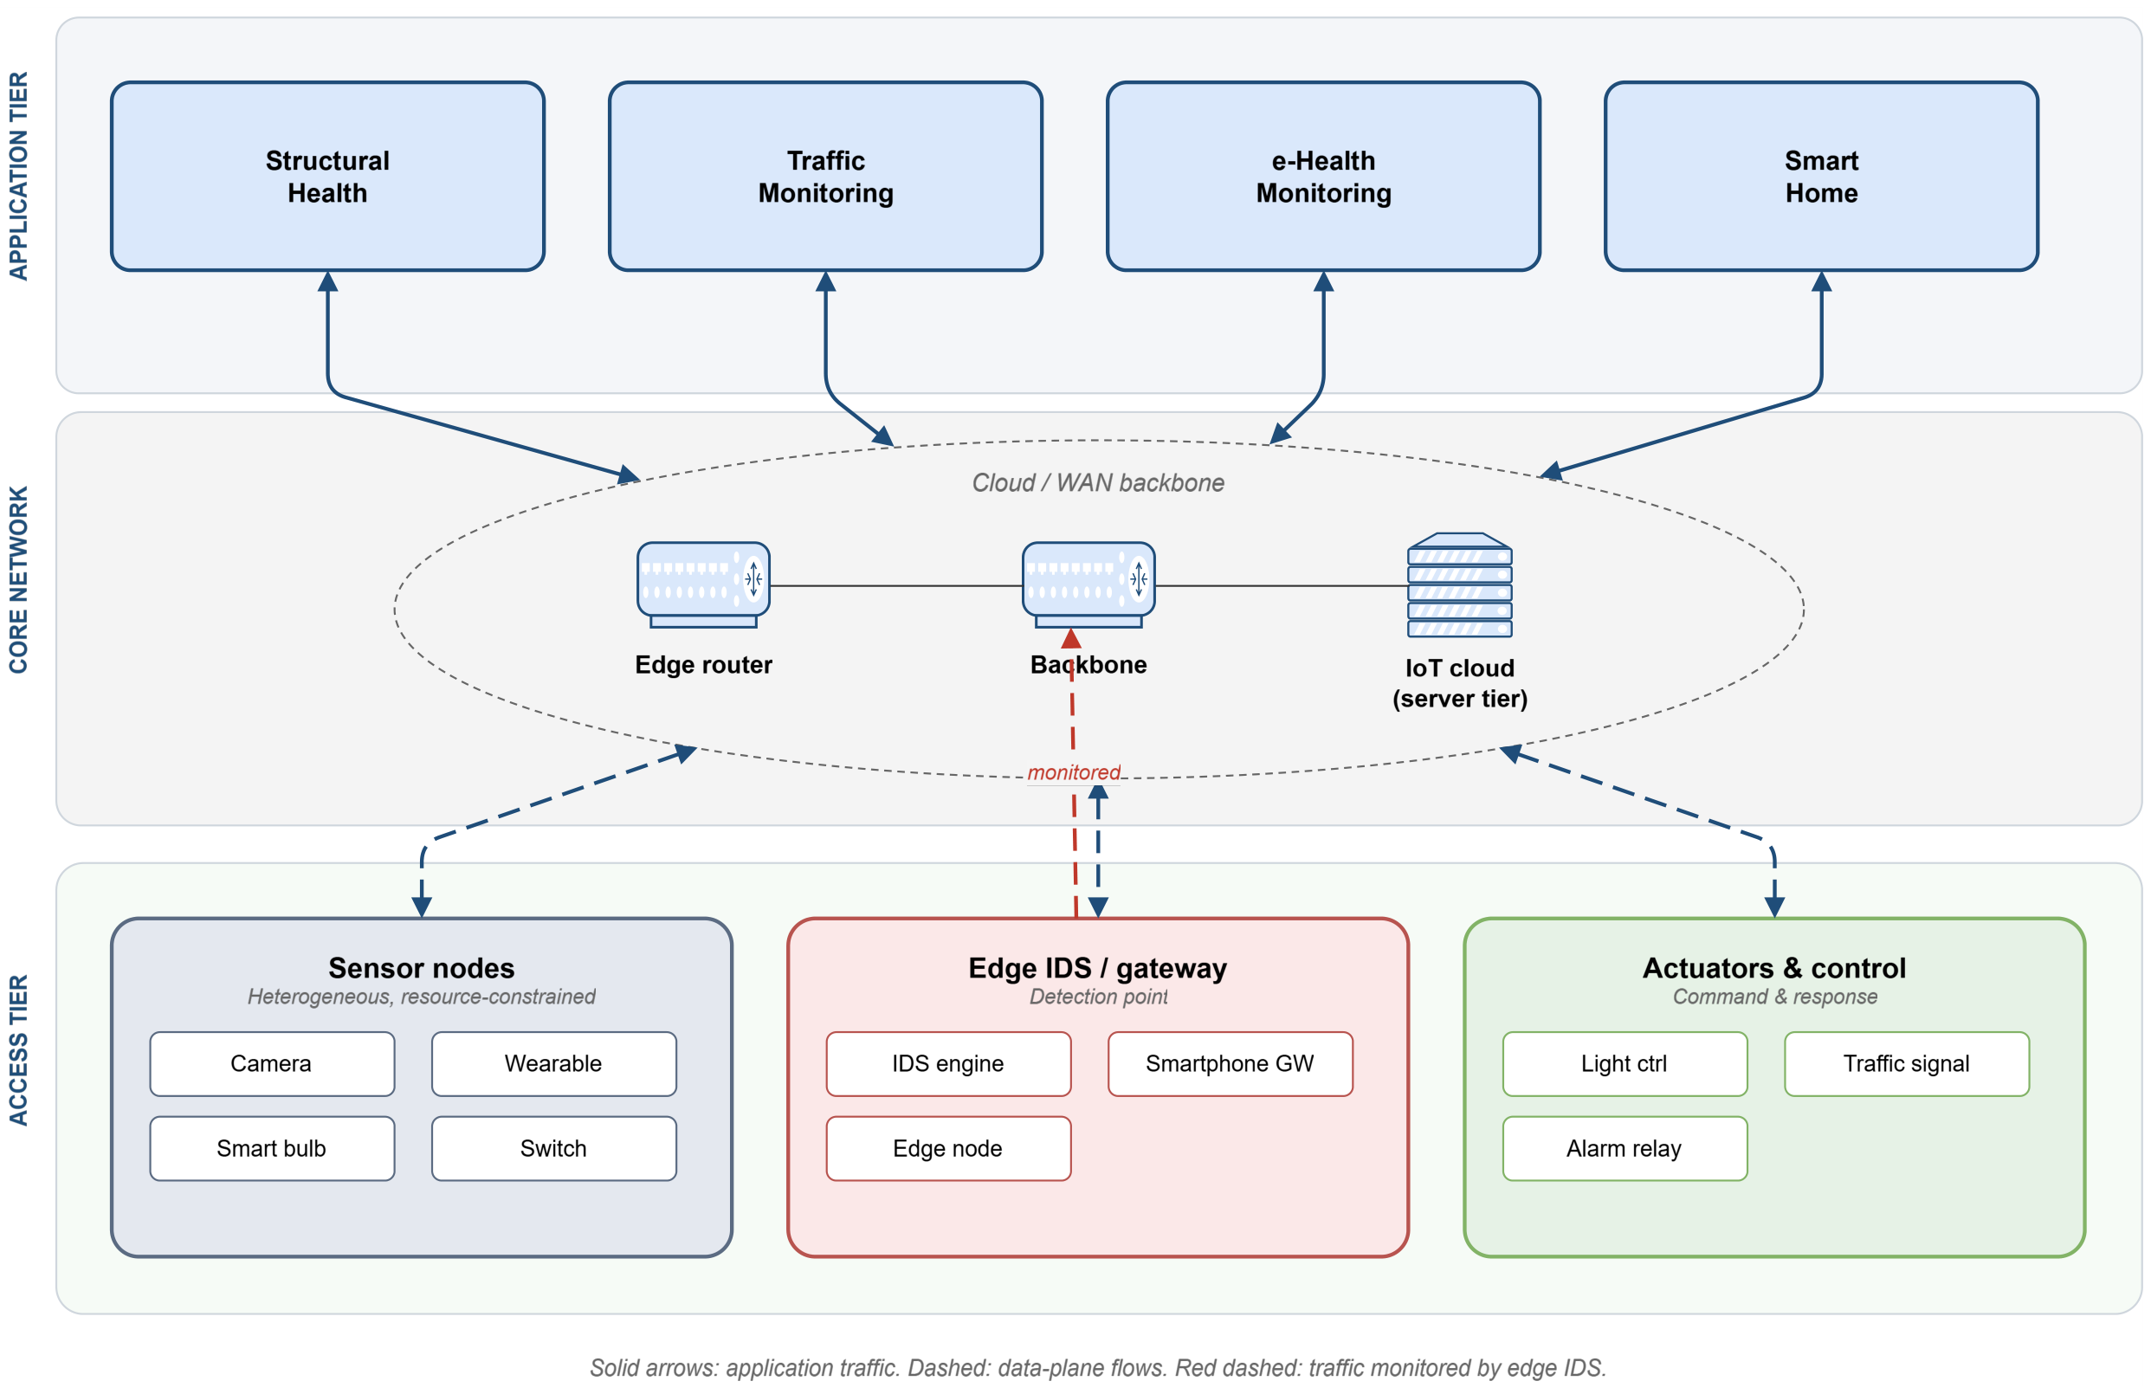
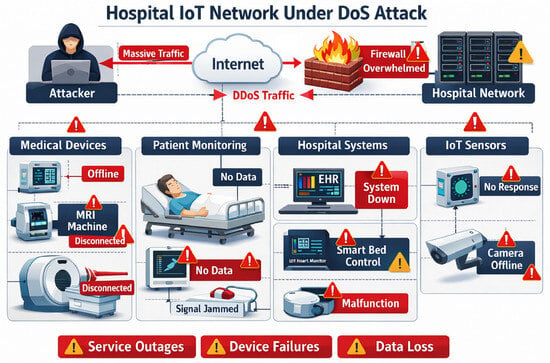
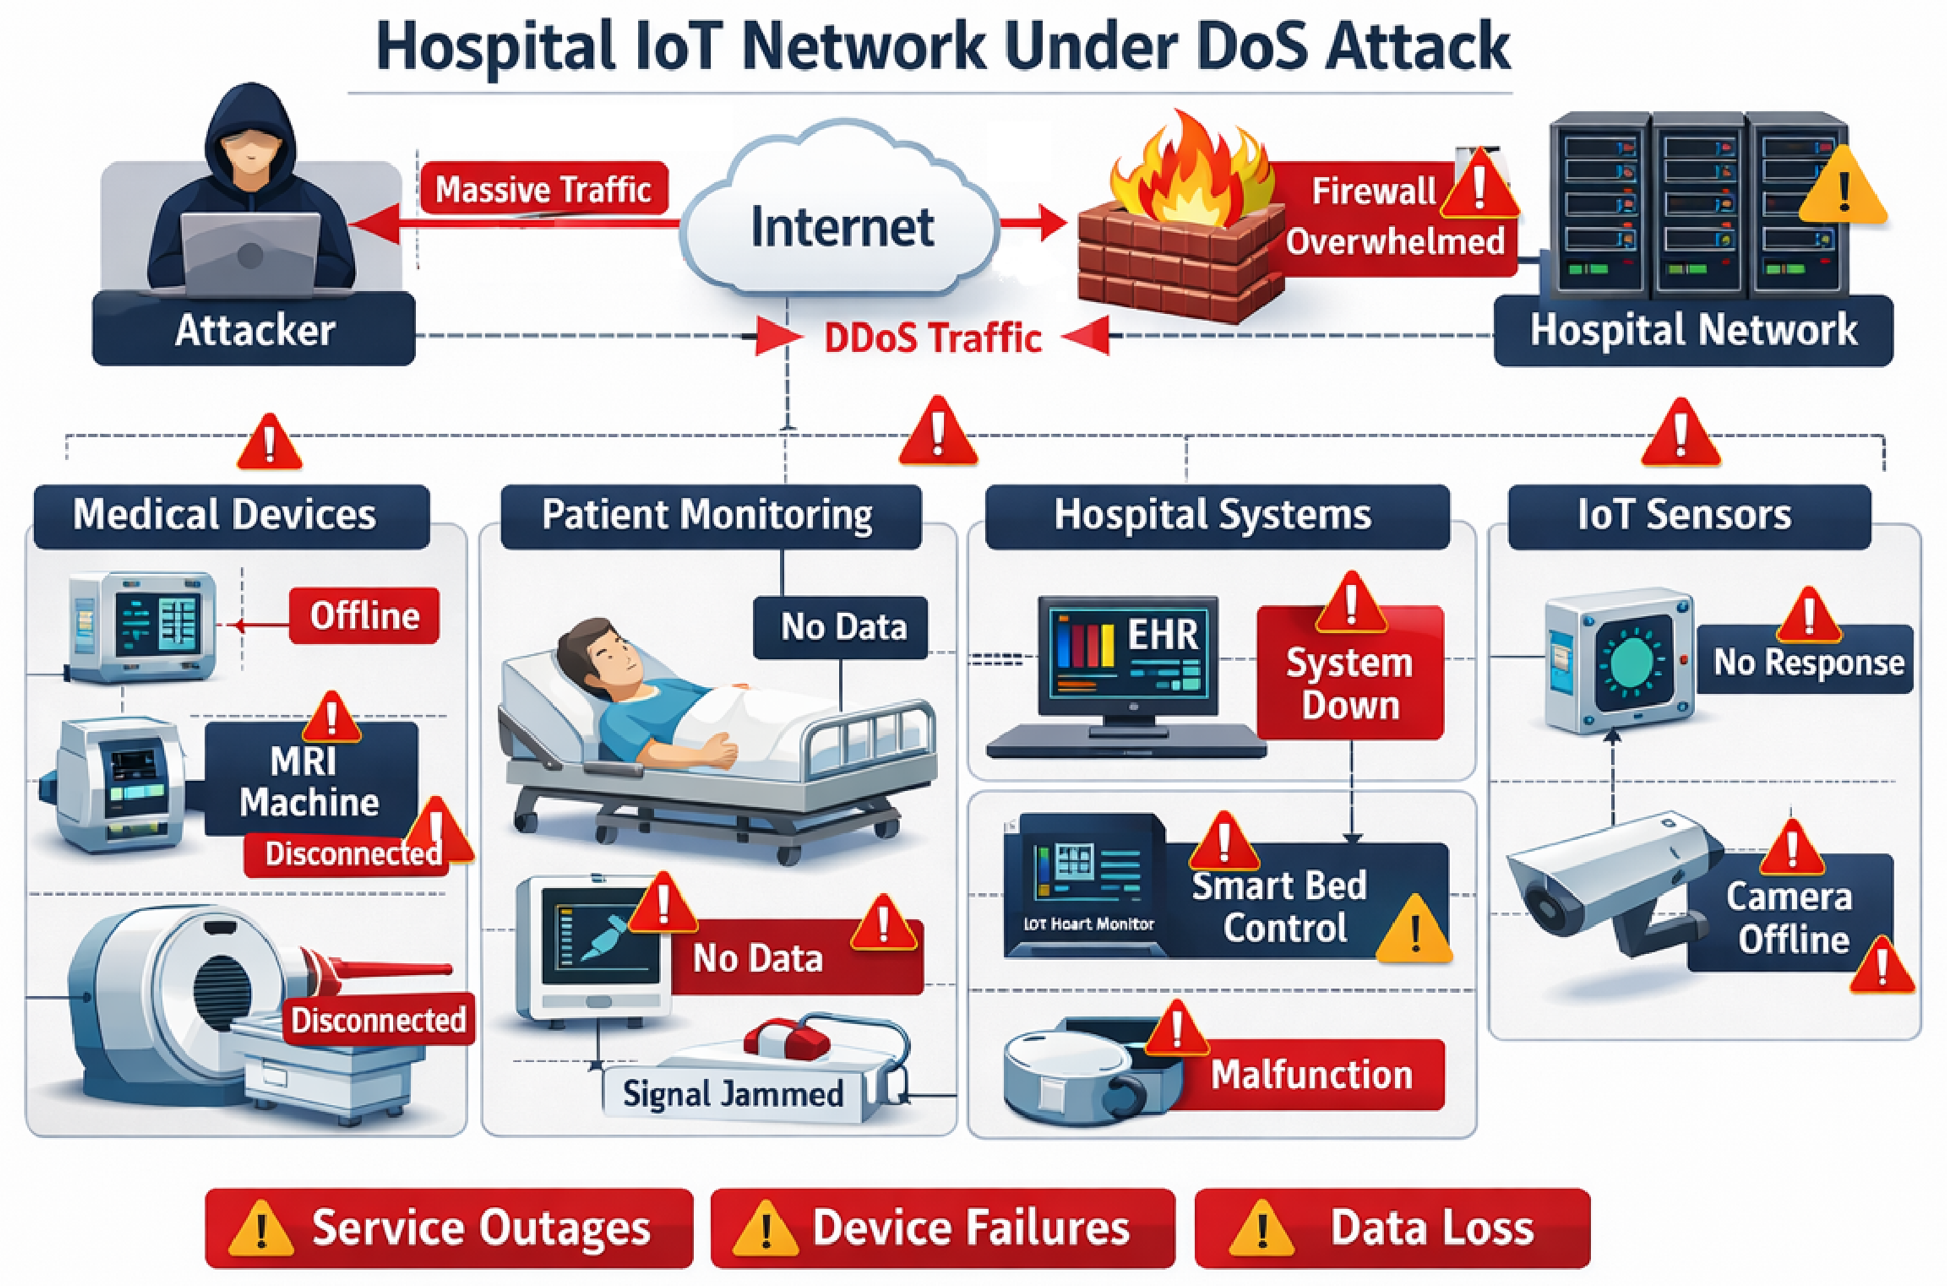
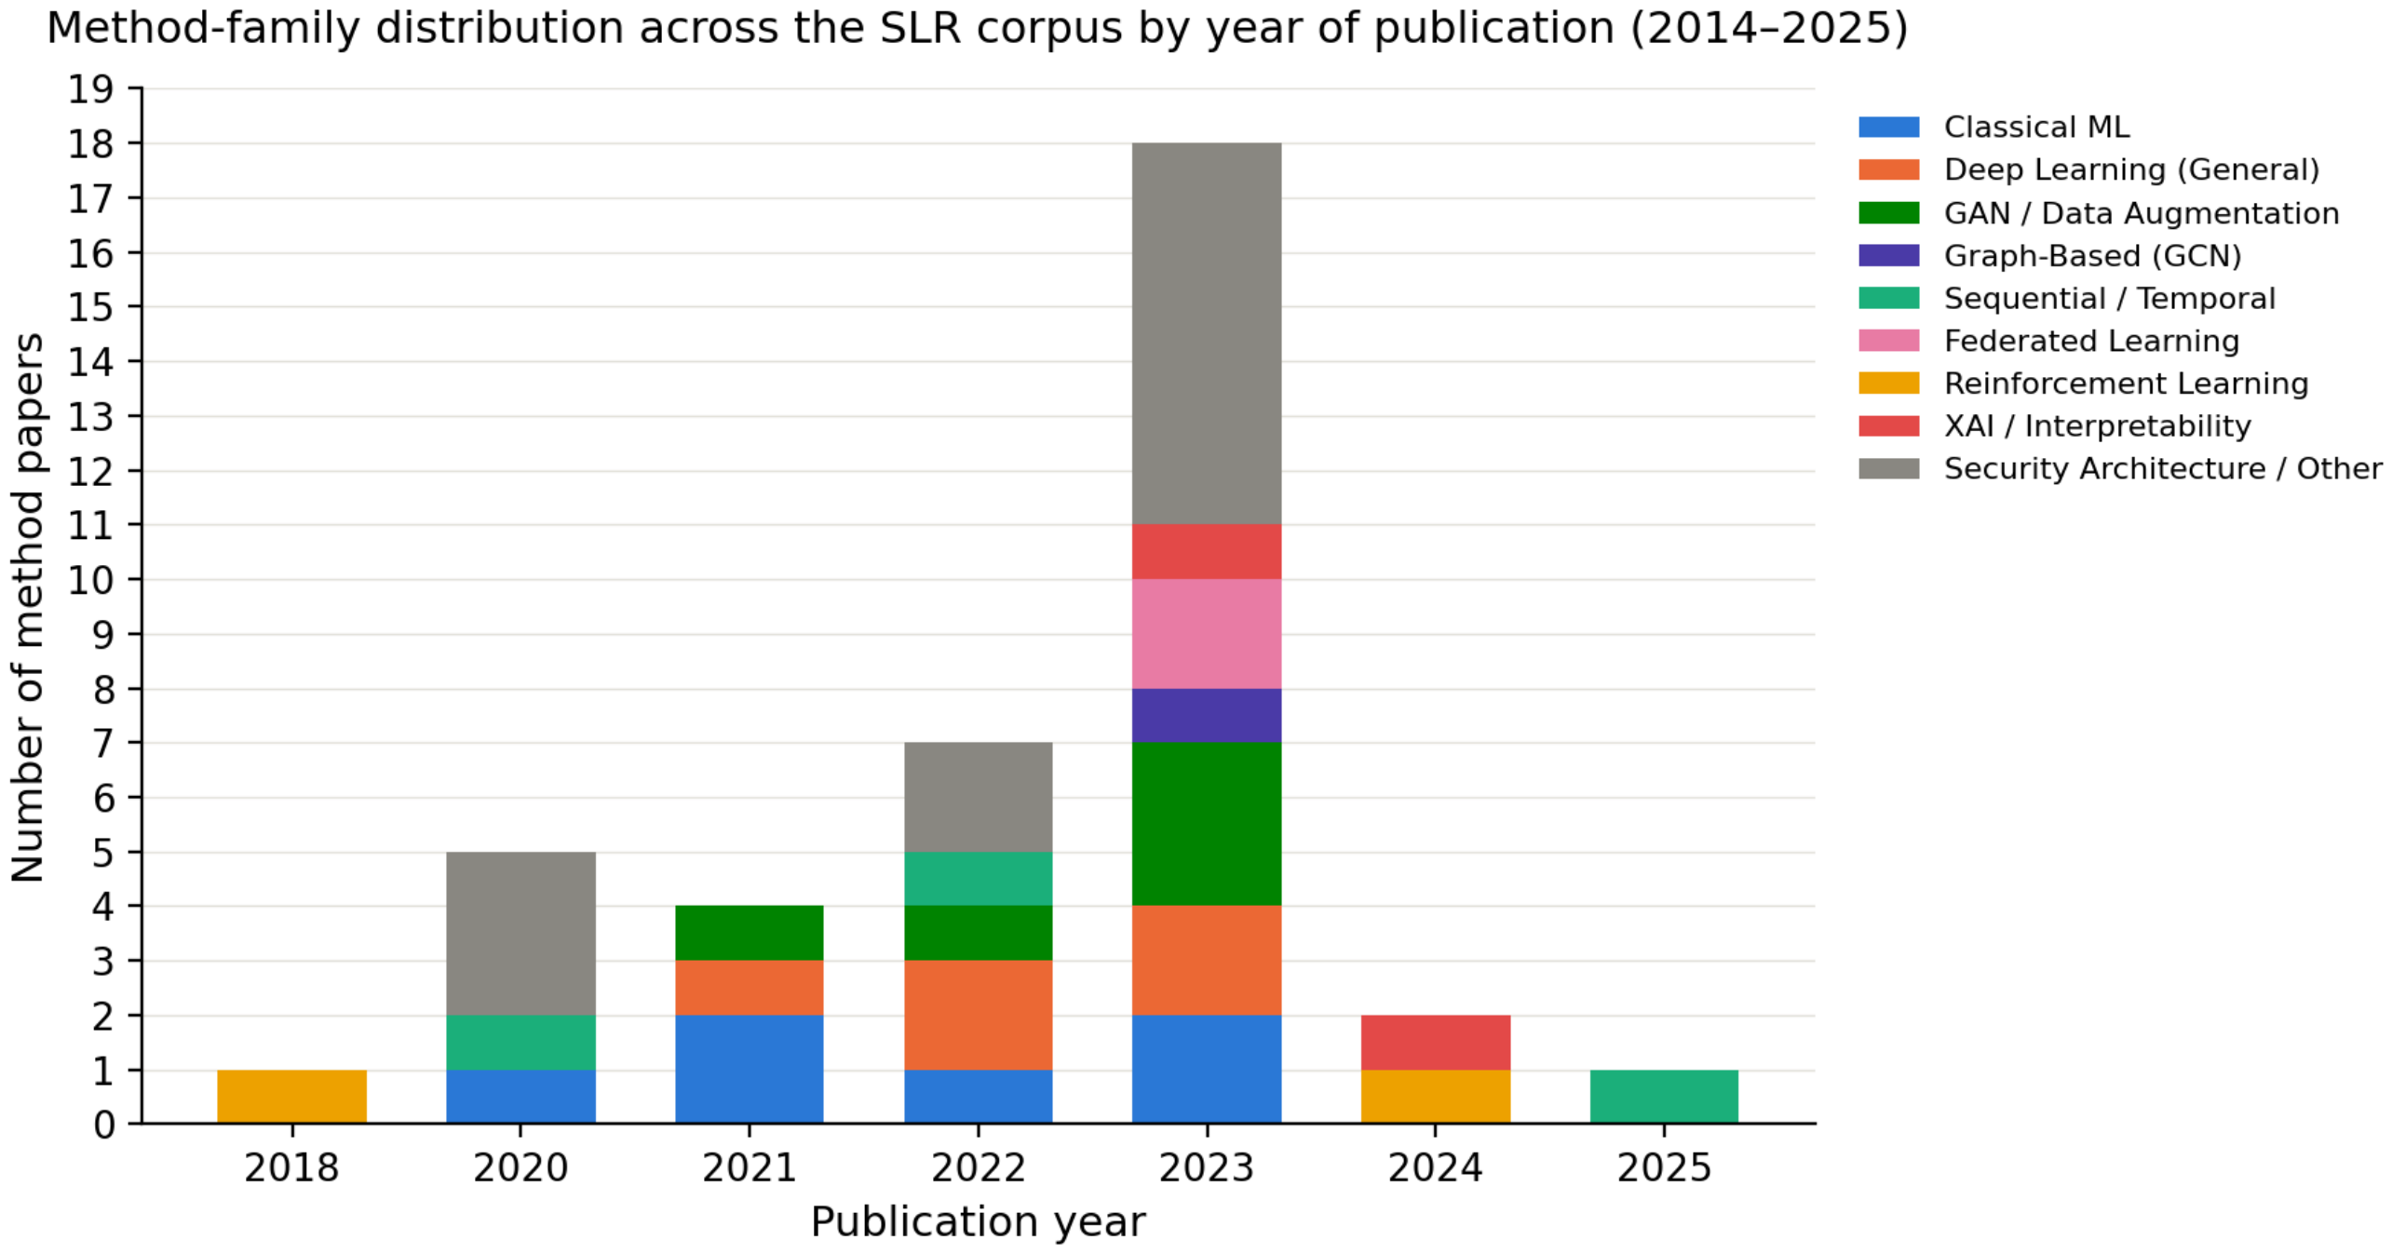

Disclaimer/Publisher’s Note: The statements, opinions and data contained in all publications are solely those of the individual author(s) and contributor(s) and not of MDPI and/or the editor(s). MDPI and/or the editor(s) disclaim responsibility for any injury to people or property resulting from any ideas, methods, instructions or products referred to in the content. |
© 2026 by the authors. Licensee MDPI, Basel, Switzerland. This article is an open access article distributed under the terms and conditions of the Creative Commons Attribution (CC BY) license.