1. Introduction
The whole world has become more digitized. According to the World Bank, high-income countries in 2000 had 30% of their population actively using the internet. In 2022 this number skyrocketed to 91% [
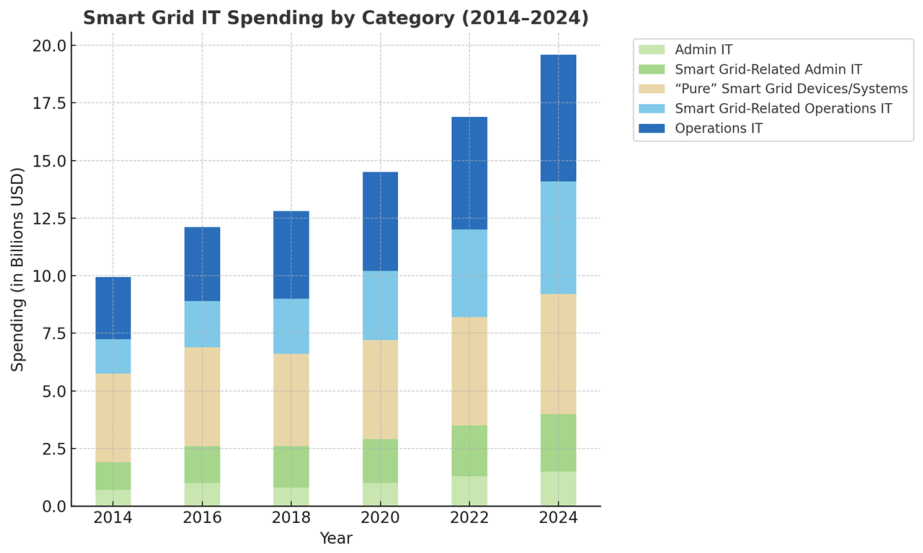
1]. Power systems are no exception to this trend. Smart grid expenses have increased by over 10 billion in the last 12 years according to the US Department of Energy (See
Figure 1) [
1].
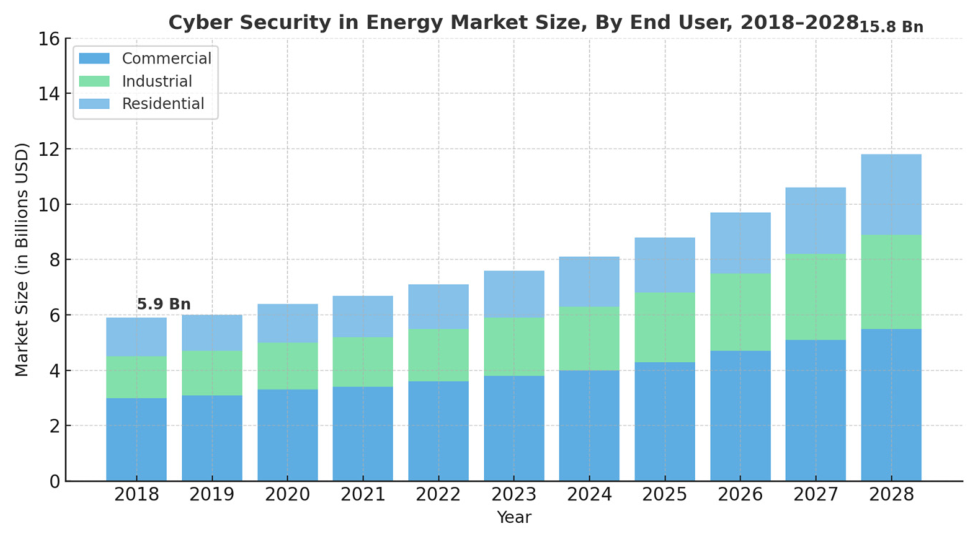
The benefits are numerous, increased automation, reliability, and response time, and the drawbacks are limited. The technology for smart microgrids has also increased in sophistication by leaps and bounds making the technology more appealing. Increased digitization always leads to increased security risks; this sector is no exception. As the attack surface expands it is often the case that security lags behind. The energy sector is critical infrastructure meaning that any attack against it has dire consequences. Without power, most other sectors cannot perform their work denying service to large swaths of industry. Thankfully along with increased attacks, there has been an increase in cybersecurity awareness in the energy market. According to Research and Markets, the Cybersecurity market in energy is projected to grow by 9.9 billion dollars from 2018 to 2028 (See
Figure 2). Cybersecurity awareness still has a long way to go in this sector and in the larger market.
A microgrid is a localized electrical system designed to operate either independently or in synchronization with the main power grid, enhancing both resilience and energy efficiency. It can integrate distributed generation sources, including solar system, wind turbines, and diesel generators, allowing electricity production close to the consumption sites [
4]. Typically, energy storage systems, such as batteries, are incorporated to store excess energy, thus maintaining stability during fluctuations in energy demand or interruptions in the main grid supply [
4]. Residential, commercial, and industrial consumers are all served by the microgrid.
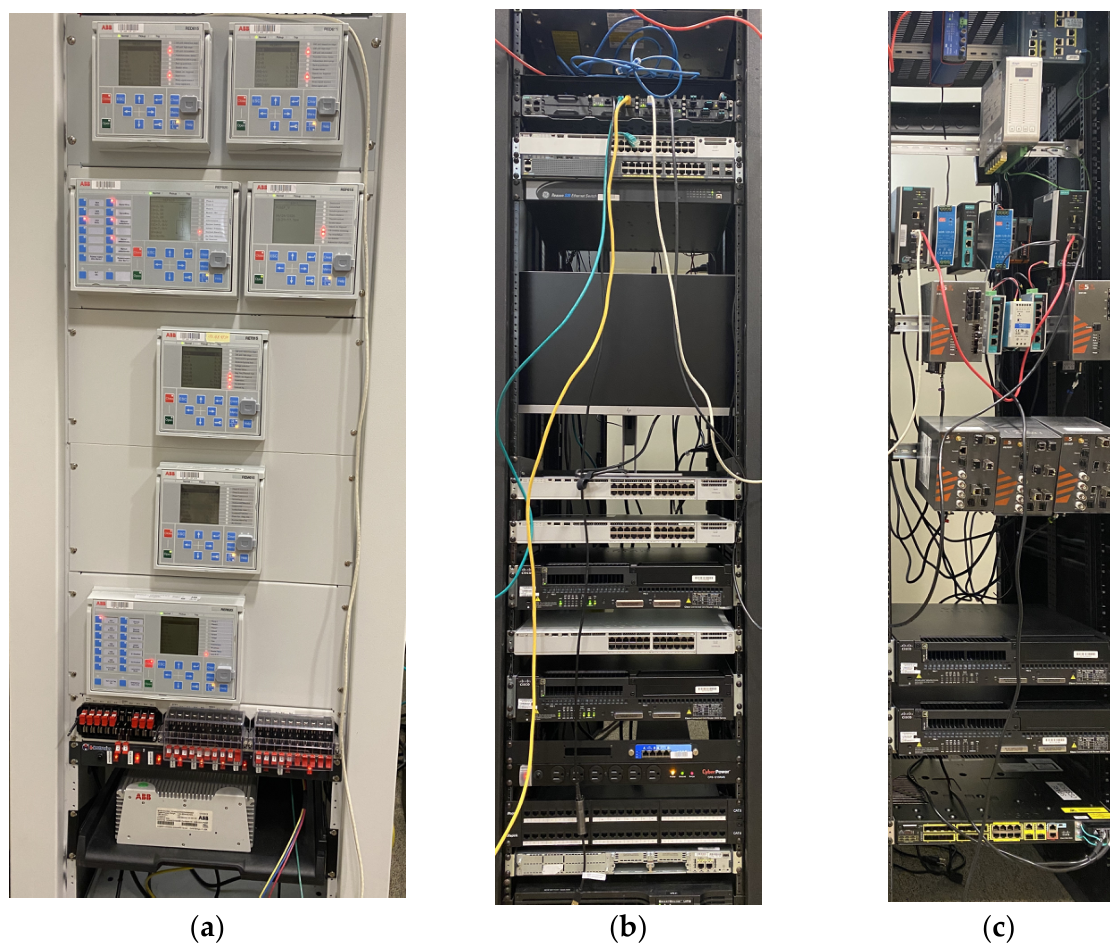
A sophisticated control system, often employing Intelligent Electronic Devices (IEDs) like ABB’s Relion series relays (e.g., REF615 vs. REF620 used in the testbed), oversees operations and enables seamless transitions between grid-connected and islanded modes [
5,
6]. For example, the ABB REF615 relay, designed for feeder protection, offers overcurrent, earth-fault, and voltage-based protection, along with IEC 61850 compatibility for real-time communication, while the RED615 provides advanced line differential protection, making them ideal for microgrid coordination and reliability. These IEDs support sustainable energy integration, particularly in remote locations or during main grid disruptions [
5,
6].
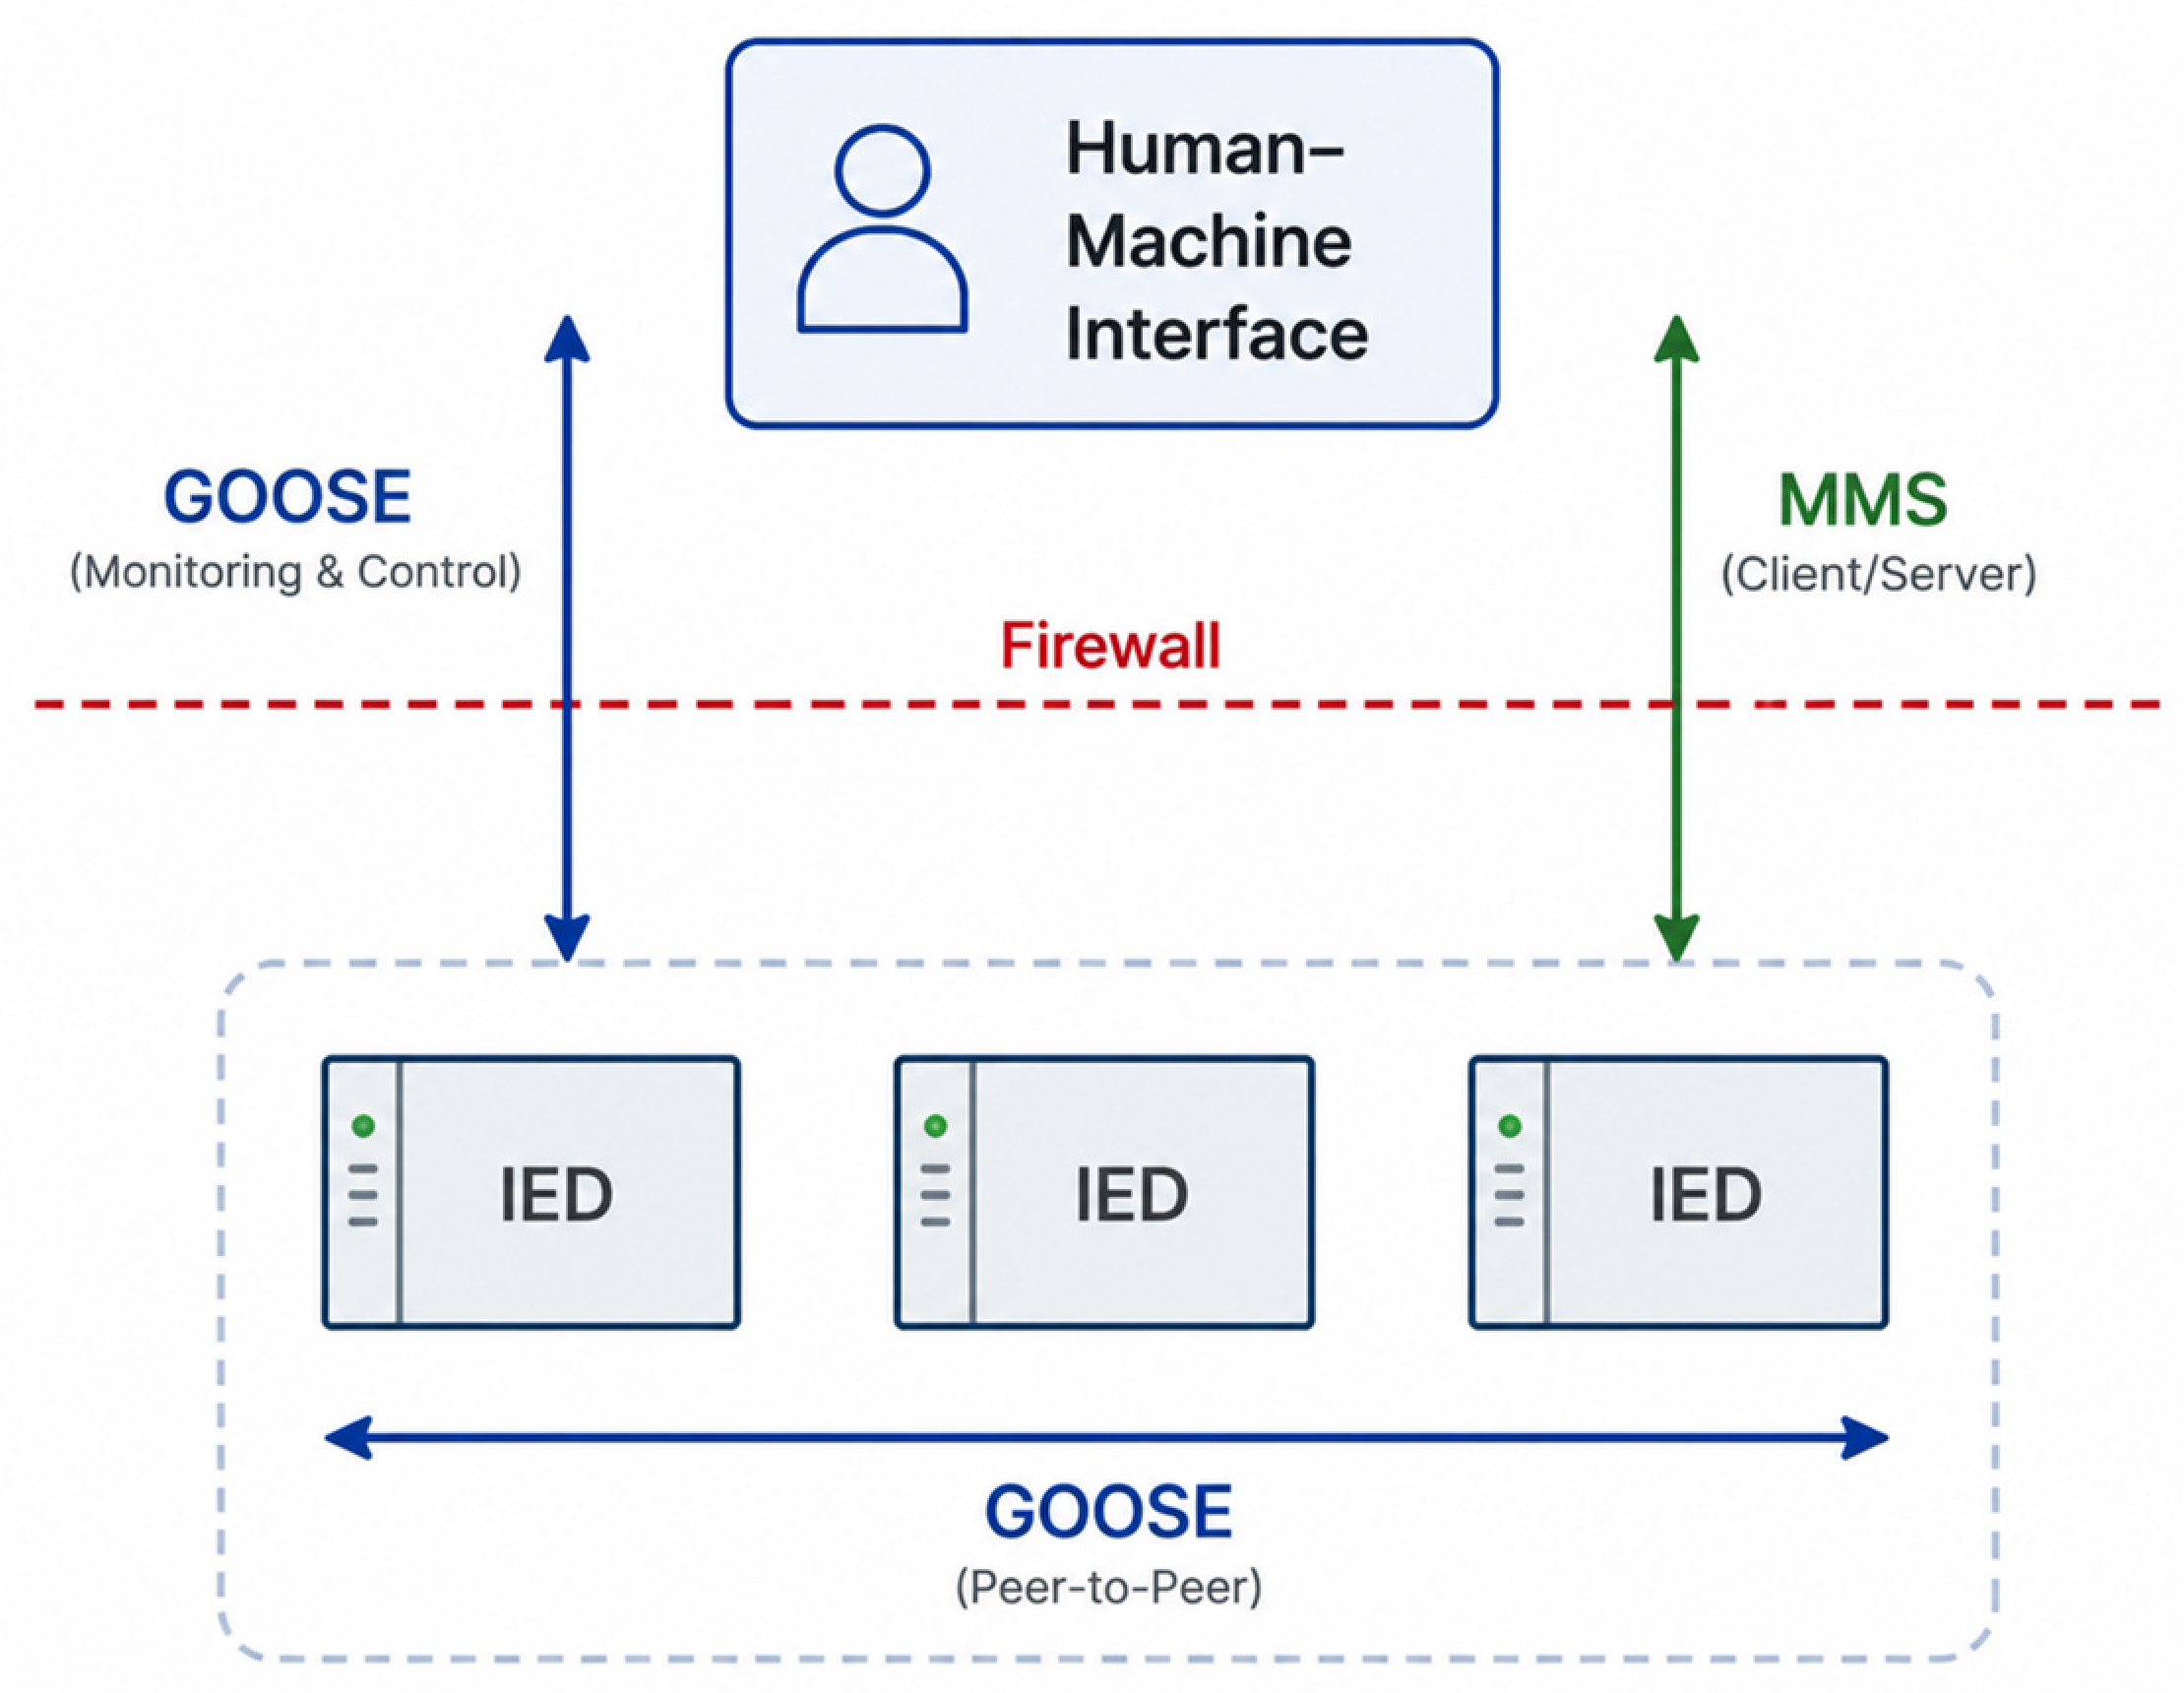
Critical to the functioning of these IEDs within the microgrid framework is the Generic Object-Oriented Substation Event (GOOSE) protocol, part of the IEC 61850 standard [
7]. GOOSE facilitates high-speed, peer-to-peer communication among devices, rapidly exchanging status and control data within 3–4 milliseconds delay, without relying on central servers. This capability ensures timely responses to dynamic conditions, such as mode transitions or fault occurrences, thereby enhancing microgrid stability and resilience. For example, relays such as ABB’s REF615 and RED615 employ GOOSE messages to swiftly detect faults and implement adaptive protection schemes [
5,
6]. The REF615, for instance, uses GOOSE to transmit fault signals for rapid isolation, while the RED615 coordinates differential protection across substations, improving distribution network reliability. Additionally, GOOSE supports the integration of distributed energy resources, managed via relays like the REF620 for comprehensive feeder management or the RET620 for transformer protection, ensuring operational responsiveness and power quality [
8,
9]. This real-time communication directly supports the control system’s objectives outlined in the microgrid architecture.
However, the inherent design of the GOOSE protocol prioritizes communication speed over cybersecurity, rendering it vulnerable to threats such as spoofing, replay attacks, and unauthorized device intrusions [
10]. GOOSE lacks native encryption or robust authentication mechanisms, making it susceptible to malicious activities, including message injection or replay attacks. While a firewall-protected Local Area Network (LAN) can restrict external access, attackers may exploit vulnerabilities by compromising internal IEDs, enabling the transmission of authenticated yet malicious messages.
Furthermore, unauthorized devices introduced into the LAN can bypass security measures like MAC address filtering, threatening operations managed by relays [
11,
12,
13,
14,
15]. Such intrusions could disrupt microgrid stability, potentially causing outages or uncoordinated responses. Although enhancements like IEC 62351-6 propose digital signatures and authentication [
10], their implementation is limited by GOOSE’s stringent timing constraints, necessitating advanced intrusion detection to balance performance and security. These vulnerabilities directly impact the communication reliability critical to the microgrid’s control system.
Automation is a significant advantage of microgrid systems, reducing the need for constant human monitoring and repetitive corrective actions. However, this reliance on automation can lead to oversight, making cyber-attacks harder to detect until significant damage has occurred. Additionally, it can delay the restoration of power to affected areas. The core issue lies in the microgrid’s dependence on high-speed network communication, which limits the ability to implement robust security measures. Adding security layers increases processing time, so most microgrid communication remains unencrypted and unauthenticated, with protection primarily provided by firewalls. These firewalls only defend against external threats, leaving internal devices vulnerable. If a device within the Local Area Network (LAN) is compromised, it can send malicious data that appears legitimate. In summary, one of the nation’s most critical sectors operates on an automated, unsecured communication network, underscoring the urgent need for enhanced cybersecurity and greater awareness.
Testing attacks on live, real-world systems is often considered the best approach. However, the potential risks involved in successfully executing such attacks typically make it an unrealistic option. To overcome this challenge, various simulations of industry networks are used for testing purposes. That said, it is rare to encounter a live network completely disconnected from power devices and dedicated solely to testing. This is the problem we set out to solve. Simulating real-world cyberattacks on microgrids in live environments is difficult due to the inherent risks. Microgrid testbeds, however, offer a controlled setting that allows for safe simulation and analysis of these attacks, helping to uncover vulnerabilities and strengthen security protocols.
This paper presents the design and development of a microgrid testbed specifically tailored to evaluate cybersecurity vulnerabilities. As the adoption of microgrids continues to grow, ensuring their security becomes increasingly critical, especially given their expanding role in modern power systems. One of the key areas of concern is the communication infrastructure, particularly protocols such as GOOSE (Generic Object Oriented Substation Event), which are widely used in protection systems for real-time data exchange.
To address this, we developed a dedicated testbed that enables controlled simulation of various cyberattack scenarios, allowing for a detailed assessment of their impact on Microgrid communications. The testbed supports the execution of diverse attack types, including Man-in-the-Middle (MITM), Denial-of-Service (DoS), and Manufacturing Message Specification (MMS) replay attacks. This comprehensive approach facilitates a thorough evaluation of vulnerabilities in critical communication protocols—specifically MMS and GOOSE—which are essential for reliable microgrid operation. Our work makes the following key contributions:
We develop a realistic microgrid testbed that incorporates industry-standard devices and communication protocols (Modbus, DNP3, and IEC 61850).
We implement and analyze the impact of several cyberattacks on the testbed environment, including Denial of Service (DoS), GOOSE spoofing, and MMS replay attacks. These experiments demonstrate the effectiveness of our testbed in simulating and evaluating cybersecurity threats within a realistic microgrid setting.
We provide insights into the vulnerabilities of microgrid communication infrastructure and highlight the potential consequences of these attacks on system stability and operation.
The findings from these evaluations are intended to help identify potential vulnerabilities, contributing to the development of more robust cybersecurity measures for microgrids and the protocols they rely on.
The remainder of the paper is organized as follows:
Section 2 provides a review of existing work,
Section 3 details the microgrid testbed settings, and
Section 4 describes the cybersecurity attacks implemented on the testbed.
Section 5 presents an analysis of the results, followed by the conclusion in
Section 6.
2. Literature Review
In today’s evolving energy landscape, the move toward decentralized power generation has made microgrids a crucial part of a reliable, efficient, and sustainable energy infrastructure. By integrating renewable energy sources, energy storage, and smart automation, microgrids are essential components of modern smart grids. However, this increased reliance on digital communication networks and IEC-61850 protocols introduces significant cybersecurity risks that could destabilize the grid. The IEC-61850 GOOSE protocol, used for real-time communication between Intelligent Electronic Devices (IEDs) in substation automation systems, is particularly vulnerable. Its lack of built-in authentication and encryption makes it a prime target for cyber threats, such as Denial-of-Service (DoS) attacks, spoofing, and message tampering. This section reviews existing studies on IEC-61850 security vulnerabilities, attack simulations, and countermeasures, while identifying gaps that require further research.
Several studies have identified critical vulnerabilities in IEC-61850 GOOSE communication, particularly focusing on Denial-of-Service (DoS) attacks and protocol spoofing. Fayaz et al. provide an in-depth analysis of DoS-based threats to substation networks [
16], for example, (1) fraudulent GOOSE messages flooding the network and causing relay failures, (2) a high rate of malicious high-priority messages delaying legitimate control commands and leading to potential substation blackouts. Rate-limiting mechanisms and anomaly-based IDS can mitigate DoS risks, but their effectiveness in operational substations remains untested. A related study further evaluates the impact of DoS on microgrids and SCADA (Supervisory Control and Data Acquisition) systems [
17]. The authors simulate GOOSE message flooding attacks and analyze the resilience of different network topologies to DoS threats and the limitations of current intrusion detection algorithms. This study concludes that existing defense mechanisms struggle to detect low-volume, stealthy DoS attacks, necessitating more adaptive security solutions.
Another major risk in IEC-61850 networks is message spoofing, where an attacker injects false GOOSE messages to manipulate substation operations. Lu et al. explore these risks and identifies that GOOSE messages’ lack of encryption makes them vulnerable to replay and spoofing attacks [
18]. Attackers can impersonate legitimate devices to issue unauthorized control commands. Authenticated encryption and secure key management could mitigate these risks, but implementation in legacy substations remains challenging. A more recent paper expands on attack methodologies used against IEC-61850 networks [
19]. The authors show that SCADA system manipulation disrupts power grid operations, communication jamming attacks interfere with real-time relay switching, and malware targets substation IEDs, altering legitimate GOOSE transmissions. The study emphasizes the need for a multi-layered defense in depth strategy, combining network monitoring, cryptographic authentication, and hardware-based security controls.
To combat these vulnerabilities, various defensive techniques have been proposed, including intrusion detection systems (IDS), cryptographic authentication, and resilient communication protocols. Gupta et al. propose signature-based IDS for detecting known cyberattacks and machine learning-driven IDS for adaptive threat detection in substation networks [
20]. However, false positives and high computational costs remain as major challenges in deploying IDS in real-time energy networks.
A widely suggested approach to securing GOOSE messages is cryptographic authentication, as explored in [
21]. The paper proposes AES-based encryption for securing message payloads, Elliptic Curve Cryptography (ECC) for fast authentication, and Hash-based Message Authentication Codes (HMAC) for integrity validation. Ahmed et al. explores cryptographic enhancements to protect GOOSE message integrity and authentication [
15]. The paper highlights the use of Message Authentication Codes (MACs) to detect tampering, digital signatures to verify message authenticity, and Intrusion Detection Systems (IDS) to monitor network traffic. However, the study warns that cryptographic methods introduce processing delays, which may impact fast response times that are necessary in substation automation.
An emerging research direction focuses on resilient and decentralized security models. Hernandez et al. present a blockchain-based approach to securing GOOSE message transmission [
22]. This paper proposed distributed ledger technology (DLT) to ensure message authenticity and traceability, smart contracts to enforce secure device authentication, and consensus mechanisms validate GOOSE messages before execution. Although blockchain enhances message security, its scalability and computational requirements pose challenges for real-time substation operations.
Existing studies have provided valuable insights into cyber threats and potential countermeasures for IEC-61850 GOOSE messages. However, there is a notable lack of real-world testing and evaluation of these countermeasures in operational microgrid environments. Furthermore, many studies focus primarily on theoretical analyses and simulations, with limited practical implementation and validation on physical testbeds.
This paper contributes to filling this gap by:
Developing a realistic microgrid testbed that incorporates industry-standard devices and communication protocols (Modbus, DNP3, and IEC 61850).
Implementing and analyzing the impact of several cyberattacks, including Denial of Service (DoS), GOOSE spoofing, and Manufacturing Message Specification (MMS) replay attacks, on this physical testbed environment.
Providing empirical evidence of the vulnerabilities in microgrid communication infrastructure and the potential consequences of these attacks on system stability and operation.
By focusing on practical testbed experimentation, this research provides valuable insights for the development of more robust and effective cybersecurity measures for microgrids [
23].
4. Cybersecurity Attacks
This section provides a detailed overview of the cyberattacks executed on the microgrid testbed. The attacks specifically target vulnerabilities in the GOOSE communication of the physical testbed’s control systems and communication infrastructure. The goal is to evaluate the system’s resilience under adversarial conditions.
4.1. DoS Attacks
In this subsection, we explore Denial of Service (DoS) attacks targeting the GOOSE protocol in a microgrid testbed. Denial of service attacks send a deluge of traffic in an effort to overwhelm the target s DoS attacks are significant because they can disrupt the critical real-time communications that microgrids rely on for protection, control, and automation. These attacks can interrupt service availability by causing downtime or, in some cases, permanently shutting down a device or server. DoS attacks can have significant consequences, such as revenue loss for businesses, operational slowdowns for government agencies, and compromised device functionality for individuals. The most critical impact occurs when DoS attacks target utilities, such as water or energy, potentially cutting off entire neighborhoods or damaging essential infrastructure, leading to widespread disruptions and significant financial losses.
4.1.1. Transport Connection Protocol
TCP (Transport Connection Protocol) establishes a connection between 2 hosts with a TCP “3-way handshake”: SYN (Synchronize), SYN-ACK (Synchronize Acknowledge), and ACK (Acknowledge). There is a receiving buffer on the server to store SYN packets and track TCP open connections. When this buffer is full it rejects new TCP connections until it receives an ACK to complete the handshake, or the device times out.
This principle is exploited in a TCP SYN flood attack. In this attack, the attacker sends SYN requests from randomly generated IP Addresses. The server sends back SYN-ACKs to these addresses and places these fake connection requests in the receiving buffer. When the server never receives an ACK, it times out and frees up the buffer. When requests constantly flood this buffer, it is never open to legitimate requests, even after some timeout the newly opened slots get snatched up by new malicious TCP packets. This results in devices being unable to communicate, which affects the services they provide. In a microgrid, if this attack targeted an IED it would make it so the device would be unable to reliably receive packets or cause extreme delay. As mentioned before the GOOSE protocol is extremely dependent on fast speeds and reliability, both of which this attack disrupts.
4.1.2. TCP SYN Flooding Attacks
We have successfully executed a TCP SYN flooding attack on the microgrid testbed targeting the IEDs. The ability to do this attack on physical devices allows for observation of the attack with the natural waves of network chatter that would otherwise be difficult to emulate.
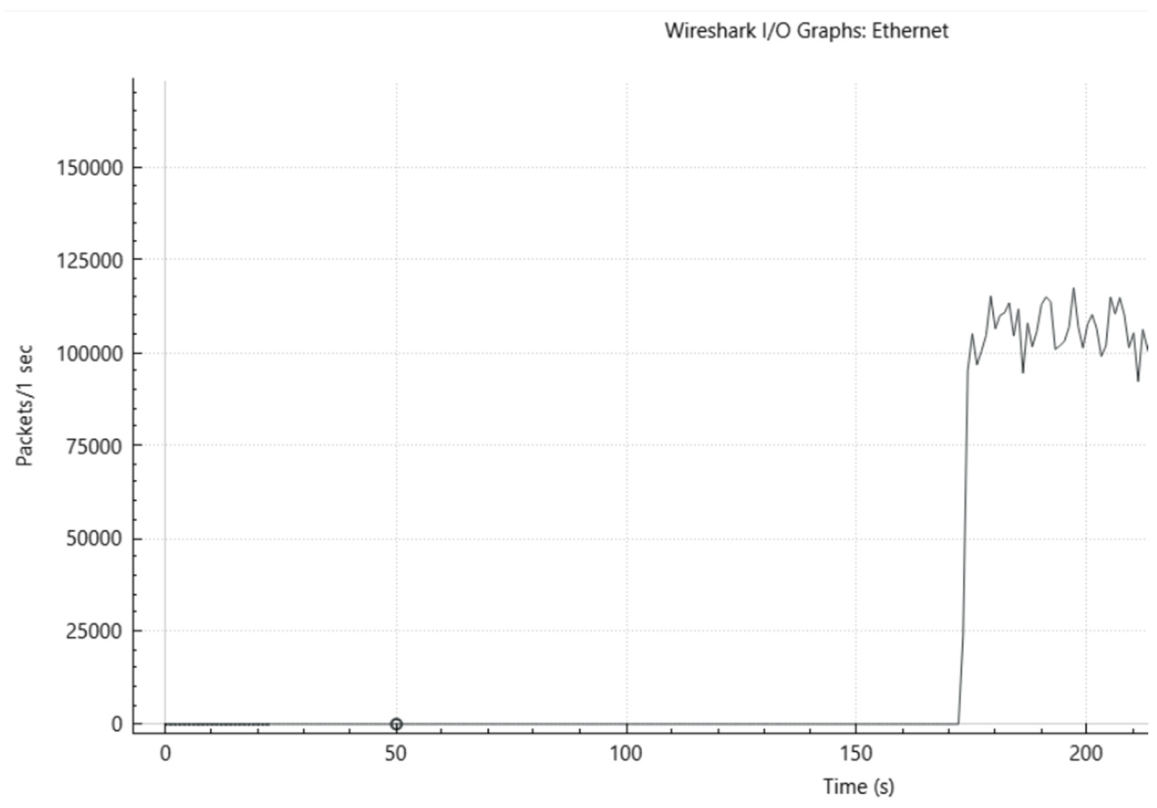
Figure 6 below shows the number of malicious packets we were able to send. The first section of the graph shows the network without any interference. Then the second section shows the network traffic once we launched our attack.
The attack resulted in a substantial increase in network traffic volume, as depicted in
Figure 6. Concurrent to the attack, the responsiveness of the IEDs was monitored using one-second interval ping requests. The results indicated a 67% packet loss rate and an average delay of 325 milliseconds for successfully received ping requests. These observations confirm that TCP SYN flood attacks can effectively disrupt the time-sensitive communication essential for GOOSE, potentially delaying or preventing critical protection functions, such as fault-induced circuit breaker tripping.
If an attacker were to execute this attack, several effects could occur based on the system this attack is implemented on. GOOSE messages indicate when the devices that the IEDs are monitoring have a fault. Whether it be an overcurrent, a feeder malfunction, or the many other things that can go wrong in the real world. The IEDs react by opening the circuit breaker to isolate the fault. This usually shuts off the power in an area but it is much better than the alternative of permanent damage to the sensitive equipment which would cause even longer downtimes. Due to the nature of what GOOSE messages communicate speed is of the essence. Under our attack valid trips were blocked or delayed, which could cause significant damage to equipment and could lead to power outages. The scope of these outages could be anything from a singular apartment complex to entire cities including critical government services such as fire, police, and hospitals.
4.1.3. GOOSE Spoof Attacks
We use Python to create a GOOSE packet for a spoofing attack. The source code below demonstrates how to generate a GOOSE packet.
def ref620_untrip_packet(st_num):
ethernet_mac = Ether(src = ‘00:21:c1:22:c8:77’, dst = ‘01:0c:cd:01:00:03’, type = 0x88b8)
goose_pdu = GoosePDU(gocbRef = “REF62030LD0/LLN0$GO$gcbREF620”,
timeAllowedtoLive = num2str(20000),
datSet = “REF62030LD0/LLN0$REF620”,
goID = “REF62030LD0/LLN0.gcbREF620”,
T = datetime.datetime.now(datetime.timezone.utc).timestamp(),
stNum = num2str(st_num),
sqNum = num2str(0),
simulation = 0,
confRev = num2str(700),
ndsCom = 0,
numDatSetEntries = num2str(4)
)
goose_data = unhexlify(“ab1084030300008301018403030000830100”)
goose_pdu.sequence_l = (len(goose_pdu) + len(goose_data) − 2)
goose_header = GooseHeader(appid = 4, length = len(goose_pdu) + len(goose_data) + 8)
goose_packet = ethernet_mac/goose_header/goose_pdu/goose_data
return goose_packet
The spoof attack exploits the lack of authentication in GOOSE messages. It also strikes right at the heart of the function of a GOOSE message: to indicate faults. We were able to capture a tripped goose message and using that data in tandem with an existing attack tool configure the packets to our network. A lot of what is contained in GOOSE messages is parameters and basic mechanisms to prevent some erroneous reading or receiving of messages by the IEDs. The only difference between a normal message and a trip is the data portion. We compare the normal GOOSE packet data and the spoofed data below in
Figure 7 and
Figure 8.
Figure 7 is from Wireshark and is the data section of a heartbeat packet (normal GOOSE packet).
Figure 8 is of the data section of our attack program that spoofs a trip. The only difference between the normal packet data and spoofed packet data is the very last hex, which is changed to 01 instead of 00 in the spoofed packet. This signals that there is a fault in a connected device.
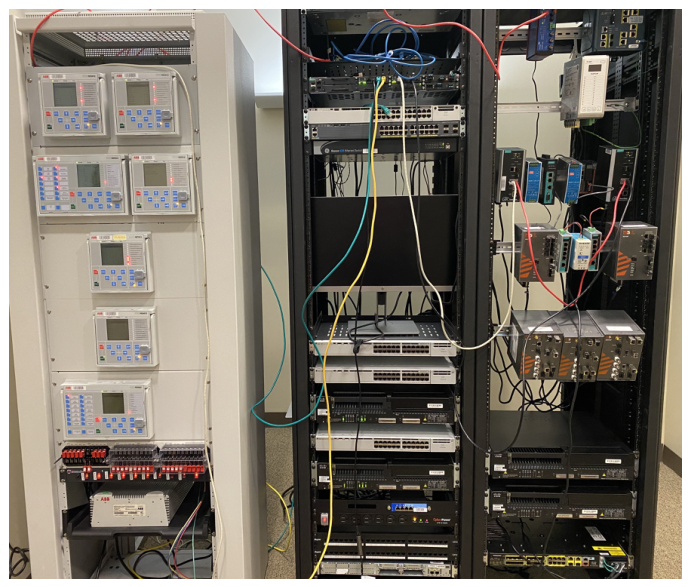
Below is our REF 620 on the testbed which was our target for this attack.
The targeted IED (REF620 relay) processed the spoofed GOOSE message and erroneously triggered a circuit breaker trip, as illustrated in
Figure 9 and
Figure 10. This outcome substantiates that attackers can exploit GOOSE communication vulnerabilities to instigate disruptive actions within the microgrid, potentially leading to unwarranted power outages. It is important to note that due to GOOSE being a Layer 2 protocol, the attack’s scope is confined to the local area network (LAN).
4.2. MMS Replay Attacks
A Manufacturing Message Specification (MMS) replay attack involves intercepting MMS communications from a legitimate source, such as the network supervisor or Supervisory Control and Data Acquisition (SCADA) system, and replaying the same message later, impersonating the original sender. The MMS protocol is used in microgrids to relay information and commands between the SCADA system and the Intelligent Electronic Devices (IEDs).
Similarly to GOOSE messages, MMS transmits real-time data but lacks built-in security features due to its requirement for fast response times. MMS messages are not encrypted and have no authentication, meaning that replayed messages are considered legitimate, allowing the attacker to access the same data and operations as the legitimate supervisor [
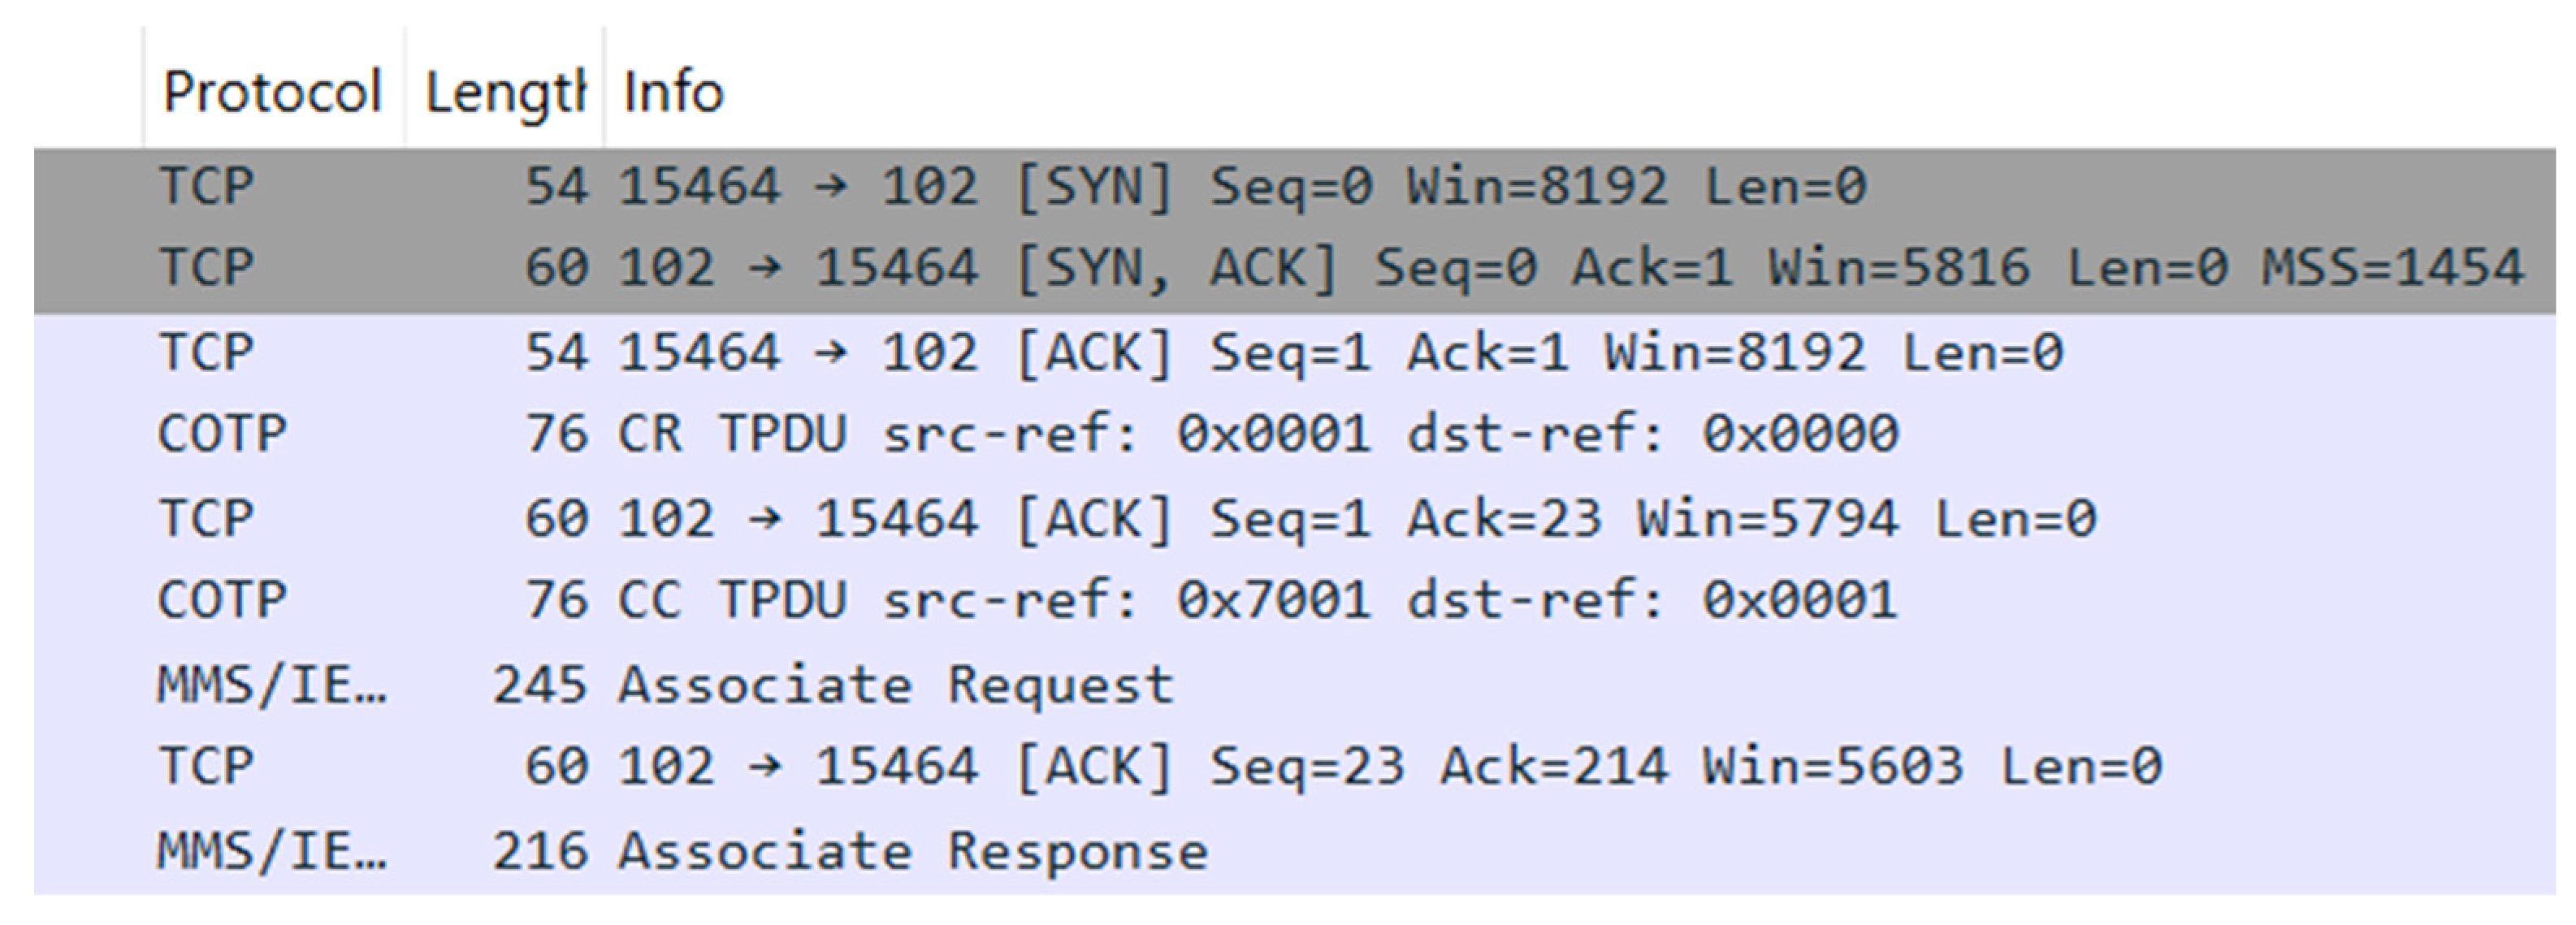
24]. MMS is particularly vulnerable to replay attacks because it operates at the network layer, unlike GOOSE, which operates at the link layer. While a GOOSE replay attack would require physical access to the microgrid, MMS replay attacks can be conducted remotely. The objective of this attack is to demonstrate the feasibility of executing MMS attacks from outside of the microgrid’s Local Area Network. Both MMS and its underlying protocols are connection-oriented, necessitating the establishment of a connection before the attack can be executed. The establishment of an MMS consists of a TCP three-way handshake, a Connection-Oriented Transport Protocol (COTP) connect request, and an MMS associate request.
4.2.1. TCP Three-Way Handshake
TCP packets include a destination port parameter which specifies the service being requested from the server and a source port parameter which designates the service being provided by the client. During the three-way handshake, the destination port for the SYN packet must be the port number for the MMS protocol, which is 102. The source port can be arbitrary, as the server requires no special service from the client.
4.2.2. COTP
Connection-Oriented Transport Protocol (COTP) is another transport layer protocol requiring reliable connection establishment like TCP. COTP is considerably older and has been replaced by TCP in most networks, but MMS communications are built on top of COTP so the connection must be made before the replay can take place. The COTP connect request involves only 2 steps as opposed to TCP’s three-way handshake. The client sends the connect request and the server sends a connect response back, and no further acknowledgment is needed.
4.2.3. MMS Associate Request
Once both TCP and COTP connections have been established, the MMS associate request can be sent.
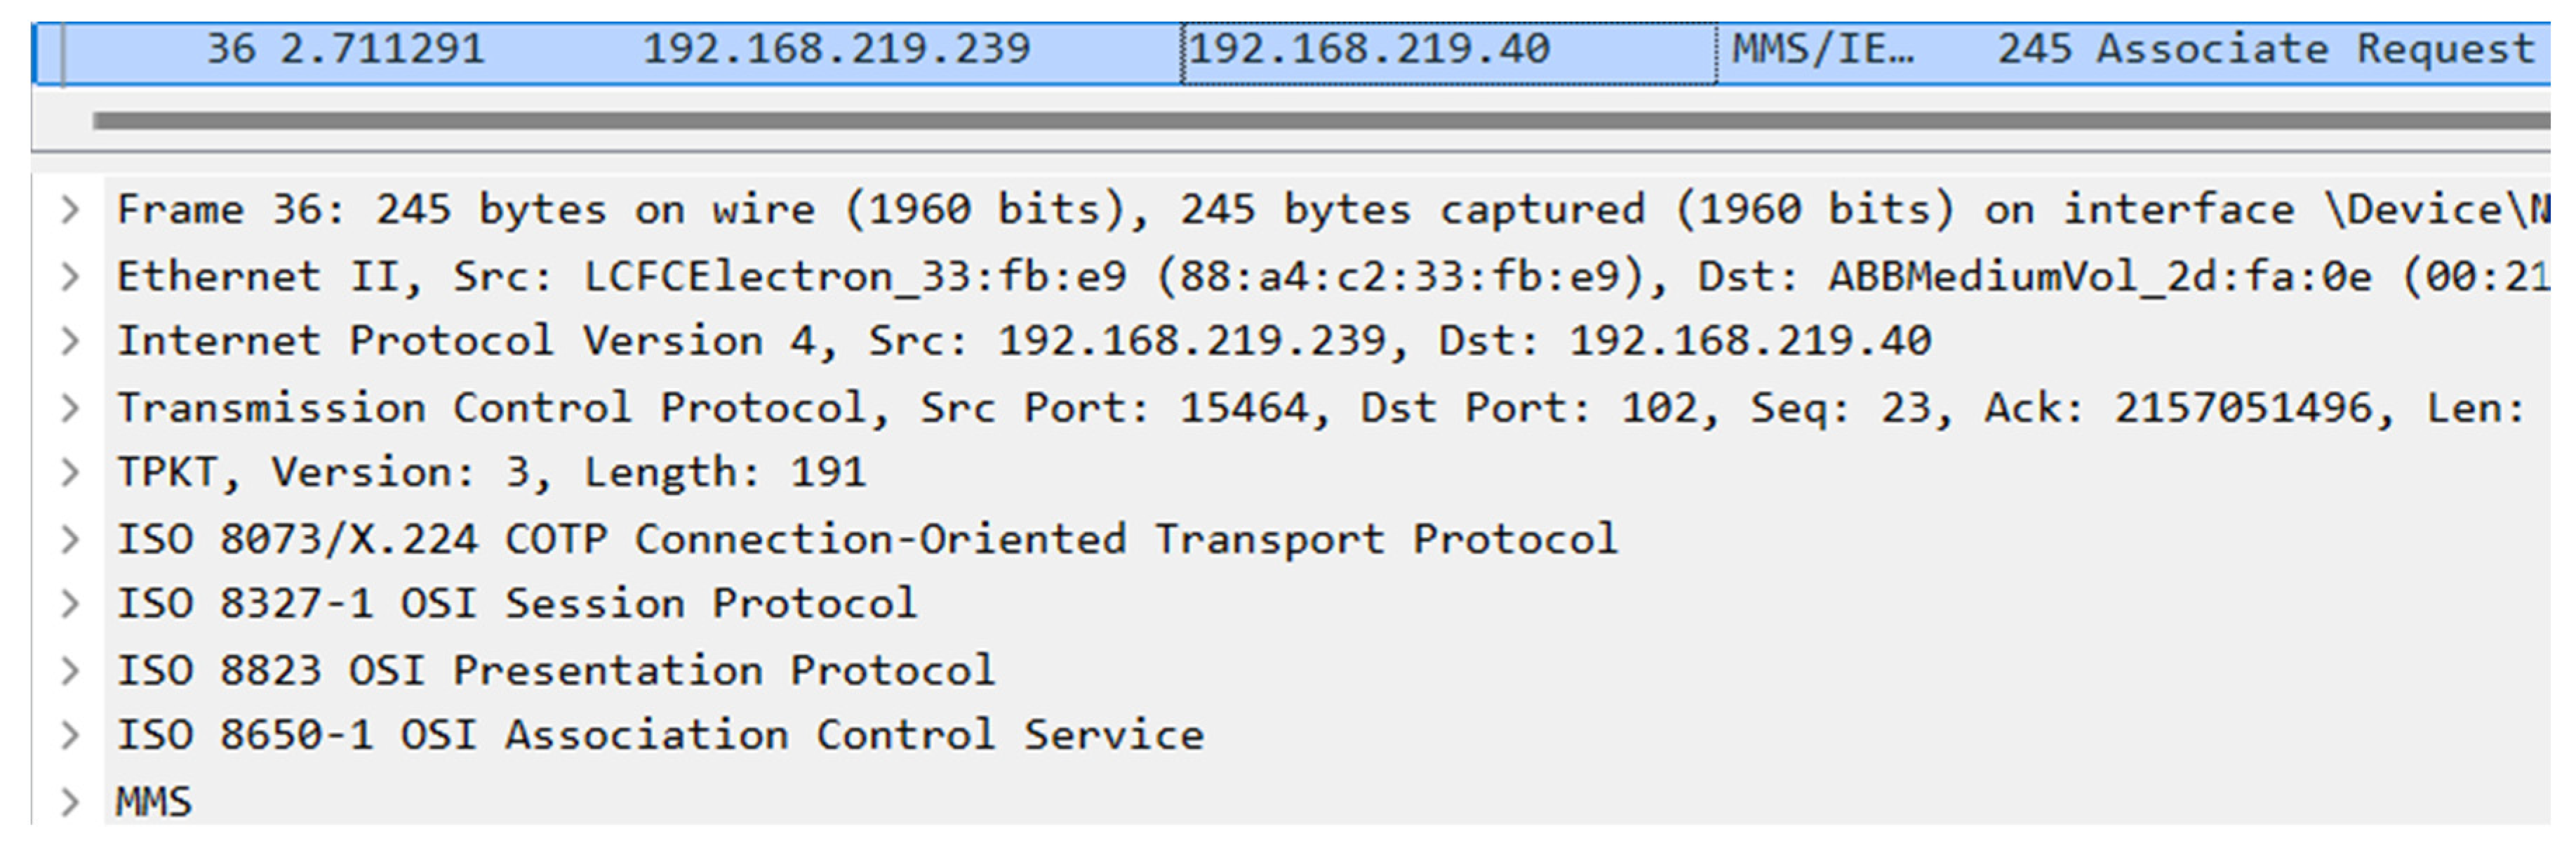
Figure 11 illustrates the MMS connection setup captured by Wireshark. However, since MMS is an application layer protocol, three underlying protocols must be configured: the OSI session protocol that manages data streams between applications, the OSI presentation protocol that determines how the data to be transferred is formatted, and the Association Control Service (ASC) protocol which verifies the association between two programs and authenticates their identities. For each of these underlying protocols, no modifications need to be made from the original capture for the attack to succeed.
Once the underlying protocols are set up, the MMS associate request can be configured. There are several flags to set underneath the “supported services calling” parameter of the associate request, and the most important flags to set for the attack are the read and write flags. These flags will allow the attacker to alter the tripped state of the REF 615 device in subsequent communications. Once the associate request is sent and the response received, all the setup for the attack is complete.
Figure 12 shows the full protocol stack.
4.2.4. MMS Set Data Value Request
The packet that causes the trip is an MMS set data value request, which is the packet that will be captured and replayed when eavesdropping on the microgrid’s traffic. This captured packet, after modifying its sequence and acknowledgment numbers, can be replayed infinitely many times and be recognized as legitimate as long as it has the correct timestamp. MMS is a time-intensive protocol, and each request is marked with a UTC (Coordinated Universal Time) timestamp with precision in the nanoseconds. Every time a set data value request is sent, it must be marked with the correct UTC timestamp otherwise it will be recognized as a retransmission and access will be denied,
Figure 13 below.
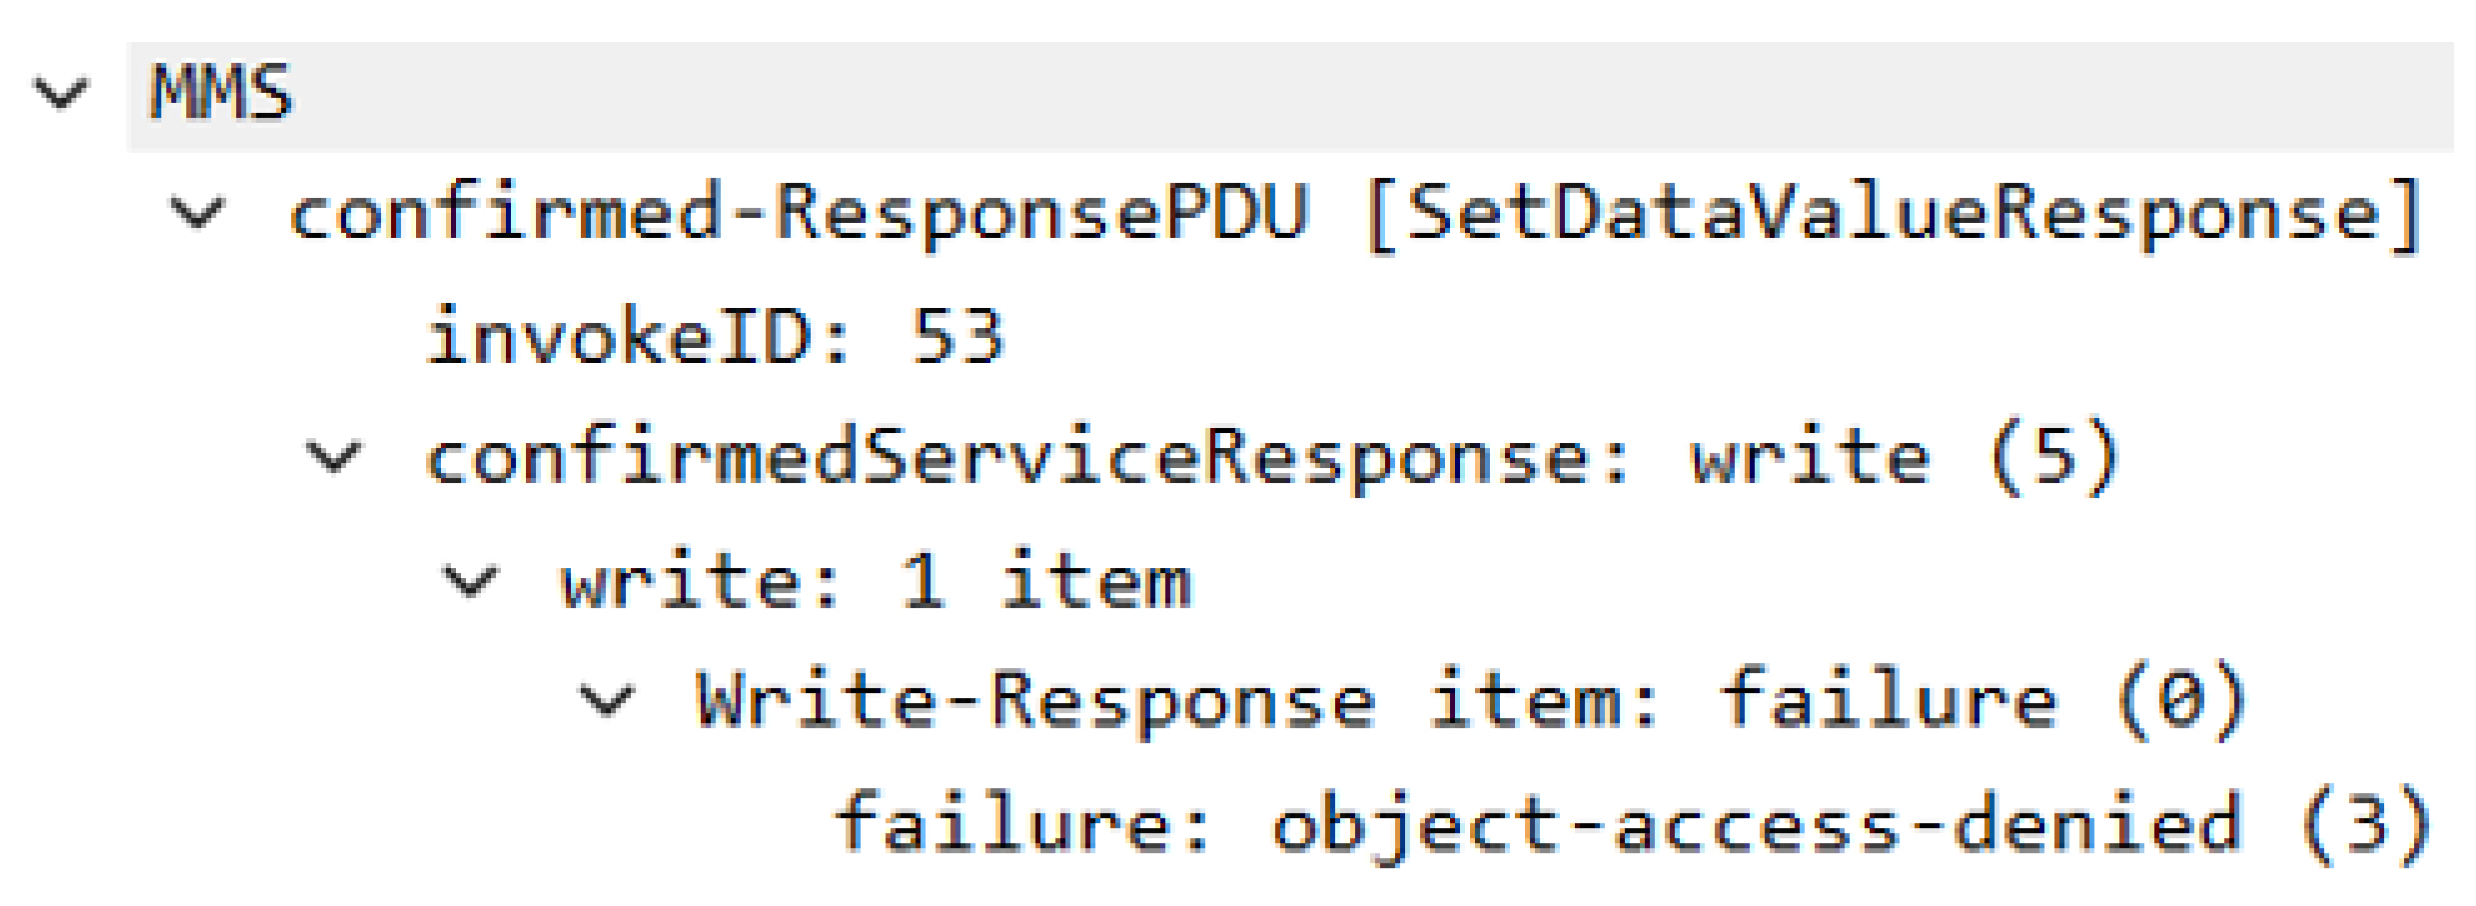
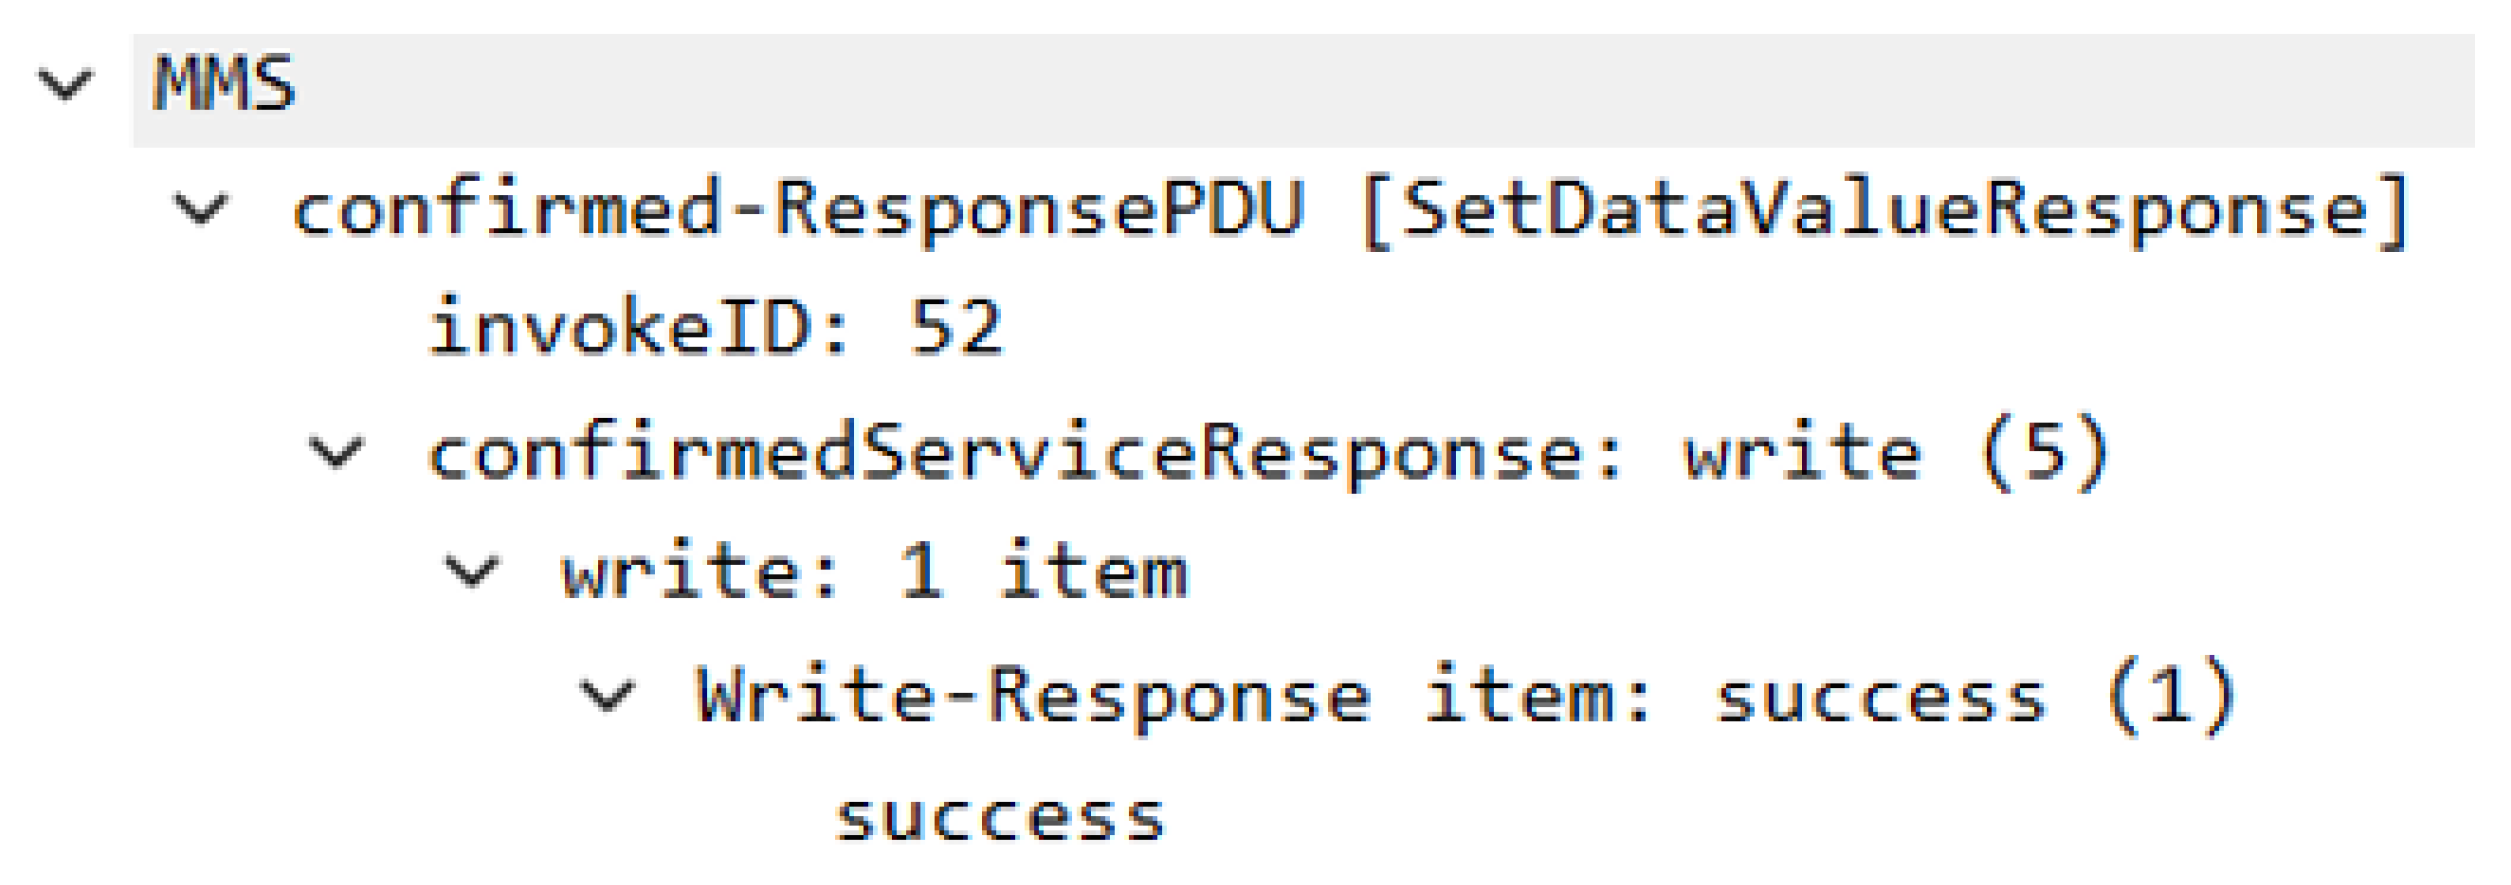
In addition to the modifications made to the application layer, the underlying COTP, session, and presentation protocols need to be reconfigured as data transfer packets as well. ASC is omitted from the set data value request’s protocol stack as all the services needed have already been called in the associate request. Two set data value requests must be sent in sequence, the first being a select command. Select Before Operate (SBO) is an IEC 61580 communication standard that requires a device to be selected before sending it an operate command. This ensures that the device is reserved only for the client that selected it. The second set data value request is the operate command itself, which performs the breaker trip. Execution of all steps described previously resulted in the targeted circuit breaker being tripped. In the Wireshark capture, the response will now indicate that the write operation succeeded meaning that the breaker was tripped, shown in
Figure 14.
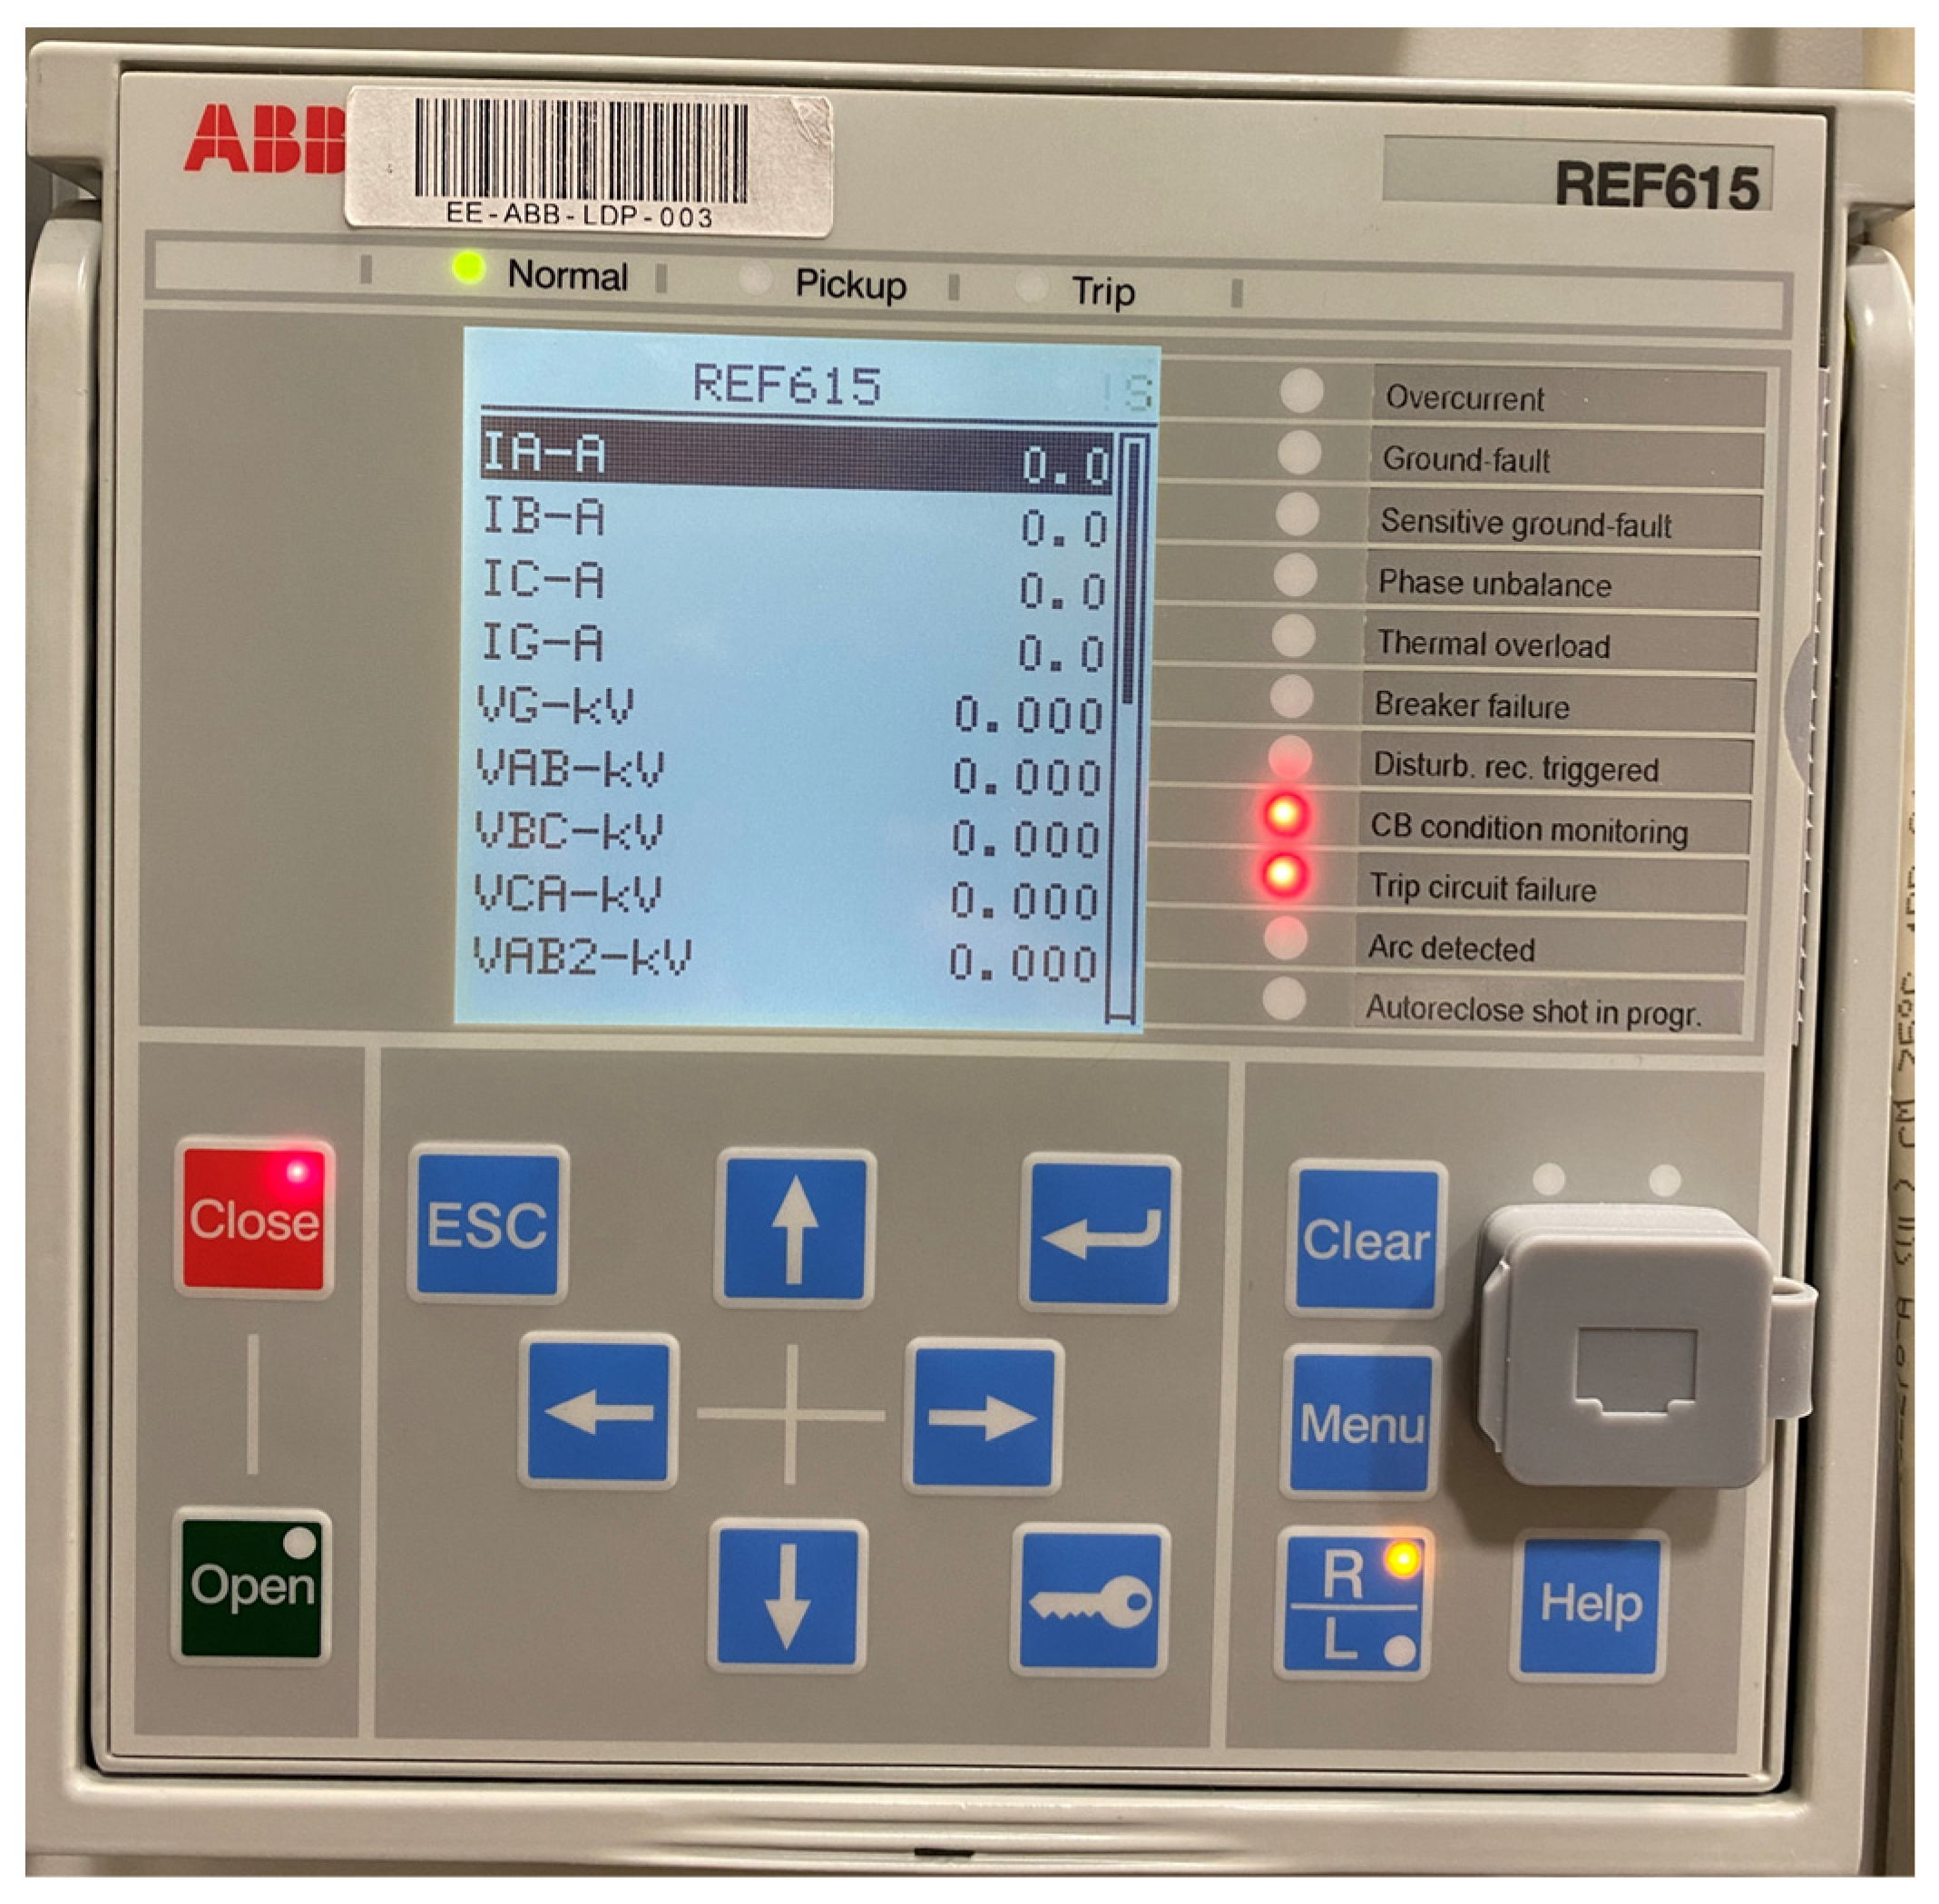
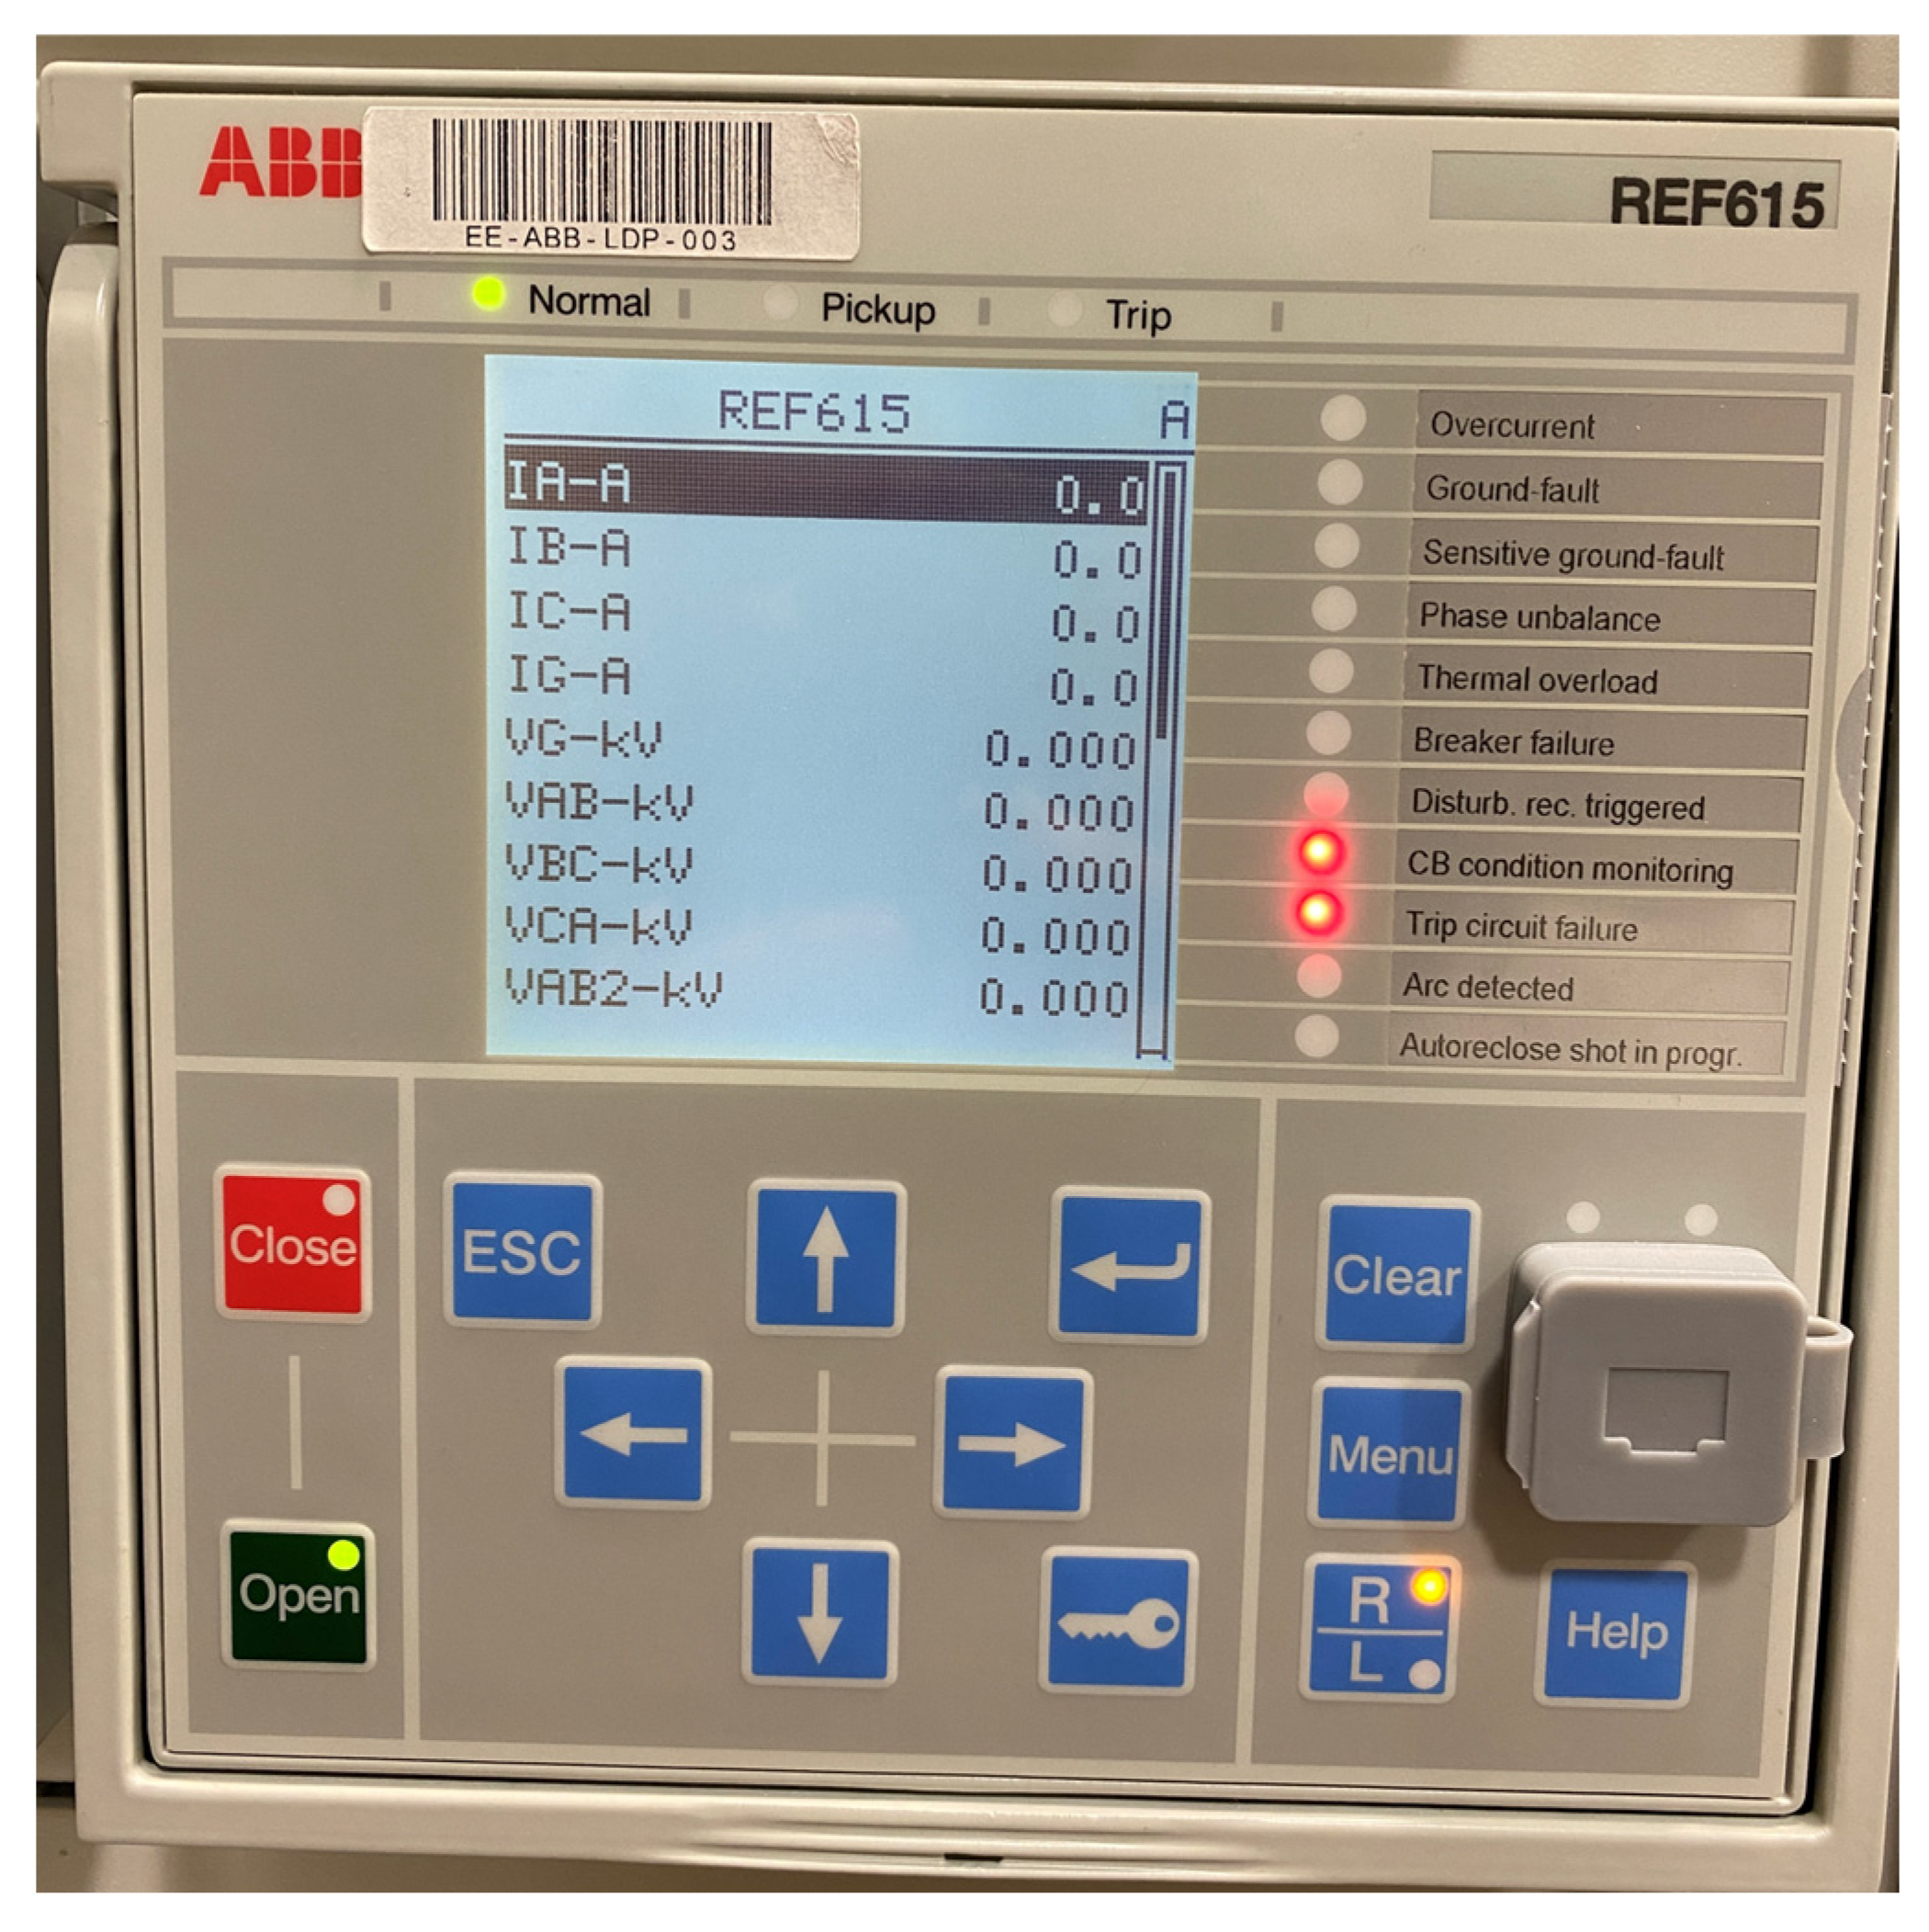
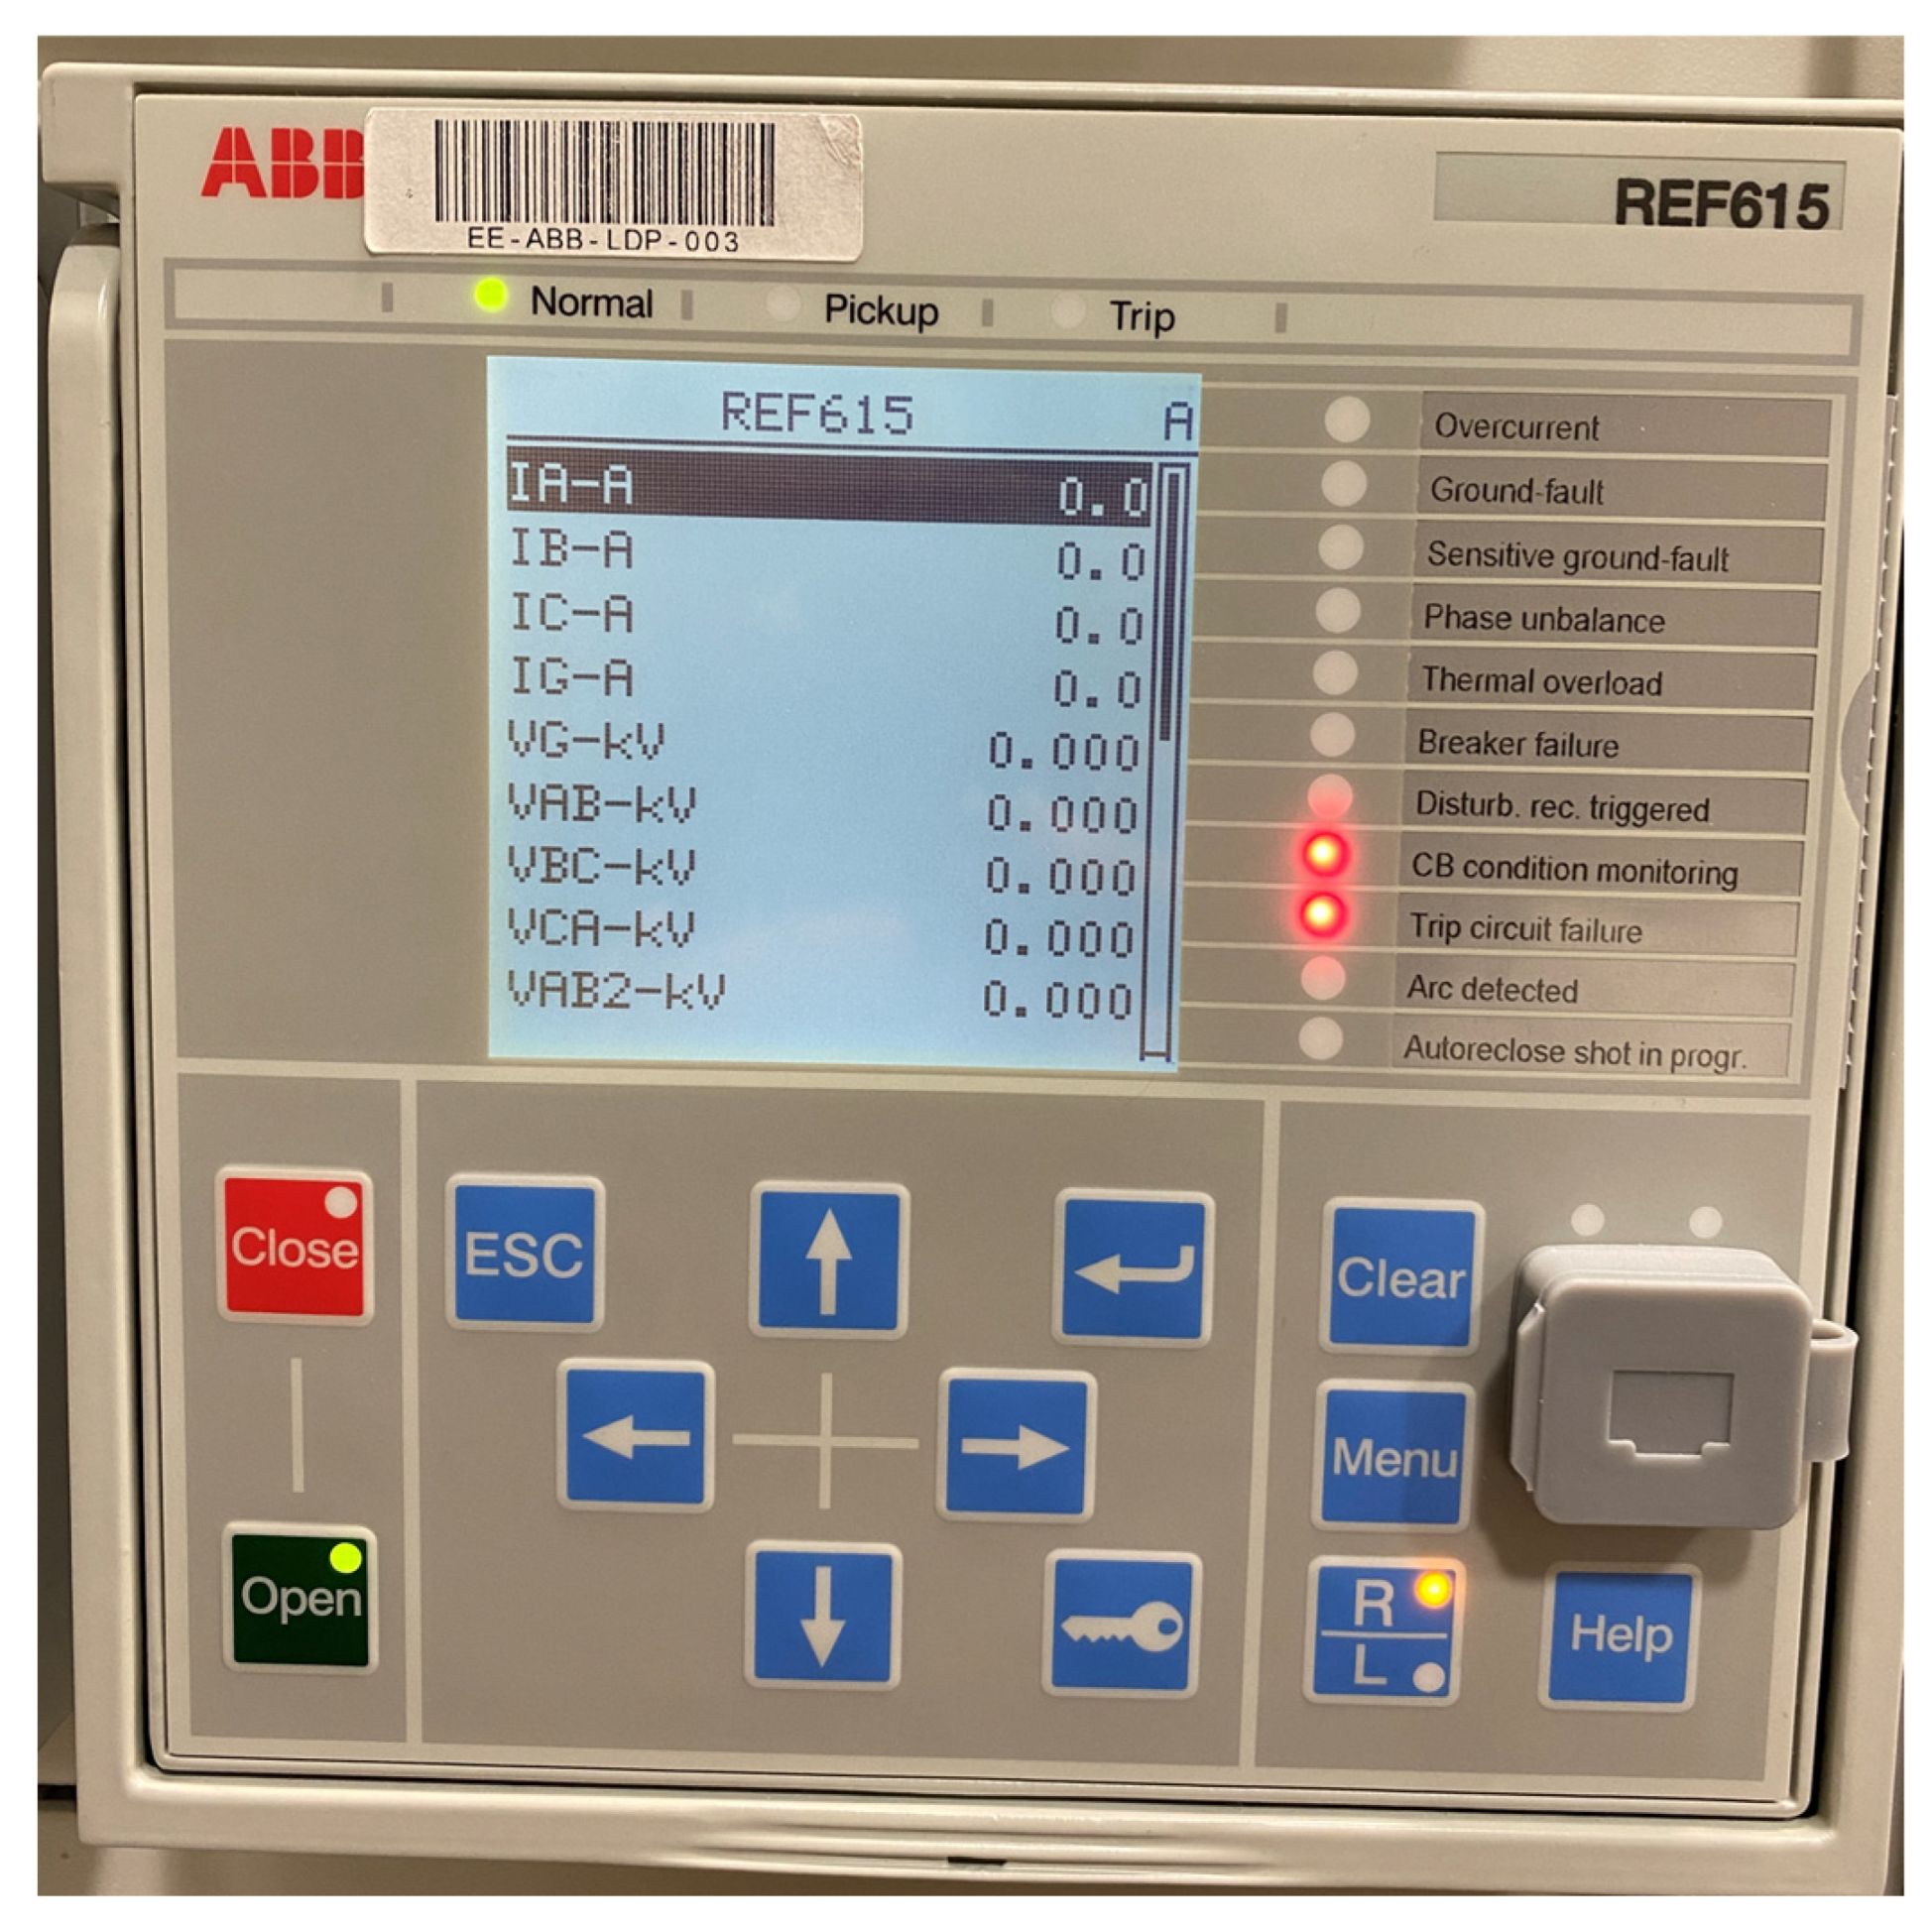
Figure 15 displays the tripped REF615.
Looking at the REF 615 device, the indicator light will have switched from on to off meaning that the attack was successful in tripping the breaker. The success of this attack demonstrates a vulnerability in MMS communications, potentially leading to disruption of microgrid operations from an attacker outside of the LAN.
4.3. MITM Attacks
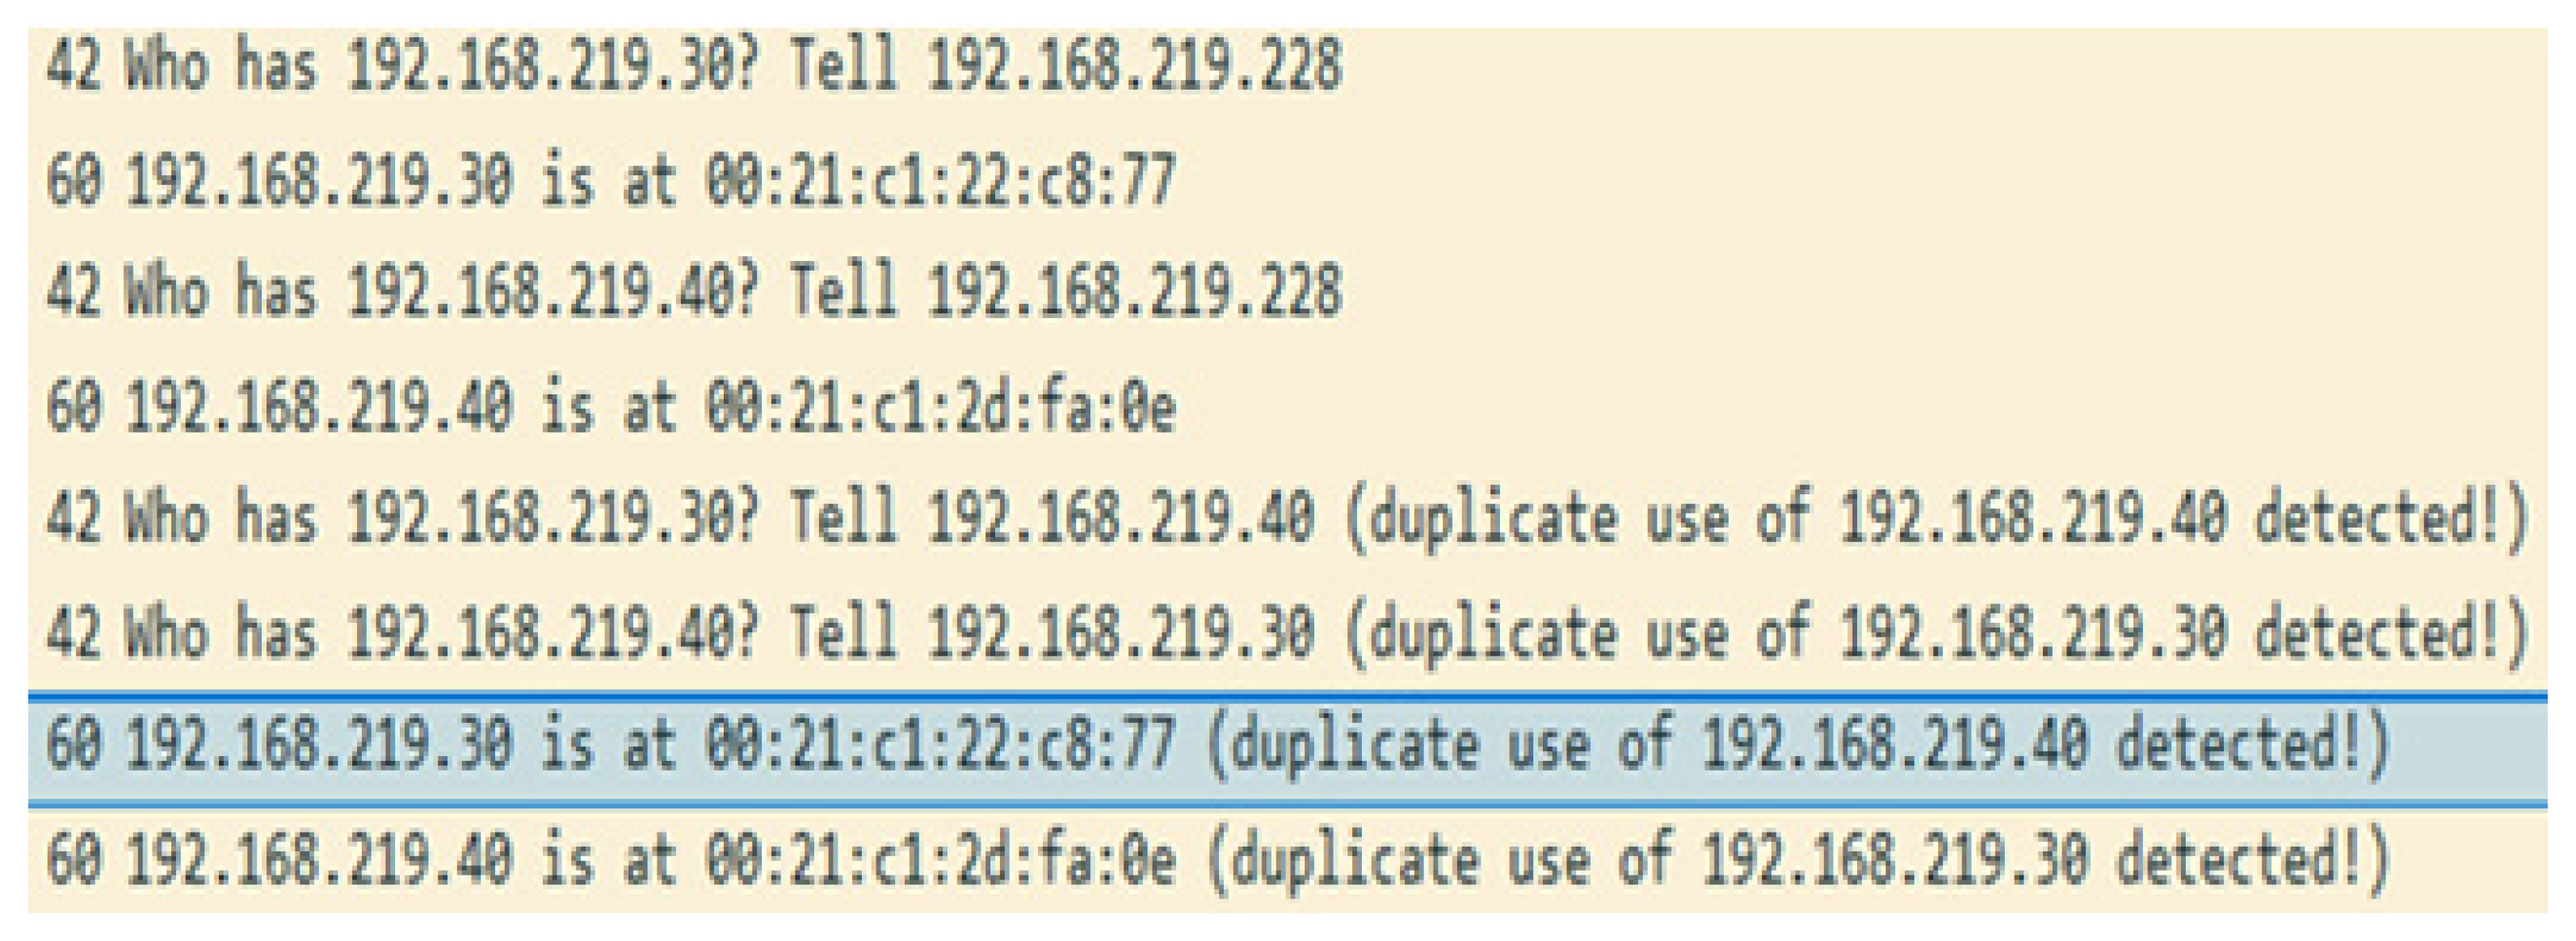
Another threat was found in the network that did not end up being an exploitable vulnerability for our current configuration but is worth mentioning for real-world systems with other communications. A man-in-the-middle attack is where an attacker intercepts traffic in the network and can alter, view, change the timing, or send completely different messages through the network. This attack occurs when an attacker intercepts communication between two devices, sending crafted messages to modify the Address Resolution Protocol (ARP) table. ARP maps Internet Protocol (IP) addresses (Layer 3) to MAC addresses (Layer 2) in a network. While the MAC address is typically static, IP addresses can change, requiring a protocol to update the ARP table. ARP packets, designed for efficiency in 1982, allow unsolicited updates to this table. The attacker sends an ARP “Who has” packet to request the mapping of an IP address to a MAC address. By spoofing the sender’s MAC and IP addresses, the attacker causes the target devices to register incorrect ARP mappings. This results in ARP poisoning. If both devices are poisoned, a man-in-the-middle attack occurs, allowing the attacker to intercept and control all communication between them.
Figure 16 shows the interacted packet captured by Wireshark.
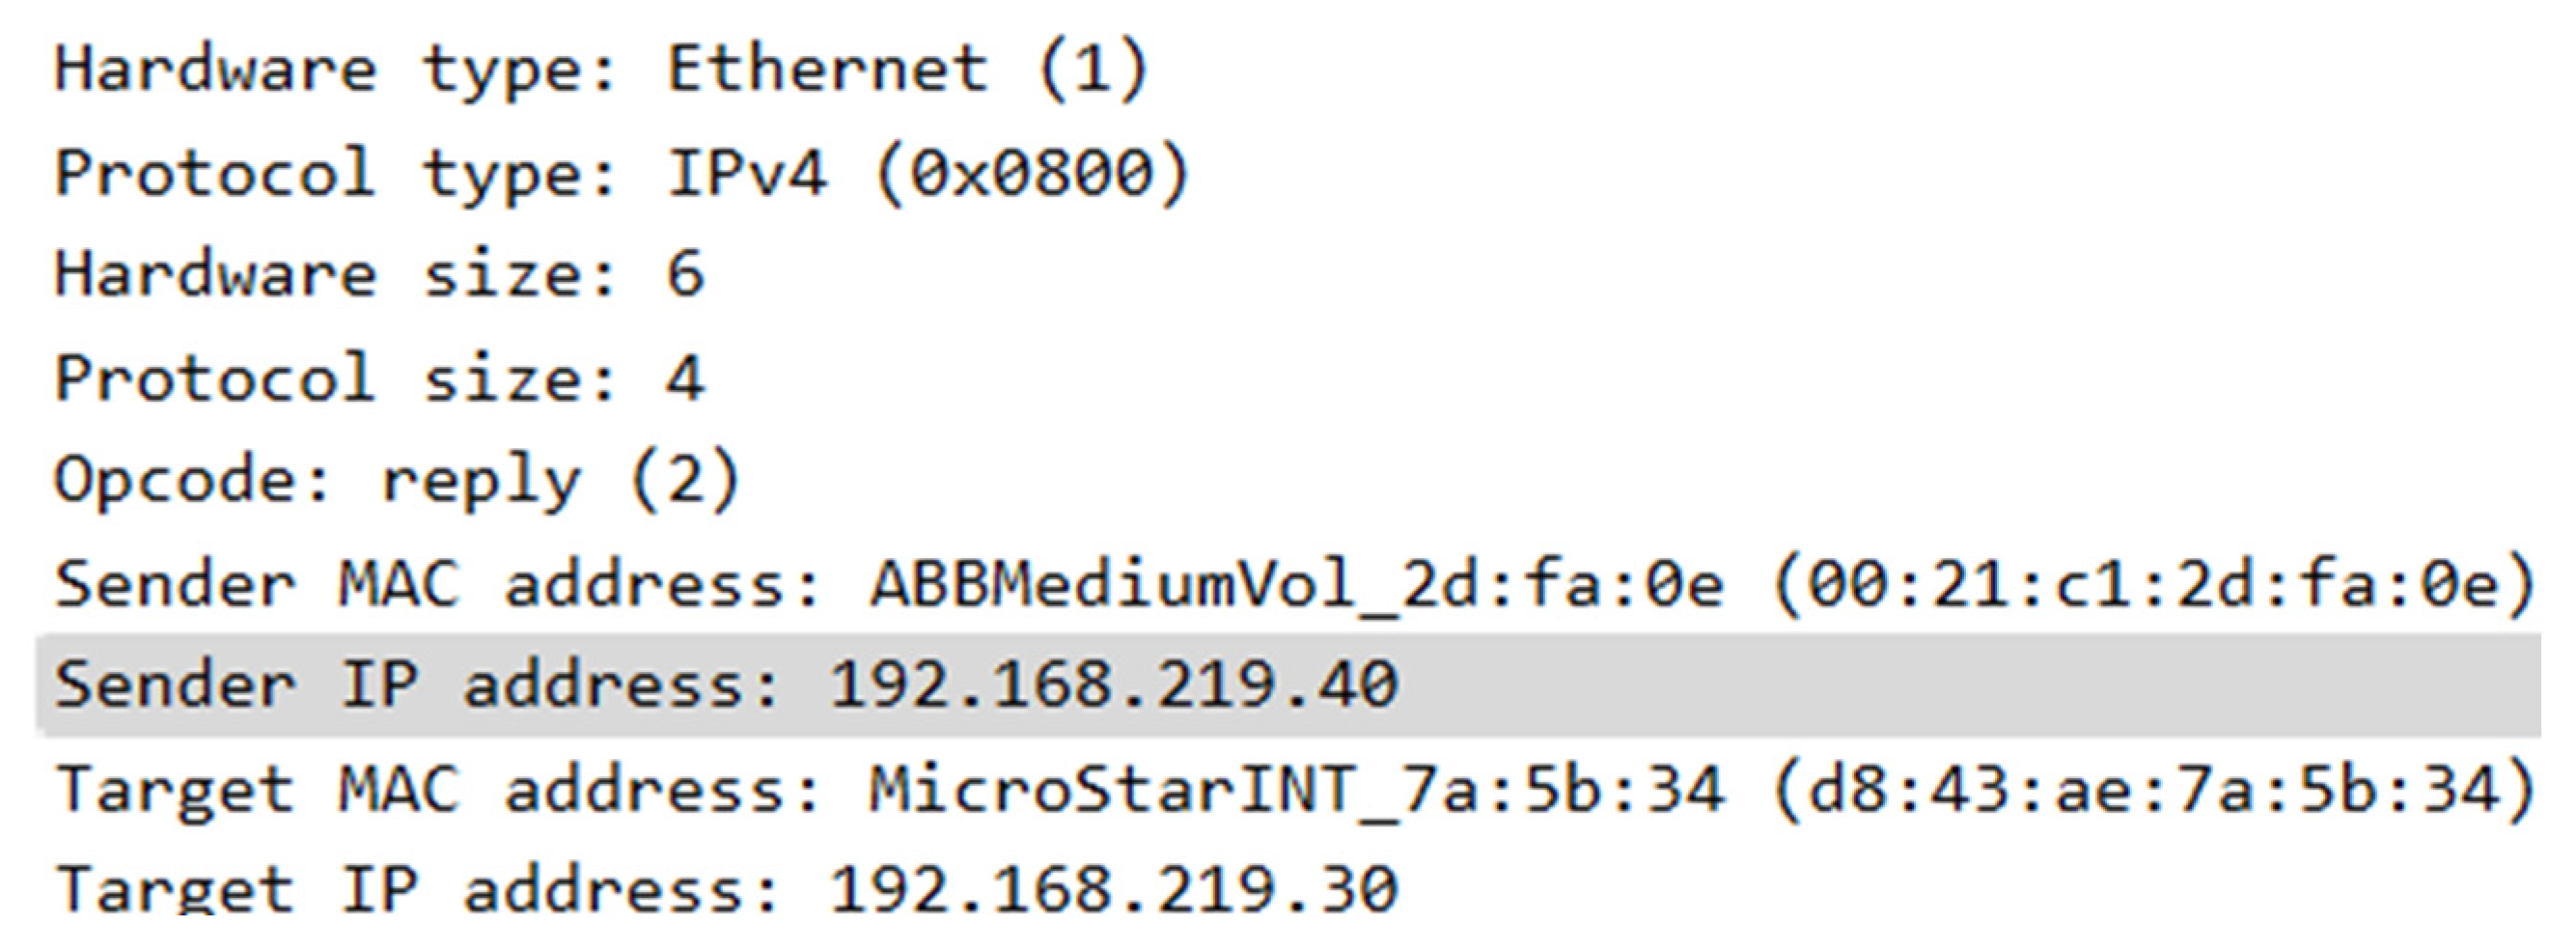
Figure 17 depicts the MITM attack is successful. On the REF 615, it shows the target MAC address is my computer where the Target IP address is the REF 620.
Conversely the REF 620 shows the REF 615’s IP address shown with my computer’s MAC address.
5. Discussion
These cybersecurity attack simulations provide valuable insights into how various attack vectors can compromise the fundamental security pillars of microgrids: integrity, availability, and confidentiality.
The testbed environment facilitated the simulation of a diverse range of cyberattacks, including Man-in-the-Middle (MITM), Denial-of-Service (DoS), and MMS replay attacks. This comprehensive approach enabled a thorough evaluation of vulnerabilities within critical communication protocols, specifically MMS and GOOSE, which are indispensable for microgrid operation.
Each attack scenario was designed to evaluate its impact on both the control and protection systems of the microgrid. The simulations focused on demonstrating how malicious actors might intercept or manipulate data transmissions, disrupt time-sensitive communication, or induce network resource exhaustion. The testbed accurately simulated these scenarios, allowing for a granular assessment of the security posture of individual devices, such as Intelligent Electronic Devices (IEDs) and Supervisory Control and Data Acquisition (SCADA) systems.
While the developed experimental testbed provides a valuable platform for testing and validating microgrid control strategies, it has limitations. Specifically, it may not fully capture the complexity and dynamic behavior of larger microgrids or extreme grid events. The limitations highlight the need for further enhancement and integration with more advanced simulation tools or hybrid testing environments to support more comprehensive microgrid research.
Our research introduces an innovative approach to microgrid studies by implementing a realistic microgrid testbed environment focused on cybersecurity study. The primary objective is to design and deploy a microgrid testbed capable of simulating cybersecurity threats within a controlled setting, thereby enabling in-depth analysis of vulnerabilities and mitigation strategies. The testbed will be used to analyze network traffic, assess vulnerabilities, and understand potential attack vectors within a microgrid infrastructure. Furthermore, the insights gained from this analysis will inform the development of robust defense mechanisms, enabling the design of more resilient microgrid systems capable of mitigating cyber threats in the future.