


Abstract
Autonomous vehicles and intelligent traffic transportation are widely investigated for road networks. Context-aware traffic light scheduling algorithms determine signal phases by analyzing the real-time characteristics and contextual information of competing traffic flows. The context of traffic flows mainly considers the existence of regular, emergency, or heavy vehicles. This is an important factor in setting the phases of the traffic light schedule and assigning a high priority for emergency vehicles to pass through the signalized intersection first. VANET technology, through its communication capabilities and the exchange of data packets among moving vehicles, is utilized to collect real-time traffic information for the analyzed road scenarios. This introduces an attractive environment for hackers, intruders, and criminals to deceive drivers and intelligent infrastructure by manipulating the transmitted packets. This consequently leads to the deployment of less efficient traffic light scheduling algorithms. Therefore, ensuring secure communications between traveling vehicles and verifying the integrity of transmitted data are crucial. In this work, we investigate the possible attacks on the integrity of transferred messages and vehicles’ identities and their effects on the traffic light schedules. Then, a new secure context-aware traffic light scheduling system is proposed that guarantees the integrity of transmitted messages and verifies the vehicles’ identities. Finally, a comprehensive series of experiments were performed to assess the proposed secure system in comparison to the absence of security mechanisms within a simulated road intersection. We can infer from the experimental study that attacks on the integrity of vehicles have different effects on the efficiency of the scheduling algorithm. The throughput of the signalized intersection and the waiting delay time of traveling vehicles are highly affected parameters.
1. Introduction
A context-aware traffic light scheduling algorithm is an example of a self-adaptive system. This system is characterized by its ability to gather real-time and dynamic information about its surrounding environment at any given period of time. Then, it adapts its behavior and sets the schedule accordingly [1]. Contextual or context-aware traffic lights use software and hardware to collect and analyze traffic data in their surrounding area. Then, they set the sequence of phases and the time of each phase according to the gathered data and driving rules over the road network. This includes the traffic densities of competing traffic flows at the shared road intersections controlled by the intelligent traffic lights. The estimated arrival times of the vehicle plateau in the different traffic flows. In addition, emergency or heavy vehicles may exist among the competing flows and their locations [2,3].
Many research studies on context-aware traffic light scheduling systems have been proposed to design intelligent algorithms and techniques [2,3,4]. In vehicular network technology, vehicles announce their existence and real-time characteristics through periodic “hello” messages transmitted within their transmission ranges [5]. Vehicles are notified and informed about their neighboring traffic characteristics by collecting and analyzing the periodic messages of their surrounding vehicles [4,6,7]. Several protocols have been proposed to investigate the traffic characteristics of surrounding traffic on road networks using the technology of vehicular networks [5,8,9]. The intelligently located traffic lights are notified of the traffic characteristics and context of the competing traffic flows by reporting messages [4,10,11]. Emergency vehicles announce their existence as all other vehicles using these periodic “hello” messages. In these messages, each vehicle announces the vehicle type as an emergency vehicle. This is considered in the data analysis protocols, and surrounding traffic and infrastructure (i.e., traffic lights) are notified regarding the existence of these emergency vehicles to set the schedule accordingly. These data are analyzed and utilized in several other real-time and efficient applications, such as efficient path recommendation and driving assistance protocols [5,12,13].
Using vehicular network technology [14,15,16] allows vehicles and intelligent infrastructure to communicate on the road network and gather basic traffic data. However, this motivates hackers and criminals to attack and utilize the intelligent system to serve their benefits [17,18,19]. In general, security threats have not been considered sufficiently in this field of research. Simple manipulation of a traveling vehicle’s periodic “hello” message can significantly affect the correctness and efficiency of the traffic light scheduling algorithm. This happens when a regular vehicle announces itself as an emergency vehicle or an emergency vehicle announces itself as a regular vehicle. Moreover, a compromised reporting message reflects inaccurate traffic characteristics, and conditions of the traffic flow negatively affect the performance of the traffic light scheduling algorithms [18,20,21,22]. Consequently, in this work, we first study the possible attack scenarios regarding the integrity of the vehicle identity and their consequences on traffic light scheduling algorithms. Then, we propose a secure context-aware traffic light scheduling system that guarantees the integrity of the transferred messages and each vehicle’s announced identity. Finally, the performance of the proposed secure system compared to the insecure version is experimentally evaluated with different simulated attacks.
The remainder of this paper is organized as follows: Section 2 investigates previous studies that developed context-aware traffic light scheduling systems and previous security mechanisms used to achieve integrity. Then, the possible attacks on the integrity targets in the context-aware traffic light scheduling systems are studied in Section 3. In Section 4, we introduced the detailed steps of the proposed secure context-aware traffic light system (SCATLS). The performance of the proposed system (SCATLS) is evaluated by an extensive set of experiments in Section 5. Finally, Section 6 concludes the entire paper.
2. Related Work
This section first investigates previously proposed context-aware traffic light scheduling algorithms. Second, the security mechanisms that have been used to guarantee the integrity of transmitted messages over VANETs have been investigated.
2.1. Context-Aware Traffic Light Scheduling Algorithms
The context-aware traffic light scheduling algorithms aim to set the sequence phases of the traffic lights installed at road intersections [2,3]. The context of the competing traffic flows in terms of traffic density, traffic speed, traffic volume, and existing emergency or heavy vehicles was also considered for scheduling the efficient sequence of phases [2,3]. Table 1 systematically summarizes the main characteristics of previous intelligent traffic light control mechanisms. We compare the mechanisms used to gather the traffic characteristics, the technology used in the proposed algorithm, the main considerations of each algorithm, and the type of vehicles considered.
Table 1.
Mechanism for intelligent traffic lights.
Emergency vehicles (i.e., ambulances, fire trucks, and police cars) are given precedence while crossing road intersections. Several traffic light scheduling algorithms have been proposed to adapt the traffic light schedule according to the appearance of the emergency vehicle on competing traffic flows. First, context-aware traffic light self-scheduling (CA-TLS) [2,3] is one of the algorithms designed to prioritize emergency vehicles to allow them to pass through the intersection quickly and safely. Whenever an emergency vehicle is detected near a signaled road intersection, the algorithm schedules a “HALT” phase for the traffic light, interrupting the green phase to allow the emergency vehicle to pass through the intersection as quickly as possible (i.e., without stopping). Indeed, the continuing traffic flow is prioritized based on the type of emergency vehicle in that flow. Moreover, if several emergency vehicles arrive at the same intersection simultaneously, the algorithm reschedules the traffic light phases to allow these vehicles to pass through the intersection smoothly and safely [2,3]. The “HALT” phase is set to a certain time to allow all detected emergency vehicles to pass the intersection successfully. Prioritizing emergency vehicles can help improve emergency response times [2,3].
To address the problem of traffic congestion caused by the increased use of vehicles, a smart vehicle system has been implemented [23,25,26]. This system collects real-time traffic data at a road intersection using VANETs (Vehicular Ad Hoc Networks). The intelligent traffic light scheduling algorithm uses the data as input to produce the sequence phases and timing schedule of the traffic lights. At each intersection, moving vehicles notify the traffic light regarding the traffic characteristics of the competing traffic flows. According to the real-time traffic characteristics, the traffic light selects the phase schedule. Moreover, the sequence of traffic lights synchronizes to determine how the platoons of vehicles can pass through these intersections smoothly without stopping. These traffic lights monitor vehicles by negotiating their requests to cross the signaled intersection using the intelligent context-aware negotiation protocol (ICANP). To synchronize and alter the passage of quantum time, the group of installed traffic lights exchange control messages. In the event of an emergency vehicle’s appearance, the sequence of existing traffic lights synchronizes to allow that emergency vehicle to pass through smoothly and fast [23].
Furthermore, an effective traffic light scheduling system (SmartLight) [4] is proposed for heavy vehicles. This system manages conflicting traffic flows at road intersections. It aims to reduce the overall fuel consumption, which reduces gas generation, the typical amount of time that vehicles are idle, and the efficiency of road intersections. The traffic light uses a proposed algorithm to determine the successive phases of each traffic light cycle and set the effective scheduling time for each phase, considering real-time traffic and environmental conditions.
In addition, a system was created for regulating traffic flow at intersections with traffic lights. This system, known as the adaptive traffic light control system (ATLCS) [24], schedules the movement of traffic competing for access to the intersection. It assigns higher priority to vehicles exiting onto the main road to coordinate the traffic light controllers at a series of intersections along the same road. Magnetometers are utilized to sense and measure the characteristics of competing traffic flows at each intersection. These sensors detect the presence of vehicles as they pass over them by sensing changes in the Earth’s magnetic field. The readings obtained from the magnetometers are then fed into the algorithm controlling the traffic light controller to select the optimal traffic light schedule.
2.2. Secure Traffic Light Scheduling Algorithms
On the other hand, several research studies have considered the security requirements for intelligent traffic light systems. Table 2 summarizes the main technologies used to secure intelligent traffic light control systems over the road network. First, a simple fog computing system for controlling traffic lights has been proposed [27], called secure intelligent traffic light control using fog computing. This system is based on a previous scheme to mitigate denial of service (DoS) attacks. The system’s security is based on creating a set of Diffie–Hellman (CDH) codes with varying levels of difficulty based on the traffic light condition. These puzzles are encoded using location-based encryption and broadcast to nearby vehicles in the selected area. Only vehicles in this area can receive the puzzle, which must be solved within a specified time. Once the puzzle is solved, the vehicle sends a hint to the traffic light to check the solution. The protocol is effective against DoS attacks, usually thwarted using cryptographic puzzles.
Table 2.
Secure intelligent traffic light.
Furthermore, a security framework called FSF-ITLCS (fog-based security framework for intelligent traffic light control system) [28] has been introduced. This is used to protect traffic signals in intelligent traffic control systems. The framework uses various technologies such as encryption, hashing functions, and digital signatures to keep traffic lights confidential and maintain their integrity and credibility. The system consists of division motor vehicles (DMVs), roadside units (RSUs), and vehicles. The DMV registers vehicles and installs RSUs with computing power and storage capacity in the monitored area. The RSU sends encrypted messages and certificates to vehicles within its monitoring area, and each vehicle has an onboard unit (OBU) with communication and computing capabilities. The proposed technique involves a random seed puzzle sent to each vehicle when it enters the monitored area. All vehicles must solve the puzzle and follow the protocols broadcast by the RSU to ensure the safety of the traffic light. The framework effectively prevented various attacks, including replay, denial of service, Sybil, and impersonation attacks.
Recently, a new intelligent traffic management system (ITMS) [29] has been proposed that uses existing VANETs and Internet of Vehicles (IoV) technologies. This system is designed to be suitable for future traffic systems and smart cities. The proposed ITMS architecture includes a smart traffic signal (STS) controller that communicates with traveling vehicles through roadside units (RSUs) installed along the road. The system uses a global navigation satellite system (GNSS) to determine the vehicle’s position, direction, and speed. An onboard unit (OBU) called the smart traffic light (STS) is also included in the system to provide the necessary services. To ensure vehicle security and privacy, the OBU has digital and anonymous certificates issued by the transportation agency or manufacturer and protects communications between the vehicle and other units, such as traffic signals. In addition, RSUs periodically send certificates to ensure that vehicles are communicating with real traffic signals.
Finally, Ozkul et al. [30] proposed one of the most important systems for secure traffic control systems. This system can detect the presence of emergency vehicles, such as ambulances, fire trucks, and police vehicles, within the communication range of each vehicle. Hence, crossing the intersection gives them a higher priority to reduce waiting times. Sensors and VANET technology were used to gather traffic characteristics. Each vehicle is designed as a virtual sensor that reports traffic conditions, such as speed and location, to a traffic signal controller through a secure, lightweight protocol that uses digital signature encryption to keep the vehicle’s identity and location anonymous from any other vehicle in the system. Each vehicle must be registered with the trusted body in the system and given a valid digital certificate. A set of false identifiers is placed on the vehicles, and the vehicle identification information is kept in its register in a database completely trusted by all vehicles. This protocol prevents message manipulation, replay attacks, and vehicle impersonation.
We can infer that previous studies did not directly consider the problems related to a simple manipulation of the transmitted packets announced by each vehicle. The problems resulting from an ordinary vehicle announcing itself as an emergency vehicle or an emergency vehicle announcing itself as a regular vehicle are serious and cause complete changes to the traffic light schedule. Drivers could waste increased time unfairly waiting at the signalized road intersection due to these attacks. This motivates us to propose a secure context-aware traffic light scheduling system. This system guarantees the integrity of the transferred messages, especially the correctness of the vehicle’s identity and type. Thus, it aims to enhance traffic safety and efficiency at the signalized road intersections. The existence of emergency vehicles at the signalized intersection has not been considered in any of the previous studies in this field of research.
3. The Possible Attacks in the Context-Aware Traffic Light Scheduling Systems and Threat Models
This section identifies possible attack scenarios on the context-aware traffic light scheduling system and the consequences of each attack. As we discussed, the intelligent traffic lights at road intersections consider the real-time traffic distribution and context of the competing traffic flows to schedule the sequence phases of the located traffic light. The technology of vehicular networks has been used to gather the basic traffic data of the competing traffic flows. Each vehicle periodically broadcasts a “hello” message that announces its existence and basic traffic data. The intelligent traffic light gathers and analyzes these messages to schedule the phases of that traffic light efficiently.
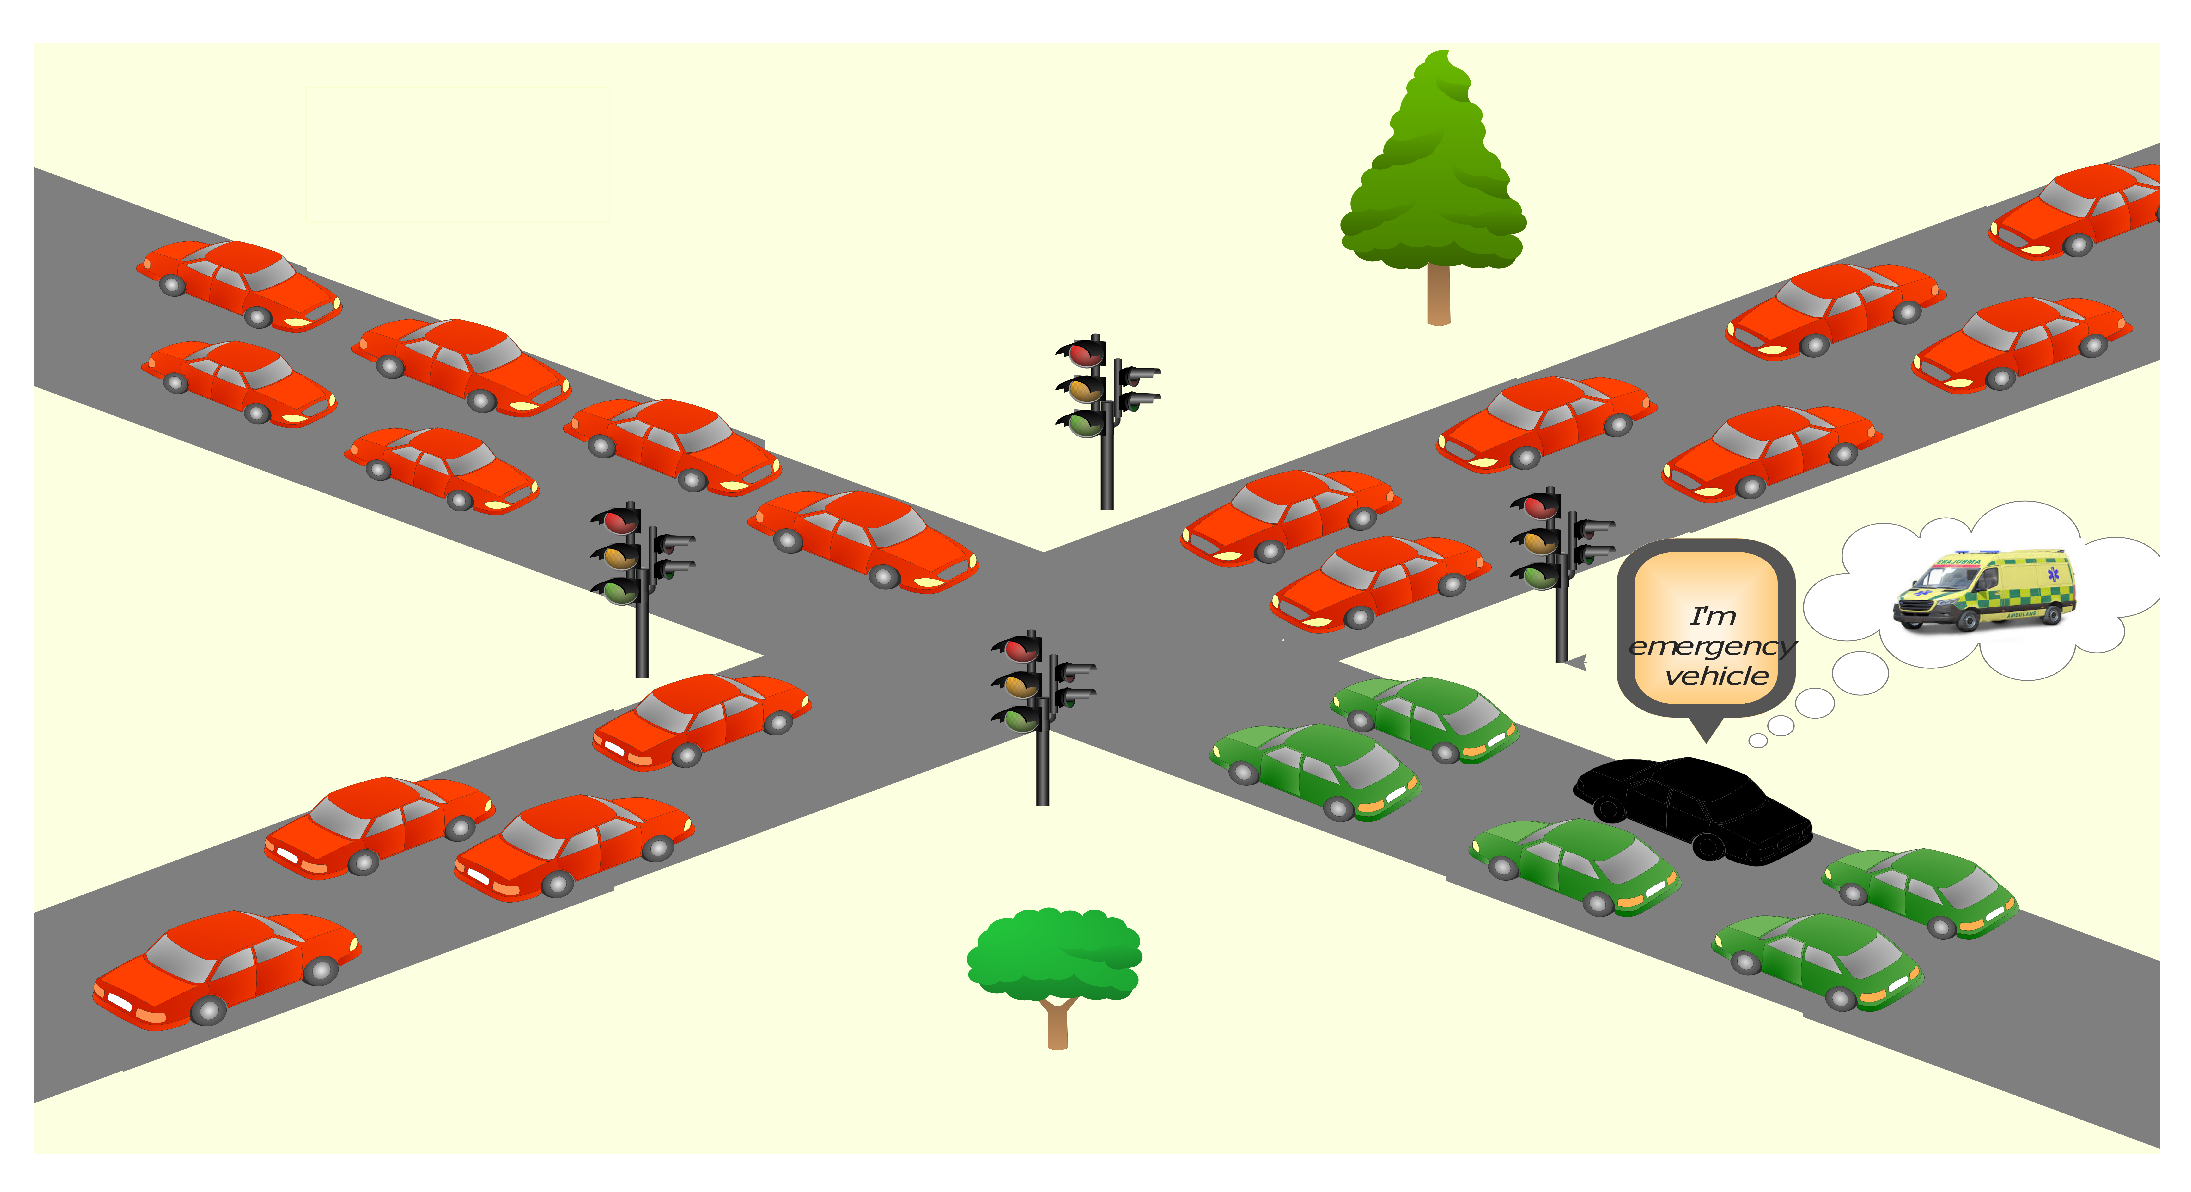
The first possible attack on the intelligent context-aware traffic light starts from regular vehicles. A regular attacker vehicle can impersonate the role of an emergency vehicle. This is mainly to obtain a higher priority to pass through the signalized intersection and avoid the waiting delay time at the busy intersection. Figure 1 graphically illustrates this attack scenario. The black vehicle announces itself as an emergency vehicle in this Figure. The traffic scheduling system in the intelligent traffic light assigns a high priority to the traffic flow that contains the fake emergency vehicle (i.e., black vehicle or attacker vehicle).
Figure 1.
Attack by a regular vehicle impersonating the role of an emergency vehicle.
This attack has two main consequences on the surrounding traffic. Vehicles mainly aim to pass through the signalized intersection:
- Vehicles on the same traffic flow as the attacker vehicle can take advantage of the attack. They are scheduled to pass the intersection fast with the fake emergency vehicle announced. Thus, we can call these vehicles innocent beneficiaries (i.e., gainers); they are colored green in Figure 1.
- Vehicles on the other flows will be negatively affected by the attack (i.e., victims). They will have to wait for the traffic flow that contains the fake emergency vehicle to pass through the intersection. These vehicles are colored red in Figure 1.
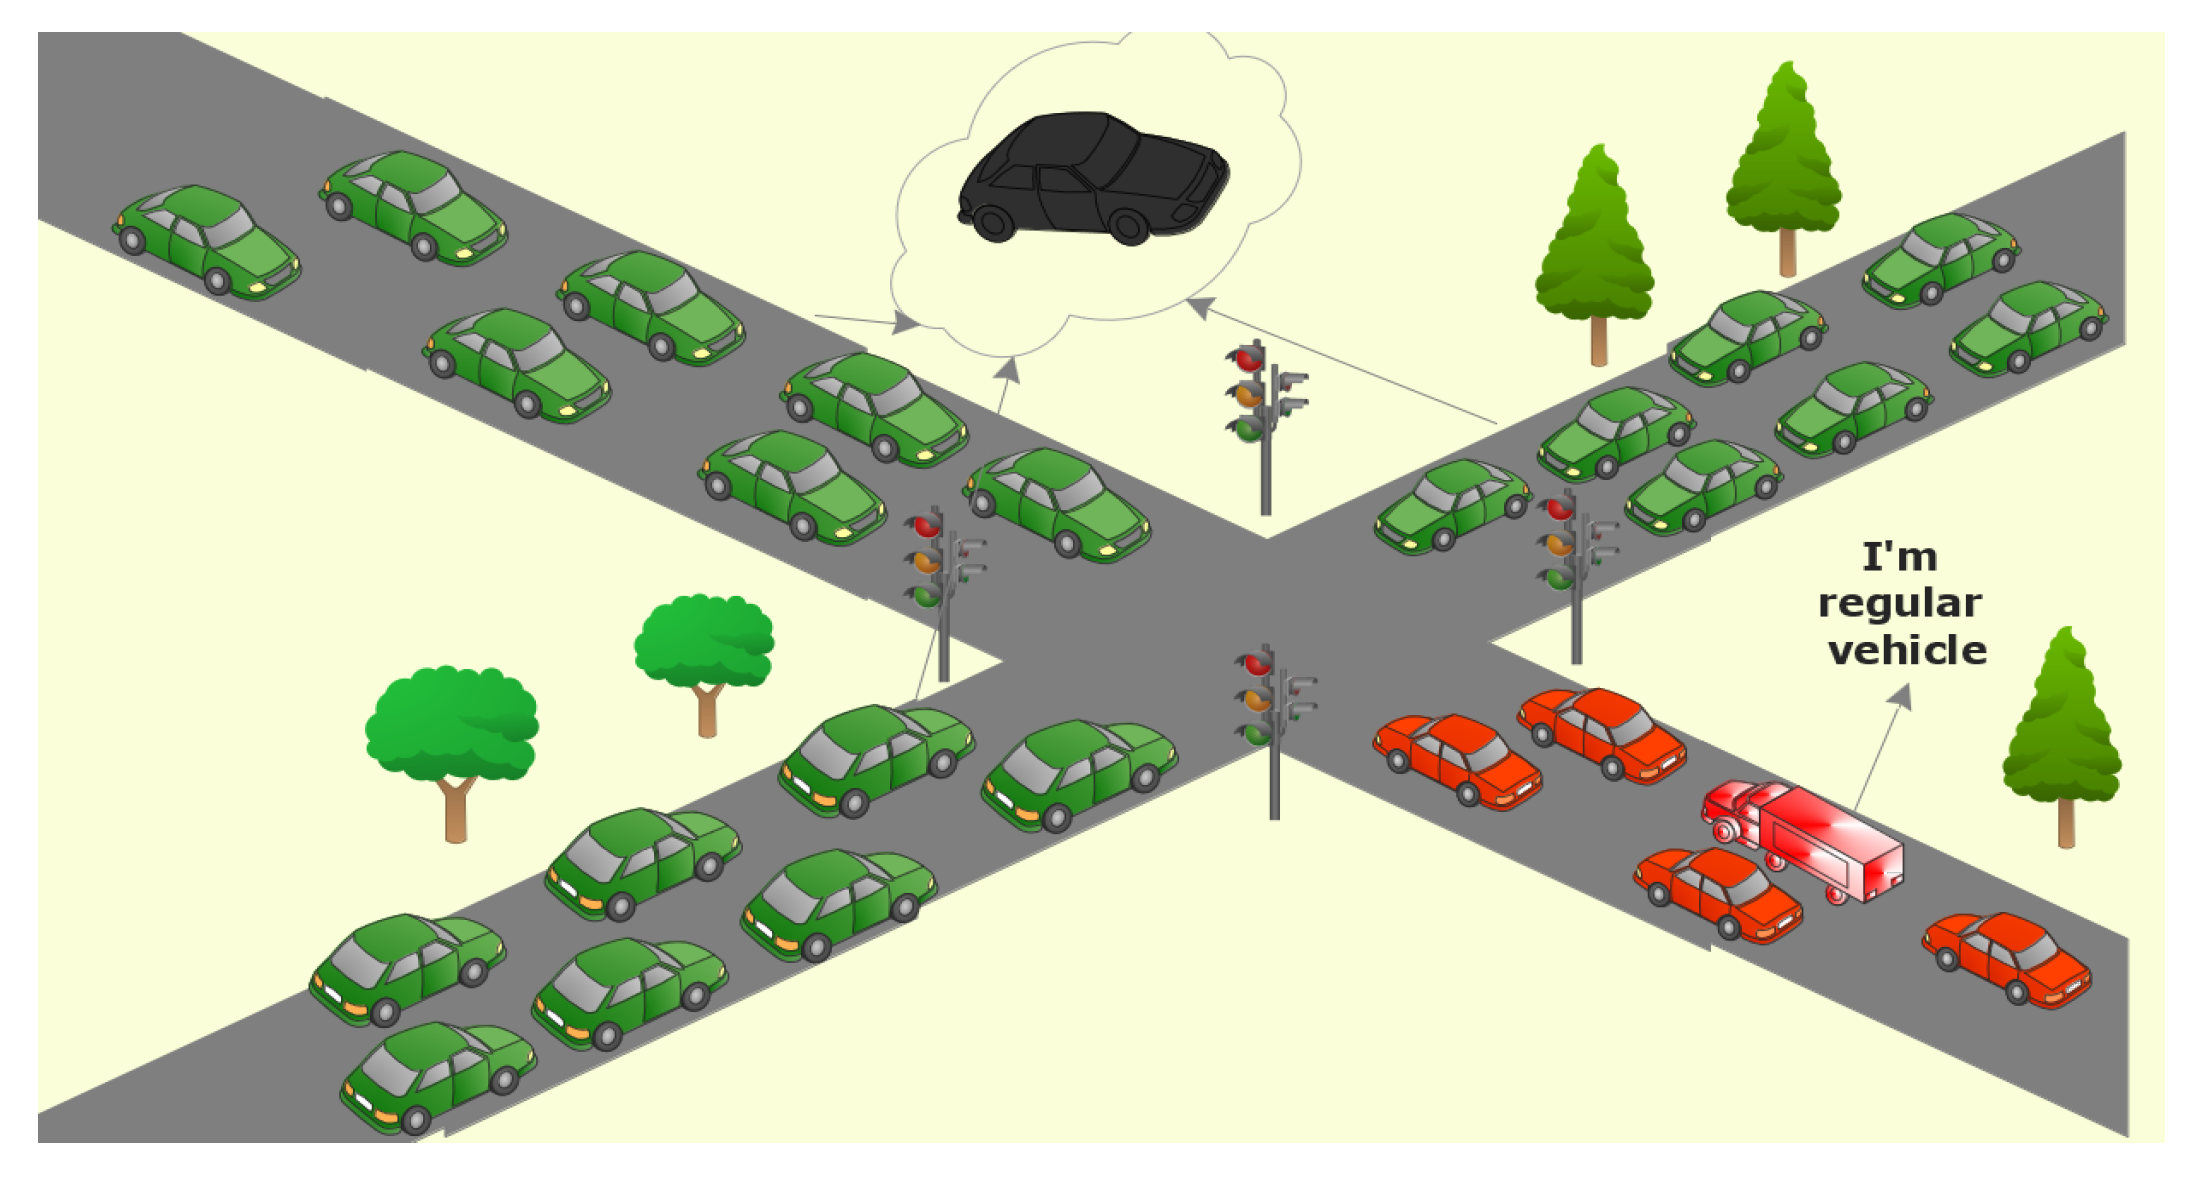
The other possible attack on the context-aware traffic light scheduling system graphically appears in Figure 2. This attack is not initiated internally by traveling vehicles as in the previous scenario. However, in this scenario, an external node manipulates the content of an existing emergency vehicle’s “hello” message. It sets the vehicle type in the announced message to “regular vehicle,” which eliminates any higher priorities that can be assigned to schedule the traffic flow.
Figure 2.
Attack on the emergency vehicle’s priority request message.
This attack also has two main consequences on the surrounding traffic, mainly on vehicles that aim to pass through the signalized intersection:
- Vehicles on the other side of the emergency vehicle can take advantage of the attack. They are scheduled to pass the intersection quickly due to the denial of emergency vehicles. Thus, these vehicles are the gainers of this attack; they are colored green in Figure 2. One of these vehicles may be the initiator of this type of attack.
- Vehicles on the same traffic flow will be negatively affected by the attack (i.e., victims). These vehicles are red in Figure 2.
Table 3 systematically illustrates the threat model of the proposed secure protocol. It mainly defines the investigated threats in the proposed work. It declares the initiator of each attack and determines the beneficiaries and affected entities of each attack. This is in terms of decreasing or increasing the waiting delay time at the signalized road intersection.
Table 3.
The threat model of the proposed secure protocol.
4. Secure Context-Aware Traffic Light Scheduling System
This section introduces a secure context-aware traffic light scheduling system (SCATLS). This is mainly based on the context-aware traffic light scheduling algorithm (i.e., CATLS) proposed by Younes et al. [2,3] that mainly considers the higher priorities of emergency vehicles at signalized road intersections. However, the newly proposed version incorporates digital signature encryption using the Elliptic Curve Digital Signature Algorithm (ECDSA) [31,32,33] and hashing algorithms [34,35] to achieve the integrity of gathered data used by the scheduling algorithm. The proposed system ensures vehicles’ identities and prevents illegal manipulations in vehicle-to-vehicle (V2V) and vehicle-to-infrastructure (V2I) communications.
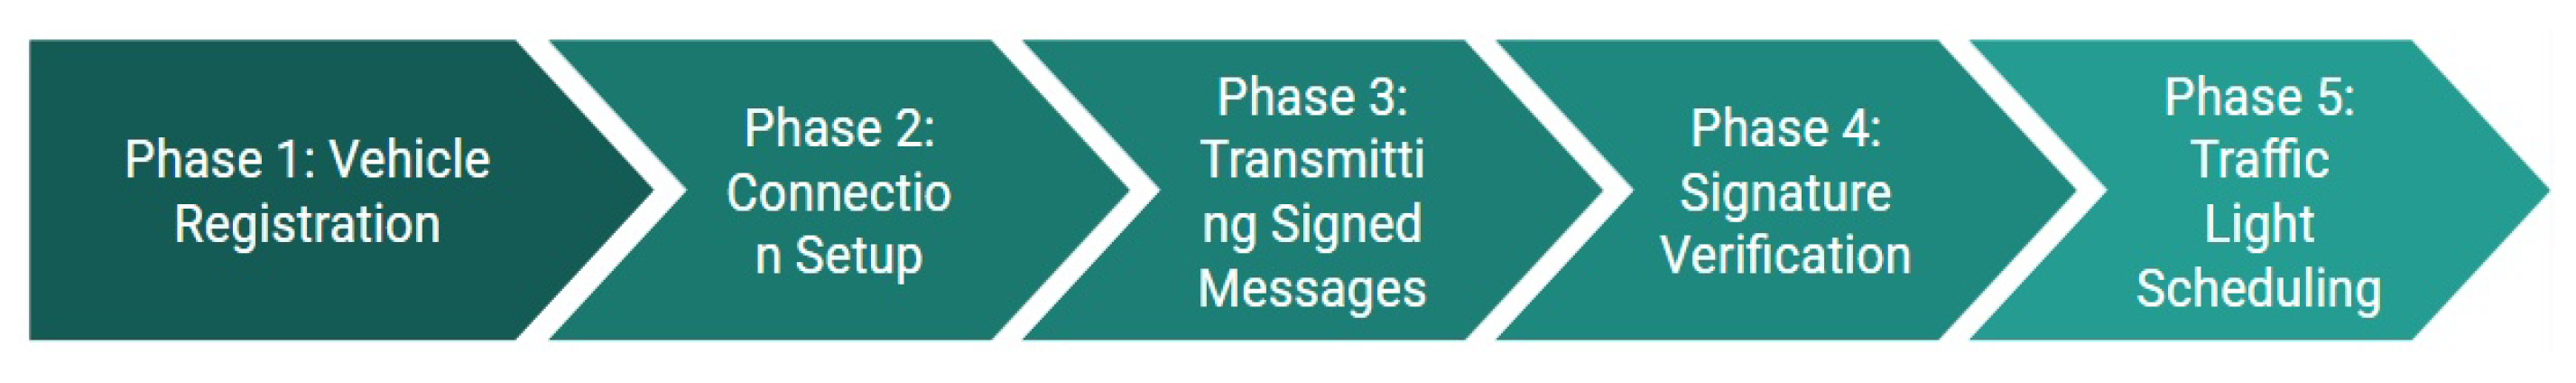
The proposed SCATLS system has two main goals: First, it prevents vehicle impersonation and identity theft. Second, it prevents manipulation of the message’s content sent by emergency vehicles that mainly aim to change the vehicle’s type. The main phases of the proposed system are presented in the rest of this section. Moreover, Figure 3 graphically shows the main phases of the proposed SCATLS.
Figure 3.
General framework of SCATLS.
- Phase 1: Vehicle Registration
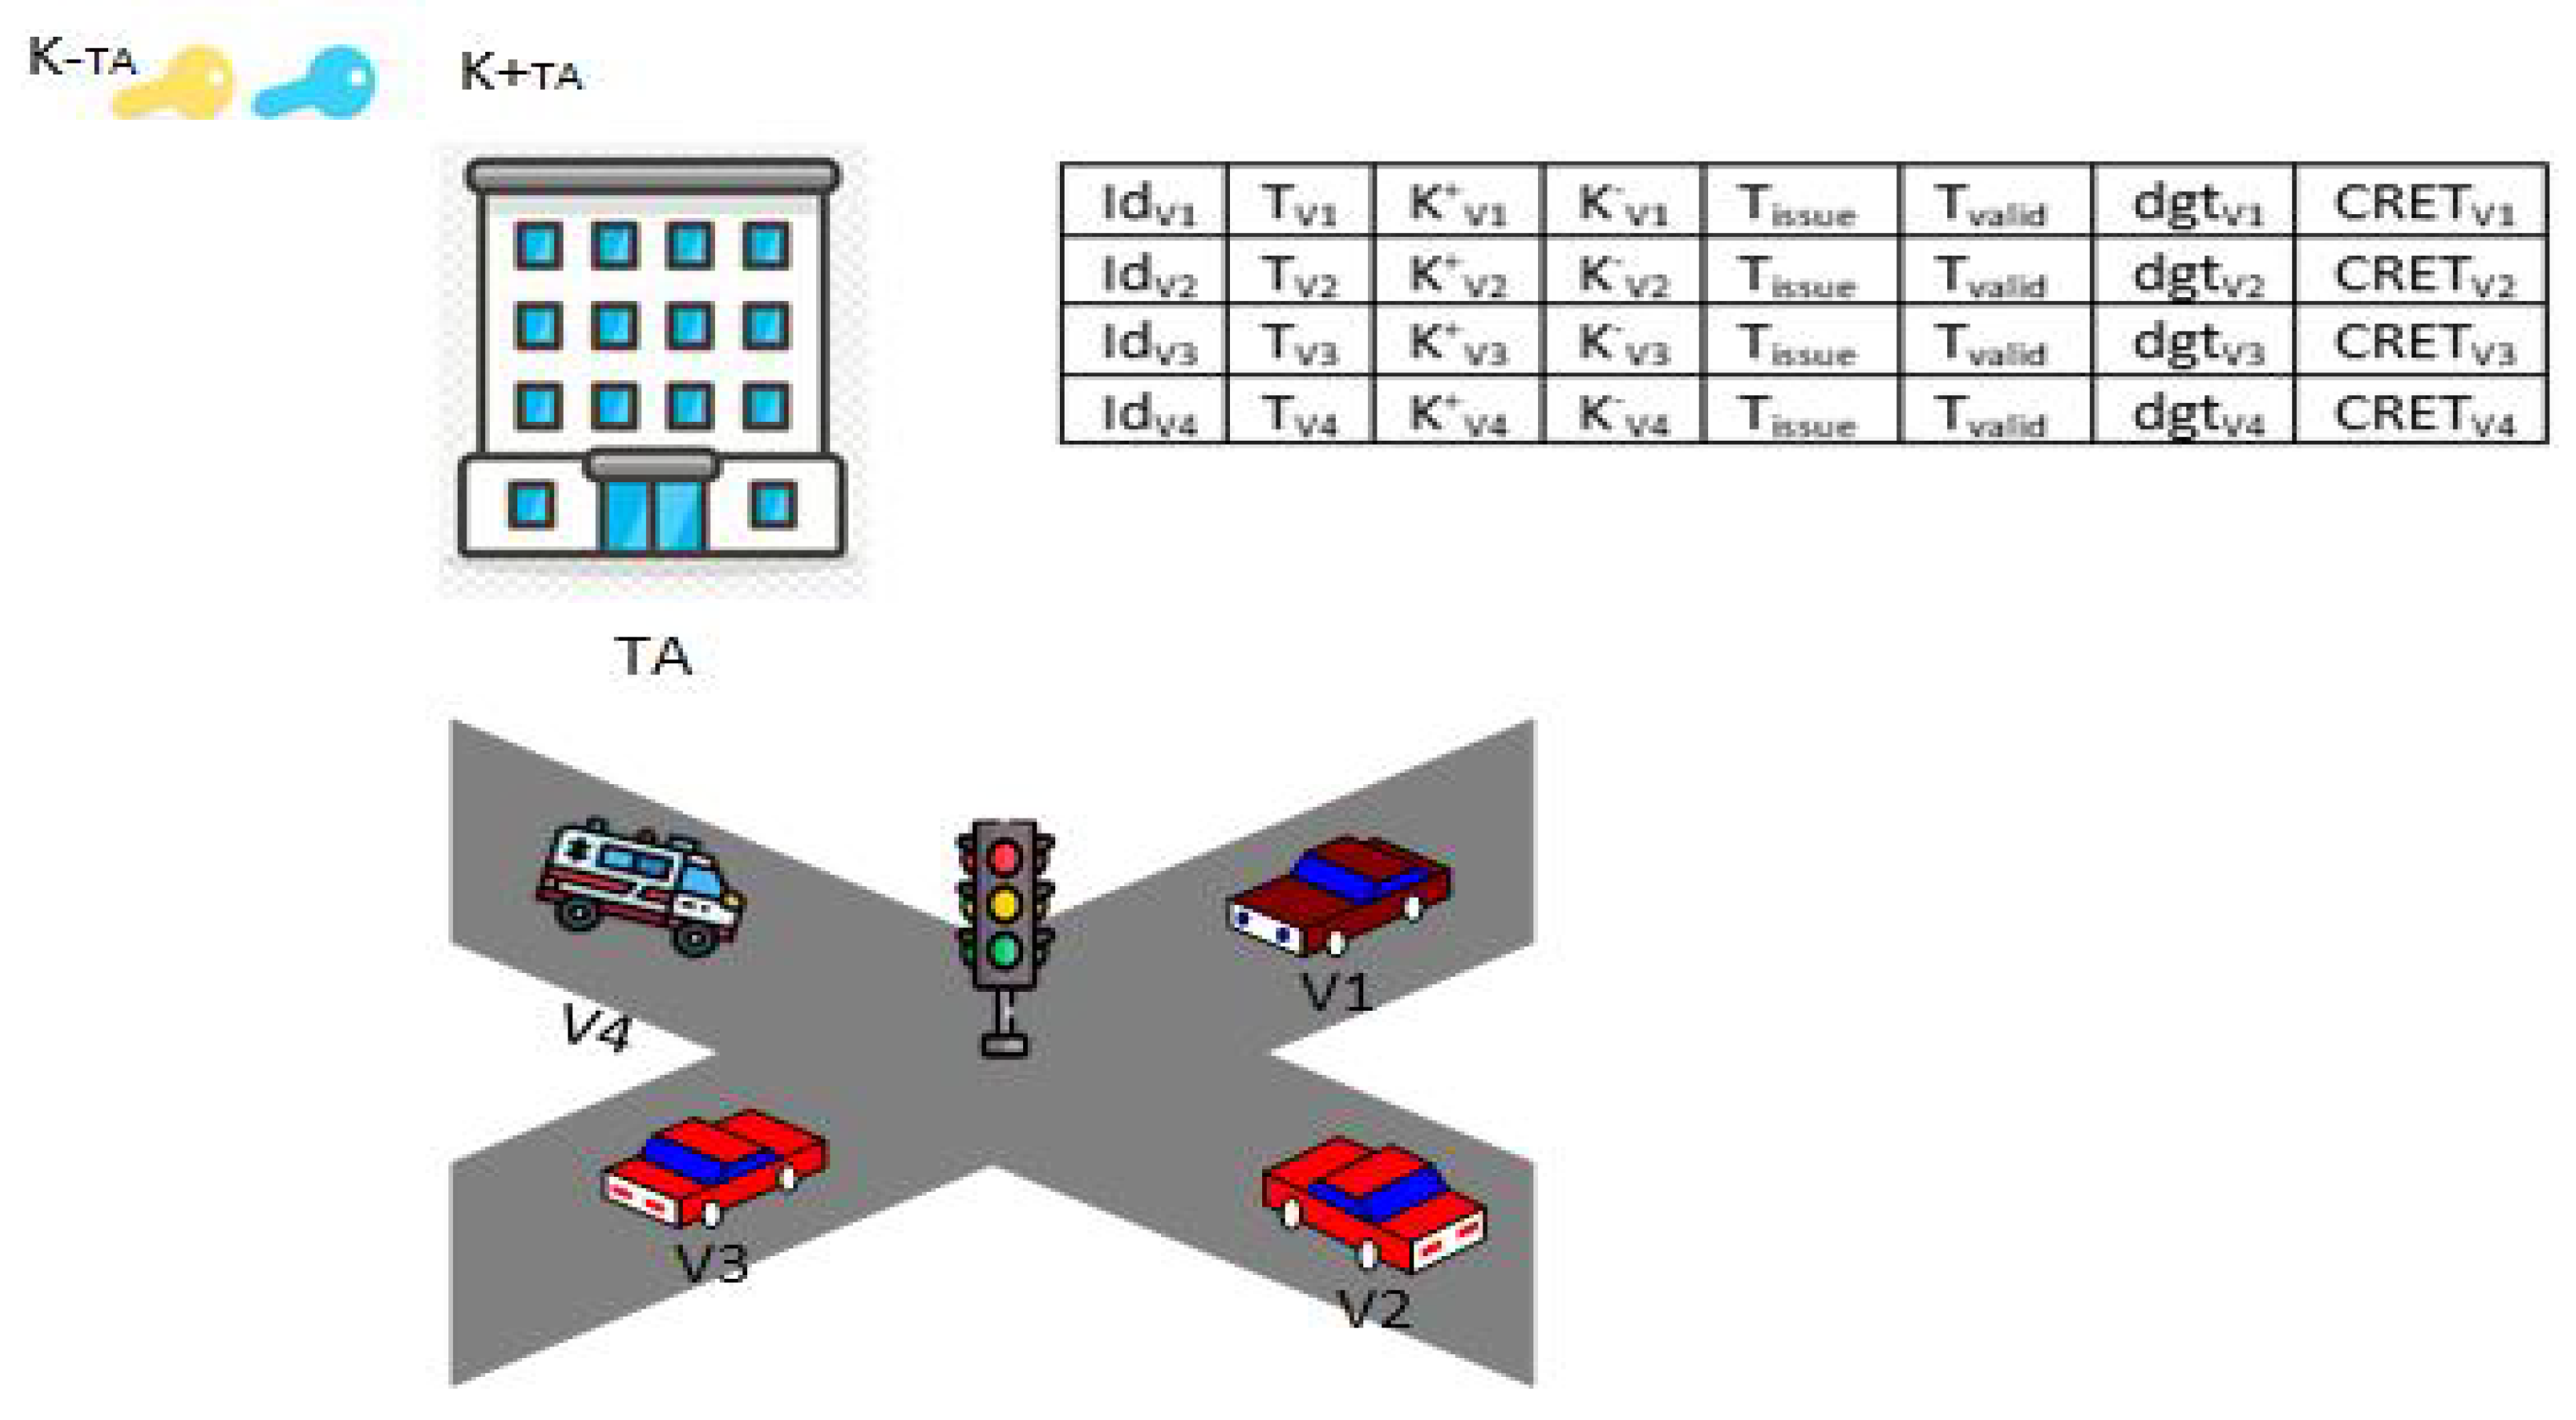
- All vehicles on the road network should be registered with a certain traffic authority (TA). This is centrally run by the government. Each vehicle should be assigned a unique identifier to be distinguished and tracked over the road network. Its type (), if it is an ambulance, fire truck, police, or regular vehicle, should also be identified inside the associated database of the TA.
- Generation of cryptographic keys: The traffic authority (TA) produces a distinct ECDSA key pair which includes a public key () and private key () for every registered vehicle, using Cryptographically Secure Pseudorandom Number Generation (CSPRNG) [36].
- Message Digest: The generated message should be hashed using an efficient and secure function such as SHA-2 [34]. This is to create a message digest for that vehicle that could be added to any message and prove the identities of vehicles. This includes the vehicle identification , emergency type , public key , issuing date/time (, and validity period . Equation (1) computes the message digest used to sign messages efficiently.
- Certificate generation: The TA generates a digital certificate () that is encrypted by the private key of that TA () for every vehicle. The is used to be encrypted by the private key of the TA. Equation (2) illustrates how to generate the certificate of each vehicle v inside the TA. The private key is known by the assigned vehicle, and it remains secure within the TA and connected to that .
Figure 4 illustrates an example of the parameters of traveling vehicles registered and assigned by the authorized traffic authority. These parameters facilitate secure communications among traveling vehicles over the road network and around the signalized road intersections.
Figure 4.
Vehicle registration phase.
- Phase 2: Connection Setup
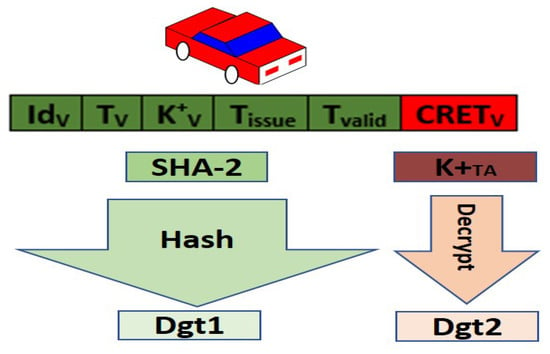
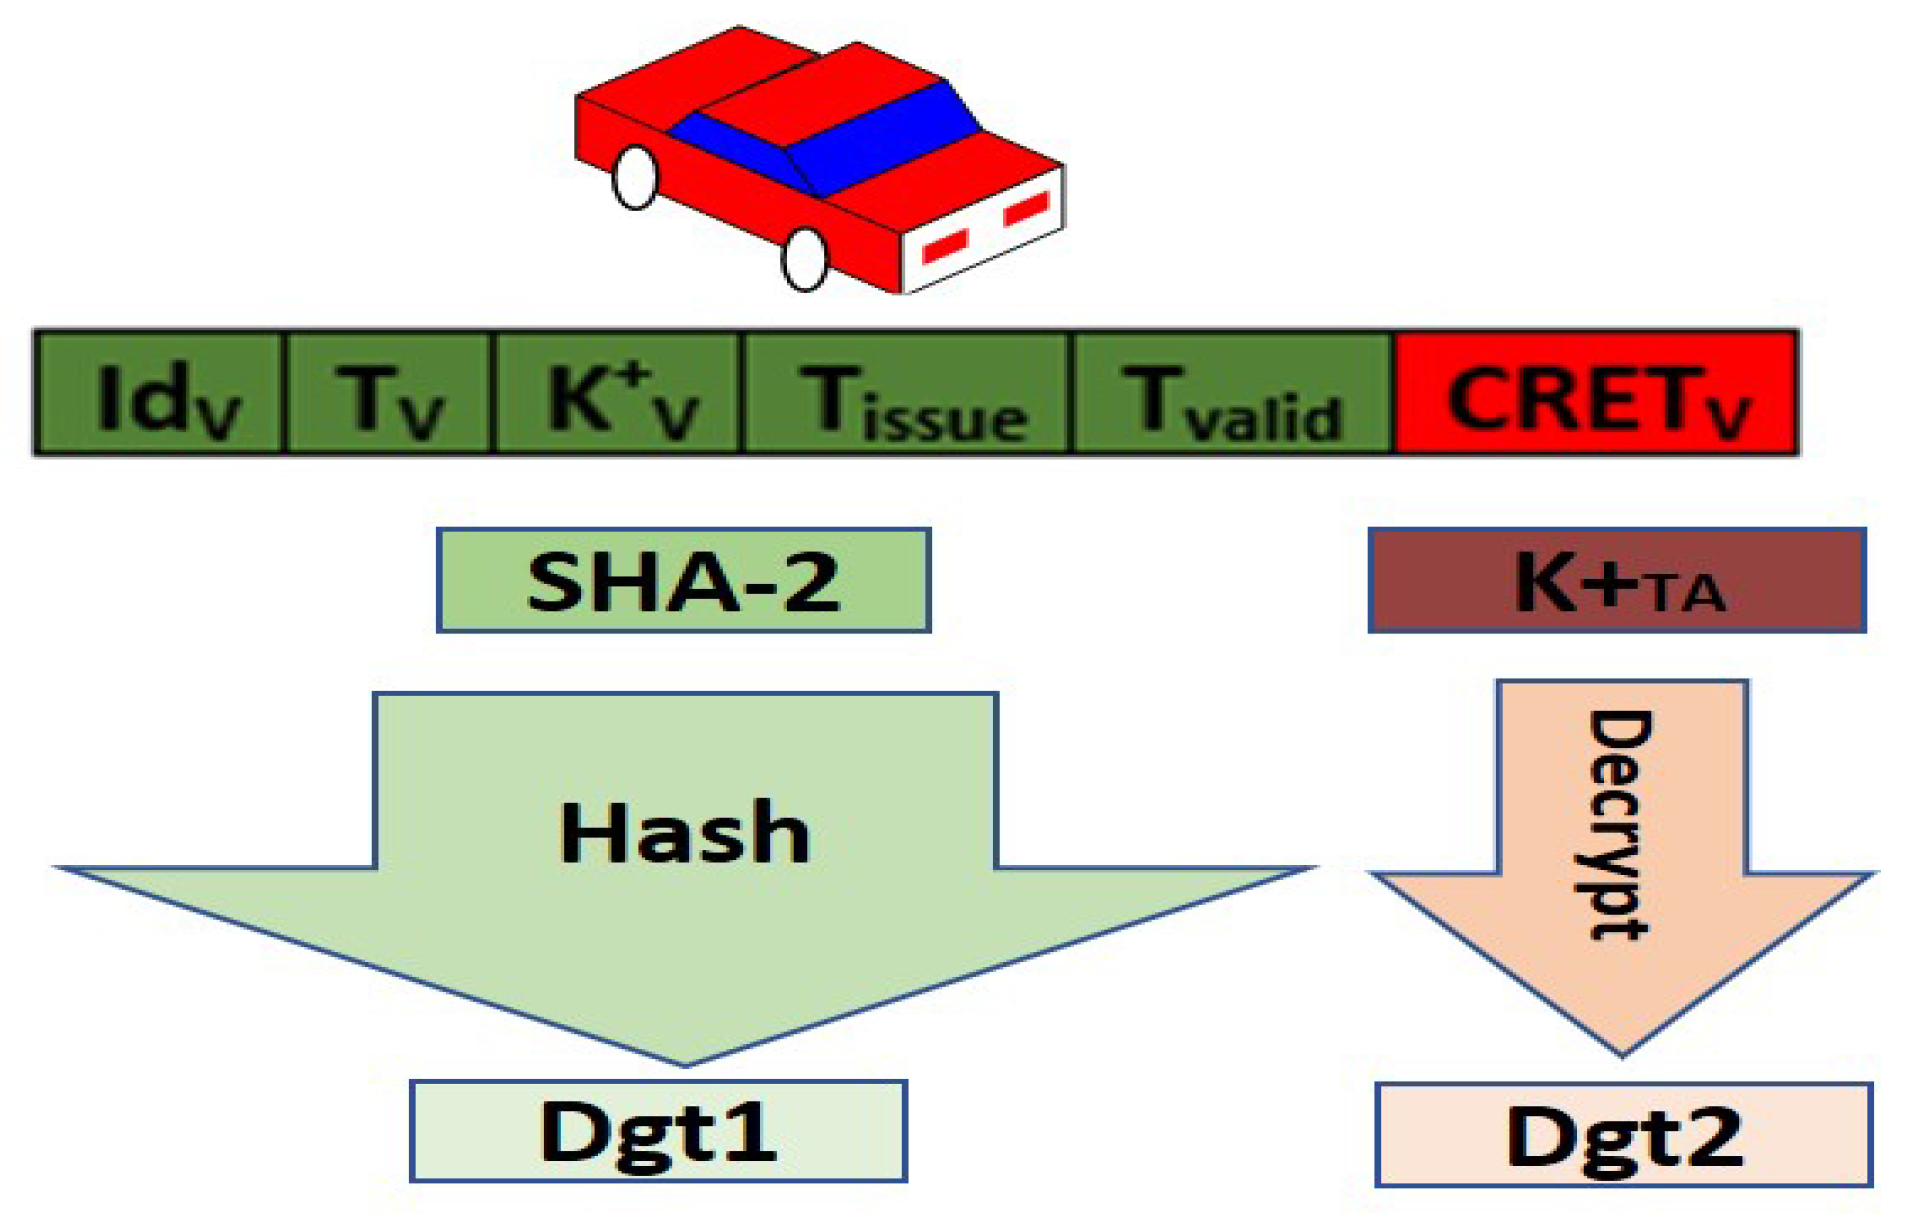
To ensure secure communication with nearby vehicles and infrastructure (e.g., traffic lights), vehicles begin by transmitting a setup message. This message includes , , , , , and . The main fields of the setup message are illustrated in Figure 5.
Figure 5.
Public key verification.
Upon receiving the setup message through VANETs, the receiver traffic light or vehicle uses the SHA-2 algorithm to hash the first five fields of the message (i.e., , , , , and ) and obtain . On the other hand, it uses the , which can be obtained directly from the TA, to decrypt the last field of the message (i.e., ) and obtains . The receiver compares and ; if they are the same, it verifies the announced key () of that vehicle (). Figure 5 illustrates the steps in verifying the contents of the setup message sent by registered vehicles.
- Phase 3: Transmitting Signed Messages.
Vehicles transmit messages around the installed traffic lights for two main reasons. First, they announce an emergency vehicle’s existence and give it a higher priority to pass through the signalized road intersection. Second, they participate in computing the traffic flow characteristics, including speed, volume, and density. The content of these messages and their integrity greatly affect the efficient real-time schedule of that traffic light.
- Message Creation: Based on the target and mission of each message, its fields are selected accordingly. For example, periodic “hello” messages contain , , , , etc. Traffic report messages contain the covered area, traffic speed, traffic density, etc. Other data announcing and gathering messages can be created and sent according to the running protocol’s targets and procedures.
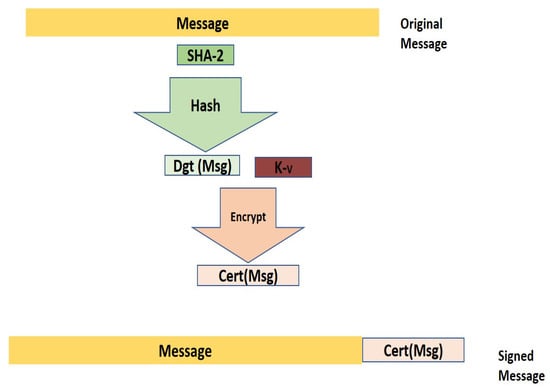
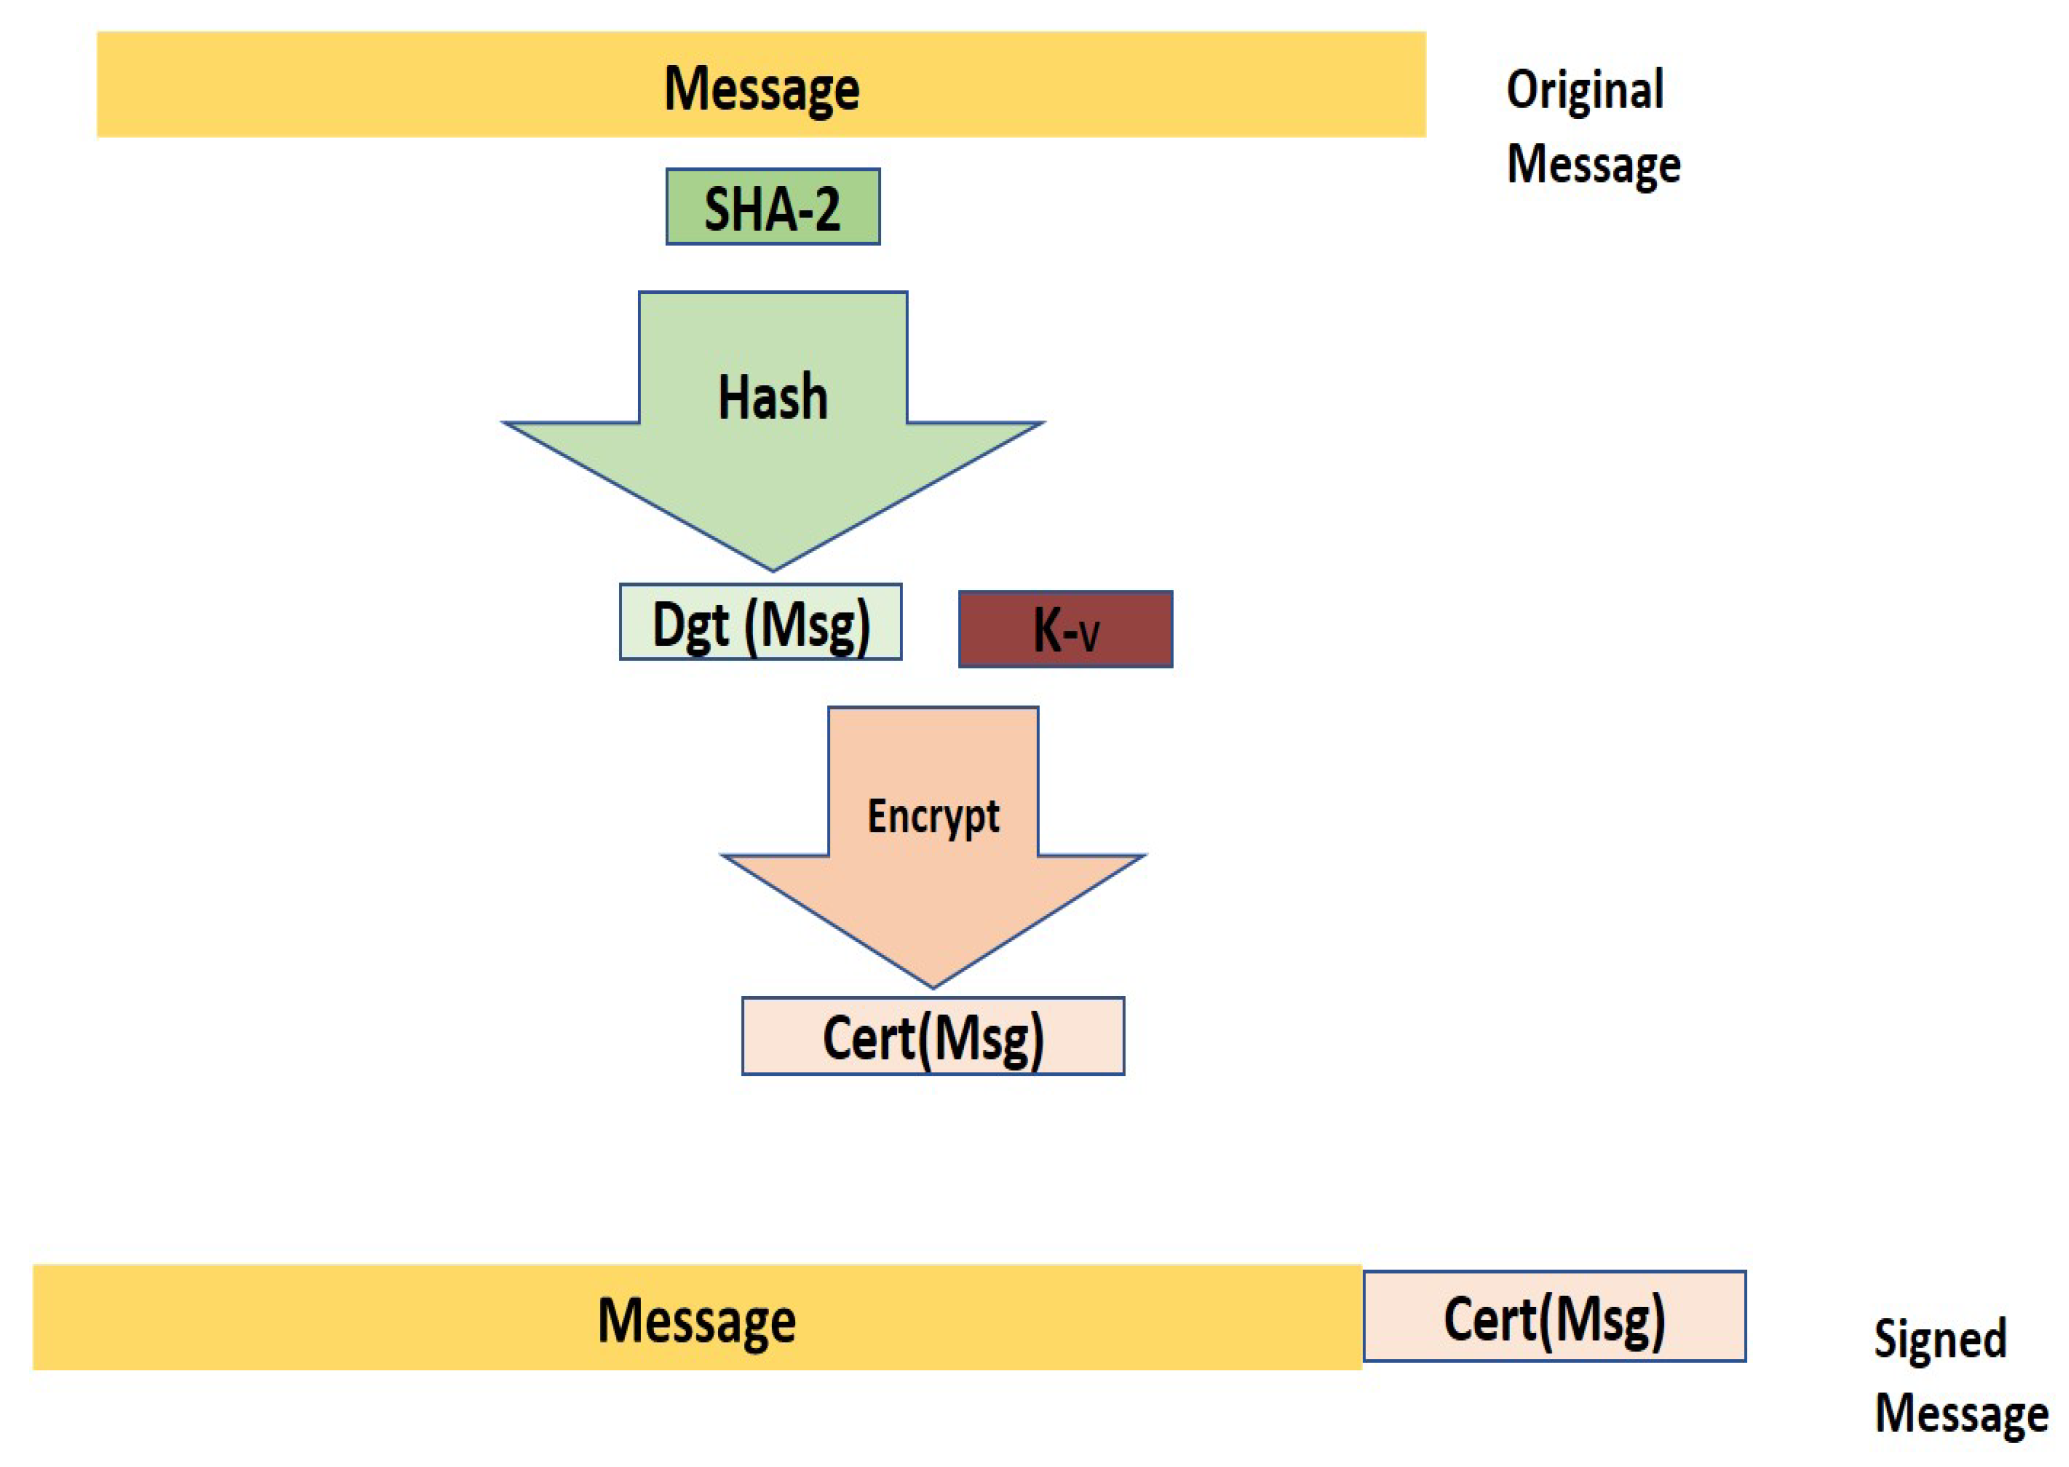
- Sign the Message: The ShA-2 hashing algorithm is used to generate a message digest for that message ()). Then, the private key of the sender vehicle () is used to create a message certificate () by encrypting the . The latter certificate ensures that this vehicle initiates that message and other fields of the message have not been manipulated by other users or attackers. Using the hashing algorithm before encrypting the data reduces its size; thus, it reduces the time complexity for the encryption and decryption processes.The value of is added as a signature at the end of the original message. It is mainly used to verify the content of the message and the identity of its initiator. Figure 6 graphically illustrates the steps and techniques of signing a message.Figure 6. Signed message.
- Phase 4: Signature Verification
When any signed message from a neighbor’s vehicle is received, it needs to be verified. The identity of the initiator vehicle and the contents of the signed message have to be checked and verified. The public key of the sender vehicle is used to decrypt the assigned to each communication message (e.g., “hello”, report). Thus, the of that message is obtained from the . At the same time, the receiver uses SHA-2 to hash the other fields in the received message and obtain . The receiver compares and ; if their values are the same, it verifies the received message. Otherwise, it discards the message and marks it as a manipulated message. Verified messages are messages signed and created by the responsible vehicle. The and its key are matched with the registered ones inside the traffic authority database.
- Phase 5: Traffic Light Scheduling
The sequential phases of the traffic light are set based on real-time traffic characteristics and the existence of emergency vehicles, as discussed in [2]. However, only verified messages are considered in the traffic evaluation and then the scheduling algorithm. Adding the security level in terms of verifying the integrity of vehicles’ identities significantly enhances the performance of the scheduling algorithm. This is to prevent impersonation and illegal modification attacks. The next section experimentally investigates the benefits of securing context-aware traffic light scheduling algorithms.
4.1. The Computational and Message Overhead Complexity
This section evaluates the computational cost and message overhead introduced by the security aspects of the proposed protocol. The proposed protocol uses ECDSA with SHA-2 (e.g., SHA-256) to secure the transmitted messages.
4.1.1. Computational Overhead
The primary computational costs are caused by signature generation, signature verification, and hashing operations. First, to generate the signature, the complexity involves the complexity of hashing the message with SHA-256, which is , where n is the message size [37]. In addition, the complexity of the elliptic curve point multiplication is , where p is the size of the elliptic curve field (e.g., 256-bit prime for P-256) [38].
On the other hand, the verification process also involves hashing the message with SHA-256, where the complexity is . Moreover, with two elliptic curve point multiplications and one addition, the complexity is as well, but typically slower than signing for ECDSA [38].
4.1.2. Message Overhead (Signature Size)
The ECDSA signature consists of two values: . Each value has the size of the curve order. For P-256, the length of each component is 256 bits (32 bytes). Then, the total signature is 64 bytes (512 bits). Thus, the signature size is fixed, regardless of the message size [38].
5. Performance Evaluation
This section aims to evaluate the performance of the proposed system (SCATLS) compared to the previous insecure version of the context-aware traffic light scheduling algorithm (CATLS) [2]. The NS-2.35 [39] simulator is used to implement the new proposed algorithm and the previous unsecured algorithm. In addition, SUMO 1.24.0 [40] is used to simulate the traffic mobility of the tested scenarios.
Two different attack scenarios on emergency vehicles at a signalized intersection are simulated. First, the impersonation attack is when a regular vehicle pretends to be an emergency vehicle. Second, the modification attack is when an intruder modifies the messages sent by an emergency vehicle and labels it as a regular vehicle. The metrics that are selected to compare the secure proposed system (SCATLS) with the insecure version (CATLS) are the throughput of each signalized intersection, the average delay time of each regular vehicle waiting at the signalized intersection, and the average delay time of the emergency vehicle. The last metric represents the time that the emergency vehicle stops waiting for the green phase to be able to pass through the intersection. The parameters of the tested experiments are summarized in Table 4. Only one vehicle is simulated to apply the attack in each scenario of these tested experiments. Each experiment has been executed thirty different times, where the simulated attack and the traffic flow mobility are generated randomly each time. The malicious vehicle is simulated completely as a random vehicle after 5000 s of running the simulator in order to obtain a more stable mobility pattern in a random location.
Table 4.
Simulation parameters.
5.1. Impersonation Attack
When a regular vehicle pretends to be an emergency vehicle at a signalized road intersection, it is assigned a higher priority to pass the intersection. The surrounding traffic cooperatively drives and waits to allow the smooth and fast movement of that vehicle. This affects the signalized intersection’s throughput and the waiting delay times of other vehicles there.
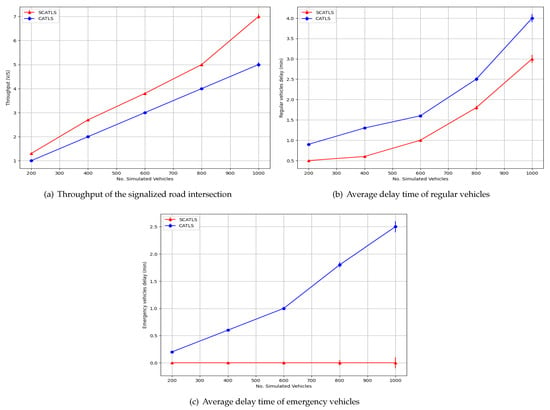
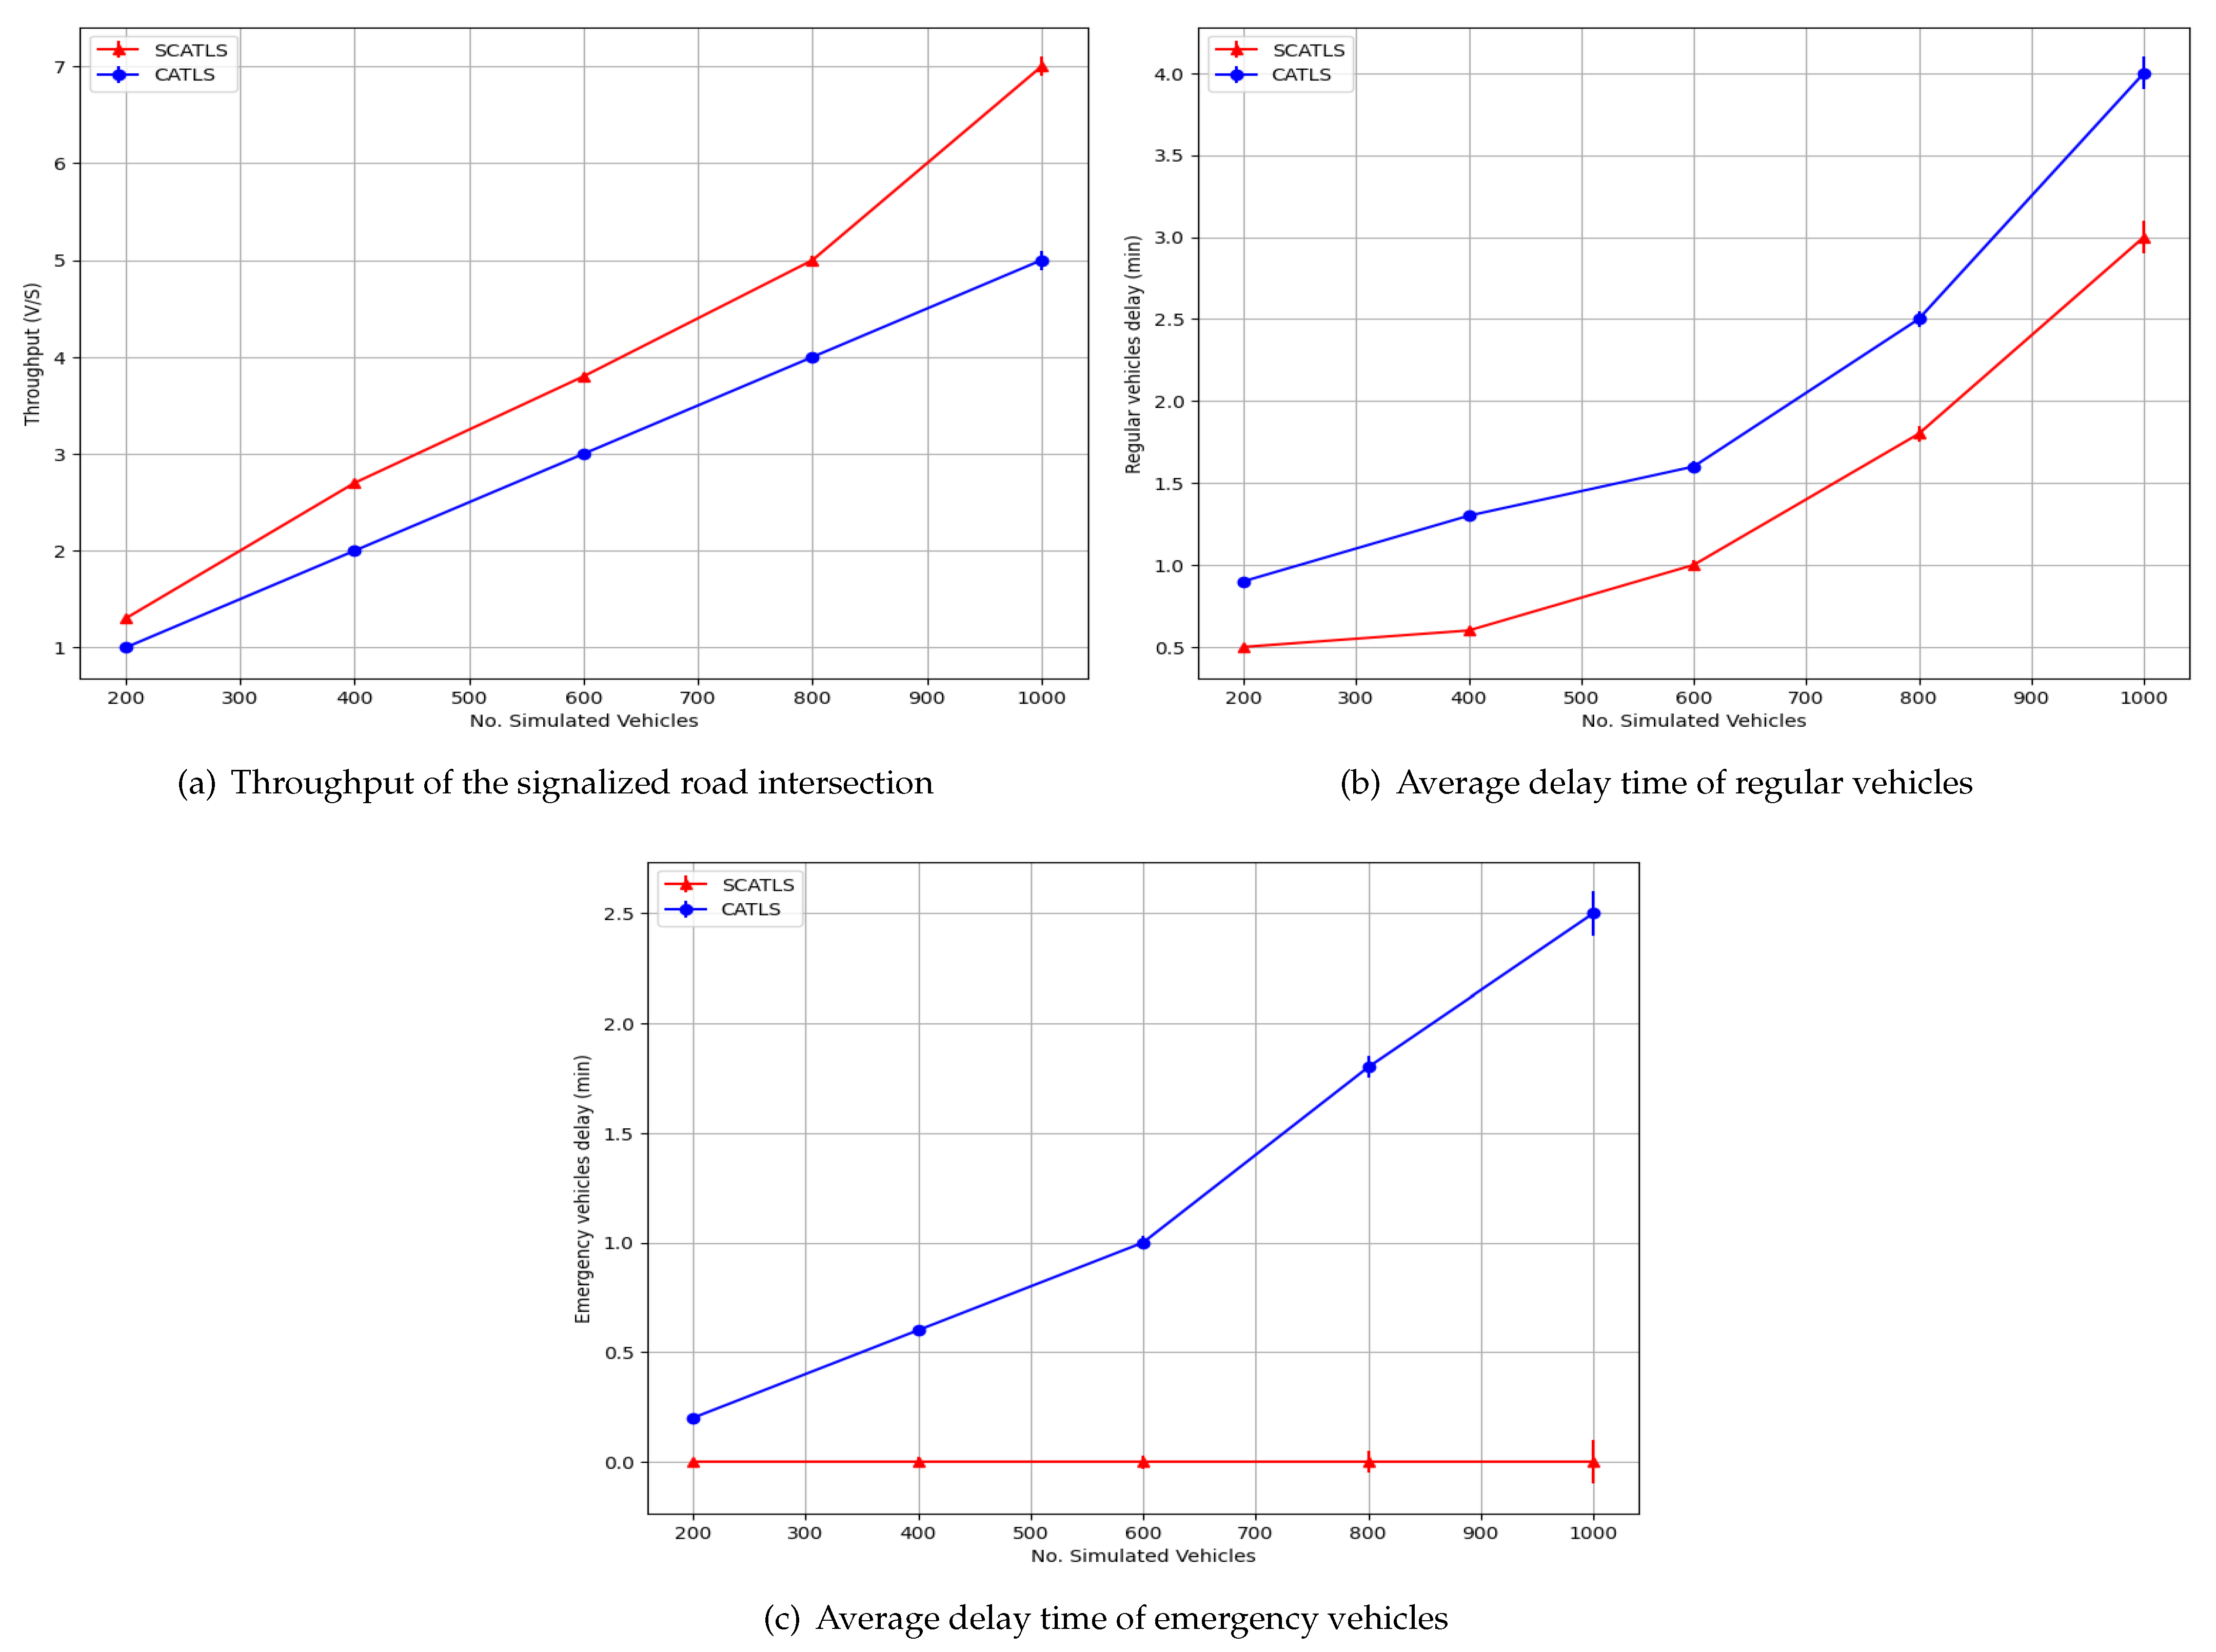
Figure 7 graphically compares the performance of the SCATLS algorithm with the performance of the CATLS algorithm. First, as we can see from Figure 7a, implementing the secure version of the context-aware traffic light scheduling algorithm (SCATLS) has increased the throughput of the signalized intersection by 20% compared to the insecure version (CATLS). This is when only one fake emergency vehicle is simulated. Granting a fake emergency vehicle high priority at the intersection decreases overall throughput by allowing low-density traffic flows to proceed before higher-density flows. SCATLS significantly outperformed CATL in terms of increasing the throughput of the signalized road intersection (t-statistic = 3.381, p-value = 0.0277, 95% confidence interval [0.1718, 1.7482]).
Figure 7.
Efficiency of SCATLS with an impersonation attack.
The average delay time of regular vehicles waiting to pass through the signalized intersection is increased by 30% for the undetected impersonation attack. Figure 7b illustrates the comparison between the detected and undetected scenarios of the impersonation attack and how it affects the waiting delay time of regular vehicles there. The throughput increased when the number of simulated vehicles increased, and the waiting delay time also increased by increasing the number of simulated vehicles there. This is for both the secure and insecure versions of the scheduling algorithm. SCATLS significantly outperformed CATL in terms of decreasing the waiting delay of regular vehicles at the signalized road intersection (t-statistic = 7.014, p-value = 0.0022, 95% confidence interval [0.4108, 0.9492]).
Finally, Figure 7c illustrates the effects of the impersonation attack on the delay of a real emergency vehicle. The context-aware scheduling algorithm aims to schedule the phases of the located traffic light in a way that allows the emergency vehicles to pass smoothly through the signalized intersection without waiting. SCATLS significantly outperformed CATL in terms of decreasing the waiting delay time of emergency vehicles at the signalized road intersection (t-statistic = 2.938, p-value = 0.0425, 95% confidence interval [0.0672, 2.3728]). However, when several emergency vehicles exist at the conflicting traffic flows, the algorithm has to prioritize them. Thus, some emergency vehicles will be delayed waiting for their turn. In the tested scenario, the real simulated emergency vehicle will be competing with the fake one. This will lead to an increased waiting delay time for the real emergency vehicle when the fake one is not detected (CATLS). However, no delay is noticed when the fake emergency vehicle is detected and removed (SCATLS), regardless of the increase in the number of traveling vehicles.
5.2. Modification Attack
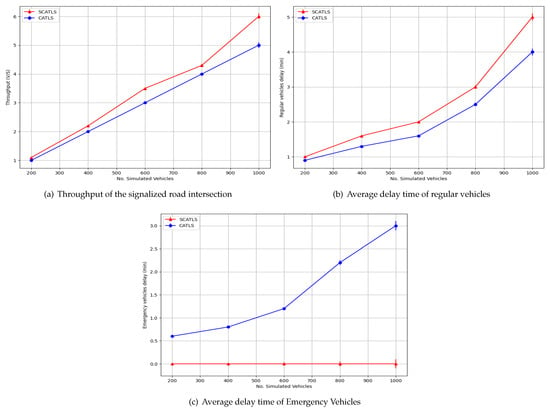
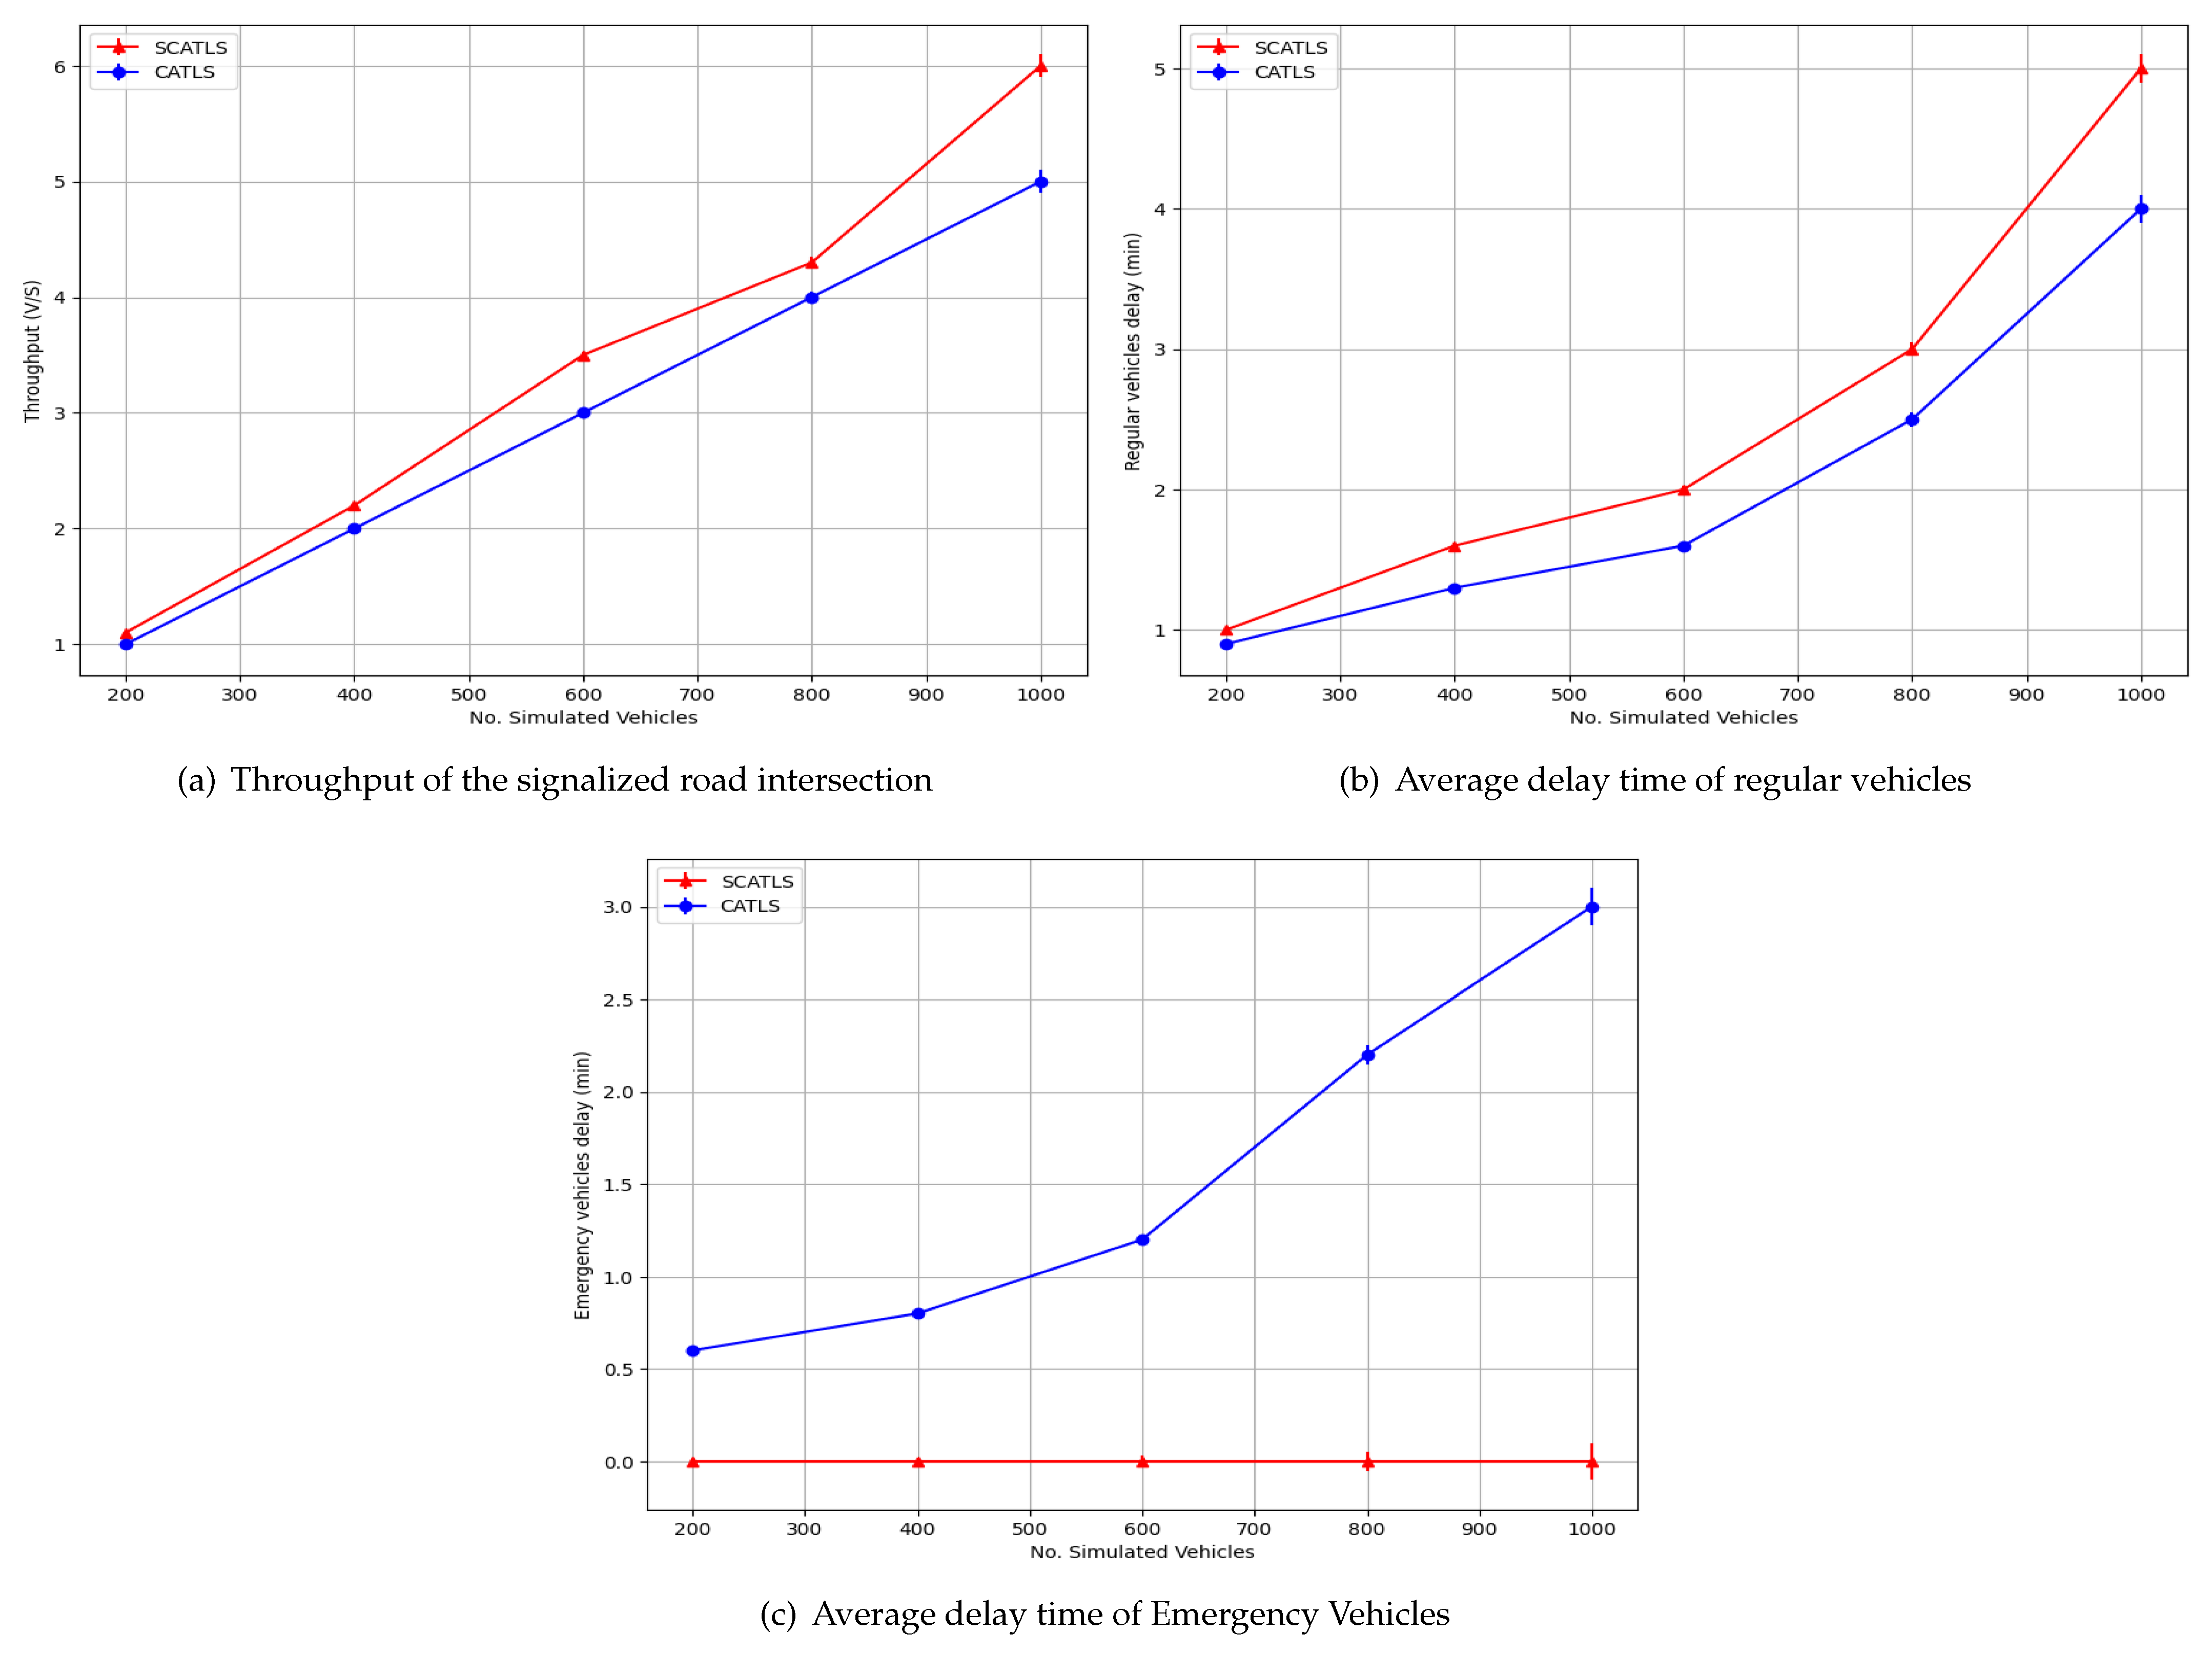
The modification attack by intruders that changes the type of vehicle announced aims to prevent the fast schedule for that emergency vehicle. This has a positive effect on the throughput of the signalized intersection because traffic flows with higher traffic densities are always scheduled first. As shown in Figure 8a, the secure version of the scheduling algorithm (SCATLS) has decreased the throughput by 15% compared to the insecure version (CATLS). SCATLS significantly outperformed CATL in terms of increasing the throughput of the signalized road intersection (t-statistic = 2.635, p-value = 0.0579, 95% confidence interval [−0.8625, 0.0225]).
Figure 8.
Efficiency of SCATLS with a modification attack.
The waiting delay time of regular vehicles is also decreased by 20% for all different numbers of vehicles due to the manipulation attack, as seen from Figure 8b. The secure version has a higher delay effect on the regular vehicles at the signalized intersection. Thus, the modification attack can be initiated by intruders or vehicles on a traffic flow that competes with the traffic flow that contains an emergency vehicle. SCATLS significantly outperformed CATL in terms of decreasing the waiting delay of regular vehicles at the signalized road intersection (t-statistic = 3.060, p-value = 0.0377, 95% confidence interval [−0.8774, −0.0426]).
Regarding the real emergency vehicles, their waiting delay time will drastically increase based on the number of vehicles in the investigated scenario. Figure 8c shows the delay time of the simulated emergency vehicle. SCATLS significantly outperformed CATL in terms of decreasing the waiting delay time of emergency vehicles at the signalized road intersection (t-statistic = 3.440, p-value = 0.0263, 95% confidence interval [0.3011, 2.8189]). We can infer that the algorithm is considering the emergency vehicle as a regular vehicle in its schedule due to the manipulation attack.
6. Conclusions
This work examines potential attack scenarios targeting the integrity of vehicle identities, analyzing the resulting consequences and damages. It also highlights the advantages criminals, attackers, or intruders may gain by manipulating vehicle identities or declared types. To address these threats, a secure context-aware traffic light scheduling system (SCATLS) is proposed. Experimental evaluations compare the performance of SCATLS with the unsecured version of the algorithm (CATLS) under two simulated attack types: (1) an impersonation attack, in which regular vehicles falsely declare themselves as emergency vehicles to gain priority at signalized intersections; and (2) a manipulation attack, where external intruders alter emergency vehicle messages and reclassify them as regular vehicles. The proposed SCATLS successfully detects and prevents both attacks before determining traffic light phases, while considering traffic density and the presence of emergency vehicles. The experimental study has shown that the SCATLS algorithm has succeeded in increasing the throughput of the signalized road intersections by 15% on average compared to CATLS. Moreover, the average waiting delay time of regular vehicles is decreased by 20% on average when the SCATLS algorithm is used. These results were obtained mainly because the impersonation and manipulation attacks were successfully detected and removed. Future work will focus on evaluating the impact of multiple emergency vehicles at intersections, analyzing scenarios involving concurrent attacks, and investigating the effects of impersonation and packet manipulation attacks across multiple connected intersections.
Author Contributions
Conceptualization, M.B.Y. and S.G.; methodology, M.Y., M.B.Y., and F.N.; software, M.Y., A.A., and M.B.Y.; validation, M.B.Y., F.N., and A.A.; formal analysis, S.G.; investigation, M.Y. and M.B.Y.; resources, M.Y. and M.B.Y.; data curation, M.Y. and A.A.; writing—original draft preparation, M.Y. and A.A.; writing—review and editing, M.B.Y.; visualization, M.Y., A.A., and M.B.Y.; supervision, M.B.Y., F.N., and S.G.; project administration, M.B.Y., F.N., and S.G.; All authors have read and agreed to the published version of the manuscript.
Funding
This research received no external funding.
Institutional Review Board Statement
Not applicable.
Informed Consent Statement
Not applicable.
Data Availability Statement
Data used in the experimental study will be available on request.
Conflicts of Interest
The authors declare no conflicts of interest.
References
- Macías-Escrivá, F.D.; Haber, R.; Del Toro, R.; Hernandez, V. Self-adaptive systems: A survey of current approaches, research challenges, and applications. Expert Syst. Appl. 2013, 40, 7267–7279. [Google Scholar]
- Younes, M.B.; Boukerche, A.; Mammeri, A. Context-aware traffic light self-scheduling algorithm for intelligent transportation systems. In Proceedings of the 2016 IEEE Wireless Communications and Networking Conference, Doha, Qatar, 3–6 April 2016; pp. 1–6. [Google Scholar] [CrossRef] [Scilit]
- Younes, M.B.; Boukerche, A. An efficient dynamic traffic light scheduling algorithm considering emergency vehicles for intelligent transportation systems. Wirel. Netw. 2018, 24, 2451–2463. [Google Scholar]
- Alqarqaz, M.; Bani Younes, M.; Qaddoura, R. An object classification approach for autonomous vehicles using machine learning techniques. World Electr. Veh. J. 2023, 14, 41. [Google Scholar]
- Younes, M.B.; Roman Alonso, G.; Boukerche, A. A distributed infrastructure-based congestion avoidance protocol for vehicular ad hoc networks. In Proceedings of the 2012 IEEE Global Communications Conference (GLOBECOM), Anaheim, CA, USA, 3–7 December 2012; IEEE: New York, NY, USA, 2012; pp. 73–78. [Google Scholar]
- Barba, C.T.; Mateos, M.A.; Soto, P.R.; Mezher, A.M.; Igartua, M.A. Smart city for VANETs using warning messages, traffic statistics and intelligent traffic lights. In Proceedings of the 2012 IEEE intelligent vehicles symposium, Madrid, Spain, 3–7 June 2012; IEEE: New York, NY, USA, 2012; pp. 902–907. [Google Scholar]
- Mahalakshmi, V.; Karthikeyana, B. Context-aware acquisition module (CAAM) using Road Side Unit (RSU) to Vehicle unicast communication for Intelligent transport systems in edge computing. Elsevier (ssrn): Amesterdam, The Netherlands, 2024; Preprint submitted.
- Younes, M.B.; Boukerche, A. A performance evaluation of a context-aware path recommendation protocol for vehicular ad-hoc networks. In Proceedings of the 2013 IEEE Global Communications Conference (GLOBECOM), Atlanta, GA, USA, 9–13 December 2013; IEEE: New York, NY, USA, 2013; pp. 516–521. [Google Scholar]
- Dzemydienė, D.; Burinskienė, A. Integration of context awareness in smart service provision system based on wireless sensor networks for sustainable cargo transportation. Sensors 2021, 21, 5140. [Google Scholar]
- Pavlin, G.; Boudreault, R.; Penders, A.; Lafond, D.; de Graaf, M.; Swiebel, A. Extracting actionable information from heterogeneous sensors in the field: A distributed hybrid AI approach in constrained domains. In Proceedings of the Conference: 2023 Ground Vehicle Systems Engineering and Technology Symposium, GVSETS, Novi, MI, USA, 15–17 August 2023. [Google Scholar]
- De Amicis, R.; Conti, G.; Piffer, S.; Prandi, F. Service oriented computing for ambient intelligence to support management of transport infrastructures. J. Ambient. Intell. Humaniz. Comput. 2011, 2, 201–211. [Google Scholar]
- Grimm, D.; Stang, M.; Sax, E. Context-aware security for vehicles and fleets: A survey. IEEE Access 2021, 9, 101809–101846. [Google Scholar]
- Dzemydienė, D.; Burinskienė, A.; Miliauskas, A. Integration of multi-criteria decision support with infrastructure of smart services for sustainable multi-modal transportation of freights. Sustainability 2021, 13, 4675. [Google Scholar]
- Sattar, F.; Karray, F.; Kamel, M.; Nassar, L.; Golestan, K. Recent advances on context-awareness and data/information fusion in ITS. Int. J. Intell. Transp. Syst. Res. 2016, 14, 1–19. [Google Scholar]
- He, Z.; Zhang, D. Cost-efficient traffic-aware data collection protocol in VANET. Ad Hoc Netw. 2017, 55, 28–39. [Google Scholar]
- Wu, Q.; Zhu, M.; Rao, N.S.V. Integration of sensing and computing in an intelligent decision support system for homeland security defense. Pervasive Mob. Comput. 2009, 5, 182–200. [Google Scholar]
- Dzemydiene, D.; Dzindzalieta, R. Multi-Layered Architecture of Decision Support System for Monitoring of Dangerous Good Transportation. In DB&Local Proceedings; 2012; pp. 128–141. Available online: https://cris.mruni.eu/cris/entities/publication/76488d8b-376b-4016-b90a-e268e6bfa83b (accessed on 5 July 2025).
- Younes, M.B.; Boukerche, A. SCOOL: A secure traffic congestion control protocol for VANETs. In Proceedings of the 2015 IEEE Wireless Communications and Networking Conference (WCNC), New Orleans, LA, USA, 9–12 March 2015; IEEE: New York, NY, USA, 2015; pp. 1960–1965. [Google Scholar]
- Dzemydienė, D. Development of intelligent service system for multimodal transport management. In Development of Smart Context-Aware Services for Cargo Transportation: An Operational Management Approach; Springer International Publishing: Cham, Switzerland, 2022; pp. 371–403. [Google Scholar]
- Rashwan, A.M. Context-Aware and Real-Time Entrustment Framework for Securing Next Generation Internet Communications. Ph.D. Thesis, Queen’s University, Kingston, ON, Canada, 2018. [Google Scholar]
- Pathre, A.; Agrawal, C.; Jain, A. A novel defense scheme against DDOS attack in VANET. In Proceedings of the 2013 Tenth International Conference on Wireless and Optical Communications Networks (WOCN), Bhopal, India, 26–28 July 2013; IEEE: New York, NY, USA, 2013; pp. 1–5. [Google Scholar]
- Sylla, T.; Chalouf, M.A.; Mendiboure, L.; Krief, F. Context-Aware Security and Privacy as a Service for the Connected and Autonomous Vehicle. In Cooperative Intelligent Transport Systems: Control and Management; ISTE Ltd.: London, UK, 2024; p. 295. [Google Scholar]
- Bermad, N.; Zemmoudj, S.; Omar, M. Context-aware negotiation, reputation and priority traffic light management protocols for VANET-based smart cities. Telecommun. Syst. 2019, 72, 131–153. [Google Scholar]
- Aleko, D.R.; Djahel, S. An efficient adaptive traffic light control system for urban road traffic congestion reduction in smart cities. Information 2020, 11, 119. [Google Scholar]
- Mizher, M.A.; Sihwail, R.; Baker, M.B.; Mazhar, A.A.; Mizher, M.A.; Ibrahim, D. A review of cybersecurity for internet-of-things based on next generation healthcare networks. In Proceedings of the AIP Conference Proceedings, Amman, Jordan, 28–29 June 2022; AIP Publishing: Melville, NY, USA, 2023; Volume 2979. [Google Scholar]
- Said Solaiman, O.; Sihwail, R.; Shehadeh, H.; Hashim, I.; Alieyan, K. Hybrid Newton–sperm swarm optimization algorithm for nonlinear systems. Mathematics 2023, 11, 1473. [Google Scholar]
- Liu, J.; Li, J.; Zhang, L.; Dai, F.; Zhang, Y.; Meng, X.; Shen, J. Secure intelligent traffic light control using fog computing. Future Gener. Comput. Syst. 2018, 78, 817–824. [Google Scholar]
- Khalid, T.; Khan, A.N.; Ali, M.; Adeel, A.; ur Rehman Khan, A.; Shuja, J. A fog-based security framework for intelligent traffic light control system. Multimed. Tools Appl. 2019, 78, 24595–24615. [Google Scholar]
- Elsagheer Mohamed, S.A.; AlShalfan, K.A. Intelligent traffic management system based on the Internet of Vehicles (IoV). J. Adv. Transp. 2021, 2021, 4037533. [Google Scholar]
- Özkul, M.; Capuni, I.; Domnori, E. Context-aware intelligent traffic light control through secure messaging. J. Adv. Transp. 2018, 2018, 4251701. [Google Scholar]
- Johnson, D.; Menezes, A.; Vanstone, S. The elliptic curve digital signature algorithm (ECDSA). Int. J. Inf. Secur. 2001, 1, 36–63. [Google Scholar]
- Sihwail, R.; Ibrahim, D. A New Image Encryption Method Using an Optimized Smart Codebook. Hum. Behav. Emerg. Technol. 2025, 2025, 7807003. [Google Scholar]
- Ibrahim, D.; Sihwail, R.; Arrifin, K.A.Z.; Abuthawabeh, A.; Mizher, M. A novel color visual cryptography approach based on Harris Hawks Optimization Algorithm. Symmetry 2023, 15, 1305. [Google Scholar]
- Pieprzyk, J.; Sadeghiyan, B. (Eds.) Design of Hashing Algorithms; Springer: Berlin/Heidelberg, Germany, 1993. [Google Scholar]
- Mizher, M.A.A.J.A.; Sulaiman, R.; Abdalla, A.M.A.; Mizher, M.A.A. A simple flexible cryptosystem for meshed 3D objects and images. J. King Saud Univ.-Comput. Inf. Sci. 2021, 33, 629–646. [Google Scholar]
- Kelly, J.R. Cryptographically Secure Pseudo-Random Number Generator. U.S. Patent No. 6,275,586, 14 August 2001. [Google Scholar]
- Chaves, R.; Sousa, L.; Sklavos, N.; Fournaris, A.P.; Kalogeridou, G.; Kitsos, P.; Sheikh, F. Secure hashing: Sha-1, sha-2, and sha-3. In Circuits and Systems for Security and Privacy; CRC Press: Boca Raton, FL, USA, 2016; pp. 105–132. [Google Scholar]
- Clark, J.; Ali, F. Analysis of ECDSA’s Computational Impact on IoT Network Performance. In Proceedings of the 2023 ACM Southeast Conference, Virtual, 12–14 April 2023; pp. 196–200. [Google Scholar]
- Network Simulator ns-2. Available online: http://www.isi.edu/nsnam/ns/ (accessed on 1 June 2025).
- Behrisch, M.; Bieker, L.; Erdmann, J.; Krajzewicz, D. SUMO–simulation of urban mobility: An overview. In Proceedings of the SIMUL 2011, The Third International Conference on Advances in System Simulation, Barcelona, Spain, 23–29 October 2011. [Google Scholar]

Disclaimer/Publisher’s Note: The statements, opinions and data contained in all publications are solely those of the individual author(s) and contributor(s) and not of MDPI and/or the editor(s). MDPI and/or the editor(s) disclaim responsibility for any injury to people or property resulting from any ideas, methods, instructions or products referred to in the content. |
© 2025 by the authors. Published by MDPI on behalf of the World Electric Vehicle Association. Licensee MDPI, Basel, Switzerland. This article is an open access article distributed under the terms and conditions of the Creative Commons Attribution (CC BY) license (https://creativecommons.org/licenses/by/4.0/).