
Securing Wireless Charging Ecosystems in Intelligent Transport Systems: An OCPP-Based Cybersecurity Impact Analysis

 ,
 ,
 and

Abstract
1. Introduction
- (a)
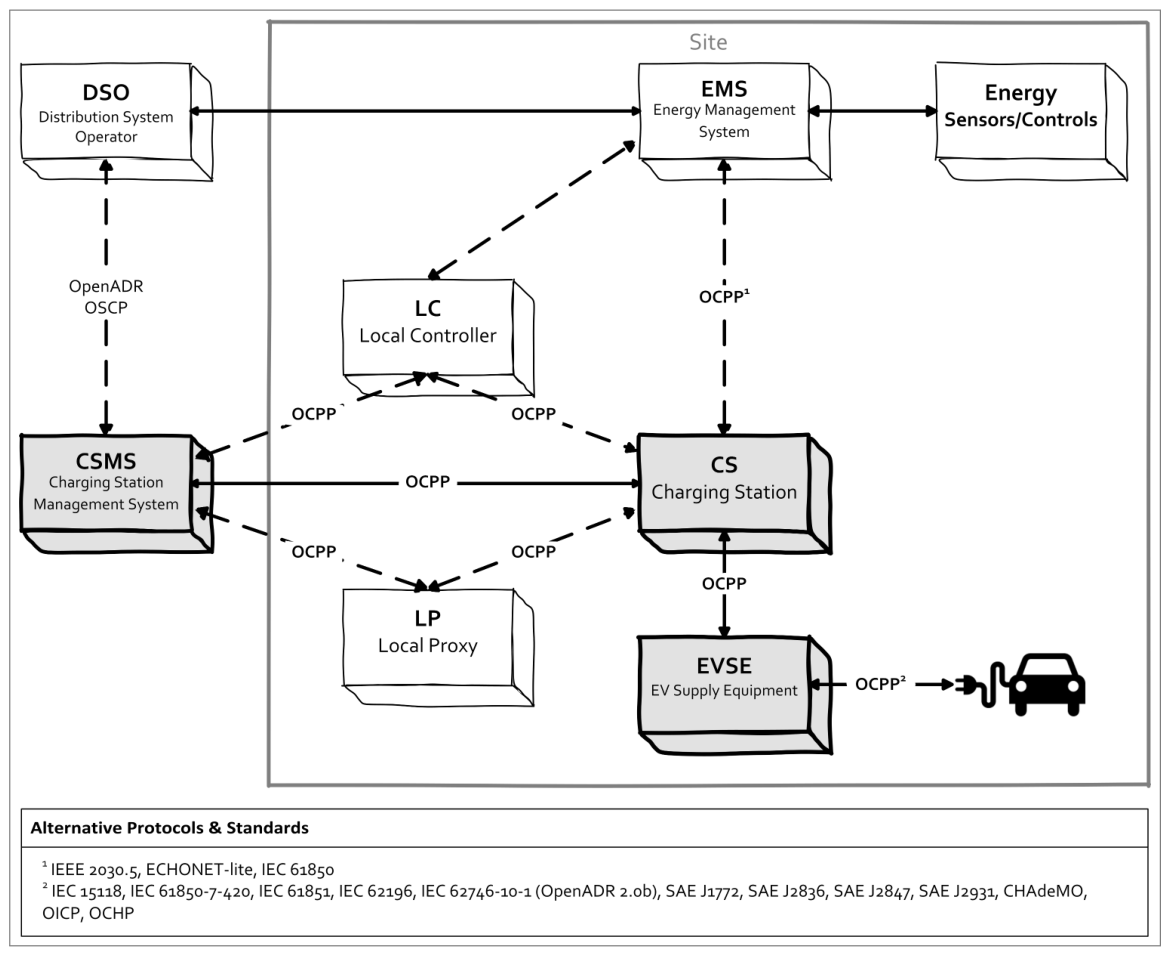
- the description of the entities involved in the OCPP-based PEV network within the formerly proposed iBuC service;
- (b)
- the presentation of the extended vulnerability list of the iBuC service considering the OCPP-based PEV network active components;
- (c)
- the security evaluation of the iBuC service on the basis of the extended vulnerability list;
- (d)
- the evaluation of the OCPP-based PEV network cybersecurity impact on the transport service.
2. Related Work
3. Modelling and Security Assessment Method
3.1. Stochastic Modelling of the Service
3.2. Weaknesses and Vulnerability List
3.3. Security Metric Calculation
4. PEV Network Security Impact
4.1. Security Weaknesses and Vulnerabilities
- CVE-2018-7800 —This vulnerability allows the attacker to access the EVSE with full privileges. With these access privileges, the attacker gains full control and can affect the availability of the service by enforcing the following [54,55]; (a) stopping any ongoing charging process, (b) falsely setting the CS status to ‘not availiable’ or ‘charging’, and (c) unlocking the charging cable to allow malicious or uncontrolled use.CVE-2018-7800 falls under the weakness [CWE-798: Use of Hard-coded Credentials] and is classified as critical severity (CVSS Base score: 9.8) [34].
- CVE-2018-7801—This is a high-risk vulnerability, the exploitation of which allows the attacker to access the EVSE with full privileges, using some arbitrary code. With these access privileges, the attacker gains full control of the charging station operating system [54,55]. CVE-2018-7801 falls under the [CWE-94: Improper Control of Generation of Code (‘Code Injection’)] weakness and is classified as of high severity (CVSS Base score: 8.8) [34].
- CVE-2018-7802—This vulnerability allows the attacker to access the EVSE with full privileges, using Structured Query Language (SQL) code injection [54,55]. CVE-2018-7802 falls under the [CWE-89: Improper Neutralization of Special Elements used in an SQL Command (‘SQL Injection’)] weakness and is classified as of high severity (CVSS Base score: 8.8) [34].
- CVE-2020-27813—This vulnerability allows attacks against OCPP messages, through manipulated JSON messages, which are used to violate the constraints governing the charging site. These messages may also include circular or encapsulated code structures [56]. CVE-2020-27813 falls under the weaknesses [CWE-190: Integer Overflow or Wrap-around] and [CWE-400: Uncontrolled Resource Consumption] and is classified as of high severity (CVSS Base score: 7.5) [34].
- CVE-2021-22706—This vulnerability allows the attacker to impersonate a trusted user of the charging station and to submit malicious parameters to the charging station web server [57]. CVE-2021-22706 falls under the [CWE-79: Improper Neutralization of Input During Web Page Generation (‘Cross-site Scripting’)] weakness and is classified as of medium severity (CVSS Base score: 6.1) [34].
- CVE-2021-22722—This vulnerability allows the attacker to change the operating parameters of the charging station by injecting malicious code through CSV files [57]. CVE-2021-22722 falls under the [CWE-79: Improper Neutralization of Input During Web Page Generation (‘Cross-site Scripting’)] weakness and is classified as of medium severity (CVSS Base score: 5.4) [34].
- CVE-2021-22729—This vulnerability allows the attacker to bypass authorisation checks and access the charging station web server with administrative rights [57]. CVE-2021-22729 falls under the [CWE-259: Use of Hard-coded Password] weakness and is classified as of critical severity (CVSS Base score: 9.8) [34].
- CVE-2021-22730—This vulnerability allows the attacker to bypass authorisation checks and access the charging station web server with administrative rights [57]. CVE-2021-22730 falls under the [CWE-798: Use of Hard-coded Credentials] weakness and is classified as of critical severity (CVSS Base score: 9.8) [34].
- (a)
- CVE-2021-22730 replaced the iBuC vulnerability CVE-2016-6829, which falls under the same weakness [CWE-798: Use of Hard-coded Credentials]. CVE-2021-22730 prevailed for being more contemporary and having a better CVSS Temporal Score. CVE-2021-22730 was chosen over CVE-2018-7800, which also falls under CWE-798 for being more contemporary;
- (b)
- CVE-2018-7802 replaced CVE-2018-12942, which falls under the same weakness [CWE-89: SQL Injection]. CVE-2018-7802 prevailed for having a better CVSS Temporal Score, while also being relevant to the charging process;
- (c)
- CVE-2021-22706 replaced CVE-2021-22722 which falls under the same weakness [CWE-79: Improper Neutralization of Input During Web Page Generation (‘Cross-site Scripting’)], due to higher severity (i.e., CVE-2021-22706 has CVSS Base score: 6.1 while CVE-2021-22722 has CVSS Base score: 5.4).
4.2. Impact on the iBuC Service Security
- (a)
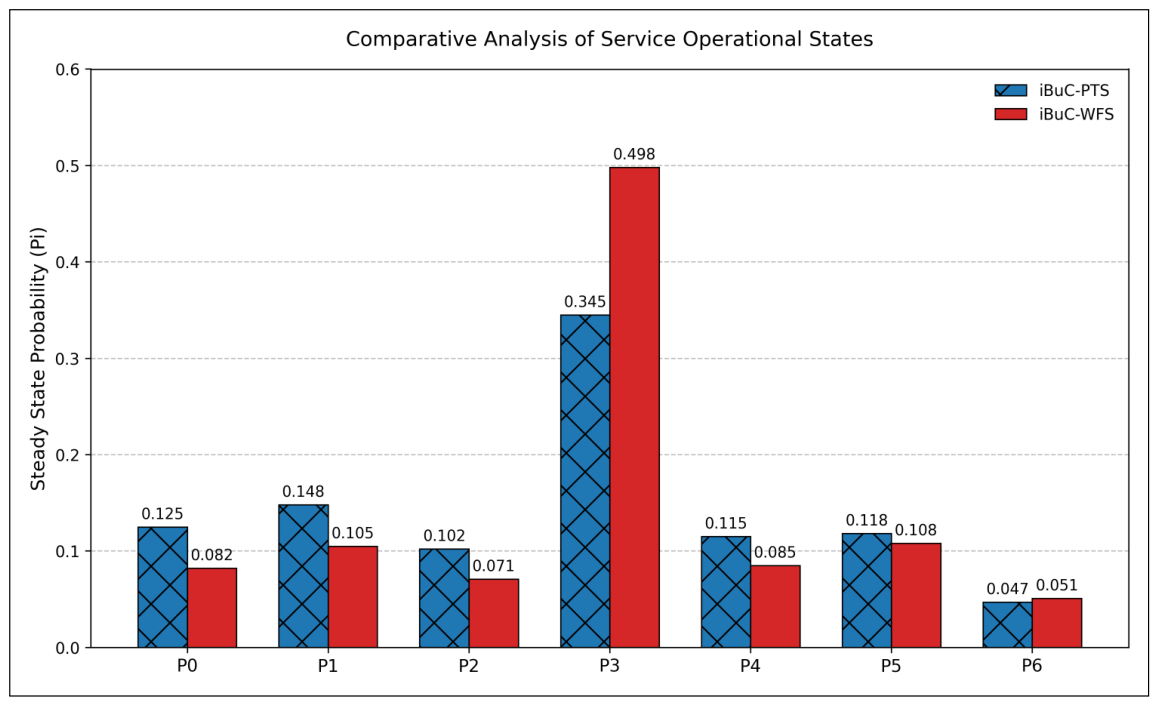
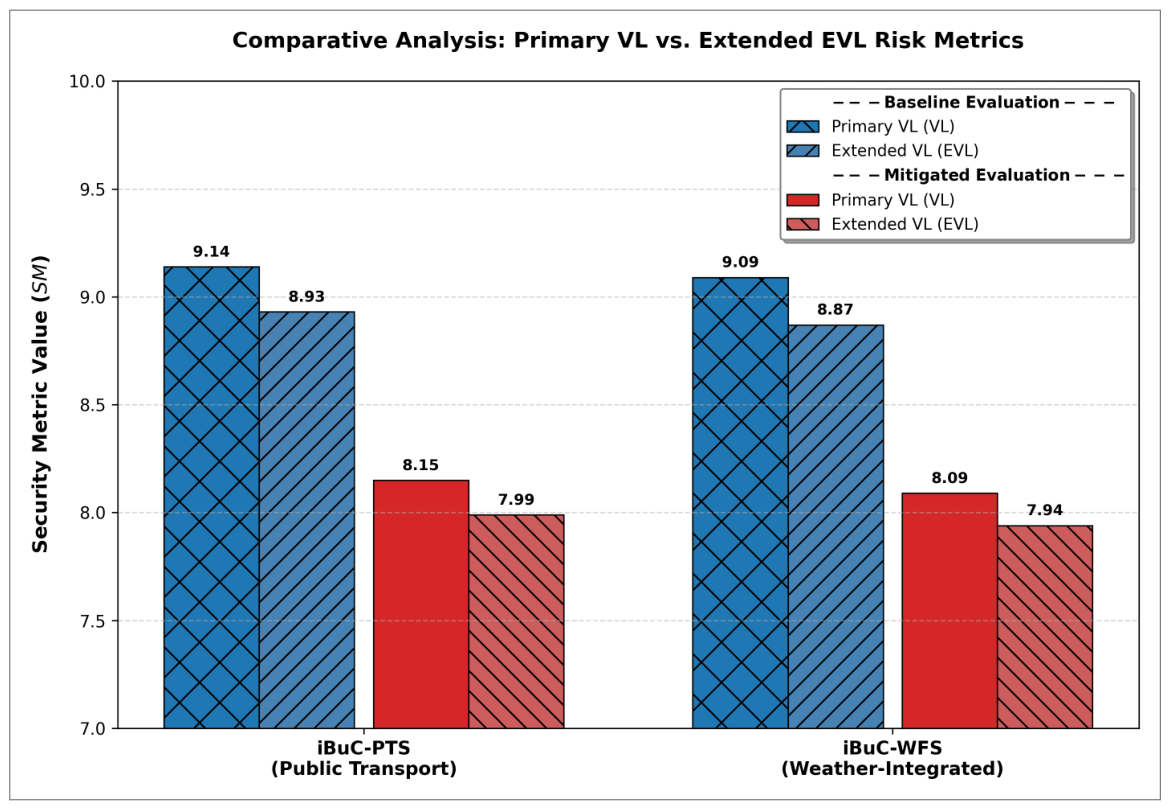
- EVL includes more vulnerabilities than VL for the same service states, resulting in an increased frequency of occurrence (), an inversely reduced proportional risk (), and, finally, reduced security metrics and .
- (b)
- The majority of the EVL additions (i.e., four of seven vulnerabilities) have a CVSS Base Score of less than 8.9 and are therefore classified as of high severity, rather than of critical severity, and two out of seven of the EVL additions have a CVSS Temporal Score of even less than 6.9, which classifies them as vulnerabilities of medium severity.
- (c)
- The EVL additions are affecting 43% of the iBuC-PTS states and 33% of the iBuC-WFS states and the impact of the added vulnerabilities increases.
5. Discussion
5.1. Comparative Framework Benchmarking
5.2. Parametric Sensitivity Analysis
6. Conclusions
Author Contributions
Funding
Institutional Review Board Statement
Informed Consent Statement
Data Availability Statement
Acknowledgments
Conflicts of Interest
Abbreviations
| AI | Artificial Intelligence |
| AV | Autonomous Vehicle |
| BN | Boarding Node |
| CS | Charging Station |
| CSMS | Charging Station Management System |
| CU | Control Unit |
| CVSS | Common Vulnerability Scoring System |
| DN | Destination Node |
| EMS | Energy Management System |
| EV | Electric Vehicle |
| EVL | Extended Vulnerability List |
| EVSE | Electric Vehicle Supply Equipment |
| HARM | Hierarchical Attack Representation Model |
| iBuC | intelligent Bus on Campus |
| IoT | Internet of Things |
| ITS | Intelligent Transportation Service |
| MITRE | Massachusetts Institute of Technology Research & Engineering |
| NVD | National Vulnerability Database |
| OCA | Open Charge Alliance |
| OCPP | Open Charge Point Protocol |
| PEV | Plug-in Electric Vehicle |
| PTS | Public Transportation System |
| RL | Reinforcement Learning |
| SPN | Stochastic Petri net |
| V2I | Vehicle-to-Infrastructure |
| VL | Vulnerability List |
| WFS | Weather Forecasting Service |
| WPT | Wireless Power Transfer |
References
- Liang, J.; Tan, C.; Yan, L.; Zhou, J.; Yin, G.; Yang, K. Interaction-Aware Trajectory Prediction for Safe Motion Planning in Autonomous Driving: A Transformer-Transfer Learning Approach. IEEE Trans. Intell. Transp. Syst. 2025, 26, 17080–17095. [Google Scholar] [CrossRef] [Scilit]
- Li, Y.; Zhan, Y.; Liang, M.; Zhang, Y.; Liang, J. UPTM-LLM: Large language models-powered urban pedestrian travel modes recognition for intelligent transportation system. Appl. Soft Comput. 2026, 186, 113999. [Google Scholar] [CrossRef] [Scilit]
- Bhargavi, K.; Jayalaksmi, N.; Malagi, S.; Jadoun, V.K. Integration of Plug-in Electric Vehicles in Smart Grid: A Review. In Proceedings of the IEEE International Conference on Power Electronics & IoT Applications in Renewable Energy and Its Control (PARC), Mathura, India, 28–29 February 2020; pp. 214–219. [Google Scholar] [CrossRef] [Scilit]
- Ortiz-Aguilar, L.; Palacios-Ortega, M.; Carpio, M.; Funes-Tapia, J. A Systematic Review of Electric Vehicle Optimization Problems: Taxonomy, Methods, and Research Challenges. Automation 2026, 7, 61. [Google Scholar] [CrossRef] [Scilit]
- Mogire, E.; Kilbourn, P.; Luke, R. Resilient Electric Vehicle Charging Stations in Urban Areas: A Systematic Literature Review. World Electr. Veh. J. 2026, 17, 148. [Google Scholar] [CrossRef] [Scilit]
- Yu, H.; Wu, C.; Liu, Y. Vehicle-to-Grid Integration in Smart Energy Systems: An Overview of Enabling Technologies, System-Level Impacts, and Open Issues. Machines 2026, 14, 418. [Google Scholar] [CrossRef] [Scilit]
- Kim, K.; Kim, J.S.; Jeong, S.; Park, J.H.; Kim, H.K. Cybersecurity for autonomous vehicles: Review of attacks and defense. Comput. Secur. 2021, 103, 102150. [Google Scholar] [CrossRef] [Scilit]
- Karras, A.; Theodorakopoulos, L.; Karras, C.; Theodoropoulou, A. Towards LLM-Driven Cybersecurity in Autonomous Vehicles: A Big Data-Empowered Framework with Emerging Technologies. Mach. Learn. Knowl. Extr. 2026, 8, 43. [Google Scholar] [CrossRef] [Scilit]
- Naseem, H.; Goswami, P.; Choi, K.; Iqbal, A.; Hakami, H. Smart Charging and Vehicle-to-Grid Integration of Electric Vehicles: Technical Insights, Cybersecurity Risks, and Mobility-OrientedControl Strategies. Appl. Sci. 2026, 16, 1748. [Google Scholar] [CrossRef] [Scilit]
- European Union. Regulation (EU) 2023/1804 of the European Parliament and of the Council of 13 September 2023 on the deployment of alternative fuels infrastructure, and repealing Directive 2014/94/EU. Off. J. Eur. Union 2023, L 234, 1–47. [Google Scholar]
- Liu, J.; Yang, X.; Zhuge, C. A joint model of infrastructure planning and smart charging strategies for shared electric vehicles. Green Energy Intell. Transp. 2024, 3, 100168. [Google Scholar] [CrossRef] [Scilit]
- Mansour, H.S.; Samir, M.; Elhady, B.; Abdelmaksoud, S. Wireless charging systems for electric vehicles: Review. Green Energy Intell. Transp. 2026, 5, 100371. [Google Scholar] [CrossRef] [Scilit]
- Chakibanda, V.; Komanapalli, V.L.N. Coil Parameter Analysis for Inductively Coupled Wireless Charging for Electric Vehicles. Vehicles 2024, 6, 468–483. [Google Scholar] [CrossRef] [Scilit]
- Wu, Y.; Madawala, U.K.; Zhao, L.; Dai, X. Research status of bidirectional wireless power transfer technology. Green Energy Intell. Transp. 2026, 5, 100266. [Google Scholar] [CrossRef] [Scilit]
- Li, G.; Cai, Z.; Feng, C.; Sun, Z.; Pan, X. DAB-Based Bidirectional Wireless Power Transfer System with LCC-S Compensation Network under Grid-Connected Application. Energies 2024, 17, 4519. [Google Scholar] [CrossRef] [Scilit]
- Open Charge Alliance. Open Charge Alliance—Our Mission; Open Charge Alliance (OCA): Arnhem, The Netherlands, 2022. [Google Scholar]
- Open Charge Alliance. Open Charge Alliance—Annual Report 2025; Open Charge Alliance (OCA): Arnhem, The Netherlands, 2025. [Google Scholar]
- Ampeco LTD. Enable Innovation and Cost Efficiency with OCPP; Ampeco LTD: London, UK, 2022. [Google Scholar]
- CURRENT Eco AS. Innovation and Cost-Efficiency in Four Letters: OCPP; CURRENT Eco AS: Oslo, Norway, 2021. [Google Scholar]
- Standard IEC 63584:2024; Electric Vehicle Supply Equipment—Open Charge Point Protocol (OCPP). International Electrotechnical Commission (IEC): Geneva, Switzerland, 2024.
- Garofalaki, Z.; Kallergis, D.; Douligeris, C. A Security Assessment Platform for Stochastic Petri Net (SPN) Modelling in the Internet of Things (IoT) Ecosystem. In Domain-Specific Conceptual Modeling: Concepts, Methods and ADOxx Tools; Karagiannis, D., Lee, M., Hinkelmann, K., Utz, W., Eds.; Springer International Publishing: Cham, Switzerland, 2022; pp. 289–311. [Google Scholar] [CrossRef] [Scilit]
- Alsaleh, A. Toward a conceptual model to improve the user experience of a sustainable and secure intelligent transport system. Acta Psychol. 2025, 255, 104892. [Google Scholar] [CrossRef] [Scilit]
- Arachchige, K.G.; Alkaabi, G.; Murtaza, M.; Haq, Q.E.U.; Abualkishik, A.Z.; Lee, C.C. Threat Landscape and Integrated Cybersecurity Framework for V2V and Autonomous Electric Vehicles. World Electr. Veh. J. 2025, 16, 469. [Google Scholar] [CrossRef] [Scilit]
- Durlik, I.; Miller, T.; Kostecka, E.; Zwierzewicz, Z.; Łobodzińska, A. Cybersecurity in Autonomous Vehicles—Are We Ready for the Challenge? Electronics 2024, 13, 2654. [Google Scholar] [CrossRef] [Scilit]
- Muslam, M.M.A. Enhancing Security in Vehicle-to-Vehicle Communication: A Comprehensive Review of Protocols and Techniques. Vehicles 2024, 6, 450–467. [Google Scholar] [CrossRef] [Scilit]
- Giannaros, A.; Karras, A.; Theodorakopoulos, L.; Karras, C.; Kranias, P.; Schizas, N.; Kalogeratos, G.; Tsolis, D. Autonomous Vehicles: Sophisticated Attacks, Safety Issues, Challenges, Open Topics, Blockchain, and Future Directions. J. Cybersecur. Priv. 2023, 3, 493–543. [Google Scholar] [CrossRef] [Scilit]
- Walch, M.; Schirrer, A.; Neubauer, M. Impact assessment of cooperative intelligent transport systems (C-ITS): A structured literature review. Eur. Transp. Res. Rev. 2025, 17, 11. [Google Scholar] [CrossRef] [Scilit]
- Khanmohamadi, M.; Guerrieri, M. Smart Intersections and Connected Autonomous Vehicles for Sustainable Smart Cities: A Brief Review. Sustainability 2025, 17, 3254. [Google Scholar] [CrossRef] [Scilit]
- Puzio, E.; Drożdż, W.; Kolon, M. The Role of Intelligent Transport Systems and Smart Technologies in Urban Traffic Management in Polish Smart Cities. Energies 2025, 18, 2580. [Google Scholar] [CrossRef] [Scilit]
- Shirvani, S.; Baseri, Y.; Ghorbani, A. Evaluation framework for electric vehicle security risk assessment. IEEE Trans. Intell. Transp. Syst. 2023, 25, 33–56. [Google Scholar] [CrossRef] [Scilit]
- Mavropoulos, O.; Mouratidis, H.; Fish, A.; Panaousis, E. Apparatus: A framework for security analysis in internet of things systems. Ad Hoc Netw. 2019, 92, 101743. [Google Scholar] [CrossRef] [Scilit]
- Harrand, N.; Fleurey, F.; Morin, B.; Husa, K.E. ThingML: A Language and Code Generation Framework for Heterogeneous Targets. In Proceedings of the ACM/IEEE 19th International Conference on Model Driven Engineering Languages and Systems (MODELS ’16); Association for Computing Machinery: New York, NY, USA, 2016; pp. 125–135. [Google Scholar] [CrossRef] [Scilit]
- Samandari, A.; Ge, M.; Hong, J.B.; Kim, D.S. Evaluating the Security of IoT Networks with Mobile Devices. In Proceedings of the IEEE 23rd Pacific Rim International Symposium on Dependable Computing (PRDC); IEEE: New York, NY, USA, 2018; pp. 171–180. [Google Scholar] [CrossRef] [Scilit]
- National Institute of Standards and Technology (NIST). National Vulnerability Database (NVD); National Institute of Standards and Technology (NIST): Gaithersburg, MD, USA, 2019.
- Hali, A.; Zirra, P. Reward Based Metrics for Assessing the Effectiveness of Shuffled Based Moving Target Defense. J. Telecommun. Electron. Comput. Eng. (JTEC) 2025, 17, 7–18. [Google Scholar] [CrossRef] [Scilit]
- Ahmadon, M.A.B.; Yamaguchi, S.; Saon, S.; Mahamad, A.K. On service security analysis for event log of IoT system based on data Petri Net. In Proceedings of the IEEE International Symposium on Consumer Electronics (ISCE); IEEE: New York, NY, USA, 2017; pp. 4–8. [Google Scholar] [CrossRef] [Scilit]
- Yamaguchi, S.; Tanaka, H. Modeling of Infection Phenomenon and Evaluation of Mitigation Methods for IoT Malware Mirai by Agent-Oriented Petri Net PN2. In Proceedings of the IEEE International Conference on Consumer Electronics-Taiwan (ICCE-TW); IEEE: New York, NY, USA, 2018; pp. 1–2. [Google Scholar] [CrossRef] [Scilit]
- Ahmadon, M.A.B.; Yamaguchi, S. On service orchestration of cyber physical system and its verification based on Petri Net. In Proceedings of the IEEE 5th Global Conference on Consumer Electronics; IEEE: New York, NY, USA, 2016; pp. 1–4. [Google Scholar] [CrossRef] [Scilit]
- Fortino, G.; Russo, W.; Savaglio, C.; Viroli, M.; Zhou, M. Opportunistic cyberphysical services: A novel paradigm for the future Internet of Things. In Proceedings of the IEEE 4th World Forum on Internet of Things (WF-IoT); IEEE: New York, NY, USA, 2018; pp. 488–492. [Google Scholar] [CrossRef] [Scilit]
- Orcioni, S.; Conti, M. EV smart charging with advance reservation extension to the OCPP standard. Energies 2020, 13, 3263. [Google Scholar] [CrossRef] [Scilit]
- Kirchner, S.R. OCPP Interoperability: A Unified Future of Charging. World Electr. Veh. J. 2024, 15, 191. [Google Scholar] [CrossRef] [Scilit]
- Hamdare, S.; Brown, D.J.; Jha, D.N.; Aljaidi, M.; Cao, Y.; Kumar, S.; Kharel, R.; Jugran, M.; Kaiwartya, O. Cyber defense in OCPP for EV charging security risks. Int. J. Inf. Secur. 2025, 24, 134. [Google Scholar] [CrossRef] [Scilit]
- Plaka, R.; Asplund, M.; Nadjm-Tehrani, S. Vulnerability analysis of an electric vehicle charging ecosystem. In Proceedings of the International Conference on Critical Information Infrastructures Security; Springer: Berlin/Heidelberg, Germany, 2023; pp. 155–173. [Google Scholar] [CrossRef] [Scilit]
- Abazari, A.; Ghafouri, M.; Jafarigiv, D.; Atallah, R.; Assi, C. Developing a security metric for assessing the power grid’s posture against attacks from EV charging ecosystem. IEEE Trans. Smart Grid 2024, 16, 254–276. [Google Scholar] [CrossRef] [Scilit]
- Garofalaki, Z.; Kallergis, D.; Katsikogiannis, G.; Ellinas, I.; Douligeris, C. Transport services within the IoT ecosystem using localisation parameters. In Proceedings of the IEEE International Symposium on Signal Processing and Information Technology (ISSPIT); IEEE: New York, NY, USA, 2016; pp. 87–92. [Google Scholar] [CrossRef] [Scilit]
- Garofalaki, Z.; Kallergis, D.; Katsikogiannis, G.; Ellinas, I.; Douligeris, C. A DSS model for IoT-based intelligent transportation systems. In Proceedings of the IEEE International Symposium on Signal Processing and Information Technology (ISSPIT); IEEE: New York, NY, USA, 2017; pp. 276–281. [Google Scholar] [CrossRef] [Scilit]
- Yu, Z.; Zhou, L.; Ma, Z.; El-Meligy, M.A. Trustworthiness Modeling and Analysis of Cyber-physical Manufacturing Systems. IEEE Access 2017, 5, 26076–26085. [Google Scholar] [CrossRef] [Scilit]
- Karagiannis, D.; Buchmann, R.A.; Burzynski, P.; Reimer, U.; Walch, M. Fundamental Conceptual Modeling Languages in OMiLAB. In Domain-Specific Conceptual Modeling: Concepts, Methods and Tools; Springer: Berlin/Heidelberg, Germany, 2016; pp. 3–30. [Google Scholar] [CrossRef] [Scilit]
- Karagiannis, D.; Burzynski, P.; Miron, E.T. The Imker Case Study—Practice with the Bee-Up Tool. 2017. Available online: https://zenodo.org/records/345846 (accessed on 27 May 2026).
- Garofalaki, Z.; Kallergis, D. On the Security of an IoT-based Intelligent Transportation Service. In Proceedings of the 4th South-East Europe Design Automation, Computer Engineering, Computer Networks and Social Media Conference (SEEDA-CECNSM); IEEE: New York, NY, USA, 2019; pp. 1–5. [Google Scholar] [CrossRef] [Scilit]
- MITRE Corporation. Common Vulnerabilities and Exposures: The Standard for Information Security Vulnerability Names. 2007. Available online: https://cve.mitre.org (accessed on 26 April 2026).
- Khamparia, A.; Pandey, B. Threat driven modeling framework using petri nets for e-learning system. SpringerPlus 2016, 5, 446. [Google Scholar] [CrossRef] [Scilit]
- Garofalaki, Z.; Kosmanos, D.; Moschoyiannis, S.; Kallergis, D.; Douligeris, C. Electric Vehicle Charging: A Survey on the Security Issues and Challenges of the Open Charge Point Protocol (OCPP). IEEE Commun. Surv. Tutor. 2022, 24, 1504–1533. [Google Scholar] [CrossRef] [Scilit]
- Harnett, K.; Watson, G.; Brown, G. Government Fleet and Public Sector Electric Vehicle Supply Equipment (EVSE) Cybersecurity Best Practices and Procurement Language Report; Report No. DOT-VNTSC-NAVFAC-20-01; John A. Volpe National Transportation Systems Center (U.S.): Cambridge, MA, USA, 2019. Available online: https://rosap.ntl.bts.gov/view/dot/43606 (accessed on 26 April 2026).
- Saadat, S.; Maingot, S.; Bahizad, S. Electric vehicle charging station security enhancement measures. In Proceedings of the 2020 5th IEEE Workshop on the Electronic Grid (eGRID); IEEE: New York, NY, USA, 2020; pp. 1–8. [Google Scholar] [CrossRef] [Scilit]
- Coats, D.; Suryanarayana, H.; Wang, Z.; Brissette, A.; Zhang, Y.; Ramanan, V.R.; Scoffield, D.; Woodbury, D.; Haltmeyer, N.; Benzinger, A. Cybersecurity for Grid Connected Extreme Fast Charging (XFC) Station (Cyberx); Final Scientific/Technical Report; Report No. DOE-ABB-8451; ABB Inc.: Zurich, Switzerland, 2021. Available online: https://www.osti.gov/biblio/1835523 (accessed on 26 April 2026).
- Nasr, T.; Torabi, S.; Bou-Harb, E.; Fachkha, C.; Assi, C. ChargePrint: A Framework for Internet-Scale Discovery and Security Analysis of EV Charging Management Systems. In Proceedings of the 2023 Network and Distributed System Security Symposium, San Diego, CA, USA, 27 February–3 March 2023; pp. 1–18. [Google Scholar] [CrossRef] [Scilit]
- Uribe-Pérez, N.; Gonzalez-Garrido, A.; Gallarreta, A.; Justel, D.; González-Pérez, M.; González-Ramos, J.; Arrizabalaga, A.; Asensio, F.J.; Bidaguren, P. Communications and Data Science for the Success of Vehicle-to-Grid Technologies: Current state and Future Trends. Electronics 2024, 13, 1940. [Google Scholar] [CrossRef] [Scilit]
- Freitas, A.A. A critical review of multi-objective optimization in data mining: A position paper. SIGKDD Explor. Newsl. 2004, 6, 77–86. [Google Scholar] [CrossRef] [Scilit]
- SAE RP J2954/3; Dynamic Wireless Power Transfer for Both Light and Heavy Duty Vehicles. SAE International: Warrendale, PA, USA, 2025.
- SAE J2954_202408; Wireless Power Transfer for Light-Duty Plug-In Electric Vehicles and Alignment Methodology. SAE International: Warrendale, PA, USA, 2024.



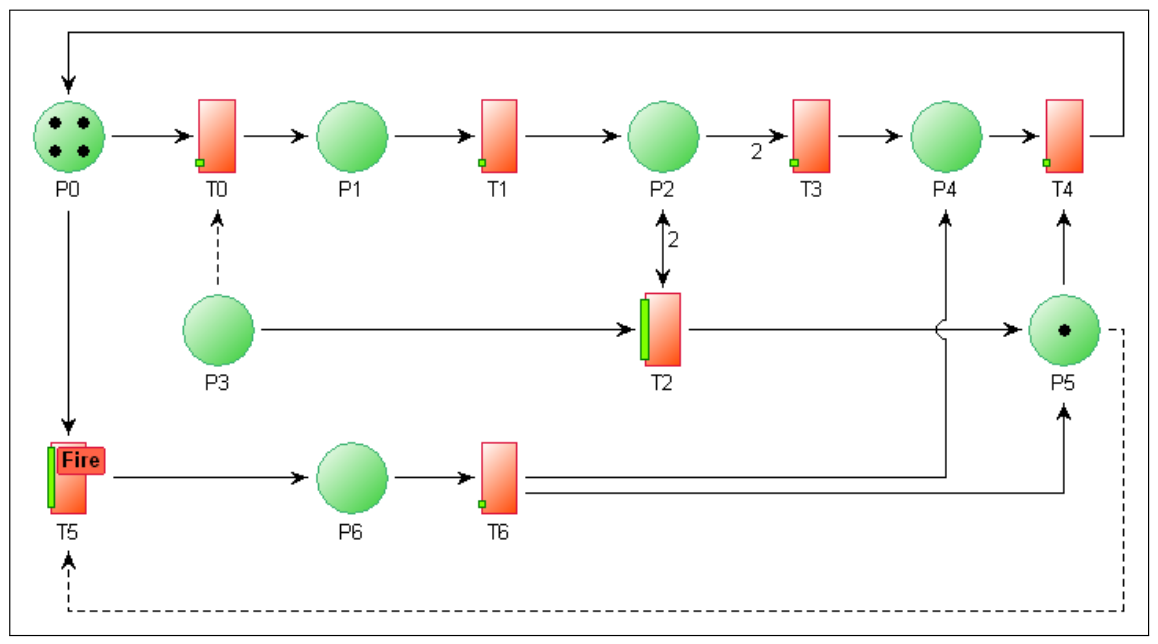
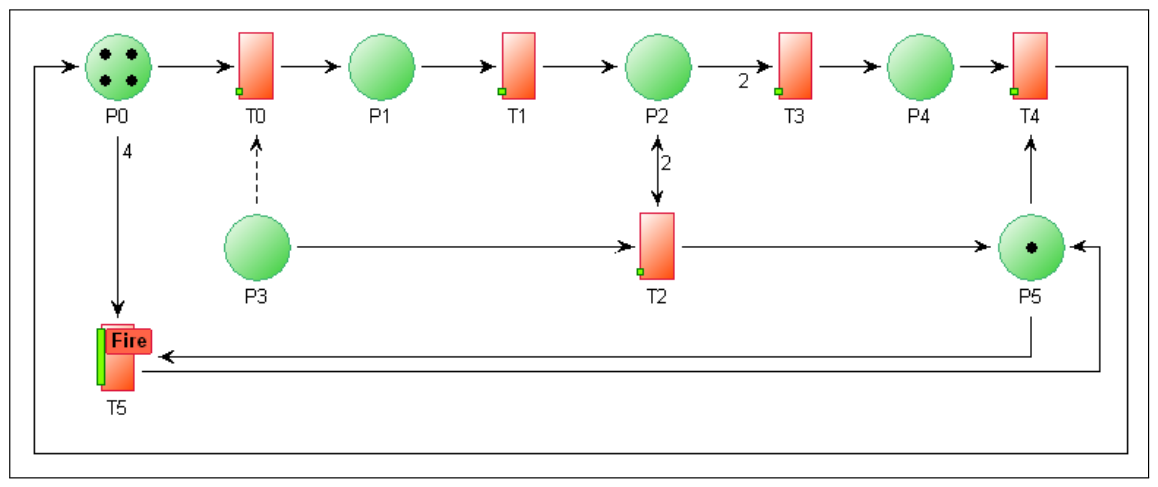
| SPN Model State | iBuC-PTS | iBuC-WFS | |
|---|---|---|---|
| Fleet idle—EV charging | • | • | |
| EV activated | • | • | |
| EV arrives at BN | • | • | |
| Service request is placed | • | • | |
| EV arrives at DN | • | • | |
| Third-party incoming data | • | • | |
| Full-route service triggered | • | ∘ | |
| CVE Identifier | Description | CVSS Score | |
|---|---|---|---|
| Base | Temporal | ||
| CVE-2017-7214 | Information Exposure | 9.8 | 9.1 |
| CVE-2018-4878 | (Resource) Use After Free | 9.8 | 9.1 |
| CVE-2018-8174 | Failure to Constrain Operations | 7.5 | 7.3 |
| CVE-2017-0199 | Access Control (Authorization) Issues | 7.8 | 6.6 |
| CVE-2018-7600 | Improper Input Validation | 9.8 | 8.5 |
| CVE-2018-12942 | OS Command Injection | 8.8 | 8.1 |
| CVE-2018-14643 | Improper Authentication | 9.8 | 8.8 |
| CVE-2018-10635 | Missing Critical Function Authentication | 9.8 | 7.9 |
| CVE-2016-6829 | Use of Hard-coded Credentials | 9.8 | 8.7 |
| CVE-2016-5788 | Improper Authorisation | 10 | 8.3 |
| CVE-2016-5062 | Incorrect Resource Transfer | 9.8 | 8.3 |
| CVE-2016-8209 | Improper Check | 7.5 | 6.6 |
| CVE-2017-5239 | Inadequate Encryption Strength | 7.5 | 7.1 |
| CVE-2017-17717 | Broken Cryptographic Algorithm | 9.8 | 9.3 |
| CVE-2017-7901 | Use of Insufficiently Random Values | 8.6 | 7.6 |
| CVE-2017-18146 | Improper Crypto Verification | 9.8 | 8.5 |
| CVE-2016-5069 | Insufficient Session Expiration | 9.8 | 9.1 |
| CVE-2016-7124 | Deserialization of Untrusted Data | 9.8 | 8.5 |
| CVE-2018-12689 | LDAP Injection | 9.8 | 9.3 |
| Scenario Model | Security Metric () | |
|---|---|---|
| Baseline (t = 0) | Mitigated (t) | |
| iBuC-PTS | 9.14 | 8.15 |
| iBuC-WFS | 9.09 | 8.09 |
| CVE Identifier | Description | CVSS Scores Across Framework Evolution | |||
|---|---|---|---|---|---|
| Primary VL | Extended VL | ||||
| Base | Temporal | Base | Temporal | ||
| CVE-2017-7214 | Information Exposure | 9.8 | 9.1 | 9.8 | 9.1 |
| CVE-2018-4878 | (Resource) Use After Free | 9.8 | 9.1 | 9.8 | 9.1 |
| CVE-2018-8174 | Out-of-bounds Write | 7.5 | 7.3 | 7.5 | 7.3 |
| CVE-2017-0199 | Access Control (Authorization) Issues | 7.8 | 6.6 | 7.8 | 6.6 |
| CVE-2018-7600 | Improper Input Validation | 9.8 | 8.5 | 9.8 | 8.5 |
| CVE-2018-12942 | SQL Injection (Legacy Vendor Code) | 8.8 | 8.1 | — | — |
| CVE-2018-7802 | SQL Injection (OCPP Interface) | — | — | 8.8 | 7.9 |
| CVE-2018-14643 | Improper Authentication | 9.8 | 8.8 | 9.8 | 8.8 |
| CVE-2018-10635 | Missing Critical Function Authentication | 9.8 | 7.9 | 9.8 | 7.9 |
| CVE-2016-6829 | Use of Hard-coded Credentials | 9.8 | 8.7 | — | — |
| CVE-2021-22730 | Use of Hard-coded Credentials | — | — | 9.8 | 8.8 |
| CVE-2016-5788 | Improper Authorisation | 10.0 | 8.3 | 10.0 | 8.3 |
| CVE-2016-5062 | Incorrect Resource Transfer | 9.8 | 8.3 | 9.8 | 8.3 |
| CVE-2016-8209 | Improper Check | 7.5 | 6.6 | 7.5 | 6.6 |
| CVE-2017-5239 | Inadequate Encryption Strength | 7.5 | 7.1 | 7.5 | 7.1 |
| CVE-2017-17717 | Broken Cryptographic Algorithm | 9.8 | 9.3 | 9.8 | 9.3 |
| CVE-2017-7901 | Use of Insufficiently Random Values | 8.6 | 7.6 | 8.6 | 7.6 |
| CVE-2017-18146 | Improper Crypto Verification | 9.8 | 8.5 | 9.8 | 8.5 |
| CVE-2016-5069 | Insufficient Session Expiration | 9.8 | 9.1 | 9.8 | 9.1 |
| CVE-2016-7124 | Deserialization of Untrusted Data | 9.8 | 8.5 | 9.8 | 8.5 |
| CVE-2018-12689 | LDAP Injection | 9.8 | 9.3 | 9.8 | 9.3 |
| CVE-2018-7801 | Code Injection (OCPP Core) | — | — | 8.8 | 8.2 |
| CVE-2020-27813 | Uncontrolled Resource Consumption | — | — | 7.5 | 6.7 |
| CVE-2021-22706 | Cross-site Scripting (Web App) | — | — | 6.1 | 5.7 |
| CVE-2021-22729 | Use of Hard-coded Password | — | — | 9.8 | 8.8 |
| CVE-2018-16669 | Insufficiently Protected Credentials | — | — | 9.8 | 8.7 |
| Scenario | Operational State | Δ | ||
|---|---|---|---|---|
| iBuC-PTS | Baseline () | 9.14 | 8.93 | 0.21 |
| Mitigated (t) | 8.15 | 7.99 | 0.16 | |
| iBuC-WFS | Baseline () | 9.09 | 8.87 | 0.22 |
| Mitigated (t) | 8.09 | 7.94 | 0.15 |
Disclaimer/Publisher’s Note: The statements, opinions and data contained in all publications are solely those of the individual author(s) and contributor(s) and not of MDPI and/or the editor(s). MDPI and/or the editor(s) disclaim responsibility for any injury to people or property resulting from any ideas, methods, instructions or products referred to in the content. |
© 2026 by the authors. Licensee MDPI, Basel, Switzerland. This article is an open access article distributed under the terms and conditions of the Creative Commons Attribution (CC BY) license.
Share and Cite
Garofalaki, Z.; Kallergis, D.; Voyiatzis, I.; Douligeris, C. Securing Wireless Charging Ecosystems in Intelligent Transport Systems: An OCPP-Based Cybersecurity Impact Analysis. Vehicles 2026, 8, 120. https://doi.org/10.3390/vehicles8060120
Garofalaki Z, Kallergis D, Voyiatzis I, Douligeris C. Securing Wireless Charging Ecosystems in Intelligent Transport Systems: An OCPP-Based Cybersecurity Impact Analysis. Vehicles. 2026; 8(6):120. https://doi.org/10.3390/vehicles8060120
Chicago/Turabian StyleGarofalaki, Zacharenia, Dimitrios Kallergis, Ioannis Voyiatzis, and Christos Douligeris. 2026. "Securing Wireless Charging Ecosystems in Intelligent Transport Systems: An OCPP-Based Cybersecurity Impact Analysis" Vehicles 8, no. 6: 120. https://doi.org/10.3390/vehicles8060120
APA StyleGarofalaki, Z., Kallergis, D., Voyiatzis, I., & Douligeris, C. (2026). Securing Wireless Charging Ecosystems in Intelligent Transport Systems: An OCPP-Based Cybersecurity Impact Analysis. Vehicles, 8(6), 120. https://doi.org/10.3390/vehicles8060120