


Abstract
In our paper, we explore the consequences of replacing the commutative group operation used in Lai–Massey structures with a quasigroup operation. We introduce four quasigroup versions of the Lai–Massey structure and prove that for quasigroups isotopic with a group , the complexity of launching a differential attack against these variants of the Lai–Massey structure is equivalent to attacking an alternative structure based on . Then, we provide the conditions needed for correct decryption and further refine the resulting structure. The emerging structure is both intriguing and novel, and we hope that it will form the basis for future secure block ciphers based on non-commutative groups. In the case of commutative groups, we show that the resulting structure reduces to the classic Lai–Massey structure.
1. Introduction
When developing a block cipher, a key challenge is to design a set of permutations that is both easily implementable and exhibits behavior akin to random permutations. In tackling this challenge, the literature presents three primary approaches [1]. The first approach involves substitution–permutation networks (SPNs), which create a large block random-looking permutation by employing a series of substitution layers (composed of several substitution boxes (s-boxes) with a small block length) and permutation layers iterated over multiple rounds. On the other hand, Feistel and Lai–Massey structures adopt a different strategy. Instead of relying on invertible building blocks, these structures construct permutations using non-invertible components.
Differential cryptanalysis, introduced by Biham and Shamir [2], stands out as one of the most efficient tools for attacking block ciphers [3]. This method exploits how changes in certain plaintext bits propagate to the corresponding ciphertext, aiming to uncover vulnerabilities in the encryption process. In an ideal scenario with truly random permutations, the probability of predicting these changes is precisely , where n denotes the number of input bits. For instance, if n is set to 128 bits, this probability would be negligible, rendering predictions practically infeasible. However, the challenge lies in the need for practical block ciphers where permutations can be easily described, a criterion not satisfied by ideal permutations.
To overcome this hurdle, designers often resort to theoretical estimates based on assumptions that might not always align with real-world conditions. Consequently, practical block ciphers deviate from the ideal, rendering them susceptible to differential cryptanalysis. Hence, guarding against this type of attack becomes a fundamental design criterion for ensuring the security of symmetric primitives [4].
Latin squares, defined as matrices containing only ℓ symbols, possess the distinctive property that each symbol appears exactly once in every row and column [5]. When a set is equipped with a multiplication table that forms a Latin square, it establishes a quasigroup, a structure akin to a group but without the requirements of associativity and the presence of an identity element.
Despite quasigroups not being a prevalent choice in constructing cryptographic primitives, the literature showcases various designs based on these structures [6,7,8,9,10,11,12,13,14]. These cryptosystems highlight the versatility of quasigroups as group-like structures, offering an alternative perspective for certain cryptographic applications.
A recent approach, as highlighted in [15,16,17,18], employs commutative regular subgroups within the symmetric group to design SPN structures that exhibit resilience against classical differential cryptanalysis. However, these structures are vulnerable to differential attacks utilizing different group operations. Specifically, the security level of such structures against differential attacks is operation-dependent, indicating a variation in susceptibility based on the chosen operation. This approach is similar to the methodology employed in our paper, where we also explore different operations for constructing differential attacks against the proposed Lai–Massey structures. It is worth noting that the focus of [15,16,17,18] was to illustrate how a designer can embed a trapdoor into a symmetric structure, defined by knowledge of the weakening group operation. In contrast, our investigation aims to explore the potential strengthening of a Lai–Massey structure against differential cryptanalysis by changing the group operation to a quasigroup one.
In [19,20,21], the author proposes a direct extension of the three fundamental symmetric structures (SPNs, Feistel, and Lai–Massey) using quasigroup operations instead of traditional group operations between keys and (intermediary) plaintexts. The study focuses on quasigroup operations isotopic with a group operation, a popular method for constructing quasigroups. We further discuss only the results concerning Lai–Massey structures since this is the focus of our paper. In [20], the author begins by establishing the necessary conditions for correct decryption when employing a quasigroup operation. Unfortunately, the previous conditions limit the generalization of the Lai–Massey structure solely to non-commutative groups. Then, two structure categories are presented, one symmetric and one asymmetric. Subsequently, the author employs several arguments to prove the equivalence of the two categories in terms of differential cryptanalysis.
In this paper, we study the quasigroup Lai–Massey structure from a different perspective. We commence by generalizing the structures outlined in [20], subsequently delving into the security analysis of the derived structures, and ultimately, focusing on the necessary conditions needed for correct decryption. We manage to prove that the symmetric and asymmetric structures are differentially equivalent; thus, we only need to focus on one of them. In the non-commutative group case, we obtain a novel symmetric structure that generalizes the symmetric structure from [20]. To the best of the authors’ knowledge, this particular design has not been previously documented in the existing literature. Consequently, we believe that this structure warrants attention for future research, offering valuable insights from both theoretical and design perspectives.
In the case of commutative groups, the structure coincides with the classic Lai–Massey symmetric structure. Therefore, in this case, we obtain a negative result. Nevertheless, we believe its significance is two-fold.
- 1.
- In the majority of scientific reports and papers, authors often depict their results as if they were achieved seamlessly, without acknowledging the intricacies and challenges encountered during the process. This tendency contributes to a skewed perception of scientific research [22,23,24,25] and fosters the misconception that failure, serendipity, and unexpected outcomes are not integral aspects of scientific endeavors [23,26]. Consequently, our report aims to provide readers with insight into the authentic processes involved in the design phase of a cryptographic primitive.
- 2.
- Negative results and misguided directions are frequently under-reported in the scientific literature [23,27], leading to the risk of repeated errors. By sharing our findings, we aspire to prevent others from traversing similar unproductive paths, thereby contributing to a collective learning process. This approach aligns with the recommendation in [28], where the author advises documenting mistakes to avoid their recurrence in the future.
Structure of the Paper
2. Preliminaries
2.1. Notations
Throughout the paper, will denote the cardinality of set , and ⊕ will denote the bitwise xor operation. Also, using , we understand the concatenation of the strings x and y, and by , the set . When defining a permutation , we further use the shorthand , which translates into for all i values. We also define the identity permutation . Let • and ⊲ be binary operators. We define the binary operators and . Let . Using and , we understand the left and right half of X, respectively.
2.2. Quasigroups
In this section, we introduce a few basic notions about quasigroups. We base our exposition on [29].
Definition 1.
A quasigroup is a set equipped with a binary operation of multiplication , in which the specification of any two of the values in the equation determines the third uniquely.
Definition 2.
For a quasigroup , we define the left division as the unique solution y to . Similarly, we define the right division as the unique solution x to .
Lemma 1.
The following identities hold:
Lemma 2.
If is a group, and .
One common approach to constructing quasigroups [7,8,11,30] involves the following procedure. A group , such as or , and three random permutations are chosen. Subsequently, we define the quasigroup operation as . To understand why this leads to a quasigroup, observe that the mappings of x, y, and z to , , and are unique. Consequently, any equation of the form is uniquely resolved in the base group when provided with , , or .
Definition 3.
Let , be two quasigroups. An ordered triple of bijections π, ρ, ω of a set onto the set is called an isotopy of to if for any . If such an isotopism exists, then , are called isotopic.
Example 1.
Let , , and . The corresponding quasigroup operations for can be found in Table 1 [19].
Table 1.
Quasigroup operations.
Example 2.
Let . Then, is isotopic with , where and [30].
To gain a deeper understanding of the concept of isotopy, it is helpful to note that its three permutations correspond to the permutation of rows, columns, and symbols within a Latin square. These permutations naturally lead to the creation of another Latin square. Notably, being isotopic establishes an equivalence relation among quasigroups but not among groups, as isotopisms do not generally preserve associativity. It is important to recall that every group is an associative quasigroup.
Note that counting the number of distinct Latin squares is challenging. More precisely, the exact number, together with that of their isotopism classes, is known only for Latin squares of order smaller or equal to 11 [31,32,33].
2.3. Group Differential Cryptanalysis
Differential cryptanalysis was introduced by Biham and Shamir in [2] to analyze the Data Encryption Standard; as such, it was formulated exclusively for the group . Subsequently, the concept was generalized to commutative groups [34], non-commutative groups [19], and quasigroups [19,20,21]. Let be a group. We further present the notions of left and right differential probabilities for a permutation. Remark that these notions can also be defined for functions.
Definition 4.
Let , where . We define the group differential probabilities as follows:
where is a permutation and . When is commutative, we simply refer to and as .
Remark 1.
Let σ be randomly chosen. When , the distribution of values is studied in [35,36] and when is a generic abelian group in [37]. When σ is static (i.e., fixed and public for all symmetric structure’s implementations), the distribution of s for is studied, for example, in [38,39,40].
3. Lai–Massey Structure
3.1. Description
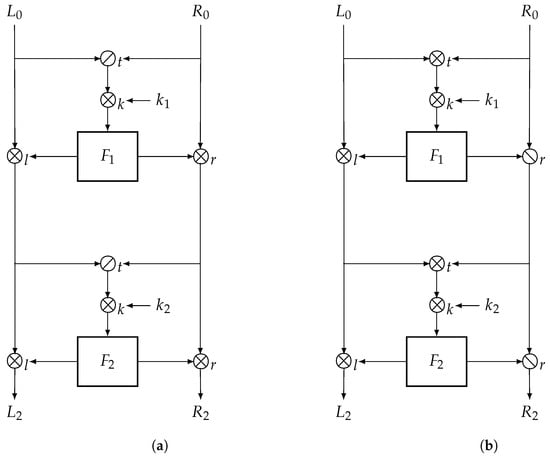
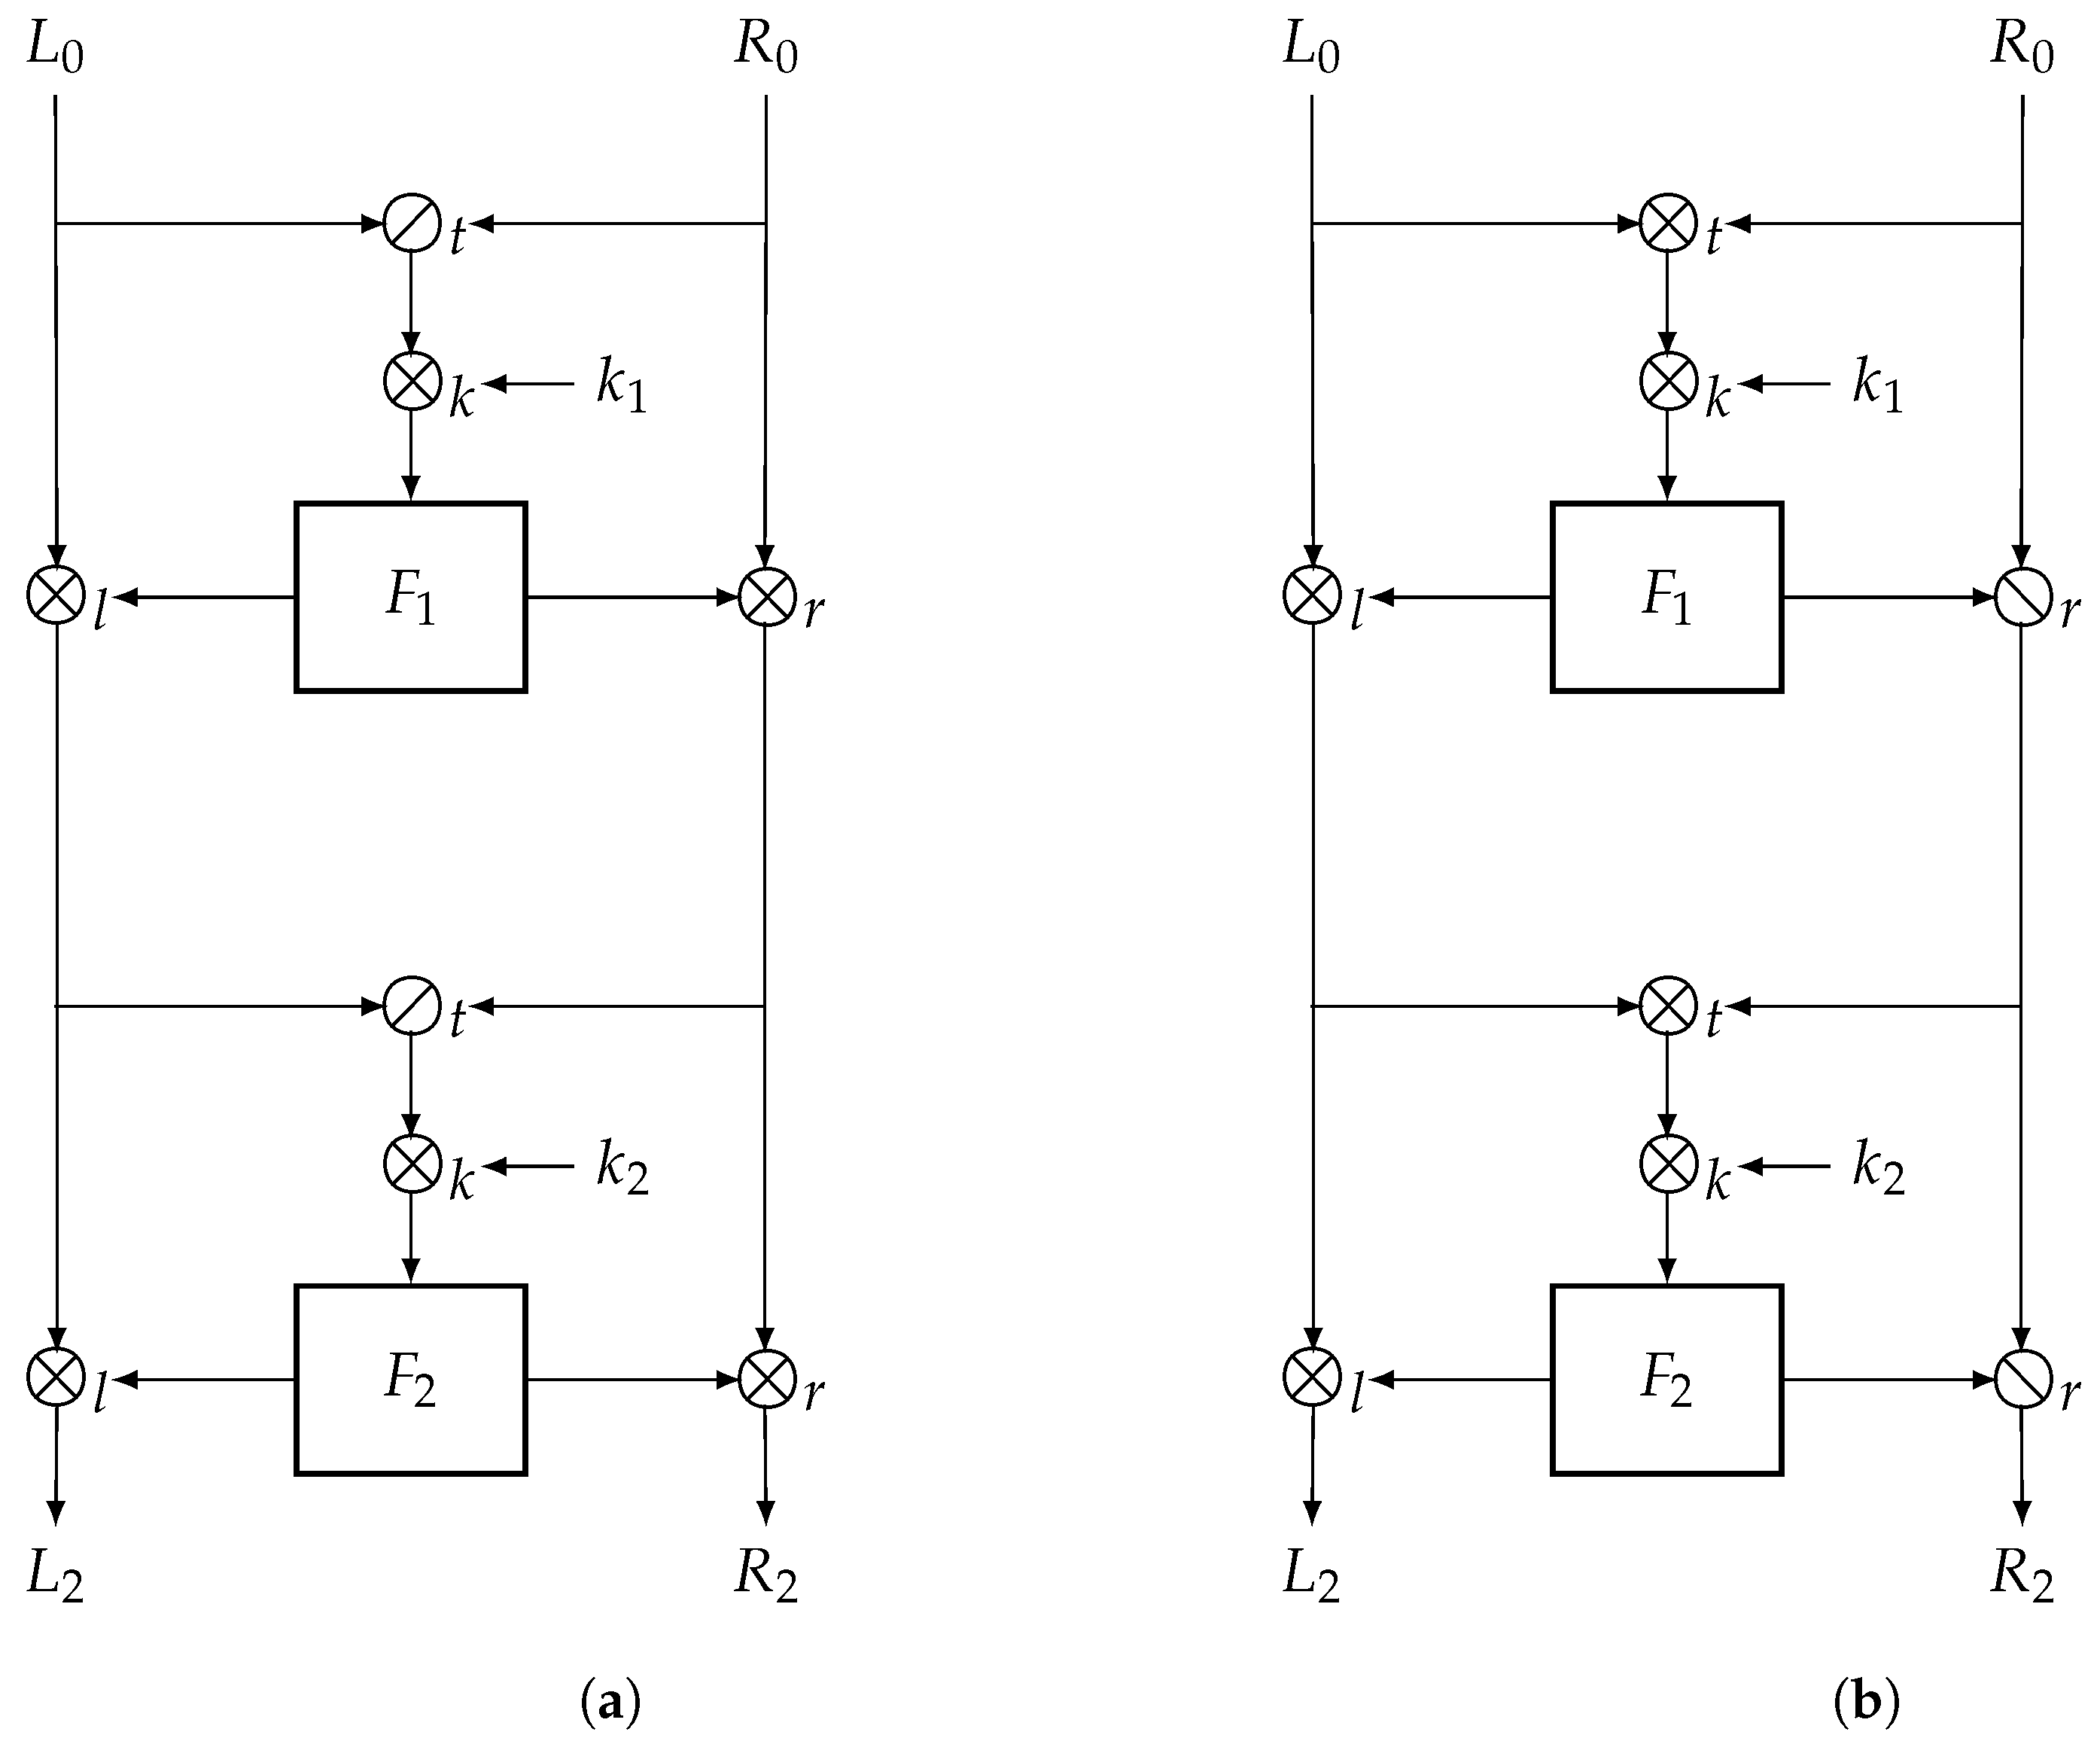
We further present two non-commutative versions of the Lai–Massey structure: a symmetric construction Figure 1a and an asymmetric one, Figure 1b. Note that, as mentioned in Section 1, we currently do not focus on their invertibility.
Figure 1.
Quasigroup Lai–Massey structures. (a) Symmetric version; (b) Asymmetric version.
In both constructions, the first step is to parse the plaintext into two halves, and . Note that for all versions, we make use of four quasigroup operations defined on indexed by t: top, l: left, r: right, and k: key, which are not necessarily distinct. In the symmetric case, for r rounds we compute the following:
where is defined as or . We further call these versions the left symmetric Lai–Massey structures. We can also define the right symmetric Lai–Massey structures as follows:
In the asymmetric case, we define the outer versions as
and the inner versions as
Remark 2.
When , and we define , , and ; the result is the symmetric non-commutative group Lai–Massey structure detailed in [21]. For the asymmetric version, as outlined in [21], we need to set , in our asymmetric structure.
3.2. Symmetric Structure Analysis
In this subsection, we extend the differential probabilities introduced in [21] for non-commutative group symmetric Lai–Massey structures to our quasigroup version.
Definition 5.
Let K be a key, , for and . We define the symmetric Lai–Massey quasigroup differential probabilities as follows:
- 1.
- Let and . Then,
- 2.
- Let and . Then,
- 3.
- Let and . Then,
- 4.
- Let and . Then,
where is a function, , and .
Remark 3.
Let be two functions. When , we denote the differential probability with . We also use the same convention for the rest of the Lai–Massey differential probabilities.
Let , where . We further study the impact of the s, s, and s on the symmetric Lai–Massey structures.
Lemma 3.
Let , , , and . Also, let , , , , and . We define , , , and , as the associated left and right divisions, where . Then, the following identities hold:
where and .
Proof.
Let and . First, we rewrite as follows:
Let . Then,
and
Let , and . Then, using Equation (2), we obtain
and
Let . From Equation (4), we derive
which leads to
Using Equations (1), (3) and (5), we obtain
The remaining equality is proven using similar techniques. □
The proof of Lemma 4 follows a similar rationale to the proof of Lemma 3; thus, it is omitted.
Lemma 4.
Let , , , . Also, let , , , , and . We define , , , and , as the associated left and right divisions, where . Then, the following identities hold:
where and .
Lemmas 3 and 4 tell us that it is irrelevant from a differential point of view (e.g., we obtain the same differential probabilities and ) if we define the quasigroup operation with or , where . The same is true for (left case) or (right case). Thus, we further restrict our study (without loss of generality) to the quasigroup operations and (left case) or (right side). Now, considering the non-linear layer F, we observe, according to Lemmas 3 and 4, that it would be simpler to study and instead of F.
Lemma 5.
Let , , , where . We define , , and , as the associated left and right divisions, where . Then, the following identities hold:
where and .
Proof.
As before, let and . Also, let and . Then,
and
Let and . Then, we derive
which leads to
Using Equations (6)–(10), we obtain
The second equality is proven using similar techniques. □
The proof of Lemma 6 follows a similar rationale to the proof of Lemma 5; thus, it is omitted.
Lemma 6.
Let , , and , where . We define , , and , as the associated left and right divisions, where . Then, the following identities hold:
where and .
Lemmas 5 and 6 indicate that the choice of (in the left case) and (in the right case) is irrelevant from a differential perspective. As illustrated in Equation (8), we can restrict our study to . Therefore, we further consider (in the left case) and (in the right case) and that . Moreover, these lemmas indicate that we can consider and instead of and . A closer examination of the non-linear layers reveals that they can be expressed as . Consequently, it is more convenient to investigate rather than .
Since K and, for example, are generated as a pair, it suffices from a differential point of view to simply consider as being the key that we want to recover. This is possible since our final scope is to recover the plaintexts and not the initial key used by the symmetric structure. As a consequence, it suffices to restrict our study to (left version) and (right version).
Taking into account the previous arguments, we obtain the Lai–Massey structure depicted in Figure 2.
Figure 2.
Symmetric non-commutative group Lai–Massey structure (version 1).
A different point of view of studying the version 1 structure is to redefine the differential probabilities as follows:
- 1.
- Let and . Then,
- 2.
- Let and . Then,
- 3.
- Let and . Then,
- 4.
- Let and . Then,
We further provide the reader with some conditions that guarantee key independence for the differential probabilities associated with the Lai–Massey round functions.
Lemma 7.
If , and are morphisms; then, and are key independents.
Proof.
We begin by rewriting and . Then,
and
Let and . Using Equations (11) and (12), we obtain
and
Let , and . From Equation (14), we derive
and
Hence, we have
Note that Equation (15) is equivalent to
Using Equations (11), (13), (15) and (16), we obtain the desired equality. The remaining relations are proven similarly. □
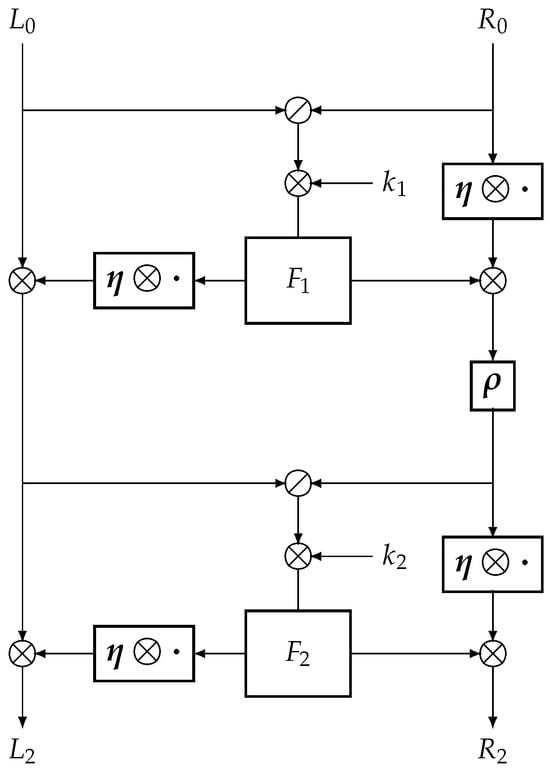
Upon closer examination of Lemma 7’s proof, it becomes evident that we can derive the equivalent structure depicted in Figure 3. Its corresponding differential probabilities are
where and , and
where and . When and are independent of the key, the security analysis simplifies and we can offer higher security guarantees (in practice, we cannot check the differential probabilities for all the keys). Hence, we restrict our study to for and .
Figure 3.
Symmetric non-commutative group Lai–Massey structure (version 2).
We further state, without proof, the conditions required for key independence for the remaining differential probabilities.
Lemma 8.
If , and are morphisms, then and are key independents.
Similarly to the previous case, we can derive an equivalent structure using Lemma 8’s proof. We provide only its corresponding differential probabilities
where and , and
where and .
The following corollaries indicate that it is sufficient to focus solely on a version 2 structure from a differential perspective if is a morphism.
Corollary 1.
Let and . Then,
Proof.
We first observe that
So, . Also,
Thus, we obtain the desired result. □
Corollary 2.
We define , and . If is a morphisms, then
Proof.
Let and . We observe that
and
Thus, we obtain the desired equality. □
We further delve into the conditions required for correct decryption. We can observe that this requirement translates into
where . We remark that Equation (17) is equivalent to
which leads to
Lemma 9.
Let . We can decrypt it if and only if and .
Proof.
First, note that Equation (18) holds for any and . Therefore, we can fix an arbitrary and denote it by . Thus, we obtain that for any . This leads to for any x since Z is simply a translation of any with a fixed point. Consequently, from Equation (18), we obtain that for any x. We leave the converse as an exercise. □
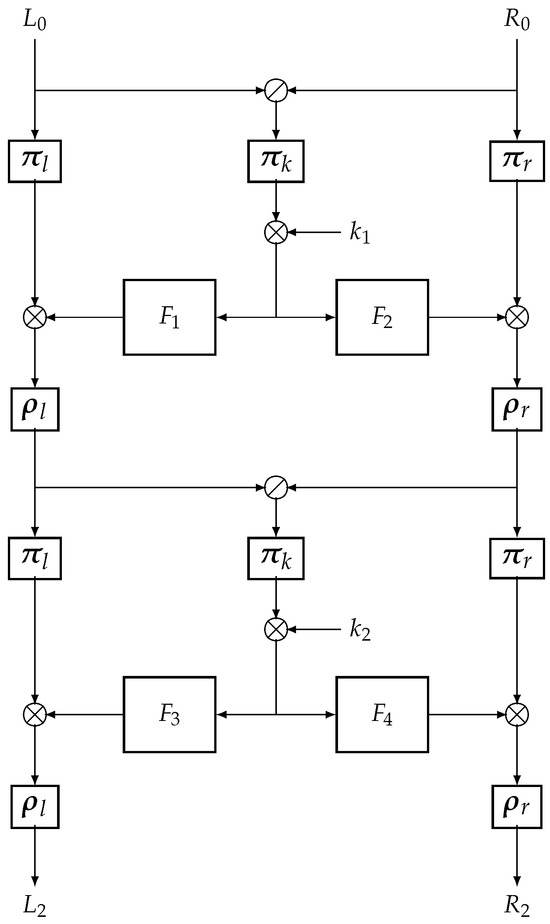
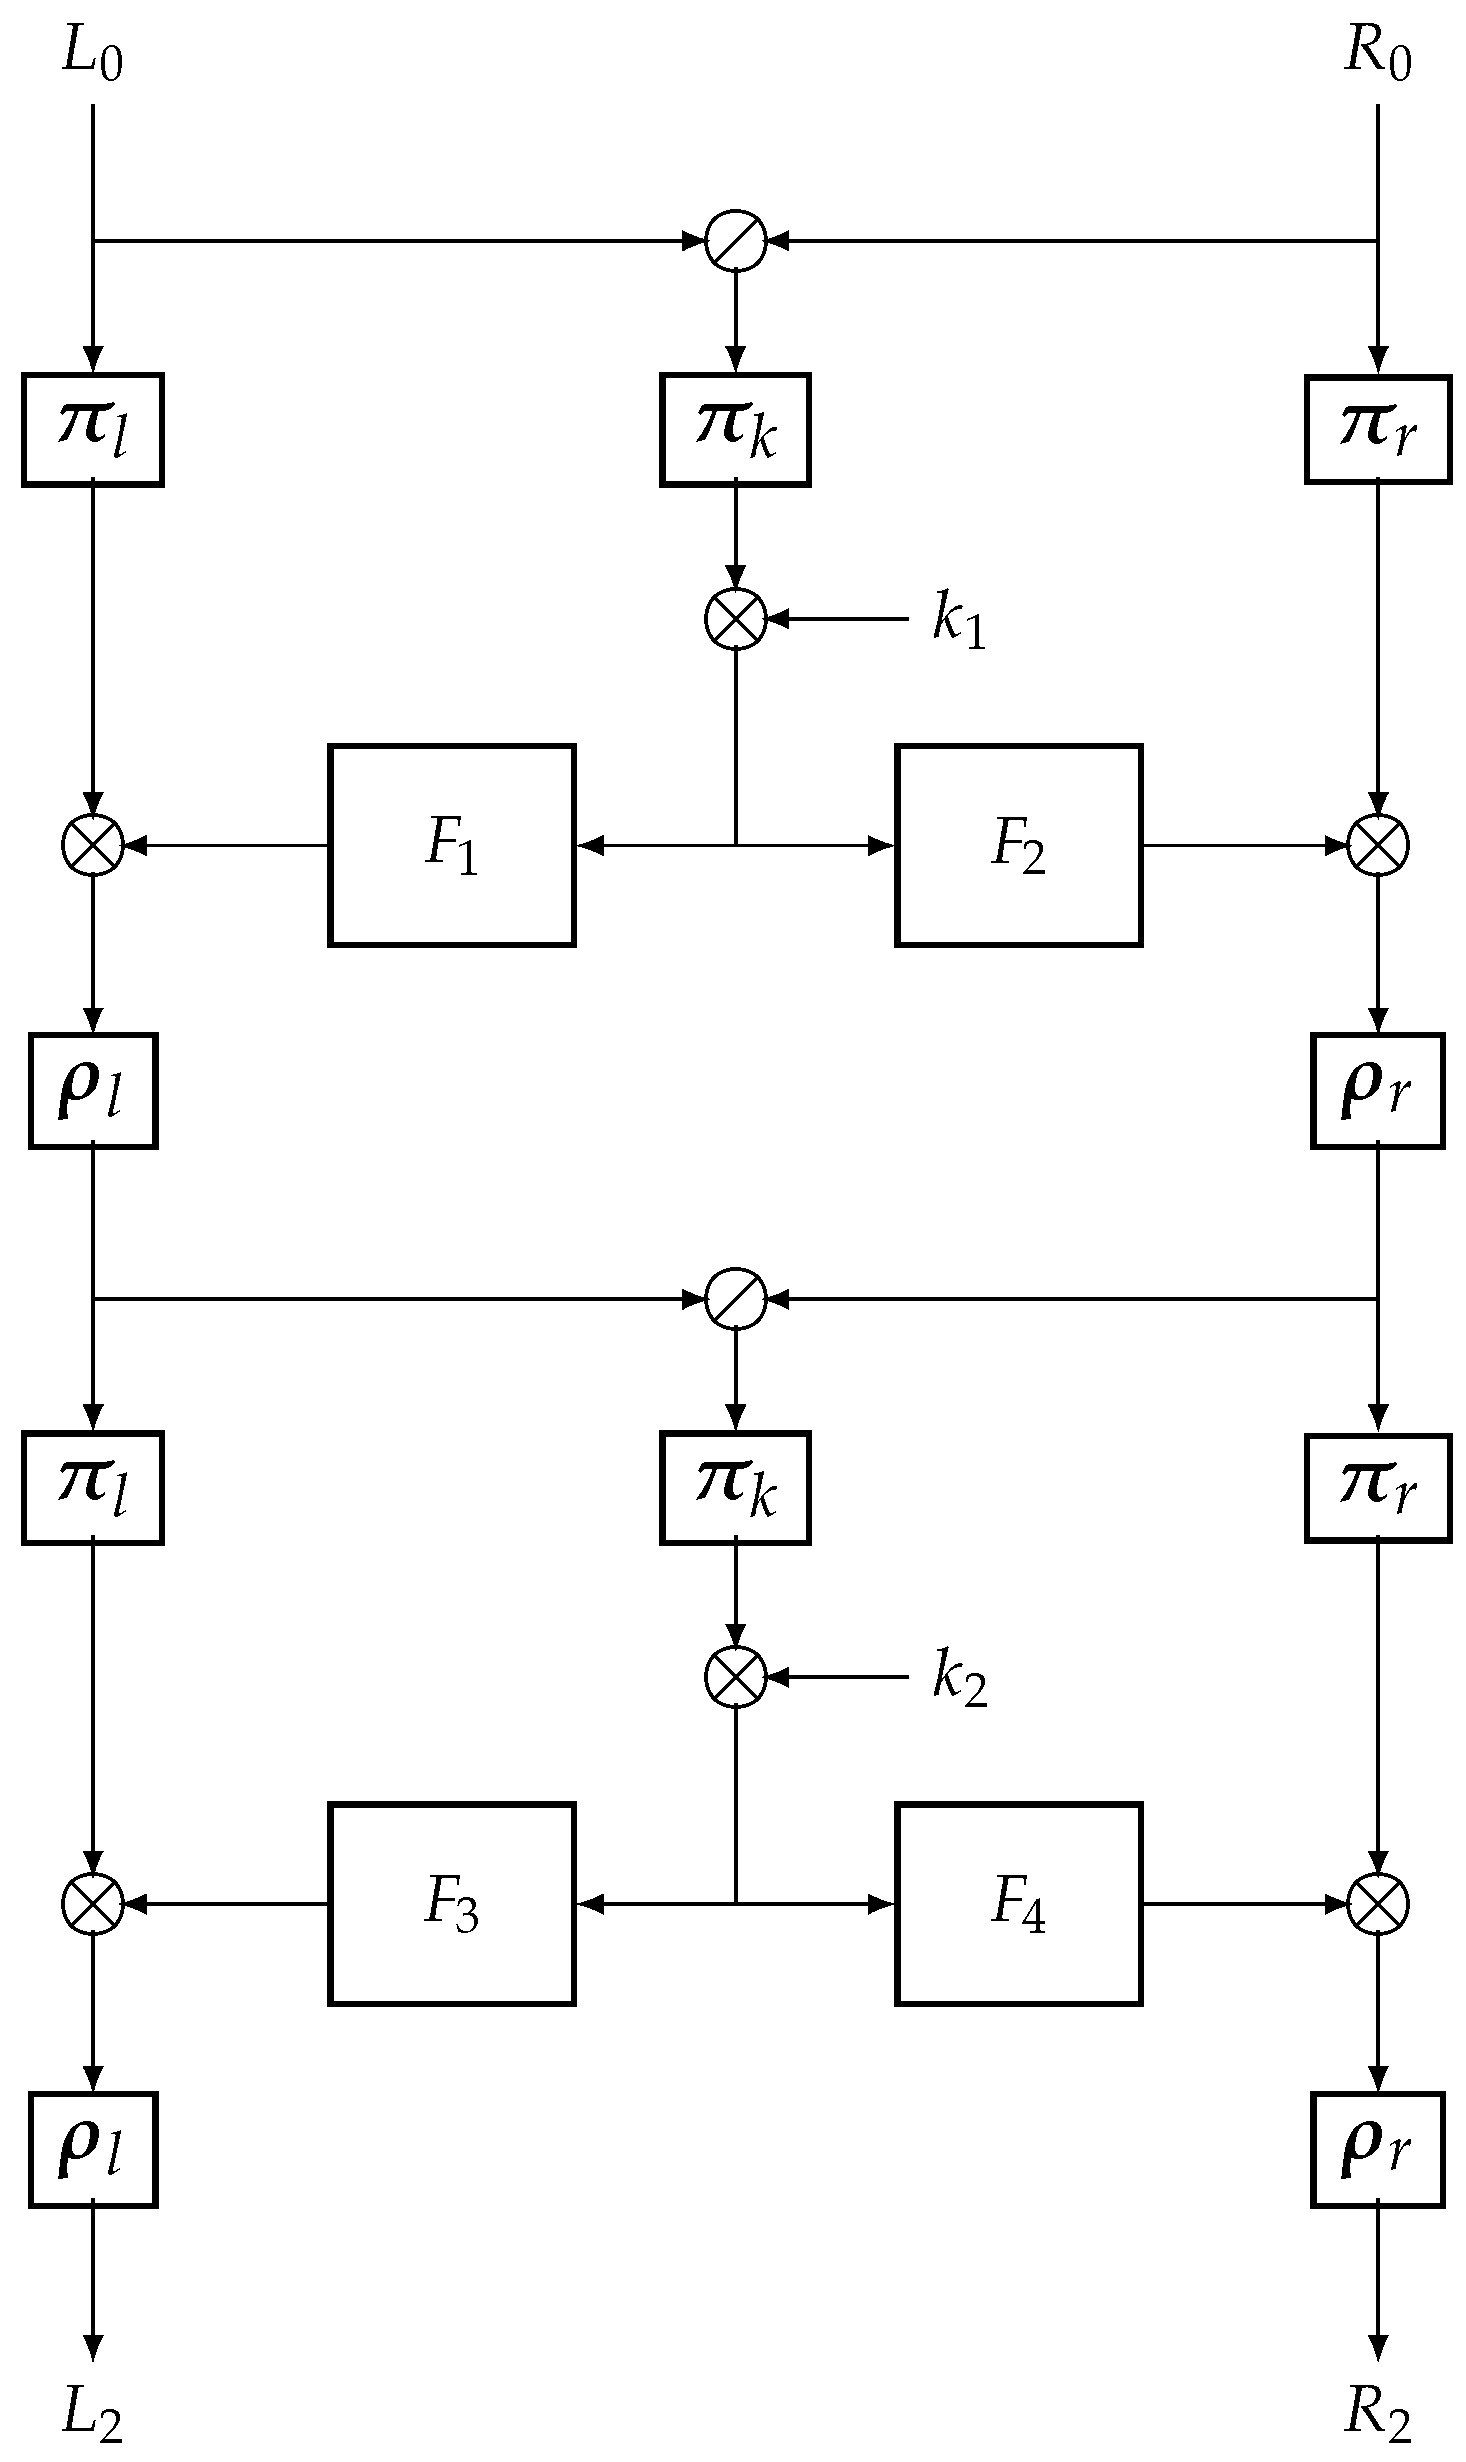
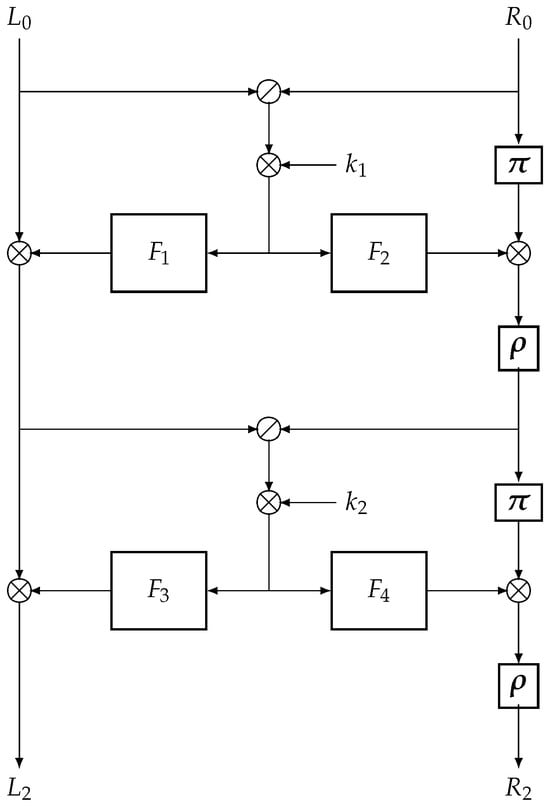
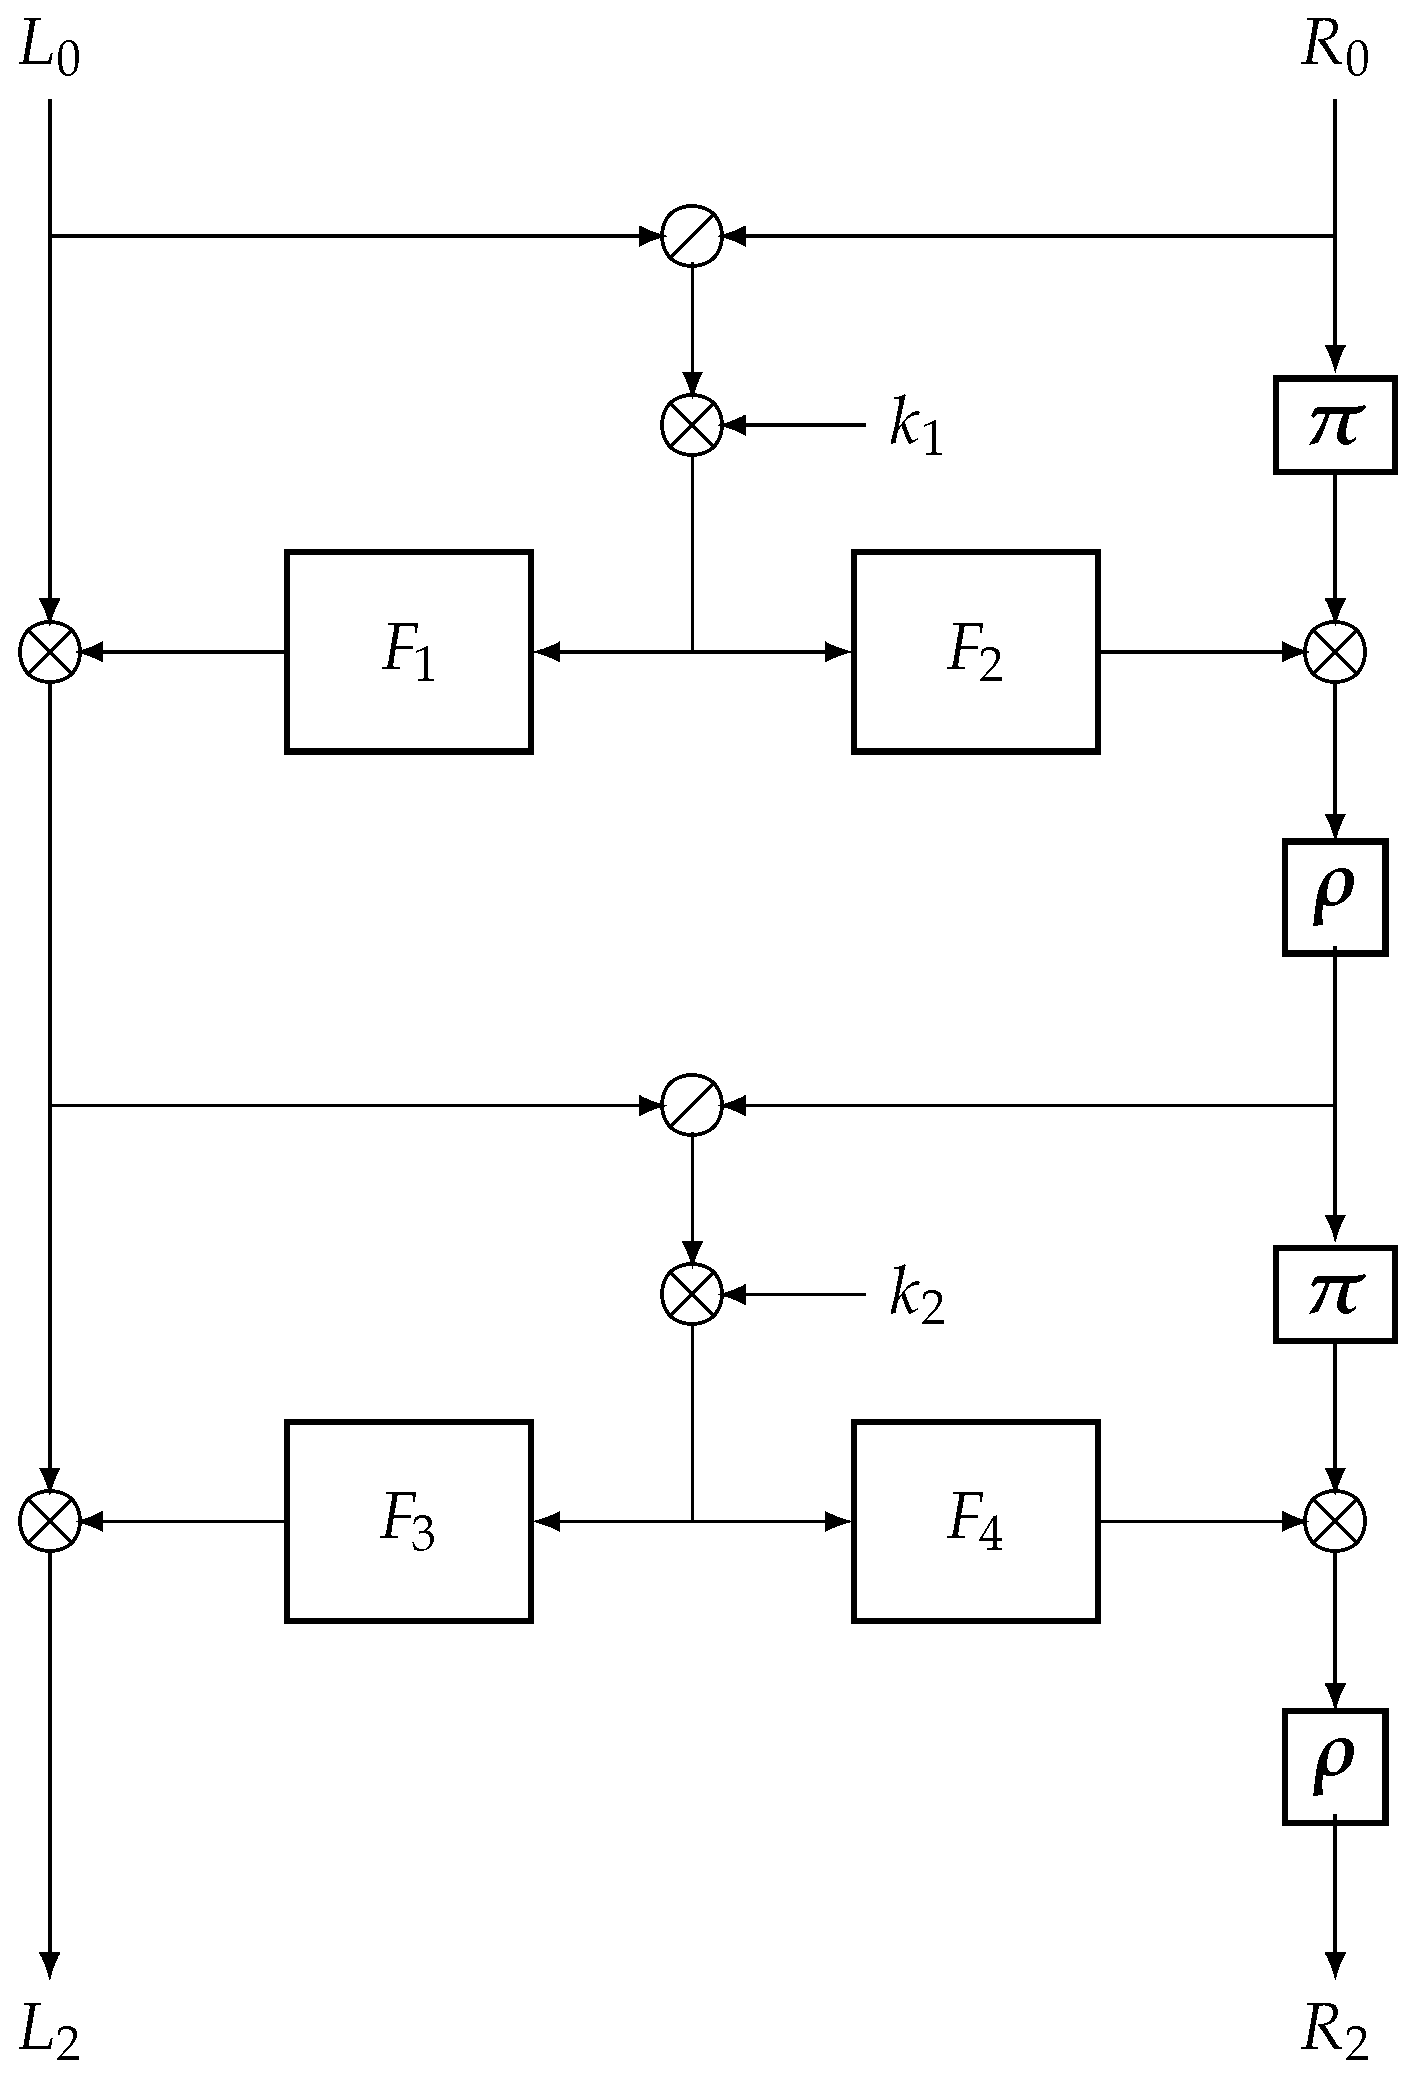
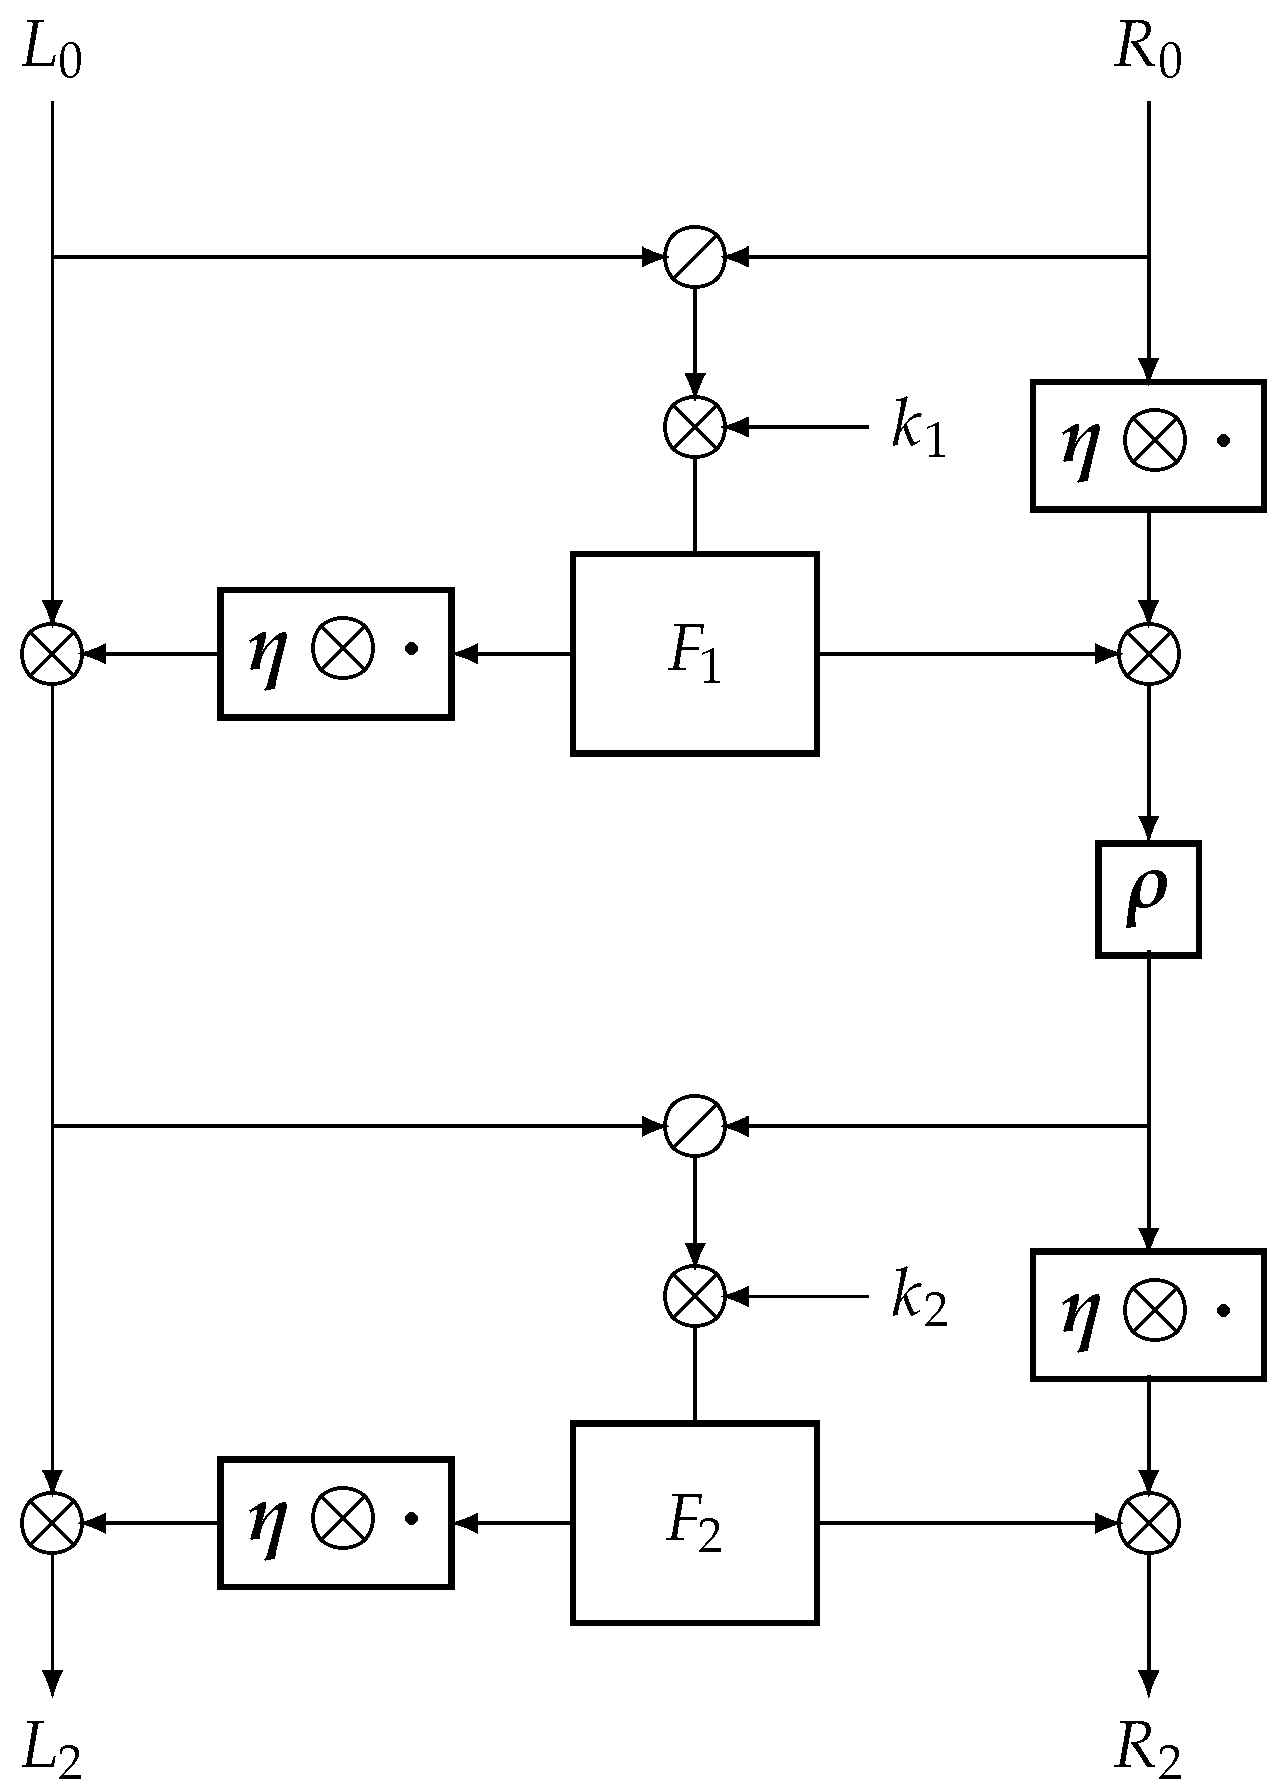
Taking into account the previous arguments, we obtain the Lai–Massey structure depicted in Figure 4.
Figure 4.
Symmetric non-commutative group Lai–Massey structure (version 3).
The following corollary tells us that, in the case of commutative groups, the only meaningful (from a differential perspective) structure is the one with and (equivalently, the one with , where is the identity element of ).
Corollary 3.
If is Abelian and is a morphism, then
Proof.
Let and . We observe that
and
Thus, we obtain the desired equality. □
When , the version 3 structure can be easily distinguished from a random permutation by simply checking if, for example, . We further introduce a definition from [20], which will prove useful for removing this vulnerability.
Definition 6.
A permutation φ is a right orthomorphism if is a permutation. If is a permutation, then φ is called a left orthomorphism.
Lemma 10.
Let and . The following property holds:
Proof.
We observe that
If we denote , we obtain
and thus, we obtain the desired property. □
Corollary 4.
If is a right orthomorphism, then is a random element.
Proof.
Let . According to Lemma 10, we obtain that
Since is random function, A is randomly distributed. Since is a right orthomorphism, is also random. Therefore, we obtain that is uniformly distributed. □
To summarize all the lemmas and observations we provide the reader with Proposition 1.
Proposition 1.
A symmetric quasigroup Lai–Massey structure derived from a symmetric non-commutative group Lai–Massey structure using an isotopy has the same differential security as version 3 (see Figure 4) if ρ is a morphism and we require correct decryption. If the group is commutative, we obtain that symmetric group Lai–Massey structure and version 3 are equivalent.
3.3. Asymmetric Structure Analysis
In this section, we extend the notion of differential cryptanalysis to asymmetric Lai–Massey structures. Then, as in the symmetric case, we show that the structure can be defined using only group operations. Finally, we show that the resulting structure is equivalent to the version 1 symmetric structure.
Definition 7.
Let K be a key and for . We define the asymmetric Lai–Massey quasigroup differential probabilities as follows:
- 1.
- Let , and . Then,
- 2.
- Let , and . Then,
- 3.
- Let , and . Then,
- 4.
- Let , and . Then,
where is a function, and , and .
The next lemmas enable us to restrict our study to the case where due to the differential equivalency. Note that the Lemmas 11 and 12 are proven similarly to Lemma 3; hence, we omit their proof.
Lemma 11.
Let , , , . Also, let , , , , and . We define , , , and , as the associated left and right divisions, where . Then, the following identities hold:
where and .
Lemma 12.
Let , , , . Also, let , , , , and . We define , , , and , as the associated left and right divisions, where . Then, the following identities hold:
where and .
The following lemmas are the asymmetric equivalents of Lemmas 5 and 6; thus, we state them without proof.
Lemma 13.
Let , , , . We define , , and , as the associated left and right divisions, where . Then, the following identities hold:
where and .
Lemma 14.
Let , , , . We define , , and , as the associated left and right divisions, where . Then, the following identities hold:
where and .
Let . Before presenting the resulting asymmetric structure, we would like to point out that
where, for the last equalities, we used Lemma 2.
Considering the aforementioned remark and employing arguments akin to the symmetric counterpart, we obtain a Lai–Massey structure similar (the top and right operations are changed to ⊗ and (OLM) or ⊘ (ILM)) to the one depicted in Figure 2. The associated differential properties are as follows:
- 1.
- Let , , and . Then,
- 2.
- Let , , and . Then,
- 3.
- Let , , and . Then,
- 4.
- Let , , and . Then,
The following lemma shows that the asymmetric and the symmetric structures are differentially equivalent. Therefore, we can directly apply the results from Section 3.2.
Lemma 15.
Let , . Then, the following identities hold:
Proof.
Let and . We observe that
and
The remaining equalities are proven similarly. □
To summarize all the lemmas and observations, we refer the reader to Proposition 2.
Proposition 2.
An asymmetric quasigroup Lai–Massey structure has the same differential security a symmetric quasigroup Lai–Massey structure.
4. Conclusions
In this paper, we studied the effect of isotropic quasigroups concerning groups in the design of cryptographic symmetric structures. More precisely, for quasigroup extensions of the Lai–Massey structure, we investigated the security implications and unveiled interesting equivalences with other symmetric structures based on the underlying group. Furthermore, we highlighted the necessary conditions for having correct decryption and we established that mounting a differential attack against the symmetric version is equivalent to attacking an alternative asymmetric structure.
Future Work
It would be intriguing to investigate the effect of using quasigroups that do not exhibit isotopy to groups. Additionally, exploring the influence of other symmetries, such as parastrophisms [41] or paratopisms [42], could provide valuable insights. Another interesting area of research is to compare the performance and security of the proposed non-commutative structure with other block cipher architectures, such as SPNs or Feistel networks.
Funding
This research received no external funding.
Data Availability Statement
No new data were created or analyzed in this study. Data sharing is not applicable to this article.
Conflicts of Interest
The author declares no conflict of interest.
References
- Vaudenay, S. A Classical Introduction to Cryptography: Applications for Communications Security; Springer Science & Business Media: Berlin/Heidelberg, Germany, 2005. [Google Scholar]
- Biham, E.; Shamir, A. Differential Cryptanalysis of DES-like Cryptosystems. J. Cryptol. 1991, 4, 3–72. [Google Scholar] [CrossRef] [Scilit]
- Knudsen, L.R.; Robshaw, M. The Block Cipher Companion; Springer Science & Business Media: Berlin/Heidelberg, Germany, 2011. [Google Scholar]
- Mouha, N. On Proving Security against Differential Cryptanalysis. In Proceedings of the CFAIL 2019, Columbia, MO, USA, 31 May–2 June 2019. [Google Scholar]
- Dénes, J.; Keedwell, A.D. Latin Squares: New Developments in the Theory and Applications; Elsevier: Amsterdam, The Netherlands, 1991; Volume 46. [Google Scholar]
- Lai, X.; Massey, J.L. A Proposal for a New Block Encryption Standard. In Advances in Cryptology—EUROCRYPT’90: Workshop on the Theory and Application of Cryptographic Techniques Aarhus, Denmark, 21–24 May 1990; Proceedings 9; Springer: Berlin/Heidelberg, Germany, 1991; Volume 473, pp. 389–404. [Google Scholar]
- Gligoroski, D.; Markovski, S.; Kocarev, L. Edon-R, An Infinite Family of Cryptographic Hash Functions. Int. J. Netw. Secur. 2009, 8, 293–300. [Google Scholar]
- Gligoroski, D.; Markovski, S.; Knapskog, S.J. The Stream Cipher Edon80. In New Stream Cipher Designs; Springer: Berlin/Heidelberg, Germany, 2008; Volume 4986, pp. 152–169. [Google Scholar]
- Bakhtiari, S.; Safavi-Naini, R.; Pieprzyk, J. A Message Authentication Code Based on Latin Squares. In Australasian Conference on Information Security and Privacy; Springer: Berlin/Heidelberg, Germany, 1997; Volume 1270, pp. 194–203. [Google Scholar]
- Dénes, J.; Keedwell, A.D. A New Authentication Scheme Based on Latin Squares. Discret. Math. 1992, 106, 157–161. [Google Scholar] [CrossRef] [Scilit]
- Kościelny, C. A Method of Constructing Quasigroup-Based Stream-Ciphers. Appl. Math. Comput. Sci. 1996, 6, 109–122. [Google Scholar]
- Chauhan, D.; Gupta, I.; Verma, R. Quasigroups and Their Applications in Cryptography. Cryptologia 2021, 45, 227–265. [Google Scholar] [CrossRef] [Scilit]
- Chauhan, D.; Gupta, I.; Verma, R. Construction of Cryptographically Strong S-boxes from Ternary Quasigroups of Order 4. Cryptologia 2021, 569, 658–680. [Google Scholar] [CrossRef] [Scilit]
- Bakeva, V.; Popovska-Mitrovikj, A.; Mechkaroska, D.; Dimitrova, V.; Jakimovski, B.; Ilievski, V. Gaussian Channel Transmission of Images and Audio Files Using Cryptcoding. IET Commun. 2019, 13, 1625–1632. [Google Scholar] [CrossRef] [Scilit]
- Brunetta, C.; Calderini, M.; Sala, M. On Hidden Sums Compatible with a Given Block Cipher Diffusion Layer. Discret. Math. 2019, 342, 373–386. [Google Scholar] [CrossRef] [Scilit]
- Calderini, M.; Sala, M. On Differential Uniformity of Maps that May Hide an Algebraic Trapdoor. In International Conference on Algebraic Informatics; Springer: Cham, Switzerland, 2015; Volume 9270, pp. 70–78. [Google Scholar]
- Calderini, M.; Civino, R.; Sala, M. On Properties of Translation Groups in the Affine General Linear Group with Applications to Cryptography. J. Algebra 2021, 569, 658–680. [Google Scholar] [CrossRef] [Scilit]
- Civino, R.; Blondeau, C.; Sala, M. Differential attacks: Using alternative operations. Des. Codes Cryptogr. 2019, 87, 225–247. [Google Scholar] [CrossRef] [Scilit]
- Teşeleanu, G. Quasigroups and Substitution Permutation Networks: A Failed Experiment. Cryptologia 2021, 45, 266–281. [Google Scholar] [CrossRef] [Scilit]
- Teşeleanu, G. Cryptographic Symmetric Structures Based on Quasigroups. Cryptologia 2023, 47, 365–392. [Google Scholar] [CrossRef] [Scilit]
- Teşeleanu, G. The Security of Quasigroups Based Substitution Permutation Networks. In International Conference on Information Technology and Communications Security; Springer: Cham, Switzerland, 2022; Volume 13809, pp. 306–319. [Google Scholar]
- Medawar, P. Is the Scientific Paper a Fraud? List 1963, 70, 377–378. [Google Scholar]
- Howitt, S.M.; Wilson, A.N. Revisiting “Is the Scientific Paper a Fraud?”. EMBO Rep. 2014, 15, 481–484. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Tao, T. Ask Yourself Dumb Questions—And Answer Them! Available online: https://terrytao.wordpress.com/career-advice/ask-yourself-dumb-questions-and-answer-them/ (accessed on 2 August 2024).
- Weidman, D.R. Emotional Perils of Mathematics. Science 1965, 149, 1048. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Schwartz, M.A. The Importance of Stupidity in Scientific Research. J. Cell Sci. 2008, 121, 1771. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Truran, P. Practical Applications of the Philosophy of Science: Thinking about Research; Springer Science & Business Media: Berlin/Heidelberg, Germany, 2013. [Google Scholar]
- Tao, T. Use the Wastebasket. Available online: https://terrytao.wordpress.com/career-advice/use-the-wastebasket/ (accessed on 2 August 2024).
- Smith, J.D. Four Lectures on Quasigroup Representations. Quasigroups Relat. Syst. 2007, 15, 109–140. [Google Scholar]
- Vojvoda, M.; Sỳs, M.; Jókay, M. A Note on Algebraic Properties of Quasigroups in Edon80. Technical Report, eSTREAM report 2007/005, 2007. Available online: https://www.academia.edu/71592476/A_Note_on_Algebraic_Properties_of_Quasigroups (accessed on 2 August 2024).
- Hulpke, A.; Kaski, P.; Östergård, P. The Number of Latin Squares of Order 11. Math. Comput. 2011, 80, 1197–1219. [Google Scholar] [CrossRef] [Scilit]
- McKay, B.D.; Wanless, I.M. On the Number of Latin Squares. Ann. Comb. 2005, 9, 335–344. [Google Scholar] [CrossRef] [Scilit]
- McKay, B.D.; Meynert, A.; Myrvold, W. Small Latin Squares, Quasigroups, and Loops. J. Comb. Des. 2007, 15, 98–119. [Google Scholar] [CrossRef] [Scilit]
- Lai, X.; Massey, J.L.; Murphy, S. Markov Ciphers and Differential Cryptanalysis. In Advances in Cryptology—EUROCRYPT’91: Workshop on the Theory and Application of Cryptographic Techniques Brighton, UK, 8–11 April 1991; Proceedings 10; Springer: Berlin/Heidelberg, Germany, 1991; Volume 547, pp. 17–38. [Google Scholar]
- O’Connor, L. On the Distribution of Characteristics in Bijective Mappings. In Advances in Cryptology—EUROCRYPT’93: Workshop on the Theory and Application of Cryptographic Techniques, Lofthus, Norway, 23–27 May 1993; Proceedings 12; Springer: Berlin/Heidelberg, Germany, 1994; Volume 765, pp. 360–370. [Google Scholar]
- O’Connor, L. On the Distribution of Characteristics in Bijective Mappings. J. Cryptol. 1995, 8, 67–86. [Google Scholar] [CrossRef] [Scilit]
- Hawkes, P.; O’Connor, L. XOR and Non-XOR Differential Probabilities. In Advances in Cryptology—EUROCRYPT’99: International Conference on the Theory and Application of Cryptographic Techniques, Prague, Czech Republic, 2–6 May 1999; Proceedings 18; Springer: Berlin/Heidelberg, Germany, 1999; Volume 1592, pp. 272–285. [Google Scholar]
- Nyberg, K. Perfect Nonlinear S-boxes. In Workshop on the Theory and Application of of Cryptographic Techniques; Springer: Berlin/Heidelberg, Germany, 1991; Volume 547, pp. 378–386. [Google Scholar]
- Canteaut, A.; Charpin, P.; Dobbertin, H. Weight Divisibility of Cyclic Codes, Highly Nonlinear Functions on F2m, and Crosscorrelation of Maximum-Length Sequences. SIAM J. Discret. Math. 2000, 13, 105–138. [Google Scholar] [CrossRef] [Scilit]
- Dobbertin, H. One-to-One Highly Nonlinear Power Functions on GF(2n). Appl. Algebra Eng. Commun. Comput. 1998, 9, 139–152. [Google Scholar] [CrossRef] [Scilit]
- Dudek, W. Parastrophes of Quasigroups. Quasigroups Relat. Syst. 2015, 23, 221–230. [Google Scholar]
- Falcón, R.M.; Falcón, Ó.J.; Núñez, J. A Historical Perspective of the Theory of Isotopisms. Symmetry 2018, 10, 322. [Google Scholar] [CrossRef] [Scilit]

Disclaimer/Publisher’s Note: The statements, opinions and data contained in all publications are solely those of the individual author(s) and contributor(s) and not of MDPI and/or the editor(s). MDPI and/or the editor(s) disclaim responsibility for any injury to people or property resulting from any ideas, methods, instructions or products referred to in the content. |
© 2024 by the author. Licensee MDPI, Basel, Switzerland. This article is an open access article distributed under the terms and conditions of the Creative Commons Attribution (CC BY) license (https://creativecommons.org/licenses/by/4.0/).