Article

Distributed Authentication Model for Secure Network Connectivity in Network Separation Technology
1
Department of Future Convergence Technology Engineering, Sungshin Women’s University, Seoul 02844, Korea
2
Department of Convergence Security Engineering, Sungshin Women’s University, Seoul 02844, Korea
*
Author to whom correspondence should be addressed.
Sensors 2022, 22(2), 579; https://doi.org/10.3390/s22020579
Submission received: 1 December 2021 / Revised: 10 January 2022 / Accepted: 11 January 2022 / Published: 12 January 2022
(This article belongs to the Special Issue Optical Network Automation)

Abstract

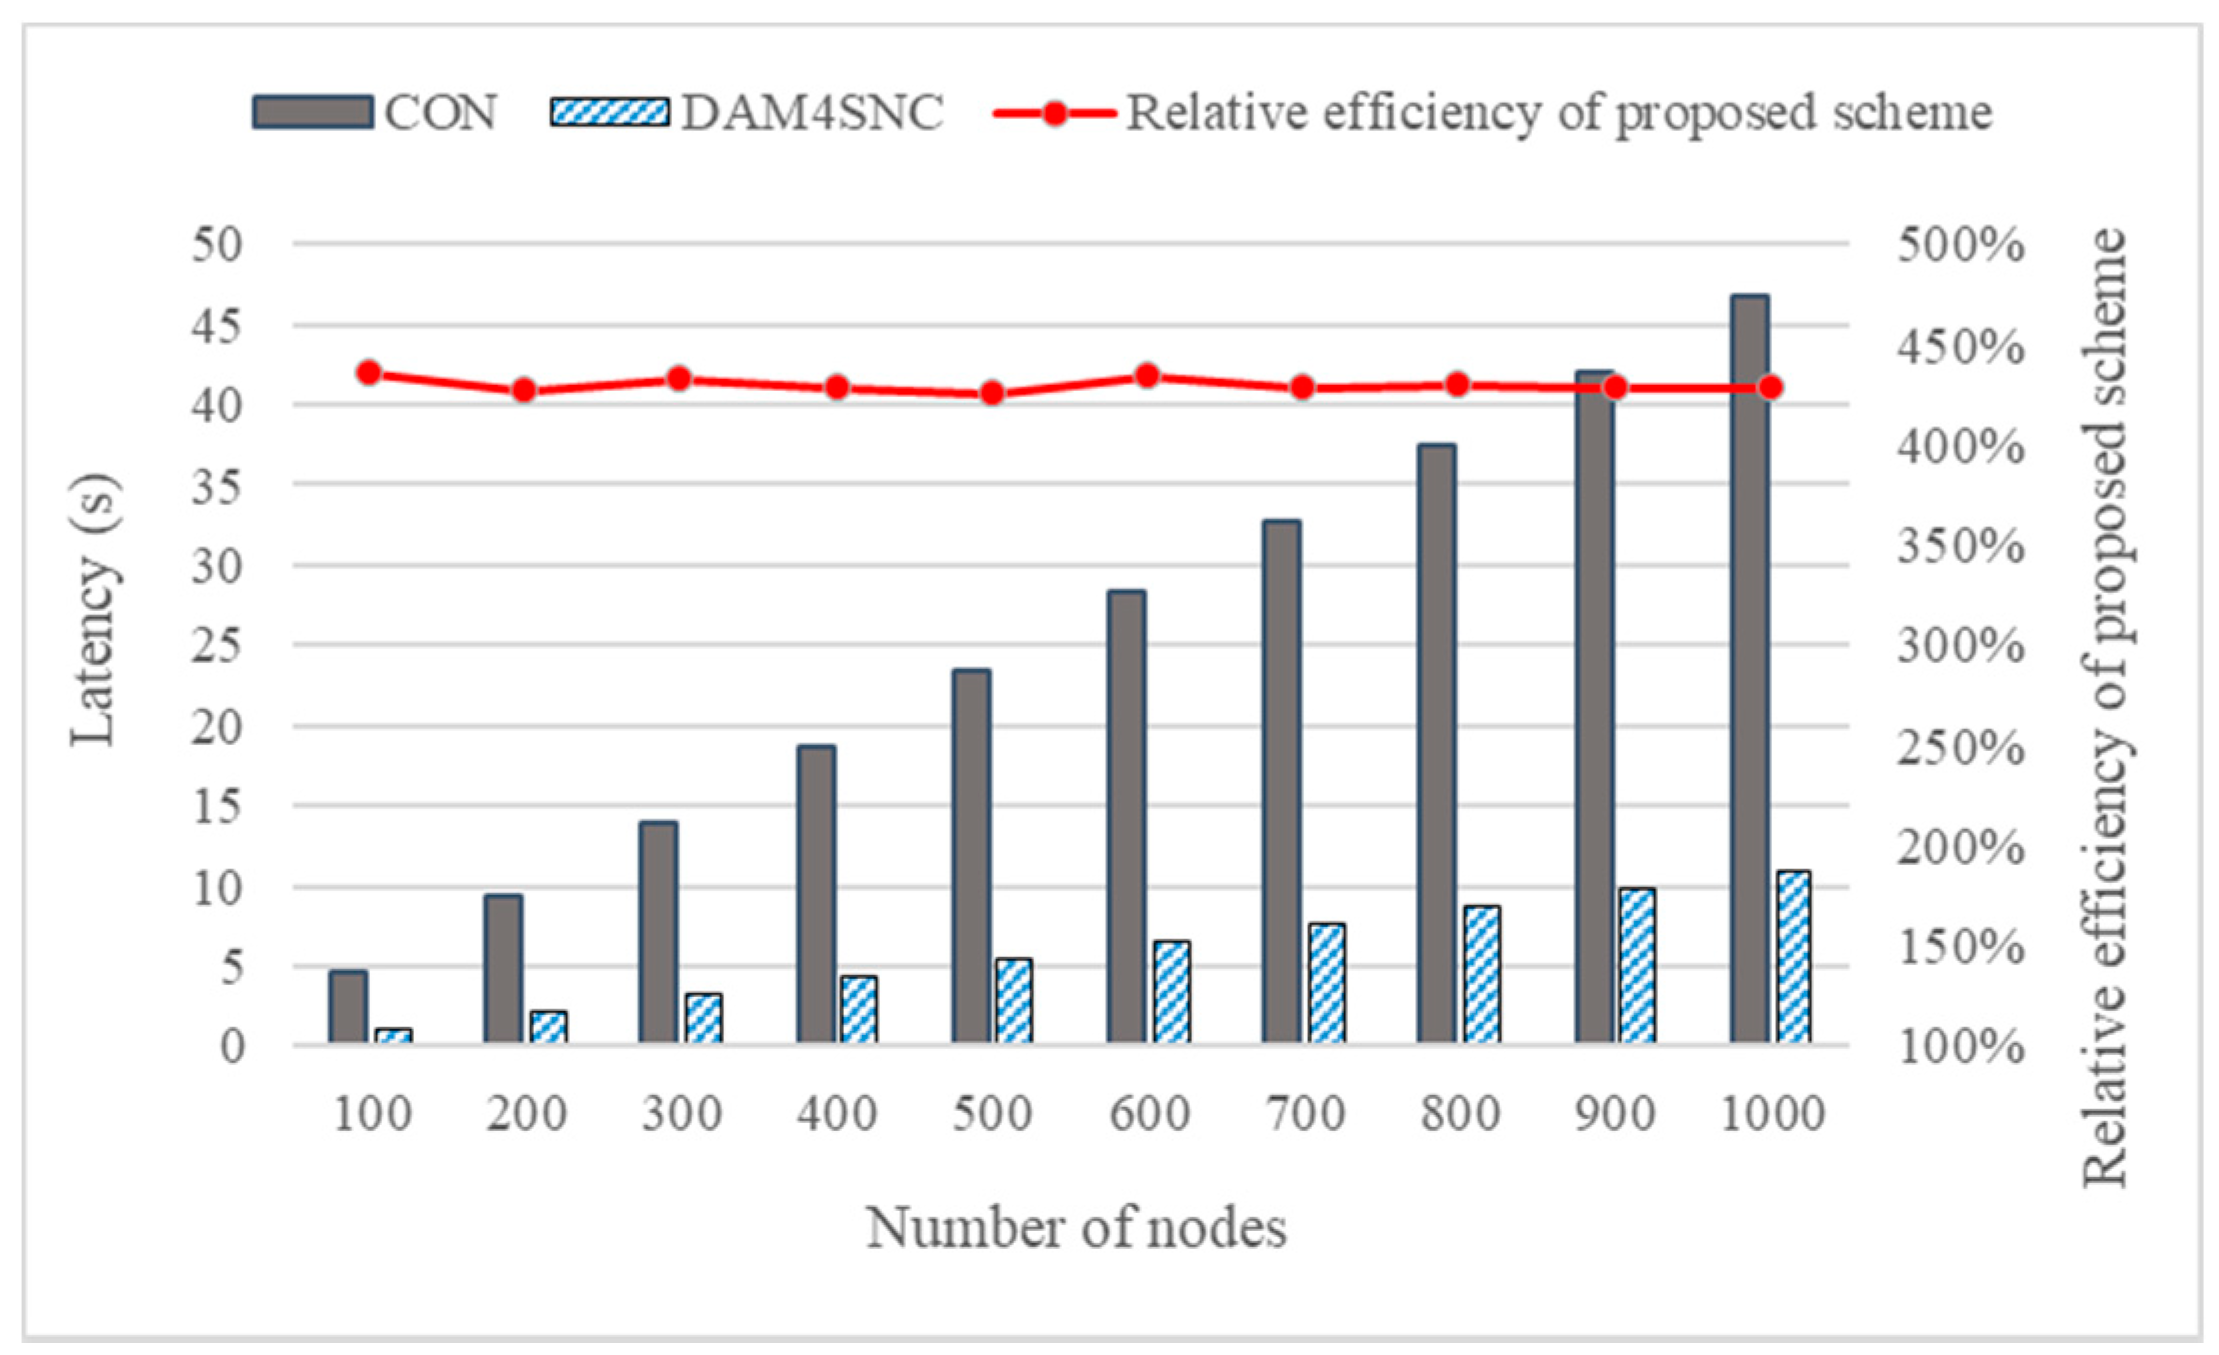
Considering the increasing scale and severity of damage from recent cybersecurity incidents, the need for fundamental solutions to external security threats has increased. Hence, network separation technology has been designed to stop the leakage of information by separating business computing networks from the Internet. However, security accidents have been continuously occurring, owing to the degradation of data transmission latency performance between the networks, decreasing the convenience and usability of the work environment. In a conventional centralized network connection concept, a problem occurs because if either usability or security is strengthened, the other is weakened. In this study, we proposed a distributed authentication mechanism for secure network connectivity (DAM4SNC) technology in a distributed network environment that requires security and latency performance simultaneously to overcome the trade-off limitations of existing technology. By communicating with separated networks based on the authentication between distributed nodes, the inefficiency of conventional centralized network connection solutions is overcome. Moreover, the security is enhanced through periodic authentication of the distributed nodes and differentiation of the certification levels. As a result of the experiment, the relative efficiency of the proposed scheme (REP) was about 420% or more in all cases.
Keywords: network separation; distributed network; decentralized authentication; n-factor authentication; trust level; frame structure network separation; distributed network; decentralized authentication; n-factor authentication; trust level; frame structure