


Abstract
Delays added by the encryption process represent an overhead for smart computing devices in ad-hoc and ubiquitous computing intelligent systems. Digital Logic Circuits are faster than other computing techniques, so these can be used for fast encryption to minimize processing delays. Chaotic Encryption is more attack-resilient than other encryption techniques. One of the most attractive properties of cryptography is known as an avalanche effect, in which two different keys produce distinct cipher text for the same information. Important properties of chaotic systems are sensitivity to initial conditions and nonlinearity, which makes two similar keys that generate different cipher text a source of confusion. In this paper a novel fast and secure Chaotic Map-based encryption technique using 2’s Compliment (CET-2C) has been proposed, which uses a logistic map which implies that a negligible difference in parameters of the map generates different cipher text. Cryptanalysis of the proposed algorithm shows the strength and security of algorithm and keys. Performance of the proposed algorithm has been analyzed in terms of running time, throughput and power consumption. It is to be shown in comparison graphs that the proposed algorithm gave better results compare to different algorithms like AES and some others.
1. Introduction
As a ubiquitous trend in the environment, chaos is a type of deterministic random process provided by nonlinear dynamical systems. The main characteristics of chaotic systems are sensitive to initial conditions, randomness, diffusion, confusion and ergodicity. Chaotic systems have become an important topic of research because of these properties and are widely used in cryptography [1,2]. The existing-related research about chaos-based cryptography includes symmetric encryptions; security protocols and algorithms, asymmetric encryption and hash functions [3,4,5].
In recent years, the one way hash functions based on chaotic logistic maps, including 1D & 2D piecewise linear/nonlinear logistical map, high dimensional chaotic map, chaotic neural networks, hyper chaos and chaos S-Box have been modified [6,7,8]. Chaos map-based different algorithms, techniques and methods are constructed using hash functions, so high dimensionality dynamic systems have become an important and interesting research area in several scientific fields in the areas of computer science and secure communications [9,10,11]. Chaotic functions are sensitive to initial conditions—any negligible difference in the initial value generates a completely different cipher text. This means the cryptosystem using chaos theory will be strong against brute force attacks [12,13,14,15]. These properties of chaos have high potential for several applications in cryptosystems provided long term predictions on chaotic systems [16,17].
A novel chaos-based cryptographic technique using digital logic circuits is proposed in this paper for fast and secure encryption and decryption of information for several real time applications [18,19]. A chaotic logistic map provides a high degree of randomness and ergodicity to resist the linear and differential attacks and also enhances the security by providing confusion and diffusion to the system [20,21,22,23,24].
These previous techniques have solved many problems of cryptography and enhanced security and performance, but these techniques have some major drawbacks. The existing algorithms and methods are not easily understandable for users because they employ many mathematical functions. Symmetric key cryptosystems use the same single key every time for encryption and decryption. If the key is known by an intruder then the message is easily deduced. In a symmetric key cryptosystem, if an intruder knows the chaos function and the initial value of the chaos function, then the intruder can easily deduce the message. The encryption speed of chaotic cryptography is much slower than traditional cryptography, so a symmetric key cryptography technique is proposed, which uses more than one key for encryption and decryption. These keys are the same for encryption and decryption at one time but different keys are used for distinct messages. Security has been enhanced by using multiple keys and the randomness of keys is also enhanced by using digital concepts like 2’s complement. Even if an intruder knows the keys used one time, then the keys are changed the next time for the same message. The speed of encryption has been also increased by using digital concepts like XORing gate rather than difficult mathematical functions.
The rest of the paper is organized into several sections. Related works and a literature survey are briefly described in Section 2. In Section 3 the proposed cryptosystem and algorithms are described. In Section 4, an example of the proposed crypto systemis explained. Then the security of keys is analyzed in Section 5 with the help of key parameters. In Section 6, the proposed technique is analyzed against all four cryptanalysis attacks. Its performance is evaluated in terms of encryption time, throughput and power consumption in Section 7. In Section 8, the performance of the algorithm is compared with some algorithms like AES and others, which are described in different papers. In Section 9, the paper is concluded.
2. Related Work
Industrial and communication systems largely use unpredictable and practical cryp to systems for highly secure and fast transmission of information with little memory capacity [10,18], so they can satisfy the requirements of industrial control and military used in WiFi and ZigBee networks [6,14]. These proposed methods are analyzed in the UACI, NPCR and NIST environment.
An electrocardiogram (ECG) encryption system for biometric recognition collects ECG signals from an encrypted person using a portable instrument [18]. Simulation results show that the secrecy and security are enhanced by using an efficient large key size and complex algorithms widely used in multimedia applications [25].
Some mathematical properties have also determined the security and performance of distinct algorithms and systems using dynamic, chaotic cryptography [11,26]. Periodic switching of cryptographic keys is a different concept to boost the security of cryptographic systems in which chaotic behavior is combined with the periodic switching of keys [8]. It is represented that the running time complexity of the chosen plaintext, and a cipher text attack can be reduced to yield a simple set of linear equations [27,28]. The performance of the algorithm is measured in terms of cost, time and speed. Several one-dimension chaotic maps have been used to generate independent and approximately uniform pseudo-dynamic sequences for faster and time efficient encryption on blocks of data. Simulation results analyzed the efficiency and resistance against difference and linear cryptanalysis attacks and showed the high performance of the algorithm [5,29]. Fast encryption provides reliability and high security slightly, but at the same time highly reduces the running time [21,30,31]. Table 1 summarizes all the author’s works on chaotic based encryption scheme on the basis of some characteristics.
Table 1.
Comparison table (Authors’ names and performance comparison of their research papers).
3. Proposed Methodology/Scheme
A novel, fast and secure “Chaotic Map based Encryption Technique using 2’s Compliment (CET-2C)” has been proposed using one or more than one keys for the encryption and decryption process but at any time instant the encryption and decryption keys are similar. It means different messages are encrypted via different multiple keys to increase the security against known cryptanalysis attacks. Firstly, the number of keys has been generated with the help of chaos logistic function (logistic map) providing only the initial condition.
These keys have been prohibited from providing some proper condition, so all the characters of the information are encrypted and decrypted with these difference and multiple keys. Multiple keys have been used to increase the randomness as well as security, and it is not necessary that any repeated characters in the information be encrypted and decrypted with a similar key.
The complexity of keys has been increased by using some digital logic like 2’s compliment code so the randomness of keys is enhanced with better security. These complex random keys have provided fast, feasible and efficient encryption in secure communication so the intruder is not sure about the generation of keys.
The necessary notations which are used for the key generation, encryption and decryption scheme are the following: = Plain text; Ci = Cipher text; = Encryption of the plain text ; = Decryption of the cipher text .
For n = 1 to j:
A = any integer (1, 2, 3, ...); = initial value of chaotic function which is 2, 3, 4,……, j = Number of keys; = keys (after applying gray code on ).
3.1. Scheme for Key Generation
(1) Initially the pseudo random numbers are generated by using the chaotic map function at both ends (sender and receiver).
For n = 1 to j:
(2) The multiple different keys are generated by applying 2’s compliment on different values of and the number of keys is fixed by providing some suitable condition j.
(3) Complexity and security of keys are enhanced by applying 2’s compliment code on Xn+1 so keys are random and independent with each other.
(4) These keys are converted into 8-bit binary form.
3.2. Scheme for Encryption Process
Each character is represented in ASCII character format which are converted into 8-bit binary numbers with respect to their decimal numbers. These characters are encrypted by using a digital logic bitwise XNOR gate function. This XNOR operation is performed on each character by a single binary coded key. Keys are also repeated for encrypting and decrypting the whole information.
= ASCII (Character 1); is represented in 8-bit binary numbers:
= ASCII (Character 2); is represented in 8-bit binary numbers:
…,
= ASCII (Character i); is represented in 8-bit binary numbers:
where m = 1 to j.
3.3. Scheme for Decryption Process
The cipher texts have been decrypted (converted into plain text) by using the reverse process of the encryption technique:
is represented into ASCII () with respect to its decimal value. Character 1 = ASCII ():
is represented into ASCII () with respect to its decimal value. Character 2 = ASCII ():
…,
where m = 1 to j; is represented in ASCII () with respect to its decimal value; Character i = ASCII ()
3.4. Key Generation Algorithm
(1) Select the values of parameter (M, A, ).
(2) Generate the pseudo random numbers from the logistic map equation.
For n = 1 to j:
(3) Apply 2’s compliment code on these pseudo random numbers which are generated from to generate the keys .
(4) Keys are converted into 8-bit binary form.
3.5. Encryption Algorithm
(1) Each character is converted into an ASCII character, = ASCII (Character i).
ASCII character is represented into 8-bit binary form.
for all i > 0, and m = 1 to j, using this equation for encrypting the message. Where is bit wise XNOR perform on plaintext with a single key .
3.6. Decryption Algorithm
(1) for all i > 0 and m = 1 to j, using this equation for decrypting the cipher text. where is bit wise XNOR perform on cipher text with a single key .
(2) Plain text is represented into ASCII () with respect to its decimal value.
(3) So Character i = ASCII ().
4. Example
Given plain text–PIYUSHS
| Letter | ASCII | Binary Number |
| P | 80 | 01010000 |
| I | 73 | 01001001 |
| Y | 89 | 01011001 |
| U | 85 | 01010101 |
| S | 83 | 01010011 |
| H | 72 | 01001000 |
| S | 83 | 01010011 |
4.1. Key Generation
Let A = 6, = 4, Number of Keys j = 5
For j = 1
- = {6 × 4 × (4 − 1)} MOD 256
- = 72
For j = 2
- = {6 × 72 × (72 − 1)} MOD 256
- = 208
For j = 3
- = {6 × 208 × (208 − 1)} MOD 256
- = 32
For j = 4
- = {6 × 32 × (32 − 1)} MOD 256
- = 64
For j = 5
- = {6 × 64 × (64 − 1)} MOD 256
- = 128
- = 72, 208, 32, 64, 128.
The keys are established by applying 2’s compliment code on pseudo random numbers . 1’s compliment is generated by converting 0 to 1 and 1 to 0 then 2’s compliment is generated by adding 1 in 1’s compliment of numbers:
= 72 = 01001000
1’s compliment 10110111
+ 1
2’s compliment 10111000 = 184
| 72 = 01001000 | 2’s compliment | = | 10111000 | = | 184 |
| 208 = 11010000 | 2’s compliment | = | 00110000 | = | 48 |
| 32 = 00100000 | 2’s compliment | = | 11100000 | = | 224 |
| 64 = 01000000 | 2’s compliment | = | 11000000 | = | 192 |
| 128 = 10000000 | 2’s compliment | = | 10000000 | = | 128 |
Keys (K1 = 184, K2 = 48, K3 = 224, K4 = 192, K5 = 128).
4.2. Encryption Algorithm
Encryption scheme converts the plain text into unreadable cipher text by using different multiple keys (Table 2).
Table 2.
Cipher text for plain text.
Given Text: -PIYUSHS
P
ASCII–80
01010000
Key () = 184 (10111000)
| Cipher Text– | ||
| Plaintext | XNOR | Key |
| P | XNOR | 184 |
| 80 | XNOR | 184 |
| 01010000 | XNOR | 10111000 |
| 0 | XNOR | 1 | = | 0 |
| 1 | XNOR | 0 | = | 0 |
| 0 | XNOR | 1 | = | 0 |
| 1 | XNOR | 1 | = | 1 |
| 0 | XNOR | 1 | = | 0 |
| 0 | XNOR | 0 | = | 1 |
| 0 | XNOR | 0 | = | 1 |
| 0 | XNOR | 0 | = | 1 |
| Cipher Text–00010111 = 23 = ↨ | ||||
4.3. Decryption Algorithm
Decryption scheme converts the unreadable cipher text into readable plain text by using the similar keys (Table 3).
Table 3.
Plain text for cipher text.
Cipher text–↨ÅFj,☼£
↨
ASCII–23
00010111
Key () = 184 (10111000)
| Plain Text: | ||
| Cipher Text | XNOR | Key |
| ↨ | XNOR | 184 |
| 23 | XNOR | 184 |
| 00010111 | XNOR | 10111000 |
| 0 | XNOR | 1 | = | 0 |
| 0 | XNOR | 0 | = | 1 |
| 0 | XNOR | 1 | = | 0 |
| 1 | XNOR | 1 | = | 1 |
| 0 | XNOR | 1 | = | 0 |
| 1 | XNOR | 0 | = | 0 |
| 1 | XNOR | 0 | = | 0 |
| 1 | XNOR | 0 | = | 0 |
| Plain Text–01010000 = 80 = P | ||||
5. Analysis of Key Security
To find and compute all the values (J, A, ) is difficult. In this section the sensitivity of the secret key has been represented with negligible difference in the key parameters:
Plain text–PIYUSHS; Parameter (J, A, ); Keys ().
5.1. Sensitivity of Number of Keys J
It has been described that if a number of keys are changed, then the cipher texts are also fully changed from one another for the same plain text. In Table 4 negligible dissimilarity in the j (number of keys) generates different cipher text.
Table 4.
Sensitivity of Number of Keys j.
5.2. Sensitivity of Constant A
It has been described that negligible changes in constant A produce fully different keys so cipher texts are also different from each other. In Table 5 it has been shown that little difference in the values of constant A produced different cipher text.
Table 5.
Sensitivity of Constant A.
5.3. Sensitivity of Initial Condition Xn
It has been described that little changes in the initial condition Xn produces fully different keys, so cipher texts are completely different. This is known as confusion. In Table 6 it has been shown that little difference in values of initial variable produced fully different cipher text.
Table 6.
Sensitivity of initial condition .
6. Cryptanalysis
Cryptanalysis is a method which is used to verify the security of an algorithm by breaking the codes of the algorithm and getting the possible encryption keys and plain text as well.
6.1. Cipher Text Only Attacks
Parameter (j = 5, A = 6, = 4)
Keys (184,48,224,192,128)
Given: where m = 1 to j.
Deduce: -Either ;
Or an algorithm to deduce
From
Keys (184,48,224,192,128)
Example:
| = Q then | (Q) = ▬ | |
| = QQ then | (QQ) = ▬₧ | |
| = QQQ then | (QQQ) = ▬₧N | |
| = QQQQ then | (QQQQ) = ▬₧Nn | |
| = QQQQQ then | (QQQQQ) = ▬₧Nn. | |
| = QQQQQQ then | (QQQQQQ) = ▬₧Nn.▬ |
From the above example, it is to be said that if any character is repeated many times in the text, the cipher text is completely different for same letter Q. The Cipher text of Character Q finding as the first letter is dissimilar from Q finding as nth character in plaintext.
6.2. Known Plain Text Attack
Parameter (j = 5, A = 6, = 4)
Keys (184,48,224,192,128)
Given: where m = 1 to j
Deduce: -Either
Or an algorithm to deduce
From
Keys (184,48,224,192,128)
Example:
| = R then | (R) = § | |
| = RR then | (RR)= §¥ | |
| = RRR then | (RRR) = §¥M | |
| = RRRR then | (RRRR) = §¥Mm | |
| = RRRRR then | (RRRRR) = §¥Mm- | |
| = RRRRRR then | (RRRRRR) = §¥Mm-§ |
From the example, it can be said that there are several plain texts with their corresponding cipher text. It is hard to compute the key or the algorithm which is used for encryption of plain texts for decrypting them. Keys are generated by very restricted and sensitive parameters. The cipher text of the Character R found as the first letter is different as that of the letter R found as the nth character in the plaintext.
6.3. Chosen Plaintext Attacks
Parameter (j = 5, A = 6, = 4)
Keys (184,48,224,192,128)
Given: Where the cryptanalysis gets to decide and m = 1 to j.
Deduce: -Either ;
Or an algorithm to deduce
From
Keys (184,48,224,192,128)
Example:
- = DE then cipher text (DE) = ♥è
- = ED then cipher text (ED) = ☻ï
It is not easy to find out the key or the algorithm to decrypt the cipher text which is to be encrypted with the same keys.
6.4. Chosen Cipher Text Attack
Parameter (j = 5, A = 6, = 4)
Keys (184,48,224,192,128)
Given: where m = 1 to j
Deduce: -
Example:
- = ♥è then plaintext (♥è) = DE
- = ☻ï then plain text (☻ï) = ED
Keys are produced by two different parameters and A which are very sensitive and independent, so it is not easy to deduce the keys by knowing the cipher text and its decrypted plaintext.
7. Performance Analysis
In this paper, pertinent metrics are recognized. Performance of the proposed chaotic algorithm(CET-2C) is measured, and finally compared with the existing one secret key, AES, encryption algorithm and also compared with different algorithms using same data size published in Springer [12], Hindawi [17] and EEA [3] publications. It is to be shown that CET-2C is not affected by the data set, and only depends upon the data size.
Metrics and Performance
In this paper, five significant metrics is described to estimate the performance of the proposed algorithm (CET-2C). The metrics include: encryption/decryption time, CPU time, cipher size, power consumption, and encryption throughput. Then the experiment is performed, and performance results are measured using a laptop having a Intel (R) Core (TM) i3-3110M processor CPU @ 2.40GHz, and a RAM of 2GB. The results are also calculated using a laptop having an Intel Pentium Dual-Core CPU @ 2.60 GHz processor and 2 GB RAM and a laptop having an Intel (R) Pentium (R) Dual CPU T2370 @ 1.73 GHz processor and 1 GB RAM for comparison with other algorithms.
Encryption Time
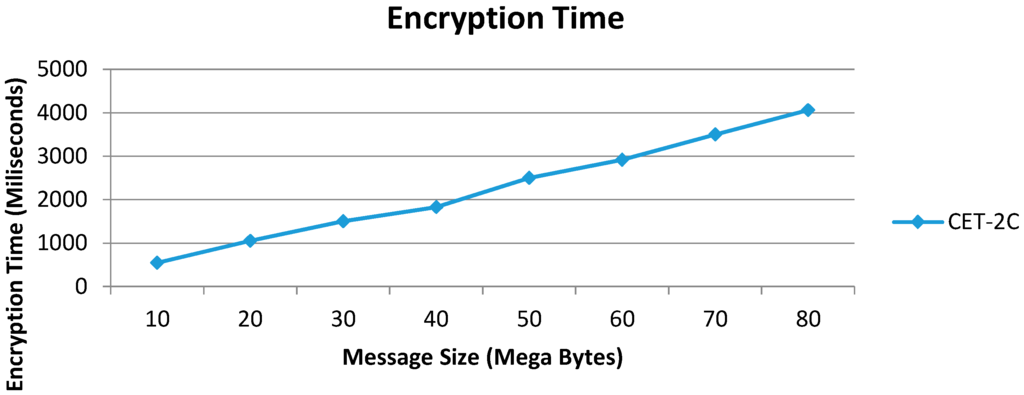
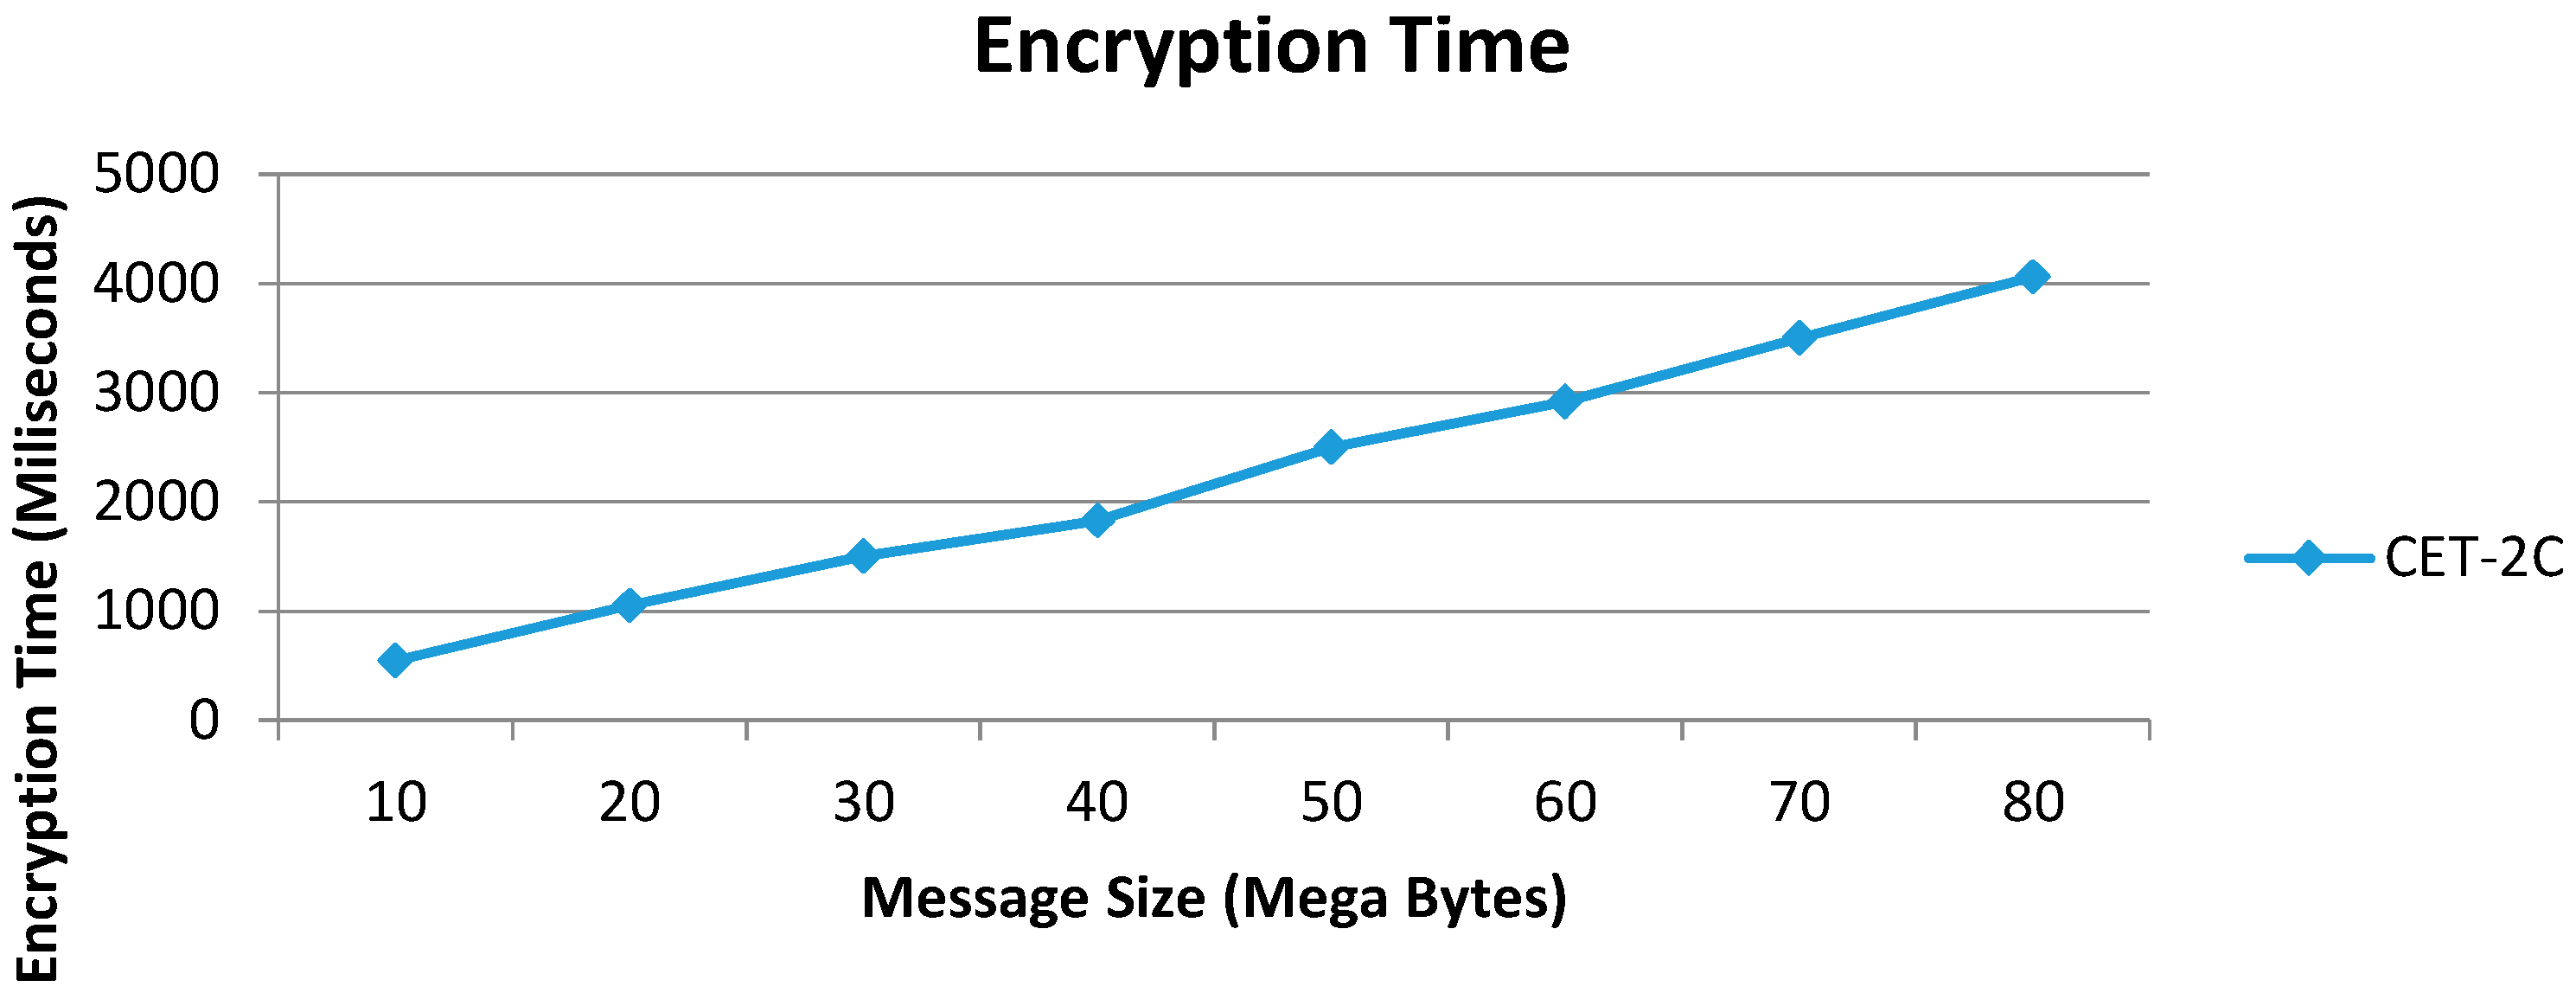
The encryption time is based on the running time complexity of the algorithm, length of the key, and the plaintext size to be encrypted with various encryption algorithms. Hence, in this paper, a number of encryption times for different plaintext sizes and key length are selected and analyzed by using CPU clock time [3]. A variety of data sizes ranging from 0 MB to 80 MB are encrypted and their corresponding encryption times are collected. It is shown by a graph that the encryption time increases with increasing the data size. The encryption time and data size are linearly increased in Figure 1.
Figure 1.
Message size versus encryption time.
Encryption Throughput, Xe
It is defined as the number of bytes of plaintext encrypted (cipher text completed) during an observation period (encryption time) [3]. Mathematically:
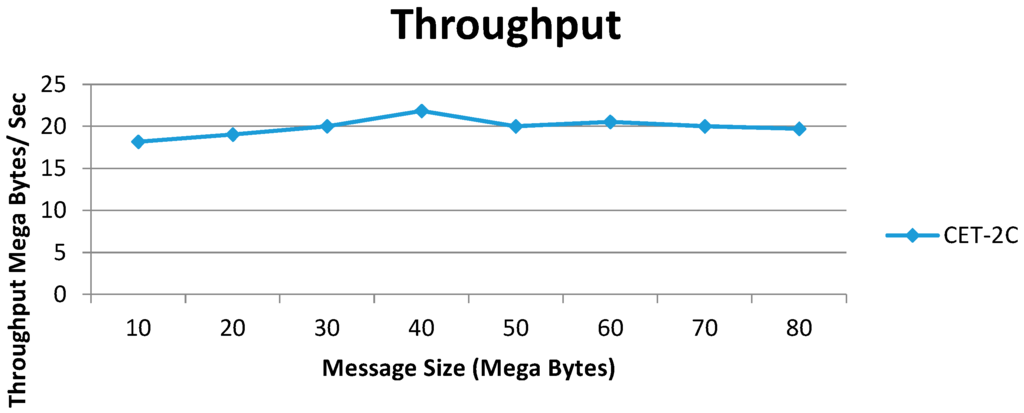
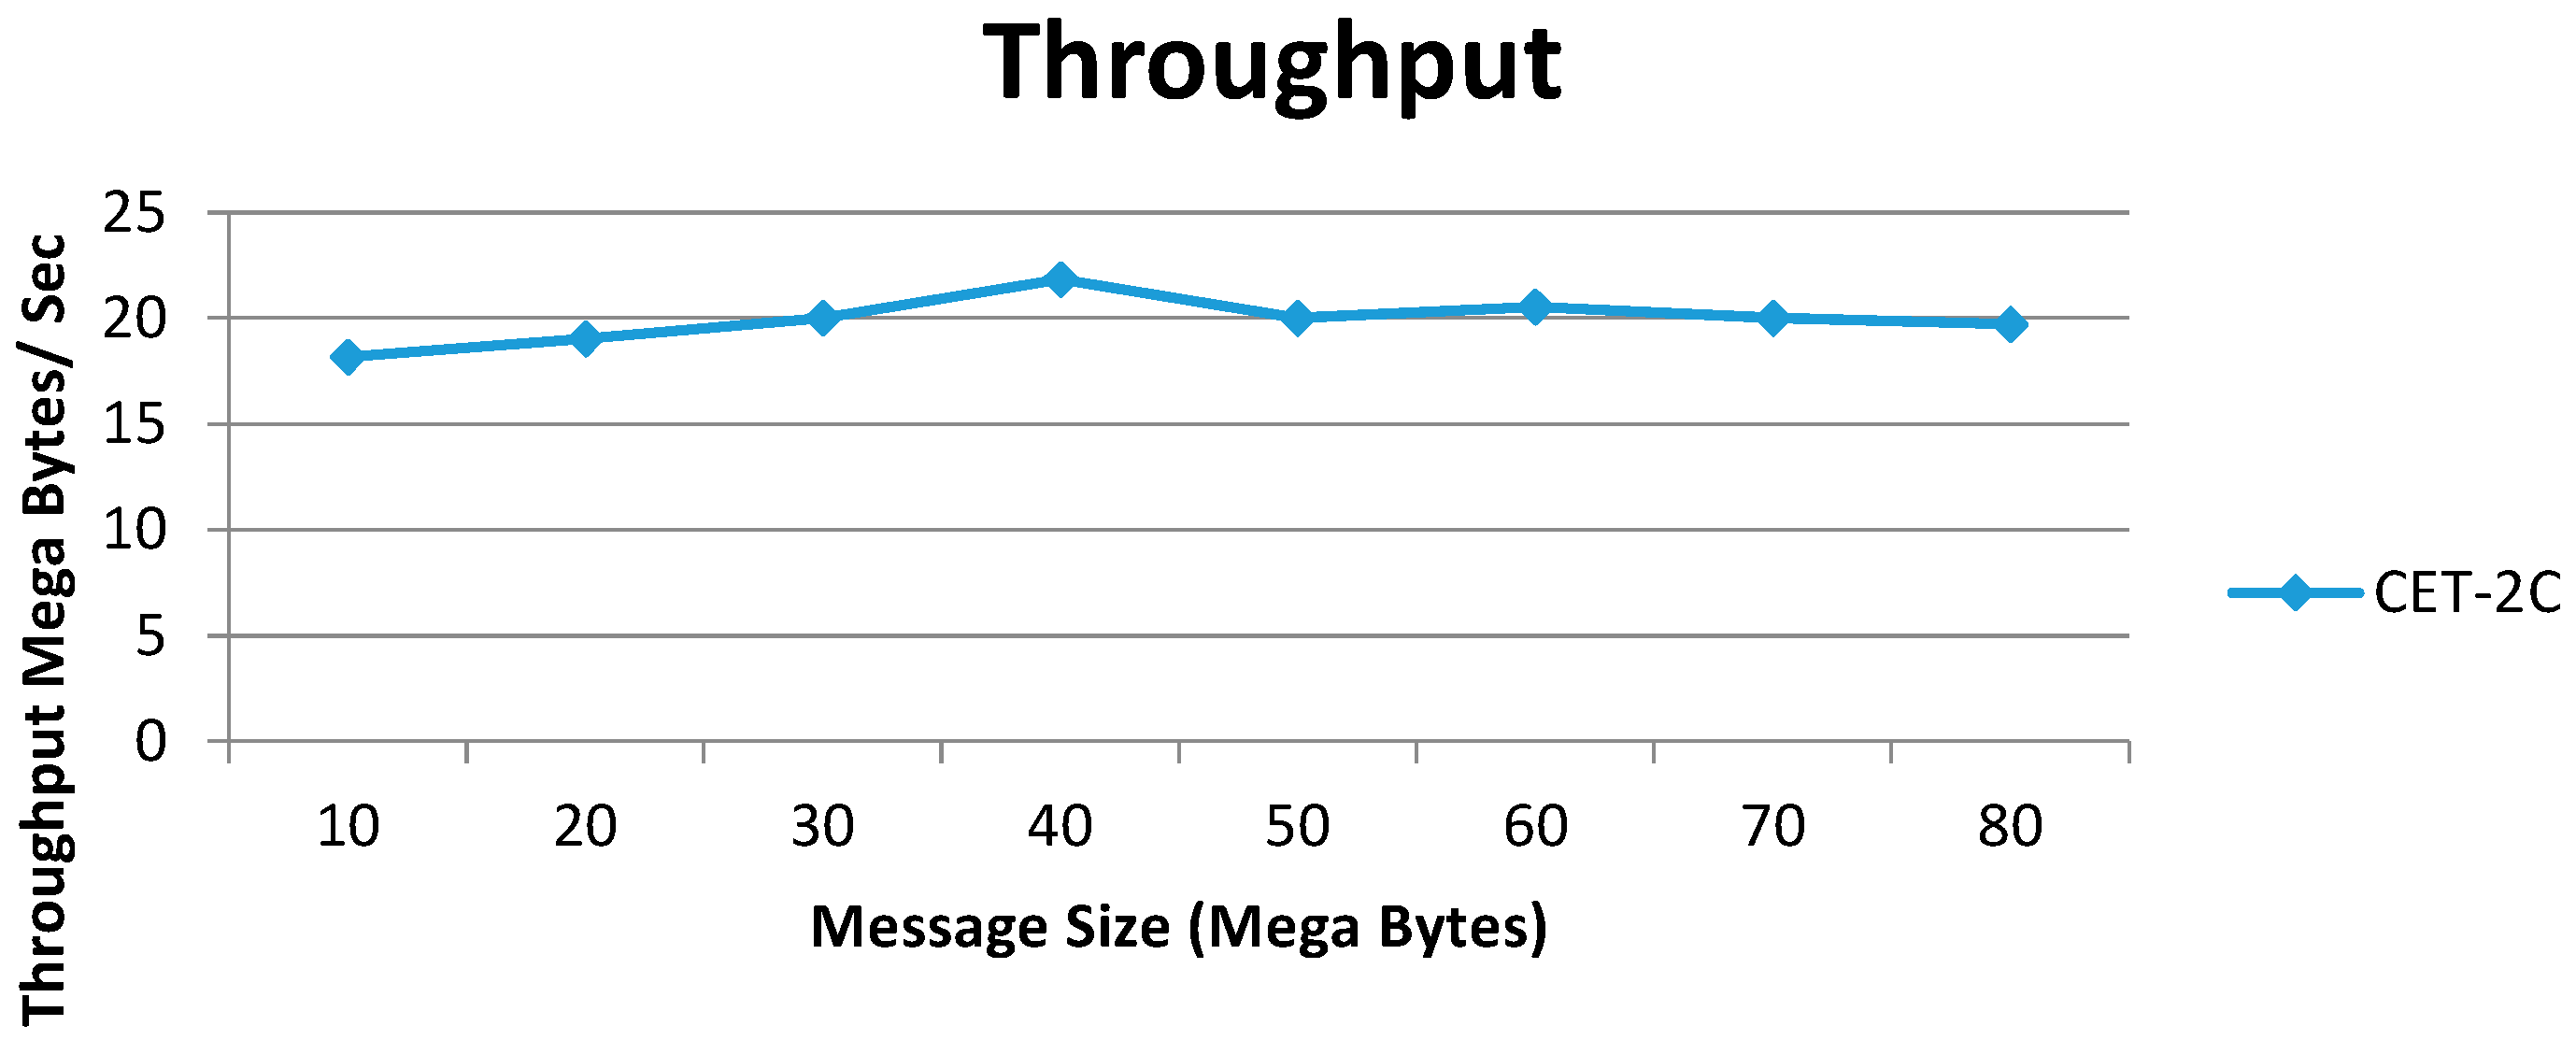
In the proposed algorithm, Throughput linearity is enhanced as the data size is increased in Figure 2.
Figure 2.
Message size versus throughput.
Power Consumption
Power is needed for running fast CPUs and memory based on the usability of devices and algorithms. The energy cost of the encryption process is defined as the product of the total number of clock cycles required by the encryption process and average current drawn by each CPU clock cycle in the ampere cycle. The total energy cost is calculated in ampere seconds by dividing the ampere cycles by the clock frequency in cycles/second of a processor [3]. Then results are multiplied with the processor’s operating voltage to obtain the energy cost in joule. The CET-2C consumed the amount of energy for encryption or decryption is given by:
where = Processor’s operating voltage; T = Encryption time; I = Average current per CPU cycle.
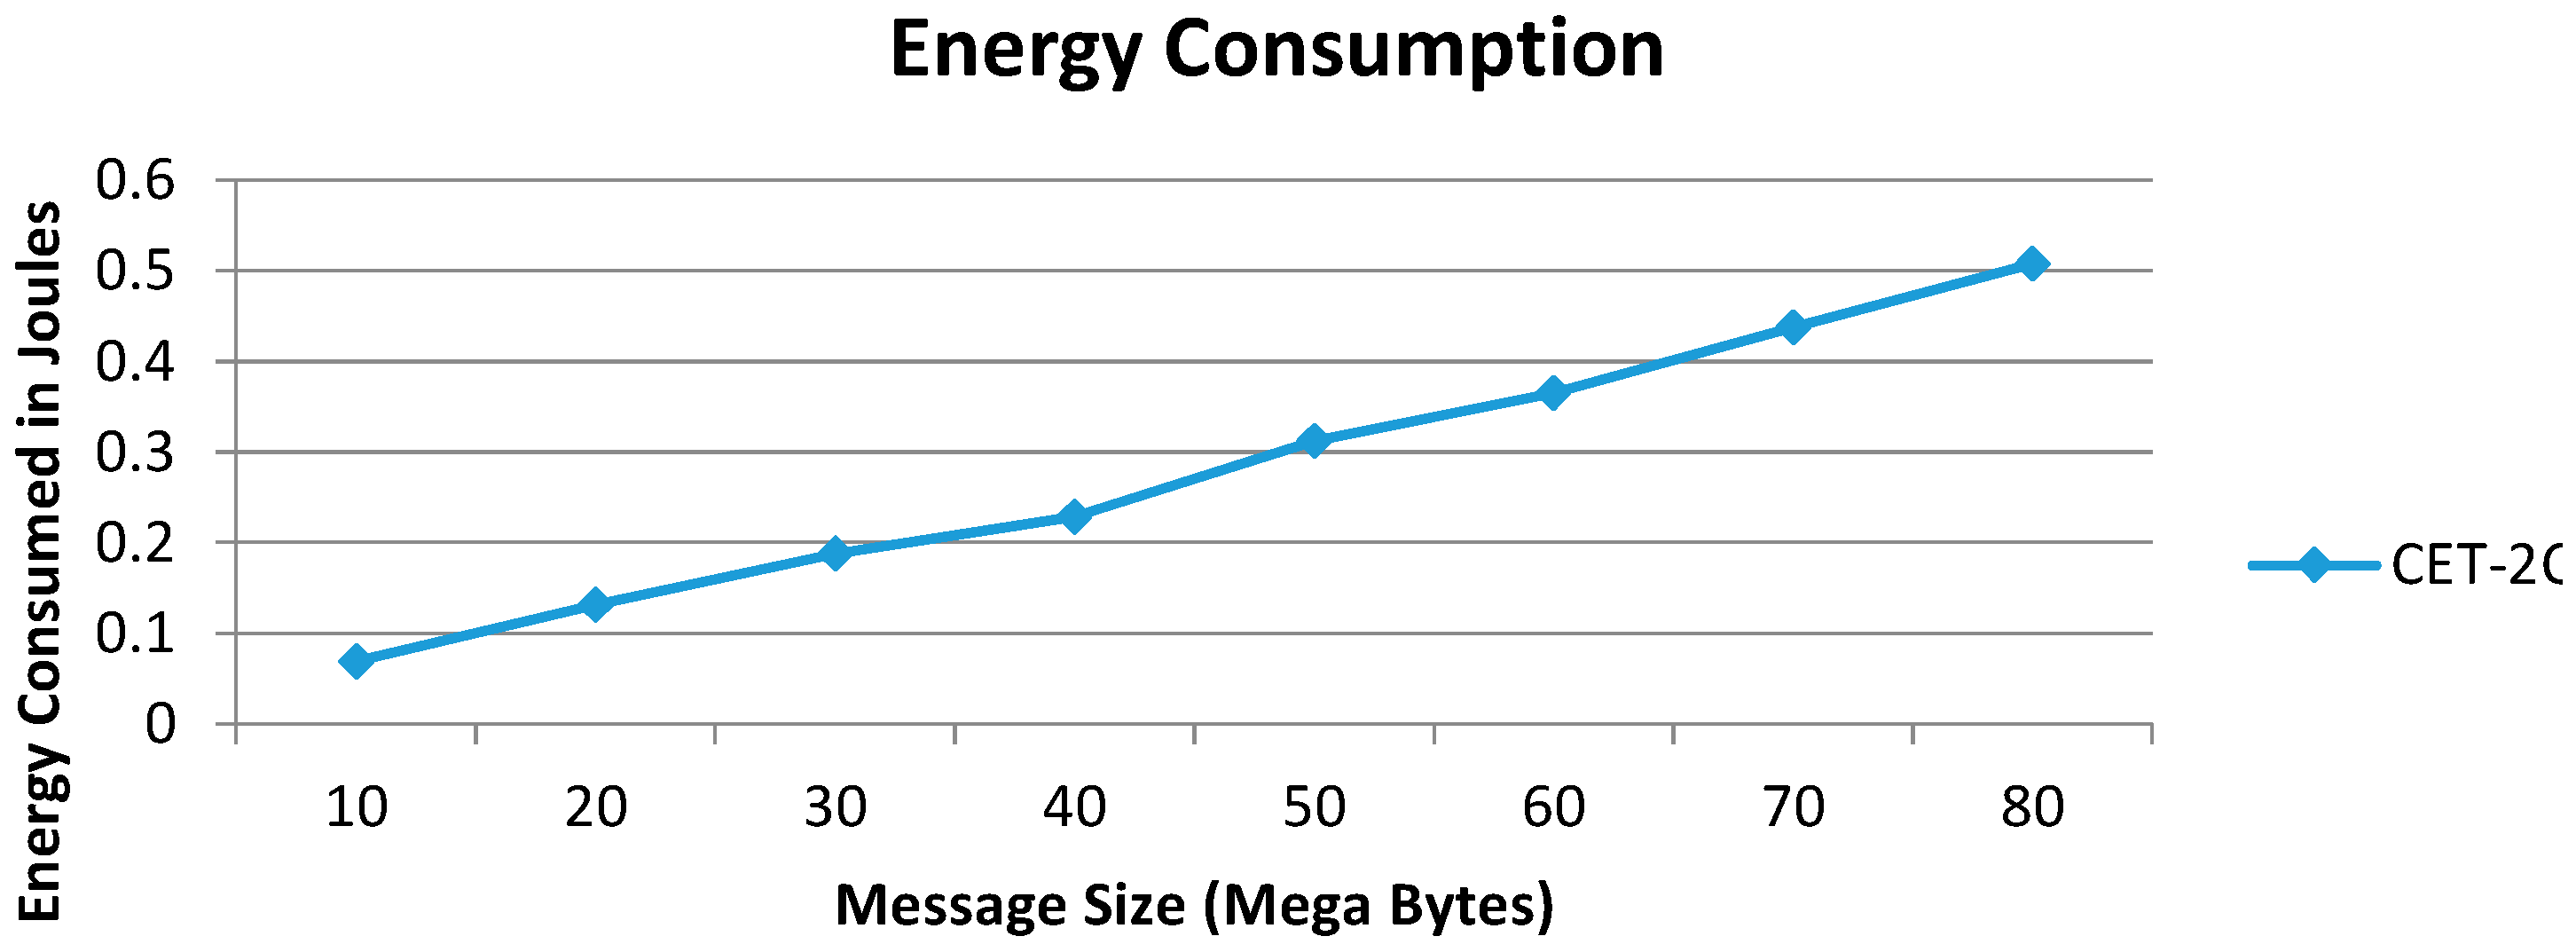
In this paper, the experiments were performed and results were collected using a laptop equipped with an Intel (R) Core (TM) i3-3110M processor CPU. The approximate average current consumed is 100 mA and the CPU voltage is = 1.25 V (both obtained from the Intel Manual).
The variations of energy consumption with different data sizes are shown in the graph which is represented that the energy consumed during an encrypting process is directly proportional to the encryption time in Figure 3.
Figure 3.
Message size versus energy consumption.
CPU Time
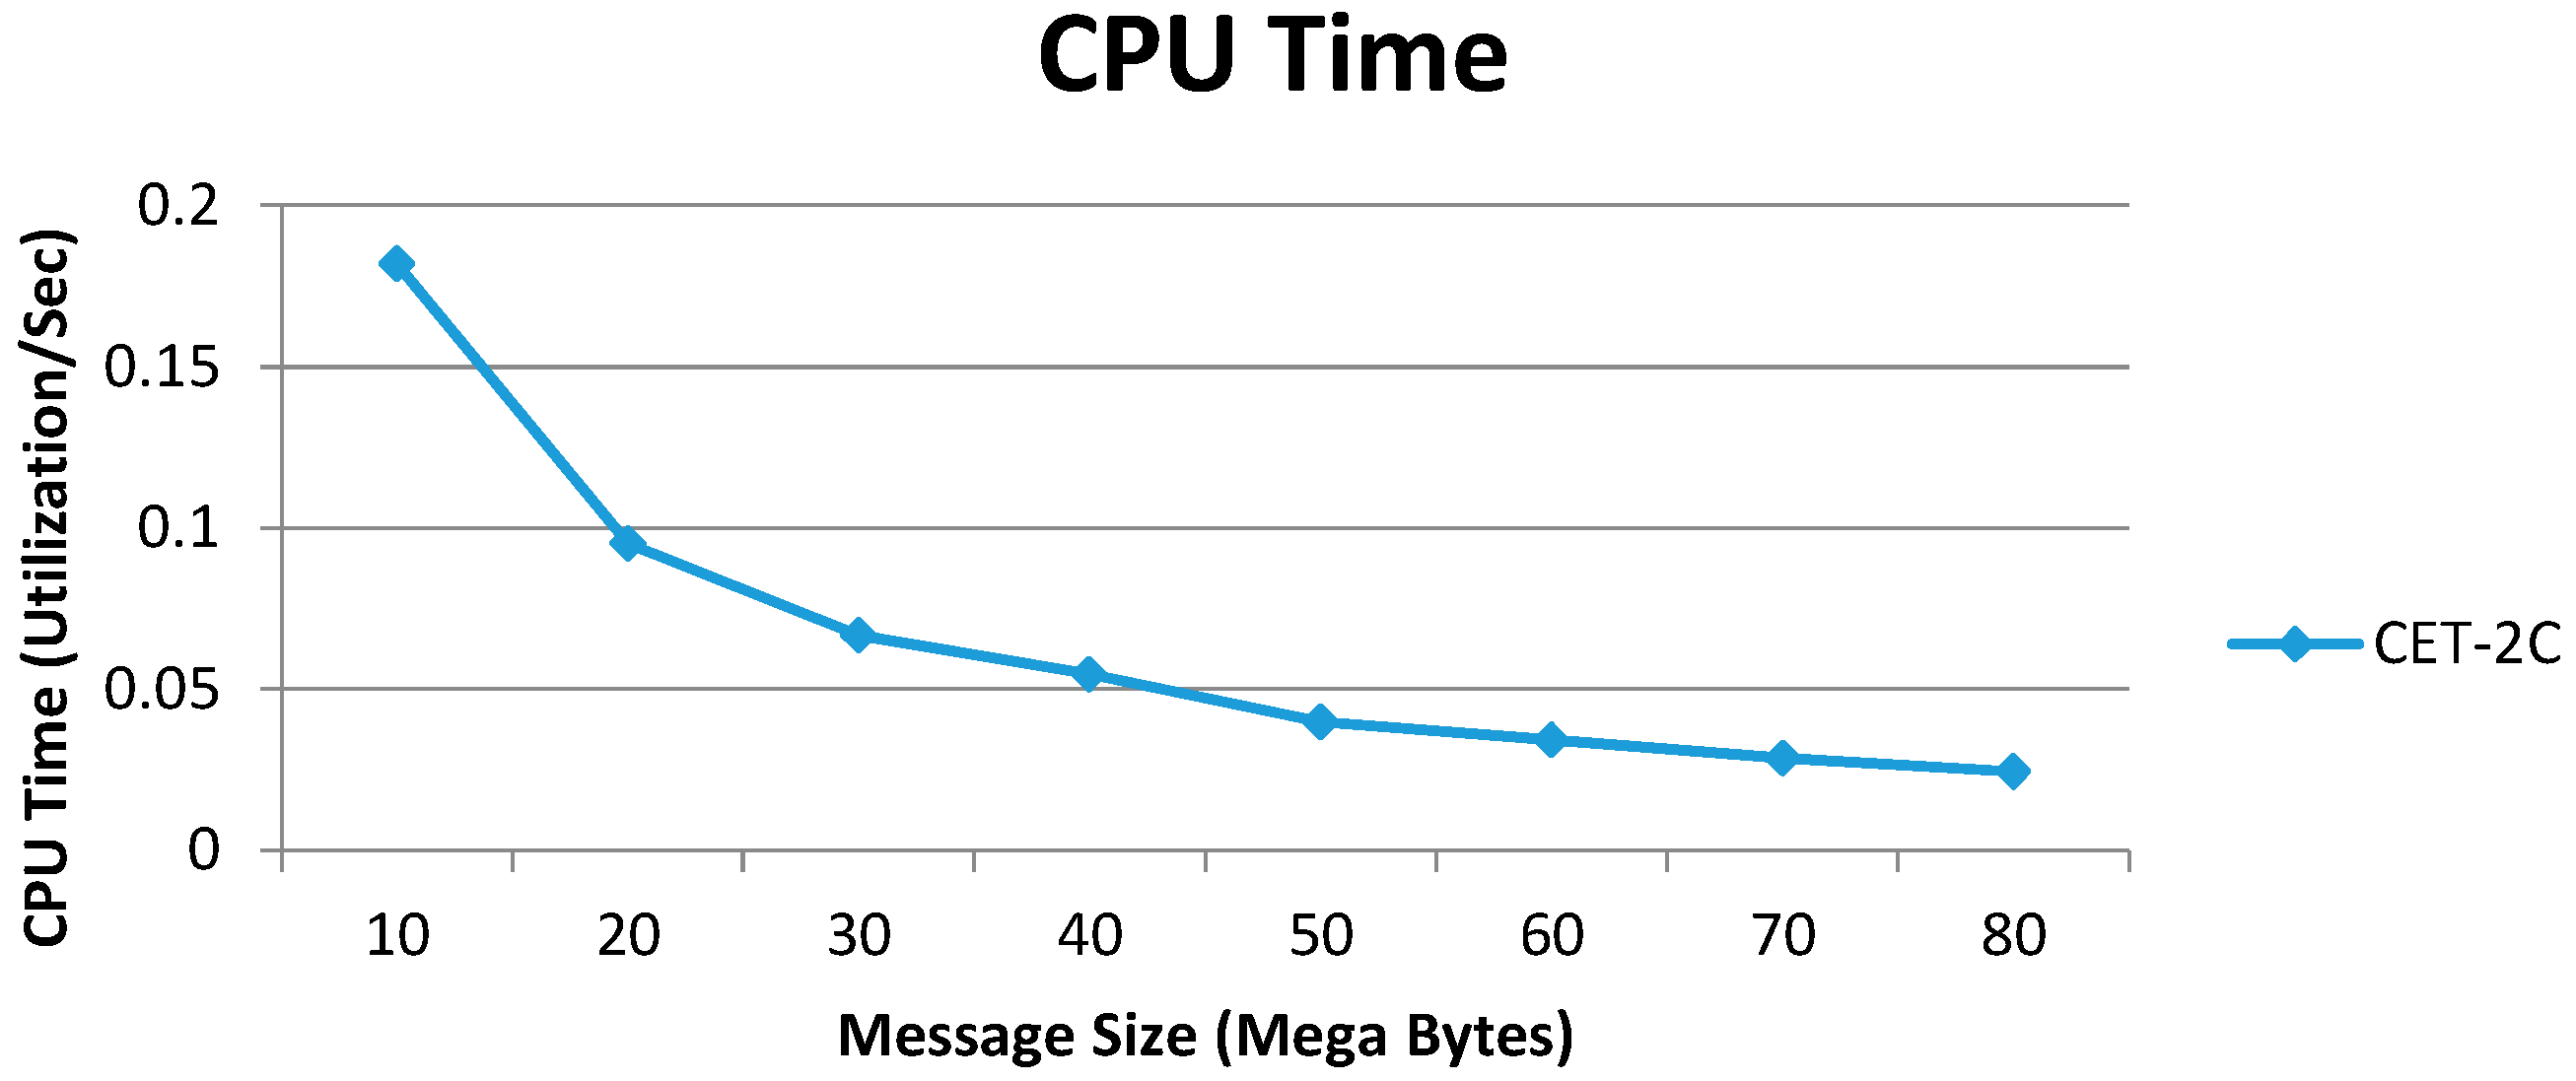
The CPU process time is defined as the time when the CPU is busy in the calculation of a particular process. When the load of CPU is increased then CPU time is also enhanced linearly [3]. In this paper, the CPU time is given by:
where CPU utilization = Obtained from the task manager; Observation period = Encryption Time in Figure 4.
Figure 4.
Message size versus CPU time.
Cipher Size
Shannon’s Characteristics of “Good” Ciphers states that the size of the encrypted text should be no larger than the plaintext of the original message. In this work, the size of plaintext and cipher text are shown to be the same, thus satisfying Shannon’s size Characteristics of “Good” Ciphers rule.
8. Comparison with AES and Chaotic Algorithms [3]
The performance of the proposed algorithm (CET-2C) is compared with a popular secret key encryption algorithm, AES, and with Chaotic Algorithms [3,12] using the data size same as provided in [3,12,17]. The plaintexts used in the proposed algorithm, are encrypted using AES, and a Chaotic Algorithm [3,12] and their performance is evaluated and analyzed using the same metrics as above.
8.1. Encryption Time
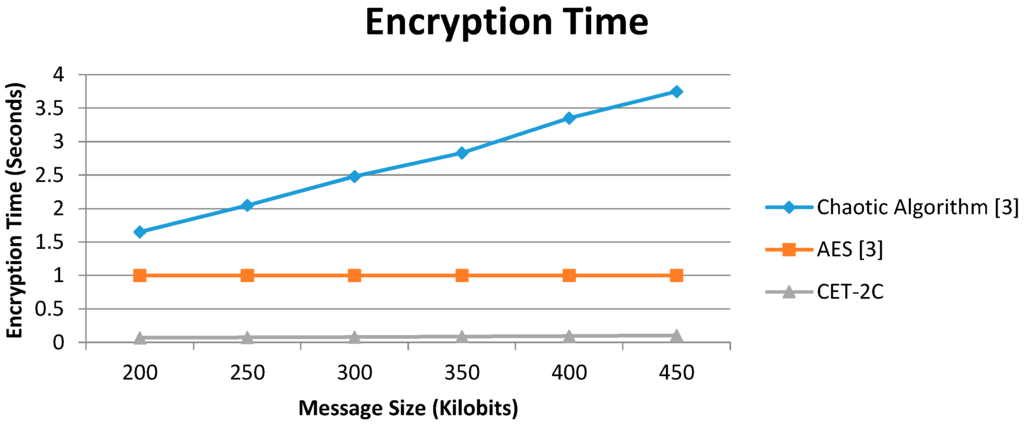
Encryption times for the same set of several data sizes (200 KB to 450 KB) are collected using a laptop equipped with an Intel (R) Pentium (R) Dual CPU T2370 @ 1.73 GHz processor, and 1 GB RAM and used to analyze the performance of the CET-2C, and the results put into graphic form and tabular form (Table 7).
Table 7.
Encryption times of Chaotic Algorithm [3], AES [3] and CET-2C.
Figure 5 shows the proposed algorithm CET-2C is much faster compared to AES [3] and the Chaotic Algorithm for multiple message sizes from 200 KB to 450 KB [3]. CET-2C is also applied for large data sizes with lower encryption time. The results illustrate that the encryption time increases linearly when it is compared with other algorithms.
Figure 5.
Encryption times of Chaotic Algorithm [3], AES [3] and CET-2C.
Overall % Gain of CET-2C over Chaotic Algorithm [3] for Encryption Time with increasing the message size:
Here = Overall % Gain at Different Message Sizes; ET = Encryption Time; CA = Chaotic Algorithm; CET-2C = Chaotic Map based Encryption Technique using 2’s Compliment.
% Gain of CET-2C over Chaotic Algorithm [3] when message size is 200 KB
% Gain of CET-2C over Chaotic Algorithm [3] when message size is 250 KB
% Gain of CET-2C over Chaotic Algorithm [3] when message size is 300 KB
% Gain of CET-2C over Chaotic Algorithm [3] when message size is 350 KB
% Gain of CET-2C over Chaotic Algorithm [3] when message size is 400 KB
% Gain of CET-2C over Chaotic Algorithm [3] when message size is 450 KB
Overall % Gain of CET-2C over AES [3] for Encryption Time with increasing the message size
where, AES = Advance Encryption Standard.
% Gain of CET-2C over AES [3] when message size is 200 KB
% Gain of CET-2C over AES [3] when message size is 250 KB
% Gain of CET-2C over AES [3] when message size is 300 KB
% Gain of CET-2C over AES [3] when message size is 350 KB
% Gain of CET-2C over AES [3] when message size is 400 KB
% Gain of CET-2C over AES [3] when message size is 450 KB
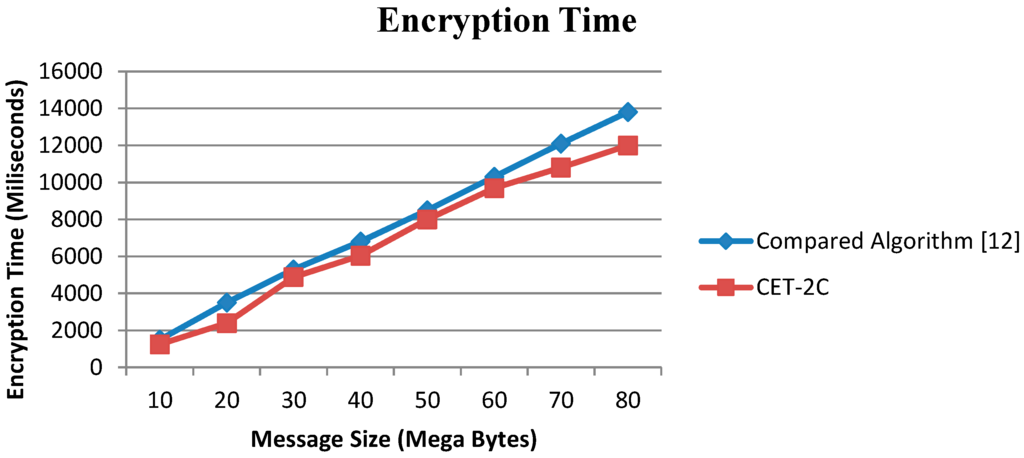
Table 8 illustrates that overall gain % of CET-2C for encryption time is higher as compared with the Chaotic Algorithm [3] and AES [3]. For the 350 KB message size the overall % gain of CET-2C is 96.85% and 91.09% when it is compared with the Chaotic Algorithm [3] and AES [3]. It shows that the performance of CET-2C is increased with multiple message sizes. The encryption time is also calculated for large data sizes in MB (10 MB to 80 MB) using a laptop with an Intel (R) Pentium (R) Dual CPU T2370 processor of @ 1.73 GHz, and 1 GB RAM (Table 9).
Table 8.
Overall % Gain of CET-2C over Chaotic Algorithm [3] and AES [3] for encryption time.
Table 9.
Encryption time of compared Algorithm [12] and CET-2C.
Figure 6 shows that the time required for encryption in the proposed CET-2C algorithm is lower compared to the algorithm [12] for different message sizes in MB. For 80 MB message the encryption time of CET-2C is 12 sand for the comparison algorithm [12] it is 13.8 s. This shows that CET-2C is much faster than the comparable algorithm [12].
Figure 6.
Encryption time of compared Algorithm [12] and CET-2C.
Overall % Gain of CET-2C over Compared Algorithm [12] for Encryption Time with increasing message size.
Here = Overall % Gain at Different Message Sizes; ET = Encryption Time; CA = Compared Algorithm; CET-2C = Chaotic Map based Encryption Technique using 2’s Compliment
% Gain of CET-2C over Compared Algorithm [12] when message size is 10 MB
% Gain of CET-2C over Compared Algorithm [12] when message size is 20 MB
% Gain of CET-2C over Compared Algorithm [12] when message size is 30 MB
% Gain of CET-2C over Compared Algorithm [12] when message size is 40 MB
% Gain of CET-2C over Compared Algorithm [12] when message size is 50 MB
% Gain of CET-2C over Compared Algorithm [12] when message size is 60 MB
% Gain of CET-2C over Compared Algorithm [12] when message size is 70 MB
% Gain of CET-2C over Compared Algorithm [12] when message size is 80 MB
Table 10 illustrates that the overall encryption time gain % of CET-2C is higher as compared with the compared algorithm [12]. At the message size 20 MB the overall % gain of CET-2C is 31.43% when compared with the compared algorithm [12]. This shows that the performance of CET-2C is increased with multiple message sizes.
Table 10.
Overall %Gain of CET-2C over the compared Algorithm [12] for encryption time.
The data sizes was also taken in bytes and experiments performed to calculate the encryption time using a laptop with an Intel (R) Core (TM) i3-3110M processor @ 2.40GHzCPU, and a RAM of 2GB (Table 11).
Table 11.
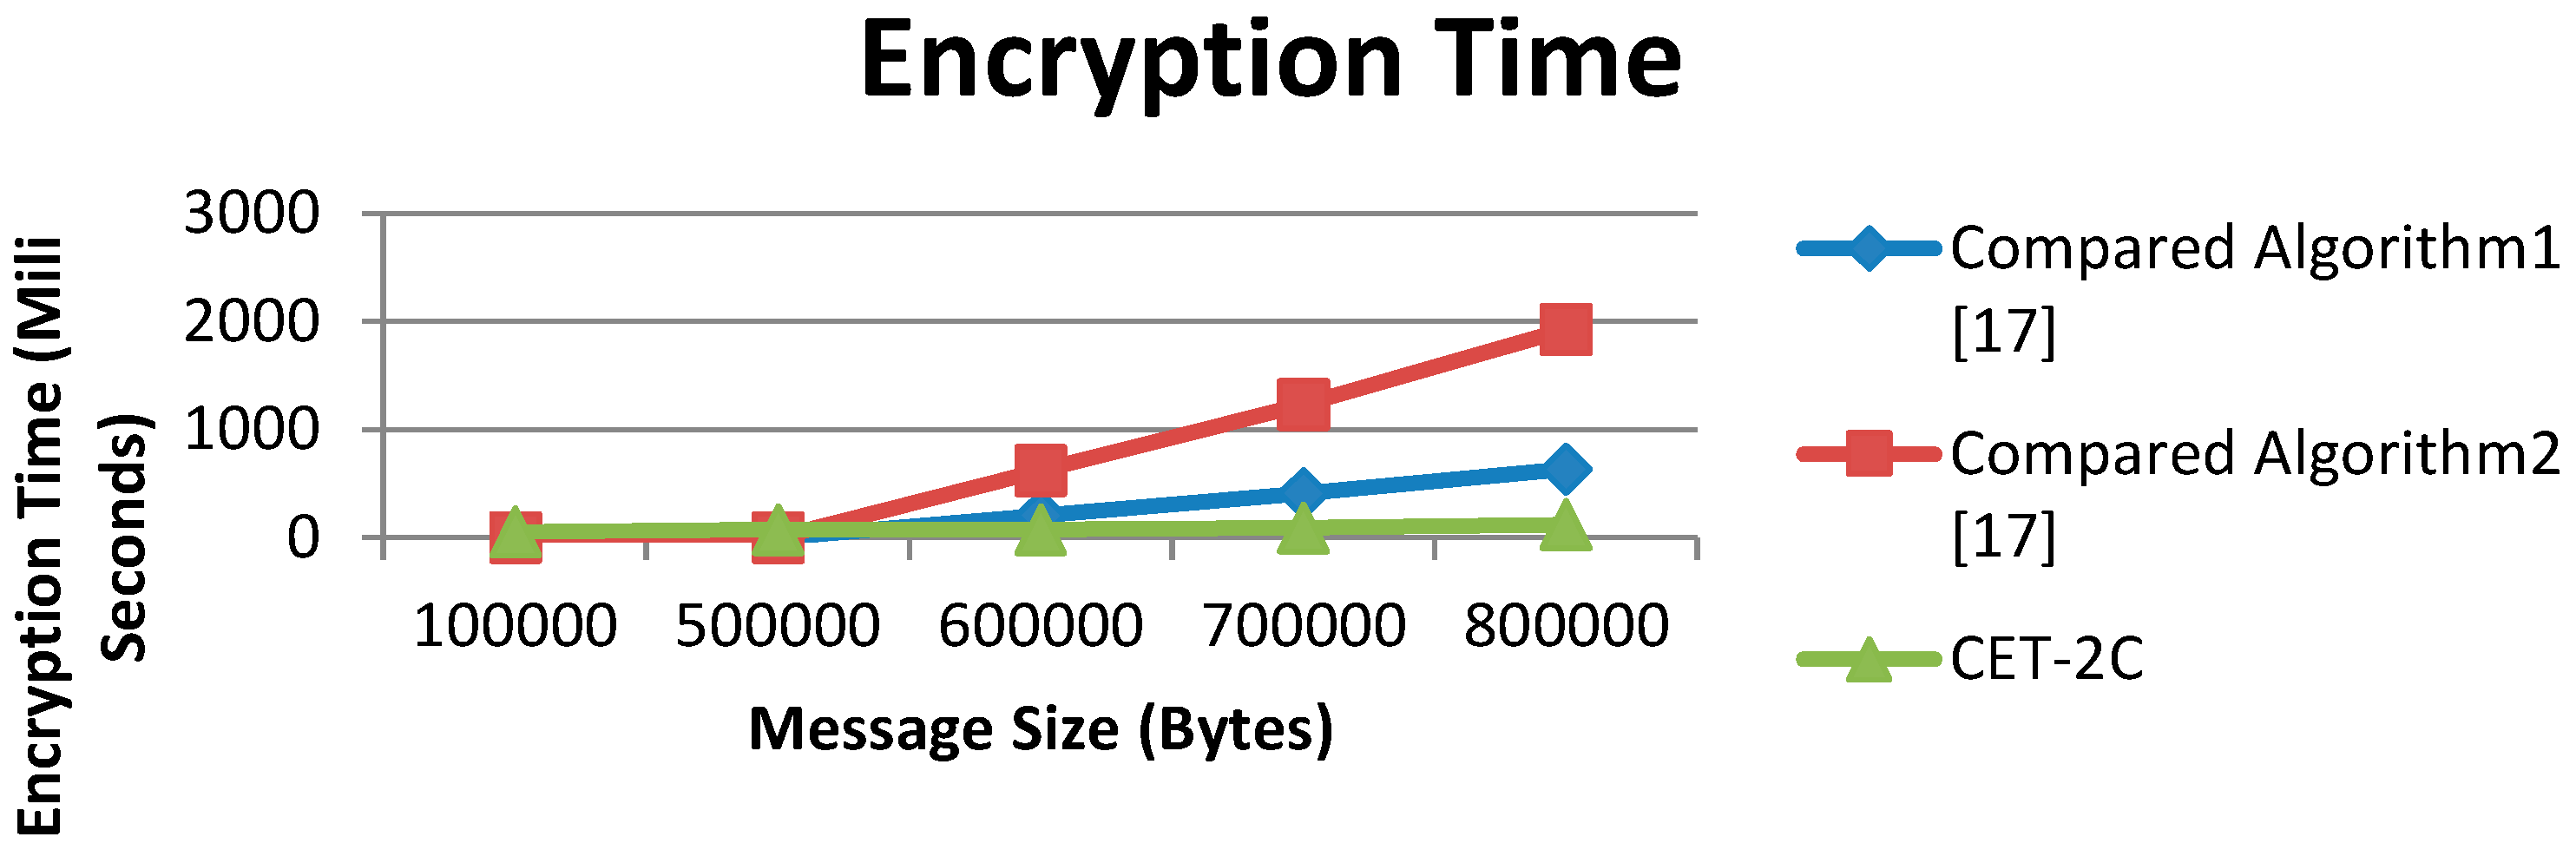
Encryption time of compared Algorithms 1 and 2 [17] and CET-2C.
Figure 7 shows that for small dataset sizes (100 KB and 500 KB) the comparison algorithms [17] performed the encryption with slightly higher speed, but for large data sizes (larger than 500 KB) the encryption time is instantly increased. The graph of our proposed algorithm CET-2C increased linearly for small to large data sizes.
Figure 7.
Encryption times of compared Algorithms 1 and 2 [17] and CET-2C.
Overall % Gain of CET-2C over compared Algorithm 1 [17] for encryption time with increasing the message size:
Here = Overall % Gain at Different Message Sizes; ET = Encryption Time; CA1 = Compared Algorithm 1; CET-2C = Chaotic Map based Encryption Technique using 2’s Compliment.
% Gain of CET-2C over Compared Algorithm 1 [17] when message size is 100,000 Bytes
% Gain of CET-2C over compared Algorithm 1 [17] when message size is 500,000 Bytes
% Gain of CET-2C over compared Algorithm 1 [17] when message size is 600,000 Bytes
% Gain of CET-2C over compared Algorithm 1 [17] when message size is 700,000 Bytes
% Gain of CET-2C over Compared Algorithm 1 [17] when message size is 800,000 Bytes
Overall % Gain of CET-2C over Compared Algorithm 2 [17] for Encryption Time with increasing the message size
Here = Overall % Gain at Different Message Sizes; ET = Encryption Time; CA2 = Compared Algorithm 2; CET-2C = Chaotic Map based Encryption Technique using 2’s Compliment.
% Gain of CET-2C over compared Algorithm 1 [17] when message size is 100,000 Bytes
% Gain of CET-2C over compared Algorithm 1 [17] when message size is 500,000 Bytes
% Gain of CET-2C over compared Algorithm 1 [17] when message size is 600,000 Bytes
% Gain of CET-2C over compared Algorithm 1 [17] when message size is 700,000 Bytes
% Gain of CET-2C over compared Algorithm1 [17] when message size is 800,000 Bytes
Table 12 illustrates that the overall gain % of CET-2C for encryption time is negative as compared with the compared Algorithms 1 and 2 [17] for small data sizes (up to 500 KB), meaning that CET-2C takes a longer time for encryption. After 500 KB the encryption time is lower than for comparable Algorithms 1 and 2 [17] so the overall performance of CET-2C is enhanced for larger data sizes. At the message size of 700 KB the overall % gain of CET-2C is 76.34% and 92.11% when it is compared with compared Algorithm 1 and 2, respectively [17].This shows that the performance of CET-2C is increased with increased message size.
Table 12.
Overall %Gain of CET-2C over compared Algorithms 1 and 2 [17] for encryption time.
8.2. Encryption Throughput
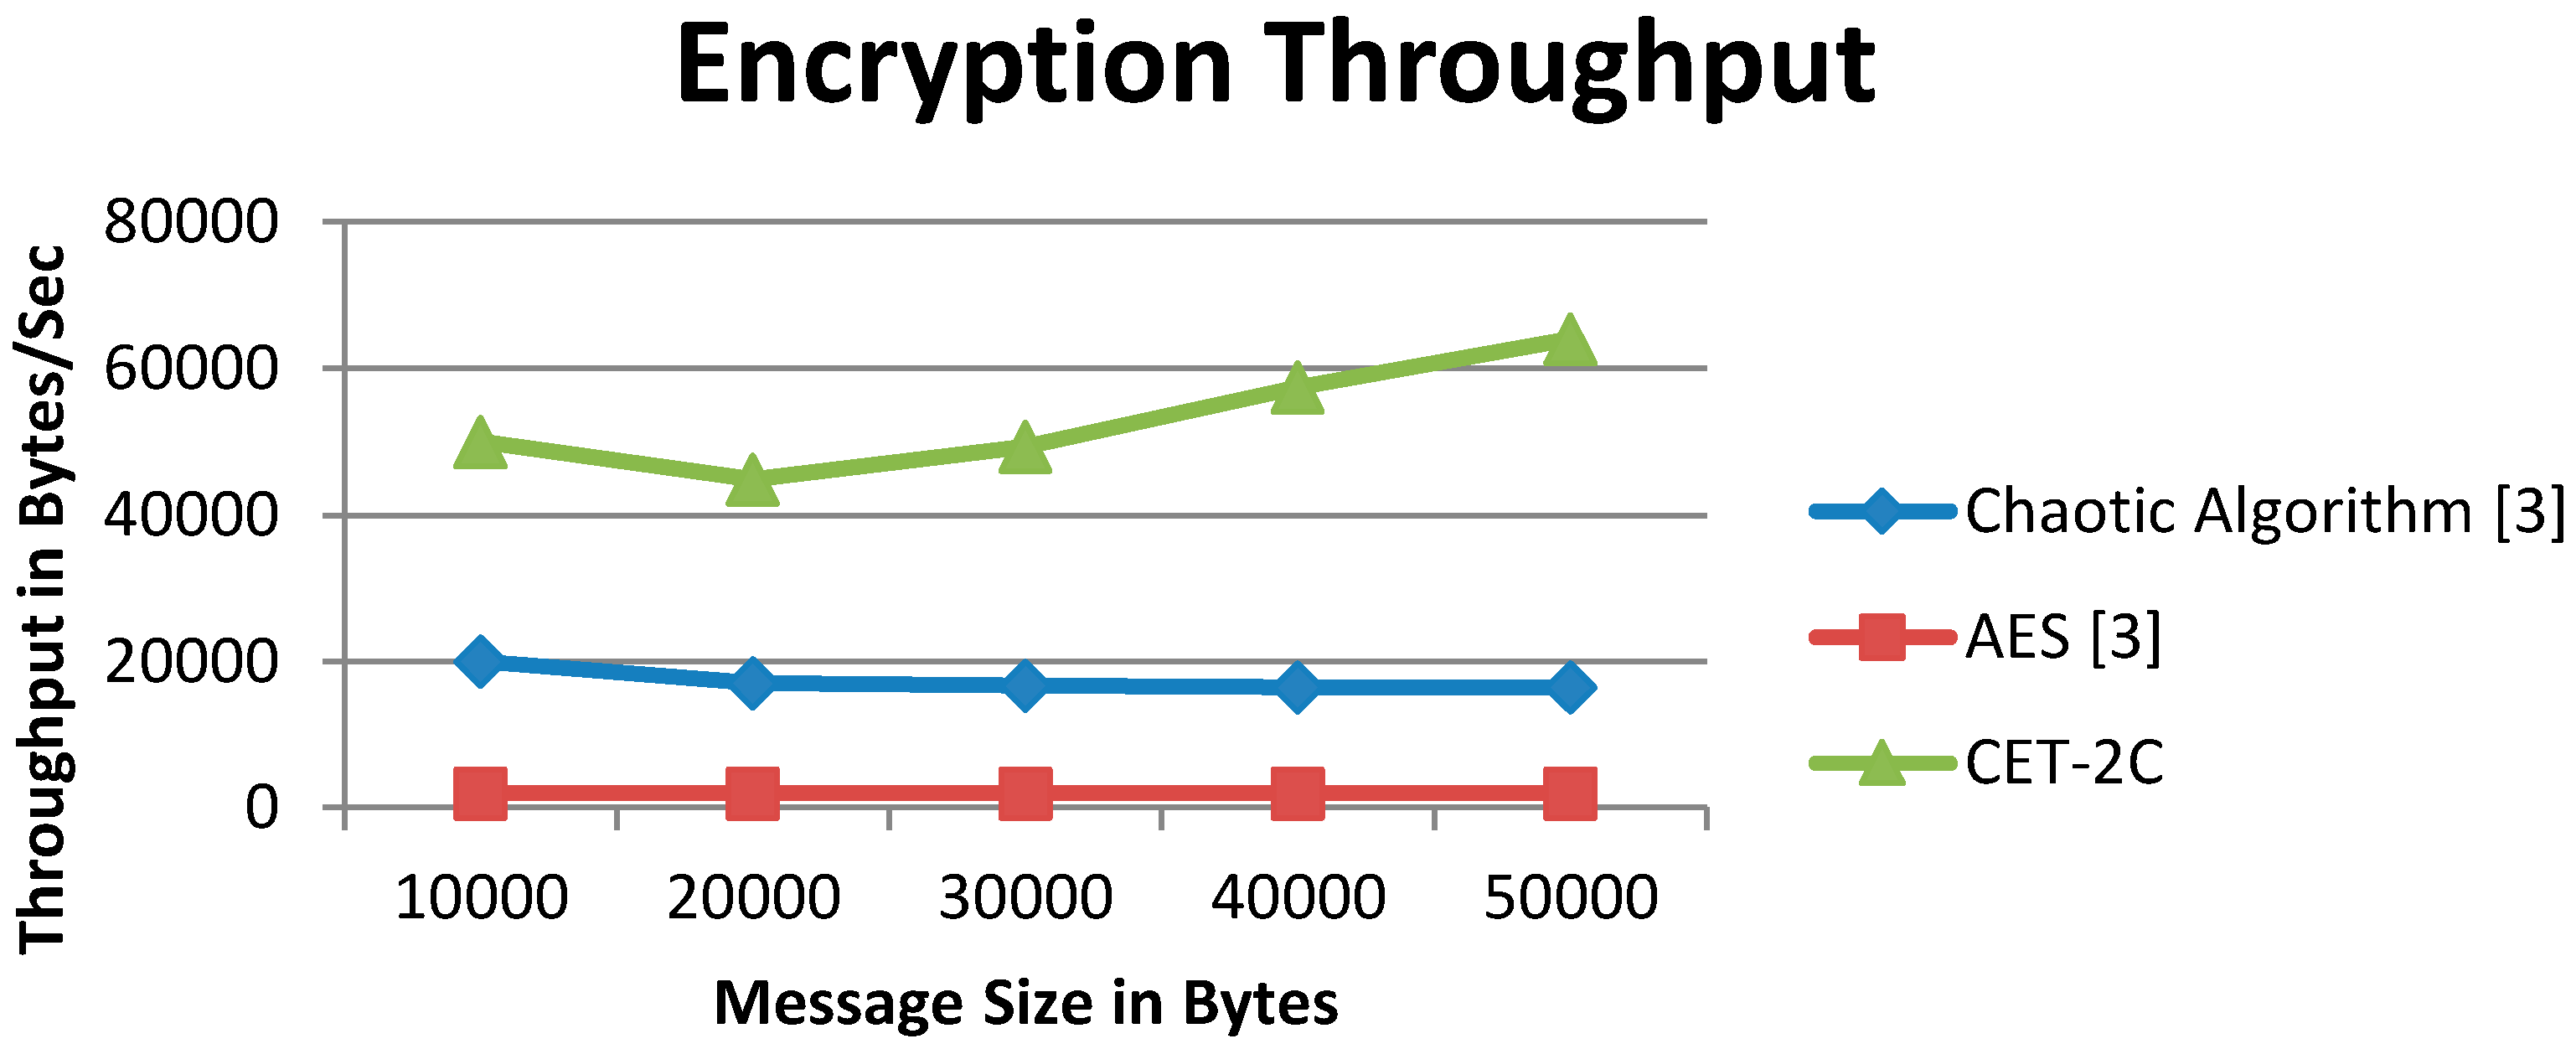
The graph representing the throughput performance of the proposed algorithm CET-2C is much higher for any data size compared to the AES and Chaotic Algorithm [3]. It was analyzed using a laptop having an Intel (R) Pentium (R) Dual T2370 @ 1.73 GHz processor CPU, and 1 GB RAM (Table 13).
Table 13.
Encryption throughput of Chaotic Algorithm [3], AES [3] and CET-2C.
Figure 8 shows that the throughput of the proposed algorithm CET-2C is much higher compared to the chaotic algorithm [3] and AES [3] for different message sizes in bytes. For a 50,000 byte message the throughput of CET-2C is 64,049 bytes/s and the Chaotic Algorithm [3] and AES [3] have throughputs of 16,400 and 2000 bytes/s, respectively. This shows that CET-2C is much faster than the comparable algorithm [3].
Figure 8.
Encryption throughput of Chaotic Algorithm [3], AES [3] and CET-2C.
Overall % Gain of CET-2C over Chaotic Algorithm [3] for Encryption Throughput with increasing the message size
Here = Overall % Gain at Different Message Sizes; ETh = Encryption Throughput; CA = Chaotic Algorithm.
% Gain of CET-2C over Chaotic Algorithm [3] when message size is 10,000 bytes
% Gain of CET-2C over Chaotic Algorithm [3] when message size is 20,000 bytes
% Gain of CET-2C over Chaotic Algorithm [3] when message size is 30,000 bytes
% Gain of CET-2C over Chaotic Algorithm [3] when message size is 40,000 bytes
% Gain of CET-2C over Chaotic Algorithm [3] when message size is 50,000 bytes
Overall % Gain of CET-2C over AES [3] for Encryption Throughput with increasing the message size
where AES = Advance Encryption Standard.
% Gain of CET-2C over Chaotic Algorithm [3] when message size is 10,000 bytes
% Gain of CET-2C over Chaotic Algorithm [3] when message size is 20,000 bytes
% Gain of CET-2C over Chaotic Algorithm [3] when message size is 30,000 bytes
% Gain of CET-2C over Chaotic Algorithm [3] when message size is 40,000 bytes
% Gain of CET-2C over Chaotic Algorithm [3] when message size is 50,000 bytes
Table 14 illustrates that overall gain % of CET-2C for encryption throughput is much higher as compared with the chaotic algorithm [3] and AES [3]. For the message size of 30,000 bytes the overall % gain of CET-2C is 195% and 2367% when it is compared with the Chaotic Algorithm [3] and AES [3]. This shows that the performance of CET-2C is increased with increasing message size. AES provides sconstant encryption time, so the throughput of AES is also constant. This indicates that CET-2Cprovidesmuchhigher encryption throughput than AES [3].
Table 14.
Overall %Gain of CET-2C over Chaotic Algorithm [3] and AES [3] for encryption throughput.
8.3. Encryption Power Consumption
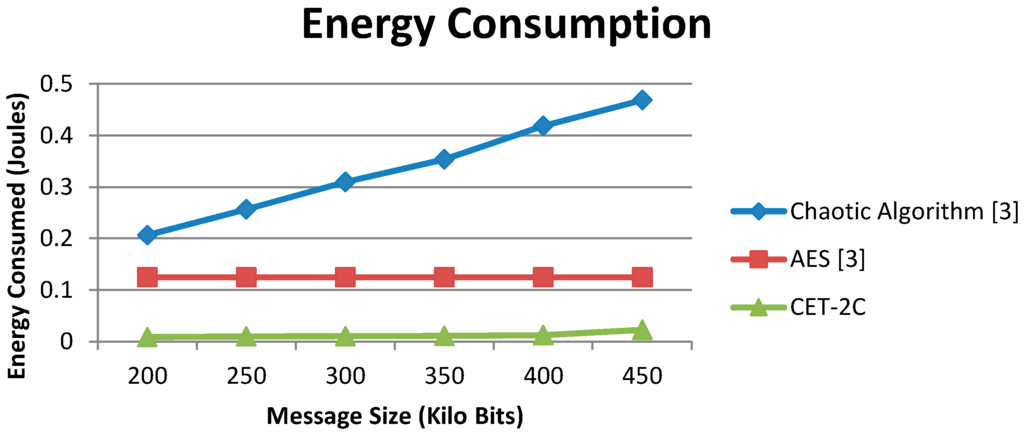
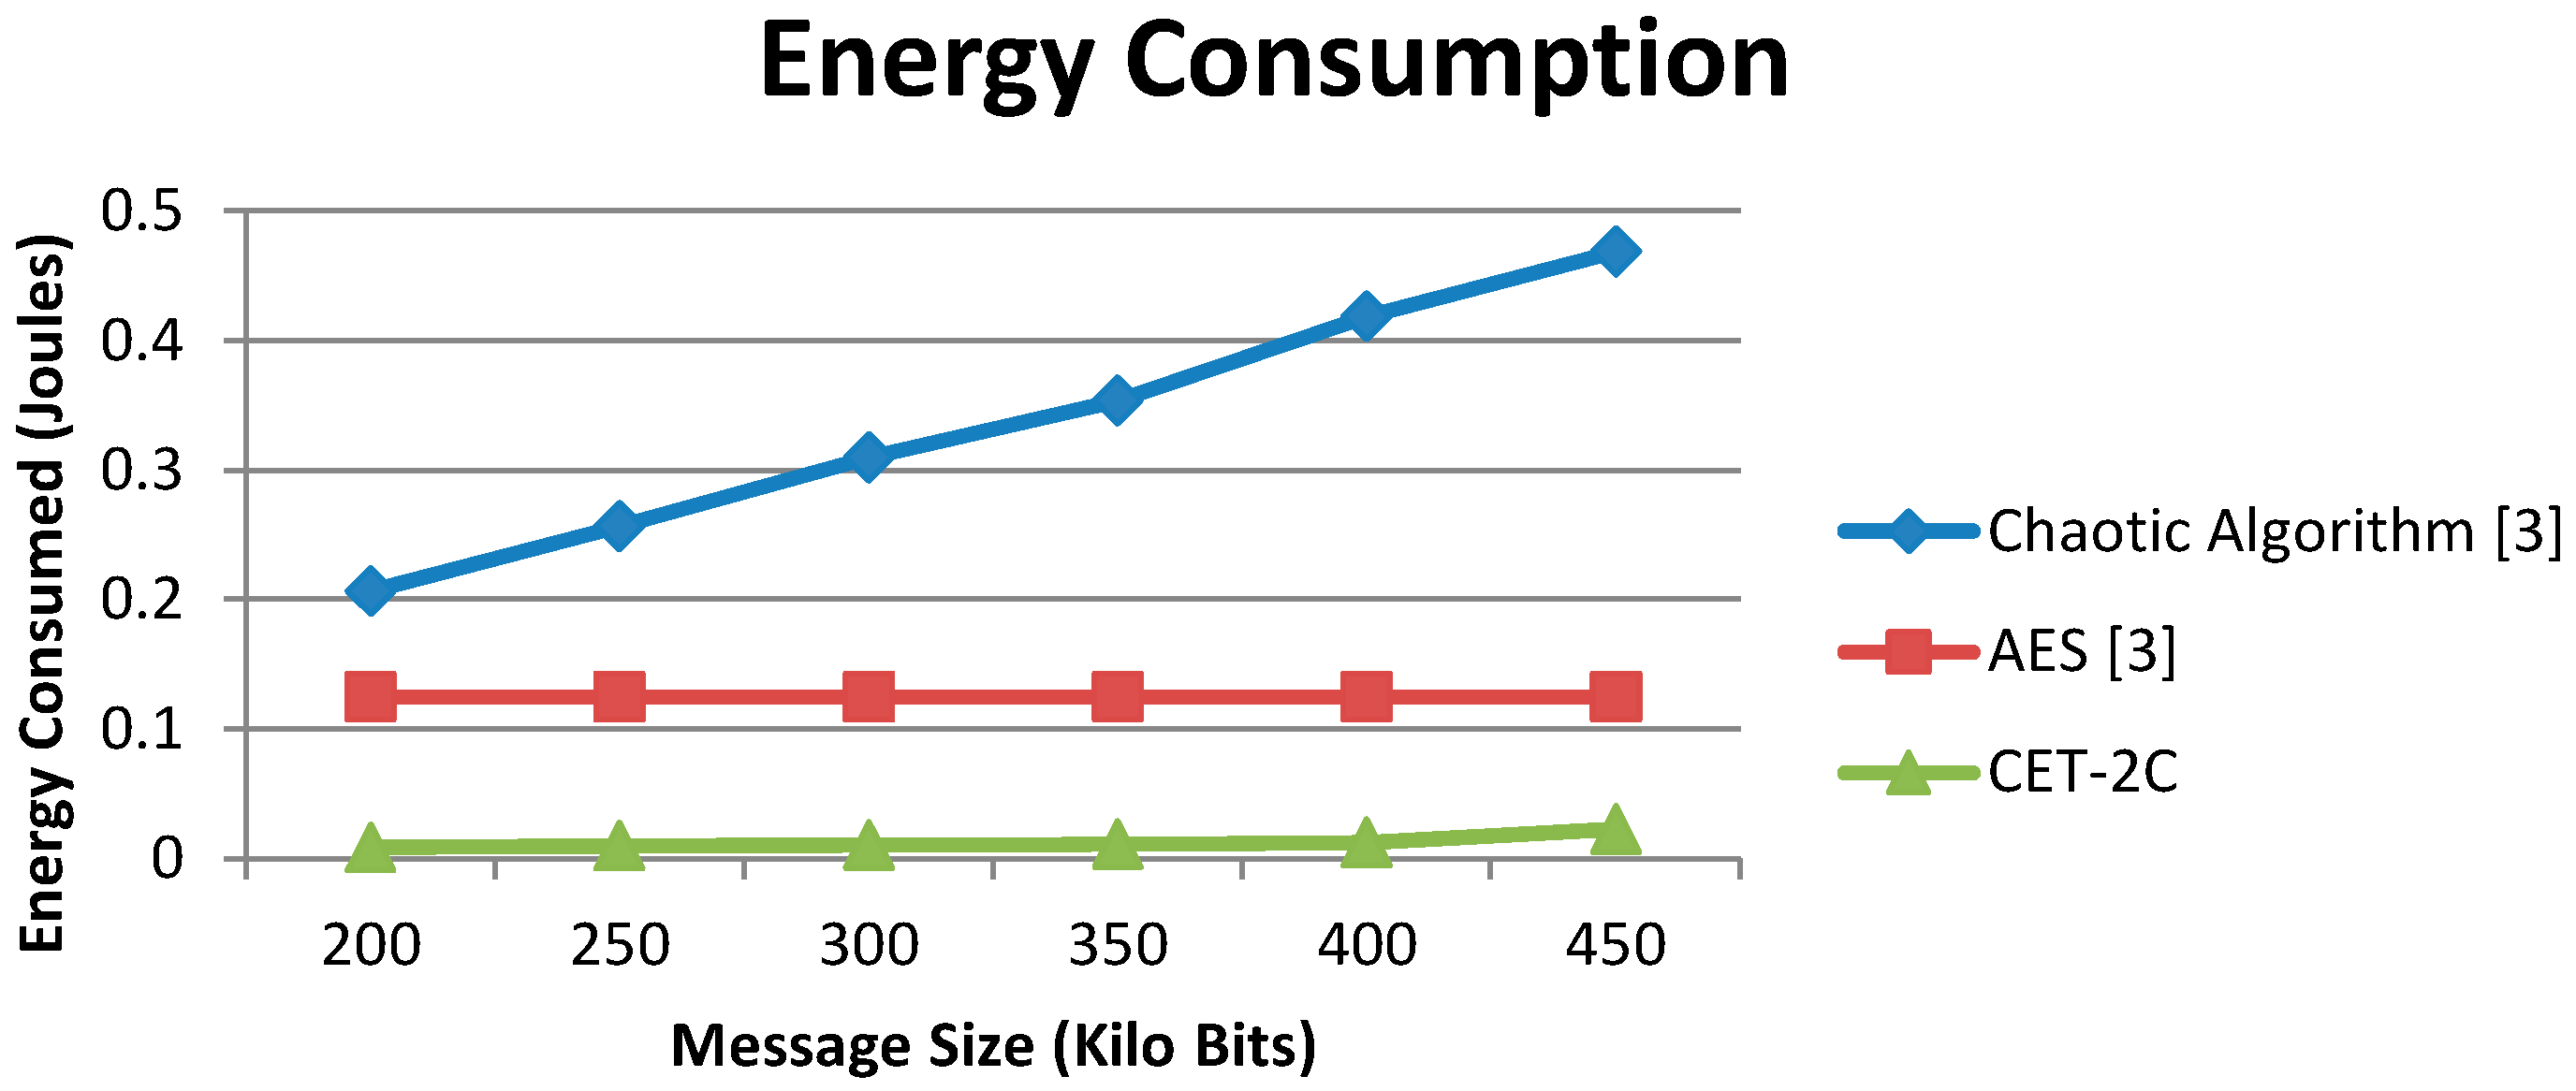
The graph demonstrates that the proposed algorithm has lesser power consumption than AES and the Chaotic Algorithm [3] for any data size. This was analyzed using a laptop having an Intel (R) Pentium (R) Dual processor T2370 @ 1.73 GHzCPU, and 1 GB RAM (Table 15).
Table 15.
Energy consumption of AES [3], Chaotic Algorithm [3] and CET-2C.
Figure 9 shows the proposed algorithm CET-2C has less power consumption compared to AES [3] and the chaotic algorithm for multiple message sizes ranging from 200 KB to 450 KB [3]. The results illustrate that the energy consumptionincreases linearly like the encryption time when it is compared with other algorithms.
Figure 9.
Energy consumption of AES [3], Chaotic Algorithm [3] and CET-2C.
Overall % Gain of CET-2C over Chaotic Algorithm [3] for Energy Consumption with increasing the message size.
Here = Overall % Gain at Different Message Sizes; EC = Energy Consumption; CA = Chaotic Algorithm.
% Gain of CET-2C over Chaotic Algorithm [3] when message size is 200 KB
% Gain of CET-2 Cover Chaotic Algorithm [3] when message size is 250 KB
% Gain of CET-2C over Chaotic Algorithm [3] when message size is 300 KB
% Gain of CET-2C over Chaotic Algorithm [3] when message size is 350 KB
% Gain of CET-2C over Chaotic Algorithm [3] when message size is 400 KB
% Gain of CET-2C over Chaotic Algorithm [3] when message size is 450 KB
Overall % Gain of CET-2C over AES [3] for Encryption Time with increasing the message size
where AES = Advance Encryption Standard.
% Gain of CET-2C over AES [3] when message size is 200 KB
% Gain of CET-2C over AES [3] when message size is 250 KB
% Gain of CET-2C over AES [3] when message size is 300 KB
% Gain of CET-2C over AES [3] when message size is 350 KB
% Gain of CET-2C over AES [3] when message size is 400 KB
% Gain of CET-2C over AES [3] when message size is 450 KB
Table 16 illustrates that the overall gain % of CET-2C of energy consumption is lower as compared with the chaotic algorithm [3] and AES [3]. At the message size of 450 Kb the overall % gain of CET-2C is 97.19% and 89.46% when it is compared with the chaotic algorithm [3] and AES [3]. This shows that the performance of CET-2C is increased with increasing message size.
Table 16.
Overall % Gain of CET-2C over Chaotic Algorithm [3] and AES [3] for energy consumption.
9. Conclusions
Chaotic functions have been widely used in different applications to generate pseudo-random numbers to produce random values in short times, which may be used for various real time applications. In this paper a novel digital logic-based, chaotic encryption technique has been developed, which works based on chaos theory, using the sensitivity of parameters like a constant A and initial condition Xn with the properties of chaotic systems for ubiquitous and ad-hoc computing. The efficiency of the encryption technique also depends on the number of keys, which are generated by the use of the chaotic function. It has been also shown that keys are completely different when the parameters are changed slightly. This demonstrates the security of the keys. Cryptanalysis of the proposed algorithm shows the strength and security of the algorithm and keys. The performance of a proposed algorithm has been analyzed in terms of running time, throughput and power consumption. It is to be shown in comparison graphs that the proposed algorithm gave better results compared to different algorithms like AES and some others. The graphs show that the CET-2C gives 97% better encryption time, 95% better throughput and 98% better power consumption as compared to the other algorithms. This could be used for providing a better trade-off between security and computational complexity. In the future chaos theory could be used in highly secure and fast encryption systems, capable of processing very large dataset sizes on the order of GB with low space complexity. Digital circuits are very useful for fast encryption, as they are easily understandable and maintainable for processing messages compared to mathematical models. The private networks have security concerns and they need several techniques for hiding and encoding the messages moving between their private systems. This could be achieved by using chaos-based cryptography in the future.
Author Contributions
Ankur Khare and Piyush Kumar Shukla studied the chaotic map based encryption techniques which are used both stream cipher and block cipher. They generate an encryption algorithm using chaos function and digital circuits with the help of other information for fast and secure encryption using multiple keys and compare the performance of encryption technique with some standard research papers on the basis of encryption time, energy consumption and CPU time etc and show the performance result on the tabular and graphical format. Murtaza Abbas Rizvi is studied the digital circuit systems and help us to make an encryption algorithm using digital logic concept like XOR and XNOR gates for secure and fast encryption and decryption. He helps us to improve the security of keys which are used for encryption and decryption by using 2’s compliment concept. Shalini Stalin helps us to check the robustness and security of algorithm against all four cryptanalysis attacks like cipher text only, known plain text, chosen cipher text, chosen plain text attacks. So we show that the algorithm is highly attack resilient.
Conflicts of Interest
The authors declare no conflict of interest.
References
- Zaher, A.A. Digital Communication using a Novel Combination of Chaotic Shift Keying and Duffing Oscillators. Int. J. Innov. Comput. Inf. Control 2013, 9, 1865–1879. [Google Scholar]
- Ozkaynak, F.; Yavuz, S. Designing chaotic S-boxes on time-delay chaotic system. Nonlinear Dyn. 2013, 74, 551–557. [Google Scholar] [CrossRef]
- Fitwi, A.H.; Nouh, S. Performance Analysis of Chaotic Encryption using a Shared Image as a Key. Zede J. 2011, 28, 17–29. [Google Scholar]
- Mousa, A.; Nigm, E.; El-Rabaie, S.; Faragallah, O. Query Processing Performance on Encrypted Databases by Using the REA Algorithm. Int. J. Netw. Secur. 2012, 14, 280–288. [Google Scholar]
- Yuan, W.X.; Qing, Y. A block encryption algorithm based on dynamic sequences of multiple chaotic systems. Commun. Nonlinear Sci. Numer. Simul. 2009, 14, 574–581. [Google Scholar]
- Bakhache, B.; Ahmad, K.; El Assad, S. A New Chaotic Encryption Algorithm to Enhance the Security of ZigBee and Wi-Fi networks. Int. J. Intell. Comput. Res. 2011, 2, 219–227. [Google Scholar]
- Mansour, I.; Chalhoub, G.; Barkhache, B. Evaluation of a fast symmetric cryptographic algorithm based on the chaos theory for wireless sensor networks. In Proceedings of the IEEE 11th International Conference on Trust, Security and Privacy in Computing and Communications, Liverpool, UK, 25–27 June 2012; pp. 913–919.
- Assad, S.E. Chaos Based Information Hiding and Security. In Proceedings of the 7th International Conference for Internet Technology and Secured Transactions, London, UK, 10–12 December 2012; pp. 67–72.
- Agrawal, B.; Agrawal, H. Implementation of AES and RSA using Chaos System. Int. J. Sci. Eng. Res. 2013, 4, 1413–1417. [Google Scholar]
- Pan, J.; Ding, Q.; Qi, N. The Research of Chaos-Based SMS Encryption in Mobile Phone. In Proceedings of the Second International Conference on Instrumentation & Measurement, Computer, Communication and Control, Harbin, China, 8–10 December 2012; pp. 501–504.
- Beltran, R.H. Low-complexity chaotic encryption system. Rev. Mex. Fis. 2007, 53, 58–65. [Google Scholar]
- Akhvan, A.; Samsudin, A.; Akhshani, A. A novel parallel hash function based on 3D chaotic map. EURASIP J. Adv. Signal Process. 2013, 126, 1–12. [Google Scholar] [CrossRef]
- Linda, F.R.; Hammami, S.; Benrejeb, M.; Borne, P. Synchronization of discrete-time hyperchaotic maps based on an aggregation technique for encryption. In Proceedings of the 9th International Multi-Conference on systems, Signals and Devices, Chemnitz, Germany, 20–23 March 2012; pp. 1–6.
- Amigo, J.M.; Kocarev, L.; Szczepanski, J. Theory and practice of chaotic cryptography. Phys. Lett. A 2007, 366, 211–216. [Google Scholar] [CrossRef]
- Kocarev, L. Chaos-Based Cryptography: A Brief Overview. IEEE Circuits Syst. Mag. 2001, 1, 1–16. [Google Scholar] [CrossRef]
- Soltani, M. A new Secure Cryptography Algorithm based on Symmetric Key Encryption. J. Basic Appl. Sci. Res. 2013, 3, 465–472. [Google Scholar]
- Wang, X.; Chen, D. A Parallel Encryption Algorithm based on the Piecewise Linear Chaotic Map. Math. Probl. Eng. 2013, 1–7. [Google Scholar] [CrossRef]
- Wei, J.; Zheng, J.; Yu, J.; Shuai, Y. Selection of chaotic states in cryptosystem based on chaos with differential analysis. In Proceedings of the 7th International Conference on Computer Science & Education, Melbourne, Australia, 14–17 July 2012; pp. 325–330.
- Wong, K.-W.; Lin, Q.; Chen, J. Simultaneous Arithmetic Coding and Encryption Using Chaotic Maps. IEEE Trans. Circuits Syst. 2010, 57, 146–150. [Google Scholar] [CrossRef]
- Pande, A.; Zambreno, J. A Chaotic Encryption Scheme for Real-Time Embedded Systems: Design and Implementation. Telecommun. Syst. 2013, 52, 551–561. [Google Scholar]
- Guo, X.; Zhang, J. Cryptanalysis of the Chaotic-based Key Agreement Protocols. In Proceedings of the International Symposium on Biometrics and Security Technologies (ISBAST), Islamabad, Pakistan, 23–24 April 2008; pp. 1–3.
- Zhao, G.; Chen, G.; Fang, J.; Xu, G. Block Cipher Design: Generalized Single-Use-Algorithm Based on Chaos. Tsinghua Sci. Technol. 2011, 16, 194–206. [Google Scholar] [CrossRef]
- Tong, X.; Liu, Y.; Zhang, M.; Xu, H.; Wang, Z. An Image Encryption Scheme Based on Hyperchaotic Rabinovich and Exponential Chaos Maps. Entropy 2015, 17, 181–196. [Google Scholar] [CrossRef]
- Soleymani, A.; Nordin, M.J.; Sundararajan, E. A Chaotic Cryptosystem for Images Based on Henon and Arnold Cat Map. Sci. World J. 2014. [Google Scholar] [CrossRef] [PubMed]
- Wei, J.; Zheng, X.; Yu, J.; Shuai, Y. A novel authentication scheme based on chaos. In Proceedings of the 8th International Conference on Computer Science & Education, Colombo, Sri Lanka, 26–28 April 2013; pp. 879–882.
- Rani, P.J.; Bhavani, S.D. Symmetric Encryption using the logistic map. In Proceedings of the 1st International Conference on Recent Advances in Information Technology (RAIT), Dhanbad, India, 15–17 March 2012; pp. 1–5.
- Azzaz, M.S.; Tanougast, C.; Sadoudi, S.; Dandache, A. New Hardware Cryptosystem Based Chaos for the Secure Real-Time of Embedded Applications. In Proceedings of the IEEE Workshop Signal Processing System SIPS, Beirut, Lebanon, 4–7 October 2011; pp. 251–254.
- Sheng, S.; Wu, X. A New Digital Anti-counterfeiting Scheme Based on Chaotic Cryptography. In Proceedings of the International Conference on ICT Convergence (ICTC), Jeju Island, Korea, 15–17 October 2012; pp. 687–691.
- Zhang, Z.; Liu, K.; Niu, X.; Bai, X. The Research of Hardware Encryption Card Based on Chaos. In Proceedings of The International Conference on Sensor Network Security Technology and Privacy Communication System (SNS & PCS), Nangang, Taiwan, 18–19 May 2013; pp. 116–119.
- Shukla, P.K.; Khare, A.; Rizvi, M.A.; Stalin, S.; Kumar, S. Applied Cryptography Using Chaos Function for Fast Digital Logic-Based Systems in Ubiquitous Computing. Entropy 2015, 17, 1387–1410. [Google Scholar] [CrossRef]
- Shi, Z.; Bi, S.; Zhang, H.; Lu, R.; Shen, X. Improved auxiliary particle filter-based synchronization of chaotic Colpitts circuit and its application to secure communication. Wirel. Commun. Mob. Comput. 2013, 1–15. [Google Scholar] [CrossRef]
© 2016 by the authors; licensee MDPI, Basel, Switzerland. This article is an open access article distributed under the terms and conditions of the Creative Commons Attribution (CC-BY) license (http://creativecommons.org/licenses/by/4.0/).