


Abstract
To prevent eavesdropping and tampering, network security protocols take advantage of asymmetric ciphers to establish session-specific shared keys with which further communication is encrypted using symmetric ciphers. Commonly used asymmetric algorithms include public key encryption, key exchange, and identity-based encryption (IBE). However, network security protocols based on classic identity-based encryption schemes do not have perfect forward secrecy. To solve this problem, we construct the first quantum IBE (QIBE) scheme based on the learning with errors (LWE) problem, which is also the first cryptographic scheme that applies the LWE problem to quantum encryption. We prove that our scheme is fully secure under the random oracle model and highlight the following advantages: (1) Network security protocols with our QIBE scheme provide perfect forward secrecy. The ciphertext is transmitted in the form of a quantum state unknown to the adversary and cannot be copied and stored. Thus, in network security protocols based on QIBE construction, the adversary does not have any previous quantum ciphertext to decrypt for obtaining the previous session key, even if the private identity key is threatened. (2) Classic key generation centre (KGC) systems can still be used in the QIBE scheme to generate and distribute private identity keys, reducing the cost when implementing this scheme. The classic KGC systems can be used because the master public and secret keys of our scheme are both in the form of classic bits. Finally, we present quantum circuits to implement this QIBE scheme and analyse its required quantum resources for given numbers of qubits, Hadamard gates, phase gates, T gates, and CNOT (controlled-NOT) gates. One of our main findings is that the quantum resources required by our scheme increase linearly with the number of plaintext bits to be encrypted.
1. Introduction
Identity-based encryption (IBE) is an advanced form of public key encryption, and the notion of IBE was first proposed by Shamir in 1984 [1]. In the IBE scheme, the public key is directly calculated from the receiver’s identity , which may be a phone number, email address, or network address, and the corresponding private identity key is generated by a trusted key generation centre (KGC), which owns the master public key and the master secret key . When the sender wants to send a message m to the receiver, the sender encrypts the message to obtain a ciphertext , where r is a random number. After receiving the ciphertext , the receiver can decrypt it and obtain the message . Compared with a public key infrastructure (PKI)-based cryptographic system, an identity-based cryptographic system avoids the high cost of storing and managing public key certificates, simplifies the process of public key management, and reduces the pressure on the system. Therefore, identity-based cryptosystems have been widely developed and applied.
The first practical IBE scheme was proposed by Boneh et al. in 2001 [2], and it was followed by numerous other classic IBE schemes. These classic IBE schemes can be divided into three categories: based on elliptic curve bilinear pairings [2,3,4], based on quadratic residue [5,6,7,8], and based on lattices [9,10,11,12,13]. With the development of quantum computers and quantum algorithms, especially the Shor algorithm [14], the security of IBE schemes based on elliptic curve bilinear pairings and quadratic residue has been seriously threatened. As there is currently no quantum algorithm that can solve lattice-based problems, the construction of lattice-based IBE schemes has become a major research area for cryptographers.
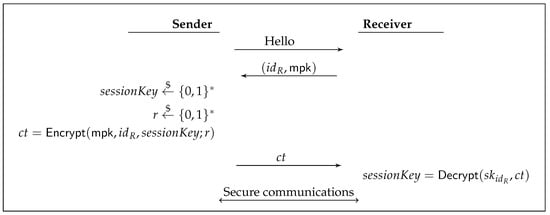
One of the main applications of IBE is the construction of network security protocols, such as the Chinese SSL VPN technology specification [15]. In the IBE-based security protocol, the receiver sends its identity and to the sender, and the sender chooses a and sends its ciphertext to the receiver. The receiver decrypts the ciphertext to obtain the . Subsequently, both the sender and the receiver can own this secret session key with which further communication is encrypted using a symmetric cipher. The entire procedure is briefly described in Figure 1. A security protocol is said to provide perfect forward secrecy [16] if the compromise of long-term keys does not compromise past session keys that were established before the compromise of the long-term key. In security protocols based on classic IBE, all session keys and their ciphertexts are in the form of classic bits. A patient attacker can capture the conversations and store the ciphertexts of the session keys, whose confidentiality is protected by a private identity key (which is the long-term key of the network security protocol based on IBEs) and wait until the long-term key is threatened. Once the patient attacker obtains the long-term key, the attacker can decrypt the ciphertexts of all previous session keys. Ultimately, all encrypted communications and sessions recorded in the past can be retrieved. Therefore, the security protocols based on the classic IBE scheme do not have perfect forward secrecy. This naturally leads to the following question:
Figure 1.
Security protocols based on IBE. The “Hello” message means that the sender wants to communicate with the receiver.
Can we construct a fully secure IBE scheme with which the network security protocol can provide perfect forward secrecy?
1.1. Our Contributions
To solve this problem, considering that an adversary cannot replicate an unknown quantum state [17], we propose the notion of quantum identity-based encryption (QIBE) and construct the first QIBE scheme based on the learning with errors (LWE) problem. Then, we prove that our scheme is fully secure under the random oracle model. Our scheme possesses the following advantages:
- Network security protocols with our QIBE scheme provide perfect forward secrecy. The ciphertext is transmitted in the form of a quantum state that is unknown to the adversary, who cannot duplicate the ciphertext. Thus, in security protocols based on QIBE construction, even if the private identity key is threatened, the adversary does not possess the previous ciphertexts of session keys to decrypt, and therefore cannot threaten the security of the previous session keys. Therefore, security protocols based on QIBE construction have perfect forward secrecy.
- The classic KGC system can still be used for QIBE schemes to generate and distribute private identity keys, reducing the cost of implementing this scheme. The classic KGC system can be used because the , algorithms of our scheme are classic, and the master public and secret keys of our scheme are both in the form of classic bits.
Finally, we present quantum circuits to implement this QIBE scheme and establish its required quantum resource estimates for given numbers of qubits, Hadamard gates, phase gates, T gates, and CNOT gates. One of our primary findings is that the quantum resources required by our scheme increase linearly with the number of plaintext bits to be encrypted.
1.2. Outline of the Paper
The remainder of this paper is organised as follows: In Section 2, we present the necessary background for the paper, including quantum computation, lattices, and classic IBE. In Section 3, we first present the definition of QIBE; then, we describe the concrete construction of the scheme and analyse its correctness, and finally, prove the security of the scheme and discuss its advantages. In Section 4, we discuss the specific quantum circuit implementation for the QIBE scheme and estimate the quantum resources needed. In Section 5, we summarise our work, discuss the drawbacks of our scheme, and suggest directions for future work.
2. Preliminaries
2.1. Quantum Computation
In this section, we briefly discuss the basic concepts used in this work. Please refer to [18] for a more detailed introduction to quantum computing. “” is defined as the bit-flip of “”, such as , , and . We begin by introducing some quantum gates.
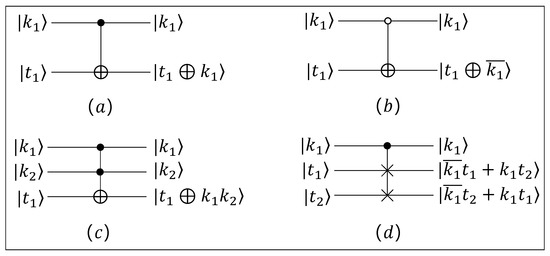
Fundamental gates. The fundamental gate set we use comprises the NOT gate, the CNOT gate, the CNOT variant gate, the Toffoli (two-controlled NOT) gate, and the Fredkin gate. These four gates are shown in Figure 2. One CNOT variant gate can be obtained by a CNOT gate and two NOT gates. The Fredkin gate is also known as a three-qubit controlled swap gate, that is, if the control qubit is in state , the two target qubits swap their states; otherwise, they remain in their initial states if the control qubit is in state . One Fredkin gate can be constructed from one Toffoli gate and two CNOT gates.
Figure 2.
Fundamental gates. The CNOT gate is shown in (a); the CNOT variant gate is shown in (b); the Toffoli gate is shown in (c); and the Fredkin gate is shown in (d).
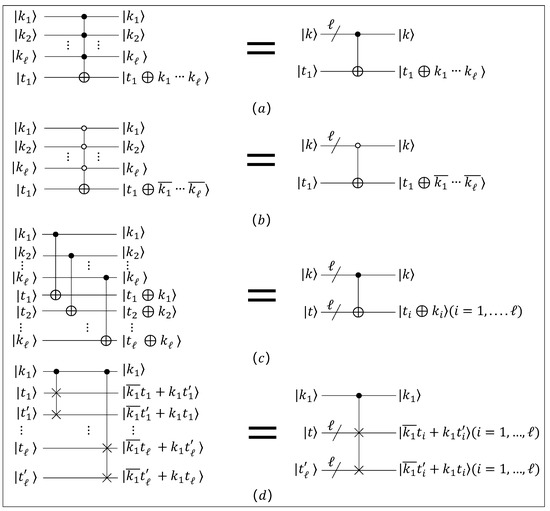
Complex Gates. We use four complex gates (Figure 3): the first gate is the ℓ-controlled-NOT gate, which can be decomposed into Toffoli gates, the second gate is the variant of the ℓ-controlled-NOT gate, which can also be decomposed into Toffoli gates, the third gate is the ℓ-combination-CNOT gate, which is a combination of ℓ CNOT gates, and the last gate is the ℓ-Fredkin gate, which can be constructed from ℓ Toffoli gates and CNOT gates.
Figure 3.
Complex gates. The ℓ-controlled-NOT gate is shown in (a); the variant of the ℓ-controlled-NOT gate is shown in (b); the ℓ-combination-CNOT gate is shown in (c); and the ℓ-Fredkin gate is shown in (d).
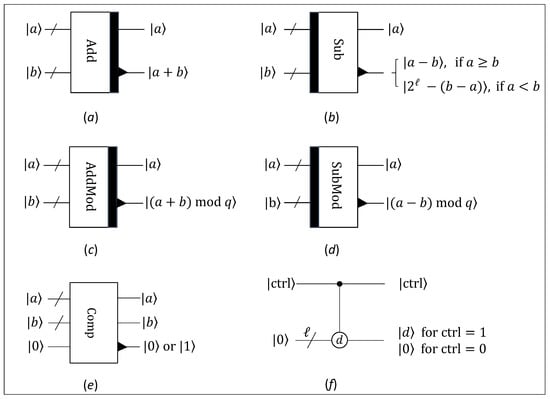
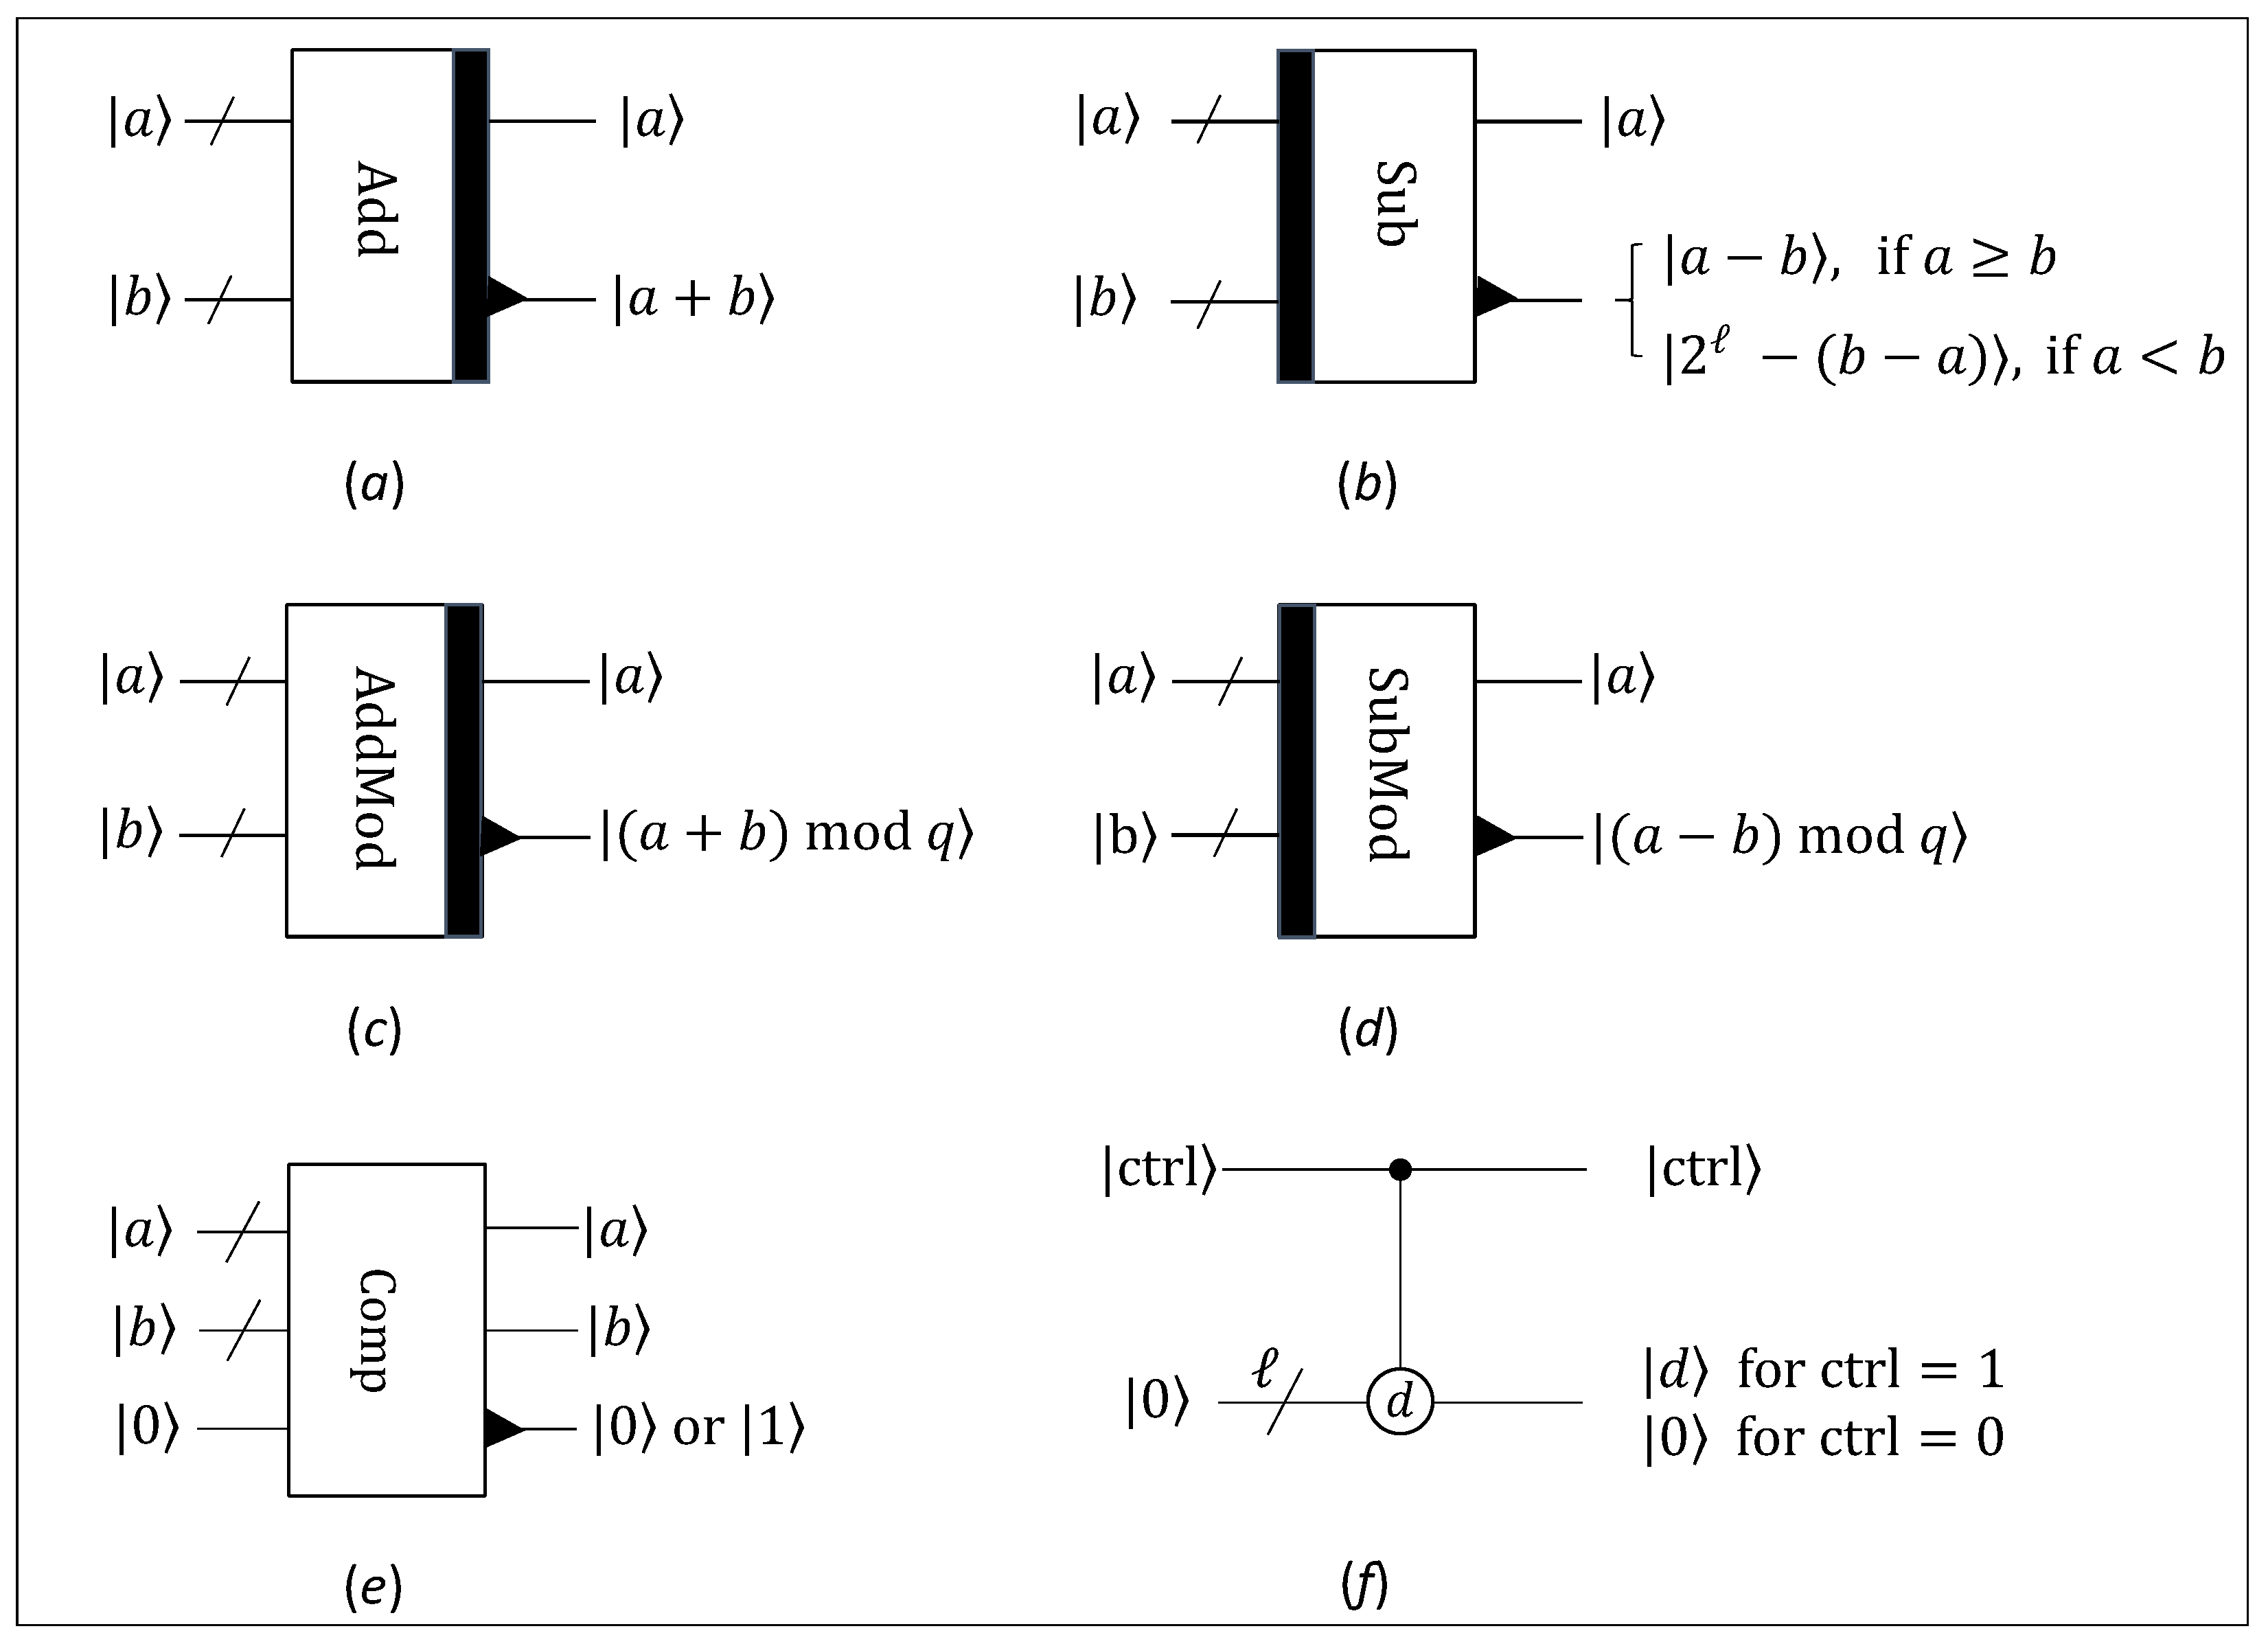
Quantum Basic Circuits.Figure 4f depicts the controlled copy circuit in which copying the integer d into the quantum register is controlled by . If the controlled bit , the output of the controlled copy circuit is . Otherwise, the output is . The output of the controlled copy circuit is . We denote the controlled copy circuit by when this algorithm takes a qubit and an ℓ-bit number d as input. According to the conclusion in [19], copying an integer uses only NOT gates so that a controlled copy circuit only uses CNOT gates. Suppose that d is a uniform integer in ; then, the controlled copy circuit uses approximately CNOT gates, where .
Figure 4.
Some quantum basic and arithmetic circuits. In the Figure, (a) shows the addition circuit while (b) shows the subtraction circuit; (c) depicts the modular addition circuit while (d) depicts the modular subtraction circuit; (e) illustrates the comparison circuit; and the controlled copy circuit is shown in (f).
Quantum Arithmetic Circuits. We introduce some quantum arithmetic circuits, including addition, subtraction, modular addition, modular subtraction, and comparison, and describe the corresponding quantum resources required, including the number of qubits and the number of CNOT gates and Toffoli gates. To simplify the description, we only show the simplified form of these quantum arithmetic circuits.
- Addition and subtraction: Cuccaro et al. [20] proposed a quantum addition circuit. The quantum addition achieves the addition of two registers, that is,To prevent overflows caused by the carry, the second register (initially loaded in state ) should be sufficiently large, i.e., if both a and b are encoded on ℓ qubits, the second register should be of size . In the addition circuit, the last carry is the most significant bit of the result and is written in the -th qubit of the second register. As a result of the reversibility of unitary operations, by reversing the addition circuit, i.e., applying each gate of the circuit in the reversed order, the subtraction circuit is obtained. The addition and subtraction circuits are shown in and of Figure 4, respectively. In this paper, a circuit with a bar on the left side represents the reversed sequence of elementary gates embedded in the same circuit with the bar on the right side.In the subtraction circuit, with the input , the output produces when . When , the output is , where the size of the second register is . i.e.,When , the significant qubit, that is, the -th qubit of the second register, which indicates whether an overflow occurred in the subtraction, always contains 1. We denote the addition circuit by when this algorithm takes two ℓ-qubit states and as input. Similarly, we denote the subtraction circuit by when this algorithm takes two ℓ-qubit states and as input. To calculate the addition or subtraction of two ℓ-bit inputs, a total of qubits, Toffoli gates, and CNOT gates are required.
- Addition and subtraction module q: Liu et al. [21] improved Roetteler’s [22] quantum modular addition circuit and reduced the number of quantum gates required. This quantum circuit produceswhere . The simplified form of the addition module q circuit is shown in Figure 4c. The modular subtraction can be obtained by reversing the modular addition circuit, and its bar is on the left-hand side. We denote the modular addition circuit by when this algorithm takes two -qubit states and as input. Similarly, we denote the modular subtraction circuit by when this algorithm takes two -qubit states and as input. To calculate the addition or subtraction module q of two -bit inputs, a total of qubits, Toffoli gates, CNOT gates are required.
- Comparison: Markov et al. [23] constructed a quantum comparison circuit by comparing and based on whether the highest bit of is or . This circuit is obtained by modifying the previous subtraction circuit so that it outputs only the highest bit of . The comparison circuit achieves the comparison of two registers, that isThe simplified form of the quantum comparison circuit is shown in Figure 4e. We denote the comparison circuit by when this algorithm takes two ℓ-qubit states and as input. To compare two ℓ-bit inputs and , a total of qubits, Toffoli gates, and CNOT gates are required.
2.2. Lattices
Let X and Y be two random variables over some finite set , , respectively. The statistical distance between X and Y is defined as
For integer , denotes the quotient ring of integer modulo q. We use bold capital letters to denote matrices, such as , and bold lowercase letters to denote column vectors, such as . The notation denotes the transpose of the matrix .
Let be a set of vectors, in . We use to denote the Gram–Schmidt orthogonalisation of the vectors in that order and to denote the length of the longest vector in . For positive integers with q prime, and a matrix , the -dimensional integer lattices are defined as follows: and . Moreover, for , the set of syndromes is defined as .
For , define the Gaussian function over centred at with parameter as . Let , and define the discrete Gaussian distribution over as , where . For simplicity, and are abbreviated as and , respectively.
Lemma 1
(Adopted from [9,24,25]). Let be positive integers with and q prime. There exist the following PPT (probabilistic polynomial-time) algorithms:
- a randomised algorithm that, when , outputs a pair such that is close to uniform in and is a basis of , satisfying with overwhelming probability.
- a randomised algorithm that, given a full rank matrix ,a basis of , a vector and , outputs a vector sampled from a distribution close to .
Discrete Gaussian Lemmas. The following lemmas are used to manipulate and obtain meaningful bounds on discrete Gaussian vectors.
Lemma 2
(Adopted from [9], Lemma 5.2). Let n, , q be positive integers such that and q is prime. Let σ be any positive real number such that . Then, for all but a fraction of , the distribution of for is -close to uniform distribution over . Furthermore, for a fixed , the conditional distribution of , given is .
The Learing with Errors Problem. The security of our construction is based on the LWE problem. The LWE problem is a hard problem based on lattices defined by Regev [26]. It is stated as follows: given an input , where for any , integer is prime, and is either of the form for and or is uniformly random (and independent of ), distinguish which is the case, with non-negligible advantage. Regev proved that the LWE problem is as hard as approximating standard lattice problems in the worst case using a quantum algorithm.
2.3. Classic Identity-Based Encryption
A classic identity-based encryption scheme consists of the following four algorithms:
- . The key generation algorithm takes a security parameter as input. It outputs a master public key and a master secret key .
- . The key extraction algorithm takes a master public key , a master secret key , and an identity as input. It outputs a private identity key . We assume that is implicitly included in .
- . The encryption algorithm takes a master public key , an identity , and the message m as input. It outputs a ciphertext .
- . The decryption algorithm takes the master public key , the private identity key , and the ciphertext as input. It outputs the message m. Correctness. For all , all identities , all messages m, and all , we haveSecurity. The security game is defined by the following experiment, which is played by a challenger and an adversary :
- The challenger runs to generate . It gives to the adversary .
- The adversary adaptively requests keys for any identity of its choice. The challenger responds with the corresponding secret key , which it generates by running .
- The adversary submits two messages of equal length, and , and a challenge identity with the restriction that is not equal to any identity requested in the previous phase. The challenger picks , encrypts under by running the encryption algorithm, and sends the ciphertext to the adversary .
- continues to issue key queries for any identity as in step (2) with the restriction that .
- The adversary outputs a guess for .
The advantage of an adversary is defined as
Definition 1.
An IBE scheme is fully secure if for all probabilistic polynomial-time adversaries , is a negligible function in λ.
3. QIBE and Its Construction
3.1. Definition of QIBE
We begin by defining a primitive for identity-based encryption schemes in which some elements may belong to a quantum space.
Definition 2.
We say that an identity-based encryption scheme is a quantum identity-based encryption (QIBE) scheme if there exists at least one quantum algorithm in its algorithms that include , and .
Note that the classification of QIBE can be analogous to that of quantum public key encryption [27] and a quantum symmetric-encryption scheme [28]. Since each algorithm in the QIBE schemes could be either classic or quantum, there exist only fifteen types of QIBE schemes in total.
3.2. Our Construction
Then, we design a QIBE scheme by utilising the proposed classic IBE scheme [9] and prove its security based on the LWE problem.
In our QIBE scheme, and are classic algorithms while and are quantum algorithms. To make it easier to distinguish between classic IBE and QIBE, we denote our scheme as , and our QIBE scheme consists of one tuple . Let integer parameters as specified in [9], where is a security parameter.
- (1) It runs to obtain a uniformly random matric and which is a good basis for . (2) Then, it selects a hash function , which maps an identity to a vector. (3) Finally, it outputs and . (4) In summary, .
- : (1) On input , and an identity , it computes and generates such that . It is clear that . (2) In summary, .
- : (1) On input of an identity , , and a bit quantum superposition state , it first computes and chooses a uniformly random , and . (2) Then, it sets and . More procedures are performed as follows:
- ⋆
- Step 1: Taking and as input, it runs and gets
- ⋆
- Step 2: Taking the second register of the above result and x as input, it runs and obtains
- ⋆
- Step 3: Finally, taking the two registers of the above result as input, it runs the unentanglement quantum circuit (which is described in Section 4, and we denote it by ) to obtain(3) In summary, .
- : To decrypt a ciphertext using an identity secret key , it computes . Then, more processes are performed as follows:
- ⋆
- Step 1: Taking and as input, it runs to obtain
- ⋆
- Step 2: Taking the above result and as input, it runs ( is a quantum circuit, which takes two ℓ-qubit quantum states and as input and outputs the absolute value of their subtraction, i.e., ) to obtainPlease refer to Section 4.1 for more information about .
- ⋆
- Step 3: Taking the above result and as input, it runs to obtainNext, the algorithm will unentangle the first and second registers of this quantum state.
- ⋆
- Step 4: Taking the first register of the above result and as input, it runs (The (which is the inverse of ) is a quantum circuit which takes in two ℓ-qubit quantum states and as input and outputs one ℓ-qubit quantum state, i.e., ) to obtainPlease refer to Section 4.1 for more information about the inverse of .
- ⋆
- Step 5: Taking the first register of the above result and as input, it runs to obtain
- ⋆
- Step 6: Taking the second register of the above result and as the input, it runs to obtain
- ⋆
- Step 7: Taking the first register and the third register of the above result as input, it runs to obtainFinally, the algorithm unentangles the second and third registers of the above result.
- ⋆
- Step 8: Taking the third register of the above result and as input, it performs the inverse of the controlled copy circuit to obtainThe quantum state is no longer entangled with other registers and the decryption procedure is completed. In summary,
3.3. Correctness
Considering a ciphertext
of a qubit quantum superposition state , it can be observed that , where . In step 2 of , it is clear that
which is equal to the absolute value of b in the of Theorem A1, i.e., . Finally, in step 3 of , we compare with and obtain m. According to Theorem A1, the decryption algorithm with the identity secret key can decrypt the ciphertext correctly with a probability of . Therefore, the decryption algorithm with the identity secret key can decrypt the ciphertext correctly with a probability of .
3.4. Security Proof
Theorem 1.
The above QIBE scheme is fully secure in the random oracle model under the assumption, namely, for any classical PPT adversary making at most random oracle queries to and identity secret key queries, there exists a classical PPT algorithm such that
Proof of Theorem 1.
Without loss of generality, we make some simplifying assumptions about . First, we assume that whenever queries a secret key or asks for a challenge ciphertext, the corresponding has already been queried to the random oracle . Second, we assume that makes the same query for the same random oracle at most once. Third, we assume that does not repeat secret key queries for the same identity more than once. We show the security of the scheme via the following games. In each game, we define as the event that the adversary wins in .
: This is a real security game. At the beginning, is run, and the adversary is given . Then, the challenger samples and keeps it secret. During the game, may make random oracle queries, secret key queries, and the challenge query. These queries are handled as follows:
- Hash queries: When makes a random oracle query to on , the challenger chooses a random vector and locally stores the tuple , and returns to .
- Identity secret key queries: When queries an identity secret key for , the challenger uses the algorithm , which takes as input to compute and returns to .
- Challenge ciphertext: When the adversary submits two messages and of equal length and a challenge identity with the restriction that is not equal to any identity requested in the previous phase, the challenger picks , and encrypts under by running the encryption algorithm to get , where and and . Then, the ciphertext is sent to .
At the end of the game, outputs a guess for . Finally, the challenger outputs . By definition, we have
: In this game, we change the way the random oracle queries to are answered.
- Hash queries: When queries the random oracle on , the challenger generates a pair by first sampling and setting . Then, it locally stores the tuple and returns to .
- Identity secret key queries: When makes an identity secret key query for , the challenger uses the algorithm , which takes as input to compute and returns to .
- Challenge ciphertext: The same as that in the .
Note that is independent of , which was generated in the simulation of the random oracle on input . Due to Lemma 2, the distribution of in is -close to that of except for fraction of as we choose . Therefore, we have
: In this game, we change the way identity secret key queries are answered. By the end of this game, the challenger will no longer require the trapdoor to generate the identity secret keys.
- Hash queries: When queries the random oracle on , the challenger generates a pair as in the previous game. Then, it locally stores the tuple and returns to .
- Identity secret key queries: When queries an identity secret key for , the challenger retrieves the unique tuple from the local storage and returns .
- Challenge ciphertext: The same as that in the .
For any fixed , let and be random variables that are distributed according to the distributions of conditional on in and , respectively. Owing to Lemma 1, we have . Owing to Lemma 2, we have . Then, we obtain . Therefore, we have
: In this game, we change the way the matrix is generated. Specifically, the challenger chooses without generating the associated trapdoor .
- Hash queries: The same as that in the .
- Identity secret key queries: The same as that in the .
- Challenge ciphertext: The same as that in the .
By Lemma 1, this makes only -statistical difference. As the challenger can answer all the secret key queries without the trapdoor owing to the change made in the previous game, the view of is altered only by . Therefore, we have
: In this game, we change the way the random oracle queries to are answered and the challenge ciphertext is created. The challenger chooses an index and a vector uniformly at random.
- Hash queries: On ’s -th distinct query to , the challenger does the following: if , then locally stores the tuple and returns to . Otherwise, for , the challenger selects and computes ; then, it locally stores the tuple and returns to .
- Identity secret key queries: The same as that in the .
- Challenge ciphertext: When produces a challenge identity (distinct from all its identity secret key queries) and messages , , assume without loss of generality that already queried on . If , i.e., if the tuple is not in the local storage, then the challenger ignores the output of and aborts the game (we denote this event as ). Otherwise, i.e., if the does not occur (we denote this event as ), the challenger picks and encrypts under by running the encryption algorithm to obtain , where and , and . Then, the ciphertext is sent to the adversary .
Conditional on the challenger not aborting, we affirm that the view it provides to in is statistically close to that in . Therefore, we have
By a standard argument, the probability that the challenger does not abort during the simulation is (this is proved by considering a game in which the challenger can answer all identity secret key queries, so that the value of is perfectly hidden from ). Therefore, we have
: In this game, we change the way the challenge ciphertext is created.
- Hash queries: The same as that in the .
- Identity secret key queries: The same as that in the .
- Challenge ciphertext: When produces a challenge identity (distinct from all its identity secret key queries) and messages , , assume without loss of generality that already queried on . If , i.e., if the tuple is not in the local storage, then the challenger ignores the output of and aborts the game. Otherwise, i.e., if the does not occur, the challenger picks and encrypts under using two random vectors to obtain , where and , and . Then, the ciphertext is sent to the adversary .
It can be seen that if are valid LWE samples (i.e., and ), the view of the adversary corresponds to . Otherwise (i.e., ), it corresponds to . Therefore, we have
Note that is statistically close to the uniform distribution over , so that
Then, because is independent of , we get
3.5. Advantages of Our QIBE
The proposed QIBE scheme has two main advantages. One is that the network security protocol based on our QIBE scheme has perfect forward secrecy, and the other is that the QIBE scheme can still use the KGC system to generate and distribute private identity keys, thus reducing the cost when this scheme is implemented.
- A fundamental fact in quantum information theory is that unknown or random quantum states cannot be replicated [17]. The probability amplitude and corresponding basis state of ciphertext are unknown to the adversary, so the ciphertext is an unknown quantum state and cannot be replicated during transmission. When attempting to attack our QIBE-based network security protocol, an attacker cannot copy and store the ciphertext of the session key, which is encrypted by a private identity key (called a long-term key). Thus, the attacker does not have the quantum ciphertext of the previous session key to decrypt, and the security of the previous session key will not be threatened even if the attacker obtains the long-term key. In other words, all encrypted communications and sessions recorded in the past cannot be retrieved. Therefore, the security protocol based on our QIBE has perfect forward secrecy, which cannot be achieved by the security protocol based on classic IBE.
- In our QIBE scheme, the KGC uses the algorithms and to generate the private identity key when it takes as input a master public key , a master secret key , and an identity . The key observation is that both the input () and the output () of are in the form of classic bits, and so are the input () and the output () of . Therefore, the classic KGC system can still be used in our QIBE scheme to generate and distribute private identity keys, reducing the cost when this scheme is implemented.
4. Quantum Circuit Realisation
The realisation of a quantum scheme requires describing the corresponding quantum circuit. To analyse the realisability of our QIBE scheme, we begin by providing details for the quantum circuits of and , and then, we analyse the complexity of these two quantum circuits.
4.1. Quantum Circuit
Note that the algorithms and of are classic, so there is no need to construct quantum circuits for these two algorithms.
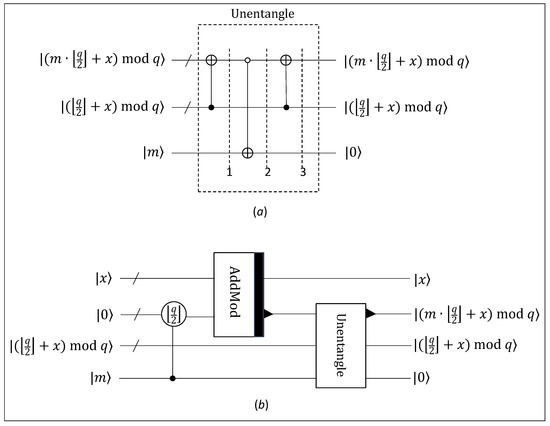
The Quantum Circuit of . The main part of is the unentangled quantum circuit . Taking an additional quantum state as input, can transform to a non-entangled quantum state , as shown in Figure 5a. The correctness of can be proven by the following facts.
Figure 5.
The quantum circuits of and . In this figure, (a) shows the circuit, and (b) depicts the circuit.
- On input , and , the initial output where the number 1 is located is , and . This is because only one -combination-CNOT operation is performed.
- The output where the number 2 is located is , and . This is because only one -controlled-NOT variant operation is performed, in which the control bits are and the target bit is . If , the control bits are -qubit , and the target qubit will change to . Otherwise, the control bits are not equal to -qubit , and the target qubit is all the time.
- The final output where the number 3 is located is , and . Only one -combination-CNOT operation is performed, in which the control bits are and the target bits are ; therefore, it can obtain .
Note that one unentangled quantum circuit is composed of two -combination-CNOT gates and one -controlled-NOT variant gate. Thus, one unentangled quantum circuit is composed of CNOT gates and Toffoli gates.
Using the unentangled quantum circuit , we can provide details for the quantum circuit of , which is depicted in Figure 5b. Note that one is composed of one controlled copy circuit, one modular addition circuit, and one unentangled quantum circuit. To encrypt one qubit, a total of qubits, Toffoli gates and CNOT gates are required.
The Quantum Circuit of . The main part of is and the inverse of . In the circuit, with the input , the output will produce when . When , the output is .
On the inverse of the circuit, i.e., , with the input , the output will produce when . When , the input is and the output is .
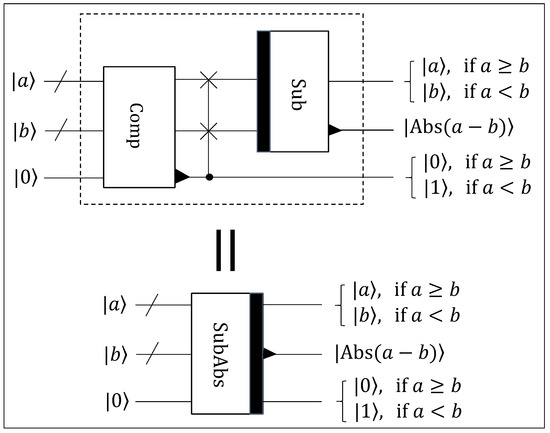
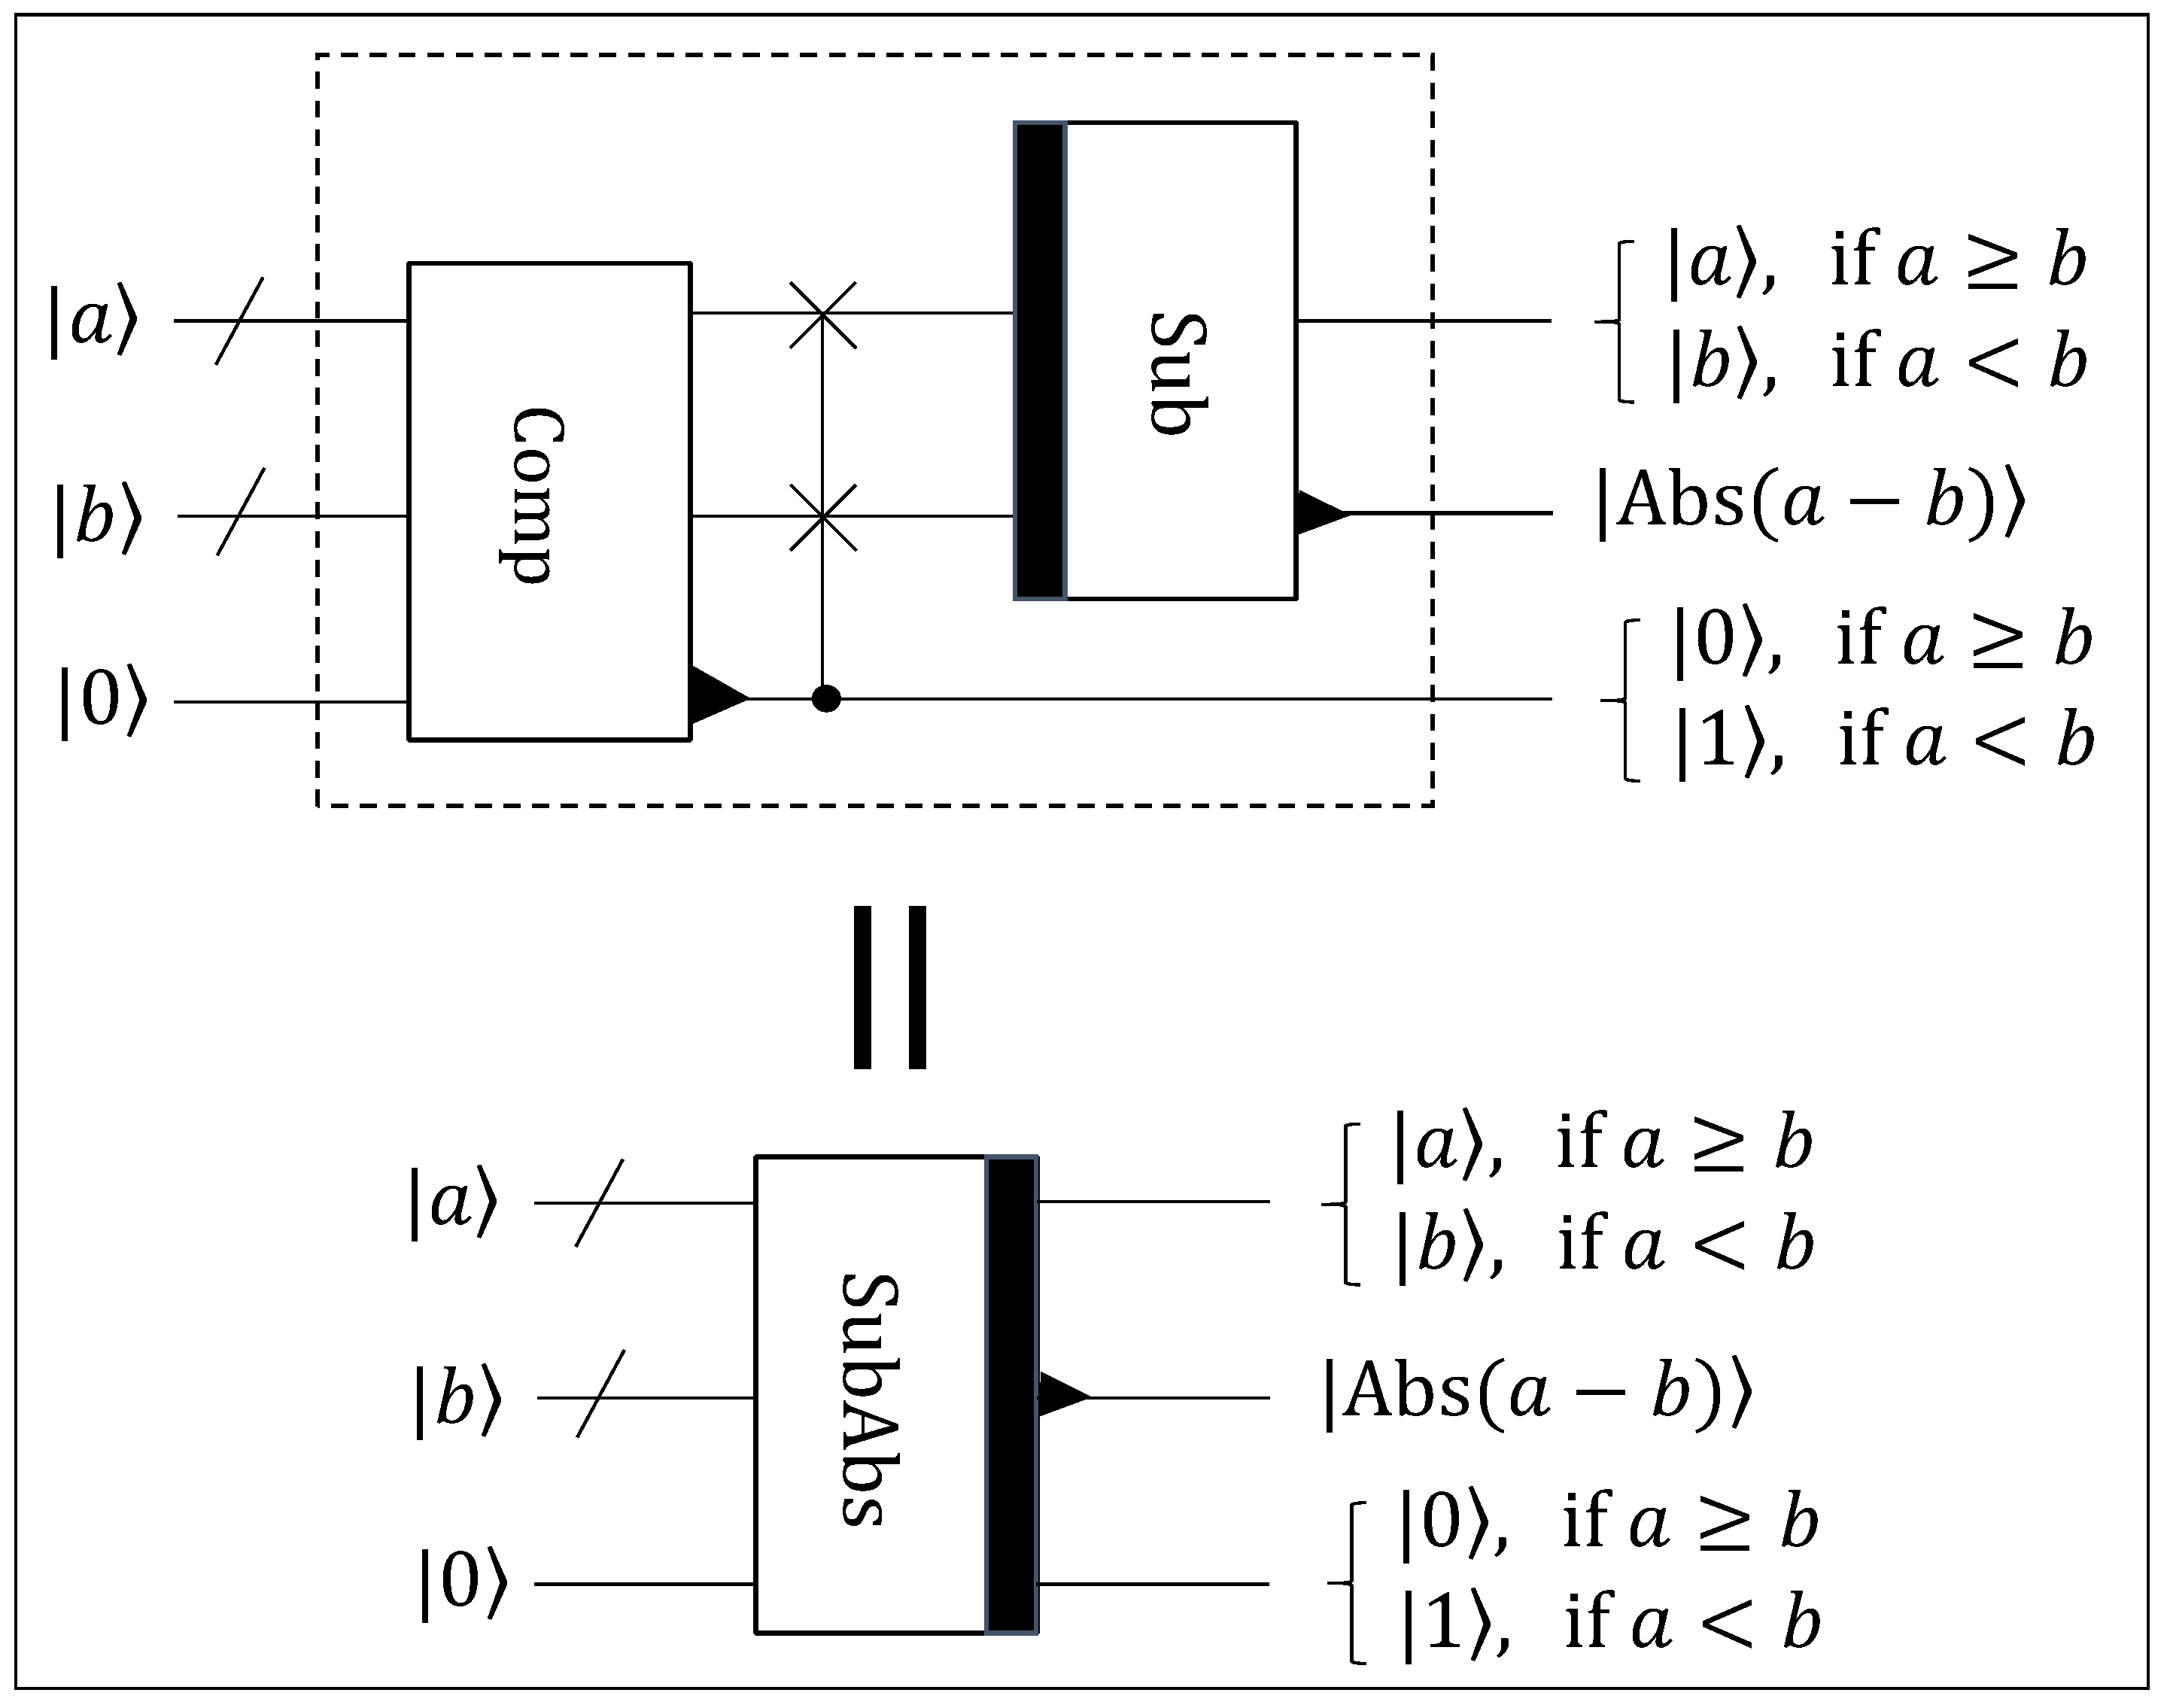
The quantum circuit of is depicted in Figure 6, and the correctness of the quantum circuit can be easily verified. As a result of the reversibility of unitary operations, by reversing the circuit of , that is, by applying each gate of the circuit in the reversed order, the quantum circuit of can be obtained.
Figure 6.
The quantum circuit of .
Note that one is composed of one comparison circuit and one subtraction quantum circuit. To compute the absolute value of the subtraction of two ℓ-bit inputs and , a total of qubits, Toffoli gates, and CNOT gates are required. The conclusion is also applicable to the inverse of , that is, .
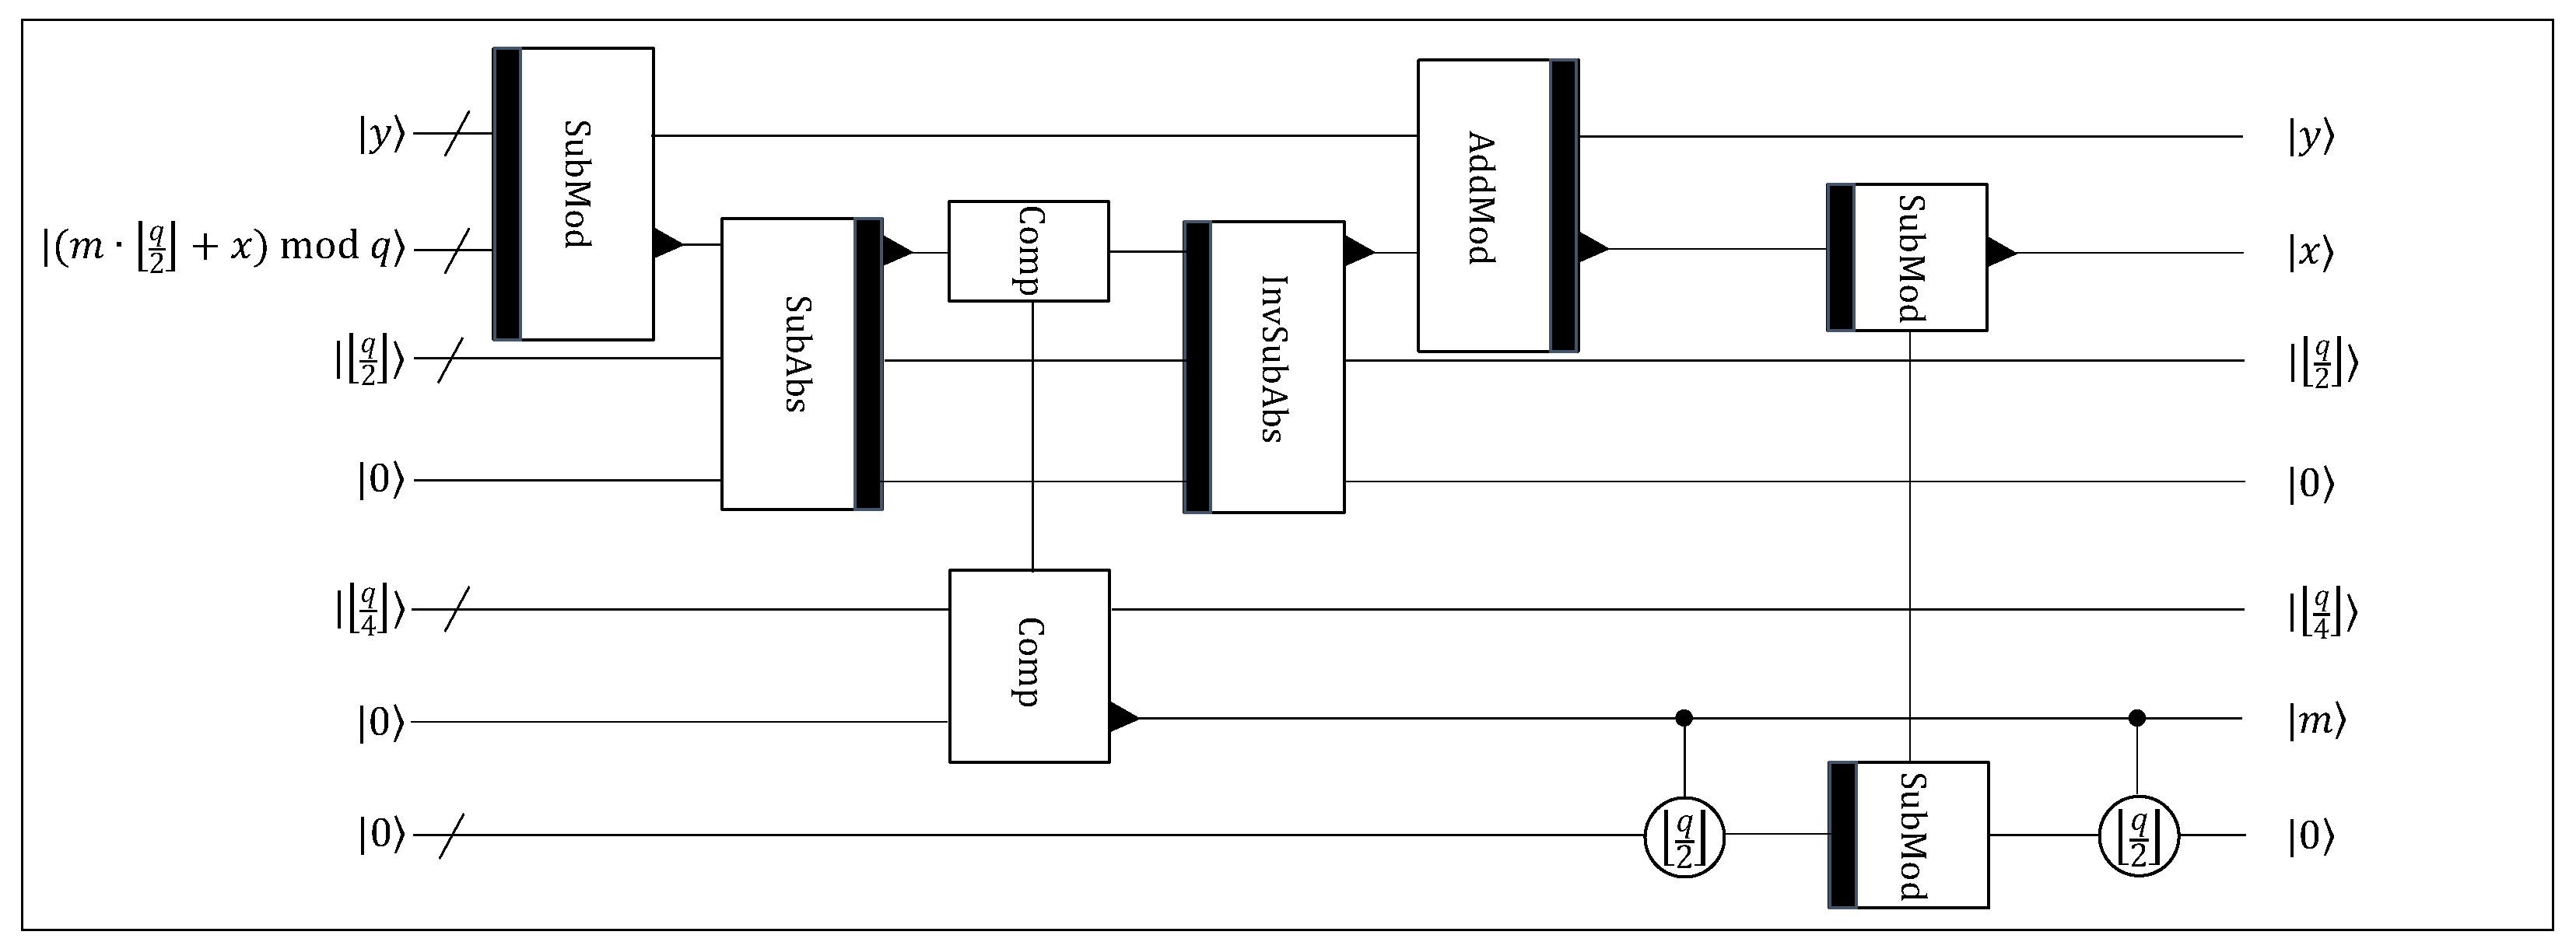
Using the quantum circuit and its reverse , we can provide particulars for the quantum circuit of which is depicted in Figure 7. Note that one is composed of two subtraction modular circuits, one quantum circuit of , one comparison quantum circuit, one quantum circuit of , one modular addition circuit, and two controlled copy quantum circuits. To decrypt one ciphertext that encrypts one qubit, a total of qubits, Toffoli gates, and CNOT gates are required.
Figure 7.
The quantum circuit of .
4.2. Complexity Analysis
To measure the complexity of a quantum circuit, we should consider the quantum resources required by the circuit.
Quantum resources. When analysing the complexity of a quantum circuit, a gate set that arises frequently and that has been studied often in the literature, but by no means the only conceivable gate set, is the so-called Clifford+T gate set. This gate set consists of the Hadamard gate, the phase gate, and the controlled NOT (CNOT) gate, along with the T gate. The Clifford+T gate set is known to be universal [18]. This comes from that any unitary operator can be accurately expressed using single-qubit gates and CNOT gates [29], and Hadamard gates, phase gates, and T gates can used to approximate any single-qubit gates with arbitrary precision [18]. In conclusion, these four types of quantum gates form a universal quantum gate group. As a result, when assessing the complexity of a quantum circuit, we need to compute the number of needed Hadamard gates, phase gates, CNOT gates, and T gates.
Quantum resources needed by and . In Section 4.1, we have concluded the following:
- To encrypt one qubit, a total of qubits, Toffoli gates, and CNOT gates are required.
- To decrypt one ciphertext that encrypts one qubit, a total of qubits, Toffoli gates, and CNOT gates are required.
According to [30], one Toffoli gate can be broken down into two Hadamard gates, one phase gate, seven T gates, and six CNOT gates. Furthermore, to save quantum resources, auxiliary bits can be reused according to the sequence of calculations in each circuit [19]. Based on the previous results and analysis, we estimate the quantum resources needed when encrypting one qubit quantum state with the algorithm and decrypting the corresponding ciphertext with the algorithm in our QIBE scheme, including the number of qubits and the number of Hadamard, phase, T, and CNOT gates. The result is shown in Table 1.
Table 1.
Quantum resource.
Note that our QIBE scheme can encrypt one qubit at a time. By integrating our scheme and the IBE scheme encrypting n-bit message (The IBE scheme is described in Appendix A), we can easily construct a new QIBE that can encrypt n-qubit at a time. It is evident that the quantum resources required by this new QIBE scheme increase linearly with the number of plaintext bits to be encrypted.
5. Conclusions and Future Work
In this paper, we proposed the first QIBE scheme based on the learning with errors problem. Then, we proved that our scheme is fully secure under the random oracle model. Furthermore, we explained that our scheme possesses the following advantages:
- The network security protocol with our QIBE scheme provides perfect forward secrecy. The ciphertext is transmitted in the form of a quantum state that is unknown to the adversary and cannot be copied and stored. Thus, in network security protocols based on our QIBE construction, the adversary cannot have access to any previous quantum ciphertext to decrypt and obtain the previous session key, even if the private identity key is threatened.
- Classic KGC systems still can be used in our QIBE scheme to generate and distribute private identity keys, thus reducing the cost when this scheme is implemented. The classic KGC systems can be used because the master public and secret keys of our scheme are both in the form of classic bits.
Finally, to analyse the realisability of this QIBE scheme, we provided particulars for the quantum circuits of and , and we analysed their required quantum resources for given numbers of qubits, Hadamard gates, phase gates, T gates, and CNOT gates. We concluded that the quantum resources required by our scheme increase linearly with the number of plaintext bits to be encrypted.
As aforementioned, network security protocols based on our QIBE scheme have forward secrecy, unlike the classic IBE. However, our QIBE scheme has certain drawbacks. In terms of quantum circuit realisation, we do not yet have a method to obtain the optimal circuit and find the lower bound of the quantum resources required by this scheme. Furthermore, this construction is a theoretical achievement, and any practical application remains a distant goal before the advent of universal quantum computers.
Our scheme is one of fifteen types of QIBE schemes described in Section 3.1, and the other fourteen types are yet to be studied. Therefore, the focus of our next work is to study and design the other fourteen types of QIBE schemes and their quantum circuit implementations, and to explore ways to find the lower bound of the quantum resources required by these schemes. Moreover, to make our scheme more practical, our next work includes making an implementation in Q# and providing a Github repository for it.
Author Contributions
Conceptualisation, W.G. and L.Y.; methodology, W.G.; formal analysis, D.Z; writing—original draft preparation, W.G; writing—review and editing, W.G., D.Z. and X.L.; supervision, L.Y.; funding acquisition, L.Y. All authors have read and agreed to the published version of the manuscript.
Funding
This work was supported by the National Natural Science Foundation of China (Grant No. 61672517), National Natural Science Foundation of China (Key Program, Grant No. 61732021).
Institutional Review Board Statement
Not applicable.
Informed Consent Statement
Not applicable.
Data Availability Statement
Not applicable.
Conflicts of Interest
The authors declare no conflict of interest.
Appendix A. Classic IBE Scheme
IBE encrypting one-bit message. In [9], Gentry et al. proposed the first lattice-based IBE scheme from the learning with errors problem. In this scheme, let integer parameters , where is a security parameter. This scheme can encrypt one bit once, and it can also encrypt n bits at a time. At first, we show the scheme which can encrypt one bit.
- (1) It runs to obtain a uniformly random matric and which is a good basis for . (2) Then, it selects a hash function which maps an identity to a vector. (3) Finally, it outputs and . (4) In summary, .
- : (1) On input , and an identity , it computes and generates such that . It is clear that . (2) In summary, .
- : (1) On input of an identity , , and a bit message , it first computes and chooses a uniformly random , and . (2) Then, it computes and , and sets , where . (3) In summary, .
- : (1) To decrypt a ciphertext using an identity secret key , it computes . (2) Then, it computes(3) Furthermore, it treats b as an integer in , and sets if ; otherwise, . (4) Finally, it returns the plaintext m. (5) In summary, .
Theorem A1.
Let integer parameters . Consider a cipertext
of one bit message m. Then, the decryption algorithm with the identity secret key can decrypt the ciphertext correctly with a probability .
IBE encrypting n-bit message. Then, we show the scheme that can encrypt more than one bit at a time.
- : (1) It runs to obtain a uniformly random matric and which is a good basis for . (2) Then, it selects a hash function which maps an identity to a matrix. (3) Finally, it outputs and . (4) In summary, .
- : (1) On input , , and an identity , it computes which is an -matrix. (2) It takes advantage of the algorithm to generate the identity secret key such that is composed of where is the i-th column of . It is easy to see that . (3) In a word, .
- : (1) On input of an identity , , and one n-bit message , it first computes and chooses a uniformly random , and . (2) Then, it computes and , and sets , where . (3) In summary, .
- : (1) To decrypt a ciphertext using an identity secret key , it computes . (2) Then, it computes(3) Furthermore, it treats each coordinate of as an integer in , and sets if , else . (4) Finally, it returns the plaintext . (5) In a word, .
Theorem A2.
Let integer parameters . Consider a cipertext
of n-bit message . Then, the decryption algorithm with the identity secret key can decrypt the ciphertext correctly with a probability .
References
- Shamir, A. Identity-Based Cryptosystems and Signature Schemes. In Advances in Cryptology, Proceedings of CRYPTO; Springer: Berlin/Heidelberg, Germany, 1984; Volume 196, pp. 47–53. [Google Scholar]
- Boneh, D.; Franklin, M.K. Identity-Based Encryption from the Weil Pairing. In Advances in Cryptology—CRYPTO 2001; Springer: Berlin/Heidelberg, Germany, 2001; Volume 2139, pp. 213–229. [Google Scholar]
- Boneh, D.; Boyen, X. Efficient Selective-ID Secure Identity-Based Encryption Without Random Oracles. In Advances in Cryptology—EUROCRYPT 2004; Springer: Berlin/Heidelberg, Germany, 2004; Volume 3027, pp. 223–238. [Google Scholar]
- Waters, B. Efficient Identity-Based Encryption Without Random Oracles. In Advances in Cryptology—EUROCRYPT 2005; Springer: Berlin/Heidelberg, Germany, 2005; Volume 3494, pp. 114–127. [Google Scholar]
- Cocks, C.C. An Identity Based Encryption Scheme Based on Quadratic Residues. In Cryptography and Coding, 8th IMA International Conference; Springer: Berlin/Heidelberg, Germany, 2001; Volume 2260, pp. 360–363. [Google Scholar]
- Boneh, D.; Gentry, C.; Hamburg, M. Space-Efficient Identity Based Encryption Without Pairings. In Proceedings of the 48th Annual IEEE Symposium on Foundations of Computer Science (FOCS’07), Providence, RI, USA, 21–23 October 2007; pp. 647–657. [Google Scholar]
- Jhanwar, M.P.; Barua, R. A Variant of Boneh-Gentry-Hamburg’s Pairing-Free Identity Based Encryption Scheme. In Information Security and Cryptology; Springer: Berlin/Heidelberg, Germany, 2008; Volume 5487, pp. 314–331. [Google Scholar]
- Joye, M. Identity-Based Cryptosystems and Quadratic Residuosity. In Public-Key Cryptography; Springer: Berlin/Heidelberg, Germany, 2016; Volume 9614, pp. 225–254. [Google Scholar]
- Gentry, C.; Peikert, C.; Vaikuntanathan, V. Trapdoors for hard lattices and new cryptographic constructions. In Proceedings of the 40th Annual Symposium on Theory of Computing, Victoria, BC, Canada, 17–20 May 2008; pp. 197–206. [Google Scholar]
- Cash, D.; Hofheinz, D.; Kiltz, E.; Peikert, C. Bonsai Trees, or How to Delegate a Lattice Basis. In Advances in Cryptology—EUROCRYPT 2010; Springer: Berlin/Heidelberg, Germany, 2010; Volume 6110, pp. 523–552. [Google Scholar]
- Agrawal, S.; Boneh, D.; Boyen, X. Efficient Lattice (H)IBE in the Standard Model. In Advances in Cryptology—EUROCRYPT 2010; Gilbert, H., Ed.; Springer: Berlin/Heidelberg, Germany, 2010; Volume 6110, pp. 553–572. [Google Scholar] [CrossRef] [Scilit]
- Xie, X.; Xue, R.; Zhang, R. Deterministic Public Key Encryption and Identity-Based Encryption from Lattices in the Auxiliary-Input Setting. In Security and Cryptography for Networks; Springer: Berlin/Heidelberg, Germany, 2012; Volume 7485, pp. 1–18. [Google Scholar]
- Yamada, S. Adaptively Secure Identity-Based Encryption from Lattices with Asymptotically Shorter Public Parameters. In Advances in Cryptology—EUROCRYPT 2016; Springer: Berlin/Heidelberg, Germany, 2016; Volume 9666, pp. 32–62. [Google Scholar]
- Shor, P.W. Polynomial-Time Algorithms for Prime Factorization and Discrete Logarithms on a Quantum Computer. SIAM J. Comput. 1997, 26, 1484–1509. [Google Scholar] [CrossRef] [Scilit]
- Chinese-State-Cryptography-Administration. Chinese SSL VPN Technology Specification. Available online: http://gmbz.org.cn/main/viewfile/20180110021416665180.html (accessed on 1 January 2022).
- Van Oorschot, P.C.; Menezes, A.J.; Vanstone, S.A. Handbook of Applied Cryptography; CRC Press: Boca Raton, FL, USA, 1996. [Google Scholar]
- Wootters, W.K.; Zurek, W.H. A single quantum cannot be cloned. Nature 1982, 299, 802–803. [Google Scholar] [CrossRef] [Scilit]
- Nielsen, M.A.; Chuang, I. Quantum Computation and Quantum Information; American. Assoc. Phys. Teach. 2002, 70, 558–559. [Google Scholar]
- Häner, T.; Jaques, S.; Naehrig, M.; Roetteler, M.; Soeken, M. Improved quantum circuits for elliptic curve discrete logarithms. In International Conference on Post-Quantum Cryptography; Springer: Berlin/Heidelberg, Germany, 2020; pp. 425–444. [Google Scholar]
- Cuccaro, S.A.; Draper, T.G.; Kutin, S.A.; Moulton, D.P. A new quantum ripple-carry addition circuit. arXiv 2004, arXiv:0410184. [Google Scholar]
- Liu, X.; Yang, H.; Yang, L. CNOT-count optimized quantum circuit of the extended Shor’s algorithm for ECDLP. arXiv 2021, arXiv:2112.11358. [Google Scholar]
- Roetteler, M.; Naehrig, M.; Svore, K.M.; Lauter, K. Quantum resource estimates for computing elliptic curve discrete logarithms. In Proceedings of the International Conference on the Theory and Application of Cryptology and Information Security, Hong Kong, China, 3–7 December 2017; pp. 241–270. [Google Scholar]
- Markov, I.L.; Saeedi, M. Constant-Optimized Quantum Circuits for Modular Multiplication and Exponentiation. Quantum Inf. Comput. 2012, 12, 361–394. [Google Scholar] [CrossRef] [Scilit]
- Ajtai, M. Generating Hard Instances of the Short Basis Problem; Springer: Berlin/Heidelberg, Germany, 1999; pp. 1–9. [Google Scholar]
- Alwen, J.; Peikert, C. Generating Shorter Bases for Hard Random Lattices; STACS Schloss Dagstuhl–Leibniz-Zentrum für Informatik: Dagstuhl, Germany, 2009; pp. 75–86. [Google Scholar]
- Regev, O. On lattices, learning with errors, random linear codes, and cryptography. STOC 2005, 56, 84–93. [Google Scholar]
- Wu, C.; Yang, L. A complete classification of quantum public-key encryption protocols. In Electro-Optical and Infrared Systems; International Society for Optics and Photonics: Bellingham, WA, USA, 2015; Volume 9648, p. 964818. [Google Scholar]
- Xiang, C.; Yang, L.; Peng, Y.; Chen, D. The classification of quantum symmetric-key encryption protocols. In Quantum and Nonlinear Optics III; International Society for Optics and Photonics: Bellingham, WA, USA, 2014; Volume 9269, p. 926909. [Google Scholar]
- Deutsch, D. Quantum theory, the Church–Turing principle and the universal quantum computer. Proc. R. Soc. Lond. A Math. Phys. Sci. 1985, 400, 97–117. [Google Scholar]
- Amy, M.; Maslov, D.; Mosca, M.; Roetteler, M. A meet-in-the-middle algorithm for fast synthesis of depth-optimal quantum circuits. IEEE Trans. Comput.-Aided Des. Integr. Circuits Syst. 2013, 32, 818–830. [Google Scholar] [CrossRef] [Scilit]
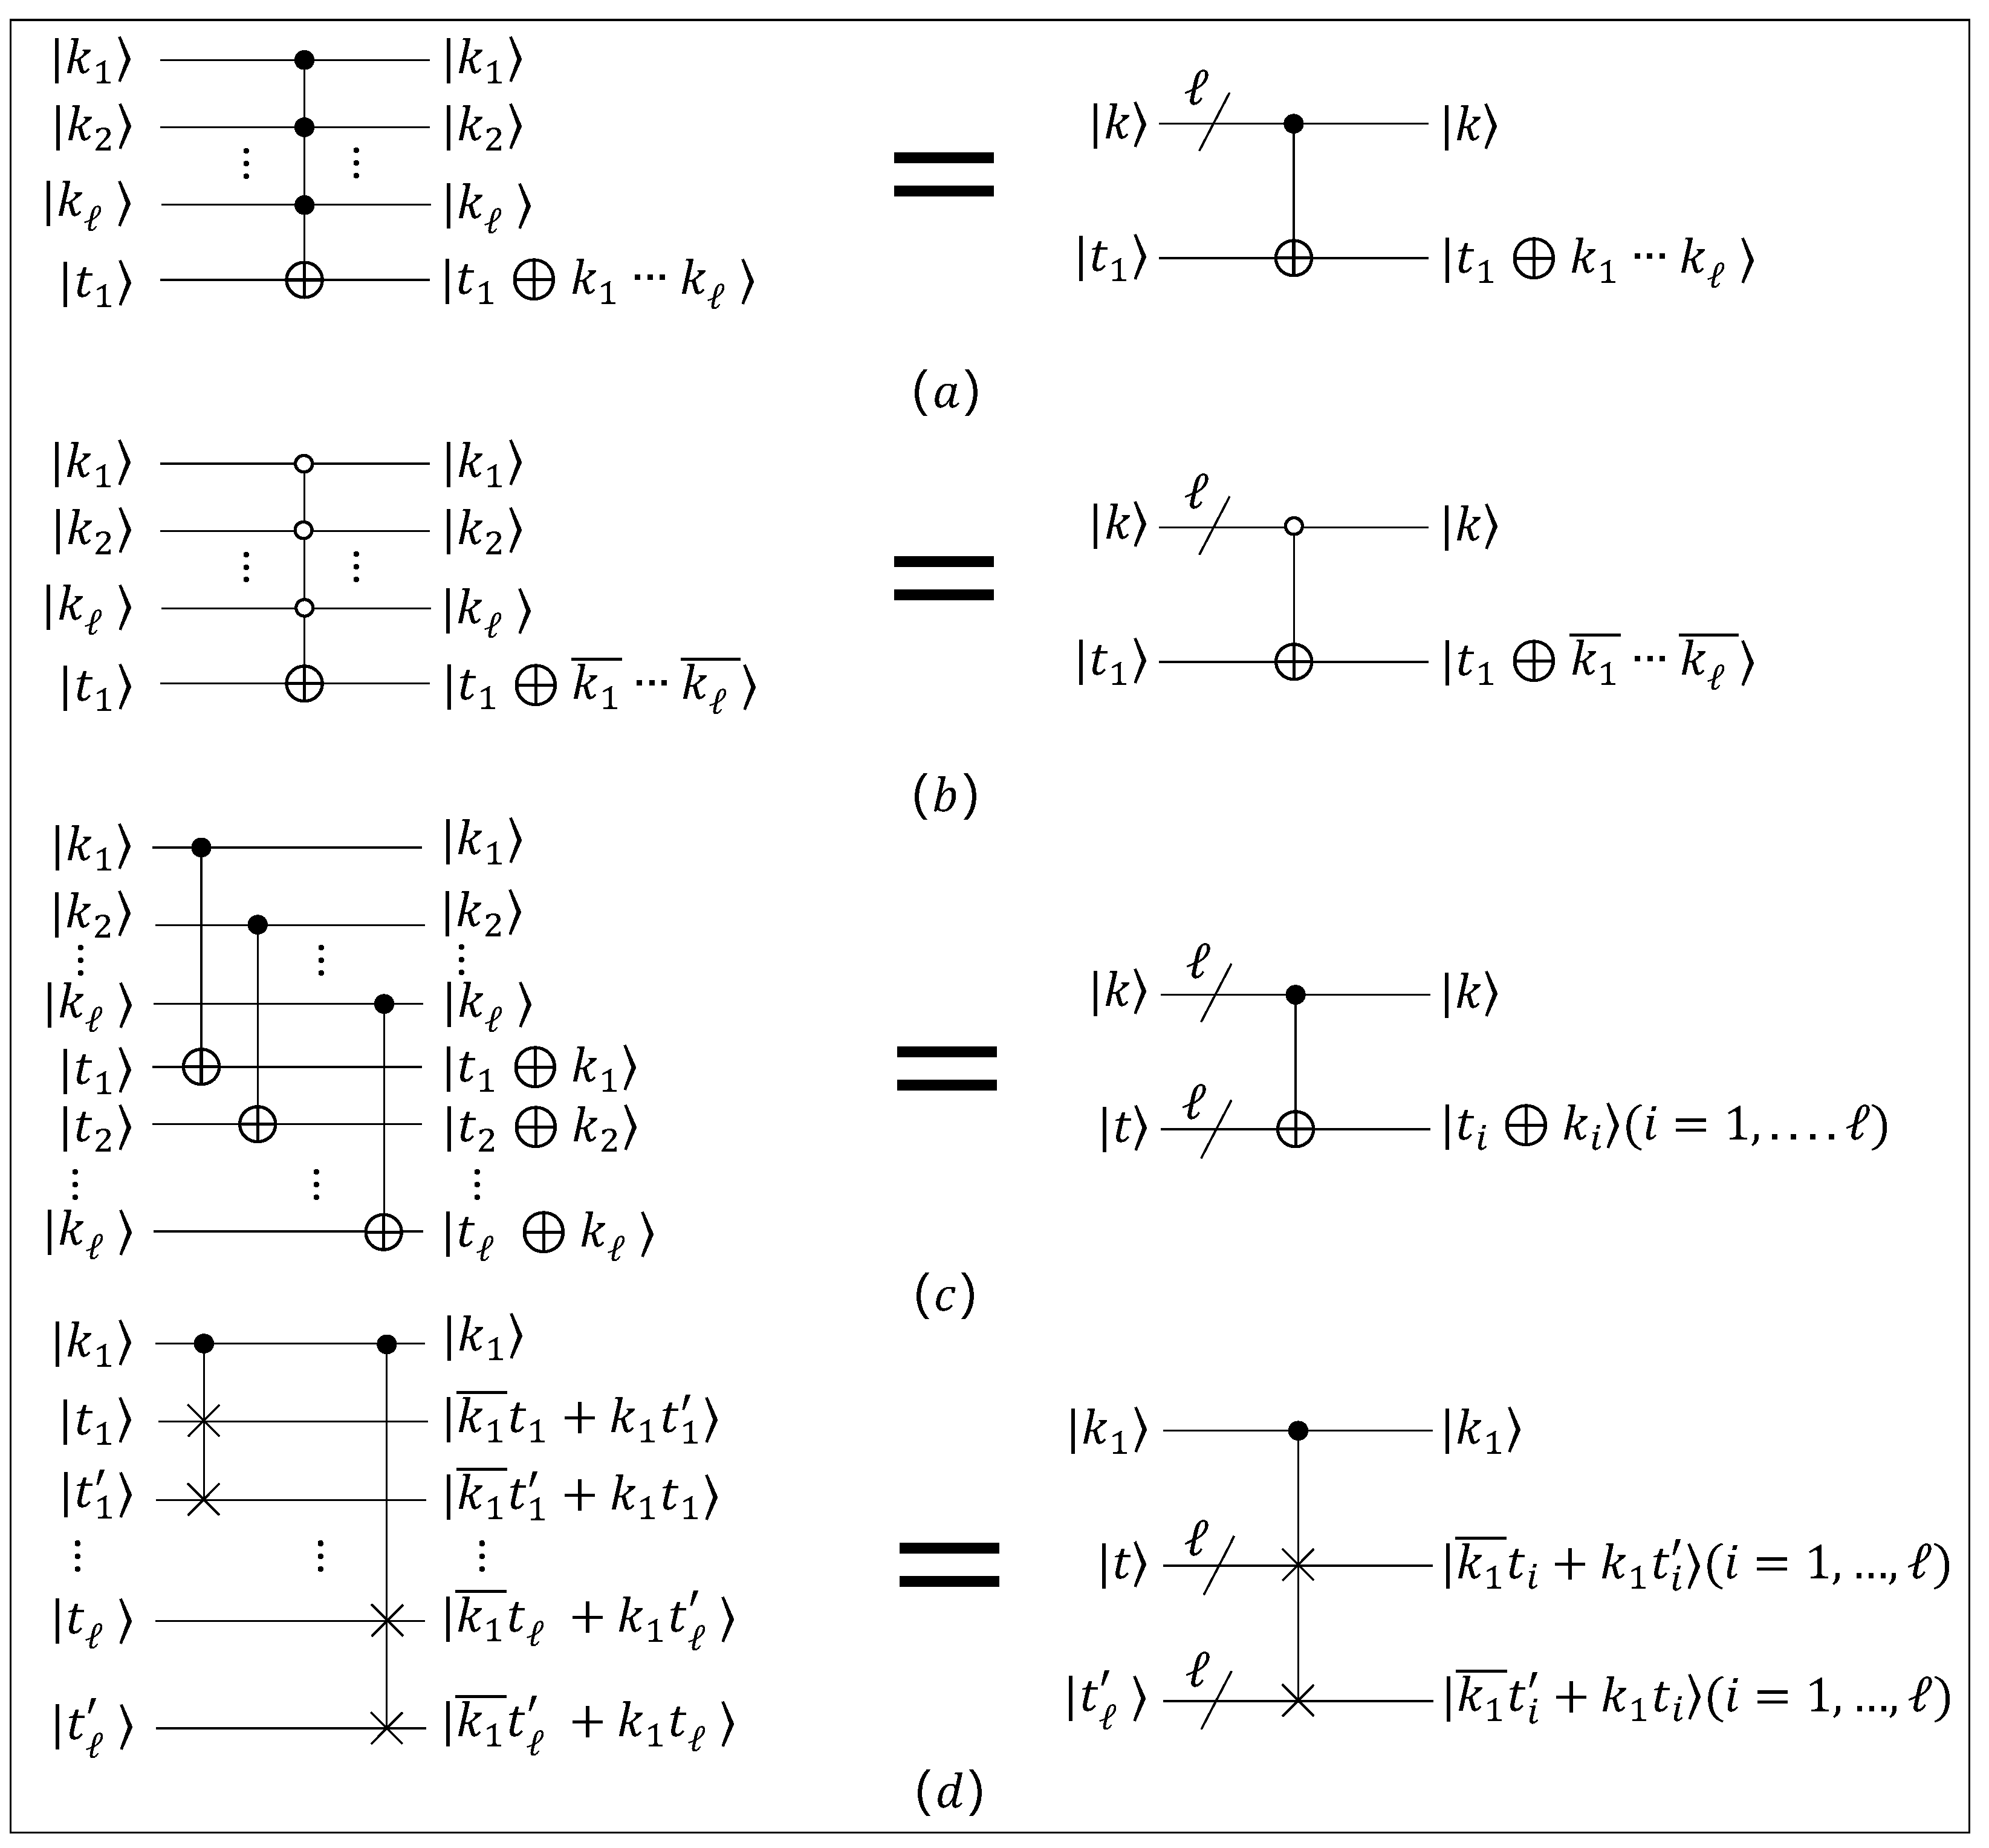
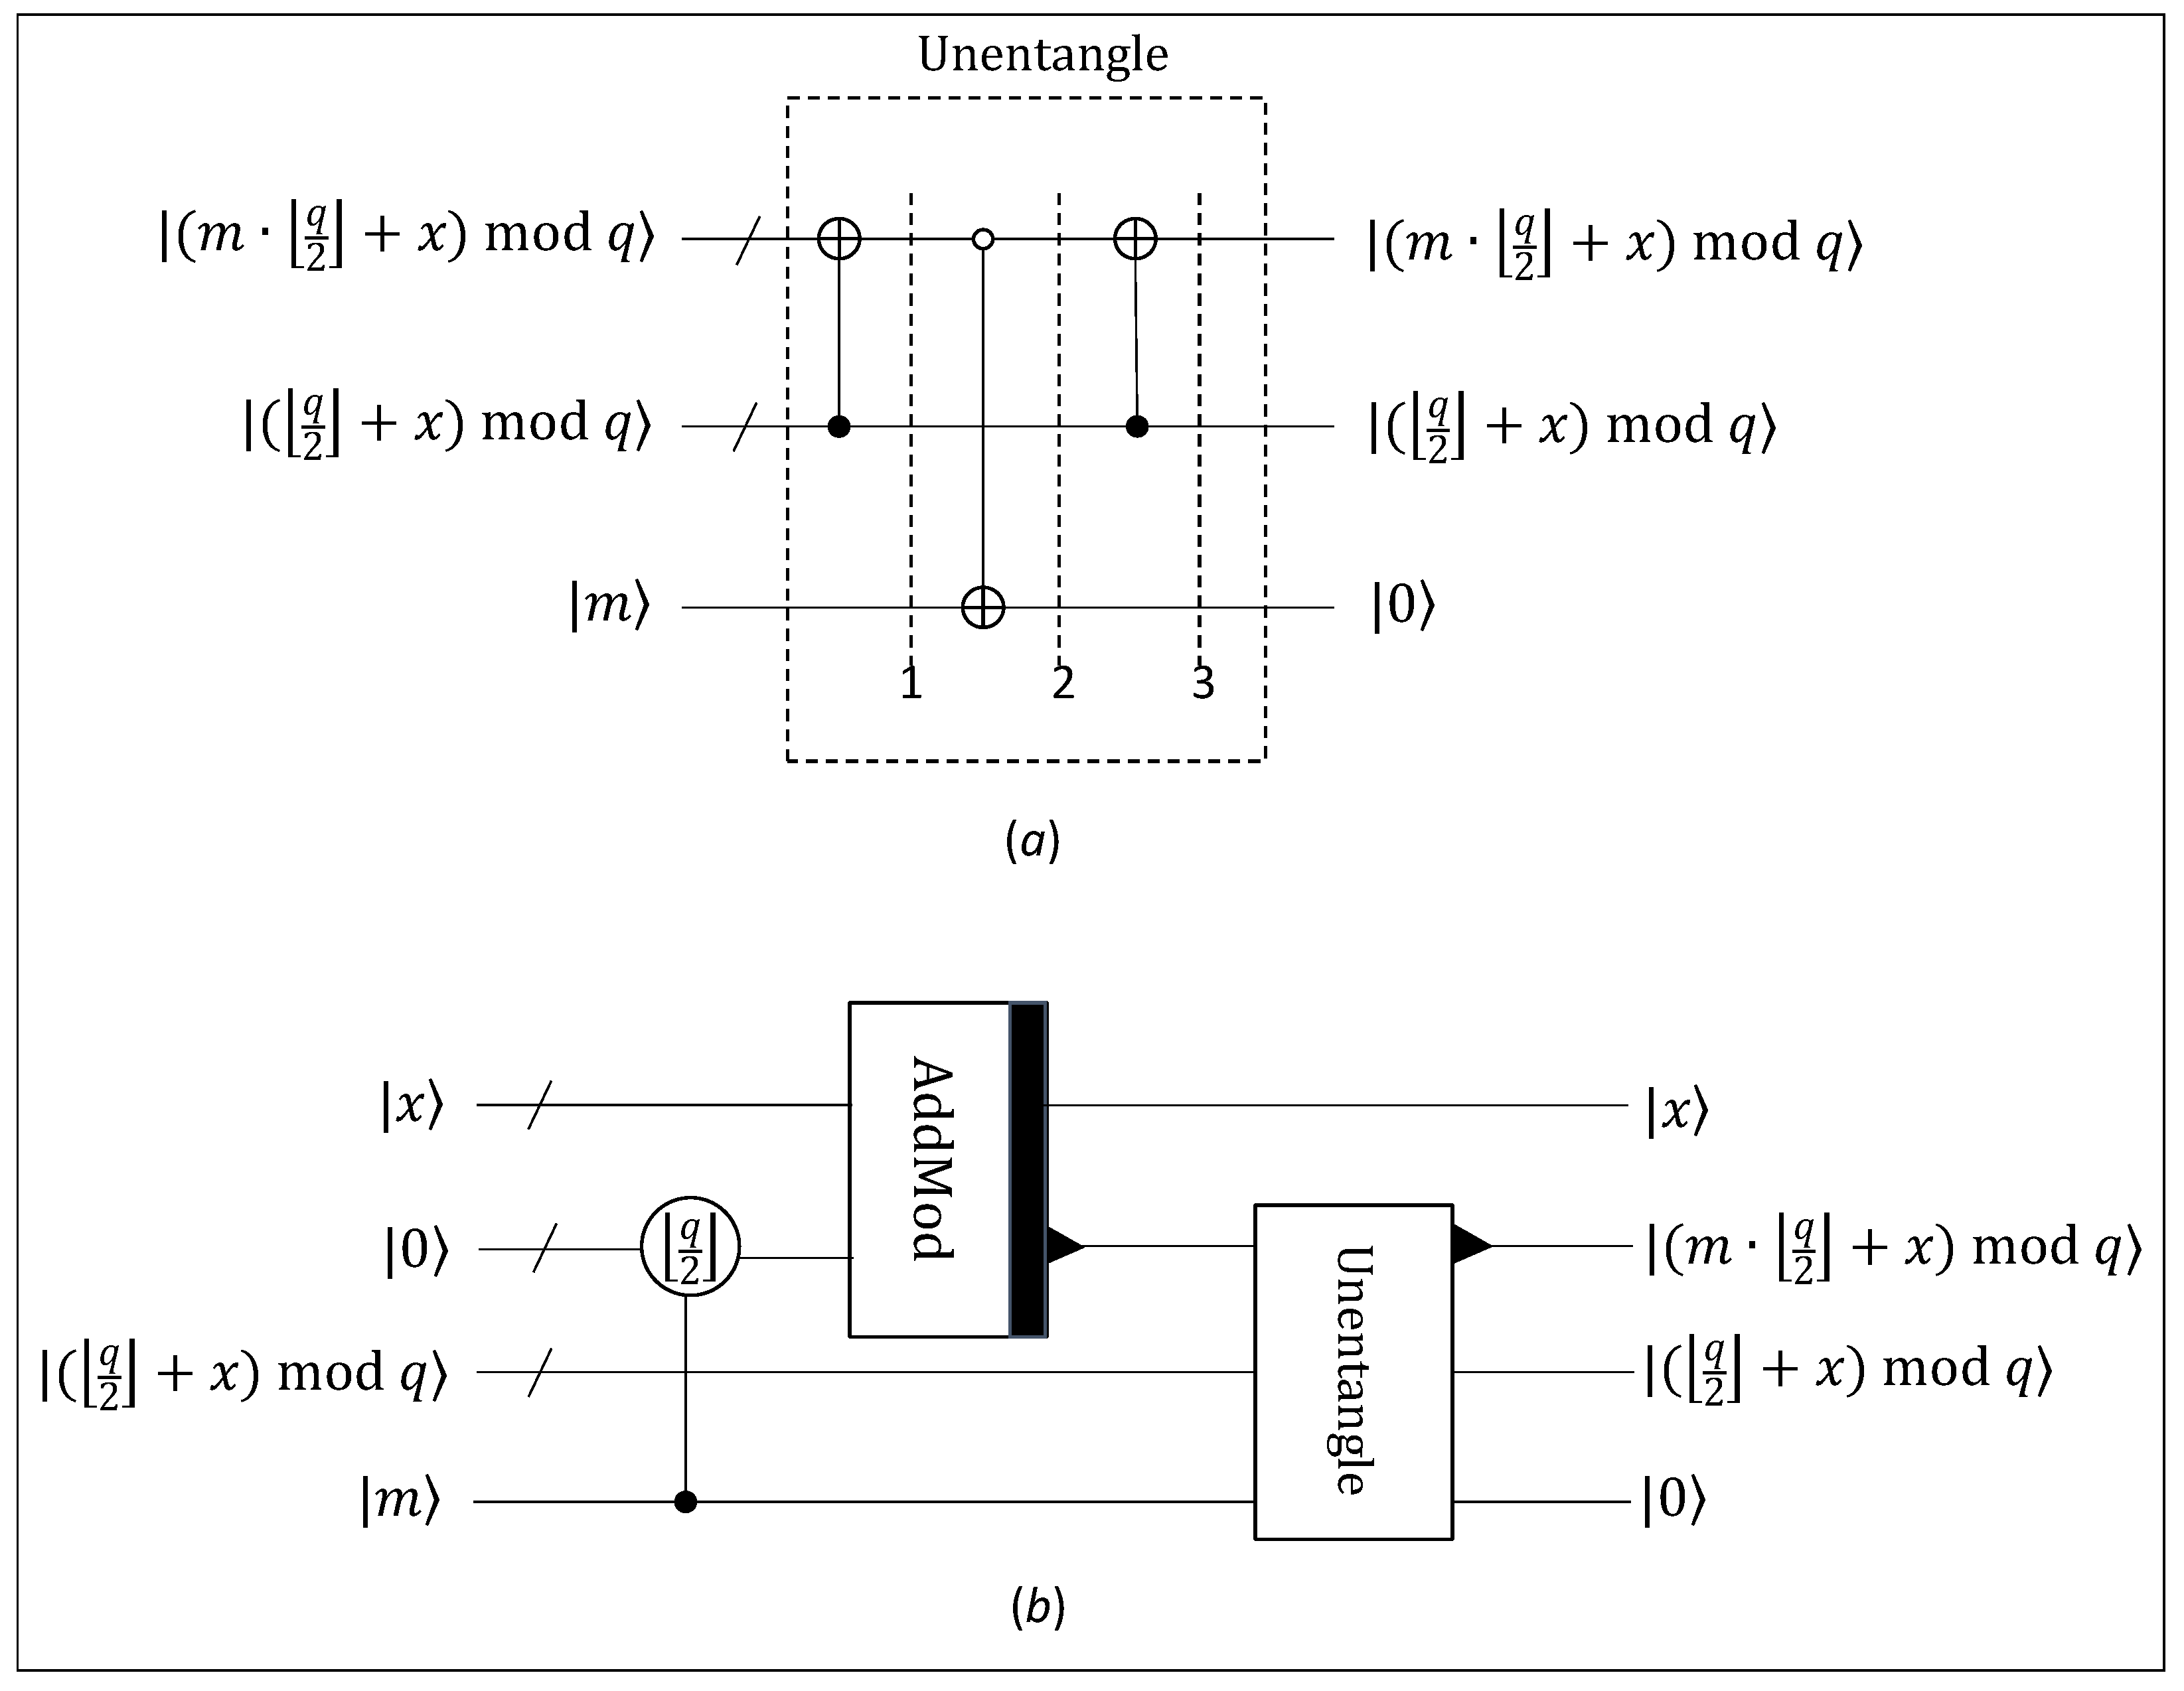

Publisher’s Note: MDPI stays neutral with regard to jurisdictional claims in published maps and institutional affiliations. |
© 2022 by the authors. Licensee MDPI, Basel, Switzerland. This article is an open access article distributed under the terms and conditions of the Creative Commons Attribution (CC BY) license (https://creativecommons.org/licenses/by/4.0/).