


Abstract
Cybersecurity in radio frequency (RF) technologies has become a critical concern, driven by the expansion of connected systems in urban and industrial environments. Although research on wireless networks and the Internet of Things (IoT) has advanced, comprehensive studies that provide a global and integrated view of cybersecurity development in this field remain limited. This work presents a scientometric and systematic review of international publications from 2009 to 2025, integrating the PRISMA protocol with semantic screening supported by a Large Language Model to enhance classification accuracy and reproducibility. The analysis identified two interdependent axes: one focusing on signal integrity and authentication in GNSS systems and cellular networks; the other addressing the resilience of IoT networks, both strongly associated with spoofing and jamming, as well as replay, relay, eavesdropping, and man-in-the-middle (MitM) attacks. The results highlight the relevance of RF cybersecurity in securing communication infrastructures and expose gaps in widely adopted technologies such as RFID, NFC, BLE, ZigBee, LoRa, Wi-Fi, and unlicensed ISM bands, as well as in emerging areas like terahertz and 6G. These gaps directly affect the reliability and availability of IoT and wireless communication systems, increasing security risks in large-scale deployments such as smart cities and cyber–physical infrastructures.
1. Introduction
The growing adoption of digital systems in critical infrastructures and urban ecosystems has intensified the global dependence on wireless communication systems [1,2,3,4,5]. In this context, cybersecurity in radio frequency (RF) technologies emerges as a strategic and interdisciplinary field, essential for strengthening the reliability of applications in the Internet of Things (IoT), Smart Cities, and Cyber–Physical Systems [6,7,8,9,10]. As connected devices take on vital functions in areas such as mobility, energy, healthcare, and public safety, the vulnerabilities of the electromagnetic spectrum become a critical factor for the technological resilience and digital sovereignty of nations and institutions [11,12,13,14,15]. Recent studies further emphasize that RF-based attacks can generate systemic risks for wireless and cyber–physical systems, particularly in safety-critical and mobility-oriented applications, reinforcing the need for structured frameworks to analyze vulnerabilities and mitigation strategies across communication layers [16,17].
In recent years, systematic reviews and scientometric studies have proven essential for understanding the evolution of emerging scientific fields and identifying relevant research gaps in cybersecurity [18,19,20,21,22]. Studies such as [23], which conducted a systematic review on radio frequency threats in connected medical devices (IoMT), highlight the severity of vulnerabilities in sensitive contexts such as digital health. Complementarily, refs. [24,25,26] conducted broad scientometric investigations on the Internet of Things, demonstrating the central role of RF based technologies in the expansion of the connected device ecosystem and the corresponding increase in attack surfaces.
Despite the advances achieved and the current stage of research, there is still no globally scoped study specifically dedicated to cybersecurity in radio frequency technologies. The literature remains fragmented, distributed across sectoral investigations and approaches limited to specific technologies or protocols [23,24,27], which hinders the formulation of an integrated view of the state of the art and the main trends in the field. Furthermore, there is a noticeable lack of comprehensive quantitative analyses capable of systematizing the evolution of scientific production on the topic, encompassing dimensions such as temporal growth, publication impact, institutional collaborations, and thematic areas.
In light of this scenario, the present article proposes a global scientometric analysis of research on RF technology cybersecurity. The study systematizes and examines publications indexed in international databases with the objective of providing a detailed view of the temporal dynamics, scientific impact, collaboration networks, and research trends that characterize this domain. By identifying patterns of production and co-authorship, as well as areas of specialization and growth, this work contributes to mapping and understanding the scientific evolution of RF cybersecurity, offering valuable insights for advancing new investigations and strengthening digital resilience in connected communication ecosystems.
Although this study provides a global scientometric perspective on cybersecurity in radio frequency technologies, many of the technologies and threats examined, such as spoofing, jamming, replay, relay, and eavesdropping, have direct implications for wireless embedded systems, IoT devices, smart infrastructure, and low-power wireless networks. To address this, this study combines scientometric analysis with the classification of cyberattack types across different RF-based wireless technologies. This integrative approach helps to identify cybersecurity priorities for IoT environments and wireless applications that rely on RF technologies, providing a foundation for future studies aimed at developing more resilient and secure communication architectures.
In this context, the main contribution of this study lies in strengthening existing and emerging cybersecurity frameworks for RF-based systems by providing a structured and evidence-based overview of how vulnerabilities, attack types, and affected technologies are distributed across the literature. By synthesizing fragmented research into a coherent scientometric and systematic perspective, the study helps clarify where current RF security frameworks are well supported by evidence and where significant gaps remain for IoT, wireless communications, and cyber–physical systems.
Unlike prior review studies that primarily address specific protocols, application domains, or individual attack classes, this work adopts an explicitly RF-centric perspective and integrates large-scale scientometric analysis with systematic attack classification across heterogeneous wireless technologies. This combination enables a cross-domain view of RF cybersecurity that goes beyond isolated technological contexts and is not commonly articulated in existing surveys.
Based on these objectives, the following research questions (RQs) were formulated to guide the analysis and systematic mapping of the field:
- RQ1:
- How has the scientific production of cybersecurity in RF technologies evolved during the period from 2009 to 2025?
- RQ2:
- Which countries, institutions, authors, and collaboration networks stand out as the main contributors to the advancement of the field?
- RQ3:
- Which journals and articles exhibit the highest impact and influence in consolidating research on RF technology cybersecurity?
- RQ4:
- What thematic and technological trends are shaping the future of research in RF cybersecurity?
- RQ5:
- Which types of RF-based attacks have received greater attention in the scientific literature?
- RQ6:
- Which RF technologies are most frequently associated with cybersecurity research?
2. Materials and Methods
The methodology of this study combines classical and well-established principles of systematic review and scientometric analysis with automated screening techniques based on Large Language Models (LLMs). The process was designed in accordance with the PRISMA 2020 protocol (Preferred Reporting Items for Systematic Reviews and Meta-Analyses) [28], using the Bibliometrix v5.1.1 package [29] for R language v4.4.3 and a Python v3.12.3 script integrated with the OpenAI API with the GPT-4o-mini model for the semantic screening stage assisted by artificial intelligence (AI) [30,31,32,33,34].
The overall methodological process comprised the following main steps:
- 1.
- Formulation of the search strategy and construction of the query strings;
- 2.
- Data collection from the Scopus and Web of Science databases;
- 3.
- Standardization and deduplication using Bibliometrix;
- 4.
- Preliminary manual screening;
- 5.
- Automated semantic screening via LLM;
- 6.
- Human-in-the-loop validation.
Figure 1 provides an overview of the methodological flow, highlighting the integration between the traditional review stages and the AI-assisted semantic classification process.
Figure 1.
Procedures for article acquisition and screening according to the PRISMA 2020 protocol, including the semantic screening assisted by LLM (highlighted in red).
This methodological integration is justified by the efficiency suggested in recent studies on the use of LLMs for automated screening and by the need to handle large volumes of scientific publications [35,36]. Evidence indicates that incorporating LLMs into systematic reviews can reduce analysis time and increase accuracy while maintaining the traceability of results [32,37,38].
The following subsections detail the methodological procedure adopted, covering the stages of search, acquisition, screening, and LLM-assisted validation.
2.1. Search Strategy and Article Acquisition
The formulation of the search strategy aimed to identify publications that address the intersection between cybersecurity and radio frequency communication technologies. This stage is methodologically critical, as it defines the scope, representativeness, and reproducibility of the corpus, reinforcing the consistency of the scientometric results and the transparency of the review process [29,39].
The search string was structured into three conceptual blocks:
- Cybersecurity and threat-related terms, encompassing cybersecurity, attack, vulnerability, threat, spoofing, replay, eavesdropping, man-in-the-middle, jamming, among others;
- RF technologies and protocols, including Bluetooth, BLE, ZigBee, Wi-Fi, LoRa, RFID, NFC, NB-IoT, LTE, 5G, GNSS, V2X, DSRC, UWB, and Satellite IoT, among others;
- Frequency bands used as technical descriptors of technologies without explicit citation of a protocol (13.56 MHz, 433 MHz, 868 MHz, 2.4 GHz, 5.8 GHz, 24 GHz, 76 GHz, 81 GHz), among others.
To minimize potential evaluation biases, semantic proximity operators (W/n in Scopus and NEAR/n in Web of Science) were applied to restrict the inclusion of generic frequency unit mentions only when associated with cybersecurity-related terms. The relevance and comprehensiveness of the strategy were corroborated through comparisons with previous reviews [23,24,25,26] and expanded to include IoT protocols, vehicular networks, and RF-based sensing systems. The complete search string and the grouping of descriptors are presented in Appendix A.
The document collection was conducted on 25 August 2025, using the Scopus and Web of Science databases. The selection of these databases aligns with previous studies that emphasize their complementarity and importance for systematic reviews [40,41]. In Scopus, 6284 records were retrieved, of which 4220 were excluded for not meeting the language and document-type criteria, including conference papers, book chapters, reviews, books, editorials, and publications in other languages. This reduction was also influenced by a temporary technical limitation in Scopus at that time, which restricted the maximum download to 5000 records per query. After the exclusions, 2163 scientific articles in English remained.
In the Web of Science database, 2514 records were initially retrieved; after excluding review articles, book chapters, editorial materials, early access papers, and retracted articles, 2415 documents remained. The combined set of articles from both databases was subsequently processed in RStudio using the remove.duplicated() function from the Bibliometrix package, resulting in 2364 unique scientific documents after deduplication. Next, a manual screening of metadata (from magazines without DOI, keywords, and affiliations) was performed, leading to the exclusion of 216 additional records and yielding a total of 2148 valid articles for the LLM-assisted semantic screening.
The review protocol was registered in the Open Science Framework (OSF) prior to the submission of this manuscript. The full protocol, the minimal documented triage script, and the final deduplicated dataset are publicly available at the following link: OSF Registration ID: https://osf.io/bqx7n/ (accessed on 11 December 2025).
2.2. Selection and Screening
Following the PRISMA 2020 protocol, the 2148 articles were subjected to two stages: (i) manual screening of titles, abstracts, and keywords according to the inclusion and exclusion criteria, and (ii) AI-assisted semantic screening (Python + OpenAI API), employed to confirm thematic relevance and reduce false positives. Figure 2 presents the adapted PRISMA flow diagram, highlighting the automated screening stage.
Figure 2.
Adapted PRISMA 2020 flow diagram, highlighting the LLM-assisted screening stage.
Figure 2 illustrates the inclusion of the LLM-assisted screening (highlighted in red), showing the number of automatic exclusions and subsequent manual reviews. The automated process also identified and removed records incorrectly classified as “Articles” under the DT tag, which in fact corresponded to reviews, as well as detected and eliminated retracted papers. This process comes after the manual screening procedure (highlighted in blue), which is an intrinsic step in PRISMA 2020 protocol.
After executing the automated process, 1462 articles were classified as out of scope, leaving 582 directly relevant and 104 labeled as “maybe”. The latter were manually re-evaluated, resulting in the inclusion of 96 articles that demonstrated a direct relationship between cybersecurity and radio frequency. The final corpus comprises 678 articles (7.7% of the initial total), published between 2009 and 2025.
It is important to clarify that the inputs analyzed in this study do not correspond to raw RF sensing data or physical signal measurements. Instead, the analysis relies on structured evidence extracted from peer-reviewed publications, including reported attack types, affected RF technologies, and application or experimental contexts described by the original authors. Consequently, signal-level characteristics such as sampling rates or noise distributions are not directly applicable. The representativeness of the analysis is therefore grounded in the diversity and scale of the scientific corpus, which spans multiple RF technologies and application domains, enabling the identification of systemic trends, research gaps, and recurring vulnerability patterns in RF cybersecurity.
In contrast to conventional systematic reviews that rely predominantly on keyword-based filtering and fully manual screening, the methodology adopted in this study incorporates an AI-assisted semantic screening stage. This design choice is particularly relevant for RF cybersecurity research, where heterogeneous terminology across technologies, attack types, and application domains can limit the effectiveness of purely lexical approaches [30,32]. By prioritizing semantic relevance while remaining aligned with the PRISMA 2020 framework, the proposed method supports improved scalability and consistency in large-scale literature screening.
2.3. LLM-Assisted Semantic Screening and Decision Rules
The semantic screening was performed using the Python RF Cybersecurity script, which integrates context retrieval (Retrieval-Augmented Generation—RAG) and contextual classification based on an LLM [35]. The process was executed locally using the official OpenAI API with the GPT-4o-mini model, without any training or fine-tuning stages.
Figure 3 presents the flowchart of the automated LLM-based semantic screening process and the human-in-the-loop validation stage.
Figure 3.
Flowchart of the LLM-assisted semantic screening and human-in-the-loop validation process. The workflow integrates RAG-based context construction, A–B–C checklist classification, supervised iterative prompt adjustment, and reliability assessment ().
The execution flow comprised: (i) extraction of article metadata (title, abstract, and keywords) from the exported spreadsheets; (ii) data enrichment via the Crossref and Unpaywall APIs; (iii) context construction using ±420-character windows around terms related to RF and cybersecurity; and (iv) querying the Chat Completions API (/v1/chat/completions), employing prompt engineering based on the A–B–C checklist.
During this stage, the model simultaneously performed semantic classification and structured extraction of thematic evidence, populating fields such as RF_Technology, Protocol_Frequency, RF_Attack_Threat_Vulnerability, Application_Example, as well as IoT_Devices. These data were recorded in spreadsheets (.XLSX, .CSV) and served as the basis for the analyses presented in Section 4.1, Section 4.2 and Section 4.3.
The GPT-4o model, as described by [32], is an LLM based on a transformer architecture capable of estimating conditional probabilities of token sequences given a context. It is a model that is pretrained on large volumes of textual data that, in this study, was guided through prompt engineering, explicitly incorporating the defined inclusion and exclusion criteria [42,43,44]. This configuration enabled the model to operate as a contextualized classifier, maintaining decision traceability based on the full content of the articles. In the present study, the model operated under a few-shot learning regime without any additional retraining. Controlled (temperature=0.0, max_tokens, stop_token) were adopted to ensure more stable and auditable outputs (minimizing randomness across executions).
The adoption of the Chat Completions API, replacing the legacy Completions API, enabled structuring the interaction in a message-based format (system and user), allowing for more robust contextual instructions and greater output control. The responses were returned in JSON format, containing fields such as Cybersecurity_RF, RF_Technology, RF_Attack_Threat_Vulnerability, Evidence_Type, Confidence, Checklist_RF, as well as Checklist_Security. This arrangement standardizes the result structure and ensures traceability and reproducibility (field mapping and version control of the .XLSX and .CSV spreadsheets).
The inclusion and exclusion criteria were previously defined and applied uniformly throughout the entire screening process to ensure objectivity, consistency, and traceability of the results [32,45].
Four central axes were considered to determine the relevance of the articles to the analytical corpus: (i) evidence of RF technology: explicit mention of wireless communication protocols or technologies such as ZigBee, Bluetooth Low Energy (BLE), Wi-Fi, LoRa/LoRaWAN, RFID/NFC, GNSS, LTE/5G/6G, ISM band, UWB, V2X, and satellite systems; (ii) evidence of cybersecurity: presence of cyberattacks, threats, or defense mechanisms such as jamming, spoofing, replay, relay, eavesdropping, man-in-the-middle, and injection; (iii) direct link between RF and cybersecurity: the vulnerability or attack occurs at the physical communication channel, directly exploiting the radio frequency spectrum; and (iv) practical or experimental approach: use of testbeds, simulations, SDR devices (HackRF, USRP, RTL-SDR), or software tools such as GNU Radio.
Studies focused solely on performance (QoS), energy efficiency, antennas, propagation, or energy harvesting were excluded, as well as works addressing logical security (encryption/authentication) without relation to the RF channel. Articles dealing with purely non-RF protocols (such as standalone TCP/IP) and studies of side-channel attacks based on passive measurements that do not exploit the wireless communication medium were also removed.
The inclusion, exclusion, or review decision was automated through a binary A–B–C heuristic: (A) presence of evidence of RF technology; (B) presence of evidence of cybersecurity; (C) direct link between both. For each article, the LLM assigned binary scores (1 = present, 0 = absent), generating a score equals . The decision rules were as follows: score 3 () for YES; score 2 () for MAYBE; and score 1 or 0 () for NO.
All “MAYBE” articles were manually reviewed under the human-in-the-loop approach, which also included random samples from the “YES” and “NO” categories. This procedure ensured the accuracy of the classifications and enabled the iterative refinement of the prompt until stable behavior consistent with the study’s methodological guidelines was achieved [35,38,46].
2.4. Reliability, Validation, and Prompt Refinement
The human-in-the-loop validation was conducted at two levels: (i) full review of the articles classified as “MAYBE” (); and (ii) random verification of “YES” () and “NO” () samples. This dual-check procedure made it possible to assess the stability of the classifications and to reduce false positives and false negatives. A false positive was defined as any article initially classified as “YES” by the model but, after manual analysis, found to have no effective connection between cybersecurity and radio frequency. Similarly, false negatives corresponded to articles classified as “NO” by the LLM but later validated as relevant.
These observations align with recent evidence on the use of LLMs in systematic reviews, which report high levels of accuracy, although they still rely on human supervision for bias mitigation and quality control [47,48]. In the present study, semantic screening was implemented in Python, integrating RAG and contextual classification based on an LLM. The model analyzed metadata, excerpts retrieved from external databases, and, when available, the full text of the articles, thereby enhancing methodological traceability and reproducibility.
The agreement between the LLM and the human review was measured using Cohen’s kappa coefficient () [49], which is commonly applied in systematic screenings involving LLMs [30,33,38,50]. The coefficient is defined as:
where:
- represents the proportion of observed agreement between the model and the human review;
- corresponds to the agreement expected by chance.
In this study, the observed values were , e , indicating an almost perfect agreement according to the criteria of [49]. The procedures used to derive the observed agreement () and the expected agreement by chance (), including the class distributions and validation samples underlying these values, are detailed in Appendix C. Similar results were reported by [38,50], who also applied the kappa coefficient in validations of LLM-assisted classifications, achieving substantial levels of agreement between human and automated evaluators.
During the development of the semantic screening stage, multiple versions of the prompt were tested, varying in the formulation of instructions, the structure of the A–B–C checklist, and the number of few-shot examples. Each version was applied to sample subsets (Sample, n) of the corpus, allowing for comparison between the performance of automated classifications and human decisions. Table 1 presents the evolution of the prompt versions and the corresponding observed (Agreement, %) and adjusted () agreement indices between the LLM and human validation. The samples ranged from 200 to 554 articles, balanced among the “YES,” “MAYBE,” and “NO” categories, ensuring statistical representativeness and consistency in the comparative evaluation.
Table 1.
Evolution of prompt refinement and comparative agreement between the LLM and human validation.
The progressive refinement of the prompt led to a substantial increase in agreement with human decisions, reaching in the final version. This result demonstrates stable and semantically consistent model behavior, showing that the supervised calibration process (human-in-the-loop) was effective at reducing ambiguities and aligning the automatic inferences with the methodological criteria of the study.
By combining classical scientometric principles with artificial intelligence, this study demonstrates the potential of LLM-assisted approaches to make systematic reviews more accurate, transparent, and reproducible [38,51,52].
3. Scientometric Analysis Results
3.1. General Information of the Corpus
Table 2 presents the general information of the bibliometric analysis, providing a comprehensive overview of the temporal evolution, productivity, and scientific collaboration in the field of cybersecurity applied to radio frequency technologies. The period considered covers publications from 2009 to 2025, totaling 678 documents distributed across 234 scientific sources. These numbers indicate that the topic has consolidated in recent years, following the expansion of the Internet of Things ecosystem [25,26,53] and the growing concerns about the security of connected devices [7,27,54,55,56,57,58].
Table 2.
Main information about the dataset.
The average annual growth rate of 28.01% highlights the rapid rise and recent relevance of the field in the international literature. The set of 1790 authors and the average of 4.12 co-authors per article reflect a collaborative and multidisciplinary pattern typical of consolidating research areas. Furthermore, the international co-authorship rate of 16.22% indicates the expansion of research networks and the strengthening of global partnerships among universities and specialized centers.
In summary, the data presented in Table 2 show that RF cybersecurity has emerged as a rapidly expanding scientific domain, characterized by thematic diversity, growing academic impact, and strong international cooperation. This initial overview establishes the foundation for the subsequent analyses on productivity, collaboration networks, and thematic trends.
3.2. Evolution of Scientific Production
Figure 4 shows, in blue, the annual evolution of scientific production on cybersecurity in radio frequency technologies between 2009 and 2025. The number of publications has grown continuously, with a particularly pronounced acceleration after 2018, when the topic began to receive greater attention from the scientific community. This trend is commonly associated with the increasing number of IoT devices and the consequent expansion of attack surfaces in connected systems [6,58,59,60,61,62,63].
Figure 4.
Annual scientific production.
The marked increase in publications observed after 2018 can be attributed to a set of converging technological and contextual factors rather than to the initial emergence of IoT or smart city concepts. While these paradigms predate this period, the years following 2018 correspond to their large-scale operational deployment, higher device density, and growing dependence on RF-based communications in critical urban and industrial systems [5,6]. In particular, the widespread adoption of LPWAN technologies operating in unlicensed spectrum, together with the commercial rollout of 5G networks, introduced new scalability, latency, and connectivity paradigms, significantly expanding the RF attack surface [11]. These developments help explain the sustained growth in scientific output related to RF cybersecurity observed in Figure 4.
This evolution reflects a growing research focus on the security of wireless networks, RF protocols, and critical devices, with particular emphasis on applications in smart cities, critical infrastructures, and industrial systems [7,64,65,66,67,68,69]. The observed growth pattern further suggests the consolidation of RF cybersecurity as an emerging interdisciplinary core that bridges electrical engineering, computer science, and applied cybersecurity [58,70,71,72,73].
Also in Figure 4, the orange curve represents the projection of future production, obtained using a second-degree polynomial regressor with parameters , , and , resulting in . The model estimates that the number of publications on the topic will reach approximately 118 in 2025 and 134 in 2026, indicating the continuation of the growth trend and the consolidation of this domain as an area of scientific and technological opportunity.
Table 3 complements this analysis by presenting the evolution of the average number of citations per article over the same period, highlighting the temporal impact of academic production. The earliest works show higher average citation counts, reflecting their seminal role in establishing the theoretical foundations of the field. Starting in 2018, the sharp increase in publication volume is accompanied by a slight reduction in the average number of citations, an expected behavior in rapidly expanding areas, where more recent studies have not yet achieved wide dissemination. These results reinforce the transition from an initial phase of conceptual consolidation to a stage of scientific maturity, characterized by the diversification of approaches and the strengthening of the field’s international recognition.
Table 3.
Average citations per year for RF cybersecurity publications (2009–2025).
Figure 5 presents the Three-Field Plot diagram [74], which relates the main article authors (AU), keywords (DE), and publication sources (SO), highlighting the ten most representative elements of the scientific production on RF cybersecurity. This visualization makes it possible to identify how the core research topics are distributed among the most productive authors and the highest-impact journals. Notable contributors include Mosavi M., Lu M., Li H., Li Y., and Wang H., who are strongly associated with terms such as “jamming,” “security,” “wireless communication,” “authentication,” and “GNSS/GPS spoofing” [75,76,77,78,79]. This thematic concentration indicates the predominance of studies focused on the analysis of attacks and the development of defense mechanisms in wireless communication systems, particularly within the physical and data link layers of the OSI model [80].
Figure 5.
Three Field Plot which associates article authors, most used keywords and journals.
Among the most relevant journals, Sensors, IEEE Access, IEEE Transactions on Information Forensics and Security, IEEE Transactions on Vehicular Technology, and the IEEE Internet of Things Journal emerge as the primary dissemination channels for RF cybersecurity research. The analysis reveals three main axes of convergence: (i) a research community centered on jamming and spoofing analysis and mitigation [54,81,82,83,84]; (ii) the growing incorporation of machine learning and intrusion detection techniques [85,86,87,88]; and (iii) the concentration of contributions in journals dedicated to the reliability and protection of IoT and wireless systems [7,11,57,89]. Together, these patterns illustrate the progressive maturation of RF cybersecurity as a research field aligned with contemporary challenges in wireless communication security.
3.3. Most Relevant Sources
Table 4 presents the most relevant journals in the scientific production on cybersecurity in RF technologies. Most studies are concentrated in high-impact journals in the fields of engineering, telecommunications, and information technology. MDPI Sensors has the highest number of publications (41 articles), followed by the IEEE Internet of Things Journal (34), IEEE Transactions on Vehicular Technology (32), and IEEE Access (31). This concentration reflects the growing interest in research focused on the security of IoT devices, wireless communication, and embedded systems.
Table 4.
Top 10 most relevant sources in the field of RF cybersecurity.
The predominance of IEEE journals reinforces the technical and applied profile of the field, highlighting the emphasis on detection methods, authentication, attack mitigation, and the protection of RF communication protocols [57,90,91]. In parallel, the prominent presence of Sensors, a multidisciplinary open access journal, highlights the relevance of research that integrates hardware, sensor networks, and the security of connected devices [92,93,94]. Together, these publication venues illustrate the consolidation of RF cybersecurity as an interdisciplinary domain at the intersection of engineering, computing, and information security [71,72,73].
Figure 6 presents the chart based on Bradford’s Law [95], which illustrates the distribution of publications across journals and identifies the core group of the most productive sources. MDPI Sensors occupies the central region (Core Sources), standing out in relevance compared to other journals, thereby confirming its role as the primary dissemination channel in the field.
Figure 6.
Bradford’s Law.
Figure 7 shows the temporal evolution of the main publication sources, illustrating how the outlets disseminating RF cybersecurity research have diversified over time. This analysis is relevant to reveal shifts in editorial focus and to contextualize how the field has expanded beyond a small set of specialized venues. In the early years, publications were largely concentrated in a limited number of journals. From 2016 onward, an increased participation of outlets such as IEEE Transactions on Vehicular Technology and IEEE Transactions on Aerospace and Electronic Systems can be observed, reflecting the growing integration of RF cybersecurity topics with embedded systems, vehicular communications, and safety-critical wireless applications [96,97].
Figure 7.
Sources’ production over time.
The most significant growth occurs from 2018 onward, driven by the expansion of publications in MDPI Sensors, IEEE Internet of Things Journal, and IEEE Access, which began to lead the dissemination of studies on IoT, wireless networks, and the protection of connected devices [7,11,89]. This movement reflects both technological advancement and the popularization of open access, high-impact journals, which facilitate the global dissemination of research findings. Thus, the observed trend confirms the consolidation and diversification of publication sources, reinforcing that RF cybersecurity has established itself as a stable, interdisciplinary field in continuous international expansion.
3.4. Productivity and Impact by Authors
Table 5 presents the most productive article authors in the field of RF cybersecurity. Li H. and Li Y. stand out with 17 publications each, followed by Liu Y. and Wang H., both with 16 articles. These researchers have consistently contributed to advancing knowledge, particularly in topics related to jamming and spoofing attacks, device authentication, and security in wireless technologies [98,99,100,101].
Table 5.
Top 10 most relevant article authors in RF cybersecurity research.
The fractional production values, ranging from 2.51 to 4.95, reflect different levels of collaboration among authors and research groups. Researchers such as Mosavi M. and Wang Y. exhibit higher individual representativeness, suggesting leadership roles in major projects and reference publications [75,90,102]. Overall, the group of the most productive authors represents a consolidated and highly cooperative scientific community, predominantly composed of Asian researchers who have driven the international advancement of studies on cybersecurity in radio frequency communications.
Figure 8 complements this analysis by illustrating the temporal evolution of productivity and impact among the main authors. Each bubble represents the number of publications per year; the larger the diameter, the greater the volume of articles, and darker shades indicate a higher average number of annual citations (TC per Year), reflecting the scientific impact of their contributions.
Figure 8.
Article authors’ (AU) production over time.
Authors such as Li H., Li Y., Liu Y., and Wang H. have maintained a stable and productive trajectory throughout the analyzed period, combining a high number of publications with strong citation impact, factors that reinforce their influence in the theoretical consolidation of the field. In more recent years, Mosavi M., Lu M., and Zhang Y. have stood out by expanding their contributions and introducing approaches based on machine learning, intelligent networks, and critical systems security [61,75,79]. This dynamic highlights the transition from a community centered on pioneering researchers to an expanding collaborative ecosystem, in which different generations of authors converge around emerging themes in RF cybersecurity.
Figure 9 shows the distribution of author productivity according to Lotka’s Law [103], which relates the proportion of researchers to the number of publications. The chart compares the theoretical curve (inverse square law) with the empirical results observed in this study, indicating the degree of adherence between them.
Figure 9.
Authors’ productivity according to Lotka’s law.
The observed curve (in blue) shows good correspondence with the theoretical curve (in orange), suggesting that a small fraction of authors, less than 0.1%, accounts for most of the publications, while the majority contribute only sporadically. This pattern is characteristic of consolidating scientific fields, in which production tends to concentrate within leading research groups.
In the context of RF cybersecurity, such concentration reflects the role of a limited number of research groups in shaping core research problems and methodological approaches, while also highlighting the importance of collaboration networks for the maturation and diversification of the field.
3.5. Scientific Productivity by Institutions
Table 6 presents the institutions with the highest publication volumes in the field of radio frequency cybersecurity. A strong predominance of Chinese universities is observed, with Xidian University (24 articles) and Tsinghua University (22 articles) standing out, followed by Beijing Jiaotong University and Southeast University, both with 21 publications. These universities have established themselves as centers of advanced research in wireless communications, embedded systems, and IoT network security, playing a central role in the scientific and technological advancement of the field [104,105,106,107].
Table 6.
Top 10 most relevant affiliations in RF cybersecurity research.
Institutions such as Nanjing University of Posts and Telecommunications, Beihang University, and Xi’an Jiaotong University show strong engagement in secure communication protocols and attack mitigation in RF networks [108,109]. Outside the continental Chinese context, Hong Kong Polytechnic University and Nanyang Technological University (Singapore) stand out for strengthening regional cooperation and expanding the integration of Asian research centers into the global landscape. Overall, the institutional distribution confirms the geographical concentration of scientific excellence in Asia, particularly in China, which leads the development of innovative solutions for the security of wireless communication systems.
Figure 10 complements this analysis by illustrating the temporal evolution of productivity among the main universities active in the field. A consistent growth trend is observed starting in 2015, driven by the increasing number of publications from institutions already ranked among the most productive, such as Tsinghua University, Beijing Jiaotong University, and Xidian University. This movement parallels the intensification of research focused on IoT network protection and wireless communications, consolidating the role of these universities as international reference centers.
Figure 10.
Affiliations’ production over time.
Starting in 2019, a more diversified expansion can be observed, marked by the entry of new institutions and the strengthening of international collaborations, particularly with universities in Hong Kong, Singapore, and European countries. This expansion indicates a movement toward internationalization and scientific cooperation, in which the topic is no longer concentrated in a few Asian hubs but has become part of a global research network on cybersecurity in RF systems. The temporal pattern, therefore, reveals a field in full consolidation, sustained by continuous growth, interinstitutional collaboration, and the progressive increase of international visibility.
3.6. Scientific Productivity by Country
Figure 11 shows the distribution of scientific production by country, distinguishing publications with exclusively national authorship (SCP—Single Country Publications) from those resulting from international collaborations (MCP—Multiple Country Publications).
Figure 11.
Author Countries.
It is observed that most countries maintain a predominance of publications with domestic authorship (SCP), reflecting the strengthening of consolidated national research groups. Conversely, nations with higher rates of international collaboration, measured by MCP, tend to exhibit greater scientific impact, corroborating the pattern already evidenced by the most productive affiliations and authors (Table 6, Figure 8 and Figure 10). Countries such as South Korea and Australia still display limited participation in multilateral networks, indicating potential for expansion toward future international collaborations.
Figure 12 shows the temporal evolution of scientific production by country, highlighting the significant growth of China throughout the analyzed period. The continuous increase in publications since 2015 confirms the country’s central role in consolidating research on cybersecurity applied to RF systems, driven by national policies on technological innovation and information security. In addition to quantitative growth, there is a progressive diversification of global scientific output, with increasing participation from countries such as the United States, India, France, and Italy, which have intensified their contributions in recent years.
Figure 12.
Countries’ production over time.
In recent years, scientific production has come to reflect a more distributed collaboration landscape, marked by the inclusion of new Asian countries and the strengthening of European research networks. This internationalization movement indicates the transition from a field once concentrated in a few hubs to a more diversified and cooperative global ecosystem. Different regions of the world now contribute to the development of solutions aimed at protecting critical infrastructures and wireless communications. The observed pattern reinforces the consolidation of RF cybersecurity as a mature research area of strategic international relevance.
3.7. Countries with the Highest Global Citation Impact
Table 7 presents the countries with the highest total number of citations in publications on cybersecurity in radio frequency technologies. China ranks first with 4154 citations, followed by the United States with 3286 citations, demonstrating the leading role of these two nations in the consolidation and dissemination of scientific knowledge on the subject. This result reflects both the substantial volume of scientific output and the growing strategic relevance of RF cybersecurity research in these countries.
Table 7.
Top 10 most cited countries in RF cybersecurity research.
Next, Italy, Iran, France, Canada, India, the United Kingdom, South Korea, and Australia stand out, completing the group of the ten most-cited countries. These results demonstrate the presence of established research hubs across Europe, North America, and Asia, with an emphasis on applications related to the Internet of Things, wireless networks, and critical systems. Overall, the geographical distribution of citations indicates a globally active and collaborative research field, characterized by Asian leadership in publication volume and strong Western participation in the consolidation of research on cybersecurity applied to radio frequency.
The metric “Average Article Citations”, presented in Table 7, represents the average number of citations per article and helps in the relative interpretation of scientific impact. However, it should not be analyzed in isolation, as it may vary depending on the total number of publications from each country and the maturity of national research programs addressing RF security in critical and large-scale systems.
Table 8 presents the ten most globally cited articles in the field of cybersecurity in RF technologies. The results show that the highest-impact works are concentrated on attacks and countermeasures in wireless communication systems, addressing topics such as spoofing, jamming, device authentication, cognitive communications, and IoT network security, particularly in contexts where RF vulnerabilities directly affect sensing, positioning, synchronization, and control functions. The study by [110], published in the International Journal of Critical Infrastructure Protection, has the highest number of citations and stands out as one of the pioneering works on vulnerabilities in positioning systems and critical infrastructure. Following that, the article by [111], published in IEEE Wireless Communications, shows high annual impact and reflects the growing interest in cooperative security and machine learning approaches applied to RF network protection.
Table 8.
Top 10 most globally cited documents in RF cybersecurity research.
Also noteworthy is the work by [112], published in IEEE Transactions on Cognitive Communications and Networking, which presents the highest normalized citation index (6.68), demonstrating its recent influence and relevance to the advancement of cognitive communication techniques and adaptive attack mitigation. Other studies, such as those by [113,114], further reinforce the importance of research on security and integrity in GNSS systems and spoofing detection, illustrating the field’s transition from conceptual studies to practical solutions with high scientific impact.
3.8. Dynamics and Frequency of Keywords
Figure 13 shows the temporal evolution of the most recurrent keywords in the literature on cybersecurity in radio frequency technologies, highlighting the gradual transformation of the field’s main thematic axes. In the early stages (2009–2014), the terms “jamming”, “authentication”, and “wireless communications” stand out, reflecting the predominant focus on denial-of-service attacks and fundamental authentication strategies in wireless systems. This initial phase consolidated the conceptual and methodological foundations of the area, establishing the theoretical basis for subsequent studies on vulnerabilities and risk mitigation in communication protocols.
Figure 13.
Words’ frequency over time.
From 2016 onward, the scientific vocabulary became more diversified, with the emergence of terms such as “spoofing attacks”, “network security”, and “GNSS”, indicating the convergence between satellite positioning, network security, and critical communications. Between 2019 and 2023, the higher frequency of expressions such as “global positioning system” and “wireless communications” demonstrates the maturation of the field and the growing interest in smart infrastructures, IoT devices, and the protection of heterogeneous networks, where RF signals play a dual role as communication and sensing enablers. Despite this thematic expansion, the term “jamming” remained constant, reaffirming its role as a central and persistent concept in research on attacks and defenses in RF systems. Taken together, these results demonstrate the transition from an initial technical focus to an interdisciplinary paradigm in which attack detection, cryptography, and defense have become consolidated as the core pillars of RF cybersecurity research.
Figure 14 complements this analysis by presenting a thematic map of the research front, divided into four quadrants according to the degree of relevance (centrality) and development (density) of the themes. Each cluster results from the relationship among co-occurring keywords, allowing the identification of the conceptual axes that support the structure of the field. The motor themes quadrant brings together the most influential and emerging topics, indicating the areas with the greatest potential for technological innovation and future impact [119], particularly in applications where RF resilience directly affects sensing accuracy, availability, and system trustworthiness.
Figure 14.
Thematic Map.
In the Motor Themes quadrant (upper right), terms such as “jamming”, “security”, “wireless communication”, and “GNSS” appear with high centrality and density, forming the core pillars of RF cybersecurity. Niche Themes (upper left), including “Wi-Fi” and “full-duplex”, are well-developed but less connected to the main research flows. Basic Themes (lower right), like “machine learning” and “GPS spoofing”, show high relevance but are still under methodological development. Meanwhile, the Emerging or Declining Themes (lower left), such as “Kalman filtering” and “mmWave sensing”, may signal either nascent investigations or reduced scientific attention. This thematic layout offers a structured view of the maturity and evolution of key topics.
The map was constructed using co-occurrence analysis with centrality–density clustering, revealing both the stable conceptual foundations and the emerging directions in the field. The results illustrate the scientific maturity and increasing global relevance of RF cybersecurity, particularly in response to the growing demands of secure and resilient wireless communication systems.
3.9. International Scientific Collaboration
Figure 15 presents the global network of scientific collaboration in the field of cybersecurity in RF technologies, highlighting the connections among the main knowledge-producing countries. The clusters are identified by the node colors. The collaboration strength between countries is denoted by the edge thickness. China and the United States form the central and most densely connected core of the network (green cluster), sustaining the most significant international partnership in terms of co-publications and researcher exchange. This bilateral connection reflects the scientific and technological leadership of these nations, which combine high productivity with continuous investment in applied research on IoT network security, wireless communications, and GNSS systems.
Figure 15.
International collaboration network among countries in RF cybersecurity research. Nodes represent countries, and edges indicate co-authorship relationships.
The second most colaborative cluster is the blue cluster which contains France, India, Pakistan and others. India has a closer collaboration with South Korea that is presented in the green cluster. Around this axis, complementary collaborations stand out with countries such as Germany, Australia, the United Kingdom, France, and India, which act as intermediate nodes in the dissemination and diversification of scientific partnerships. These countries often contribute specialized expertise in areas such as vehicular communications, satellite systems, industrial IoT, and security evaluation frameworks, reinforcing the multidimensional nature of RF cybersecurity research. The map also reveals the emergence of new regional hubs, particularly Saudi Arabia, South Korea, and Singapore, which expand Asian representation in the global landscape. Conversely, participation from Latin American and African countries remains incipient, with occasional cooperation links involving Brazil, South Africa, and Egypt, indicating potential for expansion and strengthening of intercontinental collaboration networks.
Overall, the network structure reveals a collaborative model that remains concentrated but is undergoing expansion, with China playing a central articulating role by connecting research centers across Asia, Europe, and North America. This configuration confirms that RF cybersecurity has consolidated as a globalized and cooperative field, in which the integration between leading and emerging countries is essential for developing innovative solutions and addressing cybersecurity challenges on an international scale.
4. Trends, Vulnerabilities, and Technological Impact
4.1. Temporal Trends in RF Cyberattacks
Figure 16 illustrates the cumulative evolution of the main cyberattacks in radio frequency technologies reported in scientific articles published between 2009 and 2025. The use of multiple subplots allows comparison of the temporal behavior of each attack category, highlighting different growth rates and maturity levels across research lines. This visualization reveals a significant increase in the volume of studies focused on wireless communication security, with emphasis on jamming (denial-of-service) and spoofing attacks, while other vectors such as replay, relay, and credential cloning show more moderate growth over the analyzed period.
Figure 16.
Cumulative evolution of the main cyberattacks in radio frequency technologies reported in scientific articles between 2009 and 2025. Each subplot represents a specific attack category, including jamming, spoofing, replay, and others, highlighting the cumulative growth of each type over the analyzed period.
The jamming attack, characterized by the intentional emission of interference in the communication channel, has shown an upward trend since 2015, reflecting its persistence as one of the most studied threats at the physical layer of RF systems [70,120,121,122,123,124,125]. This sustained interest can be attributed to the low technical barrier for execution, the direct coupling with spectrum occupancy, and the high impact of jamming on availability-sensitive applications such as industrial control, vehicular systems, and IoT deployments operating in unlicensed bands.
Similarly, spoofing, which involves the falsification of signals or identities, has exhibited an even more pronounced increase since 2018, accompanying the expansion of GNSS, IoT, and critical communication technologies [118,126,127,128,129]. From a sensing and communication perspective, spoofing exploits inherent trust assumptions in RF receivers and protocol designs, particularly in systems where signal authenticity is inferred from physical-layer characteristics rather than cryptographic guarantees. This explains its prominence in GNSS-based applications, autonomous systems, and low-power IoT devices.
Other vectors, such as replay attacks, eavesdropping, signal injection, and man-in-the-middle, also show a gradual increase after 2020, a period during which the diversification of connected devices significantly expanded attack surfaces [11,77,130,131,132,133,134,135]. These attacks are often associated with higher-layer protocol interactions but depend on RF channel access and timing characteristics, making them increasingly relevant in heterogeneous IoT environments where sensing, communication, and control are tightly coupled.
Meanwhile, categories such as relay attack, Primary User Emulation Attack (PUEA), and RF credential cloning have emerged more recently, with modest curves that reflect research fronts still in consolidation [136,137,138,139,140]. Their slower growth reflects the fact that these attack vectors are typically investigated in technology- and context-specific scenarios, such as cognitive radio networks, RFID systems, or proximity-based authentication, rather than across broad classes of RF communication systems.
The use of a layout with multiple subplots prevents visual overlap and highlights the differences in pace and maturity among the categories. Overall, the results indicate that the field of RF cybersecurity is evolving from classical and extensively studied attacks, such as jamming and spoofing, toward a reconfiguration of known threats in new application contexts, in parallel with the growing complexity and interconnectivity of communication ecosystems.
4.2. Mapping RF to Cyberattack Types
Figure 17 presents a heatmap correlating the main radio frequency communication technologies with the different types of cyberattacks identified in the literature. This visualization enables an integrated understanding of how vulnerabilities are distributed across protocols, frequency bands, and communication layers, revealing both consolidated patterns and emerging research gaps. Importantly, these patterns reflect differences in how each technology exposes the RF channel to interference, manipulation, or signal impersonation. The color intensity represents the number of publications related to each technology–attack combination, highlighting the most extensively studied areas as well as those that remain underexplored.
Figure 17.
Heatmap illustrating the occurrence frequency of cyberattack types in radio frequency systems reported in the scientific literature, associating each attack category with the different communication technologies analyzed.
The concentration of studies on the Global Navigation Satellite System (GNSS/GPS/ GLONASS/Galileo/BeiDou) is particularly significant, especially for spoofing (245 publications) and jamming (49 publications). This prominence underscores the critical importance of positioning technologies in strategic applications such as autonomous transportation, defense, logistics, and network synchronization, where signal reliability is essential [96,110,141,142,143,144,145]. The recurrence of these attack vectors confirms that intentional GNSS signal manipulation remains one of the most exploited vulnerabilities in RF systems, largely due to the open and broadcast nature of satellite signals, which makes them inherently susceptible to interference and signal falsification at the RF level [104,128,129,146,147,148].
Fifth- and sixth-generation mobile communications (5G and 6G) also stand out due to the high incidence of studies on jamming, spoofing, and eavesdropping, reflecting growing concern over the robustness of next-generation wireless infrastructures [8,14,149,150,151,152]. The emphasis on these technologies in the literature is explained not only by their widespread adoption, but also by their reliance on complex RF features, such as dynamic spectrum access, beamforming, and dense cell deployments, which increase sensitivity to interference, spoofing, and passive interception at the physical layer [4,5,150,151,152].
In IoT and local communication technologies such as LoRa/LoRaWAN, ZigBee, Bluetooth, BLE, and Wi-Fi, jamming continues to be the most recurrent vulnerability, reflecting these networks’ susceptibility to deliberate interference and their limited spectral isolation mechanisms [89,91,153,154,155,156]. Recent studies also report replay, relay, and man-in-the-middle (MitM) attacks, associated with authentication flaws and the distributed or cooperative nature of these protocols [131,157,158,159,160]. Taken as a whole, while jamming remains dominant, IoT technologies exhibit a progressively diversified threat landscape, reflecting the combination of constrained devices, shared spectrum usage, and lightweight authentication mechanisms typical of these RF ecosystems [57,63,122,161,162,163].
In this context, Table 9 complements the previous discussion by summarizing the ten most frequent combinations of radio frequency technologies and cyberattack types reported in published articles. It can be observed that spoofing in GNSS systems ranks first, followed by jamming attacks in 5G, 6G, Wi-Fi, 4G/LTE, LoRa/LoRaWAN, and ZigBee networks. This pattern indicates that research efforts remain concentrated on well-established technologies, whereas emerging protocols are still comparatively underexplored and thus represent relevant directions for future investigation.
Table 9.
Top 10 technology × attack combinations in RF cybersecurity research.
From this mapping, it becomes evident that vulnerabilities in RF systems are unevenly distributed across technologies. This uneven distribution reflects not only differences in protocol design, but also how each technology interacts with the RF medium, which has direct implications for risk prioritization and the definition of mitigation strategies.
4.3. Cybersecurity Implications for IoT and Wireless Systems
Table 10 organizes representative RF-based cyberattacks observed in IoT, highlighting the corresponding RF technologies, affected device categories, real-world application examples, and the key studies that document these vulnerabilities across different domains. This organization makes explicit how differences in RF communication characteristics, deployment scale, and device constraints translate into distinct security implications across IoT and wireless systems.
Table 10.
RF attacks, associated technologies, affected IoT systems, and application domains.
Many of the RF technologies addressed in this study, such as BLE, ZigBee, Wi-Fi, GNSS, LoRa/LoRaWAN, and RFID, are integral to modern IoT ecosystems and wireless infrastructures. Their prevalence in the literature is closely linked to their reliance on open or shared spectrum, low-power operation, and broadcast communication models, which expose the RF channel to interference, manipulation, and unauthorized observation.
The vulnerabilities observed across these systems, including spoofing, jamming, replay, relay, eavesdropping, and RF signal injection, have been consistently demonstrated in the literature through empirical experiments and large-scale evaluations. For example, works such as [6,154,155,167,169] show how jamming and spoofing can critically degrade navigation accuracy, disrupt wireless connectivity, and compromise device authentication in domains ranging from UAV control to smart-home automation.
The results summarized in Table 10 also reveal that certain RF technologies are more frequently associated with specific classes of vulnerabilities in the literature. For instance, jamming is prevalent in LoRa/LoRaWAN, Wi-Fi, and ZigBee systems [120,155], while GNSS technologies are especially sensitive to spoofing [67,186]. Replay attacks frequently target Bluetooth/BLE, ZigBee, and 433 MHz systems [162,191], and MitM attacks are recurrent in LoRa and RFID infrastructures [181,194]. These associations underscore the need for technology-specific countermeasures and highlight the heterogeneous nature of the RF threat landscape, in which each protocol faces distinct exposure patterns and security requirements within IoT and wireless environments. Such patterns emerge not from isolated weaknesses, but from how protocol design choices, spectrum usage, and device capabilities interact at the RF layer.
Taken together, these findings show that reports of RF vulnerabilities in the literature are not uniformly distributed across technologies, but instead follow protocol-specific and device-specific patterns. The range of affected systems, including UAVs, autonomous vehicles, smart locks, industrial nodes, and satellite-IoT components, illustrates that each communication technology faces distinct operational constraints and exposure conditions. By making these patterns explicit, the mapping helps identify where mitigation efforts should be prioritized and supports the design of protection strategies tailored to the characteristics and threat profiles of each protocol. This perspective is particularly relevant for designers, operators, and regulators of IoT and wireless systems, who must balance performance, scalability, and security under RF-constrained conditions.
5. Discussion
The analysis shows that cybersecurity research applied to radio frequency technologies has developed around two principal thematic axes. The first concerns signal integrity and authentication in GNSS and cellular networks, where spoofing and jamming remain dominant issues due to their impact on navigation, synchronization, and critical communication infrastructures [2,150,195,196,197,198,199,200]. The second axis relates to the resilience of IoT and short-range wireless systems, which face an increasingly diverse set of threats, such as replay, relay, eavesdropping, and man-in-the-middle attacks, driven by the expansion of connected devices and the distributed nature of modern wireless environments [6,54,58,61,63,67,69,71,72,153,155,164,185]. These two directions depict a research landscape that is progressively integrating RF security into discussions on spectral resilience, interoperability, and cyber–physical protection.
Beyond the overall growth in publication volume, the observed increase in co-authorship and international collaboration suggests a gradual consolidation of RF cybersecurity as a research domain. Collaborative research patterns are increasingly common in areas that involve heterogeneous technologies and complex system interactions, such as IoT and wireless communication security. In this context, the rising collaboration rate reflects the interdisciplinary nature of RF cybersecurity and the need to integrate expertise from communications, embedded systems, and security engineering.
From a temporal and geographical perspective, the scientometric evidence reveals sustained growth in RF cybersecurity publications between 2009 and 2025, accompanied by a concentration of research activity in China and the United States, alongside strong contributions from other Asian institutions. This international research structure has supported advances in the detection, mitigation, and modeling of RF-based threats, reinforcing the global relevance of the field.
The analysis of scientific influence reinforces this trajectory. Journals such as Sensors, the IEEE Internet of Things Journal, and several IEEE Transactions appear as recurring venues for RF security research. Citation and keyword analyses point to growing interest in artificial intelligence for RF anomaly detection, the protection of heterogeneous IoT environments, and the design of spectrally resilient wireless systems. These trends illustrate how RF cybersecurity research is increasingly aligned with broader technological developments related to autonomous mobility, critical infrastructure protection, and distributed sensing.
With respect to the threat landscape, the literature confirms the prominence of jamming and spoofing as the most extensively studied attack vectors, owing to their practicality and disruptive potential at the physical layer. At the same time, the increasing focus on replay, relay, credential cloning, and man-in-the-middle attacks reflects the expansion of the RF attack surface in ecosystems characterized by ubiquitous connectivity and resource-constrained devices. Technologies such as GNSS, 5G/6G, Wi-Fi, and LoRaWAN feature prominently in cybersecurity studies not only due to their widespread deployment, but also because vulnerabilities in these systems can propagate across interconnected communication layers.
From a practical standpoint, the technology- and attack-oriented mapping presented in this study can support more informed decision-making in the design and deployment of RF-based systems. By explicitly associating attack types with specific wireless technologies, the analysis provides a structured basis for prioritizing security efforts according to the relative exposure of different systems to RF-originated threats.
Although this study is limited to publications indexed in Scopus and Web of Science, the consistency of the observed patterns across technologies and attack classes suggests that the findings offer practical guidance for engineers, system designers, and researchers. In particular, the identified vulnerability profiles can assist in focusing mitigation strategies on RF technologies that exhibit higher exposure and greater potential for cascading impacts in interconnected wireless ecosystems.
Future Research Directions in RF Cybersecurity
The scientometric and systematic analyses presented in this study indicate that research on cybersecurity in radio frequency technologies has reached a stage of scientific consolidation, particularly with respect to well-known attack vectors such as jamming and spoofing across GNSS, IoT, and wireless communication systems. At the same time, the results reveal several directions in which future research is both necessary and promising, especially as RF-based systems continue to expand in scale, complexity, and criticality.
One important research direction concerns the development of RF-aware security frameworks that explicitly integrate physical-layer characteristics with higher-layer security mechanisms, such as authentication, key management, access control, and intrusion detection. While many existing studies focus on isolated protocol-level or application-level defenses, emerging RF environments, such as dense IoT deployments, smart cities, and cyber–physical systems, require holistic approaches capable of capturing spectrum dynamics, interference patterns, and cross-layer dependencies [5,7,57]. This integration is particularly relevant for low-power and resource-constrained devices, where traditional cryptographic solutions alone may be insufficient or impractical.
Another promising avenue lies in the advancement of adaptive and data-driven detection techniques for RF threats. The increasing use of machine learning and signal intelligence for jamming and spoofing detection reflects a broader shift toward data-centric security models [85,86]. However, the literature still lacks systematic evaluation of these techniques under realistic RF conditions, including heterogeneous devices, non-stationary noise, and adversarial manipulation. Future research should therefore prioritize robustness, explainability, and generalization across different RF technologies and operating conditions, rather than optimizing detection performance only under narrowly controlled or idealized experimental scenarios.
The results also highlight gaps in the security literature for emerging RF technologies, such as 6G and satellite-IoT, as well as for less extensively studied systems like ultra-wideband (UWB). Compared to established platforms such as GNSS, Wi-Fi, and LoRaWAN, these technologies remain under-represented in RF cybersecurity studies [8,150]. This gap points to the need for comparative analyses across RF technologies, studies based on realistic or semi-realistic attack scenarios, and investigations that relate spectrum characteristics to security vulnerabilities, as well as assessments of the broader system-level impact of RF attacks.
Finally, future research should place emphasis on the implications of RF cybersecurity for real-world deployments and critical infrastructures. As demonstrated by the attack–technology mappings presented in this study, RF vulnerabilities can directly affect safety-critical systems, including autonomous vehicles, industrial automation, and public safety communications. Bridging the gap between analytical research and deployable countermeasures, through standardized threat models, cross-technology benchmarks, and interdisciplinary collaboration, remains an open challenge and a key priority for the maturation of the field [6,11].
Taken together, these directions point to the need for studies that compare RF technologies and attack types in a structured way, rather than addressing each technology or vulnerability in isolation.
6. Conclusions
This study demonstrates that cybersecurity research in radio frequency technologies has expanded over the past decade and has evolved into two well-defined thematic directions. One is centered on signal integrity and authentication in GNSS and cellular networks, where spoofing and jamming remain dominant concerns; the other focuses on the resilience of IoT and short-range wireless systems, which face a broader set of threats such as replay, relay, eavesdropping, and man-in-the-middle attacks. Together, these directions reflect the growing integration of RF security into discussions on reliability, interoperability, and the protection of cyber–physical infrastructures.
The scientometric analysis highlights the prominence of Sensors and leading IEEE journals as the primary publication venues for RF security research, as well as the strong concentration of scientific production in Asia, particularly China, which has played a decisive role in advancing methods for detecting, mitigating, and modeling RF-based threats. These patterns portray a research domain that is technologically driven, globally connected, and increasingly multidisciplinary.
Despite this growth, important gaps remain. Several widely deployed RF Technologies, such as RFID, NFC, BLE, ZigBee, LoRa, Wi-Fi, and unlicensed ISM bands, still lack comprehensive cybersecurity assessments, especially regarding attack vectors like credential cloning, relay manipulation, and signal injection. Emerging fields, including terahertz communication and 6G systems, are also underexplored from a security perspective, representing promising opportunities for future investigations. In this context, future research should prioritize spectrum-aware threat modeling, experimental validation in real-world RF environments, and the development of adaptive detection mechanisms capable of operating under the scalability and latency constraints of next-generation wireless systems.
Overall, the findings of this study reinforce the importance of continued monitoring of vulnerabilities across established and emerging RF technologies, as well as strengthening international collaboration to keep pace with the rapid evolution of wireless communication ecosystems. By mapping cross-cutting threats and identifying technology-specific exposure patterns, this work provides a practical foundation to support future research and guide the development of more resilient wireless and IoT systems.
Author Contributions
Conceptualization, methodology and validation, P.R.d.A., J.A.M.d.R., D.R.d.M.F. and O.d.S.M.G.; software and resources, P.R.d.A.; analysis, P.R.d.A. and J.A.M.d.R. All authors have read and agreed to the published version of the manuscript.
Funding
This research was funded by the CyberOT project of Clavis Information Security (FINEP/Plat-Ciber), agreement number 03.23.0517.00, FINEP reference 1488/22. The corresponding researcher is a master’s scholarship student funded by CAPES.
Data Availability Statement
The review protocol and supplementary methodological materials are publicly available in the Open Science Framework (OSF) at https://osf.io/bqx7n/ (accessed on 11 December 2025).
Acknowledgments
The authors would like to thank the Federal University of Itajubá (UNIFEI), CNPq, CAPES, Clavis Information Security (FINEP/Plat-Ciber) for its financial support in CyberOT Project, Cyber Intelligence Laboratory (LInC), and the u.AI, FronTIERS HackLab, LabTel and LAIoT laboratories for their technical support and the Federal Institute of Minas Gerais (IFMG) for the work developed.
Conflicts of Interest
The authors declare no conflicts of interest. The funders had no role in the design of the study; in the collection, analyses, or interpretation of data; in the writing of the manuscript; or in the decision to publish the results.
Abbreviations
The following abbreviations are used in this manuscript:
| 4G | Fourth Generation Cellular Network |
| 5G | Fifth Generation Cellular Network |
| 6G | Sixth Generation Cellular Network |
| BLE | Bluetooth Low Energy |
| DSRC | Dedicated Short Range Communications |
| DT | Document Type |
| GLONASS | Global Orbiting Navigation Satellite System |
| GNSS | Global Navigation Satellite System |
| GNU | GNU’s Not Unix |
| GPS | Global Positioning System |
| IEEE | Institute of Electrical and Electronics Engineers |
| IoMT | Internet of Medical Things |
| IoT | Internet of Things |
| IP | Internet Protocol |
| LLM | Large Language Model |
| LoRa | Long Range |
| LoRaWAN | Long Range Wide Area Network |
| LTE | Long-Term Evolution |
| MCP | Multiple Country Publications |
| MDPI | Multidisciplinary Digital Publishing Institute |
| MitM | Man in the Middle |
| NB-IoT | Narrowband Internet of Things |
| NFC | Near Field Communication |
| OSI | Open Systems Interconnection |
| PRISMA | Preferred Reporting Items for Systematic Reviews and Meta-Analyses |
| PUEA | Primary User Emulation Attack |
| QoS | Quality of Service |
| RAG | Retrieval-Augmented Generation |
| RF | Radio Frequency |
| RFID | Radio Frequency Identification |
| RTL-SDR | Realtek Software-Defined Radio |
| SCP | Single Country Publications |
| SDR | Software-Defined Radio |
| TC | Total Citations |
| TCP | Transfer Control Protocol |
| USRP | Universal Software Radio Peripheral |
| UWB | Ultra-Wideband |
| V2X | Vehicle-to-Everything |
Appendix A. Search Strategy
Appendix A.1. General Structure of the Search String
The search string was designed to capture publications addressing the intersection between cybersecurity and radio frequency communication technologies by applying Boolean and semantic proximity operators. The goal was to achieve broad sensitivity while maintaining thematic precision, ensuring the inclusion of articles focused on threats, vulnerabilities, and protection mechanisms in RF communication systems, while excluding topics strictly related to physical-layer or antenna studies (Table A1).
Table A1.
Search strings applied in Scopus and Web of Science databases.
Appendix A.2. Lists of Thematic Descriptors
- (a)
- Cybersecurity and Threat Terms
- cybersecurity, cyber attack, vulnerability, threat;
- jamming, spoofing, replay, relay, eavesdropping, sniffing;
- man-in-the-middle, injection, denial of service, DoS, IDS, encryption, authentication;
- spectrum sensing falsification (SSDF), cognitive radio attack, side-channel attack.
- (b)
- RF Communication Technologies and Protocols
- Short-range networks: Bluetooth, BLE, ZigBee, RFID, NFC, EnOcean;
- IoT and LPWAN networks: LoRa, LoRaWAN, Sigfox, Mioty, NB-IoT, LTE-M, Z-Wave, Thread, 6LoWPAN, Wi-SUN;
- Wide-area networks: Wi-Fi (IEEE 802.11), 3G, 4G, LTE, 5G;
- Positioning and satellite technologies: GPS, GNSS, Galileo, GLONASS, BeiDou, Satellite IoT, Satellite Radio;
- Critical applications: V2X, DSRC, Radar FMCW, Electronic Toll Collection, Tire Pressure Monitoring System.
- (c)
- Frequency Bands
- Low and mid-frequency bands: 125 kHz, 13.56 MHz, 27 MHz, 40.68 MHz, 315 MHz, 433 MHz, 868 MHz, 915 MHz;
- Upper frequency bands: 2.3–2.4 GHz, 5.8–5.9 GHz, 6 GHz, 24 GHz, 76–81 GHz;
- Broadband bands: 3.1–10.6 GHz (UWB), 24–100 GHz (mmWave).
Appendix B. PRISMA 2020 Checklist
This appendix presents the complete PRISMA 2020 checklist used to guide the reporting of this systematic review. Each item is mapped to the corresponding section, subsection, figure, or table in the manuscript where the requirement is addressed. The checklist is provided to enhance transparency, reproducibility, and methodological rigor, and to facilitate verification of compliance with the PRISMA 2020 reporting guidelines.
Table A2.
PRISMA 2020 checklist for the systematic review.
Appendix C. Computation of Agreement Metrics
This appendix details the computation of the observed agreement () and the expected agreement by chance () used to calculate Cohen’s kappa coefficient reported in Section 2.4. The purpose of this appendix is to ensure full methodological transparency and reproducibility of the reliability analysis.
Appendix C.1. Validation Sample and Decision Framework
The human-in-the-loop validation was performed on a stratified sample of articles, composed of:
- 150 articles initially classified as YES;
- 300 articles initially classified as NO;
- 104 articles initially classified as MAYBE.
In this study, the MAYBE category was treated as a hybrid inclusion class. All articles labeled as MAYBE by the LLM were subjected to full human review. When a direct relationship between cybersecurity and radio frequency communication was confirmed, these articles were reclassified as YES. Consequently, the final agreement analysis was conducted in a binary decision space (YES / NO), which is consistent with common practices in systematic screening and validation studies.
After manual validation, 96 of the 104 MAYBE articles were confirmed as relevant and incorporated into the YES category, while the remaining 8 were excluded.
Appendix C.2. Observed Agreement ()
The observed agreement () represents the proportion of cases in which the LLM classification was consistent with the final human decision. Agreement was counted in the following situations:
- Articles classified as YES by both the LLM and human reviewers ();
- Articles classified as NO by both the LLM and human reviewers ();
- Articles initially classified as MAYBE by the LLM and subsequently validated as YES after human review ().
Thus, the total number of concordant decisions was:
Considering the total validation sample of articles, the observed agreement was calculated as:
Appendix C.3. Expected Agreement by Chance ()
The expected agreement by chance () was computed from the marginal class proportions of the final binary labels (YES vs. NO). In this study, the intermediate category (MAYBE) was not treated as an independent class in the kappa computation. Instead, all MAYBE cases were resolved through the human-in-the-loop (HITL) validation process and mapped to a definitive inclusion decision (YES or NO). Consequently, the final Cohen’s kappa was calculated under a binary decision framework, reflecting agreement on the final inclusion outcome after human validation.
Let and denote the marginal proportions of the final classifications produced by the LLM after HITL resolution, and and the corresponding proportions obtained from human validation. All proportions were computed on the validation sample ().
- Human (final) distribution.
After human validation, 246 articles were considered relevant (YES), while 308 were excluded (NO), yielding:
- LLM (final) distribution.
In the final accounting, the LLM YES category comprises the 150 articles initially classified as YES and confirmed by human review, plus the 96 articles initially labeled as MAYBE that were subsequently validated as relevant. The remaining 308 articles were classified as NO after validation. Therefore:
The expected agreement by chance was then computed as:
This value represents the level of agreement that would be expected by chance alone under the final binary classification scheme adopted in this study, after resolving all intermediate MAYBE cases through human validation.
Appendix C.4. Cohen’s Kappa Coefficient
Substituting the computed values of and into Equation 1, Cohen’s kappa coefficient was obtained as:
According to the interpretation scale proposed by [49], a kappa value above 0.81 indicates an almost perfect level of agreement. This result confirms the stability and reliability of the LLM-assisted semantic screening after supervised prompt refinement, and supports the robustness of the final corpus used in the scientometric analysis.
References
- Westbrook, T. Cyber security of autonomous vehicles: The implications for city planning. J. Strateg. Secur. 2025, 18, 77–88. [Google Scholar]
- Rusu-Casandra, A.; Lohan, E.S. Experimental assessment of OSNMA-enabled GNSS positioning in interference-affected RF environments. Sensors 2025, 25, 729. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Hu, J.; Ammar, M.; Hussain, B.Z.; Kim, J.; Khan, I. Reinforcement-learning-driven integrated detection and mitigation of UAV GPS spoofing attacks. IEEE Internet Things J. 2025, 12, 29965–29977. [Google Scholar] [CrossRef] [Scilit]
- Nguyen, V.-L.; Lin, P.-C.; Cheng, B.-C.; Hwang, R.-H.; Lin, Y.-D. Security and privacy for 6G: A survey on prospective technologies and challenges. IEEE Commun. Surv. Tutor. 2021, 23, 2385–2428. [Google Scholar] [CrossRef] [Scilit]
- Saad, W.; Bennis, M.; Chen, M. A vision of 6G wireless systems: Applications, trends, technologies, and open research problems. IEEE Netw. 2020, 34, 134–142. [Google Scholar] [CrossRef] [Scilit]
- Anthi, E.; Williams, L.; Ieropoulos, V.; Spyridopoulos, T. Investigating radio frequency vulnerabilities in the Internet of Things (IoT). IoT 2023, 5, 18. [Google Scholar] [CrossRef] [Scilit]
- Gul, O.M.; Kulhandjian, M.; Kantarci, B.; Touazi, A.; Ellement, C.; D’Amours, C. Secure industrial IoT systems via RF fingerprinting under impaired channels with interference and noise. IEEE Access 2023, 11, 28252–28263. [Google Scholar] [CrossRef] [Scilit]
- Ziegler, V.; Schneider, P.; Viswanathan, H.; Montag, M.; Kanugovi, S.; Rezaki, A. Security and trust in the 6G era. IEEE Access 2021, 9, 115348–115361. [Google Scholar] [CrossRef] [Scilit]
- Peterseil, P.; Etzlinger, B.; Horek, J.; Khanzadeh, R.; Springer, A. Trustworthiness for an ultra-wideband localization service. Sensors 2024, 24, 5268. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Aftatah, M.; Zebbara, K. Detecting GPS spoofing attacks using corrected low-cost INS data with an LSTM network. Int. J. Adv. Comput. Sci. Appl. 2024, 15, 145–153. [Google Scholar] [CrossRef] [Scilit]
- Zhang, N.; Fang, X.; Wang, Y.; Wu, S.; Wu, H.; Kar, D. Physical-layer authentication for Internet of Things via WFRFT-based Gaussian tag embedding. IEEE Internet Things J. 2020, 7, 8374–8385. [Google Scholar] [CrossRef] [Scilit]
- Boche, H.; Schaefer, R.F.; Poor, H.V.; Fitzek, F.H.P. On the need of neuromorphic twins to detect denial-of-service attacks on communication networks. IEEE/ACM Trans. Netw. 2024, 32, 2458–2471. [Google Scholar] [CrossRef] [Scilit]
- Ren, Y.; Restivo, R.D.; Tan, W.; Wang, J.; Liu, Y.; Jiang, B.; Wang, H.; Song, H. Knowledge distillation-based GPS spoofing detection for small UAV. Future Internet 2023, 15, 389. [Google Scholar] [CrossRef] [Scilit]
- Lee, M.-H.; Liu, I.-H.; Huang, H.-C.; Li, J.-S. Cyber security in a 5G-based smart healthcare network: A base station case study. Eng. Proc. 2023, 55, 50. [Google Scholar]
- Awan, M.A.; Dalveren, Y.; Catak, F.O.; Kara, A. Deployment and implementation aspects of radio frequency fingerprinting in cybersecurity of smart grids. Electronics 2023, 12, 4914. [Google Scholar] [CrossRef] [Scilit]
- Tan, H.; Wang, M.; Shen, J.; Vijayakumar, P.; Moh, S.; Wu, Q.M.J. Blockchain-assisted conditional anonymous authentication and adaptive tree-based group key agreement for VANETs. IEEE Trans. Dependable Secure Comput. 2025; early access.
- Sutrala, A.K.; Bagga, P.; Das, A.K.; Kumar, N.; Rodrigues, J.J.P.C.; Lorenz, P. On the design of conditional privacy preserving batch verification-based authentication scheme for Internet of Vehicles deployment. IEEE Trans. Veh. Technol. 2020, 69, 5535–5548. [Google Scholar] [CrossRef] [Scilit]
- Nambundo, J.M.; Gomes, O.S.M.; Souza, A.D.; Machado, R.C.S. Cybersecurity and major cyber threats of smart meters: A systematic mapping review. Energies 2025, 18, 1445. [Google Scholar] [CrossRef] [Scilit]
- Buyukozkan, U.; Guler, M. Cybersecurity maturity model: Systematic literature review and a proposed model. Technol. Forecast. Soc. Change 2025, 213, 123996. [Google Scholar] [CrossRef] [Scilit]
- Sharma, D.; Mittal, R.; Sekhar, R.; Shah, P.; Renz, M. A bibliometric analysis of cyber security and cyber forensics research. Results Control Optim. 2023, 10, 100204. [Google Scholar] [CrossRef] [Scilit]
- Shettar, I.; Hadagali, G.S.; Kaddipujar, M.; Bulla, S.D.; Agadi, K.; Ganjihal, G.A.; Hiremath, R.; Dundannanavar, A.; Babu, B.R. Scientometric analysis of global cyber security research output based on Web of Science. Iberoam. J. Sci. Meas. Commun. 2024, 4, 1–15. [Google Scholar] [CrossRef] [Scilit]
- Omote, K.; Inoue, Y.; Terada, Y.; Shichijo, N.; Shirai, T. A scientometrics analysis of cybersecurity using e-CSTI. IEEE Access 2024, 12, 33061–33073. [Google Scholar] [CrossRef] [Scilit]
- Jayraj, I.A.; Shanmugam, B.; Azam, S.; Samy, G.N. A systematic review of radio frequency threats in IoMT. J. Sens. Actuator Netw. 2022, 11, 62. [Google Scholar] [CrossRef] [Scilit]
- Ganji, K.; Afshan, N. A bibliometric review of Internet of Things (IoT) on cybersecurity issues. J. Sci. Technol. Policy Manag. 2025, 16, 984–1002. [Google Scholar] [CrossRef] [Scilit]
- Jain, S.; Autor2, A.B.; Autor3, C.D. A scientometric analysis of reviews on the Internet of Things. J. Supercomput. 2025, 81, 12330–12352. [Google Scholar] [CrossRef] [Scilit]
- Ruiz-Rosero, J.; Ramirez-Gonzalez, G.; Williams, J.M.; Liu, H.; Khanna, R.; Pisharody, G. Internet of Things: A scientometric review. Symmetry 2017, 9, 301. [Google Scholar] [CrossRef] [Scilit]
- Alhasnawi, M.Y.; Al-Hchaimi, A.A.J.; Muhsen, Y.R.; Lekmiti, A. A bibliometric review of trends and insights of Internet of Things on cybersecurity issues. In Current and Future Trends on AI Applications; Series: Studies in Computational Intelligence; Springer: Cham, Switzerland, 2025; Volume 1178, pp. 115–128. [Google Scholar]
- Page, M.J.; McKenzie, J.E.; Bossuyt, P.M.; Boutron, I.; Hoffmann, T.C.; Mulrow, C.D.; Shamseer, L.; Tetzlaff, J.M.; Akl, E.A.; Brennan, S.E.; et al. The PRISMA 2020 statement: An updated guideline for reporting systematic reviews. BMJ 2021, 372, n71. [Google Scholar] [CrossRef] [Scilit]
- Aria, M.; Cuccurullo, C. Bibliometrix: An R-tool for comprehensive science mapping analysis. J. Inf. 2017, 11, 959–975. [Google Scholar] [CrossRef] [Scilit]
- Syriani, E.; David, I.; Kumar, G. Screening articles for systematic reviews with ChatGPT. J. Comput. Lang. 2024, 80, 101287. [Google Scholar] [CrossRef] [Scilit]
- Ngwenyama, O.; Rowe, F. Should we collaborate with AI to conduct literature reviews? Changing epistemic values in a flattening world. J. Assoc. Inf. Syst. 2024, 25, 122–136. [Google Scholar] [CrossRef] [Scilit]
- Ye, A.; Maiti, A.; Schmidt, M.; Pedersen, S.J. A hybrid semi-automated workflow for systematic and literature review processes with large language model analysis. Future Internet 2024, 16, 167. [Google Scholar] [CrossRef] [Scilit]
- Alshami, A.; Elsayed, M.; Ali, E.; Eltoukhy, A.E.E.; Zayed, T. Harnessing the power of ChatGPT for automating systematic review process: Methodology, case study, limitations, and future directions. Systems 2023, 11, 351. [Google Scholar] [CrossRef] [Scilit]
- Bolaños, F.; Salatino, A.; Osborne, F.; Motta, E. Artificial intelligence for literature reviews: Opportunities and challenges. arXiv 2024, arXiv:2402.08565. [Google Scholar] [CrossRef] [Scilit]
- Trad, F.; Yammine, R.; Charafeddine, J.; Chakhtoura, M.; Rahme, M.; El-Hajj Fuleihan, G.; Chehab, A. Streamlining systematic reviews with large language models using prompt engineering and retrieval augmented generation. BMC Med. Res. Methodol. 2025, 25, 130. [Google Scholar] [CrossRef] [Scilit]
- Balasubramanian, P.; Liyana, S.; Sankaran, H.; Sivaramakrishnan, S.; Pusuluri, S.; Pirttikangas, S.; Peltonen, E. Generative AI for cyber threat intelligence: Applications, challenges, and analysis of real-world case studies. Artif. Intell. Rev. 2025, 58, 336. [Google Scholar] [CrossRef] [Scilit]
- Issaiy, M.; Ghanaati, H.; Kolahi, S.; Shakiba, M.; Jalali, A.H.; Zarei, D.; Kazemian, S.; Avanaki, M.A.; Firouznia, K. Methodological insights into ChatGPT’s screening performance in systematic reviews. BMC Med. Res. Methodol. 2024, 24, 78. [Google Scholar] [CrossRef] [Scilit]
- Li, Y.; Datta, S.; Rastegar-Mojarad, M.; Lee, K.; Paek, H.; Glasgow, J.; Liston, C.; He, L.; Wang, X.; Xu, Y. Enhancing systematic literature reviews with generative artificial intelligence: Development, applications, and performance evaluation. J. Am. Med. Inform. Assoc. 2025, 32, 616–625. [Google Scholar] [CrossRef] [Scilit]
- Donthu, N.; Kumar, S.; Mukherjee, D.; Pandey, N.; Lim, W.M. How to conduct a bibliometric analysis: An overview and guidelines. J. Bus. Res. 2021, 133, 285–296. [Google Scholar] [CrossRef] [Scilit]
- Rezende, J.A.M.; Leão Junior, R.G.; Gomes, O.S.M. Scientometric analysis of publications on household electricity theft and energy consumption load profiling in a smart grid context. Sustainability 2024, 16, 9921. [Google Scholar] [CrossRef] [Scilit]
- Zhu, J.; Liu, W. A tale of two databases: The use of Web of Science and Scopus in academic papers. Scientometrics 2020, 123, 321–335. [Google Scholar] [CrossRef] [Scilit]
- Cao, C.; Sang, J.; Arora, R.; Chen, D.; Kloosterman, R.; Cecere, M.; Gorla, J.; Saleh, R.; Drennan, I.; Teja, B.; et al. Development of prompt templates for large language model–driven screening in systematic reviews. Ann. Intern. Med. 2025, 178, 389–401. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Nykvist, B.; Macura, B.; Xylia, M.; Olsson, E. Testing the utility of GPT for title and abstract screening in environmental systematic evidence synthesis. Environ. Evid. 2025, 14, 7. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Kim, J.J.; Rickard, M.; Dangle, P.; Batra, N.; Chua, M.E.; Khondker, A.; Szymanski, K.M.; Misseri, R.; Lorenzo, A.J. Evaluating large language models for title/abstract screening: A systematic review and meta-analysis & development of new tool. J. Med. Artif. Intell. 2023, 8, 34. [Google Scholar]
- Delgado-Chaves, F.M.; Jennings, M.J.; Atalaia, A.; Wolff, J.; Horvath, R.; Mamdouh, Z.M.; Baumbach, J.; Baumbach, L. Transforming literature screening: The emerging role of large language models in systematic reviews. Proc. Natl. Acad. Sci. USA 2025, 122, e2411962122. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Young, R.J.; Matthews, A.M.; Poston, B. Benchmarking multiple large language models for automated clinical trial data extraction in aging research. Algorithms 2025, 18, 296. [Google Scholar] [CrossRef] [Scilit]
- Reason, J.; Benbow, E.; Langham, J.; Gimblett, A.; Klijn, S.L.; Malcolm, B. Artificial intelligence to automate network meta-analyses: Four case studies to evaluate the potential application of large language models. PharmacoEcon. Open 2024, 8, 205–220. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Iqbal, U.; Tanweer, A.; Rahmanti, A.R.; Greenfield, D.; Lee, L.T.J.; Li, Y.C.J. Impact of large language model (ChatGPT) in healthcare: An umbrella review and evidence synthesis. J. Biomed. Sci. 2025, 32, 45. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Landis, J.R.; Koch, G.G. The measurement of observer agreement for categorical data. Biometrics 1977, 33, 159–174. [Google Scholar] [CrossRef] [Scilit]
- Almeida, T.; Papanikolaou, N. Auto-METRICS: LLM-assisted scientific quality control for radiomics research. Eur. J. Radiol. 2025, 191, 112358. [Google Scholar] [CrossRef] [Scilit]
- Tao, K.; Osman, Z.A.; Tzou, P.L.; Rhee, S.Y.; Ahluwalia, V.; Shafer, R.W. GPT-4 performance on querying scientific publications: Reproducibility, accuracy, and impact of an instruction sheet. BMC Med. Res. Methodol. 2024, 24, 139. [Google Scholar] [CrossRef] [Scilit]
- Liu, X.; Ding, Z. CyberRE-LLM: Cyber threat intelligence relation extraction with large language model. In Advanced Intelligent Computing Technology and Applications; Huang, D.S., Chen, H., Li, B., Zhang, Q., Eds.; Springer: Singapore, 2025; pp. 261–271. [Google Scholar]
- Sadeghi-Niaraki, A. Internet of Things (IoT) review of reviews: Bibliometric overview since its foundation. Future Gener. Comput. Syst. 2023, 143, 361–377. [Google Scholar] [CrossRef] [Scilit]
- Han, R.; Liu, M.; Wang, J.; Bai, L.; Liu, J. Anti-jamming strategy for satellite Internet of Things: Beam switching and optimization. IEEE Internet Things J. 2023, 10, 20254–20263. [Google Scholar] [CrossRef] [Scilit]
- Li, J.; Ying, Y.; Wang, S.; Zhang, B. Slice combination convolutional neural network based radio frequency fingerprint identification for Internet of Things. Wirel. Netw. 2023, 29, 2953–2966. [Google Scholar] [CrossRef] [Scilit]
- Zhang, P.; Nagarajan, S.G.; Nevat, I. Secure Location of Things (SLOT): Mitigating localization spoofing attacks in the Internet of Things. IEEE Internet Things J. 2017, 4, 2199–2206. [Google Scholar] [CrossRef] [Scilit]
- Jing, W.; Peng, L.; Fu, H.; Hu, A. An authentication mechanism based on zero trust with radio frequency fingerprint for Internet of Things networks. IEEE Internet Things J. 2024, 11, 22654–22666. [Google Scholar] [CrossRef] [Scilit]
- Liu, I.-H.; Chen, H.-H.; Tang, B.-H.; Li, J.-S. Rogue base station detection in industrial internet of things. Sens. Mater. 2025, 37, 1605–1613. [Google Scholar] [CrossRef] [Scilit]
- Tang, X.; Ren, P.; Han, Z. Jamming mitigation via hierarchical security game for IoT communications. IEEE Access 2018, 6, 57683–57693. [Google Scholar] [CrossRef] [Scilit]
- Talbot, C.M.; Temple, M.A.; Carbino, T.J.; Betances, J.A. Detecting rogue attacks on commercial wireless Insteon home automation systems. Comput. Secur. 2018, 72, 238–254. [Google Scholar] [CrossRef] [Scilit]
- Ji, Z.; Yeoh, P.L.; Chen, G.; Zhang, J.; Zhang, Y.; He, Z.; Yin, H.; Li, Y. Physical-layer-based secure communications for static and low-latency industrial Internet of Things. IEEE Internet Things J. 2022, 9, 18392–18405. [Google Scholar] [CrossRef] [Scilit]
- Taricco, G.; Alagha, N. On jamming detection methods for satellite Internet of Things networks. Int. J. Satell. Commun. Netw. 2021, 40, 1431. [Google Scholar] [CrossRef] [Scilit]
- Huan, X.; Miao, K.; Chen, W.; Jia, P.; Hu, H. KERRA: An Internet of Things wireless key generation resistant to replay attacks. IEEE Internet Things J. 2024, 11, 28513–28525. [Google Scholar] [CrossRef] [Scilit]
- Tausiesakul, B.; Goldoni, E.; Savazzi, P. Localization based on received signal strength measurement in smart cities using constrained least squares. Comput. Electr. Eng. 2025, 127, 110564. [Google Scholar] [CrossRef] [Scilit]
- Margaria, D.; Vesco, A. Trusted GNSS-based time synchronization for Industry 4.0 applications. Appl. Sci. 2021, 11, 8288. [Google Scholar] [CrossRef] [Scilit]
- Ardizzon, F.; Crosara, L.; Laurenti, N.; Tomasin, S.; Montini, N. Authenticated timing protocol based on Galileo ACAS. Sensors 2022, 22, 6298. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Huang, D.; Al-Hourani, A. Physical layer spoof detection and authentication for IoT devices using deep learning methods. IEEE Trans. Mach. Learn. Commun. Netw. 2024, 2, 841–854. [Google Scholar] [CrossRef] [Scilit]
- Abdrabou, M.; Gulliver, T.A. Adaptive physical-layer authentication for IoT in MIMO communication systems using support vector machine. IEEE Internet Things J. 2023, 10, 19861–19873. [Google Scholar] [CrossRef] [Scilit]
- Yao, X.; Yang, H.; Zeng, W. Lightweight physical-layer authentication for IoT devices access against jamming attacks. Phys. Commun. 2025, 72, 102787. [Google Scholar] [CrossRef] [Scilit]
- Sedjelmaci, H.; Senouci, S.M.; Ansari, N. A hierarchical detection and response system to enhance security against lethal cyber-attacks in UAV networks. IEEE Trans. Syst. Man Cybern. Syst. 2018, 48, 1594–1606. [Google Scholar] [CrossRef] [Scilit]
- Farraj, A.; Hammad, E. Reading lips: An analytical framework for adversarial passive detection of wireless traffic in IoT ecosystems. IEEE Access 2025, 13, 106736–106746. [Google Scholar] [CrossRef] [Scilit]
- Huan, X.; Chen, W.; Zou, Y.; Zhang, S.; Hu, H.; Marshall, A. SNICK: Secure node identification based on covert clock feature extraction for cross-environment wireless IoT. IEEE Trans. Inf. Forensics Secur. 2025, 20, 7286–7301. [Google Scholar] [CrossRef] [Scilit]
- Liang, L.; Cheng, W.; Zhang, W.; Yao, Z. Integrated sensing and communication for anti-jamming with OAM. IEEE Trans. Wirel. Commun. 2025; in press.
- Schmidt, M. The Sankey diagram in energy and material flow management. J. Ind. Ecol. 2008, 12, 82–94. [Google Scholar] [CrossRef] [Scilit]
- Shafiee, E.; Mosavi, M.R.; Moazedi, M. Detection of spoofing attack using machine learning based on multi-layer neural network in single-frequency GPS receivers. J. Navig. 2018, 71, 1366–1384. [Google Scholar] [CrossRef] [Scilit]
- Nayfeh, M.; Li, Y.; Al Shamaileh, K.; Devabhaktuni, V.; Kaabouch, N. Machine learning modeling of GPS features with applications to UAV location spoofing detection and classification. Comput. Secur. 2023, 126, 103085. [Google Scholar] [CrossRef] [Scilit]
- Huang, K.-W.; Wang, H.-M. Intelligent reflecting surface aided pilot contamination attack and its countermeasure. IEEE Trans. Wirel. Commun. 2021, 20, 345–359. [Google Scholar] [CrossRef] [Scilit]
- Zhang, J.; Cui, X.; Xu, H.; Lu, M. A two-stage interference suppression scheme based on antenna array for GNSS jamming and spoofing. Sensors 2019, 19, 3870. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Zhou, Z.; Li, H.; Chen, Z.; Lu, M. Velocity consistency checking based GNSS spoofing detection method for vehicles. IEEE Trans. Veh. Technol. 2024, 73, 1974–1990. [Google Scholar] [CrossRef] [Scilit]
- Sarpanah, Z.; Mosavi, M.R.; Shafiee, E. GPS receivers spoofing detection based on subtractive, FCM, and DBSCAN clustering algorithms. Int. J. Bifurc. Chaos 2023, 33, 2350152. [Google Scholar] [CrossRef] [Scilit]
- Zhang, J.; Wu, X. RL-based frequency hopping with block-shifted patterns: Balancing between anti-jamming performance and synchronization overhead. IEEE Trans. Veh. Technol. 2024, 73, 909–922. [Google Scholar] [CrossRef] [Scilit]
- Liu, Y.; Li, S.; Fu, Q.; Liu, Z. Impact assessment of GNSS spoofing attacks on INS/GNSS integrated navigation system. Sensors 2018, 18, 1433. [Google Scholar] [CrossRef] [Scilit]
- Sun, C.; Cheong, J.W.; Dempster, A.G.; Zhao, H.; Feng, W. GNSS spoofing detection by means of signal quality monitoring (SQM) metric combinations. IEEE Access 2018, 6, 66428–66441. [Google Scholar] [CrossRef] [Scilit]
- Yan, Q.; Zeng, H.; Jiang, T.; Li, M.; Lou, W.; Hou, Y.T. Jamming resilient communication using MIMO interference cancellation. IEEE Trans. Inf. Forensics Secur. 2016, 11, 1486–1499. [Google Scholar] [CrossRef] [Scilit]
- Nawaz, T.; Alzahrani, A. Machine-learning-assisted cyclostationary spectral analysis for joint signal classification and jammer detection at the physical layer of cognitive radio. Sensors 2023, 23, 7144. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Ihekoronye, V.U.; Ajakwe, S.O.; Lee, J.M.; Kim, D.-S. DroneGuard: An explainable and efficient machine learning framework for intrusion detection in drone networks. IEEE Internet Things J. 2025, 12, 7708–7722. [Google Scholar] [CrossRef] [Scilit]
- Gupta, A.; Jha, R.K.; Gandotra, P.; Jain, S. Bandwidth spoofing and intrusion detection system for multistage 5G wireless communication network. IEEE Trans. Veh. Technol. 2018, 67, 618–632. [Google Scholar] [CrossRef] [Scilit]
- Le, V.H.; Nguyen, T.T.; Nguyen, K.K. Dual anti-jamming alleviation for radio frequency/free-space optical (RF/FSO) tactical systems. IEEE Trans. Veh. Technol. 2025, 74, 1092–1103. [Google Scholar] [CrossRef] [Scilit]
- Del-Valle-Soto, C.; Valdivia, L.J.; Velázquez, R.; Del-Puerto-Flores, J.A.; Varela-Aldás, J.; Visconti, P. Adaptive jamming mitigation for clustered energy-efficient LoRa-BLE hybrid wireless sensor networks. Sensors 2025, 25, 1931. [Google Scholar] [CrossRef] [Scilit]
- Wang, Z.; Li, G.; Wang, Z. GPS attack detection and defense for secure localization of automated vehicles based on vehicle-to-vehicle technology. IEEE Internet Things J. 2025, 12, 7723–7735. [Google Scholar] [CrossRef] [Scilit]
- Pirayesh, H.; Sangdeh, P.K.; Zeng, H. Securing ZigBee communications against constant jamming attack using neural network. IEEE Internet Things J. 2021, 8, 4842–4854. [Google Scholar] [CrossRef] [Scilit]
- Osanaiye, O.; Alfa, A.S.; Hancke, G.P. A statistical approach to detect jamming attacks in wireless sensor networks. Sensors 2018, 18, 1691. [Google Scholar] [CrossRef] [Scilit]
- Pritika; Shanmugam, B.; Azam, S. Risk evaluation and attack detection in heterogeneous IoMT devices using hybrid fuzzy logic analytical approach. Sensors 2024, 24, 3223. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Jeon, G.-H.; Lee, J.-H.; Sung, Y.-S.; Park, H.-J.; Lee, Y.-J.; Yun, S.-W.; Lee, I.-G. Cooperative friendly jamming techniques for drone-based mobile secure zone. Sensors 2022, 22, 865. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Bradford, S.C. Sources of information on specific subjects. J. Inf. Sci. 1934, 10, 176–180. [Google Scholar]
- Tanil, C.; Khanafseh, S.; Joerger, M.; Pervan, B. An INS monitor to detect GNSS spoofers capable of tracking vehicle position. IEEE Trans. Aerosp. Electron. Syst. 2018, 54, 131–143. [Google Scholar] [CrossRef] [Scilit]
- Yang, J.; Ji, X.; Wang, F.; Huang, K.; Guo, L. A novel pilot spoofing scheme via intelligent reflecting surface based on statistical CSI. IEEE Trans. Veh. Technol. 2021, 70, 12885–12897. [Google Scholar] [CrossRef] [Scilit]
- Fan, Y.; Zhang, Z.; Trinkle, M.; Dimitrovski, A.D.; Song, J.B.; Li, H. A cross-layer defense mechanism against GPS spoofing attacks on PMUs in smart grids. IEEE Trans. Smart Grid 2015, 6, 2659–2668. [Google Scholar] [CrossRef] [Scilit]
- Zhu, L.; Li, Y.; Yu, F.R.; Ning, B.; Tang, T.; Wang, X. Cross-layer defense methods for jamming-resistant CBTC systems. IEEE Trans. Intell. Transp. Syst. 2021, 22, 7266–7278. [Google Scholar] [CrossRef] [Scilit]
- Liu, Z.; Liu, H.; Xu, W.; Chen, Y. Exploiting Jamming-Caused Neighbor Changes for Jammer Localization. IEEE Trans. Parallel Distrib. Syst. 2012, 23, 547–555. [Google Scholar] [CrossRef] [Scilit]
- Su, H.; Qiu, M.; Wang, H. Secure Wireless Communication System for Smart Grid with Rechargeable Electric Vehicles. IEEE Commun. Mag. 2012, 50, 62–68. [Google Scholar] [CrossRef] [Scilit]
- Wang, F.; Li, H.; Lu, M. GNSS spoofing countermeasure with a single rotating antenna. IEEE Access 2017, 5, 13641–13648. [Google Scholar] [CrossRef] [Scilit]
- Lotka, A.J. The frequency distribution of scientific productivity. J. Wash. Acad. Sci. 1926, 16, 317–323. [Google Scholar]
- Wei, X.; Sun, C.; Li, X.; Ma, J. GNSS Spoofing Detection for UAVs Using Doppler Frequency and Carrier-to-Noise Density Ratio. J. Syst. Archit. 2024, 153, 103212. [Google Scholar] [CrossRef] [Scilit]
- Zhou, Z.; Li, H.; Lu, M. Doppler-Based RAIM for GNSS Spoofing Detection in Vehicular Applications. IEEE Trans. Veh. Technol. 2025, 74, 10306–10320. [Google Scholar] [CrossRef] [Scilit]
- Ma, S.; Wang, H.; Zhu, L.; Zhang, Q. Joint Security and Resilience Control in IIoT-Based Virtual Control Train Sets Under Jamming Attacks. IEEE Trans. Veh. Technol. 2023, 72, 11196–11212. [Google Scholar] [CrossRef] [Scilit]
- Xing, Y.; Hu, A.; Zhang, J.; Yu, J.; Li, G.; Wang, T. Design of a Robust Radio-Frequency Fingerprint Identification Scheme for Multimode LFM Radar. IEEE Internet Things J. 2020, 7, 10581–10593. [Google Scholar] [CrossRef] [Scilit]
- Qi, X.; Liu, Y.; Ye, Y. Attention-Enhanced Defensive Distillation Network for Channel Estimation in V2X mm-Wave Secure Communication. Sensors 2024, 24, 6464. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Bai, L.; Sun, C.; Dempster, A.G.; Zhao, H.; Feng, W. GNSS Spoofing Detection and Mitigation with a Single 5G Base Station Aiding. IEEE Trans. Aerosp. Electron. Syst. 2024, 60, 4601–4620. [Google Scholar] [CrossRef] [Scilit]
- Shepard, D.P.; Humphreys, T.E.; Fansler, A.A. Evaluation of the vulnerability of phasor measurement units to GPS spoofing attacks. Int. J. Crit. Infrastruct. Prot. 2012, 5, 146–153. [Google Scholar] [CrossRef] [Scilit]
- Xiao, L.; Wan, X.; Dai, C.; Du, X.; Chen, X.; Guizani, M. Security in mobile edge caching with reinforcement learning. IEEE Wirel. Commun. 2018, 25, 116–122. [Google Scholar] [CrossRef] [Scilit]
- Sankhe, K.; Belgiovine, M.; Zhou, F.; Angioloni, L.; Restuccia, F.; D’Oro, S. No radio left behind: Radio fingerprinting through deep learning of physical-layer hardware impairments. IEEE Trans. Cogn. Commun. Netw. 2020, 6, 165–178. [Google Scholar] [CrossRef] [Scilit]
- Humphreys, T.E. Detection strategy for cryptographic GNSS anti-spoofing. IEEE Trans. Aerosp. Electron. Syst. 2013, 49, 1073–1090. [Google Scholar] [CrossRef] [Scilit]
- Psiaki, M.L.; O’Hanlon, B.W.; Bhatti, J.A.; Shepard, D.P.; Humphreys, T.E. GPS spoofing detection via dual-receiver correlation of military signals. IEEE Trans. Aerosp. Electron. Syst. 2013, 49, 2250–2267. [Google Scholar] [CrossRef] [Scilit]
- Jiang, X.; Zhang, J.; Harding, B.J.; Makela, J.J.; Domínguez-García, A.D. Spoofing GPS Receiver Clock Offset of Phasor Measurement Units. IEEE Trans. Power Syst. 2013, 28, 3253–3262. [Google Scholar] [CrossRef] [Scilit]
- Reising, D.R.; Temple, M.A.; Jackson, J.A. Authorized and Rogue Device Discrimination Using Dimensionally Reduced RF-DNA Fingerprints. IEEE Trans. Info. Foren. Secur. 2015, 10, 1180–1192. [Google Scholar] [CrossRef] [Scilit]
- He, D.; Chan, S.; Guizani, M. Communication Security of Unmanned Aerial Vehicles. IEEE Wirel. Commun. 2017, 24, 134–139. [Google Scholar] [CrossRef] [Scilit]
- Guo, Y.; Wu, M.; Tang, K.; Tie, J.; Li, X. Covert spoofing algorithm of UAV based on GPS/INS-integrated navigation. IEEE Trans. Veh. Technol. 2019, 68, 6502–6515. [Google Scholar] [CrossRef] [Scilit]
- Yu, J.; Muñoz-Justicia, J. A bibliometric overview of Twitter-related studies indexed in Web of Science. Future Internet 2020, 12, 91. [Google Scholar] [CrossRef] [Scilit]
- Cao, X.; Shila, D.M.; Cheng, Y.; Yang, Z.; Zhou, Y.; Chen, J. GHOST-IN-ZIGBEE: Energy depletion attack on ZigBee-based wireless networks. IEEE Internet Things J. 2016, 3, 816–829. [Google Scholar] [CrossRef] [Scilit]
- Gao, N.; Han, Y.; Li, N.; Jin, S.; Matthaiou, M. When physical layer key generation meets RIS: Opportunities, challenges, and road ahead. IEEE Wirel. Commun. 2024, 31, 90–97. [Google Scholar] [CrossRef] [Scilit]
- Sabic, J.; Perkovic, T.; Begusic, D.; Solic, P. Practical realization of reactive jamming attack on long-range wide-area network. Sensors 2025, 25, 2383. [Google Scholar] [CrossRef] [Scilit]
- Barkatsa, S.; Diamanti, M.; Charatsaris, P.; Voikos, S.; Tsiropoulou, E.E.; Papavassiliou, S. Coordinated Jamming and Poisoning Attack Detection and Mitigation in Wireless Federated Learning Networks. IEEE Open J. Commun. Soc. 2025, 6, 3745–3759. [Google Scholar] [CrossRef] [Scilit]
- Li, G.; Staat, P.; Li, H.; Heinrichs, M.; Zenger, C.; Kronberger, R. RIS-jamming: Breaking key consistency in channel reciprocity-based key generation. IEEE Trans. Inf. Forensics Secur. 2024, 19, 2824–2837. [Google Scholar] [CrossRef] [Scilit]
- Lyu, B.; Hoang, D.T.; Gong, S.; Niyato, D.; Kim, D.I. IRS-based wireless jamming attacks: When jammers can attack without power. IEEE Wirel. Commun. Lett. 2020, 9, 1663–1667. [Google Scholar] [CrossRef] [Scilit]
- Yang, Z.; Ying, J.; Shen, J.; Feng, Y.; Chen, Q.A.; Mao, Z.M. Anomaly detection against GPS spoofing attacks on connected and autonomous vehicles using learning from demonstration. IEEE Trans. Intell. Transp. Syst. 2023, 24, 9484–9498. [Google Scholar] [CrossRef] [Scilit]
- Uflaz, E.; Sezer, S.I.; Tunçel, A.L.; Aydin, M.; Akyuz, E.; Arslan, O. Quantifying potential cyber-attack risks in maritime transportation under Dempster-Shafer theory FMECA and rule-based Bayesian network modelling. Reliab. Eng. Syst. Saf. 2024, 243, 109825. [Google Scholar] [CrossRef] [Scilit]
- Khan, M.M.; Kamal, M.; Shabbir, M.; Alahmari, S. Enhancing Autonomous Vehicle Security: Federated Learning for Detecting GPS Spoofing Attack. Trans. Emerg. Telecommun. Technol. 2025, 36, e70138. [Google Scholar] [CrossRef] [Scilit]
- Ma, T.; Zhang, X.; Miao, Z. Detection of UAV GPS Spoofing Attacks Using a Stacked Ensemble Method. Drones 2025, 9, 2. [Google Scholar] [CrossRef] [Scilit]
- Xie, Y.-A.; Kang, J.; Niyato, D.; Van, N.T.T.; Luong, N.C.; Liu, Z. Securing federated learning: A covert communication-based approach. IEEE Netw. 2023, 37, 58–64. [Google Scholar] [CrossRef] [Scilit]
- Salem, O.; Alsubhi, K.; Shaafi, A.; Gheryani, M.; Mehaoua, A.; Boutaba, R. Man-in-the-middle attack mitigation in Internet of Medical Things. IEEE Trans. Ind. Inf. 2022, 18, 2101–2112. [Google Scholar] [CrossRef] [Scilit]
- Bhattacharya, S.; Seshasai, B.; Koley, E.; Ghosh, S. A Cyber-Resilient Mechanism for Detection, Classification and Mitigation of Intrusion on Synchrophasor Data in Power Networks. Int. J. Crit. Infrastruct. Prot. 2025, 50, 100785. [Google Scholar] [CrossRef] [Scilit]
- Boschetti, N.; Karabulut Kurt, G.; Falco, G. High-Altitude Platform Station Systems Cybersecurity Analysis. J. Intell. Mater. Syst. Struct. 2025, 22, 693–702. [Google Scholar] [CrossRef] [Scilit]
- Suresh, D.; Joshi, P.V.; Parandkar, P.; Gambhir, A.; Sudharshan, K.M. BLE channel sounding: Novel method for enhanced ranging accuracy in vehicle access. IEEE Access 2025, 13, 19827–19838. [Google Scholar] [CrossRef] [Scilit]
- Senol, N.S.; Rasheed, A.; Baza, M.; Alsabaan, M. Identifying Tampered Radio-Frequency Transmissions in LoRa Networks Using Machine Learning. Sensors 2024, 24, 6611. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Hoque, N.; Rahbari, H. Locking down relay and spoofing attacks during concurrent connection establishments in 802.11ax. IEEE Trans. Depend. Secure Comput. 2025, 22, 7287–7301. [Google Scholar] [CrossRef] [Scilit]
- Minilal, M.; Meena, M. Security threat analysis in 5G cognitive radio networks: A deep learning ensemble approach. Int. J. Saf. Secur. Eng. 2025, 15, 159–166. [Google Scholar] [CrossRef] [Scilit]
- Gesteira-Minarro, R.; Lopez, G.; Palacios, R. Clonable key fobs: Analyzing and breaking RKE protocols. Int. J. Inf. Secur. 2025, 24, 150. [Google Scholar] [CrossRef] [Scilit]
- Pari, D.; Natarajan, J. Defense against SSDF attack and PUE attack in CR-Internet of Vehicles (IoVs) for millimeter wave massive MIMO beamforming systems. Symmetry 2022, 14, 2472. [Google Scholar] [CrossRef] [Scilit]
- Chen, S.; Pang, Z.; Wen, H.; Yu, K.; Zhang, T.; Lu, Y. Automated labeling and learning for physical layer authentication against clone node and Sybil attacks in industrial wireless edge networks. IEEE Trans. Ind. Inf. 2021, 17, 2101–2112. [Google Scholar] [CrossRef] [Scilit]
- Siamak, S.; Dehghani, M.; Mohammadi, M. Dynamic GPS spoofing attack detection, localization, and measurement correction exploiting PMU and SCADA. IEEE Syst. J. 2021, 15, 2180–2189. [Google Scholar] [CrossRef] [Scilit]
- Coluccia, A.; Fascista, A.; Nicolazzo, J.; Coronese, S. Random Slope Coding for Jamming Attack Mitigation in FMCW Radars. IEEE Trans. Aerosp. Electron. Syst. 2025, 61, 5416–5425. [Google Scholar] [CrossRef] [Scilit]
- Ma, D.; Wang, Y.; Wu, S. Against Jamming Attack in Wireless Communication Networks: A Reinforcement Learning Approach. Electronics 2024, 13, 1209. [Google Scholar] [CrossRef] [Scilit]
- She, D.; Wang, W.; Yin, Z.; Wang, J.; Shan, H. GPS Spoofing Attack Recognition for UAVs with Limited Samples. IEEE Internet Things J. 2025, 12, 250–261. [Google Scholar] [CrossRef] [Scilit]
- Chen, Q.; Li, G.; Liu, P.; Wang, Z. Anomaly Detection and Secure Position Estimation Against GPS Spoofing Attack: A Security-Critical Study of Localization in Autonomous Driving. IEEE Trans. Veh. Technol. 2025, 74, 87–99. [Google Scholar] [CrossRef] [Scilit]
- Li, S.; Lin, H.; Tang, X.; Wang, F. Blind spoofing detection for anti-jamming multiantenna GNSS receivers. IEEE Sens. J. 2024, 24, 36316–36326. [Google Scholar] [CrossRef] [Scilit]
- Wang, S.-Q.; Liu, J.; Cai, B.-G.; Wang, J.; Lu, D.-B. BOSVDD-Based GNSS Spoofing Detect for rail vehicle positioning. IEEE Trans. Instrum. Meas. 2025, 74, 8500418. [Google Scholar]
- Li, X.; Zhang, H.; Yu, X.; Liu, W.; Zhao, N. A Robust Reliability-Centric Method for Swift Spoofing Signal Detection in Advanced GNSS Security. Chin. J. Electron. 2025, 34, 774–786. [Google Scholar] [CrossRef] [Scilit]
- Singh, M.; Kumar, N. Spoofing Attack Detection in 5G Network. J. Commun. 2024, 19, 308–316. [Google Scholar]
- Focarelli, G.; Zanini, S.; Palamà, I.; Bianchi, G.; Bartoletti, S. Positioning Security in 5G and Beyond: Model and Detection of Physical Layer Threats. IEEE Trans. Wirel. Commun. 2025, 25, 1048–1061. [Google Scholar] [CrossRef] [Scilit]
- Meng, R.; Zhu, F.; Cheng, X.; Xu, X.; Wang, B.; Dong, C.; Xu, B.; Tao, X.; Zhang, P. Efficient Gaussian Process Classification-Based Physical-Layer Authentication with Configurable Fingerprints for 6G-Enabled IoT. IEEE Trans. Consum. Electron. 2025, 71, 2603–2617. [Google Scholar] [CrossRef] [Scilit]
- Sharma, H.; Kumar, N.; Tekchandani, R. Mitigating Jamming Attack in 5G Heterogeneous Networks: A Federated Deep Reinforcement Learning Approach. IEEE Trans. Veh. Technol. 2023, 72, 2439–2452. [Google Scholar] [CrossRef] [Scilit]
- Zahra, F.T.; Bostanci, Y.S.; Soyturk, M. Real-time jamming detection in wireless IoT networks. IEEE Access 2023, 11, 72016–72027. [Google Scholar] [CrossRef] [Scilit]
- Allen, A.; Mylonas, A.; Vidalis, S.; Gritzalis, D. Smart homes under siege: Assessing the robustness of physical security against wireless network attacks. Comput. Secur. 2024, 139, 103687. [Google Scholar] [CrossRef] [Scilit]
- Ingham, M.; Marchang, J.; Bhowmik, D. IoT security vulnerabilities and predictive signal jamming attack analysis in LoRaWAN. IET Inf. Secur. 2020, 14, 376–385. [Google Scholar] [CrossRef] [Scilit]
- Hou, N.; Xia, X.; Zheng, Y. Jamming of LoRa PHY and Countermeasure. ACM Trans. Sens. Netw. 2023, 19, 1–25. [Google Scholar] [CrossRef] [Scilit]
- Tsai, Y.-H.; Chen, S.-J. Exposing and Addressing Fake Base Station Vulnerabilities in 5G Through User Device Exploits. IT Prof. 2025, 27, 45–51. [Google Scholar] [CrossRef] [Scilit]
- Parameswarath, R.P.; Sikdar, B. A Secure PUF-Based Authentication Protocol for Remote Keyless Entry Systems in Cars. IEEE Trans. Veh. Technol. 2024, 73, 9451–9462. [Google Scholar] [CrossRef] [Scilit]
- Park, H.; Lee, W. Rethinking Tag Collisions for Replay and Relay Attack Resistance in Backscatter Networks. IEEE Access 2023, 11, 37210–37222. [Google Scholar] [CrossRef] [Scilit]
- Zhang, Y.; Xie, B.; Yang, Y.; Yan, Z.; Jäntti, R.; Han, Z. AuthScatter: Accurate, Robust, and Scalable Mutual Authentication in Physical Layer for Backscatter Communications. IEEE Trans. Inf. Forensics Secur. 2025, 20, 6937–6952. [Google Scholar] [CrossRef] [Scilit]
- Shi, Y.; Lu, X.; An, K.; Li, Y.; Zheng, G. Efficient index-modulation-based FHSS: A unified anti-jamming perspective. IEEE Internet Things J. 2024, 11, 3124–3138. [Google Scholar] [CrossRef] [Scilit]
- Pospisil, O.; Fujdiak, R.; Mikhaylov, K.; Ruotsalainen, H.; Misurec, J. Testbed for LoRaWAN security: Design and validation through man-in-the-middle attacks study. Appl. Sci. 2021, 11, 7642. [Google Scholar] [CrossRef] [Scilit]
- Zhang, T.; Xu, D.; Ma, J.; Bashir, A.K.; Al Dabel, M.M.; Feng, H. Deep Federated Fractional Scattering Network for Heterogeneous Edge Internet of Vehicles Fingerprinting: Theory and Implementation. IEEE Internet Things J. 2025, 12, 4212–4226. [Google Scholar] [CrossRef] [Scilit]
- Abdollahi, M.; Malekinasab, K.; Tu, W.; Bag-Mohammadi, M. Physical-Layer Jammer Detection in Multihop IoT Networks. IEEE Internet Things J. 2023, 10, 20574–20585. [Google Scholar] [CrossRef] [Scilit]
- Lee, S.-J.; Lee, Y.-R.; Jeon, S.-E.; Lee, I.-G. Machine Learning-Based Jamming Attack Classification and Effective Defense Technique. Comput. Secur. 2023, 128, 103169. [Google Scholar] [CrossRef] [Scilit]
- Loukil, S.; Chaari Fourati, L.; Nayyar, A.; So-In, C. Investigation on Security Risk of LoRaWAN: Compatibility Scenarios. IEEE Access 2022, 10, 98933–98947. [Google Scholar] [CrossRef] [Scilit]
- Bajracharya, C. Performance Evaluation for Secure Communications in Mobile Internet of Vehicles with Joint Reactive Jamming and Eavesdropping Attacks. IEEE Trans. Intell. Transp. Syst. 2022, 23, 20756–20766. [Google Scholar] [CrossRef] [Scilit]
- Sharma, K. Internet of Healthcare Things Security Vulnerabilities and Jamming Attack Analysis. Expert Syst. 2023, 40, e12853. [Google Scholar] [CrossRef] [Scilit]
- Ronen, R.; Ben-Moshe, B. Cyberattack on Flight Safety: Detection and Mitigation Using LoRa. Sensors 2021, 21, 4610. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Perković, T.; Rudeš, H.; Damjanović, S.; Nakić, A. Low-Cost Implementation of Reactive Jammer on LoRaWAN Network. Electronics 2021, 10, 864. [Google Scholar] [CrossRef] [Scilit]
- Letafati, M.; Kuhestani, A.; Behroozi, H.; Ng, D.W.K. Jamming-Resilient Frequency Hopping-Aided Secure Communication for Internet-of-Things in the Presence of an Untrusted Relay. IEEE Trans. Wirel. Commun. 2020, 19, 6790–6805. [Google Scholar] [CrossRef] [Scilit]
- Danish, S.M.; Lestas, M.; Qureshi, H.K.; Zhang, K.; Asif, W.; Rajarajan, M. Securing the LoRaWAN Join Procedure Using Blockchains. Clust. Comput. 2020, 23, 2123–2138. [Google Scholar] [CrossRef] [Scilit]
- Bhamidipati, S.; Gao, G.X. Locating Multiple GPS Jammers Using Networked UAVs. IEEE Internet Things J. 2019, 6, 3108–3118. [Google Scholar] [CrossRef] [Scilit]
- Proto, A.; Miers, C.C.; Carvalho, T.C.M.B. Lightweight Architecture for Intrusion Detection of Energy Depletion Attacks in LoRaWAN End Devices. SN Comput. Sci. 2025, 6, 690. [Google Scholar] [CrossRef] [Scilit]
- Asemian, G.; Amini, M.; Kantarci, B. Active RIS-NOMA Uplink in URLLC, Jamming Mitigation via Surrogate and Deep Learning. IEEE Open J. Commun. Soc. 2025, 6, 2399–2414. [Google Scholar] [CrossRef] [Scilit]
- Arcangeloni, L.; Testi, E.; Giorgetti, A. Detection of Jamming Attacks via Source Separation and Causal Inference. IEEE Trans. Commun. 2023, 71, 4519–4533. [Google Scholar] [CrossRef]
- Razgūnas, M.; Rudys, S.; Aleksiejūnas, R. GNSS 2×2 Antenna Array with Beamforming for Multipath Detection. Adv. Space Res. 2023, 71, 4142–4154. [Google Scholar] [CrossRef] [Scilit]
- Okada, S.; Akashi, K.; Miyamoto, D.; Sekiya, Y.; Takase, H.; Nakamura, H. Memory-Saving LDoS Attacker Detection Algorithms in ZigBee Network. J. Inf. Process. 2023, 31, 537–546. [Google Scholar] [CrossRef] [Scilit]
- Li, T.; Deng, J.; Ren, J. Security and Energy Efficiency: Breaking the Barriers of High Peak-to-Average Power Ratio and Disguised Jamming in NextG IoT System Design. IEEE Internet Things J. 2023, 10, 2471–2481. [Google Scholar] [CrossRef] [Scilit]
- Ahmar, A.-U.-H.; Aras, E.; Nguyen, T.D.; Michiels, S.; Joosen, W.; Hughes, D. Design of a Robust MAC Protocol for LoRa. ACM Trans. Internet Things 2023, 4, 1–25. [Google Scholar] [CrossRef] [Scilit]
- Miniaoui, S.; Muammar, S.; Lubamba, C.; Fachkha, C. Comparing Cyber Physical Systems with RFID Applications: Common Attacks and Countermeasure Challenges. Int. J. Bus. Inf. Syst. 2022, 40, 540–559. [Google Scholar] [CrossRef] [Scilit]
- Mbarek, B.; Ge, M.; Pitner, T. Trust-Based Authentication for Smart Home Systems. Wirel. Pers. Commun. 2021, 117, 2157–2172. [Google Scholar] [CrossRef] [Scilit]
- O’Mahony, G.D.; McCarthy, K.G.; Harris, P.J.; Murphy, C.C. Developing Novel Low Complexity Models Using Received In-Phase and Quadrature-Phase Samples for Interference Detection and Classification in Wireless Sensor Network and GPS Edge Devices. Ad Hoc Netw. 2021, 120, 102562. [Google Scholar] [CrossRef] [Scilit]
- Wei, X.; Wang, T.; Tang, C. Throughput Analysis of Smart Buildings-Oriented Wireless Networks Under Jamming Attacks. Mob. Netw. Appl. 2021, 26, 1440–1448. [Google Scholar] [CrossRef] [Scilit]
- Halder, S.; Newe, T. Radio Fingerprinting for Anomaly Detection Using Federated Learning in LoRa-Enabled Industrial Internet of Things. Future Gener. Comput. Syst. 2023, 143, 322–336. [Google Scholar] [CrossRef] [Scilit]
- Xu, W.; Liu, J.; Zhang, S.; Zheng, Y.; Lin, F.; Xiao, F. Anti-Spoofing Facial Authentication Based on COTS RFID. IEEE Trans. Mob. Comput. 2024, 23, 2917–2931. [Google Scholar] [CrossRef] [Scilit]
- Nosouhi, M.R.; Sood, K.; Grobler, M.; Doss, R. Towards Spoofing Resistant Next Generation IoT Networks. IEEE Trans. Inf. Forensics Secur. 2022, 17, 2654–2668. [Google Scholar] [CrossRef] [Scilit]
- He, D.; Chan, S.; Qiao, Y.; Guizani, N. Imminent Communication Security for Smart Communities. IEEE Commun. Mag. 2018, 56, 42–47. [Google Scholar] [CrossRef] [Scilit]
- Xiao, L.; Greenstein, L.J.; Mandayam, N.B.; Trappe, W. Channel-Based Detection of Sybil Attacks in Wireless Networks. IEEE Trans. Inf. Forensics Secur. 2009, 4, 492–503. [Google Scholar] [CrossRef] [Scilit]
- Wang, J.; Nie, L.; Gu, Z.; Wang, J.; Tan, R.; Kumari, S. Real-Time GPS Spoofing Detection in Consumer Drones Through Multi-Sensor Data Fusion and TimesNet. IEEE Trans. Consum. Electron. 2025, 71, 327–339. [Google Scholar] [CrossRef] [Scilit]
- Gao, S.-Y.; Li, X.-H.; Ma, M.-D. A Malicious Behavior Awareness and Defense Countermeasure Based on LoRaWAN Protocol. Sensors 2019, 19, 5122. [Google Scholar] [CrossRef] [Scilit] [PubMed]
- Mohan, V.S.; Sankaran, S.; Kumar, V.; Achuthan, K. EP-CuMAC: Energy and Performance-Efficient Integrity Protection for Narrow-Band IoT. Internet Things 2024, 25, 101004. [Google Scholar] [CrossRef] [Scilit]
- Wang, G.; Cai, H.; Qian, C.; Han, J.; Shi, S.; Li, X. Hu-Fu: Replay-Resilient RFID Authentication. IEEE/ACM Trans. Netw. 2020, 28, 707–720. [Google Scholar] [CrossRef] [Scilit]
- Giannakas, F.; Troussas, C.; Krouska, A.; Voyiatzis, I.; Sgouropoulou, C. Blending Cybersecurity Education with IoT Devices: A u-Learning Scenario for Introducing the Man-in-the-Middle Attack. Inf. Secur. J. Glob. Perspect. 2022, 32, 371–382. [Google Scholar] [CrossRef] [Scilit]
- Hadi, H.J.; Cao, Y.; Khan, M.K.; Ahmad, N.; Hu, Y.; Fu, C. UAV-NIDD: A dynamic dataset for cybersecurity and intrusion detection in UAV networks. IEEE Trans. Netw. Sci. Eng. 2025, 12, 1974–1986. [Google Scholar] [CrossRef] [Scilit]
- Cetinkaya, A.; Ishii, H.; Hayakawa, T. Effects of Jamming Attacks on Wireless Networked Control Systems Under Disturbance. IEEE Trans. Autom. Control 2022, 67, 4275–4290. [Google Scholar] [CrossRef] [Scilit]
- Cynthia, J.; Rathi, S. A Novel EKF-Integrated Attention-Enhanced CNN-GRU Framework for Precise GPS Spoofing Detection. Signal Image Video Process. 2025, 19, 491. [Google Scholar] [CrossRef] [Scilit]
- Tan, H.; Xie, N.; Huang, L.; Li, H. Enhancing GNSS Signal Authentication Through Multi-Antenna Systems. IEEE Trans. Wirel. Commun. 2025, 24, 4361–4376. [Google Scholar] [CrossRef] [Scilit]
- Wang, Z.; Cheng, L.; Yun, Z.; Rusen, L.; Meng, Y. Anti-Spoofing: Integrated Information Authentication of BeiDou-II Civil Navigation Message. China Commun. 2024, 21, 242–261. [Google Scholar]
- Wu, Z.; Bai, Y.; Zhang, Y.; Liu, L.; Yue, M. TrustCNAV: Certificateless Aggregate Authentication of Civil Navigation Messages in GNSS. Comput. Secur. 2025, 148, 104172. [Google Scholar] [CrossRef] [Scilit]
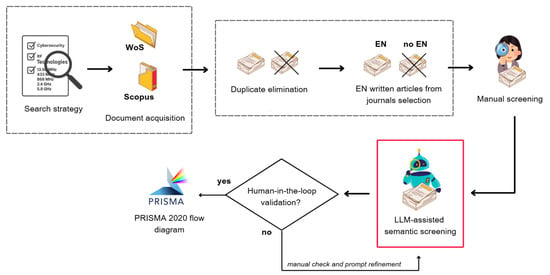
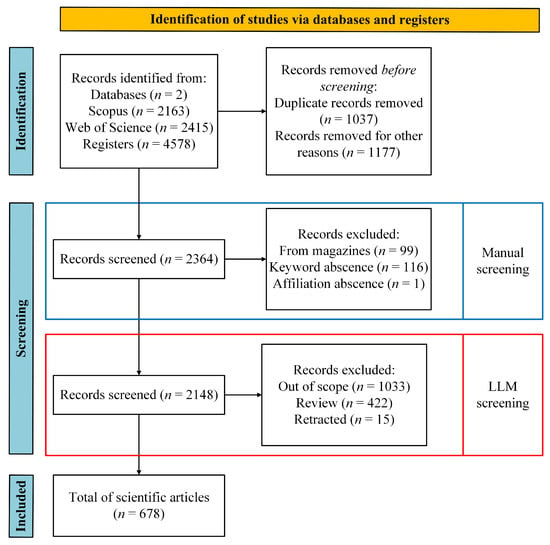
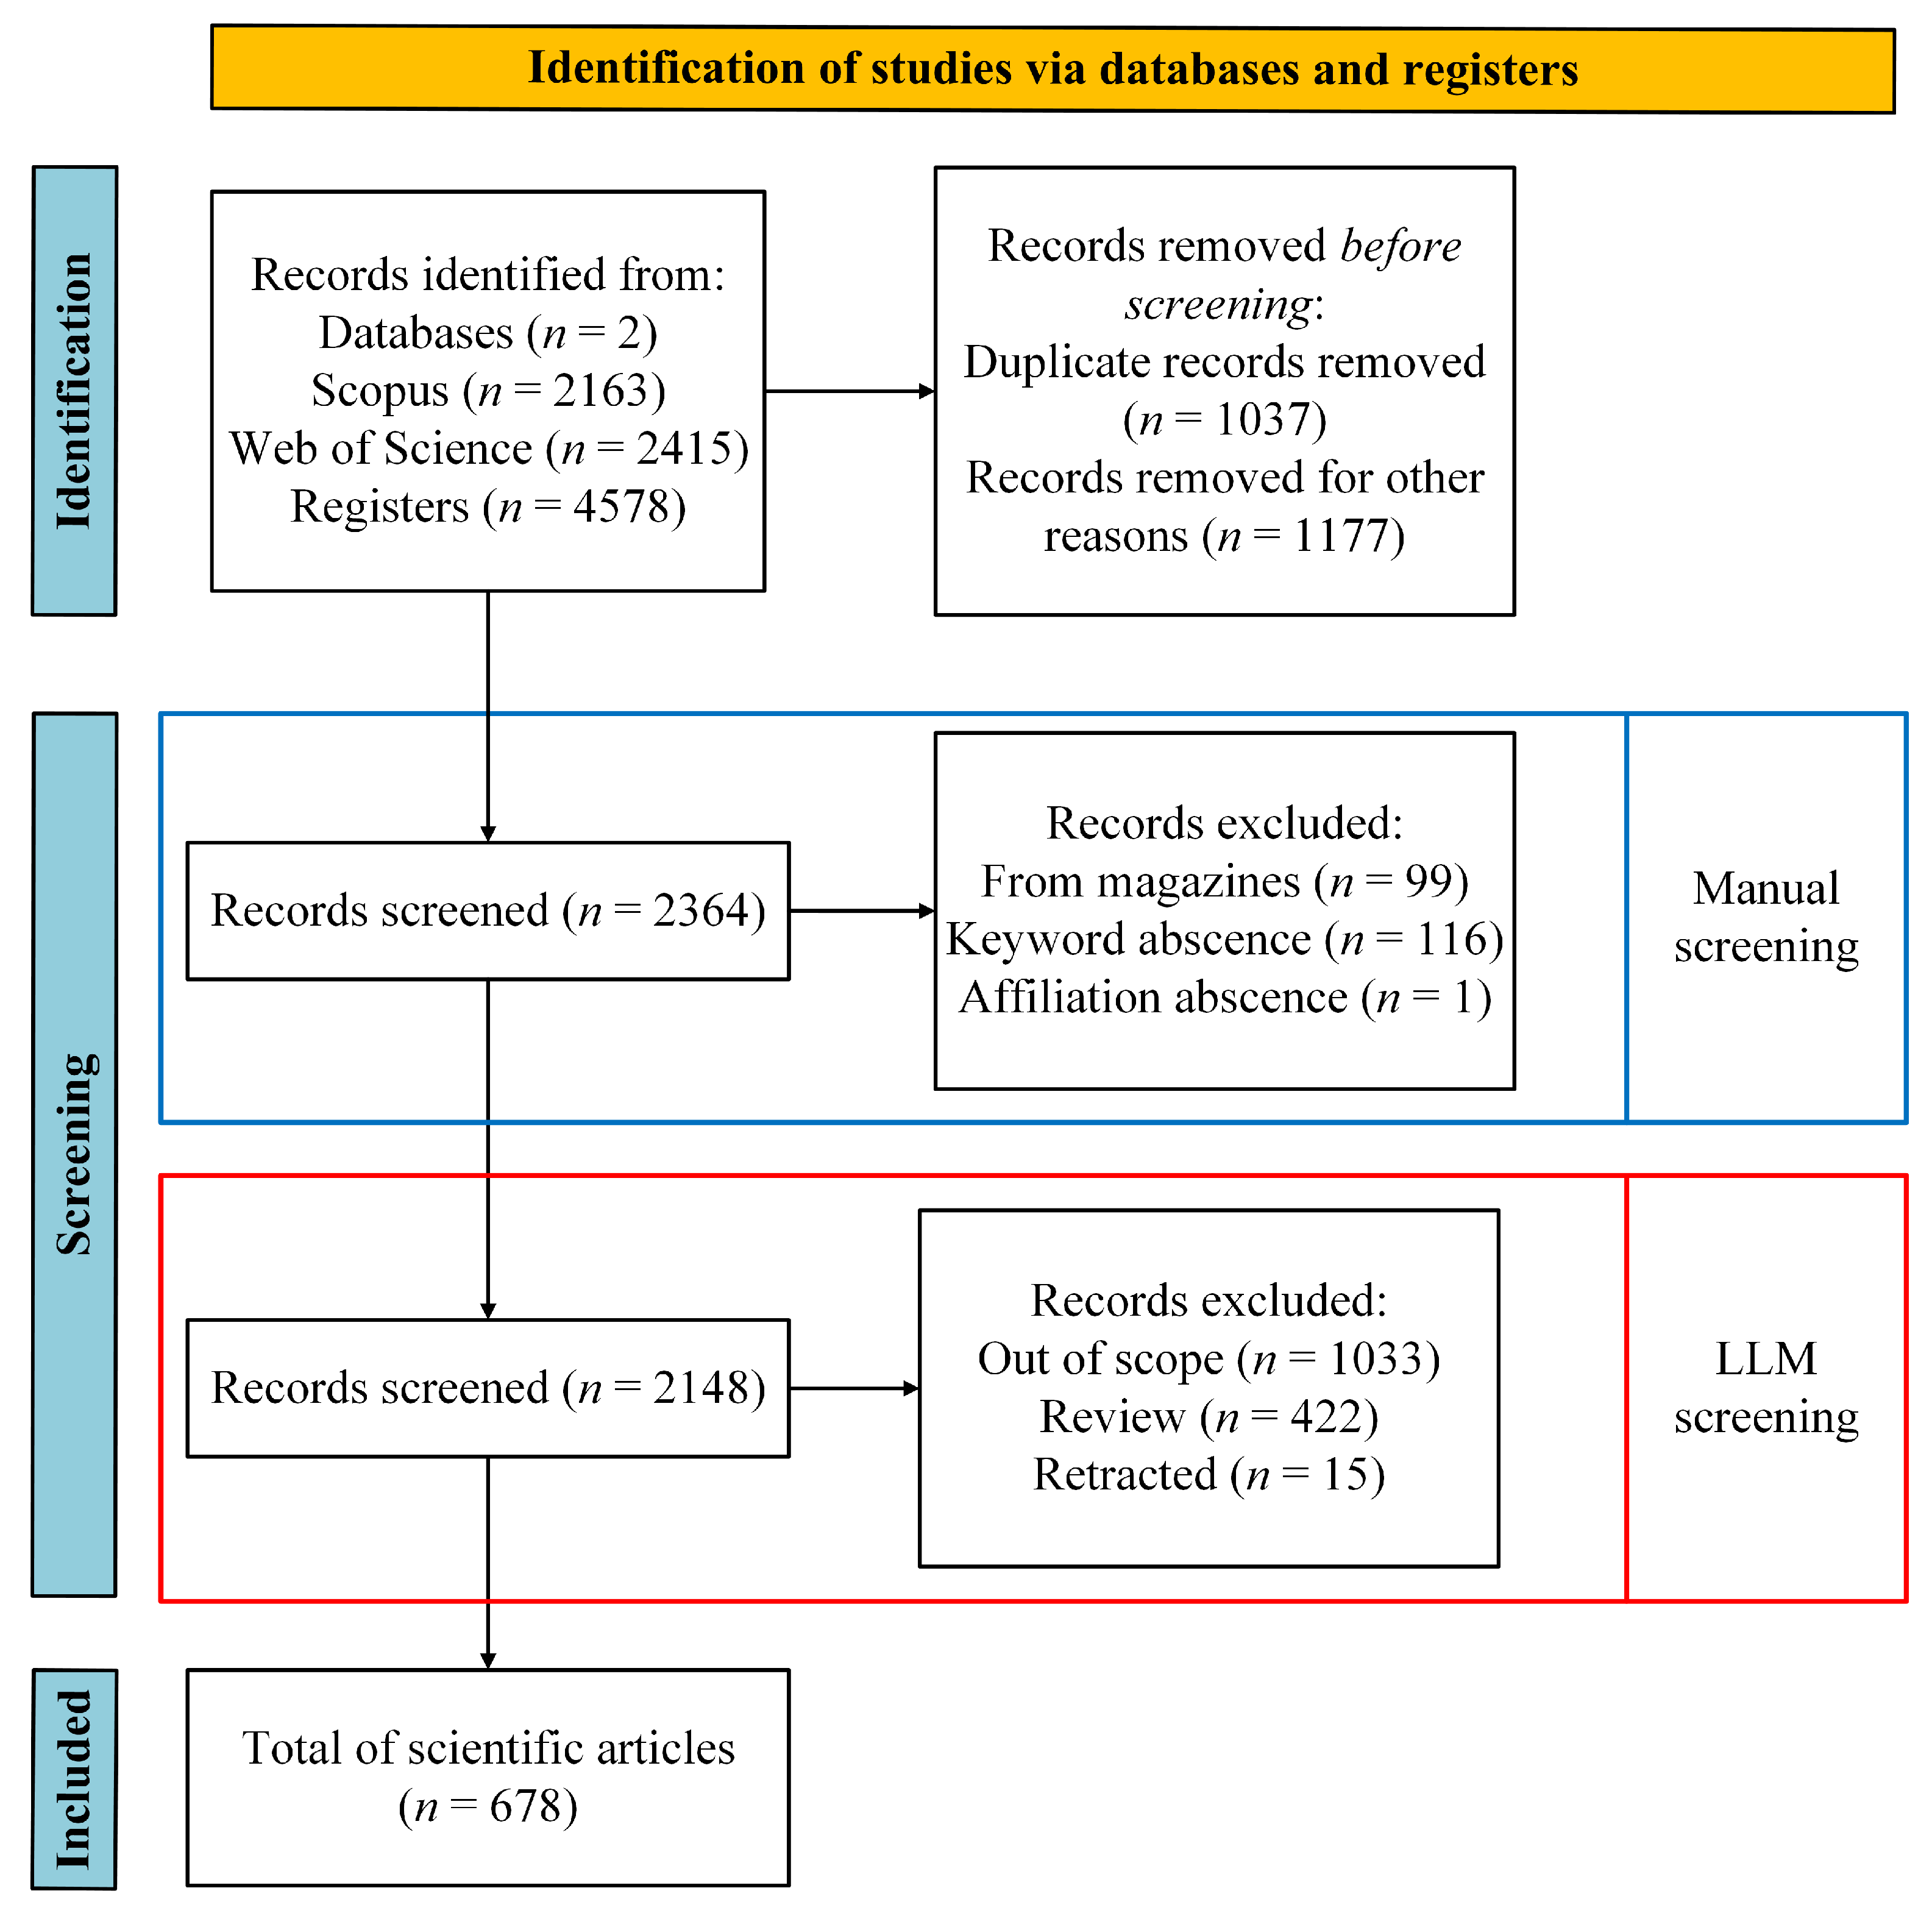
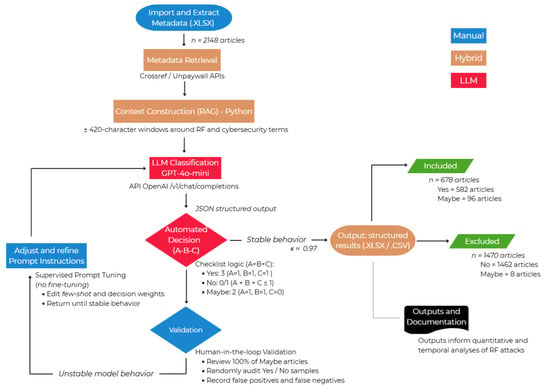
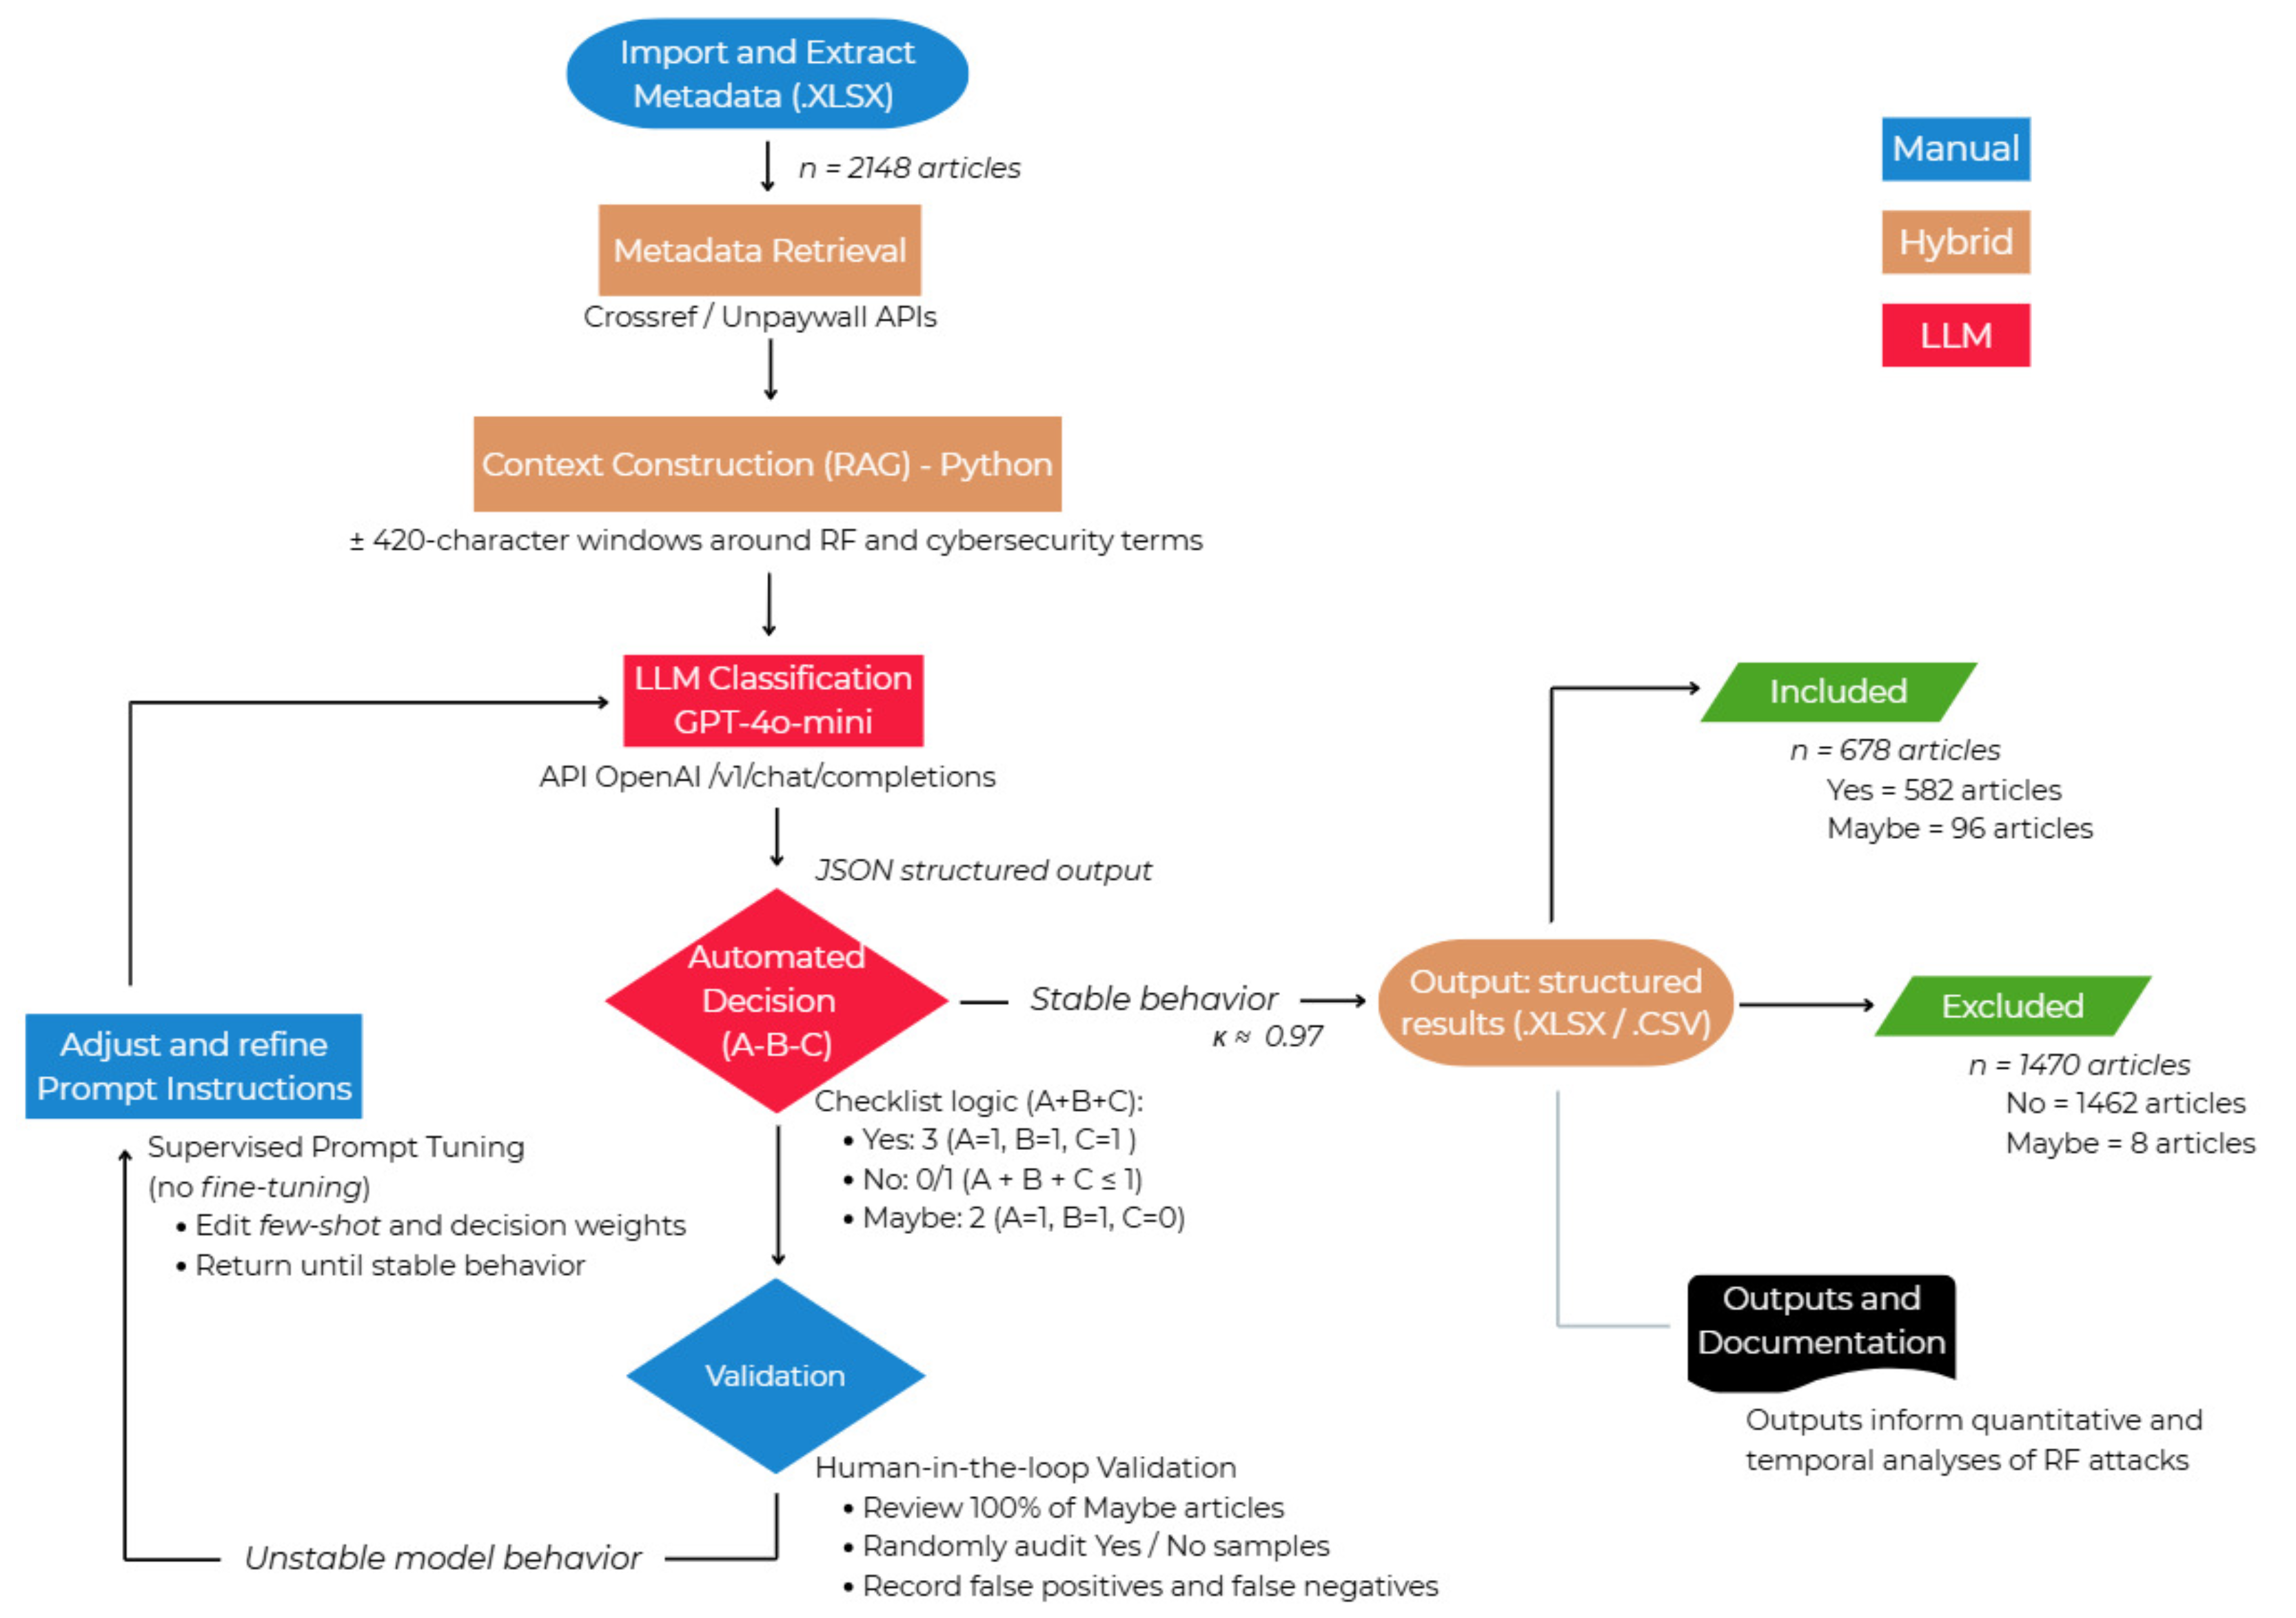
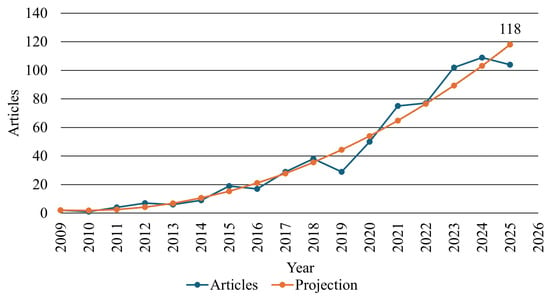
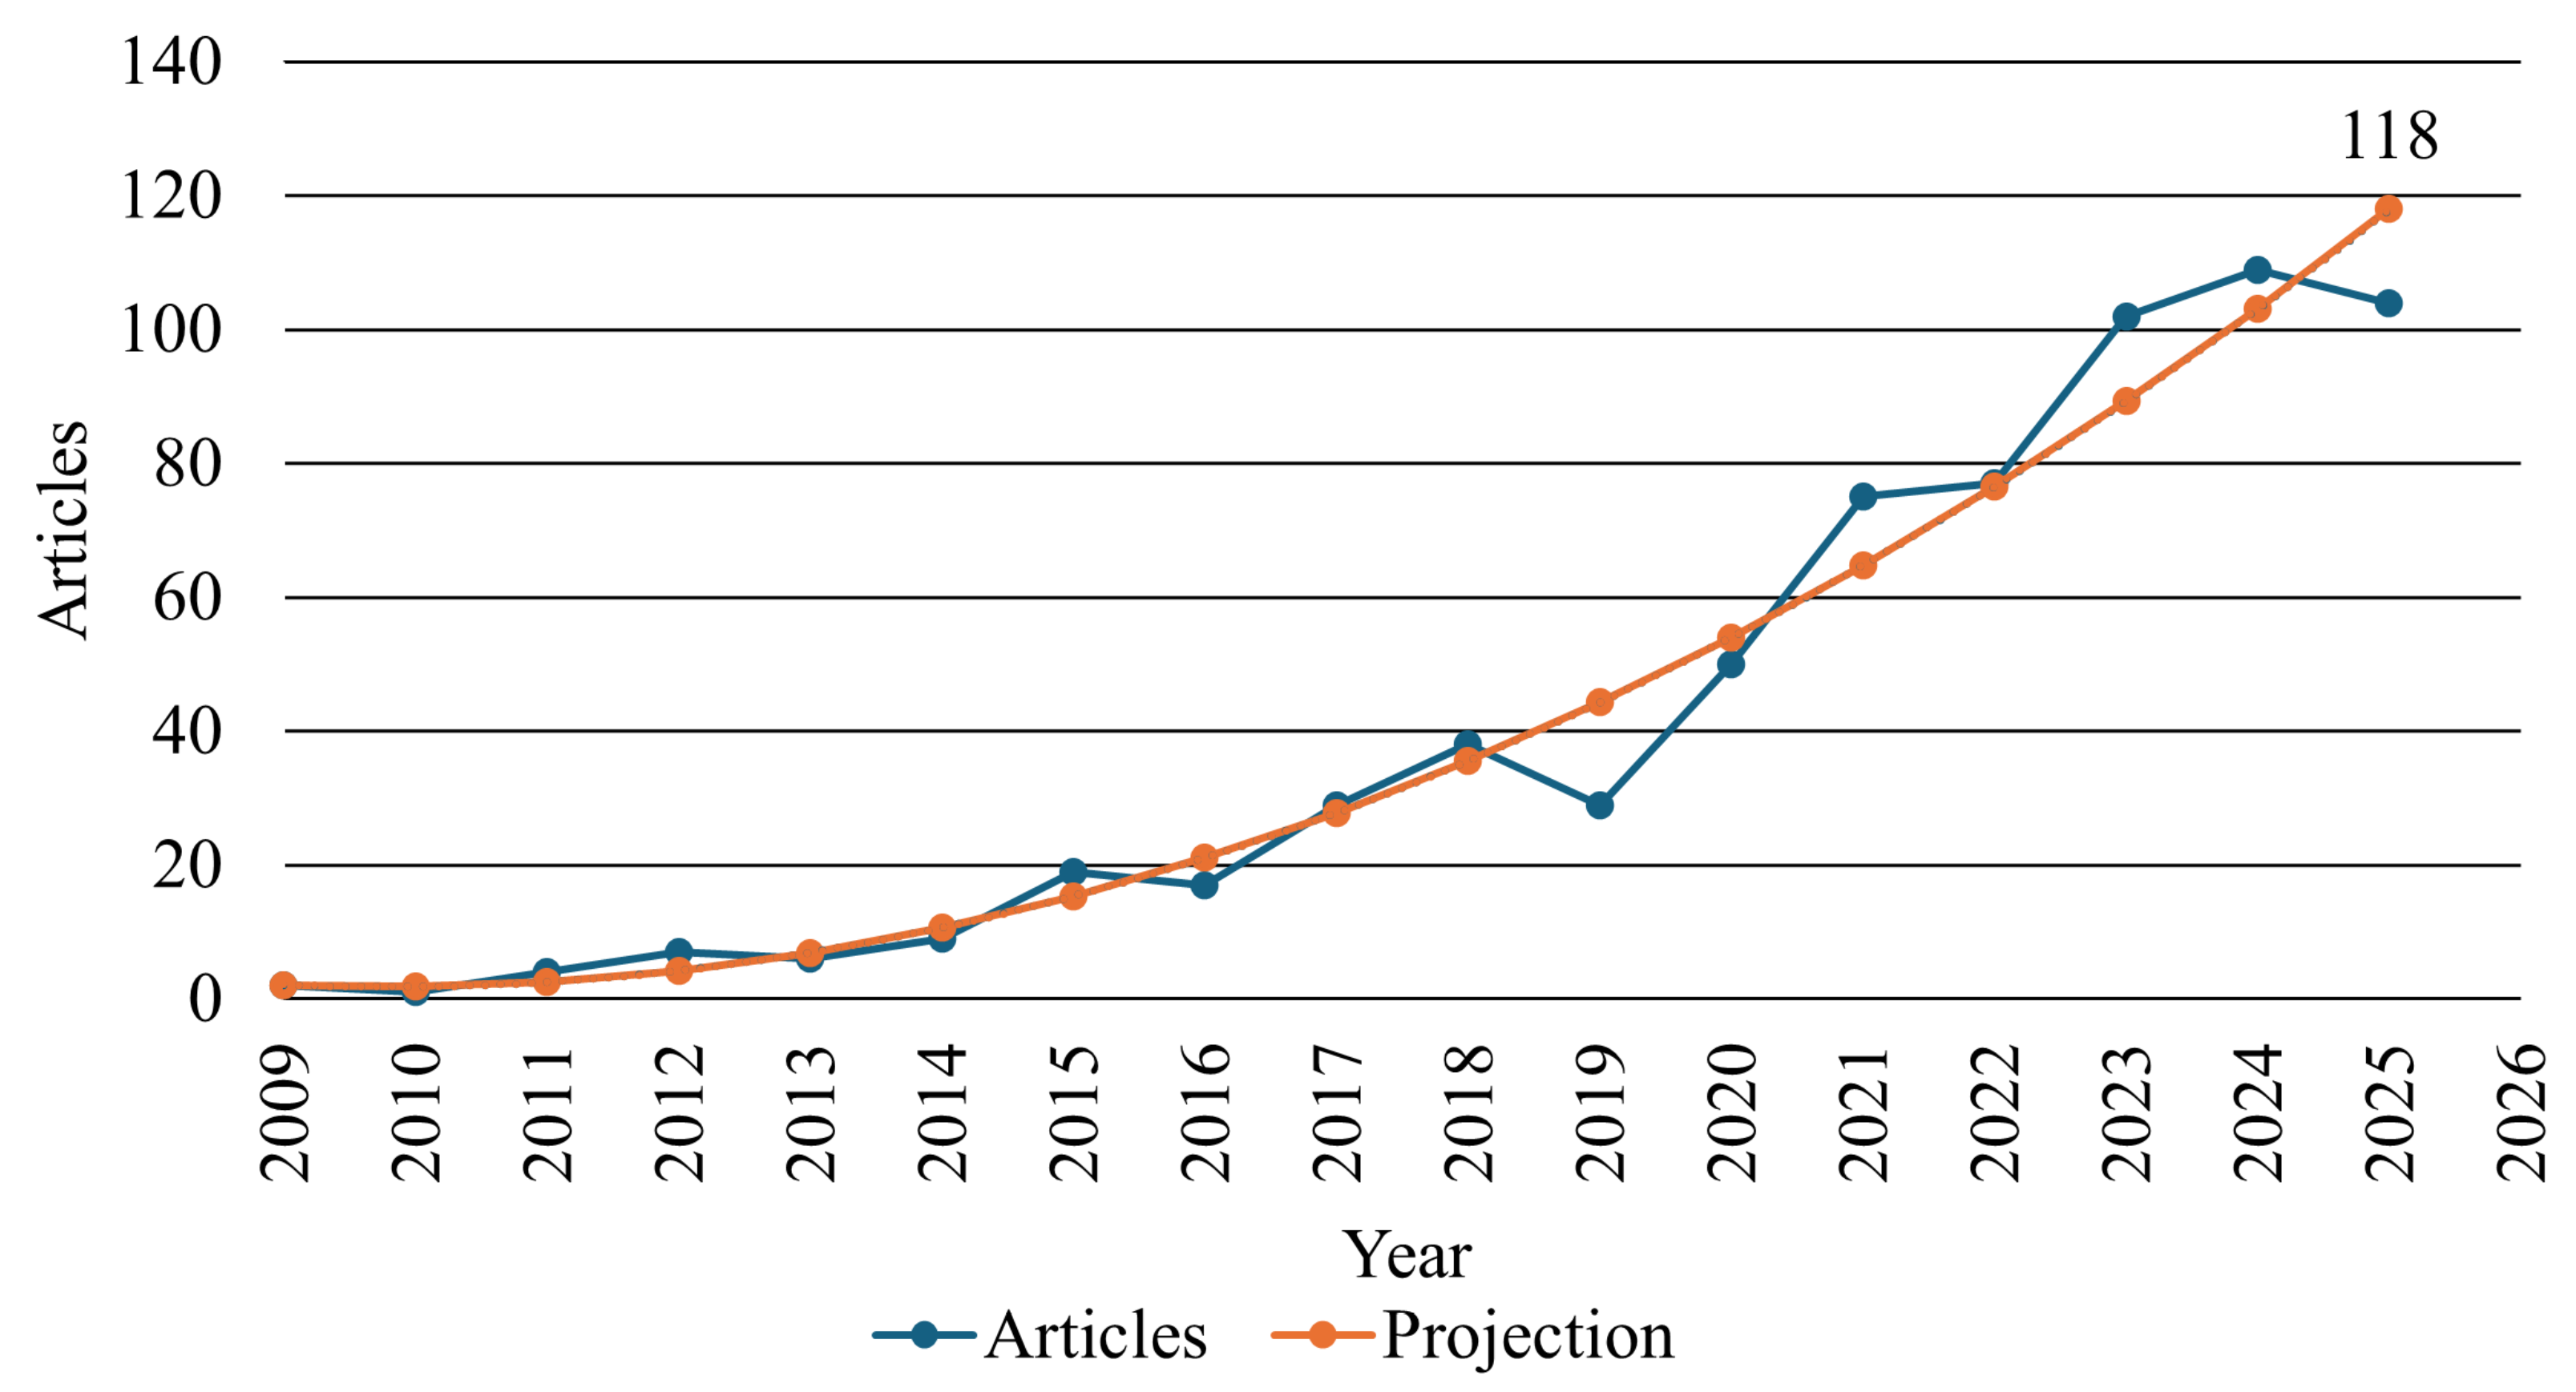
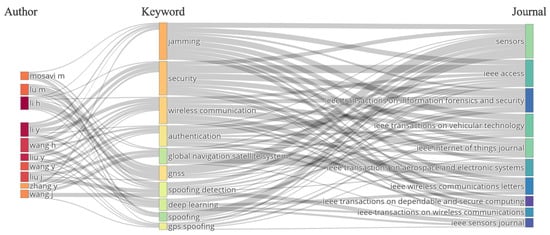
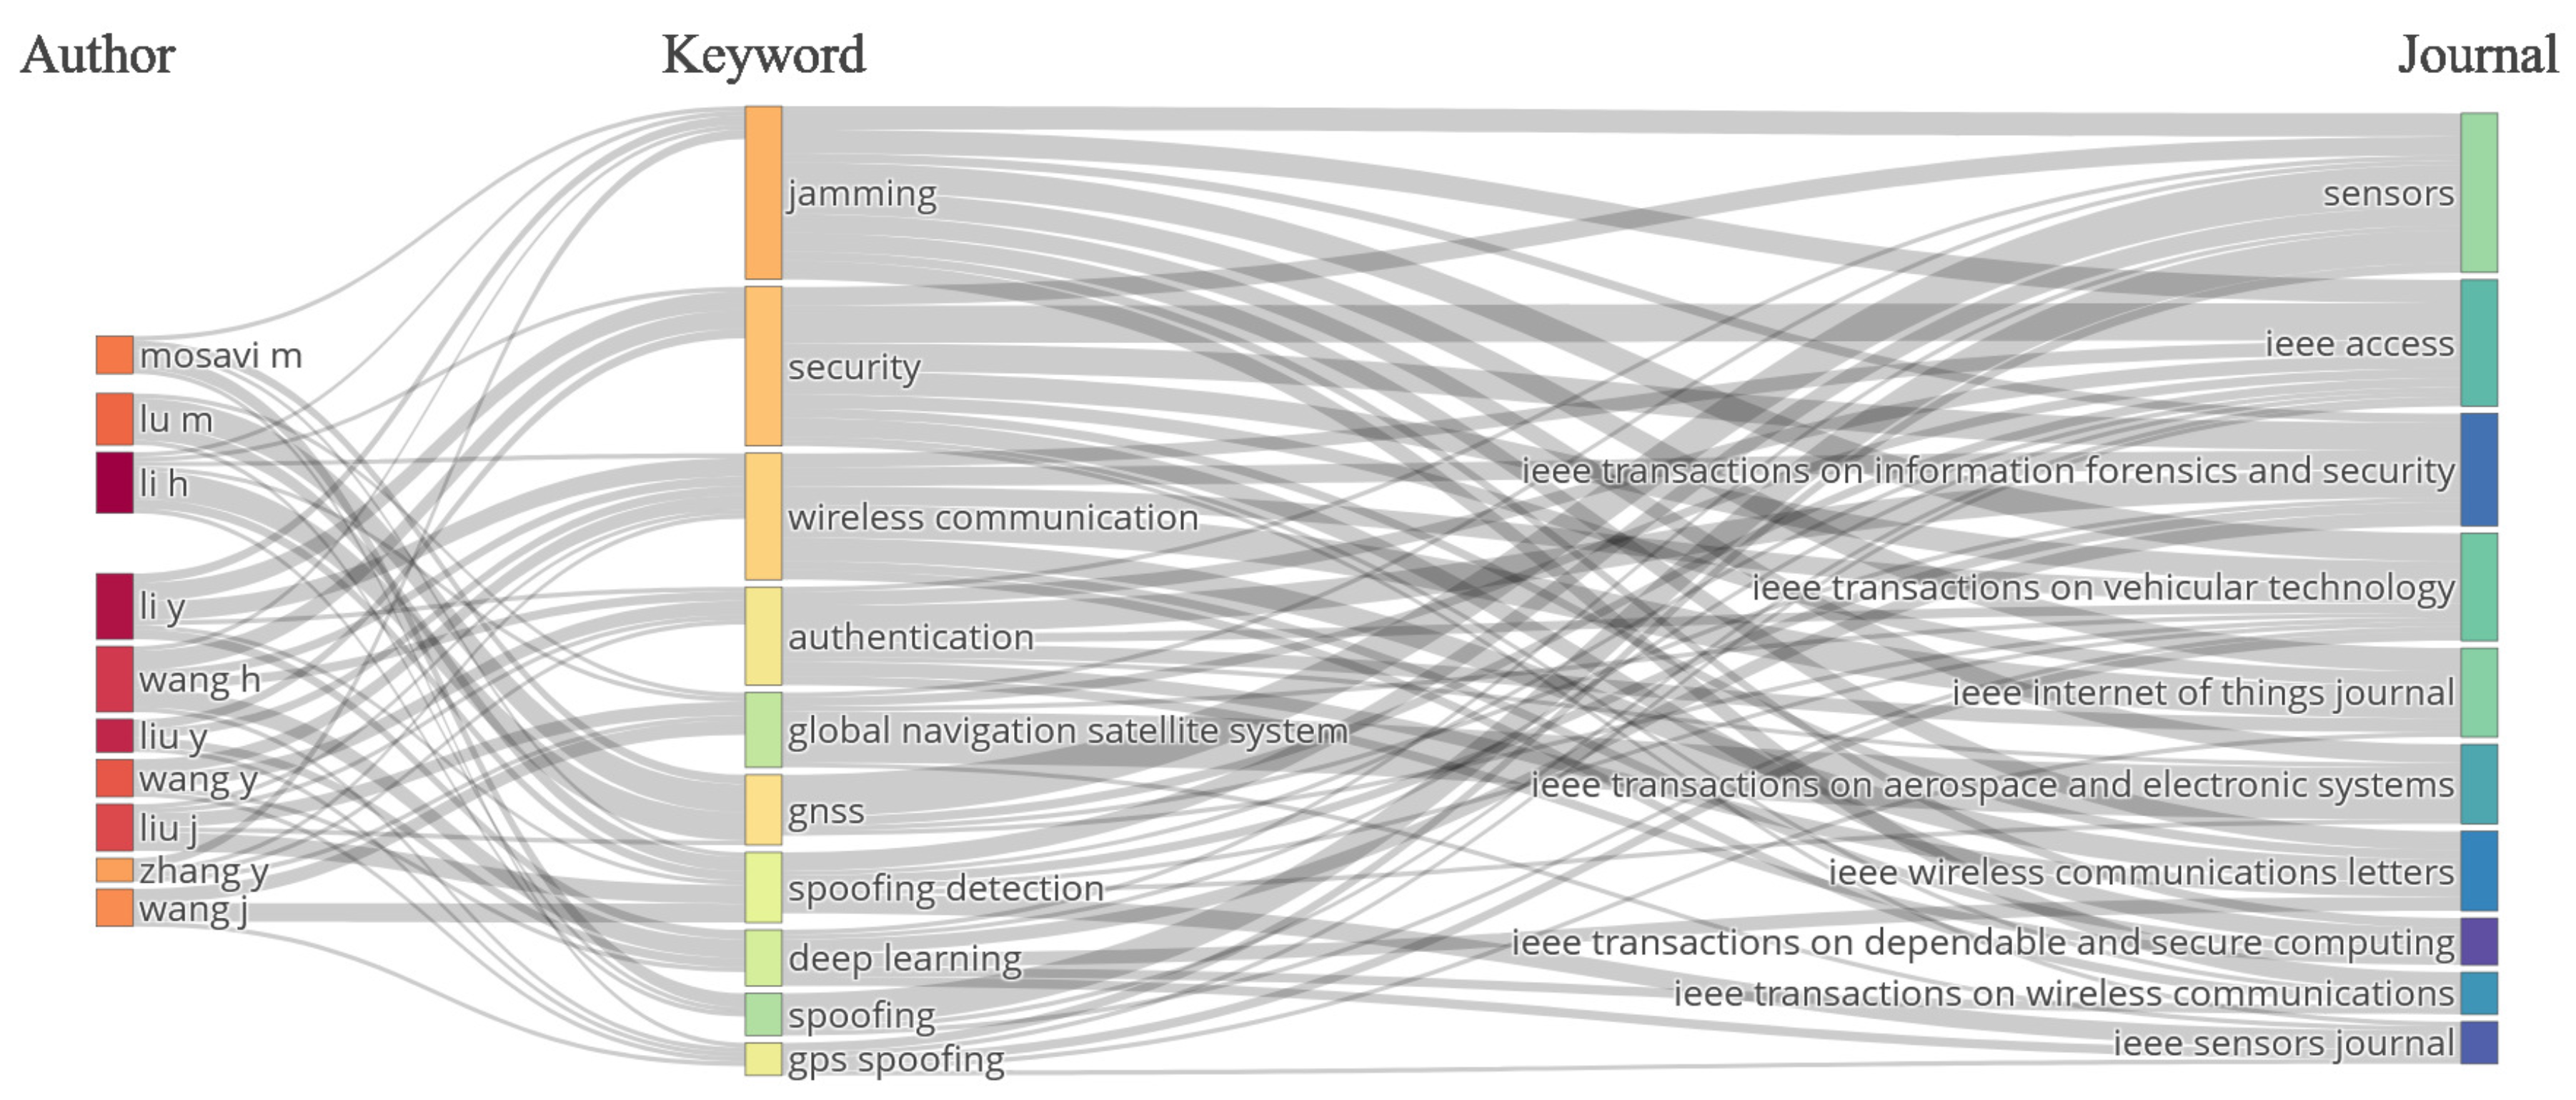
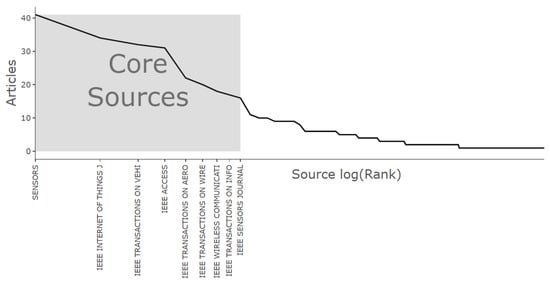
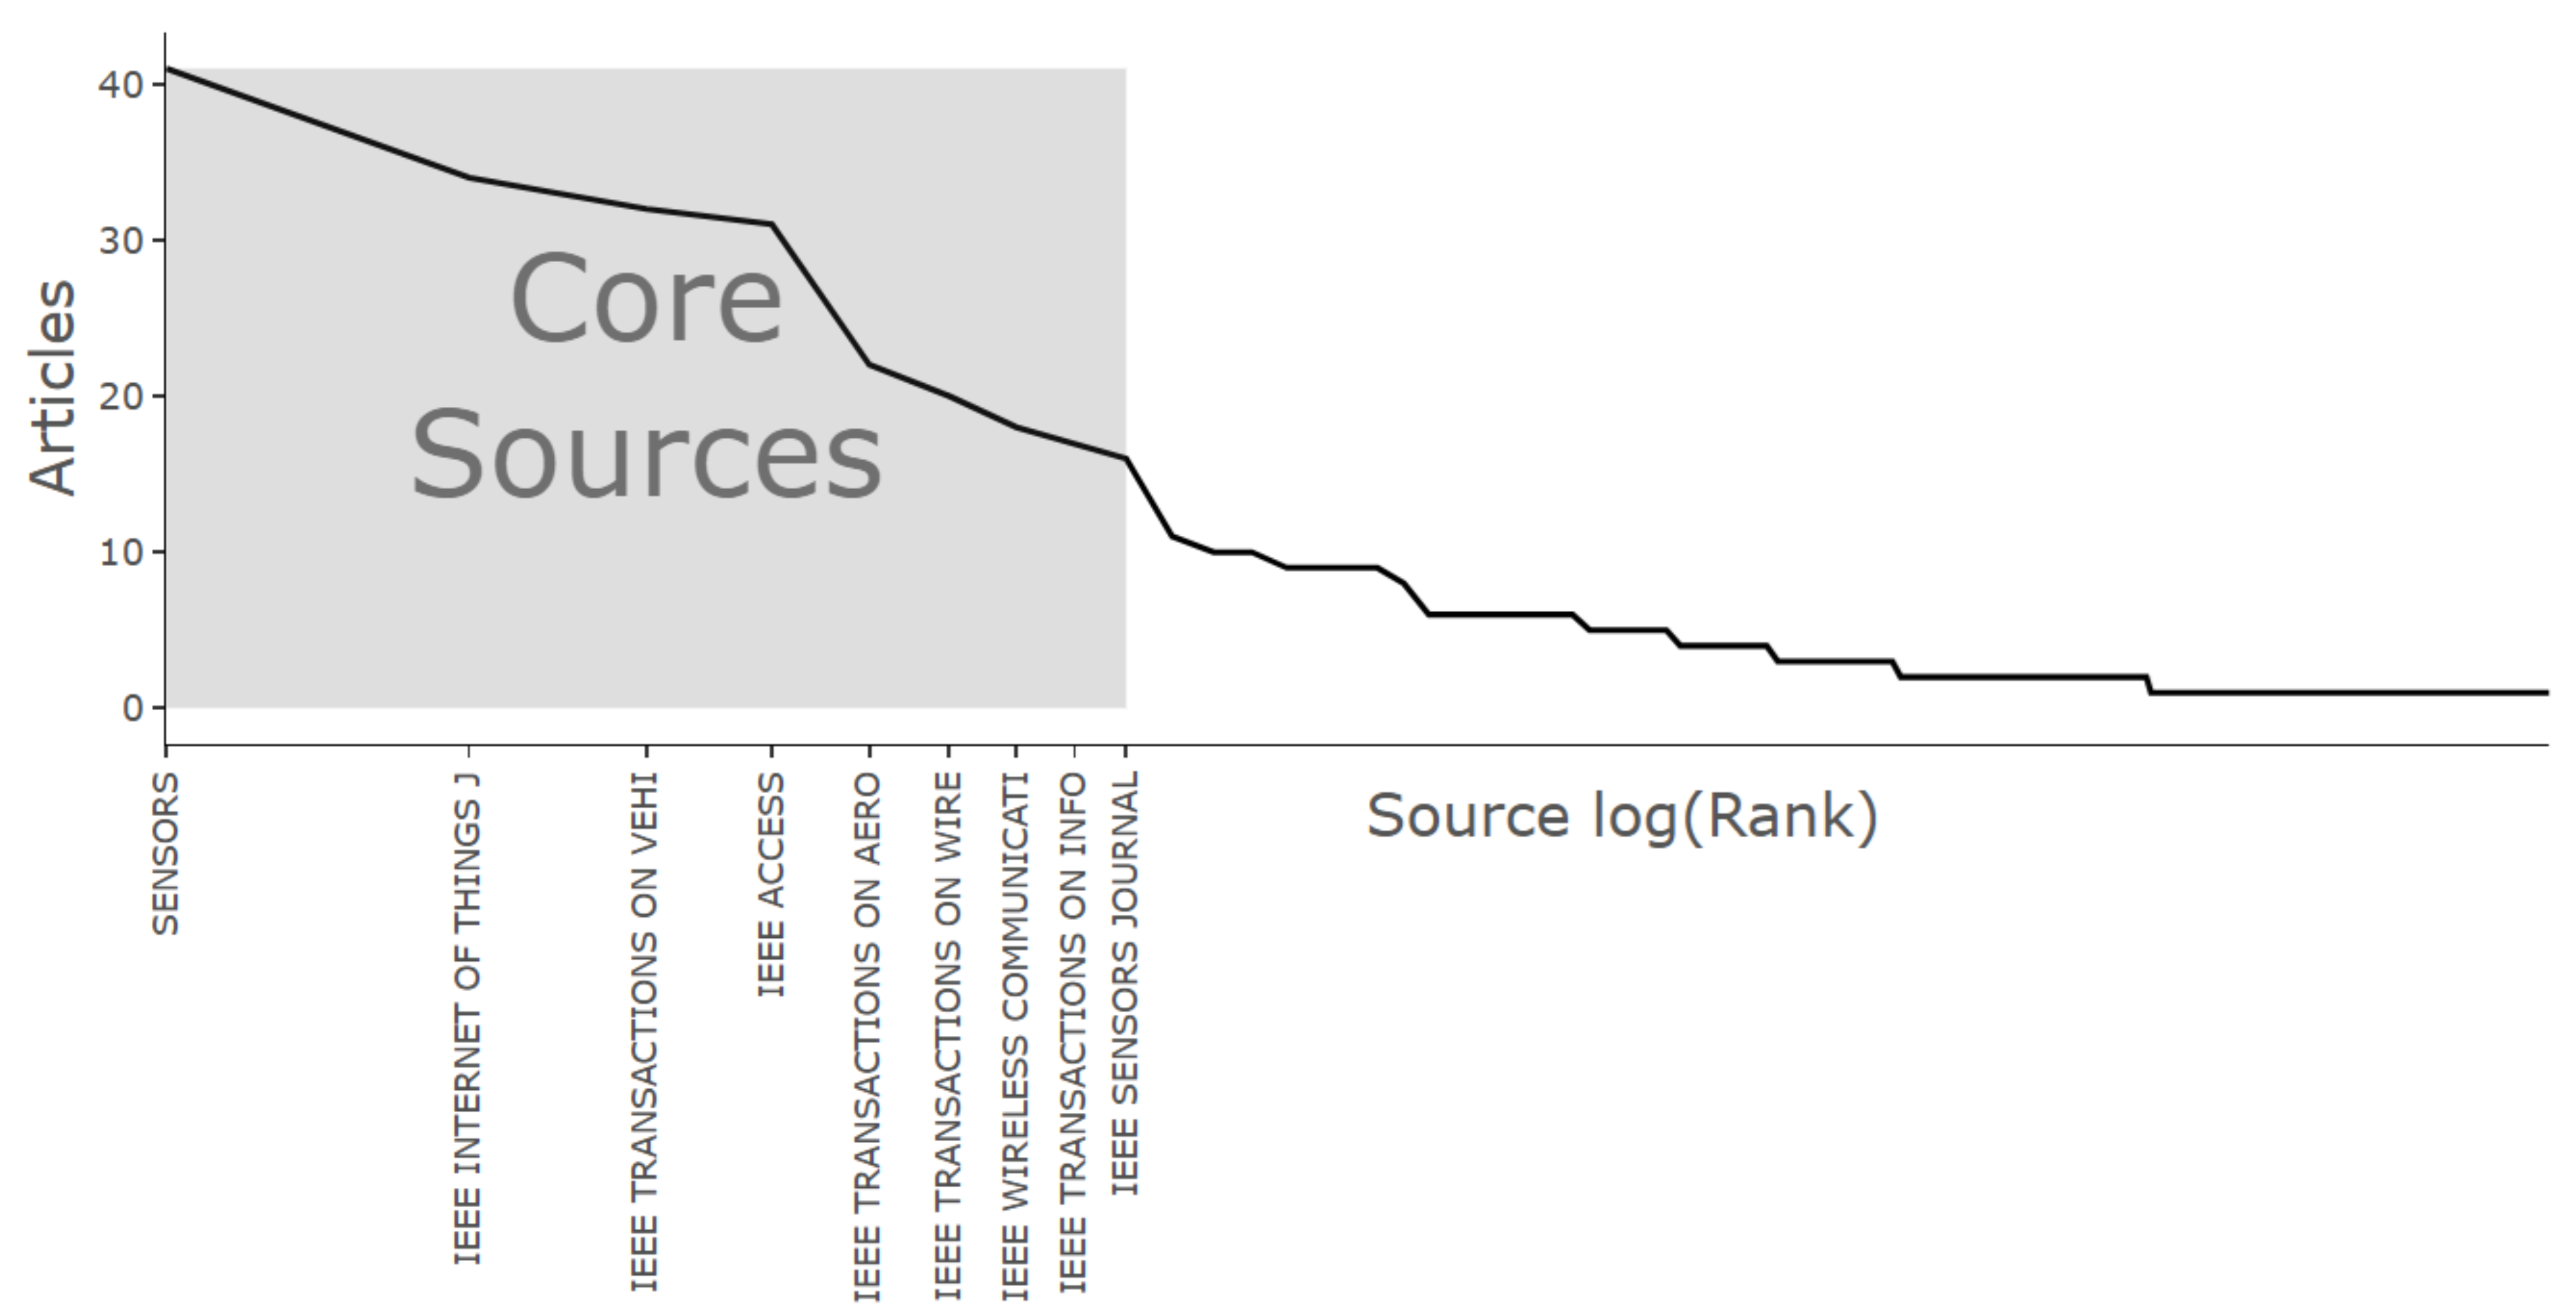
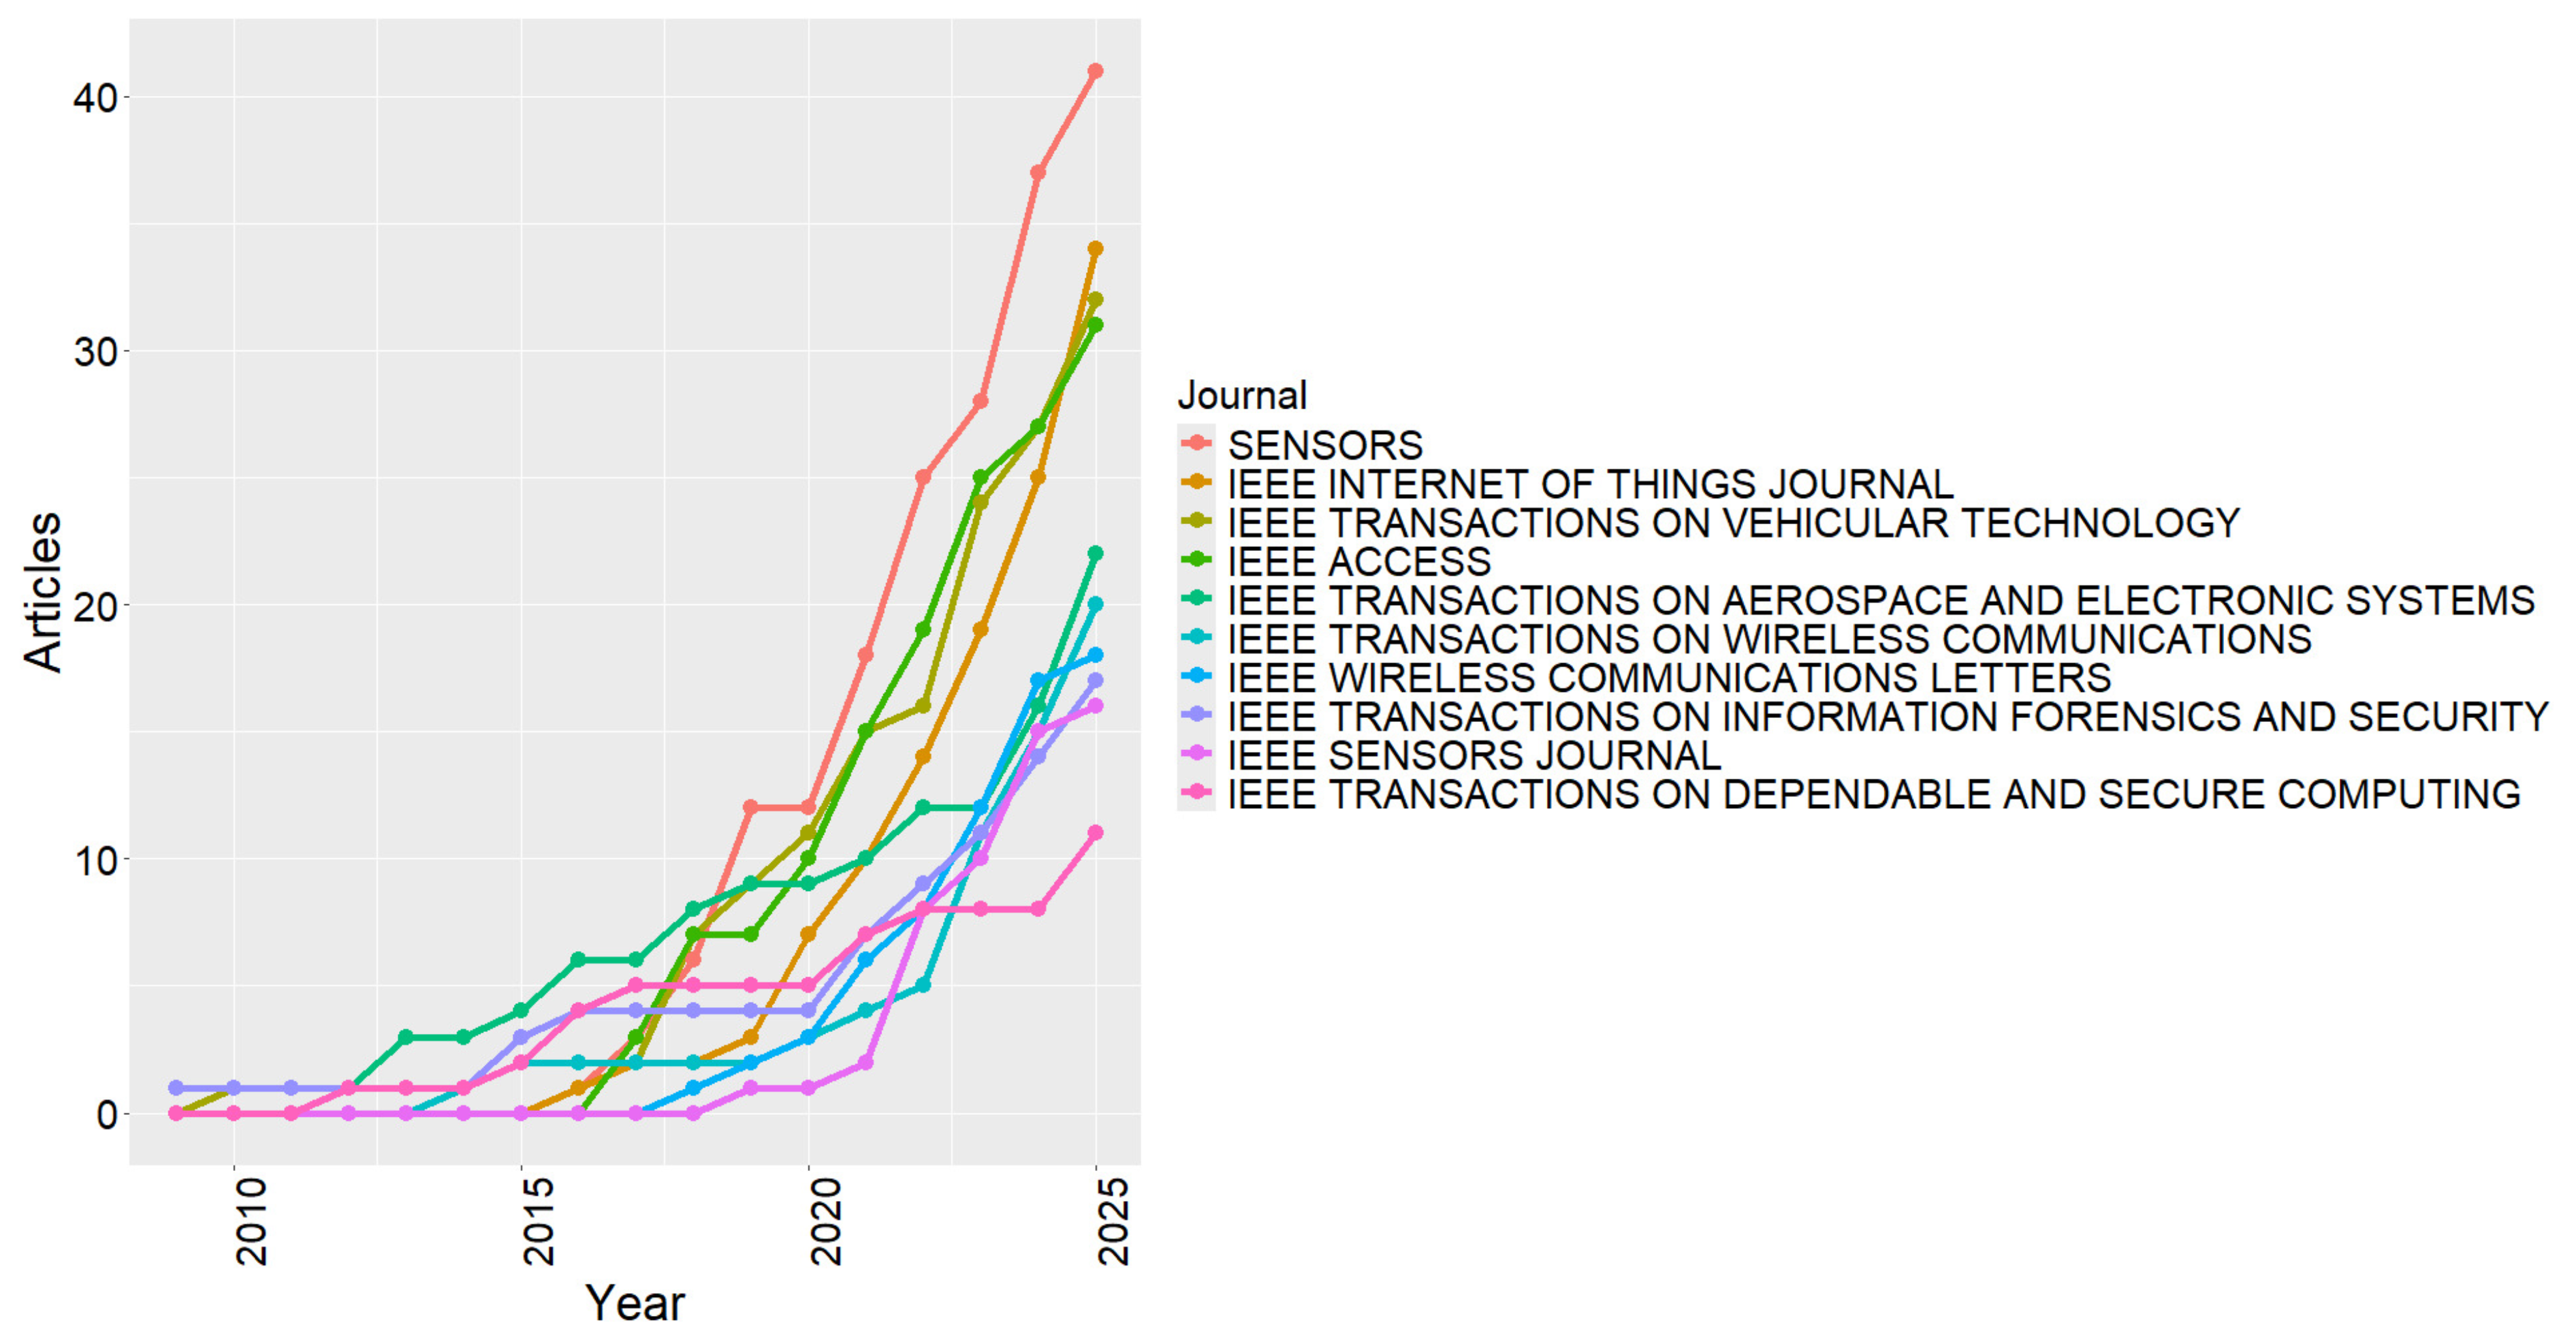
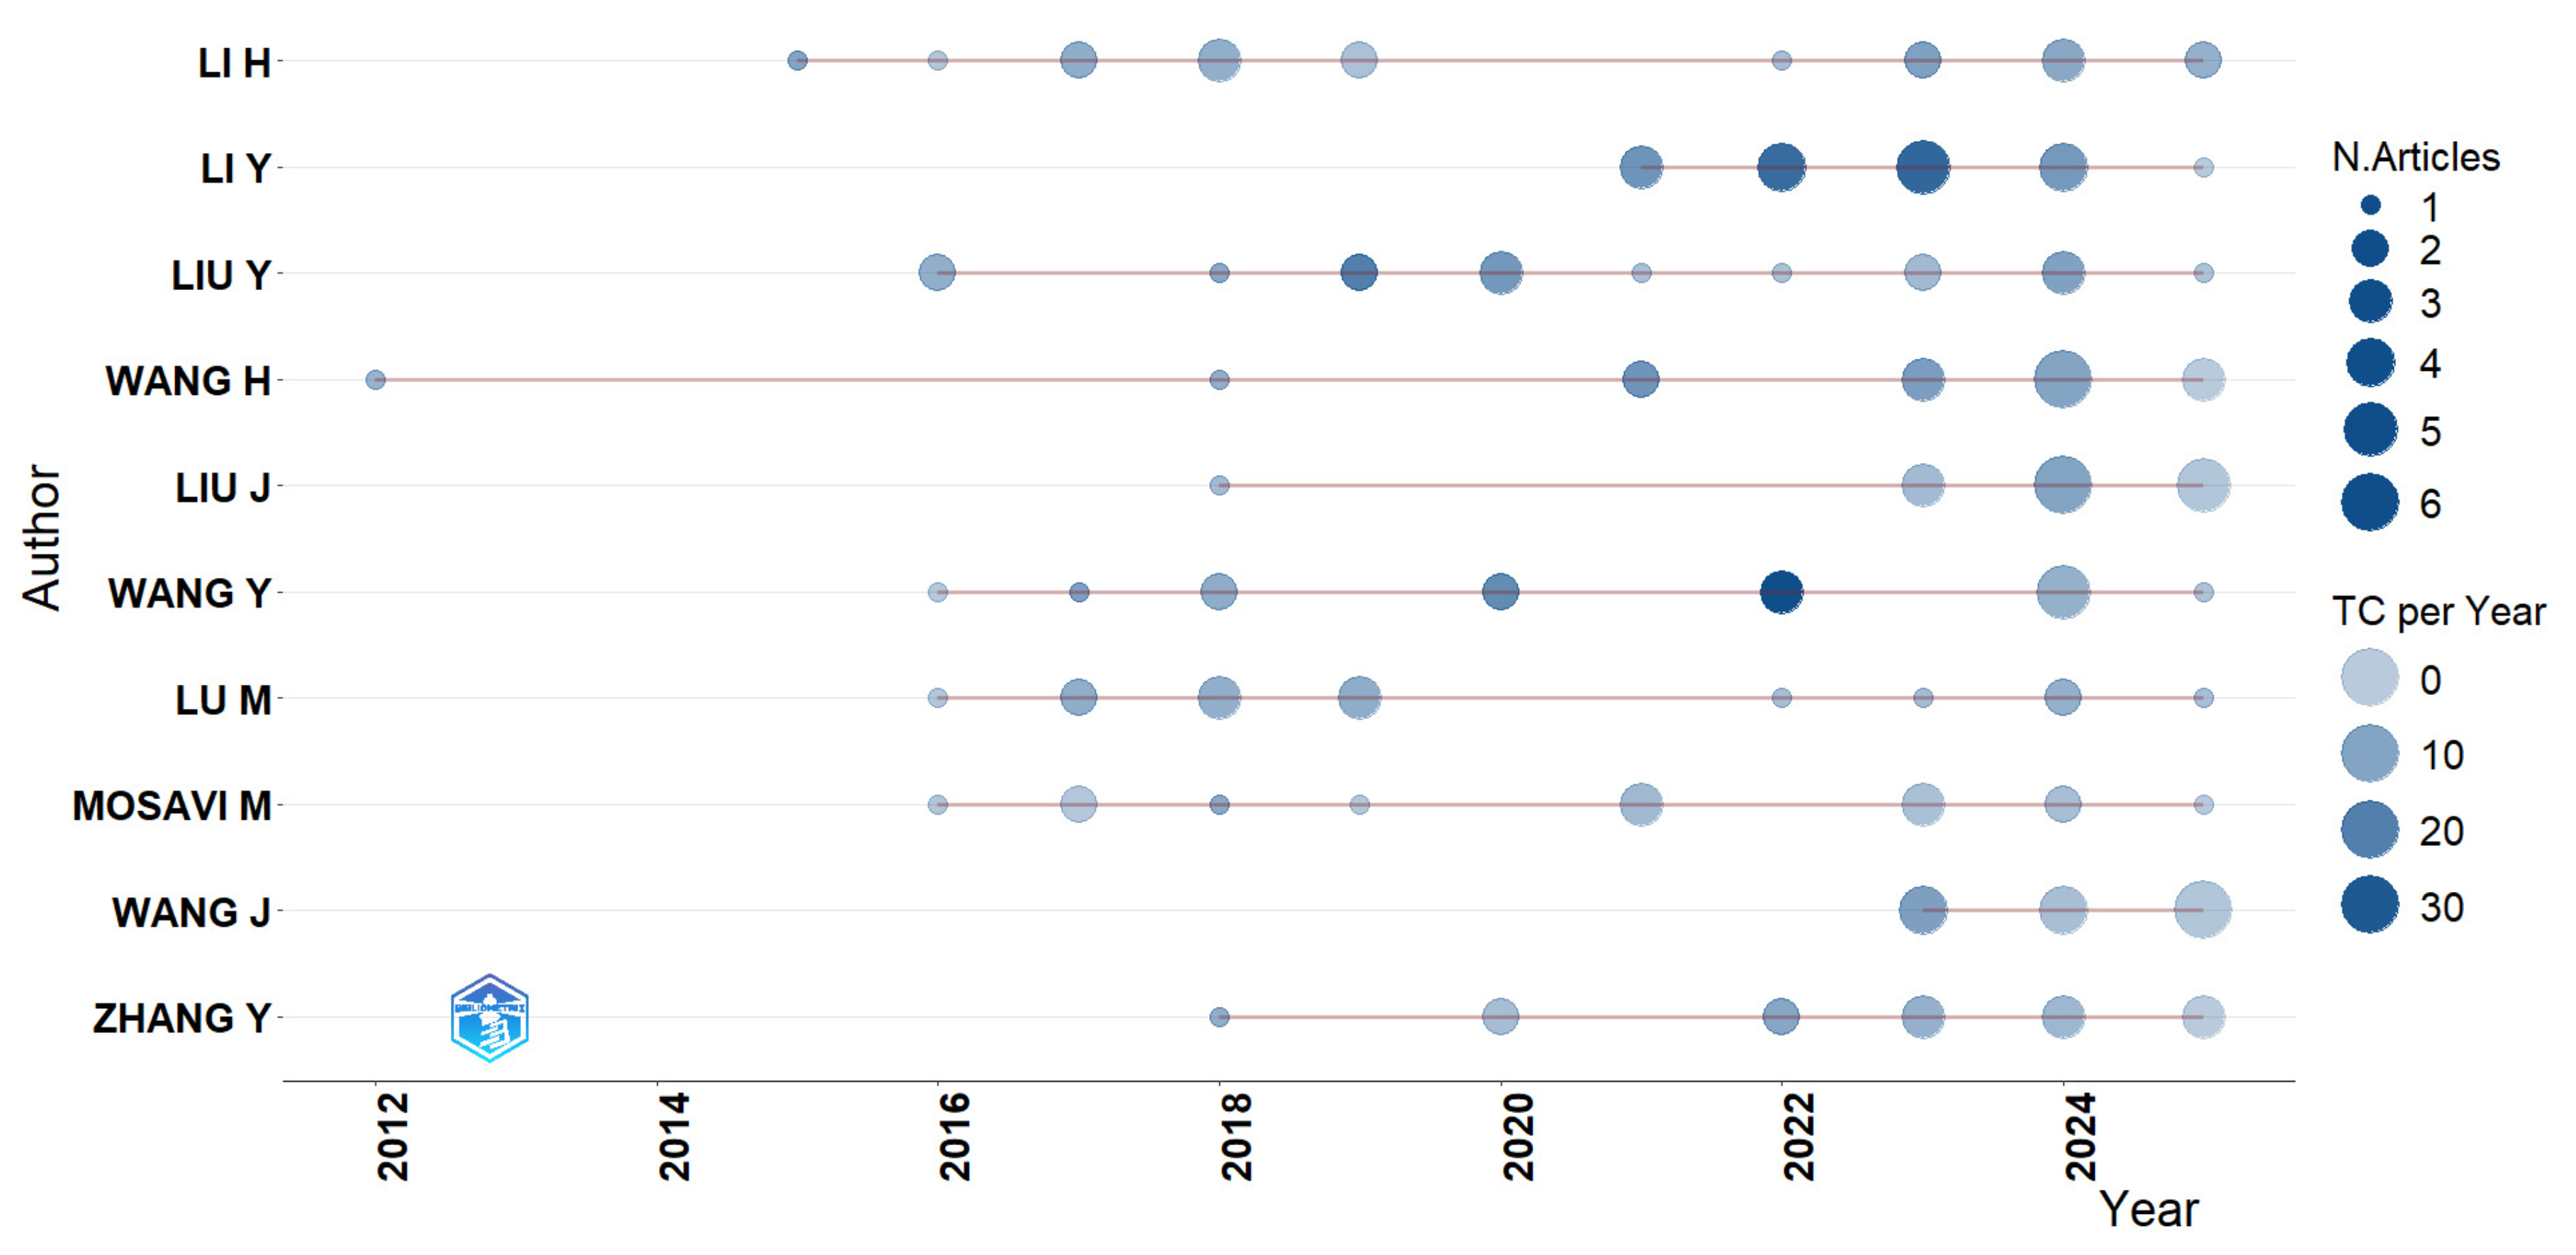
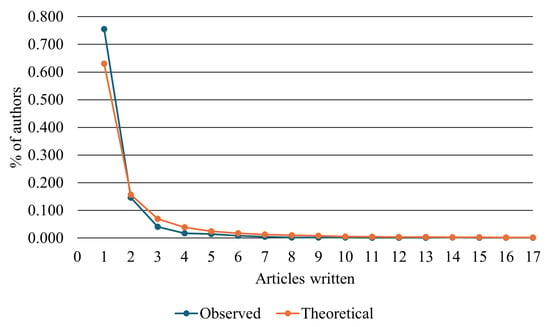
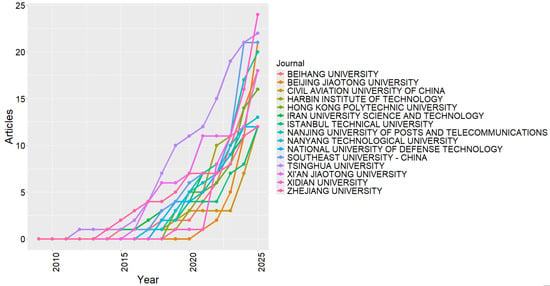
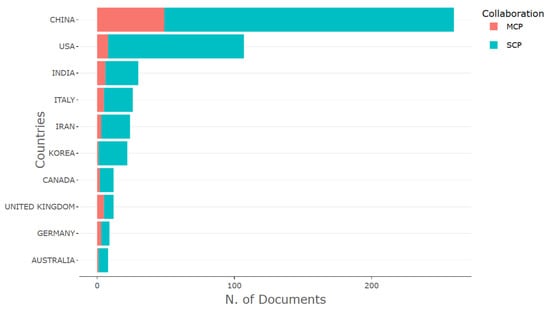
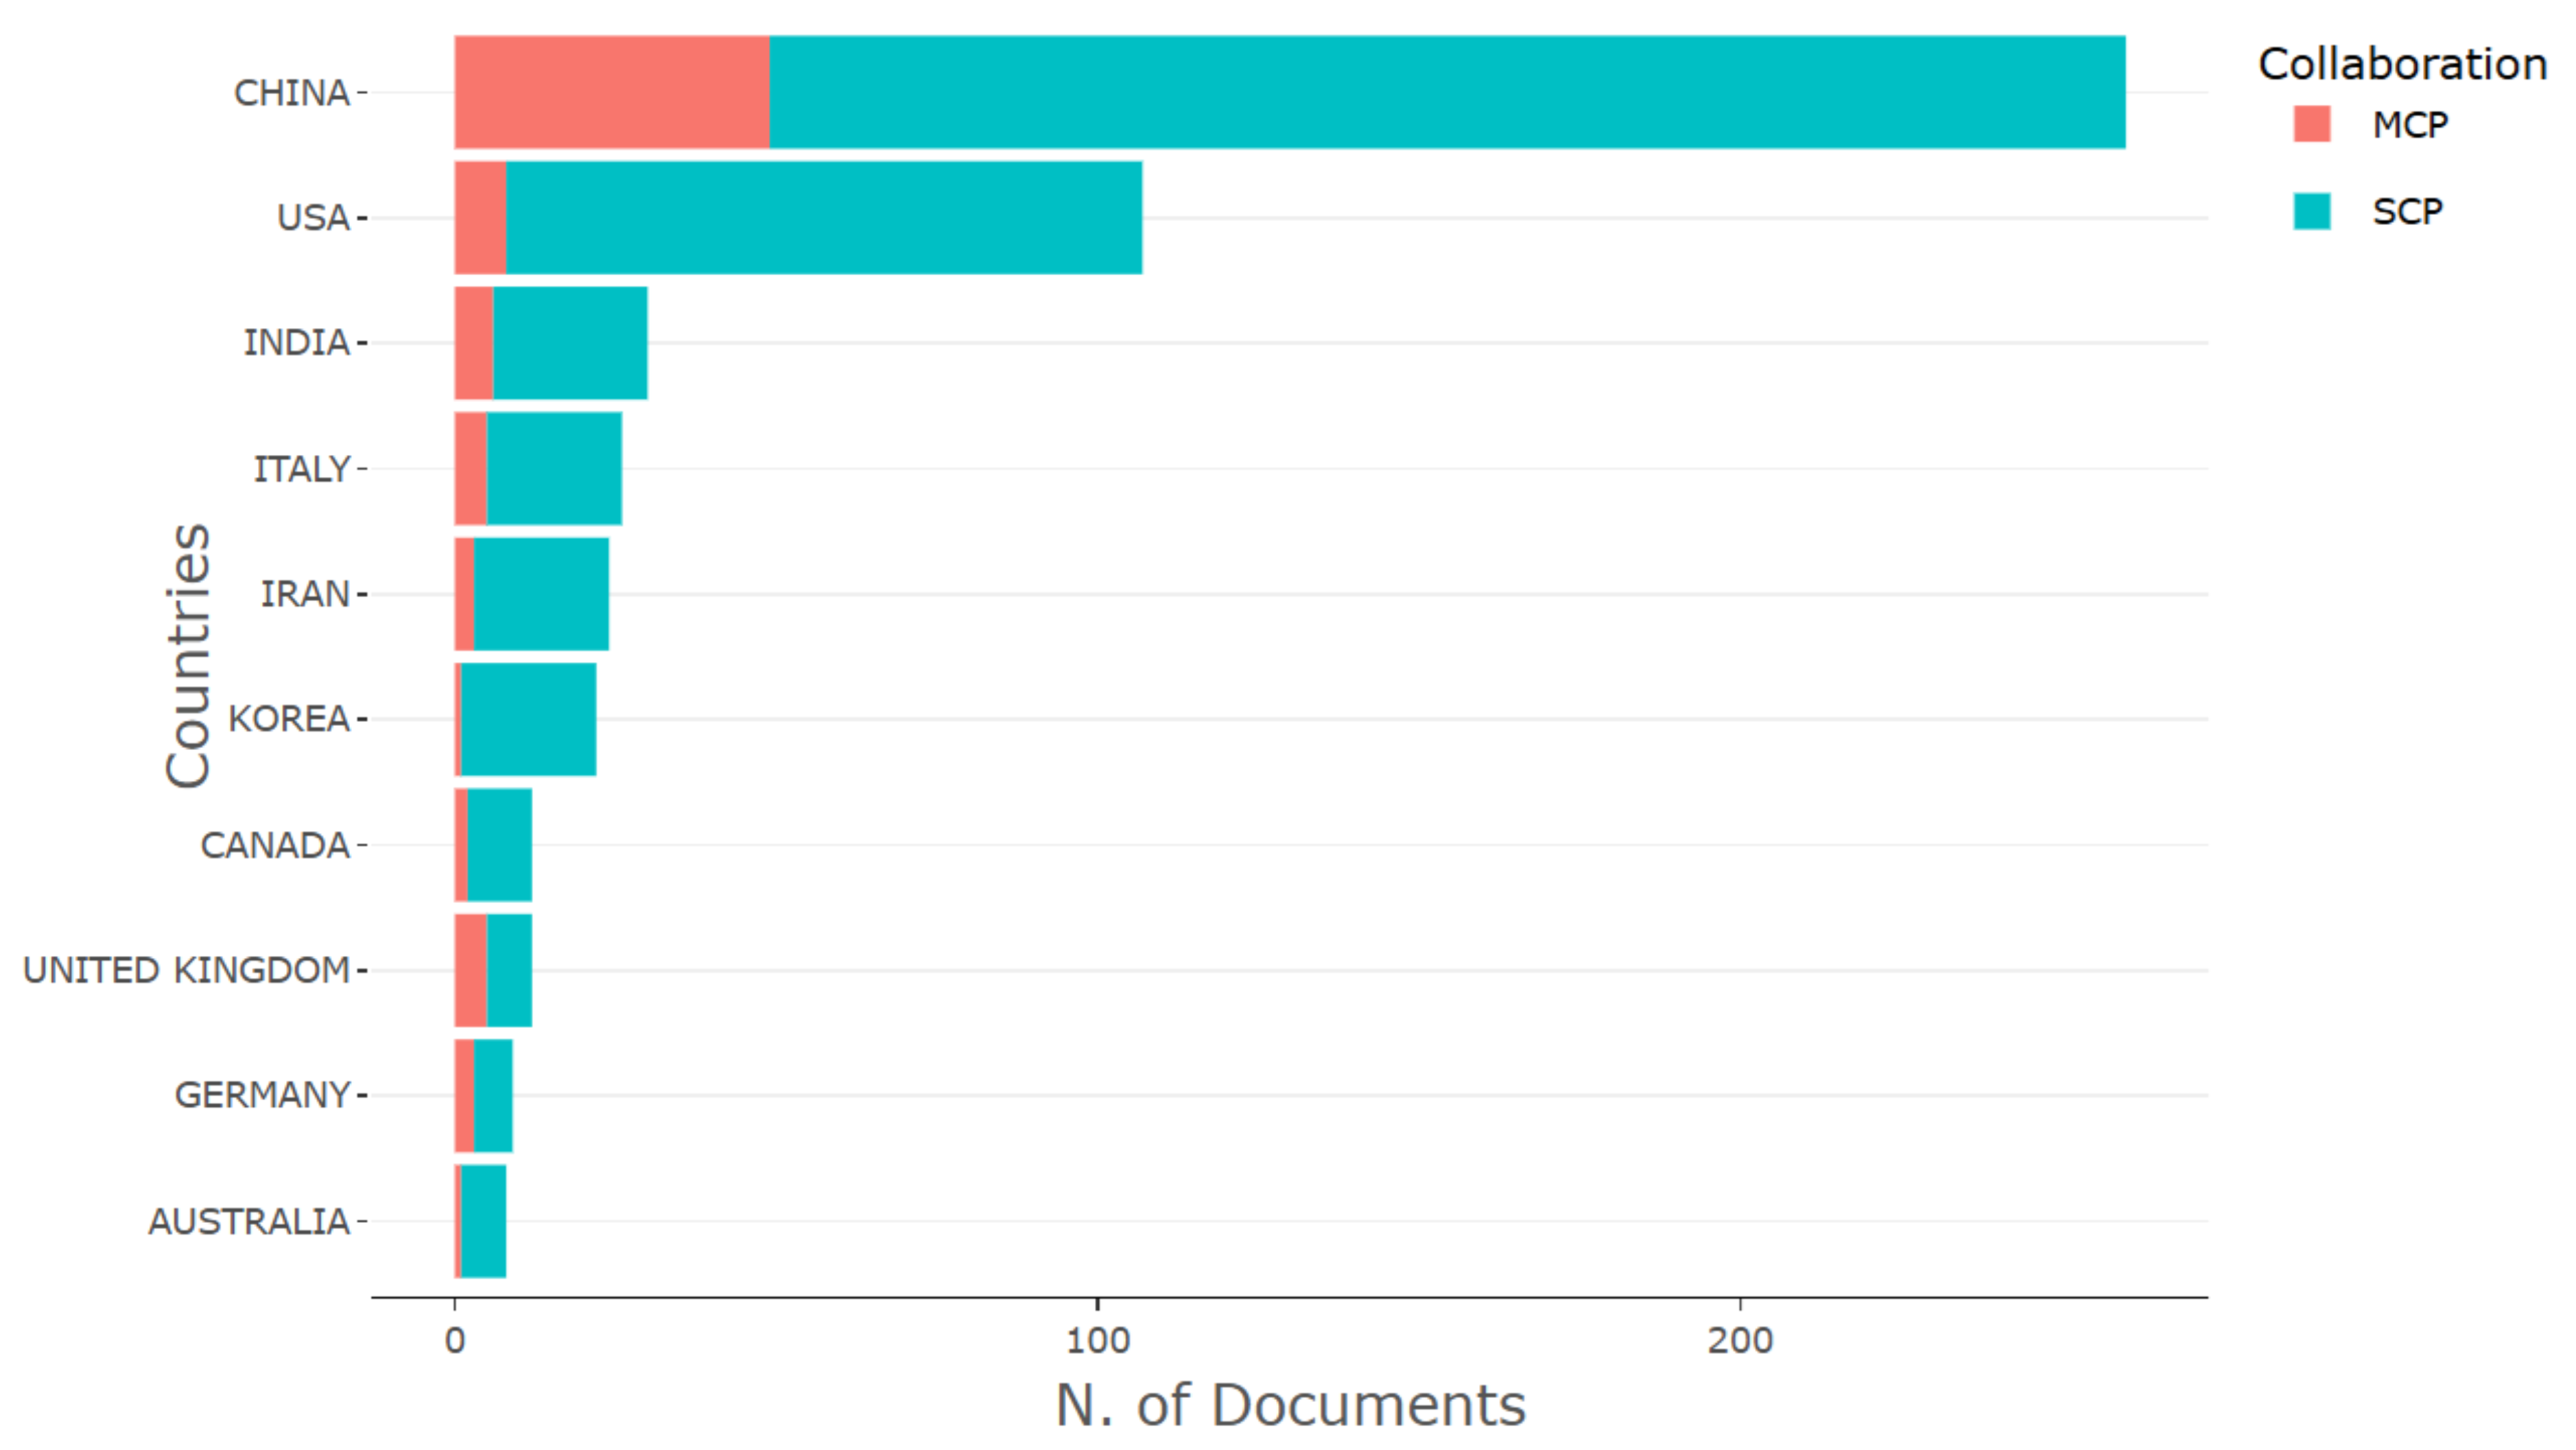
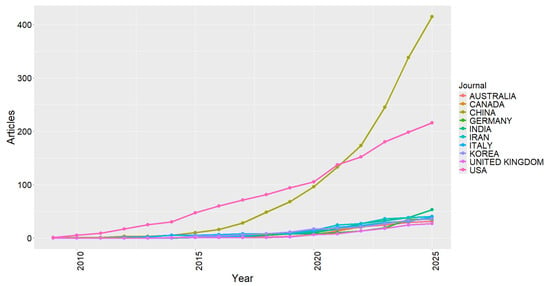
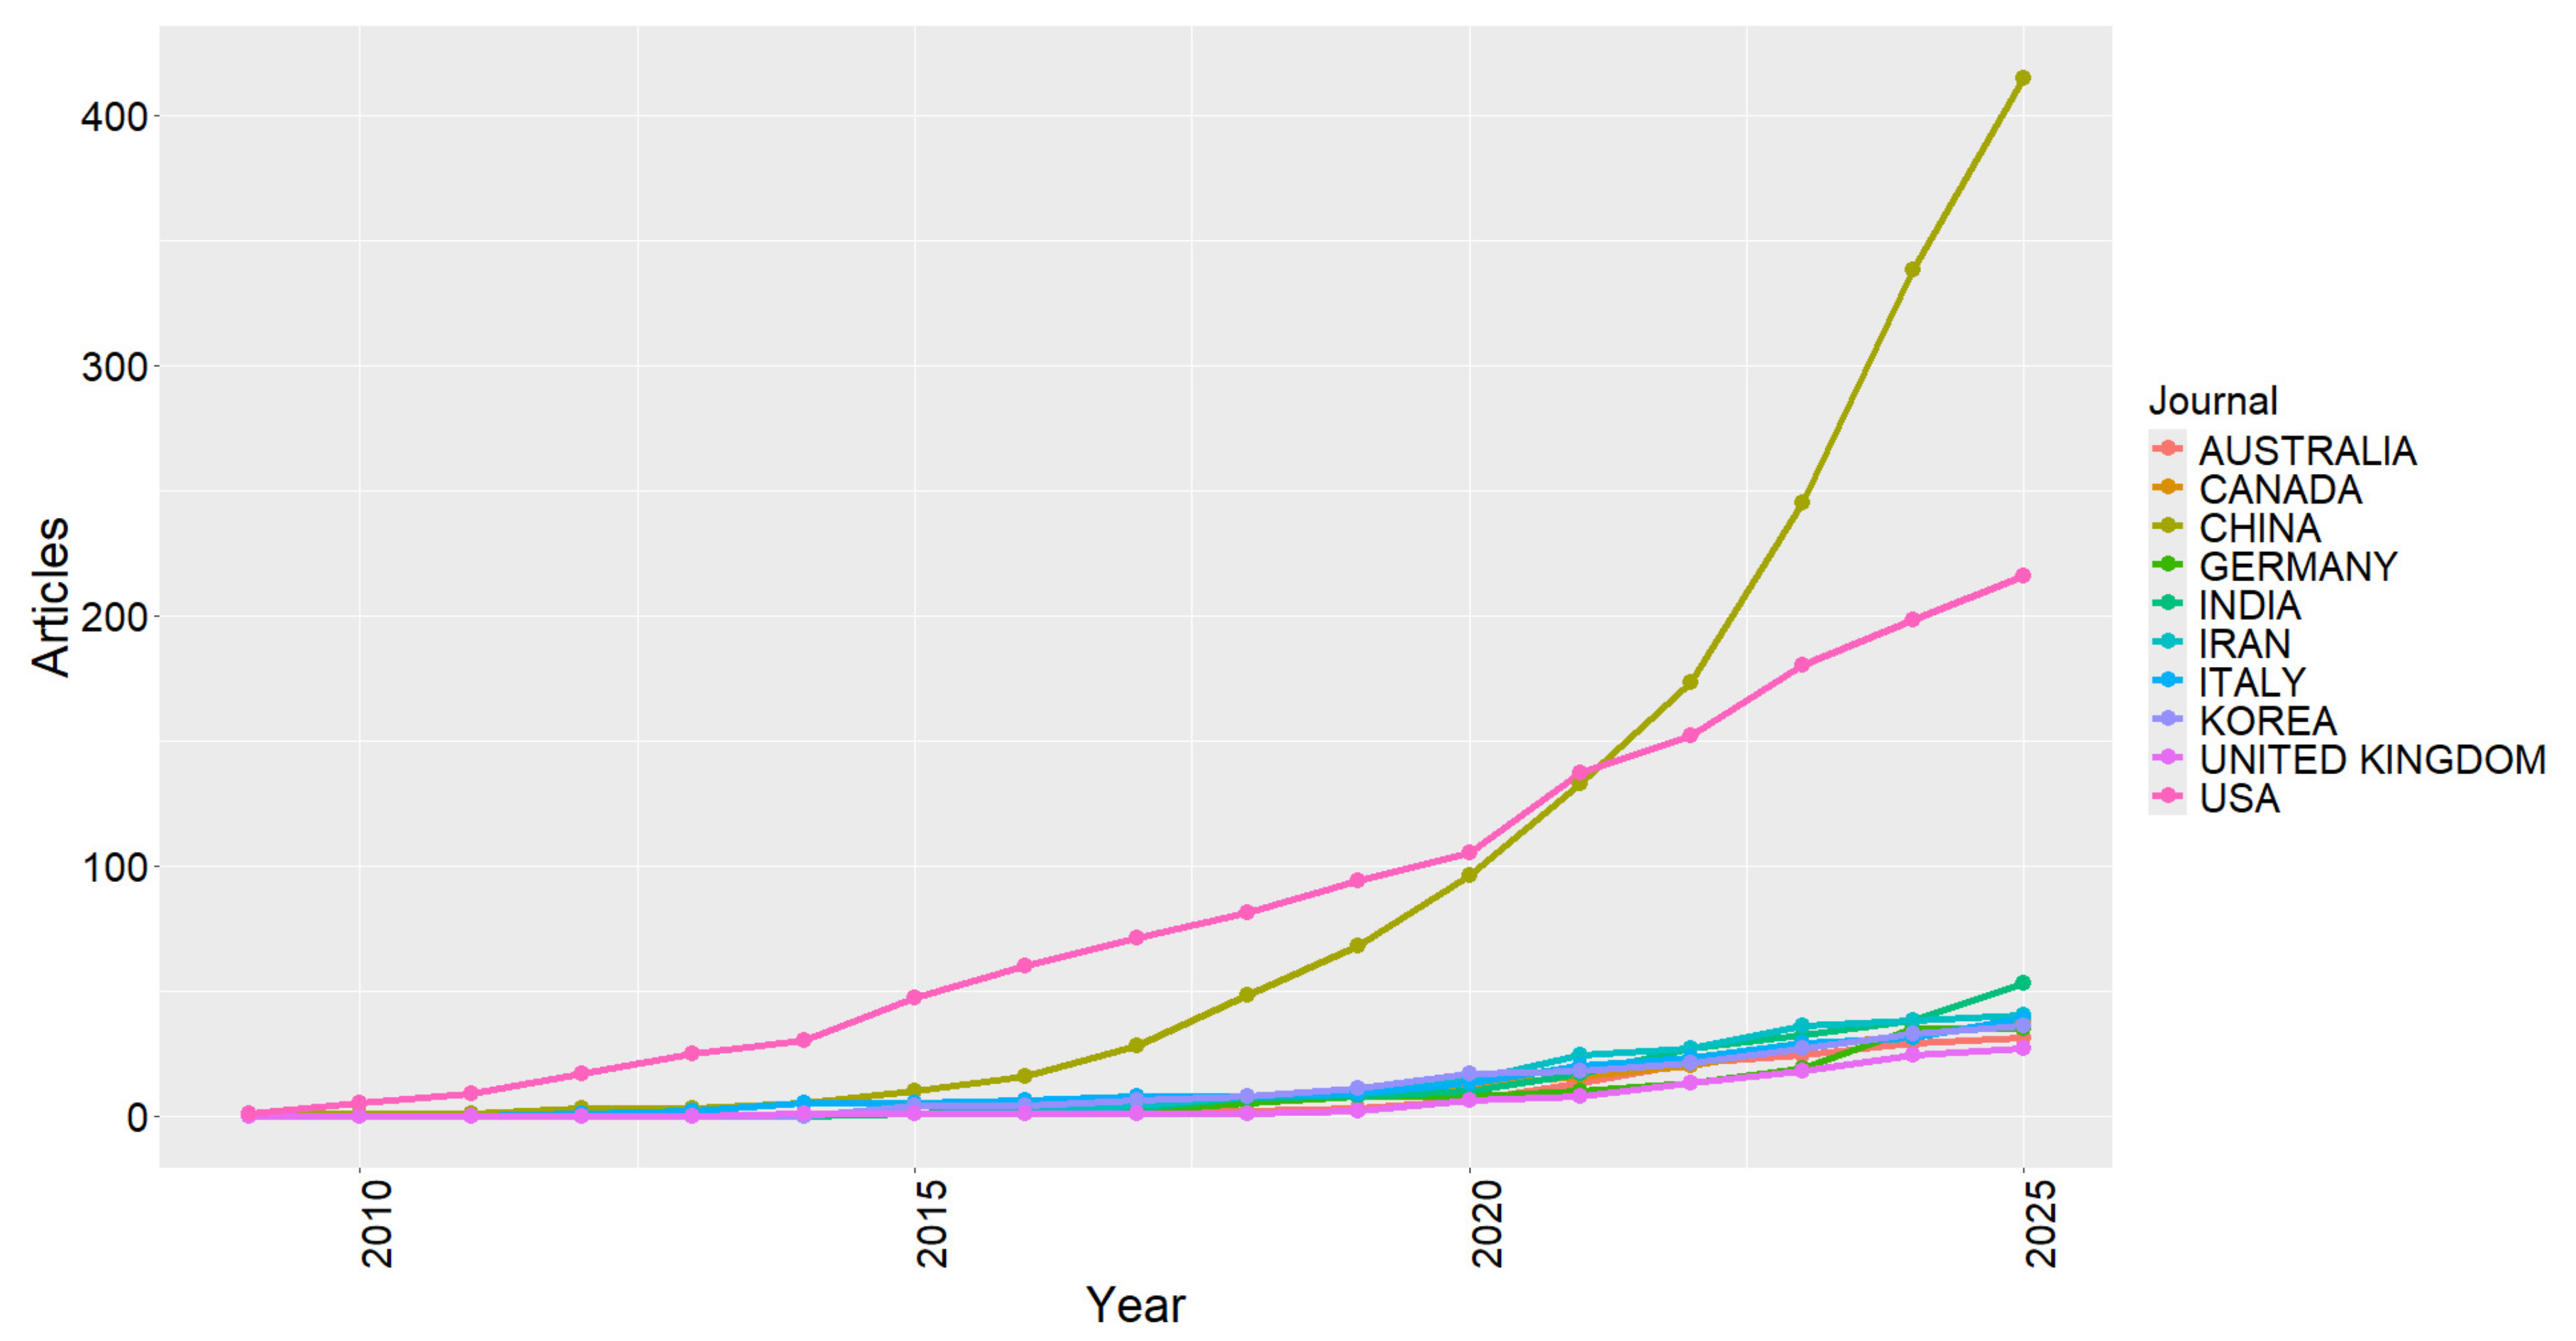
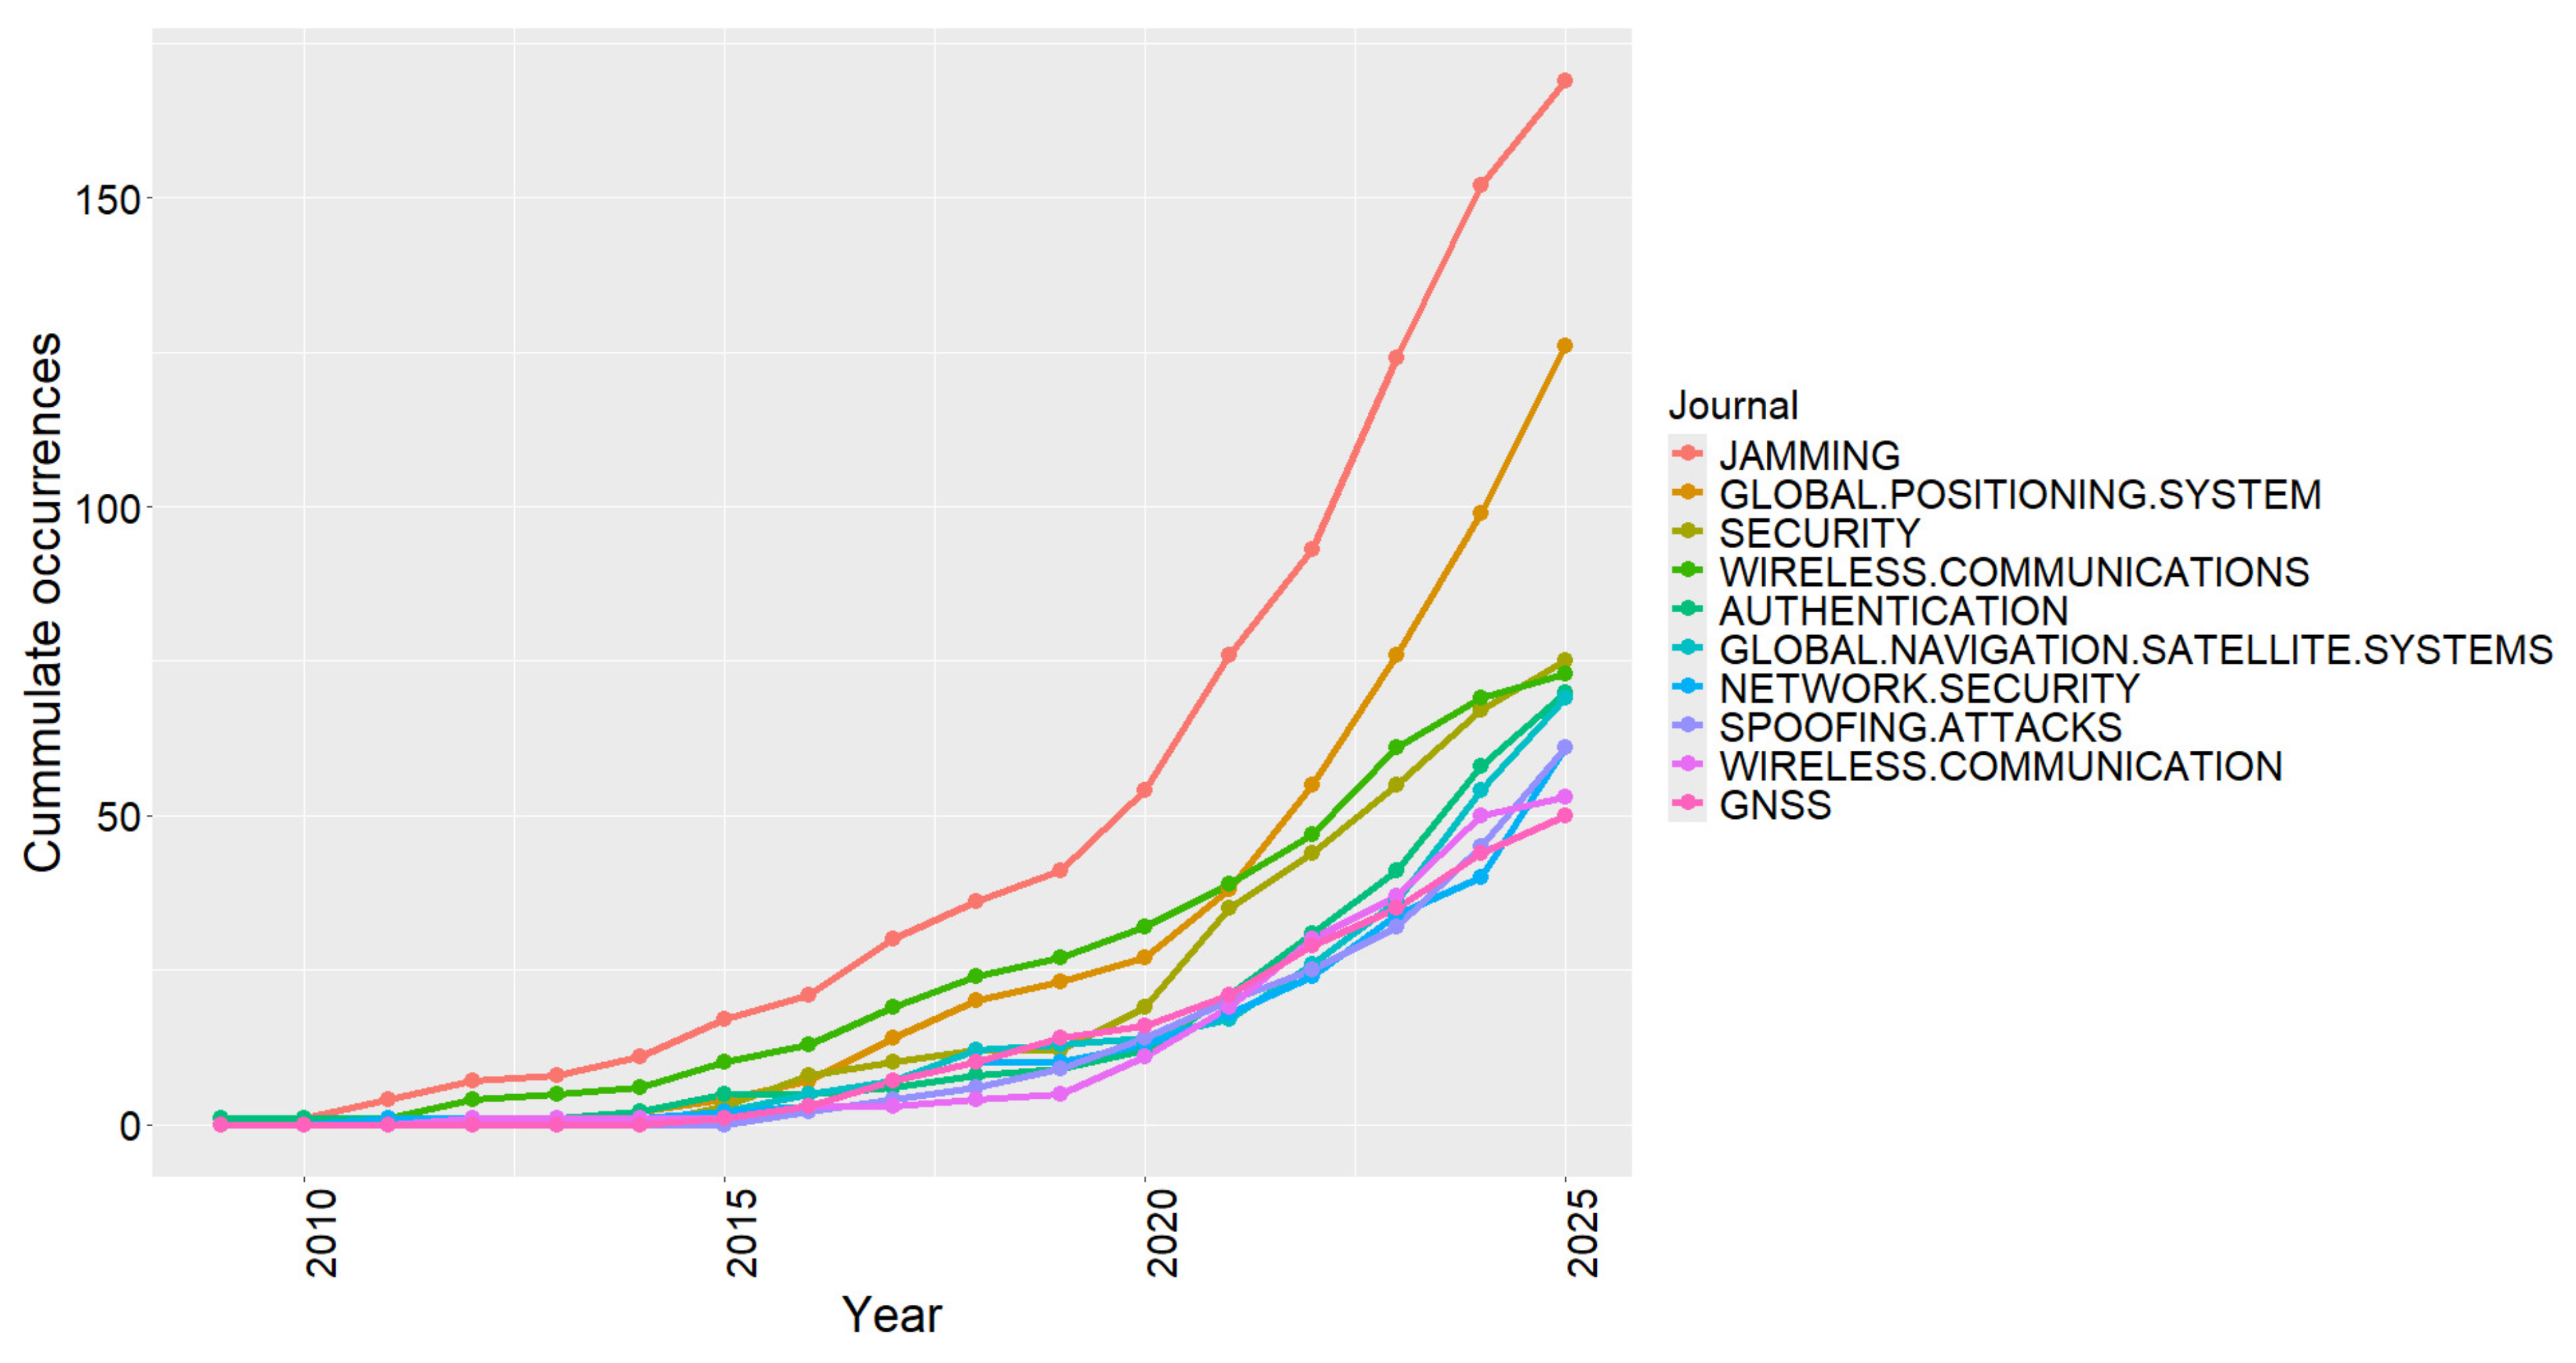
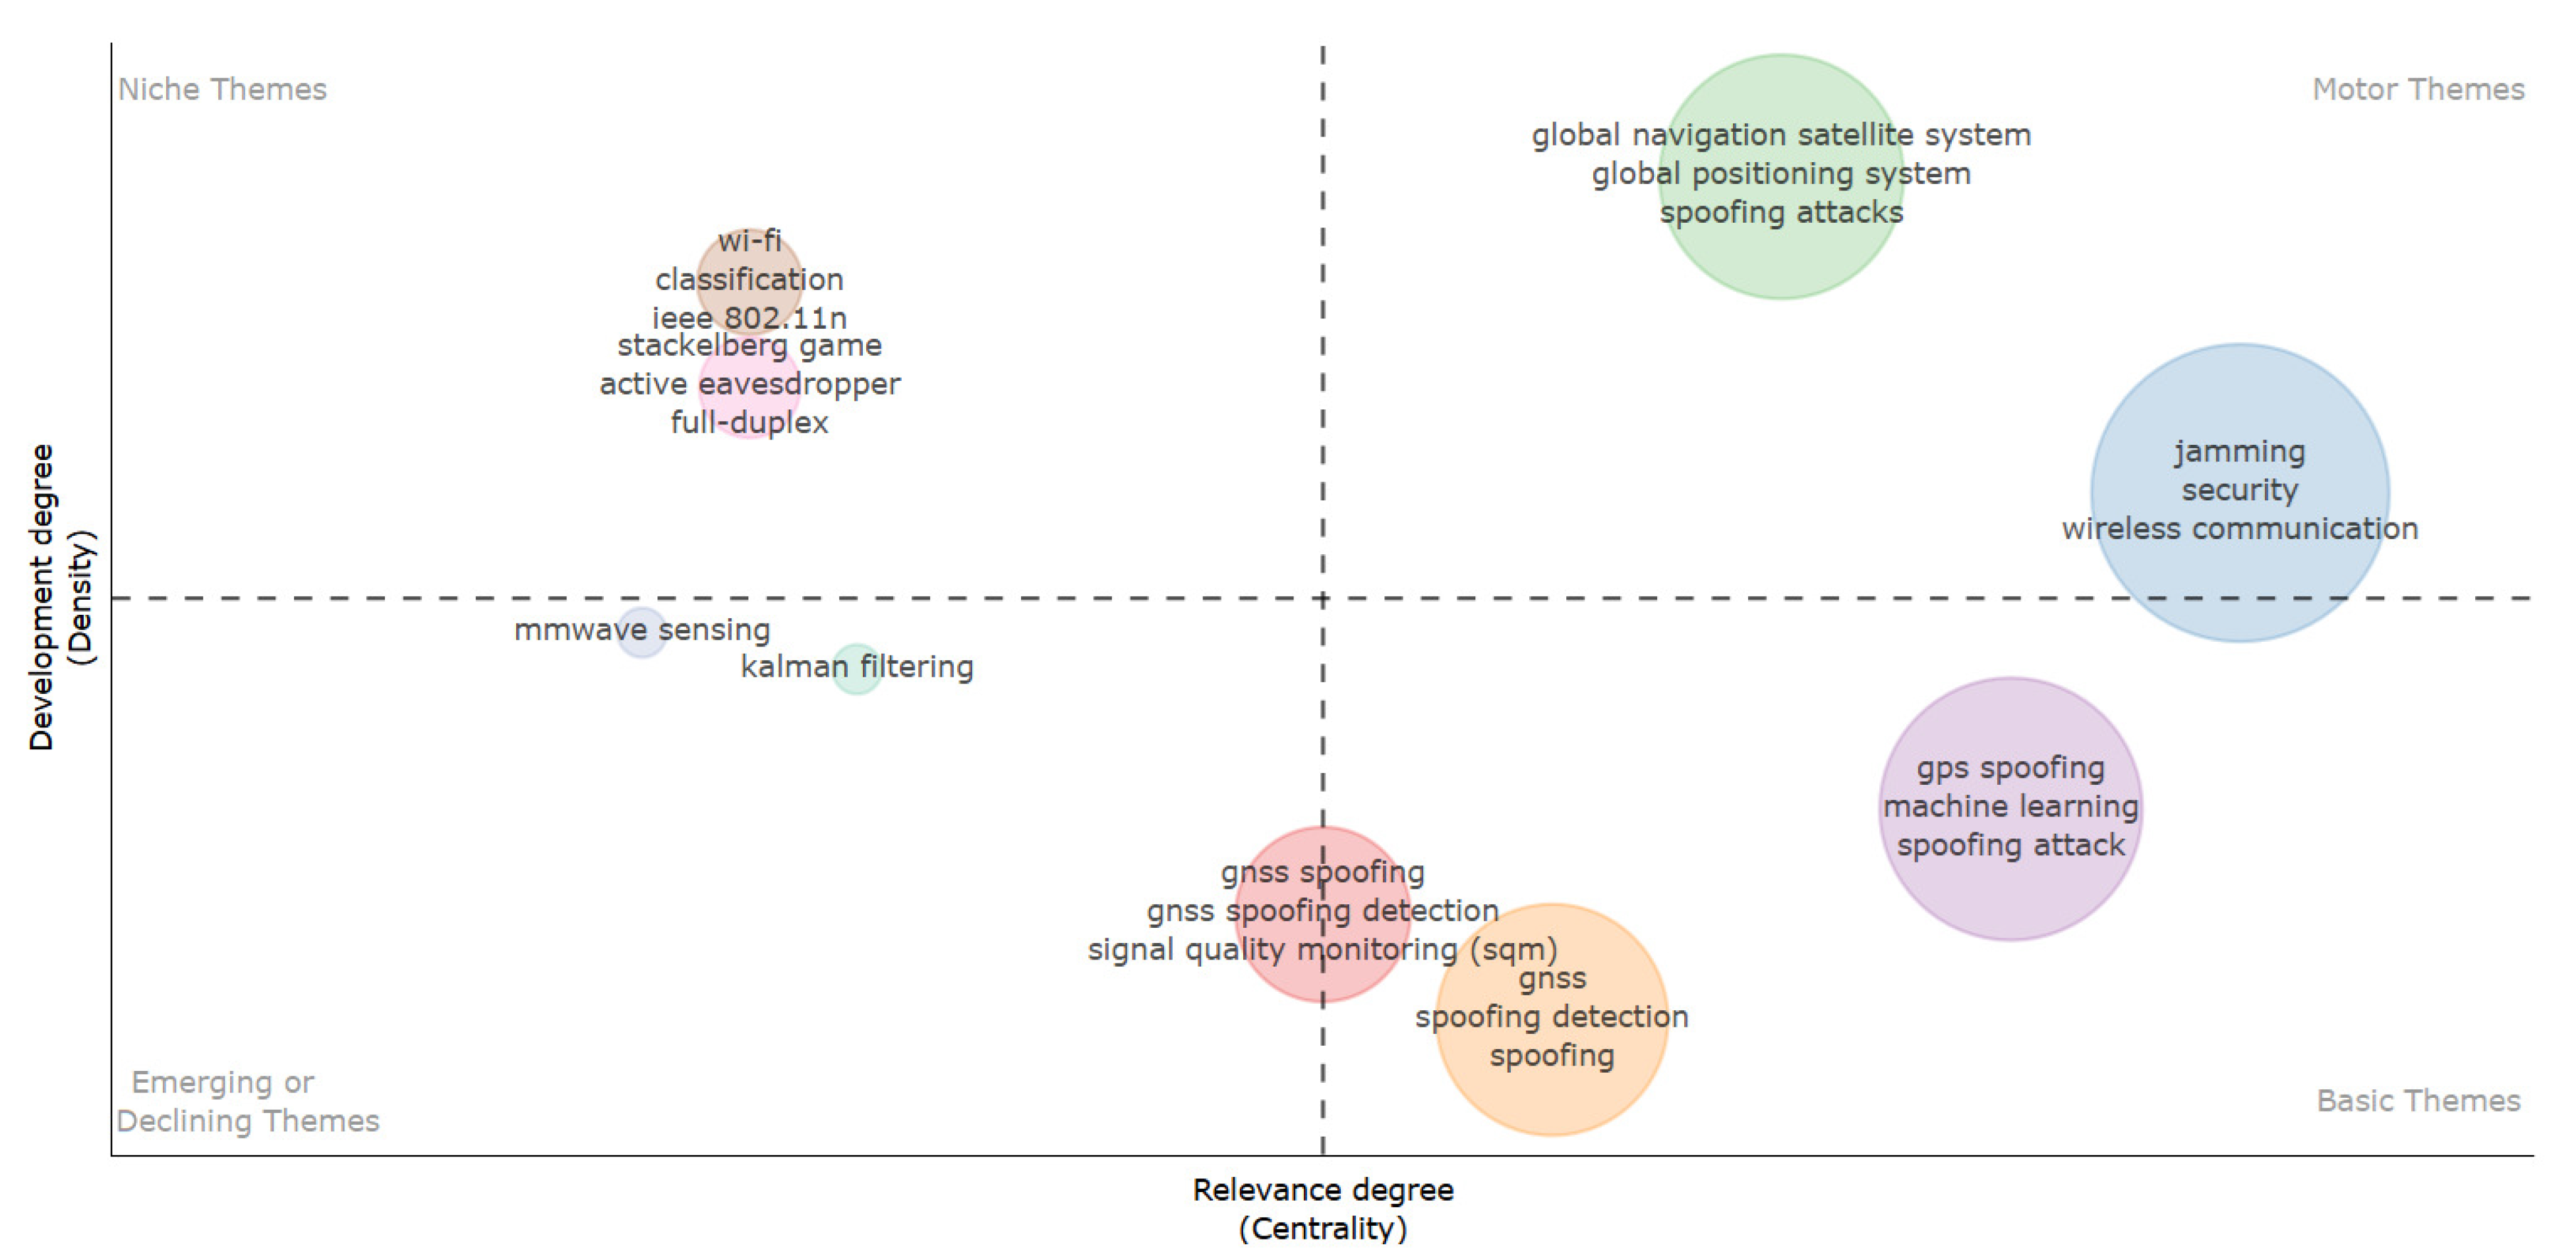
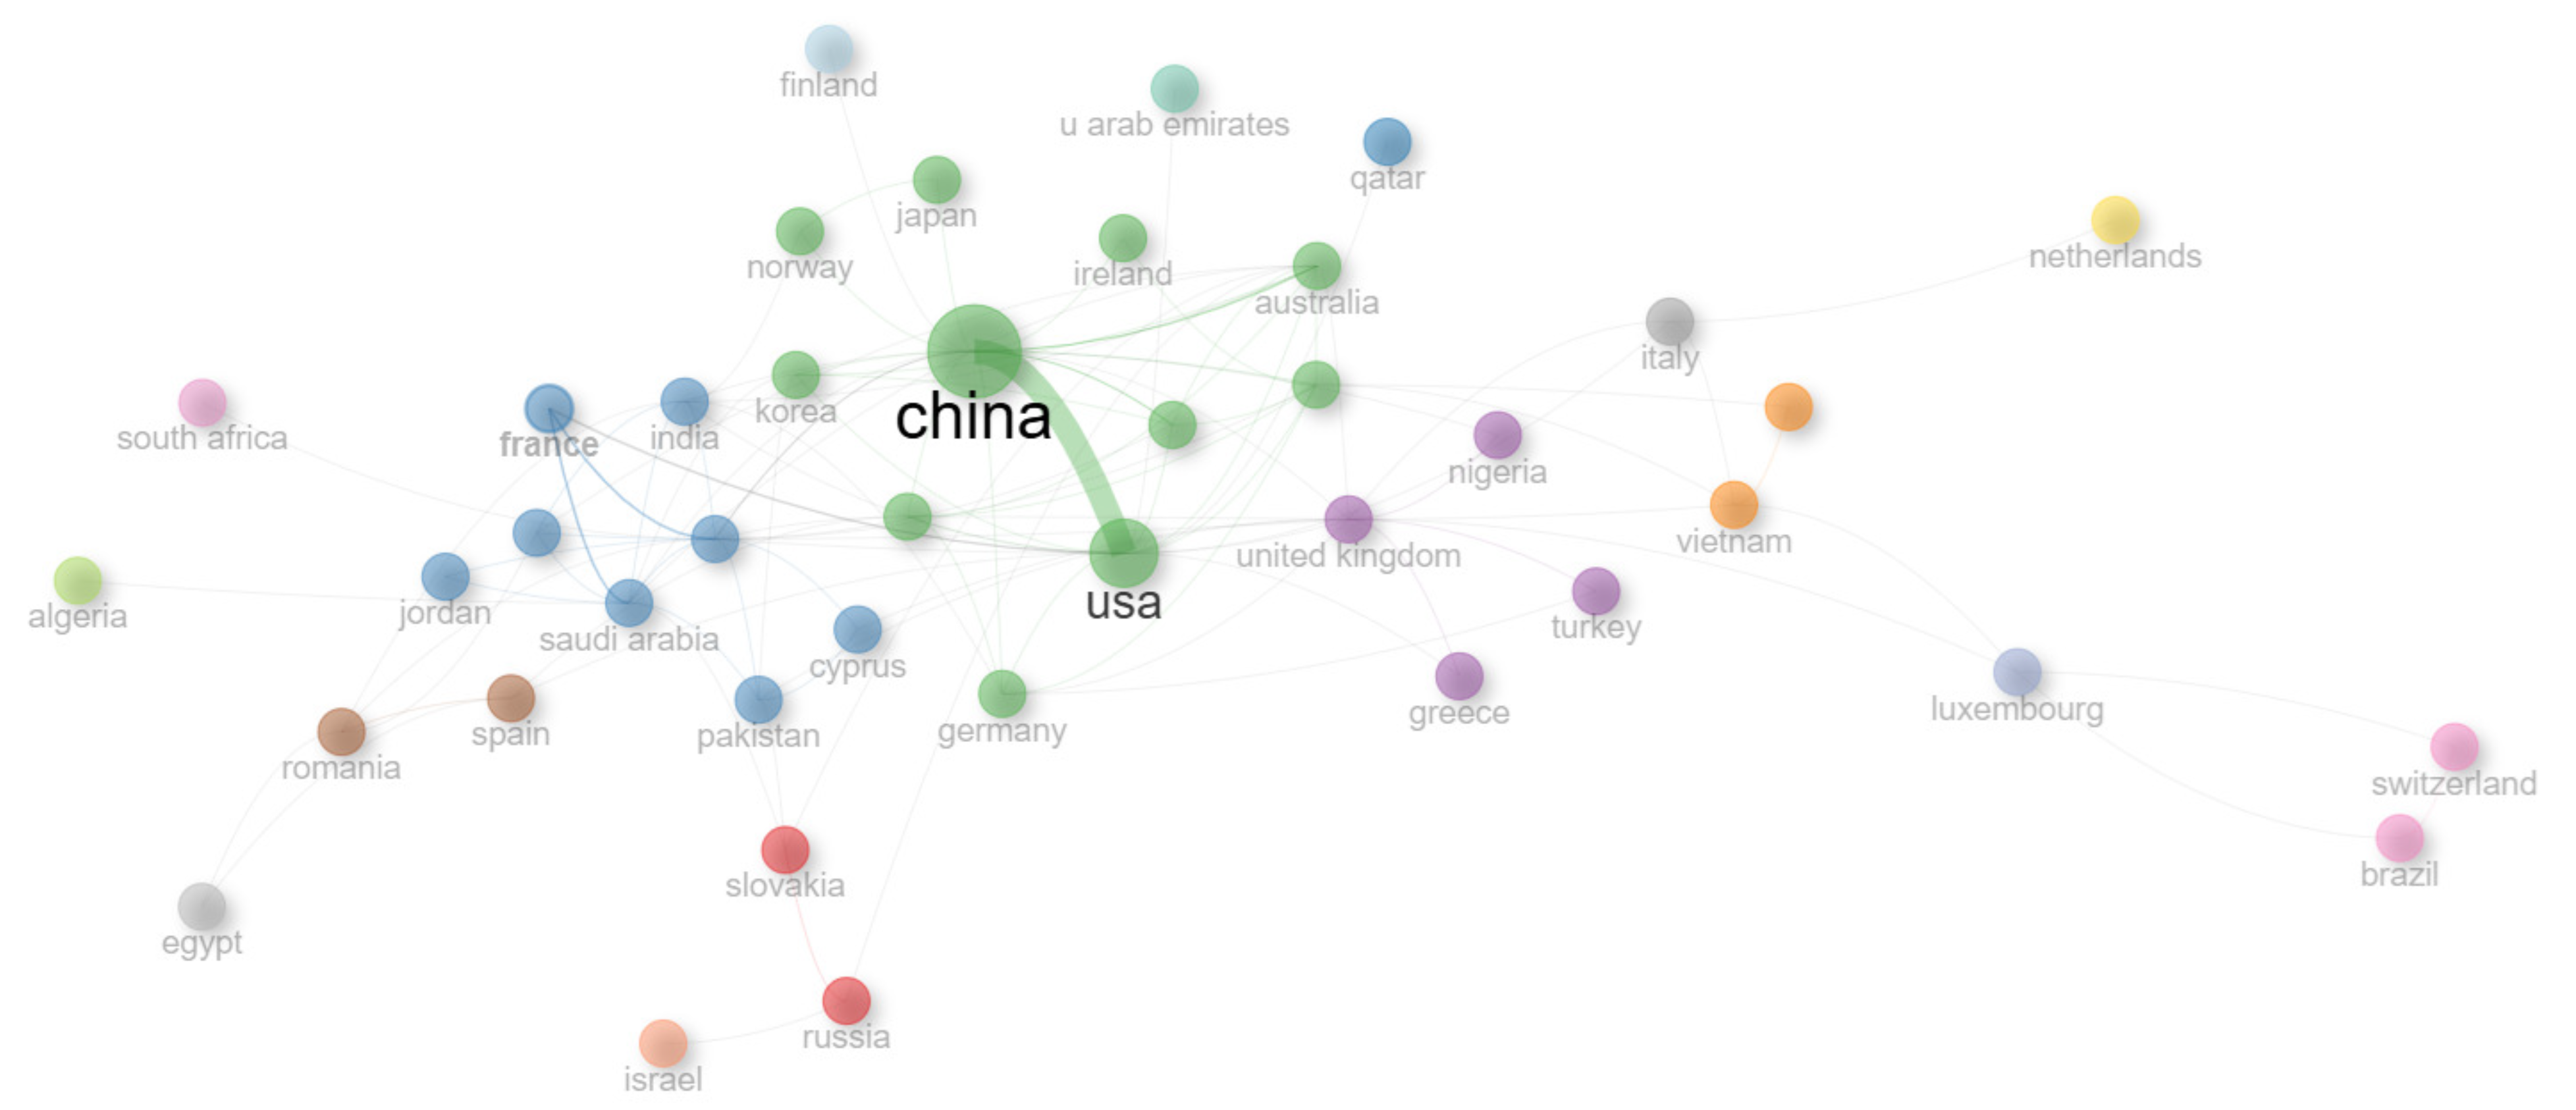
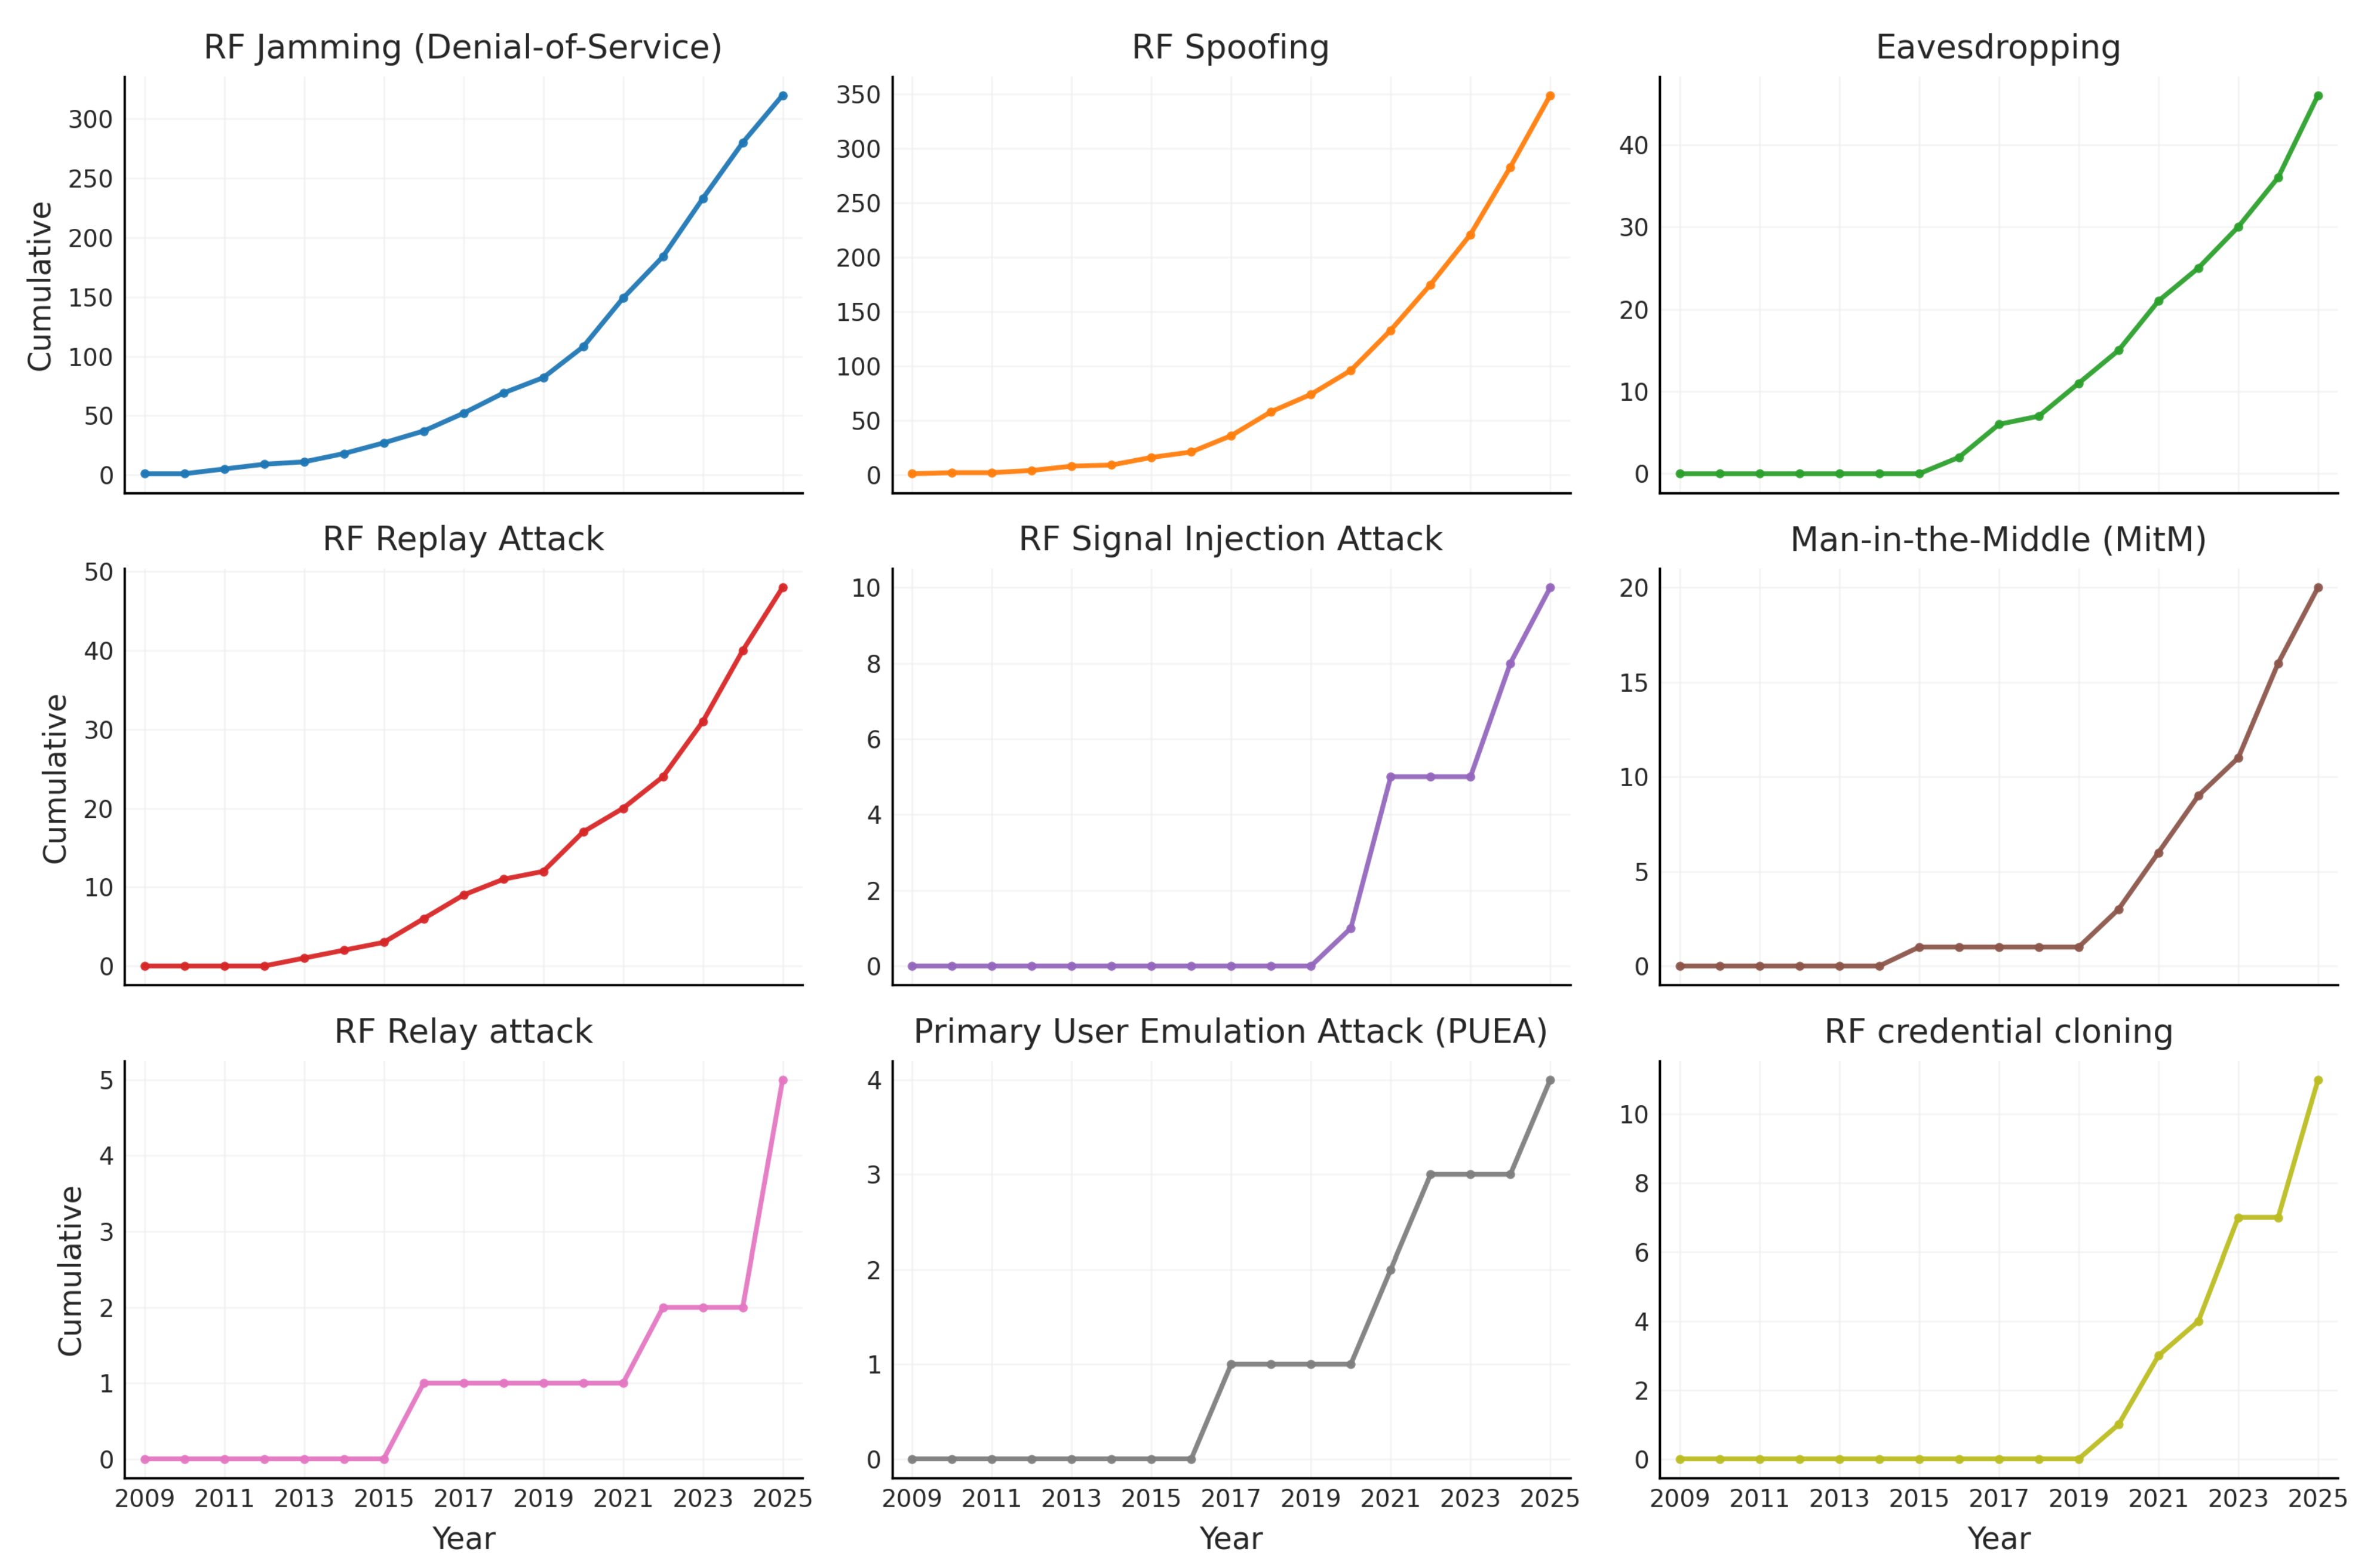
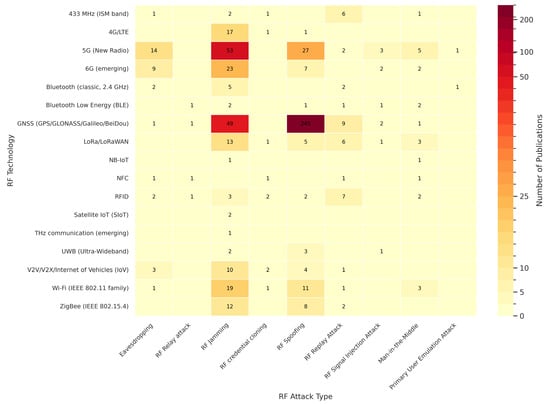
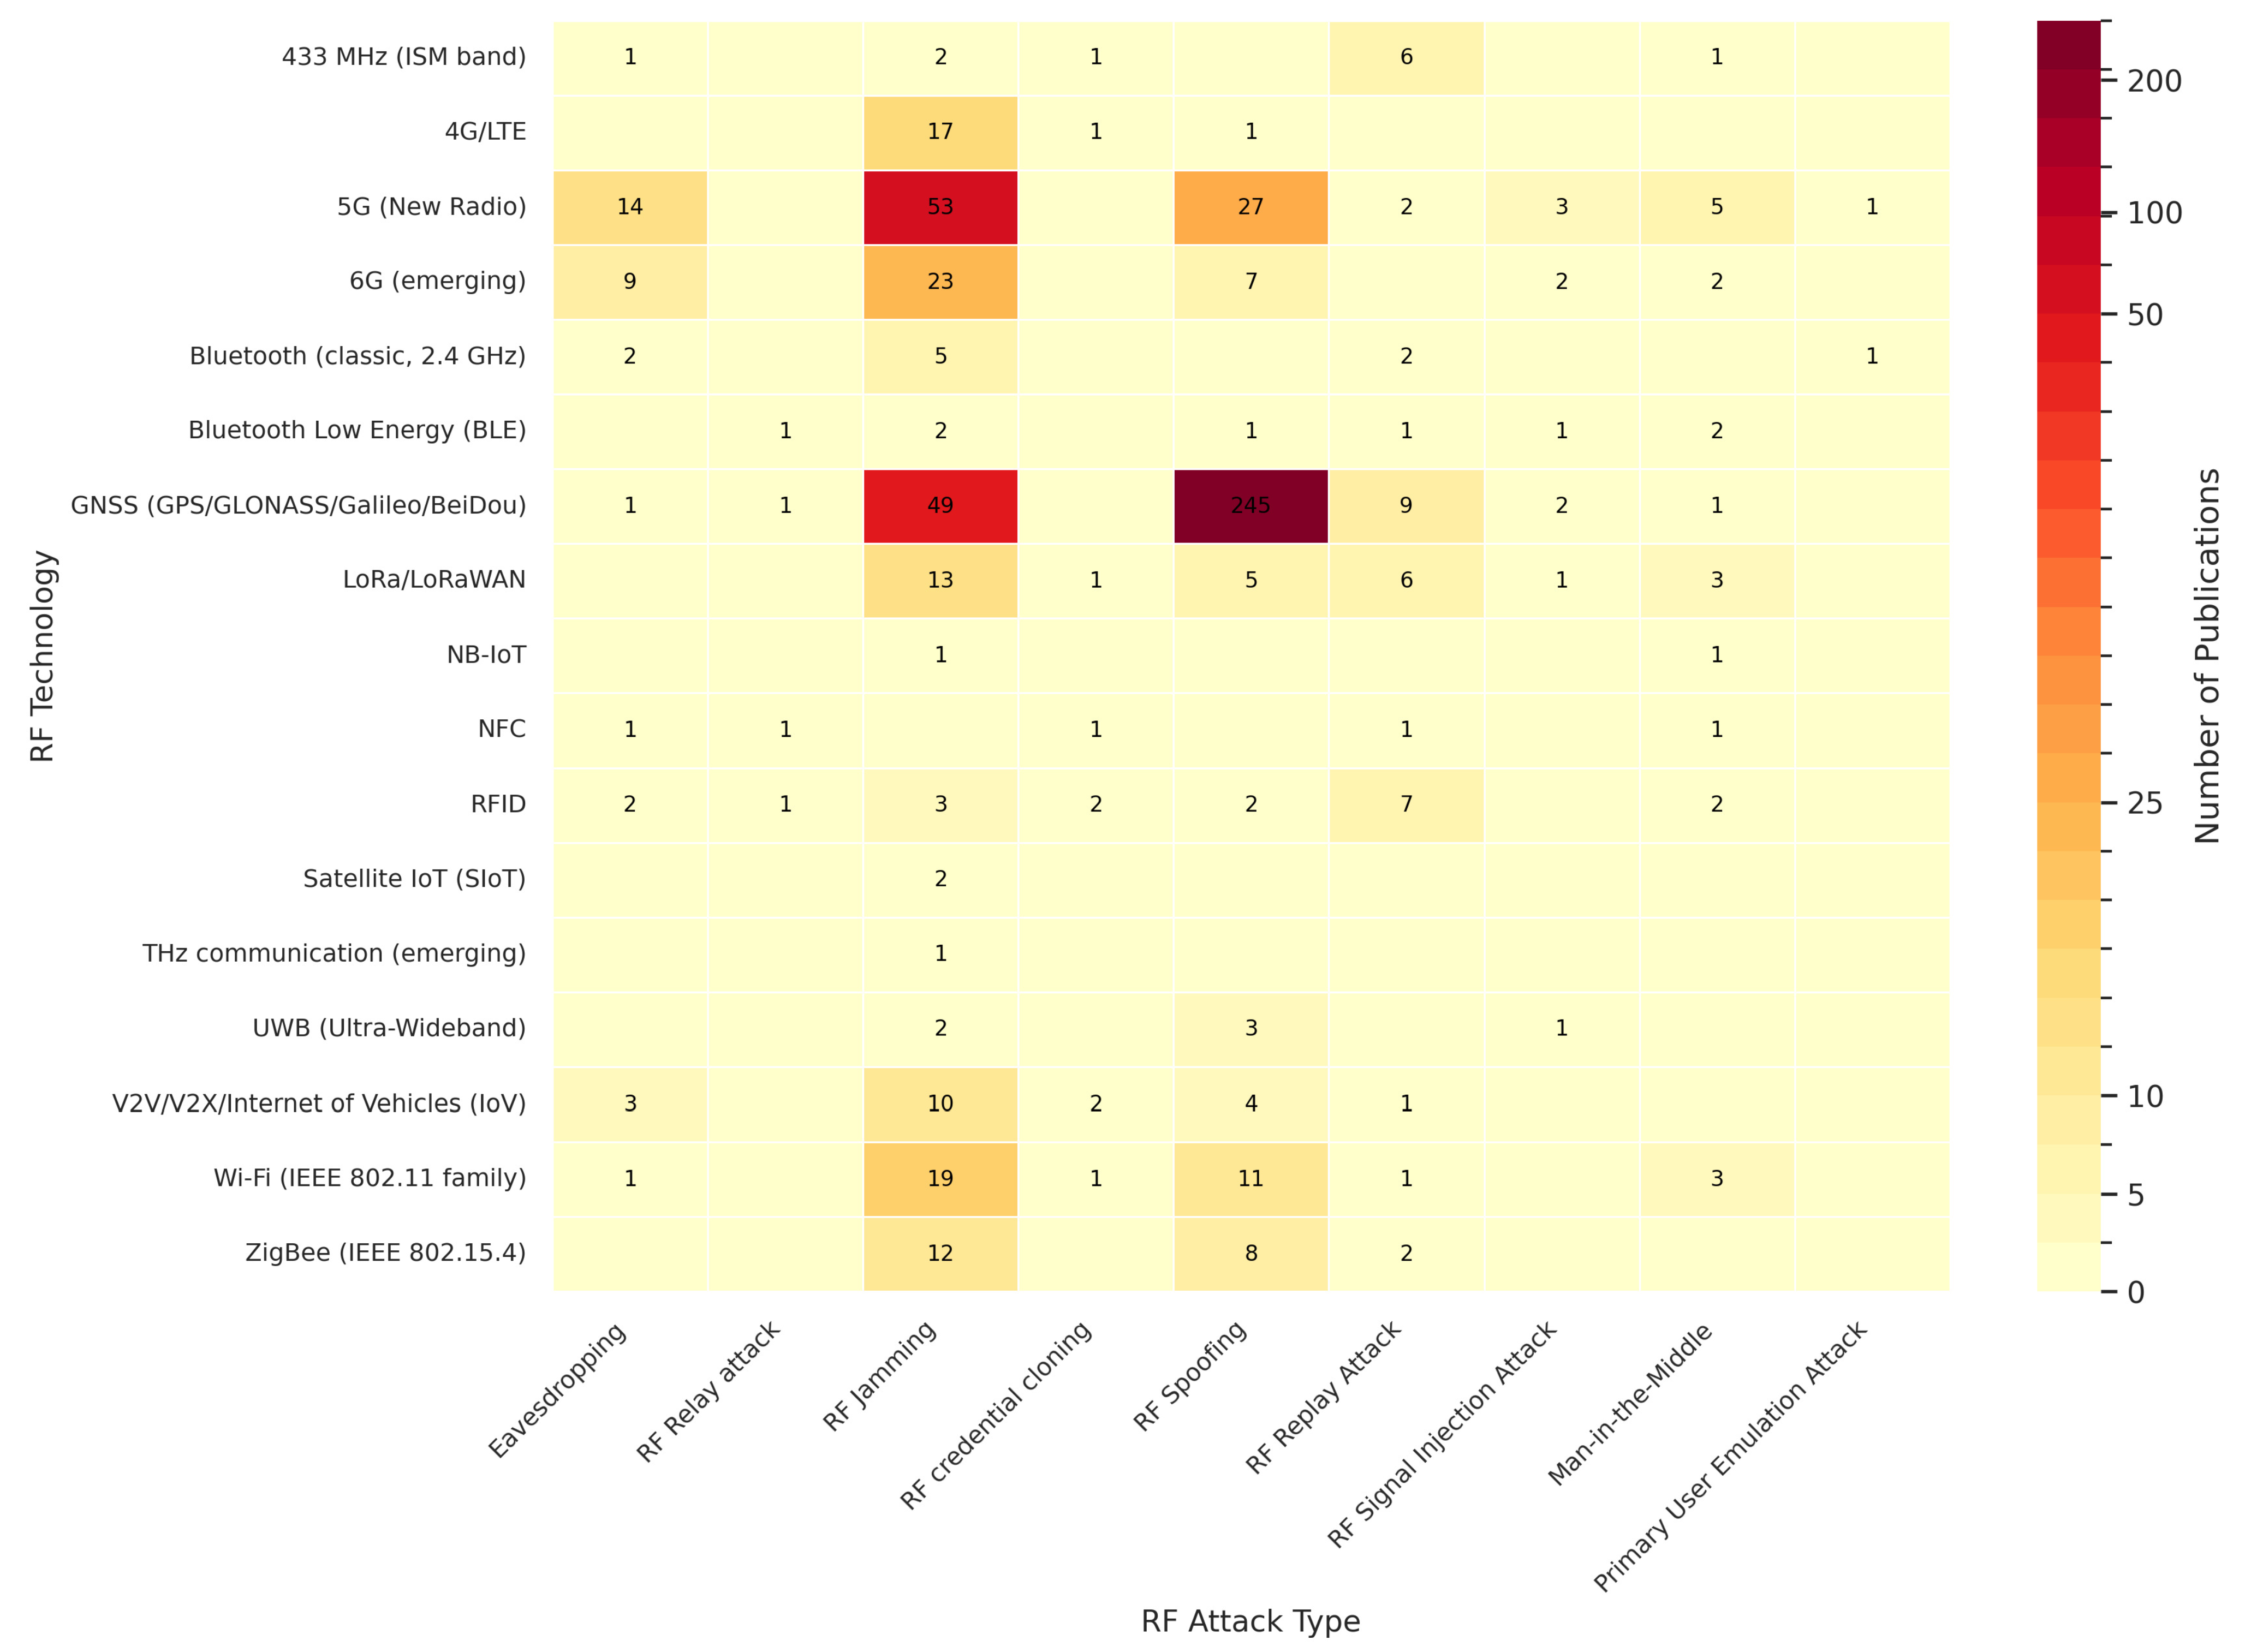

Disclaimer/Publisher’s Note: The statements, opinions and data contained in all publications are solely those of the individual author(s) and contributor(s) and not of MDPI and/or the editor(s). MDPI and/or the editor(s) disclaim responsibility for any injury to people or property resulting from any ideas, methods, instructions or products referred to in the content. |
© 2026 by the authors. Licensee MDPI, Basel, Switzerland. This article is an open access article distributed under the terms and conditions of the Creative Commons Attribution (CC BY) license.